Overview
- Type Red Team Labs
- OS Mixed
- Severity Insane
- Creator xct
- Release date 2023 Nov 25
Showcased proficiency
- Exploiting a hardened Hybrid-AD Environment without relying on publicly known vulnerabilities (CVEs)
- Exploiting Azure cloud services
- Bypassing modern EDR, WDAC & other security controls
- Exploiting common enterprise software
- No CVEs
Rule of Engagement (ROE)
Task
Your task is to conduct a red team assessment on the fictive company “Shiva Consulting”. Their main web presence can be found at https://www.shiva.vulnlab.com. Your primary goal in this engagement is to read the emails of the CEO of the company - an email with a flag was planted on his account.
It’s important to not disrupt any business activtity and be as stealthy as possible. The blue team is monitoring the situation and is authorized to take any action they deem necessary to throw attackers out of the network.
Additional Information
Inside the RTL-VPN your target range is 172.16.30.0/24. The only assets that are in scope outside of the VPN are the companies Azure AD tenant & website, make sure to not attack anything else on the internet.
When talking to online services like Azure your IP and actions will get logged by the vendor so be careful and protect yourself with rotating IPs or a VPN. A custom password spraying/guessing suffix will be posted on the internal lab channel once the lab releases.
There is only one password that needs to be guessed and it’s on the very first step - spraying over all users will likely not help.
- The entry point is cloud based - you can’t access the on-premise labs before you find secrets on an online service.
- After you found your first user, check his/her personal files to find credentials and then continue on-prem via the VPN.
- If you manage to get Global Administator notify
@xct_deimmediatly on the Vulnlab’s discord.
Completing the lab awards a badge.
Lab Rules
- Do not change anything on the cloud side. This includes not sending emails, no teams messages, no password changes - treat it as read only. Failure to follow these rules will lead to a ban from the lab.
- Do not attack any microsoft or lab infrastructure - only the lab machines and normal usage of online services used in the lab are in scope.
- Do not under any circumstances leak credentials or tokens - this includes not posting them on discord (also not in DMs) or any walkthroughs / streams / videos.
- Do not attack any infrastruture (usually IPs ending in .1 & .2, if you are unsure ask)
- Do not execute any spoofing attacks
Enumeration
Start and join the instance via Discord /rtl lab:Shiva (Insane) and let’s go:
Go to https://www.shiva.vulnlab.com:
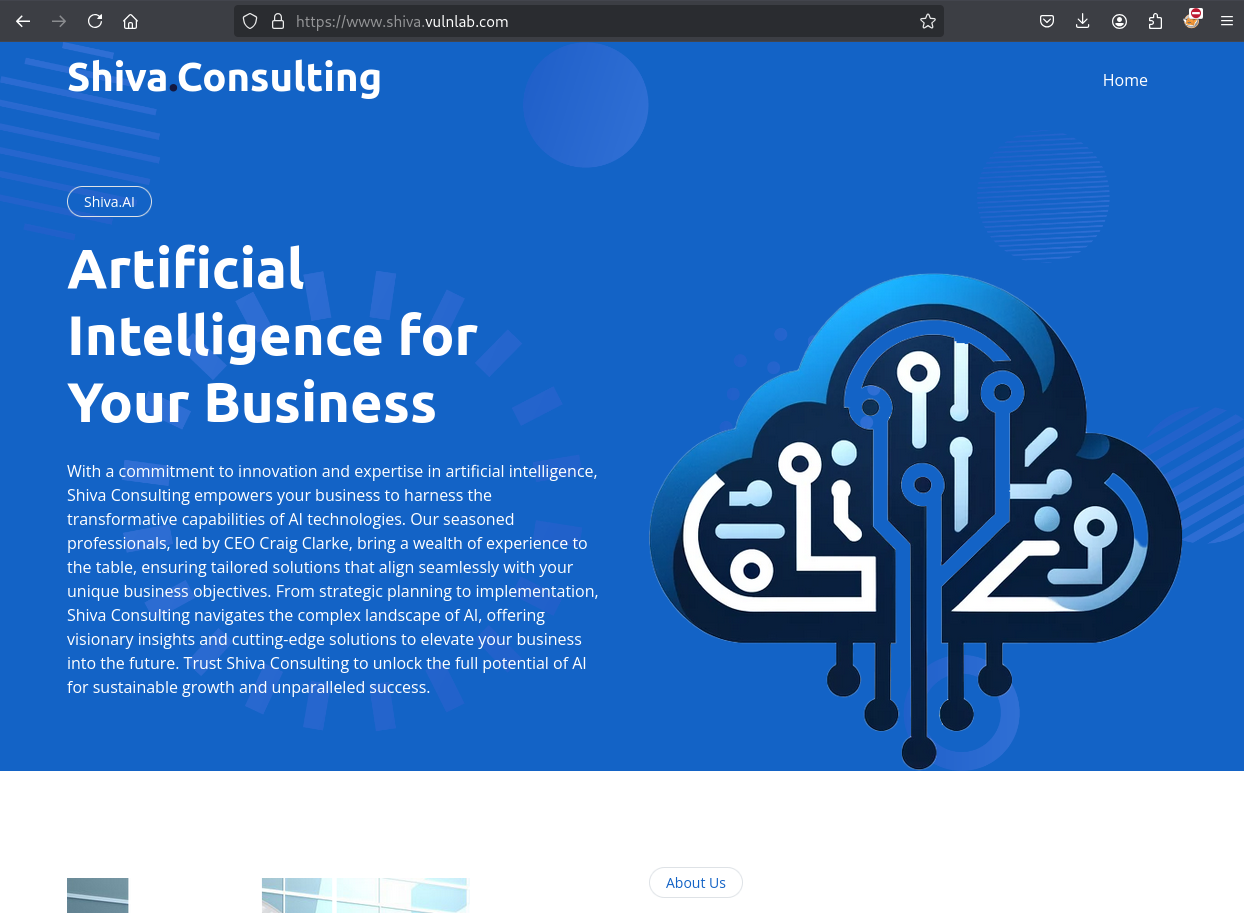
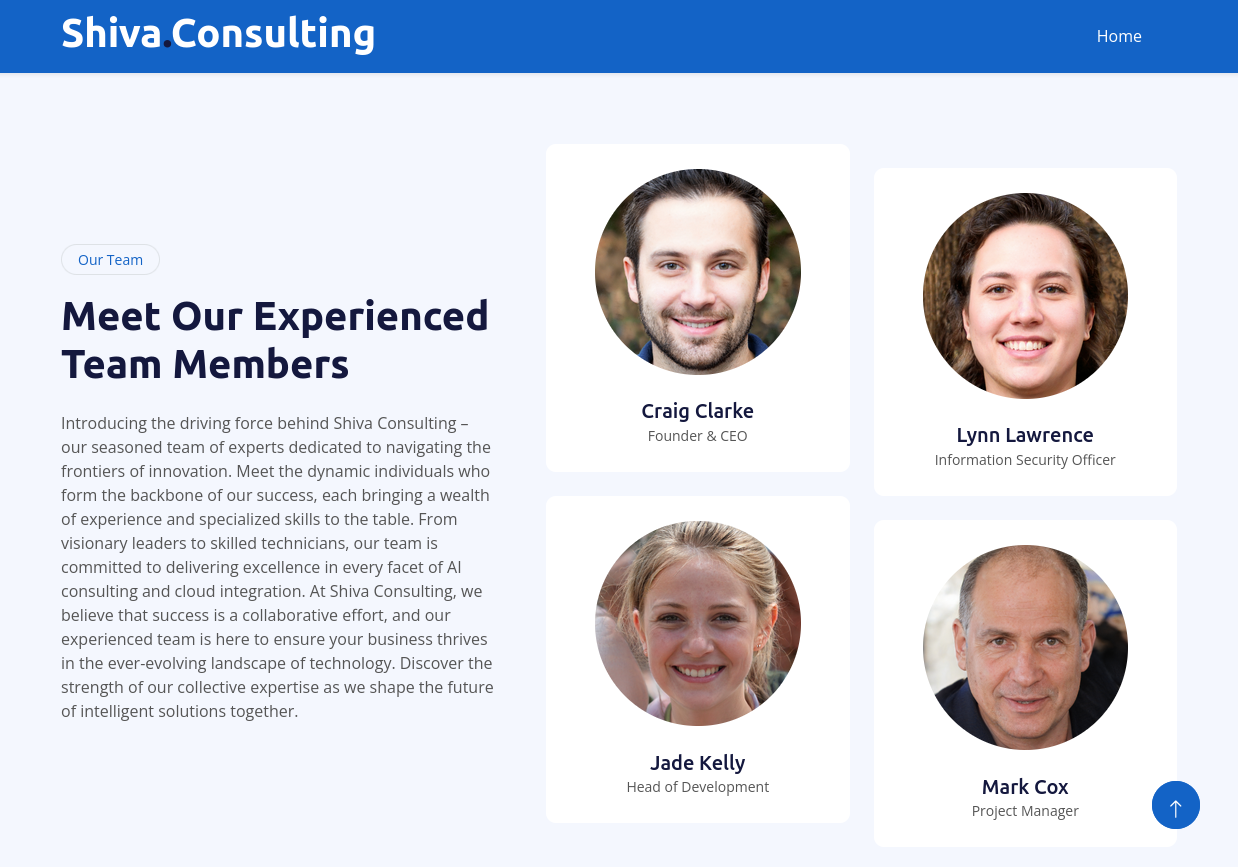
Members list including the CEO:
| Name | Role |
|---|---|
| Craig Clarke | Founder & CEO |
| Lynn Lawrence | Information Security Officer |
| Jade Kelly | Head of Development |
| Marx Cox | Project Manager |
Found
rita.gray@shiva.vulnlab.com
We found also an info about migration to the Azure Cloud.
Let’s check if rita.gray@shiva.vulnlab.com is an account existing in Microsoft Entra ID - https://entra.microsoft.com:
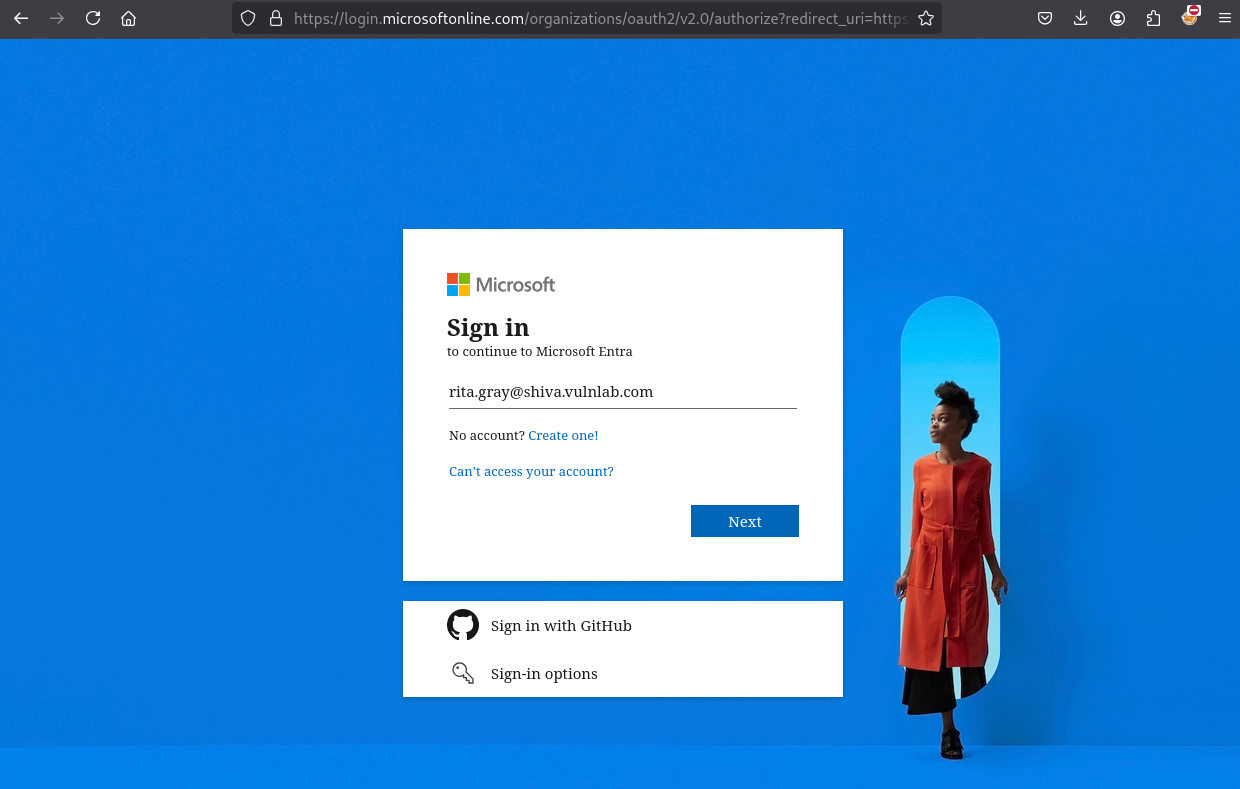
Seems account exists as a password is asked: