
Overview
- Type Red Team Labs
- OS Mixed
- Severity Medium
- Creator xct
- Release date 2023 Apr 9
Showcased proficiency
- Credential Phishing & Credential Spraying
- Active Directory Attacks with 4 Domains & Forests
- Reverse Engineering
- Custom Backdoors
- Lateral Movements across multiple Domains & Forests
- PKI Attacks
- Bypassing modern AV
Rule of Engagement (ROE)
The Wutai Group has tasked you with performing a penetration test on its networks.
This includes the Wutai Parent Company & its subsidiary Junon.
Wutai is concerned about its security posture since a leak of domain usernames was found online on pastebin.
https://pastebin.com/BBZkJGU1 (password is KE37vTed5S)
The goal of this test is to reach Enterprise Administrator in the wutai.vl domain.
Wutai employs a small SOC but its blue team capabilities are still on a rather basic level.
Wutai’s external systems can be reached through the RTL VPN on the 172.16.20.0/24 network.
Everything is in scope except the infrastructure (172.16.xx.1/172.16.xx.2).
To access the network we need to use an appropriate ovpn file: rtl-aws.ovpn.
Completing the lab awards a badge.
Enumeration
Before starting the enumeration, we will grab the users list from the pastebin:
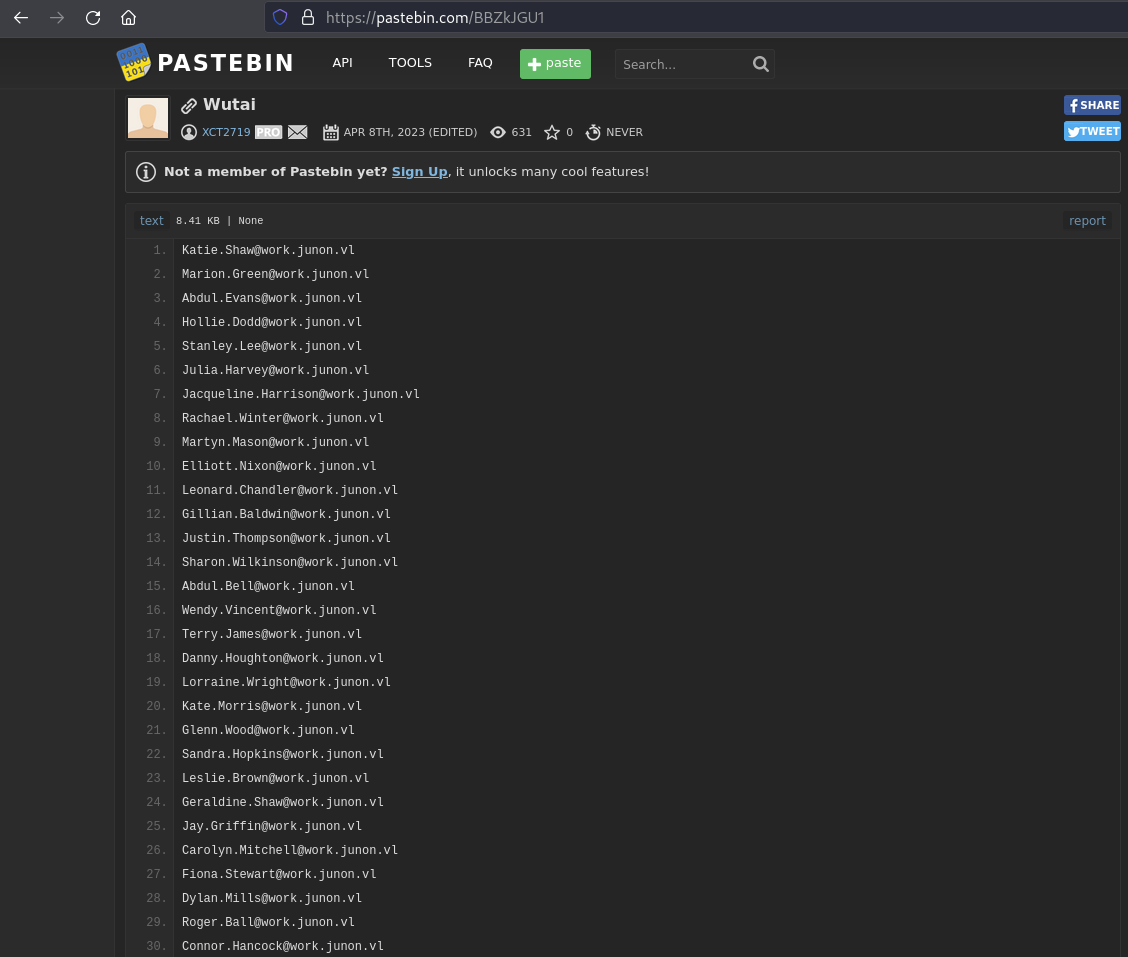
$ cut -d '@' -f 1 users_pastebin.txt | sed 's/^ *//g' > usernames.txt
$ head usernames.txt
Katie.Shaw
Marion.Green
Abdul.Evans
Hollie.Dodd
Stanley.Lee
Julia.Harvey
Jacqueline.Harrison
Rachael.Winter
Martyn.Mason
Elliott.Nixon
...
Start and join the instance via Discord /rtl lab:Wutai (Medium) and let’s go:
Nmap
Following the ROE, we will ignore .1 and .2:
$ nmap --top-ports 100 -n -T5 --max-rtt-timeout 1s --min-parallelism 100 --max-retries 1 -Pn 172.16.20.3-254
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-08-09 01:50 JST
...
Nmap scan report for 172.16.20.50
Host is up (0.23s latency).
Not shown: 98 filtered tcp ports (no-response)
PORT     STATE SERVICE
22/tcp   open  ssh
8080/tcp open  http-proxy
...
Nmap scan report for 172.16.20.100
Host is up (0.22s latency).
Not shown: 93 closed tcp ports (conn-refused)
PORT    STATE    SERVICE
22/tcp  open     ssh
53/tcp  filtered domain
143/tcp filtered imap
443/tcp open     https
548/tcp filtered afp
646/tcp filtered ldp
873/tcp filtered rsync
...
Found 2 machines Up.
$ nmap -p8080 -sC -sV -T4 -Pn 172.16.20.50
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-08-09 01:58 JST
Nmap scan report for 172.16.20.50
Host is up (0.25s latency).

PORT     STATE SERVICE    VERSION
8080/tcp open  http-proxy Squid http proxy 5.2
|_http-title: ERROR: The requested URL could not be retrieved
|_http-server-header: squid/5.2
Found a proxy squid
$ nmap -p443 -sC -sV -T4 -Pn 172.16.20.100
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-08-09 01:59 JST
Nmap scan report for 172.16.20.100
Host is up (0.24s latency).

PORT    STATE SERVICE  VERSION
443/tcp open  ssl/http nginx
|_http-title: Site doesn't have a title (text/html).
| ssl-cert: Subject: commonName=wutai-vdi-gw/organizationName=None/stateOrProvinceName=VA/countryName=US
| Not valid before: 2023-03-10T15:01:48
|_Not valid after:  2028-03-08T15:01:48
|_ssl-date: TLS randomness does not represent time
Add
wutai-vdi-gwin /etc/hosts
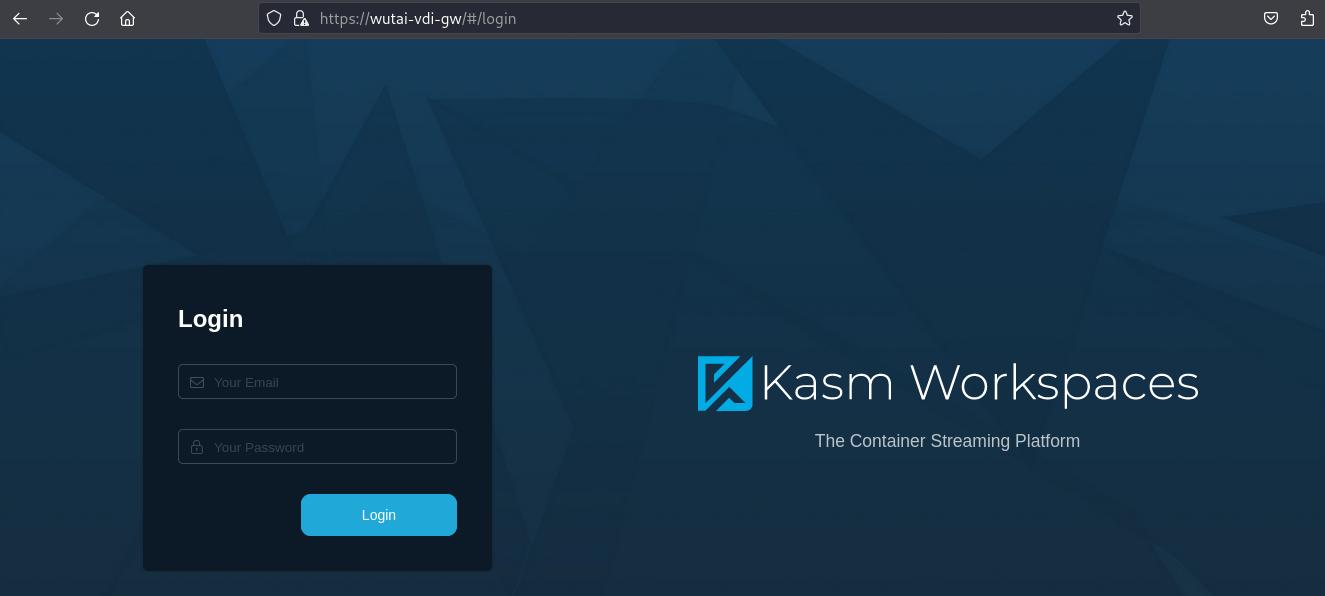
Found a VDI portal (for KASM Workspaces, kind of VDI through the browser)
We add the entry in our proxychains:
$ cat /etc/proxychains4.conf
# proxychains.conf  VER 4.x
...
[ProxyList]
# add proxy here ...
# meanwile
# defaults set to "tor"
#socks4 	127.0.0.1 9050
#socks5	127.0.0.1 1080
http 172.16.20.50 8080